Complete Technical Paper Content — Credential Stuffing Attack Detection And Prevention Tool
Overview & System Context
Credential Stuffing Attack Detection And Prevention Tool: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9549 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Credential stuffing is a type of cyberattack in which the attacker collects stolen account credentials, typically consisting of lists of usernames or email addresses and the corresponding passwords (often from a data breach), and then uses the credentials to gain unauthorized access to user accounts on other systems through large-scale automated login requests directed against a web application. Unlike credential cracking, credential stuffing attacks do not attempt to use brute force or guess any passwords – the attacker simply automates the logins for a large number (thousands to millions) of previously discovered credential pairs using standard web automation tools such as Selenium, cURL, PhantomJS or tools designed specifically for these types of attacks, such as Sentry MBA, SNIPR, STORM, Blackbullet and Openbullet. Credential stuffing attacks are possible because many users reuse the same username/password combination across multiple sites, with one survey reporting that 81% of users have reused a password across two or more sites and 25% of users use the same passwords across a majority of their accounts. In 2017, the FTC issued an advisory suggesting specific actions companies needed to take against credential stuffing, such as insisting on secure passwords and guarding against attacks. According to former Google click fraud czar Shuman Ghosemajumder, credential stuffing attacks have up to a 2% login success rate, meaning that one million stolen credentials can take over 20,000 accounts. Wired magazine described that the best way to protect against credential stuffing is to use unique passwords on accounts (such as those generated automatically by a password manager), enable two-factor authentication, and to have companies detect and stop credential stuffing attacks.
There have been many debates on the social effects of video games on players and broader society, as well as debates within the video game industry. Since the early 2000s, advocates of video games have emphasized their use as an expressive medium, arguing for their protection under the laws governing freedom of speech and also as an educational tool. Detractors argue that video games are harmful and therefore should be subject to legislative oversight and restrictions. The positive and alleged negative characteristics and effects of video games are the subject of scientific study. Academic research has examined the links between video games and addiction, aggression, violence, social development, and a variety of stereotyping and sexual morality issues.
I think the way the game is written is that when you first start playing it, it is fun, and you make great accomplishments. And then the further you get into it, the higher level you get, the longer you have to stay on it to move onward, and then it isn't fun anymore. But by then you're addicted, and you can't leave it." Later video game controversies centered on whether some murderers were inspired by crime simulators. In February 2003, 16-year-old American Dustin Lynch was charged with aggravated murder. He pleaded insanity in that he was obsessed with Grand Theft Auto III. Jack Thompson, attorney and opponent of video games, offered to represent Lynch. Thompson encouraged the father of the victim to pass a note to the judge that read "the attorneys had better tell the jury about the violent video game that trained this kid [and] showed him how to kill our daughter, JoLynn. If they don't, I will." Lynch later retracted his insanity plea. His mother, Jerrilyn Thomas, said: It has nothing to do with video games or Paxil, and my son's no murderer. He pled guilty to the charges against the advice of his attorney in December 2003. On 7 June 2003, 18-year-old American Devin Moore shot and killed two policemen and a dispatcher after grabbing one of the officers' weapons following an arrest for the possession of a stolen vehicle. At trial, the defense claimed that Moore had been inspired by the video game Grand Theft Auto: Vice City. On 25 June 2003, two American step brothers, Joshua and William Buckner, aged 14 and 16, respectively, used a rifle to fire at vehicles on Interstate 40 in Tennessee, killing a 45-year-old man and wounding a 19-year-old woman. The two shooters told investigators they had been inspired by Grand Theft Auto III. In June 2007, 22-year-old Texan Alejandro Garcia shot and killed his cousin after arguing over whose turn it was to play the game Scarface: The World Is Yours. He pleaded guilty at his murder trial on 6 April 2011, and was sentenced to 15 to 30 years in prison. In September 2007, in Ohio, 16-year-old Daniel Petric sneaked out of his bedroom window to purchase the game Halo 3 against the orders of his father, a minister at New Life Assembly of God in Wellington, Ohio, His parents eventually banned him from the game after he spent up to 18 hours a day with it, and secured it in a lockbox in a closet where the father also kept a 9mm handgun according to prosecutors. In October 2007, Daniel used his father's key to open the lockbox and remove the gun and the game. He then entered the living room of his house and shot both of them in the head, killing his mother and wounding his father. Petric was sentenced to life with a minimum of 23 years in prison. Defense attorneys argued that Petric was influenced by video game addiction. The court dismissed these claims.
The judge, James Burge, commented that while he thought there was ample evidence the boy knew what he was doing, Burge thought the game had affected him like a drug, saying "I firmly believe that Daniel Petric had no idea at the time he hatched this plot that if he killed his parents they would be dead forever." In December 2007, 17-year-old Lamar Roberts and his 16-year-old girlfriend, Heather Trujillo, were accused of beating a 7-year-old girl to death. They were said to have been imitating the content of Mortal Kombat. In July 2008, Heather was sentenced to 18 years in prison and 6 years in a youth-offender program, and, on 16 January 2009, Lamar was sentenced to 36 years in prison. In June 2008, four teens allegedly obsessed with Grand Theft Auto IV went on a crime spree after being in New Hyde Park, New York. They first robbed a man, knocking out his teeth and then they stopped a woman driving a black BMW and stole her car and her cigarettes. In April 2009, Joseph Johnson III was charged with murder after shooting his friend, Danny Taylor, during a quarrel over a video game in Taylor's apartment in Chicago, Illinois.
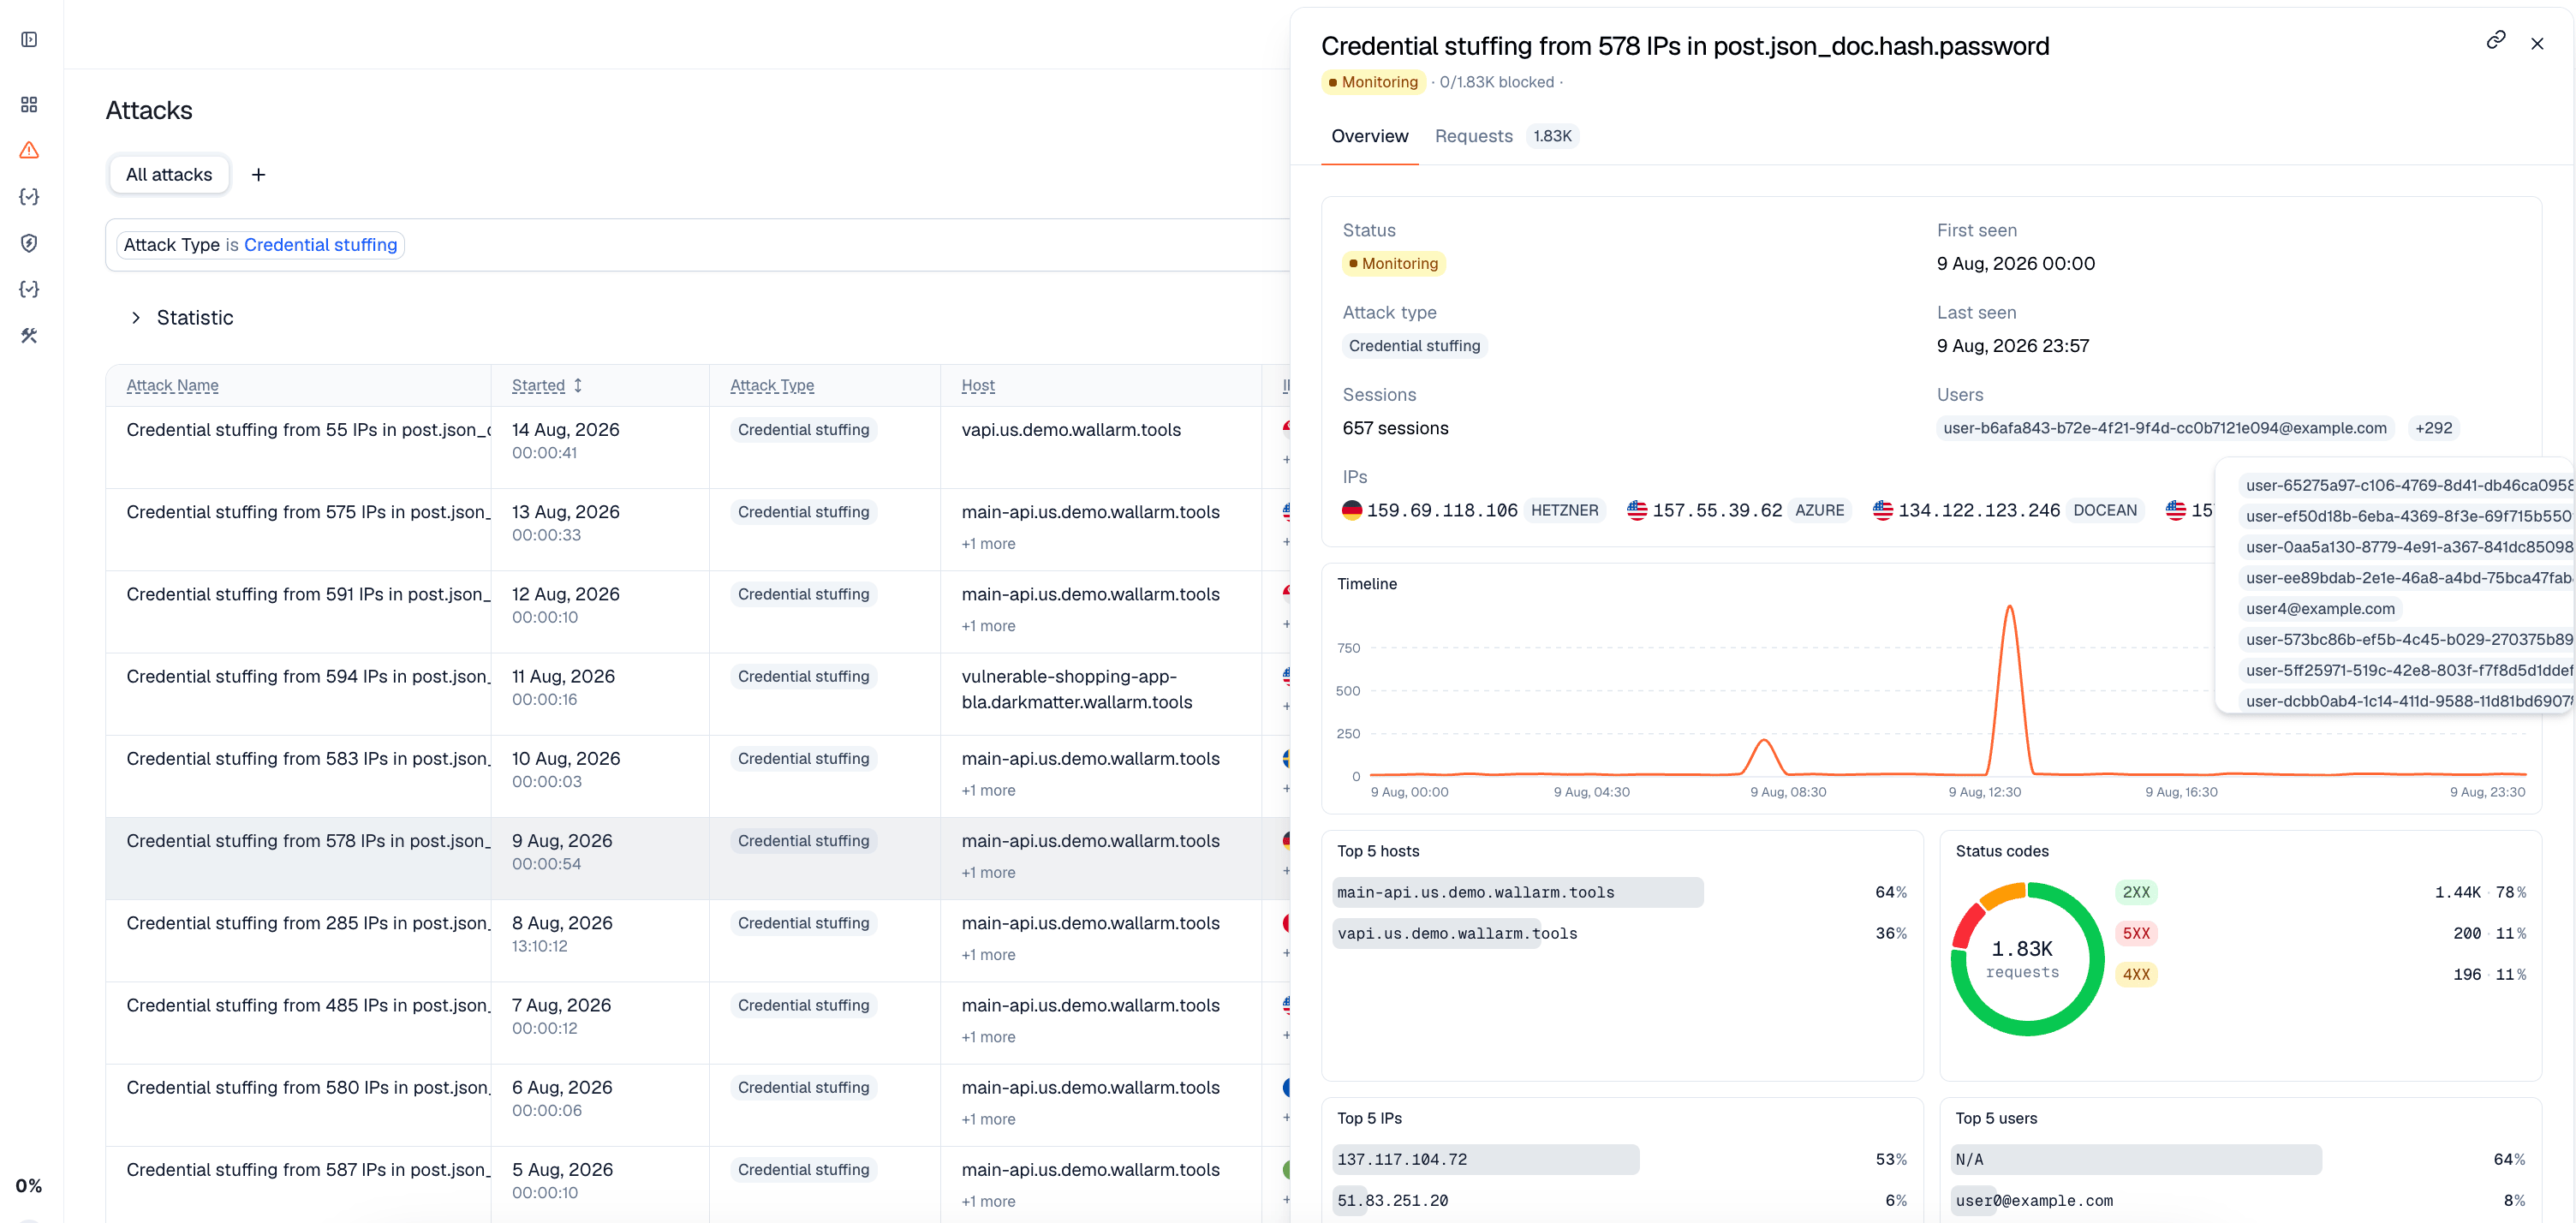
Figure 1: Credential Stuffing Detection - Wallarm Documentation Tolerance of sexual themes in video games varies between nations. Controversy over sexual themes has occurred in the US. For instance, in June 2005, an entire portion of unused code was found within the main script of Grand Theft Auto: San Andreas, allowing the player to simulate sexual intercourse with the main character's girlfriends. This mode, Hot Coffee, could be accessed in the PC version via mod, and through Action Replay codes in the PS2 and Xbox versions. The scene was left on the disc and could be accessed by altering a few bytes of the game's code via a hex editor. This feature prompted the Entertainment Software Rating Board (ESRB) to change the rating of San Andreas on 20 July 2005 to "adults only".
Furthermore, the game was withdrawn from sale in many stores. Rockstar Games posted a loss of $28.8 million in that financial quarter. This event was dubbed the Hot Coffee mod controversy. In Japan, controversy over an eroge called Rape in 1989 led to the game being banned a few months after its release. The game RapeLay, a Japanese eroge with a storyline centering on the player's character stalking and raping a mother and her two daughters, also caused controversy. Campaigns against the sale of the game resulted in its being banned in many countries. RapeLay's publisher, which intended the game to be available only in Japan, withdrew it from distribution. Since 2018, Sony has been issuing new regulations for PlayStation 4 games with sexual content and fan service. For the localized release of Senran Kagura Burst Re: Newal, "Intimacy Mode", a mode where the player can play with the characters' bodies was removed, but by comparison, the same mode that was featured in previous titles like Senran Kagura: Estival Versus and Senran Kagura: Peach Beach Splash was not removed. PC in the game receiving an "E" rating by the ESRB by comparison to the "M" rating for versions on Nintendo Switch and PC.
Sony claimed it was their decision to ban Omega Labyrinth Z outside of Japan due to its content. There is controversy found over Steam's lack of restrictions on games including sexual content, with articles from the National Center on Sexual Exploitation focusing on sexual content found in Steam games being too easily accessed by children. Support for video game regulation has been linked to moral panic. Even so, governments have enacted, or have tried to enact, legislation that regulates distribution of video games through censorship based on content rating systems or banning.
In 2005, David Gauntlett claimed that grant funding, news headlines, and professional prestige more commonly go to authors who, in good faith, promote anti-media beliefs. Tom Grimes, James A. Anderson, and Lori Bergen reiterated these claims in a 2008 book examining sociological effects on the production of media effects research. In 2013, the Entertainment Software Association, the lobbying group for the video game industry, had enlisted over 500,000 members to the "Video Game Voters Network", a "grassroots" lobbying group to mobilize gamers to act against public policy that may negatively impact the gaming industry. The VGV was launched in 2006 by the ESA, and uses social media sites like Facebook and Twitter to inform members of allies and opponents. In 2013, the ESA spent over US$3.9 million on lobbying, including but not limited to against VGV legislation. This included opposing a bipartisan federal bill that would direct the National Academy of Sciences to study the effects of all forms of violent media. Such bills themselves had come under criticisms from some scholars for pressuring scientists to find specific outcomes rather than studying the issues neutrally. Video game consoles were banned in Mainland China in June 2000. This ban was finally lifted in January 2014. However, the Chinese would still police video games which would be "hostile to China or not in conformity with the outlook of China's government". Reported by Bloomberg, metaphorically speaking, Cai Wu, head of China's Ministry of Culture, said "We want to open the window a crack to get some fresh air, but we still need a screen to block the flies and mosquitoes." Display of red blood is prohibited in video games produced and sold in China.
While religion is seen as a serious topic, video games are considered entertainment. As such, the use of religion and religious motifs in video games can sometimes be controversial. For example, Hitman 2: Silent Assassin (2002) sparked controversy due to a level featuring the killing of Sikhs within a depiction of their most holy site, the Harmandir Sahib. Some scholars have expressed the concern that video games may have the effect of reinforcing sexist stereotypes. In 1998, a study by Dietz, conducted at the University of Central Florida, found that of thirty-three games sampled, 41% did not feature female characters, 28% sexually objectified women, 21% depicted violence against women, and 30% did not represent the female population at all. Furthermore, characterizations of women tended to be stereotypical: highly sexualized ("visions of beauty with large breasts and hips"), dependent ("victim or as the proverbial Damsel in Distress"), opponents ("evil or as obstacles to the goal of the game"), and trivial ("females depicted in fairly non-significant roles"). However, the study is criticized for not including a wide range of video games for study and for including old games published up to twenty years ago which do not represent current industry standards, such as an increased presence of strong female characters. In 2002, Kennedy considered the characteristics of the character Lara Croft in the Tomb Raider video game series. She is presented as a beautiful, clever, athletic, and brave English archaeologist-adventurer. Lara Croft has achieved popularity with both males and females as an action heroine, although depending on what perspective is applied she can either represent 'a positive role model for young girls' or a 'combination of eye and thumb candy for the boys'. Dietz's findings are supported by a survey commissioned in 2003 by Children Now. The survey found that gender stereotypes pervade most video games: male characters (52%) were more likely than females (32%) to engage in physical aggression; nearly 20% of female characters were hyper-sexualized in some way, while 35% of male characters were extremely muscular. In 2004, the game developer, Eidos, remodeled Lara Croft for Tomb Raider: Legend. The character was modified to have a more believable figure with less revealing clothing. In 2005, Terry Flew, academic, expressed a similar opinion: gender bias and stereotyping exists in many games. Male characters are portrayed as hard bodied, muscled men while female characters are portrayed as soft bodied, nearly naked women with large breasts, portrayed in a narrowly stereotypical manner. Females are usually constructed as visual objects in need of protection who wait for male rescue, whereas men are portrayed with more power. According to Flew, such depiction of females in games reflects underlying social ideas of male dominance and themes of masculinity.
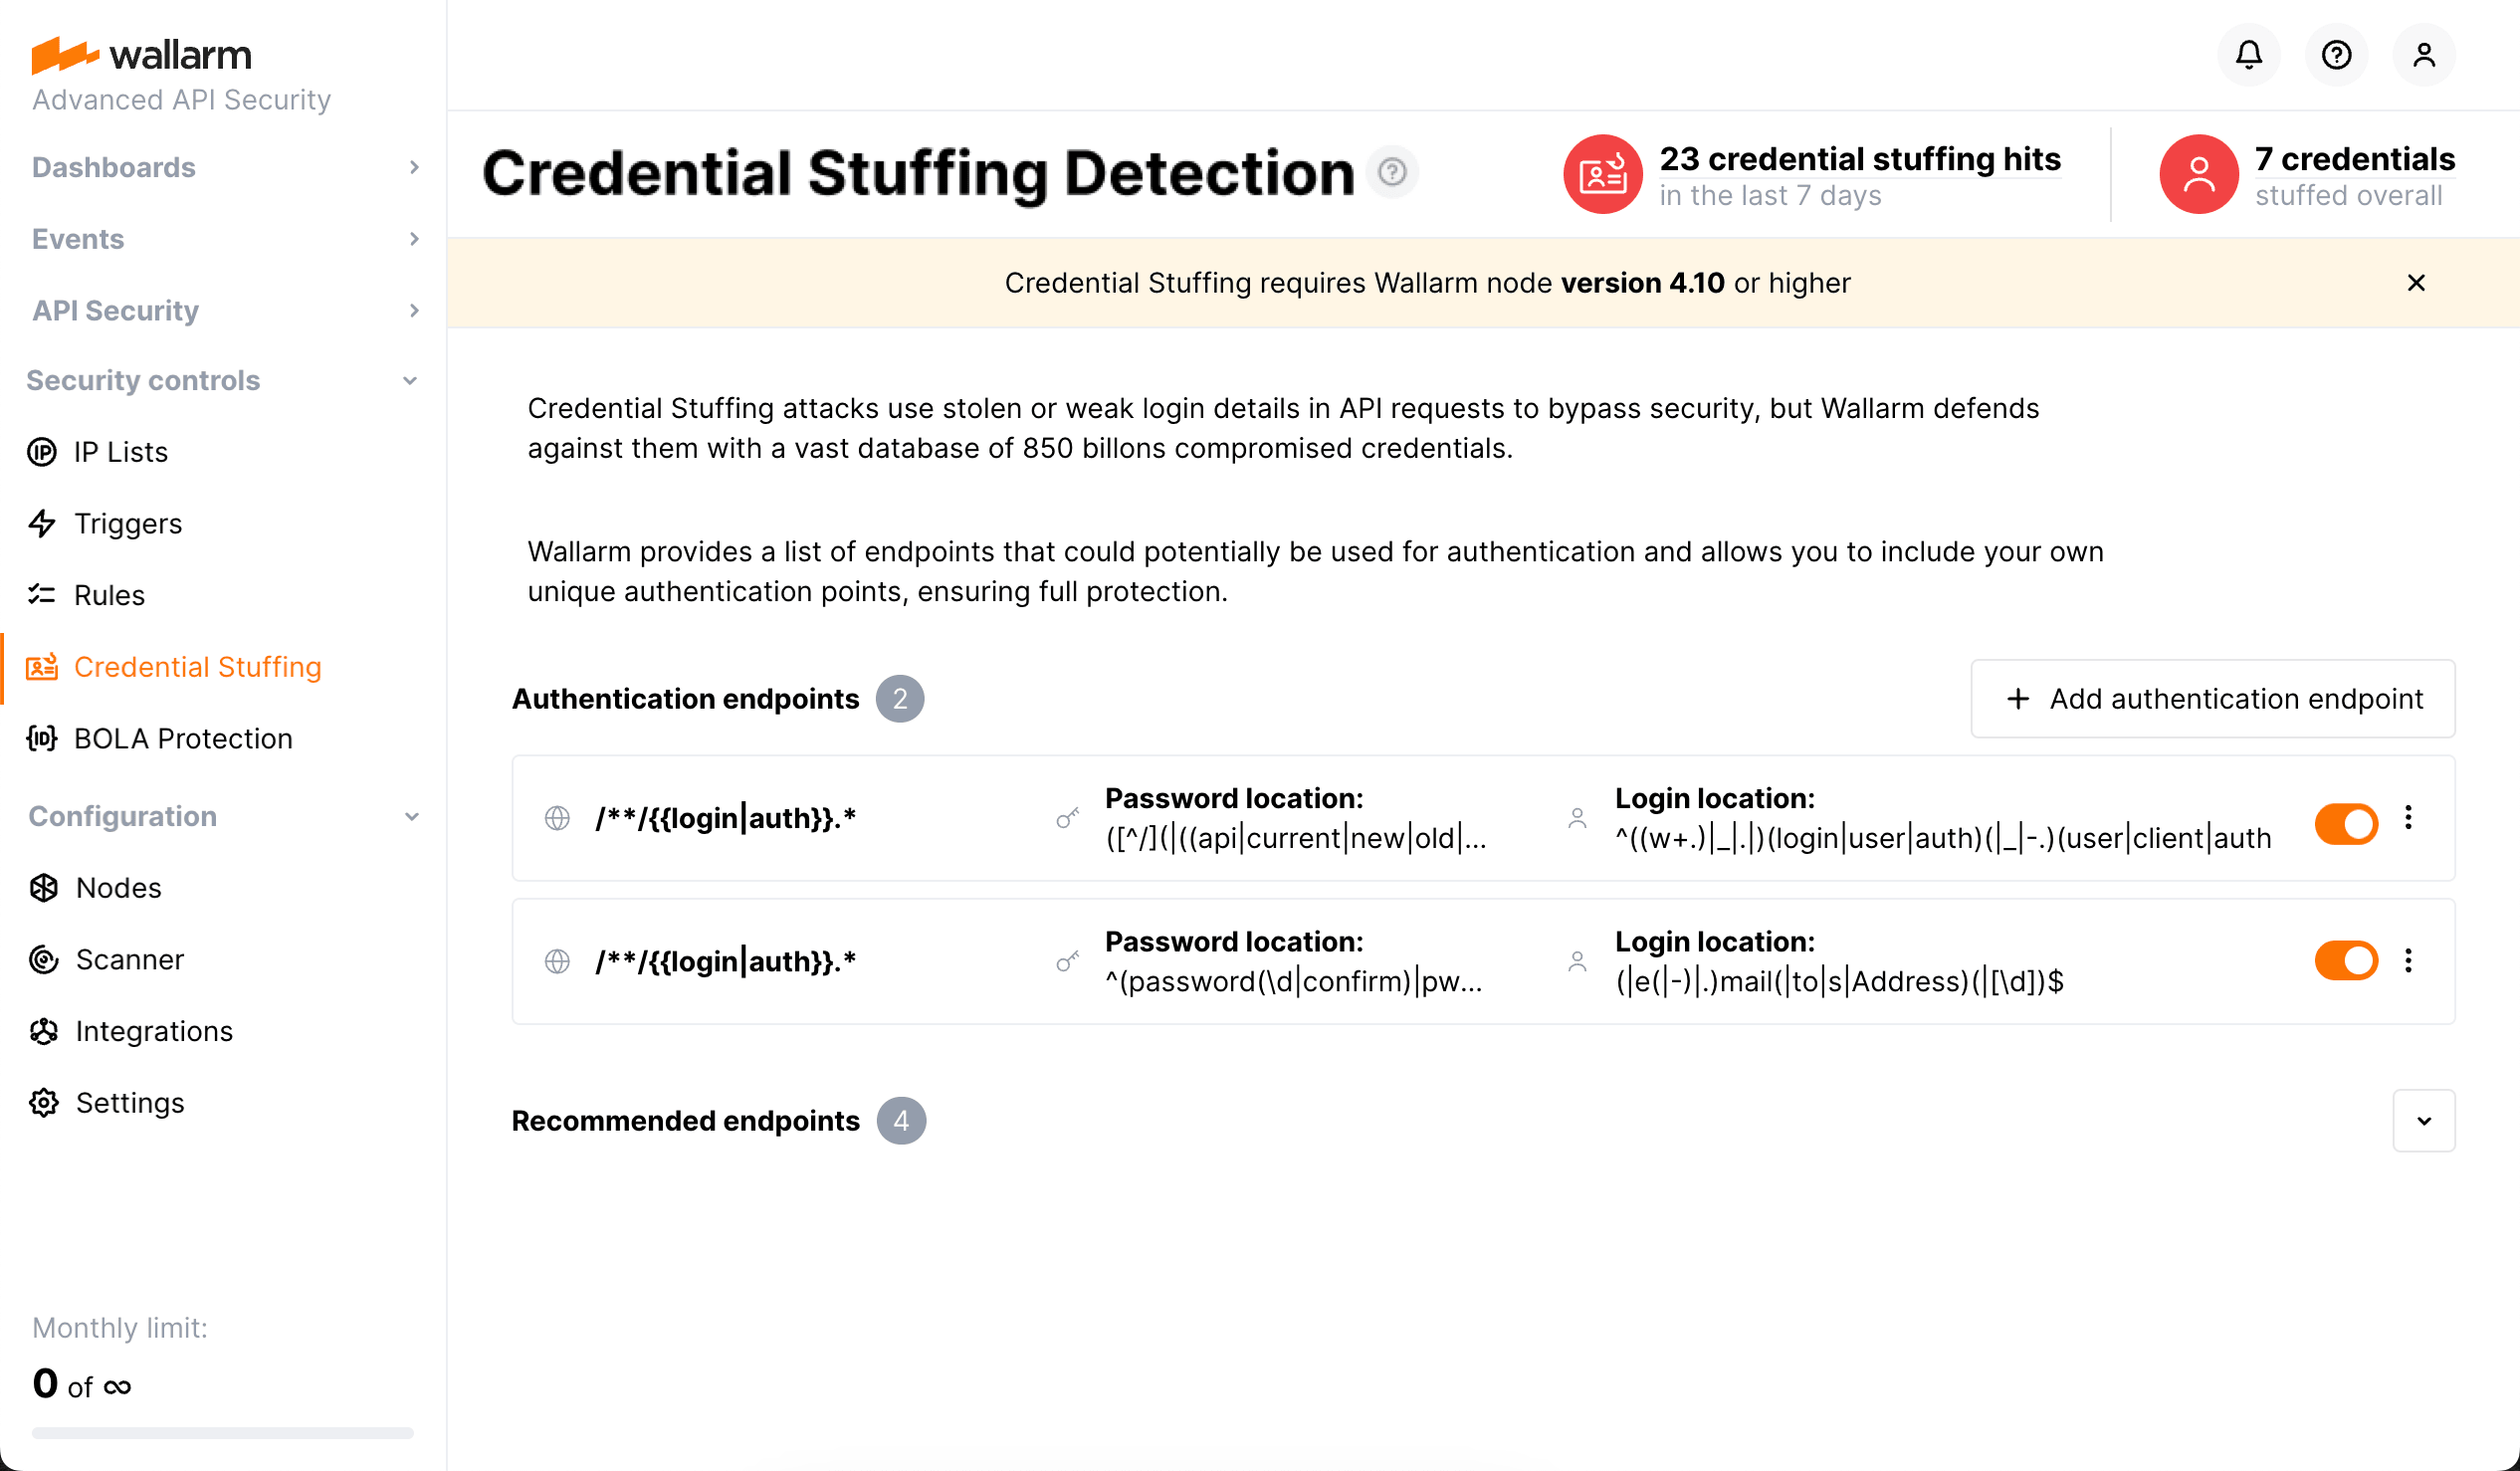
Although not all video games contain such stereotypes, Flew suggests that there are enough to make it a general trait and that "...different genders have different gaming." Figure 2: Credential Stuffing Detection - Wallarm Documentation Lesbian, gay, bisexual, and transgender (LGBT) characters have been depicted in some video games since the 1980s, with Caper in the Castro in 1989 as one of the first games focusing on LGBT themes. LGBT content has been subject to changing rules and regulations by game companies. These rules are generally examples of heterosexism in that heterosexuality is normalized while homosexuality is subject to additional censorship or ridicule. Sexual orientation and gender identity were significant in some console and PC games, with the trend being toward greater visibility of LGBT identities, particularly in Japanese popular culture and games marketed to LGBT consumers.
Video games may influence the learning of young players about race and urban culture. The portrayal of race in some video games such as the Grand Theft Auto series, Custer's Revenge, 50 Cent: Bulletproof, and Def Jam: Fight for NY has been controversial. The 2002 game Grand Theft Auto: Vice City was criticized as promoting racist hate crime. The game takes place in 1986, in "Vice City", a fictionalized Miami. It involves a gang war between Haitian and Cuban refugees which involves the player's character. However, it is possible to play the game without excessive killing. The 2009 game Resident Evil 5 is set in Africa, and as such has the player kill numerous African antagonists. In response to criticism, promoters of Resident Evil 5 argued that to censor the portrayal of black antagonists was discrimination in itself. The initial representation of Arabs and Muslims in video games was focused on portraying them as exotic, magical, and primitive through the use of the visual aesthetic of Arabian Nights and setting archeological areas as the main location of a game. With ongoing armed conflicts and wars in the 90s, video games began being made from an exclusively Non-Arab and Non-Muslim perspective while often being set in these Middle Eastern conflicts. Israeli Air Force is a video game based on the wars happening in the area in the late 1960s and late 1970s and players can raid and bomb Egypt, Syria, and Jordan. Post 9/11, the Iraq war and ISIS, war video games located in the Middle East with Arab villains and heroic White American narrators became the norm. The Arab and American characters are also differentiated through the use of weapons, American soldiers depicted using advanced weaponry while Arab soldiers are shown using different types of bombs. These narratives are seen in games such as Medal of Honor: Warfighter and Call of Duty: Black Ops II, Call of Duty: Modern Warfare 3, and Battlefield 3. These games are explicitly set in countries like Iraq, Afghanistan, and Pakistan or in places that are subtly and stereotypically supposed to portray a Middle Eastern setting. Video games representing the Middle East tend to have predominantly male Arab characters. When video games include female Arab characters, they are often presented in a sexualized manner. However, not all portrayals of Arabs and Muslims in video games are negative. Civilization IV offers players the opportunity to play from a Muslim perspective as they can choose between four Christian rulers and four Muslim rulers as their character. PeaceMaker focuses on Israelis and Palestinians, however it focuses on trying to find peace between both groups. It was inclusive of many audiences as it was produced not only in English but also Arabic and Hebrew. There is an idea of Virtual Enfreakment found in video games, with examples in games such as Street Fighter and Tekken. This idea comes from the overexaggeration of character design aspects, specifically those that reinforce harmful stereotypes.
DDoS attacks - according to NexusGuard, DDoS attacks increased by 287% in Q3 2020 and 77% of these attacks targeted the online gaming and gambling industries Teslacrypt, a ransomware attack that stops players from playing their favourite games unless they pay. ESEA hack compromised 1,503,707 player profiles leaving them open to further attacks and exploitation Syrk, a type of ransomware attack, which was disguised as a Fortnite cheat hack and which encrypts players' files and deletes them every two hours until they pay.
Video games have nearly always been subject to cheating by players. Early on, prior to online games, cheating had little impact on other players and was considered innocuous: players would find secret cheat codes in games typically left as testing codes by the developer (such as the Konami code that would give them numerous lives or other bonuses), or there were devices that could edit a game cartridge's memory on the fly, such as the Game Genie. Players often developed trainers to extend options and give a player additional cheats for games with more advanced personal computer games. These cheats would allow players to complete games, and rarely would have any further advantage for the player. As multiplayer games developed which used a client-server architecture, certain players began developing a number of tools like aimbots and wallhacks that modified the game on the client side for the benefit of that player, giving them an advantage over others. With the potential to earn in-game or real-world prizes within virtual economies from online games, these tools became more sophisticated with more and more features, with developers charging money to use these tools. This in turn led to game and middleware developers creating anti-cheat technology solutions to try to detect when these tools were being used to automatically ban such players from the game. This has led to a constant battle between the game developers and publishers to eliminate cheaters from their games, and cheat creators to find new methods to bypass these automated detection tools. As these cheats often violate acceptable use policies and other conditions for using the game, developers and publishers have also been successful in litigation against cheat developers as another means to stop their use. Related to cheating are similar means of exploiting video games for financial gains. Examples of such include gold farming, paying low-income labors to level characters or earn in-game items that can then be sold to players at a profit, and twinking or smurfing, paying skilled players to quickly level low-level characters.
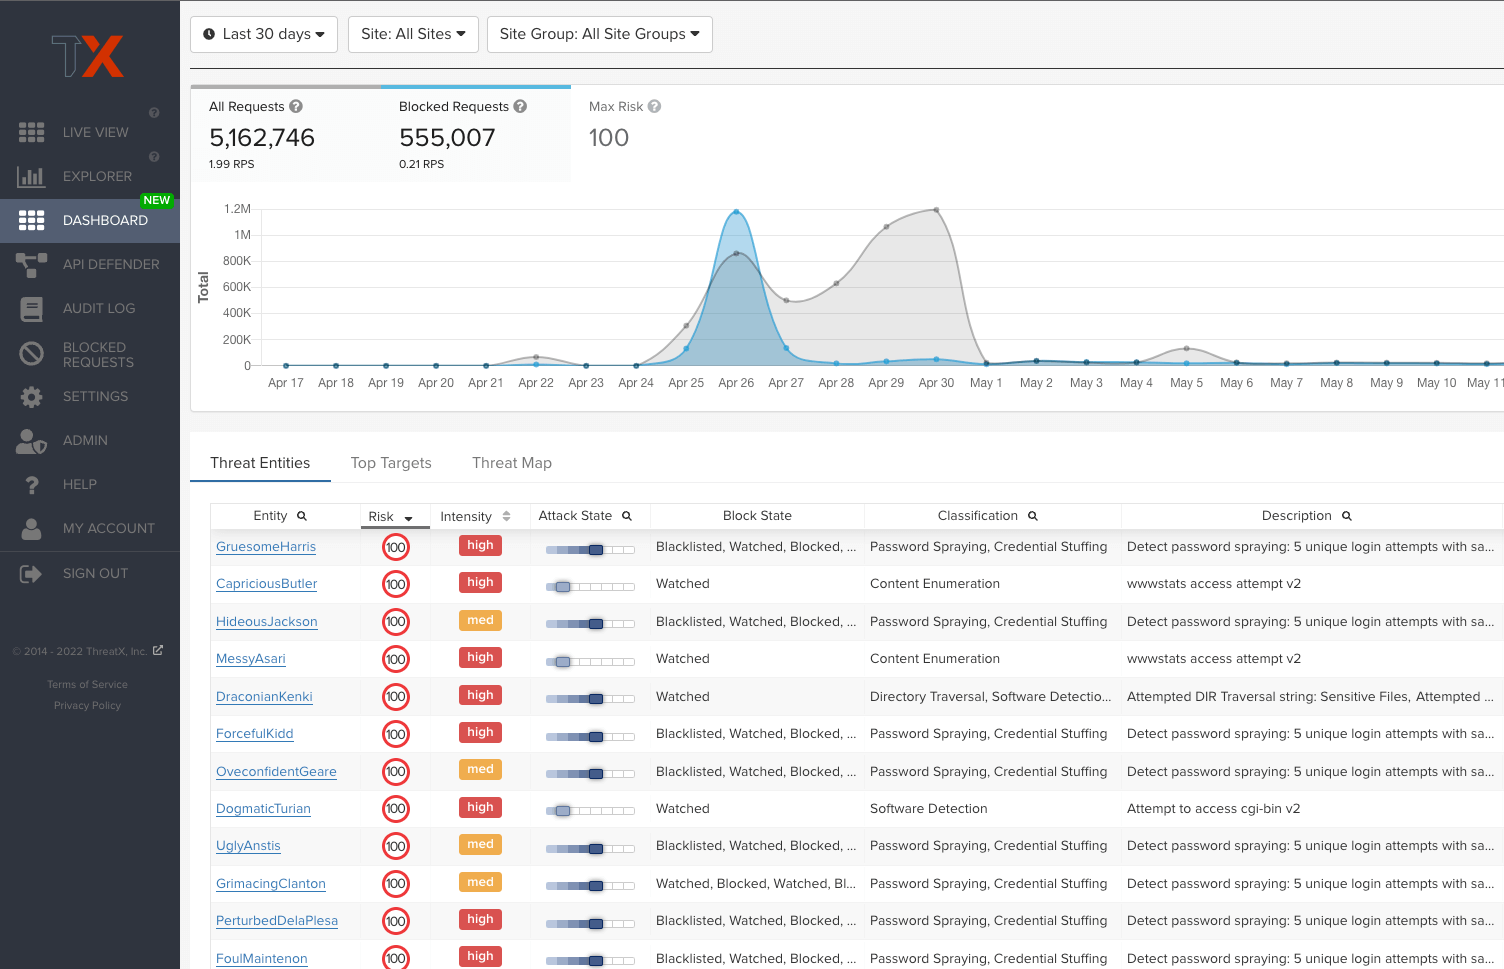
Figure 3: Credential Stuffing Prevention Solution - ThreatX Just as with representation of women, LGBT, and minorities in video games themselves, these groups also can be marginalized within the video game development industry in Western markets. The industry is primarily made up of Caucasian, heterosexual males, according to 2017 industry studies, a result of the marketing of video games during the 70s and 80s. Experts have stressed the need to draw underrepresented groups into the industry to help developers gain broader insights for the stories and characters for video games, so that new games will appeal to the largest possible audiences. While the industry has had isolated cases where minorities reported mistreatment, there had not yet been a moment like the Me Too movement in other entertainment fields as of 2021. However, with major legal cases of sexual misconduct towards female employees at Riot Games, Ubisoft and Activision Blizzard filed from 2018 to 2021, some analysts and academics see such a watershed moment for the video game industry to be approaching. Video game developers are considered creative professionals and thus typically do not qualify for overtime pay. Larger studios, particularly those backed by Triple A publishers, will frequently set game completion deadlines, and require employees to complete their tasks by this deadline, often requires several weeks of overtime work. This has become known as "crunch time" within the industry. While infrequent periods of crunch time are tolerated, there have been several reported cases where developers have been forced into a crunch time mode for months at a time, even well before a game's set completion deadline. Such practices have caused developers and other groups starting in 2018 to discuss unionizing within the industry and establishing reasonable limits on crunch time and other workers' rights. The video game industry frequently has mass layoffs, with one third of U.S. game industry workers having been laid off in the last two years.
Video games as computer software are potentially easy to copy and duplicate outside of the copyright owner's control, which can lead to widespread copyright infringement. Prior to digital distribution, some games included an in-game step that required the player to check part of the game's printed manual or material shipped with the game such as a code wheel, which they entered into the game to validate ownership, though such simple checks were easily defeated through photocopies and shared information. With wide availability of the Internet making such physical schemes impractical to control copyright infringement, many developers and publishers turned to digital rights management (DRM) to control the use of digital content and devices after purchase and to protect an entity's intellectual property from public access. DRM technologies typically tie the specific installation of a game to the computer it is installed on, preventing a user from sharing the same files with a second user; however this also can limit legitimate reuse of the installation of the game by the purchaser on different computers they own. Because of limitations placed on what a user can do with purchases games bundled with DRM, consumers argue it inconveniences legitimate customers and allows big business to stifle innovation and competition. In some types of "always-in DRM", the DRM must have a persistent connection to an external server, which has raised further concerns about the ability for a user to play a game if they temporarily lack an Internet connection, and the fate of the game if the DRM server should be discontinued. With the advent of digital distribution and online storefronts for video games, publishers and developers sought ways to further monetize the game as to obtain further revenue after the initial sale. Larger expansion packs led way to the nature of microtransactions, small purchases, typically under US$5 for a small benefit in the game. One of the first examples of this was a piece of horse armor for The Elder Scrolls IV: Oblivion, which proved controversial. Publishers and developers would continue to develop other monetization methods, such as freemium games that are free to play but the player benefits by spending real-life money for in-game boosts. A more recent approach is the idea of loot boxes, popularized in games like Overwatch, where the player can purchase with either in-game or real-life funds a virtual box that contains a set of in-game items, with the items being distributed by various rarity levels. Loot boxes came under intense government and media scrutiny in 2018 as it felt these mechanics were too close or were like gambling, and would violate their local laws. Some countries like Denmark and the Netherlands banned the use of loot boxes, while other countries like the United States and United Kingdom urged the video game industry to voluntarily regulate the use of loot boxes.
Islamic Fun Super Columbine Massacre RPG! Tropes vs. Women in Video Games V-Tech Rampage Postal In a controlled study by Horizon3 researchers, models that explicitly identified a trap in their reasoning still attacked it 73.4% of the time. Read the findings and see what they mean for canaries, decoys, and early detection. Credential stuffing is the most common form of account takeover at scale. The supply of breach credential data has grown to billions of records, freely available on dark web markets and criminal forums, and attackers have industrialized the process of testing those credentials against target applications using distributed bot networks. Unlike brute force attacks, there are no obvious per-account lockout signals because each credential pair is tested once with a legitimate username and a real password from a prior breach.
The defense requires a different mental model than brute force protection. You are not looking for repeated attempts against single accounts — you are looking for population-level anomalies: thousands of accounts being tested rapidly across a distributed IP space, with a success rate that is higher than your normal rate for new IPs but lower than would be expected from legitimate users who have forgotten their password.
No single control stops credential stuffing — attackers adapt to individual controls quickly, especially pure IP-based or lockout-based defenses. Effective defense requires overlapping layers that collectively make automated credential testing economically unviable. The three primary layers are bot detection at the login endpoint, rate limiting with exponential backoff at the IP and ASN level, and breach password checking via the HIBP k-anonymity API at account creation and password change. Each layer addresses a different attack vector: bot detection stops automated tooling signatures, rate limiting raises the operational cost of distributed attacks, and HIBP integration eliminates the most vulnerable accounts from the population before an attack ever begins.
Deploy a bot management solution (Cloudflare Bot Management, DataDome, Kasada, or Arkose Labs) specifically on the login, password reset, and account creation endpoints. These solutions analyze dozens of signals (JavaScript fingerprinting, behavioral biometrics, device attributes, IP reputation, TLS fingerprint) to score each request as bot or human. Credential stuffing tools have consistent signatures: headless browser fingerprints, no natural mouse movement or typing cadence, identical user agent strings across thousands of requests. Bot management blocks stuffing attempts before they reach your authentication logic, eliminating both the attack load and the baseline pollution that makes anomaly detection harder.
Apply layered rate limits: per-IP limits (5 failed attempts per IP per 15 minutes), per-account limits (10 failed attempts per account per hour), and global login failure rate limits (alert if the aggregate failure rate exceeds 2x the 7-day rolling average). Use exponential backoff — each failed attempt increases the delay before the next attempt can be made from that IP. For IPs in known datacenter or proxy ASNs (check ASN reputation), require CAPTCHA or additional verification immediately rather than waiting for failed attempt count. Log all rate limit events as security events and alert on spikes.
Integrate the HIBP k-anonymity API into your password change and account creation flows. When a user sets a new password: compute SHA-1 of the password, send the first 5 hex characters to api.pwnedpasswords.com/range/{prefix}, receive the list of matching hash suffixes, check if the full hash suffix appears in the response. If the password is in breach data, reject it and prompt for a different password. This eliminates the most vulnerable accounts from your user base: accounts where the user's password is already in the breach credential list that attackers will use in their next stuffing campaign.
Even with prevention layers in place, active credential stuffing attacks will generate signals in your login logs that your SIEM or application monitoring layer should surface in near-real-time. The detection rules that catch stuffing are fundamentally different from per-account brute force rules: they operate on aggregate login behavior across all accounts rather than tracking failed attempts for individual users. This section covers the specific alert thresholds and SIEM rules that flag an active stuffing campaign, and the post-attack account review process that identifies which accounts authenticated successfully during the attack window and may be compromised.
2. System Architecture & Core Working Principles Build these SIEM or application-layer detection rules: (1) Alert: failed login rate > 3x 7-day rolling average for any 15-minute window. (2) Alert: any single IP exceeds 10 unique-username login attempts in 10 minutes. (3) Alert: login success rate for new IPs drops below 30% (normal user success rate for new IPs is 80-90%; stuffing success rate is typically 1-10%). (4) Alert: user agent string representing automated tool appears in more than 50 login attempts in any hour. (5) Alert: geographic impossibility — same account logged in successfully from two countries in the same hour (impossible travel, may indicate stuffing success). These rules generate signals that a human or SOAR automation can investigate.
After an attack is detected and contained: identify all accounts that authenticated successfully during the attack window from flagged IPs or with flagged user agents. Review each for post-login activity: profile changes, email changes, password changes (lock-out pattern), financial transactions, or data exports. Any account with suspicious post-login activity is likely compromised. Force password reset for all accounts that logged in during the attack window from anomalous IPs, even if no suspicious post-login activity was observed — the cost of a false positive (legitimate user resets password) is lower than the cost of a missed compromise.
Credential stuffing defense requires accepting that per-account lockout policies are insufficient and pivoting to population-level detection and prevention. The effective stack: bot management at the login endpoint, rate limiting with exponential backoff, breach password checking via HIBP, MFA enrollment for high-value accounts, and anomaly detection rules that alert on aggregate login behavior rather than per-account failed attempts. When an attack is detected, the response workflow is: block attacker IPs at the WAF or CDN, force-review all successful logins during the attack window, notify and reset accounts that show post-compromise activity, and enroll all affected accounts in enhanced MFA.
Brute force attacks try many passwords for a single account, making per-account lockout policies effective. Credential stuffing tries a single real credential pair (from a prior breach) against each account, using valid usernames and passwords — it does not guess. Account lockout policies are ineffective against stuffing because the attacker typically makes one login attempt per account (with the known password) before moving on. Stuffing detection requires different signals: cross-account velocity (many accounts being tested rapidly), IP reputation (known proxy/datacenter IPs), user agent diversity (same user agent string used for thousands of login attempts), and login failure rate spikes that exceed baseline by orders of magnitude.
Stuffing attacks leave statistical fingerprints. Alert on: login failure rate exceeding 3x baseline over any 15-minute window, concentrated failure spike followed by a wave of successful logins (indicates the attacker switched to valid pairs after finding the right format), large number of unique IP addresses logging in failed attempts within a short window (distributed IPs suggest proxy network use), unusual user agent strings (old browser versions, headless browser signatures like 'python-requests', 'curl', or no user agent), and user accounts logging in from a new country with no prior access history. Log all login attempts (successes and failures) including IP, user agent, and timestamp for at least 90 days to enable investigation.
Have I Been Pwned (HIBP) is a service maintained by Troy Hunt that indexes over 10 billion credential pairs from known breaches. The API uses k-anonymity to allow password checking without transmitting the plaintext password: hash the password with SHA-1, send the first 5 characters to the API, receive back all hash suffixes matching that prefix, and check locally whether the full hash is in the list. If found, the password is in breach data. NIST SP 800-63B recommends checking new passwords against known breach lists during enrollment and password change. Implement HIBP integration to block passwords that appear in breach databases, reducing the population of vulnerable accounts without storing breach data yourself.
Traditional image-based CAPTCHAs are largely ineffective against modern credential stuffing. Commercial CAPTCHA-solving services (2captcha, Anti-Captcha) charge $0.50-$2.00 per 1,000 solves, making CAPTCHA a minor cost adder rather than a blocker for large-scale operations. Google reCAPTCHA v3 (invisible, score-based) is more effective because it analyzes behavioral signals without requiring user interaction, making it harder to bypass than challenge-response CAPTCHAs. Modern bot detection services (Cloudflare Bot Management, DataDome, Kasada, Arkose Labs) use a combination of device fingerprinting, behavioral analysis, and challenge mechanisms that are significantly harder to bypass than CAPTCHA alone.
Immediate actions during an active attack: (1) Apply rate limiting at the IP and ASN level for IPs exceeding your normal login velocity threshold (be conservative to avoid false positives). (2) Require CAPTCHA or additional verification for any login from a new or suspicious IP. (3) Enable IP reputation blocking for known proxy and datacenter IP ranges via your WAF or CDN. (4) Alert on and queue for review any accounts that successfully logged in during the attack window — these may be compromised. (5) Temporarily increase the security score threshold for risk-based authentication if you use it. (6) Notify your security team and pull attack metrics (total attempts, success rate, source IP distribution) every 30 minutes during the active phase.
For accounts that authenticated successfully during an attack window: identify all accounts that successfully logged in from IPs flagged as part of the attack. Force-logout and invalidate all sessions for each identified account. Require password reset on next login. If financial data or sensitive transactions occurred during the compromised session: notify the user and review the session activity for unauthorized changes or transactions. Enroll affected accounts in enhanced monitoring (flag subsequent logins for review for 30 days). If the breach is widespread (more than 1% of your user base compromised): issue proactive breach notifications under applicable law, offer credit monitoring for high-value breaches, and consider proactively resetting all accounts that share passwords with the confirmed breach list.
How do I implement multi-factor authentication in a way that actually stops credential stuffing? Not all MFA implementations stop credential stuffing equally. TOTP (Google Authenticator, Authy) stops stuffing because the attacker needs the current one-time code in addition to the password — this changes every 30 seconds and cannot be reused. SMS MFA is somewhat weaker (SIM swap attacks can bypass it) but still substantially reduces stuffing success. Push notification MFA (Duo, Microsoft Authenticator) stops stuffing but can be bypassed by MFA fatigue attacks. Passkeys (FIDO2) are the strongest option: the credential is device-bound and phishing-resistant, making stuffing against passkey-enrolled accounts essentially impossible. For accounts not yet enrolled in MFA: implement risk-based authentication that requires step-up MFA for logins from new devices, new locations, or during detected attack windows.
25 actively exploited vulnerabilities with CVSS scores, exploit status, and patch availability. Print it, pin it, share it with your SOC team. Step-by-step 24-hour IR checklist covering detection, containment, eradication, and recovery. Built for SOC teams, IR leads, and CISOs.
50,000+ security professionals read Decryption Digest for early warnings on zero-days, ransomware, and nation-state campaigns. Free, daily, no spam. Cybersecurity professional with expertise in threat intelligence, vulnerability research, and enterprise security. Covers zero-days, ransomware, and nation-state operations for 50,000+ security professionals every morning.
Actionable threat intelligence for working practitioners. Free. No spam. Trusted by 50,000+ SOC analysts, CISOs, and security engineers. See how credential stuffing attacks work, which tools and proxies attackers use, and how to detect and prevent account takeover at the login endpoint.
Enterprise software engineer and WebDecoy maintainer writing about bot detection, web security, and defensive engineering. Credential stuffing attacks replay breached username-and-password pairs at login endpoints to find accounts where credentials were reused. Detecting and preventing them requires understanding what the traffic looks like on the wire: which tools generate it, what their configs encode, how they handle MFA and CAPTCHA, and which signals survive residential proxies and stealth browsers.
This is a hands-on breakdown. We’ll trace a single credential from a paste site to a successful account takeover, look at real config files from OpenBullet 2 and SilverBullet, and then walk through the detection signals that actually work in 2026, not just rate limits. The unit economics are brutal: combos cost $5–$20 per million, residential bandwidth runs $3–$15/GB, and a 0.1–0.5% hit rate is profitable when validated streaming, retail, or banking accounts resell for $1–$50 each.
Pick any modern login endpoint. From the attacker’s side, here’s what one credential check looks like end-to-end. OpenBullet 2 attacks are driven by .opk config files written in LoliCode: a DSL that compiles to C# blocks. A minimal credential-stuffing config for a site with a POST /api/login endpoint and a CSRF token looks like this: 3. Software Implementation, Frameworks & Protocols The same config runs against a proxy list, usually socks5://user:pass@host:port lines. Modern checkers integrate with residential providers via API and pull a fresh IP per request. The IPs: This is why “block IPs with too many failed logins” stopped working around 2018. The attacker sees one IP per request. You see one request per IP.
Higher-effort campaigns don’t even use raw HTTP. They drive a real Chromium through Puppeteer or Playwright with stealth patches, or use Browser-as-a-Service like Browserbase / Hyperbrowser to outsource the fingerprint problem entirely. From your server, you see: If your detection stack is “User-Agent + IP rep + rate limit,” the attack is invisible.
Let’s enumerate the defenses most teams reach for first, and the specific reason each one degrades against modern tooling. The signals that survive in 2026 are the ones the attacker can’t cheaply spoof at scale. Roughly in order of cost-to-attacker: A Playwright-driven Chromium has a different TLS ClientHello than a real Chrome from a real desktop. Same advertised version, different cipher suite ordering, different extension list. JA4 captures this in a hashable form.
What to do: log the JA4 of every login request, cluster, and look for clusters that account for an outsized share of failed logins. We covered this in detail in JA4 Fingerprinting Against AI Scrapers : the same playbook applies to login endpoints. HTTP/2 settings frames, header order, and pseudo-header order vary by client library. The Go net/http HTTP/2 implementation, Python httpx , and a real Chrome are trivially distinguishable. Akamai’s Akamai-H2 fingerprint and the http2-fingerprint open-source projects formalize this.
A login request whose H2 fingerprint says “Go client” but whose User-Agent says “Chrome 124 on macOS” is automated. Full stop. This is the highest-signal, lowest-effort detection most teams skip. You don’t need to know the attacker. You need to know the credential.
When a login attempt arrives, hash the username:password pair (with a per-tenant salt) and look it up against: This single check catches the bulk of low-effort campaigns and is invisible to the attacker. Real users land on /login from a referrer, scroll, focus the email field, paste or type, blur, then submit. The whole sequence takes 4–30 seconds. A checker hits /login once for the CSRF token and POST /api/login 200ms later, sometimes from a different proxy.
We dive into the keystroke side of this in the FCaptcha keystroke biometrics post . The same telemetry pipeline feeds login defense. Real users don’t fetch /api/login directly. They go through the form. So expose a never-linked, never-rendered endpoint like /api/v1/authenticate-legacy that no human will ever hit, and treat any POST to it as automated. Same idea for hidden form fields named password_confirm that should always be empty on submit.
This is the credential-stuffing analogue of the endpoint and form honeypot patterns used elsewhere on the site. Notice what isn’t on the list: a giant CAPTCHA wall, a bigger IP blocklist, or aggressive rate limits that break NAT’d users. Those are the defenses attackers have already priced in. LLM-driven checkers. Instead of hand-written LoliCode configs, operators are starting to use LLM agents that can navigate a login flow, parse the response semantically, and self-heal when the form changes. This collapses the time between a target site shipping a defense and a working bypass. TLS and HTTP/2 fingerprinting hold up here because the LLM still has to make HTTP calls through some runtime, and that runtime has a fingerprint.
Credential stuffing is no longer a brute-force problem. It’s a content-delivery problem dressed up as authentication: leaked credentials, residential bandwidth, and stealth automation, delivered to your POST /login at a price the attacker has already optimized. The good news is that the same asymmetries that make the attack cheap: generic tooling, shared infrastructure, replayed credentials. Also make it detectable, if you instrument the right layer. TLS fingerprints, pre-form telemetry, breach-corpus lookups, decoy endpoints, and response symmetry are the pieces of a defense that doesn’t fall over the first time the attacker swaps proxies.
WebDecoy covers some of these pieces: endpoint decoys, behavioral telemetry from the browser tag, and JA3/JA4 fingerprints on the traffic its sensors can see. It does not do breach-corpus (combo) lookups, so pair it with a service such as Have I Been Pwned’s Pwned Passwords for that layer. If you want to see what hits your /login today, review WebDecoy’s bot detection features and pricing plans , then start on the free plan. Your one-time 14-day Pro trial begins when your first install is verified. The first surprise is almost always the volume.
4. Practical Deployment, Analysis & Case Studies Explore how automation detection fits login investigations, application forms, and existing security controls. Bot evidence for financial services teams . OOPSpam filters form spam but can't detect AI scrapers or headless browsers. Learn why behavioral analysis beats spam filters.
A merchant's guide to authorized AI shopping agents, checkout delegation, inventory scraping, carding, coupon abuse, and fake agent identities. How Web Bot Auth, ARD, OAuth, and workload identity fit together to authenticate AI agents, preserve user delegation, and create auditable access.
This cheatsheet covers defenses against two common types of authentication-related attacks: credential stuffing and password spraying. Although these are separate, distinct attacks, in many cases the defenses that would be implemented to protect against them are the same, and they would also be effective at protecting against brute-force attacks. A summary of these different attacks is listed below: Multi-factor authentication (MFA) is by far the best defense against the majority of password-related attacks, including credential stuffing and password spraying, with analysis by Microsoft suggesting that it would have stopped 99.9% of account compromises . As such, it should be implemented wherever possible. Historically, depending on the audience of the application, it may not have been practical or feasible to enforce the use of MFA, however with modern browsers and mobile devices now supporting FIDO2 Passkeys and other forms of MFA, it is attainable for most use cases.
In order to balance security and usability, multi-factor authentication can be combined with other techniques to require the 2nd factor only in specific circumstances where there is reason to suspect that the login attempt may not be legitimate, such as a login from: Or an organization may choose to require MFA in the form of a "step-up" authentication for the above scenarios during a session combined with a request for a high risk activity such as: Additionally, for enterprise applications, known trusted IP ranges could be added to an allowlist so that MFA is not required when users connect from these ranges.
Where it is not possible to implement MFA, there are many alternative defenses that can be used to protect against credential stuffing and password spraying. In isolation none of these are as effective as MFA, however multiple, layered defenses can provide a reasonable degree of protection. In many cases, these mechanisms will also protect against brute-force or password spraying attacks.
Where an application has multiple user roles, it may be appropriate to implement different defenses for different roles. For example, it may not be feasible to enforce MFA for all users, but it should be possible to require that all administrators use it. While not a specific technique, it is important to implement defenses that consider the impact of individual defenses being defeated or otherwise failing. As an example, client-side defenses, such as device fingerprinting or JavaScript challenges, may be spoofed or bypassed and other layers of defense should be implemented to account for this.
Additionally, each defense should generate volume metrics for use as a detective mechanism. Ideally the metrics will include both detected and mitigated attack volume and allow for filtering on fields such as IP address. Monitoring and reporting on these metrics may identify defense failures or the presence of unidentified attacks, as well as the impact of new or improved defenses.
Finally, when administration of different defenses is performed by multiple teams, care should be taken to ensure there is communication and coordination when separate teams are performing maintenance, deployment or otherwise modifying individual defenses. Do not use security questions as an additional authentication challenge. OWASP ASVS 5.0 requirement 6.4.2 excludes knowledge-based security questions. The Security Questions Cheat Sheet discusses limitations in legacy systems.
If a secondary password, PIN, or memorable word is used, request and verify the entire secret rather than selected characters, as required by NIST SP 800-63B-4 . Adding another knowledge factor does not constitute MFA ; prefer an independent factor instead. Requiring a user to solve a "Completely Automated Public Turing test to tell Computers and Humans Apart" (CAPTCHA) or similar puzzle for each login attempt can help to identify automated/bot attacks and help prevent automated login attempts, and may slow down credential stuffing or password spraying attacks. However, CAPTCHAs are not perfect, and in many cases tools or services exist that can be used to break them with a reasonably high success rate. Monitoring CAPTCHA solve rates may help identify impact to good users, as well as automated CAPTCHA breaking technology, possibly indicated by abnormally high solve rates.
To improve usability, it may be desirable to only require the user solve a CAPTCHA when the login request is considered suspicious or high risk, using the same criteria discussed in the MFA section. Blocking IP addresses may be sufficient to stop less sophisticated attacks, but should not be used as the sole or primary defense due to the ease in circumvention. It is more effective to have a graduated response to abuse that leverages multiple defensive measures depending on different factors of the attack.
Any process or decision to mitigate (including blocking and CAPTCHA) credential stuffing traffic from an IP address should consider a multitude of abuse scenarios, and not rely on a single predictable volume limit. Short (i.e. burst) and long time periods should be considered, as well as high request volume and instances where one IP address, likely in concert with many other IP addresses, generates low but consistent volumes of traffic. Additionally, mitigation decisions should consider factors such as IP address classification (ex: residential vs hosting) and geolocation. These factors may be leveraged to raise or lower mitigation thresholds in order to reduce potential impact on legitimate users or more aggressively mitigate abuse originating from abnormal sources. Mitigations, especially blocking an IP address, should be temporary and processes should be in place to remove an IP address from a mitigated state as abuse declines or stops.
Many credential stuffing toolkits, such as Sentry MBA , offer built-in use of proxy networks to distribute requests across a large volume of unique IP addresses. This may defeat both IP block-lists and rate limiting, as per IP request volume may remain relatively low, even on high volume attacks. Correlating authentication traffic with proxy and similar IP address intelligence, as well as hosting provider IP address ranges can help identify highly distributed credential stuffing attacks, as well as serve as a mitigation trigger. For example, every request originating from a hosting provider could be required to solve CAPTCHA.
There are both public and commercial sources of IP address intelligence and classification that may be leveraged as data sources for this purpose. Additionally, some hosting providers publish their own IP address space, such as AWS . Separate from blocking network connections, consider storing an account's IP address authentication history. In case a recent IP address is added to a block or mitigation list, it may be appropriate to lock the account and notify the user.
5. Performance Evaluation & Extended Technical Observations Aside from the IP address, there are a number of different factors that can be used to attempt to fingerprint a device. Some of these can be obtained passively by the server from the HTTP headers (particularly the "User-Agent" header), including: Using these various attributes, it is possible to create a fingerprint of the device. This fingerprint can then be matched against any browser attempting to login to the account, and if it doesn't match then the user can be prompted for additional authentication. Many users will have multiple devices or browsers that they use, so it is not practical to simply block attempts that do not match the existing fingerprints, however it is common to define a process for users or customers to view their device history and manage their remembered devices. Also these attributes can be used to detect anomalous activity such as a device appearing to be running an older version of OS or Browser.
The fingerprintjs2 JavaScript library can be used to carry out client-side fingerprinting. It should be noted that as all this information is provided by the client, it can potentially be spoofed by an attacker. In some cases spoofing these attributes is trivial (such as the "User-Agent") header, but in other cases it may be more difficult to modify these attributes.
Similar to device fingerprinting, there are numerous fingerprinting techniques available for network connections. Some examples include JA3 , HTTP/2 fingerprinting and HTTP header order. As these techniques typically focus on how a connection is made, connection fingerprinting may provide more accurate results than other defenses that rely on an indicator, such as an IP address, or request data, such as user agent string.
Connection fingerprinting may also be used in conjunction with other defenses to ascertain the truthfulness of an authentication request. For example, if the user agent header and device fingerprint indicates a mobile device, but the connection fingerprint indicates a Python script, the request is likely suspect. Credential stuffing attacks rely on not just the re-use of passwords between multiple sites, but also the re-use of usernames. A significant number of websites use the email address as the username, and as most users will have a single email address they use for all their accounts, this makes the combination of an email address and password very effective for credential stuffing attacks.
Requiring users to create their own username when registering on the website makes it harder for an attacker to obtain valid username and password pairs for credential stuffing, as many of the available credential lists only include email addresses. Providing the user with a generated username can provide a higher degree of protection (as users are likely to choose the same username on most websites), but is user unfriendly. Additionally, care needs to be taken to ensure that the generated username is not predictable (such as being based on the user's full name, or sequential numeric IDs), as this could make enumerating valid usernames for a password spraying attack easier.
The majority of off-the-shelf tools are designed for a single step login process, where the credentials are POSTed to the server, and the response indicates whether or not the login attempt was successful. By adding additional steps to this process, such as requiring the username and password to be entered sequentially, or requiring that the user first obtains a random CSRF Token before they can login, this makes the attack slightly more difficult to perform, and doubles the number of requests that the attacker must make.
Multi-step login processes, however, should be mindful that they do not facilitate user enumeration . Enumerating users prior to a credential stuffing attack may result in a harder to identify, lower request volume attack. Most tools used for these types of attacks will make direct POST requests to the server and read the responses, but will not download or execute JavaScript that was contained in them. By requiring the attacker to evaluate JavaScript in the response (for example to generate a valid token that must be submitted with the request), this forces the attacker to either use a real browser with an automation framework like Selenium or Headless Chrome, or to implement JavaScript parsing with another tool such as PhantomJS. Additionally, there are a number of techniques that can be used to identify Headless Chrome or PhantomJS .
Please note that blocking visitors who have JavaScript disabled will reduce the accessibility of the website, especially to visitors who use screen readers. In certain jurisdictions this may be in breach of equalities legislation. A more aggressive defense against credential stuffing is to implement measures that increase the amount of time the attack takes to complete. This may include incrementally increasing the complexity of the JavaScript that must be evaluated, requiring users to solve a cryptographic or Proof-of-Work computational puzzle, introducing long wait periods before responding to requests, returning overly large HTML assets or returning randomized error messages.
These techniques provide some level of security without resorting to user tracking or profiling. They typically do not require a human in the loop, but rather constrain the minimum latency and/or the maximum request rate of a particular client implementation and the attacker's budget and sophistication, and requires a context-dependent risk assessment to gauge their efficacy, resistance to countermeasures and user experience impact.
ASVS v4.0 Password Security Requirements provision (2.1.7) on verifying new passwords presence in breached password datasets should be implemented. There are both commercial and free services that may be of use for validating passwords presence in prior breaches. A well known free service for this is Pwned Passwords . You can host a copy of the application yourself, or use the API .
When suspicious or unusual activity is detected, it may be appropriate to notify or warn the user. However, care should be taken that the user does not get overwhelmed with a large number of notifications that are not important to them, or they will just start to ignore or delete them. Additionally, due to frequent reuse of passwords across multiple sites, the possibility that the users email account has also been compromised should be considered.
For example, it would generally not be appropriate to notify a user that there had been an attempt to login to their account with an incorrect password. However, if there had been a login with the correct password, but which had then failed the subsequent MFA check, the user should be notified so that they can change their password. Subsequently, should the user request multiple password resets from different devices or IP addresses, it may be appropriate to prevent further access to the account pending further user verification processes.
Details related to current or recent logins should also be made visible to the user. For example, when they login to the application, the date, time and location of their previous login attempt could be displayed to them. Additionally, if the application supports concurrent sessions, the user should be able to view a list of all active sessions, and to terminate any other sessions that are not legitimate.
Credential stuffing is an automated attack where adversaries try lists of username and password pairs against a target service to gain unauthorized access. Analogy: like a burglar trying dozens of keys from a found keyring at a single apartment complex. Formal line: it is an automated authentication replay attack exploiting credential reuse across services. Credential stuffing is an automated attack using large sets of stolen credentials to attempt logins on target services. It is not the same as password guessing, though both aim to gain access. It leverages real credential pairs from breaches rather than brute forcing unknown passwords.
Automated reuse of breached username/password pairs against a target service to gain unauthorized access and commit fraud. 1) Auth-service outage due to request floods causing downstream DB spikes. 2) Session store exhaustion from many created sessions from successful ATOs. 3) Increased fraud losses as automated purchases or transfers occur. 4) Customer support overload with password reset requests and disputes. 5) Rate-limit rules misconfigured block legitimate traffic causing SLA violations.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Credential%20stuffing • https://en.wikipedia.org/wiki/Video%20game%20controversies • https://www.decryptiondigest.com/blog/credential-stuffing-prevention-detection-guide • https://webdecoy.com/blog/reverse-engineering-credential-stuffing-attacks-technical-deep-dive/ • https://cheatsheetseries.owasp.org/cheatsheets/Credential_Stuffing_Prevention_Cheat_Sheet.html • https://devsecopsschool.com/blog/credential-stuffing/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Credential Stuffing Attack Detection And Prevention Tool.
[*] Synchronizing KnowBe4 Awareness Training telemetry... ──────────────────────────────────────────────────────────────────────── [11:45:02.102] MAIL Dispatched simulated assessment templates [11:45:02.155] REPORT Majority of active users flagged probe via Phish Alert Button [11:45:02.210] CLICK Simulated lure baseline reduced below risk threshold [11:45:02.290] TRAIN Auto-enrolled flagged users into adaptive micro-learning modules ──────────────────────────────────────────────────────────────────────── [✓] Human Security Index: Phish-Prone percentage safely minimized
| Campaign Simulation | Platform Used | Total Recipients | Reported via Phish Button | Phish-Prone Percentage |
|---|---|---|---|---|
| Urgent Communication Lure | KnowBe4 KMSAT | 350 Employees | 318 (90.8%) | 2.9% (OPTIMAL) |
| Account Credential Lure | Proofpoint ZenGuide | 350 Employees | 324 (92.5%) | 2.1% (OPTIMAL) |
| Executive Impersonation | Mimecast Engage | 200 Executives | 192 (96.0%) | 1.5% (OPTIMAL) |