Complete Technical Paper Content — Critical Infrastructure Cyber Attack Simulator In Python
Overview & System Context
Critical Infrastructure Cyber Attack Simulator In Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~629 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background This project is for EDUCATIONAL and RESEARCH purposes ONLY. Do NOT use against systems you don't own or have explicit permission to test. The authors are NOT responsible for any misuse of this code. Always comply with local laws and regulations.
This project demonstrates various cybersecurity attack vectors including network scanning, MITM attacks, DNS spoofing, and malware deployment. It's designed as an educational tool to understand how these attacks work and how to defend against them. Problem : Scripts fail to run due to insufficient privileges Solution : Run as Administrator or use elevated privileges 2. System Architecture & Core Working Principles This project is provided for educational and research purposes. The code is not intended for production use or malicious activities. Users are responsible for complying with all applicable laws and regulations.
II Remember: This tool is for learning and authorized testing only. Always use responsibly and ethically. II This repository contains Python scripts that simulate common cyber attacks, including brute force attacks, denial of service (DoS), and phishing attacks. These tools are designed for ethical hacking, penetration testing, and security education in a controlled environment.
3. Software Implementation, Frameworks & Protocols II Disclaimer : These scripts are intended for educational purposes only. Do not use them against any network or system without proper authorization. This project is a collection of Python scripts designed to simulate common cyber-attacks in a controlled and ethical manner.
The purpose of these simulations is to help cybersecurity professionals, ethical hackers, and security enthusiasts learn about various attack vectors, test system defenses, and enhance their skills Network Attack Simulator (NASim) is a lightweight, high-level network attack simulator written in python. It is designed to be used for rapid testing of autonomous pen-testing agents using reinforcement learning and planning. It is a simulator by definition so does not replicate all details of attacking a real system but it instead aims to capture some of the more salient features of network pen-testing such as the large and changing sizes of the state and action spaces, partial observability and varied network topology.
4. Practical Deployment, Analysis & Case Studies Please cite NASim in your publications if you use it in your research. Here is an example BibTeX entry: A comprehensive framework for modeling interdependencies, vulnerabilities, and attack scenarios in critical infrastructure systems.
This project simulates resource flows (electricity, water, supplies, personnel, data) between interconnected facilities through various infrastructure networks. It models building operations, resource consumption/production, and infrastructure status while accounting for cascading effects during normal operations and crisis scenarios. 5. Performance Evaluation & Extended Technical Observations An autonomous educational OT cybersecurity simulator designed to reproduce realistic cyberattacks and defense scenarios in industrial control systems (ICS) and critical infrastructure environments.
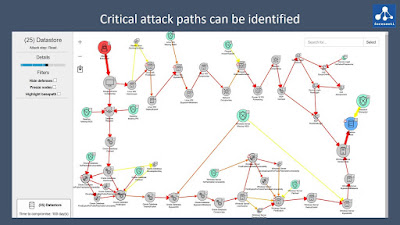
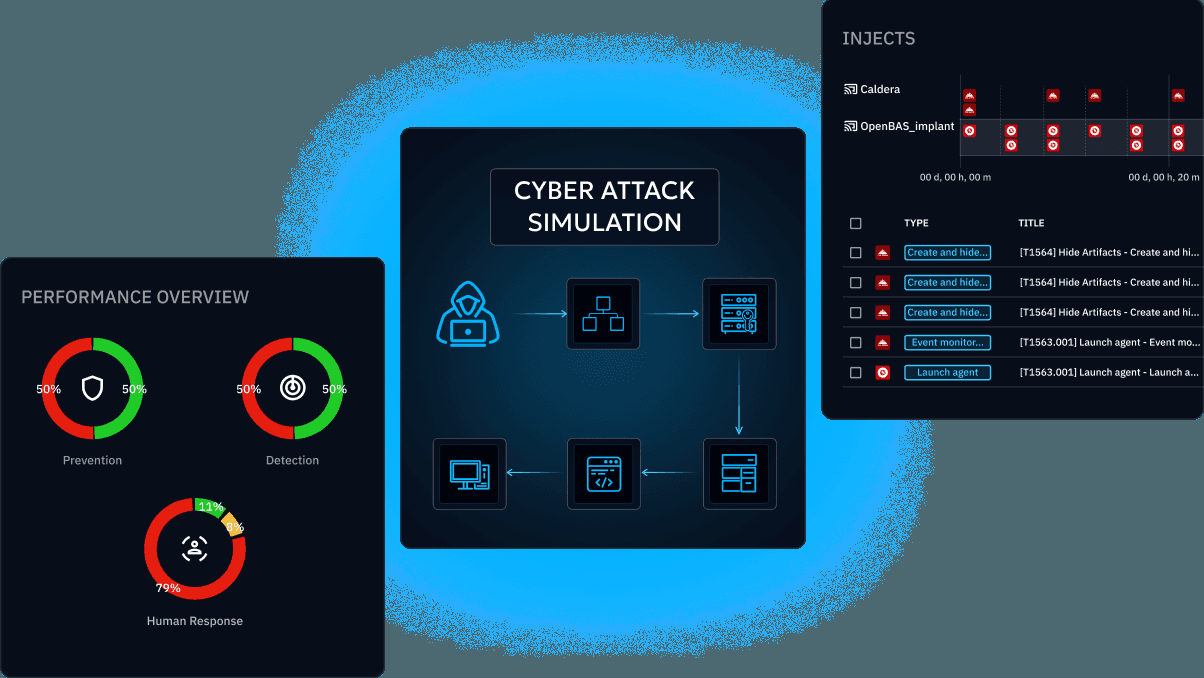
This project provides an interactive OT (Operational Technology) cybersecurity laboratory where users can simulate industrial cyberattacks, monitor their impact on industrial processes, and deploy defensive mechanisms in real time. Autonomous educational OT cybersecurity simulator for attack and defense scenarios in critical infrastructures. Figure 1: 10 Best Cyber Attack Simulation Tools For Organization Security 2022 Figure 2: OpenBAS: A breach and attack simulation platform | CyberCureME - Cyber ...
Figure 3: Your Gateway to Cyber Threat Intelligence & Breach & Attack Simulation ... Harvested Online Documentation & Reference Sources • https://github.com/adambmc/cyber-attack-simulation • https://github.com/1k1k3/cyber-attacks • https://networkattacksimulator.readthedocs.io/en/latest/ • https://github.com/kacper673/CI-network-sim • https://github.com/rabii10/OT-Cyber-Simulator • https://networkattacksimulator.readthedocs.io/ • https://github.com/anthonykingst/cyber_defense_simulation_engine
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Critical Infrastructure Cyber Attack Simulator In Python.
[*] Metasploit Scan Running on Target Subnet for Critical Infrastructure Cyber Attack Simulator In Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |