Complete Technical Paper Content — Cross Site Request Forgery Vulnerability Scanner Project
Overview & System Context
Cross Site Request Forgery Vulnerability Scanner Project: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9523 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background In computer security, a vulnerability is a flaw or weakness in a system's design, implementation, or management that can be exploited by a malicious actor to compromise its security. Despite a system administrator's best efforts to achieve complete correctness, virtually all hardware and software contain bugs where the system does not behave as expected. If the bug could enable an attacker to compromise the confidentiality, integrity, or availability of system resources, it can be considered a vulnerability. Insecure software development practices as well as design factors such as complexity can increase the burden of vulnerabilities. Vulnerability management includes identifying systems and prioritizing which are most important, scanning for vulnerabilities, and taking action to secure the system. Vulnerability management typically is a combination of remediation, mitigation, and acceptance. Vulnerabilities can be scored for severity according to the Common Vulnerability Scoring System (CVSS) and added to vulnerability databases such as the Common Vulnerabilities and Exposures (CVE) database. As of April 2026, more than 327,000 vulnerabilities had been recorded in the CVE database. A vulnerability is initiated when it is introduced into hardware or software. It becomes active and exploitable when the software or hardware containing the vulnerability is running. The vulnerability may be discovered by the administrator, vendor, or a third party. Publicly disclosing the vulnerability (through a patch or otherwise) is associated with an increased risk of compromise, as attackers can use this knowledge to target existing systems before patches are implemented. Vulnerabilities will eventually end when the system is either patched or removed from use.
Complexity: Large, complex systems increase the possibility of flaws and unintended access points. Familiarity: Using common, well-known code, software, operating systems, and/or hardware increases the probability an attacker has or can find the knowledge and tools to exploit the flaw. However, using well-known software, particularly free and open-source software, comes with the benefit of having more frequent and reliable software patches for any discovered vulnerabilities. Connectivity: any system connected to the internet can be accessed and compromised. Disconnecting systems from the internet can be extremely effective at preventing attacks, but it is not always feasible. Legacy software and hardware is at increased risk by nature. System administrators should consider upgrading from legacy systems, but this is often prohibitive in terms of cost and downtime.
The National Vulnerability Database classifies vulnerabilities into eight root causes that may be overlapping, including: Input validation vulnerabilities exist when input checking is not sufficient to prevent the attacker from injecting malicious code. Buffer overflow exploits, buffer underflow exploits, and boundary condition exploits typically take advantage of this category. Access control vulnerabilities enable an attacker to access a system that is supposed to be restricted to them, or engage in privilege escalation. When the system fails to handle and exceptional or unanticipated condition correctly, an attacker can exploit the situation to gain access. Configuration vulnerability come into existence when configuration settings cause risks to the system security, leading to such faults as unpatched software or file system permissions that do not sufficiently restrict access. A race condition—when timing or other external factors change the outcome and lead to inconsistent or unpredictable results—can cause a vulnerability.
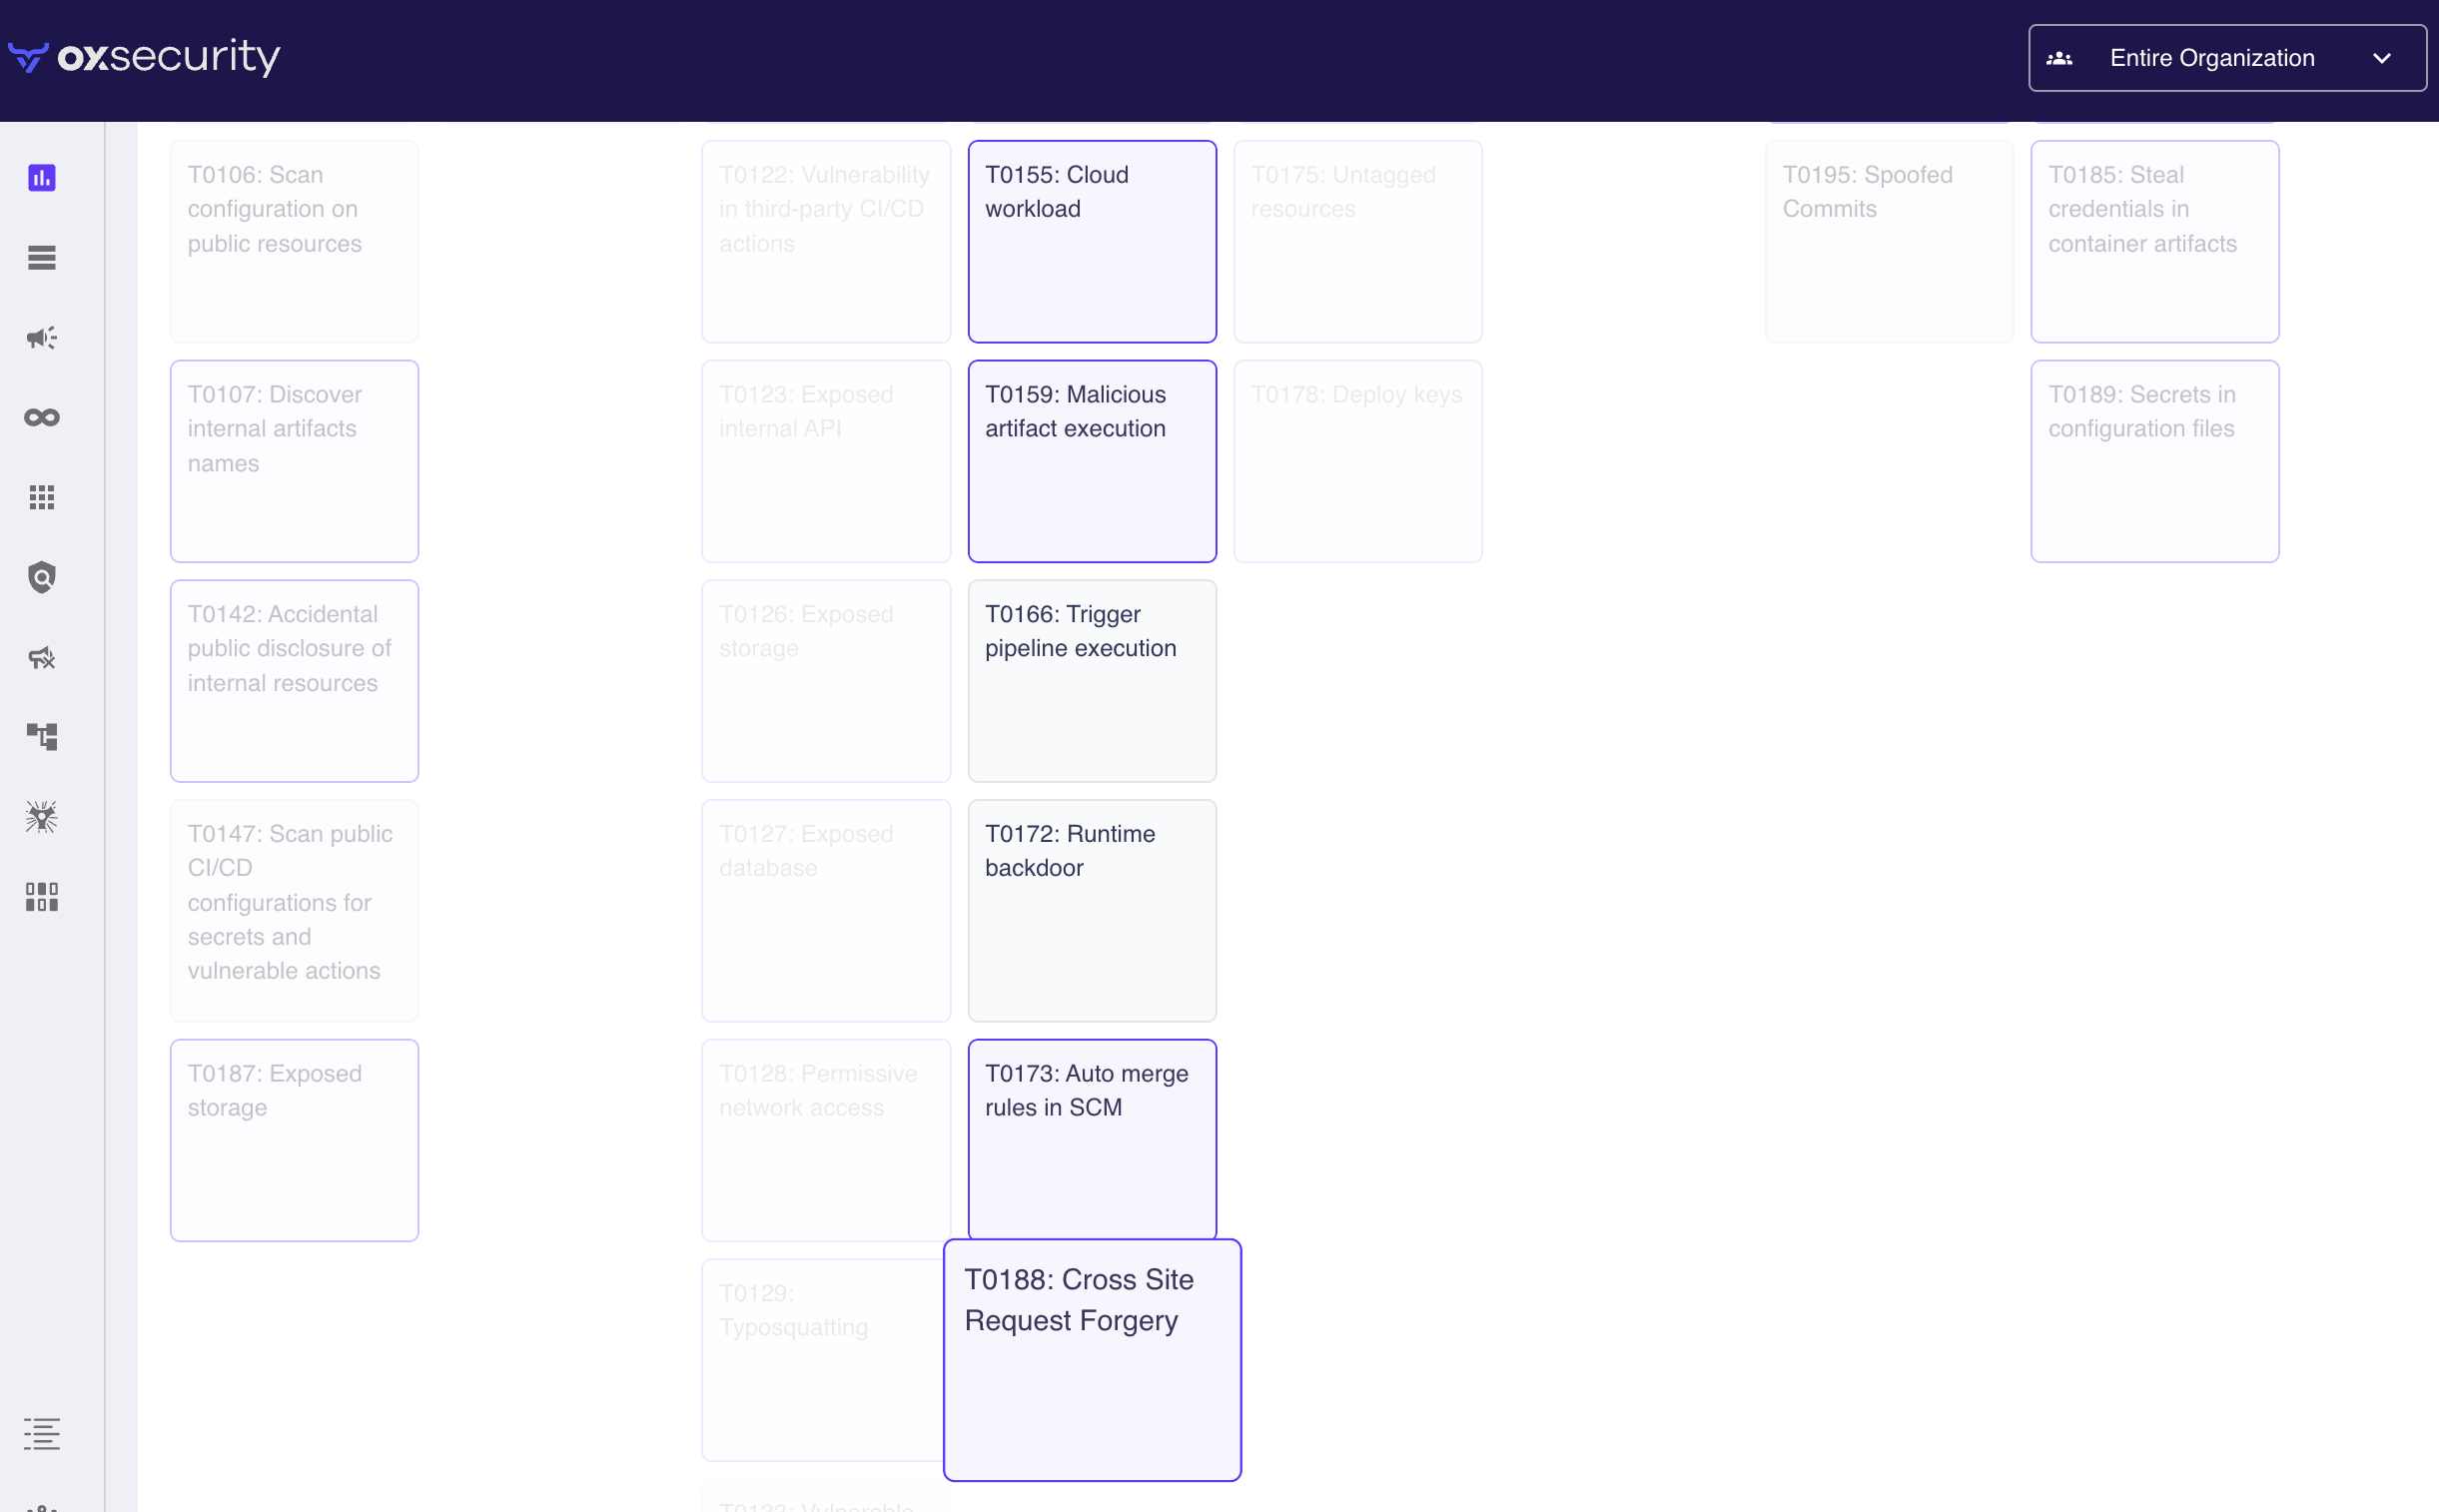
Figure 1: Cross Site Request Forgery - OSC&R | OX Security Although operating system vulnerabilities vary depending on the operating system in use, a common problem is privilege escalation bugs that enable the attacker to gain more access than they should be allowed. Open-source operating systems such as Linux and Android have a freely accessible source code and allow anyone to contribute, which could enable the introduction of vulnerabilities. However, the same vulnerabilities also occur in proprietary operating systems such as Microsoft Windows and Apple operating systems. All reputable vendors of operating systems provide patches regularly.
Unencrypted data that is in permanent storage or sent over a network is relatively easy for attackers to steal. Process hijacking occurs when an attacker takes over an existing computer process. Authentication and authorization failures enable attackers to access data that should be restricted to trusted users. Business logic vulnerability occurs when programmers do not consider unexpected cases arising in business logic. Attacks used against vulnerabilities in web applications include: Cross-site scripting (XSS) enables attackers to inject and run JavaScript-based malware when input checking is insufficient to reject the injected code. XSS can be persistent, when attackers save the malware in a data field and run it when the data is loaded; it can also be loaded using a malicious URL link (reflected XSS). Attackers can also insert malicious code into the domain object model. SQL injection and similar attacks manipulate database queries to gain unauthorized access to data.
Command injection is a form of code injection where the attacker places the malware in data fields or processes. The attacker might be able to take over the entire server. Cross-site request forgery (CSRF) is creating client requests that do malicious actions, such as an attacker changing a user's credentials. Server-side request forgery is similar to CSRF, but the request is forged from the server side and often exploits the enhanced privilege of the server. Business logic vulnerability occurs when programmers do not consider unexpected cases arising in business logic.
Figure 2: PaperCut NG/MF Vulnerability: Understanding the Cross-Site Request ... Memory safety (e.g. buffer overflow and dangling pointer bugs) Race condition Secure input and output handling Faulty use of an API Improper use case handling Improper exception handling Resource leaks, often but not always due to improper exception handling Preprocessing input strings before they are checked for being acceptable There is little evidence about the effectiveness and cost-effectiveness of different cyberattack prevention measures. Although estimating the risk of an attack is not straightforward, the mean time to breach and expected cost can be considered to determine the priority for remediating or mitigating an identified vulnerability and whether it is cost effective to do so. Although attention to security can reduce the risk of attack, achieving perfect security for a complex system is impossible, and many security measures have unacceptable cost or usability downsides. For example, reducing the complexity and functionality of the system is effective at reducing the attack surface. Successful vulnerability management usually involves a combination of remediation (closing a vulnerability), mitigation (increasing the difficulty, and reducing the consequences, of exploits), and accepting some residual risk. Often a defense in depth strategy is used for multiple barriers to attack. Some organizations scan for only the highest-risk vulnerabilities as this enables prioritization in the context of lacking the resources to fix every vulnerability. Increasing expenses is likely to have diminishing returns.
The vulnerability lifecycle begins when vulnerabilities are introduced into hardware or software. Detection of vulnerabilities can be by the software vendor, or by a third party. In the latter case, it is considered most ethical to immediately disclose the vulnerability to the vendor so it can be fixed. Government or intelligence agencies buy vulnerabilities that have not been publicly disclosed and may use them in an attack, stockpile them, or notify the vendor. As of 2013, the Five Eyes (United States, United Kingdom, Canada, Australia, and New Zealand) captured the plurality of the market and other significant purchasers included Russia, India, Brazil, Malaysia, Singapore, North Korea, and Iran. Organized criminal groups also buy vulnerabilities, although they typically prefer exploit kits. Even vulnerabilities that are publicly known or patched are often exploitable for an extended period. Security patches can take months to develop, or may never be developed. A patch can have negative effects on the functionality of software and users may need to test the patch to confirm functionality and compatibility. Larger organizations may fail to identify and patch all dependencies, while smaller enterprises and personal users may not install patches. Research suggests that risk of cyberattack increases if the vulnerability is made publicly known or a patch is released. Cybercriminals can reverse engineer the patch to find the underlying vulnerability and develop exploits, often faster than users install the patch. Vulnerabilities become deprecated when the software or vulnerable versions fall out of use. This can take an extended period of time; in particular, industrial software may not be feasible to replace even if the manufacturer stops supporting it.
An exploit is a method or piece of code that takes advantage of vulnerabilities in software, applications, networks, operating systems, or hardware, typically for malicious purposes. The term "exploit" derives from the English verb "to exploit," meaning "to use something to one’s own advantage." Exploits are designed to identify flaws, bypass security measures, gain unauthorized access to systems, take control of systems, install malware, or steal sensitive data. While an exploit by itself may not be a malware, it serves as a vehicle for delivering malicious software by breaching security controls. Estimates of the economic cost of cyberattacks that rely on exploits vary widely depending on methodology and scope; a 2020 McAfee/CSIS report estimated the global cost of cybercrime at more than US$1 trillion annually. In response to this threat, organizations are increasingly utilizing cyber threat intelligence to identify vulnerabilities and prevent hacks before they occur.
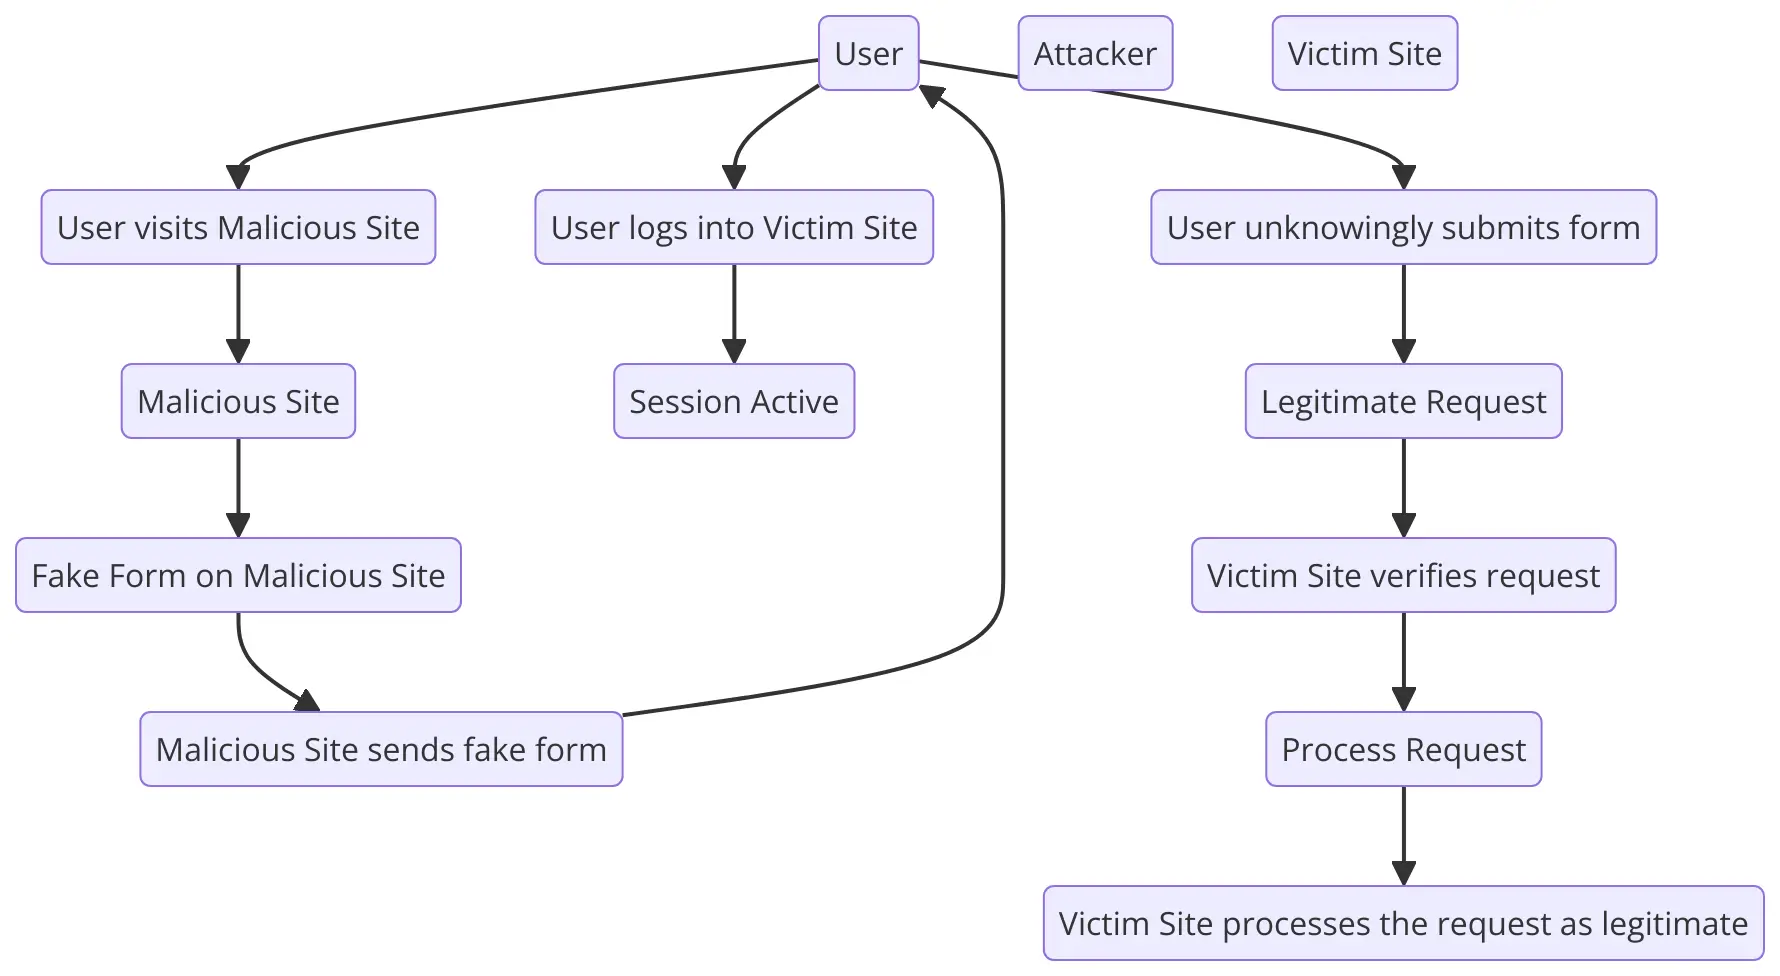
Figure 3: What is Cross-site request forgery (CSRF)? Remote exploits – Works over a network and exploits the security vulnerability without any prior access to the vulnerable system. Local exploits – Requires prior access or physical access to the vulnerable system, and usually increases the privileges of the person running the exploit past those granted by the system administrator.
Server-side exploits – Target vulnerabilities in server applications, such as web servers or database servers, often by sending maliciously crafted requests to exploit security flaws. Client-side exploits – Target vulnerabilities in client applications, such as web browsers (browser exploits) or media players. These exploits often require user interaction, like visiting a malicious website or opening a compromised file. Exploits against client applications may also require some interaction with the user and thus may be used in combination with the social engineering method.
Code execution exploits – Allow attackers to execute arbitrary code on the target system, potentially leading to full system compromise. Denial-of-service (DoS) exploits – Aim to disrupt the normal functioning of a system or service, making it unavailable to legitimate users. Privilege escalation exploits – Enable attackers to gain higher privileges on a system than initially granted, potentially leading to unauthorized actions. Information disclosure exploits – Lead to unauthorized access to sensitive information due to vulnerabilities in the system.
Buffer overflow – Attackers send more data to a buffer than it can handle, causing it to overflow and overwrite adjacent memory, potentially allowing arbitrary code execution. SQL injection – Malicious SQL code is inserted into input fields of web applications, enabling attackers to access or manipulate databases. Cross-site scripting (XSS) – Attackers inject malicious scripts into web pages viewed by other users, potentially leading to session hijacking or data theft. Cross-site request forgery (CSRF) – Attackers trick users into performing actions they did not intend, such as changing account settings, by exploiting the user's authenticated session.
Proxy pivoting is the practice of channeling traffic through a compromised target using a proxy payload on the machine and launching attacks from the computer. This type of pivoting is restricted to certain TCP and UDP ports that are supported by the proxy. VPN pivoting enables the attacker to create an encrypted layer to tunnel into the compromised machine to route any network traffic through that target machine, for example, to run a vulnerability scan on the internal network through the compromised machine, effectively giving the attacker full network access as if they were behind the firewall. Typically, the proxy or VPN applications enabling pivoting are executed on the target computer as the payload of an exploit. Pivoting is usually done by infiltrating a part of a network infrastructure (as an example, a vulnerable printer or thermostat) and using a scanner to find other devices connected to attack them. By attacking a vulnerable piece of networking, an attacker could infect most or all of a network and gain complete control.
A security hacker or security researcher is someone who explores methods for breaching or bypassing defenses and exploiting weaknesses in a computer system or network. Hackers may be motivated by a multitude of reasons, such as profit, protest, sabotage, information gathering, challenge, recreation, or evaluation of a system weaknesses to assist in formulating defenses against potential hackers.
A white hat hacker breaks security for non-malicious reasons, either to test their own security system, perform penetration tests or vulnerability assessments for a client, or while working for a security company that makes security software. The term is generally synonymous with ethical hacker, and certifications, courseware, classes, and online training covering the diverse arena of ethical hacking have been developed.
A black hat hacker is a hacker who "violates computer security for little reason beyond maliciousness or for personal gain". The term was coined by Richard Stallman, to contrast the maliciousness of a criminal hacker versus the spirit of playfulness and exploration in hacker culture, or the ethos of the white hat hacker who performs hacking duties to identify places to repair or as a means of legitimate employment. Black hat hackers form the stereotypical, illegal hacking groups often portrayed in popular culture, and are "the epitome of all that the public fears in a computer criminal".
A grey hat hacker lies between a black hat and a white hat hacker, hacking for ideological reasons. A grey hat hacker may surf the Internet and hack into a computer system for the sole purpose of notifying the administrator that their system has a security defect, for example. They may then offer to correct the defect for a fee. Grey hat hackers sometimes find the defect in a system and publish the facts to the world instead of a group of people. Even though grey hat hackers may not necessarily perform hacking for their personal gain, unauthorized access to a system can be considered illegal and unethical.
A script kiddie (also known as a skid or skiddie) is an unskilled hacker who breaks into computer systems by using automated tools written by others (usually by other black hat hackers), hence the term script (i.e. a computer script that automates the hacking) kiddie (i.e. kid, child an individual lacking knowledge and experience, immature), usually with little understanding of the underlying concept.
A blue hat hacker is someone outside computer security consulting firms who is used to bug-test a system prior to its launch, looking for exploits so they can be closed. Microsoft also uses the term BlueHat to represent a series of security briefing events. Hackers can usually be sorted into two types of attacks: mass attacks and targeted attacks. They are sorted into the groups in terms of how they choose their victims and how they act on the attacks. A typical approach in an attack on Internet-connected system is: Network enumeration: Discovering information about the intended target. Vulnerability analysis: Identifying potential ways of attack. Exploitation: Attempting to compromise the system by employing the vulnerabilities found through the vulnerability analysis. In order to do so, there are several recurring tools of the trade and techniques used by computer criminals and security experts.
A security exploit is a prepared application that takes advantage of a known weakness. Common examples of security exploits are SQL injection, cross-site scripting and cross-site request forgery which abuse security holes that may result from substandard programming practice. Other exploits would be able to be used through File Transfer Protocol (FTP), Hypertext Transfer Protocol (HTTP), PHP, SSH, Telnet and some Web pages. These are very common in Web site and Web domain hacking.
Andrew Auernheimer, sentenced to three years in prison, is a hacker whose security group Goatse Security exposed a flaw in AT&T's iPad security. Dan Kaminsky was a DNS expert who exposed multiple flaws in the protocol and investigated Sony's rootkit security issues in 2005. He spoke in front of the United States Senate on technology issues. Ed Cummings (also known as Bernie S) is a longstanding writer for 2600: The Hacker Quarterly. In 1995, he was arrested and charged with possession of technology that could be used for fraudulent purposes, and set legal precedents after being denied both a bail hearing and a speedy trial. Eric Corley (also known as Emmanuel Goldstein) is the longstanding publisher of 2600: The Hacker Quarterly.
He is also the founder of the Hackers on Planet Earth (HOPE) conferences. He has been part of the hacker community since the late 1970s. Susan Headley (also known as Susan Thunder), was an American hacker active during the late 1970s and early 1980s widely respected for her expertise in social engineering, pretexting, and psychological subversion. She became heavily involved in phreaking with Kevin Mitnick and Lewis De Payne in Los Angeles, but later framed them for erasing the system files at US Leasing after a falling out, leading to Mitnick's first conviction. Gary McKinnon is a Scottish hacker who was facing extradition to the United States to face criminal charges. Many people in the UK called on the authorities to be lenient with McKinnon, who has Asperger syndrome. The extradition has now been dropped. Gordon Lyon, known by the handle Fyodor, authored the Nmap Security Scanner as well as many network security books and web sites. He is a founding member of the Honeynet Project and Vice President of Computer Professionals for Social Responsibility. Guccifer 2.0, who claimed that he hacked into the Democratic National Committee (DNC) computer network Jacob Appelbaum is an advocate, security researcher, and developer for the Tor project. He speaks internationally for usage of Tor by human rights groups and others concerned about Internet anonymity and censorship. Joanna Rutkowska is a Polish computer security researcher who developed the Blue Pill rootkit and Qubes OS. Jude Milhon (known as St. Jude) was an American hacker and activist, founding member of the cypherpunk movement, and one of the creators of Community Memory, the first public computerized bulletin board system. Kevin Mitnick was a computer security consultant and author, formerly the most wanted computer criminal in United States history. Len Sassaman was a Belgian computer programmer and technologist who was also a privacy advocate. Meredith L. Patterson is a well-known technologist and biohacker who has presented research with Dan Kaminsky and Len Sassaman at many international security and hacker conferences. Kimberley Vanvaeck (known as Gigabyte) is a Belgian hacker recognized for writing the first virus in C#. MichaI Zalewski (lcamtuf) is a prominent security researcher. Solar Designer is the pseudonym of the founder of the Openwall Project. Kane Gamble, sentenced to 2 years in youth detention, who is autistic, gained access to highly sensitive information and "cyber-terrorised" high-profile U.S.
intelligence officials such as then CIA chief John Brennan or Director of National Intelligence James Clapper. The computer underground is supported by regular real-world gatherings called hacker conventions or "hacker cons". These events include SummerCon (Summer), DEF CON, HoHoCon (Christmas), ShmooCon (February), Black Hat Conference, Chaos Communication Congress, AthCon, Hacker Halted, and H.O.P.E. Local Hackfest groups organize and compete to develop their skills to send a team to a prominent convention to compete in group pentesting, exploit and forensics on a larger scale. Hacker groups became popular in the early 1980s, providing access to hacking information and resources and a place to learn from other members. Computer bulletin board systems (BBSs), such as the Utopias, provided platforms for information-sharing via dial-up modem. Hackers could also gain credibility by being affiliated with elite groups.
Unauthorised access to computer material, with a penalty of up to six months in prison and/or a £5000 fine. Unauthorised access to computer materials with intent to commit a further crime, with a penalty of up to five years in prison and/or an unlimited fine. Unauthorised modification of data, with a penalty of up to five years in prison and/or an unlimited fine. Making, supplying or obtaining anything which can be used in computer misuse offences, with a penalty of up to ten years in prison and/or an unlimited fine.
A computer exclusively for the use of a financial institution or the United States Government, or, in the case of a computer not exclusively for such use, used by or for a financial institution or the United States Government and the conduct constituting the offense affects that use by or for the financial institution or the Government. A computer which is used in or affecting interstate or foreign commerce or communication, including a computer located outside the United States that is used in a manner that affects interstate or foreign commerce or communication of the United States; The maximum imprisonment or fine for violations of the Computer Fraud and Abuse Act depends on the severity of the violation and the offender's history of violations under the Act. The FBI has demonstrated its ability to recover ransoms paid in cryptocurrency by victims of cybertheft.
The most notable hacker-oriented print publications are Phrack, Hakin9 and 2600: The Hacker Quarterly. While the information contained in hacker magazines and ezines was often outdated by the time they were published, they enhanced their contributors' reputations by documenting their successes. Hackers often show an interest in fictional cyberpunk and cyberculture literature and movies. The adoption of fictional pseudonyms, symbols, values and metaphors from these works is very common.
Kali Linux - Linux-based OS and tools focusing on network penetration testing Ghidra - open-source software decompiler IDA Pro - proprietary software decompiler SoftICE - proprietary software debugger (legacy) Nmap - open-source network inspection tool Media related to Hacking (computer security) at Wikimedia Commons CNN Tech PCWorld Staff (November 2001). Timeline: A 40-year history of hacking from 1960 to 2001 Can Hackers Be Heroes? Video produced by Off Book (web series) Cross-Site Request Forgery (CSRF) is an attack that forces an end user to execute unwanted actions on a web application in which they’re currently authenticated. With a little help of social engineering (such as sending a link via email or chat), an attacker may trick the users of a web application into executing actions of the attacker’s choosing. If the victim is a normal user, a successful CSRF attack can force the user to perform state changing requests like transferring funds, changing their email address, and so forth. If the victim is an administrative account, CSRF can compromise the entire web application.
See the OWASP Code Review Guide article on how to review code for CSRF vulnerabilities . Most frameworks have built-in CSRF support such as Joomla , Spring , Struts , Ruby on Rails , .NET and others. John Melton also has an excellent blog post describing how to use the native anti-CSRF functionality of the OWASP ESAPI . 2. System Architecture & Core Working Principles CSRF attacks target functionality that causes a state change on the server, such as changing the victim’s email address or password, or purchasing something. Forcing the victim to retrieve data doesn’t benefit an attacker because the attacker doesn’t receive the response, the victim does. As such, CSRF attacks target state-changing requests.
An attacker can use CSRF to obtain the victim’s private data via a special form of the attack, known as login CSRF. The attacker forces a non-authenticated user to log in to an account the attacker controls. If the victim does not realize this, they may add personal data—such as credit card information—to the account. The attacker can then log back into the account to view this data, along with the victim’s activity history on the web application.
It’s sometimes possible to store the CSRF attack on the vulnerable site itself. Such vulnerabilities are called “stored CSRF flaws”. This can be accomplished by simply storing an IMG or IFRAME tag in a field that accepts HTML, or by a more complex cross-site scripting attack. If the attack can store a CSRF attack in the site, the severity of the attack is amplified. In particular, the likelihood is increased because the victim is more likely to view the page containing the attack than some random page on the Internet. The likelihood is also increased because the victim is sure to be authenticated to the site already.
CSRF attacks are also known by a number of other names, including XSRF, “Sea Surf”, Session Riding, Cross-Site Reference Forgery, and Hostile Linking. Microsoft refers to this type of attack as a One-Click attack in their threat modeling process and many places in their online documentation. A number of flawed ideas for defending against CSRF attacks have been developed over time. Here are a few that we recommend you avoid.
Applications can be developed to only accept POST requests for the execution of business logic. The misconception is that since the attacker cannot construct a malicious link, a CSRF attack cannot be executed. Unfortunately, this logic is incorrect. There are numerous methods in which an attacker can trick a victim into submitting a forged POST request, such as a simple form hosted in an attacker’s Website with hidden values. This form can be triggered automatically by JavaScript or can be triggered by the victim who thinks the form will do something else.
Multi-Step transactions are not an adequate prevention of CSRF. As long as an attacker can predict or deduce each step of the completed transaction, then CSRF is possible. This might be seen as a useful CSRF prevention technique as the attacker cannot guess the victim’s session ID. However, the user’s session ID is exposed in the URL. We don’t recommend fixing one security flaw by introducing another.
However, HTTPS should be considered a prerequisite for any preventative measures to be trustworthy. This doesn’t work in practice because the referrer header can be easily spoofed by an attacker. Additionally, some users or browsers might not send the referrer header due to privacy settings or policies, leading to false positives. Moreover, there are situations where the referrer can be null, such as when a user navigates to a site from a bookmark or any other resource without a traditional url. In these scenarios, legitimate requests could be mistaken as potential CSRF attacks, which would result in more potential false positive flags.
There are numerous ways in which an end user can be tricked into loading information from or submitting information to a web application. In order to execute an attack, we must first understand how to generate a valid malicious request for our victim to execute. Let us consider the following example: Alice wishes to transfer $100 to Bob using the bank.com web application that is vulnerable to CSRF. Maria, an attacker, wants to trick Alice into sending the money to Maria instead. The attack will comprise the following steps: If the application was designed to primarily use GET requests to transfer parameters and execute actions, the money transfer operation might be reduced to a request like: Maria now decides to exploit this web application vulnerability using Alice as the victim. Maria first constructs the following exploit URL which will transfer $100,000 from Alice’s account to Maria’s account. Maria takes the original command URL and replaces the beneficiary name with herself, raising the transfer amount significantly at the same time: The social engineering aspect of the attack tricks Alice into loading this URL when Alice is logged into the bank application.
This is usually done with one of the following techniques: The exploit URL can be disguised as an ordinary link, encouraging the victim to click it: If this image tag were included in the email, Alice wouldn’t see anything. However, the browser will still submit the request to bank.com without any visual indication that the transfer has taken place.
A real life example of CSRF attack on an application using GET was a uTorrent exploit from 2008 that was used on a mass scale to download malware. The only difference between GET and POST attacks is how the attack is being executed by the victim. Let’s assume the bank now uses POST and the vulnerable request looks like this: Such a request cannot be delivered using standard A or IMG tags, but can be delivered using a FORM tags: This form will require the user to click on the submit button, but this can be also executed automatically using JavaScript: Modern web application APIs frequently use other HTTP methods, such as PUT or DELETE. Let’s assume the vulnerable bank uses PUT that takes a JSON block as an argument: Fortunately, this request will not be executed by modern web browsers thanks to same-origin policy restrictions. This restriction is enabled by default unless the target web site explicitly opens up cross-origin requests from the attacker’s (or everyone’s) origin by using CORS with the following header: “This paper serves as a living document for Cross-Site Request Forgery issues. This document will serve as a repository of information from existing papers, talks, and mailing list postings and will be updated as new information is discovered.”* Access to this page requires authorization. You can try signing in or changing directories .
Cross-site request forgery is an attack against web-hosted apps whereby a malicious web app can influence the interaction between a client browser and a web app that trusts that browser. These attacks are possible because web browsers send some types of authentication tokens automatically with every request to a website. This form of exploit is also known as a one-click attack or session riding because the attack takes advantage of the user's previously authenticated session.
Cross-site request forgery is also known as XSRF or CSRF. The malicious site, www.bad-crook-site.example.com , contains an HTML form similar to the following example: Notice that the form's action posts to the vulnerable site, not to the malicious site. This is the "cross-site" part of CSRF. The request runs on the www.good-banking-site.example.com server with the user's authentication context and can perform any action that an authenticated user is allowed to perform.
In addition to the scenario where the user selects the button to submit the form, the malicious site could: These alternative scenarios don't require any action or input from the user other than initially visiting the malicious site. Using HTTPS doesn't prevent a CSRF attack. The malicious site can send https://www.good-banking-site.example.com/ a request just as easily as it can send an insecure request.
Some attacks target endpoints that respond to GET requests, in which case an image tag can be used to perform the action. This form of attack is common on forum sites that permit images but block JavaScript. Apps that change state on GET requests, where variables or resources are altered, are vulnerable to malicious attacks. GET requests that change state are insecure. A best practice is to never change state on a GET request.
In this context, session refers to the client-side session during which the user is authenticated. It's unrelated to server-side sessions or ASP.NET Core session middleware . However, CSRF vulnerabilities are fundamentally a problem with the web app, not the end user. When a user is authenticated, they're issued a token (not an antiforgery token). The token contains user information in the form of claims or a reference token that points the app to user state maintained in the app. When a user attempts to access a resource that requires authentication, the token is sent to the app with an extra authorization header in the form of a Bearer token. This approach makes the app stateless. In each subsequent request, the token is passed in the request for server-side validation. This token isn't encrypted ; it's encoded . On the server, the token is decoded to access its information. To send the token on subsequent requests, store the token in the browser's local storage. Placing a token in the browser local storage and retrieving it and using it as a bearer token provides protection against CSRF attacks. However, should the app be vulnerable to script injection via XSS or a compromised external JavaScript file, a cyberattacker could retrieve any value from local storage and send it to themselves. ASP.NET Core encodes all server side output from variables by default, reducing the risk of XSS. If you override this behavior by using Html.Raw or custom code with untrusted input then you may increase the risk of XSS.
Shared hosting environments are vulnerable to session hijacking, sign-in CSRF, and other attacks. Modern browsers attach Fetch Metadata request headersâIImost importantly Sec-Fetch-Site âIIto every request. Sec-Fetch-Site describes the relationship between the origin that initiated the request and the origin being requested: same-origin identifies a request the site made to itself, while same-site and cross-site identify requests initiated by another origin. The Origin header carries the initiating origin and serves as a fallback for browsers that predate Fetch Metadata.
3. Software Implementation, Frameworks & Protocols Sec-Fetch-Site and Origin are forbidden request headers : the browser sets them, and JavaScript running in a page can't override or forge them. That makes them a trustworthy signal for telling a site's own requests apart from cross-site requests without a server-issued token. The automatic CSRF protection built into ASP.NET Core uses this signal to reject cross-site form posts that aren't explicitly trusted.
ASP.NET Core ships an automatic CSRF protection middleware that's enabled by default in apps built with WebApplication.CreateBuilder . Unlike the token-based antiforgery system , this middleware doesn't issue or validate tokens. Instead, it inspects the Sec-Fetch-Site and Origin Fetch metadata headers and records a validation verdict on the request. Components that process submitted form data enforce that verdict, rejecting cross-origin form posts that aren't explicitly trusted.
For most apps, no code changes are required: same-origin browser requests, safe HTTP methods, and non-browser clients ( curl , server-to-server, mobile apps) all pass through unaffected. The middleware primarily affects apps that accept cross-origin form posts from a browser, such as a site that posts a form to an API on a different origin. Those scenarios need to either configure CORS to declare the trusted origin or opt the endpoint out.
This middleware is additive to the token-based antiforgery system. The two protections coexist and can both be active on the same endpoint. For a comparison of when each one applies, see Interaction with token-based antiforgery . For every request, the middleware evaluates a short chain of rules to reach a verdictâII allowed or denied . The checks run in order, and the first match wins: The middleware records this verdict on the request rather than ending the request itself. For how and when a denied verdict turns into an HTTP 400 Bad Request response, see Deferred validation .
The middleware doesn't reject a request on its own. Instead, it records its verdict on the request's IAntiforgeryValidationFeature âIIthe same feature the token-based antiforgery system usesâIIwhere a denied verdict is recorded as invalid . The request continues down the pipeline. An invalid verdict becomes an HTTP 400 Bad Request only when a component that processes form data observes it. This deferral matches how the token-based system already behaves: the verdict is produced early but enforced at the point where a form is consumed.
The following components read IAntiforgeryValidationFeature and reject a request with 400 - Bad Request when the recorded verdict is invalid: Each consumer first confirms that an antiforgery or CSRF middleware actually ran before it trusts the verdict, so a pipeline without either middleware doesn't produce false rejections.
The middleware is registered automatically by WebApplication.CreateBuilder and runs after authentication and authorization. It validates each request using the registered ICsrfProtection implementation, which by default applies the rules described in How it works . The default implementation can be replaced; see Customizing: implement ICsrfProtection . To turn the middleware off entirely, see Disabling globally .
The result is that a minimal app with a form-handling endpoint like the following is already protected: A browser making a same-origin POST /widgets request reaches the endpoint normally. A browser at https://attacker.example.com posting the same form is rejected with 400 - Bad Request when the endpoint binds the form, before the handler body runs. A curl request without Sec-Fetch-Site or Origin is allowed.
Because rejection is deferred to form consumers , an endpoint that doesn't read form dataâIIsuch as a JSON API that binds its body from JSONâIIisn't rejected automatically, even on a cross-origin request. The verdict is still recorded on the request for code that wants to inspect it. The most common scenario that requires action is a browser-based client that submits a cross-origin formâIIfor example, a site at https://app.contoso.com posting a form to an API at https://api.contoso.com . Such form posts are denied by default because Sec-Fetch-Site is same-site or cross-site rather than same-origin , and the form consumer enforces that verdict with a 400 - Bad Request .
The CSRF middleware doesn't introduce its own trust list. It reuses the same CORS policy that the CORS middleware resolves for the endpoint: if that policy allows the request's Origin and the policy has .AllowCredentials() configured, the CSRF middleware records an allowed verdict for the request. Allowing an origin with WithOrigins does not, by itself, permit browser JavaScript at that origin to read responses to credentialed requests. .AllowCredentials() grants that permission. Omitting it does not guarantee that requests arrive without credentials, so CORS alone is not a defense against CSRF. The CSRF middleware requires both an allowed origin and .AllowCredentials() as an explicit trust signal. Otherwise, the request falls through to the remaining Sec-Fetch-Site and Origin-vs-Host checks.
[DisableCors] on an endpoint isn't a CSRF opt-out. It skips the CORS-derived trust step, and the request still has to satisfy the Sec-Fetch-Site and Origin-vs-Host rules. To opt out of CSRF protection, see Opting an endpoint out . For details on configuring CORS itselfâII AddCors , AddDefaultPolicy , AddPolicy , WithOrigins , and the rest of the policy builder APIâIIsee Enable Cross-Origin Requests (CORS) in ASP.NET Core .
Either approach adds IAntiforgeryMetadata { RequiresValidation = false } to the endpoint, which the CSRF middleware honors by skipping validation. The middleware can be disabled across the entire app using the DisableCsrfProtection configuration key. This is an escape hatchâIIprefer per-endpoint opt-outs.
When this key is set to true , WebApplication skips registering the middleware in the pipeline. The ICsrfProtection service remains registered, so anything that resolves it directly continues to work. The automatic CSRF middleware also satisfies the antiforgery requirement for endpoints that require validation, even when an app doesn't call app.UseAntiforgery() . If an app relies on antiforgery but doesn't call app.UseAntiforgery() , disabling the CSRF middleware globally or running on a host that isn't built with WebApplication , where the middleware isn't injected, leaves those endpoints with no antiforgery middleware. A request to such an endpoint then throws an exception. Call app.UseAntiforgery() in that configuration.
Sec-Fetch-Site is supported by all current versions of Chromium-based browsers, Firefox, and Safari. For an authoritative compatibility table, see the MDN reference for Sec-Fetch-Site . Older browsers that predate Fetch Metadata don't send Sec-Fetch-Site . For those clients, the middleware falls back to comparing the Origin header against the request's scheme and host. Browsers have sent Origin on cross-origin write requests for many years, so this fallback covers essentially all legacy browser traffic.
To replace the default implementation, register a singleton in DI. Because the framework uses TryAddSingleton , an explicit AddSingleton call overrides the default: A custom implementation is useful when the trust model doesn't fit CORSâIIfor example, when a fixed allowlist of partner origins is preferred, or when stricter rules are needed: The middleware still honors .DisableAntiforgery() / [IgnoreAntiforgeryToken] regardless of which implementation is registeredâIIopt-out is handled by the middleware itself before ValidateAsync is called.
The two CSRF defenses target different layers and are designed to coexist. They also share the same request feature: both record their result on IAntiforgeryValidationFeature , and form consumers enforce whatever verdict is present. The automatic CSRF middleware replaces the token-based system in many scenarios, because both protect the same form-handling endpoints. Keep the token-based system when: For details on the token-based system, including form integration, AJAX flows, configuration via AntiforgeryOptions , and IAntiforgery APIs, see Antiforgery in ASP.NET Core .
When an app calls app.UseAntiforgery() , the token-based middleware runs after the automatic CSRF middleware. The token middleware clears any verdict the CSRF middleware recorded and replaces it with the result of token validation. The token result is authoritative: This ordering means apps that use the token system see the same end-to-end behavior they had before the automatic middleware existed, while apps that don't use tokens fall back to the CSRF middleware's verdict.
Blazor static server-side rendering (SSR) endpoints participate in the same deferred model. The Razor Components endpoint trusts the verdict recorded on IAntiforgeryValidationFeature by the upstream middleware and returns 400 - Bad Request for a form post only when that verdict is invalid. The endpoint no longer validates the request itself. This is a behavior change for static SSR that previously removed app.UseAntiforgery() : they're now protected by the CSRF middleware rather than left unprotected, and they stop emitting antiforgery tokens. For migration guidance, see Migrate from ASP.NET Core in .NET 10 to ASP.NET Core in .NET 11 . For the formal breaking-change notice, see Blazor server-side rendering defers antiforgery validation to middleware .
Symptom: Same-origin requests from a browser succeed, but cross-origin form posts return 400 - Bad Request with no body. Cause: The CSRF middleware recorded an invalid verdict for the cross-origin request, and a form-processing componentâIIsuch as an MVC action, a Minimal API form binding, or a Blazor SSR form postâIIenforced that verdict with a 400 - Bad Request . This is the expected default behavior for endpoints that process forms.
Diagnosing: The middleware logs every invalid verdict at Debug level under the category Microsoft.AspNetCore.Antiforgery.CsrfProtectionMiddleware with event name CsrfValidationFailed . Enable Debug logging for that category in appsettings.Development.json : Reproducing locally: Use curl with an explicit Origin header to simulate a cross-origin browser request against a form endpoint: 4. Practical Deployment, Analysis & Case Studies Replace {PORT} with the app's local HTTPS port. The 400 - Bad Request is observed because the endpoint binds the form, which enforces the recorded verdict. A non-form endpoint returns its normal response because nothing reads the verdict.
Without the Origin header, the same request is allowed because curl doesn't send Sec-Fetch-Site either and a request with neither header is treated as a non-browser client. The token-based antiforgery system described in the rest of this article predates this middleware and remains available. For most apps, the automatic protection is enough on its own. For guidance on when to keep the token-based system and how to migrate, see Migrate from ASP.NET Core in .NET 10 to ASP.NET Core in .NET 11 .
ASP.NET Core implements antiforgery using ASP.NET Core Data Protection . The data protection stack must be configured to work in a server farm. For more information, see Configuring data protection . Antiforgery services are registered in the dependency injection container when one of the following APIs is called in Program.cs : Registering the services doesn't add the Antiforgery middleware to the request processing pipeline. Calling AddRazorComponents or AddAntiforgery only registers the antiforgery services in DI; it doesn't add the middleware. Blazor and Minimal APIs require an explicit call to UseAntiforgery in Program.cs to add the middleware to the request processing pipeline. MVC and Razor Pages validate tokens with built-in filters and don't require the middleware. For more information, see ASP.NET Core Blazor authentication and authorization and Antiforgery with Minimal APIs .
Registering the services doesn't add the Antiforgery middleware to the request processing pipeline. Calling AddRazorComponents or AddAntiforgery only registers the antiforgery services in DI; it doesn't add the middleware. Blazor and Minimal APIs require an explicit call to UseAntiforgery in Program.cs to add the middleware to the request processing pipeline (present by default in the Blazor Web App project template). MVC and Razor Pages validate tokens with built-in filters and don't require the middleware. For more information, see ASP.NET Core Blazor authentication and authorization and Antiforgery with Minimal APIs .
The FormTagHelper injects antiforgery tokens into HTML form elements. The following markup in a Razor file automatically generates antiforgery tokens: Similarly, IHtmlHelper.BeginForm generates antiforgery tokens by default if the form's method isn't GET. The automatic generation of antiforgery tokens for HTML form elements happens when the
The most common approach to protecting against CSRF attacks is to use the Synchronizer Token Pattern (STP). STP is used when the user requests a page with form data: The token is unique and unpredictable. The token can also be used to ensure proper sequencing of a series of requests (for example, ensuring the request sequence of: page 1 > page 2 > page 3). All of the forms in ASP.NET Core MVC and Razor Pages templates generate antiforgery tokens. The following pair of view examples generates antiforgery tokens: Explicitly add an antiforgery token to a
Multiple tabs logged in as different users, or one logged in as anonymous, are not supported. The ValidateAntiForgeryToken action filter can be applied to an individual action, a controller, or globally. Requests made to actions that have this filter applied are blocked unless the request includes a valid antiforgery token: The ValidateAntiForgeryToken attribute requires a token for requests to the action methods it marks, including HTTP GET requests. If the ValidateAntiForgeryToken attribute is applied across the app's controllers, it can be overridden with the IgnoreAntiforgeryToken attribute.
Instead of broadly applying the ValidateAntiForgeryToken attribute and then overriding it with IgnoreAntiforgeryToken attributes, the AutoValidateAntiforgeryToken attribute can be used.
This attribute works identically to the ValidateAntiForgeryToken attribute, except that it doesn't require tokens for requests made using the following HTTP methods: We recommend use of AutoValidateAntiforgeryToken broadly for non-API scenarios. This attribute ensures POST actions are protected by default. The alternative is to ignore antiforgery tokens by default, unless ValidateAntiForgeryToken is applied to individual action methods. It's more likely in this scenario for a POST action method to be left unprotected by mistake, leaving the app vulnerable to CSRF attacks. All POSTs should send the antiforgery token.
The IgnoreAntiforgeryToken filter is used to eliminate the need for an antiforgery token for a given action (or controller). When applied, this filter overrides ValidateAntiForgeryToken and AutoValidateAntiforgeryToken filters specified at a higher level (globally or on a controller). Tokens should be refreshed after the user is authenticated by redirecting the user to a view or Razor Pages page.
Using JavaScript with views, the token can be created using a service from within the view. Inject the IAntiforgery service into the view and call GetAndStoreTokens : The preceding example uses JavaScript to read the hidden field value for the AJAX POST header. Assuming the script sends the token in a request header called X-XSRF-TOKEN , configure the antiforgery service to look for the X-XSRF-TOKEN header: The following example uses JavaScript to make an AJAX request to obtain the token and make another request with the appropriate header: When the antiforgery token is provided in both the request header and in the form payload, only the token in the header is validated.
Call AddAntiforgery to register antiforgery services in DI, and UseAntiforgery to add the Antiforgery Middleware to the request processing pipeline. Antiforgery tokens are used to mitigate cross-site request forgery attacks . Antiforgery middleware doesn't short-circuit the request pipeline. Endpoint code always runs, even if token validation fails. To observe the outcome of the token validation, resolve the IAntiforgeryValidationFeature from HttpContext.Features and inspect its IsValid property or the Error property for failure details. This approach is useful when endpoints require custom handling for failed antiforgery validation.
Note: When enabled manually, the antiforgery middleware must run after the authentication and authorization middleware to prevent reading form data when the user is unauthenticated. By default, Minimal APIs that accept form data require antiforgery token validation and fail before running application code if antiforgery validation isn't successful.
The preceding code has three arguments, the action, the antiforgery token, and a bool indicating whether the token should be used. Calling .DisableAntiforgery() disables cross-site request forgery (CSRF) protection for the endpoint. This should only be used when an endpoint is not vulnerable to CSRF attacks, such as: For the middleware-based antiforgery path, AntiforgeryMiddleware and UseAntiforgery() validate antiforgery tokens only for HTTP POST , PUT , and PATCH requests. Other HTTP methods, such as DELETE , aren't validated automatically.
To validate antiforgery tokens for other HTTP methods, resolve IAntiforgery from DI and call ValidateRequestAsync or IsRequestValidAsync explicitly: When HttpMethodOverrideMiddleware is configured with FormFieldName (form-field mode) and placed before AntiforgeryMiddleware , a POST request can be overridden to DELETE (or another non-validated method). Because AntiforgeryMiddleware validates only POST, PUT, and PATCH, the overridden request bypasses antiforgery validation.
5. Performance Evaluation & Extended Technical Observations The IAntiforgeryAdditionalDataProvider type allows developers to extend the behavior of the anti-CSRF system by round-tripping additional data in each token. The GetAdditionalData method is called each time a field token is generated, and the return value is embedded within the generated token. An implementer could return a timestamp, a nonce, or any other value and then call ValidateAdditionalData to validate this data when the token is validated. The client's username is already embedded in the generated tokens, so there's no need to include this information. If a token includes supplemental data but no IAntiForgeryAdditionalDataProvider is configured, the supplemental data isn't validated.
Cross-site request forgery (also known as XSRF or CSRF) is an attack against web-hosted apps whereby a malicious web app can influence the interaction between a client browser and a web app that trusts that browser. These attacks are possible because web browsers send some types of authentication tokens automatically with every request to a website. This form of exploit is also known as a one-click attack or session riding because the attack takes advantage of the user's previously authenticated session.
The malicious site, www.bad-crook-site.example.com , contains an HTML form similar to the following example: Notice that the form's action posts to the vulnerable site, not to the malicious site. This is the "cross-site" part of CSRF. The request runs on the www.good-banking-site.example.com server with the user's authentication context and can perform any action that an authenticated user is allowed to perform.
In addition to the scenario where the user selects the button to submit the form, the malicious site could: These alternative scenarios don't require any action or input from the user other than initially visiting the malicious site. Using HTTPS doesn't prevent a CSRF attack. The malicious site can send https://www.good-banking-site.example.com/ a request just as easily as it can send an insecure request.
Some attacks target endpoints that respond to GET requests, in which case an image tag can be used to perform the action. This form of attack is common on forum sites that permit images but block JavaScript. Apps that change state on GET requests, where variables or resources are altered, are vulnerable to malicious attacks. GET requests that change state are insecure. A best practice is to never change state on a GET request.
In this context, session refers to the client-side session during which the user is authenticated. It's unrelated to server-side sessions or ASP.NET Core session middleware . However, CSRF vulnerabilities are fundamentally a problem with the web app, not the end user. When a user is authenticated, they're issued a token (not an antiforgery token). The token contains user information in the form of claims or a reference token that points the app to user state maintained in the app. When a user attempts to access a resource that requires authentication, the token is sent to the app with an extra authorization header in the form of a Bearer token. This approach makes the app stateless. In each subsequent request, the token is passed in the request for server-side validation. This token isn't encrypted ; it's encoded . On the server, the token is decoded to access its information. To send the token on subsequent requests, store the token in the browser's local storage. Placing a token in the browser local storage and retrieving it and using it as a bearer token provides protection against CSRF attacks. However, should the app be vulnerable to script injection via XSS or a compromised external javascript file, a cyberattacker could retrieve any value from local storage and send it to themselves. ASP.NET Core encodes all server side output from variables by default, reducing the risk of XSS. If you override this behavior by using Html.Raw or custom code with untrusted input then you may increase the risk of XSS.
Shared hosting environments are vulnerable to session hijacking, login CSRF, and other attacks. ASP.NET Core implements antiforgery using ASP.NET Core Data Protection . The data protection stack must be configured to work in a server farm. For more information, see Configuring data protection . Antiforgery services are registered in the dependency injection container when one of the following APIs is called in Program.cs : The FormTagHelper injects antiforgery tokens into HTML form elements. The following markup in a Razor file automatically generates antiforgery tokens: Similarly, IHtmlHelper.BeginForm generates antiforgery tokens by default if the form's method isn't GET.
The automatic generation of antiforgery tokens for HTML form elements happens when the
The most common approach to defending against CSRF attacks is to use the Synchronizer Token Pattern (STP). STP is used when the user requests a page with form data: The token is unique and unpredictable. The token can also be used to ensure proper sequencing of a series of requests (for example, ensuring the request sequence of: page 1 > page 2 > page 3). All of the forms in ASP.NET Core MVC and Razor Pages templates generate antiforgery tokens. The following pair of view examples generates antiforgery tokens: Explicitly add an antiforgery token to a
With the Synchronizer Token Pattern, only the most recently loaded page contains a valid antiforgery token. Using multiple tabs can be problematic. For example, if a user opens multiple tabs: The ValidateAntiForgeryToken action filter can be applied to an individual action, a controller, or globally. Requests made to actions that have this filter applied are blocked unless the request includes a valid antiforgery token: The ValidateAntiForgeryToken attribute requires a token for requests to the action methods it marks, including HTTP GET requests. If the ValidateAntiForgeryToken attribute is applied across the app's controllers, it can be overridden with the IgnoreAntiforgeryToken attribute.
Instead of broadly applying the ValidateAntiForgeryToken attribute and then overriding it with IgnoreAntiforgeryToken attributes, the AutoValidateAntiforgeryToken attribute can be used.
This attribute works identically to the ValidateAntiForgeryToken attribute, except that it doesn't require tokens for requests made using the following HTTP methods: We recommend use of AutoValidateAntiforgeryToken broadly for non-API scenarios. This attribute ensures POST actions are protected by default. The alternative is to ignore antiforgery tokens by default, unless ValidateAntiForgeryToken is applied to individual action methods. It's more likely in this scenario for a POST action method to be left unprotected by mistake, leaving the app vulnerable to CSRF attacks. All POSTs should send the antiforgery token.
The IgnoreAntiforgeryToken filter is used to eliminate the need for an antiforgery token for a given action (or controller). When applied, this filter overrides ValidateAntiForgeryToken and AutoValidateAntiforgeryToken filters specified at a higher level (globally or on a controller). Tokens should be refreshed after the user is authenticated by redirecting the user to a view or Razor Pages page.
Using JavaScript with views, the token can be created using a service from within the view. Inject the IAntiforgery service into the view and call GetAndStoreTokens : The preceding example uses JavaScript to read the hidden field value for the AJAX POST header. Assuming the script sends the token in a request header called X-XSRF-TOKEN , configure the antiforgery service to look for the X-XSRF-TOKEN header: The following example uses JavaScript to make an AJAX request to obtain the token and make another request with the appropriate header: When the antiforgery token is provided in both the request header and in the form payload, only the token in the header is validated.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Vulnerability%20%28computer%20security%29 • https://en.wikipedia.org/wiki/Exploit%20%28computer%20security%29 • https://en.wikipedia.org/wiki/Security%20hacker • https://community.owasp.org/attacks/csrf • https://learn.microsoft.com/en-us/aspnet/core/security/anti-request-forgery?view=aspnetcore-10.0
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Cross Site Request Forgery Vulnerability Scanner Project.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Cross Site Request Forgery Vulnerability Scanner Project... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |