Complete Technical Paper Content — Cyber Bullying Detection Using Natural Language Processing
Overview & System Context
Cyber Bullying Detection Using Natural Language Processing: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~254 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Cyber bullying detection and mitigation system using NLP and machine learning for safer social media.
2. System Architecture & Core Working Principles This 3rd year mini project was completed with my project partner. It focuses on detecting harmful or bullying content in social media text using Natural Language Processing and Machine Learning. The project also considers mitigation steps for flagged content to support safer online communication.
3. Software Implementation, Frameworks & Protocols This repository now includes a small rebuilt sample implementation based on the original project concept. The sample uses safe demo comments and is meant to show the project workflow without exposing private datasets or personal social media content.
4. Practical Deployment, Analysis & Case Studies Private datasets, model files, virtual environments, and generated outputs are intentionally excluded from GitHub. 5. Performance Evaluation & Extended Technical Observations This project helped me understand how NLP and ML can be used to identify harmful online behavior and support safer social media environments.
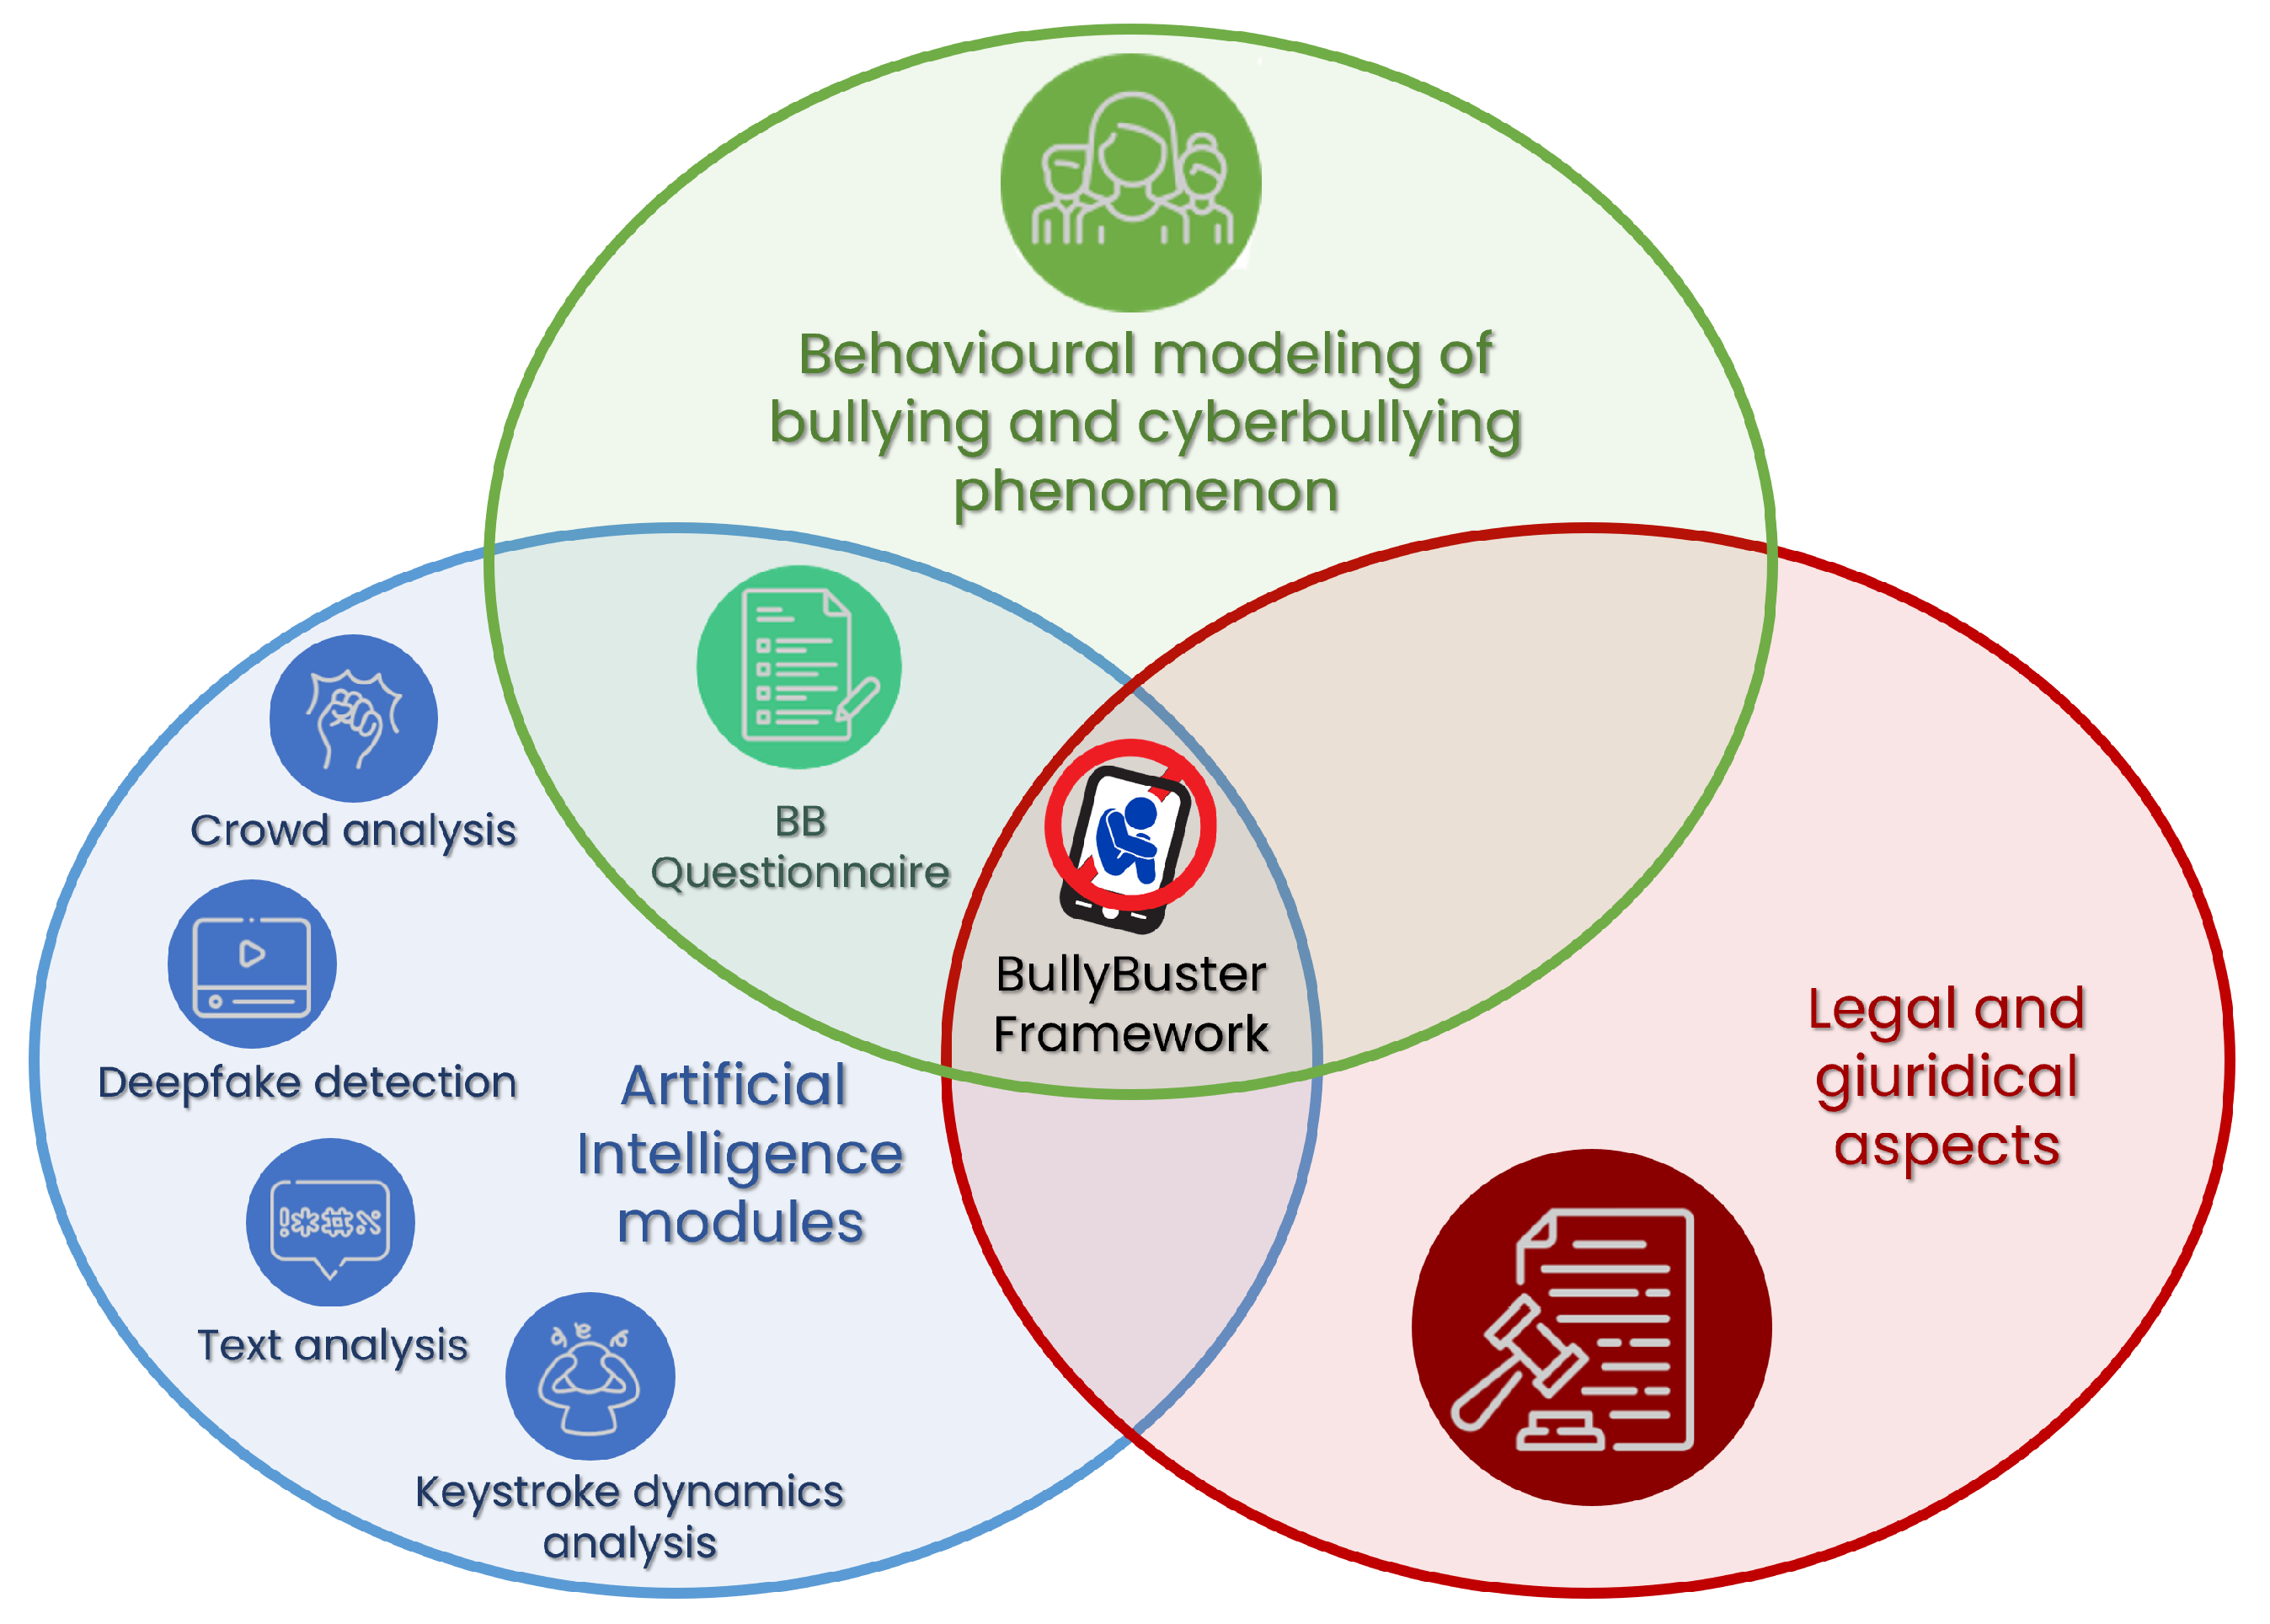
Figure 1: Development of Technologies for the Detection of (Cyber)Bullying ... Figure 2: Cyberbullying Detection Using Machine Learning and Deep Learning - PPTX ... Figure 3: GitHub - JaneAjodo/Cyber-Bullying-Detection-System-Using-NLP: This ... Harvested Online Documentation & Reference Sources • https://github.com/raksh097/cyber-bullying-detection-nlp-ml • https://github.com/vemalaharshitha/CyberBullying-Detection-Using-NLP
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Cyber Bullying Detection Using Natural Language Processing.
[*] Metasploit Scan Running on Target Subnet for Cyber Bullying Detection Using Natural Language Processing... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |