Complete Technical Paper Content — Cyber Threat Hunting Tool Using MITRE ATT&CK Framework
Overview & System Context
Cyber Threat Hunting Tool Using Mitre Attck Framework: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9604 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background In a controlled study by Horizon3 researchers, models that explicitly identified a trap in their reasoning still attacked it 73.4% of the time. Read the findings and see what they mean for canaries, decoys, and early detection.
MITRE ATT&CK is the most widely referenced framework in enterprise security, and also one of the most widely misused. Teams cite ATT&CK technique IDs in threat reports, require vendors to show ATT&CK heatmaps in procurement, and list ATT&CK alignment as a compliance checkbox, without ever systematically mapping their own detection coverage against it or using it to drive hunting hypotheses.
This guide covers how to actually use ATT&CK operationally: how to map your existing detections to the framework, identify the coverage gaps that matter most for your threat profile, build threat actor profiles relevant to your industry, and run structured threat hunts using ATT&CK as the hypothesis source. The first operational use of ATT&CK is understanding what you already detect and what you do not. This requires mapping every detection rule, alert, and analytic in your SIEM and EDR against specific ATT&CK techniques.
Figure 1: How Container Workloads Are Changing The Future of Cybersecurity Start with ATT&CK Navigator (attack.mitre.org/resources/attack-navigator/), the free browser-based tool for visualizing coverage. Create a layer representing your current detection coverage: color each technique green if you have at least one high-confidence detection for it, yellow if you have a low-confidence or easily bypassed detection, and leave uncovered techniques blank.
Be honest about detection quality. A rule that triggers on every PowerShell execution is not a detection for T1059.001 (PowerShell), it is an alert factory that trains analysts to ignore PowerShell alerts. A detection counts as coverage only if it fires specifically on malicious patterns with an acceptable false positive rate in your environment. The resulting heatmap will almost certainly reveal large gaps in specific tactic areas. Most organizations that do this exercise for the first time find strong coverage for Initial Access (phishing, exploit, etc.) and poor coverage for later-stage tactics: Defense Evasion, Credential Access, Lateral Movement, and Collection. These late-stage gaps are where attackers spend the most time before exfiltration and where early detection would have the most impact on breach cost.
Not all ATT&CK coverage gaps are equally important. A financial services organization faces different threat actors using different techniques than a healthcare provider or a defense contractor. Prioritization requires overlaying your coverage gaps with the techniques most commonly used by threat actors targeting your sector. Figure 2: Sprocket Security | Sprocket Introduces MITRE ATT&CK Heat Map in the ...
ATT&CK Groups (attack.mitre.org/groups/) documents the techniques associated with named threat actor groups. Identify the three to five groups most commonly reported targeting your industry, this information is available from sector-specific ISACs, vendor threat intelligence reports, and CISA alerts. Pull their technique lists into Navigator as a separate layer and overlay it with your coverage map. The intersection of 'techniques used by actors targeting your industry' and 'techniques you do not currently detect' is your highest-priority detection development backlog.
CISA's Known Exploited Vulnerabilities catalog and the techniques associated with major ransomware groups provide a useful baseline for organizations without sophisticated threat intelligence programs. The techniques most commonly used in financially motivated ransomware intrusions (phishing lure, credential dumping via LSASS, lateral movement via RDP and SMB, data staging before exfiltration) form a practical minimum coverage baseline for any organization regardless of industry.
ATT&CK provides a structured vocabulary for generating threat hunting hypotheses. Instead of hunting based on intuition or ad-hoc IOC lists, ATT&CK-aligned hunting starts with a specific technique and asks: do we have evidence of this technique being used in our environment in the past 30, 60, or 90 days? A well-formed ATT&CK hunting hypothesis follows this structure: 'Adversaries using [Technique ID] may be present in our environment, as evidenced by [specific observable data in our logs or telemetry].' For example: 'Adversaries using T1055 (Process Injection) may be present, as evidenced by non-standard parent-child process relationships where a browser process spawns a command shell.' Figure 3: Unlocking Cyber Threat Intelligence with MITRE ATT&CK™ Industry ...
Effective ATT&CK-aligned hunting requires rich telemetry. Map your data sources against ATT&CK's data source model (attack.mitre.org/datasources/) before hunting. If you are hunting for T1003 (OS Credential Dumping) but you do not have Sysmon event ID 10 (process access to LSASS) in your SIEM, the hunt will find nothing regardless of whether credential dumping is occurring. Data source coverage assessment is a prerequisite to reliable hunting.
For teams building a hunting program, the ATT&CK Evaluations results (attackevals.mitre-engenuity.org) provide a useful technique prioritization guide: the techniques that appear most frequently in evaluation scenarios represent the techniques that detection vendors consider most important to cover, which correlates with real-world adversary prevalence. ATT&CK threat actor profiles let you answer the specific question: if [Actor Group] targeted our organization today, using their documented TTPs, which of their actions would we detect and which would we miss? Start with the ATT&CK Groups page and identify the actor groups most relevant to your sector. For each group, export their technique list and overlay it against your coverage map in Navigator. The result tells you exactly which phases of their kill chain you would see and which you would miss.
Update these profiles quarterly. ATT&CK is continuously updated with newly documented techniques and group attributions. A technique that was not associated with a given group six months ago may have been added based on recent incident reports. Treat your threat actor profiles as living documents that require the same maintenance cadence as your vulnerability management program.
For organizations with access to commercial threat intelligence , the ATT&CK mapping in platforms like Recorded Future, Mandiant Advantage, and ThreatConnect allows you to pull real-time technique-to-group associations rather than relying only on the public ATT&CK database. The public database lags real-world attribution by weeks to months; commercial platforms narrow that gap significantly.
You cannot make informed coverage decisions without knowing what you already detect. ATT&CK Navigator makes this visual and fast. Generic coverage improvement is less valuable than coverage of the specific techniques used by actors targeting your sector. ATT&CK hunting against missing telemetry produces false negatives, not true negatives. Know what you can and cannot see.
The techniques featured in MITRE evaluations represent those most important to cover based on real adversary prevalence. ATT&CK group attributions are updated continuously. Stale profiles miss newly documented techniques. ATT&CK is most valuable as an operational tool when used to answer three questions on a continuous cycle: what do we currently detect, what are we missing that matters most for our threat profile, and what evidence of adversary activity exists in our environment right now? Teams that use the framework only for vendor evaluation and compliance reporting are leaving its most valuable capability unused.
Techniques describe the general method an adversary uses (e.g., T1059 Command and Scripting Interpreter). Sub-techniques describe specific implementations of that method (e.g., T1059.001 PowerShell, T1059.003 Windows Command Shell). Detection rules can target techniques broadly or sub-techniques specifically. Sub-technique targeting is generally more precise but requires more specific telemetry. Most mature detection programs implement rules at the sub-technique level for high-priority coverage areas.
ATT&CK Navigator is a free browser-based tool at mitre-attack.github.io/attack-navigator/. You can run it locally by cloning the GitHub repository or use the hosted version at that URL. Create a new layer, select the Enterprise matrix, and begin coloring techniques to represent your coverage state. The tool supports importing and exporting layers as JSON, which allows team members to collaborate on coverage maps and version-control them alongside detection rule repositories.
Coverage of 100% of ATT&CK techniques is not achievable or a useful goal. A realistic target for a mature enterprise security program with good endpoint, identity, and network telemetry is 60 to 70% technique coverage in the Initial Access, Execution, Persistence, Privilege Escalation, Defense Evasion, Credential Access, and Lateral Movement tactics. Focus coverage depth (high-confidence, low-FP detections) over breadth (rules that technically cover a technique but fire on everything).
Lockheed Martin's Cyber Kill Chain describes a linear attack progression from reconnaissance through actions on objectives in seven stages. ATT&CK is a non-linear, comprehensive taxonomy of adversary techniques organized by tactic, with documented associations to specific threat actor groups and malware families. ATT&CK is significantly more granular and operationally useful for detection development and hunting. The Kill Chain is more useful as a communication framework for explaining attack phases to non-technical leadership.
Yes. ATT&CK maintains separate matrices for Cloud (AWS, Azure, GCP, Office 365, Google Workspace), ICS (industrial control systems), and Mobile in addition to Enterprise (Windows, macOS, Linux). The Cloud matrix covers techniques specific to cloud-native attacks: account manipulation, storage object discovery, cloud service exploitation, and serverless function abuse. Organizations with significant cloud infrastructure should maintain coverage maps across both the Enterprise and Cloud matrices.
25 actively exploited vulnerabilities with CVSS scores, exploit status, and patch availability. Print it, pin it, share it with your SOC team. Step-by-step 24-hour IR checklist covering detection, containment, eradication, and recovery. Built for SOC teams, IR leads, and CISOs.
50,000+ security professionals read Decryption Digest for early warnings on zero-days, ransomware, and nation-state campaigns. Free, daily, no spam. Cybersecurity professional with expertise in threat intelligence, vulnerability research, and enterprise security. Covers zero-days, ransomware, and nation-state operations for 50,000+ security professionals every morning.
2. System Architecture & Core Working Principles Actionable threat intelligence for working practitioners. Free. No spam. Trusted by 50,000+ SOC analysts, CISOs, and security engineers. Elevate your security team's focus from indicators to adversary behavior. This guide introduces the MITRE ATT&CK Framework as the essential knowledge base for proactive threat hunting. Learn the structured methodology to map real-world threat intelligence directly to specific TTPs (Tactics, Techniques, and Procedures) , turning narratives into actionable detection strategies. Now you can Emphasize the Shift from Artifacts to Behavior.
Threat hunting is the proactive, iterative search for unknown threats hidden within a computer network. The MITRE ATT&CK Framework provides the essential common language and structured knowledge base needed to perform this task effectively. The central concept of this approach is moving from simple Indicators of Compromise (IoCs) —which are static and quickly change—to Adversary Behavior s defined by Tactics, Techniques, and Procedures (TTPs) . This shift allows defenders to hunt for how an attacker operates, not just what artifact they used.
As we mentioned in the context of cyber threat intelligence, Tactics, Techniques, and Procedures (TTPs) describe adversary behavior as follows: Here is a diagram-style example that illustrates the relationship, using a real-world procedure often associated with groups like APT29 (Cozy Bear).
Let’s now focus on how we can use Threat hunting in Google TI using MITRE ATT&CK Enterprise . You can leverage some Advanced Search Modifiers to find files exhibiting specific behavioral characteristics. This filters for the tactic Persistence . The attacker is trying to maintain their foothold in the system across restarts, changed credentials, or other interruptions (e.g., creating a scheduled task or a registry run key).
This filters for the technique Process Injection . The adversary is injecting code into the address space of a running process to migrate into another process, hide their presence, or evade process-based defenses. behaviour: More generic than the other ones. It returns all those files whose dynamic behavioral report contains the literal provided.
behaviour_processes: Related to any process fields such as processes_killed, processes_terminated, command_executions, injected_processes, etc. crowdsourced_ids: Filters the files that match a crowdsourced IDS rule during sandbox execution. Example: crowdsourced_ids:”crowdsourced_ids:"ET INFO DNS Query to Alibaba Cloud CDN Domain"” For next uses cases presenting some different TTPs we will use the search bar in the top menu: Our goal will be to proactively find malware samples that try to maintain Persistence on a system by creating a new scheduled task. This is a common TTP for sophisticated actors like APT29 (Cozy Bear) and FIN7.
The attackers can implement this technique using, for example, this specific command in the terminal: Our next goal is to find malware that uses PowerShell scripts to download and execute code directly from a URL in memory (a "Download Cradle"). This technique achieves Execution without dropping a file to disk, making it a favorite of groups like APT41 and Lazarus.
The attackers can implement this technique using, for example, this specific command in the terminal: Download cradles leverage various cmdlets such as: – Invoke-WebRequest –Invoke-Expression and – System.Net.WebClient that you can use as a pattern for your advanced search query. In the previous example the Net.WebClient object retrieves the content of http://example.com/script.ps1, and Invoke-Expression executes it in-memory.
behaviour_processes:" powershell.exe " behaviour_command_executions: "IEX (New-Object Net.WebClient).DownloadString " (Google TI link ) This behavior maps to MITRE T1490 ( Inhibit System Recovery) and is frequently used by actors like Conti, Ryuk, and REvil. The attackers can implement this technique using, for example, this specific command in the terminal: behaviour_processes:" vssadmin.exe " behaviour_command_executions:" vssadmin.exe delete shadows /all /quiet " (Google TI link ) sigma_rule:" Shadow Copies Deletion Using Operating Systems Utilities " (Google TI link ) This behavior maps to MITRE T1567.002 (Exfiltration to a web service) and is frequently used by actors like Kimsuky and FIN7 .
In this case attackers can use curl, wget, or even custom scripts to POST data to pastebin-like services. For example: In this case our Google TI query to hunt this behaviour should be similar to this one: Our mission here is to find malware samples that install a specific Windows service. For example, in some cases install and use legitimate remote access software like AnyDesk.
This behavior maps to MITRE T1543.003 (Create or Modify System Process: Windows Service) and is used by BlackByte . behaviour_services:" anydesk " behaviour_created_processes:" sc.exe " and NOT tag: signed (Google TI link ) Our mission here is to find malware samples that use the unauthorized export (dumping) of critical Windows Registry Hives (SAM, SYSTEM, SECURITY) which contain local credentials and security secrets.
This behavior maps to MITRE T1003.002 (Security Account Manager) or T1003.004 (LSA Secrets). 3. Software Implementation, Frameworks & Protocols (behaviour_registry:" \sam " or behaviour_registry:" \system " or behaviour_registry:" \security ") behaviour_processes:" reg export " (Google TI link ) Shifting to a MITRE ATT&CK -centric approach allows security teams to conduct more strategic and enduring threat hunts, creating detections that are resilient against trivial changes in malware composition.
We learned through practical use cases how to leverage Advanced Search Modifiers within Google Threat Intelligence to translate TTPs into specific, powerful search queries. This allows for the proactive discovery of malware samples exhibiting these behaviors. Enter your E-mail address. We'll send you an e-mail with instructions to reset your password.
MITRE ATT&CK ® is a globally-accessible knowledge base of adversary tactics and techniques based on real-world observations. The ATT&CK knowledge base is used as a foundation for the development of specific threat models and methodologies in the private sector, in government, and in the cybersecurity product and service community. With the creation of ATT&CK, MITRE is fulfilling its mission to solve problems for a safer world — by bringing communities together to develop more effective cybersecurity. ATT&CK is open and available to any person or organization for use at no charge.
MITRE ATT&CK (Adversarial Tactics, Techniques, and Common Knowledge) is a comprehensive matrix of tactics and techniques threat actors use in cyber attacks. Implementing MITRE ATT&CK techniques involves understanding and utilizing the framework for various cybersecurity purposes, such as threat modeling , security assessment, and defense strategies. Using MITRE ATT&CK techniques effectively requires a strategic approach tailored to your organization's needs and security posture. Using MITRE ATT&CK techniques is not just about defending against attacks; it's also about understanding the evolving landscape of cyber threats and continuously adapting your security posture. It's important to remember that these techniques should be part of an overall cybersecurity strategy and not the sole focus.
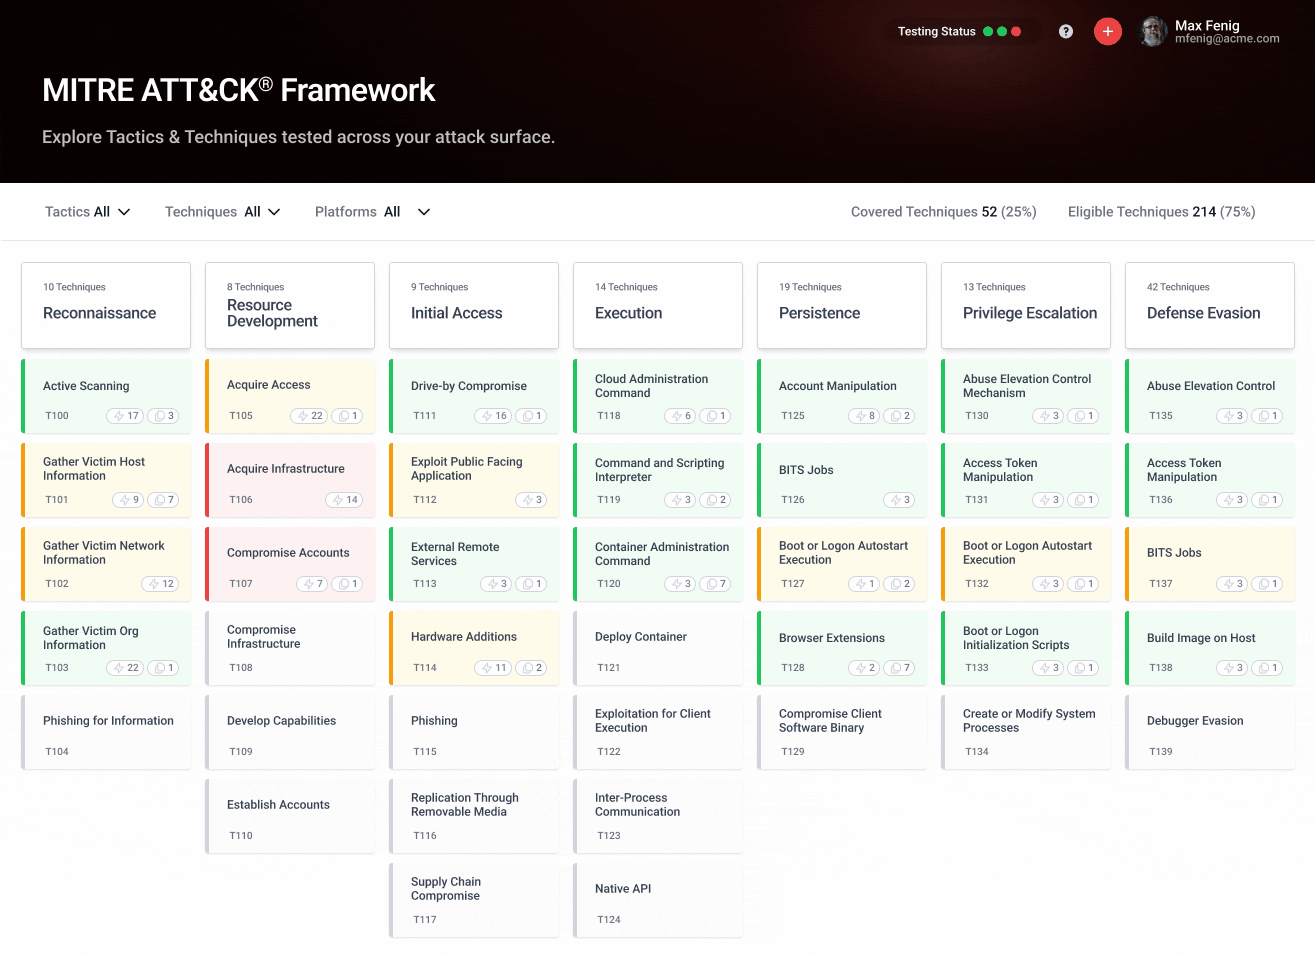
The MITRE ATT&CK framework is a comprehensive matrix of tactics and techniques representing a cyber attack's various phases and methods. The framework is constantly updated to reflect the evolving nature of cyber threats. The ATT&CK framework is used for various purposes, such as threat intelligence, security assessment, training, and improving cybersecurity defenses. It's a living document continually updated by MITRE Corporation, based on real-world observations of cyber attacks.
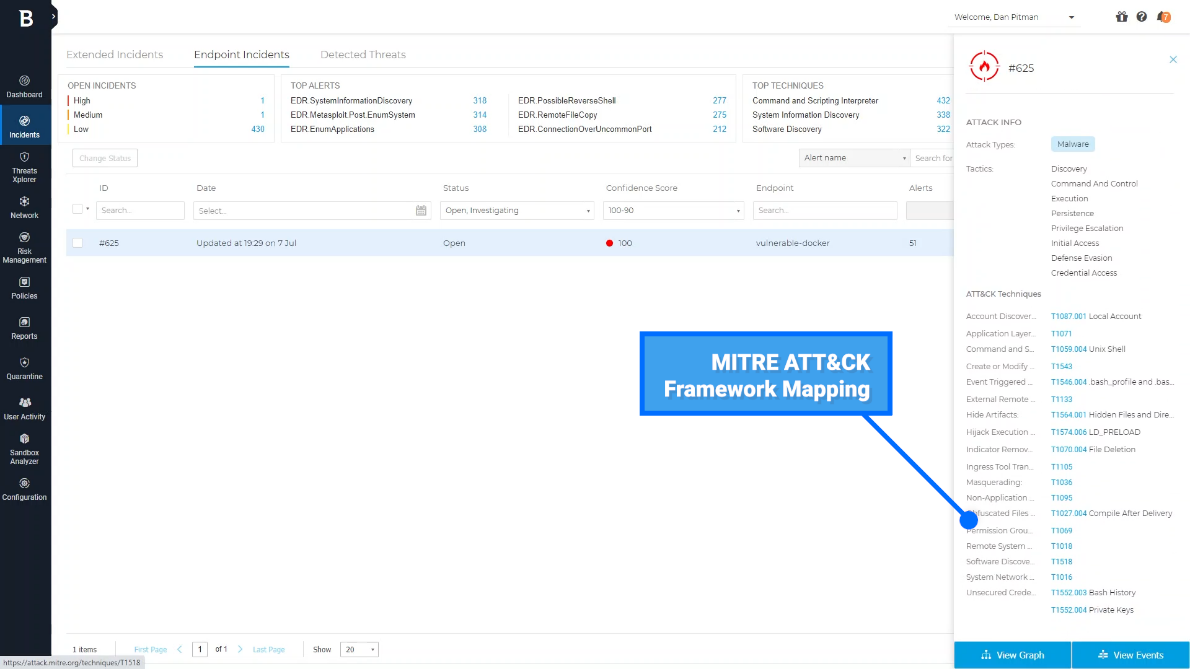
The MITRE ATT&CK framework: Turla. Explore in ATT&CK Navigator . Note: The items in blue are the techniques in the MITRE ATT&CK Enterprise framework that were emulated. In the dynamic and ever-evolving landscape of cybersecurity, the implementation of MITRE ATT&CK techniques stands as a pivotal strategy for enhancing organizational defense mechanisms against cyber threats. This comprehensive approach, which pivots around the MITRE ATT&CK framework, is a crucial roadmap for organizations seeking to bolster their cybersecurity posture.
By meticulously understanding, identifying, and adapting these techniques, organizations can fortify their defenses against potential cyber attacks and develop a more proactive and informed stance in their security strategy. Familiarize yourself with the MITRE ATT&CK matrix, which categorizes various tactics (what an attacker is trying to achieve) and techniques (how they achieve it). The framework is available on the MITRE ATT&CK website .
Identify the most relevant tactics and techniques based on your organization's environment and threat landscape. This might involve understanding the common threats in your industry or the specific vulnerabilities of your systems. Use the framework to model potential threats against your organization. This involves thinking like an attacker and identifying which tactics and techniques they might use to compromise your systems.
Assess your current security posture against the techniques identified in the MITRE ATT&CK framework. This will help you identify gaps in your defenses. Based on the gap analysis, improve your security measures. This could involve implementing new security controls, enhancing existing ones, or changing processes and policies.
Educate your security team and relevant staff about the MITRE ATT&CK techniques and how to recognize and respond to them. This training should be part of an ongoing security awareness program. Incorporate knowledge of these techniques into your incident response planning. Ensure that your response plans include steps to detect, investigate, and mitigate attackers' tactics and techniques.
Regularly monitor your security systems for signs of these techniques. Use threat intelligence to stay updated on emerging tactics and techniques and continuously improve your defenses. Engage with the cybersecurity community to share insights and learn from the experiences of others using the MITRE ATT&CK framework.
Utilize security tools and technologies to detect and mitigate the techniques listed in the MITRE ATT&CK framework. Many modern security solutions are designed with this framework in mind. Using MITRE ATT&CK techniques effectively requires a strategic approach tailored to your organization's needs and security posture. Here's a step-by-step guide on how to use these techniques: Using MITRE ATT&CK techniques is not just about defending against attacks; it's also about understanding the evolving landscape of cyber threats and continuously adapting your security posture. It's important to remember that these techniques should be part of an overall cybersecurity strategy and not the sole focus.
Cyber attackers frequently use the following MITRE ATT&CK techniques. However, it's important to note that the relevance of these techniques can change rapidly as attackers adapt their strategies and organizations improve their defenses. It is critical to stay informed about the latest trends and developments in cyber threats and MITRE ATT&CK techniques. MITRE ATT&CK Techniques can indeed assist in predicting future cyber attacks to some extent. While they may not predict the specifics of individual attacks, they provide a framework for understanding adversary behaviors and methodologies. This knowledge can help organizations anticipate potential attack vectors and prepare defenses accordingly.
While ATT&CK is a powerful tool, it’s important to note that the cyber threat landscape is constantly evolving. Therefore, continuous monitoring, updating security practices, and integrating new intelligence are crucial for staying ahead of potential threats. How Should Organizations Implement MITRE ATT&CK Techniques in Their Security Strategy? Organizations should implement MITRE ATT&CK Techniques in their security strategy by following a structured approach that aligns with their business objectives and security needs.
By systematically implementing MITRE ATT&CK Techniques, organizations can enhance their ability to detect, prevent, and respond to cyber threats more effectively. The MITRE ATT&CK framework is a widely adopted tool for enhancing cybersecurity, supporting threat intelligence, incident response, attack modeling, and vulnerability prioritization. This paper synthesizes research on its application across these domains by analyzing 417 peer-reviewed publications. We identify commonly used adversarial tactics, techniques, and procedures (TTPs) and explore the integration of natural language processing (NLP) and machine learning (ML) with ATT&CK to improve threat detection and response. Additionally, we examine ATT&CK’s integration with other frameworks, such as the Cyber Kill Chain, NIST guidelines, and STRIDE, highlighting its versatility. The paper also evaluates ATT&CK’s effectiveness, validation methods, and challenges in sectors like industrial control systems (ICS) and healthcare. We conclude by discussing current limitations and proposing future research directions to enhance ATT&CK’s application in dynamic cybersecurity environments.
MITRE ATT&CK (or Adversarial Tactics, Techniques, and Common Knowledge) is a curated knowledge base that details cyber adversary behavior across various domains, including enterprise, mobile, and industrial control systems (ICS) ( Strom et al., 2018 ; Son et al., 2023 ) . Organized into matrices, ATT&CK outlines specific adversarial tactics (high-level objectives) and techniques (specific actions) that describe how an attacker seeks to compromise or persist in a system.
4. Practical Deployment, Analysis & Case Studies MITRE ATT&CK has become a foundational tool in cybersecurity practices. By enabling the mapping of adversarial tactics, techniques, and procedures (TTPs), ATT&CK enhances the systematic detection and analysis of cyber threats, particularly advanced persistent threats (APTs) ( Golushko and Zhukov, 2022 ) . The framework has been widely applied across industries like healthcare, finance, and critical infrastructure, where its TTPs significantly contribute to enhanced threat detection and mitigation through tools such as AI, ML, and endpoint detection and response (EDR) systems ( Roy et al., 2023 ; Oosthoek and Doerr, 2019 ; Al-Sada et al., 2024 ) .
However, despite its widespread use, there remains a need to explore ATT&CK’s integration within broader cybersecurity methodologies and to address the technical challenges associated with its application. This paper aims to systematically review the academic literature on MITRE ATT&CK, consolidating insights into its applications, technical integration, and the limitations researchers have encountered. The review will also identify opportunities for future research, proposing directions for refining and extending the framework to address existing gaps.
Why is it important to adopt the MITRE ATT&CK framework, what are its primary uses, and how effective is its application across different cybersecurity domains? What are the technical methods, tools, and data sources used in studies applying the MITRE ATT&CK framework, and how are the results validated? What are the common challenges, limitations, and future directions identified in the literature regarding the use of MITRE ATT&CK? This paper analyzes the application of the MITRE ATT&CK framework across cybersecurity domains, such as threat intelligence, incident response, attack modeling, and vulnerability prioritization. Based on a review of 417 articles, we identify frequently employed TTPs and their use in industries like enterprise systems, manufacturing, and healthcare. We also highlight the integration of natural language processing (NLP) and machine learning (ML) with ATT&CK, improving adversarial behavior detection and threat response. We examine ATT&CK’s integration with other frameworks, such as the Cyber Kill Chain, NIST guidelines, STRIDE, and CIS Controls, emphasizing its adaptability in fostering a comprehensive cybersecurity approach. Additionally, we evaluate various validation methods, including case studies and empirical experiments, to assess ATT&CK’s effectiveness. This paper provides insights for researchers and practitioners seeking to enhance cybersecurity strategies while addressing ATT&CK’s challenges and limitations.
This paper is structured to guide readers from foundational concepts to actionable insights, identifying research gaps and future directions. Section 2 introduces key concepts, while Section 3 outlines the systematic review process. Core findings are detailed in Sections 4 – 8 , covering research focuses, data sources, tools, ATT&CK integrations, and validation methods. Section 9 synthesizes these findings, highlighting challenges and gaps, and Section 10 summarizes insights and future directions. A conceptual diagram is included to visually illustrate the organization and relationships between sections, enhancing clarity and navigation.
This section provides an overview of foundational concepts, establishing key background and terminology for the study. Developed in 2013 as part of MITRE’s Fort Meade Experiment (FMX), MITRE ATT&CK ( Strom et al., 2018 ) is a research initiative aimed at enhancing forensic analysis of cyberattacks by emulating adversarial and defensive tactics. The framework serves as a comprehensive knowledge base of real-world adversarial techniques, focusing on how attackers interact with systems rather than the tools or malware they use. It is structured around four core components: tactics (adversarial goals), techniques (methods to achieve goals), sub-techniques (detailed methods breaking down techniques), and documented usage (procedures and metadata).
MITRE ATT&CK is organized into three technology domains representing the environments where adversaries operate: Enterprise (traditional networks and cloud technologies), Mobile (mobile devices), and ICS (Industrial Control Systems). Each domain features distinct tactics and techniques, with techniques further detailed into sub-techniques, describing specific adversarial behaviors. Complementing ATT&CK, the MITRE FiGHT framework addresses supply chain threats, mapping 5G-relevant techniques to attack tactics.
Al-Sada Bader et al. ( Al-Sada et al., 2024 ) categorize 50 research contributions based on various use cases, including behavioral analytics, red teaming, defensive gap assessment, and CTI enrichment. This categorization highlights different applications, methodologies, and data sources in the implementation of ATT&CK, with a focus on adversarial behavior modeling, automated threat detection, and framework enhancements. The categorization draws from a white paper ( Strom et al., 2018 ) discussing the design philosophy, structure, and use cases of MITRE ATT&CK, and a similar white paper ( Alexander et al., 2020 ) on the development and application of the ATT&CK for ICS framework.
Roy Shanto et al. ( Roy et al., 2023 ) provide a taxonomic classification of ATT&CK-related research, identifying use cases, application domains, and methodologies. Key areas include CTI, intrusion detection, offensive security, cyber risk assessment, professional training, and threat-driven approaches. This study also identifies a gap between academic and industry use of ATT&CK, with industry focusing on practical implementations and tools, while academia explores theoretical models.
Several studies focus on specific applications of ATT&CK. Kris Oosthoek and Christian Doerr ( Oosthoek and Doerr, 2019 ) analyze 951 Windows malware families from the Malpedia repository, mapping post-compromise malware techniques to ATT&CK and examining techniques observed in a controlled sandbox environment. Joshua Bolton et al. ( Bolton et al., 2023 ) explore the use of knowledge graphs (KG) in cybersecurity, particularly in conjunction with MITRE ATT&CK.
Given the rapid evolution of cyber threats and the increasing complexity of defensive strategies, understanding the MITRE ATT&CK framework’s role across cybersecurity domains is crucial. Despite its widespread adoption, there is limited systematic analysis of ATT&CK’s application across sectors, methodologies, and advanced technologies. To address this, we conduct a comprehensive literature review analyzing ATT&CK’s application in threat intelligence, incident response, attack modeling, and vulnerability prioritization.
This section presents the methodology of our systematization in a step-by-step manner, and clearly defines the criteria for literature selection, databases, and search keywords used, as well as inclusion and exclusion criteria. A comprehensive literature search was conducted on May 31, 2024 in three digital libraries, namely IEEE Xplore, Scopus, and the ACM Digital Library. The initial search yielded 738 results from IEEE Xplore, which, after filtering out non-research content such as books and magazines, was reduced to 563. Similarly, the search in the ACM Digital Library resulted in 23 entries after removing non-research materials. Scopus produced 922 initial results, which were reduced to 847 after excluding non-research content. After removing duplicates across these databases, a total of 1,168 unique papers remained in the pool for further evaluation.
We assessed the relevance of papers through a multi-phase screening process. In the initial phase, we reviewed titles, abstracts, and keywords for alignment with key MITRE ATT&CK concepts, including threat modeling, intrusion detection, incident management, threat intelligence, attack modeling, and vulnerability analysis. If the abstract alone did not provide sufficient information, the full text was reviewed. Papers were included if they applied, extended, or compared MITRE ATT&CK with other frameworks, methodologies, or tools. Any ambiguity regarding inclusion was resolved through discussion among the research team. Exclusion criteria include: MITRE ATT&CK Elaboration: Papers that only mentioned MITRE ATT&CK without detailed elaboration.
The screening process occurred in two rounds. In the first, papers were filtered based on abstracts and keywords. A total of 419 papers were excluded. This phase was conducted by two cybersecurity experts, with two additional researchers independently verifying the final selection. After filtering, 396 papers remained for in-depth review. To ensure comprehensive coverage, both backward and forward snowballing techniques were applied. In forward snowballing, we tracked citations of selected papers using Google Scholar, ensuring the inclusion of recent studies. In backward snowballing, we reviewed references and citations within those references until no additional relevant papers were found. Each paper identified through snowballing was re-evaluated against the inclusion and exclusion criteria. This process led to the addition of 21 papers, bringing the total to 417 papers 1 1 1 https://github.com/LeThiHongMinh/MITRE-review-papers included in the review.
We employed a structured data extraction process to systematically gather relevant information from the selected studies. Using a predefined template, we extracted bibliographic details such as authors, title, publication year, source, document type, abstract, and keywords. This ensured consistency and facilitated subsequent analysis. In addition, we manually categorized each paper based on its methodologies, theoretical frameworks, evaluation techniques, and real-world applications. Key features extracted included: The domain or specific focus (e.g., threat intelligence) for categorizing application areas.
The methodologies used in each study (e.g., empirical experiments, case studies, simulations, surveys) was detailed, providing insight into how MITRE ATT&CK was operationalized. ATT&CK tactics, techniques, and integration with other frameworks (e.g., Cyber Kill Chain). The tools, techniques, data sources, and approaches used in each paper were cataloged.
The main insights and the effectiveness of MITRE ATT&CK in cybersecurity applications. Evaluation approaches used (e.g., experimental validation, real-world case validation). This extraction was carried out collaboratively by two researchers and validated by two additional researchers to minimize misinterpretation or coding bias.
Our analysis strategy synthesized the extracted data to identify broader themes and trends across the literature. We first summarized key features of each study into thematic categories (e.g., research focus areas, methodologies, technical tools, and evaluation methods). These summaries were reviewed to uncover recurring patterns and relationships. We also mapped the relationships among predominant methodologies, design features, and frameworks used in the literature.
This process facilitated the exploration of potential synthesis and cross-pollination of ideas across studies, providing a comprehensive overview of how MITRE ATT&CK has been applied, extended, or integrated with other frameworks in the field. This section synthesizes key focus areas and industry-specific applications in MITRE ATT&CK research. The MITRE ATT&CK framework is widely applied across cybersecurity research domains, with ten key research areas identified in the reviewed papers, as summarized in Table 1 . These ten key areas were built on top of and extended from the research areas identified in ( Roy et al., 2023 ; Alexander et al., 2020 ) . Each paper is categorized into one to three primary areas, with uncategorized papers grouped under Others . CTI and Threat Hunting dominate ATT&CK-related research, accounting for 30.2% (126 out of 417) and 17.5% (73 out of 417) of the papers, respectively.
Research leveraging the MITRE ATT&CK framework focuses on extracting CTI information from raw data through the application of NLP and ML techniques. Studies such as ( Li et al., 2024 ; Huang et al., 2024 ; Kim and Kim, 2022 ; Liu et al., 2022 ; Rani et al., 2023 ) have proposed frameworks for extracting TTPs from unstructured reports using LLMs and transformer-based architectures like BERT ( Li et al., 2024 ; Huang et al., 2024 ; Rani et al., 2023 ) . Quantitative evaluations across large, TTP-labeled datasets indicate comprehensive coverage of MITRE ATT&CK tactics and techniques in ( Huang et al., 2024 ; Kim and Kim, 2022 ; Liu et al., 2022 ) , whereas ( Li et al., 2024 ; Rani et al., 2023 ) focus on subsets of techniques. For instance, ( Li et al., 2024 ) employs DistilBERT-based multi-label classifiers to categorize tactics and techniques, incorporating pre-processing for CTI text denoising and post-processing for correction. Similarly, ( Huang et al., 2024 ) integrates ontology knowledge with sentence-level BERT models, combining classification outcomes using a voting algorithm to address the lack of labeled datasets. TTPHunter by ( Rani et al., 2023 ) refines BERT embeddings for extracting TTPs from APT reports. In addition to LLMs, innovative approaches such as ( Liu et al., 2022 ) introduce an Attention-based Transformer Hierarchical Recurrent Neural Network, while ( Kim and Kim, 2022 ) enhances small, imbalanced datasets with data augmentation techniques for ML classifiers.
5. Performance Evaluation & Extended Technical Observations Broader CTI applications expand beyond TTPs to include malware profiles, attack tools, and other features ( Tang et al., 2023 ; Irshad and Siddiqui, 2023 ; Alam et al., 2023 ) . For example, ( Irshad and Siddiqui, 2023 ) proposed Attack2Vec , a domain-specific text embedding model extracting CTA features from CTI reports for classification. ( Tang et al., 2023 ) integrates ATT&CK-based networks with BERT for semantic analysis, categorizing malware and other CTAs. Similarly, LADDER by ( Alam et al., 2023 ) extracts entities and relationships for TTP classification and threat intelligence knowledge graph construction, aiding campaign inference from new CTI sources. This work also introduces an open-source benchmark dataset for malware-related CTI studies.
MITRE ATT&CK framework serves as a foundational tool for threat hunting, particularly in network traffic analysis, system log analysis, and attack graph modeling. Several studies utilize ATT&CK for analyzing network traffic to classify malicious activities ( Sharma et al., 2023a ; Bagui et al., 2023b ; Kang et al., 2022 ) . RADAR ( Sharma et al., 2023a ) classifies network logs using an ontology of adversary behavior, combining explainable classifiers with detection rules for TTP classification. However, RADAR covers only 13 techniques across six tactics. Similarly, ActDetector ( Kang et al., 2022 ) processes NIDS alerts to detect attack phases aligned with 14 ATT&CK tactics. Using Doc2Vec embeddings and temporal sequence classifiers, it identifies multi-stage attack activities. Graph-based approaches, such as ( Bagui et al., 2023b ) , leverage Neo4j for representing network traffic patterns, focusing on the reconnaissance tactic.
System logs are extensively used to map ATT&CK techniques for threat detection ( Rodríguez et al., 2023 ; Takey et al., 2022 ; Kuwano et al., 2022 ; Okada et al., 2024 ) . ( Rodríguez et al., 2023 ) employs process mining to detect adversarial patterns by profiling system event logs into TTPs and mining process models. Similarly, ( Takey et al., 2022 ) integrates IoC-based ATT&CK mapping with ML models to detect multi-stage attacks in real time. In lateral movement detection, ( Okada et al., 2024 ) extracts ATT&CK techniques from Windows logs and identifies movement paths through quantitative analysis. A recommendation system proposed in ( Kuwano et al., 2022 ) predicts attacker behaviors using KNN-based collaborative filtering, correlating logs with ATT&CK TTPs.
Attack graphs provide a comprehensive view of multi-step attack scenarios by integrating ATT&CK tactics. One paper ( Sadlek et al., 2022 ) has combined MITRE ATT&CK framework and attack graph for attack path identification in multi-step cyber threat scenarios. Similar to ( Kang et al., 2022 ) , ATT&CK tactics are utilized as kill chain stages. The attack graph, constructed based on threat and security property violation categories, contains asset property, attack technique, goal and countermeasure information for effective security investigation.
MITRE ATT&CK framework has been extensively applied across diverse sectors for cyber threat modeling, including enterprise IT ( Xiong et al., 2022 ) , ICS ( Hotellier et al., 2024 ; Fujita et al., 2023 ; Zhang et al., 2022 ) , mobile networks ( van Do et al., 2023 ; Rao et al., 2023 ) , and 5G networks ( Vanderveen, 2022 ; Santos et al., 2022 ; Pell et al., 2021 ) . A threat modeling language tailored for enterprise IT is proposed in ( Xiong et al., 2022 ) , integrating the MITRE ATT&CK Enterprise Matrix with meta-language framework (MAL). The language defines a entity-relationship model, covering assets and their associations, attack steps represented by ATT&CK techniques, and defenses.
In ICS, ATT&CK-based methodologies focus on enhancing system security ( Hotellier et al., 2024 ) ( Fujita et al., 2023 ) ( Zhang et al., 2022 ) . A specification-based IDS correlating safety standards with attack properties is proposed in ( Hotellier et al., 2024 ) , whereby MITRE ATT&CK is integrated in process-aware attack modeling as the basis attack framework. ( Fujita et al., 2023 ) proposed a structured model to represent cyber attack scenarios in ICS based on the diamond model. Attack state is defined in the attacker behavioral model part, including attack phrase, capability, location and other properties.
Additionally, ( Zhang et al., 2022 ) introduces an ICS-specific security ontology grounded in the Purdue model for effective asset-based threat reasoning. Threat modeling research has extensively applied the MITRE ATT&CK framework to both mobile ( van Do et al., 2023 ; Rao et al., 2023 ) and 5G ( Vanderveen, 2022 ; Santos et al., 2022 ; Pell et al., 2021 ) networks, addressing shared and unique challenges within these domains. Mobile network threat modeling focuses on categorizing known attacks against cellular communications and extending ATT&CK’s Mobile Matrix. For example, ( van Do et al., 2023 ) extends ATT&CK’s mobile matrix into more threat behaviors in 5G by integrating it with the CONCORDIA Mobile Threat Modelling Framework (CMTMF), addressing gaps in ATT&CK’s mobile threat coverage. The techniques in mobile matrix is mapped to techniques in the enterprise matrix to form a extended ATT&CK mobile network matrix, and subsequently integrated into other mobile frameworks. Similarly, ( Rao et al., 2023 ) categorizes cellular attack TTPs using ATT&CK tactics and maps them to the Bhadra framework for structured analysis. In the context of 5G networks, ( Vanderveen, 2022 ) introduces FiGHT , a 5G-specific threat modeling framework, which extracts granular attack behaviors from existing publications and maps them to adversarial techniques using ATT&CK. Similarly, ( Santos et al., 2022 ) constructs the mobile threat modeling framework named CMTMF to cover a broader range of 5G-specific tactics and techniques, incorporating emerging adversarial strategies into a unified framework. ( Pell et al., 2021 ) further enriches 5G modeling by mapping adversarial TTPs to core network components, leveraging historical attacks, threat assessments, and industry reports to provide a comprehensive view of 5G vulnerabilities.
Beyond IT and telecommunications, MITRE ATT&CK is applied in finance ( Alevizos and Stavrou, 2023 ) , transport ( Yekta et al., 2023 ) , wastewater systems ( Davis and Keskin, 2024 ) , maritime security ( Yousaf and Zhou, 2024 ) and several other domains, showcasing its versatility across critical infrastructure domains (detailed in Section 4.2 ). MITRE ATT&CK framework is a cornerstone for modeling adversarial TTPs in attack simulation research, leveraging its matrices for various system domains. Researchers have utilized the Enterprise and ICS matrices for simulating attacks in enterprise IT systems and operational technology (OT) environments ( Ajmal et al., 2021 ; Mohamed, 2022 ; Takahashi et al., 2020 ; Choi et al., 2021 ; Toker et al., 2021 ) .
Adversary emulation is a prominent approach in attack simulation ( Ajmal et al., 2021 ; Toker et al., 2021 ) . ( Ajmal et al., 2021 ) constructs attack emulation plans using CTI-derived TTPs to simulate attack flows, enabling proactive threat hunting and hypothesis validation. Similarly, ( Toker et al., 2021 ) applies ATT&CK ICS techniques to simulate multi-step attack scenarios on water management systems. Detection methods, including SVM-based classifiers and Wazuh host-based intrusion detection system (HIDS), are evaluated to visualize attack propagation on an ELK dashboard.
Attack simulations also support the generation of datasets for incident response and methodology evaluation ( Takahashi et al., 2020 ; Choi et al., 2021 ) . ( Takahashi et al., 2020 ) introduces APTGen , a top-down framework leveraging ATT&CK Enterprise techniques to generate targeted attack datasets. The process includes attack sequence generation from cybersecurity reports and selecting specific attack tools based on environmental contexts. Similarly, ( Choi et al., 2021 ) employs a hidden semi-Markov model to generate probabilistic attack sequences based on ATT&CK ICS TTPs, tested on the HAI testbed using Metasploit.
Platforms like MITRE Caldera ( Chetwyn et al., 2024 ; Lee et al., 2023a ; Noel et al., 2023 ; Gjerstad et al., 2022 ; Mohamed, 2022 ) automate attack simulations, offering a flexible tool for executing TTP sequences. ( Mohamed, 2022 ) demonstrates Caldera’s effectiveness in simulating APT attacks that bypass Windows 10 security measures using GoLang agents, providing actionable recommendations for mitigating identified vulnerabilities.
MITRE ATT&CK framework is widely adopted for its clear categorization of cyber threat actors, with both the enterprise matrix ( Manocha et al., 2021 ; Derbyshire et al., 2021 ; Ahmed et al., 2022 ) and ICS ATT&CK matrix ( Amro and Gkioulos, 2023a ; Adaros-Boye et al., 2021 ; Brenner et al., 2023 ; Yockey et al., 2023 ; Yoon et al., 2023 ) integrated into risk assessment methodologies. Risk assessment is often combined with other research areas, such as vulnerability management ( Yoon et al., 2023 ; Muthia et al., 2023 ) and threat modeling ( Naik et al., 2022 ; Mondal et al., 2023 ; Lanni and Kurniawan, 2024 ) , for a more comprehensive security evaluation.
In risk assessment, ATT&CK Enterprise TTPs are used for attack graph construction to assess the risks of successful attacks ( Adaros-Boye et al., 2021 ) . Several studies ( Manocha et al., 2021 ; Derbyshire et al., 2021 ; Ahmed et al., 2022 ) focus on using ATT&CK Enterprise tactics to calculate system risk ratings and scores. For example, ( Manocha et al., 2021 ) computes risk scores based on system security tests and ATT&CK tactics, while ( Derbyshire et al., 2021 ) proposes a framework for adversary attack cost estimation, developing security controls based on ATT&CK tactics. Similarly, ( Ahmed et al., 2022 ) introduces a cyber digital twin, linking past attacks to ATT&CK tactics and using attack graph analytics to assess and prioritize security control impacts.
The ATT&CK ICS framework is applied across multiple industries, including maritime ( Oruc et al., 2022 ; Amro and Gkioulos, 2023a ; Amro and Gkioulos, 2023b ) , energy ( Gourisetti et al., 2022 ; Mccarty et al., 2023 ; Ullah et al., 2019 ) , water ( Alfageh et al., 2023 ) , and general ICS systems. ATT&CK is used as a knowledge base to assess and quantify risks in maritime cyber components ( Oruc et al., 2022 ) and to enhance current CPS risk evaluation methodologies with semantic knowledge ( Amro and Gkioulos, 2023b ) . In the energy sector, risks are mapped to the ATT&CK ICS matrix for power systems applications ( Gourisetti et al., 2022 ) , and multi-step attack scenarios are analyzed for impact in cyber-physical wind energy sites ( Mccarty et al., 2023 ) . Additionally, ( Adaros-Boye et al., 2021 ) uses the ICS matrix to construct a knowledge base for continuous ICS risk monitoring. Automation of risk assessment in manufacturing systems is explored in ( Ehrlich et al., 2023 ) , where the ATT&CK ICS framework is integrated with industrial standards to assess the security level of cyber components.
MITRE ATT&CK framework provides detection sources and mitigation measures for attack techniques, making it a critical component in incident response research. ATT&CK has been applied to the selection and evaluation of security controls ( Rahman and Williams, 2022b ; Tavolato et al., 2024 ; Mohamed et al., 2024 ) . For example, ( Rahman and Williams, 2022b ) examines current security controls, assessing their effectiveness based on mappings between controls and ATT&CK techniques. Similarly, ( Mohamed et al., 2024 ) integrates ATT&CK into a multi-criteria decision-making methodology to prioritize security controls in defense planning.
ATT&CK is also leveraged for defense policy evaluation in empirical studies ( Outkin et al., 2022 ; Mashima, 2022 ; Boakye-Boateng et al., 2023 ) . ( Outkin et al., 2022 ) uses a game-theory approach to optimize defense strategies against multi-step attacks, evaluated with ATT&CK data. ( Mashima, 2022 ) focuses on in-network deception technology for defense, evaluating it against ATT&CK ICS attack profiles. ( Boakye-Boateng et al., 2023 ) proposes a comprehensive smart grid attack defense framework, conducting model tests on ATT&CK ICS-based attacks.
Several studies focus on attack detection and mitigation as part of incident response plans. ( Rajesh et al., 2022 ) compares threat detection methods and analyzes ATT&CK-based mitigations. ( Mundt and Baier, 2023 ) focuses on mitigating data exfiltration, using simulations based on automatically extracted ATT&CK attack data to generate potential mitigations. Additionally, some incident response works integrate CTI, using ATT&CK as a CTI source for attack techniques and mitigations ( Leite et al., 2022 ) .
IDS relies on inbuilt detection rules and external CTI sources to detect suspicious activities in the cyber system, in IDS related research, ATT&CK framework is widely utilized in AI-based IDS enhancements ( Wang et al., 2022 ; Arreche et al., 2024b ; Arreche et al., 2024a ; Hermawan et al., 2021 ) . In ( Wang et al., 2022 ) , MITRE ATT&CK tactics are utilized for attack profiling for Linux system interaction information. Feature extraction and threat detection modules are subsequently developed based on the labelled attacks. ( Hermawan et al., 2021 ) designs a threat hunting platform similar to an IDS. MITRE ATT&CK and diamond model are utilized for incident analysis and detection rule generation. Another use of ATT&CK lies in the generation and study of IDS datasets ( Zacharis and Patsakis, 2023 ; Dehlaghi-Ghadim et al., 2023 ; Landauer et al., 2022 ; Borisenko et al., 2022 ) . These datasets are usually generated by IDS from benign network activities and simulated attacks, where ATT&CK is utilised as the attack generation and data labelling framework. For example, ( Zacharis and Patsakis, 2023 ) aims to generate cyber attack contents for security exercises, labelling the attack scenario steps with ATT&CK tactics.
MITRE ATT&CK framework is widely utilized in advanced persistent threats (APTs) detection, including attack modeling ( Jabar et al., 2022 ; Soliman et al., 2023 ) and experimental evaluation ( Park et al., 2023 ) . For instance, ( Jabar et al., 2022 ) models APT attack fingerprints using ATT&CK TTP attack trees, while ( Soliman et al., 2023 ) uses ATT&CK techniques to map correlated alerts and construct an APT attack graph. The framework’s attack group profiles and techniques are employed as data sources for evaluating APT detection models in ( Park et al., 2023 ) . ( Park et al., 2023 ) also uses the coverage percentage against ATT&CK as a metric for APT detection performance. Beyond detection, ATT&CK is also applied in APT attribution ( González-Manzano et al., 2023 ; Shin et al., 2021 ; Sachidananda et al., 2023 ) . For example, ( Shin et al., 2021 ) presents a threat actor classification method by comparing the TTPs of various APT groups, using ATT&CK matrices extracted from cyber threat reports.
ATT&CK is also extensively used in general malware detection. Several studies incorporate ATT&CK with ransomware research ( Ahn et al., 2023 ; Song et al., 2023a ; Singh and Tripathy, 2024 ) . In ( Ahn et al., 2023 ) , APT scenarios based on ATT&CK are used for evaluation. ATT&CK is also correlated with ransomware data semantic features for detection ( Singh and Tripathy, 2024 ) . Malware attribution approaches, similar to APT attribution, profile malware to ATT&CK tactics and techniques using NLP methods ( Domschot et al., 2024 ) . Additional uses of ATT&CK include playbook generation for malware deception ( Sajid et al., 2023 ) , and malware evolution analysis ( Chierzi and Mercês, 2021 ) .
Researchers analyze the vulnerabilities for effective threat prevention and security patching. With the incorporation of MITRE ATT&CK, vulnerability management is often combined with risk assessment ( Yoon et al., 2023 ; Devaux et al., 2021 ; Muthia et al., 2023 ) and cross-data source analysis ( Hacks et al., 2022 ; Touloumis et al., 2021 ; Nazzal et al., 2022 ) . Vulnerabilities are mapped to ATT&CK TTPs in ( Muthia et al., 2023 ) and ( Touloumis et al., 2021 ; Nazzal et al., 2022 ) for threat-integrated risk score computation and in-depth vulnerability analysis. In ( Devaux et al., 2021 ) , ATT&CK and cyber kill chain are used to construct operational risk scenarios linked to vulnerabilities for vulnerability-based risk management. Other vulnerability researches also leverage the linkage between ATT&CK and vulnerability information, such as estimating attack time-to-compromise based on vulnerabilities ( Rencelj Ling and Ekstedt, 2023 ) and evaluating security robustness through vulnerability testing ( Sikandar et al., 2022 ) .
In addition to analyzing research focus areas, we examined the application of the MITRE ATT&CK framework across various industries. Drawing from the 16 critical infrastructure sectors defined by CISA ( Cybersecurity and Infrastructure Security Agency ([n. d.]), CISA ) , we identified 12 key industry pillars encompassing critical assets, systems, and networks vital for maintaining societal and economic stability. To ensure comprehensive coverage, we include General category for papers that lack a direct industry focus. Table 2 summarizes these industries, their descriptions, and associated research papers. This section highlights ATT&CK’s use in industries with at least five related papers, emphasizing unique applications rather than reiterating models and approaches discussed earlier. The General category, accounting for 43.1% of the papers (180 out of 417), reflects ATT&CK’s broad applicability across domains but also indicates the need for more industry-specific applications.
Sectors like Energy (9 papers, 2.2%), Transportation Systems (10 papers, 2.4%), Media (5 papers, 1.2%), and Healthcare (5 papers, 1.2%) are underrepresented. The categorization of ATT&CK-related papers into the IT, OT & manufacturing, and communications sectors is based on the types of cyber systems and assets investigated. Table 3 summarizes the applications of the MITRE ATT&CK framework across four domains, highlighting the cyber systems in each sector. While there is significant overlap in how ATT&CK is utilized across different cybersecurity systems, the specific ATT&CK matrix employed often varies. The framework’s diverse applications are prominently seen in enterprise IT networks, OT industrial control systems, and 5G/IoT communication environments.
In the transportation industry, the MITRE ATT&CK framework is primarily applied to maritime and railroad security. In maritime cyber risk assessment, studies such as ( Amro and Gkioulos, 2023b ; Amro and Gkioulos, 2023a ) focus on autonomous passenger ships, integrating ATT&CK to enhance existing risk assessment methodologies. Similarly, ( Oruc et al., 2022 ) addresses the cyber risks of marine components within integrated navigation systems, modifying traditional risk assessment frameworks to include ATT&CK TTPs and mitigation strategies. ATT&CK framework is also employed in maritime threat modeling. For example, ( Yousaf and Zhou, 2024 ) uses a case study involving an attack on a ship’s ballast water management system to model threats using the ATT&CK matrix. This study further proposes defense strategies derived from ATT&CK mitigations and the MITRE D3FEND framework, showcasing the practical utility of MITRE tools. Similarly, ( Jo et al., 2022 ) presents an attack model for shipping equipment that leverages ATT&CK TTPs to characterize attack stages based on vulnerability and threat research.
The application of MITRE ATT&CK framework in railroad systems is observed in ( Yekta et al., 2023 ; Kim and Kim, 2023 ) . ( Yekta et al., 2023 ) introduces the VATT&EK framework, which categorizes common cyber threats in intelligent transport systems using ATT&CK TTPs, formalizing vehicle-related attacks and supporting threat prioritization. Meanwhile, ( Kim and Kim, 2023 ) applies the ATT&CK matrix to generate attack sequence diagrams for evaluating the resilience of a proposed blockchain-based non-stop customs clearance (NSCC) system, designed to reduce resource requirements and delays in railroad operations.
ATT&CK framework, specifically the ICS matrix, is applied in the energy sector for cyber resilience assessments. Studies like ( Mccarty et al., 2023 ; Gourisetti et al., 2022 ) leverage ATT&CK to evaluate the cyber resilience of energy systems. ( Mccarty et al., 2023 ) performs cost-benefit analysis and risk assessments of security controls on cyber-physical wind energy sites, using the ATT&CK ICS matrix to generate attack scenarios for both remote and local energy system network access.
Similarly, ( Gourisetti et al., 2022 ) evaluates Distributed Ledger Technology (DLT) in the energy sector, proposing a cyber resilience model where TTPs are mapped to various DLT stack layers for risk analysis and mitigation recommendations. ATT&CK framework also supports cyber threat modeling for energy systems. For example, ( Cerotti et al., 2020 ) develops an attack knowledge base by mapping publicly reported attack data to ATT&CK ICS TTPs in distributed energy control systems.
The study models these scenarios as attack graphs with attacker state nodes and attack technique edges. Dynamic Bayesian Networks derived from these graphs capture causal and temporal dependencies of threats, enabling detailed risk assessments. Similarly, ( Ullah et al., 2019 ) identifies threat indicators and network topology in energy delivery systems to construct TTP-based attack graphs. These models assess the likelihood of asset compromise along attack paths using defined risk metrics.
In the oil and gas sector, field flooding attacks targeting the memory structure of Modbus operations in programmable logic controllers (PLCs) have become a growing concern. ( Amro and Gkioulos, 2023b ) uses the ATT&CK framework to assess flooding attacks on an industrial testbed. This study identifies the associated ATT&CK TTPs, evaluates the attack methodology and impacts, and proposes a tailored detection algorithm to mitigate such threats.
Research in the healthcare sector primarily focuses on securing healthcare infrastructures and medical devices. For instance, ATT&CK is employed for threat and attack route identification in the security analysis of radiological medical devices, with mitigation strategies proposed using the ATT&CK knowledge base ( Zisad and Hasan, 2024 ) . Similarly, ( Ampel et al., 2024 ) introduces the ATT&CK-Link framework, which utilizes a transformer-based model and multimodal classification to link hacker threats in hospital systems to ATT&CK. This approach generates actionable CTI for comprehensive security analysis in healthcare infrastructure.
Harvested Online Documentation & Reference Sources • https://www.decryptiondigest.com/blog/mitre-attack-framework-practitioner-guide • https://security.googlecloudcommunity.com/google-threat-intelligence-67/adoption-guide-threat-hunting-using-mitre-att-ck-6 388 • https://attack.mitre.org/ • https://www.paloaltonetworks.com/cyberpedia/how-to-implement-mitre-attack-techniques • https://arxiv.org/html/2502.10825v1
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Cyber Threat Hunting Tool Using MITRE ATT&CK Framework.
[*] Metasploit Scan Running on Target Subnet for Cyber Threat Hunting Tool Using MITRE ATT&CK Framework... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |