Complete Technical Paper Content — Cyber Warfare Attack Simulation Tool In Network Sandbox
Overview & System Context
Cyber Warfare Attack Simulation Tool In Network Sandbox: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9983 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background This is a confirmed list of video games in development, but are scheduled for release beyond 2027 or currently carry no announced, reported, or confirmed release date at all.
The following list includes games that were announced but have not seen progress updates in years, also known as being in development hell, or have been put on indefinite hold. They may be also deemed as vaporware. In this part of the lab series, we are going to simulate an end-to-end cyber-attack on ProjectXâIIs business network. The end goal is to capture sensitive files and achieve persistence inside the business network, so that we can log back in at our discretion.
Up until this point, we have built an enterprise or business network to âIIemulateâII a real-world environment, something you would often see deployed to a much larger scale in the real-world. Figure 1: 10 Best Cyber Attack Simulation Tools For Organization Security 2022 Threat actors (will use this interchangeably with attacker) have various motives. Most of what you see on the major news outlets and dedicated security news websites are financially motivated attackers, opportunistic in conducting their operations in hopes of financial gain or extortion.
Attackers can act alone, in a disparate community, using or helping others along the way, or in a selective group. Outside of financial motives, attackers can align with different motives, a few the major ones are: LetâIIs overview the anatomy of a cyber-attack and review the major steps involved to achieve our objective. Figure 2: Cyber Visual Simulation Stock Illustrations – 14,582 Cyber Visual ...
Each of these steps aims to achieve a specific outcome. To conduct a successful cyber-attack, its imperative attackers take the proactive steps from initial access to persistence. These steps are leveraged in separate phases but are often chained together. For example, once an attacker gains initial access or lateral movement, they will perform additional reconnaissance on the network to see what is available.
Most often, attackers want to stay hidden in the network with unfettered access for as long as possible. Each of these steps brings the attacker closer to their end goal or motive. These steps were first built by Lockheed Martin as a conceptual model to understand and defend against cyber-attacks, known as the Cyber Attack Kill Chain.
Figure 3: New Research Shows that Breach and Attack Simulation Technology is Key ... As the industry continued to mature its approach to proactive detection, the MITRE ATT&CK framework was built to expand these ideas by providing a real-world repository of tactics, techniques, and procedures (TTPs) used by threat actors, broken down into generalized steps attackers take to control a business or organization.
Also referred to as 'recon'. This is first phase of a cyber-attack where attackers gather information about their target to identify vulnerabilities they can exploit. This phase is all about preparation and involves collecting as much data as possible about the target's systems, network, employees, or infrastructure without triggering alarms. Attackers establish a foothold in the targetâIIs environment. This is the entry point, achieved by exploiting vulnerabilities, phishing, using compromised credentials, or exploiting misconfigurations. The goal is to gain access to the target network while avoiding detection, setting the stage for further malicious activities.
Attackers navigate through a compromised network to access more systems, resources, or sensitive data. They move from the initial access point by exploiting vulnerabilities, using stolen credentials, and leveraging tools at their disposal. The aim is to expand control and find valuable assets without raising suspicion. Attackers increase their level of access within the target environment. This is done by exploiting system vulnerabilities, misconfigurations, or weak permissions to move from a standard user to an admin or system-level account. It allows attackers to execute critical tasks and access sensitive data more freely.
Attackers transfer stolen data out of the target environment. This may include sensitive files, credentials, or intellectual property. Attackers often disguise or encrypt the data to evade detection during the transfer process, using channels like email, file-sharing platforms, or compromised systems. Attackers ensure ongoing access to the compromised system even after reboots or initial detection attempts. This involves creating backdoors, modifying system configurations, or installing malware that enables them to maintain control over the environment for extended periods.
Attackers employ techniques to avoid detection and bypass security measures. This includes obfuscating malware, disabling security tools, using fileless attacks, or manipulating logs. The objective is to operate undetected, prolonging their access and reducing the chances of discovery. We now have a basic overview of the steps or actions threat actors take to achieve their outcomes.
In this lab, we are going to âIIsimulateâII each step by leveraging techniques and tools at our disposal as an attacker. By leveraging default, insecure, and outdated configurations and software, our attacker wants to use their skills for their own personal gain. These configurations, although outdated and disabled by default, can still often be found in business networks to this day.
Our attacker is financially motivated, attempting to steal sensitive data. They have identified ProjectX as a target organization to conduct their operations so they can extort and steal some sensitive information, perhaps a username, password, and proprietary files. Throughout this guide, you will find highlighted sections with questions or comments related to a quick tool or service overview.
One common pattern you will find in entry-level cybersecurity training content is outdated techniques and legacy systems in use. These attack techniques may not be as relevant or prolific as they once were. Tools receive updates and legacy systems are End-of-Life (EoL). Attacks conducted a few decades ago are no longer viable in today's landscape. These attack and legacy systems are still used to showcase the technique while remaining entry-level friendly. Attacks and exploits have gotten more advanced. Although there are still some trivial attack paths.
It's good to know if these attack techniques and systems are still relevant today and thatâIIs why there is a box to help you gauge how common this is. This will highlight a specific tool being used to conduct an operation. You will find these tools to be very popular once you start researching this industry.
You will also see a âIIMandatory VMs Powered-OnâII section. These are the mandatory VMs that must be powered on. If your system is limited on resources, you can only have the listed VMs turned on while the others remain off for that particular section. The reconnaissance phase, often referred to as "recon," is the initial step in a cyber-attack or security assessment where attackers or penetration testers gather information about their target. The primary goal is to understand the targetâIIs systems, networks, and environment to identify potential vulnerabilities or points of entry. Reconnaissance is used to collect as much data as possible about the target without actively engaging or alerting the target. It involves gathering information that will inform the next steps of the attack or test.
In this scenario, we are going to assume the [ project-x-corp-svr ] is Internet reachable. ðIII nmap (Network Mapper): Open-source tool used for network discovery and security auditing. It allows users to scan and map networks to identify live hosts, open ports, running services, and system vulnerabilities. You will use this so often, that is basically a standard in this industry.
We know the IP address is up and running. It appears SSH is running as a service. We would not yet know what kind of services or server this is as an attacker. Perhaps a jumphost, a license server, or email server. (of course we know, because we set it up.) LetâIIs proceed forward with attempting to login to the account using SSH as our medium for access. Leveraging a password cracking tool, called Hydra, we can initiate a brute force and use a wordlists file, such as rockyou.txt to see if there are any matches.
ðIII Hydra: Password-cracking tool used for brute-force attacks on various network services. It automates the process of attempting multiple username and password combinations to gain unauthorized access to systems. First, letâIIs source the rockyou.txt file by unzipping it, rockyou.txt comes installed as a default wordlist in Kali. Navigate to the search menu, search âIIrockyouâII, you should see a wordlists option display, click this.
Navigate to the same terminal as the nmap scan and supply the following hydra command: hydra -l root -P /usr/share/wordlists/rockyou.txt ssh://10.0.0.8 ðII¡ How are we getting the username? A username can be anythingâI¦ - Like a password, usernames are often used interchangeably across various systems. User accounts may be provisioned by default, as root always has an account in Linux. We could use other names such as user, admin, administrator, user1, etc. Check out SecLists for common usernames.
You can also supply usernames in Hydra by using the -L flag. - Ex: hydra -L /usr/share/wordlists/usernames.txt -P /usr/share/wordlists/rockyou.txt ssh://10.0.0.8 After a few minutes, you should see Hydra locate the username and its associated password. Initial Access is the first phase in a cyber-attack where adversaries seek to establish a foothold in the target network or system. It is the gateway for attackers to gain entry, enabling them to progress through subsequent stages of an attack, such as privilege escalation, lateral movement, and data exfiltration. We have already established initial access with this Ubuntu server by cracking the weak password.
Now we need to perform additional reconnaissance on this device to see what type of device it is, what services are running and perhaps if thereâIIs any connection to other devices. The steps or phases of cyber attacks are often chained. Meaning you will perform some reconnaissance or information gathering, attempt to gain access, if failed, move onto something else, if successful, gain initial access, perform more reconnaissance.
LetâIIs first see what type of device this is. We know we have root access since we were able to break into the account. We also want to see if there are any active services to find potential attack vectors. We can also attempt to find configuration files, user credentials, and other sensitive information. Since we are root, we do not need to escalate privileges. We will look at how to perform privilege escalation in the next step.
2. System Architecture & Core Working Principles ðI¤I How Relevant Is This Today?: The attackerâIIs machine would almost never be on the same network as the target victim. Often, malware and scripts are dropped to establish an initial communication with the attackerâIIs infrastructure. Which then is able to communicate with the compromised device. You will see this in Networks & Attacks 101 Core Section.
Based on our discovery steps, we can attempt to devise a picture of maybe what role this server has. We see simulated SMTP 1025 is listening, perhaps this device may act as some sort of email relay, server, or something to do with email. We can also see we are in the 10.0.0.0/24 range, a private IP address range, used in Local Area Network (LAN)s.
Based on our nmap scans, we can see there is a device called linux-client running on 10.0.0.101. It appears SSH is running. We could attempt to use the same technique as before, leveraging Hydra and a default password list. If we use rockyou.txt , you will notice that we do not receive any successful tries. Onto something else. And this is exactly what happens while hacking. It is a lot of trial and error.
Back to SMTP, as an attacker, we may investigate seeing what type of configuration files reside on the device. Performing a quick Google search on the ports, we can identify that MailHog is an SMTP service running. Let's take a look to see if there is an interface on port 8025 as highlighted in the Google search. It appears we have some emails meant for this server, perhaps it was routing these emails to other clients.
You need to send the test_message.py email on [ project-x-corp-svr ] first. MailHog is stateless, the email inbox resets every time the container stops. Looking into the first email, we can see thereâIIs an email address, janed@linux-client . We are going to send an email to this user, impersonating the email server (since itâIIs trusted in the network) and will likely route directly to the inbox.
LetâIIs attempt to get some credentials from this user (the attacker can probably conclude Jane is a part of the userâIIs name). ðI¤I How Relevant Is This Today?: Most email servers are managed and run by major cloud service providers, think Gmail or Outlook. Running a dedicated on-premise email server was mostly a thing of the past.
Since it appears our medium for this attack is text-based (normal email would support attachments, images, etc), the attacker is going to set up a spear-phishing email website impersonating a password verification website. We are going to build a small static website which captures the username and password of any user who types the link in, the credentials will be logged.
Leveraging AI LLMs are at our disposal, we can quickly generate a static website. You can download the project files from Github to pull the specific content and page used for this part. You are welcome to generate your own static website, you will have to customize html. Navigate to the /var/www/html folder, this is where default websites can be provisioned Download the project files: - git clone https://github.com/collinsmc23/projectsecurity-e101 Make a new logging file to log the captured credentials, set permissions on this file: Open your browser in Kali, navigate to http://localhost . You should get a page like the following.
Going back to our Kali terminal, you should see new credentials captured when looking at the creds.log file. To craft a seemingly innocent, yet descriptive email, we can use ChatGPT (or your LLM of choice) to create an email. HereâIIs what ChatGPT came up with for me. Dear Jane, We noticed an unusual login attempt on your account, and for your security, we have temporarily locked access.
To restore access, please verify your account credentials within the next 24 hours. Failure to do so may result in permanent restrictions on your account. To verify your credentials, please click the link below: Verify My Account For assistance, please contact our support team at support@company.com. Thank you for your prompt attention to this matter. Best regards, ProjectX Security Team ðIII : Make this your Kali Linux IP address. You can find the address by going back to your attacker machine and supplying, ip a .
ðII¡ Why are we wrapping the email in HTML ? - If Jane were to open this email on a regular email client, such as Gmail or Thunderbird, we could get the email to use the âIIhyperlinkâII feature, which makes the address concealed. In this scenario, Jane would likely know this is a phishing email just by looking at the contents in . If you can recall from our MailHog section, we created a email_poller.sh script to run in the background and check the fake email inbox every 30 seconds.
Based on our previous nmap scans, we know that the host 10.0.0.101 has SSH up and running, letâIIs attempt to see if we can login. Lateral movement is a tactic used by attackers to navigate through a compromised network to gain access to additional systems, resources, or data.
It occurs after an initial breach and is an essential phase in many cyber-attacks. It helps them maintain persistence, avoid detection, and prepare for further actions like data exfiltration or ransomware deployment. Common methods include credential dumping, exploiting vulnerabilities, and leveraging legitimate tools like PowerShell or RDP. In the Privilege Escalation phase, attackers aim to increase their level of access within the compromised environment. By obtaining higher privileges, such as administrator or root access, adversaries gain greater control over the systems.
Techniques include exploiting software vulnerabilities, misconfigured user accounts, or password weaknesses. For example, attackers may exploit unpatched privilege escalation bugs to override normal restrictions. This expanded access enables attackers to modify system configurations, disable security measures, and access sensitive data, making it a critical phase in advancing their attack.
LetâIIs collect some information, like what we did before. Performing some additional information gathering. We also want to see if there are any active services to find potential attack vectors. ðII¡ For the sake of time saving, you can use -p 5985, 5986 instead of probing through all 65535 ports. WinRM has been heavily abused in the past to perform lateral movement and privilege escalation. We are going to attempt to get shell by performing some additional password spraying.
ðIII Windows Remote Management (WinRM): A Windows-based protocol and service that allows administrators to manage and interact with remote computers. WinRM is a service that must be running on both the client and the target system. A "listener" is set up on the remote machine to accept incoming connections on specific ports 5985 (HTTP) 5986 (HTTPS). ðI¤I How Relevant Is This Today?: WinRM is still heavily used in todayâIIs threat landscape.
There are many password spraying tools offered. We could use a module in Metasploit or dedicated password spraying tools such as NetExec . ðIII NetExec: A tool used to compromise services within a network such as: SMB; SSH; LDAP; FTP; WMI; WINRM; RDP; VNC; MSSQL.
Like Hydra, NetExec takes a list of usernames and passwords. We can source usernames and password lists for SecLists . SecLists is a very popular, open-source word list for usernames and passwords. One common technique is to spawn a shell by leveraging insecure protocols and outdated software packages with known exploits.
After searching around, you will likely find a popular open-source project called EvilWinRM. ðIIIEvil-WinRM: An open-source, command-line tool that provides remote shell access to Windows machines over WinRM. Evil-WinRM connects to a target system via the WinRM service, you must have valid credentials. Once authenticated, it initiates a Powershell session. So it helps us with establishing a connection.
ðI¤I How Relevant Is This Today?: Password spraying is still a very commonly used today. Just take a look at âIIPassword SprayingâII on Google and you will find updated articles with APTs and organizations. In terms of getting access direct Administrator account, this will not be very common in updated networks, as these accounts usually have strong authentication and enforce the principle of least privilege.
We have access to the [project-x-win-client] and we have the Administrator account. LetâIIs see if we can pivot to the domain controller. 3. Software Implementation, Frameworks & Protocols One thing you will often find while attackers conduct their cyber-attacks is a combination of all the steps. You will find initial access, then reconnaissance, then lateral movement, then more reconnaissance, etc.
First, letâIIs see what domain this workstation is a part of and itâIIs corresponding IP address: LetâIIs see what open ports this device has. (We could install nmap on our Windows 11 machine if our attacker machine was not on the same network). Going back to a new terminal in Kali, letâIIs use the xfreerdp utility to establish a new session: Navigating around the file system, we will eventually a folder called âIIProduction DocumentsâII inside the Documents folder secrets.txt .
Attackers extract valuable or sensitive information from the compromised network. The goal here is to transfer data such as intellectual property, customer records, or financial information to an external location controlled by the adversary. Methods include encrypting and compressing data to avoid detection, using covert channels like DNS tunneling or HTTPS, or exfiltrating data in small chunks to evade bandwidth monitoring. Successful data exfiltration can result in significant reputational, operational, and financial damage to the target.
Since we have access via RDP, we could use a cloud storage provider to upload our sensitive files or we could use SMB to share files between our Kali machine since we are connected on the same network, although this is not very realistic. We are just going to use scp command line program to copy the files, to take the simple way (also not very realistic). Now that we have effectively pwned the environment, itâIIs time to ensure we can come back to where we left off. Since the attacker has important business to take care of. Persistence refers to attackers maintain access to a system even after their initial intrusion is discovered and remediated. This ensures the attackerâIIs operations can continue despite interruptions.
Common techniques include installing backdoors, creating rogue accounts, or leveraging legitimate tools for remote access like RDP or VPNs. Persistence mechanisms are often embedded deep in the system, such as registry modifications or startup scripts, to resist detection and removal. This tactic is especially critical for long-term campaigns where adversaries intend to maintain a foothold over extended periods.
We can now implement persistence techniques to ensure we can get back to where we are after. Similar to the above steps, there are many ways to do thisâI¦ One of the easiest methods is to create a new user account. Call it something generic to blend in: project-x-user . Open a new terminal with administrator privileges or use the one from the previous step.
Windows allows you to create scheduled tasks to perform various automations on a timeline. Back into the Kali machine, create a new file using nano and add the following to a script called reverse.ps1 . Use a python webserver to upload the copy from [project-x-attacker] to [project-x-dc] , from where the reverse.ps1 script is, perform: Now at 12:00 PM we can catch a reverse shell by opening a listener on port 4444 on [project-x-attacker] .
Looking back at the Kali terminal, we should see a message with âIIConnected to reverse shell!âII Windows Defender may block this from happening. You can turn off Windows Defender by going to Windows Security âIIVirus & Threat protectionâII âIIVirus & threat protection settingsâII Turn off all toggles. And with this final step complete, we have finished our attack, from Initial Access to Breached.
This labâIIs intention was to serve as a primer for how threat actors approach compromising a target organization. With various tools, techniques, and procedures, threat actors can leverage their skills, open-source knowledge, and now LLMs to achieve their objectives. As defenders (or ethical offenders), it is our responsibility to be deeply informed and educated on how attackers launch and maintain their attacks.
There are additional courses (called Core Sections) coming up, so stay tuned on our social media accounts! arXivLabs is a framework that allows collaborators to develop and share new arXiv features directly on our website. Both individuals and organizations that work with arXivLabs have embraced and accepted our values of openness, community, excellence, and user data privacy. arXiv is committed to these values and only works with partners that adhere to them.
Have an idea for a project that will add value for arXiv's community? Learn more about arXivLabs . This project aims to simulate network attacks and defenses using widely used, powerful tools. It includes the setup, execution, and analysis of common cyber attacks and defenses in a virtualized environment. Contributions are welcome! Please fork this repository and submit a pull request with your changes.
This project is licensed under the Apache License 2.0 - see the LICENSE file for details. Ce projet vise à simuler des attaques et des défenses réseau en utilisant des outils puissants et couramment utilisés. Il inclut la configuration, l'exécution et l'analyse d'attaques et de défenses courantes dans un environnement virtualisé. Veuillez télécharger les fichiers ISO suivants et placez-les dans le répertoire « ressources » : Les contributions sont les bienvenues ! Veuillez forker ce dépôt et soumettre une pull request avec vos modifications.
Ce projet est sous licence Apache Licence 2.0 - voir le fichier LICENSE pour plus de détails. Simulation of network attacks and defenses using powerful tools such as Metasploit, Snort, and PFsense. This project demonstrates the setup, execution, and analysis of common cyber attacks and defenses in a virtualized environment. I Overview This comprehensive guide walks you through setting up a fully functional Security Operations Center (SOC) home lab, compatible with both VirtualBox and VMware Workstation. You'll build a safe, isolated environment using Windows 10, Kali Linux, Sysmon, and Splunk to simulate real-world attacker–defender scenarios. Designed for both beginners and intermediate learners, the guide provides in-depth, hands-on instruction covering everything from virtual machine setup and secure networking to malware generation, event telemetry, and log analysis using enterprise-grade tools.
Ensure you have the following components prepared before beginning the SOC home lab setup: I Tip: If your C: drive has low storage, you can save VMs to another drive like D:/ or E:/ . Feel free to customize with more machines (like Ubuntu for ELK stack, Security Onion, etc.) as your system allows. There are several ways to install Windows 10, including using third-party ISO files or pre-made images. However, creating your own Windows ISO image using Microsoft's official tool is one of the safest and most reliable methods .
Choose language, edition, and architecture, or leave "Use the recommended options" checked. Download the official Kali Linux virtual machine image for easy import into VirtualBox. Once you've set up the internal network and isolated the virtual machines, they will no longer have internet access. Therefore, make sure you complete the installations of Sysmon and Splunk while the network is still in NAT mode (the default setting).
Once this is done, you can proceed to network isolation safely. Objective : The goal is to generate telemetry on the Windows target machine so you can detect attacker behavior. Download Olaf Hartong’s configuration (I Big thanks to Olaf Hartong for his outstanding work on Sysmon Modular – this configuration makes deep endpoint visibility much more accessible.) file: sysmonconfig.xml Alternatively, use Event Viewer → Applications and Services Logs → Microsoft → Windows → check for Sysmon .
I Tip: If you're new to Splunk, check out the Splunk Fundamentals 1 course (free): I https://www.splunk.com/en_us/training/splunk-fundamentals.html When setting up virtual machines, default settings are usually fine for general use. However, if you're planning to analyze malware or potentially harmful software , using default networking configurations may put your host machine at risk .
4. Practical Deployment, Analysis & Case Studies This guide primarily uses VirtualBox , but instructions for VMware Workstation are also provided for users who prefer that platform. To minimize the chance of infecting your host system during malware analysis, the key area to focus on is network configuration .
I Reminder : For malware analysis, use "Host-only Adapter" , "Internal Network" , or "Not Attached" to reduce exposure to your host and external networks. When analyzing malware, it’s essential to isolate the virtual machines from the internet and your host system. The Internal Network option is ideal in this case. This mode places your virtual machines in a completely separate network with no internet access or LAN access. You’ll need to manually assign IP addresses for each VM.
Avoid using Generic Driver or Cloud Network unless you're confident about their configurations. They are rarely used and not recommended for malware labs. Configure both Windows and Kali Linux VMs to be on the same isolated internal network: I Reminder : Ensure both VMs use the exact same network name ( test ) so they can communicate.
Since the Internal Network has no DHCP server, you need to assign static IPs manually. If you're using VMware Workstation , the concept is similar but the naming is different. Instead of "Internal Network" (used in VirtualBox), VMware uses LAN Segment for isolated networking Just like in VirtualBox, you’ll need to assign static IPs manually in each VM to ensure they’re on the same subnet.
Now you're ready to safely analyze malware in an isolated environment using either VirtualBox or VMware. Thanks! Here's the corrected version of that section with your instruction clearly reflected: I Important: Don’t edit the file manually. Instead, replace everything in inputs.conf with the preconfigured version provided in the GitHub repo.
This configuration ensures that Splunk is correctly set up to collect all relevant Sysmon logs using the lab's custom settings. Here's your full rewritten and neatly organized note with all points preserved, formatted clearly for ease of understanding and reference during your lab work or demonstrations: I Take note of your IP address – we’ll use this as the LHOST value while generating the malware and setting up the listener.
The output file Resume.pdf.exe will attempt to connect back to the attacker machine on port 4444 (default for Meterpreter). Note: The default payload is usually generic/shell_reverse_tcp . We’ll change it to match our malware: In a new terminal tab , make sure you're in the same directory as Resume.pdf.exe , then start a Python HTTP server: Download Resume.pdf.exe . If you see a warning about the file not being commonly downloaded — ignore it only for this lab .
Once you've successfully ingested Sysmon logs into Splunk and executed the simulated attack (e.g., Nmap scan and Resume.pdf.exe malware), here’s how to investigate these activities: I While this log shows an incoming connection attempt, Sysmon alone doesn't show full Nmap scan behavior (like sequential port scanning). That’s why: II It's highly recommended to have a network sensor (e.g., Zeek or Suricata) deployed between your machines. These can detect: Without it, the telemetry is limited to what the endpoint sees—making it harder to distinguish between legitimate access and reconnaissance attempts.
A Python-based cybersecurity training tool that simulates real-world network attacks in a safe, sandboxed environment. A Python-based cybersecurity training tool that simulates real-world network attacks in a safe, sandboxed environment. This is a simulated cybersecurity project built in Cisco Packet Tracer. It demonstrates network segmentation, threat detection, logging, access control, and incident response using a multilayer switch and multiple VLANs.
To implement core cybersecurity concepts in a simulated enterprise network environment using practical tools such as VLAN segmentation, ACLs, port security, DHCP snooping, ARP inspection, syslog, and simulated attacks. This simulation offers a full-stack view of how security can be layered in an enterprise network. From segmentation and ACLs to logging and spoofing defense, it serves as a strong foundational project for entry-level network security learning and demonstration.
This project is a practical simulation focused on securing a segmented network environment using Cisco Packet Tracer. It demonstrates key cybersecurity practices including VLAN segmentation, DHCP snooping, port security, ARP inspection, ACLs, attack simulation, and incident response Follow this real-life network attack simulation, covering 6 steps from Initial Access to Data Exfiltration. See how attackers remain undetected with the simplest tools and why you need multiple choke points in your defense strategy.
Surprisingly, most network attacks are not exceptionally sophisticated, technologically advanced, or reliant on zero-day tools that exploit edge-case vulnerabilities. Instead, they often use commonly available tools and exploit multiple vulnerability points. By simulating a real-world network attack, security teams can test their detection systems, ensure they have multiple choke points in place, and demonstrate the value of networking security to leadership.
In this article, we demonstrate a real-life attack that could easily occur in many systems. The attack simulation was developed based on the MITRE ATT&CK framework, Atomic Red Team, Cato Networks ' experience in the field, and public threat intel. In the end, we explain why a holistic security approach is key for network security . These steps were chosen since they exemplify common techniques that are ubiquitous in attacks.
The attack begins with spear-phishing, which establishes initial entry into the network. For example, with an email sent to an employee with a lucrative job offer. The email has an attached file. In the backend, the malicious attachment in the email runs a macro and exploits a remote code execution vulnerability in Microsoft Office with a Hoaxshell, which is an open-source reverse shell.
According to Dolev Attiya, Staff Security Engineer for Threats at Cato Networks, “A defense-in-depth strategy could have been useful as early as this initial access vector. The phishing email and the Hoaxsheel could have been caught through an antivirus engine scanning the email gateway, an antivirus on the endpoint or through visibility into the network and catching command and control of the network artifact generated by the malicious document. Multiple controls increase the chance of catching the attack.” Once access is gained, the attacker transfers various tools into the system to assist with further stages of the attack. This includes Powershell, Mimikatz, PSX, WMI, and additional tools that live off the land.
Attiya adds, “Many of these tools are already inside the Microsoft Windows framework. Usually, they are used by admins to control the system, but attackers can use them as well for similar, albeit malicious, purposes.” Now, the attacker explores the network to identify valuable resources, like services, systems, workstations, domain controllers, ports, additional credentials, active IPs, and more.
According to Attiya, “Think of this step as if the attacker is a tourist visiting a large city for the first time. They are asking people how to get to places, looking up buildings, checking street signs, and learning to orient themselves. This is what the attacker is doing.” Once valuable resources are identified the previously added tools are used to extract credentials for multiple users to compromised systems. This helps the attacker prepare for lateral movement.
With the credentials, the attacker moves laterally across the network, accessing other systems. The attacker’s goal is to expand their foothold by getting to as many users and devices as possible and with as high privileges as possible. This enables them to hunt for sensitive files they can exfiltrate. If the attacker obtains the administrator’s credentials, for example, they can obtain access to large parts of the network. In many cases, the attacker might proceed slowly and schedule tasks for a later period of time to avoid being detected. This allows attackers to advance in the network for months without causing suspicion and being identified.
Etay Maor, Sr. Director of Security Strategy, says “I can’t emphasize enough how common Mimikatz is. It’s extremely effective for extracting passwords, and breaking them is easy and can take mere seconds. Everyone uses Mimikatz, even nation-state actors.” Finally, valuable data is identified. It can be extracted from the network to a file-sharing system in the cloud, encrypted for ransomware , and more.
Effectively protecting against attackers requires multiple layers of detection. Each layer of security in the kill chain must be strategically managed and holistically orchestrated to prevent attackers from successfully executing their plans. This approach helps anticipate every possible move of an attacker for a stronger security posture. To watch this entire attack and learn more about a defense-in-depth strategy, watch the entire masterclass here.
AI agents are already accessing sensitive data and systems—learn how to discover them, control their permissions, and reduce insider risk before it becomes a breach. 5. Performance Evaluation & Extended Technical Observations Learn how to assess AI threat readiness, strengthen attack surface visibility, and prepare security operations for emerging threats in this practical webinar.
Tamnoon CEO Marina Segal on the Self-Healing Cloud: Why It Starts With a Machine That Knows When Not to Act Dive into a practical demonstration of a network attack, tracing its progression across six pivotal stages—from Initial Access to Data Exfiltration. Learn how attackers leverage basic tools to stay hidden and discover why having multiple layers of defense is critical.
Most network threats surprisingly don’t rely on high-tech or obscure zero-day exploits. Instead, they exploit well-known vulnerabilities using readily available tools. Through this simulation based on real-world models like the c, Atomic Red Team, and insights from Cato Networks and public threat intelligence, security teams can test their defenses, ensure robust multi-layer security, and showcase the significance of network security to their leadership.
Dolev Attiya, a security engineer, notes, “A layered defense strategy is essential from the start. The phishing attempt and the exploit could be detected through multiple controls like email scanning, endpoint antivirus, or network monitoring.” 2. Ingress Tool Transfer : Post-access, the attacker introduces tools like Powershell and Mimikatz into the system, tools that are commonly part of the Windows environment but are repurposed here for malicious activities.
3. Discovery : The attacker maps the network, identifying critical assets such as servers, workstations, and domain controllers, much like a tourist navigating a new city. 4. Credential Dumping : Using the tools deployed earlier, the attacker extracts credentials from various systems, preparing for the next phase.
5. Lateral Movement and Persistence : With these credentials, the attacker spreads laterally across the network, aiming to reach as many systems and gain as high privileges as possible. This phase is crucial for setting up long-term access and preparing for eventual data extraction. Etay Maor, a security strategist, comments, “The ubiquity of tools like Mimikatz in such attacks underlines their effectiveness in bypassing security measures within seconds.” 6. Data Exfiltration : The final stage involves identifying and siphoning off valuable data, which might be uploaded to a cloud service or encrypted for a ransomware attack.
To guard against such attacks, a multi-layered security approach is vital. Effective protection involves strategic and holistic management of all security layers within the attack chain, preparing for every possible move by an attacker to fortify the network’s defenses. Reach out to us at PivIT Strategy to start a conversation of protecting yourself further. Jeff, the CEO of PivIT Strategy, brings over 30 years of IT and cybersecurity experience to the company. He began his career as a programmer and worked his way up to the role of CIO at a Fortune 500 company before founding PivIT Strategy.
CyberTask is an enterprise cyber range platform to build and run realistic environments for SOC training, incident response, cybersecurity labs, CTFs, and talent assessment. Everything you need to build, deploy, and manage enterprise-grade cybersecurity training environments. Design multi-subnet networks with virtual machines, firewalls, and advanced networking controls — mirroring production environments for realistic training scenarios.
Create rich, multi-page labs with an intuitive visual builder. Design diverse challenges from answer-based tasks to guided walkthroughs — with hints, scoring, and automated validation. Each student receives a fully cloned, isolated copy of the lab's virtual network — complete with VMs, credentials, and network configuration. No cross-contamination, no shared state.
From network simulation to performance analytics — every tool you need in one platform. Access Windows and Linux VMs directly from the browser — RDP, SSH, and file transfer with no client software needed. Define inbound/outbound firewall rules and manage routing tables synced to live infrastructure. Run team CTFs with captain-managed teams, shared scoring, join keys, and aggregate leaderboards. Configure min/max team sizes per lab.
Per-question success rates, attempt analytics, hint usage patterns, score distributions, and time-spent breakdowns for every lab. Organize users with role-based access control, delegated management, and branch-level resource governance. Set limits on VNets, VMs, vCPUs, RAM, and storage at system, branch, and individual user levels. Monitor usage in real time.
Take point-in-time snapshots of virtual machines and restore them instantly. Manage snapshot versions and roll back to any state. Execute provisioning scripts and commands on machines remotely. Deploy startup scripts during machine creation for automated setup.
Cross-lab competitive ranking with time-period filtering (all-time, monthly, weekly), search, and task completion grid visualization. Automatically generate and issue downloadable PDF certificates with unique UUIDs upon lab completion. Track scores and pass percentages.
Multi-criteria rating system — content quality, difficulty accuracy, real-world relevance — with open-ended feedback and recommendations. Complete audit trail of all user actions, CRUD operations, role changes, and system events with IP and user-agent tracking. Use the VNet Manager to create subnets, deploy VMs with your OS images, configure firewalls and routing — all from a visual interface.
Link your network to a lab. Add tasks, hints, and scoring rules with the drag-and-drop lab builder. Set difficulty, categories, and certificates. Publish your lab. Each participant gets an isolated clone of the entire environment — access VMs from the browser and solve challenges.
Every lab you complete, every challenge you solve — it all builds into your cybersecurity profile. Your rank, skills, badges, and certificates demonstrate real expertise, verified through action. Whether you're training a SOC team or running a national CTF — CyberTask scales to your needs. Deploy fully virtualized attack-and-defend environments with live VMs, real networking, and enterprise-grade isolation. Run red-team/blue-team exercises, incident response drills, and penetration testing labs on cloud or on-premises infrastructure.
Build structured learning paths with progressive labs, from beginner tutorials to advanced exploitation challenges. Track student progress through multi-criteria analytics, automated scoring, and completion certificates. Design bespoke training scenarios replicating your organization's specific infrastructure and threat landscape. Configure network topologies, OS images, firewall policies, and vulnerability chains to match real-world conditions.
Evaluate cybersecurity candidates through timed challenges, proctored exams, and competitive CTF events. Compare performance across teams with global leaderboards, score distributions, and detailed attempt analytics. Universities and colleges running cybersecurity programs with hands-on lab coursework and student assessments. National cyber agencies and defense organizations conducting operator training and exercise scenarios.
Security operations centers running continuous training, tabletop exercises, and incident response drills. Event organizers hosting competitive capture-the-flag challenges with team management and live scoring. Start building virtualized training environments, CTF challenges, and assessment programs today. Creating a virtual lab for cybersecurity practice provides a safe environment for hands-on learning in penetration testing, ethical hacking, and network security. Learn to set up virtual machines, configure networks, install essential tools, and maintain a sandbox environment to develop practical skills effectively while preparing for real-world cybersecurity challenges.
Building a virtual lab for cybersecurity practice is an essential step for anyone looking to gain practical experience in ethical hacking or network security. A well-prepared lab allows learners to simulate real-world cyber attacks safely and explore vulnerabilities in different operating systems without risking actual systems. Institutes such as Ethical Hacking Training Institute, Webasha Technologies, and Cybersecurity Training Institute provide structured guidance for building labs that mirror professional environments. Beginners often use comprehensive online courses to learn how to install virtual machines, configure networks, and deploy security tools effectively before progressing to advanced exercises. Practicing in a virtual lab also helps develop analytical thinking and problem-solving skills critical for cybersecurity roles. Choosing the Right Virtualization Platform Select a virtualization platform such as VMware, VirtualBox, or Hyper-V that is compatible with your hardware and operating system. Ensure the platform supports snapshots and cloning to restore VMs easily after testing experiments. Consider performance aspects including RAM, CPU, and storage to efficiently run multiple virtual machines simultaneously. Check for platform stability, frequent updates, and a large community for troubleshooting and support.
Advanced learners can leverage Hyper-V or VMware for networking simulations and enterprise-level configurations. Webasha Technologies provides detailed tutorials on choosing the best platform and configuring virtual networks for secure lab environments. Platforms should support cross-platform guest OS installation to allow flexibility for Windows, Linux, or Mac virtual machines. Choosing the right virtualization platform ensures smooth lab operations and provides a scalable foundation for more complex cybersecurity scenarios. Beginners benefit from platforms with extensive community support, as it simplifies troubleshooting and configuration guidance. Efficient platform selection also minimizes technical interruptions and allows learners to focus on hands-on security exercises while experimenting with multiple OS environments in parallel. Setting Up Virtual Machines Virtual machines (VMs) are the core of any cybersecurity lab. They provide isolated environments where learners can test exploits, perform penetration tests, and analyze system behavior without endangering real systems. Ethical Hacking Training Institute recommends starting with Kali Linux for penetration testing, Windows Server for administrative exercises, and Ubuntu for network simulations. Allocating appropriate RAM, CPU, and storage ensures smooth operation, especially when running multiple VMs concurrently. Taking snapshots before performing any tests allows learners to restore machines to their original state, preventing permanent misconfigurations or corruption during experiments. Beginners can follow step-by-step tutorials to learn VM deployment and gradually expand their lab capabilities. Install a host OS such as Windows, Linux, or MacOS to run virtualization software efficiently. Create separate virtual machines for different purposes, such as penetration testing, system administration, or web application testing. Allocate sufficient CPU cores, RAM, and storage for each VM to ensure performance stability. Enable snapshots and backup options to restore the system to a clean state after exercises. Install guest additions or VM tools to improve integration and performance between host and guest OS.
Configure virtual networks to simulate isolated or interconnected systems for advanced testing scenarios. Regularly update each VM to include the latest security patches and tools for effective learning. Correctly setting up virtual machines provides a realistic learning environment, allowing repeated practice and experimentation. Students can safely simulate real attacks and analyze system behavior without affecting live networks or systems. Proper VM setup also facilitates experimenting with multiple operating systems, enhancing overall cybersecurity knowledge and practical experience. Configuring the Network Create isolated networks within the virtualization platform to safely test attacks and vulnerabilities. Use NAT, bridged, or host-only adapters to control network access and prevent accidental exposure. Set up multiple subnets to simulate enterprise or cloud environments for more complex testing scenarios. Monitor network traffic using Wireshark or similar tools to analyze communication between virtual machines. Practice penetration testing in controlled network setups to understand real-world security challenges. Webasha Technologies provides training on network simulation techniques for ethical hacking labs.
Document network configurations for reproducibility and to track lab exercises over time. Network configuration is critical for simulating realistic attack scenarios and understanding how traffic flows between systems. Properly isolated networks also ensure the host machine remains secure during experiments. Students gain hands-on experience with routing, firewall rules, and packet analysis, which strengthens their practical cybersecurity skills and prepares them for professional challenges.
Installing Security Tools Security tools form the backbone of any ethical hacking lab. Tools like Metasploit, Nmap, Wireshark, John the Ripper, and Hydra allow students to discover vulnerabilities, analyze traffic, and perform controlled exploits. Beginners often start with individual tools to understand functionality and gradually combine them for complete penetration testing scenarios. Cybersecurity Training Institute recommends following structured exercises while practicing with tools, ensuring that learners gain both theoretical knowledge and hands-on skills. Using Nmap tutorials , students can learn network scanning techniques to identify open ports, services, and potential vulnerabilities in a safe environment. Install Metasploit for exploiting vulnerabilities and testing payloads on lab machines. Use Nmap for discovering network hosts, services, and security weaknesses. Wireshark enables packet capture and traffic analysis for network monitoring exercises. Hydra and John the Ripper are essential for learning password cracking techniques. Deploy OWASP tools like WebGoat for practicing web application security testing. Keep all tools updated to cover the latest exploits and vulnerabilities. Document each tool usage and findings to track learning progress effectively. Proper tool installation and structured practice ensure learners gain hands-on expertise. Using these tools in controlled virtual labs mirrors real-world ethical hacking scenarios, enhancing practical skills. Structured exercises help beginners transition from theoretical knowledge to practical application, building confidence and preparing them for real cybersecurity environments. Creating Vulnerable Machines Deploy intentionally vulnerable machines like Metasploitable to practice exploitation techniques safely. Use older Windows versions to simulate environments with known vulnerabilities. Install OWASP WebGoat to practice web application attacks and secure coding techniques. Configure vulnerable services such as FTP, SSH, and HTTP for practical learning. Ethical Hacking Training Institute provides exercises for safely exploiting vulnerabilities on test machines. Use snapshots before performing attacks to ensure easy recovery of machines. Simulate multi-layer attacks by connecting vulnerable machines across isolated virtual networks. Practicing on intentionally vulnerable machines allows learners to explore real-world attack techniques in a controlled, safe environment. This method encourages critical thinking, problem-solving, and analytical skills. Repeated exercises on these machines help build confidence, understanding, and the ability to anticipate potential security threats in professional scenarios. Maintaining the Lab Update all virtual machines regularly to ensure security and functionality. Reset machines to snapshots after each session to maintain a clean environment. Document all lab exercises, configurations, and outcomes for reproducibility. Backup VMs and configurations to prevent data loss or corruption. Monitor system resources such as RAM and CPU to avoid performance issues during practice. Cybersecurity Training Institute emphasizes disciplined lab maintenance for consistent learning outcomes. Maintain network isolation to prevent accidental exposure to the host machine or external networks. Proper lab maintenance ensures that students can continue learning effectively without interruptions or technical failures. Regular updates and backups prevent potential loss of data and corrupted lab setups.
Documenting exercises and configurations helps learners track their progress and replicate scenarios accurately, improving both skills and confidence in cybersecurity practice. Conclusion Setting up a virtual lab is crucial for anyone pursuing a career in cybersecurity or ethical hacking. It provides a safe and realistic environment to learn, experiment, and develop practical skills. By carefully selecting a virtualization platform, configuring VMs and networks, installing security tools, creating vulnerable machines, and maintaining the lab properly, learners can simulate real-world attack scenarios safely. Institutes like Ethical Hacking Training Institute, Webasha Technologies, and Cybersecurity Training Institute offer structured guidance and mentorship, ensuring students gain the skills required for professional cybersecurity roles. Frequently Asked Questions Why do I need a virtual lab for cybersecurity? A virtual lab provides a safe space to practice ethical hacking, penetration testing, and security analysis without risking real systems or networks. It allows experimentation and learning in a controlled environment. Which virtualization platforms are best for a lab? VMware, VirtualBox, and Hyper-V are widely used for cybersecurity labs, providing flexibility, stability, and features like snapshots and networking options for safe testing. What OS should I install on my lab VMs? Kali Linux, Ubuntu, and Windows Server are popular choices. Each OS allows students to practice different security techniques, from penetration testing to system administration. How do I practice hacking safely? Use isolated virtual machines and intentionally vulnerable environments. Never test attacks on real-world systems without explicit permission. What tools are essential for a virtual lab? Metasploit, Nmap, Wireshark, Hydra, John the Ripper, and OWASP WebGoat are critical tools for learning practical ethical hacking skills. Can I use my personal computer for a lab? Yes, provided it has sufficient resources to run virtual machines and is properly isolated from your main network to prevent accidental exposure. What is Metasploitable? Metasploitable is a deliberately vulnerable virtual machine designed to practice penetration testing techniques safely. How do I reset my lab after experiments? Use VM snapshots to restore machines to their clean state after testing. This ensures the environment is ready for new exercises. Can I connect lab VMs to the internet? Yes, using NAT or controlled bridged connections. Isolated networks are recommended for practicing attacks without affecting the host or external systems. How many VMs do I need for a lab? Start with 2–3 VMs for beginner exercises and gradually increase as your skills progress to cover advanced penetration testing scenarios. Are there online labs available? Yes, Ethical Hacking Training Institute and other providers offer cloud-based lab environments for remote practice and guided exercises.
What is the role of Webasha Technologies in training? They offer structured lab exercises, tutorials, and mentoring to help learners practice cybersecurity techniques in a safe environment. Do I need internet to use a lab? Internet is required for updates, tool downloads, and accessing tutorials. However, the lab itself can run offline for exercises once tools are installed. How can I track my progress in a virtual lab? Maintain logs of exercises, document configurations, save snapshots, and review results to track improvement and replicate experiments. Is building a virtual lab expensive? No, free virtualization platforms and open-source tools allow learners to set up an effective lab without significant cost, making it accessible for beginners.
Choosing the right virtualization platform ensures smooth lab operations and provides a scalable foundation for more complex cybersecurity scenarios. Beginners benefit from platforms with extensive community support, as it simplifies troubleshooting and configuration guidance. Efficient platform selection also minimizes technical interruptions and allows learners to focus on hands-on security exercises while experimenting with multiple OS environments in parallel. Setting Up Virtual Machines Virtual machines (VMs) are the core of any cybersecurity lab. They provide isolated environments where learners can test exploits, perform penetration tests, and analyze system behavior without endangering real systems. Ethical Hacking Training Institute recommends starting with Kali Linux for penetration testing, Windows Server for administrative exercises, and Ubuntu for network simulations. Allocating appropriate RAM, CPU, and storage ensures smooth operation, especially when running multiple VMs concurrently. Taking snapshots before performing any tests allows learners to restore machines to their original state, preventing permanent misconfigurations or corruption during experiments. Beginners can follow step-by-step tutorials to learn VM deployment and gradually expand their lab capabilities. Install a host OS such as Windows, Linux, or MacOS to run virtualization software efficiently. Create separate virtual machines for different purposes, such as penetration testing, system administration, or web application testing. Allocate sufficient CPU cores, RAM, and storage for each VM to ensure performance stability. Enable snapshots and backup options to restore the system to a clean state after exercises. Install guest additions or VM tools to improve integration and performance between host and guest OS. Configure virtual networks to simulate isolated or interconnected systems for advanced testing scenarios. Regularly update each VM to include the latest security patches and tools for effective learning. Correctly setting up virtual machines provides a realistic learning environment, allowing repeated practice and experimentation. Students can safely simulate real attacks and analyze system behavior without affecting live networks or systems. Proper VM setup also facilitates experimenting with multiple operating systems, enhancing overall cybersecurity knowledge and practical experience. Configuring the Network Create isolated networks within the virtualization platform to safely test attacks and vulnerabilities. Use NAT, bridged, or host-only adapters to control network access and prevent accidental exposure. Set up multiple subnets to simulate enterprise or cloud environments for more complex testing scenarios. Monitor network traffic using Wireshark or similar tools to analyze communication between virtual machines. Practice penetration testing in controlled network setups to understand real-world security challenges. Webasha Technologies provides training on network simulation techniques for ethical hacking labs.
Document network configurations for reproducibility and to track lab exercises over time. Network configuration is critical for simulating realistic attack scenarios and understanding how traffic flows between systems. Properly isolated networks also ensure the host machine remains secure during experiments. Students gain hands-on experience with routing, firewall rules, and packet analysis, which strengthens their practical cybersecurity skills and prepares them for professional challenges.
Installing Security Tools Security tools form the backbone of any ethical hacking lab. Tools like Metasploit, Nmap, Wireshark, John the Ripper, and Hydra allow students to discover vulnerabilities, analyze traffic, and perform controlled exploits. Beginners often start with individual tools to understand functionality and gradually combine them for complete penetration testing scenarios. Cybersecurity Training Institute recommends following structured exercises while practicing with tools, ensuring that learners gain both theoretical knowledge and hands-on skills. Using Nmap tutorials , students can learn network scanning techniques to identify open ports, services, and potential vulnerabilities in a safe environment. Install Metasploit for exploiting vulnerabilities and testing payloads on lab machines. Use Nmap for discovering network hosts, services, and security weaknesses. Wireshark enables packet capture and traffic analysis for network monitoring exercises. Hydra and John the Ripper are essential for learning password cracking techniques. Deploy OWASP tools like WebGoat for practicing web application security testing. Keep all tools updated to cover the latest exploits and vulnerabilities. Document each tool usage and findings to track learning progress effectively. Proper tool installation and structured practice ensure learners gain hands-on expertise. Using these tools in controlled virtual labs mirrors real-world ethical hacking scenarios, enhancing practical skills. Structured exercises help beginners transition from theoretical knowledge to practical application, building confidence and preparing them for real cybersecurity environments. Creating Vulnerable Machines Deploy intentionally vulnerable machines like Metasploitable to practice exploitation techniques safely. Use older Windows versions to simulate environments with known vulnerabilities. Install OWASP WebGoat to practice web application attacks and secure coding techniques. Configure vulnerable services such as FTP, SSH, and HTTP for practical learning. Ethical Hacking Training Institute provides exercises for safely exploiting vulnerabilities on test machines. Use snapshots before performing attacks to ensure easy recovery of machines. Simulate multi-layer attacks by connecting vulnerable machines across isolated virtual networks. Practicing on intentionally vulnerable machines allows learners to explore real-world attack techniques in a controlled, safe environment. This method encourages critical thinking, problem-solving, and analytical skills. Repeated exercises on these machines help build confidence, understanding, and the ability to anticipate potential security threats in professional scenarios. Maintaining the Lab Update all virtual machines regularly to ensure security and functionality. Reset machines to snapshots after each session to maintain a clean environment. Document all lab exercises, configurations, and outcomes for reproducibility. Backup VMs and configurations to prevent data loss or corruption. Monitor system resources such as RAM and CPU to avoid performance issues during practice. Cybersecurity Training Institute emphasizes disciplined lab maintenance for consistent learning outcomes. Maintain network isolation to prevent accidental exposure to the host machine or external networks. Proper lab maintenance ensures that students can continue learning effectively without interruptions or technical failures. Regular updates and backups prevent potential loss of data and corrupted lab setups.
Documenting exercises and configurations helps learners track their progress and replicate scenarios accurately, improving both skills and confidence in cybersecurity practice. Conclusion Setting up a virtual lab is crucial for anyone pursuing a career in cybersecurity or ethical hacking. It provides a safe and realistic environment to learn, experiment, and develop practical skills. By carefully selecting a virtualization platform, configuring VMs and networks, installing security tools, creating vulnerable machines, and maintaining the lab properly, learners can simulate real-world attack scenarios safely. Institutes like Ethical Hacking Training Institute, Webasha Technologies, and Cybersecurity Training Institute offer structured guidance and mentorship, ensuring students gain the skills required for professional cybersecurity roles. Frequently Asked Questions Why do I need a virtual lab for cybersecurity? A virtual lab provides a safe space to practice ethical hacking, penetration testing, and security analysis without risking real systems or networks. It allows experimentation and learning in a controlled environment. Which virtualization platforms are best for a lab? VMware, VirtualBox, and Hyper-V are widely used for cybersecurity labs, providing flexibility, stability, and features like snapshots and networking options for safe testing. What OS should I install on my lab VMs? Kali Linux, Ubuntu, and Windows Server are popular choices. Each OS allows students to practice different security techniques, from penetration testing to system administration. How do I practice hacking safely? Use isolated virtual machines and intentionally vulnerable environments. Never test attacks on real-world systems without explicit permission. What tools are essential for a virtual lab? Metasploit, Nmap, Wireshark, Hydra, John the Ripper, and OWASP WebGoat are critical tools for learning practical ethical hacking skills. Can I use my personal computer for a lab? Yes, provided it has sufficient resources to run virtual machines and is properly isolated from your main network to prevent accidental exposure. What is Metasploitable? Metasploitable is a deliberately vulnerable virtual machine designed to practice penetration testing techniques safely. How do I reset my lab after experiments? Use VM snapshots to restore machines to their clean state after testing. This ensures the environment is ready for new exercises. Can I connect lab VMs to the internet? Yes, using NAT or controlled bridged connections. Isolated networks are recommended for practicing attacks without affecting the host or external systems. How many VMs do I need for a lab? Start with 2–3 VMs for beginner exercises and gradually increase as your skills progress to cover advanced penetration testing scenarios. Are there online labs available? Yes, Ethical Hacking Training Institute and other providers offer cloud-based lab environments for remote practice and guided exercises.
What is the role of Webasha Technologies in training? They offer structured lab exercises, tutorials, and mentoring to help learners practice cybersecurity techniques in a safe environment. Do I need internet to use a lab? Internet is required for updates, tool downloads, and accessing tutorials. However, the lab itself can run offline for exercises once tools are installed. How can I track my progress in a virtual lab? Maintain logs of exercises, document configurations, save snapshots, and review results to track improvement and replicate experiments. Is building a virtual lab expensive? No, free virtualization platforms and open-source tools allow learners to set up an effective lab without significant cost, making it accessible for beginners.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/List%20of%20video%20games%20in%20development • https://docs.projectsecurity.io/e101/cyberattacksimulation/ • https://arxiv.org/abs/2412.01421 • https://github.com/Tom-Souillard/network_attack_defense_simulation • https://github.com/Danishcx/Building-a-Cyber-Fortress-SOC-Lab-for-Attack-Defense-Simulation/blob/main/README.md • https://github.com/ApurvaanshSharma/Network-Attack-Simulator • https://github.com/Manar-Hossam/cyber-shield-network-simulation • https://thehackernews.com/2024/04/network-threats-step-by-step-attack.html • https://pivitstrategy.com/network-threats-through-a-step-by-step-attack-simulation/ • https://cybertask.com/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
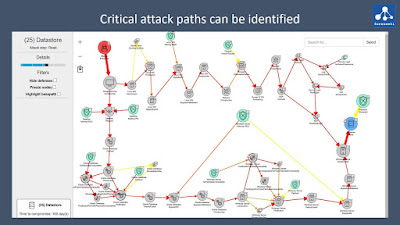
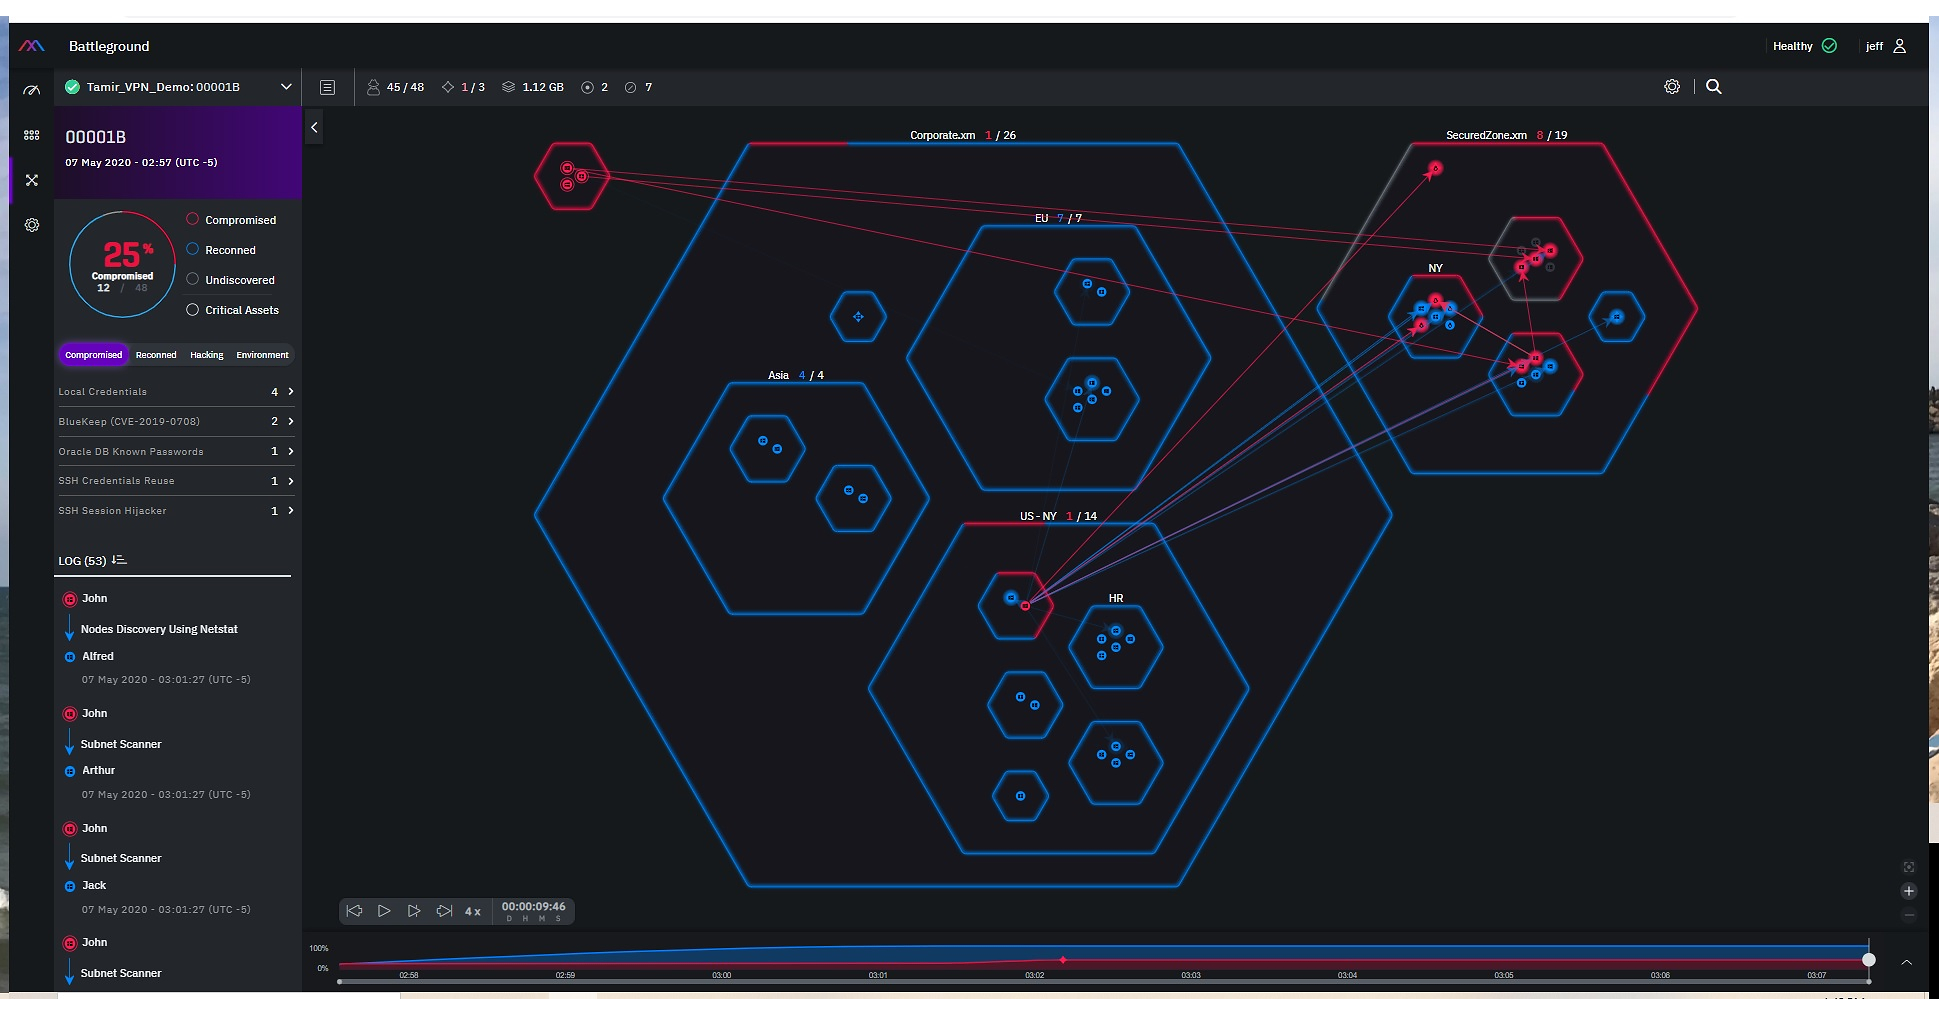
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Cyber Warfare Attack Simulation Tool In Network Sandbox.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |