Complete Technical Paper Content — DDoS Attack Detection Using Machine Learning In Software Defined Networks
Overview & System Context
Ddos Attack Detection Using Machine Learning In Software Defined Networks: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9533 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A distributed denial-of-service (DDoS) attack is a malicious attempt to disrupt the normal traffic of a targeted server, service, or network by overwhelming the target or its surrounding infrastructure with a flood of internet traffic. DDoS attacks achieve effectiveness by utilizing multiple compromised computer systems as sources of attack traffic. Exploited machines can include computers and other networked resources such as IoT devices. From a high level, a DDoS attack is like an unexpected traffic jam clogging up the highway, preventing regular traffic from arriving at its destination. It's critical to act soon after discovering a DDoS attack since it provides you the chance to avert significant disruption. The server can start to crash on waiting too long, and a full recovery might take hours. The hardest part about mitigating a DDoS attack is that often it’s virtually impossible to do so without impacting legitimate traffic. This is because attackers go to great lengths to masquerade fake traffic as real.
For enterprises operating at the edge with mission-critical activities that cannot afford downtime, DDoS mitigation as a protective layer is crucial. DDoS mitigation contributes to maintaining such activities' and services' ongoing availability. SDN allows for network design, construction, and operation. Attacks via distributed denial-of-service (DDoS) represent a serious risk to data centers. New security concerns and assaults, particularly Distributed Denial of Service (DDoS) attacks, are frequently launched against SDN networks.
[2] This work proposes a method of DDoS attack detection based on deep belief network feature extraction and LSTM model. This technique uses deep learning to extract IP packet attributes, builds an LSTM traffic prediction model, and then recognises DDoS attacks using the built-in LSTM model. Technology for detecting DDoS attacks is appropriate for this system. The model can effectively forecast the pattern of typical network traffic, spot irregularities brought on by DDoS attacks, and be used to develop more DDoS attack detection techniques in the future.
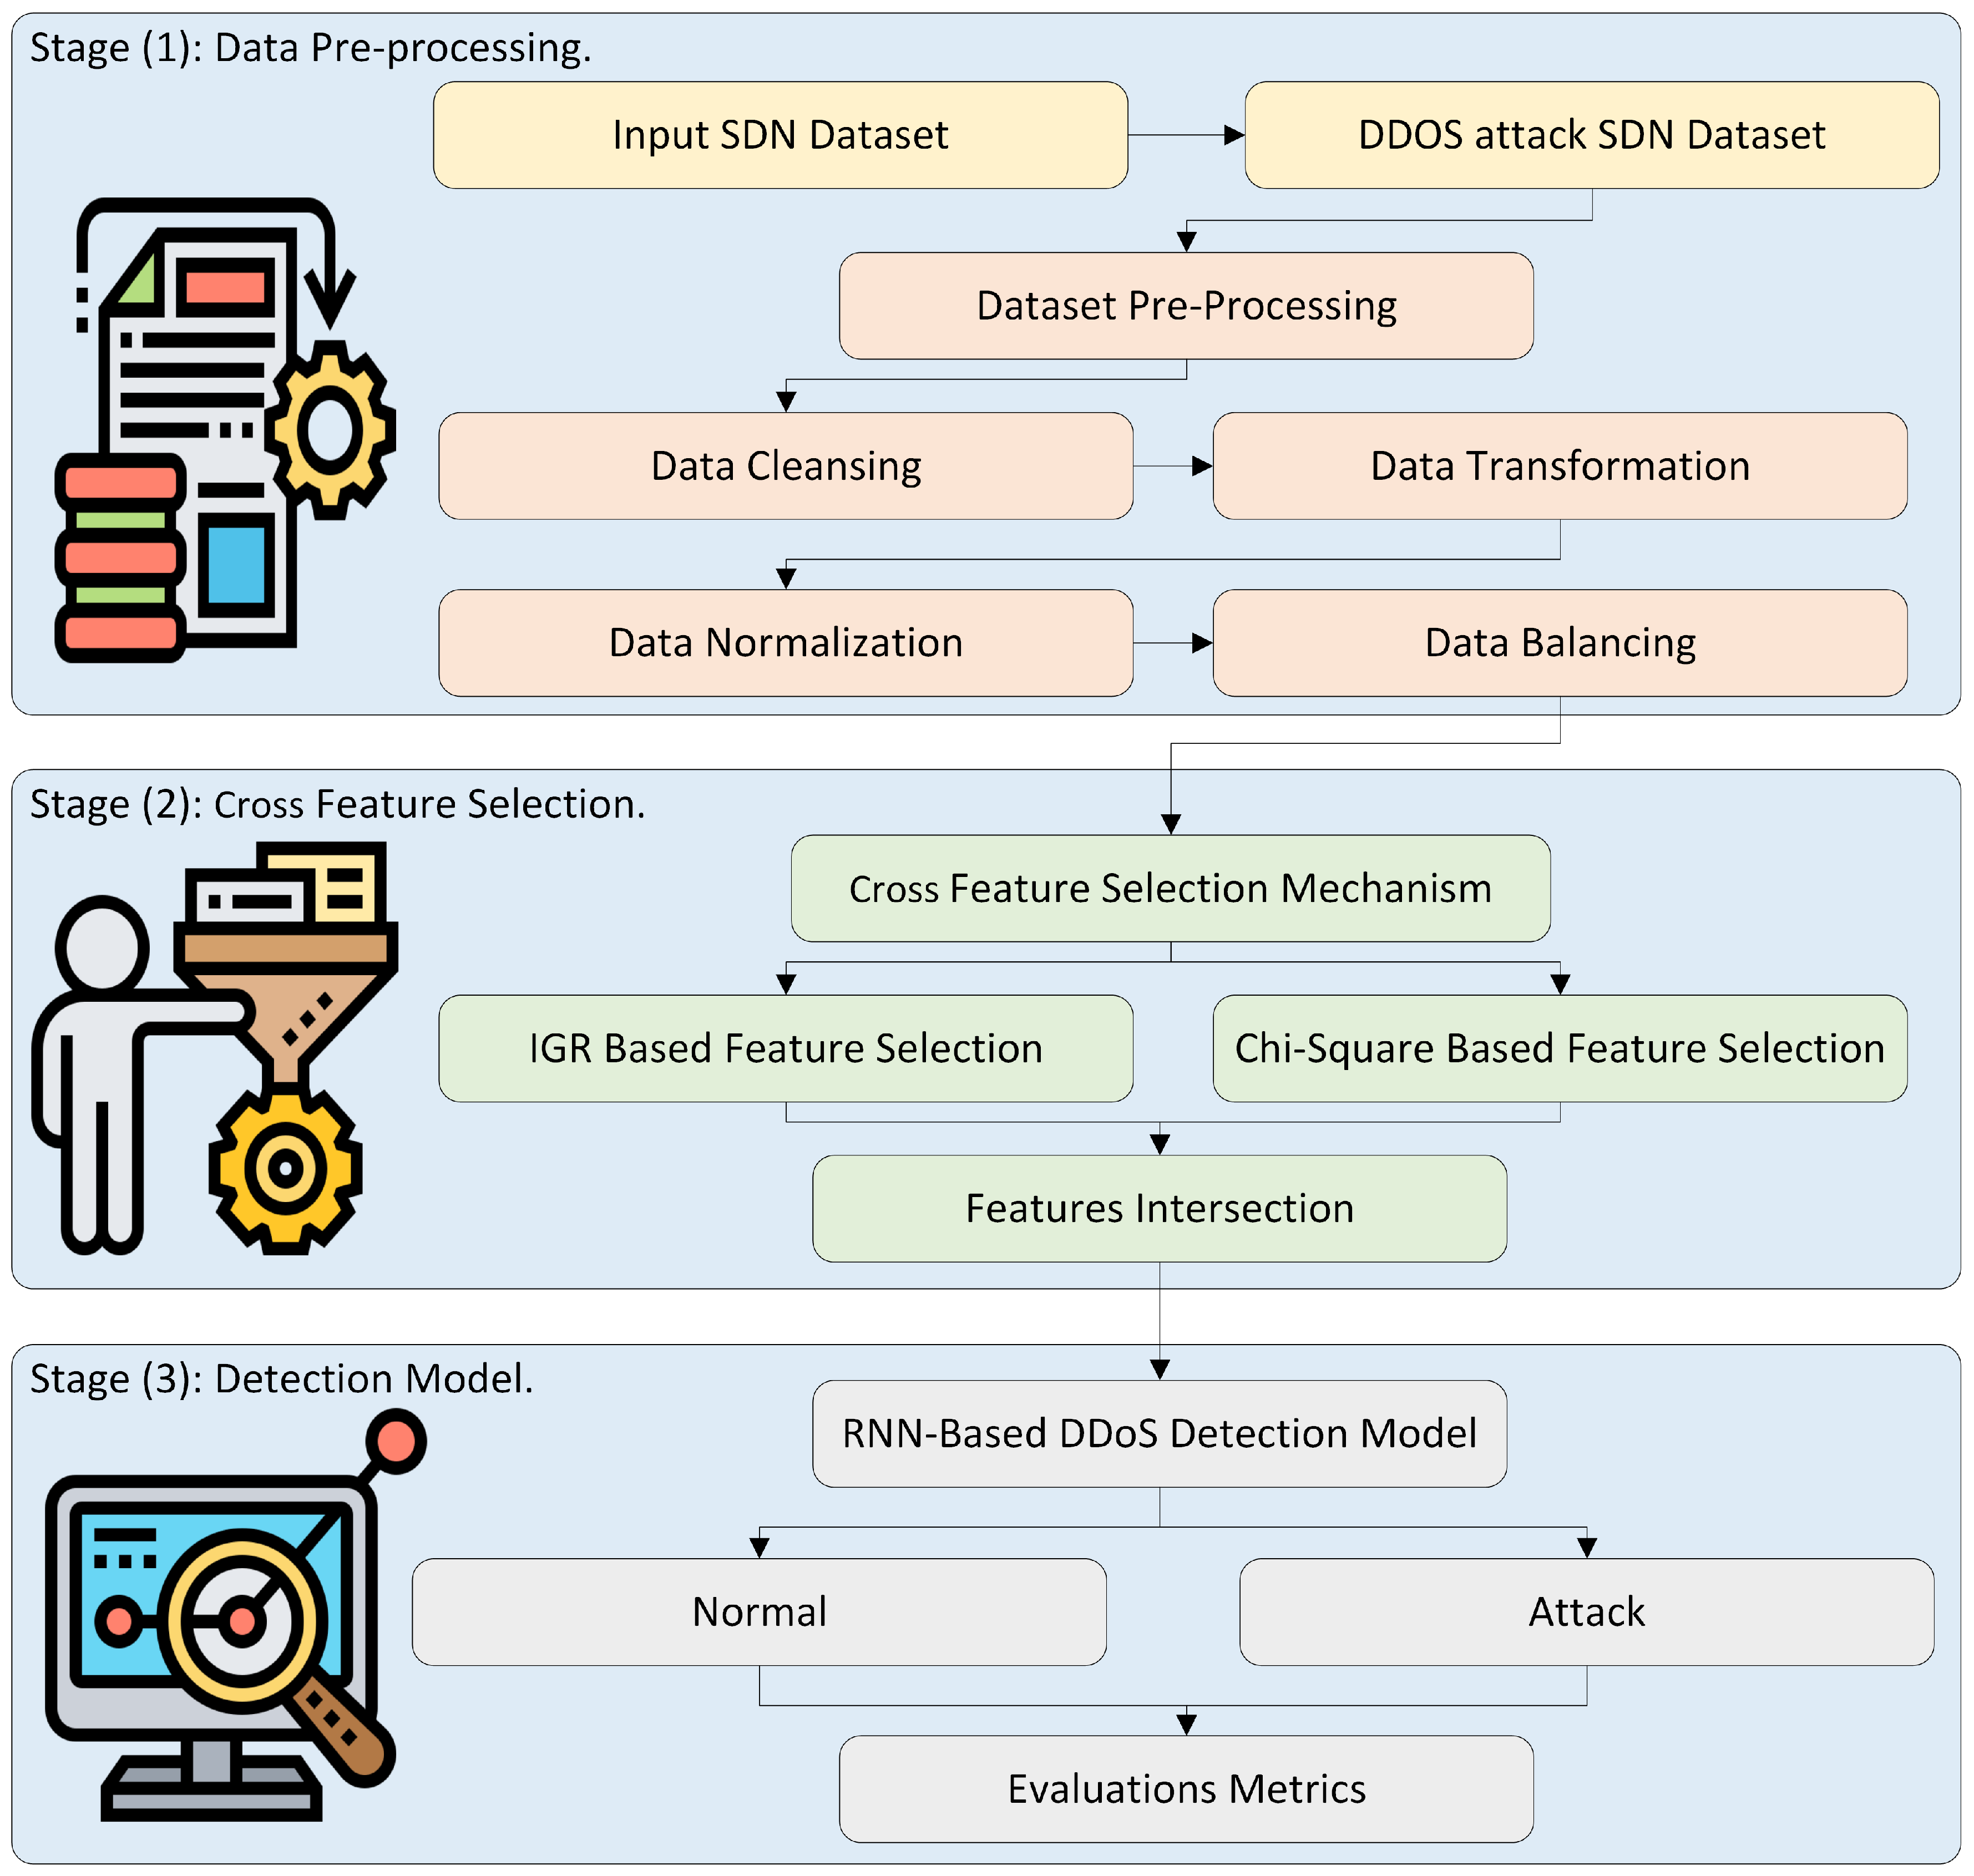
[3] In this work, the authors proposed a model which analyzes the correlation information of flows in data centers. It offers a reliable method of detecting DDoS attacks based on CKNN (K-nearest neighbors traffic categorization with correlation analysis). Figure 1: Systems | Free Full-Text | Deep Learning-Based Approach for Detecting ...
[4] This paper proposes a new model to detect DDoS attacks in SDN based on SVM . Firstly a trained Support Vector Machine (SVM) approach is used by the model to extract numerous important features from the packet-in messages and measure the distribution of each feature using entropy. Studies reveal that this technique is highly effective at both real-time DDoS mitigation and security event detection.
To achieve the goal of detection of DDoS attack and mitigation model for SDN networks, a model is build on the application plane. The architecture of implemented method consists of the flow collector module, feature extender module, anomaly detection module, and anomaly mitigation module. The task of the flow collector is to regularly collect information on traffic flow from the flow tables of each switch. These flow entries will be delivered to the feature extender, which will produce new features for each entry.
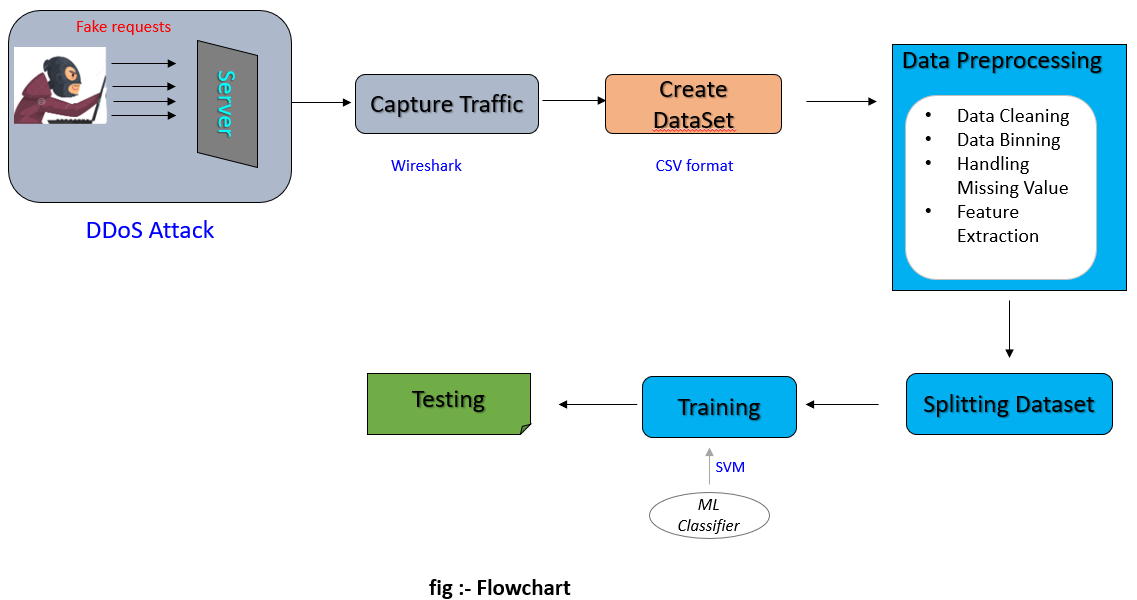
The anomaly detection module will receive the gathered data and use machine learning (ML) to perform flow-based detection and classify each flow as normal or abnormal. An aberrant flow will be sent to the Mitigation module in order to stop the source of the attack, else no action will be taken. In order to obtain traffic data, the flow collector first contacts the controller. When the controller receives a request for traffic information, it employs Figure 2: GitHub - Akash23678/Detection-Of-DDoS-Attack-Using-Machine-Learning-Model To gather data from flow tables, openflow protocol is used. Every switch connected to the controller receives a flow-stats request from the controller, which asks the switch for flow statistics. As a result, each switch responds with a flow-stats reply message that includes all flow entries from all flow tables, each entry of which includes the flow description and any associated counters. The controller then replies to this component after compiling the traffic data from all the switches.
The flow collector parses the flow information after receiving it and discards any unnecessary data. The flow identifier (flow-id) and the flow counters are the pertinent data that are kept. The source IP address, destination IP address, source MAC address, destination MAC address, TCP/UDP source port, TCP/UDP destination port, and transport protocol identification make up the seven-tuple that is referred to as the flow-id (protocol). It's crucial to remember that this tuple can be modified to meet the requirements of the network infrastructure.
Software Requirement Definition (SRS) is a comprehensive specification and description of the software requirements that must be met for the software systems to be developed successfully. Depending on the sort of demand, they may be both functional and non-functional. In order to thoroughly grasp the demands of consumers, contact between various customers and contractors is done.
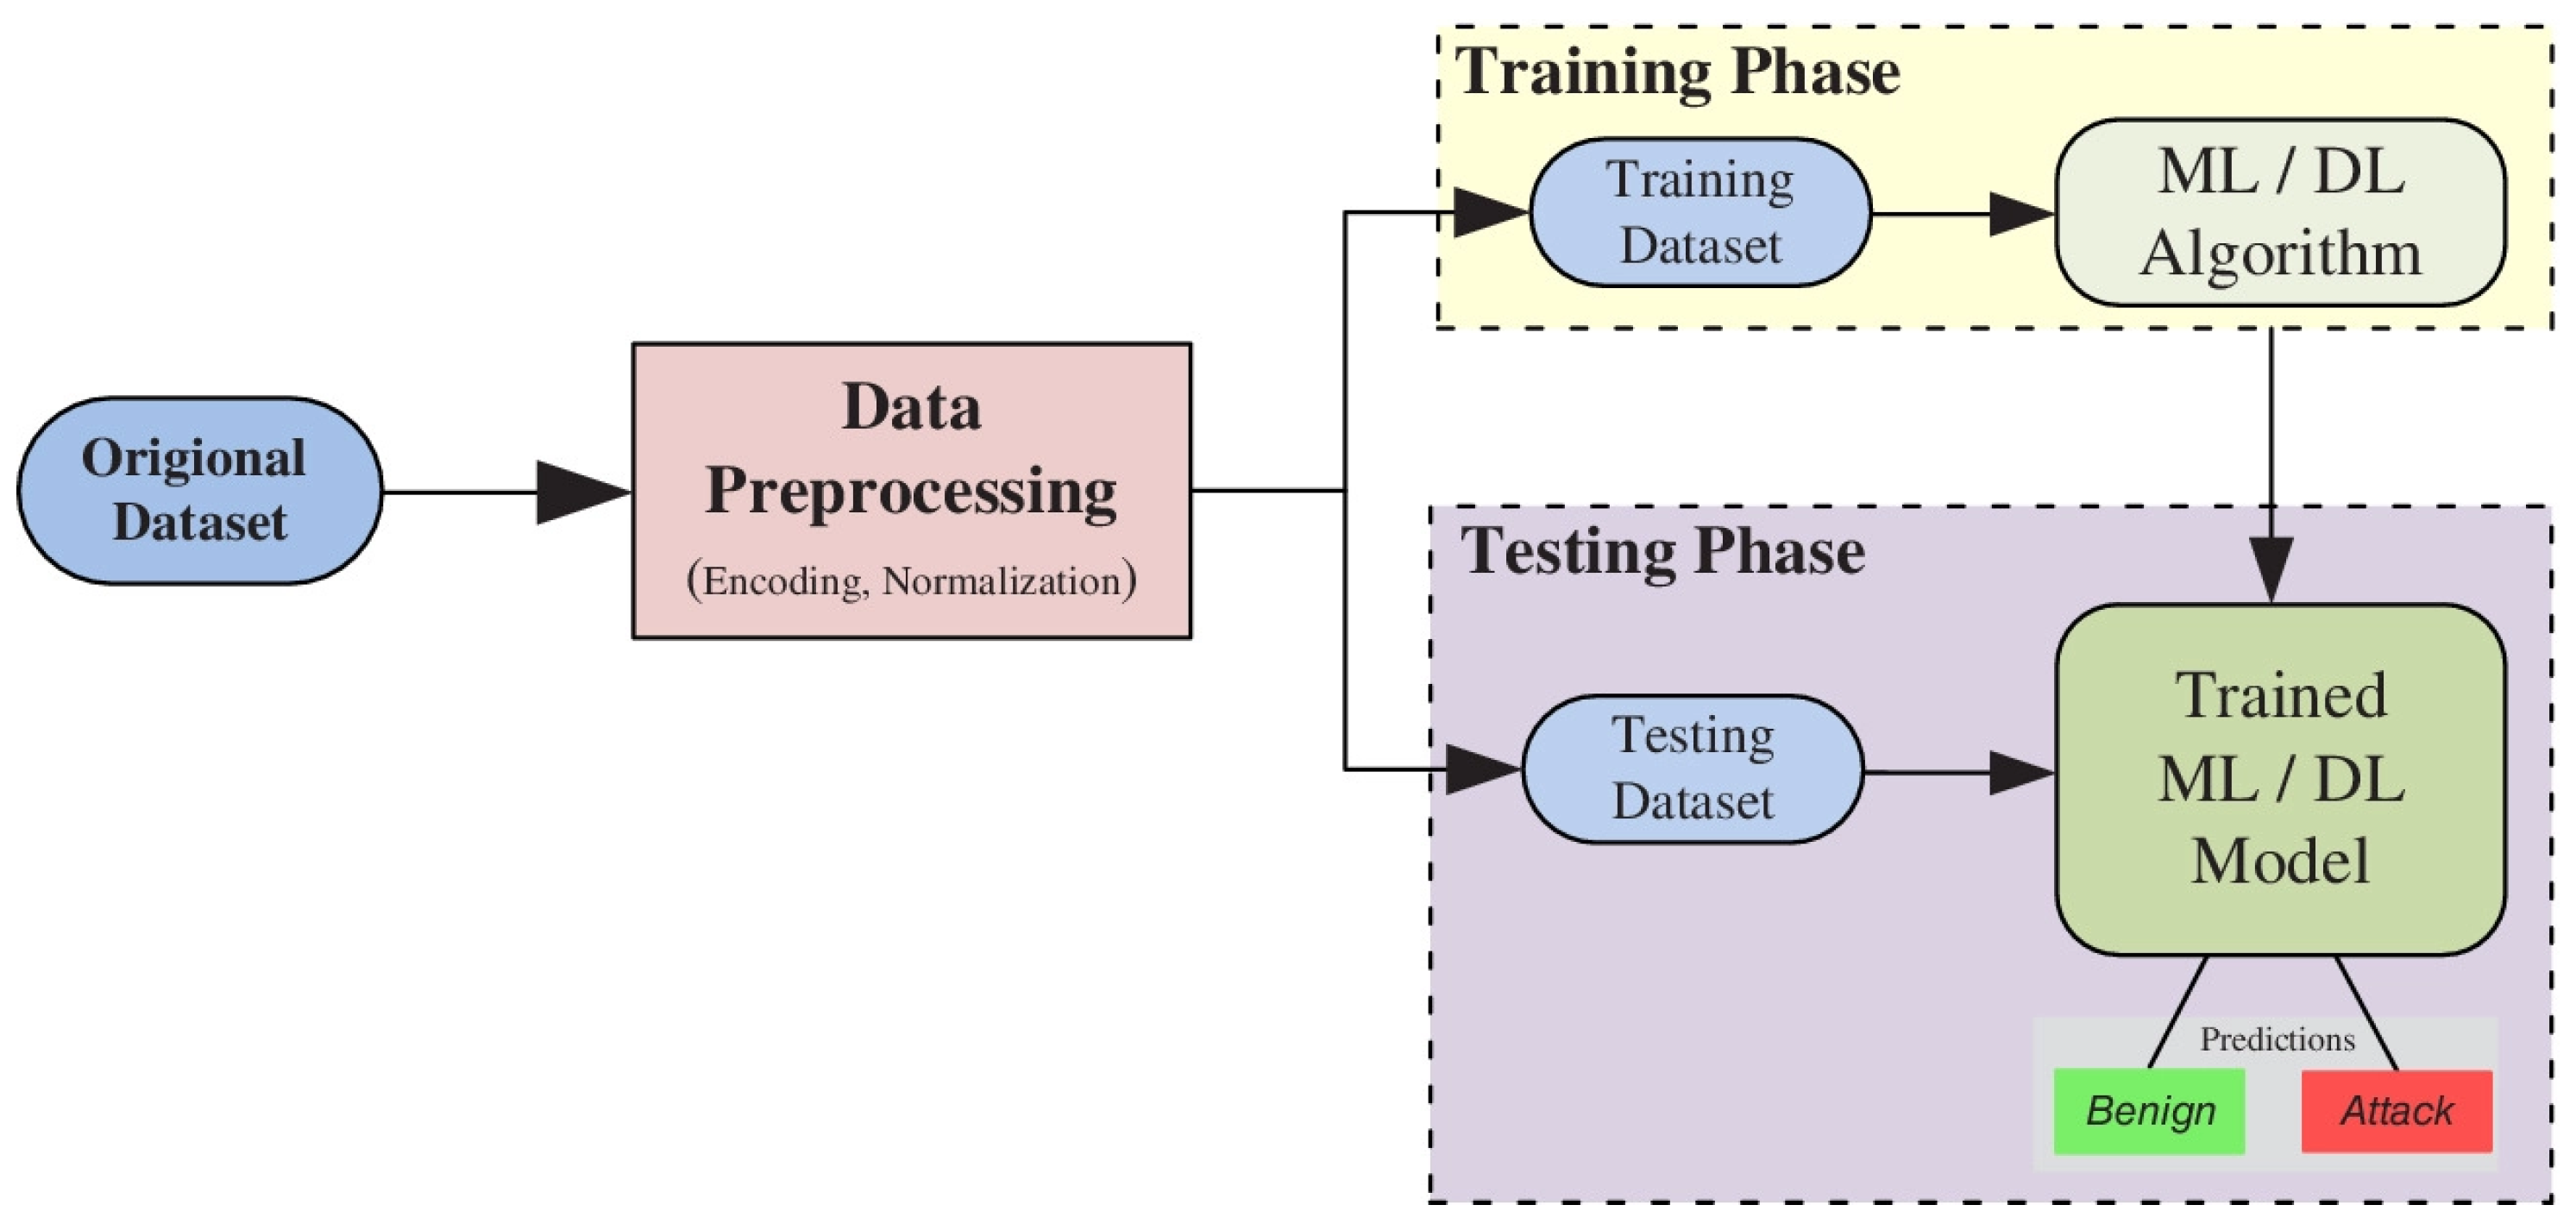
The application layer is where the network applications, such as network management, traffic engineering, and security, are implemented. Figure 3: Machine Learning Techniques to Detect a DDoS Attack in SDN: A ... The control layer represents the centralized SDN controller software that acts as the brain of the software-defined networking.
This controller resides on a server and manages policies and traffic flows throughout the network. Dataset is generated using python scripts for malicious traffic and legitimate traffic The Implemented system consists of a detection module and a mitigation module. The model is trained on the dataset that is generated .
To generate the dataset, a topology in SDN using mininet. simulated network traffic(normal traffic and anomalous traffic) is created. Then feature's source IP, destination IP, port number, and timestamp from the packets using the RYU controller are extracted. In order to obtain traffic data, the Flow Collector first contacts the controller. When the controller receives a request for traffic information, it employs To gather data from flow tables, 1use OpenFlow protocol. Every switch connected to the controller receives a flow-stats request from the controller, which asks the switch for flow statistics. As a result, each switch responds with a flow-stats reply message that includes all flow entries from all flow tables, each entry of which includes the flow description and any associated counters. The controller then answers this component after compiling the traffic data from all the switches. The Flow Collector parses the flow information after receiving it and discards any unnecessary data. The flow identifier (flow-id) and the flow counters are the pertinent data that are kept. The source IP address, destination IP address, source MAC address, destination MAC address, TCP/UDP source port, TCP/UDP destination port, and transport protocol identification make up the seven-tuple that is referred to as the flow-id (protocol). It's crucial to remember that this tuple can be modified to meet the requirements of the network infrastructure. Only three counters—the packet count, byte count, and duration—are included in the OpenFlow flow counters.
Depending on the source of the data to be studied or the method used to identify anomalous occurrences, there are several categories that might be used to classify intrusion detection. Flow-based or packet-based detection is employed depending on the data to be processed, and depending on the detection method, signature-based or anomaly-based detection can be utilized.
Flow-based detection was selected based on the source of the data to be evaluated since it would be more suited for high-speed networks and more effective than packet-based detection in terms of processing and memory overhead. Anomaly-based intrusion detection is implemented as a detection method, and more specifically, detection with ML. Once a malicious flow has been verified by the anomaly detection module, the Anomaly Mitigation module is in charge of implementing mitigation measures to prevent network disruption or performance degradation. In the framework, attack at its source is stopped. The preventing attacks caused by IP spoofing does not necessarily involve banning the attackers' IP addresses. For proof-of-concept purposes, in this case, attacker's Ethernet address is blocked.
After designing the attack detection and mitigation method,the results are tested and evaluated. The evaluation of the framework includes the evaluation of the different ML algorithms, and a comparison of the different models used. The below table shows the accuracies of different models used: From the above table, it can be seen that random forest gives the best accuracy to categorize normal and malicious traffic.
In order to evaluate the performance of the model, a test is performed by process of online traffic classification and attack mitigation. For mitigating attacks, firewall rules were set to block attacks that were detected. Thus, for every flow detected as malicious, a firewall rule is installed to block the Ethernet address from which the attack is launched. The Python code of the generated prototype is implemented , and then normal traffic is generated as background traffic, and DDoS attack is detected.
Results from the below graph shows that after the traffic is launched it is collected and detected and firewall rules were installed to block the source attack.After this point all the attacks generated from the source were blocked without affecting normal traffic. In this work, a random forest machine learning algorithm is used to develop a model that can automatically identify and mitigate DDoS assaults in SDN networks. All of the traffic flow entries are regularly collected by the model, which then extracts the native flow features and expands them by including additional features. A detection module uses five criteria to categorize each flow as normal or anomalous. When an attack is discovered, its source is prevented. Three ML algorithms were assessed with regard to the classification ML method utilized in the detection module, including random forest, SVM, and KNN. The outcomes of the experiment demonstrated that RF is the best classifier for the generated network. Without disrupting regular traffic, the implemented methodology proved effective at swiftly and correctly identifying and thwarting threats.
[1] Dong Li,Chang Yu, Qizhao Zhou and Junqing Yu .”Using SVM to Detect DDoS Attacks in SDN Network.” 2018 IOP Conf. Ser.: Mater. Sci. Eng. 466 012003,2018 . [2] Yijie Li, Boyi Liu, Shang Zhai and Mingrui Chen ,”DDoS attack detection method based on feature extraction of deep belief networks.”,IOP Conference Series: Earth and Environmental Science, Volume 252, Issue 3,2019.
[3] Peng Xiao,Wenyu Qu,Heng Qi ,Zhiyang Li.”Detecting DDoS attacks against data centers with correlation analysis.”,Computer Communications 67,2015. [4] Fatima Khashab, Joanna Moubarak, Antoine Feghali , and Carole Bassil.”DDoS Attack Detection and Mitigation in SDN using Machine Learning”,IEEE 7th International Conference on Network Softwarization (NetSoft),2021.
2. System Architecture & Core Working Principles [5] Bawany NZ, Shamsi JA, Salah K. DDoS attack detection and mitigation using SDN: methods, practices, and solutions. Arabian Journal for Science and Engineering. 2017 Feb;42(2):425-41. [6] Dharma, N.G., Muthohar, M.F., Prayuda, J.A., Priagung, K. and Choi, D., 2015, August. Time-based DDoS detection and mitigation for SDN controller. In 2015 17th Asia-Pacific Network Operations and Management Symposium (APNOMS) (pp.
550-553). IEEE. [7] da Silveira Ilha, A., Lapolli, A.C., Marques, J.A. and Gaspary, L.P., 2020. Euclid: A fully in-network, P4-based approach for pp.3121-3139. [8] Singh, J. and Behal, S., 2020. Detection and mitigation of DDoS attacks in SDN: A comprehensive review, research challenges and future directions. Computer Science Review, 37, p.100279.
[9] Mihoub A, Fredj OB, Cheikhrouhou O, Derhab A, Krichen M. Denial of service attack detection and mitigation for internet of things using looking-back-enabled machine learning techniques. Computers & Electrical Engineering. 2022 Mar 1;98:107716. [10] Miao, R., Yu, M. and Jain, N., 2014. Nimbus: cloud-scale attack detection and mitigation. Acm sigcomm computer communication review, 44(4), pp.121-122.
[11] Srinivasan, Karthik, Azath Mubarakali, Abdulrahman Saad Alqahtani, and A. Dinesh Kumar. "A survey on the impact of DDoS attacks in cloud computing: prevention, detection and mitigation techniques." In Intelligent Communication Technologies and Virtual Mobile Networks, pp. 252-270. Springer, Cham, 2019. [12] Kautish, Sandeep, A. Reyana, and Ankit Vidyarthi. "SDMTA: Attack Detection and Mitigation Mechanism for DDoS [13] Gadze, James Dzisi, Akua Acheampomaa Bamfo-Asante, Justice Owusu Agyemang, Henry Nunoo-Mensah, and Kwasi Adu-Boahen Opare. "An investigation into the application of deep learning in the detection and mitigation of DDOS attack on SDN controllers." Technologies 9, no. 1 (2021): [14] Jaramillo, L.E.S., 2018. Malware detection and mitigation techniques: lessons learned from Mirai DDOS attack. Journal of Information Systems Engineering & Management, 3(3), p.19.
[15] Al-Duwairi, B., Al-Kahla, W., AlRefai, M.A., Abedalqader, Y., Rawash, A. and Fahmawi, R., 2020. SIEM-based detection SDN networks (Software Defined Networking ) are exposed to new security threats and attacks, especially Distributed Denial of Service (DDoS) attacks. For this aim, we have proposed a model able to detect and mitigate attacks automatically in SDN networks using Machine Learning (ML) Thank you for visiting nature.com. You are using a browser version with limited support for CSS. To obtain the best experience, we recommend you use a more up to date browser (or turn off compatibility mode in Internet Explorer). In the meantime, to ensure continued support, we are displaying the site without styles and JavaScript.
Software-defined networks (SDNs) have been growing rapidly due to their ability to provide an efficient network management approach compared to traditional methods. However, one of the major challenges facing SDNs is the threat of Distributed Denial of Service (DDoS) attacks, which can severely impact network availability. Detecting and mitigating such attacks is challenging, given the constantly evolving range of attack techniques. In this paper, a novel hybrid approach is proposed that combines statistical methods with machine-learning capabilities to address the detection and mitigation of DDoS attacks in SDN environments. The statistical phase of the approach utilizes an entropy-based detection mechanism, while the machine-learning phase employs a clustering mechanism to analyze the impact of active users on the entropy of the system.
The k-means algorithm is used for clustering. The proposed approach was experimentally evaluated using three modern datasets, namely, CIC-IDS2017, CSE-CIC-2018, and CICIDS2019. The results demonstrate the effectiveness of the system in detecting and blocking sudden and rapid attacks, highlighting the potential of the proposed approach to significantly enhance security against DDoS attacks in SDN environments.
A hybrid machine learning approach for detecting DDoS attacks in software-defined networks Distributed denial-of-service (DDOS) attack detection using supervised machine learning algorithms An efficient federated learning based defense mechanism for software defined network cyber threats through machine learning models SDN is a cutting-edge approach to network management architecture that enhances adaptability, programmability, and responsiveness to dynamic service and application needs. It centralizes the control plane, managing data traffic routing and communication between network parts. Traditional network topologies integrate control planes into routers and switches, while SDN control is centralized in a software-based controller, with control and data planes separated 1 .
The intentional attempt to disrupt traffic on the network is known as a DDoS attack. Disrupting the availability and quality of service (QoS) of essential services by flooding the targeted system’s bandwidth and resources 2 . Attackers exploit SDN's centralized control plane, a single point of failure, to create undetected traffic patterns, making detection and mitigation of DDoS attacks challenging 3 .
Although SDNs are more flexible and manageable, because of their centralized control and programmable nature, they are also vulnerable to DDoS attacks. Due to the dynamic and complicated nature of network traffic patterns and the attackers' constantly changing techniques. It might be difficult to detect and mitigate these attacks in SDN systems. Figure 1 shows the DDoS attack mitigation main steps: traffic routing, attack fingerprint detection, response, and machine learning adaptation 4 . Lately, DDoS attacks have become more challenging to detect due to their variety. For example, multi-vector attacks, where a combination of multiple attack protocols is common. Therefore, more robust defense techniques are required.
The umbrella of DDoS detection and mitigation is wide. It includes several approaches, such as statistical-based ones, that aim to protect networks by analyzing and collecting flow-related statistics 5 . They can be applied in several ways, such as entropy-based techniques, trust management, time-series analysis, and anomaly detection. However, these methods are facing limitations in accurately distinguishing normal and malicious traffic and adjusting to emerging threats. This may lead to potential false positives or false negatives 6 .
Machine learning (ML) algorithms showed a promising potential for detecting and mitigating DDoS attacks 7 . These approaches can analyze network traffic in real time, identify malicious behavior, and adapt detection models based on real-time network data. In addition, they can handle large volumes of network data and detect zero-day attack patterns. It makes them an effective defense against evolving and sophisticated DDoS attacks. On the other hand, ML-based DDoS detection approaches face limitations due to imbalanced datasets and the dynamic nature of attacks 8 . Imbalances can lead to biased behavior and reduced accuracy in recognizing novel attack patterns as discussed by Ullah et al. 9 . Continuous model retraining and adaptation to evolving threats are necessary to maintain efficacy 10 . ML presents an added privilege to traditional detection techniques since there is no single detection method that can provide 100% accuracy 11 .
Blockchain technology is proposed for DDoS detection and mitigation, enhancing network security, scalability, and performance. However, their use in DDoS detection and mitigation faces challenges like potential latency and scalability 12 . The motivation behind this research is to develop a novel model that improves DDoS attack detection and mitigation in SDN networks by utilizing system entropy and ML clustering techniques. System entropy, a measure of disorder or randomness within a system, presents valuable details regarding the normal behavior of network traffic. Anomalies indicative of DDoS attacks can be identified by tracking variations in entropy levels.
However, depending only on statistical techniques, such as entropy-based detection, could not be accurate or responsive enough, especially in large-scale and dynamic SDN systems 6 . In addition to complementing the statistical method, ML clustering techniques like the K-means algorithm enable the analysis of complex patterns and the identification of anomalous network activity groups.
The combination of system entropy with ML clustering techniques aims to create a comprehensive defense and address several key challenges in DDoS attack detection and mitigation: Real-time Detection: The model can identify DDoS attacks in real-time, allowing for quick response and mitigation measures, by continuously monitoring system entropy and utilizing machine learning clustering methods.
Adaptability: DDoS attack techniques are always changing; therefore, detection systems must adjust and detect new attack patterns. By using machine learning clustering techniques, the model's resilience against new threats is increased since it may dynamically modify its detection skills in response to observed network behavior. Scalability: Several network devices and a variety of traffic patterns are common in SDN systems. The suggested approach is made to be scalable to manage the complexity and volume of network traffic, providing accurate detection and extensive coverage throughout the network.
3. Software Implementation, Frameworks & Protocols Surveying the state-of-the-art literature on detecting intrusions in SDN environments and analyzing the research gap. Proposing a novel approach that combines a statistical entropy-based technique with an ML one for the effective detection and mitigation of DDoS attacks. This leads to a comprehensive SDN defense mechanism. This mechanism can mitigate attacks in real time, adapt to evolving attack strategies, and minimize false positives.
Conducting an empirical evaluation by utilizing three modern SDN datasets, i.e. CIC-IDS2017, CSE-CIC-2018, and CICIDS2019. Benchmarking with other anomaly detection approaches using three recent public datasets. Reducing false positives and minimizing the impact of false alarms on network operations by combining system entropy with machine learning clustering.
Enhancing the efficiency of DDoS detection while improving network resilience and security posture in the face of evolving cyberattacks. The remaining of this paper is as follows, " Related work " section discusses the related work. " Methods " section demonstrates the proposed methodology for DDoS detection and mitigation. " Evaluation scheme " section provides an in-depth analysis of the evaluation environment used in this study, outlining the dataset, data preprocessing methodologies, and performance metrics for transparent analysis. " Results " section describes the experimental setup and proposed methodology evaluation and compares the results with the state-of-the-art approaches. Finally, the conclusion is provided in Section " Conclusion and future work " in addition to further probable directions for future research.
This section examines different defense mechanisms for detecting DDoS attacks. It emphasizes the significance of statistical, machine learning, deep learning, and blockchain approaches. The survey of the literature on DDoS attacks detection and mitigation techniques, as listed in the introduction section, follows the methodological approaches detailed in the literature review methods outlined in Saied et al 13 .
Statistical-based attack detection and mitigation methods aim to protect the network by analyzing and collecting flow-related statistics. This is achieved by generating a statistical model for regular traffic to identify malicious flows 5 . Koay et al. 14 proposed a novel method to enhance the accuracy of detecting Distributed Denial of Service (DDoS) attacks by introducing a comprehensive set of new entropy-based features. They addressed the limitation of traditional DDoS detection systems, which often rely on a small number of features, leading to certain types of attacks being undetected. To overcome this, they introduced a multi-classifier system that combines multiple entropy-based features with machine learning classifiers.
This system improves the generality and accuracy of detecting both low-intensity and high-intensity DDoS attacks. Although this approach may cause slightly longer detection delays due to increased complexity, the trade-off is justified by the system's ability to detect a broader range of DDoS attack types, ultimately enhancing network security. Tsobdjou et al. 15 introduced a dynamic entropy threshold technique based on Chebyshev inequality, which offers improved adaptability compared to static criteria across different online scenarios. Through comparative tests, their approach showed superior performance in adjusting to changing conditions, making it promising for dynamic environments.
In a separate study, Sahoo et al. 16 proposed a method for detecting attacks on the controller by utilizing defined entropy and information distance to identify low-rate DDoS attacks. While this method effectively detected low DDoS attack traffic rates, it encountered challenges in identifying high traffic rates due to variations in network traffic flow. Despite this limitation, the proposed method contributes significantly to DDoS attack detection, especially in scenarios involving low-rate attacks.
P´erez-D´Iaz et al. 17 introduced a versatile approach for identifying and mitigating both low-rate and high-rate DDoS attack traffic within SDN networks, exhibiting behavior akin to regular traffic. The methodology relies on Intrusion Detection and Prevention Systems (IDS and IPS). Utilizing six machine learning models for DDoS classification within the IDS, a notable limitation emerges: the method incorporates a fixed threshold, rendering it ineffective in detecting low-rate DDoS attack traffic targeting multiple victims.
In contrast, our model offers several advantages for DDoS attack detection in SDN networks. Firstly, it provides flexibility in detection by dynamically adjusting clusters based on entropy values, enabling the identification of varying attack intensities and patterns, including low-rate attacks targeting multiple victims. Secondly, it facilitates the identification of anomalies in network traffic patterns by clustering traffic based on entropy values, allowing for the detection of deviations from normal behavior indicative of potential DDoS attacks. Additionally, k-means clustering is scalable and computationally efficient, making it well-suited for real-time DDoS detection in large-scale SDN networks. Finally, the model's adaptability to evolving threats is enhanced using entropy-based features and clustering, enabling it to adjust to changing attack strategies and network conditions over time.
Machine learning is a powerful technique that can be used for DDoS attack detection and mitigation. It can analyze large volumes of network traffic data and learn to identify patterns and anomalies that are associated with DDoS attacks 18 . Li et al. 19 introduced a DDoS detection model leveraging a support vector machine (SVM) algorithm, utilizing packet-in messages to acquire traffic data and extracting essential features such as the source IP address. While the model demonstrates high efficiency, its reliance on a small number of features may not adequately capture all attack behaviors. This limitation becomes apparent in scenarios where attackers embed malicious code within payload packets, leading to reduced accuracy in detecting application-level attacks. As a result, while the model efficiently processes traffic data, its effectiveness in detecting sophisticated DDoS attacks targeting application layers may be compromised.
Ye et al. 20 developed an SVM classifier-based DDoS detection strategy. The suggested detection methodology involved gathering flow status information, extracting features, and categorizing the collected feature values. Additionally, the authors created a feature extraction module to extract DDoS attack-related features for the classifier to be trained, and they used flood-based attack traffic to show how well the suggested approach worked. In comparison to previously suggested methodologies, the strategy was proven to offer a high detection accuracy and a decreased false alarm rate. However, it should be emphasized that all the previously mentioned techniques suffered from the issue of unidentified real detection effects, in addition to the previously mentioned need for manually extracting a sizable number of features for training.
Cui et al. 21 introduced a new approach for detecting and defending against DDoS attacks, grounded in cognitive-inspired computing and focusing on entropy analysis. Their method utilized switch flow table data to evaluate the entropy of data packet flows, particularly focusing on source and destination IP addresses. Through training a support vector machine (SVM), the system could generate specific DDoS attack detection modes, thereby enhancing its capability to identify and respond to different attack patterns. This cognitive-inspired computing strategy not only utilized advanced machine learning techniques but also emphasized the significance of entropy analysis in DDoS detection and mitigation. By incorporating entropy considerations into packet flow analysis, their technique provided a promising avenue for enhancing the effectiveness and adaptability of DDoS detection and defense mechanisms within network environments.
In contrast, the proposed model presents a more automated, scalable, and adaptable approach to DDoS attack detection, potentially overcoming limitations associated with SVM classifier-based strategies. Hannache et al. 22 developed a cutting-edge Neural Network-based Traffic Flow Classifier (TFC-NN) aimed at real-time detection of DDoS attacks. Their model was trained and implemented using a dataset comprising both regular and malicious traffic, and it was deployed within a real SDN architecture. Impressively, the TFC-NN achieved a remarkable global accuracy rate of 96.13%, showcasing its effectiveness in accurately discerning between normal and malicious network activity.
In another study, Cui et al. 23 utilized clustering technologies such as K-means to identify malicious traffic within network streams. They further evaluated the efficacy of their approach by assessing communication latency, detection accuracy, and defense effectiveness. By leveraging packet-in message registers to filter out malicious traffic, they demonstrated the practical applicability of their scheme in real-world network environments.
Furthermore, Gu et al. 24 introduced a sophisticated hybrid feature selection-based, semi-supervised K-means detection technique. This approach not only addressed the challenges posed by outliers and local optimality but also incorporated an enhanced density-based initial cluster center selection procedure. By integrating feature selection strategies and semi-supervised learning techniques, they aimed to enhance the robustness and accuracy of DDoS attack detection within SDN networks, highlighting the importance of advanced methodologies in mitigating cyber threats effectively.
Deep learning (DL) has shown significant promise in the field of DDoS attack detection and mitigation. DL techniques, particularly neural networks (NNs), can effectively analyze large and complex datasets, learning intricate patterns and adapting to evolving attack strategies 25 . In comparison to traditional machine learning (ML) techniques, deep neural network (DNN)-based solutions offer superior accuracy in identifying network traffic anomalies 26 . By leveraging sophisticated architectures and advanced learning algorithms, DNNs can effectively capture complex patterns and relationships within data. However, these solutions encounter challenges when dealing with large input dimensions and data volumes due to issues such as dimensionality and gradient diffusion. The gradient descent algorithm, commonly used in training DNNs, may struggle to converge efficiently in high-dimensional spaces, leading to longer training times and increased computational complexity. Furthermore, the heightened processing time and resource usage associated with analyzing network traffic data can impede the efficiency of DNN-based detection systems, particularly in real-time scenarios where rapid response is essential. Despite these challenges, the superior accuracy offered by DNNs underscores their potential to enhance network security and anomaly detection capabilities in various contexts.
Using the CICIDS 2017 dataset, Makuvaza et al. 27 created a DNN-based technique for real-time DDoS threat detection in SDN. Using less time and resources, the algorithm detects DDoS threats with a 97.59% accuracy rate. Additionally, the authors suggested a two-level security detection system based on Snort, DNN, and SVM techniques. The DNN approach was tested and trained using the KDD Cup 1999 dataset, and results showed that it was more accurate than SVM.
For detecting slow DDoS attacks in the SDN environment, a deep learning framework has been created by Nugraha et al. 28 . The model gathers and analyses traffic flow statistics using the SDN controller’s REST API. Convolutional neural network-long short-term memory (CNN-LSTM) is the basis of the model. The model performs better than other deep learning models like the Multilayer Perceptron and 1-Class Support Vector Machine, according to experimental findings. The technique, though, is time-consuming and expensive for real-time detection.
Doriguzzi-Corin et al. 29 introduced LUCID, a novel DDoS detection system designed to address computational constraints by using a one-dimensional convolutional neural network (CNN). Unlike traditional deep learning approaches, LUCID prioritizes efficiency without sacrificing accuracy. Experimental evaluations conducted on diverse datasets, including ISCX2021, CIC-IDS2017, and CSE-CIC2018, showcased remarkable results. LUCID exhibited a significant 40 × reduction in processing time compared to alternative deep learning techniques, making it highly suitable for deployment in resource-constrained environments. This efficiency enhancement underscores the system's potential to revolutionize DDoS detection by providing rapid and reliable protection against malicious attacks while minimizing computational overhead.
Liang et al. 30 employed long short-term memory (LSTM) within their DDoS detection framework, leveraging the capabilities of recurrent neural networks (RNNs) to capture intricate temporal dependencies inherent in network traffic data. LSTM networks, equipped with three gating units, excel in modeling sequential data by selectively retaining and updating information over time. This feature enables LSTM to effectively capture the implicit sequence representations present in input vectors, making it well-suited for analyzing time-series data such as network traffic patterns. Unlike conventional methods that rely on labor-intensive and error-prone feature engineering, LSTM-based approaches facilitate automated learning of flow-level patterns directly from raw data. This automation not only enhances detection accuracy but also streamlines the development process by eliminating the need for manual feature extraction, thereby paving the way for more efficient and reliable DDoS detection systems.
Cil et al. 31 introduced a traffic classification model utilizing deep neural networks (DNNs) to enhance accuracy in network traffic analysis. The model features a streamlined architecture with feature extraction stages, requiring only three fully connected layers for training completion. Experimental evaluation on the CIC-DDoS2019 dataset demonstrated impressive accuracy, reaching 95%. This highlights the effectiveness of DNN-based approaches in accurately classifying network traffic patterns, promising improved network security and anomaly detection capabilities. Moreover, the model's simplicity and high accuracy suggest its potential for practical deployment in real-world network environments, offering a valuable tool for enhancing network monitoring and defense systems.
4. Practical Deployment, Analysis & Case Studies A fully connected (FC) architecture was used in an explainable DL framework for the Industrial Internet of Things (IIoT) developed by Khan et al. 32 . An autoencoder-based detection framework that used convolutional and recurrent networks was proposed to identify cyber threats in IIoT networks. To enhance the learning of data features, the framework used a two-step sliding window (SW) method to extract temporal and spatial characteristics for attack event categorization and explanation.
When compared to modern techniques, the empirical results showed how well the framework extracted contextual elements of dangerous patterns and how robust it was in identifying malicious events. The model performed better than state-of-the-art techniques, incorporated explanation mechanisms for model decisions, and presented an inventive approach for addressing cyber threats in IIoT networks. Additionally, Khan et al. 33 introduced a deep-autoencoder-based intrusion detection system (IDS) for IIoT networks. The model, based on an LSTM auto-encoder design, accurately identified invasive events in real time.
The model outperformed existing methods, achieving accuracy rates of 97.95% and 97.62% on benchmark datasets like the gas pipeline and UNSWNB-15. Khan et al. 34 also proposed a privacy-conserving intrusion detection framework named PC-IDS, tailored for securing Contemporary Smart Power Systems (SPNs) against cyber-attacks. The model used a hybrid machine learning approach, transforming raw data into a privacy-preserving format, and identifying malicious events using a probabilistic neural network.
The framework outperformed existing methods in terms of false positive rate, detection rate, and computational processing time, enhancing SPN security and privacy. The framework achieved detection rates of 96.03% and 95.91%, demonstrating its effectiveness in enhancing SPN security. Additionally, Khan et al. 35 highlighted the importance of protecting industrial control systems (ICSs) against cyber-attacks due to their integration with IoT technologies. The paper proposed a novel intrusion detection system (IDS) model called federated-simple recurrent units (SRUs) for IoT-based ICSs. The model used simple recurrent units’ architecture to mitigate computational costs and address gradient vanishing issues. Experimental validation showed that the model accurately detected intrusions in real-time without compromising privacy or security.
In comparison, the proposed model offers scalability, efficiency, and real-time detection. It can also adapt to changing network conditions and quickly identify anomalies, reducing processing time and resource usage. The entropy-based model with k-means clustering balances accuracy and efficiency, allowing for timely detection without significant processing delays. Blockchain technology has been proposed as a potential solution for DDoS detection and mitigation 36 .
Bose et al. 37 devised a novel strategy to block DDoS attacks at the switch stage by incorporating blockchain-based encryption into the interaction channels between data and control planes. This innovative approach aims to enhance the security and resilience of SDN switches against malicious activities. Through simulation, the study illustrated the efficacy and reliability of employing blockchain technology as a defense mechanism, showcasing its potential to fortify SDN infrastructure against attackers. However, despite its promising benefits, the system exhibited certain limitations, notably unauthorized access, and data leakage, which emerged as significant drawbacks. Addressing these concerns is crucial for ensuring the comprehensive security and integrity of the SDN environment, underscoring the need for further refinement and optimization of blockchain-integrated defense mechanisms.
A confidence evaluation system with a focus on SDN and blockchain was introduced by Mathieu et al. 38 . The solution demonstrates how the SDN reduces surface attacks on the household network. The end user struggles with judgment and lacks the requisite abilities. The SDN architecture requires an appropriate access control mechanism for multiple organizations, including SDN controllers and switches. To address this issue, Durbadal et al. 39 present blockchain-based access control. The outcome demonstrates that the Blockchain-based Access Control SDN (BACC-SDN) safeguards against possible threats, which is essential for an SDN network’s security. Addressing these limitations is crucial for effective integration into DDoS detection and mitigation strategies.
In comparison to existing studies in the field, the proposed model, which integrates system entropy with machine learning clustering techniques for DDoS detection and mitigation in SDN networks, offers several significant differentiators. Integration of System Entropy: While many articles only discuss statistical or ML techniques for DDoS detection, the suggested model incorporates system entropy as a fundamental element. A measure of the network's disorder, system entropy sheds light on how network traffic typically behaves. The model improves its capacity to recognize anomalies indicative of DDoS attacks by adding entropy analysis to the detection procedure, resulting in more precise and rapid detection.
Real-Time Detection and Mitigation: Enabling real-time DDoS attack detection and mitigation is one of the main objectives of the proposed model. The model can detect anomalies and start mitigation measures promptly by continuously monitoring system entropy and applying ML clustering algorithms. This real-time responsiveness is essential for minimizing the impact of DDoS attacks on network availability and performance.
Reduced False Positives: In DDoS detection, false positives are a common challenge that can result in needless alert fatigue and resource usage. By integrating machine learning clustering techniques with system entropy, the suggested model aims to address this issue. By analyzing several aspects of network traffic and detecting abnormal behavior clusters, the model can lower false positives and enhance DDoS detection precision.
Experimental Validation: Experimental assessment of modern SDN environment-specific datasets, including CIC-IDS2017, CSE-CIC-2018, and CICIDS2019 strengthens the suggested model. These experiments show the model's practical application and performance by offering empirical evidence of its ability to identify and mitigate DDoS attacks in real-world scenarios.
This section introduces the proposed scheme. It describes the overall design of the proposed comparative scheme, including the entropy-based, machine learning algorithms employed, and the system’s main parameters. The proposed scheme consists of entropy-based and machine-learning clustering modules, strategically integrated to enhance the effectiveness of DDoS attack detection and mitigation. Figure 2 illustrates the comprehensive architecture of this model. The primary step involves data preprocessing which is performed through the following sequence: where \({ip}_{src}\) , ip are \({ip}_{dest}\) , addresses of both source and destination and pktSize is the packet size.
Extract important features from the dataset based on flow-based feature extraction technique. This technique aims to analyze how features are distributed across traffic packets 40 , like These network flow attributes enable packets, whether normal or anomalous, to be specified. The entropy values are then compared to a preset threshold to locate the presence of anomalies in these features.
Group requests in the same interval from the same uid as follows: interval #, uid , count , label . Subsequently, the request flows are divided into multiple time intervals of equal duration, denoted as T. After each time interval, the entropy detection module comes into play, assessing whether an attack occurred in the last interval. In the case of a detected attack, the machine learning technique starts the clustering of active users within that interval into three distinct clusters: normal users, suspicious users, and attackers. This sequential process emphasizes the model's dynamic responsiveness to potential attacks, integrating both entropy-based detection and machine learning clustering for a comprehensive defense mechanism.
After each time interval, the frequencies, representing the total attempt requests of active users within that interval, go through a normalization process. This normalization, shown by the following equation, ensures that the frequencies are scaled appropriately. In this equation, \({\widehat{\text{x}}}_{\text{i}}\) is the normalized frequency of user i, \({\text{x}}_{\text{i}}\) represents the frequency of user i within set X, \({\text{x}}_{\text{min}}\) is the minimum frequency in set X, and \({\text{x}}_{\text{max}}\) denotes the maximum frequency in set X. This normalization step is instrumental in maintaining consistency and relevance in the dataset, facilitating a robust analysis of user behavior, and aiding subsequent detection processes.
Entropy is a scientific concept, as well as a measurable physical property, associated with disorder, randomness, or uncertainty. A fundamental assumption is introduced, that the system's randomness decreases during a DDoS attack. After each time interval, the system's overall entropy is calculated using the following equation. In this equation, entropy reaches its maximum when all elements have the same frequencies, and subsequently decreases as the randomness of requests decreases. Here, X represents the set of active users in the interval, and \({\text{x}}_{\text{i}}\) \({\text{x}}_{\text{i}}\) is the frequency of user \(\text{i}\) requests in the interval. This entropy calculation serves as an essential metric for calculating the level of randomness and potential irregularities in the system, thereby helping in the identification of DoS attacks.
The module sets a lower threshold \({\upbeta }_{\text{lower}}\) for the system’s overall entropy H(X), which indicates that the system is under attack. Figure 3 shows the system entropy during the DDoS attack and the entropy of the normal users only in the same intervals on a part of the CIC-IDS2017 dataset with an interval size of 120 s. The figure shows a noticeable decrease in entropy after the DDoS attack started, yet sometimes both entropy values were near each other, possibly due to having slow attack rates. This interaction between the system and normal user entropy provides valuable insights into the changes in the DDoS attack, particularly during intervals marked by subtle variations in attack intensity.
Entropy for the system during DDoS and entropy for the normal users in the same intervals on the CIC-IDS2017 dataset. The first procedure, the attack detection has O(n) time complexity and O(n) space complexity, where n is the number of users in the interval. The detection procedure consists of a clustering procedure and an attacker detection procedure. The clustering has a time complexity of O ( \(K \times n \times I\) ) where k is the number of clusters (3 in our case) and I the number of iterations which is fixed in our case, so overall the clustering has O(n) time complexity and O(n) space complexity. The attacker detection procedure has O(n) time complexity (using Algorithm 3.2). Therefore, the overall time complexity for the system is O(n) and O(n) space complexity, where n is the number of active users in the interval.
Algorithm 3.1 encapsulates the comprehensive detection procedure, offering a brief overview of the steps involved in identifying potential attackers within the system. Algorithm 3.2 provides a detailed illustration of the applied optimization method, specifically designed to compute. H (X ∪ \({u}_{j}\) ) This optimization serves the purpose of significantly reducing computational complexity, transitioning from O ( \({n}^{2}\) ) to a more efficient O ( \(n\) ). This strategic enhancement contributes to the algorithm's streamlined efficiency, ensuring a more scalable and expedited process for calculating entropy.
Following the detection of an attack by the entropy module within the system, the subsequent step involves the application of the K-means algorithm to cluster active users from the previous interval. These users are clustered into three distinct groups: normal users, suspicious users, and potential attackers, as shown in Fig. 4 . The utilization of the K-means clustering method is attributed to its versatility and efficiency in handling substantial volumes of data promptly. The algorithm's effectiveness lies in its ability to efficiently group network traffic data points into clusters, making it suitable for the rapid and real-time identification of user behavior patterns. However, a key challenge in employing K-means is the selection of an appropriate value for "k", representing the number of clusters. Selecting an unsuitable "k" value can lead to suboptimal clustering outcomes.
To address this challenge, we have opted for a value of "k" equal to 3, aligning with the need to classify users into three primary clusters. This decision ensures that the K-means algorithm effectively captures the nuances of user behavior and facilitates the differentiation of normal users, suspicious users, and potential attackers within the system. After clustering the users into the three clusters, the evaluation process proceeds to test each user ( \({\text{u}}_{\text{j}})\) within the suspicious and potential attackers' clusters against the normal users' cluster. This examination aims to assess the impact of each user on the entropy of the normal users' cluster, as expressed in the following equation. Within the examined clusters, distinct thresholds are established for the entropy ratio change, denoted as Suspicious Cluster Entropy Change Delta ( \({\updelta }_{\text{susp}}\) ) and Attacker Cluster Entropy Change Delta ( \({\updelta }_{\text{attack}}\) ). The evaluation criterion involves comparing the \({\text{ratio}}_{\text{i}}\) (h) with the corresponding \({\updelta }_{\text{i}}\) for each cluster. If the ratio change is less than the predetermined threshold \({\updelta }_{\text{i}}\) ( \({\text{ratio}}_{\text{i}}\) (h) < corresponding, \({\updelta }_{\text{i}}\) ), the user is identified as a potential attacker. This demanding assessment process ensures a robust and accurate identification of suspicious and potential attacker users within the system.
5. Performance Evaluation & Extended Technical Observations The system includes a variety of parameters (data attributes) that manage its interaction with incoming request flows. These parameters collaboratively influence the system's performance, serving a crucial role in guaranteeing optimal functionality and responsiveness. A summary of these parameters is described in Table 1 : In this study, we focused on four main parameters, namely interval size, \({\upbeta }_{\text{lower}},\) \({\updelta }_{\text{susp}}\) , and \({\updelta }_{\text{attack}}\) . From self-assessment on CIC-IDS2017 41 , the four parameters presented similar behavior concerning system accuracy. Initially, accuracy starts increasing with the increase of the respected parameter until it reaches its peak and then starts decreasing with the continuousincrease in the parameter value. This pattern mirrors the characteristic curve observed in normal distribution patterns.
This section provides a comprehensive overview of the evaluation environment employed in this study. It includes an extensive exploration of the datasets utilized. To ensure a comprehensive and open discussion about the results, it also specifies the exact evaluation criteria that will be used to evaluate the effectiveness of the suggested approaches. CIC-IDS2017 dataset has been curated by the Canadian Institute for Cybersecurity (UNB) to accurately describe network activities and simulate attack scenarios based on real security reports. The dataset offers a comprehensive range of network behaviors for analysis. It includes various protocols like Hypertext Transfer Protocol (HTTP), Secure Shell Protocol (SSH), File Transfer Protocol (FTP), Hop-by-Hop IPv6 (HOPOPT), Transmission Control Protocol (TCP), and User Datagram Protocol (UDP). The refined data preserves key characteristics like Source IP, Destination IP, Source Port, Protocol, Timestamp, and Label and simplifies it for efficient model evaluation 41 .
CSECIC2018 dataset is a crucial tool for cybersecurity researchers, providing network traffic data for intrusion and DDoS detection models and algorithms. Like CIC-IDS2017, this dataset covers various protocols, offering a comprehensive view of network behaviors, including HTTP DDoS attacks 42 . CICDDoS2019 analyzes DDoS attacks, including both benign and common ones. The dataset enables the analysis of network traffic and the extraction of over 80 traffic features. It features labeled flows categorized by timestamp, source and destination IPs, source and destination ports, protocols, and attack types 43 .
Table 2 provides a summary of the three datasets. The model assessment was carried out on CIC-IDS2017 41 dataset. To conduct a comprehensive performance evaluation, it is essential to consider a variety of metrics. The confusion matrix is used to evaluate the performance of the model. The performance assessment is done through four main measures as follows: true positive (TP), true negative (TN), false positive (FP), and false negative (FN). Where the positive indicates being an attacker. The system accuracy is calculated as the number of correct labeling as shown in the subsequent equation.
In our model, accuracy (acc) and the other confusion metrics are calculated for the mitigation effect, in other words, if the entropy detected that the user is an attacker, the TP value will be affected in the next interval since all the requests in the current interval were handled (i.e., FN). In addition to the accuracy, false positive rate (FPR), Precision, Recall, and F1-Score are calculated for the technique as the following. Recall (sensitivity) measures the percentage of attackers that are correctly detected. Additionally, F1-score symmetrically represents both recall and precision.
One of the main challenges when utilizing datasets for training and testing machine learning models, including those considered for evaluating the proposed approach, is data imbalance. Data imbalance can cause machine learning algorithms to prioritize accuracy for the majority class while neglecting the minority class, resulting in biased models. To make sure that the model can effectively identify patterns from all classes, dataset imbalance must be addressed. Dataset dimension reduction can help address data imbalance by mitigating the impact of the majority class dominating the feature space 44 .
Performance measures such as Matthews Correlation Coefficient (MCC), and Geometric Mean (G-means) are frequently used to evaluate how well machine learning models perform, especially when dealing with imbalanced datasets. MCC considers true and false positives and negatives and ranges from − 1 to 1. A coefficient of 1 represents a perfect prediction, 0 represents a random prediction, and − 1 indicates total disagreement between prediction and observation.
On the other hand, G-means evaluates the classifier's performance by considering both sensitivity and specificity. Sensitivity measures the classifier's accuracy in detecting stuck-up events, while specificity evaluates its ability to identify non-stuck-up events, providing a balanced assessment of classification accuracy 45 . These metrics provide a more comprehensive assessment of the model’s performance, enabling more accurate decision-making in real-world applications.
This study conducts a series of experiments, including both self-assessment and comparative analyses. In the beginning, a single-protocol dataset generator was implemented, to be as an initial phase to test the sensitivity of the system parameters. After that, the system parameters go through comprehensive testing against the CIC-IDS2017 41 dataset. Finally, the system's performance was thoroughly assessed against multiple datasets, including CIC-IDS2017 41 , CSECIC2018 42 , and CIC-DDoS2019 43 . The system parameters’ sensitivity was used to plan the training approach used later. The rest of this section illustrates the results of both the self-assessment and comparative analyses, detailing the various phases of our methodology and the outcomes observed at each step.
The proposed model contains multiple parameters that control its results, as shown in " Methods " section. In this work, we focused on the following parameters. In the beginning, the model is trained at a selected interval size (mostly 120-s intervals). After that, each parameter has a value range depending on its type, for the entropy lower threshold, entropy deltas [0, 1].
The experiments reveal distinct phases in the behavior of the key parameters \({\upbeta }_{\text{lower}}\) , \({\updelta }_{\text{attack}}\) , and \({\updelta }_{\text{susp}}\) , each affecting the system's accuracy and false positive rate (FPR) differently. For instance, varying \({\upbeta }_{\text{lower}}\) shows three distinct phases, with the system transitioning from low accuracy to high accuracy as it is adapted to different entropy ranges. Similarly, \({\updelta }_{\text{attack}}\) shows three phases, with its impact on accuracy being less significant compared to \({\upbeta }_{\text{lower}}\) , but still contributing to overall system performance.
A detailed self-assessment of our model is conducted using CIC-IDS2017 41 dataset. Experiments measure the impact of each attribute \({\upbeta }_{\text{lower}}\) , \({\updelta }_{\text{attack}}\) , and \({\updelta }_{\text{susp}}\) on metrics such as accuracy, FPR, and F1-Score. Figure 5 a shows the results of changing the value of \({\upbeta }_{\text{lower}}\) where the accuracy is the lowest with FPR = 0 since the entropy detection alarm is never fired and thus no additional checks are carried out. Then, the accuracy starts to increase significantly after \({\upbeta }_{\text{lower}}\) = 0.2, and this can be justified by Fig. 3 where the entropy of all attacking intervals H(U) > 0.25, so \({\upbeta }_{\text{lower}}\hspace{0.17em}\) < 0.25 won’t cause any checks. After \({\upbeta }_{\text{lower}}\hspace{0.17em}\) = 0.2, with the increase in \({\upbeta }_{\text{lower}}\) value, the system starts inspecting more intervals and detecting more attackers, which increases the TP rate and accuracy till it reaches a certain limit. With the continuous increase of \({\upbeta }_{\text{lower}}\) , the system starts considering normal intervals as under-attack intervals, and thus FP rate increases, and accuracy decreases due to considering high-rate normal users as attackers.
Regarding FPR, as shown in Fig. 5 b, the curve can be divided into three phases: very low FPR with \({\upbeta }_{\text{lower}}\hspace{0.17em}\) < 0.2 where FP = TP = 0, rapidly increased accuracy with rapid FP and FPR, and a remarkably increased FP affecting accuracy, resulting in higher FPR. Figure 5 c shows that the F1-Score has observations as in accuracy.
Overall, the effect of \({\upbeta }_{\text{lower}}\) has three phases. The first phase, where \({\upbeta }_{\text{lower}}
The study demonstrates a similar effect on the \({\updelta }_{\text{attack}}\) in three phases, as shown in Fig. 6 . Figure 6 a shows that at lower values, accuracy is very low since most of the attackers fall in the possible attackers’ cluster. As \({\updelta }_{\text{attack}}\) increase, more attackers are detected, increasing TP, FP, and accuracy. However, the impact of the \({\updelta }_{\text{attack}}\) on system accuracy is less remarkable compared to the effect of \({\upbeta }_{\text{lower}}\) value. In the third phase, increasing \({\updelta }_{\text{attack}}\) doesn't significantly impact accuracy due to the higher likelihood of the system being attacked.
The analysis shows nuanced relationships between the attributes ( \({\upbeta }_{\text{lower}}\) , \({\updelta }_{\text{attack}}\) , and \({\updelta }_{\text{susp}}\) ) and system performance. For example, lower values of \({\updelta }_{\text{attack}}\) lead to lower accuracy due to missed detections of attackers, while higher values increase false positives. These observed patterns help in understanding the behavior of the model under different conditions, guiding parameter tuning and training approaches for improved performance.
Overall, the effect of \({\delta }_{attack}\) can be divided into three phases. In the first phase, at low \({\delta }_{attack}\) values, the procedure will not detect attackers, i.e. very low TP, and thus very low accuracy and high FN. Followed by the second phase, where accuracy reaches a peak due to high TP and low FN rates. Finally, at high \({\delta }_{attack}\) rates, the FP starts increasing due to considering high-rate normal users as attackers, causing a slight decrease in accuracy and F1-score.
Finally, Fig. 7 shows the effect of \({\updelta }_{\text{susp}}\) . There is no remarkable effect on the system. It seems that no true attackers fall in the suspicious cluster, so the system has lower accuracy with lower \({\updelta }_{\text{susp}}\) as shown in Fig. 7 a. Only at higher values of \({\updelta }_{\text{susp}}\) , the system starts to falsely mark normal users as attackers, increasing FP and FPR and decreasing the system’s accuracy and F1-Score.
The \({\delta }_{susp}\) was expected to have a similar pattern as the \({\delta }_{attacker}\) , yet it showed no significant effect on the system, except at very high values, where it decreased accuracy due to an increase in FP. With further investigations, we found no attackers falling into this cluster in our datasets. Yet, it’s safer to consider checking the suspicious cluster to detect cases where there exists a very high-rate attacker that will change the cluster of lower-rate attackers resulting in some attackers falling into the suspicious cluster.
The proposed system is evaluated using three distinct datasets: CICIDS2017 41 , CSECIC2018 42 , and CICDDOS2019 43 . Performance metrics such as accuracy, FPR, TPR, F1-Score, G-means, and MCC are used for comparison. The results of the evaluation are presented in Table 3 . For each dataset, the system performance is compared to multiple techniques. The results will be discussed in the remainder of this subsection.
In the context of the CICIDS2017 41 dataset, the performance of the system is compared against other notable techniques, including Lucid 29 , Multi-layer Perception (MLP), 1D-CNN 46 , LSTM 46 , and the combined approach of 1D-CNN + LSTM 46 . This comparative analysis aims to provide a thorough understanding of how the proposed system fares against established methods, shedding light on its strengths and effectiveness in the specific context of the CICIDS2017 41 dataset. The ensuing discussion will clarify these comparative results as shown in Table 4 .
Roopak et al. 46 proposed four different DL models for DDoS attack detection in Internet of Things (IoT) networks. The models are built with combinations of LSTM, CNN, and fully connected layers. The input layer of all the models consists of 82 units, one for each flow-level feature available in CICIDS2017 41 , while the output layer returns the probability of a given flow being part of a DDoS attack. The model intelligent detection convolutional neural network (ID-CNN) + LSTM 46 produces good classification scores, while the others seem to suffer from high FN rates. The same observations are found on the CICIDS2017 41 dataset, the increase in FN and decrease in FP leads to an increase in accuracy compared to Lucid 29 , and eventually, the other techniques used. Then, the CSECIC2018 42 dataset results were compared to the Lucid 29 technique as shown in Table 5 .
The CSECIC2018 42 showed different behavior than the other two datasets, the FP increased, and the FN decreased, but overall, the system has a simple improvement in accuracy due to the Lucid 29 technique. The dataset had a flow with a high rate compared to other flows which caused this increase in FP rate since this flow was falsely detected as an attack. Finally, the CICDDOS2019 43 dataset results were compared to Cil et al. 31 and Alghazzawi et al. 47 techniques as shown in Table 6 . The proposed system shows higher accuracy rates compared to Cil et al. 31 and Alghazzawi et al. 47 . The system showed higher FP rates compared to CICIDS2017 41 .
The proposed model consistently outperforms existing techniques across all datasets, demonstrating superior accuracy and robustness in DDoS attack detection. Comparative analysis with techniques such as Lucid 29 , MLP, and 1D-CNN 46 highlight the strengths of our model, particularly in mitigating false positives and achieving high accuracy rates. Harvested Online Documentation & Reference Sources • https://github.com/chiragbiradar/DDoS-Attack-Detection-and-Mitigation • https://www.nature.com/articles/s41598-024-67984-w
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for DDoS Attack Detection Using Machine Learning In Software Defined Networks.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |