Complete Technical Paper Content — Decentralized Honeypot Network Using Smart Contracts
Overview & System Context
Decentralized Honeypot Network Using Smart Contracts: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8639 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Mustafa Al-Bassam (born January 1995) is an Iraqi-British computer security researcher, hacker, and co-founder of Celestia Labs. Al-Bassam co-founded the hacker group LulzSec in 2011, which was responsible for several high profile breaches. He later went on to co-found Chainspace, a company implementing a smart contract platform, which was acquired by Facebook in 2019. In 2021, Al-Bassam graduated from University College London, completing a PhD in computer science with a thesis on Securely Scaling Blockchain Base Layers. In 2016, Forbes listed Al-Bassam as one of the 30 Under 30 entrepreneurs in technology.
In 2011 as a 16 year old teenager, Al-Bassam was one of the six core members of LulzSec during its 50-day hacking spree, going by the alias "tflow". The group used denial-of-service attacks and compromised a number of high profile organizations and corporations, including Sony, Fox, News International, Nintendo and the CIA. He was also affiliated with the online association of hacktivists known as Anonymous, where he was involved with the hacking of emails from HBGary Federal, an intelligence contractor for the U.S. government. The emails revealed that HBGary Federal was working to develop astroturfing software to create an "army" of fake social media profiles, and was hired by the U.S. Chamber of Commerce to spy on and smear political opponents with fake documents and communications. As a result, members of the U.S. Congress called for an investigation into HBGary Federal.
Smart contract attacks cost protocols over $3.8 billion in 2022 alone. While most teams react to breaches after they occur, forward-thinking security professionals deploy honeypots to detect threats before they strike production systems. Smart contract honeypots transform passive security into active threat intelligence gathering. These decoy contracts attract malicious actors, revealing their techniques and tools while keeping real assets safe. This guide shows you how to build, deploy, and monitor honeypot systems that strengthen your blockchain security posture.
Figure 1: Phenomenon of smart contract honeypots continuation of the list of ... Smart contract honeypots differ fundamentally from traditional network honeypots. They operate on immutable, transparent blockchains where every interaction becomes permanent public record. This transparency creates both opportunities and challenges for security teams.
A well-designed honeypot mimics vulnerable contracts that attackers target. It might simulate a DeFi protocol with apparent reentrancy flaws or an NFT marketplace with weak access controls. When attackers interact with these decoys, they reveal their methods, tools, and wallet addresses. Early Warning Systems : Detect attack patterns before they target production contracts. Monitor emerging exploitation techniques as they develop in real-time.
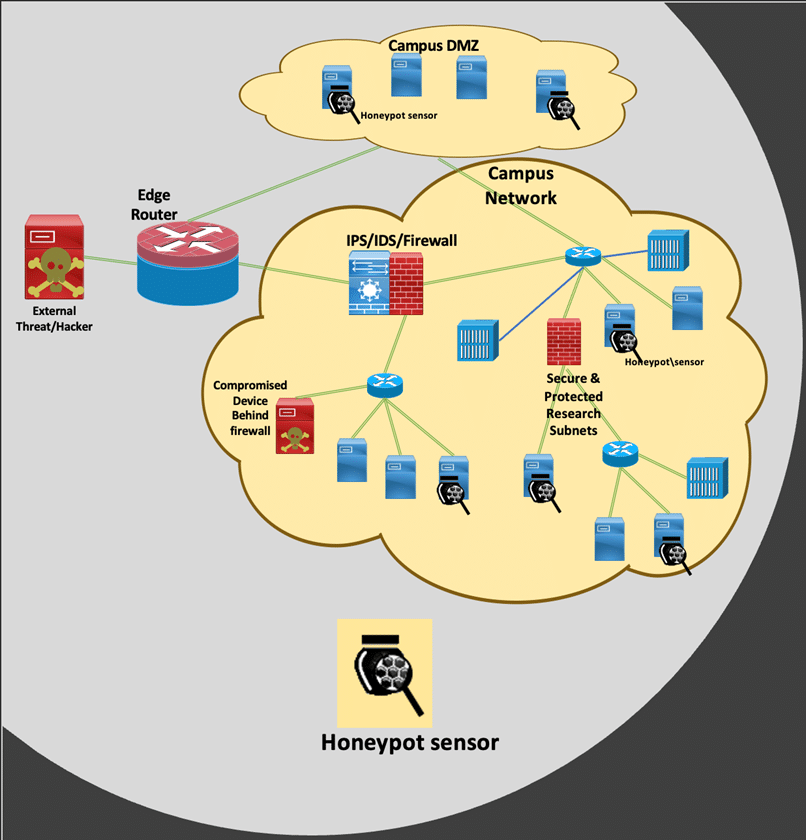
Threat Actor Profiling : Track attacker wallets, analyze their funding sources, and understand their operational patterns. Build comprehensive threat intelligence databases. Figure 2: Honeypots: An Advanced Solution in IT Threat Detection - ACUA Security Testing : Validate your detection systems and incident response procedures. Train security teams with real attack scenarios in controlled environments.
Building robust honeypot infrastructure requires four core elements working in harmony: Decoy Contracts : Deploy convincing smart contracts that appear vulnerable. Include common weaknesses like reentrancy bugs, integer overflows, or access control flaws. Balance realism with safety to avoid creating actual vulnerabilities. Event Monitoring Layer : Implement comprehensive logging for all contract interactions. Capture transaction data, function calls, and state changes. Use event emissions to track detailed attacker behavior.
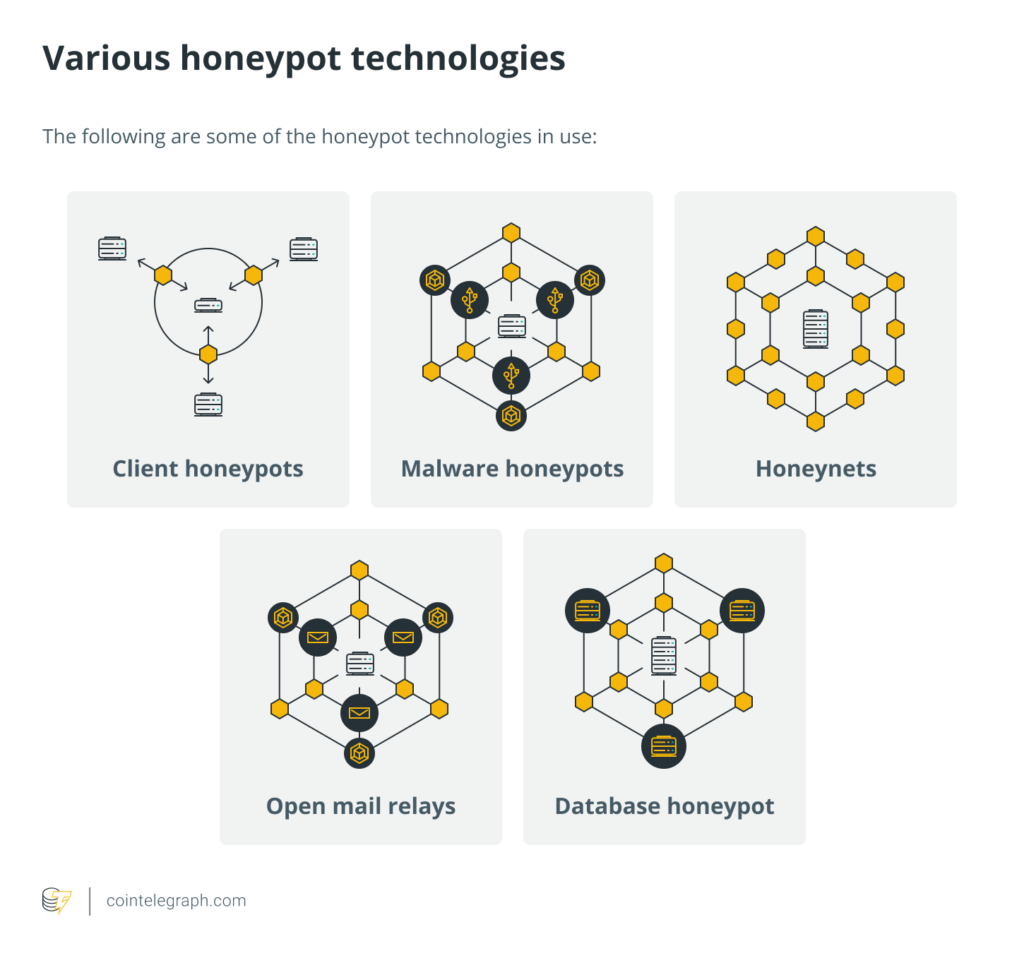
Figure 3: Satsdaily - What is a honeypot crypto scam and how to spot it? Data Collection Pipeline : Stream blockchain events to analysis systems in real-time. Index transactions for efficient querying and pattern matching. Store raw data for forensic investigation. Alert Mechanisms : Configure instant notifications for suspicious activities. Set thresholds for automated responses and escalation procedures. Integrate with existing security operations centers.
Distributed Networks : Deploy multiple honeypots across different chains and protocols. Vary vulnerability types to attract diverse attackers. Correlate data across honeypots for comprehensive intelligence. Layered Defenses : Create honeypots at multiple sophistication levels. Simple contracts catch automated scanners while complex systems engage advanced attackers. Each layer provides unique intelligence value.
Dynamic Adaptation : Rotate honeypot configurations regularly to maintain effectiveness. Update vulnerabilities based on current threat trends. Evolve defenses as attackers develop new techniques. Start with clear objectives for your honeypot deployment. Define specific threats you want to detect and intelligence goals you need to achieve. Consider your risk tolerance and available resources.
Select target platforms based on your protection priorities. Ethereum mainnet attracts sophisticated attackers but costs more to operate. Layer 2 networks and alternative chains offer lower-cost testing grounds. Deploy across multiple chains for comprehensive coverage. Design believable vulnerabilities that align with current attack trends. Research recent exploits in your sector to understand attacker interests. Create honey tokens with apparent value to increase engagement rates.
Begin deployment with thorough testing on testnets. Verify logging systems capture all necessary data without performance impacts. Ensure safety mechanisms prevent honeypots from becoming actual attack vectors. Deploy contracts using dedicated wallets with minimal funding. Implement time-locks and withdrawal limits as safety measures. Monitor gas costs and optimize for sustainable long-term operation.
Configure monitoring infrastructure before going live. Set up real-time dashboards for activity visualization. Establish baseline metrics for normal versus suspicious behavior. Create automated alerts for critical events. Effective monitoring combines automated detection with human analysis. Configure systems to flag specific patterns while allowing analyst review of edge cases.
Track key indicators including unusual function call sequences, rapid transaction patterns, and known attacker addresses. Monitor funding flows to identify attack preparation. Analyze gas usage patterns for exploitation attempts. Implement correlation engines that connect related activities. Link multiple honeypot interactions to identify coordinated attacks. Map attacker infrastructure through wallet relationship analysis.
Transform raw honeypot data into actionable intelligence through systematic analysis. Profile attacker techniques, tactics, and procedures (TTPs). Document new exploitation methods as they emerge. Build threat actor databases with wallet addresses, funding sources, and behavioral patterns. Track evolution of attack tools and automation scripts. Share intelligence with security communities while protecting sensitive details.
Generate regular reports highlighting emerging threats and trends. Provide early warnings to protocol teams about targeted vulnerabilities. Support incident response with historical attack data. Maintain strict separation between honeypot and production systems. Use dedicated infrastructure with no connections to real assets. Implement network segmentation and access controls.
Protect honeypot operator identities through operational discipline. Use separate wallets and avoid linking to known addresses. Consider privacy tools for sensitive deployments. Regularly audit honeypot configurations for safety. Verify isolation measures remain effective over time. Update security controls based on lessons learned.
Understand legal implications in your jurisdiction before deployment. Some regions restrict deception-based security measures. Consult legal counsel for compliance requirements. Follow ethical guidelines for honeypot operations. Never entrap legitimate users or create public hazards. Focus exclusively on detecting malicious activities.
Document your defensive intent clearly. Maintain logs showing security purposes. Prepare disclosure procedures for responsible vulnerability reporting. Implement multiple safety layers to prevent honeypot compromise. Use minimal funding and time-locked withdrawals. Deploy circuit breakers for emergency shutdown.
Monitor honeypots for unexpected behaviors continuously. Watch for attempts to weaponize your decoys. Respond quickly to contain any security incidents. 2. System Architecture & Core Working Principles Plan decommissioning procedures from the start. Know how to safely shut down compromised honeypots. Archive data securely for future analysis needs.
Major DeFi protocols deploy honeypots to detect flash loan attacks early. Decoy lending pools reveal new manipulation techniques before they threaten real liquidity. Teams correlate honeypot data with on-chain analytics for comprehensive threat visibility. Successful implementations include mock AMMs with apparent arbitrage opportunities. These systems captured over 200 attack attempts in 2023, preventing potential losses exceeding $50 million.
NFT platforms use honeypots to identify wash trading and manipulation schemes. Fake collections with pricing vulnerabilities attract bad actors revealing their methods. This intelligence improves fraud detection across legitimate marketplaces. Recent deployments detected coordinated bot networks attempting price manipulation. The intelligence gathered led to blocking over 10,000 malicious addresses across multiple platforms.
Bridge protocols face unique security challenges requiring specialized honeypots. Decoy validators and relayers expose attack vectors specific to cross-chain communication. Teams use this intelligence to harden production bridge implementations. Honeypot data revealed critical vulnerabilities in three major bridge designs during 2024. Early detection through honeypots prevented potential nine-figure losses.
Smart contract honeypots represent the future of proactive blockchain security. By deploying these systems today, you position your protocol ahead of emerging threats tomorrow. Start with a single honeypot targeting your highest-risk vulnerability. Expand gradually as you build expertise and infrastructure. Share intelligence responsibly with the security community to strengthen collective defenses.
The investment in honeypot infrastructure pays dividends through prevented attacks and improved security posture. Begin your implementation now to stay ahead of evolving threats in the rapidly changing blockchain landscape. Take action today: Deploy your first honeypot on a testnet, join threat intelligence sharing communities, and integrate honeypot data into your security operations. The earlier you start gathering intelligence, the stronger your defenses become.
This paper addresses the challenge of enhancing cybersecurity in Blockchain-based Internet of Things (BIoTs) systems, which are increasingly vulnerable to sophisticated cyberattacks. It introduces an AI-powered system model for the dynamic deployment of honeypots, utilizing an Intrusion Detection System (IDS) integrated with smart contract functionalities on IoT nodes. This model enables the transformation of regular nodes into decoys in response to suspicious activities, thereby strengthening the security of BIoT networks. The paper analyses strategic interactions between potential attackers and the AI-enhanced IDS through a game-theoretic model, specifically Bayesian games. The model focuses on understanding and predicting sophisticated attacks that may initially appear normal, emphasizing strategic decision-making, optimized honeypot deployment, and adaptive strategies in response to evolving attack patterns.
The Internet of Things (IoT) has revolutionized numerous sectors through its vast network of interconnected devices. However, the rapid expansion of the IoT introduces significant security and privacy concerns, as these devices often have limited computational resources, making them vulnerable to attacks [ 1 ] . Traditional security solutions, which sometimes rely on centralized systems, encounter scalability issues and introduce further vulnerabilities [ 1 , 2 ] .
Blockchain technology has emerged as a promising solution to enhance the security and privacy of IoT systems. Its decentralized nature facilitates secure, transparent, and tamper-resistant transactions, effectively mitigating the challenges associated with the IoT’s growth [ 1 , 2 , 3 ] . Integrating blockchain and IoT, offers a more secure and resilient framework for IoT systems. However, BIoT systems still face unique cybersecurity challenges, necessitating the development of innovative defense mechanisms [ 1 ] .
Honeypots have proven to be an effective tool in the fight against cyber threats. By acting as decoys, honeypots attract and analyze cyberattacks, providing valuable insights into the methods and strategies employed by attackers. The strategic deployment of honeypots in BIoT systems strengthens the overall security posture and addresses pressing privacy concerns [ 4 ] .
Numerous studies have explored using honeypots in various settings, leveraging game theory to optimize their effectiveness. La et al. [ 5 ] and Diamantoulakis et al. [ 6 ] investigated the deployment of honeypots in IoT networks and smart grid systems to counteract DDoS attacks using Bayesian games of incomplete information. Li et al. [ 7 ] proposed using honeypots in smart grids to monitor cyber penetration, applying stochastic games to understand the complex dynamics of these environments.
In the context of Advanced Persistent Threats (APTs), Tian et al. [ 8 ] introduced prospect theoretic games to assess bounded rational behavior when deploying honeypots in Software-Defined Networks (SDNs) within the Industrial Internet of Things (IIoT). Wang et al. [ 9 ] focused on honeypot deployment in Advanced Metering Infrastructure (AMI) networks to strategize against DDoS attacks using Bayesian games.
Shi et al. [ 10 ] contributed a three-party evolutionary game model for array honeypot systems, introducing a novel aspect to honeypot strategy. Carroll [ 11 ] reviewed game-theoretic approaches in cybersecurity, highlighting the role of deception in securing networks through signaling and Bayesian repeated games. Li et al. [ 12 ] explored distributed honeypot schemes and game theory models like Bayesian and evolutionary games to address network security challenges in IoT, Unmanned Aerial Vehicles (UAVs), and cloud computing.
Boumkheld et al. [ 13 ] focused on honeypots in smart grids for Security Information and Event Management (SIEM) training and post-incident analysis, applying a Bayesian game with complete but imperfect information. Tian et al. [ 14 ] and Lee et al. [ 15 ] explored honeypot applications in Cyber-Physical Systems (CPS) and industrial control systems, proposing game-theoretical models to optimize defense against APTs, considering honeypot allocation costs and human analysis.
Florea and Craus [ 16 ] reviewed network security tactics, including honeypots in software-defined networks, discussing cyber deception games and honeypots as cyber camouflage methods. Despite the extensive research on honeypot deployment in various domains, there remains a gap in the literature regarding the strategic deployment of honeypots in BIoT systems. The unique characteristics of BIoT environments, such as the decentralized architecture and smart contracts, necessitate the development of tailored defense mechanisms that can adapt to the evolving threat landscape.
We propose an AI-powered model for strategically deploying honeypots in BIoT systems to address this gap. Our model leverages game-theoretic principles to optimize defense mechanisms against sophisticated cyber threats, contributing to the field with a deceptive defense solution designed to secure BIoT environments and enhance their resilience. We introduce an AI-powered system model for the dynamic deployment of honeypots in BIoT systems, utilizing an Intrusion Detection System (IDS) integrated with smart contract functionalities on IoT nodes.
We develop a game-theoretic model, specifically Bayesian games, to analyze the strategic interactions between potential attackers and the AI-enhanced IDS, focusing on understanding and predicting sophisticated attacks that may initially appear normal. We conduct simulations to evaluate the effectiveness of various honeypot deployment strategies in a BIoT security context, considering the trade-off between detecting attacks and minimizing false positives.
We provide insights and recommendations for developing more sophisticated intrusion detection systems that optimize the balance between security and operational costs in BIoT environments. The remainder of this paper is organized as follows: Section II outlines our proposed AI-powered system model for the dynamic deployment of honeypots in BIoT systems; Section III discusses the game-theoretic model and its analysis; Section IV presents the simulation setup and results; Section V concludes the paper and outlines future research directions.
Blockchain-based Internet of Things (BIoT) networks comprise interconnected smart devices crucial for service delivery. These devices, including smart home appliances, health monitors, and environmental sensors, perform data collection and real-time monitoring autonomously through smart contracts. Their critical role and blockchain connectivity make them attractive targets for cyber attackers.
We propose a multi-layered security strategy incorporating honeypots as a proactive defense mechanism to address these security challenges. Inspired by the work of La et al. [ 5 ] , our model integrates an AI-powered Intrusion Detection System (IDS) with smart contract capabilities to scrutinize incoming network traffic. Suspicious traffic is rerouted to honeypots for analysis, while legitimate traffic continues uninterrupted, ensuring continuous service.
As depicted in Figure 1 , the IDS dynamically changes the status of IoT nodes within the system, isolating them from the main network when suspicious activity is detected. This isolation allows suspicious traffic to be redirected to a honeypot server, which can be safely analyzed without compromising the main network’s integrity. Meanwhile, normal traffic continues to flow seamlessly, ensuring uninterrupted service.
IoT Nodes: These are the smart devices connected to the BIoT network, performing various tasks such as data collection, monitoring, and actuation. Blockchain Network: The BIoT system is built on a blockchain network that ensures secure, transparent, and tamper-proof transactions among the IoT nodes. Smart contracts are deployed on the blockchain to facilitate the autonomous execution of predefined rules and actions.
AI-powered IDS: The Intrusion Detection System is a critical component of the proposed model. It leverages machine learning algorithms to analyze network traffic patterns and detect suspicious activities. The IDS is trained on a diverse dataset of normal and malicious traffic patterns to enhance its accuracy and effectiveness. Honeypot Server: The honeypot server is a dedicated system that hosts various honeypots designed to attract and trap attackers. When the IDS detects suspicious traffic, it redirects it to the honeypot server for further analysis. The honeypots mimic vulnerabilities and entice attackers to reveal their tactics and intentions.
Smart Contracts: Smart contracts play a vital role in automating the deployment of honeypots and the isolation of compromised nodes. When the IDS detects a potential threat, it triggers a smart contract that automatically reconfigures the network topology, isolating the suspicious node and redirecting its traffic to the honeypot server. The AI-powered IDS continuously monitors the network traffic of each IoT node in the BIoT system.
When the IDS detects suspicious traffic patterns, it triggers a smart contract on the blockchain network. The smart contract automatically isolates the suspicious node from the main network and redirects its traffic to the honeypot server. 3. Software Implementation, Frameworks & Protocols The honeypot server analyzes the redirected traffic to identify the attacker’s tactics, techniques, and procedures (TTPs).
Based on the analysis, the system updates its threat intelligence and refines the IDS’s detection models to improve its accuracy and effectiveness. The isolated node remains in the honeypot environment until it is deemed safe to reintegrate into the main network. Normal traffic continues to flow uninterrupted, ensuring the availability and functionality of the BIoT system.
Integrating smart contracts with an AI-powered IDS enables our BIoT security model to leverage smart contracts’ self-executing capabilities for enforcing and automating security protocols. Smart contracts enable decentralized and autonomous actions, such as real-time rerouting of suspicious network traffic to honeypots, based on the AI’s analysis of data patterns and anomalies. The AI component employs machine learning algorithms to continuously analyze network traffic patterns and compare them against known threat signatures and anomalies, while smart contracts ensure the automatic deployment of honeypots upon anomaly detection.
The proposed model offers several advantages over traditional security approaches. By dynamically isolating suspicious nodes and redirecting their traffic to honeypots, the system can effectively contain potential threats and prevent them from spreading across the network. Smart contracts enable automated and rapid response to detected anomalies, reducing the response time and minimizing the potential impact of an attack. Furthermore, the AI-powered IDS continuously learns and adapts to new threat patterns, enhancing the system’s resilience against evolving attack vectors.
One of the key advantages of our proposed model is its dynamic honeypot deployment strategy. Traditional honeypot deployment approaches often introduce additional computational overhead and resource consumption by dedicating specific nodes as permanent honeypots, which may impact the overall performance of the BIoT system and increase operational costs. In contrast, our approach dynamically changes the state of normal nodes to honeypots when suspicious activity is detected. This dynamic adaptation allows for more efficient resource utilization, as the nodes can continue to perform their regular tasks when not acting as honeypots. By temporarily isolating suspicious nodes and redirecting their traffic to the honeypot server, our model minimizes the performance impact on the overall BIoT system while still providing effective threat detection and analysis capabilities. This dynamic approach also leads to cost savings, as it eliminates the need for dedicated honeypot hardware and reduces the overall resource consumption of the security infrastructure.
However, the proposed model also presents some challenges. The accuracy and effectiveness of the IDS heavily depend on the quality and diversity of the training dataset. Obtaining a comprehensive dataset that covers a wide range of attack scenarios can be difficult and time-consuming. Additionally, the dynamic nature of the honeypot deployment raises questions about the optimal strategies for both defenders and attackers. Defenders must decide when and where to deploy honeypots based on the perceived threat level, while attackers may adapt their strategies to avoid detection and maximize their chances of success.
To address these challenges, we propose a game-theoretic approach to model the strategic interactions between the defenders (i.e., the BIoT system equipped with the AI-powered IDS) and the attackers. Game theory provides a mathematical framework for analyzing the decision-making processes of rational agents in strategic situations. By modeling the incentives, costs, and benefits of different strategies, game theory can help us derive optimal defense mechanisms that consider the attackers’ potential actions.
Optimal honeypot deployment: Determining the best strategies for deploying honeypots based on the perceived threat level and the cost-benefit trade-offs. Adaptive defense mechanisms: Developing defense strategies that can adapt to the evolving strategies of the attackers, taking into account the potential for sophisticated attacks that may initially appear normal.
Balancing security and performance: Identifying the optimal balance between maximizing the security of the BIoT system and minimizing the performance overhead introduced by the honeypot deployment and IDS operations. We analyze the dynamics between defenders and potential attackers in a BIoT system. Attackers aim to exploit these networks, employing tactics from naive, basic methods to sophisticated strategies designed to mimic legitimate operations.
Sophisticated attackers, in particular, present a significant challenge; their deep understanding of the BIoT environment allows them to carefully plan their activities to avoid detection, often behaving indistinguishably from legitimate users to infiltrate the system. Defenders, equipped with AI-powered IDS and smart contracts, monitor network activities to distinguish between legitimate operations and potential threats, deploying honeypots as a strategic countermeasure to entrap attackers. The IDS’s activity assessment influences the deployment decision, with a higher probability of honeypot use as the risk of sophisticated attack increases.
In the BIoT security game, defenders and attackers have distinct actions. Defenders can either deploy a honeypot ( D h ) (D_{h}) , aiming to trap attackers by simulating vulnerabilities or choose not to ( D n ) (D_{n}) . Attackers, on the other hand, decide to either launch an attack ( A t ) (A_{t}) or abstain ( A b ) (A_{b}) . Sophisticated attackers might attack discreetly, while naive attackers are more likely to be readily detected. The decision to abstain reflects a strategic choice to avoid engagement under potentially risky conditions. For instance, sophisticated attackers, appearing as normal users, might attack with only a 50% probability to minimize suspicion, whereas naive attackers, easily identified as suspicious, may attack with a 100% probability due to their less cautious approach.
We model the attack and defense scenario in the BIoT system as a one-shot, sequential game between an attacker (A) and a defender (D), concluding after a single round of actions [ 5 ] . Table I presents the notation used in the game model to clarify the symbols and their meanings for the reader. Figure 2 depicts the game tree for the BIoT security game. The game begins with Nature deciding the attacker’s type, introducing uncertainty. The attacker’s behavior is categorized as either Sophisticated ( S S ) or Naive ( N N ). To capture this uncertainty, the game defines two primary information sets: N = { ( N | S ) , ( N | N ) } N=\{(N|S),(N|N)\} and S = { ( S | S ) , ( S | N ) } S=\{(S|S),(S|N)\} . In these sets, the first element represents the defender’s perception based on the observed signal, while the second element denotes the actual type of the attacker.
We formulate the game as a Bayesian game to capture the uncertainty regarding the attacker’s type. The defender must decide whether to deploy a honeypot based on the perceived threat level, influenced by the IDS’s accuracy. Attackers choose their actions based on their type and perceived defensive measures. Table II presents the game’s payoff matrix, detailing each player’s utilities under different action profiles and attacker types.
Players: The Defender ( D D ) and the Attacker ( A A ). The attacker can be either sophisticated ( S S ) or naive ( N N ), formally captured as a type θ ∈ { S , N } \theta\in\{S,N\} . Defender: Deploy honeypot ( D h D_{h} ) or not ( D n D_{n} ). Formally, the action set is D a = { D h , D n } D_{a}=\{D_{h},D_{n}\} .
Attacker: Attack ( A t A_{t} ) or abstain ( A b A_{b} ). The action set is A a = { A t , A b } A_{a}=\{A_{t},A_{b}\} . Payoffs: U i I ( θ , a D , a A ) U_{i}(\theta,a_{D},a_{A}) , where i i stands for player type (defender or attacker). We define the Bayesian Nash Equilibrium (BNE) concept to analyze the game’s equilibria. Definition (BNE): A strategy profile ( σ ∗ , τ ∗ ) (\sigma^{*},\tau^{*}) , accompanied by a belief system µ ∗ \mu^{*} , forms a BNE if, under µ ∗ \mu^{*} , σ ∗ \sigma^{*} and τ ∗ \tau^{*} represent the best response strategies for the attacker and defender, respectively.
In the BIoT game, a pure strategy BNE arises when the defender opts to deploy a honeypot ( τ ∗ = D h \tau^{*}=D_{h} ) with probability 1 if the expected utility of such deployment exceeds that of non-deployment, factoring in both the cost of honeypot deployment and the benefits of attacker detection. Proof: The defender’s deployment decision hinges on whether the expected utility of deploying a honeypot surpasses abstaining based on beliefs µ \mu about the attacker’s type. The defender prefers deployment ( D h D_{h} ) over non-deployment ( D n D_{n} ) if: indicating that honeypot deployment is the defender’s best strategy under these conditions.
A mixed-strategy BNE, where both parties randomize their strategies, emerges when neither can justify a pure strategy based on expected costs and benefits alone. Proof: For a mixed-strategy BNE, we consider the defender deploying a honeypot with probability β \beta and the attacker choosing to attack based on their type with probabilities α S \alpha_{S} and α N \alpha_{N} . Equilibrium requires indifference in strategy choice for both parties, leading to equilibrium probabilities β \beta , α S \alpha_{S} , and α N \alpha_{N} , contingent on the game’s parameters. To achieve a mixed-strategy BNE, the following indifference conditions must hold: Defender’s Indifference: The defender must be indifferent between deploying ( D h ) (D_{h}) and not deploying ( D n ) (D_{n}) : Attackers’ Indifference: Each attacker type must be indifferent between attacking ( A t ) (A_{t}) and abstaining ( A b ) (A_{b}) : Expanding these expected utilities in terms of the game’s parameters and solving the resulting system of equations for β \beta , α S \alpha_{S} , and α N \alpha_{N} will yield the mixed-strategy BNE. For a detailed mathematical framework for analyzing Bayesian Nash Equilibria, refer to [ 17 ] .
We conducted a series of simulation experiments to evaluate the effectiveness of various honeypot deployment strategies in a BIoT security context. The objective was to optimize the balance between detecting attacks (both naive and sophisticated) and minimizing the misidentification of legitimate traffic as malicious (false positives). The simulation parameters, as shown in Table III , were carefully chosen to reflect the cost-benefit analysis of honeypot deployment, the likelihood of facing sophisticated or naive attackers, and the performance of the IDS system in detecting these attacks. The rationale behind each parameter value is provided to ensure the simulation aligns with realistic scenarios.
Let U D I ( e ) U_{D}(e) be the defender’s utility for an event e e , which can be a legitimate event, a sophisticated attack, or a naive attack. The simulation began by initializing a set of honeypot deployment strategies, including fixed threshold strategies (FS50, FS60, FS70, FS80, FS90) and a variable strategy (VS) that adapted the deployment probability based on the IDS’s F1-score. Each simulated trial represented a day of network operation with a mix of legitimate activity and a smaller, defined percentage of attacks from both sophisticated and naive types.
4. Practical Deployment, Analysis & Case Studies The simulation iterated through the events, categorizing them and determining the deployment strategy for each event based on the IDS’s F1-score. Fixed strategies deployed a honeypot if the F1-score exceeded a set threshold, while the variable strategy adjusted the deployment probability dynamically.
The utility was calculated for each event to assess whether an attack was detected or missed, and the average utility achieved by each strategy was determined at the end of each trial. We conducted three main simulation experiments to evaluate the effectiveness of the proposed honeypot deployment strategies: Comparison of deployment strategy utilities with and without false positive penalties (Figure 3 ): This experiment assessed the performance of each strategy in scenarios where false positives were penalized and not penalized. The variable strategy (VS) consistently performed better, suggesting its effectiveness in minimizing false positives and associated costs.
Impact of varying cost of deployment and penalties on strategy utility (Figure 4 ): This experiment explored the effects of varying the cost of honeypot deployment and the penalties for false positives on the utility of each strategy. The results showed that increasing deployment costs reduced utility, but the strategies demonstrated resilience to cost changes. Comparison of deployment strategy utilities with varying attack rates (Figure 5 ): This experiment evaluated the performance of the strategies under different attack rates. The variable strategy exhibited a stable, gradual decrease in utility as the attack rate increased, suggesting its robustness to variations in attack rates, while the fixed strategies showed inconsistent utility fluctuations.
These simulation experiments provide insights into the effectiveness of different honeypot deployment strategies in various BIoT security scenarios. They highlight the importance of selecting the appropriate defense strategy based on the specific operational environment and the potential costs associated with security breaches and false alarms. The results demonstrate the effectiveness of our proposed AI-powered dynamic honeypot deployment approach in optimizing the balance between security and operational efficiency in BIoT systems.
This paper introduced an AI-powered model for strategically deploying honeypots in Blockchain-based Internet of Things (BIoT) systems. By leveraging game-theoretic principles and dynamic adaptation based on the perceived threat level, our approach enhances the security and resilience of BIoT systems while minimizing the performance overhead associated with traditional honeypot deployment strategies.
The game-theoretic analysis provided valuable insights into the strategic interactions between defenders and attackers, revealing the conditions under which pure and mixed strategy equilibria emerge. The simulation results demonstrated the effectiveness of our proposed AI-powered dynamic honeypot deployment approach in optimizing the balance between security and operational efficiency, particularly when compared to fixed deployment strategies.
However, our study has some limitations that should be acknowledged. First, while based on carefully chosen parameters and rationale, the simulation experiments may not fully capture the complexity and diversity of real-world BIoT systems. Future research could involve more comprehensive simulations or real-world experiments to validate the performance of our proposed approach in more complex and realistic settings.
Second, the game-theoretic model assumes that attackers and defenders are rational agents with complete information about the game’s parameters. Attackers and defenders may have bounded rationality and incomplete information, which could impact their decision-making processes. Future work could explore more complex game-theoretic models, such as Bayesian games with incomplete information or evolutionary games, to capture these real-world considerations.
Third, while the simulation results provide valuable insights into the effectiveness of different honeypot deployment strategies, they are based on specific parameter settings and assumptions. Further sensitivity analysis and robustness tests could be conducted to assess the proposed approach’s performance under various parameter configurations and assumptions. Despite these limitations, our study makes significant contributions to BIoT security. By introducing an AI-powered model for the strategic deployment of honeypots and analyzing the problem through a game-theoretic lens, we provide a foundation for developing more sophisticated and adaptive defense mechanisms in BIoT systems.
Future research directions could include incorporating more advanced machine learning techniques, such as deep reinforcement learning, to enable the AI-powered IDS to continuously adapt its detection models and honeypot deployment strategies based on real-time feedback and evolving threat patterns; investigating the integration of our proposed approach with other security mechanisms, such as blockchain-based access control or secure multi-party computation, to create a more comprehensive defense framework for BIoT systems; exploring the scalability and performance of the proposed approach in large-scale BIoT networks with a high volume of devices and traffic; and conducting user studies to assess the usability and acceptability of our proposed approach from the perspective of BIoT system administrators and end-users.
This paper was presented at the 6th IEEE International Conference on Artificial Intelligence Circuits and Systems (IEEE AICAS 2024). Tutorial on how to create your own honeypot erc20/ bep20 tokens and listing to Uniswap How to create honeypot token ? Step by step guide and learn how to list them into dex exchanges.
Tool for creating a honeypot token on Solana. We will guide you through creating Solana honeypot token, adding it to Raydium, blocking sales for all token holders and withdrawing liquidity. Solana Honeypot Token from CryptoKoki developers. Advanced script for creating a honeypot token on Solana. Download the Solana Honeypot Pro source code and access bactch freezing holders of your token as soon as they buy. Fully automated honeypot token code in Solana space. Freeze bundler script for SOL, fast and reliable. Listing on Raydium DEX with Freeze Authority.
To associate your repository with the smart-contract-honeypot topic, visit your repo's landing page and select "manage topics." Honeypot smart contracts are purposefully deceptive programs deployed on blockchains such as Ethereum, designed to lure would-be attackers or malicious users by appearing vulnerable or exploitable. Unlike conventional vulnerabilities, which are passively present in poorly coded contracts, honeypots are a class of “proactive scam” in which the creator carefully engineers subtle traps to induce the victim to believe exploitation is possible, ultimately trapping the funds for the attacker's benefit. Their detection, taxonomy, real-world prevalence, and socio-technical impact on blockchain ecosystems have become important research areas due to their financial and security ramifications.
Honeypot smart contracts employ distinct techniques at multiple abstraction layers of the Ethereum stack. The seminal taxonomy delineated in "The Art of The Scam: Demystifying Honeypots in Ethereum Smart Contracts" ( Torres et al., 2019 ) organizes these into eight categories distributed across the EVM, compiler, and explorer layers: Later analyses extend taxonomy boundaries by introducing social engineering-based traps (address manipulation, homograph techniques), demonstrating the evolving complexity and interdisciplinary nature of honeypot engineering ( Ivanov et al., 2021 ).
2. Honeypot Detection Methodologies: Symbolic Execution, Data Science, and Deep Learning Initial honeypot identification centered on static symbolic analysis. HoneyBadger ( Torres et al., 2019 ) automates detection by generating a control flow graph (CFG) from bytecode, performing symbolic execution (tracking path predicates such as I v > 0 I_v > 0 I v I > 0 ), and extracting transfer event tuples ( c r , c v , c f , c a , c t , c g ) (c_r, c_v, c_f, c_a, c_t, c_g) ( c r I , c v I , c f I , c a I , c t I , c g I ) to match heuristics for each taxonomic honeypot type. The system employs Z3 SMT-solving to prove satisfiability of path conditions flagging honeypot behavior. Performance metrics from large-scale application show high precision rates (e.g., up to 100% for balance disorder).
The alternative data science approach ( Camino et al., 2019 ) leverages a triad of feature classes—contract static features, transaction aggregates, and partitioned fund movement frequencies—feeding them into an XGBoost model. Partitioning is based on eight variables per transaction, yielding 244 valid fund flow cases whose normalized frequencies serve as powerful predictive markers. This approach generalizes to both known and unknown techniques, successfully discovering new classes such as “Unexecuted Call” and “Map Key Encoding Trick” by statistical anomaly ranking rather than explicit code pattern matching.
Deep learning approaches further abstract feature engineering by analyzing n-gram sequences of raw bytecode with recurrent neural networks ( GRU with attention) ( Hu et al., 2021 ). This framework learns high-dimensional fraud fingerprints and achieves high detection efficacy: accuracy (~94.7%), precision (~94.2%), recall (~98.9%). Compared to static and rule-based methods, deep learning generalizes rapidly to novel scam types and scales efficiently to massive datasets.
Empirical evidence from multi-million-contract scans exposes persistent, though not ubiquitous, deployment of honeypots. HoneyBadger flagged 690 honeypots among 2 million contracts on Ethereum, with 240 victims traced—one contract capturing 97 victims, but most trapping a single adversary. The collective profit for honeypot creators exceeded USD 90,000 (257.25 ether), with techniques such as Straw Man Contract and Uninitialised Struct showing varying profitability (average ~1.76 ETH and ~0.46 ETH, respectively) ( Torres et al., 2019 ).
In decentralized exchanges ( DEXs ), honeypot traps have altered the attack surface. "Why Trick Me: The Honeypot Traps on Decentralized Exchanges" ( Gan et al., 2023 ) demonstrated that 8,443 of 10,000 Uniswap V2/V3 pools (84.43%) exhibited honeypot-like abnormalities. Attack types included Invalid Buy, Unauthorized Transfer, Cannot Sell, and Invalid Sell, each engineered via token tax manipulation, stealthy balance resets, sell restrictions, or dynamic upgrade switches. The outcome is widespread asset theft, trust erosion, and an increased demand for simulation-based detection.
The brevity of honeypots’ lifespans (often exploited and drained within 24 hours) combined with abort rates (~54% aborted, ~10% remaining with nonzero balance) underline their high-risk, opportunistic financial strategy. Ethnographic and technical investigations ( Ivanov et al., 2021 ) identify honeypot contracts as the canonical class of social engineering attacks in blockchain prior to the recent expansion. Beyond code traps, attackers now exploit vulnerabilities in human cognition: Large-scale reviews, including case studies on high-profile contracts (USDT, BNB, LINK, LEO, CryptoKitties), show these patterns can be surreptitiously embedded with negligible code alteration, activating in production to lock assets or disrupt operations. Surveys of auditing experts corroborate the seriousness and subtlety of these risks.
Defensive innovation has focused on improving detection generalizability, efficiency, and adaptability. HoneyBadger’s symbolic pipeline, data science aggregative ensembles, and n-gram GRU architectures represent the methodological evolution toward broad, automated scam identification. For DEX honeypots, simulation-driven monitoring systems ( Gan et al., 2023 ) analyze historical event logs and synthetic transaction bundles—mimicking “sell” and “buy” sequences, scrutinizing anomaly thresholds (e.g., balance changes < < < 50% of estimated outputs)—enabling the flagging of abnormal pools. Technical recommendations emphasize more rigorous audit requirements, automated verification tools, real-time user alerts, and integration of code-level simulation in trader interfaces.
Advanced honeypot architectures such as HoneyDOC ( Fan et al., 2024 ) propose modular decoupling for generalized cyber trap deployment: Decoy modules emulate realistic attack surfaces, Captor modules optimize multi-channel data logging and analysis, and Orchestrator modules coordinate countermeasures and traffic redirection. Software-Defined Networking (SDN) further augments programmability, enabling stealthy session handoff and granular traffic control; metrics such as efficiency ( η = Q / T ) (\eta = Q/T) ( η = Q / T ) and stealthiness ( S = 1 − Detection Rate ) (S = 1 - \text{Detection Rate}) ( S = 1 − Detection Rate ) provide theoretical grounding for performance assessment.
In Blockchain-based IoT (BIoT) systems ( Commey et al., 2024 ), AI-powered Intrusion Detection Systems (IDS) coupled with smart contract automation can dynamically repurpose nodes as honeypots, isolating vectors and gathering adversarial intelligence. Bayesian game-theoretic models formalize the equilibrium tradeoffs in strategic honeypot deployment, optimizing defender payoffs under uncertainty regarding attacker sophistication.
Honeypot smart contracts challenge conventional security paradigms by combining software engineering, behavioral economics, and adversarial strategy. Key implications and open questions include: 5. Performance Evaluation & Extended Technical Observations Ongoing research is focused on integrating crowdsourced intelligence, expanding simulation-based verification, developing machine learning models for anomaly detection, and constructing adaptive, modular honeypot systems for both blockchain and broader cyber-infrastructures. The evolution of honeypot smart contracts represents a microcosm of adversarial dynamics in open, programmable financial systems, where attackers and defenders continuously innovate to outwit and outlast each other.
Get notified by email when new papers are published related to Honeypot Smart Contracts . As cryptocurrency adoption continues to grow in 2026, so do the tactics used by cybercriminals to exploit unsuspecting investors. While decentralized finance (DeFi) has created new opportunities for financial innovation, it has also become a prime target for sophisticated scams that hide behind seemingly legitimate blockchain projects. Among the most dangerous of these threats is the crypto honeypot, a malicious smart contract designed to lure investors into purchasing tokens they can never sell.
Understanding what a crypto honeypot is and how to identify one has become an essential skill for anyone participating in the Web3 ecosystem. Whether you’re investing in a newly launched token, interacting with a decentralized application, or exploring emerging blockchain projects, recognizing the warning signs can help protect your assets from irreversible losses. By combining careful research with security solutions such as SecureDApp’s Solidity Shield for smart contract auditing and SecureWatch for continuous blockchain threat monitoring, users can significantly reduce their exposure to malicious contracts and build greater confidence in their Web3 activities.
Most crypto honeypots begin with hype. A developer or team launches a new token, often promoted as the next revolutionary DeFi project or NFT platform. The project may have a flashy website, fabricated whitepaper, and fake social media followers to create an illusion of legitimacy. Investors, seeing activity and liquidity on decentralized exchanges, are drawn in by the fear of missing out. Once they buy the token and attempt to sell it, the hidden truth emerges the contract blocks their transactions.
Only the creator’s wallet address has the privilege to sell or transfer funds. The technical mechanism behind these scams often lies in restrictive smart contract code. A small condition buried deep in the code might specify that only certain addresses can perform “transfer” or “sell” functions. Some contracts even contain misleading or reversible functions that trick users into thinking withdrawals are possible. The scammer waits until a sufficient number of investors have bought in, then drains all liquidity, leaving victims with worthless tokens.
Although these scams can be sophisticated, several warning signs can help investors detect them early. One major indicator is the absence of a verified smart contract. If a project’s contract is not verified on trusted blockchain explorers like Etherscan or BscScan, that’s an immediate cause for concern. Another red flag is unrealistic tokenomics. Projects that promise enormous returns, guaranteed profits, or risk-free staking are almost always too good to be true.
Additionally, lack of transparency in team information and unclear liquidity management are major concerns. If liquidity is locked for only a very short period or worse, not locked at all the project could easily execute a “rug pull.” Many honeypot tokens also build false hype using bots on social media or Telegram groups that appear overly enthusiastic but lack real engagement. Observing these behavioral patterns can be just as important as analyzing the technical side of a project.
Avoiding honeypots requires a mix of caution, technical awareness, and the right tools. One of the most effective preventive steps is to ensure that every project you interact with has undergone a smart contract audit. Services such as Solidity Shield by SecureDApp provide thorough audits that identify vulnerabilities and hidden code designed to restrict users. These audits are vital for both developers and investors who want assurance that a project’s contract is safe and transparent.
Lastly, investors should use reputable decentralized exchanges, verified launchpads, and blockchain analytics tools when evaluating new projects. While many established platforms conduct security reviews before listing tokens, sophisticated scams can still bypass initial screening. In 2026 , attackers increasingly combine honeypot contracts with fake social media campaigns, phishing websites, and AI-generated content to create convincing investment opportunities. Performing independent research and verifying smart contracts remain essential before committing funds.
In the Web3 world, trust is not established through central authorities but through code. Because smart contracts execute automatically, even a small flaw or hidden line of malicious logic can lead to massive losses. That’s why audits are a non-negotiable part of blockchain security . A professional audit, such as those provided by Solidity Shield, goes far beyond a surface review. It includes code-level analysis, vulnerability testing, simulation of potential attacks, and compliance checks against industry standards.
Without a comprehensive audit, investors and developers risk exposure to backdoors, logic errors, and honeypot-like behaviors that could compromise funds. An audit also builds credibility for a project, assuring users that the contract is safe to interact with. In decentralized environments where reversals are impossible, prevention through auditing is the strongest defense.
A striking case of a honeypot scam involved a token that appeared to have over a million dollars in liquidity and thousands of active holders. The project’s website showcased fake testimonials and claimed upcoming exchange listings. Investors eagerly purchased the token, but when they tried to sell, every transaction failed. The underlying code contained a condition allowing only one wallet address the scammer’s to sell. Within hours, the developer withdrew all liquidity and disappeared, leaving investors with no recourse.
This incident illustrates how convincing these scams can be. Activity, liquidity, and hype can all be simulated, but code never lies. The only reliable way to identify such traps is through verification, auditing, and continuous threat monitoring . Web3 offers incredible freedom and innovation, but this freedom demands awareness and responsibility. Tools like Secure Watch help investors and developers maintain security visibility across multiple blockchains, detecting risks in real time. For developers, integrating Solidity Shield during the development phase ensures that contracts remain secure from vulnerabilities that could later be exploited.
Combining these solutions from SecureDApp.io creates a robust security framework that helps protect users from honeypots, rug pulls, and smart contract exploits. These tools make it possible to focus on innovation and growth without constantly worrying about potential threats lurking in the code. The world of cryptocurrency and decentralized finance thrives on opportunity, but it also attracts deception. Knowing what a crypto honeypot is and how to avoid it can mean the difference between profit and loss. The key lies in being informed, cautious, and well-equipped with reliable security tools. Before investing in any project, always verify its contract , examine its transparency, and check whether it has been independently audited.
Using trusted tools like Secure Watch and Solidity Shield can dramatically reduce the risk of falling into malicious traps. As Web3 continues to evolve, your security practices must evolve with it. Staying one step ahead of scammers isn’t just about protecting your assets; it’s about building a safer and more trustworthy decentralized future. A crypto honeypot is a malicious smart contract that allows users to buy a token but secretly prevents them from selling or withdrawing it. The scam is designed so that only the contract creator or specific wallet addresses can move funds, trapping investors.
Before investing, verify that the smart contract is publicly available, review its audit status, examine token permissions, and use trusted blockchain analysis tools. Looking for independent security audits and community feedback can also help identify potential risks. Yes. A comprehensive smart contract audit can identify hidden transfer restrictions, unauthorized permissions, malicious logic, and other vulnerabilities commonly used in honeypot scams. Professional auditing significantly reduces the likelihood of interacting with malicious contracts.
No. Honeypot scams can appear on any blockchain that supports smart contracts, including Ethereum, BNB Chain, Base, Polygon, Arbitrum, Avalanche, Solana ecosystems with programmable contracts, and other emerging Web3 networks. SecureDApp helps reduce honeypot risks through Solidity Shield, which performs comprehensive smart contract security audits, and SecureWatch, which continuously monitors blockchain activity for suspicious behavior and emerging threats.
Together, these solutions help developers build secure applications while giving investors greater confidence before interacting with smart contracts. The DPDP Act has moved data protection in India from a set of best practices to a hard legal requirement with real financial and reputational consequences. Consent sits at the very center of this law, and managing it well requires more than good intentions, it requires infrastructure.… The Law Has Changed. Has Your Platform? India’s Digital Personal Data Protection Act, 2023 is no longer just a policy discussion. It is active law, and organizations handling personal data are being held to a new standard. At the center of this law sits one critical concept:… This blog breaks down the FATF Travel Rule for crypto transfers over $1,000, mandating VASP data sharing like names and wallet addresses. DApp developers and founders learn compliance hurdles in decentralization, KYC integration, plus SecureDApp tools for automated triggers, encrypted handling, and cross-chain alignment via case studies… A honeypot token is a type of cryptocurrency scam built directly into the token's smart contract. The contract is written so that anyone can buy the token on a decentralized exchange, but only the deployer (or a small set of insider wallets) can sell. When you attempt to sell your tokens, the transaction fails, reverts, or deducts a fee so large that you receive nothing back. Your investment is effectively locked forever.
The name comes from the concept of a honey pot used in security: something attractive that lures victims in and traps them. In the crypto context, the bait is usually a token with a rapidly rising price chart. New buyers see the price going up, buy in expecting to sell later at a profit, and then discover they cannot sell at all. Honeypot tokens are estimated to account for 20-40% of newly launched tokens on some chains, particularly on low-fee networks like BNB Chain and Base where deploying a scam contract costs very little. This makes learning how to detect honeypot tokens an essential skill for anyone trading on decentralized exchanges.
For a deeper explanation of what honeypot tokens are and why they exist, see our dedicated article on what a honeypot token is . Honeypot contracts use a variety of techniques to block sells while keeping buys open. Understanding these techniques is the first step toward being able to detect a honeypot token. Here are the five most common methods scammers use.
The contract includes functions like setBlacklist, addToBlacklist, or isBlacklisted that allow the deployer to block specific wallet addresses from executing sell transactions. After you buy, the deployer adds your address (or all buyer addresses) to the blacklist. Any subsequent attempt to call the transfer or sell function reverts with an error. Because the blacklist is controlled by the contract owner, only the deployer can remove addresses from it, which they never do.
The contract contains a setMaxTxAmount or setMaxSellAmount function that the deployer can modify at any time. Initially, the limit is set high enough to allow normal trading. After buyers accumulate tokens, the deployer sets the maximum sell amount to zero or an extremely small number like 1 wei. Your sell transaction reverts because it exceeds the allowed maximum. The buy function is not subject to the same limit, so new victims can still purchase tokens.
The contract applies asymmetric tax rates for buy and sell transactions. The buy tax is set to a reasonable percentage, typically between 1-5%, to avoid raising suspicion. However, the sell tax is set to 90-100%, which means attempting to sell returns almost nothing or causes the transaction to fail entirely. Some contracts use a dynamic fee function that starts low and gradually increases the sell tax over time, making early detection more difficult.
This technique targets the ERC-20 approval mechanism that decentralized exchanges rely on. After you buy the token and approve the DEX router to spend your tokens, the contract silently revokes or modifies the approval. When you attempt to sell, the router lacks the necessary allowance to transfer your tokens, and the transaction fails. Some contracts override the approve function itself so that approvals for the router address are never actually stored.
The contract overrides the standard transfer or transferFrom function with custom logic that selectively blocks transactions. Common implementations check whether the sender is the contract owner or the liquidity pair, allowing only the deployer to sell. Other variations use a cooldown timer set to an impossibly long period, a whitelist that only includes the deployer, or conditional logic that restricts transfers based on block number or timestamp.
Honeypot crypto scams trap your funds in tokens you can't sell. Learn how honeypot smart contracts work, the latest scam variants in 2026, and the best tools to detect them before you invest. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Mustafa%20Al-Bassam • https://drcodes.com/posts/smart-contract-honeypots-build-threat-intelligence-systems • https://arxiv.org/html/2405.12951 • https://github.com/topics/smart-contract-honeypot • https://www.emergentmind.com/topics/honeypot-smart-contracts • https://blog.securedapp.io/what-is-a-crypto-honeypot-how-to-avoid-this-tricky-trap/ • https://coinibi.com/learn/honeypot-guide • https://www.kerberus.com/learn/honeypot-crypto-scam/ • https://hackernoon.com/understanding-and-preventing-honeypot-attacks-in-smart-contracts
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Decentralized Honeypot Network Using Smart Contracts.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |