Complete Technical Paper Content — Decentralized Identity Management System Using Blockchain
Overview & System Context
Decentralized Identity Management System Using Blockchain: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8527 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A blockchain is a distributed ledger with growing lists of records (blocks) that are securely linked together via cryptographic hashes. Each block contains a cryptographic hash of the previous block, a timestamp, and transaction data (generally represented as a Merkle tree, where data nodes are represented by leaves). Since each block contains information about the previous block, they effectively form a chain (viz. linked list data structure), with each additional block linking to the ones before it. Consequently, blockchain transactions are resistant to alteration because, once recorded, the data in any given block cannot be changed retroactively without altering all subsequent blocks and obtaining network consensus to accept these changes. Blockchains are typically managed by a peer-to-peer (P2P) computer network for use as a public distributed ledger, where nodes collectively adhere to a consensus algorithm protocol to add and validate new transaction blocks.
Although blockchain records are not unalterable, since blockchain forks are possible, blockchains may be considered secure by design and exemplify a distributed computing system with high Byzantine fault tolerance. A blockchain was created by a person (or group of people) using the name (or pseudonym) Satoshi Nakamoto in 2008 to serve as the public distributed ledger for bitcoin cryptocurrency transactions, based on previous work by Stuart Haber, W. Scott Stornetta, and Dave Bayer.
The implementation of the blockchain within bitcoin made it the first digital currency to solve the double-spending problem without the need for a trusted authority or central server. The bitcoin design has inspired other applications and blockchains that are readable by the public and are widely used by cryptocurrencies. The blockchain may be considered a type of payment rail. Private blockchains have been proposed for business use. Computerworld called the marketing of such privatized blockchains without a proper security model "snake oil"; however, others have argued that permissioned blockchains, if carefully designed, may be more decentralized and therefore more secure in practice than permissionless ones.
A blockchain is a decentralized, distributed, and often public, digital ledger consisting of records called blocks that are used to record transactions across many computers so that any involved block cannot be altered retroactively, without the alteration of all subsequent blocks. This allows the participants to verify and audit transactions independently and relatively inexpensively. A blockchain database is managed autonomously using a peer-to-peer network and a distributed timestamping server. They are authenticated by mass collaboration powered by collective self-interests. Such a design facilitates robust workflow where participants' uncertainty regarding data security is marginal. The use of a blockchain removes the characteristic of infinite reproducibility from a digital asset. It confirms that each unit of value was transferred only once, solving the long-standing problem of double-spending. A blockchain has been described as a value-exchange protocol. Logically, a blockchain can be seen as consisting of several layers: infrastructure (hardware) networking (node discovery, information propagation and verification) consensus (proof of work, proof of stake) data (blocks, transactions) application (smart contracts/decentralized applications, if applicable) Permissioned blockchains use an access control layer to govern who has access to the network. It has been argued that permissioned blockchains can guarantee a certain level of decentralization, if carefully designed, as opposed to permissionless blockchains, which are often centralized in practice.
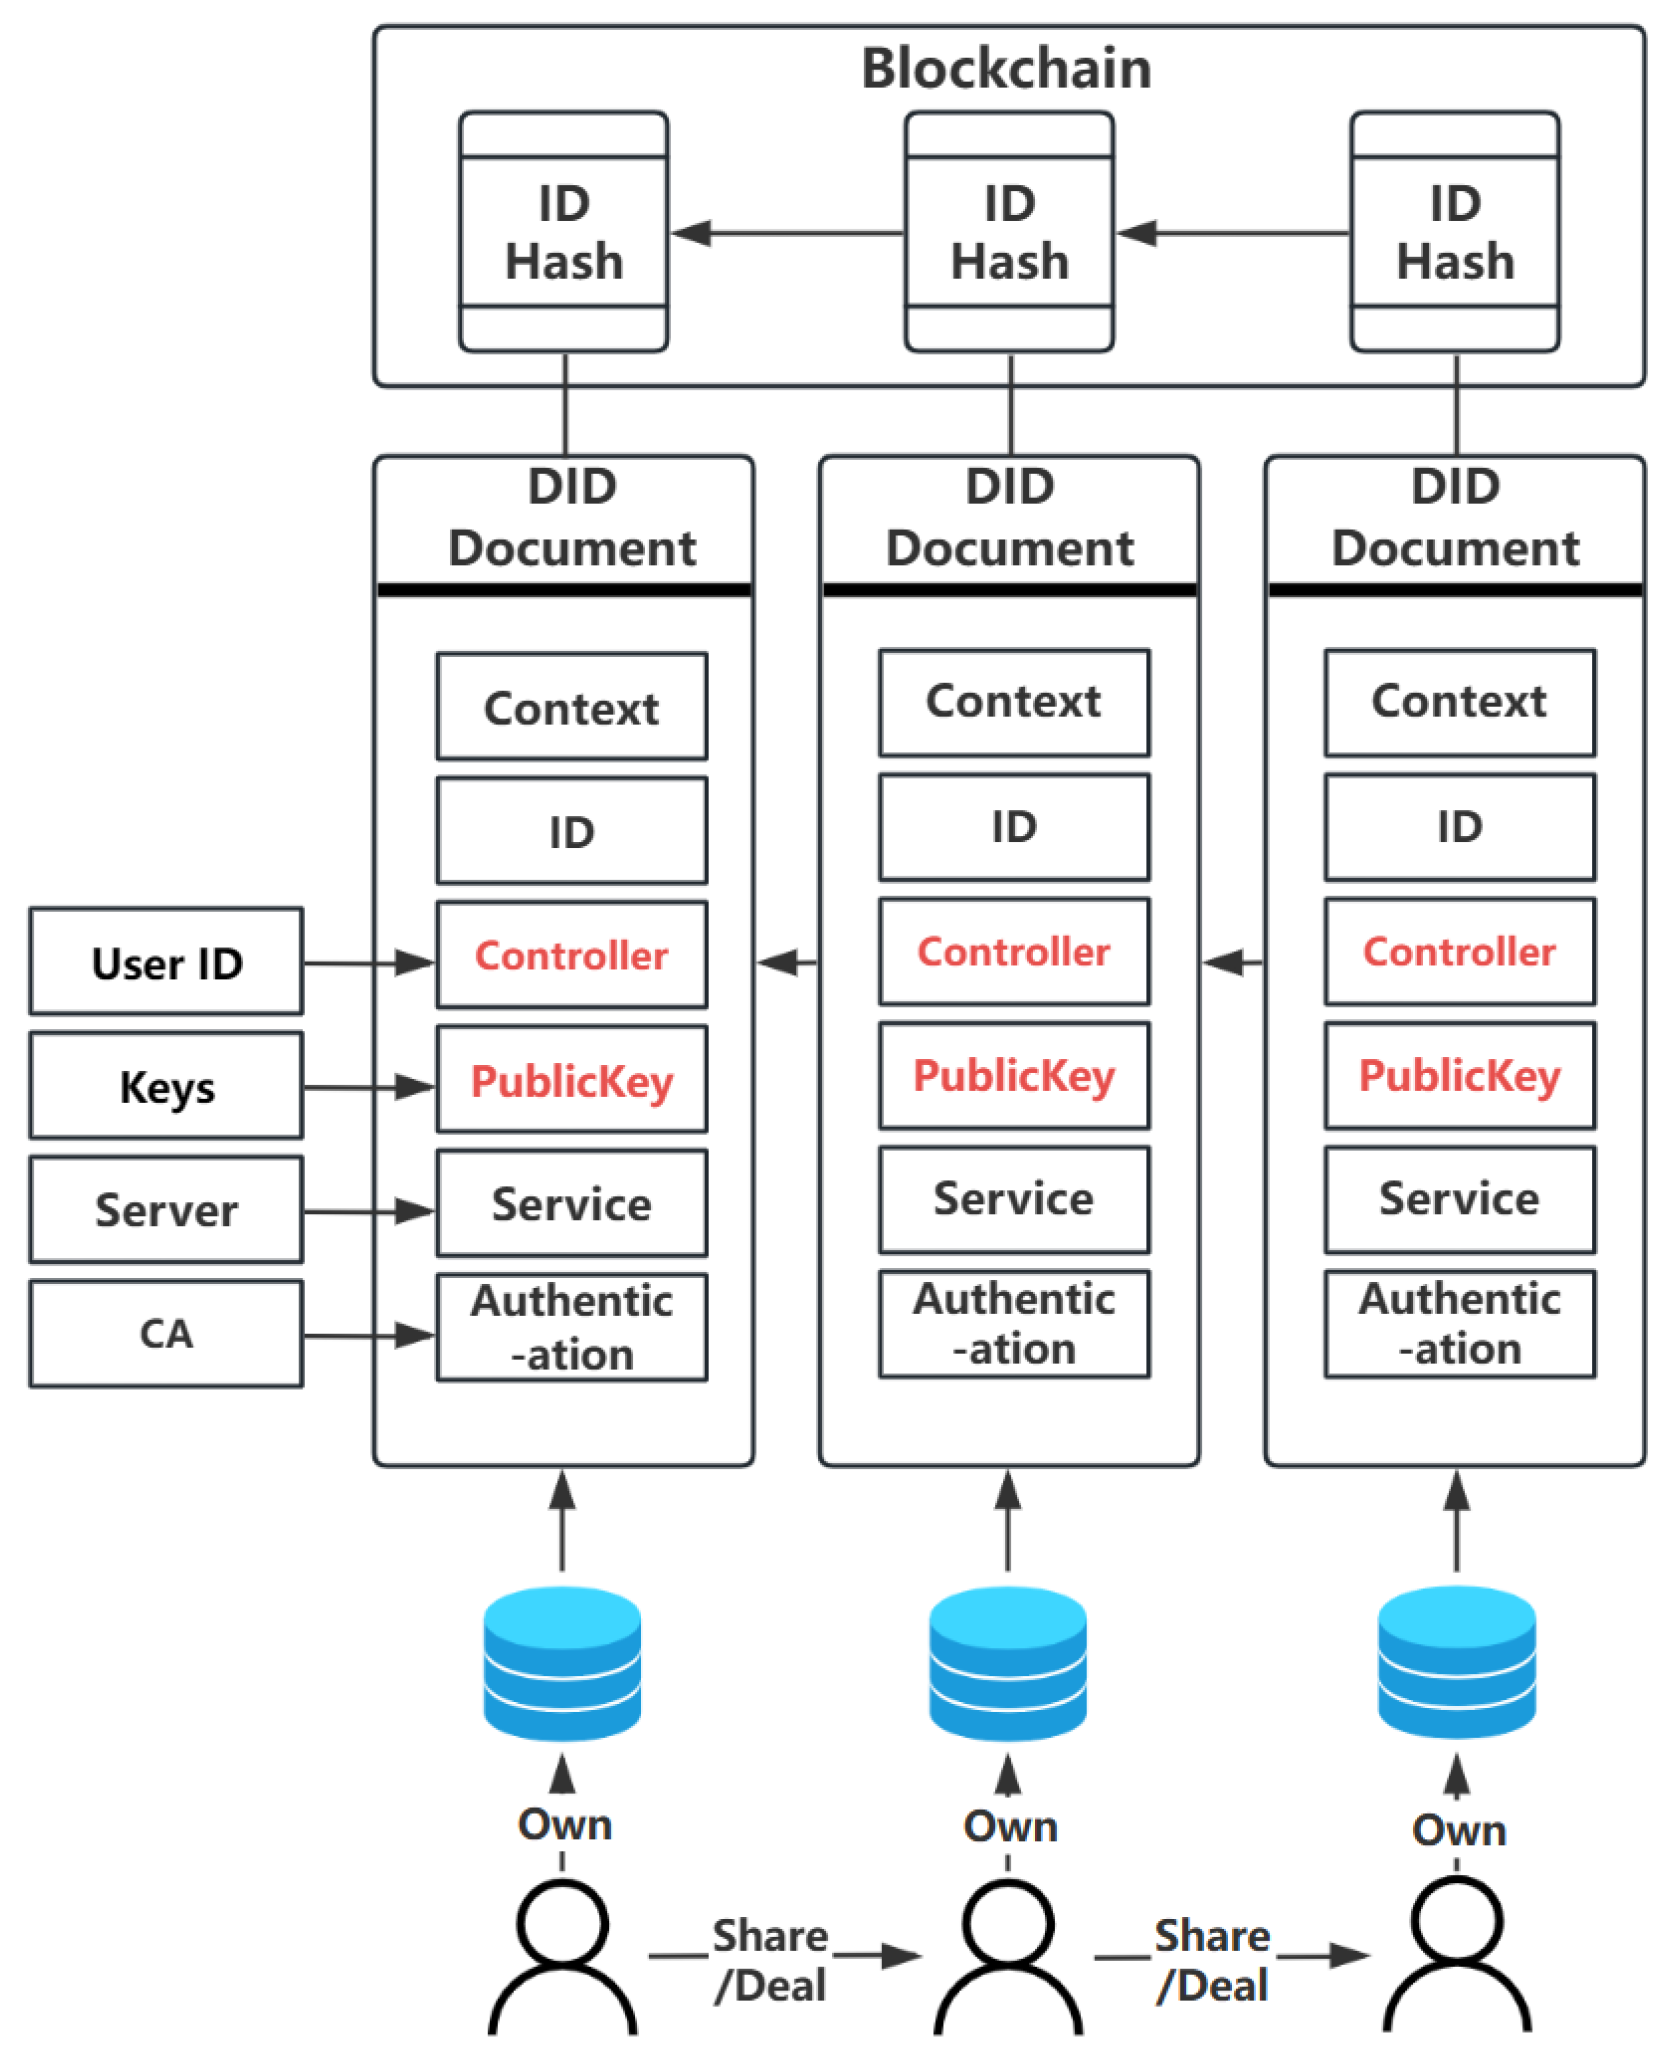
Figure 1: BDIDA-IoT: A Blockchain-Based Decentralized Identity Architecture ... Blockchain-based smart contracts are contracts that can be partially or fully executed or enforced without human interaction. One of the main objectives of a smart contract is automated escrow. A key feature of smart contracts is that they do not need a trusted third party (such as a trustee) to act as an intermediary between contracting entities — the blockchain network executes the contract on its own. This may reduce friction between entities when transferring value and could subsequently open the door to a higher level of transaction automation. An IMF staff discussion from 2018 reported that smart contracts based on blockchain technology might reduce moral hazards and optimize the use of contracts in general, but "no viable smart contract systems have yet emerged." Due to the lack of widespread use, their legal status was unclear.
Blockchain technology, such as cryptocurrencies and non-fungible tokens (NFTs), has been used in video games for monetization. Many live-service games offer in-game customization options, such as character skins or other in-game items, which the players can earn and trade with other players using in-game currency. Some games also allow for trading of virtual items using real-world currency, but this may be illegal in some countries where video games are seen as akin to gambling, and has led to gray market issues such as skin gambling, and thus publishers typically have shied away from allowing players to earn real-world funds from games. Blockchain games typically allow players to trade these in-game items for cryptocurrency, which can then be exchanged for money. The first known game to use blockchain technologies was CryptoKitties, launched in November 2017, where the player would purchase NFTs with Ethereum cryptocurrency, each NFT consisting of a virtual pet that the player could breed with others to create offspring with combined traits as new NFTs. The game made headlines in December 2017 when one virtual pet sold for more than US$100,000. CryptoKitties also illustrated scalability problems for games on Ethereum when it created significant congestion on the Ethereum network in early 2018 with approximately 30% of all Ethereum transactions being for the game. By the early 2020s, there had not been a breakout success in video games using blockchain, as these games tend to focus on using blockchain for speculation instead of more traditional forms of gameplay, which offers limited appeal to most players. Such games also represent a high risk to investors as their revenues can be difficult to predict. However, limited successes of some games, such as Axie Infinity during the COVID-19 pandemic, and corporate plans towards metaverse content, refueled interest in the area of GameFi, a term describing the intersection of video games and financing typically backed by blockchain currency, in the second half of 2021.
Several major publishers, including Ubisoft, Electronic Arts, and Take Two Interactive, have stated that blockchain and NFT-based games are under serious consideration for their companies in the future. In October 2021, Valve Corporation banned blockchain games, including those using cryptocurrency and NFTs, from being hosted on its Steam digital storefront service, which is widely used for personal computer gaming, claiming that this was an extension of their policy banning games that offered in-game items with real-world value. Valve's prior history with gambling, specifically skin gambling, was speculated to be a factor in the decision to ban blockchain games. Journalists and players responded positively to Valve's decision as blockchain and NFT games have a reputation for scams and fraud among most PC gamers, and Epic Games, which runs the Epic Games Store in competition to Steam, said that they would be open to accepted blockchain games in the wake of Valve's refusal.
There have been several different efforts to employ blockchains in supply chain management. Precious commodities mining — Blockchain technology has been used for tracking the origins of gemstones and other precious commodities. In 2016, The Wall Street Journal reported that the blockchain technology company Everledger was partnering with IBM's blockchain-based tracking service to trace the origin of diamonds to ensure that they were ethically mined. As of 2019, the Diamond Trading Company (DTC) has been involved in building a diamond trading supply chain product called Tracer. Food supply — As of 2018, Walmart and IBM were running a trial to use a blockchain-backed system for supply chain monitoring for lettuce and spinach – all nodes of the blockchain were administered by Walmart and located on the IBM cloud. Fashion industry — There is an opaque relationship between brands, distributors, and customers in the fashion industry, which prevents the sustainable and stable development of the fashion industry. Blockchain could make this information transparent, assisting sustainable development of the industry. Motor vehicles — Mercedes-Benz and partner Icertis developed a blockchain prototype used to facilitate consistent documentation of contracts along the supply chain so that the ethical standards and contractual obligations required of its direct suppliers can be passed on to second tier suppliers and beyond. In another project, the company uses blockchain technology to track the emissions of climate-relevant gases and the amount of secondary material along the supply chain for its battery cell manufacturers.
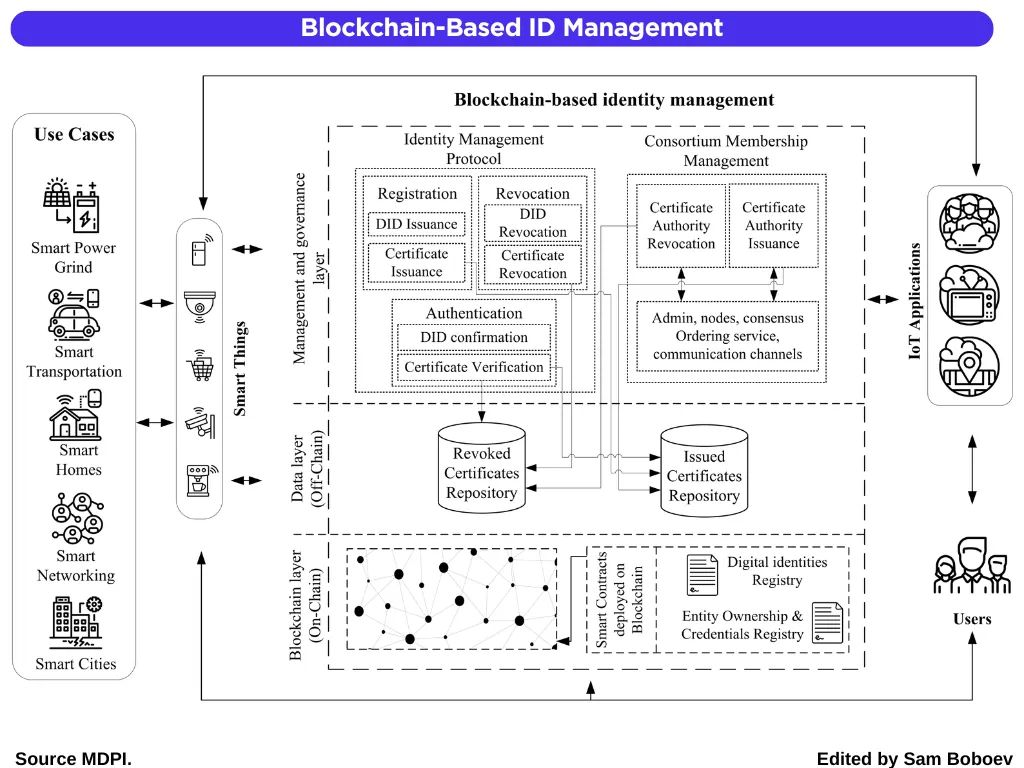
Figure 2: Blockchain-Based Identity Management Architecture and Protocols ... Blockchain technology can be used to create a permanent, public, transparent ledger system for compiling data on sales, tracking digital use and payments to content creators, such as wireless users or musicians. The Gartner 2019 CIO Survey reported 2% of higher education respondents had launched blockchain projects and another 18% were planning academic projects in the next 24 months. In 2017, IBM partnered with ASCAP and PRS for Music to adopt blockchain technology in music distribution. Imogen Heap's Mycelia service has also been proposed as a blockchain-based alternative "that gives artists more control over how their songs and associated data circulate among fans and other musicians." New distribution methods are available for the insurance industry such as peer-to-peer insurance, parametric insurance and microinsurance following the adoption of blockchain. The sharing economy and IoT are also set to benefit from blockchains because they involve many collaborating peers. The use of blockchain in libraries is being studied with a grant from the U.S. Institute of Museum and Library Services. Other blockchain designs include Hyperledger, a collaborative effort from the Linux Foundation to support blockchain-based distributed ledgers, with projects under this initiative including Hyperledger Burrow (by Monax) and Hyperledger Fabric (spearheaded by IBM). Another is Quorum, a permissioned private blockchain by JPMorgan Chase with private storage, used for contract applications. Oracle introduced a blockchain table feature in its Oracle 21c database.
Blockchain is also being used in peer-to-peer energy trading. Blockchain and distributed ledger technologies have been investigated for managing access permissions, consent, provenance and audit trails in health care. A 2026 scoping review of 892 studies found that most involved prototypes or simulated evaluations, while evidence of sustained real-world implementation remained limited. Lightweight blockchains, or simplified blockchains, are more suitable for internet of things (IoT) applications than conventional blockchains. One experiment suggested that a lightweight blockchain-based network could accommodate up to 1.34 million authentication processes every second, which could be sufficient for resource-constrained IoT networks. Blockchain could be used in detecting counterfeits by associating unique identifiers to products, documents and shipments, and storing records associated with transactions that cannot be forged or altered. It is however argued that blockchain technology needs to be supplemented with technologies that provide a strong binding between physical objects and blockchain systems, as well as provisions for content creator verification ala KYC standards.
The EUIPO established an Anti-Counterfeiting Blockathon Forum, with the objective of "defining, piloting and implementing" an anti-counterfeiting infrastructure at the European level. The Dutch Standardisation organisation NEN uses blockchain together with QR Codes to authenticate certificates. Beijing and Shanghai are among the cities designated by China to trial blockchain applications as January 30, 2022. In Chinese legal proceedings, blockchain technology was first accepted as a method for authenticating internet evidence by the Hangzhou Internet Court in 2019 and has since been accepted by other Chinese courts.
In October 2014, the MIT Bitcoin Club, with funding from MIT alumni, provided undergraduate students at the Massachusetts Institute of Technology access to $100 of bitcoin. The adoption rates, as studied by Catalini and Tucker (2016), revealed that when people who typically adopt technologies early are given delayed access, they tend to reject the technology. Many universities have founded departments focusing on crypto and blockchain, including MIT, in 2017. In the same year, Edinburgh became "one of the first big European universities to launch a blockchain course", according to the Financial Times.
The need for internal audits to provide effective oversight of organizational efficiency will require a change in the way that information is accessed in new formats. Blockchain adoption requires a framework to identify the risk of exposure associated with transactions using blockchain. The Institute of Internal Auditors has identified the need for internal auditors to address this transformational technology. New methods are required to develop audit plans that identify threats and risks. The Internal Audit Foundation study, Blockchain and Internal Audit, assesses these factors. The American Institute of Certified Public Accountants has outlined new roles for auditors as a result of blockchain.
In September 2015, the first peer-reviewed academic journal dedicated to cryptocurrency and blockchain technology research, Ledger, was announced. The inaugural issue was published in December 2016. The journal covers aspects of mathematics, computer science, engineering, law, economics and philosophy that relate to cryptocurrencies. The journal encourages authors to digitally sign a file hash of submitted papers, which are then timestamped into the bitcoin blockchain.
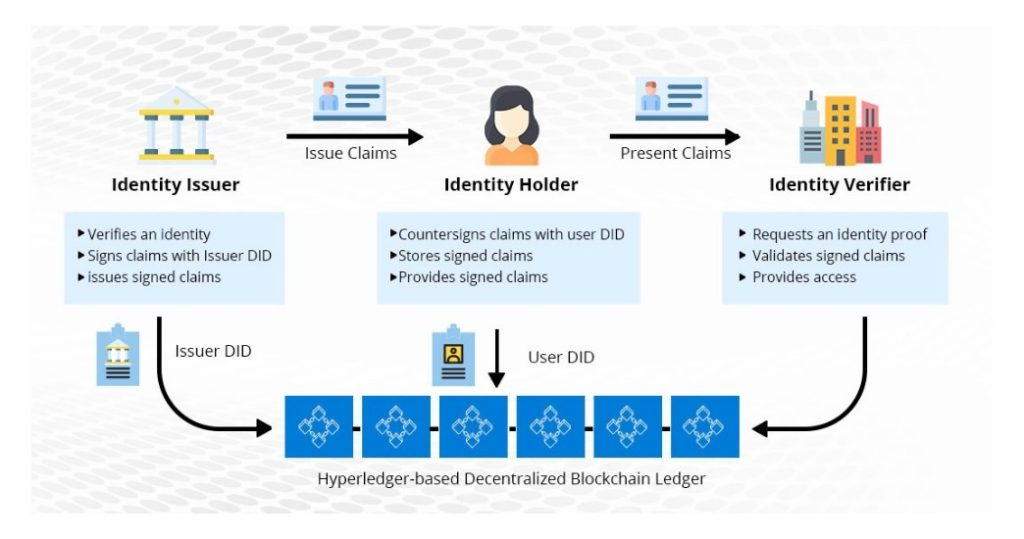
Authors are also asked to include a personal bitcoin address on the first page of their papers for non-repudiation purposes. Figure 3: Spydra Blog | 5 Unique Blockchain Applications in Identity Management Changelog – a record of all notable changes made to a project Checklist – an informational aid used to reduce failure Economics of digitization Git – a version control system where the commit hash value depends on the previous commit hash value, also with Merkle tree inside List of blockchains Privacy and blockchain Real-World Assets Version control – a record of all changes (mostly of software project) in a form of a graph This page introduces the fundamental concepts of Decentralized Identity (DID) in blockchain technology. We'll explore what DIDs are, their evolution, implementation challenges, and how IOST 3.0 creates a comprehensive framework for secure, private, and user-controlled digital identity.
Identity systems have evolved significantly over time, moving from centralized to increasingly decentralized models: Traditional Identity Systems : Centralized authorities issue and verify identities, creating siloed data and single points of failure Federated Identity : Multiple identity providers with cross-platform authentication, still relying on centralized authorities Self-Sovereign Identity (SSI) : Users control their identity data without relying on central authorities Blockchain-Based DIDs : Combining cryptographic security and distributed ledger technology for tamper-proof, verifiable digital identity Decentralized Identifiers are a type of globally unique identifier that enables verifiable, self-sovereign digital identity. Key characteristics include: Self-Sovereignty : Users create and control their identifiers without depending on central authorities Persistence : DIDs remain valid regardless of changes in underlying systems or providers Decentralization : No central point of control for creating, resolving, or managing DIDs DID Documents : Machine-readable documents containing public keys, authentication methods, and service endpoints associated with a specific DID Verifiable Credentials (VCs) : Cryptographically secure claims about the identity subject Verifiable Presentations : User-controlled disclosure of credential data to specific parties DID Registries : Systems that record and resolve DIDs, often implemented on blockchains Recovery Mechanisms : Secure methods for identity recovery without central authorities Cryptographic Layer : Public-key cryptography, zero-knowledge proofs, and secure hashing IOST 3.0 introduces an innovative DID framework designed to address existing challenges in digital identity while providing enhanced security, privacy, and usability for mainstream adoption.
Identity Anchoring Layer : Secure and efficient DID registry implemented on BNB Chain with optimized storage design. Credential Management System : Comprehensive framework for issuing, storing, and verifying credentials with privacy preservation. Biometric Authentication Module : Industry-first hardware-backed identity verification using wearable devices.
Privacy-Preserving Identity Hub : Secure personal data storage with user-controlled access rights. Enterprise Compliance Framework : Tools for organizations to issue and verify credentials while meeting regulatory requirements. Cross-Chain DID Resolver : Protocol enabling interoperability with DIDs from other blockchain networks.
The DID framework is designed to work seamlessly with other core components of the IOST 3.0 ecosystem: Payment Infrastructure : Enabling KYC-compliant transactions with privacy preservation Cross-Chain Technology : Allowing identities to function seamlessly across blockchain ecosystems By integrating advanced technologies with user-centric design, IOST 3.0 creates a DID framework that balances security, privacy, and usability, making truly self-sovereign digital identity accessible to individuals and organizations worldwide.
In an increasingly digital world, identity management is crucial. Traditional identity management systems, which rely on centralized authorities, are prone to issues such as data breaches and privacy violations. This is where decentralized identity management comes into play. Decentralized identity management allows individuals to own and control their personal information without relying on a central authority. Hyperledger Indy, an open-source project under the Hyperledger umbrella, is specifically designed for this purpose. When combined with React, a popular frontend library, it becomes a powerful tool for creating decentralized identity management systems that are both secure and user-friendly.
This guide will walk you through the process of building a decentralized identity management system using Hyperledger Indy and React. We will cover everything from the basics of decentralized identity to the installation and implementation of Hyperledger Indy and React, complete with coding examples, best practices, and real-world applications. For those interested in diving deeper into similar technologies, consider exploring building a remote GPU .
Decentralized identity (DID) is a concept where individuals can create and manage their own identities without relying on a central authority, such as a government or corporation. This is achieved through the use of blockchain technology, which ensures that identity information is stored in a secure and immutable manner. Decentralized identities are represented by Decentralized Identifiers (DIDs), which are globally unique identifiers that are created, owned, and controlled by the individual. These DIDs can be used to authenticate users, access services, and share information, all while maintaining privacy and control over personal data.
2. System Architecture & Core Working Principles Blockchain technology is fundamental to decentralized identity management. It provides a secure and transparent way to store and manage identity data without the need for a central authority. Each DID is anchored on the blockchain, ensuring that it is immutable and verifiable.
Hyperledger Indy is a blockchain platform specifically designed for decentralized identity. It offers a range of tools and libraries that make it easy to create and manage DIDs, issue and verify credentials, and build secure identity systems. Hyperledger Indy provides a comprehensive framework for decentralized identity management. It includes: Hyperledger Indy is designed to be interoperable with other identity systems, making it a versatile choice for building decentralized identity solutions.
For developers interested in other cutting-edge technologies, exploring IPFS and Ethereum integration might be beneficial. Before diving into the implementation, it's important to understand the architecture of Hyperledger Indy. At its core, Hyperledger Indy consists of the following components: To begin building your decentralized identity management system, you need to set up a development environment. This includes installing the necessary tools and dependencies.
If you're new to Node.js or React, you might find WebAssembly advantages and disadvantages guide useful for understanding modern web development practices. Once the prerequisites are installed, you can install the necessary dependencies. Start by installing the Indy SDK, which provides the core libraries for building decentralized identity solutions.
For more complex applications, you may want to explore [using Zod with TypeScript]( https://bytesup To test your application, you'll need to set up a local Indy network. This can be done using Docker, which allows you to run multiple Indy nodes on your local machine. This command will create a pool of Indy nodes that you can use for testing your application.
If you are interested in scaling your solutions or integrating other services, you might consider looking into Zookeeper distributed lock service to manage distributed systems effectively. A wallet in Hyperledger Indy is a secure storage container that holds identity data, such as DIDs, credentials, and private keys. Each wallet is protected by a key, ensuring that only the owner can access the data stored within it.
Wallets are fundamental to decentralized identity management because they provide a secure way to store and manage sensitive identity information. Decentralized Identifiers (DIDs) are a key component of decentralized identity systems. A DID is a unique identifier that is created and controlled by the individual, without the need for a central authority. DIDs are globally unique and can be used to authenticate users, access services, and share information securely.
Each DID is associated with a DID document, which contains information about the DID, such as public keys and service endpoints. This document is stored on the blockchain, ensuring that it is secure and immutable. In a decentralized identity system, credentials are issued by trusted entities and stored in the user's wallet. These credentials can be used to verify the user's identity when accessing services.
For more advanced concepts and use cases, consider reading GraphQL microservices tutorial to explore how microservices can enhance decentralized systems. The first step in building your backend is to set up a Node.js environment. This involves creating a new Node.js project and installing the necessary dependencies.
This command creates a new Node.js project and installs the Indy SDK and Express.js, a popular web framework for Node.js. The Indy SDK provides a set of libraries for interacting with the Indy network. You can use these libraries to create and manage wallets, DIDs, and credentials. In many cases, you'll need to store identity data in a database. While Hyperledger Indy stores DIDs and credentials on the blockchain, other data, such as user profiles and application settings, may need to be stored in a traditional database.
You can connect your Node.js backend to a database, such as PostgreSQL or MongoDB, using an ORM (Object-Relational Mapping) tool like Sequelize or Mongoose. This command installs Sequelize and the PostgreSQL driver. You can then use Sequelize to define models and interact with the database: Security is a critical concern when building decentralized identity systems. Here are some best practices for securing your backend: For those looking to deepen their understanding of security in decentralized systems, the WebAssembly advantages and disadvantages guide offers valuable insights into secure code execution in the browser.
The frontend of your decentralized identity management system will be built using React. React is a popular JavaScript library for building user interfaces, known for its component-based architecture and powerful state management features. As your project grows, it's important to structure your code in a way that is easy to maintain and scale. Here is a suggested directory structure for your React project: For those interested in enhancing their React projects with advanced features, check out the GraphQL microservices tutorial for integrating microservices into your application.
To connect your React frontend to the Hyperledger Indy backend, you'll need to create a service module that interacts with the Indy SDK. This module provides functions for creating wallets and DIDs, which can be called from your React components. React Hooks provide a powerful way to manage state and side effects in your components. Here is an example of how to use hooks to manage the state of a wallet in a React component: This component allows users to create a wallet and generate a DID. The state of the wallet and DID is managed using React Hooks.
A user-friendly UI is essential for a decentralized identity management system. In this section, we will create a simple form that allows users to create a wallet and manage their identity. The React Context API is a powerful tool for managing global state in your application. It allows you to share state across multiple components without having to pass props down the component tree.
Here is an example of how to use the Context API to manage the state of a user's wallet: This code creates a WalletContext that can be used to access the wallet state from any component in your application. Error handling is an important aspect of any application. In a decentralized identity system, it is crucial to handle errors gracefully, especially when dealing with sensitive operations like creating wallets and issuing credentials.
Lazy loading is a technique that allows you to load components only when they are needed. This can improve the performance of your application by reducing the initial load time. This code uses the lazy function to load the IdentityForm component only when it is needed. A responsive design ensures that your application looks good on all devices, from desktops to mobile phones. You can achieve this by using CSS media queries and a responsive grid system, such as CSS Grid or Flexbox.
For those looking to improve their UI development skills, the WebAssembly advantages and disadvantages guide is a great resource for learning how to optimize performance and security in web applications. In some applications, users may need to manage multiple wallets and DIDs. You can extend your React application to support this by modifying the state management logic to handle an array of wallets.
Biometric authentication, such as fingerprint or facial recognition, can enhance the security of your decentralized identity system. You can integrate biometric authentication into your React application using a library like WebAuthn or the device's native biometric APIs. This code starts a WebAuthn authentication process, which can be used to authenticate users with their biometric data.
3. Software Implementation, Frameworks & Protocols Role-Based Access Control (RBAC) is a method for restricting access to certain parts of your application based on the user's role. You can implement RBAC in your React application by defining roles and permissions in your backend and enforcing them in your frontend.
The InterPlanetary File System (IPFS) is a decentralized storage network that allows you to store and share files in a distributed manner. You can use IPFS to store identity data, credentials, and other sensitive information in your decentralized identity management system. Here is an example of how to upload a file to IPFS using the ipfs-http-client library: For more on decentralized storage, the article on IPFS and Ethereum integration provides a comprehensive overview.
Real-time notifications can enhance the user experience by providing instant feedback on identity-related actions, such as credential issuance or verification. You can implement real-time notifications in your React application using WebSockets. This component listens for WebSocket messages and updates the UI with new notifications. In some cases, you may need to integrate your decentralized identity system with other blockchains, such as Ethereum. This can be useful for creating cross-chain identity management solutions or for leveraging smart contracts.
Here is an example of how to interact with an Ethereum smart contract from your React application: For more information on blockchain integration, the article on IPFS and Ethereum integration provides valuable insights. Unit testing is essential for ensuring the quality and reliability of your code. Jest and React Testing Library are popular tools for testing React applications.
End-to-end testing involves testing your application from the user's perspective. Cypress is a popular tool for end-to-end testing. This test simulates a user creating a new wallet and checks that the DID is created successfully. When working with Hyperledger Indy, you may encounter common issues, such as wallet errors or connection problems. Here are some tips for debugging these issues: Performance testing is important to ensure that your application can handle the expected load. Here are some tools and techniques for profiling and performance testing: For developers interested in performance optimization, the GraphQL microservices tutorial provides insights into building scalable and efficient microservices.
Deploying your decentralized identity management system involves setting up the infrastructure, configuring the environment, and deploying the application. Containerization is a popular method for packaging and deploying applications. Docker allows you to package your application and its dependencies into a container, which can be deployed on any platform that supports Docker.
For those managing complex deployments, the Zookeeper distributed lock service is a valuable resource for managing distributed systems. Kubernetes is an open-source platform for automating the deployment, scaling, and management of containerized applications. You can use Kubernetes to deploy your application and scale it based on demand.
This configuration deploys three replicas of your React application and exposes it on port 5000. You can deploy your application on a cloud platform, such as AWS, Azure, or GCP. Each platform offers services for hosting web applications, managing databases, and scaling infrastructure. Continuous Integration (CI) and Continuous Deployment (CD) are practices that involve automatically building, testing, and deploying your application. Setting up a CI/CD pipeline ensures that your application is always in a deployable state.
This pipeline installs dependencies, runs tests, builds the application, and deploys it to an AWS S3 bucket. Monitoring and logging are essential for maintaining the health and performance of your application in production. Prometheus is a popular monitoring tool that collects and stores metrics, while Grafana is used to visualize these metrics. For developers interested in advanced monitoring techniques, the Zookeeper distributed lock service article provides insights into monitoring distributed systems.
Logging is essential for diagnosing issues and understanding the behavior of your application. Here are some best practices for logging: Decentralized identity management is being adopted in various industries, including finance, healthcare, and education. Here are some real-world use cases: Many enterprises are adopting Hyperledger Indy to build decentralized identity solutions. Here are some examples: In this case study, we will explore how a healthcare organization implemented Hyperledger Indy to create a decentralized identity system for managing patient records.
The healthcare organization faced challenges in managing patient records, such as data breaches, interoperability issues, and the inability to The organization implemented a decentralized identity system using Hyperledger Indy. The system allowed patients to create and manage their own identities and gave them control over their health records.
The decentralized identity system improved the security and privacy of patient records, reduced the risk of data breaches, and improved the interoperability of health records across different healthcare providers. For those interested in other advanced applications, consider exploring GraphQL microservices tutorial for integrating microservices into enterprise systems.
Decentralized identity management is a rapidly evolving field. Here are some trends to watch in the coming years: Decentralized identity management raises a number of regulatory and compliance issues, such as data protection, privacy, and compliance with laws and regulations. Privacy is a major concern in decentralized identity management. Here are some solutions to address privacy concerns: Scalability is a challenge in decentralized identity management, especially as the number of users and transactions grows.
Here are some strategies to address scalability challenges: Interoperability is critical in decentralized identity management, especially as more organizations and systems adopt decentralized identity solutions. Here are some strategies to ensure interoperability: User adoption and education are critical to the success of decentralized identity systems. Here are some strategies to manage user adoption and education: Building a decentralized identity management system with Hyperledger Indy and React is a powerful way to ensure privacy, security, and control over personal information. In this guide, we have covered everything from the basics of decentralized identity to the installation and implementation of Hyperledger Indy and React, along with coding examples, best practices, and real-world applications.
Decentralized identity is a rapidly evolving field, and there is much more to explore. Whether you are a developer, a business owner, or simply someone interested in the future of identity management, we hope this guide has provided you with valuable insights and practical knowledge. For further reading on modern web development and decentralized technologies, consider exploring the following resources: What if verifying a customer’s identity also made your business a bigger target for hackers? That means more data to protect, more compliance pressure, and more risk when something goes wrong.
Blockchain identity management changes this model with Self-Sovereign Identity (SSI), letting users control their credentials while businesses verify them without storing unnecessary personal data. 4. Practical Deployment, Analysis & Case Studies Traditional Identity access management augments access control with additional layers of security based on identity.
However, a working blockchain identity management system uses a framework known as Self-Sovereign Identity (SSI) . Blockchain Identity management puts the user first. Individuals hold complete ownership and control over their data through a private digital wallet on their device. Here, your blockchain's role is very specific and limited. The traditional identity model pushes your company into being a single point where things can go wrong. You must collect, store, and protect massive, centralized databases of Personally Identifiable Information (PII).
The user's PII (the VCs) is kept only in their own encrypted digital wallet. When you need to check on a user, they show a cryptographic proof, not the data itself. Blockchain identity management shifts the liability of storage away from your enterprise. This drastically cuts down your risk profile and the potential impact of a system breach.
In high-compliance sectors like BFSI (Banking, Financial Services, and Insurance), Know Your Customer (KYC) and Anti-Money Laundering (AML) processes are a major source of cost, delays, and customer drop-off. Decentralized identity makes the concept of re-usable KYC possible. A user carries out a thorough KYC check with one trusted entity (like their primary bank). That entity then gives them a KYC Verified Verifiable Credential.
The user can then show this VC to any other service. Examples include a new bank, an investment platform, or a healthcare provider. Blockchain identity management helps businesses to run more smoothly by making it possible to: Blockchain-based identity can simplify parts of the architecture, but still requires careful design for privacy, revocation, and governance. Because the PII is never stored on the blockchain and is kept only in the user's wallet, compliance with data deletion requests is simple.
The user deletes the credential from their wallet. The data was never in your database to begin with. The only thing on the blockchain is the DID (a string of numbers and letters). The public key of the issuer is also there. No PII is present. Blockchain-based SSI makes verification easier, but full auditability still depends on how revocation, logging and governance are implemented. You can do this without ever having stored the sensitive data itself.
Today's users are pushed into an all-or-nothing data-sharing transaction. To prove they are over 21, they must show a driver's license. This action also gives away their full name, home address, exact birthdate, and more. This is giving away too much PII for a simple yes/no question. This is the main problem that minimal disclosure gets around. A Verifiable Credential can hold many pieces of information.
However, the user's wallet can be set up to respond only with the specific claim needed. Your enterprise does not just manage customer identities. Your enterprise also manages employees, contractors, and B2B partners. A blockchain identity framework can be used internally. This can replace the password with verifiable employee credentials.
Microsoft's Entra Verified ID platform is a prime example. An employee is given a Verified Employee VC. They store this in their wallet. To get into a system, they scan a QR code. Their wallet shows the credential. The system checks it in seconds. Blockchain identity systems processes are faster for the employee and dramatically more secure for the company. Using Blockchain identity access control is a process resistant to phishing attacks that try to steal passwords.
How do you trust that a paper university diploma is real? Or that a PDF of a certification has not been changed? In the physical world, checking is slow, manual, and not dependable. Blockchain identity makes credentials tamper-proof and instantly verifiable. When a university gives out a digital diploma as a VC, it is cryptographically signed by the university's private key.
The public key is stored on the blockchain. The key is linked to the university's DID. An employer (Verifier) can instantly check the VC's signature against the university's public key. I The employer can cryptographically verify that the credential was issued by the claimed issuer and has not been altered. They also know it has not been changed.
A new and urgent reason for this technology is the rise of sophisticated AI and deepfake threats. How can your helpdesk know they are really talking to a customer? A deepfaked voice or video can get around traditional security questions. How can you trust a trusted partner? Their email could be a perfectly crafted AI spear-phishing attack. I Cryptographic proofs offer strong protection against deepfake impersonation, but secure key storage and device protection are still essential. In this new-threat landscape, the only way to build up trust is to demand cryptographic proof.
A user proving their identity with a VC from their wallet is a superior defense. This shifts authentication toward possession-based, cryptographic identity, which strengthens zero-trust defenses — when combined with secure device protection. The current model requires you to set up data stores. These are massive, centralized PII databases.
Centralized Identity can be a single point where things can go wrong. This makes you a high-value target for hackers. Breaches are not a matter of if but when. Recent incidents show this systemic failure affects billions of records. As the data controller, you bear 100% of the liability. You are responsible for securing data you do not need to own. You also face ever-increasing compliance costs from regulations like GDPR.
The Right to be Forgotten is almost impossible to manage. This is because user data is scattered across all your systems. Identity systems are dangerously vulnerable to theft because they are based on static information like passwords and security questions. They are also defenseless against threats like AI-driven deepfakes and spear-phishing attacks, which can easily bypass old security measures.
It makes it easy for attackers to steal those secrets through social engineering or phishing. A deepfaked voice or video can easily trick a helpdesk into resetting an account, leading to a full takeover. Fake identity scams and documents can also defeat traditional verification processes with alarming ease. Centralized identity management forces your business to create massive, toxic databases of Personally Identifiable Information (PII). These data stores create a single point of failure, making your company a high-value target for hackers.
With this you place 100% of the liability and regulatory burden, such as from GDPR, directly on your company. Even federated models create large, interconnected targets that lock users into specific platforms and make collaboration complex. This entire architecture is rigid, expensive, and fundamentally broken in the modern, high-threat landscape. This Web2 model grants you, the platform, complete control over a user's data. Centralized Identity creates a deep conflict with your users (They’re forced to agree to data collection). This platform-controlled access destroys user trust. Studies show only a tiny fraction of consumers actually trust companies with their identity data.
Your users are forced to manage dozens of separate accounts, passwords, and security questions. Centralized Identity has registration fatigue that creates a terrible, difficult user experience. Centralized Identity models can lead to abandoned sign-ups. This also leads to endless forgot password requests which are costly for your helpdesk and add to your IT overhead.
Processes like Know Your Customer (KYC) are a massive problem point and cost center. You spend significant time and money to check on an identity. Centralized Identity is a process that every other business in your industry is also doing for the same user. This makes it a slow, manual, and colossally redundant system for both you and your customer.
Because your identity system is a proprietary, closed system, working with partners is difficult. Your users' identities are locked into your platform. This rigidity makes B2B collaboration complex and slow. Centralized Identity also hinders innovation. This happens by forcing all services to build their own identity silo from scratch.
Stop letting data liability and compliance costs harm your company's performance. In the age of AI and massive data breaches, this way of working just makes no sense. So why wait to make a change? Using open, interoperable standards can speed up verification, get rid of data stores, and free your teams to build value rather than just protect data. With a standards-based method, you get: With over 17 years of experience in the software industry, Kapil is a serial entrepreneur and business leader with a deep understanding of identity and access management (IAM). As CMSO of Infisign Inc., Kapil leads strategic efforts to deliver the company’s zero-trust IAM product suite to market, offering solutions to critical enterprise challenges.His strategic vision and dedication to addressing real-world security challenges have established him as a trusted authority in the IAM industry.
5. Performance Evaluation & Extended Technical Observations Identity underpins virtually every aspect of your life today. Using online services, opening a bank account, voting in elections, buying property, securing employment—all of these things require proving your identity. However, traditional identity management systems have long relied on centralized intermediaries who issue, hold, and control your identifiers and . This means you cannot control your identity-related information or decide who has access to personally identifiable information (PII) and how much access these parties have.
To solve these problems, we have decentralized identity systems built on public blockchains like Ethereum . Decentralized identity allows individuals to manage their identity-related information. With decentralized identity solutions, you can create identifiers and claim and hold your attestations without relying on central authorities, like service providers or governments. Identity means an individual's sense of self, defined by unique characteristics. Identity refers to being an individual , i.e., a distinct human entity. Identity could also refer to other non-human entities, such as an organization or authority.
An explainer on how decentralized identity gives users more control over their digital identity, and keeps personal information on the internet safer using blockchain-based credentials. An identifier is a piece of information that acts as a pointer to a particular identity or identities. Common identifiers include: These traditional examples of identifiers are issued, held and controlled by central entities. You need permission from your government to change your name or from a social media platform to change your handle.
Decentralized identity increases individual control of identifying information. Decentralized identifiers and attestations can be verified without relying on centralized authorities and third-party services. Decentralized identity solutions facilitate a trustless, seamless, and privacy-protecting method for verifying and managing user identity.
Decentralized identity harnesses blockchain technology, which creates trust between different parties and provides cryptographic guarantees to prove the validity of attestations. Decentralized identity makes identity data portable. Users store attestations and identifiers in a mobile wallet and can share with any party of their choice. Decentralized identifiers and attestations are not locked into the database of the issuing organization.
Decentralized identity should work well with emerging technologies that will enable individuals to prove they own or have done something without revealing what that thing is. This could become a powerful way to combine trust and privacy for applications such as voting. Decentralized identity enables mechanisms to identify when one individual human is pretending to be multiple humans to game or spam some system.
Decentralized identity can help replace password-based logins with decentralized authentication. Service providers can issue attestations to users, which can be stored in an Ethereum wallet. An example attestation would be an granting the holder access to an online community. A Sign-In with Ethereum (opens in a new tab) function would then enable servers to confirm the user's Ethereum account and fetch the required attestation from their account address. This means users can access platforms and websites without having to memorize long passwords and improves the online experience for users.
Using many online services requires individuals to provide attestations and credentials, such as a driving license or national passport. But this approach is problematic because private user information can be compromised and service providers cannot verify the authenticity of the attestation. Decentralized identity allows companies to skip on conventional Know-Your-Customer (KYC) (opens in a new tab) processes and authenticate user identities via Verifiable Credentials. This reduces the cost of identity management and prevents the use of fake documentation.
Online voting and social media are two novel applications for decentralized identity. Online voting schemes are susceptible to manipulation, especially if malicious actors create false identities to vote. Asking individuals to present onchain attestations can improve the integrity of online voting processes. Decentralized identity can help create online communities that are free of fake accounts. For example, each user might have to authenticate their identity using an onchain identity system, like the Ethereum Name Service, reducing the possibility of bots.
Grant-giving applications that use are vulnerable to because the value of a grant is increased when more individuals vote for it, incentivizing users to split their contributions across many identities. Decentralized identities help to prevent this by raising the burden on each participant to prove that they are really human, although often without having to reveal specific private information.
Governments can use the principles of decentralized identity to issue foundational identity documents—such as national IDs, passports, or driver's licenses—as verifiable credentials on Ethereum, providing strong cryptographic guarantees of authenticity to reduce fraud and forgery in online identity verification. Citizens can store these attestations in their personal wallet and use them to prove their identity, age, or right to vote.
This model allows for selective disclosure, especially when combined with zero-knowledge proof (ZKP) privacy technology. For example, a citizen could cryptographically prove they are over 18 to access an age-restricted service without revealing their exact date of birth, offering greater privacy than a traditional ID. The Kingdom of Bhutan migrated its National Digital Identity (NDI) system (opens in a new tab) to Ethereum in October 2025.
Built on the principles of decentralized identity and self-sovereign identity, Bhutan’s NDI system uses decentralized identifiers and verifiable credentials to issue digitally signed credentials directly to a citizen's personal wallet. By anchoring issuer schemas of these credentials on Ethereum, the system ensures they are authentic, tamper-proof, and can be verified by any party without querying a central authority.
An attestation is a claim made by one entity about another entity. If you live in the United States, the driver's license issued to you by the Department of Motor Vehicles (one entity) attests that you (another entity) are legally allowed to drive a car. Attestations are different from identifiers. An attestation contains identifiers to reference a particular identity, and makes a claim about an attribute related to this identity. So, your driver's license has identifiers (name, date of birth, address) but is also the attestation about your legal right to drive.
Traditional identifiers like your legal name or email address rely on third parties—governments and email providers. Decentralized identifiers (DIDs) are different—they aren't issued, managed, or controlled by any central entity. Decentralized identifiers are issued, held, and controlled by individuals. An is an example of a decentralized identifier. You can create as many accounts as you want without permission from anyone and without the need to store them in a central registry.
Decentralized identifiers are stored on distributed ledgers ( ) or . This makes DIDs globally unique, resolvable with high availability, and cryptographically verifiable (opens in a new tab) . A decentralized identifier can be associated with different entities, including people, organizations, or government institutions. Public-key cryptography is an information security measure that generates a and for an entity. Public-key is used in blockchain networks to authenticate user identities and prove ownership of digital assets.
Some decentralized identifiers, such as an Ethereum account, have public and private keys. The public key identifies the account's controller, while the private keys can sign and decrypt messages for this account. Public key cryptography provides proofs needed to authenticate entities and prevent impersonation and use of fake identities, using cryptographic signatures (opens in a new tab) to verify all claims.
A blockchain serves as a verifiable data registry: an open, trustless, and decentralized repository of information. The existence of public blockchains eliminates the need to store identifiers in centralized registries. If anyone needs to confirm the validity of a decentralized identifier, they can look up the associated public key on the blockchain. This is different from traditional identifiers that require third parties to authenticate.
Decentralized identity is the idea that identity-related information should be self-controlled, private, and portable, with decentralized identifiers and attestations being the primary building blocks. In the context of decentralized identity, attestations (also known as Verifiable Credentials (opens in a new tab) ) are tamper-proof, cryptographically verifiable claims made by the issuer. Every attestation or Verifiable Credential an entity (e.g., an organization) issues is associated with their DID.
Because DIDs are stored on the blockchain, anyone can verify the validity of an attestation by cross-checking the issuer's DID on Ethereum. Essentially, the Ethereum blockchain acts like a global directory that enables the verification of DIDs associated with certain entities. Decentralized identifiers are the reason attestations are self-controlled and verifiable. Even if the issuer doesn't exist anymore, the holder always has proof of the attestation's provenance and validity.
Decentralized identifiers are also crucial to protecting the privacy of personal information through decentralized identity. For instance, if an individual submits proof of an attestation (a driver's license), the verifying party doesn't need to check the validity of information in the proof. Instead, the verifier only needs cryptographic guarantees of the attestation's authenticity and the identity of the issuing organization to determine if the proof is valid.
How attestation information is stored and retrieved in an Ethereum-based identity ecosystem is different from traditional identity management. Here is an overview of the various approaches to issuing, storing, and verifying attestations in decentralized identity systems: One concern with storing attestations onchain is that they might contain information individuals want to keep private. The public nature of the Ethereum blockchain makes it unattractive to store such attestations.
The solution is to issue attestations, held by users offchain in digital wallets, but signed with the issuer's DID stored onchain. These attestations are encoded as JSON Web Tokens (opens in a new tab) and contain the issuer's digital signature—which allows for easy verification of offchain claims. A university (the issuer) generates an attestation (a digital academic certificate), signs with its keys, and issues it to Bob (the identity owner).
Bob applies for a job and wants to prove his academic qualifications to an employer, so he shares the attestation from his mobile wallet. The company (the verifier) can then confirm the validity of the attestation by checking the issuer's DID (i.e., its public key on Ethereum). Under this arrangement attestations are transformed into JSON files and stored offchain (ideally on a decentralized cloud storage platform, such as IPFS or Swarm). However, a of the JSON file is stored onchain and linked to a DID via an onchain registry. The associated DID could either be that of the issuer of the attestation or the recipient.
This approach enables attestations to gain blockchain-based persistence, while keeping claims information encrypted and verifiable. It also allows for selective disclosure since the holder of the private key can decrypt the information. Onchain attestations are held in on the Ethereum blockchain. The smart contract (acting as a registry) will map an attestation to a corresponding onchain decentralized identifier (a public key).
A company (XYZ Corp) plans to sell ownership shares using a smart contract but only wants buyers that have completed a background check. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Blockchain • https://docs.iost.io/core-concepts/did-basics • https://dev.to/bytesupreme/building-a-decentralized-identity-management-system-with-hyperledger-indy-and-react-flo • https://www.infisign.ai/blog/blockchain-identity-management-a-complete-guide • https://ethereum.org/decentralized-identity
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Decentralized Identity Management System Using Blockchain.
[*] Metasploit Scan Running on Target Subnet for Decentralized Identity Management System Using Blockchain... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |