Complete Technical Paper Content — Deception Technology In Networks
Overview & System Context
Deception Technology In Networks: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9552 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Deception technology (also deception and disruption technology) is a category of cyber security defense mechanisms that provide early warning of potential cyber security attacks and alert organizations of unauthorized activity. Deception technology products can detect, analyze, and defend against zero-day and advanced attacks, often in real time. They are automated, accurate, and provide insight into malicious activity within internal networks which may be unseen by other types of cyber defense. Deception technology seeks to deceive an attacker, detect them, and then defeat them. Deception technology considers the point of view of human attackers and method for exploiting and navigating networks to identify and exfiltrate data. It integrates with existing technologies to provide new visibility into the internal networks, share high probability alerts and threat intelligence with the existing infrastructure.
Traditional cyber defense technologies such as firewalls and endpoint security seek primarily to defend a perimeter, but they cannot do so with 100% certainty. Heuristics may find an attacker within the network, but often generate so many alerts that critical alerts are missed. In a large enterprise, the alert volume may reach millions of alerts per day. Security operations personnel cannot process most of the activity easily, yet it only takes one successful penetration to compromise an entire network. This means cyber-attackers can penetrate these networks and move unimpeded for months, stealing data and intellectual property. Deception technology produces alerts that are the end product of a binary process. Probability is essentially reduced to two values: 0% and 100%. Any party that seeks to identify, ping, enter, view any trap or utilizes a lure is immediately identified as malicious by this behavior because anyone touching these traps or lures should not be doing so.
This certainty is an advantage over the many extraneous alerts generated by heuristics and probability-based. Best practice shows that deception technology is not a stand-alone strategy. Deception technology is an additional compatible layer to the existing defense-in-depth cyber defense. Partner integrations make it most useful. The goal is to add protection for the most advanced and sophisticated human attackers that will successfully penetrate the perimeter.
Deception is the act of convincing one or many recipients of untrue information. The person creating the deception knows it to be false while the receiver of the information does not. It is often done for personal gain or advantage. Deceit and dishonesty can also form grounds for civil litigation in tort, or contract law (where it is known as misrepresentation or fraudulent misrepresentation if deliberate), or give rise to criminal prosecution for fraud.
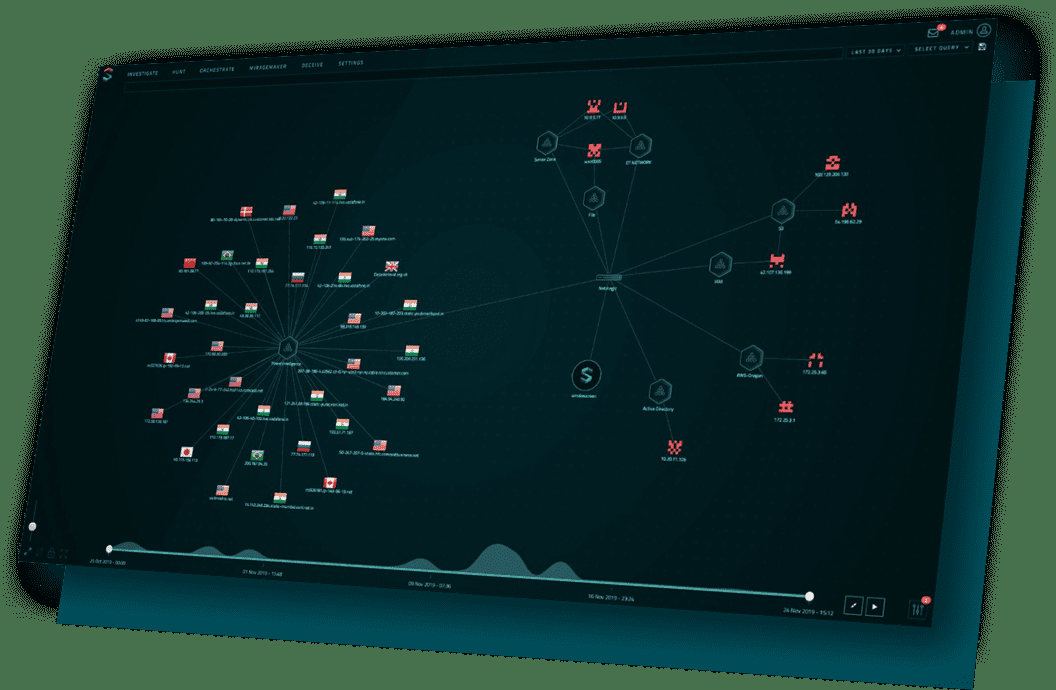
The Interpersonal Deception Theory explores the interrelation between communicative context and sender and receiver cognitions and behaviors in deceptive exchanges. Some forms of deception include: Figure 1: Deception Technology 101 | Smokescreen Lies: making up information or giving information that is the opposite or very different from the truth. Equivocations: making an indirect, ambiguous, or contradictory statement. Concealments: omitting information that is important or relevant to the given context, or engaging in behavior that helps hide relevant information. Exaggerations: overstatement or stretching the truth to a degree. Understatements: minimization or downplaying aspects of the truth. Untruths: misinterpreting the truth. Buller and Burgoon (1996) have proposed three taxonomies to distinguish motivations for deception based on their Interpersonal Deception Theory: Instrumental: to avoid punishment or to protect resources Relational: to maintain relationships or bonds Identity: to preserve "face" or the self-image The camouflage of a physical object often works by breaking up the visual boundary of that object. This usually involves colouring the camouflaged object with the same colours as the background against which the object will be hidden. Military camouflage as a form of visual deception is a part of many campaigns.
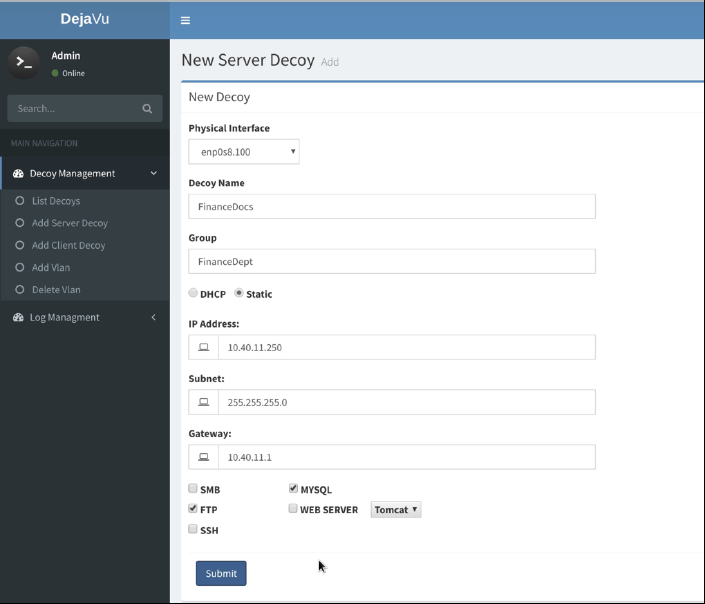
Disguises are used to create the impression of a false appearance. A seventeenth-century story collection, Zhang Yingyu's The Book of Swindles (ca. 1617), offers multiple examples of the bait-and-switch and fraud techniques involving the stimulation of greed in Ming-dynasty China. Figure 2: Dejavu - Open Source Deception Framework To Improve Network Defense Deception has also been observed and studied in romantic relationships. There are three primary motivations for deception in relationships.
Deception impacts the perception of a relationship in a variety of ways, for both the deceiver and the deceived. The deceiver typically perceives less understanding and intimacy from the relationship, in that they see their partner as less empathetic and more distant. The act of deception can also result in feelings of distress for the deceiver, which become worse the longer the deceiver has known the deceived, as well as in longer-term relationships. Once discovered, deception creates feelings of detachment and uneasiness surrounding the relationship for both partners; this can eventually lead to both partners becoming more removed from the relationship or deterioration of the relationship. In general, discovery of deception can result in a decrease in relationship satisfaction and commitment level, however, in instances where a person is successfully deceived, relationship satisfaction can actually be positively impacted for the person deceived, since lies are typically used to make the other partner feel more positive about the relationship. In general, deception tends to occur less often in relationships with higher satisfaction and commitment levels and in relationships where partners have known each other longer, such as long-term relationships and marriage. In comparison, deception is more likely to occur in casual relationships and in dating where commitment level and length of acquaintanceship is often much lower.
Unique to exclusive romantic relationships is the use of deception in the form of infidelity. When it comes to the occurrence of infidelity, many individual difference factors can impact this behavior. Infidelity is impacted by attachment style, relationship satisfaction, executive function, sociosexual orientation, personality traits, and gender. Attachment style impacts the probability of infidelity and research indicates that people with an insecure attachment style (anxious or avoidant) are more likely to cheat compared to individuals with a secure attachment style, especially for avoidant men and anxious women.
Insecure attachment styles are characterized by a lack of comfort within a romantic relationship resulting in a desire to be overly independent (avoidant attachment style) or a desire to be overly dependent on their partner in an unhealthy way (anxious attachment style). Those with an insecure attachment style are characterized by not believing that their romantic partner can/will support and comfort them in an effective way, either stemming from a negative belief regarding themselves (anxious attachment style) or a negative belief regarding romantic others (avoidant attachment style). Women are more likely to commit infidelity when they are emotionally unsatisfied with their relationship whereas men are more likely to commit infidelity if they are sexually unsatisfied with their current relationship. Women are more likely to commit emotional infidelity than men while men are more likely to commit sexual infidelity than women; however, these are not mutually exclusive categories as both men and women can and do engage in emotional or sexual infidelity. Executive control is a part of executive functions that allows individuals to monitor and control their behavior through thinking about and managing their actions. The level of executive control that an individual possesses is impacted by development and experience and can be improved through training and practice. Those individuals who show a higher level of executive control can more easily influence/control their thoughts and behaviors in relation to potential threats to an ongoing relationship which can result in paying less attention to threats to the current relationship (other potential romantic mates). Sociosexual orientation is concerned with how freely individuals partake in casual sex outside of a committed relationship and their beliefs regarding how necessary it is to be in love to engage in sex with someone. Individuals with a less restrictive sociosexual orientation (more likely to partake in casual sex) are more likely to engage in infidelity. Individuals who have personality traits including (high) neuroticism, (low) agreeableness, and (low) conscientiousness are more likely to commit infidelity. Men are generally speculated to cheat more than women, but it is unclear if this is a result of socialization processes where it is more acceptable for men to cheat compared to women or due to an actual increase in this behavior for men. Research conducted by Conley and colleagues (2011) suggests that the reasoning behind these gender differences stems from the negative stigma associated with women who engage in casual sex and inferences about the sexual capability of the potential sexual partner.
In their study, men and women were equally likely to accept a sexual proposal from an individual who was speculated to have a high level of sexual prowess. Additionally, women were just as likely as men to accept a casual sexual proposal when they did not anticipate being subjected to the negative stigma of sexually permissible women as slutty. Research on the use of deception in online dating has shown that people are generally truthful about themselves with the exception of physical attributes to appear more attractive. According to the Scientific American, "nine out of ten online daters will fib about their height, weight, or age" such that men were more likely to lie about height while women were more likely to lie about weight. In a study conducted by Toma and Hancock, "less attractive people were found to be more likely to have chosen a profile picture in which they were significantly more attractive than they were in everyday life". Both genders used this strategy in online dating profiles, but women more so than men. Additionally, less attractive people were more likely to have "lied about objective measures of physical attractiveness such as height and weight". In general, men are more likely to lie on dating profiles the one exception being that women are more likely to lie about weight.
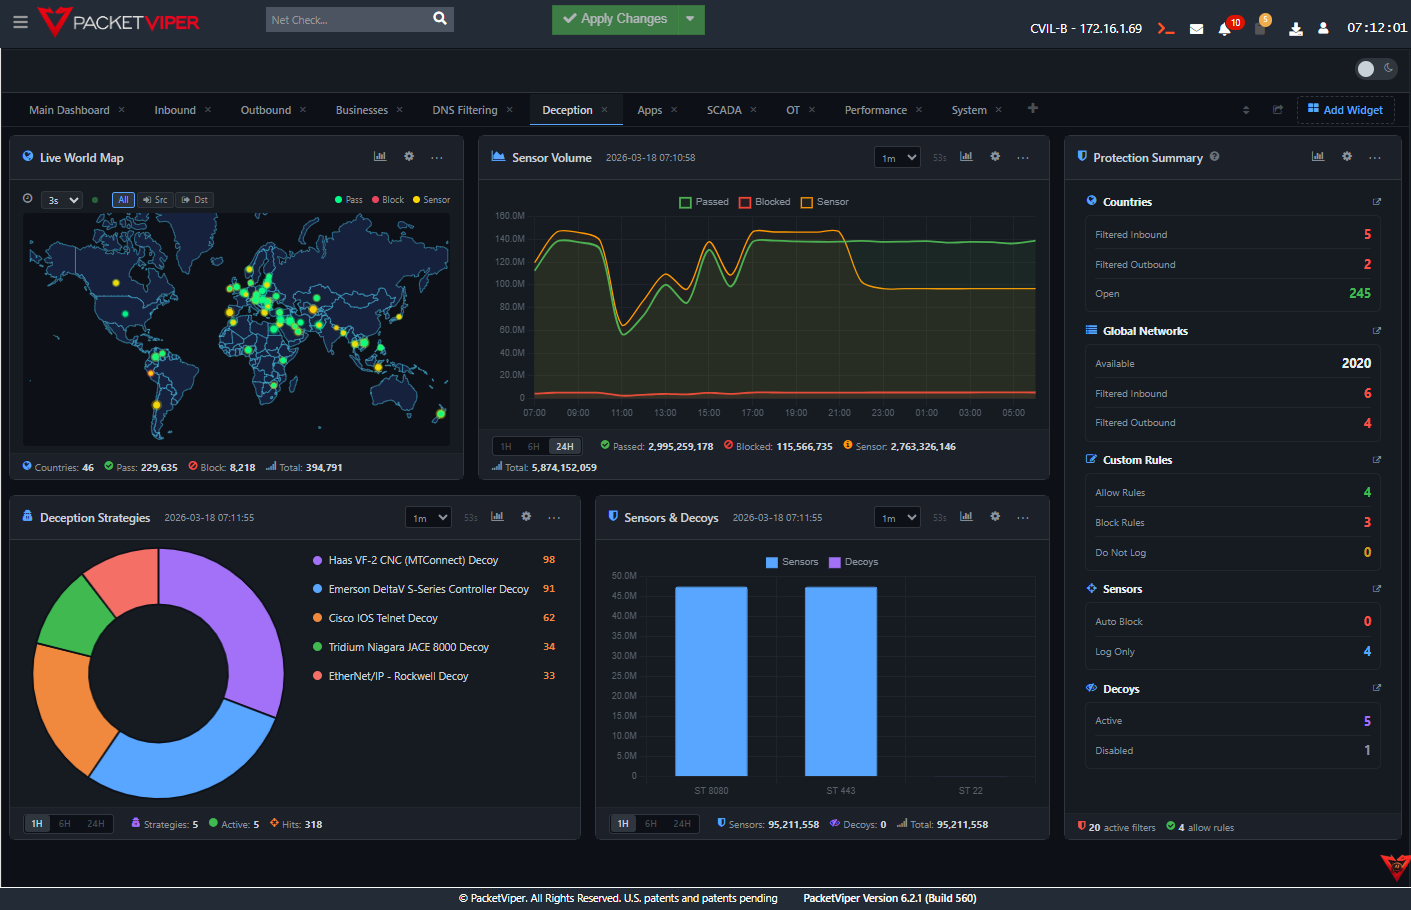
Figure 3: Deception Technology & AMTD for OT/IT Networks | PacketViper Price reservation: Not stating the real budget or price that one has in mind. Misrepresentation of interests: Getting interests if the buyer seems desperate. Fabrication of facts: This is the most immoral part, where the person lies about materials and misleading information to get a sale. Omitting relevance: Not stating something helpful to know: for example, a car can be like new but it does not help if the seller omits the fact that there is a problem with the transmission.
Journalistic deception ranges from passive activities (i.e. blending into a civil rights march) to active deception (i.e. falsely identifying oneself over the telephone, getting hired as a worker at a mental hospital). Paul Braun says that the journalist does not stand apart from the rest of the populace in the use of deception. For legal purposes, deceit is a tort that occurs when a person makes a factual misrepresentation, knowing that it is false (or having no belief in its truth and being reckless as to whether it is true) and intending it to be relied on by the recipient, and the recipient acts to his or her detriment in reliance on it. Deceit may also be grounds for legal action in contract law (known as misrepresentation, or if deliberate, fraudulent misrepresentation), or a criminal prosecution, on the basis of fraud.
In general, Islam never allows deception and lies. Prophet Muhammad said, "He who deceives is not of me (is not my follower)". However, there are some exceptions, especially in case of war or peace making or in case of safeguarding one's faith. For an example, Taqiya is an Islamic juridical term for the cases in which a Muslim is allowed to lie under the circumstances when needed to deny their faith due to force or when faced with persecution. The concept mainly followed by Shi'ite sect, but it varies "significantly among Islamic sects, scholars, countries, and political regimes", and has been evoked by critics of Islam to portray the faith allowing dishonesty.
Active defense can refer to a defensive strategy in the military or cybersecurity arena. In the cybersecurity arena, active defense may mean "asymmetric defenses," namely defenses that increase costs to cyber-adversaries by reducing costs to cyber-defenders. For example, an active defense data protection strategy leverages dynamic data movement, distribution, and re-encryption to make data harder to attack, steal, or destroy. Prior data protection approaches relied on encryption of data at rest, which leaves data vulnerable to attacks including stealing of ciphertext, cryptographic attack, attacks on encryption keys, destruction of encrypted data, ransomware attacks, insider attacks, and others. Three ACM computing conferences have explored moving target defense as a strategy for network and application-level security as well, for instance by rotating IP addresses or dynamically changing network topologies. Production implementations of MTD are provided by companies for applications including legacy systems, communications, and election security. Additionally, "active defense measures" are often another term used to define and refer to offensive cyber operations (OCOs) or computer network attacks (CNAs). Some have defined active defenses as including of deception or honeypots, which seek to confuse attackers with traps and advanced forensics. Examples of such honeypot technologies include Illusive Networks, TrapX, Cymmetria, Attivo, and others. Other types of active defenses might include automated incident response, which attempts to tie together different response strategies in order to increase work for attackers and decrease work for defenders.
Deception technology (also deception and disruption technology ) is a category of cyber security defense mechanisms that provide early warning of potential cyber security attacks and alert organizations of unauthorized activity. Deception technology products can detect, analyze, and defend against zero-day and advanced attacks, often in real time. They are automated, accurate, [ 1 ] and provide insight into malicious activity within internal networks which may be unseen by other types of cyber defense. Deception technology seeks to deceive an attacker, detect them, and then defeat them.
Deception technology considers the point of view of human attackers and method for exploiting and navigating networks to identify and exfiltrate data. It integrates with existing technologies to provide new visibility into the internal networks, share high probability alerts and threat intelligence with the existing infrastructure. Deception technology automates the creation of traps (decoys) and lures, which are strategically integrated among existing IT resources. These decoys provide an additional layer of protection to thwart attackers who have breached the network. Traps can be IT assets that utilize genuine licensed operating system software or emulate various devices, such as medical devices , automated teller machines (ATMs), retail point-of-sale systems , switches, routers, and more. On the other hand, lures typically consist of real information technology resources, such as files of different types, that are placed on actual IT assets .
Due to advancement in the area of cybersecurity, deception technology programs are increasingly proactive in approach and produce fewer false-positive alerts. The goal is to accurately discover the intention of the attacker and their tactics, technique and procedure. These information will enable effective response from the deception technology platforms. [ 2 ] Upon penetrating the network, attackers seek to establish a backdoor and then use this to identify and exfiltrate data and intellectual property. They begin moving laterally through the internal VLANs and almost immediately will "encounter" one of the traps. Interacting with one of these "decoys" will trigger an alert. These alerts have very high probability and almost always coincide to an ongoing attack. The deception is designed to lure the attacker in – the attacker may consider this a worthy asset and continue by injecting malware . Deception technology generally allows for automated static and dynamic analysis of this injected malware and provides these reports through automation to the security operations personnel. Deception technology may also identify, through indicators of compromise (IOC), suspect end-points that are part of the compromise cycle. Automation also allows for an automated memory analysis of the suspect endpoints, and then automatically isolating the suspect endpoints.
Internet of things (IoT) devices are not usually scanned by legacy defense in depth and remain prime targets for attackers within the network. Deception technology can identify attackers moving laterally into the network within these devices. Integrated turnkey devices that utilize embedded operating systems but do not allow these operating systems to be scanned or closely protected by embedded end-point or intrusion detection software are also well protected by a deception technology deployment in the same network. Examples include process control systems (SCADA) used in many manufacturing applications on a global basis. Deception technology has been associated with the discovery of Zombie Zero , [ 3 ] an attack vector . Deception technology identified this attacker utilizing malware embedded in barcode readers which were manufactured overseas.
Medical devices are particular vulnerable to cyber-attacks within the healthcare networks. As FDA -certified devices, they are in closed systems and not accessible to standard cyber defense software. Deception technology can surround and protect these devices and identify attackers using backdoor placement and data exfiltration. Recent documented cyber attacks on medical devices include x-ray machines , CT scanners , MRI scanners, blood gas analyzers, PACS systems and many more.
Networks utilizing these devices can be protected by deception technology. This attack vector, called medical device hijack or medjack, is estimated to have penetrated many hospitals worldwide. [ 4 ] Specialized deception technology products are now capable of addressing the rise in ransomware by deceiving ransomware into engaging in an attack on a decoy resource, while isolating the infection points and alerting the cyber defense software team. [ 5 ] Honeypots were perhaps the first very simple form of deception. A honeypot appeared simply as an unprotected information technology resource and presented itself in an attractive way to a prospective attacker already within the network. However, most early honeypots exhibit challenges with functionality, integrity and overall efficacy in meeting these goals. A key difficulty was lack of automation that enabled broad scale deployment; a deployment strategy that aimed to cover an enterprise where up to tens of thousands of VLANS needed to be protected would not be economically efficient using manual processes and manual configuration.
The gap between legacy honeypots and modern deception technology has diminished over time and will continue to do so. Modern honeypots constitute the low end of the deception technology space today. Traditional cyber defense technologies such as firewalls and endpoint security seek primarily to defend a perimeter, but they cannot do so with 100% certainty. Heuristics may find an attacker within the network, but often generate so many alerts that critical alerts are missed. In a large enterprise, the alert volume may reach millions of alerts per day. Security operations personnel cannot process most of the activity easily, yet it only takes one successful penetration to compromise an entire network. This means cyber-attackers can penetrate these networks and move unimpeded for months, stealing data and intellectual property .
Deception technology produces alerts that are the end product of a binary process. Probability is essentially reduced to two values: 0% and 100%. Any party that seeks to identify, ping , enter, view any trap or utilizes a lure is immediately identified as malicious by this behavior because anyone touching these traps or lures should not be doing so. This certainty is an advantage over the many extraneous alerts generated by heuristics and probability-based.
Best practice shows that deception technology is not a stand-alone strategy. Deception technology is an additional compatible layer to the existing defense-in-depth cyber defense. Partner integrations make it most useful. The goal is to add protection for the most advanced and sophisticated human attackers that will successfully penetrate the perimeter. 2. System Architecture & Core Working Principles Deception enables a more proactive security act. Deception aims to avoid a cybercriminal that has managed to penetrate a network from doing any huge damage. It offers a more accurate and quicker detection of attackers. It creates no false positives. Honeypots were the first simple form of deception. It is intended to detect existing intrusions and return that breach intelligence directly to the network’s security team. Any other cybersecurity sends a huge amount of alerts for being attacked each alert needs to be solved specifically but a maximum of them are false positives this is too time-consuming and requires more and more employees. So all we need to reduce the false positives alerts but that increases the possibility of false negatives. The potential for false negatives is more effective than false positives, to detect this kind of threats we need to use the Deception Technology.
Working Principle of Deception Technology: The Deception Technology is for MILDEC or military deception. The Deception Technology's working principle is much simpler to understand, a false decoy network will run on-existing infrastructure, but not visible by genuine staff. When any hacker or intruder visits that infrastructure they will be able to see the decoy as an opportunity to hack the infrastructure and they will fall for that. The decoy for the intruder must be simple, so the intruder can easily break through the guard and fall for the trap. The decoy should behave like important information or data for the organization only then the attacker will penetrate the security. The setup of Deception Technology should not be distinguishable by the intruders. Set-up is best done automatically by a system that maps the real network which defines the content and positioning of decoys. Deception Technology applicable methods: Importance of Deception Technology: Deception Technology depends upon recognition of presence rather than known signatures. It will identify all types of intrusion and intruder whether that is a cybercriminal, a contractor doing more than the agreement specifies, or an employee seeking information on an upcoming merger.
Deception technology deploys believable traps and decoys to detect, study, and derail attackers by luring them into interacting with fake assets. Analogy: a digital honeypot garden where the weeds reveal the intruder. Formal: engineered artifact set that generates high-fidelity alerts via intentional attacker interactions. Deception technology is a defensive security approach that intentionally introduces decoys, fake services, credentials, and breadcrumbs into an environment to detect adversaries, gather intelligence, and disrupt attack progress. It is not a replacement for prevention controls like firewalls or patching. It is complementary: detection-first, investigation-focused, and threat-intelligence producing.
Deception technology creates realistic but inert traps and breadcrumbs in an environment to reliably detect and analyze attacker activity while minimizing noise and risk to production. Glossary entries below contain term — definition — why it matters — common pitfall. Each entry is concise. 1) Prerequisites: – Inventory of assets and high-value targets. – Observability pipeline with low-latency collectors. – SOC or assigned analyst team and runbooks. – CI/CD access for injecting breadcrumbs. – Legal and compliance review.
2) Instrumentation plan: – Identify asset classes for decoy placement. – Decide decoy types (honeyfile, fake service, token). – Create templates and naming conventions that blend in. – Define lifecycle and rotation schedule. 3) Data collection: – Ensure collectors capture decoy interactions with full headers and context. – Route telemetry to SIEM/observability and to a secure forensic store. – Apply enrichment and tagging rules.
4) SLO design: – Define SLIs such as time to detect and containment success. – Set SLOs per environment criticality. – Allocate error budget for security operations related to deception. 5) Dashboards: – Build executive, on-call, and debug dashboards following guidance above. 6) Alerts & routing: – Define severity mapping for deception interactions. – Integrate with pager system and SOC ticketing. – Build automated containment runbooks with kill-switches and manual approval gates.
7) Runbooks & automation: – Create triage playbook templates. – Define containment automation safe paths (isolate NIC, revoke token). – Version runbooks in source control. 8) Validation (load/chaos/gamedays): – Run red-team exercises and gamedays. – Test decoy resilience under load. – Validate enrichment latencies and artifact capturing.
9) Continuous improvement: – Rotate decoys and refine fingerprints. – Use postmortems to update deployment and triage flows. – Track KPI trends and adjust SLOs. 1) Credential exfiltration detection – Context: Leaked creds accessed by attacker. – Problem: Silent lateral movement using stolen tokens. – Why deception helps: Fake credentials alert on first use. – What to measure: Credential interaction rate and time to detect. – Typical tools: CICanary Plugin, CloudTrap Metrics.
2) Lateral movement mapping – Context: Multi-host compromise progression. – Problem: Hard to observe attacker path in microservices. – Why deception helps: Decoys across hosts reveal hop sequence. – What to measure: Interaction diversity and sequence length. – Typical tools: Distributed Overlay Pattern, K8sHoney Controller. 3) Early pipeline leak detection – Context: Secrets leak from build artifacts. – Problem: Exposure before production deploys. – Why deception helps: Canary tokens in CI detect misuse early. – What to measure: Repo token triggers and downstream access. – Typical tools: CICanary Plugin.
4) Cloud instance metadata abuse – Context: Attackers request metadata to get tokens. – Problem: IMDS exploitation for privilege escalation. – Why deception helps: Fake IMDS endpoints capture calls. – What to measure: IMDS access attempts to decoys. – Typical tools: CloudTrap Metrics. 5) Ransomware staging detection – Context: Attacker prepares data exfiltration. – Problem: Encryption and staging often precede ransom. – Why deception helps: Honeyfiles detect file collection attempts. – What to measure: Honeyfile open and copy events. – Typical tools: Endpoint deception agents.
6) Compromised third-party tool detection – Context: Vendor tools used for maintenance. – Problem: Attacker leverages third-party paths. – Why deception helps: Breadcrumbs indicate misuse of vendor paths. – What to measure: Access to vendor-named decoys. – Typical tools: Managed decoys, SIEM integration. 7) Insider threat detection – Context: Privileged user exfiltrates data. – Problem: Hard to distinguish malicious from legitimate work. – Why deception helps: Targeted honeytokens trigger only for misuse. – What to measure: Internal user interactions and anomalous patterns. – Typical tools: Honeytoken rotation and forensic locker.
8) Red team validation – Context: Security maturity assessment. – Problem: Measuring detection capabilities. – Why deception helps: Provides measurable interactions for validation. – What to measure: Detection rate for planted red team actions. – Typical tools: Decoy orchestration and playbook integration. 9) Supply chain compromise detection – Context: Malicious updates propagate through tooling. – Problem: Silent compromise through CI/CD. – Why deception helps: Decoys in package repos detect stolen signing keys. – What to measure: Package access to decoy artifacts. – Typical tools: CI-integrated deception plugins.
10) API abuse detection – Context: Undocumented endpoints accessed by bots. – Problem: Abuse or data scraping. – Why deception helps: Fake API endpoints trap attackers without affecting users. – What to measure: API interaction patterns to decoys. – Typical tools: Application decoys. Context: Multi-tenant Kubernetes cluster hosting several apps. Goal: Detect lateral movement between namespaces and service account token misuse. Why Deception Technology matters here: Attackers commonly steal serviceaccount tokens to pivot; namespace decoys reveal movement paths. Architecture / workflow: K8sHoney Controller deploys fake pods, serviceaccounts, and configmaps; sensor sidecars emit events to collector; SIEM correlates with RBAC logs. Step-by-step
Implementation
Context: Serverless functions ingest files from external sources. Goal: Detect unauthorized data extraction initiated by serverless flows. Why Deception Technology matters here: Serverless is ephemeral and hard to instrument with traditional EDR. Architecture / workflow: Deploy fake serverless endpoints named like backup-export and place honey tokens in environment variables and storage. Invocation logs and storage access to honey objects route to collectors. Step-by-step
Implementation Synonym
Context: Production compromise detected by normal alerts but timeline incomplete. Goal: Use deception logs to fill timeline gaps and validate attacker activity. Why Deception Technology matters here: Deception artifacts provide high-fidelity evidence for root cause. Architecture / workflow: ForensicLocker stores decoy interactions; SOC triage links decoy events to host and timestamps. Postmortem integrates decoy timeline. Step-by-step implementation: Context: Large fleet where decoy maintenance costs scale with asset count. Goal: Balance detection coverage against cost and performance overhead. Why Deception Technology matters here: Over-deployment causes OPEX spikes and alert noise.
Implementation Meaning
Architecture / workflow: Hybrid approach with targeted decoys on high-value assets and light canaries elsewhere. Use orchestration to scale decoys on demand. Step-by-step implementation: 3. Software Implementation, Frameworks & Protocols Scenario #5 — Serverless CI/CD leakage detection (must include serverless/managed-PaaS) Context: CI pipelines use serverless runners and occasionally leak secrets. Goal: Detect secret use from compromised runners. Why Deception Technology matters here: Secrets in pipelines often escalate to production access. Architecture / workflow: CICanary Plugin embeds honeytokens into build artifacts; any downstream use triggers alerts. Step-by-step
Implementation Science
List of mistakes with Symptom -> Root cause -> Fix (15–25 entries; include at least 5 observability pitfalls). 1) Symptom: Frequent low-value alerts. -> Root cause: Overly broad decoys catching benign automation. -> Fix: Whitelist known automation and tune decoy naming. 2) Symptom: No decoy interactions for months. -> Root cause: Poor placement or attacker avoidance. -> Fix: Rotate decoys and perform red-team validation. 3) Symptom: Alerts lack context. -> Root cause: Missing enrichment pipeline. -> Fix: Integrate asset inventory and cloud metadata. 4) Symptom: Telemetry gaps during peak windows. -> Root cause: Collector overload. -> Fix: Scale collectors and add buffering. 5) Symptom: Decoys cause production latency. -> Root cause: Decoy placed inline with request path. -> Fix: Reposition to sidecar or isolated overlay. 6) Symptom: Analysts ignore deception alerts. -> Root cause: Low trust due to false positives. -> Fix: Improve TTP signatures and enrichment quality. 7) Symptom: Decoys detected by attackers. -> Root cause: Static fingerprints or naming patterns. -> Fix: Randomize attributes and rotate frequently. 8) Observability pitfall Symptom: Long enrichment latency. -> Root cause: Synchronous enrichment with slow APIs. -> Fix: Use async enrichment and caching. 9) Observability pitfall Symptom: Missing correlated logs. -> Root cause: Inconsistent timestamps. -> Fix: Ensure NTP and consistent timezones. 10) Observability pitfall Symptom: Hard to pivot from alert to traces. -> Root cause: No linking identifiers. -> Fix: Add session IDs and asset tags in telemetry. 11) Observability pitfall Symptom: SIEM overwhelmed. -> Root cause: Raw low-value events forwarded. -> Fix: Pre-filter and aggregate events at collector. 12) Symptom: Legal/regulatory flags for deception. -> Root cause: Data capture conflicts. -> Fix: Engage legal and apply data minimization. 13) Symptom: Decoy content leaks. -> Root cause: Insecure decoy hosting. -> Fix: Sanitize and isolate decoy content. 14) Symptom: Containment automation failed. -> Root cause: Missing API permissions or race conditions. -> Fix: Harden automation with retries and fallbacks. 15) Symptom: High maintenance burden. -> Root cause: Manual decoy lifecycle. -> Fix: Automate rotation and templating through orchestration.
Implementation Specialist
16) Symptom: Decoys accidentally used by developers. -> Root cause: Decoy naming mimics real assets. -> Fix: Provide clear developer documentation and labeling. 17) Symptom: False alerts from security scans. -> Root cause: Internal vulnerability scanning hitting decoys. -> Fix: Configure scanners to ignore decoy ranges or tag them. 18) Symptom: No measurable ROI. -> Root cause: No SLOs or metrics defined. -> Fix: Define SLIs and track metrics like MTTD and containment rate. 19) Symptom: Forensic artifacts incomplete. -> Root cause: Late snapshot or missing context. -> Fix: Snapshot immediately on interaction and capture multi-source logs. 20) Symptom: Multi-tenant decoys cross-talk. -> Root cause: Shared decoy infrastructure. -> Fix: Namespace isolation and strict tenancy boundaries. 21) Symptom: Alerts trigger noisy paging. -> Root cause: Poor severity tuning. -> Fix: Reclassify alerts into page vs ticket with thresholds. 22) Symptom: Decoy orchestration fails on upgrades. -> Root cause: Compatibility regressions. -> Fix: Test upgrades in staging and use canary rollouts. 23) Symptom: Decoys expose sensitive metadata. -> Root cause: Overly realistic decoy content. -> Fix: Use synthetic data with no PII. 24) Symptom: Inaccurate attack mapping. -> Root cause: Sparse decoy coverage. -> Fix: Increase strategic placement near high-risk paths. 25) Symptom: SOC lacks playbooks. -> Root cause: Deployment without process. -> Fix: Draft triage and containment playbooks and train analysts.
Implementation Definition
A honeytoken is a single fake item like a credential; a decoy is a broader simulated resource like a fake service. Honeytokens are a subset of decoys. Yes if decoys are placed inline or misconfigured. Best practice is to isolate and validate before wide deployment. Document decoy placements, use naming conventions, whitelist legitimate automation, and provide an internal verification checklist.
Implementation Manager
Varies / depends on jurisdiction and data capture. Always perform legal review for forensic capture and monitoring. Rotate based on threat model; typical cadence is weekly to monthly. High-risk assets prefer faster rotation. No. It complements those controls by providing high-fidelity indicators and intelligence. Use metrics like mean time to detect, containment success rate, and cost per detected incident.
Implementation Consultant
Depends on asset criticality; start small with targeted decoys and scale based on signal value. Yes, captured interactions provide TTPs and indicators that enrich threat intel feeds. Low-latency collectors, consistent timestamps, enrichment connectors, and linking identifiers across telemetry. Yes; serverless can host fake functions and storage decoys to detect misuse despite ephemeral nature.
Implementation Intentions
Yes; avoid capturing unnecessary personal data and perform privacy reviews before deployment. Varies / depends on scope and scale. Consider tooling, telemetry storage, and analyst time. Deception technology is a pragmatic, high-fidelity detection layer that complements traditional security controls. When designed with cloud-native patterns, careful orchestration, and observability integration, it provides early detection, richer forensic evidence, and a measurable reduction in attacker dwell time. Operationalizing deception requires collaboration between security, SRE, and legal teams, plus automation to reduce toil.
Implementation Engineers
#Automation #CareerGrowth #CICD #CI_CD #CloudAutomation #CloudComputing #CloudDevOps #CloudNative #DataScience #DevOps #DevOpsAutomation #DevOpsCareer #DevOpsCareers #DevOpsSkills #DevOpsTools #DevOpsTraining #DevSecOps #EnterpriseDevOps #InfrastructureAsCode #ITTraining #Kubernetes #MachineLearning #Microservices #Observability #SiteReliabilityEngineering #SoftwareDevelopment #SRE #TechCareer #TechSkills #TechTraining Cyberattacks have become more sophisticated than ever, making traditional security tools like firewalls, antivirus software, and intrusion prevention systems insufficient on their own. Threat actors increasingly use stealthy techniques to bypass defenses, remain undetected, and move laterally across networks.
Cyber deception has emerged as an effective strategy for detecting attackers early, slowing their progress, and gathering valuable threat intelligence. Instead of relying solely on prevention, deception technology creates realistic decoys that lure attackers away from critical assets while exposing malicious activity. In this guide, you'll learn how to implement cyber deception effectively, understand its benefits, and discover best practices for protecting your enterprise network.
Cyber Deception is a proactive cybersecurity approach that uses fake assets, decoys, credentials, applications, databases, servers, and network services to detect attackers. Unlike traditional security controls that attempt to block threats, deception technology assumes attackers may eventually gain access. Once inside, deceptive assets attract adversaries, revealing their presence before they can compromise valuable systems.
Because legitimate users never interact with these assets, any activity directed toward them is considered highly suspicious and generates high-confidence alerts. Instead of waiting until systems are compromised, defenders receive alerts as soon as attackers touch deceptive assets. Attackers typically perform reconnaissance before launching attacks. Deceptive systems expose these activities immediately.
False positives are dramatically reduced because legitimate employees have no reason to access fake systems. Since Active Directory is frequently targeted, deception here provides excellent visibility. Understanding what requires protection helps determine where deception will provide the greatest value. 4. Practical Deployment, Analysis & Case Studies Organizations across industries are adopting deception technology to address specific security challenges.
Detects attackers before encryption begins by identifying reconnaissance and credential misuse. Strengthens monitoring and incident detection capabilities to help organizations meet regulatory and security framework requirements. Cyber deception works best as part of a layered security strategy rather than as a replacement for existing controls.
These capabilities help maximize detection coverage while minimizing administrative effort. Cyber deception is evolving alongside modern security operations. Emerging capabilities include: As cyber threats become increasingly sophisticated, deception technology will play a larger role in proactive defense strategies.
Cyber deception shifts security from a purely defensive mindset to a proactive one. By deploying realistic decoys, honey credentials, and deceptive services throughout your environment, organizations can detect attackers during reconnaissance, credential theft, and lateral movement—often long before critical assets are at risk. When integrated with XDR, NDR, SIEM, SOAR, and endpoint security solutions, cyber deception provides high-confidence alerts, accelerates incident response, and delivers valuable insights into attacker behavior. As enterprises embrace hybrid, multi-cloud, and Zero Trust architectures, implementing cyber deception is becoming an increasingly effective way to strengthen network resilience and improve overall cyber defense.
Deception technology offers a proactive approach to identifying and mitigating cyber threats. By deploying strategic traps, it diverts attackers, protecting crucial assets. Deception technology involves creating false information or misleading environments to engage and mislead cyber attackers. Decoys, traps, and fake systems mimic real network elements, making attackers believe they’re accessing valuable data. This technology operates by redirecting malicious activities to controlled environments, allowing security teams to observe and analyze attack methods without jeopardizing actual assets. Techniques include honeypots, honeytokens, and deceptive networks, which collectively increase the difficulty and risk for attackers.
Understanding where deception technology fits within a broader security architecture requires some grounding in how conventional perimeter defenses operate. The comparison between firewalls and intrusion detection systems illustrates a fundamental limitation: both tools are designed primarily to block or alert on known threats at the network boundary, leaving organizations exposed once an attacker has already moved past that perimeter. Deception technology addresses precisely this gap, operating inside the network to engage and misdirect adversaries who have already bypassed traditional controls.
Deception technology is essential in modern cyber security because it offers unique advantages in threat detection and mitigation. Traditional defenses, like firewalls and antivirus solutions, often fail against sophisticated threats. Deception systems can identify zero-day attacks and advanced persistent threats (APTs) by luring attackers into false environments. This approach provides real-time intelligence on attacker behavior and tactics, helping develop more robust defenses.
Moreover, deception technology reduces false positives, enhancing overall security accuracy and responsiveness. Through these methods, deception technology significantly contributes to a proactive and resilient cyber defense strategy. Deception technology creates a layer of false data, systems, and networks to lure cyber attackers and collect intelligence on their tactics. It enhances cyber defense by identifying and mitigating threats early.
Decoys and traps are central to deception technology. Decoys, which mimic real servers, workstations, and network components, mislead attackers. For instance, a decoy server might display typical enterprise software and data to attract intruders. Traps, or honeypots, trigger alerts when accessed by unauthorized entities. When an attacker interacts with these decoys or triggers a trap, it signals a potential breach attempt. This allows security teams to analyze attack methods and respond before real assets are compromised.
Deception technology integrates seamlessly with existing security tools. It enhances the capabilities of SIEM (Security Information and Event Management) systems by providing contextualized alerts. For example, when a decoy or trap logs attacker activity, the SIEM system can correlate this data with other events, providing a comprehensive view of the threat landscape. Endpoint detection and response (EDR) systems also benefit, as they can link deception alerts to specific endpoints, offering deeper insights. This integration enhances overall security posture by making existing technologies more effective in threat detection and response.
Deception technology offers several advantages in strengthening our cyber defense strategy. It enhances threat detection, minimizes response time, and improves overall security. Deception technology significantly enhances our detection and response capabilities by providing early and accurate threat identification. When attackers interact with decoys or traps, these interactions generate alerts that are distinct from regular traffic. This immediate detection enables us to quickly identify potential breaches and take appropriate actions. Additionally, by deploying deceptive elements that mimic critical systems, we can gather valuable intelligence on attacker tactics, techniques, and procedures (TTPs). This information informs our security teams and sharpens our defense strategies.
The deployment of deception technology effectively reduces our incident response time. Traditional security measures often rely on identifying anomalies within vast amounts of data, leading to delays in detection and response. Conversely, interactions with deception elements are inherently suspicious, thus triggering swift alerts. These alerts allow our security teams to rapidly isolate affected systems, assess the threat, and execute necessary remediation steps. The proactive nature of deception technology ensures that response times are minimized, mitigating potential damage to our network and reducing downtime.
While the speed advantage deception technology provides is significant, it becomes even more powerful when paired with a disciplined, hypothesis-driven hunt program. Rather than waiting for decoys to fire, skilled analysts can use the behavioral intelligence gathered from those interactions to actively pursue adversaries who may be operating just below the detection threshold. Our proactive threat hunting techniques and preemptive strategies extend this visibility further, transforming isolated decoy alerts into structured campaigns that systematically surface latent threats across the entire environment before they escalate.
Deception technology plays a crucial role in actual cyber defense scenarios across various sectors. Its diverse applications offer unique insights and tactical advantages. Financial Sector : Many financial institutions, including banks and stock exchanges, utilize deception technology to protect their sensitive data. By deploying decoys and traps mimicking databases and transaction systems, they effectively divert attackers and gather data on hacking attempts. For instance, JPMorgan Chase has leveraged deception strategies to safeguard customer information and enhance their threat detection capabilities.
Healthcare : Healthcare providers deploy deceptive environments to protect patient records and medical devices. Systems like these create fake patient databases and decoy devices to lure attackers, helping the institutions identify and mitigate threats early. The Cleveland Clinic’s use of such technology has substantially decreased unauthorized access attempts. Government and Defense : Government agencies use deception technology to protect national security information and operational systems. Fake networks and decoys simulate sensitive military databases and communication channels, diverting potential threats and providing critical intelligence. For example, the Department of Defense has integrated deception technology into its cybersecurity strategy to detect and respond to threat actors more effectively.
Retail : Retailers, such as e-commerce platforms, use deception tactics to protect customer data and payment information. Decoy credit card databases and transactional systems lure cybercriminals, minimizing real data exposure. Amazon has incorporated these techniques to reduce the risk of data breaches and enhance their cyber defense posture. Improved threat intelligence results from analyzing attacker behavior in deceptive environments. Hackers interacting with traps and decoys inadvertently reveal their tactics, techniques, and procedures (TTPs). By studying these interactions, we gain invaluable insight into potential vulnerabilities and emerging threats.
This intelligence aids in refining existing security measures and updating signatures in systems like SIEM and EDR. Real-time data helps create robust threat profiles for faster detection and more effective response strategies. Moreover, threat intelligence gathered from decoys can be shared across industries, improving collective cybersecurity defenses. By integrating deception technology, organizations can more effectively preempt cyber threats, minimize incident response times, and reinforce their cybersecurity frameworks. These real-world applications demonstrate deception technology’s pivotal role in modern cyber defense.
Incorporating deception technology in cyber defense requires addressing several challenges. These include mitigating false positives and handling scalability and management concerns. 5. Performance Evaluation & Extended Technical Observations False positives can overwhelm security teams and dilute the effectiveness of deception technology. Identifying genuine threats while discarding benign activities is crucial. Machine learning algorithms help refine detection processes by analyzing patterns and reducing erroneous alerts. Implementing customizable thresholds ensures only significant deviations trigger alerts. Regular updates to the deception environment improve accuracy and adaptability.
Managing a scalable deception environment is complex. Deploying and maintaining numerous decoys across large networks requires significant resources. Automated orchestration tools streamline deployment and monitoring, reducing manual workload. Integrating with existing security information and event management (SIEM) systems unifies threat data, simplifying oversight. Regularly evaluating and updating the deception framework improves performance and scalability.
By addressing these considerations, our organizations can maximize the benefits of deception technology, ensuring a robust and proactive cyber defense. Deception technology represents a game-changer in the realm of cybersecurity. By proactively misleading attackers and gathering critical intelligence, it enhances our threat detection and mitigation capabilities. Its integration with existing security systems and the ability to adapt through machine learning and automation make it a versatile tool across various sectors. As we continue to refine these technologies and address challenges like false positives and scalability, the potential for a robust and proactive cyber defense becomes increasingly attainable. Embracing deception technology is a strategic move towards safeguarding our digital assets and staying ahead of evolving cyber threats.
In a controlled study by Horizon3 researchers, models that explicitly identified a trap in their reasoning still attacked it 73.4% of the time. Read the findings and see what they mean for canaries, decoys, and early detection. Deception technology occupies a unique position in the security tool landscape because it inverts the economics of detection. Every other detection mechanism works against the attacker's ability to hide: the defender tries to find malicious behavior in a sea of legitimate activity. Deception technology creates artifacts that have no legitimate use case: a fake AWS key that should never be accessed, a fake admin account that should never log in, a network service that no legitimate user would ever connect to. When any of these objects is touched, the alert has near-zero false positive probability because no legitimate operation should ever interact with them. This property makes deception one of the highest-fidelity detection mechanisms available, and it is deployable by teams with modest security budgets and limited SIEM infrastructure.
The fundamental asymmetry of deception technology is this: the defender must place deception artifacts correctly once, while the attacker must avoid every deception artifact every time. A single trip wire in a password manager, a code repository, an Active Directory OU, or a network segment generates an alert on first contact. The attacker who discovers a fake credential and uses it has identified themselves without knowing they have done so. The attacker who is sophisticated enough to identify and avoid the deception object must expend additional time and resources at each step, which increases dwell time, increases the probability of detection through other mechanisms, and may disrupt the attack timeline enough to enable a response.
Traditional detection mechanisms suffer from the problem of signal-to-noise ratio. A SIEM ingesting endpoint, network, and identity logs generates thousands to tens of thousands of events per day, and the detection rules that identify malicious behavior also match legitimate activity patterns that resemble malicious ones. The analyst workload of investigating false positives consumes the capacity that should be directed at real threats. Deception solves this problem architecturally: a honeytoken that generates exactly one alert type (this fake thing was accessed) produces a signal with effectively no noise.
The operational overhead argument against deception technology is typically overstated. The concern is that maintaining realistic-looking deception artifacts requires ongoing effort to keep them believable. In practice, the highest-value deception artifacts require minimal maintenance: a fake AWS key in a code repository does not need to be updated to remain functional as a trip wire. A fake admin account in Active Directory does not need to have its password changed or its group memberships updated to generate an alert when someone attempts to authenticate with it. A network honeypot emulating an RDP server does not need to be updated when Windows Server gets a new patch. The maintenance burden argument against deception is much stronger for enterprise deception platforms that attempt to build complete deceptive environments than for targeted honeytoken deployments, which is where most organizations should start.
The deception technology spectrum ranges from a single honeytoken costing nothing to deploy to a commercial enterprise deception fabric costing hundreds of thousands of dollars annually. Understanding what each tier of the spectrum provides helps match the investment to the organization's threat model and operational capacity. A honeytoken is a single fake data object with a monitoring mechanism attached. The simplest example is a URL that, when accessed, sends an HTTP request to a logging server. A more sophisticated example is an AWS access key that, when used in an API call, generates a CloudTrail event flagged as unauthorized access. Honeytokens can be deployed in minutes, cost nothing to maintain, and generate extremely high-confidence alerts on contact. Their limitation is that they only detect activity that directly contacts the specific object: an attacker who finds the fake AWS key and doesn't use it, or who finds the code repository but not the specific file containing the key, generates no alert.
A honeypot is a fake system or service that appears functional but captures and alerts on all connection attempts. A fake RDP server that looks like a real Windows Server, logs every connection attempt, and generates an alert on any inbound session is a network honeypot. Unlike a honeytoken, a honeypot provides network-level detection: any host that scans the honeypot's IP address generates an alert, even if the scanner never attempts to authenticate. Honeypots detect network reconnaissance and lateral movement probing that honeytokens miss.
Full deception platforms create an entire parallel deceptive environment: fake servers, fake network shares, fake Active Directory objects, fake credentials distributed across real endpoints, and full correlation of all deception interactions into a unified alert timeline. Commercial platforms like Attivo Networks (acquired by SentinelOne), Illusive Networks, and Acalvio automate the creation and distribution of deception objects at scale and provide an analyst interface for investigating deception alerts. They also include anti-deception analysis: the platform monitors for attacker behaviors that suggest they are identifying and avoiding deception objects, which is itself an indicator of sophisticated adversary tradecraft.
Canarytokens.org, operated by Thinkst, is the most accessible entry point to deception technology. The service is free and generates unique URLs, DNS names, or payloads that send an HTTP callback to Thinkst's logging infrastructure (or to your own server using the self-hosted version) when triggered, delivering an alert with the source IP address, user-agent, and timestamp of the access event.
The available canary token types cover most high-value placement scenarios. A DNS token generates an alert when a DNS query is made for a unique subdomain, which fires when a document embedding the token is opened and its DNS beacon resolves, even if the user is on an internal network. A Word document token embeds a DNS beacon in a .docx file that fires when the document is opened in Microsoft Word, making it a high-value trip wire for document stores. An AWS key token uses a real AWS IAM key with no permissions attached; any attempt to use the key in an AWS API call generates a CloudTrail event and a webhook alert, making it an ideal fake credential for code repositories. A Windows credential token creates a .URL file that, when opened by Windows Explorer, attempts to authenticate to a UNC path controlled by Canarytokens, capturing NTLM hashes in a way that resembles a credential capture attempt but alerts the defender instead.
For self-hosted environments where sending alert data to a third-party service is not acceptable, the Canarytokens open-source project provides the full platform for deployment on internal infrastructure. A self-hosted Canarytokens server on an internal host with alerting configured to your SIEM or email provides all the same token types with complete data sovereignty. The setup requires a Linux server with Docker, a DNS entry pointing a subdomain to the server, and a port 80/443 listener for HTTP callback tokens. The entire deployment takes two to three hours and provides ongoing high-fidelity detection infrastructure.
Deploying a portfolio of canary tokens across an environment should follow a placement strategy based on where attackers typically look for credentials and access paths during post-exploitation enumeration. File shares accessed by many users, source code repositories, password managers, cloud infrastructure credentials, and administrative tool configurations are the primary placement targets. Place at least one token in each category that applies to your environment before moving on to more complex deception techniques.
The value of a honeytoken is proportional to how likely an attacker who has achieved initial access is to encounter and interact with it during their post-exploitation workflow. Placing honeytokens in locations that attackers systematically search during the reconnaissance and credential harvesting phases of an intrusion maximizes the probability of early detection. A fake admin credential in a password manager is a high-priority placement because attackers who compromise a workstation frequently harvest credentials from browser-stored passwords and password managers. A KeePass database or browser password store that contains an entry labeled 'server-admin' or 'domain-admin' with a URL pointing to a canary token will fire when the attacker copies or attempts to use the credential. The account name should match the naming convention of real administrative accounts in the environment to be convincing.
A fake AWS access key embedded in a code repository is high-value because automated secret scanning tools used by attackers scan public and private repositories for AWS key patterns immediately after gaining access. A fake key with a name like 'aws-prod-backup-key' in a .env file or configuration file will be extracted and tested against the AWS API, generating a CloudTrail alert with the source IP of the system attempting to use the key. This alert fires before the attacker has gained any actual access, providing an extremely early warning signal.
A fake domain admin account in Active Directory is valuable for detecting Active Directory enumeration and credential stuffing attempts. Create an account with a name that fits the convention of real admin accounts, populate it with realistic AD attributes (description, department, manager), and configure the account to never expire and to require password at next login so it looks dormant. Any authentication attempt against this account, whether through Kerberoasting, password spray, or direct login attempt, should generate an alert via SIEM rule on the account name. This alert fires during the privilege escalation phase, well before the attacker has achieved their objective.
A fake database connection string in an application configuration file is valuable for detecting attackers who are searching for database credentials after compromising an application server. A connection string containing a canary DNS token in the server hostname will resolve the DNS token when any process attempts to connect to the fake database, identifying which process on which host is attempting the connection.
An entry labeled with an admin account name containing a canary token URL that fires on access. Detects credential harvesting from workstations. A real-format AWS access key with no permissions in a .env or config file. API usage generates a CloudTrail event with the attacker's source IP.
A convincing-looking AD account with realistic attributes that should never be authenticated against. Any auth attempt generates an alert. A connection string with a canary DNS hostname that fires when any process attempts to resolve the server address, identifying unauthorized database access attempts.
A document named to attract attention (passwords.xlsx, network-diagram.docx) containing a DNS canary token that fires when the file is opened. Active Directory is the primary target for privilege escalation in Windows environments, and deception objects within AD provide detection coverage for the reconnaissance and enumeration techniques attackers use to identify and target privileged accounts. AD deception operates at a different level than canary tokens: rather than detecting access to a specific object, AD deception detects the LDAP enumeration and authentication attempts that precede targeted credential attacks.
Fake service principal names (SPNs) attached to fake service accounts are a specific AD deception technique targeting Kerberoasting. Kerberoasting extracts Kerberos service tickets for accounts with SPNs and attempts to crack the service account password offline. Creating a fake service account with a compelling SPN (like HTTP/intranet-payroll.domain.com) and an extremely strong password, then monitoring for Kerberos TGS requests for that specific SPN in the domain controller event logs (Event ID 4769), detects Kerberoasting attempts that target the fake account. The fake SPN is never used for any legitimate service, so any TGS request for it is unambiguously an attack indicator.
Fake Group Policy Objects with names that suggest elevated privilege access (like 'Domain Admin Desktop Policy' or 'Privileged Access Workstation Configuration') attract attackers who enumerate GPOs looking for policy objects that reveal administrative workflows or contain embedded credentials. The GPO itself does not need to be functional as a detection mechanism: the detection comes from monitoring LDAP queries for the GPO's GUID in domain controller logs or from a canary token embedded in the GPO's script content.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Deception%20technology • https://en.wikipedia.org/wiki/Deception • https://en.wikipedia.org/wiki/Active%20defense • https://en.wikipedia.org/wiki/Deception_technology • https://www.geeksforgeeks.org/ethical-hacking/deception-technology/ • https://devsecopsschool.com/blog/deception-technology/ • https://www.molecularcloud.org/p/implementing-cyber-deception-to-protect-your-network-a-complete-guide-for-2026 • https://www.deepthreatanalytics.com/network-security/deception-technology-cyber-defense-enhancing/ • https://www.decryptiondigest.com/blog/deception-technology-honeypot-deployment
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Deception Technology In Networks.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |