Complete Technical Paper Content — Digital Forensics Artifact Extraction Tool Using Python
Overview & System Context
Digital Forensics Artifact Extraction Tool Using Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9522 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Computer forensics (also known as computer forensic science) is a branch of digital forensic science pertaining to evidence found in computers and digital storage media. The goal of computer forensics is to examine digital media in a forensically sound manner with the aim of identifying, preserving, recovering, analyzing, and presenting facts and opinions about the digital information. Although it is most often associated with the investigation of a wide variety of computer crime, computer forensics may also be used in civil proceedings. The discipline involves similar techniques and principles to data recovery, but with additional guidelines and practices designed to create a legal audit trail. Evidence from computer forensics investigations is usually subjected to the same guidelines and practices as other digital evidence. It has been used in a number of high-profile cases and is accepted as reliable within U.S. and European court systems.
BTK Killer: Dennis Rader was convicted of a string of serial killings over sixteen years. Towards the end of this period, Rader sent letters to the police on a floppy disk. Metadata within the documents implicated an author named "Dennis" at "Christ Lutheran Church," helping lead to Rader's arrest. Joseph Edward Duncan: A spreadsheet recovered from Duncan's computer contained evidence showing him planning his crimes. Prosecutors used this to demonstrate premeditation and secure the death penalty. Sharon Lopatka: Hundreds of emails on Lopatka's computer led investigators to her killer, Robert Glass.
Corcoran Group: In this case, computer forensics confirmed parties' duties to preserve digital evidence when litigation had commenced or was reasonably anticipated. Hard drives were analyzed, though the expert found no evidence of deletion, and evidence showed that the defendants intentionally destroyed emails. Dr. Conrad Murray: Dr. Conrad Murray, the doctor of Michael Jackson, was convicted partially by digital evidence, including medical documentation showing lethal amounts of propofol. Mark Twitchell, also known as the "Dexter Killer," Twitchell was convicted with the help of a deleted document recovered from his laptop titled "SKConfessions." This file, which detailed his criminal activities, served as a key piece of evidence in the case.
Computer forensic investigations typically follow the standard digital forensic process, consisting of four phases: acquisition, examination, analysis, and reporting. Investigations are usually performed on static data (i.e., acquired images) rather than "live" systems. This differs from early forensic practices, when a lack of specialized tools often required investigators to work on live data.
Cross-drive analysis This technique correlates information found on multiple hard drives and can be used to identify social networks or detect anomalies. Live analysis The examination of computers from within the operating system using forensic or existing sysadmin tools to extract evidence. This technique is particularly useful for dealing with encrypting file systems where encryption keys can be retrieved, or for imaging the logical hard drive volume (a live acquisition) before shutting down the computer. Live analysis is also beneficial when examining networked systems or cloud-based devices that cannot be accessed physically. Deleted files A common forensic technique involves recovering deleted files. Most operating systems and file systems do not erase the physical file data, allowing investigators to reconstruct it from the physical disk sectors.
Forensic software can "carve" files by searching for known file headers and reconstructing deleted data. Stochastic forensics This method leverages the stochastic properties of a system to investigate activities without traditional digital artifacts, often useful in cases of data theft. Steganography Steganography involves concealing data within another file, such as hiding illegal content within an image. Forensic investigators detect steganography by comparing file hashes, as any hidden data will alter the hash value of the file.
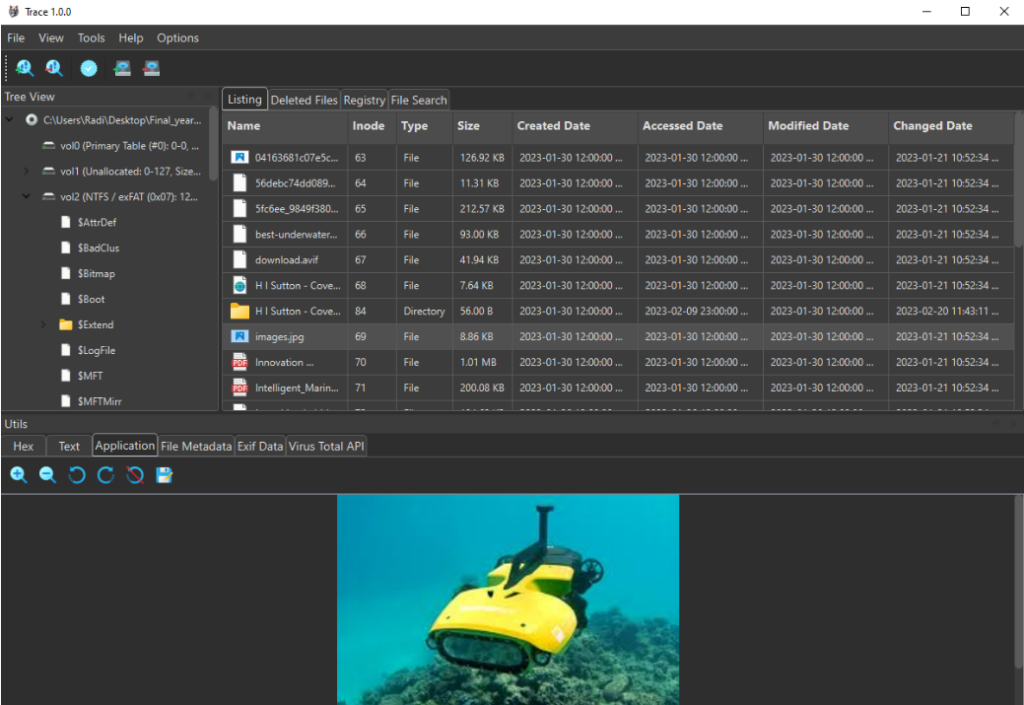
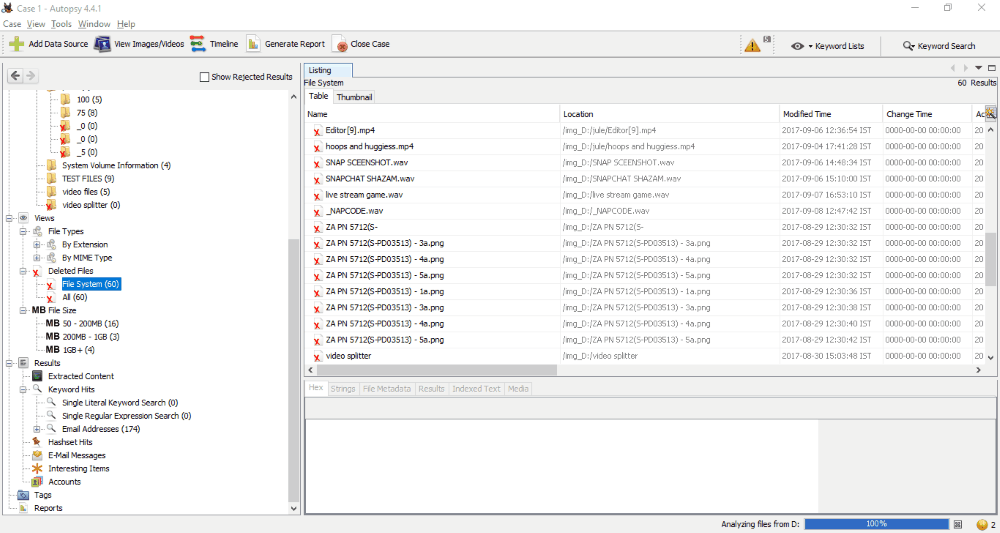
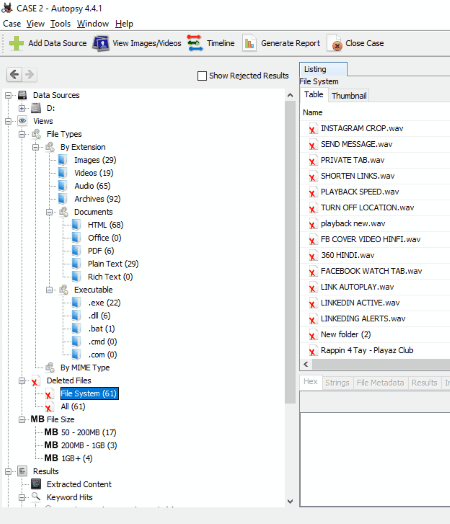
Figure 1: Open-Source Solutions For Digital Forensic Investigators - Forensic Focus Numerous open-source and commercial tools exist for computer forensics. Common forensic analysis includes manual reviews of media, Windows registry analysis, password cracking, keyword searches, and the extraction of emails and images. Tools such as Autopsy (software), Belkasoft Evidence Center X, Forensic Toolkit (FTK), and EnCase are widely used in digital forensics.
Digital forensics (sometimes known as digital forensic science) is a branch of forensic science encompassing the recovery, investigation, examination, and analysis of material found in digital devices, often in relation to mobile devices and computer crime. The term "digital forensics" was originally used as a synonym for computer forensics but has been expanded to cover investigation of all devices capable of storing digital data. With roots in the personal computing revolution of the late 1970s and early 1980s, the discipline evolved in a haphazard manner during the 1990s, and it was not until the early 21st century that national policies emerged. Digital forensics investigations have a variety of applications. The most common is to support or refute a hypothesis before criminal or civil courts. Criminal cases involve the alleged breaking of laws that are defined by legislation and enforced by the police and prosecuted by the state, such as murder, theft, and assault against the person. Civil cases, on the other hand, deal with protecting the rights and property of individuals (often associated with family disputes), but may also be concerned with contractual disputes between commercial entities where a form of digital forensics referred to as electronic discovery (ediscovery) may be involved. Forensics may also feature in the private sector, such as during internal corporate investigations or intrusion investigations (a special probe into the nature and extent of an unauthorized network intrusion). The technical aspect of an investigation is divided into several sub-branches related to the type of digital devices involved: computer forensics, network forensics, forensic data analysis, and mobile device forensics. The typical forensic process encompasses the seizure, forensic imaging (acquisition), and analysis of digital media, followed with the production of a report of the collected evidence. As well as identifying direct evidence of a crime, digital forensics can be used to attribute evidence to specific suspects, confirm alibis or statements, determine intent, identify sources (for example, in copyright cases), or authenticate documents. Investigations are much broader in scope than other areas of forensic analysis (where the usual aim is to provide answers to a series of simpler questions), often involving complex time-lines or hypotheses.
Seizing, preserving, and analyzing evidence stored on a computer is the greatest forensic challenge facing law enforcement in the 1990s. Although most forensic tests, such as fingerprinting and DNA testing, are performed by specially trained experts the task of collecting and analyzing computer evidence is often assigned to patrol officers and detectives. Through cyberspace, enemies will target industry, academia, government, as well as the military in the air, land, maritime, and space domains. In much the same way that airpower transformed the battlefield of World War II, cyberspace has fractured the physical barriers that shield a nation from attacks on its commerce and communication. The field of digital forensics still faces unresolved issues. A 2009 paper, "Digital Forensic Research: The Good, the Bad and the Unaddressed" by Peterson and Shenoi, identified a bias towards Windows operating systems in digital forensics research. In 2010, Simson Garfinkel identified issues facing digital investigations in the future, including the increasing size of digital media, the wide availability of encryption to consumers, a growing variety of operating systems and file formats, an increasing number of individuals owning multiple devices, and legal limitations on investigators. The paper also identified continued training issues, as well as the prohibitively high cost of entering the field. Additionally, since 2024 there has been an integration of Artificial Intelligence (AI) and Machine Learning (ML) which has poised to amplify the efficiency as well as the precision behind digital forensics investigations Figure 2: 13 Best Free Digital Forensic Tools For Windows During the 1980s, very few specialized digital forensic tools existed. Consequently, investigators often performed live analysis on media, examining computers from within the operating system using existing sysadmin tools to extract evidence. This practice carried the risk of modifying data on the disk, either inadvertently or otherwise, which led to claims of evidence tampering. A number of tools were created during the early 1990s to address the problem. The need for such software was first recognized in 1989 at the Federal Law Enforcement Training Center, resulting in the creation of IMDUMP (by Michael White) and in 1990, SafeBack (developed by Sydex). Similar software was developed in other countries; DIBS (a hardware and software solution) was released commercially in the UK in 1991, and Rob McKemmish released Fixed Disk Image free to Australian law enforcement. These tools allowed examiners to create an exact copy of a piece of digital media to work on, leaving the original disk intact for verification. By the end of the 1990s, as demand for digital evidence grew, more advanced commercial tools such as EnCase and FTK were developed, allowing analysts to examine copies of media without using any live forensics. More recently, a trend towards "live memory forensics" has grown, resulting in the availability of tools such as WindowsSCOPE. More recently, the same progression of tool development has occurred for mobile devices; initially investigators accessed data directly on the device, but soon specialist tools such as XRY or Radio Tactics Aceso appeared.
Police forces have begun implementing risk-based triage systems to manage the overwhelming demand for digital forensic services. acquisition or imaging of exhibits, analysis, and reporting. Acquisition does not normally involve capturing an image of the computer's volatile memory (RAM) unless this is done as part of an incident response investigation. Typically the task involves creating an exact sector level duplicate (or "forensic duplicate") of the media, often using a write blocking device to prevent modification of the original. However, the growth in size of storage media and developments such as cloud computing have led to more use of 'live' acquisitions whereby a 'logical' copy of the data is acquired rather than a complete image of the physical storage device. Both acquired image (or logical copy) and original media/data are hashed (using an algorithm such as SHA-1 or MD5) and the values compared to verify the copy is accurate. An alternative (and patented) approach (that has been dubbed 'hybrid forensics' or 'distributed forensics') combines digital forensics and ediscovery processes. This approach has been embodied in a commercial tool called ISEEK that was presented together with test results at a conference in 2017.
During the analysis phase an investigator recovers evidence material using a number of different methodologies and tools. In evidence related to the suspected crime." In 2006, forensics researcher Brian Carrier described an "intuitive procedure" in which obvious evidence is first identified and then "exhaustive searches are conducted to start filling in the holes." The actual process of analysis can vary between investigations, but common methodologies include conducting keyword searches across the digital media (within files as well as unallocated and slack space), recovering deleted files and extraction of registry information (for example to list user accounts, or attached USB devices). The evidence recovered is analyzed to reconstruct events or actions and to reach conclusions, work that can often be performed by less specialized staff. When an investigation is complete the data is presented, usually in the form of a written report, in lay persons' terms.
Digital forensics is commonly used in both criminal law and private investigation. Traditionally it has been associated with criminal law, where evidence is collected to support or oppose a hypothesis before the courts. As with other areas of forensics this is often a part of a wider investigation spanning a number of disciplines. In some cases, the collected evidence is used as a form of intelligence gathering, used for other purposes than court proceedings (for example to locate, identify or halt other crimes). As a result, intelligence gathering is sometimes held to a less strict forensic standard. In civil litigation or corporate matters, digital forensics forms part of the electronic discovery (or eDiscovery) process. Forensic procedures are similar to those used in criminal investigations, often with different legal requirements and limitations. Outside of the courts digital forensics can form a part of internal corporate investigations. A common example might be following unauthorized network intrusion. A specialist forensic examination, into the nature and extent of the attack, is performed as a damage limitation exercise, both to establish the extent of any intrusion and in an attempt to identify the attacker. Such attacks were commonly conducted over phone lines during the 1980s, but in the modern era are usually propagated over the Internet. The main focus of digital forensics investigations is to recover objective evidence of a criminal activity (termed actus reus in legal parlance).
However, the diverse range of data held in digital devices can help with other areas of inquiry. Attribution Meta data and other logs can be used to attribute actions to an individual. For example, personal documents on a computer drive might identify its owner. Alibis and statements Information provided by those involved can be cross checked with digital evidence. For example, during the investigation into the Soham murders the offender's alibi was disproved when mobile phone records of the person he claimed to be with showed she was out of town at the time. Intent As well as finding objective evidence of a crime being committed, investigations can also be used to prove the intent (known by the legal term mens rea). For example, the Internet history of convicted killer Neil Entwistle included references to a site discussing How to kill people. Evaluation of source File artifacts and meta-data can be used to identify the origin of a particular piece of data; for example, older versions of Microsoft Word embedded a Global Unique Identifier into files which identified the computer it had been created on. Proving whether a file was produced on the digital device being examined or obtained from elsewhere (e.g., the Internet) can be very important. Document authentication Related to "Evaluation of source," meta data associated with digital documents can be easily modified (for example, by changing the computer clock you can affect the creation date of a file). Document authentication relates to detecting and identifying falsification of such details.
Figure 3: 13 Best Free Digital Forensic Tools For Windows When used in a court of law, digital evidence falls under the same legal guidelines as other forms of evidence, as courts do not usually require more stringent guidelines. In the United States, the Federal Rules of Evidence are used to evaluate the admissibility of digital evidence. The United Kingdom PACE and Civil Evidence acts have similar guidelines and many other countries have their own laws. US federal laws restrict seizures to items with only obvious evidential value. This is acknowledged as not always being possible to establish with digital media prior to an examination. Laws dealing with digital evidence are concerned with two issues: Integrity - it's ensuring that the act of seizing and acquiring digital media does not modify the evidence (either the original or the copy). Authenticity - refers to the ability to confirm the integrity of information; for example that the imaged media matches the original evidence. The ease with which digital media can be modified means that documenting the chain of custody from the crime scene, through analysis and, ultimately, to the court, (a form of audit trail) is important to establish the authenticity of evidence. Attorneys have argued that because digital evidence can theoretically be altered it undermines the reliability of the evidence. US judges are beginning to reject this theory, in the case US v. Bonallo the court ruled that "the fact that it is possible to alter data contained in a computer is plainly insufficient to establish untrustworthiness." In the United Kingdom, guidelines such as those issued by ACPO are followed to help document the authenticity and integrity of evidence. Digital investigators, particularly in criminal investigations, have to ensure that conclusions are based upon factual evidence and their own expert knowledge. In the US, for example, Federal Rules of Evidence state that a qualified expert may testify "in the form of an opinion or otherwise" so long as: (1) the testimony is based upon sufficient facts or data, (2) the testimony is the product of reliable principles and methods, and (3) the witness has applied the principles and methods reliably to the facts of the case. The sub-branches of digital forensics may each have their own specific guidelines for the conduct of investigations and the handling of evidence. For example, mobile phones may be required to be placed in a Faraday shield during seizure or acquisition to prevent further radio traffic to the device. In the UK forensic examination of computers in criminal matters is subject to ACPO guidelines. There are also international approaches to providing guidance on how to handle electronic evidence. The "Electronic Evidence Guide" by the Council of Europe offers a framework for law enforcement and judicial authorities in countries who seek to set up or enhance their own guidelines for the identification and handling of electronic evidence.
The goal of computer forensics is to explain the current state of a digital artifact; such as a computer system, storage medium or electronic document. The discipline usually covers computers, embedded systems (digital devices with rudimentary computing power and onboard memory) and static memory (such as USB pen drives). Computer forensics can deal with a broad range of information; from logs (such as internet history) through to the actual files on the drive. In 2007, prosecutors used a spreadsheet recovered from the computer of Joseph Edward Duncan to show premeditation and secure the death penalty. Sharon Lopatka's killer was identified in 2006 after email messages from him detailing torture and death fantasies were found on her computer.
Mobile device forensics is a sub-branch of digital forensics relating to recovery of digital evidence or data from a mobile device. It differs from Computer forensics in that a mobile device will have an inbuilt communication system (e.g. GSM) and, usually, proprietary storage mechanisms. Investigations usually focus on simple data such as call data and communications (SMS/Email) rather than in-depth recovery of deleted data. SMS data from a mobile device investigation helped to exonerate Patrick Lumumba in the murder of Meredith Kercher. Mobile devices are also useful for providing location information; either from inbuilt GPS/location tracking or via cell site logs, which track the devices within their range. Such information was used to track down the kidnappers of Thomas Onofri in 2006.
Network forensics is concerned with the monitoring and analysis of computer network traffic, both local and WAN/internet, for the purposes of information gathering, evidence collection, or intrusion detection. Traffic is usually intercepted at the packet level, and either stored for later analysis or filtered in real-time. Unlike other areas of digital forensics network data is often volatile and rarely logged, making the discipline often reactionary. In 2000, the FBI lured computer hackers Aleksey Ivanov and Gorshkov to the United States for a fake job interview. By monitoring network traffic from the pair's computers, the FBI identified passwords allowing them to collect evidence directly from Russian-based computers.
Forensic Data Analysis is a branch of digital forensics. It examines structured data with the aim to discover and analyze patterns of fraudulent activities resulting from financial crime. Database forensics is a branch of digital forensics relating to the forensic study of databases and their metadata. Investigations use database contents, log files and in-RAM data to build a timeline or recover relevant information.
IoT forensics is a branch of Digital forensics that has the goal of identifying and extracting digital information from devices belonging to the Internet of things field, to be used for forensics investigations as potential source of evidence. Forensic identification is the application of forensic science, or "forensics", and technology to identify specific objects from the trace evidence they leave, often at a crime scene or the scene of an accident. Forensic means "for the courts".
People can be identified by their fingerprints. This assertion is supported by the philosophy of friction ridge identification, which states that friction ridge identification is established through the agreement of friction ridge formations, in sequence, having sufficient uniqueness to individualize. Friction ridge identification is also governed by four premises or statements of facts: Friction ridges develop on the fetus in their definitive form prior to birth. Friction ridges are persistent throughout life except for permanent scarring, disease, or decomposition after death. Friction ridge paths and the details in small areas of friction ridges are unique and never repeated. Overall, friction ridge patterns vary within limits which allow for classification. People can also be identified from traces of their DNA from blood, skin, hair, saliva, and semen by DNA fingerprinting, from their ear print, from their teeth or bite by forensic odontology, from a photograph or a video recording by facial recognition systems, from the video recording of their walk by gait analysis, from an audio recording by voice analysis, from their handwriting by handwriting analysis, from the content of their writings by their writing style (e.g. typical phrases, factual bias, and/or misspellings of words), or from other traces using other biometric techniques. Many methods that are used in forensic science evidence have been proven to be unreliable. A lot of trials have been reviewed and testimony involving mostly microscopic hair comparison, but also bite mark, shoe print, soil, fiber, and fingerprint comparisons have been overturned because forensic analysts have provided invalid testimony at the trial. Since forensic identification has been first introduced to the courts in 1980, the first exoneration due to DNA evidence was in 1989 and there have been 336 additional exonerations since then. Those who specialize in forensic identification continue to make headway with new discoveries and technological advances to make convictions more accurate. Body identification is a subfield of forensics concerned with identifying someone from their remains, usually from fingerprint analysis, dental analysis, or DNA analysis.
Fingerprints from the hands and feet are unique and remain unchanged (unless major external factors are involved) from birth to death. Even with minor injuries, they regenerate following the same pattern. Considering the existence of databases in states and countries worldwide containing records of fingerprints from their residents, there is the possibility of searching and comparing fingerprints. This enables an accurate comparison for victim identification.
Forensic odontology (dentistry) plays an important role in human identification, especially in cases where individuals are in an advanced stage of decomposition, charred, or skeletonized. This is due to the high resistance of teeth, which can remain intact even after exposure to harsh conditions. Considering that many people have visited a dentist and have dental records, there is the possibility of retrieving this data for comparison with post-mortem examination data. Such a method enables quick, cost-effective, and reliable identification. The most commonly used ante-mortem data are dental X-rays, dental models, and dental records. However, these data rely on the existence of dental records registered by a dentist. Nevertheless, even if a person does not have such records, a photograph of their smile or an old dental prosthesis can be used for comparison.
Forensic DNA analysis can be a useful tool in aiding forensic identification because DNA is found in almost all cells of the body except mature red blood cells. Deoxyribonucleic acid is located in two different places of the cell, the nucleus; which is inherited from both parents, and the mitochondria; inherited maternally. As with fingerprints, an individual's DNA profile and characteristics are unique. Forensic identification using DNA can be useful in different cases such as determining suspects in violent crimes, solving paternity/maternity, and identifying human remains of victims from mass disasters or missing person cases. It is also used to link suspects or victims to each other or to crime scenes. When a sample is located at a crime scene, it must be collected, processed, and transported, along with a chain of custody, to the laboratory for analysis, so that if a DNA profile is generated it can be accepted in court. Proper evidence collection and preservation is crucial to ensure evidence is not being contaminated. Main procedures investigators must use when packaging biological material is allowing the evidence to air dry and then package into paper bags. Plastic bags should never be used on biological evidence because it could degrade DNA or lead to bacterial growth. DNA can be sourced from biological material such as semen, blood, saliva, feces, urine, teeth, bone, and hair that is left behind from an individual. There are different presumptive and confirmatory tests used for each type of biological material found at a scene. Presumptive tests are quick, sensitive and are relatively specific to bodily fluids that give the analyst an idea of what might be present. Confirmatory tests confirm what the biological sample is. In addition to looking for biological material at a crime scene, pieces of evidence can also be examined and analyzed for the presence of DNA. Evidence pieces that may have the presence of DNA could include clothing, bedding, weapons, masks, gloves, among many others. This is attributed to touch DNA, where only minute samples are left after an object has been touched. It is defined as "evidence with no visible staining that would likely contain DNA resulting from the transfer of epithelial cells from the skin to an object." A forensic scientist can attempt to obtain a DNA profile from the sample with as few as six cells. The first step in the DNA process with a piece of evidence is extraction. Extraction is a technique used to remove the DNA from the cell. The next step would be quantification which determines how much DNA is present. The third step is amplification in order to yield multiple copies of DNA. Next is separation, to separate the DNA out to use for identification.
Finally, the analyst can now complete analysis and interpretation of the DNA sample and compare to known profiles. An unknown sample found at a crime scene is called a questioned sample. A known sample can be taken either from a suspect or found in a database. The FBI's database used for DNA is CODIS, Combined DNA Index System. It has data at three levels: local, state, and national. The national level data is stored in NDIS, National DNA Index system. CODIS/NDIS allows analysts to compare their questioned DNA profile among those of arrestees, convicted offenders, and other unknown samples to try and produce investigative leads. If questioned and known samples are similar, statistics and interpretation will then be completed. The DNA profile will be compared to a population database and a random match probability will be determined.
Random match probability is defined as the chance that an individual selected randomly from a population will have an identical DNA profile to the markers tested. If they do not equal each other, they are not a match, termed exclusion. During DNA typing, several markers are examined, termed loci. When more markers are examined, this could result in either a greater probability that two unrelated individuals will have different genotypes or adds to the confidence of connecting an individual to an unknown sample. One locus difference between a questioned and known sample is enough to exclude that suspect as the contributor. The FBI has identified 13 core STR loci that are effective for human identification. STR is short tandem repeats which are short DNA regions in the genome and are 2–6 base pairs in length. STR is common in forensic analysis because they are easily amplified using polymerase chain reaction (PCR) and they have unique variation among individuals for human identification. PCR is the technique of copying DNA by making millions of copies. When all 13 core loci are tested on a DNA profile, the random match probability is more than one in a trillion. Since DNA was first used in a criminal investigation in 1986, it has aided investigators to solve many cases. DNA profiling is one of the most important tools in forensics and continued research will increase its ability and accuracy to provide more techniques for the future.
Note: You can easily convert this markdown file to a PDF in VSCode using this handy extension Markdown PDF . Digital Forensics is the process of recovering and preserving material found on digital devices during the course of criminal investigations. Digital forensics tools include hardware and software tools used by law enforcement to collect and preserve digital evidence and support or refute hypotheses before courts.
Computer Forensics is the process of examining digital media in a forensic-like manner with the goal of identifying, preserving, recovering, analyzing and presenting facts and opinions about the digital information. Mobile device forensics is the science of recovering digital evidence from a mobile device under forensically sound conditions using accepted methods. Mobile device forensics is an evolving specialty in the field of digital forensics.
2. System Architecture & Core Working Principles Network forensics is a science that centers on the discovery and retrieval of information surrounding a cybercrime within a networked environment. Common forensic activities include the capture, recording and analysis of events that occurred on a network in order to establish the source of cyberattacks.
Database forensics is the process of interrogating a failed database and trying to reconstruct the metadata and page information from within a data set, whereas database recovery implies some kind of restorative process that will enable the database to become viable enough to be put back into a production environment, or healthy enough to provide a backup that can be used in a database restore.
Art of Memory Forensics - Detecting Malware and Threats in Windows, Linux, and Mac Memory. Crafting the InfoSec Playbook: Security Monitoring and Incident Response Master Plan - by Jeff Bollinger, Brandon Enright and Matthew Valites. Digital Forensics and Incident Response: Incident response techniques and procedures to respond to modern cyber threats - by Gerard Johansen.
Incident Response & Computer Forensics, Third Edition - The definitive guide to incident response. Incident Response Techniques for Ransomware Attacks - A great guide to build an incident response strategy for ransomware attacks. By Oleg Skulkin. Incident Response with Threat Intelligence - Great reference to build an incident response plan based also on Threat Intelligence. By Roberto Martinez.
Operator Handbook: Red Team + OSINT + Blue Team Reference - Great reference for incident responders. Practical Memory Forensics - The definitive guide to practice memory forensics. By Svetlana Ostrovskaya and Oleg Skulkin. The Practice of Network Security Monitoring: Understanding Incident Detection and Response - Richard Bejtlich's book on IR. Open Source Security Foundation (OpenSSF) Identifying Security Threats in Open Source Projects Securing The Software Supply Chain: Recommended Practices Guide for Developers | CISA, NSA, and ODNI (PDF) Playbooks can help automate and orchestrate your response, and can be set to run automatically when specific alerts or incidents are generated, by being attached to an analytics rule or an automation rule.
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It is used by law enforcement, military, and corporate examiners to investigate what happened on a computer. You can even use it to recover photos from your camera's memory card. The Sleuth Kit® (TSK) is a library and collection of command line tools that allow you to investigate disk images. The core functionality of TSK allows you to analyze volume and file system data. The library can be incorporated into larger digital forensics tools and the command line tools can be directly used to find evidence.
PTK Forensics is a computer forensic framework for the command line tools in the SleuthKit plus much more software modules. DFF (Digital Forensics Framework) is a free and Open Source computer forensics software built on top of a dedicated Application Programming Interface (API). It can be used both by professional and non-expert people in order to quickly and easily collect, preserve and reveal digital evidences without compromising systems and data.
Mobile Device Investigator® is a security tool that powers rapid investigations of iOS and Android devices by connecting a suspect device via USB port to perform logical acquisitions. Digital Evidence Investigator® is a digital forensic tool for Windows, Linux, and macOS (including T2 and M1 chips). DEI collects digital evidence and presents it in a timeline view to tie the user to files and artifacts.
Digital Evidence Investigator® PRO is a tool that includes Windows, Linux and macOS (including T2 and M1 chips) computer forensic capabilities of Digital Evidence Investigator® and Mobile Device Investigator® iOS/Android capabilities in a single license. Guymager is a free forensic imager for media acquisition. Its main features are: Easy user interface in different languages.
Really fast, due to multi-threaded, pipelined design and multi-threaded data compression. Generates flat (dd), EWF (E01) and AFF images, supports disk cloning. Free of charges, completely open source. X-Ways Investigator is a reduced, simplified version of X-Ways Forensics for police investigators, lawyers, and auditors. WinHex is a Hex editor, disk editor, and RAM editor. Computer forensics, data recovery, and IT security tool.
F-Response is a remote network drive analysis capability, remote RAM access, and cloud storage access. AccessData Forensics Toolkit (FTK®) is built for speed, stability and ease of use. It provides comprehensive processing and indexing up front, so filtering and searching is faster than with any other product. This means you can zero in on the relevant evidence quickly, dramatically increasing your analysis speed.
OpenText™ EnCase™ is a commercial forensics platform. It offers support for evidence collection from over twenty-five different types of devices, including desktops, mobile devices and GPS. Within the tool, a forensic investigator can inspect the collected data and generate a wide range of reports based upon predefined templates. Redline® is FireEye's premier free endpoint security tool, provides host investigative capabilities to users to find signs of malicious activity through memory and file analysis and the development of a threat assessment profile. It collects information about running processes on a host, drivers from memory and gathers other data like meta data, registry data, tasks, services, network information and internet history to build a proper report.
Paraben's Electronic Evidence Examiner—E3 is a comprehensive digital forensic platform designed to handle more data, more efficiently while adhering to Paraben's paradigm of specialized focus of the entire forensic exam process. Paraben has capabilities in: Bulk Extractor is a program that extracts features such as email addresses, credit card numbers, URLs, and other types of information from digital evidence files. It is a useful forensic investigation tool for many tasks such as malware and intrusion investigations, identity investigations and cyber investigations, as well as analyzing imagery and pass-word cracking.
Registry Recon is a powerful computer forensics tool developed by Arsenal Recon. The tool is used to extract, recover, and parse registry data from Windows systems. The process of manually scouring Windows Registry files proves to be extremely time consuming and leaves gaping holes in the ability to recover critical information. 3. Software Implementation, Frameworks & Protocols Volatility is the memory forensics framework. It is used for incident response and malware analysis. With this tool, you can extract information from running processes, network sockets, network connection, DLLs and registry hives. It also has support for extracting information from Windows crash dump files and hibernation files.
WindowsSCOPE is a commercial memory forensics and reverse engineering tool used for analyzing volatile memory. It is basically used for reverse engineering of malware. It provides the ability to analyze the Windows kernel, drivers, DLLs and virtual and physical memory. Wireshark is the most widely used network traffic analysis tool in existence. It has the ability to capture live traffic or ingest a saved capture file.
Network Miner is an open source Network Forensic Analysis Tool (NFAT) for Windows (also Linux, macOS, and FreeBSD). NetworkMiner can be used as a passive network sniffer/packet capturing tool in order to detect operating systems, sessions, hostnames, and open ports without putting any traffic on the network. Xplico is an open-source network forensic analysis tool. It is used to extract useful data from applications which use Internet and network protocols. It supports most of the popular protocols including HTTP, IMAP, POP, SMTP, SIP, TCP, UDP, TCP and others. Output data of the tool is stored in an SQLite database or MySQL database. It also supports both IPv4 and IPv6.
Oxygen Forensic Detective is a forensic's tool that focuses on mobile devices but is capable of extracting data from a number of different platforms, including mobile, IoT, cloud services, drones, media cards, backups and desktop platforms. It uses physical methods to bypass device security (such as screen lock) and collects authentication data for a number of different mobile applications.
XRY is a collection of different commercial tools for mobile device forensics. XRY Logical is a suite of tools designed to interface with the mobile device operating system and extract the desired data. XRY Physical, on the other hand, uses physical recovery techniques to bypass the operating system, enabling analysis of locked devices. SIFT Workstation is another open-source Linux virtual machine that aggregates free digital forensics tools. This platform was developed by the SANS Institute and its use is taught in a number of their courses.
HashKeeper is a central database repository of Forensic Intelligence donated by various sources, usually obtained by law enforcement during the course of forensic investigations of suspect systems. Forensic Explorer Command Line (FEX CLI) is a forensic data processing engine used for computer forensics and electronic discovery. The FEX CLI can be run on a single workstation to an enterprise level virtual environment spawning multiple simultaneous processing instances.
FEX Memory Imager (FEX Memory) is a free imaging tool designed to capture the physical Random Access Memory (RAM) of a suspect’s running computer. This allows investigators to recover and analyze valuable artifacts found only in memory. FEX Imager™ is a free forensic imaging program that will acquire or hash a bit-level forensic image with full MD5, SHA1, SHA256 hash authentication. It can acquire a physical drive, logical drive, folders and files, remote devices (using servlet), or re-acquire a forensic image.
Forensic Explorer™ is a flexible and easy to use GUI with advanced sort, filter, keyword search, data recovery and script technology. It can quickly process large volumes of data, automate complex investigation tasks, produce detailed reports and increase productivity. Rehex is a cross-platform (Windows, Linux, Mac) hex editor for reverse engineering, and everything else.
DIRTY is a Augmenting Decompiler Output with Learned Variable Names and Types developed by the Socio-Technical Research Using Data Excavation Lab, at Carnegie Mellon University. Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from various disk and file formats, developed by Fox-IT (part of NCC Group).
Acquire is a tool to quickly gather forensic artifacts from disk images or a live system into a lightweight container. Artifactcollector is a project that provides a software that collects forensic artifacts on systems. Cold Disk Quick Response is a streamlined list of parsers to quickly analyze a forensic image file ( dd , E01, .vmdk , etc) and output nine reports.
CyLR - is a tool that collects forensic artifacts from hosts with NTFS file systems quickly, securely and minimizes impact to the host. UAC (Unix-like Artifacts Collector) is a Live Response collection script for Incident Response that makes use of native binaries and tools to automate the collection of AIX, Android, VMware ESXi, FreeBSD, Linux, macOS, NetBSD, NetScaler, OpenBSD and Solaris systems artifacts.
Magnet ACQUIRE is a Forensics tool that allows various types of disk acquisitions to be performed on Windows, Linux, and macOS as well as mobile operating systems (iOS & Android). HVM (Hardware Virtual Machine) is a virtualization type that provides the ability to run an operating system directly on top of a virtual machine without any modification, as if it were run on the bare-metal hardware.
PV(ParaVirtualization) is an efficient and lightweight virtualization technique introduced by the Xen Project team, later adopted by other virtualization solutions. PV does not require virtualization extensions from the host CPU and thus enables virtualization on hardware architectures that do not support Hardware-assisted virtualization. Virtualization-based Security (VBS) is a hardware virtualization feature to create and isolate a secure region of memory from the normal operating system.
Hypervisor-Enforced Code Integrity (HVCI) is a mechanism whereby a hypervisor, such as Hyper-V, uses hardware virtualization to protect kernel-mode processes against the injection and execution of malicious or unverified code. Code integrity validation is performed in a secure environment that is resistant to attack from malicious software, and page permissions for kernel mode are set and maintained by the hypervisor.
KVM (for Kernel-based Virtual Machine) is a full virtualization solution for Linux on x86 hardware containing virtualization extensions (Intel VT or AMD-V). It consists of a loadable kernel module, kvm.ko, that provides the core virtualization infrastructure and a processor specific module, kvm-intel.ko or kvm-amd.ko. QEMU is a fast processor emulator using a portable dynamic translator. QEMU emulates a full system, including a processor and various peripherals. It can be used to launch a different Operating System without rebooting the PC or to debug system code.
Hyper-V enables running virtualized computer systems on top of a physical host. These virtualized systems can be used and managed just as if they were physical computer systems, however they exist in virtualized and isolated environment. Special software called a hypervisor manages access between the virtual systems and the physical hardware resources. Virtualization enables quick deployment of computer systems, a way to quickly restore systems to a previously known good state, and the ability to migrate systems between physical hosts.
VirtManager is a graphical tool for managing virtual machines via libvirt. Most usage is with QEMU/KVM virtual machines, but Xen and libvirt LXC containers are well supported. Common operations for any libvirt driver should work. oVirt is an open-source distributed virtualization solution, designed to manage your entire enterprise infrastructure. oVirt uses the trusted KVM hypervisor and is built upon several other community projects, including libvirt, Gluster, PatternFly, and Ansible.Founded by Red Hat as a community project on which Red Hat Enterprise Virtualization is based allowing for centralized management of virtual machines, compute, storage and networking resources, from an easy-to-use web-based front-end with platform independent access.
4. Practical Deployment, Analysis & Case Studies HyperKit is a toolkit for embedding hypervisor capabilities in your application. It includes a complete hypervisor, based on xhyve / bhyve , which is optimized for lightweight virtual machines and container deployment. It is designed to be interfaced with higher-level components such as the VPNKit and DataKit . HyperKit currently only supports macOS using the Hypervisor.framework making it a core component of Docker Desktop for Mac.
Intel® Graphics Virtualization Technology (Intel® GVT) is a full GPU virtualization solution with mediated pass-through, starting from 4th generation Intel Core (TM) processors with Intel processor graphics(Broadwell and newer). It can be used to virtualize the GPU for multiple guest virtual machines, effectively providing near-native graphics performance in the virtual machine and still letting your host use the virtualized GPU normally.
Apple Hypervisor is a frameowrk that builds virtualization solutions on top of a lightweight hypervisor, without third-party kernel extensions. Hypervisor provides C APIs so you can interact with virtualization technologies in user space, without writing kernel extensions (KEXTs). As a result, the apps you create using this framework are suitable for distribution on the Mac App Store .
Apple Virtualization Framework is a framework that provides high-level APIs for creating and managing virtual machines on Apple silicon and Intel-based Mac computers. This framework is used to boot and run a Linux-based operating system in a custom environment that you define. It also supports the Virtio specification , which defines standard interfaces for many device types, including network, socket, serial port, storage, entropy, and memory-balloon devices.
Apple Paravirtualized Graphics Framework is a framework that implements hardware-accelerated graphics for macOS running in a virtual machine, hereafter known as the guest. The operating system provides a graphics driver that runs inside the guest, communicating with the framework in the host operating system to take advantage of Metal-accelerated graphics. Cloud Hypervisor is an open source Virtual Machine Monitor (VMM) that runs on top of KVM . The project focuses on exclusively running modern, cloud workloads, on top of a limited set of hardware architectures and platforms. Cloud workloads refers to those that are usually run by customers inside a cloud provider. Cloud Hypervisor is implemented in Rust and is based on the rust-vmm crates.
VMware vSphere Hypervisor is a bare-metal hypervisor that virtualizes servers; allowing you to consolidate your applications while saving time and money managing your IT infrastructure. Xen is focused on advancing virtualization in a number of different commercial and open source applications, including server virtualization, Infrastructure as a Services (IaaS), desktop virtualization, security applications, embedded and hardware appliances, and automotive/aviation.
Ganeti is a virtual machine cluster management tool built on top of existing virtualization technologies such as Xen or KVM and other open source software. Once installed, the tool assumes management of the virtual instances (Xen DomU). Packer is an open source tool for creating identical machine images for multiple platforms from a single source configuration. Packer is lightweight, runs on every major operating system, and is highly performant, creating machine images for multiple platforms in parallel. Packer does not replace configuration management like Chef or Puppet. In fact, when building images, Packer is able to use tools like Chef or Puppet to install software onto the image.
Vagrant is a tool for building and managing virtual machine environments in a single workflow. With an easy-to-use workflow and focus on automation, Vagrant lowers development environment setup time, increases production parity, and makes the "works on my machine" excuse a relic of the past. It provides easy to configure, reproducible, and portable work environments built on top of industry-standard technology and controlled by a single consistent workflow to help maximize the productivity and flexibility of you and your team.
Parallels Desktop is a Desktop Hypervisor that delivers the fastest, easiest and most powerful application for running Windows/Linux on Mac (including the new Apple M1 chip ) and ChromeOS. VMware Fusion is a Desktop Hypervisor that deliver desktop and ‘server’ virtual machines, containers and Kubernetes clusters to developers, and IT professionals on the Mac.
VMware Workstation is a hosted hypervisor that runs on x64 versions of Windows and Linux operating systems; it enables users to set up virtual machines on a single physical machine, and use them simultaneously along with the actual machine. GlusterFS is a free and open source scalable network filesystem. Gluster is a scalable network filesystem. Using common off-the-shelf hardware, you can create large, distributed storage solutions for media streaming, data analysis, and other data- and bandwidth-intensive tasks.
Ceph is a software-defined storage solution designed to address the object, block, and file storage needs of data centers adopting open source as the new norm for high-growth block storage, object stores and data lakes. Ceph provides enterprise scalable storage while keeping CAPEX and OPEX costs in line with underlying bulk commodity disk prices. Hadoop Distributed File System (HDFS) is a distributed file system that handles large data sets running on commodity hardware. It is used to scale a single Apache Hadoop cluster to hundreds (and even thousands) of nodes. HDFS is one of the major components of Apache Hadoop, the others being MapReduce and YARN .
ZFS is an enterprise-ready open source file system and volume manager with unprecedented flexibility and an uncompromising commitment to data integrity. OpenZFS is an open-source storage platform. It includes the functionality of both traditional file systems and volume manager. It has many advanced features including: Btrfs is a modern copy on write (CoW) filesystem for Linux aimed at implementing advanced features while also focusing on fault tolerance, repair and easy administration. Its main features and benefits are: Squashfs is a compressed read-only filesystem for Linux. It uses zlib, lz4, lzo, or xz compression to compress files, inodes and directories. Inodes in the system are very small and all blocks are packed to minimize data overhead.
Apple File System (APFS) is the default file system for Mac computers using macOS 10.13 or later, features strong encryption, space sharing, snapshots, fast directory sizing, and improved file system fundamentals. NTFS(New Technology File System) is the primary file system for recent versions of Windows and Windows Server—provides a full set of features including security descriptors, encryption, disk quotas, and rich metadata, and can be used with Cluster Shared Volumes (CSV) to provide continuously available volumes that can be accessed simultaneously from multiple nodes of a failover cluster.
exFAT(Extended File Allocation Table ) is the file system that was the successor to FAT32 in the FAT family of file systems. It was optimized for flash memory such as USB flash drives and SD cards. Federal Risk and Authorization Management Program (FedRAMP) is a government-wide program that provides a standardized approach to security assessment, authorization, and continuous monitoring for cloud products and services.
FedRAMP empowers agencies to use modern cloud technologies, with emphasis on security and protection of federal information, and helps accelerate the adoption of secure, cloud solutions. Federal Information Security Management Act (FISMA) is a United States federal law that defines a comprehensive framework to protect government information, operations, and assets against natural and manmade threats. This risk management framework was signed into law as part of the Electronic Government Act of 2002. Since 2002, FISMA's scope has widened to apply to state agencies that administer federal programs, or private businesses and service providers that hold a contract with the U.S. government.
Common Criteria for Information Technology Security Evaluation (CC) is an international standard (ISO / IEC 15408) for computer security. It allows an objective evaluation to validate that a particular product satisfies a defined set of security requirements. ISO 22301 is the international standard that provides a best-practice framework for implementing an optimised BCMS (business continuity management system).
ISO27001 is the international standard that describes the requirements for an ISMS (information security management system). The framework is designed to help organizations manage their security practices in one place, consistently and cost-effectively. ISO 27701 specifies the requirements for a PIMS (privacy information management system) based on the requirements of ISO 27001. It is extended by a set of privacy-specific requirements, control objectives and controls. Companies that have implemented ISO 27001 will be able to use ISO 27701 to extend their security efforts to cover privacy management.
SOC 2 is an auditing procedure that ensures your service providers securely manage your data to protect the interests of your comapny/organization and the privacy of their clients. 5. Performance Evaluation & Extended Technical Observations NIST CSF is a voluntary framework primarily intended for critical infrastructure organizations to manage and mitigate cybersecurity risk based on existing best practice.
EU GDPR (General Data Protection Regulation) is a privacy and data protection law that supersedes existing national data protection laws across the EU, bringing uniformity by introducing just one main data protection law for companies/organizations to comply with. CCPA (California Consumer Privacy Act) is a data privacy law that took effect on January 1, 2020 in the State of California. It applies to businesses that collect California residents’ personal information, and its privacy requirements are similar to those of the EU’s GDPR (General Data Protection Regulation).
Payment Card Industry (PCI) Data Security Standards (DSS) is a global information security standard designed to prevent fraud through increased control of credit card data. Landlock LSM(Linux Security Module) is a framework to create scoped access-control (sandboxing). Landlock is designed to be usable by unprivileged processes while following the system security policy enforced by other access control mechanisms (DAC, LSM, etc.).
Secure boot is a security standard developed by members of the PC industry to help make sure that a device boots(Unified Extensible Firmware Interface (UEFI) BIOS) using only software(such as bootloaders, OS, UEFI drivers, and utilities) that is trusted by the Original Equipment Manufacturer (OEM). Symmetric is a data encryption method whereby the same private key is used to encode and decode information.
Asymmetric is a data encryption method that allows users to encrypt information using shared keys. For example, if you need to send a message across the internet, but you don't want anyone but the intended recipient to see what you've written. Triple DES (Triple Data Encryption Algorithm) is a symmetric-key block cipher, which applies the DES cipher algorithm three times to each data block(contains 64 bits of data).
AES (Advanced Encryption Standard) is an algorithm that encrypts and decrypts data in blocks of 128 bits. It can do this using 128-bit, 192-bit, or 256-bit keys. RSA (Rivest–Shamir–Adleman) is a type of public-key cryptography used for secure data transmission of e-mail and other digital transactions over the Internet.
Twofish is a symmetric key block cipher with a block size of 128 bits and key sizes up to 256 bits. It is an advanced version of Blowfish encryption. Format Preserving Encryption (FPE) is a valid encryption algorithm to be used for compliance with NIST standards. It is mostly used in on-premise encryption and tokenization solutions.
Hashes is a function that converts an input of letters and numbers into an encrypted output of a fixed length. For example, algorithms such as MD5 (Message Digest 5) or SHA (Secure Hash Algorithm) . Digital Certificates is a file that verifies the identity of a device or user and enables encrypted connections. A digital signature is a hashing approach that uses a numeric string to provide authenticity and validate identity. Digital certificates are typically issued by a certificate authority (CA) , which is a trusted third-party entity that issues digital certificates for use by other parties.
Netdata is high-fidelity infrastructure monitoring and troubleshooting, real-time monitoring Agent collects thousands of metrics from systems, hardware, containers, and applications with zero configuration. It runs permanently on all your physical/virtual servers, containers, cloud deployments, and edge/IoT devices, and is perfectly safe to install on your systems mid-incident without any preparation.
Acra is a single database security suite with 9 strong security controls: application level encryption, searchable encryption, data masking, data tokenization, secure authentication, data leakage prevention, database request firewall, cryptographically signed audit logging, security events automation. It is designed to cover the most important data security requirements with SQL and NoSQL databases and distributed apps in a fast, convenient, and reliable way.
OWASP Nettacker is a project created to automate information gathering, vulnerability scanning and eventually generating a report for networks, including services, bugs, vulnerabilities, misconfigurations, and other information. This software will utilize TCP SYN, ACK, ICMP, and many other protocols in order to detect and bypass Firewall/IDS/IPS devices. OpenSCAP is U.S. standard maintained by National Institute of Standards and Technology (NIST) . It provides multiple tools to assist administrators and auditors with assessment, measurement, and enforcement of security baselines. OpenSCAP maintains great flexibility and interoperability by reducing the costs of performing security audits. Whether you want to evaluate DISA STIGs, NIST‘s USGCB, or Red Hat’s Security Response Team’s content, all are supported by OpenSCAP.
OWASP is an online community, produces freely-available articles, methodologies, documentation, tools, and technologies in the field of web application security. Open Vulnerability and Assessment Language is a community effort to standardize how to assess and report upon the machine state of computer systems. OVAL includes a language to encode system details, and community repositories of content. Tools and services that use OVAL provide enterprises with accurate, consistent, and actionable information to improve their security.
Terrascan is a static code analyzer for Infrastructure as Code to mitigate risk before provisioning cloud native infrastructure. Sliver is an open source cross-platform adversary emulation/red team framework, it can be used by organizations of all sizes to perform security testing. Sliver's implants support C2 over Mutual TLS (mTLS), WireGuard, HTTP(S), and DNS and are dynamically compiled with per-binary asymmetric encryption keys.
Payloads All The Things is a list of useful payloads and bypass for Web Application Security and Pentest/CTF. Flipper Zero is a portable multi-tool for pentesters and geeks in a toy-like body. It loves hacking digital stuff, such as radio protocols, access control systems, hardware and more. It's fully open-source and customizable, so you can extend it in whatever way you like.
TheHive is a scalable 3-in-1 open source and free Security Incident Response Platform designed to make life easier for SOCs, CSIRTs, CERTs and any information security practitioner dealing with security incidents that need to be investigated and acted upon swiftly. It is the perfect companion to MISP . Cortex is a Powerful Observable Analysis and Active Response Engine. This solves a common problem frequently encountered by SOCs, CSIRTs and security researchers in the course of threat intelligence, digital forensics and incident response.
MITRE ATT&CK® is a global knowledge base of adversary tactics and techniques based on real-world security observations. It is used as a foundation for the development of specific threat models and methodologies in the private sector, in government, and in the cybersecurity product and service community. CALDERA™ is a cyber security platform designed to easily automate adversary emulation, assist manual red-teams, and automate incident response.
Atomic Red Team™ is a library of tests mapped to the MITRE ATT&CK® framework. Security teams can use Atomic Red Team to quickly, portably, and reproducibly test their environments. OpenCTI is an open source platform allowing organizations to manage their cyber threat intelligence knowledge and observables. It has been created in order to structure, store, organize and visualize technical and non-technical information about cyber threats.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Computer%20forensics • https://en.wikipedia.org/wiki/Digital%20forensics • https://en.wikipedia.org/wiki/Forensic%20identification • https://github.com/mikeroyal/Digital-Forensics-Guide
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Digital Forensics Artifact Extraction Tool Using Python.
[*] Metasploit Scan Running on Target Subnet for Digital Forensics Artifact Extraction Tool Using Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |