Complete Technical Paper Content — Digital Image Steganography Using Lsb Algorithm And Python
Overview & System Context
Digital Image Steganography Using Lsb Algorithm And Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~4226 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Step up your coding game with AI-powered Code Explainer . Get insights like never before! In this tutorial, you will learn how you can hide data into images with Python using OpenCV and NumPy libraries. This is called Steganography.
Steganography is the practice of hiding a file, message, image, or video within another file, message, image, or video. The word Steganography is derived from the Greek words "steganos" (meaning hidden or covered) and "graphe" (meaning writing). Hackers often use it to hide secret messages or data within media files such as images, videos, or audio files. Even though there are many legitimate uses for Steganography, such as watermarking, malware programmers have also been found to use it to obscure the transmission of malicious code.
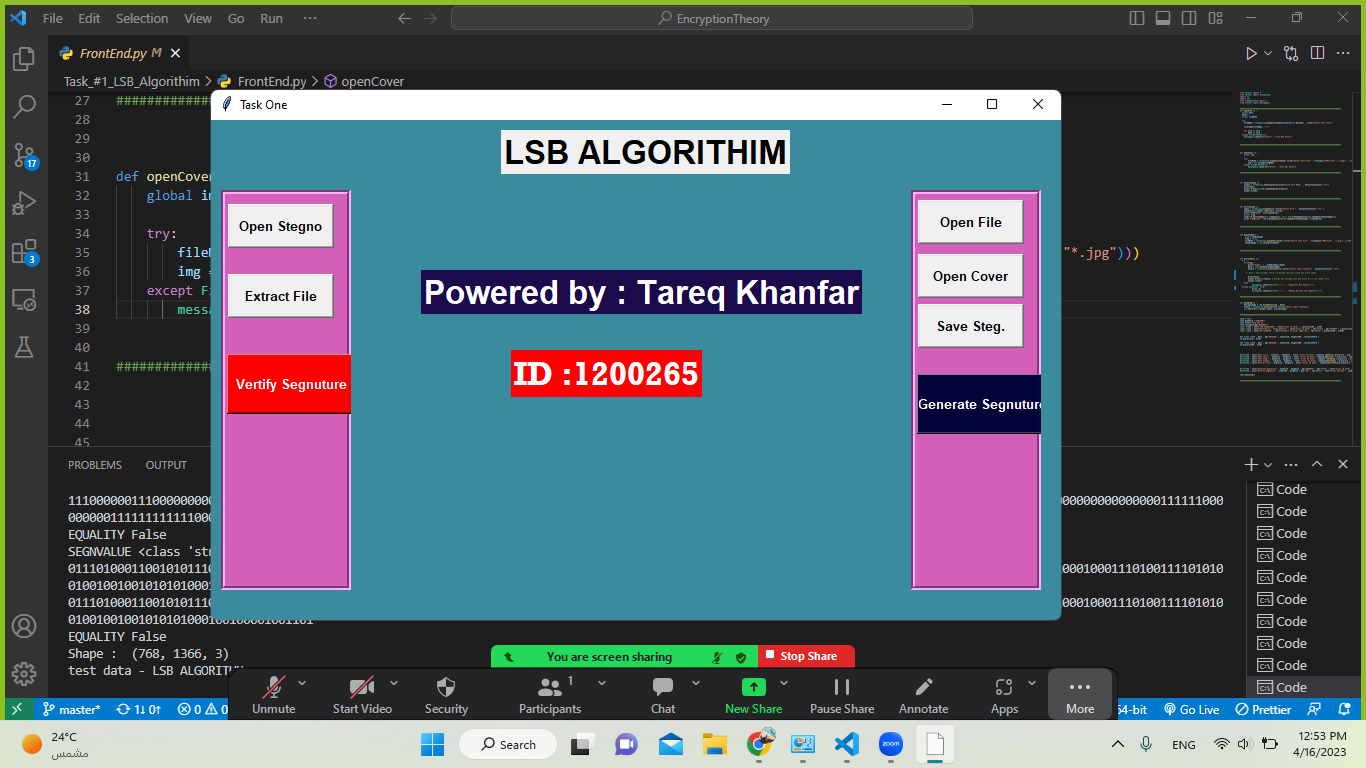
Figure 1: GitHub - tareqkhanfar/Steganography-Encryption---LSB-Algorithm In this tutorial, we will write Python code to hide text messages using Least Significant Bit . L east S ignificant B it (LSB) is a technique in which the last bit of each pixel is modified and replaced with the data bit. This method only works on Lossless-compression images, which means the files are stored in a compressed format. However, this compression does not result in the data being lost or modified. PNG , TIFF , and BMP are examples of lossless-compression image file formats.
As you may already know, an image consists of several pixels, each containing three values (Red, Green, and Blue); these values range from 0 to 255 . In other words, they are 8-bit values. For example, a value of 225 is 11100001 in binary, and so on. To simplify the process, let's take an example of how this technique works; say I want to hide the message "hi" in a 4x3 image.
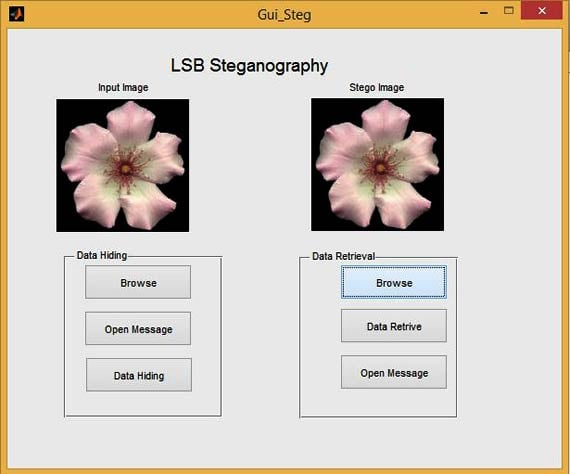
Here are the example image pixel values: Figure 2: Matlab Code for LSB Steganography -Image processing project By looking at the ASCII Table , we can convert the "hi" message into decimal values and then into binary: Now, we iterate over the pixel values one by one; after converting them to binary, we replace each least significant bit with that message bit sequentially. 225 is 1110000 1 , we replace the last bit (highlighted), the bit in the right ( 1 ), with the first data bit ( 0 ), which results in 11100000, meaning it's 224 now.
After that, we go to the next value, which is 0000110 0 , and replace the last bit with the following data bit (1), and so on until the data is completely encoded. This will only modify the pixel values by +1 or -1 , which is not visually noticeable. You can also use 2-Least Significant Bits, which will change the pixel values by a range of -3 to +3 .
Figure 3: Image Steganography using Python – THE NUCLEAR GEEKS You can also use the three or four least significant bits when the data you want to hide is a little bigger and won't fit your image if you use only the least significant bit. In the upcoming sections, we will add an option to use any number of bits you want. Now that we understand the technique we are going to use, let's dive into the Python implementation; we are going to use OpenCV to manipulate the image, you can use any other imaging library you want (such as PIL ): Let's start by implementing a function to convert any type of data into binary, and we will use this to convert the secret data and pixel values to binary in the encoding and decoding phases: We read the image and then get the last bits of every image pixel. After that, we keep decoding until we see the stopping criteria we used during encoding.
I have an example PNG image here; use whatever picture you want. Just make sure it is a Lossless-compression image format such as PNG, as discussed earlier. The above code will take image.PNG image, encode secret_data string into it and save it into encoded_image.PNG . After that, we use the decode() function that loads the new image and decodes the hidden message in it.
After the execution of the script, it will write another file "encoded_image.PNG" with precisely the same image looking but with secret data encoded in it. Here is the output: So we can decode about 122KB ( 125028 bytes) on this particular image. This will vary from one image to another based on its resolution size.
In this section, we will make another script that is more advanced than the previous one, which has the following additional features: To get started, we import the necessary libraries and the to_bin() function as before: Besides that, we wrap the encoding with another for loop iterating n_bits times. The default n_bits parameter is set to 2, meaning we encode the data in the two least significant bits of each pixel, and we will pass command-line arguments to this parameter. It can be as low as 1 (won't encode much data) or as high as 6, but the resulting image will look different and a bit noisy.
2. System Architecture & Core Working Principles For the decoding part, it's the same as before, but we add the in_bytes boolean parameter to indicate whether it's binary data. If it is so, then we use bytearray() instead of a regular string to construct our decoded data: Next, we use the argparse module to parse command-line arguments to pass to the encode() and decode() functions: Master Ethical Hacking with Python by building 35+ Tools from scratch. Get your copy now! We pass the image using the -e parameter, and the file we want to hide using the -f parameter. I also specified the number of least significant bits to be one. Unfortunately, see the output: This error is totally expected since using only one bit on each pixel value won't be sufficient to hide the entire 363KB file.
Therefore, let's increase the number of bits ( -b parameter): Two bits is still not enough. The maximum bytes to encode is 250KB, and we need around 370KB. Increasing to 3: You'll see now the data.csv is successfully encoded into a new image_encoded.PNG and it appeared in the current directory: Amazing! This time I have passed the encoded image to the -d parameter. I have also passed data_decoded.csv to -f for the resulting filename to write. Let's recheck our directory: As you can see, the new file appeared identical to the original. Note that you must set the same -b parameter when encoding and decoding.
I emphasize that you only increase the -b parameter when necessary (i.e., when the data is big). I have tried to hide a larger file (over 700KB) into the same image, and the minimum allowed least significant bit was 6. Here's what the resulting encoded image looks like: So there is clearly something wrong with the image, as the pixel values change in the range of -64 and +64 , so that's a lot.
As you may notice, the resulting image will look exactly the same as the original image only when the number of least significant bits ( -b parameter) is low such as one or two. So whenever a person sees the image, they won't be able to detect whether there is hidden data within it. If the data you want to hide is big, then make sure you take a high-resolution image instead of increasing the -b parameter to a higher number than 4 because it will be so evident that there is something wrong with the picture.
Also, if you're familiar with Linux commands, you can also perform Steganography using standard Linux commands. Finally, we have an Ethical Hacking with Python Ebook , where we build 35+ hacking tools and scripts! Make sure to check it out if you're interested. Save time and energy with our Python Code Generator . Why start from scratch when you can generate? Give it a try! Learn how to extract and download images from a single web page in Python using requests and BeautifulSoup libraries.
Learning how you can generate and read QR Code in Python using qrcode and OpenCV libraries. Learn how you can extract image metadata such as GPS info, camera make, model and much more using Exchangeable Image file Format (EXIF) in Python with Pillow library. Got a coding query or need some guidance before you comment? Check out this Python Code Assistant for expert advice and handy tips. It's like having a coding tutor right in your fingertips! This project implements Image Steganography using the Least Significant Bit (LSB) technique in Python. It allows users to securely hide a secret image inside a cover image and later extract the hidden image without causing noticeable visual changes to the cover image.
The project demonstrates a practical application of digital image processing, bit manipulation, and information security concepts. A Python-based image steganography system that uses the Least Significant Bit (LSB) technique to securely hide one image inside another and recover it without noticeable visual changes.
3. Software Implementation, Frameworks & Protocols Steganography (Hiding Data Inside Images) is the technique of concealing secret information within an image, audio, or video file. The goal is to embed data in such a way that it remains undetectable to the naked eye. The idea behind image-based Steganography is very simple. Images are made up of pixels, and each pixel consists of three color values: Red , Green , and Blue (RGB). We can modify these values slightly to encode hidden data without significantly altering the image's appearance.
1. Convert Data to Binary: Each character in the secret message is converted to its 8-bit binary representation using ASCII values. [(27, 64, 164), (248, 244, 194), (174, 246, 250), (149, 95, 232), (188, 156, 169), (71, 167, 127), (132, 173, 97), (113, 69, 206), (255, 29, 213), (53, 153, 220), (246, 225, 229), (142, 82, 175)] Notice There are currently 28 levels available. More levels will be added in the next months. Stay tuned for updates! Table of ContentsâIIâIIâIIâIIâIIâIIâIIâIIâIIâIIâIIâIIâIIâIIâIIâIIâIIâIIâIIâIIâIIâIIâI IâIIâIIâIIâIIâIIâIIâIIâIIâIIâIIâIIâIIâIIâIIâIIâIIâII YouâIIve played the game. YouâIIve uncovered secrets hidden in metadata, source code, and even the fabric of sound itself. You understand the theory behind Least Significant Bit (LSB) steganography: the art of making tiny, invisible changes to an imageâIIs pixels to encode data.
In this tutorial, weâIIre going to build our own simple steganography tool from scratch. Using Python, one of the most popular and accessible programming languages, we will write a script that can both hide a secret message inside a PNG image and extract a hidden message from one. Before writing any code, hereâIIs the entire idea in one paragraph: every pixel in an RGB image is three numbers (red, green, and blue), each somewhere between 0 and 255. Changing only the very last bit of one of those numbers shifts its value by at most 1 (from 200 to 201, say), which is far too small a difference for a human eye to notice but is trivial for a computer to write and read back deterministically. LSB steganography spends those âIIfreeâII last bits, one at a time, to encode a secret message bit by bit across as many pixel channels as it needs.
Do that once per bit of the message, across the red, green, and blue channel of every pixel in turn, and youâIIve hidden an entire message inside an image that still looks, to any human eye, completely unchanged. The one piece of bookkeeping this needs: something has to tell reveal where the message ends . A tempting shortcut is a text delimiter: some fixed string appended after the message, so reveal just keeps decoding characters until it sees that string.
ItâIIs simple, but fragile: if the secret message itself happens to contain that exact string, reveal stops early and mangles the result. The script below avoids that entirely by writing the messageâIIs exact byte length as a small header before the message. reveal reads that header first, then reads exactly that many bytes and stops, with nothing to search for and nothing that can collide.
Python 3: Most modern systems (macOS, Linux) have it pre-installed. For Windows, you can download it from python.org . The Pillow Library: This is a powerful and easy-to-use Python Imaging Library. You can install it by opening your terminal or command prompt and running: A Carrier Image: Find a simple, medium-sized PNG image. Using PNG is important because it is a âIIlosslessâII format, meaning it wonâIIt be altered by compression, which could destroy our hidden message. Save it as carrier.png in the same folder where youâIIll save your script. The script below works with RGB, RGBA, grayscale, and palette images alike; more on that in a moment.
Create a new file named stego.py and letâIIs start building it, section by section. Every code block below fits together into one file; if youâIId rather copy the whole thing at once, jump to the Complete Script Listing at the end. First, two small helper functions to convert between bytes and their binary-string representation: Next, a function that tells us exactly how many message bytes a given image can hold, so we can give a precise, useful error instead of a vague one: A few things worth calling out about what changed from the simplest possible version of this function: Now the reverse function, which reads the length header first and then exactly that many bytes of message: no delimiter to search for: Notice read_bits pulls from a single bit-level generator ( bit_stream() ) rather than looping over pixels directly. ThatâIIs a deliberate, slightly subtle choice: the header is 32 bits, which isnâIIt a multiple of 3, so the last pixel the header reads from will have one or two channels left over that belong to the message , not the header. A generator that yields one bit at a time picks up exactly where it left off on the very next call, mid-pixel if necessary. A pixel-at-a-time loop would silently skip those leftover channels and corrupt every bit that follows.
Since reveal_message never searches for a delimiter, a message containing something that looks like an old-style delimiter ( ##### , say) causes no problems at all. ItâIIs just more UTF-8 bytes, counted and consumed exactly like any other. Rather than hand-rolling argument checks against sys.argv , weâIIll use PythonâIIs built-in argparse module. It gives us free --help text, automatic error messages for missing or malformed arguments, and a cleaner way to define two distinct subcommands: Run python stego.py --help or python stego.py hide --help at any point and argparse prints usage text for you, no need to maintain it by hand.
4. Practical Deployment, Analysis & Case Studies Save the complete stego.py file. Make sure you have your carrier.png in the same directory. Now, open your terminal in that directory and try it out! This will create a new file named stego_image.png . Open it: it will look identical to carrier.png ! You have now successfully built a working steganography tool. You can use it to create your own puzzles, hide data for fun, and better understand the practical application of the techniques youâIIve been learning. Welcome to the other side of the game.
Before you trust this script for anything, even a CTF puzzle youâIIre building for a friend, run it through a handful of edge cases. Each of these is a genuinely different code path, not just a repeat of the happy path above: list(image.getdata()) loads every pixel of the image into memory as Python tuples before we touch a single bit. For a tutorial-sized image thatâIIs a non-issue; for a genuinely large image (a multi-megapixel photo, say), itâIIs slow and memory-hungry compared to a vectorized approach. If you outgrow this scriptâIIs performance, two directions are worth knowing about: One more thing you may notice depending on your installed Pillow version: newer Pillow releases mark Image.getdata() as deprecated in favor of a newer method, and will print a DeprecationWarning when you run this script. ThatâIIs expected, not a bug. getdata() still works today, and the warning is simply Pillow signaling a future API change.
The natural next step, if you want this to hide something you actually care about staying private, is to encrypt the message before hiding it , for example with AES, or with the XOR/one-time-pad concepts covered in our OTP and XOR Cryptography article. Encrypt first, then hide the resulting ciphertext bytes with this script; that way, even a successful reveal only recovers ciphertext, not your actual secret. That combination, steganography for concealment, real cryptography for confidentiality, is exactly the layered approach our Steganography vs. Cryptography article argues for.
LSB (Least Significant Bit) steganography hides data by altering the least significant bit of each pixelâIIs RGB values in an image. This script encodes a message as UTF-8 bytes, prepends a 4-byte length header, converts the whole thing to binary, and embeds each bit into the LSB of the imageâIIs red, green, and blue channels in turn, changes far too small for the human eye to see.
PNG is a lossless format, meaning it preserves pixel data without compression artifacts that could corrupt the hidden message. Formats like JPEG use lossy compression, which can destroy the embedded data. The script calculates your imageâIIs exact usable capacity (width ÃI height ÃI 3 channels, converted to bytes, minus 4 bytes for the length header) and tells you precisely how many bytes it can hold if your message is too big. Larger images can hold proportionally more data.
Not very, if âIIsecureâII means confidential. This basic LSB method offers concealment, not encryption: statistical steganalysis can detect that an image likely carries hidden data, and anyone who knows the method can extract it with no passphrase at all. See Limitations and Security above for the full picture, including why encrypting the message first is the right fix.
reveal_message reads what it assumes is a 4-byte length header from the imageâIIs LSBs. On an ordinary image, those bits are essentially random, so the âIIdeclared lengthâII it computes almost always turns out to be nonsensical, either far larger than the image could actually hold, or the resulting bytes simply arenâIIt valid UTF-8. Either way, the script reports one of its âIINo hidden message foundâII messages rather than crashing or printing garbage.
Yes. Messages are encoded as UTF-8 before embedding and decoded as UTF-8 on the way out, so accented letters, CJK text, emoji, and anything else representable in Unicode round-trip correctly. The one caveat is display, not encoding: some terminals (particularly older Windows consoles) canâIIt print certain Unicode characters even though the script decoded them correctly. See the note in How to Use Your New Tool above.
HereâIIs the entire stego.py , combining every piece above into one file you can copy and run directly. This is the exact code that was tested throughout this article, including the ASCII/Unicode round-trip, the ##### -containing message, a too-small cover image, a grayscale carrier, and a reveal on an image with no hidden data at all. Steganography is a technique of hiding information behind the scene. Unlike cryptography which focuses on encrypting data through algorithms like SHA1 or MD5, steganography focuses on hiding data (files, images, messages, or videos) within another medium to avoid detection.
In this tutorial, we'll create a Python program that hides information behind an image without noticeable changes to the image appearance. The program has two main components ? an encoding function to embed secret messages into images, and a decoding function to extract hidden information. We'll use the Python Pillow library and the stepic library for steganography operations ? Pixels are the smallest individual elements of an image. Each pixel represents a portion of the original image ? higher pixel count means more accurate representation.
In black and white images, pixels have binary values: 1 for black and 0 for white. In colored images, pixels use the RGB color model (Red, Green, Blue) with values ranging from 0-255 for each component. A pixel value of (255, 255, 255) represents white, while (0, 0, 0) represents black. Since 8-bit binary numbers can represent values up to 255, we can convert binary to decimal easily. For example, binary 01010101 converts to decimal as ? The stepic library uses Least Significant Bit (LSB) steganography. It modifies the least significant bits of pixel values to store message bits. Since LSB changes are minimal (±1), they're imperceptible to human eyes but can store substantial data.
? Invisibility: Hidden data is undetectable to casual observation ? Simplicity: Easy implementation with existing Python libraries ? Versatility: Works with various image formats (PNG, JPEG, BMP) ? Capacity: Can hide significant amounts of text data Steganography provides an effective method for hiding information within images using Python. The stepic library simplifies LSB steganography, allowing you to embed and extract secret messages without visible image changes. This technique has applications in secure communication, digital watermarking, and data protection.
5. Performance Evaluation & Extended Technical Observations This repository contains Python scripts for hiding messages within images and extracting hidden messages from encoded images. The scripts utilize the Python Imaging Library (PIL) for image manipulation. encode_message.py: This script hides a message within an image using LSB (Least Significant Bit) manipulation.
decode_message.py: This script extracts a hidden message from an encoded image using the provided key. Ensure to keep the generated key file (key.txt) secure and accessible for decoding messages. Avoid lossy compression formats (e.g., JPEG) for encoded images to prevent loss of hidden data. Encoding and hiding messages within images using LSB manipulation, with keys generated from system parameters.
Decoding messages from images using corresponding keys, ensuring security and uniqueness. This Python code implements a simple image steganography project using the Least Significant Bit (LSB) method. Here's a brief explanation: The data2binary function converts input data (either a string, bytes, or numpy array) into its binary representation. Hide Data in Image: The hide_data function takes an image and data as input and hides the data in the image using the LSB method. It also includes a password in the hidden data. Encoding: The encode function prompts the user to input an image file, a message, and a password. It then encodes the message into the image using the hide_data function and saves the result as a new image file. Find Data in Image: The find_data function extracts hidden data from an image using the LSB method. It also takes a password as input and uses it during decoding. Decoding: The decode function prompts the user to input an encoded image file and a password. It then decodes the hidden message using the find_data function and prints the result. Main Steganography Function: The steganography function is the main control loop. It allows the user to choose between encoding and decoding operations and continues until the user decides to exit. In summary, this code allows users to hide messages in images using steganography and retrieve them later with the correct password. The encoding process embeds the message in the image, and the decoding process extracts the hidden message using the provided password.
This repository houses a Python implementation of Image Steganography, a technique that conceals information within digital images using the Least Significant Bit (LSB) method. Steganography is the practice of hiding secret information within a non-suspicious file, message, or image, making it appear normal. Unlike encryption, where the content of the message is scrambled, steganography focuses on keeping the very existence of the message hidden. For example, a simple image could contain a hidden message without altering its visible appearance.
In digital steganography, information is often embedded in image, audio, or video files. A popular method involves modifying the least significant bits (LSB) of the pixel values in an image, which doesn't affect the overall appearance of the image but can store binary data. This project uses LSB steganography to hide a secret message within the red color channel of a PNG image.
This Python script allows you to hide a secret message inside a PNG image by manipulating the least significant bit (LSB) of the red channel in each pixel. The encoded message is appended with a marker 11111111 to indicate the end of the message, and the message is retrieved by decoding the LSBs of the red channel from the image. The script uses Python’s Pillow library for image manipulation and tkinter to open a file selection dialog for ease of use.
The message you wish to hide is converted to its binary representation. Each character is converted to its corresponding 8-bit binary equivalent. The script prompts the user to select an image file (PNG) using tkinter 's file dialog. The output image ( encoded_image.png ) will be saved in the same directory as the script, and the secret message will be automatically decoded to verify successful encoding.
A Python-based steganographic tool that conceals data in images using the Least Significant Bit (LSB) method. This project allows you to hide secret messages within image files with minimal visual distortion. This steganography tool implements the LSB (Least Significant Bit) technique to hide text messages within digital images. The LSB method modifies the least significant bit of each color channel (RGB) in an image to store binary data representing your secret message.
The tool can be used in two modes: Interactive Mode (menu-driven) or Command Line Mode (with arguments). Harvested Online Documentation & Reference Sources • https://thepythoncode.com/article/hide-secret-data-in-images-using-steganography-python • https://github.com/mohammadumair-lgtm/Image-Steganography-Python • https://www.geeksforgeeks.org/python/image-based-steganography-using-python/ • https://venatus.me/blog/diy-steganography-python-script/ • https://www.tutorialspoint.com/article/image-based-steganography-using-python • https://github.com/ayushpatel2307/Image_Steganography-Using-Python • https://github.com/megh212/Image-Steganography-using-LSB-Technique • https://github.com/eng-MohamedFayed/Image-Steganography • https://github.com/Intruder2614/lsbs_steganography
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Digital Image Steganography Using Lsb Algorithm And Python.
[*] Metasploit Scan Running on Target Subnet for Digital Image Steganography Using Lsb Algorithm And Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |