Complete Technical Paper Content — Digital Signature Based Document Verification System
Overview & System Context
Digital Signature Based Document Verification System: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9501 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A digital signature is a mathematical scheme for verifying the authenticity of digital messages or documents. A valid digital signature on a message gives any recipient confidence that the message came from a sender known to the recipient. In contrast, a message authentication code only gives confidence to a specific recipient that the message came from a known sender. Digital signatures are a type of public-key cryptography, and are commonly used for software distribution, financial transactions, contract management software, and in other cases where it is important to detect forgery or tampering. A digital signature on a message or document is similar to a handwritten signature on paper, but it is not restricted to a physical medium like paper—any bitstring can be digitally signed—and while a handwritten signature on paper could be copied onto other paper in a forgery, a digital signature on a message is mathematically bound to the content of the message so that it is infeasible for anyone to forge a valid digital signature on any other message. Digital signatures are often used to implement electronic signatures, which include any electronic data that carries the intent of a signature, but not all electronic signatures use digital signatures.
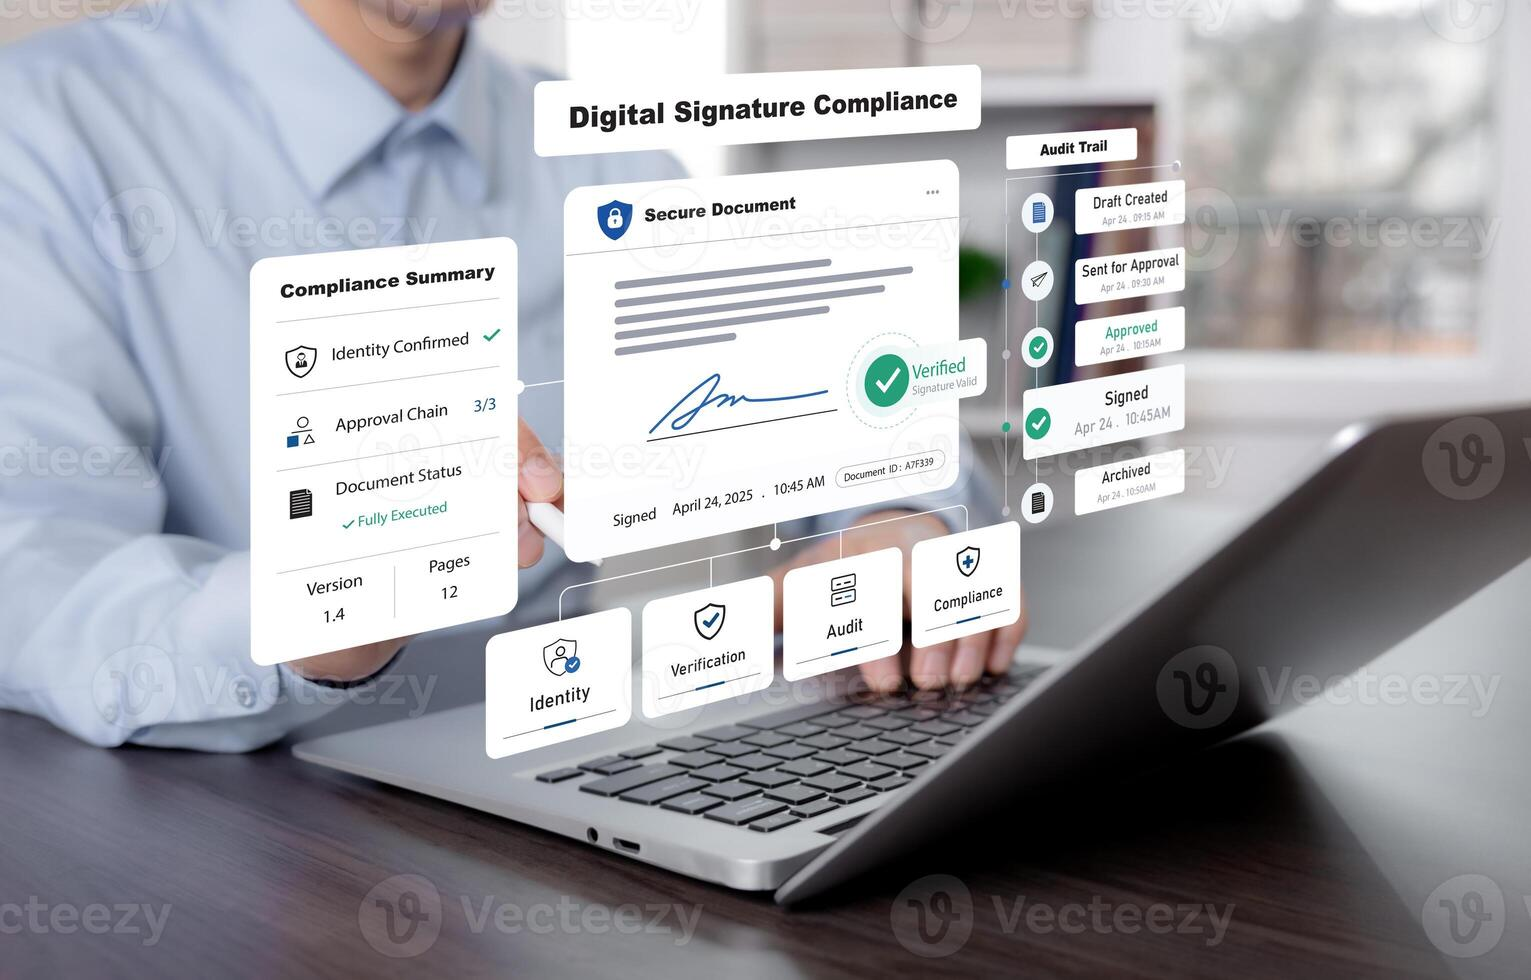
A key generation algorithm that selects a private key at random from a set of possible private keys. The algorithm outputs the private key and a corresponding public key. A signing algorithm that, given a message and a private key, produces a signature. A signature verifying algorithm that, given the message, public key and signature, either accepts or rejects the message's claim to authenticity. Two main properties are required: Correctness: Signatures produced by the signing algorithm with a private key pass the verification algorithm with the corresponding public key. Security (existential unforgeability under chosen-message attack, or EUF-CMA): It should be computationally infeasible to generate a valid signature for a party without knowing that party's private key. Formally, a digital signature scheme is a triple of probabilistic polynomial-time algorithms, (G, S, V), satisfying: G (key-generator) generates a public key (pk), and a corresponding private key (sk), on input 1n, where n is the security parameter. S (signing) returns a tag, t, on the inputs: the private key (sk), and a string (x). V (verifying) outputs accepted or rejected on the inputs: the public key (pk), a string (x), and a tag (t). Here 1n refers to a unary number in the formalism of computational complexity theory. For correctness, S and V must satisfy Figure 1: Digital signature compliance interface with secure document ...
Pr [(pk, sk) ← G(1n), V(pk, x, S(sk, x)) = accepted] = 1. A digital signature scheme is secure if for every non-uniform probabilistic polynomial time adversary A, Pr [(pk, sk) ← G(1n), (x, t) ← AS(sk, · )(pk, 1n), x ∉ Q, V(pk, x, t) = accepted] < negl(n), where AS(sk, · ) denotes that A has access to the oracle, S(sk, · ), Q denotes the set of the queries on S made by A, which knows the public key, pk, and the security parameter, n, and x ∉ Q denotes that the adversary may not directly query the string, x, on S.
One digital signature scheme (of many) is based on RSA. To create signature keys, generate an RSA key pair containing a modulus, N, that is the product of two random secret distinct large primes, along with integers, e and d, such that e d ≡ 1 (mod φ(N)), where φ is Euler's totient function. The signer's public key consists of N and e, and the signer's secret key contains d. Used directly, this type of signature scheme is vulnerable to key-only existential forgery attack. To create a forgery, the attacker picks a random signature σ and uses the verification procedure to determine the message, m, corresponding to that signature. In practice, however, this type of signature is not used directly, but rather, the message to be signed is first hashed to produce a short digest, that is then padded to larger width comparable to N, then signed with the reverse trapdoor function.
This forgery attack, then, only produces the padded hash function output that corresponds to σ, but not a message that leads to that value, which does not lead to an attack. In the random oracle model, hash-then-sign (an idealized version of that practice where hash and padding combined have close to N possible outputs), this form of signature is existentially unforgeable, even against a chosen-plaintext attack. There are several reasons to sign such a hash (or message digest) instead of the whole document.
For efficiency The signature will be much shorter and thus save time since hashing is generally much faster than signing in practice. For compatibility Messages are typically bit strings, but some signature schemes operate on other domains (such as, in the case of RSA, numbers modulo a composite number N). A hash function can be used to convert an arbitrary input into the proper format. For integrity Without the hash function, the text "to be signed" may have to be split (separated) in blocks small enough for the signature scheme to act on them directly. However, the receiver of the signed blocks is not able to recognize if all the blocks are present and in the appropriate order.
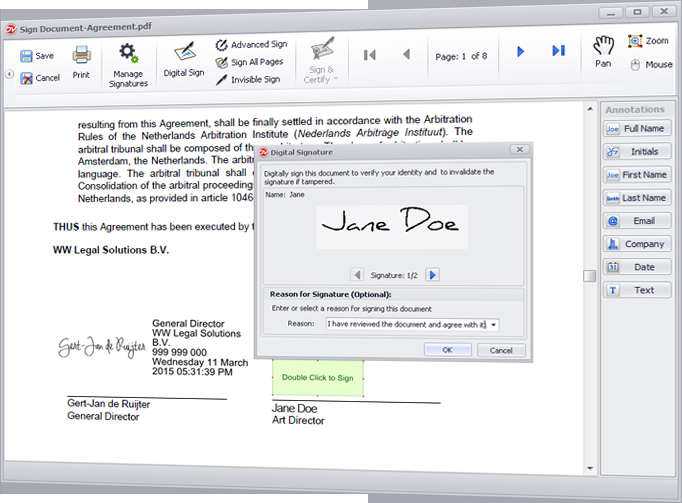
Figure 2: Digital Signatures and Validation Trust tool | Docsvault In a key-only attack, the attacker is only given the public verification key. In a known message attack, the attacker is given valid signatures for a variety of messages known by the attacker but not chosen by the attacker. In an adaptive chosen message attack, the attacker first learns signatures on arbitrary messages of the attacker's choice. They also describe a hierarchy of attack results: A total break results in the recovery of the signing key. A universal forgery attack results in the ability to forge signatures for any message. A selective forgery attack results in a signature on a message of the adversary's choice. An existential forgery merely results in some valid message/signature pair not already known to the adversary. The strongest notion of security, therefore, is security against existential forgery under an adaptive chosen message attack.
the user can only sign documents on that particular computer the security of the private key depends entirely on the security of the computer A more secure alternative is to store the private key on a smart card. Many smart cards are designed to be tamper-resistant (although some designs have been broken, notably by Ross Anderson and his students). In a typical digital signature implementation, the hash calculated from the document is sent to the smart card, whose CPU signs the hash using the stored private key of the user, and then returns the signed hash. Typically, a user must activate their smart card by entering a personal identification number or PIN code (thus providing two-factor authentication). It can be arranged that the private key never leaves the smart card, although this is not always implemented. If the smart card is stolen, the thief will still need the PIN code to generate a digital signature. This reduces the security of the scheme to that of the PIN system, although it still requires an attacker to possess the card. A mitigating factor is that private keys, if generated and stored on smart cards, are usually regarded as difficult to copy, and are assumed to exist in exactly one copy. Thus, the loss of the smart card may be detected by the owner and the corresponding certificate can be immediately revoked. Private keys that are protected by software only may be easier to copy, and such compromises are far more difficult to detect.
Technically speaking, a digital signature applies to a string of bits, whereas humans and applications "believe" that they sign the semantic interpretation of those bits. In order to be semantically interpreted, the bit string must be transformed into a form that is meaningful for humans and applications, and this is done through a combination of hardware and software based processes on a computer system. The problem is that the semantic interpretation of bits can change as a function of the processes used to transform the bits into semantic content. It is relatively easy to change the interpretation of a digital document by implementing changes on the computer system where the document is being processed. From a semantic perspective this creates uncertainty about what exactly has been signed. WYSIWYS (What You See Is What You Sign) means that the semantic interpretation of a signed message cannot be changed. In particular this also means that a message cannot contain hidden information that the signer is unaware of, and that can be revealed after the signature has been applied. WYSIWYS is a requirement for the validity of digital signatures, but this requirement is difficult to guarantee because of the increasing complexity of modern computer systems. The term WYSIWYS was coined by Peter Landrock and Torben Pedersen to describe some of the principles in delivering secure and legally binding digital signatures for Pan-European projects.
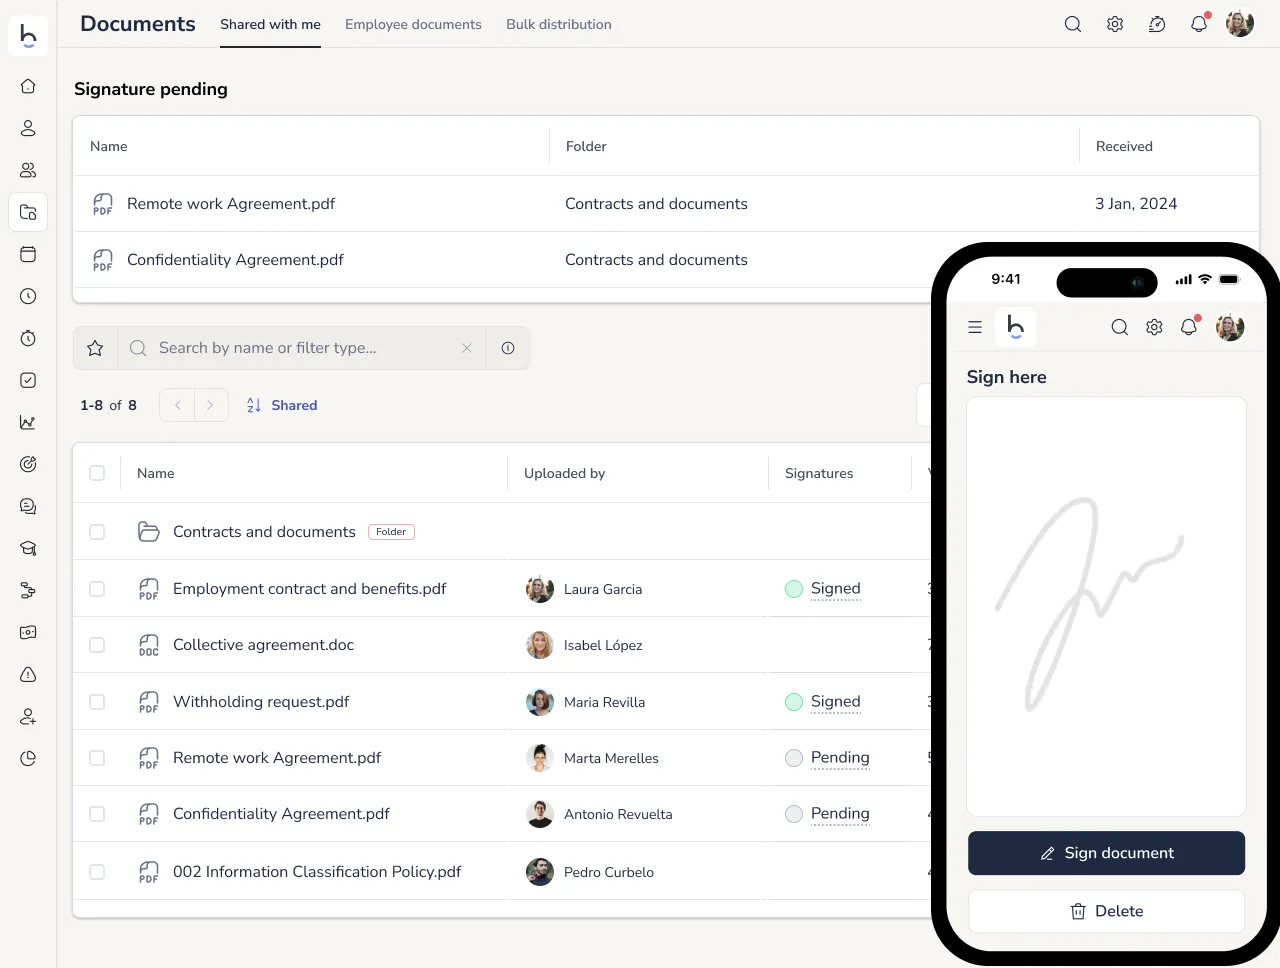
Figure 3: Digital Signature Software for Employment Contracts and HR Documents Most digital signature schemes share the following goals regardless of cryptographic theory or legal provision: Quality algorithms: Some public-key algorithms are known to be insecure, as practical attacks against them have been discovered.
Quality implementations: An implementation of a good algorithm (or protocol) with mistake(s) will not work. The private key must remain private: If the private key becomes known to any other party, that party can produce perfect digital signatures of anything. The public key owner must be verifiable: A public key associated with Bob actually came from Bob. This is commonly done using a public key infrastructure (PKI) and the public key↔user association is attested by the operator of the PKI (called a certificate authority). For 'open' PKIs in which anyone can request such an attestation (universally embodied in a cryptographically protected public key certificate), the possibility of mistaken attestation is non-trivial. Commercial PKI operators have suffered several publicly known problems. Such mistakes could lead to falsely signed, and thus wrongly attributed, documents. 'Closed' PKI systems are more expensive, but less easily subverted in this way. Only if all of these conditions are met will a digital signature actually be any evidence of who sent the message, and therefore of their assent to its contents. Legal enactment cannot change this reality of the existing engineering possibilities, though some such have not reflected this actuality. Legislatures, being importuned by businesses expecting to profit from operating a PKI, or by the technological avant-garde advocating new solutions to old problems, have enacted statutes and/or regulations in many jurisdictions authorizing, endorsing, encouraging, or permitting digital signatures and providing for (or limiting) their legal effect. The first appears to have been in Utah in the United States, followed closely by the states Massachusetts and California. Other countries have also passed statutes or issued regulations in this area as well and the UN has had an active model law project for some time. These enactments (or proposed enactments) vary from place to place, have typically embodied expectations at variance (optimistically or pessimistically) with the state of the underlying cryptographic engineering, and have had the net effect of confusing potential users and specifiers, nearly all of whom are not cryptographically knowledgeable. Adoption of technical standards for digital signatures have lagged behind much of the legislation, delaying a more or less unified engineering position on interoperability, algorithm choice, key lengths, and so on what the engineering is attempting to provide.
Some industries have established common interoperability standards for the use of digital signatures between members of the industry and with regulators. These include the Automotive Network Exchange for the automobile industry and the SAFE-BioPharma Association for the healthcare industry. 21 CFR 11 X.509 Advanced electronic signature Blind signature Detached signature Public key certificate Digital signature in Estonia Electronic lab notebook Electronic signature Electronic signatures and law eSign (India) GNU Privacy Guard Public key infrastructure Public key fingerprint Server-based signatures Probabilistic signature scheme The Digital Signature Algorithm (DSA) is a public-key cryptosystem and Federal Information Processing Standard for digital signatures, based on the mathematical concept of modular exponentiation and the discrete logarithm problem. In a digital signature system, there is a keypair involved, consisting of a private and a public key. In this system a signing entity that declared their public key can generate a signature using their private key, and a verifier can assert the source if it verifies the signature correctly using the declared public key. DSA is a variant of the Schnorr and ElGamal signature schemes. The National Institute of Standards and Technology (NIST) proposed DSA for use in their Digital Signature Standard (DSS) in 1991, and adopted it as FIPS 186 in 1994. Five revisions to the initial specification have been released. The last standard, however, removed NIST's approval for DSA signature generation.
Choose an integer x {\displaystyle x} randomly from { 1 … q − 1 } {\displaystyle \{1\ldots q-1\}} . Compute y := g x mod p {\displaystyle y:=g^{x}\mod p} . x {\displaystyle x} is the private key and y {\displaystyle y} is the public key. Choose an integer k {\displaystyle k} randomly from { 1 … q − 1 } {\displaystyle \{1\ldots q-1\}} Compute r := ( g k mod p ) mod q {\displaystyle r:=\left(g^{k}{\bmod {\,}}p\right){\bmod {\,}}q} . In the unlikely case that r = 0 {\displaystyle r=0} , start again with a different random k {\displaystyle k} . Compute s := ( k − 1 ( H ( m ) + x r ) ) mod q {\displaystyle s:=\left(k^{-1}\left(H(m)+xr\right)\right){\bmod {\,}}q} . In the unlikely case that s = 0 {\displaystyle s=0} , start again with a different random k {\displaystyle k} . The signature is ( r , s ) {\displaystyle \left(r,s\right)} The calculation of k {\displaystyle k} and r {\displaystyle r} amounts to creating a new per-message key. The modular exponentiation in computing r {\displaystyle r} is the most computationally expensive part of the signing operation, but it may be computed before the message is known. Calculating the modular inverse k − 1 mod q {\displaystyle k^{-1}{\bmod {\,}}q} is the second most expensive part, and it may also be computed before the message is known. It may be computed using the extended Euclidean algorithm or using Fermat's little theorem as k q − 2 mod q {\displaystyle k^{q-2}{\bmod {\,}}q} .
Verify that 0 < r < q {\displaystyle 0
s = k − 1 ( H ( m ) + x r ) mod q {\displaystyle s=k^{-1}(H(m)+xr){\bmod {\,}}q} k ≡ H ( m ) s − 1 + x r s − 1 ≡ H ( m ) w + x r w ( mod q ) {\displaystyle {\begin{aligned}k&\equiv H(m)s^{-1}+xrs^{-1}\\&\equiv H(m)w+xrw{\pmod {q}}\end{aligned}}} Since g {\displaystyle g} has order q {\displaystyle q} we have g k ≡ g H ( m ) w g x r w ≡ g H ( m ) w y r w ≡ g u 1 y u 2 ( mod p ) {\displaystyle {\begin{aligned}g^{k}&\equiv g^{H(m)w}g^{xrw}\\&\equiv g^{H(m)w}y^{rw}\\&\equiv g^{u_{1}}y^{u_{2}}{\pmod {p}}\end{aligned}}} r = ( g k mod p ) mod q = ( g u 1 y u 2 mod p ) mod q = v {\displaystyle {\begin{aligned}r&=(g^{k}{\bmod {\,}}p){\bmod {\,}}q\\&=(g^{u_{1}}y^{u_{2}}{\bmod {\,}}p){\bmod {\,}}q\\&=v\end{aligned}}} 2. System Architecture & Core Working Principles A signature (; from Latin: signare, "to sign") is a depiction of someone's name, nickname, or even a simple "X" or other mark that a person writes on documents as a proof of identity and intent. Signatures are often, but not always, handwritten or stylized. The writer of a signature is a signatory or signer. A signature may be confused with an autograph, which is chiefly an artistic signature. This can lead to confusion when people have both an autograph and signature and as such some people in the public eye keep their signatures private whilst fully publishing their autograph.
The traditional function of a signature is to permanently affix to a document a person's uniquely personal, undeniable self-identification as physical evidence of that person's personal witness and certification of the content of all, or a specified part, of the document. For example, the role of a signature in many consumer contracts is not solely to provide evidence of the identity of the contracting party, but also to provide evidence of deliberation and informed consent. In the United States, signatures encompass marks and actions of all sorts that are indicative of identity and intent. The legal rule is that unless a statute specifically prescribes a particular method of making a signature it may be made in any number of ways. These include by a mechanical or rubber stamp facsimile. A signature may be made by the purported signatory; alternatively someone else duly authorized by the signatory, acting in their presence and at their direction, may make the signature. Many individuals have much more fanciful signatures than their normal cursive writing, including elaborate ascenders, descenders and exotic flourishes, much as one would find in calligraphic writing. As an example, the final "k" in John Hancock's famous signature on the US Declaration of Independence loops back to underline his name. This kind of flourish is also known as a paraph, a French term meaning flourish, initial or signature. The paraph is used in graphology analyses. Several cultures whose languages use writing systems other than alphabets do not share the Western notion of signatures per se: the "signing" of one's name results in a written product no different from the result of "writing" one's name in the standard way. For these languages, to write or to sign involves the same written characters.
In some jurisdictions, an illiterate signatory can make a "mark" (often an "X" but occasionally a personalized symbol) on legal documents, so long as the document is countersigned by a literate witness. Courts in England and Wales are generally likely to recognise such a mark as legally valid. In some countries, illiterate people place a thumbprint on legal documents in lieu of a written signature.
Special signature machines, called autopens, are capable of automatically reproducing an individual's signature. These are typically used by people required to sign a lot of printed matter, such as celebrities, heads of state or CEOs. More recently, Members of Congress in the United States have begun having their signature made into a TrueType font file. This allows staff members in the Congressman's office to easily reproduce it on correspondence, legislation, and official documents. In the East Asian languages of Chinese, Japanese, and Korean, people traditionally use stamp-like objects known as name-seals with the name carved in tensho script (seal script) in lieu of a handwritten signature.
In e-mail and newsgroup usage, another type of signature exists which is independent of one's language. Users can set one or more lines of custom text known as a signature block to be automatically appended to their messages. This text usually includes a name, contact information, and sometimes quotations and ASCII art. A shortened form of a signature block, only including one's name, often with some distinguishing prefix, can be used to simply indicate the end of a post or response.
Some web sites also allow graphics to be used. Note, however, that this type of signature is not related to electronic signatures or digital signatures, which are more technical in nature and not directly understandable by humans. Handwriting experts say "it is extremely difficult for anyone to be able to figure out if a signature or other very limited writing sample has been forged." High volume review of signatures, to decide if a signature is true or forged, occurs when election offices decide whether to accept absentee ballots arriving from voters, and possibly when banks decide whether to pay checks. The highest error rates in signature verification are found with lay people, higher than for computers, which in turn make more errors than experts. Genuine signatures can exhibit substantial variation because signature production is a neuromuscular behavior influenced by factors such as writing conditions and the circumstances of execution. Consequently, forensic examination generally considers a range of variation across multiple known signatures rather than expecting genuine signatures to be identical. There have been concerns that signature reviews improperly reject ballots from young and minority voters at higher rates than others, with no or limited ability of voters to appeal the rejection. When errors are made with bank checks, the payer can ask the bank for corrections. In 2018, a fifth of adults in the United Kingdom said they sign so rarely they have no consistent signature, including 21% of people 18-24 and 16% of people over age 55. 55% of UK adults said they rarely sign anything.
Researchers have published error rates for computerized signature verification. They compare different systems on a common database of true and false signatures. The best system falsely rejects 10% of true signatures, while it accepts 10% of forgeries. Another system has error rates on both of 14%, and the third-best has error rates of 17%. It is possible to be less stringent and reject fewer true signatures, at the cost of also rejecting fewer forgeries. Computer algorithms:look for a certain number of points of similarity between the compared signatures ... a wide range of algorithms and standards, each particular to that machine's manufacturer, are used to verify signatures. In addition, counties have discretion in managing the settings and implementing manufacturers' guidelines ... there are no statewide standards for automatic signature verification ... most counties do not have a publicly available, written explanation of the signature verification criteria and processes they use. In an experiment, experts rejected 5% of true signatures and 71% of forgeries. They were doubtful about another 57% of true signatures and 27% of forgeries. If computer verification is adjusted to reflect what experts are sure about, it will wrongly reject 5% of true signatures and wrongly accept 29% of forgeries. If computers were adjusted more strictly, rejecting all signatures which experts have doubts about, the computers would set aside 62% of true signatures, and still wrongly accept 2% of forgeries. Lay people made more mistakes and were doubtful less often, though the study does not report whether their mistakes were to accept more forgeries or reject more true signatures. Voters with short names are at a disadvantage, since experts make more mistakes on signatures with fewer "turning points and intersections." Participants in this study had 10 true signatures to compare to, which is more than most postal ballot verifications have. A more recent study for the US Department of Justice confirms the probabilistic nature of signature verification, though it does not provide numbers.
The signature on a painting or other work of art is an important factor in assessing provenance. Fake signatures are sometimes added to enhance the value of a painting, or are added to a fake painting to support its authenticity. A notorious case was the signature of Johannes Vermeer on the fake "Supper at Emmaus" made by the art forger Han van Meegeren. However, the fact that painters' signatures often vary over time (particularly in the modern and contemporary periods) might complicate the issue. The signatures of some painters take on an artistic form that may be of less value in determining forgeries. If a painting is abstract or ambiguous, the signature may be the only clue to determine which side is up.
Autograph club Autograph Collector Magazine Biometric signature as form of the electronic signature Builder's signature Initials Images of signatures manu propria (m.p.) Memorial to the 56 Signers of the Declaration of Independence, includes depicted signatures Monogram Pawtograph, an animal's paw print Round robin, a signed document where the signatures are arranged in a circle Royal sign-manual Shakespeare's handwriting Signum manus Tughra Huaya Why Do We Sign For Things? A Rabbi, A Lawyer And A MasterCard Exec Explain NPR / Planet Money History of signatures at Slate What is Signature? Signature of 100 famous people (video on YouTube) Digital signatures are a fundamental building block of modern cryptography. We often use digital signatures without realizing it in our day to day lives. For example, when you visit a website, your browser verifies the authenticity of the website using a digital signature. In this article, we’ll explore how digital signature works, how to generate and verify digital signatures, and how to use digital signatures to sign and verify files.
My original motivation to write this article is to develop some fundamental understanding of digital signatures for the embedded systems and system engineering community. I have often seen that digital signatures are seen as a mystery by many developers. I hope that this article will help demystify digital signatures and help developers understand how digital signatures work and how to use them in their projects.
While there is an abundance of digital signature usage in the cryptocurrency world, I will not be covering that in this article. I have built a web-tool to play around with digital signatures at https://vppillai.github.io/cryptoScript/FileSigner.html . You can use this tool to generate and verify digital signatures for files. The tool is written in Javascript and uses the WebCrypto API to generate and verify digital signatures. The source code for the tool and a few other useful crypto scripts are available at https://github.com/vppillai/cryptoScript We will cover the details of the tool in the later sections of this article. For now, let’s start with the basics.
I would recommend that you also read my articles on Introduction to digital certificates and Understanding X.509 Certificate Structure before continuing with this article if you are new to cryptography. A digital signature is a mathematical scheme for verifying the authenticity of digital messages or documents. A valid digital signature gives a recipient reason to believe that the message was created by a known sender, and that the message was not altered in transit. Digital signatures are commonly used for software distribution, financial transactions, and in other cases where it is important to detect forgery or tampering.
``bash DzjGzKR5LZgAdU9ObP/bt9LFf5/+YtlTHJNtWZH8kAOQE5cTW0lE/Q9jQcdScVsNuvktdhfaBZhowgoY08S8Fw== To understand how a digital signature is generated and how its useful in verifying the authenticity of data, we need to understand the underlying cryptographic primitives that are used to generate a digital signature. Most importantly, we need to understand the concept of a cryptographic hash function .
A cryptographic hash function is a mathematical algorithm that maps data of arbitrary size to a bit string of a fixed size (a hash) and is designed to be a one-way function, that is, a function which is non-feasible to invert. The only way to recreate the input data from an ideal cryptographic hash function’s output is to attempt a brute-force search of possible inputs to see if they produce a match, or use a rainbow table of matched hashes. (rainbow tables are pre-computed lookup tables where the hash of every possible text input combination is stored. This allows for quick lookup of data given the hash).
Since the hashing function converts an input of arbitrary size to a fixed size output, it is often called a Digest function. The length of the hash determines how easy or difficult it is to find a hash collision for a given input. The longer the hash, the more difficult it is to find a collision. For example, the SHA-1 hash function produces a 160-bit hash. This means that there are 2^160 possible hashes. This is a very large number. If you were to try to find a collision for a given input, you would have to try 2^160 different inputs to find a collision. This is not feasible. However, if the hash function produces a 32-bit hash, then there are only 2^32 possible hashes. This is a much smaller number. If you were to try to find a collision for a given input, you would only have to try 2^32 different inputs to find a collision. This is feasible given the computational capability we have today.
A cryptographic hash function is different from a regular hash function in that it has to satisfy the following properties: Simply put, a digital signature is an “Encrypted hash” of a message. This implies that an encryption algorithm is involved in the process of creating a digital signature. However, the encryption algorithm used to create a digital signature is different from the encryption algorithm used to encrypt data. The encryption algorithm used to create a digital signature is called a Signing Algorithm . The encryption algorithm used to encrypt data is called an Encryption Algorithm . The signing algorithm is a part of a larger class of algorithms called Public Key Cryptography algorithms.
We will not go into the details of key generation and the mathematics behind the ECDSA algorithm. We will focus on the steps involved in generating a digital signature. Note: These steps provide a simplified overview of the ECDSA process. In practice, there may be additional considerations such as encoding, padding, and other security measures that need to be taken into account for proper implementation.
A private key and a corresponding public key. The private key ( signing key ) is kept secret, while the public key ( verification key ) can be shared with others in order to verify the signature. The resulting signature is a pair of 32 byte values (r, s) . The signature is 64 bytes in total. Note that the signature is also dependent on the hash algorithm used. typically sha256 is used with ECDSA .
My web-tool available here can be used to generate a signature using the ECDSA algorithm. The tool also provides the option to generate a key pair and verify a signature. You can also try this out using the openssl command line tool. With the commands below, you can generate a key pair, sign a message, and view the signature. note the hashing algorithm used is sha256 . Openssl lets you use any of the following hashing algorithm selectors here : -sha1 , -sha224 , -sha256 , -sha3-224 , -sha3-256 , -sha3-384 , -sha3-512 , -sha384 , -sha512 , -sha512-224 , -sha512-256 , -shake128 , -shake256 .
The signature is generated in the DER format. The hexdump command can be used to view the contents of the signature file. You would notice that the output is larger than 64 bytes (32 bytes for r and 32 bytes for s ). This is because the signature is encoded in the DER format. To see the actual r and s values, you can use the asn1parse command: Its interesting to note that the signature changes every time you sign the same message. This is because the nonce is chosen randomly every time. This is a security feature to prevent the private key from being exposed. You can opt out of this feature by using a deterministic nonce. An example is Deterministic ECDSA RFC 6979 . This is not supported by openssl yet.
3. Software Implementation, Frameworks & Protocols Following the steps in the signature generation section, you can verify the signature using the openssl command line tool: Any change to the message will result in a different signature, and the verification will fail. The digital signature algorithms do not specify how the generated digital signatures can be clubbed with the original data. This is left to the implementer. The simplest form of transmitting the signature is one where the r and s values are concatenated together. This is called the raw format. The resulting signature is 64 bytes in length. There is no reference to the signer or the message that was signed. This is not a recommended format for transmitting signatures unless it is part of a larger, well defined protocol.
DER formatted signatures as defined in RFC 3279 are just a step up from the raw format. The DER format is a binary format that is not human readable. The base64 encoding of the DER format is 88 bytes in length and can be appended to the original message and transmitted over the network. The receiver can then extract the signature and verify it. Unlike other PEM format headers specified in specifications like RFC 7468 , there is no header defined to store just the base64 encoded signature since the signature alone cannot be used without additional data about the signer or the message.
However, in all these methods standalone signature transmission is possible since the process of signature verification recomputes the hash of the message and compares it with the hash in the signature. Note that the key used to verify the signature must be stored securely in a root of trust. CMS, also commonly referred to as PKCS#7 (Public Key Cryptography Standards #7), is a standard syntax for securely exchanging signed or encrypted messages. The ECDSA digital signature is typically included as part of a SignedData structure, along with the original message, the signer’s certificate, and any necessary cryptographic information. CMS allows for more advanced features like including multiple signers, certificates, and timestamps. (Dat ain CMS is often referred to as CMS container or PKCS#7 container) PKCS#7 has an embedded mode where the original message is included in the signature. It also has a detached mode where the original message is not included in the signature. The detached mode is typically used when the original message is too large to be included in the signature or is wrapped in another data format like PDF already.
The openssl command line tool can be used to generate a CMS container. However, a certificate is required to hold the public key of the signer. The certificate can be self-signed or issued by a certificate authority. An ECC certificate can be generated using the openssl command line tool as follows: In this case, the pkcs7-data is empty. However, if you use the -nodetach flag when signing, the pkcs7-data will contain the data that was signed.
The signer information is packaged along with the signature. The signer information includes the signer’s certificate, which contains the signer’s public key. The recipient can use the signer’s public key to verify the signature. The recipient can also use the signer’s certificate to verify the signer’s identity. typically, (unlike this example of a self signed certificate), the signer’s certificate is signed by a trusted certificate authority (CA), which means that the recipient can verify the signer’s identity using its root of trust.
Note that we are passing the CA certificate to the -CAfile flag. This is because the signer’s certificate is self-signed, so we need to tell openssl to trust it. If the signer’s certificate was signed by a trusted CA, we would not need to pass the CA certificate to the -CAfile flag. GPG (GNU Privacy Guard) is a widely-used software tool that provides encryption and cryptographic functionality, including the ability to generate and verify digital signatures. GPG is an implementation of the OpenPGP (Pretty Good Privacy) standard, which is a widely-adopted protocol for secure communication and data encryption.
GPG uses the standard algorithms like RSA and ECDSA. But adds some custom layers on top of it. The overall steps to generate a digital signature are very similar and are as follows: To create a digital signature, the owner of the private key uses GPG to sign a document or a message, generating a unique cryptographic hash of the data and encrypting it with the private key. This creates a digital signature that can be attached to the document.
To verify the digital signature, recipients of the signed document can use GPG and the signer’s public key. GPG performs the necessary cryptographic operations to validate the digital signature and confirm the integrity and authenticity of the document. If the verification process is successful, it means that the document has not been tampered with and was indeed signed by the owner of the corresponding private key.
GPG provides a command-line interface (CLI) as well as integration with various email clients and other software applications. It is widely used for secure communication, file encryption, and digital signatures in both personal and enterprise contexts. While importing an existing PEM format key into GPG is possible, it need some amount of key manipulation and is outside the scope of this article. Instead, we will generate a new key pair using GPG. The following command will generate a new key pair: The --expert flag is used to enter the expert mode, which allows us to specify the key type and size.
I generated a P-256 ECC key pair. To sign a message, we can use the following command: This generates a detached signature file called content.txt.asc . If the --armor option is not passed, the signature will be binary. We can also use the gpg command to encrypt and decrypt files. The following command will encrypt the file content.txt using the public key of the recipient: To decrypt the file, we can use the following command. In a real-world scenario, the recipient would use their private key to decrypt the file. Contents of the file cannot be decrypted without the private key.
GPG key servers are used to share public keys. The following command can be used to upload the public key to a key server: X.509 is a standard format for public key certificates. It is used in many applications, including TLS/SSL, email, and code signing. X.509 certificates are used to authenticate the identity of the communicating parties and ensure the integrity of the exchanged messages.
When a certificate is requested from a certificate authority (CA), the CA verifies the identity of the requester and issues a certificate. The certificate contains the requester’s public key and is digitally signed by the CA. The CA’s signature is created using the CA’s private key. The certificate also contains the CA’s public key, which is used to verify the CA’s signature, along with the root of trust present in the client’s system.
you can see the signature algorithm used in the certificate and the signature using the command: In the TLS 1.2 protocol, digital signatures are primarily used for authentication and integrity verification of data exchanged between the client and server. The key areas where digital signatures are used in TLS 1.2 are: Handshake Protocol: to authenticate the identities of the communicating parties and ensure the integrity of the exchanged messages.
Server Authentication: When the server presents its digital certificate to the client during the handshake, it includes a digital signature created using the private key of the certificate authority (CA) that issued the certificate. The client verifies this signature using the corresponding CA’s public key to ensure the authenticity of the server’s certificate. Client Authentication (optional): In case of mutual authentication, the server may request the client to present its digital certificate. Similar to server authentication, the client’s certificate includes a digital signature from a trusted CA, and the server verifies it to authenticate the client.
4. Practical Deployment, Analysis & Case Studies Key Exchange: The key exchange process in TLS 1.2 ensures that the client and server can establish a shared secret key to encrypt and decrypt data during the secure communication. Digital signatures are used to ensure the integrity of the key exchange process.
Server Key Exchange: In certain cases, the server may use a digital signature to sign the parameters used in the key exchange, ensuring that they have not been tampered with during transmission. An example of this is the Diffie-Hellman key exchange method, where the server signs the Diffie-Hellman parameters using its private key. Client Key Exchange: The client may also employ digital signatures during the key exchange, depending on the key exchange method used. For example, in the Diffie-Hellman key exchange method, the client signs the Diffie-Hellman parameters using its private key.
Certificate Revocation: TLS 1.2 supports checking the revocation status of certificates to ensure they have not been revoked or invalidated. Digital signatures are utilized in the certificate revocation process, where revocation information is signed by the CA or certificate issuer. When a client connects to an SSH server for the first time, the server presents its host key. The client verifies the authenticity of the host key by checking its digital signature, which is typically performed using a public key infrastructure (PKI) scheme.
This process involves the following the client sends a challenge to the server, which signs the challenge using its private key and sends the digital signature back to the client. The client verifies the signature using the server’s public key to authenticate the server. This is defined in the SSH Transport Layer Protocol. If an SSH, users initiates auth using public key cryptography. The challenge response process is similar to host key authentication, but the client and server roles are reversed. The client generates a key pair (public key and private key) and adds the public key to the server’s authorized keys file. When the user attempts to connect, the server sends a challenge to the client, which signs the challenge using its private key and sends the digital signature back to the server. The server verifies the signature using the user’s public key to authenticate the user.
SSH also supports certificate-based authentication. In this case, users have certificates issued by a trusted certificate authority (CA). The certificates contain public keys and digital signatures from the CA. When a user connects to the server, the client sends its certificate to the server. The server verifies the certificate’s digital signature with the CA’s public key to authenticate the user. This also includes the challenge response process to prove access to the private key.
The protocol commonly used for implementing digital signatures in emails is the Secure/Multipurpose Internet Mail Extensions (S/MIME). It operates within the protocol the framework of the MIME standard, which allows the inclusion of non-textual attachments, such as images or documents, in email messages. S/MIME relies on X.509 digital certificates issued by trusted Certificate Authorities (CAs) and relies on PKI to verify the authenticity of the sender. The sender’s email client uses the private key of the sender’s digital certificate to sign the email message. The recipient’s email client uses the sender’s public key to verify the signature and authenticate the sender. The recipient’s email client also uses the sender’s public key to encrypt the email message, ensuring confidentiality.
The sender and the receiver have to exchange their public key with each other. This process happens automatically when the sender and recipient exchange emails for the first time with most of the modern email clients. GPG provides a similar functionality for email signing and encryption. It uses a web of trust model, where users can sign each other’s public keys to verify their authenticity. GPG also supports the use of X.509 certificates for email signing and encryption.
ARC (Authenticated Received Chain) and DKIM (DomainKeys Identified Mail) aim at protecting emails in transit: ARC is a protocol designed to address the challenges of email authentication when messages pass through intermediaries, such as mailing lists or forwarding services. These intermediaries can modify the message or its headers, potentially breaking the existing email authentication mechanisms like SPF, DKIM, and DMARC.
ARC provides a mechanism to create a chain of authentication results as the email passes through these intermediaries. It adds ARC headers to the message, containing cryptographic seals and signatures that verify the integrity of the email’s original authentication results. When an email recipient receives a message with ARC headers, they can use these headers to validate the authenticity and integrity of the authentication results. By examining the ARC-Seal and ARC-Message-Signature, the recipient can ensure that the email’s authentication results have not been tampered with during transit.
DKIM is an email authentication method that allows the receiver to verify the authenticity of an email’s domain and ensure that the message hasn’t been altered during transit. When an email is sent using DKIM, the sending domain adds a digital signature to the email headers using asymmetric cryptography. The signature is generated by the sending domain’s private key, and the recipient can verify it using the domain’s public key published in DNS (Domain Name System) records.
The DKIM-Signature header contains information such as the signing algorithm, domain, selector, timestamp, and a hash value of selected headers. By recalculating the hash and verifying the signature with the public key, the recipient can confirm that the email has indeed been sent by the claimed domain and hasn’t been modified. DKIM helps combat email spoofing and provides a level of trust in the authenticity of the email’s source. It is one of the components used by email providers to determine the email’s reputation and whether it should be delivered to the recipient’s inbox or treated as suspicious or spam.
Both ARC and DKIM enhance email authentication and integrity. While DKIM focuses on verifying the domain and message integrity, ARC focuses on preserving the authentication results as the email passes through intermediaries. Together, they contribute to a more secure email ecosystem by preventing spoofing, tampering, and enhancing trust in email communication. Git can be configured to digital signatures to verify the authenticity of commits and tags. Git uses the GPG tool to generate and manage the keys. The following commands can be used to configure Git to use GPG: A signed commit or tag can be verified using the git verify-commit and git verify-tag commands: While source signing as we saw in the Git section is technically a form of code signing, the term code signing is typically used to refer to the signing of compiled code. Code signing is used to verify the authenticity of software and to ensure that the software has not been tampered with. Code signing is commonly used for software distribution, such as software updates, and for mobile apps. Code signing is also used for driver signing in Windows and for kernel modules in Linux.
There is no standard way to store a signature as part of a binary like format like ELF. The signature is typically stored in a separate file, which is then distributed along with the binary. The signature file can be in any format, such as CMS, PGP, or XML. The signature file can also be stored in a separate location, such as a database, and referenced by the binary. The Linux kernel handles signed modules differently. While the details are available in the Linux documentation , the highlights are outlined below.
JSON Web Token (JWT) is an open standard for securely transmitting information between parties as a JSON object. The information can be verified and trusted because it is digitally signed. JWTs can be signed using a secret (with the HMAC algorithm) or a public/private key pair using RSA or ECDSA. You can read more about JWTs in detail in my previous article on the topic .
By system engineering, I refer to the low level software that is responsible for booting the system and loading the operating system. secure system boot and secure software update are two important aspects of system engineering. Secure boot ensures that the system boots only authorized software. Secure software update ensures that the software is not tampered with during the update process. Image signing is an important aspect of both secure boot and secure software update.
The topics in the following sub sections require a detailed explanation. I will cover them in detail in future posts. For now, I will provide a brief overview of each topic. UEFI stands for Unified Extensible Firmware Interface. UEFI is a specification that defines a software interface between an operating system and platform firmware. UEFI is a replacement for the legacy BIOS firmware interface. UEFI is a very broad topic that requires its own post. So, in order to avoid mis-representation or over simplification of data, I will just state that when Secure Boot is enabled, the UEFI firmware checks the digital signatures of the bootloader and any subsequent components before allowing them to execute. I will later write a detailed post on UEFI and Secure Boot, going into the details of the signature header, signing and key exchange process etc.
Das U-Boot (Universal Bootloader) is an open source, primary boot loader used in embedded devices to boot the Linux kernel, among other things. U-Boot provides a mechanism known as Verified boot to verify the integrity of the boot image. The boot image is a FIT image that contains the kernel, device tree, and other components. The boot image is signed using a private key. The public key is stored in the U-Boot environment. The signature is verified by U-Boot before booting the image.
U-Boot Flattened Image Tree (FIT) is a very flexible, structured container format which supports multiple kernel images, device trees, ram disks, etc. It includes hashes to verify images. So adding signatures to it is straight forward. 5. Performance Evaluation & Extended Technical Observations U-Boot can be configured to use a variety of signature formats, such as PKCS7, CMS, and raw signatures. The signature is stored in the FIT image itself. The signature is verified by U-Boot before booting the image. U-Boot can also be configured to use a TPM to store the public key. The TPM can be used to verify the signature.
GRUB (GRand Unified Bootloader) is a popular bootloader used in many Linux-based operating systems. Starting with version 2.02, GRUB introduced support for digital signatures to ensure the authenticity and integrity of its configuration files and executable modules. GRUB Configuration File (grub.cfg): The main configuration file for GRUB, which specifies the boot options and configuration settings. The configuration file can be signed using digital signatures to prevent unauthorized modifications.
Executable Modules: GRUB can load and execute various modules during the boot process, such as filesystem drivers or cryptographic libraries. These modules can also be signed to ensure their integrity and authenticity. Signature Verification: During the boot process, GRUB verifies the digital signatures of its configuration file and executable modules to ensure they haven’t been tampered with or modified by unauthorized sources. The signatures are verified using the corresponding public keys.
The specific signature format used by GRUB is based on the GNU gpg (GNU Privacy Guard) format. GRUB utilizes the GPG toolchain, including GPG keys and the gpg utility, for creating and verifying the digital signatures. The process generally involves signing the GRUB configuration file and modules using a private key, and the corresponding public key is embedded within the GRUB bootloader or stored in a secure location accessible by GRUB. During the boot process, GRUB verifies the digital signatures using the embedded or trusted public key.
The exact steps and configuration options for setting up and managing digital signatures in GRUB can vary depending on the specific version and distribution of GRUB being used. It’s important to consult the GRUB documentation and distribution-specific guides for detailed instructions on generating keys, signing files, and configuring GRUB to perform signature verification.
Android Verified Boot (AVB) is a security feature implemented in Android devices to ensure the integrity and authenticity of the boot process. AVB utilizes digital signatures to verify the integrity of boot components, including the bootloader, kernel, and device tree. Boot Image Signatures: Android devices use a verified boot process where each boot image (bootloader, kernel, and device tree) is digitally signed. The digital signature is generated using an asymmetric cryptography algorithm, such as RSA, and is based on a private key held by the device manufacturer or trusted entity.
Signature Verification: During the boot process, the bootloader verifies the digital signatures of the boot images using the corresponding public key. If the signatures are valid and match the computed hash of the boot images, the boot process continues. If the signatures are invalid or the hashes do not match, the bootloader will not proceed, indicating a potential tampering or compromise.
Chain of Trust: AVB establishes a chain of trust by ensuring that each subsequent boot component is verified using its own digital signature. This means that the bootloader verifies the kernel, and the kernel verifies the device tree, ensuring the integrity of each stage. Key Management: The public key used for verifying the boot image signatures is stored in the device’s trusted hardware, such as a Trusted Execution Environment (TEE), or in a read-only memory location that is tamper-resistant. This ensures that only authorized parties can update the boot components and corresponding digital signatures.
Updates and Rollback Protection: When updating the firmware or boot images, AVB enforces version checks and prevents downgrades to older, potentially vulnerable versions. It ensures that the updated boot images are signed with a newer version of the digital signature. The exact implementation of Android Verified Boot, including the signature formats and key management mechanisms, can vary across different device manufacturers and Android versions. However, the underlying principle of using digital signatures to verify the integrity and authenticity of boot components remains consistent.
Linux IMA (Integrity Measurement Architecture) and EVM (Extended Verification Module) are security features in the Linux kernel that provide mechanisms for measuring and verifying the integrity of files and data on a Linux system. Here’s a brief overview of IMA and EVM: Together, IMA and EVM provide a framework for enforcing and verifying the integrity and authenticity of files and data on a Linux system. They are often used in security-sensitive environments where ensuring the integrity of system components and detecting unauthorized changes is crucial.
It’s important to note that the specific implementation and configuration of IMA and EVM may vary across Linux distributions and kernel versions. Detailed documentation and configuration options can be found in the Linux kernel source tree and the documentation provided by the specific distribution or security frameworks built on top of IMA and EVM. There are so many more places and ways to use digital signatures. This is just a small sample of the many ways digital signatures are used in the real world. Hopefully this gives you a better understanding of how digital signatures are used in practice. Its important to note that the use of digital signatures in any system is only as good as the system design that can store Signer Public Keys in a tamper resistant way. If the Signer Public Keys can be tampered with, then the entire system is compromised.
From RTL written by AI agents to a physical die on silicon - notes from an end-to-end tapeout of a VGA bouncing-text demo using TinyTapeout, the IHP 130nm PD... Passbook: Architecting a Zero-Cost Serverless Kids Allowance Tracker and Delegating the Build to AI Agents My notes on building a serverless allowance tracker for my 10-year-old; where I owned the architecture and the constraints, and an army of AI agents did most...
I thought building a RISC-V processor with Chipyard would be straightforward - clone, build, run. Instead, I spent days debugging a halt failure that took me... My notes from building a scalable and production-ready infrastructure in AWS. This post covers the basics of setting up a load-balanced infrastructure using ...
Digital signatures have become a cornerstone in digital-first environments—be it verifying the authenticity of a PDF, ensuring software packages are uncompromised, or securing email communications. Understanding how to verify digital signature accurately is critical to maintaining data integrity, preventing fraud, and ensuring compliance with security protocols across organizations.
This comprehensive guide walks you through the entire process of signature verification. Whether you are an IT administrator, business user, or software developer, this blog provides step-by-step methods, tools, and best practices tailored to both technical and non-technical audiences. We also introduce how platforms like Certinal can streamline digital verification workflows.
A digital signature is a mathematical technique used to validate the authenticity and integrity of a digital message or document. Unlike handwritten signatures, digital counterparts use encryption protocols and digital certificates issued by trusted Certificate Authorities (CAs). When a document is signed, the hash of its content is encrypted using the sender’s private key . The recipient verifies it by decrypting the signature using the sender’s public key and ensures the contents match the original hash. If they do, the document is verified as untampered and authentic.
Digital signature verification is not just a technical step—it’s a trust-building process. It ensures: Organizations rely on this for everything from onboarding new clients and sharing financial reports to submitting government filings and sealing software distributions. There are multiple ways to verify a digital signature, depending on the context—PDF files, emails, software, or code. Below are the most commonly used methods, complete with tools and step-by-step instructions.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Digital%20signature • https://en.wikipedia.org/wiki/Digital%20Signature%20Algorithm • https://en.wikipedia.org/wiki/Signature • https://embeddedinn.com/articles/tutorial/Demystifying-Digital-Signatures/ • https://www.certinal.com/blog/how-to-verify-digital-signature
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Digital Signature Based Document Verification System.
[*] Metasploit Scan Running on Target Subnet for Digital Signature Based Document Verification System... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |