Complete Technical Paper Content — Distributed Denial Of Service Mitigation System Using Iptables
Overview & System Context
Distributed Denial Of Service Mitigation System Using Iptables: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~3518 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Detect and mitigate DDoS attacks in under 1 second, respond automatically, and keep your users informed.
From indie hosts to ISPs, see how teams like yours use Flowtriq to detect and stop DDoS attacks. A hands-on guide to building local firewall rules that stop SYN floods, UDP amplification, ICMP abuse, and connection exhaustion. Every rule shown in both iptables and nftables syntax. Local firewall rules are your first line of defense when a DDoS attack is moderate enough that your server's NIC and uplink can still handle the raw packet volume. If the attack is 500 Mbps and your server has a 1 Gbps link, iptables or nftables can drop the malicious traffic before it reaches your application. Your kernel processes the packets and discards them in the network stack, keeping your services responsive.
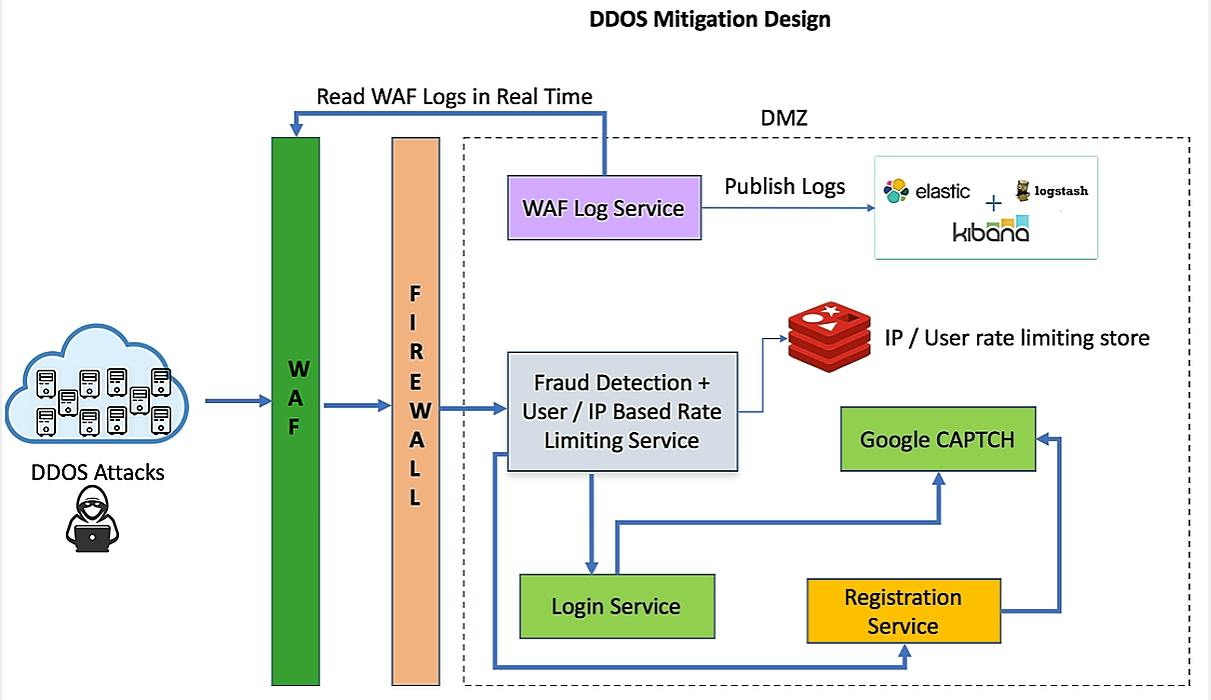
Figure 1: Distributed Denial Of Service (DDOS) Mitigation | HackerNoon However, local rules become useless when the attack saturates your uplink. If 10 Gbps of traffic is hitting your 1 Gbps port, the packets are already being dropped by your upstream router or switch before they even reach your kernel. No amount of firewall rules on the host can help because the bottleneck is the physical link, not the software stack. In that scenario you need upstream mitigation: scrubbing centers, BGP blackholing, or a DDoS protection service that filters traffic before it reaches your network.
That said, local rules are still worth maintaining even if you have upstream protection. Upstream mitigation takes time to activate. BGP propagation can take 30 seconds to several minutes. During that window, your local firewall rules keep your server alive. They are also effective against low-and-slow attacks, application-layer floods, and scanning that upstream filters may not catch.
nftables is the modern replacement for iptables in the Linux kernel. It was merged into the kernel in version 3.13 (2014) and has been the default firewall framework in Debian 10+, Ubuntu 20.04+, RHEL 8+, and most current distributions. If you are setting up a new server today, you should use nftables. That said, iptables is not gone. The iptables-nft compatibility layer translates iptables commands into nftables bytecode under the hood. On most modern systems, the iptables command is actually a symlink to iptables-nft . Your existing iptables rules still work; they are just being translated.
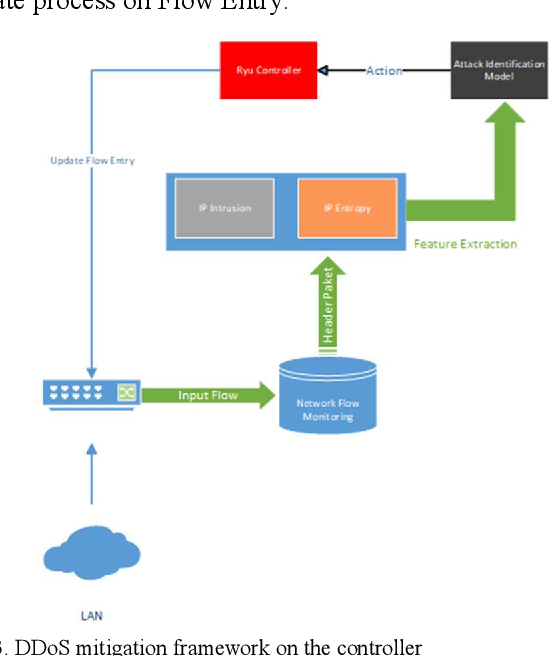
Figure 2: Figure 3 from Evaluation of the Effectiveness Mitigation of Distributed ... In this guide, every rule is shown in both syntaxes so you can use whichever matches your environment. Before addressing specific attack types, every server should have a baseline set of rules that drop obviously malicious traffic. These rules cost almost nothing in performance and catch a surprising amount of junk.
Invalid packets are those that do not match any known connection and do not have valid flags for starting a new connection. They are generated by scanners, broken attack tools, and spoofed traffic. Bogon addresses are IP ranges that should never appear as source addresses on the public internet. Dropping them eliminates a large class of spoofed traffic.
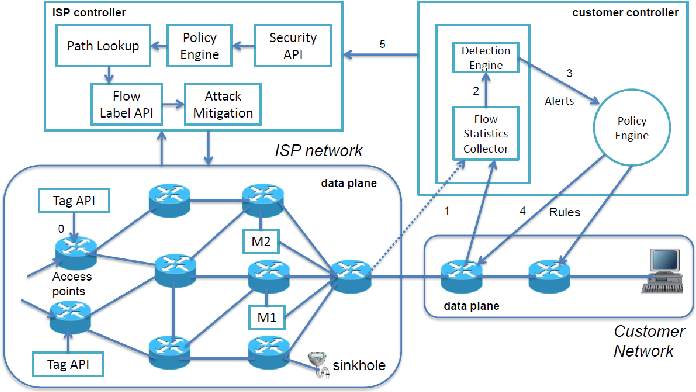
Figure 3: Figure 1 from Towards Autonomic DDoS Mitigation using Software Defined ... If your server is behind a private network or uses RFC 1918 addresses internally, remove the corresponding ranges from the bogon list. Dropping 10.0.0.0/8 on a server that receives traffic from a 10.x load balancer will break everything. ICMP is necessary for path MTU discovery and diagnostics, but unlimited ICMP can be abused for ping floods. Rate limiting keeps ICMP functional while preventing abuse.
Fragmented packets are rarely legitimate on modern networks (path MTU discovery prevents fragmentation in normal operation). They are frequently used in evasion techniques and fragment-based attacks. SYN floods remain the most common volumetric attack type. They exploit the TCP handshake by sending millions of SYN packets with spoofed source IPs. Each SYN causes the server to allocate memory for a half-open connection. The server's connection table fills up and legitimate users cannot connect.
The hashlimit module provides per-source-IP rate limiting, which is far more effective than a global rate limit. A global limit of 500 SYN/s means a single attacker using one IP can consume the entire budget. Per-source limiting ensures each IP gets its own bucket. 2. System Architecture & Core Working Principles This allows each source IP up to 30 SYN packets per second with a burst of 50. Legitimate users rarely exceed 5-10 SYN packets per second to any single server, so 30/s provides generous headroom while stopping flood sources.
UDP floods are the second most common DDoS vector. Because UDP is connectionless, there is no handshake to exploit. Attackers simply blast high volumes of UDP packets at the target. Amplification attacks (DNS, NTP, memcached, CLDAP) use UDP to achieve amplification factors of 50x or more. If your server only needs UDP on specific ports (for example, DNS on 53 or a game server on a custom port), drop all other inbound UDP. This eliminates entire classes of amplification traffic.
DNS amplification attacks use spoofed queries to open DNS resolvers. The responses (which can be 50x larger than the query) are directed at the victim. If your server is not expecting DNS responses from external resolvers, drop inbound UDP from source port 53. NTP amplification exploits the monlist command on misconfigured NTP servers. The amplification factor can reach 556x. Drop inbound UDP from source port 123 if your server does not use NTP over UDP from external sources (most modern systems use chrony which handles this differently).
These rules use conntrack to only drop NEW packets from these source ports. Responses to outbound queries your server initiated (ESTABLISHED state) are still allowed through. Your server can still query DNS and sync time. Even without a volumetric flood, an attacker can exhaust your server's resources by opening many connections and holding them open. Slowloris, R-U-Dead-Yet, and similar application-layer attacks use this technique. Connection limiting caps the number of concurrent connections from any single source.
A limit of 100 concurrent connections per IP is generous for web traffic. Most browsers open 6-8 connections per domain. If a single IP has 100 connections open simultaneously, it is either a proxy, a CDN node, or an attacker. Adjust upward if you serve traffic through known proxy IPs. The connection tracking subsystem (conntrack) is the foundation of stateful firewalling. Under a DDoS attack, the conntrack table can fill up, causing the kernel to drop all new connections, including legitimate ones. Tuning conntrack parameters is critical.
Memory impact: Each conntrack entry uses approximately 300 bytes of kernel memory. Setting nf_conntrack_max to 2,097,152 reserves about 600 MB. Ensure your server has enough RAM to support this alongside your applications. The hashlimit module (iptables) and meters (nftables) provide the most flexible rate limiting for DDoS mitigation. Unlike the basic limit module which applies a global rate, hashlimit creates separate rate buckets per source IP, destination IP, source port, or destination port.
This approach limits traffic per port, preventing any single service from being overwhelmed while leaving others unaffected. The burst parameter is critical for avoiding false positives. Legitimate traffic is bursty: a user loads a page and their browser fires 20-30 requests in rapid succession, then goes quiet. Without a sufficient burst allowance, your rate limits will drop legitimate traffic during these natural bursts. Set the burst to 1.5x your per-second limit as a starting point, then adjust based on observed traffic patterns.
For quick reference, here is a summary of the most important rule translations between iptables and nftables: Firewall performance matters during a DDoS attack because every microsecond spent processing a malicious packet is a microsecond not spent serving legitimate traffic. Here are the key factors: If you run Docker, you need to know about the DOCKER-USER chain. Docker manipulates iptables extensively, creating its own chains and DNAT rules to route traffic to containers. The critical problem: rules you add to the INPUT chain do not apply to traffic destined for Docker containers. Container traffic goes through the FORWARD chain, bypassing INPUT entirely.
Docker provides the DOCKER-USER chain specifically for user-defined rules that should apply to container traffic. Rules in this chain are evaluated before Docker's own rules. 3. Software Implementation, Frameworks & Protocols Always use -I DOCKER-USER (insert) instead of -A DOCKER-USER (append) to ensure your rules are evaluated before the default RETURN rule that Docker places at the end of the chain.
If you use Docker Compose or Docker Swarm, test your DOCKER-USER rules carefully. Docker recreates its iptables rules when containers start and stop. Your DOCKER-USER rules persist across container restarts, but you should verify they are still in place after a Docker daemon restart. Manually adding firewall rules during an attack is slow and error-prone. Flowtriq's auto-mitigation feature can trigger iptables or nftables rules automatically when an attack is detected, and remove them when the attack subsides.
This approach combines the precision of Flowtriq's detection (which identifies the exact attack vector and source characteristics) with the speed of local firewall rules (which take effect instantly, with no upstream propagation delay). You can configure which mitigation actions Flowtriq is allowed to take in the auto-mitigation settings . Options range from notification-only (Flowtriq tells you what rules to apply) to fully automatic (Flowtriq applies and removes rules without human intervention).
Below is a complete iptables-save format ruleset that you can adapt for your server. It incorporates all the rules discussed in this guide. Save it to a file and load it with iptables-restore < ruleset.rules . Test thoroughly. Lock yourself out of SSH and you will have a bad day. Always have out-of-band console access (IPMI, cloud console, KVM) available before applying restrictive firewall rules remotely.
Try our nftables Rule Generator - generate production-ready nftables rulesets for SYN flood, UDP flood, and ICMP rate limiting with one click. Flowtriq automates this. Instead of manually crafting and maintaining firewall rules, Flowtriq monitors your traffic in real time, detects attacks within seconds, and can apply targeted mitigation rules automatically. Rules are tailored to the specific attack vector, not generic templates. Start your 14-day free trial to see it in action.
How to detect and mitigate UDP-based volumetric attacks including DNS and NTP amplification. iptables and nftables rules help when the attack volume is smaller than your server uplink capacity. If you have a 1 Gbps link and the attack is 500 Mbps, local firewall rules can drop malicious packets before they reach your application. However, when the attack saturates your uplink (e.g., 10 Gbps hitting a 1 Gbps port), local rules are useless because packets are dropped by your upstream router before reaching your kernel. In that case, upstream mitigation like BGP blackholing or cloud scrubbing is required.
Use nftables for new server setups. nftables uses a single-pass classifier, supports native sets and maps for O(1) IP matching (replacing the separate ipset tool), and allows atomic ruleset replacement. It is the default in Debian 10+, Ubuntu 20.04+, and RHEL 8+. Existing iptables rules still work through the iptables-nft compatibility layer. The key advantage for DDoS mitigation is that nftables handles large IP blacklists far more efficiently than iptables linear rule chains.
The hashlimit module in iptables (and meters in nftables) provides per-source-IP rate limiting, which is far more effective than global rate limits. A global limit of 500 SYN/s means one attacker can consume the entire budget. Per-source hashlimit gives each IP its own rate bucket, so one attacker sending 10,000 SYN/s gets limited while legitimate users are unaffected. Set burst to approximately 1.5x your per-second limit to avoid false positives from natural traffic bursts.
Docker bypasses the INPUT chain entirely for container traffic, routing it through the FORWARD chain instead. You must use the DOCKER-USER chain for DDoS protection rules that apply to containers. Use iptables -I DOCKER-USER (insert, not append) to add rules before Docker default RETURN rule. For example: iptables -I DOCKER-USER -p tcp --syn -m hashlimit --hashlimit-name syn_limit --hashlimit-mode srcip --hashlimit-above 30/s --hashlimit-burst 50 -j DROP.
Drop unsolicited DNS responses by matching inbound UDP from source port 53 in NEW connection state: iptables -A INPUT -p udp --sport 53 -m conntrack --ctstate NEW -j DROP. Apply the same pattern for NTP (source port 123), memcached (source port 11211), SSDP (source port 1900), and CLDAP (source port 389). Using conntrack state NEW ensures you only block unrequested responses while allowing replies to outbound queries your server initiated.
Each conntrack entry uses approximately 300 bytes of kernel memory. The default nf_conntrack_max is often 65,536 entries (about 20 MB). For servers under DDoS, increase to 2,097,152 entries (about 600 MB). Set nf_conntrack_buckets to one-quarter of nf_conntrack_max for optimal hash table performance. Reduce timeouts for SYN_RECV (30s), TIME_WAIT (30s), FIN_WAIT (30s), and CLOSE_WAIT (15s) to free entries faster during attacks.
In the realm of cybersecurity, the importance of deploying robust iptables configurations cannot be overstated, especially when defending against the persistent threat of DDoS (Distributed Denial of Service) attacks. These insidious attacks are designed to flood your network with malicious traffic, seeking to overwhelm your server resources and disrupt critical services. The consequences can be severe, leading to downtime, financial losses, and tarnished reputation. However, by implementing carefully crafted iptables rules, you can significantly bolster your network’s resilience and minimize the impact of these malicious assaults.
4. Practical Deployment, Analysis & Case Studies Effective iptables rules act as a frontline defense mechanism, allowing you to selectively filter and control incoming traffic based on defined criteria. By strategically configuring these rules, you can block unauthorized access attempts, mitigate the effects of volumetric attacks, and safeguard the availability and integrity of your network infrastructure. This proactive approach not only defends against DDoS threats but also enhances the overall security posture of your organization’s digital assets.
iptables is a powerful firewall utility in Linux that allows you to configure rules for packet filtering and network address translation (NAT). It operates at the kernel level, making it a robust solution for controlling network traffic. To begin configuring iptables for DDoS mitigation, you’ll first need to access your server’s command-line interface. Here’s a step-by-step guide to implementing basic rules: While the above rules provide a foundational layer of protection, customizing iptables rules based on your specific needs is crucial for effective DDoS mitigation. Consider the following advanced configurations: After applying your iptables rules, it’s crucial to conduct thorough testing to ensure they function as intended without disrupting legitimate traffic. Continuously monitor your server’s performance and adjust rules as necessary to adapt to evolving DDoS threats.
In conclusion, a well-configured iptables setup is instrumental in defending against DDoS attacks by filtering and controlling incoming traffic. By following the outlined guidelines and customizing rules to suit your environment, you can significantly enhance the security posture of your network. A Distributed Denial of Service (DDoS) attack floods your server with fake traffic until it can’t respond to real visitors. DDoS protection isn’t a single switch you flip — it’s a layered approach that combines network-level filtering, server-side rate limiting, and traffic analysis. If your site is going down unexpectedly, or you’re seeing massive spikes in bandwidth with no clear cause, you may already be under attack.
This article covers practical mitigation steps for VPS and dedicated server users running Linux (Ubuntu 20.04/22.04 or CentOS 7/8). Some steps apply equally to managed environments; others require root access. I’ll flag which is which as we go. It’s worth understanding upfront that no single tool stops every attack. A large volumetric attack — say, 10 Gbps of junk UDP traffic — will saturate your network port before your server even sees the packets. That’s why combining on-server tools with upstream network filtering gives you the best coverage.
Before you configure anything, figure out what you’re dealing with. Run the following to see active connections and spot unusual volume from specific IPs or ports: If the SYN_RECV count is in the hundreds or thousands, you’re likely looking at a SYN flood. If you see a handful of IPs sending thousands of requests, that’s an application-layer (Layer 7) attack — which is actually easier to block than volumetric floods.
These rules won’t stop a massive volumetric attack, but they’ll knock out most script-kiddie floods and slow down application-layer attacks significantly. I Note: These rules are not persistent by default. On Ubuntu, install iptables-persistent and run netfilter-persistent save to survive reboots. On CentOS/AlmaLinux, use service iptables save .
I Warning: Always confirm your SSH port is explicitly allowed BEFORE applying DROP rules. Locking yourself out of port 22 (or your custom SSH port) requires console access to fix. Fail2Ban monitors log files and auto-bans IPs that hit thresholds you define. It’s not just for SSH — you can configure it for Apache, Nginx, and custom applications.
Create a local override file — don’t edit /etc/fail2ban/jail.conf directly, because package updates will overwrite it: For HTTP flood protection, add a custom jail. Create /etc/fail2ban/jail.d/http-flood.conf : 5. Performance Evaluation & Extended Technical Observations I Note: If you’re running Apache, change the logpath to /var/log/apache2/access.log (Ubuntu) or /var/log/httpd/access_log (CentOS).
For HTTP/HTTPS floods targeting your application, ModSecurity is the standard open-source WAF. On cPanel/WHM servers, you can enable ModSecurity directly from WHM under Security Center > ModSecurity™ Tools . Use the OWASP Core Rule Set (CRS) as a starting point. Then enable it in your Nginx config by adding to the http block in /etc/nginx/nginx.conf : Here’s the honest reality: if you’re getting hit with 5+ Gbps of traffic, your server’s CPU and iptables rules are already overwhelmed. The traffic is filling your uplink before your firewall can inspect it. The only solution at that scale is upstream filtering — where traffic gets scrubbed before it reaches your server.
Host & Tech’s Dedicated Servers include upstream DDoS mitigation at the network layer, which handles volumetric attacks that on-server tools simply can’t. If you’re on a VPS and getting targeted frequently, it’s worth evaluating whether a dedicated server with network-level protection better fits your requirements. For Cloudflare users, enabling “Under Attack” mode in your Cloudflare dashboard adds a JavaScript challenge to all visitors, which eliminates most bot-based HTTP floods immediately — it’s crude but effective in an emergency.
This is common when the --limit-burst value is too low. A real user loading a page triggers multiple simultaneous connections, and aggressive limits catch them. Raise --limit-burst to 200 or higher and monitor. Also check whether a CDN or load balancer is sending all traffic from a single IP — if so, whitelist that IP before applying rate limits. The most common cause is a mismatched log path or a filter that doesn’t match your log format. Run fail2ban-client status http-flood and check the “Currently banned” count. Then test your filter manually: If it shows 0 matches, your regex doesn’t match your log format. Nginx and Apache log formats vary between distros and custom configs.
If traffic is saturating your network interface, iptables rules run too late in the stack — the packets have already consumed bandwidth. Check your interface saturation with iftop -i eth0 . If you’re seeing consistent 100% utilization, this requires upstream mitigation, not on-server rules. Contact your host to engage network-level filtering. If you can no longer SSH in, you’ll need to access your server via the VPS console in the Host & Tech control panel, or request KVM/IPMI access for dedicated servers. Once in, flush all iptables rules with iptables -F and rebuild them carefully, confirming your SSH port is explicitly permitted before any DROP rules.
This is annoyingly common after enabling the OWASP CRS in blocking mode. I’d recommend starting in detection-only mode — set SecRuleEngine DetectionOnly in /etc/nginx/modsecurity/modsecurity.conf — then review /var/log/modsec_audit.log for false positives before switching to enforcement. Wholesale enabling blocking mode on a live site without testing first causes real outages.
No, and anyone who tells you otherwise is overselling their product. What you can do is significantly raise the cost and effort of attacking you, automatically block the majority of automated floods, and have upstream network filtering in place for volumetric attacks. Most attackers move on when a target is hardened enough. The most common signs are sudden unexplained downtime, extremely slow response times, and bandwidth usage that spikes far above your normal baseline. Run ss -ntu | awk '{print $5}' | cut -d: -f1 | sort | uniq -c | sort -rn | head -20 to see if a small number of IPs are generating a huge share of connections. Your hosting control panel’s bandwidth graphs will also show the spike clearly.
Cloudflare’s free plan includes basic DDoS protection and is genuinely useful for HTTP-layer attacks. For larger volumetric attacks, Cloudflare’s paid tiers offer better mitigation. That said, if your server’s IP is publicly known, attackers can bypass Cloudflare entirely and hit your origin IP directly — so make sure your real server IP isn’t exposed in DNS records or email headers.
Done correctly, it shouldn’t be noticeable. Rate limiting only affects connections that exceed thresholds real users rarely hit. The main risk is misconfiguration — setting limits too aggressively or enabling a WAF in blocking mode without testing. Start with conservative settings, monitor your logs, and tighten rules gradually. Host & Tech’s dedicated server plans include network-level DDoS mitigation at the infrastructure layer, which handles volumetric attacks before they reach your server. For specific details on protection thresholds and what’s covered on your plan, reach out to the support team or check your plan details in the client portal.
Harvested Online Documentation & Reference Sources • https://flowtriq.com/blog/iptables-nftables-ddos-mitigation • https://docs.upzilla.co/posts/guides/2024/04/basic-iptables-configuration-for-ddos-mitigation/ • https://hostandtech.com/kb/security/preventing-ddos-attacks-on-your-server/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Distributed Denial Of Service Mitigation System Using Iptables.
[*] Metasploit Scan Running on Target Subnet for Distributed Denial Of Service Mitigation System Using Iptables... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |