Complete Technical Paper Content — Dll Injection Detection And Process Monitoring Tool
Overview & System Context
Dll Injection Detection And Process Monitoring Tool: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8857 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background BlackEnergy Malware was first reported in 2007 as an HTTP-based toolkit that generated bots to execute distributed denial of service attacks. It was created by Russian hacker Dmyrtro Oleksiuk around 2007. Oleksiuk also utilized the alias Cr4sh. In 2010, BlackEnergy 2 emerged with capabilities beyond DDoS. In 2014, BlackEnergy 3 came equipped with a variety of plug-ins. A Russian-based group known as Sandworm (aka Voodoo Bear) is attributed with using BlackEnergy targeted attacks. The attack is distributed via a Word document or PowerPoint attachment in an email, luring victims into clicking the seemingly legitimate file.
Can target more than one IP address per hostname Has a runtime encrypter to evade detection by antivirus software Hides its processes in a system driver (syssrv.sys) fs.dll — File system operations si.dll — System information, “BlackEnergy Lite” jn.dll — Parasitic infector ki.dll — Keystroke Logging ps.dll — Password stealer ss.dll — Screenshots vs.dll — Network discovery, remote execution tv.dll — Team viewer rd.dll — Simple pseudo “remote desktop” up.dll — Update malware dc.dll — List Windows accounts bs.dll — Query system hardware, BIOS, and Windows info dstr.dll — Destroy system scan.dll — Network scan A rootkit is a collection of typically malicious computer software designed to enable access to a computer or to part of its software that would not otherwise be allowed (for example, by an unauthorized user). Rootkits often mask their presence or that of other software. The term rootkit is a compound of "root" (the traditional name of the privileged account on Unix-like operating systems) and the word "kit" (which refers to the software components that implement the tool). The term "rootkit" has negative connotations through its association with malware. Rootkit installation can be automated, or an attacker can install a rootkit after having obtained root or administrator access. Obtaining this access is a result of a direct attack on a system, i.e., exploiting a vulnerability (such as privilege escalation) or a password (obtained by cracking or social engineering tactics like "phishing"). Once installed, it becomes possible to hide the intrusion as well as to maintain privileged access. Full control over a system means that existing software can be modified, including software that might otherwise be used to detect or circumvent it. Rootkit detection is difficult because a rootkit may be able to subvert the software that is intended to find it.
Detection methods include using an alternative and trusted operating system, behavior-based methods, signature scanning, difference scanning, and memory dump analysis. Removal can be complicated, especially in cases where the rootkit resides in the kernel; reinstallation of the operating system may be the only available solution to the problem. When dealing with firmware rootkits, removal may require hardware replacement, or specialized equipment.
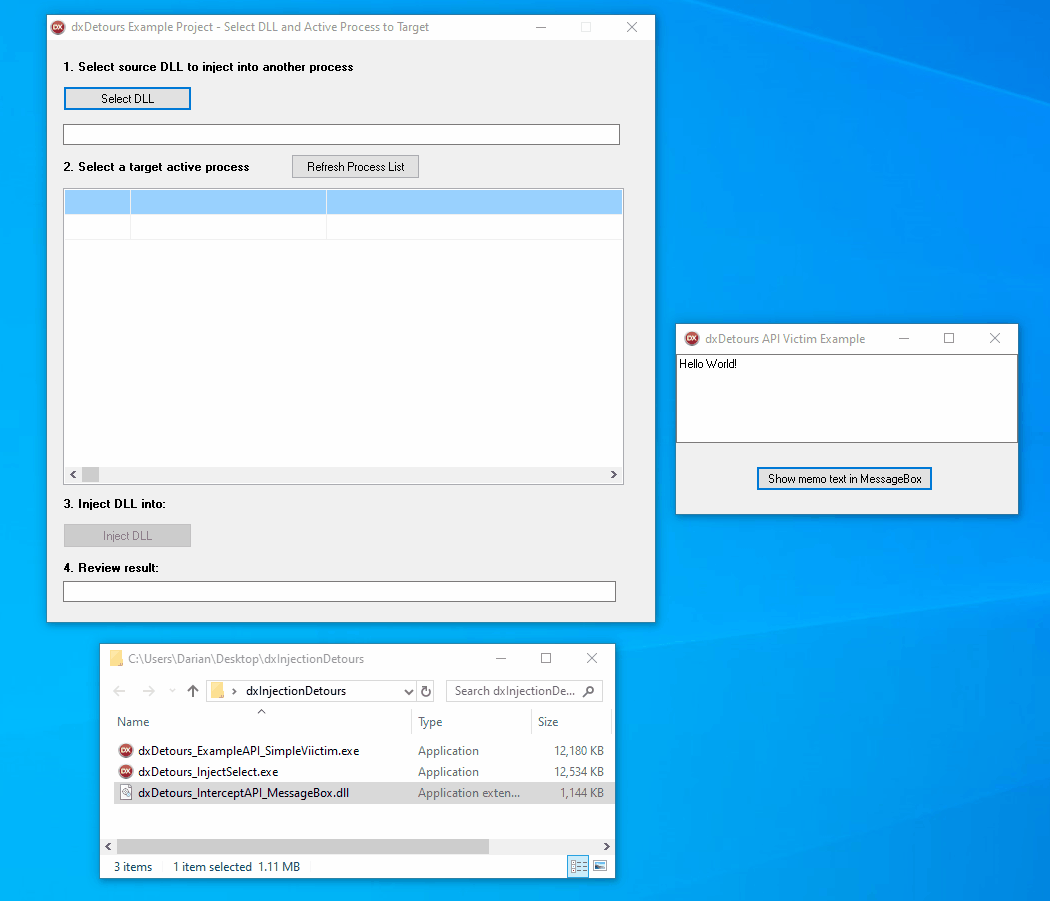
Figure 1: DLL Injection with DelphiIIII - xalion - III Stuxnet, uncovered in 2010, was a highly sophisticated worm widely believed to have been developed in a joint U.S.–Israeli intelligence operation targeting Iran’s nuclear facilities. It notably included a Windows kernel-mode rootkit that concealed the malware’s files and processes, enabling the worm to silently sabotage industrial control systems. Stuxnet is often cited as the first known cyberweapon; it destroyed a significant part of Iran’s uranium centrifuges, while remaining difficult to detect.
In 2005, Sony BMG published CDs with copy protection and digital rights management software called Extended Copy Protection, created by software company First 4 Internet. The software included a music player but silently installed a rootkit which limited the user's ability to access the CD. Software engineer Mark Russinovich, who created the rootkit detection tool RootkitRevealer, discovered the rootkit on one of his computers. The ensuing scandal raised the public's awareness of rootkits. To cloak itself, the rootkit hid any file starting with "$sys$" from the user. Soon after Russinovich's report, malware appeared which took advantage of the existing rootkit on affected systems. One BBC analyst called it a "public relations nightmare." Sony BMG released patches to uninstall the rootkit, which exposed users to an even more serious vulnerability.
The company eventually recalled the CDs. In the United States, a class-action lawsuit was brought against Sony BMG. The 2004–2005 Greek wiretapping case, also referred to as Greek Watergate, involved the illegal telephone tapping of more than 100 mobile phones on the Vodafone Greece network belonging mostly to members of the Greek government and top-ranking civil servants. The taps began sometime near the beginning of August 2004 and were removed in March 2005 without discovering the identity of the perpetrators. The intruders installed a rootkit targeting Ericsson's AXE telephone exchange. According to IEEE Spectrum, this was "the first time a rootkit has been observed on a special-purpose system, in this case an Ericsson telephone switch." The rootkit was designed to patch the memory of the exchange while it was running, enable wiretapping while disabling audit logs, patch the commands that list active processes and active data blocks, and modify the data block checksum verification command. A "backdoor" allowed an operator with sysadmin status to deactivate the exchange's transaction log, alarms and access commands related to the surveillance capability. The rootkit was discovered after the intruders installed a faulty update, which caused SMS texts to be undelivered, leading to an automated failure report being generated. Ericsson engineers were called in to investigate the fault and discovered the hidden data blocks containing the list of phone numbers being monitored, along with the rootkit and illicit monitoring software.
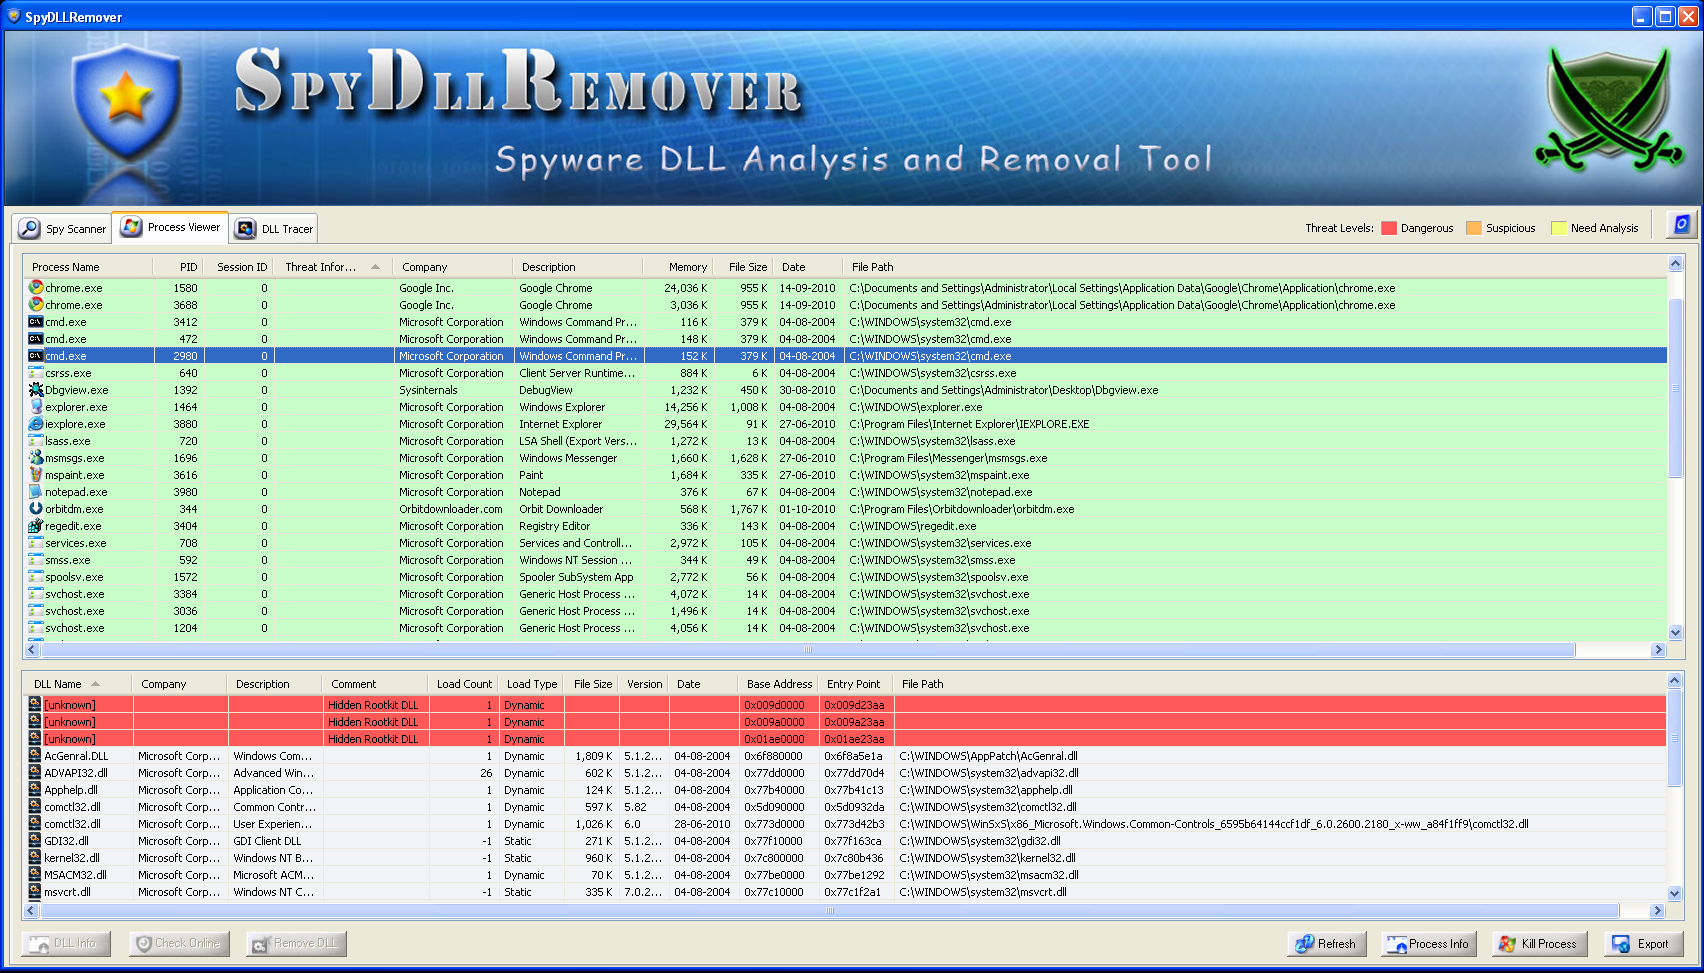
Provide an attacker with full access via a backdoor, permitting unauthorized access to, for example, steal or falsify documents. One of the ways to carry this out is to subvert the login mechanism, such as the /bin/login program on Unix-like systems or GINA on Windows. The replacement appears to function normally, but also accepts a secret login combination that allows an attacker direct access to the system with administrative privileges, bypassing standard authentication and authorization mechanisms. Conceal other malware, notably password-stealing key loggers and computer viruses. Appropriate the compromised machine as a zombie computer for attacks on other computers. (The attack originates from the compromised system or network, instead of the attacker's system.) "Zombie" computers are typically members of large botnets that can–amongst other things–launch denial-of-service attacks, distribute email spam, and conduct click fraud. In some instances, rootkits provide desired functionality, and may be installed intentionally on behalf of the computer user: Figure 2: SpyDllRemover showing the new Scan Settings Detect attacks, for example, in a honeypot. Enhance emulation software and security software. Alcohol 120% and Daemon Tools are commercial examples of non-hostile rootkits used to defeat copy-protection mechanisms such as SafeDisc and SecuROM. Kaspersky antivirus software also uses techniques resembling rootkits to protect itself from malicious actions. It loads its own drivers to intercept system activity, and then prevents other processes from doing harm to itself. Its processes are not hidden, but cannot be terminated by standard methods. Anti-theft protection: Laptops may have BIOS-based rootkit software that will periodically report to a central authority, allowing the laptop to be monitored, disabled or wiped of information in the event that it is stolen. Bypassing Microsoft Product Activation There are at least five types of rootkit, ranging from those at the lowest level in firmware (with the highest privileges), through to the least privileged user-based variants that operate in Ring 3. Hybrid combinations of these may occur spanning, for example, user mode and kernel mode.
User-mode rootkits run in Ring 3, along with other applications as user, rather than low-level system processes. They have a number of possible installation vectors to intercept and modify the standard behavior of application programming interfaces (APIs). Some inject a dynamically linked library (such as a .DLL file on Windows, or a .dylib file on Mac OS X) into other processes, and are thereby able to execute inside any target process to spoof it; others with sufficient privileges simply overwrite the memory of a target application. Injection mechanisms include: Use of vendor-supplied application extensions. For example, Windows Explorer has public interfaces that allow third parties to extend its functionality. Interception of messages. Debuggers. Exploitation of security vulnerabilities. Function hooking or patching of commonly used APIs, for example, to hide a running process or file that resides on a filesystem. ...since user mode applications all run in their own memory space, the rootkit needs to perform this patching in the memory space of every running application. In addition, the rootkit needs to monitor the system for any new applications that execute and patch those programs' memory space before they fully execute.
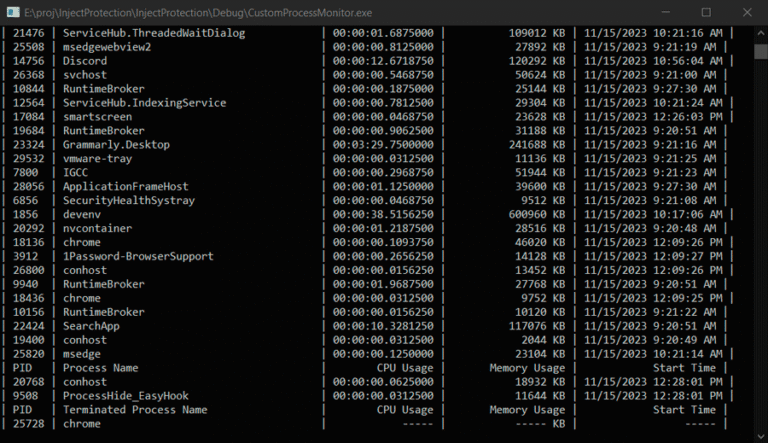
Figure 3: Mitigate DLL Injection Attacks - Apriorit Code signing uses public-key infrastructure to check if a file has been modified since being digitally signed by its publisher. Alternatively, a system owner or administrator can use a cryptographic hash function to compute a "fingerprint" at installation time that can help to detect subsequent unauthorized changes to on-disk code libraries. However, unsophisticated schemes check only whether the code has been modified since installation time; subversion prior to that time is not detectable. The fingerprint must be re-established each time changes are made to the system: for example, after installing security updates or a service pack. The hash function creates a message digest, a relatively short code calculated from each bit in the file using an algorithm that creates large changes in the message digest with even smaller changes to the original file. By recalculating and comparing the message digest of the installed files at regular intervals against a trusted list of message digests, changes in the system can be detected and monitored—as long as the original baseline was created before the malware was added.
More-sophisticated rootkits are able to subvert the verification process by presenting an unmodified copy of the file for inspection, or by making code modifications only in memory, reconfiguration registers, which are later compared to a white list of expected values. The code that performs hash, compare, or extend operations must also be protected—in this context, the notion of an immutable root-of-trust holds that the very first code to measure security properties of a system must itself be trusted to ensure that a rootkit or bootkit does not compromise the system at its most fundamental level.
BattlEye is proprietary kernel–level anti-cheat software designed to detect players that hack or abusively use exploits in an online game. It was initially released as a third-party anti-cheat for Battlefield Vietnam in 2004 and has since been officially implemented in numerous video games, primarily shooter games such as PUBG: Battlegrounds, Arma 3, Destiny 2, War Thunder, and DayZ. BattlEye is developed by German company BattlEye Innovations e. K., headquartered in Reutlingen.
BattlEye supports Valve Corporation's Proton compatibility layer and is usable on the Steam Deck if the game developer opts in. DLL Injection is a technique that forces a target process to load and execute code from an attacker-controlled Dynamic Link Library (DLL). It is a foundational post-exploitation and persistence mechanism on Windows, used for privilege escalation, credential theft, lateral movement, and defense evasion . This guide covers the major injection methods with working examples and detection guidance.
DLL Injection exploits the Windows dynamic linking mechanism to execute arbitrary code inside the address space of another process. By injecting a DLL into a trusted process (e.g., explorer.exe , svchost.exe ), the attacker’s code inherits the target’s privileges, tokens, and network context. The most well-known technique. It writes a DLL path into the target process’s memory and creates a remote thread that calls LoadLibraryA to load it.
Reflective DLL Injection loads a DLL entirely from memory without ever calling LoadLibrary or writing the DLL to disk. The DLL contains its own PE loader as an exported function, which manually maps itself into memory. DLL Hollowing loads a legitimate DLL into the target process, then overwrites its .text (code) section with malicious code. This evades detection because the loaded module appears legitimate in memory scans.
Process Hollowing creates a new legitimate process in a suspended state , unmaps its original code, and replaces it with the attacker’s PE image. The process then resumes execution with the malicious code. This technique does not inject code into a running process . Instead, it places a malicious DLL in a location that the target application searches before the legitimate DLL location.
This reveals DLLs that applications attempt to load but cannot find — perfect hijacking candidates. To avoid breaking the application, the malicious DLL can forward all legitimate exports to the real DLL: OSCP note: DLL Hijacking is especially useful for privilege escalation when a service running as SYSTEM loads DLLs from a user-writable directory.
Instead of creating a new thread, this technique hijacks an existing thread in the target process by suspending it, modifying its instruction pointer, and resuming it. In the field of Windows security offense and defense, Function Hooking is a core technology for EDR (Endpoint Detection and Response) to monitor process behavior and for attackers to bypass protections. To counter modern EDR interception, the first step is to master the operating mechanism of function hooking in user mode. Centered on the framework of “FUNCTION-HOOKING DLLS”, this article starts with basic concepts and memory layout, then delves into implementation processes, detection methods, and evasion techniques. Even readers new to this topic can follow along to set up experimental environments and verify code examples.
When a Windows application executes a system call, it does not interact directly with the kernel. Instead, it goes through multiple intermediate layers: User Code → Win32 API → ntdll.dll → Kernel . By setting a “Trampoline” at any of these layers, EDR tools or debuggers can monitor or even alter process behavior without modifying the application’s source code—that is the core value of function hooking.
Based on the location of modifications, common hooking techniques are divided into three categories, each with distinct application scenarios and characteristics: This article focuses on the most widely used Inline Hook . Understanding it only requires grasping three basic concepts: Using CreateFileW (a function for monitoring file creation) as an example, Inline Hook implementation consists of 4 key steps, each requiring strict adherence to memory operations and instruction logic: Call VirtualProtect to change the attribute of the memory page where CreateFileW resides to PAGE_EXECUTE_READWRITE , ensuring that jump instructions can be written later.
Copy the first few bytes (usually 16 bytes, enough to cover multiple complete instructions) of CreateFileW and save them to the InlineHook::original structure. Meanwhile, add a jmp instruction to InlineHook::trampoline to jump back to the unmodified part of the original function. Write an unconditional jump instruction at the start of CreateFileW (commonly MOV RAX + JMP RAX for x64, or JMP rel32 for x86), redirecting function calls directly to custom processing logic.
Subsequent calls to CreateFileW will first execute the custom processing function (e.g., recording file paths, identifying potentially dangerous operations), then jump back to the original function via the trampoline—ensuring the original functionality remains intact. The following is the C++ implementation code for the core logic of Inline Hook, which also serves as the underlying foundation for hook frameworks like Detours: Manually writing Inline Hook often leads to issues like exception recovery, instruction length calculation, and thread safety.
Microsoft’s open-source Detours library encapsulates these details into transactional APIs, significantly reducing development complexity while supporting edge scenarios such as WOW64 compatibility, exception filtering, and thread recovery. The process of implementing hooks with Detours is fixed in 4 steps. Below is an example of intercepting CreateFileW to log file access: Call DetourTransactionBegin to freeze the current thread’s execution flow, preventing thread race conditions during patching.
2. System Architecture & Core Working Principles Use DetourUpdateThread to inform Detours which thread to suspend. Typically, pass GetCurrentThread() (the current thread). Use DetourAttach to install the hook (bind the target function to the custom function) and DetourDetach to uninstall the hook.
Call DetourTransactionCommit to write all patches at once. After success, resume thread execution, and the hook takes effect. The following is the complete Detours-based C++ code for intercepting CreateFileW , which can be compiled and run directly: Hook code is usually encapsulated in a DLL. For the DLL to take effect, it must first be injected into the address space of the target process. EDRs commonly use two types of injection methods—user-mode and kernel-mode—each suited to different scenarios.
Before Windows 8, many security tools used the AppInit_DLLs registry entry (path: HKLM\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Windows ). Whenever a process loaded user32.dll , the system would automatically inject the DLLs listed in this registry. This method is simple to implement and offers wide coverage but is easily abused by malware. It also slows down system startup. Since Windows 8, systems with Secure Boot enabled have completely disabled this mechanism, and it is now only used for compatibility scenarios.
Create a remote thread via CreateRemoteThread to make the target process load a specified DLL. This method is suitable for injecting into existing processes and follows a clear workflow: The following is the C++ implementation code for remote thread injection, suitable for testing in experimental environments: User-mode injection may be blocked by the target process’s anti-injection policies (e.g., PROCESS_MITIGATION_DYNAMIC_CODE_POLICY ). Therefore, modern EDRs increasingly use kernel-mode KAPC injection.
Since the logic runs in kernel mode, KAPC injection can bypass user-mode protections and insert monitoring at the earliest stage of process initialization, offering higher stealth and success rates. Whether building an EDR or securing an application, detecting function hooking is a core requirement. Common detection strategies are based on “memory comparison” and “integrity verification”. Below are 4 practical methods: Read the starting bytes of the target function in memory and compare them with the original bytes of the DLL containing the function on disk. If jump instructions (e.g., 0xE9 , 0xFFE0 ) or meaningless padding exist, the function may be hooked.
Calculate the MD5 or SHA256 hash of the memory page containing the target function and compare it with a pre-stored “clean” hash value. If the hashes do not match, the memory has been tampered with, indicating a potential hook risk. Traverse the process’s import address table and check if each function pointer points to the expected DLL module (e.g., kernel32.dll , ntdll.dll ). If a pointer points to an unknown module or custom memory area, it is likely an IAT hook.
Load a read-only copy of the target DLL from disk (without executing code) and perform a byte-level comparison with the DLL already loaded in the process. Identify all memory differences to determine if hooking exists. The following is the C++ implementation code for “byte comparison detection”, which can quickly determine if CreateFileW has been tampered with: When EDRs monitor critical APIs via hooking, attackers need to bypass these interception points. The three techniques below have both learning value and practical significance, but note: All operations must be performed in authorized experimental environments; unauthorized use is prohibited .
Win32 APIs like WriteFile and CreateFileW called by Windows applications ultimately pass through functions such as NtWriteFile and NtCreateFile in ntdll.dll , which trigger kernel services via the syscall instruction. By directly calling these “kernel interface functions” in ntdll.dll , you can bypass EDR hooks on Win32 APIs. Taking NtWriteFile as an example, its assembly logic (viewed via debugger for ntdll!NtWriteFile ) is as follows: The following is the C++ implementation of directly calling NtWriteFile , which can bypass hooks on WriteFile : If EDRs hook not only Win32 APIs but also functions in ntdll.dll (e.g., NtWriteFile ), the address obtained directly via GetProcAddress may be a tampered function address. In this case, you need to resolve the original SSN from a disk-based copy of ntdll.dll to avoid using the hooked module in memory.
The following code implements the logic of resolving the export function address from the disk-based ntdll.dll, preparing for subsequent SSN extraction: If ntdll.dll is heavily hooked, the above methods may fail. In this case, you can directly load a “clean” copy of ntdll.dll from disk and remap it to the current process memory, completely avoiding the hooked module in memory.
The following is the implementation code for remapping ntdll.dll, which can be used to obtain an unhooked NtWriteFile : This article focuses on user-mode Function Hooking , covering hook classification, manual Inline Hook implementation, Detours library usage, EDR DLL injection methods, and detection/evasion techniques from both offensive and defensive perspectives. Through specific C++ code examples, readers can set up experimental environments to verify each step of the logic and deepen their understanding of Windows underlying mechanisms.
For defenders (e.g., EDR developers),priority should be placed on the stealth of hooks and the comprehensiveness of detection. For example, combining kernel-mode monitoring with hardware-assisted virtualization (such as Intel VT-x/AMD-V) can achieve more reliable control flow protection. For offensive security researchers, mastering low-level technologies like system calls, PE parsing, and module remapping is essential to explore the boundaries of countermeasures in authorized scenarios.
Function hooking technology is the “cornerstone” of Windows security offense and defense. Only by deeply understanding its principles and boundaries can one gain the initiative in offense-defense confrontation. Whether building more secure protection systems or conducting compliant vulnerability research, mastery of this technology is indispensable. A Windows-based security tool that monitors running processes and detects malicious code injection techniques commonly used by malware, exploits, and advanced persistent threats (APTs).
Process injection is a technique used by malware to insert and execute malicious code within the address space of legitimate processes. This allows attackers to evade detection, bypass security controls, and gain persistence. This tool continuously monitors running processes for signs of various injection techniques, providing real-time alerts when suspicious activity is detected.
This project is structured as a Python package for better organization and maintainability: This project includes a harmless test DLL source file ( test_injection.c ) and an injection script that you can use to safely test the process injection detection capabilities. If you'd like to contribute to this project, please see the CONTRIBUTING.md file for guidelines.
This tool is for educational and defensive security purposes only. It's designed to help identify potentially malicious activities but should be used responsibly and legally. Always ensure you have proper authorization before monitoring systems. Windows monitor that detects process-injection techniques used by malware — classic DLL injection, process hollowing and RWX memory anomalies — with real-time alerting.
A cybersecurity lab project demonstrating DLL Injection attack detection using Wazuh , Sysmon , and MITRE ATT&CK T1055.001 techniques. Dynamic-Link Library (DLL) injection is a process injection technique used by attackers to execute malicious code within the address space of another process. This technique is commonly associated with Privilege Escalation and Defense Evasion activities and is categorized under MITRE ATT&CK T1055.001 – Dynamic-link Library Injection .
This project demonstrates how Wazuh and Sysmon can be used to detect DLL injection activity in a Windows environment. A controlled lab environment was created to simulate the attack using InjectProc , while Sysmon generated the corresponding events and Wazuh correlated and generated alerts based on the observed behavior. 3. Software Implementation, Frameworks & Protocols Before performing the attack simulation, install and configure the following components: This section describes the step-by-step setup of the lab environment used to simulate and detect DLL Injection attacks.
Install the required Visual C++ runtime on the Windows endpoint to ensure proper execution of InjectProc and related binaries. Download the InjectProc tool and the DLL payload ( hello-world-x64.dll ) and place them in a dedicated working directory. Install the Wazuh agent on the Windows endpoint and register it with the Wazuh Manager.
Edit the Wazuh Agent configuration file ( ossec.conf ) and add the following configuration: Sysmon generates Event ID 8 (CreateRemoteThread) , which is a strong indicator of process injection activity. Wazuh successfully detected the DLL injection behavior and generated an alert based on the custom rule. This lab demonstrated how DLL Injection attacks can be detected using Sysmon for telemetry generation and Wazuh for log analysis and alerting.
The implementation successfully mapped malicious behavior to the MITRE ATT&CK framework, providing valuable visibility into process injection techniques commonly used by attackers. This approach can help Security Operations Center (SOC) teams improve detection coverage for advanced endpoint threats. In today's mature enterprise environments, adversaries must choose a stealthy means of beacon execution. The advancement of antivirus (AV) engines has forced threat actors to migrate many heavily-signatured implants from disk to memory, where they are not scanned as often if at all. Process Injection [T1055] is a common technique used to achieve this goal. In this article, we will explore the Windows logging mechanisms available for defenders to detect and prevent process injection, as well as the evasion techniques used by advanced threat actors to circumvent detection. At a high-level, the figure below demonstrates the general steps that adversaries must take in order to perform Process Injection or Reflective Code Loading [T1620] , and the coverage / visibility that good endpoint detection and response (EDR) products have along the way.
With the myriad of publicly available shellcode loaders, broad detection mechanisms should be utilized to detect as many variations as possible. Most process injection techniques can be abstracted into memory allocation, write, and execution primitives to dynamically execute code. The more generic the abstractions that we can create, the more individual procedures that we can potentially identify.
The first step that adversaries commonly employ is loading a PE file from disk to establish command and control (C2) [TA0011] communications. The implant loaded from disk can then callback to an attacker-controlled server, facilitating control over the compromised system. However, stage-less implants directly loaded like this can be easily signatured by AV. While some static indicators can be encrypted to hide their presence, excessively high file entropy can also be an indicator itself.
Additionally, EDRs often perform automated dynamic analysis in a sandbox before allowing execution of suspicious binaries to take place. This naturally led to the development of "stagers", which are small programs designed to load and execute position-independent shellcode. Stagers decouple functionality and allow for retrieval of the shellcode at runtime, thereby bypassing AV scans. While impractical for some environments, application whitelisting or code signing enforcement can restrict the usage of unknown applications. This would prevent a stager from directly executing in the first place. While these defenses can potentially be bypassed via DLL Hijacking [T1574.001] and other techniques, for now, we will assume that the attacker is able to execute a stager on the machine with the goal of injecting code into a remote process.
Next, the attacker needs to identify a process to inject code into. While code can be reflectively loaded into the stager itself (the local process), attackers often use remote process injection to better mask execution and masquerade as a legitimate process. For stability reasons, many opt to create the desired remote process and spawn it at runtime, rather than potentially crashing an existing live process. Then, attackers (usually) need to acquire a handle for the target process to perform virtual memory operations in the context of the remote address space. So, what telemetry sources do defenders have for these actions? Since most EDRs operate using a kernel-mode driver, they can register a set of custom kernel callback routines to get notified whenever certain actions take place. For example, EDRs can utilize the PsSetCreateProcessNotifyRoutine* family of functions to register a callback that is invoked whenever a process is created 1 . An EDR can use this notification as an opportunity to inject a hooking library into the new process, as a source of telemetry for certain sensitive API calls.
Additionally, ObRegisterCallbacks() can be used to register a callback routine for thread, process, and desktop handle operations. On its own, these behaviors are usually not enough to trigger an alert. However, when combined with other indicators, the general process injection flow becomes clearer. Depending on the injection method, memory usually needs to be explicitly allocated before shellcode can be written and executed. Windows provides several different memory allocation methods, each with slightly different functionality.
To allocate memory on the heap, HeapAlloc() or one of its wrappers ( GlobalAlloc() and LocalAlloc() ) can be used. Today, these wrapper functions are functionally equivalent and remain as artifacts from the old days of 16-bit Windows . The C runtime (CRT) provides malloc() and new , but they also internally call HeapAlloc() . For COM-aware allocations, CoTaskMemAlloc() or IMalloc::Alloc() with an OLE memory allocator can be used. VirtualAlloc() and VirtualAllocEx() are similar, but align allocations to page granularity (usually 64KB) and round up the length to the minimum page size (typically 4KB).
Despite the multitude of different options, most are simply wrappers and end up calling the same low-level implementations (as shown in this example call stack): Another important distinction for the VirtualAlloc* family of functions is that, by default, they (along with the NtAllocateVirtualMemory() NT API syscall) will treat executable pages as valid indirect call targets for Control Flow Guard (CFG) . CFG, which is Microsoft's implementation of Control Flow Integrity (CFI) , is an exploit mitigation feature designed to restrict arbitrary code execution by validating call targets using a bitmap. It is worth noting that CFG is only designed to limit exploitation of memory corruption vulnerabilities, as Microsoft exposes the SetProcessValidCallTargets() API for programs to manually designate call targets as valid or not.
Additionally, with the widespread adoption of Data Execution Prevention (DEP) , stack and heap allocations are often automatically marked as non-executable in their corresponding page table entry (PTE) control bits. One way that EDRs can get telemetry from allocation events is via usermode (ring 3) API hooks. Once an EDR is notified of a new process creation, it can inject its hooking library and detour functions by overwriting their function body in memory. This strategy is known as an inline hook, but there are many other methods that could be employed as well, such as import address table (IAT) hooking or previously system service dispatch table (SSDT) hooking. AV and EDR vendors used to more readily patch kernel memory, but this led to system instability and insecure implementations. With the introduction of Kernel Patch Protection (KPP / PatchGuard) in Windows XP, security vendors have now been forced to migrate their hooks to usermode instead.
Using native system services routines (syscalls) instead of their corresponding WinAPI wrappers can bypass some high-level hooks, but they can ultimately be scrutinized by an EDR just as easily. If an adversary directly executes a syscall stub (from the exported function in ntdll.dll ), the stub could be hooked just like any other function. Additionally, the EDR can analyze the call stack during execution of the syscall and see that it directly returns to user code (instead of through the normal wrappers), which is a high fidelity indicator of malicious activity. Some attackers may choose to embed custom syscall stubs inside an implant to bypass inline hooks. These stubs consist of a short function prologue in Assembly that sets up the required registers ( mov rax,
An alternative approach taken by some malware authors is to launch the sacrificial process in a suspended state, in an effort to beat the EDR before its hooks can be fully initialized ( Process Hollowing [T1055.012] ). However, using Event Tracing for Windows (ETW) , EDR vendors can tap into the Threat-Intelligence (TI) log provider to receive telemetry without relying on hooking.
While ETW largely operates at the kernel-level, some events are sent from userland via ntdll!EtwEventWrite() . As a result, implants may patch this function in memory to disable some ETW providers. However, telemetry from ETW can be used to detect this tampering (via the THREATINT_PROTECTVM* and THREATINT_WRITEVM* events), which may actually increase the chances of detection. In some cases, attempting to unhook or disable security controls unintentionally results in an increased likelihood of detection. In social psychology, this is known as the boomerang effect .
Now, back to memory allocation. Since EDRs have plenty of data surrounding explicit allocation, one alternative is to perform actions that have the side effect of allocating memory, like sending messages to a graphical window message queue ( Shatter Attacks ), or stuffing shellcode into the environment strings of a child process. Other techniques, such as enumerating existing PAGE_EXECUTE_READWRITE protected memory pages ( Mockingjay ), overwriting linker padding in a PE ( Code Cave ), or abusing the shared Extra Window Memory region of Explorer's tray window ( Extra Window Memory Injection [T1055.011] ), can even take advantage of existing memory without the need to explicitly allocate it. These techniques are much more difficult to atomically detect since they depart from the normal process injection paradigm. From a defensive perspective, allocation events by themselves present far too much noise to be a reliable indicator of process injection. But, they can help paint a full picture, especially when using temporal correlation to observe and link other injection steps.
After suitable memory has been identified and/or allocated, the payload can be written. This is usually performed using WriteProcessMemory() or its NT API equivalent, NtWriteVirtualMemory() . While most loaders simply use PAGE_EXECUTE_READWRITE protected memory pages, PAGE_READWRITE can also be used if the protection is changed after the data is written (using either VirtualProtect() or NtProtectVirtualMemory() ).
Most of the same telemetry sources are applicable from the previous section. Using the ETW-TI provider, EDRs have visibility into memory writes as well as protection modifications via THREATINT_WRITEVM* and THREATINT_PROTECTVM* events. But, before discussing specific detection mechanisms, it’s important to understand the different types of memory first. For now, we will ignore the first 3 since we're more interested in the type of memory rather than it's current state. Most dynamically allocated memory, like those resulting from the previously mentioned allocation functions, typically falls under the category of private memory. Consequently, it is almost always protected as PAGE_READWRITE , which aligns with its usage as stack and heap storage. Private memory is rarely ever marked as executable, with the exception of JIT compilers in a web browser or .NET Framework Common Language Runtime (CLR) allocations. Mapped memory, on the other hand, often originates from a file on disk via CreateFileMappingA() or NtCreateSection() . After using these functions to create a shared mapping/section object, a process can map a view of the section using MapViewOfFile() or NtMapViewOfSection() to interact with its contents. If the mapping object is backed specifically by an executable file and was created using the SEC_IMAGE flag, then subsequent views are marked as MEM_IMAGE regions instead of MEM_MAPPED . Since MEM_IMAGE regions originate from an executable file on disk, page protections for these views are determined by the PE itself from the permissions listed in the section table . Naturally, MEM_IMAGE blocks receive the least amount of scrutiny, since their contents were likely already scanned by AV on disk.
Since image section views are usually where executable code resides, what's stopping an attacker from overwriting it with shellcode? The answer lies in a mechanism called "copy-on-write". When a DLL is mapped into memory, Windows employs a resource sharing technique called "copy-on-write" to optimize memory management. Subsequent loads of the same file will be backed by the same shared memory pages, with a transparent "copy" made if a process tries to modify the shared region. The original page remains unmodified, while Windows creates a private copy of the page for the process to write to. This reduces overhead and avoids unnecessary duplication of unmodified pages across multiple processes. Since executable code segments are marked as PAGE_EXECUTE_WRITECOPY , once an attacker modifies the page, the Shared bit in that page's extended working set information will be cleared 2 . This detection methodology (unshared MEM_MAPPED or MEM_IMAGE pages) can also be used to detect hooks and other memory patching, like disabling ETW.
One injection technique that works around these limitations is Process Doppelgänging [T1055.013] / Phantom DLL Hollowing . This technique abuses transactional NTFS (TxF) by opening an isolated file handle to alter the .text section of a DLL. This is done without ever flushing the changes back to disk, and occurs before the view is mapped into memory, making detection much more difficult. However, due to the isolation provided by the TxF transaction, this technique has the unique side effect causing calls to GetMappedFileNameW() to fail when attempting to query the name of the file associated with the image region. Additionally, the MmDoesFileHaveUserWritableReferences() function can be used by an EDR to determine if there are any writable references to the file object of a section (broken section coherency).
Other detection logic is largely focused on private memory. Using the data sources described earlier, EDRs have visibility into the parameters passed to memory management functions. This is sufficient to cover certain anomalous behaviors, like private RWX allocation or fluctuating memory protections (RW I RX). Contextual behaviors like these can elevate a process' risk score, and trigger further investigation. One such investigative tool is memory scanning. Since full memory scanning is far too resource intensive, EDRs often rely on event-triggered scans. For example, an EDR could choose to scan the buffer being written to memory if the pages being written to are executable. These scans can be used to detect PE Injection [T1055.002] by searching for a PE header ( MZ ) found in private memory, which indicates that an executable file was loaded in an abnormal way (and not via LoadLibrary() ). Another potential indicator is buffer size. As noted in the previous section, VirtualAlloc() rounds the allocation up to the minimum page size. Since most programs don't need to write large chunks of memory to a remote process, the vast majority of legitimate remote memory operations are performed on a single page.
Shellcode, on the other hand, can be much larger — especially when using an off-the-shelf framework like Metasploit or Cobalt Strike. After staging the payload in memory, the final step is to trigger execution. There's a wide variety of execution primitives, with the most common being CreateRemoteThread() / RtlCreateUserThread() / NtCreateThreadEx() . These functions simply create and insert a new thread into the target process, with the specified starting address. In a "classic" DLL Injection [T1055.001] , LoadLibraryA() is used as the starting address. Using the PsSetCreateThreadNotifyRoutine kernel callback, these techniques can be detected by determining if the starting address points to private memory or a suspicious trampoline function.
Another method is to hijack the state of an existing thread using the SetThreadContext() API ( Thread Execution Hijacking [T1055.003] ). This function modifies the register state (context) of a suspended thread, and can be used to redirect execution flow by directly setting the RIP register. However, it is primarily only used by debuggers and can be caught using API hooks or THREATINT_SETTHREADCONTEXT_REMOTE ETW-TI events.
Existing threads can also be used to execute an asynchronous procedure call (APC) by using QueueUserAPC() or NtQueueApcThread() to insert a user-mode APC object into the thread’s APC queue ( Asynchronous Procedure Call [T1055.004] ). This will cause the thread to execute the specified APC the next time it enters an alertable state. ETW-TI also provides visibility into these events via THREATINT_QUEUEUSERAPC_REMOTE logs.
Message hook functions, like SetWindowsHookEx() or NtUserSetWindowsHookEx() , are yet another option. These functions install a custom hook procedure into the hook chain, which triggers execution whenever the specified WH_* event occurs 3 . Due to their widespread abuse by keyloggers, defensive tooling often has the capability to detect suspicious message hooks by enumerating gSharedInfo members, performing API hooking, or even keeping a stateful list to determine anomalies 4 .
Lastly, a large class of injection methods involve overwriting a pointer to code (often a callback). These methods take advantage of the fact that many pointers to code are stored in writable memory, and overwriting these pointers can redirect the execution flow to arbitrary locations when the callback is triggered. This includes attacks that abuse Window subclassing ( PROPagate ), window message handlers ( ConsoleWindowClass ), PE entry points ( AddressOfEntryPoint ), thread local storage (TLS) callbacks ( Thread Local Storage [T1055.005] ), control signal handler callbacks ( Ctrl-Inject ), the KernelCallbackTable PEB member, and many many more. While there's an almost innumerable amount of execution primitives, most can be detected using a combination of API hooking, validating the target address of a remote memory writes, as well as monitoring new threads that originate from unbacked memory.
Technically , this callback isn't invoked until the first thread is created and inserted into the process, see NtCreateProcessEx() https://learn.microsoft.com/en-us/windows/win32/api/memoryapi/nf-memoryapi-virtualquery#remarks 4. Practical Deployment, Analysis & Case Studies https://learn.microsoft.com/en-us/windows/win32/api/winuser/nf-winuser-setwindowshookexa#parameters Adversaries may inject dynamic-link libraries (DLLs) into processes in order to evade process-based defenses as well as possibly elevate privileges. DLL injection is a method of executing arbitrary code in the address space of a separate live process.
DLL injection is commonly performed by writing the path to a DLL in the virtual address space of the target process before loading the DLL by invoking a new thread. The write can be performed with native Windows API calls such as VirtualAllocEx and WriteProcessMemory , then invoked with CreateRemoteThread (which calls the LoadLibrary API responsible for loading the DLL). [1] Variations of this method such as reflective DLL injection (writing a self-mapping DLL into a process) and memory module (map DLL when writing into process) overcome the address relocation issue as well as the additional APIs to invoke execution (since these methods load and execute the files in memory by manually preforming the function of LoadLibrary ). [2] [1] Another variation of this method, often referred to as Module Stomping/Overloading or DLL Hollowing, may be leveraged to conceal injected code within a process. This method involves loading a legitimate DLL into a remote process then manually overwriting the module's AddressOfEntryPoint before starting a new thread in the target process. [3] This variation allows attackers to hide malicious injected code by potentially backing its execution with a legitimate DLL file on disk. [4] Running code in the context of another process may allow access to the process's memory, system/network resources, and possibly elevated privileges. Execution via DLL injection may also evade detection from security products since the execution is masked under a legitimate process.
Aria-body has the ability to inject itself into another process such as rundll32.exe and dllhost.exe. [5] BackdoorDiplomacy has dropped legitimate software onto a compromised host and used it to execute malicious DLLs. [6] BADHATCH has the ability to execute a malicious DLL by injecting into explorer.exe on a compromised machine. [7] The Bumblebee loader can support the Dij command which gives it the ability to inject DLLs into the memory of other processes. [9] [10] During C0015 , the threat actors used a DLL named D8B3.dll that was injected into the Winlogon process. [11] Carberp 's bootkit can inject a malicious DLL into the address space of running processes. [12] ComRAT has injected its orchestrator DLL into explorer.exe. ComRAT has also injected its communications module into the victim's default browser to make C2 connections appear less suspicious as all network connections will be initiated by the browser process. [16] [17] Duqu will inject itself into different processes to evade detection. The selection of the target process is influenced by the security software that is installed on the system (Duqu will inject into different processes depending on which security suite is installed on the infected host). [22] Emotet has been observed injecting in to Explorer.exe and other processes. [27] [28] [29] FinFisher injects itself into various processes depending on whether it is low integrity or high integrity. [30] [31] The FunnyDream FilepakMonitor component can inject into the Bka.exe process using the VirtualAllocEx , WriteProcessMemory and CreateRemoteThread APIs to load the DLL component. [32] IronNetInjector has the ability to inject a DLL into running processes, including the IronNetInjector DLL into explorer.exe. [38] If running in a Windows environment, Kazuar saves a DLL to disk that is injected into the explorer.exe process to execute the payload. Kazuar can also be configured to inject and execute within specific processes. [39] Kimsuky has the ability to load DLLs via reflective injection by allocating memory using VirtualAllocEx() , then decrypting a DLL with WriteProcessMemory() and invoking execution through CreateRemoteThread() . [40] Leviathan has utilized techniques like reflective DLL loading to write a DLL into memory and load a shell that provides backdoor access to the victim. [44] Lizar has used the PowerKatz plugin that can be loaded into the address space of a PowerShell process through reflective DLL loading. [45] Matryoshka uses reflective DLL injection to inject the malicious library and execute the RAT. [47] Metamorfo has injected a malicious DLL into the Windows Media Player process (wmplayer.exe). [51] The Netwalker DLL has been injected reflectively into the memory of a legitimate running process. [52] PipeMon can inject its modules into various processes using reflective DLL loading. [53] PowerSploit contains a collection of CodeExecution modules that inject code (DLL, shellcode) into a process. [56] [57] An executable dropped onto victims by Putter Panda aims to inject the specified DLL into a process that would normally be accessing the network, including Outlook Express (msinm.exe), Outlook (outlook.exe), Internet Explorer (iexplore.exe), and Firefox (firefox.exe). [60] Qilin can inject pwndll.dll, a patched DLL from the legitimate DLL WICloader.dll, into svchost.exe for continuous execution.
[61] After decrypting itself in memory, RARSTONE downloads a DLL file from its C2 server and loads it in the memory space of a hidden Internet Explorer process. This "downloaded" file is actually not dropped onto the system. [63] Sagerunex is designed to be dynamic link library (DLL) injected into an infected endpoint and executed directly in memory.
[67] SDBbot has the ability to inject a downloaded DLL into a newly created rundll32.exe process. [34] SombRAT can execute loadfromfile , loadfromstorage , and loadfrommem to inject a DLL from disk, storage, or memory respectively. [58] Stuxnet injects an entire DLL into an existing, newly created, or preselected trusted process. [71] Sykipot injects itself into running instances of outlook.exe, iexplore.exe, or firefox.exe. [72] TajMahal has the ability to inject DLLs for malicious plugins into running processes. [76] TONESHELL has used DLL injection to execute payloads received from the C2 server. [77] Tropic Trooper has injected a DLL backdoor into dllhost.exe and svchost.exe. [78] [79] 5. Performance Evaluation & Extended Technical Observations Turla has used Metasploit to perform reflective DLL injection in order to escalate privileges. [80] [81] Wizard Spider has injected malicious DLLs into memory with read, write, and execute permissions. [83] [84] Some endpoint security solutions can be configured to block some types of process injection based on common sequences of behavior that occur during the injection process.
Detects DLL injection through correlation of memory allocation and writing to remote process memory (e.g., VirtualAllocEx, WriteProcessMemory), followed by remote thread creation (e.g., CreateRemoteThread) that loads a suspicious or unsigned DLL using LoadLibrary or reflective loading. Threat Monitoring, Detection Engineering, and Incident Investigation for MITRE ATT&CK T1055 This project demonstrates how a SOC Engineer can detect, monitor, investigate, and respond to DLL Injection-related activities using: The objective is to build a detection pipeline capable of identifying suspicious process access, remote thread creation, and malicious DLL loading behaviors commonly associated with Process Injection (T1055).
Successfully implemented a SOC detection lab capable of identifying suspicious process-access and DLL-loading behaviors, providing visibility into potential Process Injection techniques while supporting threat hunting, incident response, and detection engineering activities. Threat Monitoring, Detection Engineering, and Incident Investigation for MITRE ATT&CK T1055 A cybersecurity lab project demonstrating DLL Injection attack detection using Wazuh, Sysmon, and MITRE ATT&CK T1055.001 techniques.
Dynamic-Link Library (DLL) injection is a process injection technique used by attackers to execute malicious code within the address space of another process. This technique is commonly associated with privilege escalation and defense evasion activities and is categorized under MITRE ATT&CK technique T1055.001. This project demonstrates how Wazuh and Sysmon can be used to detect DLL injection activity in a Windows environment. A controlled lab environment was created to simulate the attack using InjectProc, while Sysmon generated the corresponding events and Wazuh correlated and generated alerts based on the observed behavior.
Attacker / Victim Machine (Windows) -> InjectProc.exe + hello-world-x64.dll -> Sysmon Event Logs -> Wazuh Agent -> Wazuh Manager -> Wazuh Dashboard Alert Before performing the attack simulation, the following components were installed and configured: This section describes the step-by-step setup of the lab environment used to simulate and detect DLL Injection attacks.
The required Visual C++ runtime was installed on the Windows endpoint to ensure proper execution of InjectProc and related binaries. The InjectProc tool and payload ( hello-world-x64.dll ) were downloaded and placed in a dedicated working directory. The Wazuh agent was installed on the Windows endpoint and successfully connected to the Wazuh manager.
Sysmon was installed using Sysinternals page Sysmon tool with a predefined configuration file to monitor system activity, including process creation and remote thread injection events. Sysmon logs were integrated into Wazuh by modifying the agent configuration file (ossec.conf).Restart the Wazuh agent to apply the changes.
Add the following detection rules to the /var/ossec/etc/rules/local_rules.xml file on the Wazuh manager: After completing the setup, a DLL injection attack was executed using InjectProc to simulate malicious process injection behavior. Sysmon generated Event ID 8 (CreateRemoteThread), which is a strong indicator of process injection.
Wazuh successfully detected the malicious behavior using built-in rules and generated an alert. This lab demonstrated how DLL Injection attacks can be detected using Sysmon for telemetry generation and Wazuh for log analysis and alerting. The implementation successfully mapped malicious behavior to MITRE ATT&CK framework, providing visibility into process injection techniques in a Windows environment.
A cybersecurity lab project demonstrating DLL Injection attack detection using Wazuh, Sysmon, and MITRE ATT&CK T1055.001 techniques. Process injection is the backbone of modern malware evasion — shellcode injected into svchost.exe, code running from NTDLL, and Cobalt Strike sleeping in a hollowed process. This guide covers the host-based artifacts, Sigma rules, and KQL queries for detecting T1055 sub-techniques across Windows environments.
Process injection is one of the most abused techniques in post-exploitation tradecraft. It lets attackers execute code inside a legitimate, trusted process — appearing as svchost.exe, explorer.exe, or lsass.exe in the process tree rather than malware.exe. Nearly every major C2 framework (Cobalt Strike, Brute Ratel, Sliver, Havoc) uses injection as a core evasion mechanism. So does most commercial spyware and a substantial fraction of commodity malware.
T1055 encompasses a broad category, but the sub-techniques that matter most for defenders are: This guide focuses on detection logic for Windows endpoints — the primary target in enterprise environments. Windows automatically loads the DLL and runs its DllMain . The injected thread appears to belong to the target process. The hollowed process has the legitimate name and parent, but its memory sections contain attacker code.
The simplest form: allocate, write, and execute a shellcode blob without needing a DLL or PE header. Often used with reflective loading to avoid disk writes entirely. Modern C2 beacons (Cobalt Strike’s default sleep technique) use this pattern along with memory obfuscation to hide from memory scanners. Rule 3: Shellcode via VirtualAllocEx + WriteProcessMemory + CreateRemoteThread Sequence Modern attackers have adapted injection techniques to evade EDR hooks placed in NTDLL: Direct syscalls : Instead of calling NtCreateThread via NTDLL (where EDR hooks live), malware resolves the syscall number directly and invokes the kernel without going through the hooked DLL. Sysmon won’t log these; you need kernel-level ETW or a hypervisor-based solution.
Module stomping : Overwriting a legitimate, already-loaded DLL’s code sections (rather than allocating new RWX memory) avoids the RWX allocation indicator. Memory scanning tools detect this by checking whether in-memory DLL content matches the on-disk version. Sleep obfuscation : Cobalt Strike’s Ekko and similar techniques encrypt the beacon’s memory when sleeping and decrypt it only when active, evading memory scanners that run during sleep intervals.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/BlackEnergy • https://en.wikipedia.org/wiki/Rootkit • https://en.wikipedia.org/wiki/BattlEye • https://morimori-dev.github.io/en/posts/tech-dll-injection-guide/ • https://dev.to/tiger_smith_9f421b9131db5/modern-edr-countermeasures-fundamentals-and-practical-guide-to-user-mode-fu nction-hooking-3a26 • https://github.com/carbon-evolution/process_injection_detector • https://github.com/bappy-cybersec142225/-DLL-Injection-Attack-Detection-using-Wazuh-SIEM/blob/main/README.md • https://blog.blacklanternsecurity.com/p/detecting-process-injection • https://attack.mitre.org/techniques/T1055/001/ • https://github.com/bappy-cybersec142225/DLL-Injection-Detection-Lab-with-Wazuh-SIEM
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Dll Injection Detection And Process Monitoring Tool.
[*] Metasploit Scan Running on Target Subnet for Dll Injection Detection And Process Monitoring Tool... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |