Complete Technical Paper Content — Docker Container Forensic Investigation Tool Project
Overview & System Context
Docker Container Forensic Investigation Tool Project: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9547 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Inert gas asphyxiation is a form of asphyxiation that results from breathing a physiologically inert gas in the absence of oxygen, or a low amount of oxygen (hypoxia), rather than atmospheric air (which is composed largely of nitrogen and oxygen).
Examples of physiologically inert gases, which have caused accidental or deliberate death by this mechanism, are argon, xenon, helium and nitrogen. The term "physiologically inert" is used to indicate a gas that has no toxic or anesthetic properties and does not act upon the heart or hemoglobin. Instead, the gas acts as a simple diluent to reduce the oxygen concentration in inspired gas and blood to dangerously low levels, thereby eventually depriving cells in the body of oxygen. According to the U.S. Chemical Safety and Hazard Investigation Board, in humans, "breathing an oxygen deficient atmosphere can have serious and immediate effects, including unconsciousness after only one or two breaths. The exposed person has no warning and cannot sense that the oxygen level is too low." In the US, at least 80 people died from accidental nitrogen asphyxiation between 1992 and 2002. Hazards with inert gases and the risks of asphyxiation are well-established. An occasional cause of accidental death in humans, inert gas asphyxia has been used as a suicide method. Inert gas asphyxia has been advocated by proponents of euthanasia, using a gas-retaining plastic hood device colloquially referred to as a suicide bag. Nitrogen asphyxiation has been approved in some places as a method of capital punishment. In the world's first instance of its use, on January 25, 2024, Alabama executed convicted murderer Kenneth Eugene Smith via this method. It has since been used seven more times, six times in Alabama and once in Louisiana, which first used it on March 18, 2025. Alternatively, the term hypoxia has been used but this usage is flawed given that hypoxia does not necessarily imply death. On the other hand, asphyxiation is technically incorrect given respiration continues and the carbon dioxide metabolically produced from the oxygen inhaled prior to inert gas asphyxiation can be exhaled without restriction, which can prevent acidosis and the strong urge to breathe caused by hypercapnia.
When the duration of over-ventilation with nitrogen was greater than 8–10 sec the subject reported a transient dimming of vision. In the experiments in which nitrogen breathing was carried out for 15–16 sec the subject experienced some general clouding of consciousness and impairment of vision. Vision was frequently lost in these experiments for a short period. In the few experiments in which nitrogen was breathed for 17–20 sec unconsciousness supervened and was accompanied on most occasions by a generalized convulsion. The duration of the interval between the start of over-ventilation with nitrogen and the onset of symptoms was 12–14 sec. The study did not report how much discomfort the subjects felt.
Controlled atmosphere killing (CAK) or controlled atmosphere stunning (CAS) is a method for slaughtering or stunning animals such as swine, poultry, or cane toads by placing the animals in a container in which the atmosphere lacks oxygen and consists of an asphyxiant gas (one or more of argon, nitrogen or carbon dioxide), causing the animals to lose consciousness. Argon and nitrogen are important components of a gassing process which seem to cause no pain in some species, and for this reason many consider some types of controlled atmosphere killing more humane than other methods of killing. Other species, such as pigs, show aversion to highly concentrated nitrogen and argon. Most animals are stunned by carbon dioxide.
If carbon dioxide is used, controlled atmosphere killing is not the same as inert gas asphyxia, because carbon dioxide at high concentrations (above 5%) is not biologically inert, but rather is toxic and also produces initial distress in some animal species. The addition of toxic carbon dioxide to hypoxic atmospheres used in slaughter without animal distress is a complex and highly species-specific matter, which also depends on the concentration of carbon dioxide.
Use of inert gas for suicide was first proposed by a Canadian, Bruce Dunn. Dunn commented that "...the acquisition of a compressed gas cylinder, an appropriate pressure reducing regulator, and suitable administration equipment... [was] not inaccessible to a determined individual, but relatively difficult for a member of the public to acquire casually or quickly". Dunn collaborated with other researchers, notably the Canadian campaigner John Hofsess, who in 1997 formed the group "NuTech" with Derek Humphry and Philip Nitschke. Two years later, NuTech had streamlined Dunn's work by using readily-available party balloon cylinders of helium. The method of suicide based on self-administration of helium in a bag, a colloquial name being the "exit bag" or suicide bag, has been referenced by some medical euthanasia advocacy groups.
Originally, such bags were used with helium, and 30 deaths were reported with use of them from 2001 to 2005, and another 79 from 2005 to 2009. This suggested to one set of reviewers that the popularity of the technique was increasing, as also did the increase in helium suicides in Sweden during the latter half of the same decade. After attempts were made by authorities to control helium sales in Australia, a new method was introduced that instead uses nitrogen. Nitrogen became the main gas promoted by euthanasia advocates, such as Philip Nitschke, who founded a company called Max Dog Brewing in order to import canisters of nitrogen into Australia. Nitschke stated that the gas cylinders can be used for both brewing and, if required, to end life at a later stage in a "peaceful, reliable [and] totally legal" manner. Nitschke said that nitrogen is "undetectable even by autopsy, which was important to some people". Nitschke used 3D printing to build a "Sarco pod" device that fills with nitrogen at the push of a button, claiming to cause its user to become unconscious within a minute and then die of oxygen deprivation.
Figure 1: kasmweb/forensic-osint - Docker Image Law enforcement in Australia is one of the three major components of the country's justice system, along with courts and corrections. Law enforcement officers are employed by all three levels of government – federal, state/territory, and local. Federally, the primary law enforcement agency is the Australian Federal Police (AFP), which has a wide mandate to enforce Australian criminal law and protect its national interests. There is also a number of other agencies that have powers confined to specific areas, such as customs and immigration (Australian Border Force), and white-collar crime (Australian Taxation Office, Australian Competition & Consumer Commission, Australian Securities & Investments Commission). Each branch of the Australian Defence Force (ADF) has its own military police which operates under the Joint Military Police Unit (JMPU).
The ADF Investigative Service also forms part of the JMPU and is the primary agency for complex investigations that fall under the Defence Force Discipline Act. General law enforcement duties are generally the responsibility of state police forces, who are in turn responsible to a state government minister (usually a Minister for Police). These forces carry out uniformed policing throughout the entire state in which they operate. Other state government agencies may also have investigative or enforcement powers for specific offences within their purview, such as fisheries. The Northern Territory is the only Australian territory with its own police force, but in Australia's other territories (including the Australian Capital Territory) law enforcement is handled by the Federal Government, specifically ACT Policing under the Australian Federal Police. Local governments may also employ their authorised officers, commonly known as council rangers, to enforce local government by-laws or certain state laws pertaining solely to the local government jurisdiction in which they're employed. Council rangers do not have full police powers unless they are sworn as special constables. State police officers and Australian Federal Police officers routinely carry firearms, other state and federal law enforcement officers may carry firearms or other items for personal defence depending on their agency or the condition in which they're deployed. While on duty, an armed law enforcement officer's duty belt generally consists of a handgun, Taser, expandable baton, pepper spray, a set of handcuffs, ammunition magazines, gloves, torch, and a two-way radio.
The Australian Border Force is responsible for customs and immigration enforcement and border protection at Australia's ports as well as in Australian waters, and conducts investigations where the AFP does not have primary jurisdiction. Unlike AFP Officers, Border Force Officers do not have fully vested federal police powers, and can only exercise arrest and detain powers at airport and seaport jurisdictions. They may, however, detain persons for state or federal crimes or warrants until that person can be presented to a federal or state law enforcement officer with the appropriate powers. Australian Border Force officers have the authority to carry firearms when trained. In practice, only maritime, counter-terrorism, and investigation officers carry firearms.
Military Police, also known as Service Police, are the law enforcement branches of the services of a military tasked with enforcing and investigating offences violating military law. In Australia, each branch of the Australian Defence Force maintains its independent police force made up of military personnel from that service. In the Australian Army, the Royal Australian Corps of Military Police conducts general law enforcement duties including security on military installations, investigations and close personal protection. In the Royal Australian Navy, policing functions are undertaken by Coxswains. In the Royal Australian Air Force, security and law enforcement duties are undertaken by Security Forces and Airfield Defence personnel.
Along with the independent service police forces is the Australian Defence Force Investigative Service (ADFIS), a special ADF unit made up of Investigators from each service's police and tasked with investigating more serious military offences. All ADF policing agencies come under the umbrella of the Joint Military Police Unit (JMPU), an agency of the Australian Department of Defence led by the Provost Marshal and tasked with providing specialised military policing services and supporting civilian police in defence matters.
Each state, as well as the Northern Territory, is responsible for maintaining its police force which is responsible for policing at the state and local levels. This involves general law and order, forensics, traffic policing, major crime, anti-terrorism branches, water police, search and rescue and in some states transit police. Local policing in the Australian Capital Territory, Jervis Bay Territory and Australian external territories is contracted to the Australian Federal Police (AFP). Each state has a Department of Corrections which looks after the jails and prisoners. In some states, local governments employ by-laws officers or rangers to enforce local by-laws or ordinances relating to such matters as parking, dog ownership, retailing, littering, or water usage.
These local government officers are not considered to be police forces as they generally only have the power to issue fines and do not have the same powers as state police. They may rely upon appointment as a special constable or legislated powers for their authority. Figure 2: Scan Container Images for Vulnerabilities with Docker Scout - The New Stack State police also perform certain functions on behalf of the Australian government such as the enforcement of various Commonwealth Acts and regulations in conjunction with the Australian Federal Police and other Commonwealth officers. The Australian Capital Territory (ACT) and Jervis Bay Territory are serviced by the Australian Federal Police (AFP) ACT Policing.
The AFP also provide local policing the Australian external territories. While ACT Policing is under the jurisdiction of the Australian Federal Police, the following policing agencies are regulated by their respective state or territory government and are highly visible: In addition to the Australian Fisheries Management Authority, each state and the Northern Territory have Fisheries officers authorised to enforce State and Federal fisheries laws within their state's jurisdiction. The powers of these fisheries officers vary from State to State but generally, these officers have the power to board vessels, search vehicles, vessels, and persons and conduct arrests all in relation to fisheries laws. In some States, such as New South Wales, fisheries officers are authorised to carry personal defense equipment like their Federal counterparts.
Council rangers are officers employed by local government areas in Australia to enforce the by-laws (local laws in Western Australia); of those local governments and a limited range of state laws relating to such matters as litter control, animal control, dog and cat laws, fire control, off-road vehicles, emergency management, and parking. Unless they are also sworn in as special constables rangers do not have full police powers. Council rangers are also referred to as local laws officers in some of Australia's eastern states. Most Council rangers have the power to issue fines that do not exceed a certain amount.
The Australia New Zealand Policing Advisory Agency (ANZPAA) was established in October 2007. ANZPAA is a joint initiative of the Australian and New Zealand Police Commissioners and is funded by contributions to Australia and New Zealand Police jurisdictions. ANZPAA is a non-operational policing agency that provides strategy and policy advice, and secretarial services to the ANZPAA Board on cross-jurisdictional policing initiatives that help enhance community safety and security. ANZPAA's strategic direction is set by ANZPAA’s board and the Australia New Zealand Council of Police Professionalisation (ANZCoPP, formerly Australasian Police Professional Standards Committee, APPSC). The Australasian Police Professional Standards Committee (APPSC) was an organisation that served all police jurisdictions around Australia and New Zealand. It was the body for police education and training in Australia and New Zealand; the council comprising each of the police commissioners from Australia and New Zealand along with the president of the Police Federation of Australia and the president of the New Zealand Police Association. On 9 November 2007, APPSC roles and functions were amalgamated into ANZPAA. In 2013, APPSC was retitled to the Australia New Zealand Council of Police Professionalisation. Crime Stoppers programs run in each state and on a national level. These programs collect information about crimes and pass them on to police, ensuring that the community can participate in fighting crime.
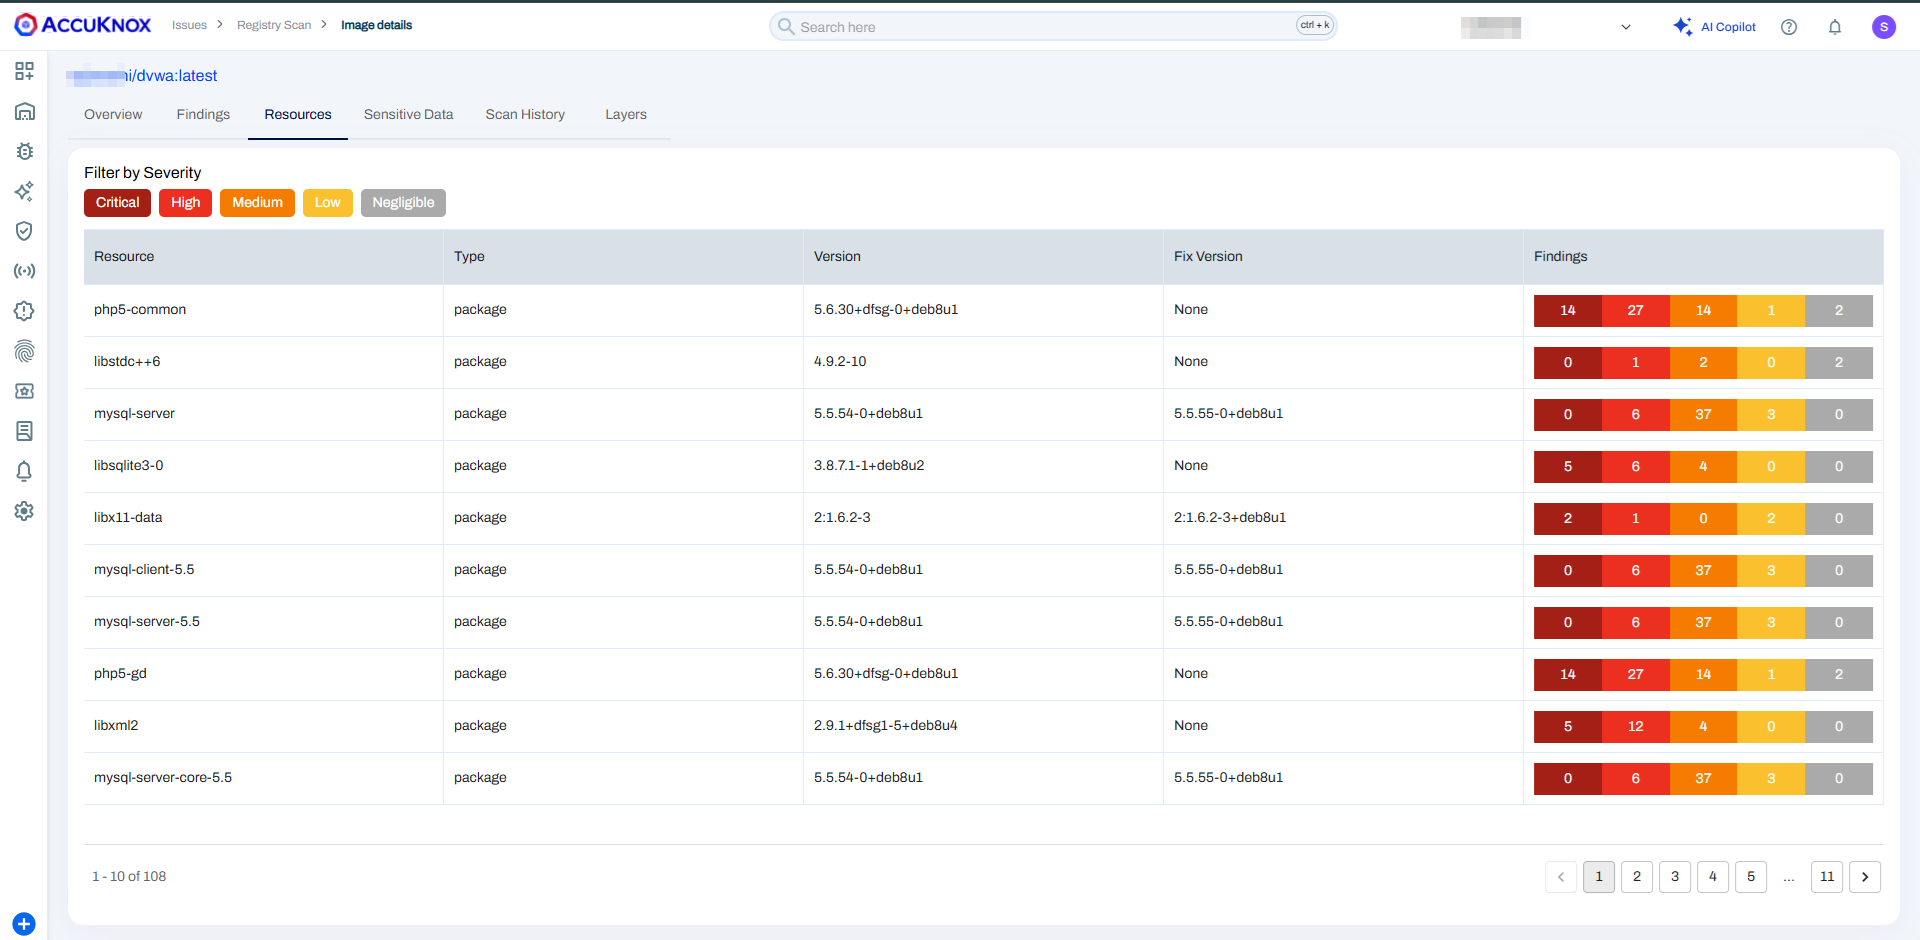
Figure 3: Detecting and Blocking Vulnerable Docker Images with AccuKnox Container ... Involvement of state law enforcement in suppressing Indigenous resistance to colonisation has been widely controversial. The New South Wales Mounted Police were formed following the Bathurst War between British colonists and the Wiradjuri people in 1824, and in modern Australia continue to be deployed as part of police presence at peaceful protests in many states.
Across colonial Australia, police forces were mobilised in violent conflict during the Australian frontier wars and were heavily involved in the many Indigenous fatalities that led to sharp decline of Indigenous populations since colonisation. The Queensland Native Police Force alone were responsible for an estimated 24,000 "violent Aboriginal deaths" between 1859 and 1897, as calculated by professor Raymond Evans in 2009. In the Northern Territory, the Aboriginals Ordinance 1918 (Cth) allowed forced recruitment of Indigenous people and legal non-payment of wages, granting Protectors and police the right to uphold this arrangement.
By agreement between the various commissioners, most police cars in Australia are predominantly white, with a blue and white Sillitoe tartan checkered strip on the side. Historically, police fleets were composed predominantly of domestically built models such as the Holden Commodore and Ford Falcon. With the demise of Holden and Ford production in Australia, fleets have grown to include models such as the Chrysler 300, BMW 5 Series, Kia Stinger, Volkswagen Passat, Mercedes-Benz E-Class, and Hyundai Sonata. Prisoner transport vehicles are based on light commercial vehicles such as the Ford Ranger, Toyota Hilux, Holden Colorado, Mercedes Vito, or Volkswagen Transporter. A wide range of vehicles are used for unmarked purposes to blend in with civilian vehicles. Emergency vehicle lighting differs across Australian jurisdictions and may vary based on law enforcement functions (e.g. parks compliance, fisheries, local law enforcement, etc.). However, primary law enforcement agencies utilise blue and red flashing warning lights. Most Australian police services have mounted police units that are prominently used for ceremonial purposes, although in New South Wales, South Australia, Western Australia, and Victoria the mounted police also undertake operational policing duties.
Australian court hierarchy Crime in Australia Immigration detention in Australia List of Australian prisons Punishment in Australia Reasonable and probable grounds in Australia Terrorism in Australia The Moroccan mafia (Arabic: IIIII IIIII, Berber languages: IIIII IIIIIIIII, Dutch: Mocro Maffia) is a collection of criminal organisations that are primarily made up of people of Moroccan descent. These organisations are specialised in trafficking large quantities of cocaine and synthetic drugs through Spain, Portugal, the Netherlands and Belgium, from where it is distributed to the rest of the European continent, thus being one of the most dominant participants in the European drug trade. In broader terms of Moroccan organised crime, this also includes northern Moroccan hash kingpins and southern Moroccan traffickers who play a key-role in the African drug trade, as well as in human trafficking, arms trafficking and the trafficking of contraband such as cigarettes and alcohol, although they are seen as a separate entity from the Mocro Maffia who are mostly active in the northern part of Morocco and Europe. Moroccan criminal networks in Europe have mainly been active since the 1990s, and consist mostly of Belgian and Dutch citizens with a Moroccan immigrant background. These criminal networks have privileged relationships with Colombian and Mexican cartels, and they often import drugs into Europe through the harbours of Antwerp, Rotterdam and Algeciras. The Moroccan mafia does not, however, include Moroccan Jewish crime families such as the Abergil crime family as well as the Abutbul, and Domrani clans, who are rather considered to be a part of the Israeli mafia. That said, Moroccan-Israeli mafia clans are known for having collaborated closely together with the Mocro Maffia in the Netherlands and Belgium, especially in the worldwide distribution of synthetic drugs such as MDMA. This is mostly due to the fact that the Netherlands is the largest producer of MDMA and amphetamines in the world.
Moroccans (mainly from the Rif region) have migrated in large waves to the Benelux, who were invited to these countries as guest workers. This dense and rather late emigration in the 1960s and 1970s eventually never stopped, and many of the invited guest workers decided to build a new life in the Benelux instead. Most of these Moroccan immigrants came from the Rif region, which is one of the poorest regions in all of Morocco. The Rif region was, and still is a very rural and little urbanised area, which had very few schools for an excessive time, whether in Arabic or French. This Mediterranean peasant and mountain society is quite comparable to other Mediterranean regions like Corsica, Sicily, Sardinia, Calabria and the Aurès. It is characterised by very strong community relationships, a spirit of silence (omertà) and self-governance. This mountainous region has always stayed somewhat uncontrollable. After decolonisation, more than tens of thousands of Riffians lost their jobs in the vineyards and farms of Morocco and Algeria. Afterward, this process continued, as if from the 1970s and onwards, many of these migrated Riffians have lost their jobs in the European mines and steel industry as well. Since then this workforce has converted on a massive scale into different ways of commerce and businesses, both legal and illegal, with the illegal side, in particular, being the smuggling of cannabis. The earned money was reinvested in cafes, small businesses and real estate in Morocco. The ones who gained some wealth, reinvested into the economy around the Costa del Sol region in southern Spain. The Riffian diaspora has thus spread its economic system throughout Europe. During the 1960s, Belgium and the Netherlands, unlike other countries in Western Europe, had no North African colonial past, welcomed massive Moroccan immigration from northern Morocco to work in the mines, iron and steel industry in Wallonia. Afterward, this process continued in Flanders, and the Netherlands, in the midst of an economic boom. The drug trade eventually followed these communities in exile, from Morocco to the Netherlands, through Spain, France, and Belgium. During the 1980s, De Pijp and Bos en Lommer districts located in Amsterdam, housed the most Moroccan immigrants. During this period, many Dutch-Moroccans saw this as an opportunity to export hashish from the Ketama mountains in Morocco to the Netherlands, often aboard their old vehicles such as Mercedes-Benz S-Class cars. It was around this time in the mid-1980s that the modern mafia structures started to evolve. The traffickers were used to crossing borders, carrying weapons, and they were known in Morocco to be very violent.
The Moroccan state has abandoned and neglected the Rif region for many years by refusing to invest in the infrastructure, which has prompted most Moroccans from cities like Al Hoceïma and Nador to devote themselves entirely to the production of Hashish. In the 1980s, cocaine gained a lot of popularity. These were also the years when Dutch Penose crime syndicates were inspiring the Moroccan community to enter the hard drug business, which would make them eventually more money than hashish.
Cocaine is delivered daily in containers to the Port of Antwerp, before it is distributed throughout Europe by Dutch- and Belgian-Moroccan drug traffickers. The Port of Antwerp, which is considered to be the largest port for cocaine import in Europe, is dominated and controlled by 5 Moroccan drug clans who export these large quantities of cocaine to the European mainland. Gangs preferred to use the Port of Antwerp as a trafficking destination for drugs due to the lawlessness within the port. Additionally, with an area of 12,068 hectares (~24,000 football fields), the scale of the port is what makes it attractive to criminals. Within a single cargo ship, it is possible to place up to 15,000 containers. Customs officers use scanners, that are only able to scan a single container in 5 minutes, which makes full control over the entire cargo pretty much impossible. This makes drug trafficking easier for gangs operating in the port. What also attracted the gangs, is the fact that the Port of Antwerp is considered to be an "open port". This is not the case for the Port of Rotterdam, which is closed off daily and under high surveillance. Bart De Wever, at the time mayor of Antwerp (since 2025 Prime Minister of Belgium), declared in 2017 that dozens of surveillance cameras are destroyed daily by young people between the age of 13 and 15 from neighbourhoods in Antwerp. They receive in exchange a sum of up to €5,000 from traffickers to prevent the police from investigating the drug trade that takes place in these neighbourhoods.
You have to be careful, a lot of young people go to the port to see how everything works. You have to know the exits by heart in case you get chased by enemies or overseers. Communication between networks of the Moroccan mafia was mostly exercised by the use of Blackberry smartphone messaging equipped with PGP technology. On 19 April 2016, the Canadian authorities intervened a hosting company with the aim of decrypting the Dutch telecommunication servers of Ennetcom. The servers contained millions of messages that were sent through Ennetcom. The cybercrime investigators of the Netherlands Forensic Institute finally managed to decrypt the messages in Canada. When the messages were deciphered, the investigators found out that the messages were all written in Tarifit, a language that was unknown to them. The names of the criminals were also replaced by nicknames. Between 2016 and 2018, the Dutch police forces investigated the nicknames to identify commanders as well as contract killers. Following the dismantling of the Ennetcom network, several criminal organisations have converted to the use of other encrypted communication services. Some criminals, including Saïd Razzouki, have been avoiding to communicate through electronic devices. Because of this, Razzouki could operate unknowingly for over 8 years before being arrested in Medellín by the DEA and FBI. Commanders or crime bosses are rarely found in Europe. They often stay hidden under the radar in places like Morocco, Latin-America, Arab states of the Persian Gulf, and Thailand.
EncroChat was a Europe-based communications network and service provider used primarily by organised crime members to plan criminal activities. Police infiltrated the network between March and June 2020 during a Europe-wide investigation. Other than major criminal activities such as large scale drug trafficking, the investigation exposed what would be a torture chamber alongside self made prisons, which were all built in shipping containers. It also exposed an excessive number of Dutch police uniforms owned by a criminal organisation. All of these were owned by a known rival of Ridouan Taghi, who allegedly used the torture chamber on members of Ridouan Taghi's organisation. Sky Global was also a communications network and service provider based in Vancouver, Canada. Its most notable products were the secure messaging application Sky ECC and crypto-phones. A significant number of users were part of international crime organisations involved in drug trafficking, and the company management was also suspected of collusion. In a series of raids against criminal organisations in several countries in early 2021, a part of Sky's infrastructure in western Europe was dismantled, and the US Department of Justice issued an arrest warrant against the company's CEO Jean-François Eap. The decryption of Sky ECC exposed in particular the inner workings of the Turtle clan and the El Ballouti clan. 27 tonnes of cocaine were also intercepted which were believed to be largely trafficked by these organisations, as well as corrupted police officers and lawyers who were involved.
Taghi allegedly wanted to kill Nabil B. as a punishment for being involved in killing the wrong person, which eventually led to Nabil B. collaborating with the Dutch authorities instead. As a result of this, Taghi ordered to kill Nabil B.'s innocent brother, who was a non-criminal, respected business owner in Amsterdam-Noord. Also Nabil B.'s lawyer Derk Wiersum was assassinated on the orders of Taghi, which eventually shocked the Netherlands. The Dutch parliament considered this as an attack on the Dutch legal system and the Dutch state, and a manhunt on Taghi by the Dutch authorities was eventually launched. In August 2020, six prominent lawyers in the Netherlands were accused of having delivered information to Ridouan Taghi's organisation in exchange for high sums of money. Their names were also added to the Marengo trials. T. Youssef one of Taghi's lawyers, and also his cousin, had been arrested on 8 October 2021, after being suspected of planning a jailbreak and smuggling messages out of prison to Taghi's organisation. In July 2021, the most prominent Dutch crime journalist Peter R. de Vries was assassinated after he left the studio of RTL Boulevard in Amsterdam, right after he appeared on a popular TV show. This assassination deeply shocked the Netherlands, with many politicians and celebrities sharing their condolences and speaking out on the increase of violence in the Netherlands. According to the Dutch authorities, all tracks lead to the already imprisoned Taghi. De Vries acted as a close confidant to Nabil B., the crown witness in the Marengo trial whose own brother, alongside his lawyer, were assassinated by Taghi's organisation for exposing their inner workings. The person who is suspected of killing De Vries, is a relative of the person who is in charge of Taghi's hit squad, which gives the Dutch authorities more reason to believe that Taghi's organisation is responsible for the killing. However, it is still unclear who gave the order of the shooting, since Taghi himself was already in a high-security prison at the time of the shooting.
In order to locate Razzouki, we needed the same techniques that were used 30 years ago to track down Pablo Escobar, because Razzouki applied the same routines in order to stay under the radar and escape every surveillance by the Colombian authorities. Razzouki did not use any technology or social media for eight years, to the extent that he did not update his family in the Netherlands of any news. Our investigators tracked him down by using intelligence planes that regularly flew over the city of Medellín with the aim of locating him. The last time the Elite Colombian Police Unit intervened in such a case, was during the operation carried out on 2 December 1993 to track down and shoot Pablo Escobar. Razzouki is suspected of drug trafficking, manufacture and possession of illegal substances, homicide, and terrorism. He had changed his physical appearance with the help of cosmetic surgery in order to look older. Razzouki belonged to a European criminal organisation of the Moroccan Mafia and was at the head of a group of traffickers from the Clan del Golfo cartel who were involved in the international export of cocaine, especially to Spain and Portugal. The Iranian government allegedly protected Taghi as he worked together with the Iranian secret service, to assassinate enemies of the Iranian state who were hiding out on European soil. On 16 December 2019, Taghi was arrested in his mansion in Dubai after a manhunt by the Moroccan and European authorities, and three days later he was deported to the Netherlands. He is currently incarcerated in the maximum security prison of Vught, and he is the main suspect in the current marengo trial, which is considered to be the largest criminal trial in Dutch history. He is facing life of imprisonment without the possibility of parole. The former president of Suriname, Dési Bouterse, is faced with corruption charges after cooperating with Taghi and his left hand man Mao R.
The Bouyakhrichan organisation was a criminal organisation led by Samir Bouyakhrichan (also known as Scarface), who was a billionaire entrepreneur and drug lord. Samir was specialised in large scale drug trafficking which he gained through collaborations with Colombian cartels. His organisation also operated in Spain, where it controlled parts of the Costa del Sol region. Bouyakhrichan was known for using his fortune to organise extravagant private parties by renting luxurious rooms in places like Dubai and Amsterdam, which included champagne, cocaine, and a lot of women and escorts. The guests were mostly Moroccan and British. One of these private parties was that of 30 June 2012, at the Apollo Hotel in Amsterdam. During this evening, many major drug lords were present, alongside the famous Dutch singer Gordon. Samir Bouyakhrichan was a known rival of the Taghi organisation, and he was also considered to be a rival of "Noffel". On 29 August 2014, at the age of 34, Samir was assassinated in southern Spain by 2 contract killers. The assassination was allegedly orchestrated by "Noffel"'s organisation. After his death, his organisation was taken over by his brother Karim Bouyakhrichan (also known as Taxi).
According to the Dutch authorities, Taghi and his associate Rico "El Rico" Eduardo Riquelme Vega were "hunting" for Karim to dismantle the Bouyakhrichan organisation. 2. System Architecture & Core Working Principles Mimoun "Rocky" Kaabouni, who was nicknamed "The Moroccan Escobar", was born in Ben Taïeb, a village in the province of Nador. He grew up in Hoensbroek, in the Netherlands, where he and his brother owned a coffeeshop named Happy Days.
While often visiting Amsterdam, he eventually started meeting big names within the Moroccan mafia with whom he maintained regular contact. Mimoun left the Netherlands for southern Spain and Romania, where he founded his own criminal organisation made up of Lithuanians and Colombians. Mimoun, who was already bringing in tons of cocaine through the ports of Antwerp, Rotterdam, Amsterdam, and Algeciras, wanted to create a new route in Romania through the port of ConstanIa.
He is currently serving a 19-year prison sentence in Romania for a record seizure of 2.5 tons of cocaine (the biggest seizure of cocaine in the country's history). Mimoun was arrested in 2016 when he tried to leave Spain through the Málaga Airport after the seizure in Romania, which was worth €600 million. It was one of the largest drug seizures in Eastern European history. During the 2010s, the Moroccan mafia was widely talked about in Dutch and Belgian politics. After the assassination of Derk Wiersum, a lawyer with information about Ridouan Taghi, Geert Wilders expressed his discontent in the Dutch parliament.
We are no more boss in our own country and there is no more authority. Disorder, violence, terror, this is what affects Amsterdam and several other parts of the country. A brutally murdered lawyer, the brother of a key witness killed, rocket launcher attacks on our media outlets, grenades exploding in our streets and decapitated [sic] heads in front of our coffee shops. The Moroccan mafia has become the boss in this country. And they are getting stronger and more violent every day.
Everyone in the street is fed up with the presence of Moroccans. This mafia in Amsterdam is not from Norway, it is from Morocco. Don't contradict me when I tell you that the Netherlands has a problem of Moroccans. I agree with Wilders if he says that there is a Moroccan mafia problem in the Netherlands. I also agree with him if he says that Moroccans are predominantly present in the crime statistics of the Netherlands. But I wonder what you are implying with "a problem of Moroccans in the Netherlands". The other Moroccans who are living honest lives and hear that "there is a problem of Moroccans" can be affected very deeply by this. Personally, as a liberal, as a member of this democratic society, I think that we must judge people on their individual behavior, and not on the ethnic group they belong to. Every Moroccan who wants to build a future in the Netherlands by obeying our system is in their right to do so. I have a lot of people who come to my house to complain, telling me that they see a lot of Moroccans hanging out in the alleys with bulletproof vests under their jackets. They are undoubtedly men who have relations with the Moroccan mafia. Death threats should not be taken into account. It won't change anything.
These men can appear at any time and shoot you. It is inevitable. Of course, the Netherlands is not on the same level as Mexico yet. We do not have 14.400 assassinations. But if you look at the infrastructure, the amount of money raised by organised crime, and the black market, then yes, we are becoming a narco-state. Journalist and crime reporter John van den Heuvel was targeted by the Moroccan mafia after he made numerous statements about the workings of their criminal activities. In June 2018, the headquarter of the Dutch newspaper Panorama was attacked by a rocket launcher after they published articles on the Moroccan mafia. Shortly afterwards, the headquarter of another Dutch news-outlet De Telegraaf was attacked by a car, which was rammed into the office and set on fire afterwards. John van den Heuvel, who worked for De Telegraaf in the past, delivered his personal opinion on Dutch television by evoking the name of the criminal who was allegedly responsible: Ridouan Taghi is the most wanted criminal in the Netherlands. Every time we say or write something about him, there are consequences, attacks and threats. When you are a journalist who writes about him, you take risks of getting murdered.
Following this statement, John van den Heuvel was targeted by criminals who planned attacks against him. During a police investigation, a rocket launcher was found in the home of Yassine A., which he had prepared to use on the residence of John van den Heuvel. As a result of this, John van den Heuvel cancelled his television program on RTL Boulevard where he was to participate as the host of a show. A year later he also received death threats from Ridouan Taghi, who was on the run. He warned John van den Heuvel that his name was on Taghi's blacklist. Taghi also placed a bounty on John van den Heuvel for a large sum of money. In December 2019, Ridouan Taghi was eventually arrested in Dubai. Following this event, John van den Heuvel had delivered another statement I am so relieved. I can't even believe it. Exactly two years ago I was forced to have as much security as possible due to threats. Ever since then, i have never walked alone in the streets. It was heavy. Fortunately, I could still do my job. It was a difficult time in my career. When you hear such news, it is an incredible relief. In 2017, writer Raf Sauviller published his book Borgerokko Maffia, which was distributed to many libraries across Flanders (Belgium) and the Netherlands. In his book, he discusses the corruption that takes place in the Port of Antwerp amongst police officers and Customs controls. According to research which was carried out in 2018, the municipality of Borgerhout, Antwerp, had an illegal economy which was larger than the regular economy due to the influx of funds by the Moroccan mafia. During an interview by the newspaper De Morgen on the context of this book, the mayor of Antwerp, Bart De Wever, admitted that there were many difficulties on intercepting the main commanders of the Moroccan mafia in Antwerp. He also stated: It is very easy for the Moroccan mafia to infiltrate Belgian politics. They do more damage than the drugs itself. I think it is unfair for leaders of political parties to see their party collapse. I already prefer to warn them that my political party will not be a potential collaborator. These organisations are content with an incredible turnover that can make them amongst the richest in Morocco. This week we have created the Kali-team. A team that is made up of 40 investigators to combat the Moroccan mafia in the Port of Antwerp.
The impact is heavy on editors, journalism and society, but we will never remain silent. Almost a thousand people work in the head office. We are far from ignoring their feelings of insecurity in their workplace. Our social rights and democracy are under unbearable pressure, and we must all fight together. From these attacks, we learned a lot of things, notably that we must always remain vigilant. Over the years, foreign media outlets also reported on the Moroccan mafia, particularly in Germany, Spain, Italy, Brazil, Colombia, Chile, Morocco, and the United Kingdom. BBC News stated in 2019 that the Netherlands was in the process of becoming a narco-state.
Learn how to use our cloud products and solutions at your own pace in the Red Hat® Hybrid Cloud Console. Discover resources and tools to help you build, deliver, and manage cloud-native applications and services. Find solutions from our collaborative community of experts and technologies in the Red Hat® Ecosystem Catalog. You’ve seen it countless times in television’s most popular dramas: professional investigators descend on the scene of a crime to meticulously record and analyze every detail and clue before anyone else can disrupt the scene. If the crime appears to be related to other ongoing cases, clues are tacked to the peg board back at headquarters. Only once all the pieces have been assembled do patterns emerge.
Forensics in the realm of container environments are somewhat similar, only that suspicious activity unfolds much faster. Following the trail invariably means piecing together data from multiple systems, and that data needs to be captured with as little modification or disruption as possible. Containers make digital forensics incredibly complex, as they are scheduled and orchestrated across different hosts according to usage and need. Furthermore, container environments yield enormous amounts of data at high velocity, which is difficult to capture without the right type of instrumentation and tools.
In contrast with virtual machine (VM) environments, containers running on a host share the underlying operating system kernel. There isn’t any hardware isolation at play. There may also be new restrictions to account for, such as network overlay isolation, even within the same host. The good news is: the IT industry has seen this sort of complexity transition before. When VMs were first introduced, the standard practice was to copy the memory and disk contents directly from the physical server. Multiple VMs may have been transitioned to or from a host machine that was first exploited, or a copy might be running on another bare metal machine.
Despite the fact that VMs can be migrated between different data centers, they are considered sufficiently self-contained to provide evidential preservation. StackRox envisions the same situation with respect to containers. Similar to the transition from physical servers to VMs, there will be nuanced complexities, with associated advantages and disadvantages.
Though not intended to be taken as legal advice, this technically-focused blog post offers up an overview of some of the key elements of digital forensics, along with key considerations for conducting effective forensic investigations in container environments. Containers differ from bare metal or virtual machines in a number of ways that impact obtaining actionable evidence. At this time there is no default “container snapshot” function available; containers must be captured as a set of distinct components.
Leading container runtimes use a copy-on-write file system. This is a great advantage to forensic acquisition. All of the default system and application files exist within the container image. Any changes since the container started are stored in a separate directory from the original image. Furthermore, any deletion of original files from the image is also recorded. If you’re using Docker, you may manually explore the copy-on-write diffs inside /var/lib/docker . But we can go one step further: Docker will capture all file modifications, since the container was started into a new layer on the copy-on-write file system. Simply commit an existing container, running or not, into a new image: docker commit $CONTAINER_ID imagename . Committing a container into a new image does not otherwise modify the container in any way.
Note that committing a container differs from snapshotting a VM. Committing only records file system changes, but not the current process execution state. If you resume a container from a commit, it will need to launch new processes and is not guaranteed to execute any suspicious behavior. Containers offer additional benefits in terms of memory isolation. Containers are not a first-class primitive in linux; they are an abstraction on top of multiple subsystems, such as process namespaces and cgroups. Processes running inside a container manage memory the same as any other process. By default, processes inside a container may not interact or interfere with memory controlled by any process outside the container. This provides the following characteristic: if you capture all of the memory for each process in a container, you have captured all allocated memory for that container.
There exist multiple per-process memory dump utilities in linux. The utility gcore suspends the process during acquisition but does not modify it; it executes it quickly, and the output format is compatible with YARA. Alternatives include obdump , [memfetch](https://github.com/citypw/lcamtuf-memfetch) , gdb , or even dd directly from memory devices. 3. Software Implementation, Frameworks & Protocols Containers are ephemeral. Malware might not be aware of this and write some interesting data to the container’s allocated disk space. Ultimately the most sensitive data is likely stored via a volume, typically mounted against persistent online storage. This is where container isolation breaks down.
Mounted volumes rely on a storage backend. By default, that’s the host’s native file system. Frequently, a distributed or cloud file system is used, such as gluster or Amazon S3. Acquiring and exploring these file systems will require interacting with the file system directly. It is not recommended to use a container that also mounts this volume to enumerate files – that may tarnish the file access and modification metadata. If you absolutely must access the volume this way, be sure to mount it into the container as ‘read-only’.
Identifying the volume mount is simple; one inspects the container. Volumes are identified via the Volume and Mount configuration. Existing examination techniques will be needed for each backing service. Containers are typically employed within a microservices-based architecture. While great for speed and scalability, this means that suspicious activity will likely involve multiple containers pertaining to multiple services, across various hosts and with access to different data stores.
While investigating a container breach, make note of any data stores or services that this container accessed. Container acquisition is much faster than VM acquisition, but the price we pay is that one may need to acquire evidence from all of these associated containers. The web of lateral movement across containers will differ according to the sophistication of an attack. It is better to acquire more now than wish you had, later on.
StackRox is an indispensible asset to security teams, as it records network traffic information between individual containers and detects malicious lateral movement. This enables an analyst to track down potentially compromised containers very quickly. There are vulnerabilities and misconfigurations that could allow malware to escape a container. If there is any evidence of suspicious behavior on the host itself, or evidence of this type of malware, it is prudent to image the entire host, whether bare-metal or VM.
Even if you must capture the entire host, organizing the evidence by container can dramatically reduce the investigation effort required. A container may not be fully isolated in some cases, but until there is evidence of an isolation bypass, one may assume that the suspicious behavior is constrained to the container’s environment. Note that all of these default isolation properties may be explicitly bypassed. For example, a Docker container mounting the root of the host file system, or using the host pid namespace will be able to easily escape the container environment, perhaps without leaving behind any indicators. If a container is launched using any of the following flags, host examination is warranted: StackRox can alert you if any containers launch with these increased privileges and when the container uses them.
At this time, there isn’t a formal mechanism for running a captured container. Once they’re shut down, even if both file system and memory contents are exported, there is no mechanism for combining the two back into the previous running state. Containers are designed to be ephemeral and thus start processes and allocate new memory, upon initialization. To that extent, interaction during execution is mandatory, and it is possible to preserve the container and remove it from a production environment. There are a few mechanisms one can use to persist the running container without the container further impacting the cluster in a significant way.
First, containers may be paused at any time. Container execution is completely suspended, memory remains allocated, volumes remain mounted, etc. Any malware currently executing is interrupted. Second, containers may be quarantined by removing network access or system call privileges. The container processes – and possibly the malware – will continue to execute, but will be unable to send, receive, read, or write any data, or even unmap existing memory. However, this causes errors. Depending on how the processes handle these errors, this may stop the container.
As a container security platform, StackRox is unique in that we offer a comprehensive set of response features that can be automatically executed according to user-defined security policies. Beyond alerting on anomalous or malicious activity – such as lateral movement, or a container with excessive privileges – StackRox will block unauthorized Docker commands, system calls, and quarantine, isolate, or instantly pause compromised or rogue containers.
Once a container is paused or quarantined (if one desires a clean operating environment), it’s possible to scale up a cluster. An administrator can add a new node to the system, drain all other containers from this node, and optionally remove it from the orchestrator. At that point, network access may be restricted from the node, and the container can be resumed or switched to a different network.
Even as enterprises move away from monolithic applications to containers and microservices architectures, they still face a wide spectrum of cyber attacks aimed at stealing valuable data, commandeering infrastructure, or causing wanton disruption and destruction. Forensic analysis is a critical capability of any enterprise security program, and it must take into account the characteristics of the significantly different attack surface and environment that containers form. Understanding container ephemerality and isolation is required in order to identify infected containers, capture components, and analyze them safely.
StackRox enables detailed, comprehensive visibility into container activity, and puts a best-in-class set of policy-driven response capabilities in the hands of security practitioners that will dramatically enhance the efficiency and effectiveness of investigations. Michael Foster is a CNCF Ambassador, the Community Lead for the open source StackRox project, and Principal Product Marketing Manager for Red Hat based in Toronto. In addition to his open source project responsibilities, he utilizes his applied Kubernetes and container experience with Red Hat Advanced Cluster Security to help organizations secure their Kubernetes environments. With StackRox, Michael hopes organizations can leverage the open source project in their Kubernetes environments and join the open source community through stackrox.io . Outside of work, Michael enjoys staying active, skiing, and tinkering with his various mechanical projects at home. He holds a B.S. in Chemical Engineering from Northeastern University and CKAD, CKA, and CKS certifications.
The future of enterprise virtualization for your workloads on-premise or across clouds Red Hat is an open hybrid cloud technology leader, delivering a consistent, comprehensive foundation for transformative IT and artificial intelligence (AI) applications in the enterprise. As a trusted adviser to the Fortune 500 , Red Hat offers cloud, developer, Linux, automation, and application platform technologies, as well as award-winning services.
Learn & practice AWS Hacking: HackTricks Training AWS Red Team Expert (ARTE) Learn & practice GCP Hacking: HackTricks Training GCP Red Team Expert (GRTE) Learn & practice Az Hacking: HackTricks Training Azure Red Team Expert (AzRTE) Browse the full HackTricks Training catalog . 4. Practical Deployment, Analysis & Case Studies You can easily find changes made to this containerâIIs filesystem since it was created with: [1] In the previous command C means Changed and A means Added . [1] If you find that some interesting file like /etc/shadow was modified you can download it from the container to check for malicious activity with: [2] You can also compare it with the original one running a new container and extracting the file from it: [2] [3] If you find that some suspicious file was added you can access the container and check it: [4] When you are given an exported docker image (probably in .tar format) you can use container-diff to extract a summary of the modifications : [5] [6] Then, you can decompress the image and access the blobs to search for suspicious files you may have found in the changes history: [7] In order to find added/modified files in docker images you can also use the dive (download it from releases ) utility: [11] [12] This allows you to navigate through the different blobs of docker images and check which files were modified/added/removed.
Use tab to move to the other view and space to collapse/open folders. [11] With dive you wonâIIt be able to access the content of the different stages of the image. To do so you will need to decompress each layer and access it . You can decompress all the layers from an image from the directory where the image was decompressed executing: On Linux, the hostâIIs ancestor PID namespace can see processes in a containerâIIs child PID namespace, so a host process listing such as ps -ef can show them. [14] When host credentials, capabilities, and LSM/ptrace policy permit it, an appropriately privileged host investigator can dump process memory and search for credentials just like in the following example . [15] Learn & practice AWS Hacking: HackTricks Training AWS Red Team Expert (ARTE) Learn & practice GCP Hacking: HackTricks Training GCP Red Team Expert (GRTE) Learn & practice Az Hacking: HackTricks Training Azure Red Team Expert (AzRTE) Browse the full HackTricks Training catalog .
Export the container filesystem, identify webshells in web root, analyze access logs for exploitation attempts, check for added files and modified configurations, examine network connections for C2 communication, review container capabilities for escalation paths. Analyze image layers with dive to identify which layer added malicious content, compare with the official base image using container-diff, check image history for suspicious RUN commands, scan for embedded backdoors and cryptocurrency miners, trace the image pull from registry logs.
Check if container ran privileged or with dangerous capabilities, examine host filesystem mount points for unauthorized access, review Docker socket mount enabling Docker-in-Docker abuse, analyze host system logs for container escape indicators, check for kernel exploit artifacts. Identify high-CPU containers, export and analyze the container image for mining binaries, check for unauthorized images in the registry, review container creation events for rogue deployments, examine network connections for mining pool communications.
Claw GRC Tip : When this skill is executed by a registered agent, compliance evidence is automatically captured and mapped to the relevant controls in your active frameworks. When executed through Claw GRC, every step of this skill generates tamper-evident audit records: Schedule this skill for recurring execution to maintain continuous compliance posture. Claw GRC monitors for drift and alerts when re-execution is needed.
This skill is fully compatible with Claw GRC's autonomous agent system. Deploy it to any registered agent via MCP, and every execution will be logged in the tamper-evident audit trail. This repo contains a toolkit for performing post-mortem analysis of Docker runtime environments based on forensic HDD copies of the docker host system.
Testing this tool in integration with a real Docker host image is complicated because: Therefore there are two ways to test this tool: one with a real docker Host Image and one with a temporary folder containing select files from a Docker Host image (created by running the create_zipfile_from_testimage.py script. For local development it's recommended to use the first way while CI may use the latter.
sudo python src/dof/main.py mount-image testimages/alpine-host/output-virtualbox-iso/packer-virtualbox-iso-*-disk001.vmdk.raw 5. Performance Evaluation & Extended Technical Observations The toolkit is distributed as a runnable 'fat' binary, bundled with a Python interpreter. The binary is created by PyInstaller . To create such a binary run: A toolkit for the post-mortem examination of Docker containers from forensic HDD copies At 2:47 AM, our Security Operations Center detected anomalous network traffic from a production container. Within minutes, we discovered a sophisticated attack: an attacker had exploited a vulnerability, gained container access, and was actively exfiltrating customer data. This incident exposed a critical gap in our security posture - we had no forensics capability for containerized environments. By the time we understood what happened, evidence was gone, containers deleted, and logs incomplete. This is the complete story of how we built an enterprise-grade container forensics and incident response framework that has since detected and contained 23 security incidents with zero data loss.
This comprehensive guide covers container forensics fundamentals, evidence collection procedures, threat hunting techniques, compliance requirements, and automated investigation workflows for production Kubernetes and Docker environments. Traditional server forensics assumes long-lived, persistent infrastructure. Containers break every assumption: Pitfall 1 : Relying on container logs alone Solution : Capture multiple evidence types (memory, network, filesystem) Pitfall 2 : Not preserving container state before remediation Solution : Automate snapshot creation before any response action Pitfall 3 : Insufficient storage for evidence Solution : Plan for 1TB+ evidence storage with automatic lifecycle management Container forensics requires a fundamentally different approach than traditional server forensics. The ephemeral nature of containers, rapid deployment cycles, and dynamic orchestration create unique challenges that traditional tools cannot address.
Our enterprise forensics framework has successfully investigated 23 security incidents over 18 months, with 100% evidence preservation rate and zero compliance violations. The key to success was automation: by the time a human investigator is alerted, all evidence has already been collected, preserved, and uploaded to secure storage. The investment in forensics capability paid for itself after the first major incident, where proper evidence collection enabled us to identify the attack vector, patch the vulnerability, and provide compliance documentation to auditors - all within 24 hours of detection.
Developing a cloud-native container forensics system to capture ephemeral artifacts, container metadata, and process activity. A Docker container forensics framework designed to capture and preserve volatile forensic evidence from compromised containers before they are terminated or deleted. The project collects container-level artifacts, correlates them across processes, files, and network activity, and reconstructs an attack timeline to support container-based incident investigation.
Containers are designed to be ephemeral . When a compromised container is stopped or deleted, valuable forensic evidence such as running processes, temporary files, network connections, and executed commands can disappear. This project addresses the problem by collecting and preserving relevant forensic artifacts before the evidence disappears . The framework attempts to preserve the relevant artifacts and reconstruct the incident: This allows an investigator to understand what happened, when it happened, and which artifacts are related .
This project is developed for educational, research, and authorized security investigation purposes . Testing should only be performed on systems and containers for which you have permission. M.Sc. Digital Forensics & Information Security Cybersecurity | Digital Forensics | Cloud Security The project is currently under development, with additional forensic collection, artifact correlation, and investigation capabilities planned.
Docker container forensics framework for capturing volatile evidence, correlating forensic artifacts, and reconstructing security incidents before containers are deleted. This repo contains a toolkit for performing post-mortem analysis of Docker runtime environments based on forensic HDD copies of the docker host system.
Testing this tool in integration with a real Docker host image is complicated because: Therefore there are two ways to test this tool: one with a real docker Host Image and one with a temporary folder containing select files from a Docker Host image (created by running the create_zipfile_from_testimage.py script. For local development it’s recommended to use the first way while CI may use the latter.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Inert%20gas%20asphyxiation • https://en.wikipedia.org/wiki/Law%20enforcement%20in%20Australia • https://en.wikipedia.org/wiki/Moroccan%20mafia • https://www.redhat.com/en/blog/docker-forensics-for-containers-how-to-conduct-investigations • https://hacktricks.wiki/en/generic-methodologies-and-resources/basic-forensic-methodology/docker-forensics.html • https://clawgrc.com/skills/analyzing-docker-container-forensics • https://github.com/docker-forensics-toolkit/toolkit • https://support.tools/container-forensics-incident-response-enterprise-security-framework/ • https://github.com/Kalpkataria/Container-Forensic-Autopsy-Evidence-Reconstruction- • https://kalilinuxtutorials.com/the-docker-forensics-toolkit/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Docker Container Forensic Investigation Tool Project.
[*] Metasploit Scan Running on Target Subnet for Docker Container Forensic Investigation Tool Project... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |