Complete Technical Paper Content — Docker Container Vulnerability Scanning Tool Using Trivy
Overview & System Context
Docker Container Vulnerability Scanning Tool Using Trivy: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9500 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Container images consist of files. For instance, new files will be installed if you install a package.
By default, vulnerability and secret scanning are enabled, and you can configure that with --scanners . It is enabled by default. You can simply specify your image name (and a tag). It detects known vulnerabilities in your container image. See here for the detail. It is supported, but it is not useful in most cases. As mentioned here , Trivy mainly supports Infrastructure as Code (IaC) files for misconfigurations. If your container image includes IaC files such as Kubernetes YAML files or Terraform files, you should enable this feature with --scanners misconfig .
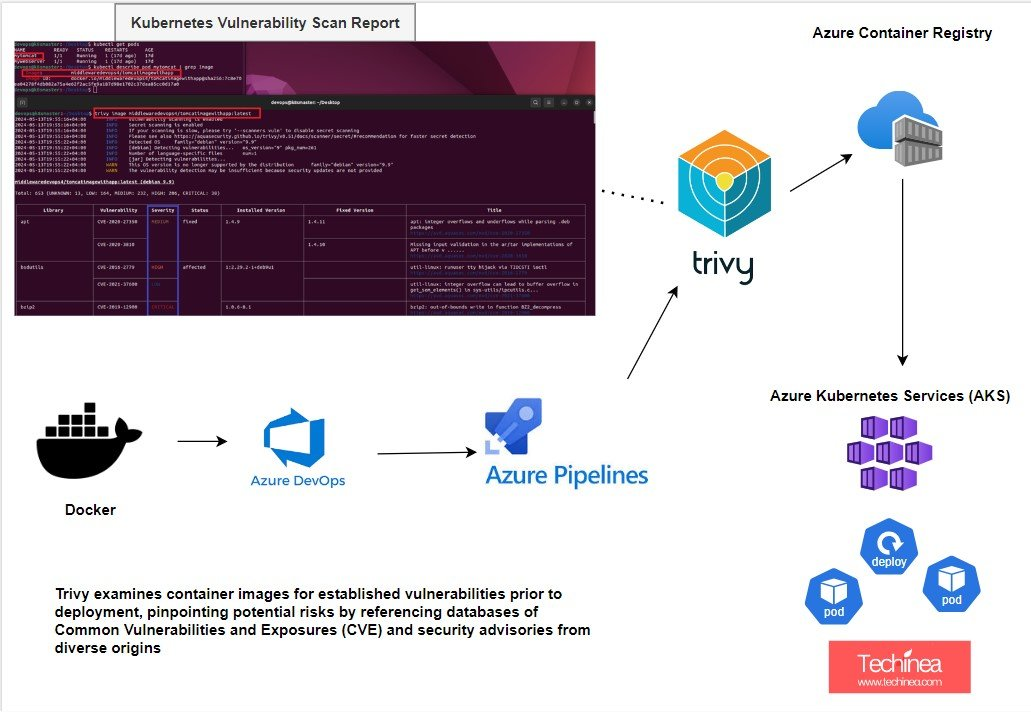
Figure 1: Mastering Kubernetes Security: Installing Trivy and Scanning Docker ... It is experimental and disabled by default. It requires the CycloneDX format, since the assets are reported as CycloneDX components. See here for the detail. Container images have configuration . docker inspect and docker history show the information according to the configuration.
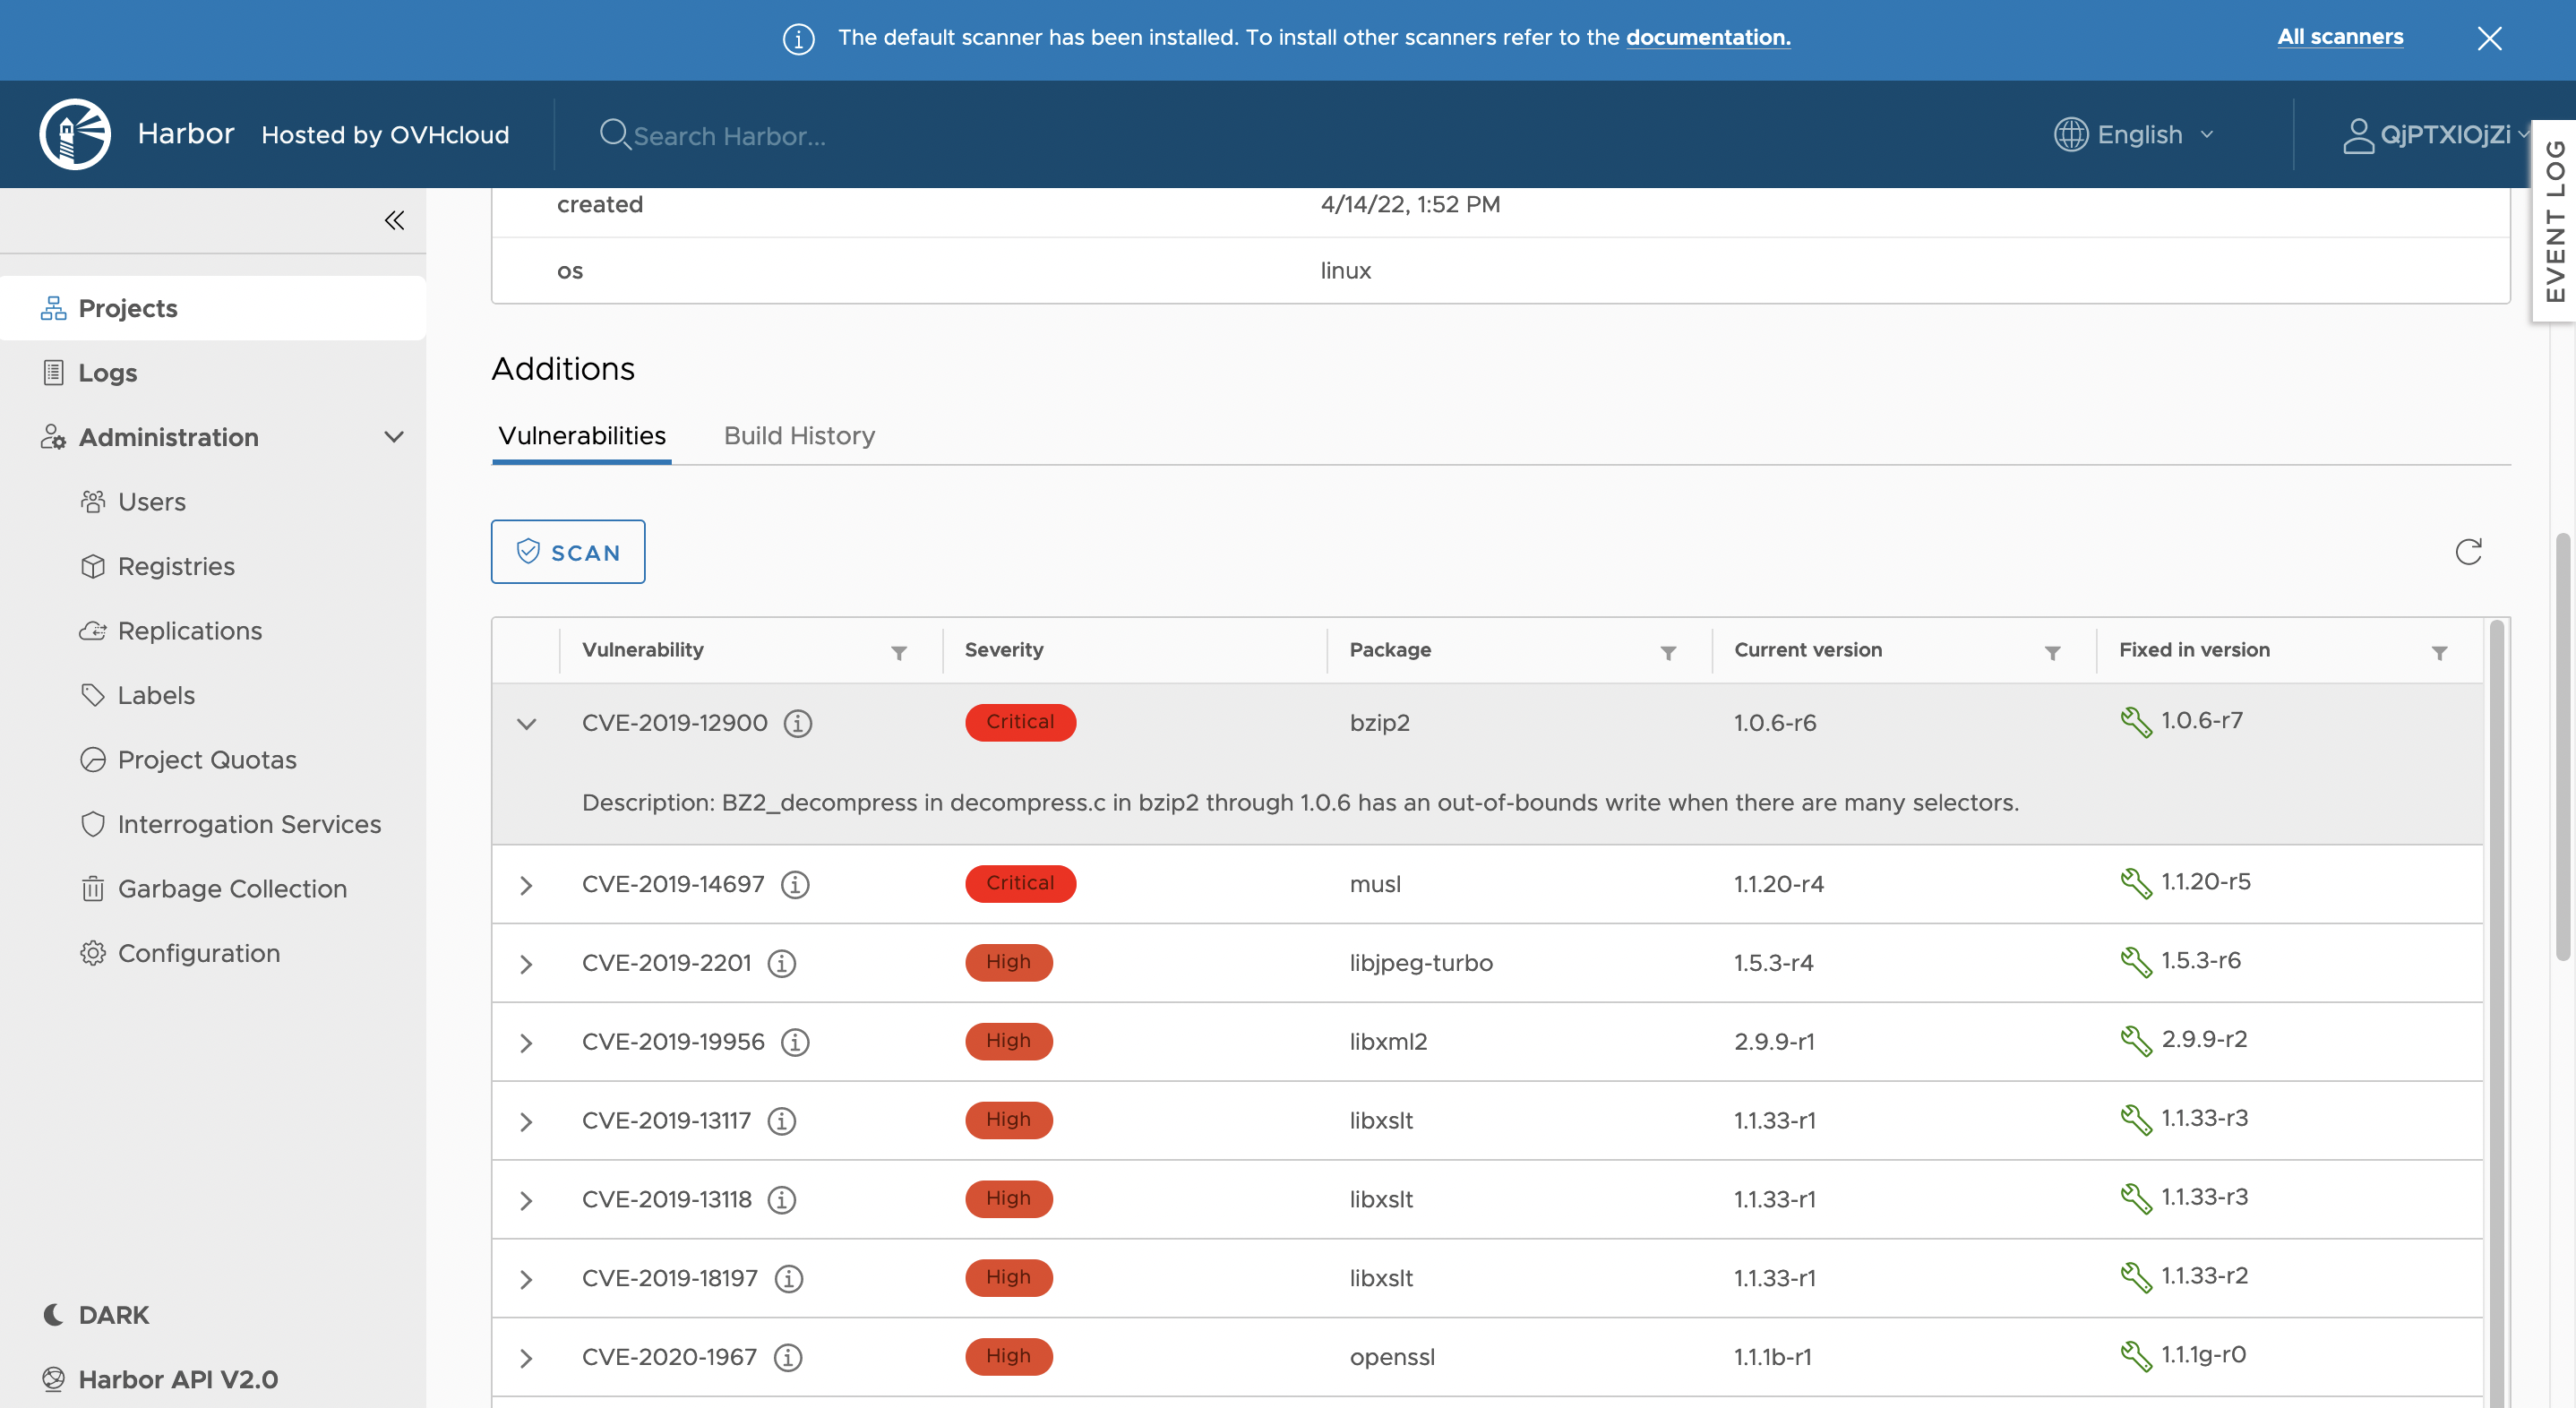
Trivy detects misconfigurations on the configuration of container images. The image config is converted into Dockerfile and Trivy handles it as Dockerfile. See here for the detail of Dockerfile scanning. The following checks are disabled for this scan type due to known issues. See the linked issues for more details. Figure 2: Scanning Docker Images for Vulnerabilities with OVHcloud Managed ...
Trivy detects secrets on the configuration of container images. The image config is converted into JSON and Trivy scans the file for secrets. It is especially useful for environment variables that are likely to have credentials by accident. See here for the detail. Trivy will look for the specified image in a series of locations. By default, it will first look in the local Docker Engine, then Containerd, Podman, and finally container registry.
Will first search in Podman. If the image is found there, it will be scanned and the results returned. If the image is not found in Podman, then Trivy will search in Containerd. If the image is not found there either, the scan will fail and no more image sources will be searched. Trivy tries to look for the specified image in your local Docker Engine. It will be skipped if Docker Engine is not running locally.
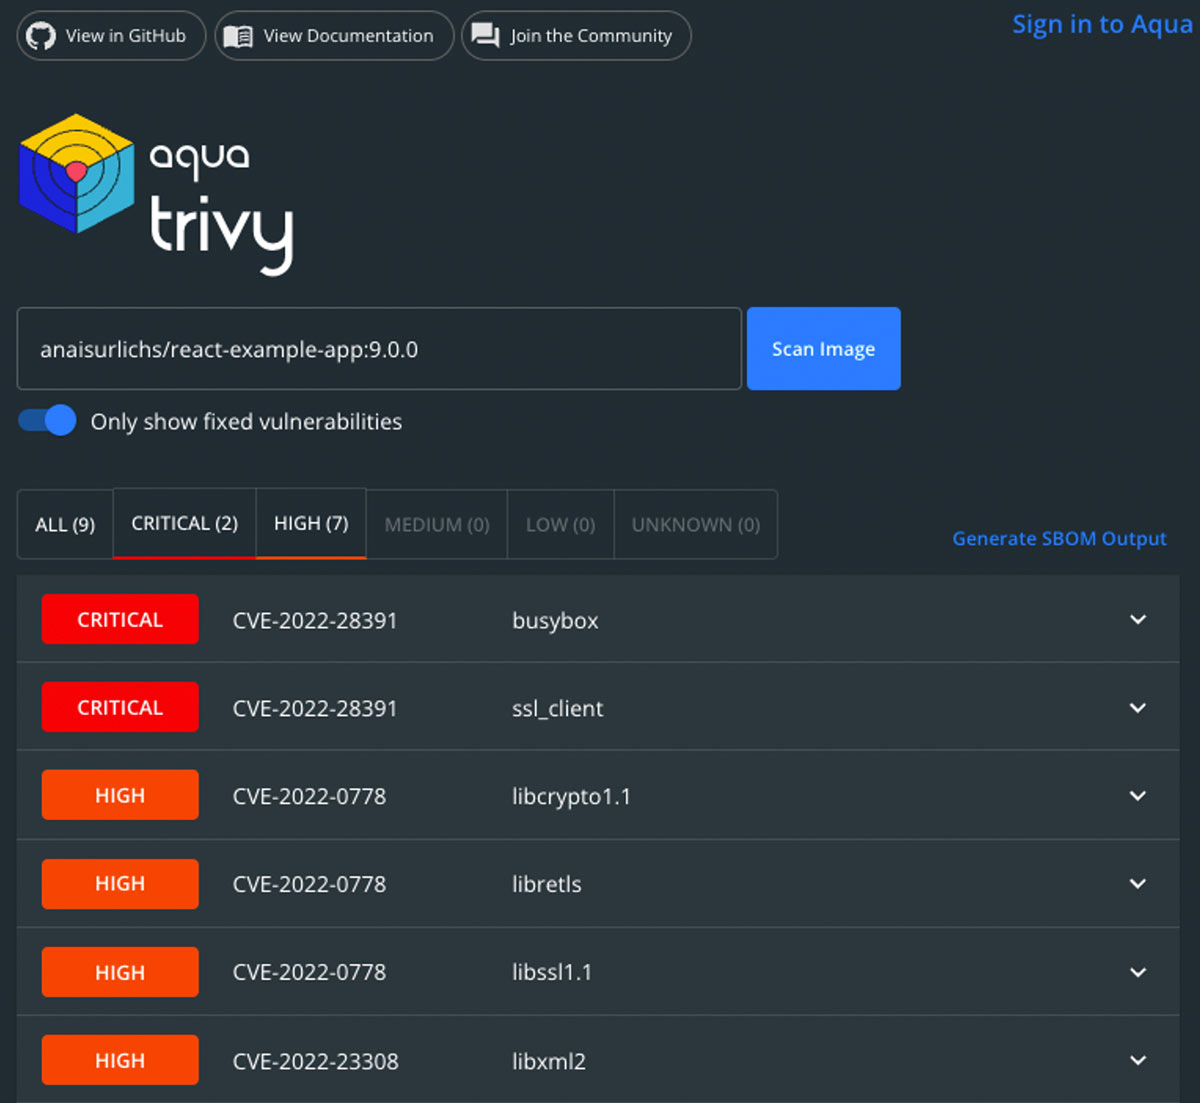
Figure 3: Unlimited Container Image Scanning in Docker Desktop with Trivy Trivy tries to look for the specified image in your local containerd . It will be skipped if containerd is not running locally. If your containerd socket is not the default path ( //run/containerd/containerd.sock ), you can override it via CONTAINERD_ADDRESS .
If your scan targets are images in a namespace other than containerd's default namespace ( default ), you can override it via CONTAINERD_NAMESPACE . Scan your image in Podman (>=2.0) running locally. The remote Podman is not supported. If you prefer to keep the socket open at all times, then before performing Trivy commands, you can enable the podman.sock systemd service on your machine. For more details, see here .
If you prefer not to keep the socket open at all times, but to limit the socket opening for your trivy scanning duration only then you can scan your image with the following command: Trivy supports image directories compliant with Open Container Image Layout Specification . Referencing specific images can be done by their tag or by their manifest digest: # Referenced by tag $ trivy image --input /path/to/alpine:3.15 # Referenced by digest $ trivy image --input /path/to/alpine@sha256:82389ea44e50c696aba18393b168a833929506f5b29b9d75eb817acceb6d54ba Trivy supports the generation of Software Bill of Materials (SBOM) for container images and the search for SBOMs during vulnerability scanning.
Trivy can search for Software Bill of Materials (SBOMs) within container image files and scan their components for vulnerabilities. SBOM specifications define key requirements for component documentation 2 . However, different tools and systems often have varying approaches to documenting component types and their relationships.
Due to these variations, Trivy cannot always accurately interpret SBOMs generated by other tools. For example, it may have difficulty determining the correct file paths to component information files (such as lock files or binaries). In such cases, Trivy uses the path to the scanned SBOM file itself to maintain traceability and ensure accurate dependency reporting. Trivy can search for Software Bill of Materials (SBOMs) that reference container images. If an SBOM is found, the vulnerability scan is performed using the SBOM instead of the container image. By using the SBOM, you can perform a vulnerability scan more quickly, as it allows you to skip pulling the container image and analyzing its layers.
To enable this functionality, you need to specify the --sbom-sources flag. The following two sources are supported: The OCI Registry utilizes the Referrers API . For more information about Rekor, please refer to its documentation . This section describes container image specific compliance reports. For an overview of Trivy's Compliance feature, including working with custom compliance, check out the Compliance documentation .
When scanning container images, it stores analysis results in the cache, using the image ID and the layer IDs as the key. This approach enables faster scans of the same container image or different images that share layers. By default, Trivy loads an image on a "linux/amd64" machine. To customise this, pass a --platform argument in the format OS/Architecture for the image: Use the --max-image-size flag to avoid scanning images that exceed a specified size. The size is specified in a human-readable format 1 (e.g., 100MB , 10GB ).
The layers are pulled into a temporary folder during their pulling and are always cleaned up, even after a successful scan. Example Usage: # Limit uncompressed image size to 10GB $ trivy image --max-image-size = 10GB myapp:latest Error Output: Error: uncompressed image size ( 15GB ) exceeds maximum allowed size ( 10GB ) Your homelab runs dozens of Docker containers. Each image pulls in layers from upstream registries — Alpine, Debian, nginx, Python, PostgreSQL. And every layer can ship with known vulnerabilities that get discovered months after you pulled it.
Manual audits don’t scale. You need an automated scanner that checks every running image against the latest CVE databases, flags misconfigurations, detects embedded secrets, and generates reports you can actually act on. Trivy from Aqua Security does all of this. It is fast, dependency-free (one binary or a container), covers OS packages and language-specific libraries, and integrates cleanly into a homelab automation workflow. This guide walks through installation, scanning workflows, output formats, and a complete systemd timer setup for weekly unattended scans.
Trivy ships as a single static binary, a Docker image, and packages for every major distro. For a Proxmox or bare-metal Linux host, install the binary directly — it avoids the overhead of scanning images from inside a container. Trivy downloads a vulnerability database on first run. The database is cached under ~/.cache/trivy and updated automatically when you scan with a DB older than 12 hours. You can force an update with: The most useful scan for a homelab: check every image currently running for known CVEs.
This produces a severity-sorted table of every CVE found in the OS packages inside that image. Critical findings are highlighted in red. Add --ignore-unfixed to skip CVEs that have no available fix — this reduces noise significantly in production-style scans. Trivy is not just for CVEs. It also scans Dockerfiles and docker-compose files for misconfigurations and hardcoded secrets.
The secrets scanner checks for embedded API keys, tokens, passwords, and private keys in image layers. Useful before pushing custom images to a registry. Plain terminal output is fine for interactive use, but for automated scans you want formats you can archive, email, or visualize. The most valuable setup for a homelab: unattended weekly scans that email or log results. Systemd timers are the cleanest way on Linux.
The Nice=19 and IOSchedulingClass=idle lines ensure the scan doesn’t compete with production workloads. Trivy JSON output can be visualized in Grafana or Grafana Alloy. A lightweight alternative: serve the HTML reports with a one-liner HTTP server and catch them in your monitoring stack. Scanning is only half the battle. When Trivy flags a critical CVE, the fix is almost always a newer version of the base image. A practical workflow: For images you build yourself, rebuild with updated base images and redeploy. If you run Watchtower (covered in a previous post ), it can handle the pulling step automatically — but Trivy gives you the visibility to decide which updates matter.
Security is a process, not a one-time task. An automated weekly scan with Trivy keeps your homelab safe with minimal effort — and gives you the confidence that your containers aren’t running known-critical vulnerabilities between updates. Trivy scans code projects and build artifacts for security issues such as vulnerabilities, IaC misconfigurations, secrets, and more.
In order reuse previously dowloaded vulnerability database, and pulled layers, you should mount the cache directory from the host, for example by adding the following to the docker tun command: -v [YOUR_CACHE_DIR]:/root/.cache/ . Also consider mounting the Docker socket, for example: -v /var/run/docker.sock:/var/run/docker.sock Scanner for vulnerabilities in container images, file systems, and Git repositories, as well as for configuration issues and hard-coded secrets 2. System Architecture & Core Working Principles In modern software development, containers are the default unit of packaging and deployment. They provide portability, reproducibility, and scalability. But they also expand your attack surface. A widely cited industry report claimed that 87% of container images contain high or critical vulnerabilities , a statistic that highlights how common inherited risk can be.
The deeper issue is that most vulnerabilities are silent. Your build succeeds. Your tests pass. Your container starts without errors. Everything looks fine, until it is not. A vulnerable base image or outdated dependency can become the entry point an attacker needs. This is where automated scanning becomes essential. Trivy is an open-source security scanner designed to detect vulnerabilities, misconfigurations, and secrets across containers, repositories, and infrastructure as code. Instead of treating security as a final checkpoint, Trivy makes it something you can continuously verify.
When you deploy a container image, you are not shipping just your code. You are inheriting: This is the essence of software supply chain risk. You are trusting every upstream maintainer in your dependency graph. New Common Vulnerabilities and Exposures, or CVEs, are published daily. Manually tracking them is unrealistic. That is why DevSecOps emphasizes “shifting left.” Security checks should run early and often, not just before deployment.
Trivy helps operationalize that principle. Trivy is an open-source scanner created by Aqua Security and widely adopted across the ecosystem. It is often described as an “all-in-one” tool because of its breadth. Most importantly, Trivy is designed for automation . It works just as well in a local terminal as it does inside a pipeline.
One of the most common use cases is scanning a container image for vulnerabilities. Trivy can be run directly via its official container image. Trivy downloads its vulnerability database, analyzes the image layers, and prints a structured report. The installed and fixed versions are especially useful because they tell you exactly what to upgrade to resolve the issue .
Trivy can return a non-zero exit code when it detects vulnerabilities that match your criteria. In CI systems, a non-zero exit code fails the job. This means if at least one CRITICAL vulnerability is found, the process exits with code 1 . In a CI pipeline, that blocks the build automatically.
This mechanism turns Trivy from a reporting tool into a security gate . Instead of relying on manual review, the pipeline enforces your risk threshold. Vulnerabilities are not the only risk. Misconfigurations can create insecure defaults even when dependencies are patched. The -v $(pwd):/project flag mounts your current directory into the container so Trivy can scan it.
Because Trivy supports exit codes, severity filtering, and multiple scan targets, it adapts to different enforcement strategies. Some teams block on CRITICAL only. Others block on both HIGH and CRITICAL . The tooling remains consistent. Containerized and cloud-native systems introduce significant supply chain complexity. Manual security review cannot scale to modern dependency graphs. Automated scanning is the only realistic solution.
By scanning images, infrastructure as code, and entire repositories, you gain early visibility into vulnerabilities and misconfigurations. By enforcing exit codes in CI, you transform visibility into prevention. On December 10, 2021, alert curves on the monitoring dashboard spiked red. Someone dropped CVE-2021-44228 in the ops chat—Log4Shell. More than a dozen microservices were on affected base images; the team spent the night rebuilding and redeploying.
Research we cite in this article found that 76% of Docker Hub images contain known vulnerabilities. Your python:3.9 or nginx:latest tags may ship with dozens of CVEs. Commands and configs are copy-paste ready. If you are building a scanning habit, this should shorten the learning curve. "A study by NSFOCUS showed that 76% of images on Docker Hub contain known security vulnerabilities." Honestly, when I first started with containers, I thought Docker images were just “packaged programs” - if they run, they’re fine. It wasn’t until we got scanned for 3 days online that I realized image vulnerabilities come in several categories, each one enough to give you a headache.
Operating System Package Vulnerabilities - This is the most common. In your Alpine or Ubuntu base images, system libraries like OpenSSL, glibc, and curl regularly have new vulnerabilities. For example, the OpenSSL 3.0.x critical vulnerability in 2022 affected a huge batch of images. Application Dependency Vulnerabilities - This is more subtle. Your Python project depends on Flask, Flask depends on Werkzeug, and some version of Werkzeug has a code execution vulnerability. You think upgrading the Python version makes you safe? Not necessarily - vulnerabilities hidden in the dependency tree might go completely unnoticed. Log4j is a typical case - how many Java projects didn’t even know they were using Log4j.
Configuration Errors and Sensitive Information Leakage - Some developers, for convenience, write database passwords directly in Dockerfiles or forget to delete the .git directory before packaging. Others run containers as root, handing out permissions more generously than their house keys. Supply Chain Risks - This is the hardest to defend against. You pull what looks like a normal image from Docker Hub, and one day it’s discovered to have been planted with mining programs or backdoors. Research in 2018 found quite a few “malicious images” on Docker Hub, specifically fishing for people who just pull without thinking.
I was genuinely shocked when I first saw the 76% figure. NSFOCUS’s research report from March 2018 showed that in random samples from Docker Hub, over three-quarters contained known vulnerabilities. You might think this data is old, right? But the problem is, those old images are still being used. And many “official images” aren’t updated in real-time. That python:3.9 tag you see might have been built six months ago, with system packages that are already outdated.
What’s more frustrating is that Docker Hub image quality varies widely. Some are maintained by individual developers who might not update for half a year; some are labeled “official” but are actually just uploaded by some company. There’s no unified security audit standard - using them is pure luck. I had a colleague who, for convenience, pulled a Node.js environment image from Docker Hub. Later scans revealed over 30 high-risk vulnerabilities. When we asked the image author, they replied: “This image hasn’t been maintained in two years, fix it yourself.” Tragicomic.
So my principle now is: images pulled from Docker Hub must be scanned first, even those with “official” tags are no exception. When it comes to Docker image scanning tools, there are quite a few options, but I now almost exclusively use Trivy. Not that other tools are bad, but Trivy really nails the balance between “ease of use” and “functionality.” The first time I used Trivy, I was amazed by its speed. Scanning a several hundred MB image, the first scan takes about 10 seconds, and subsequent scans take only a few seconds. The key is you don’t need to maintain any local database or configure additional services - install and use.
What satisfies me most is that Trivy has already been integrated by mainstream platforms like GitHub Actions and Harbor. In other words, you don’t need to fiddle with integration solutions yourself - the official path is already paved for you. Snyk - This is a commercial product with really comprehensive functionality. It can integrate directly into your IDE, giving you real-time alerts about dependency vulnerabilities while coding. It also supports automatically generating fix PRs - very smart.
But the problem is the free version has quite a few limitations, and if you really want to use it deeply you’ll need to pay, suitable for companies with sufficient budgets. Clair - This is the scanning engine for the Quay image registry, open-source and deeply customizable. But honestly, configuration is quite complex. Its working method is to pull CVE information from various Linux distribution security teams, focusing on threat detection. If your team has dedicated security engineers and wants a highly customizable solution, Clair is a good choice. But for ordinary development teams, the learning curve is a bit steep.
Anchore - Enterprise-level solution supporting policy management. For example, you can set rules like: “Block deployment if CRITICAL level vulnerabilities are found.” Suitable for scenarios with particularly strict compliance requirements, like finance and healthcare industries. But same problem - configuration and maintenance are quite heavy. Docker Scout / Hardened Images (DHI) - This is a new product Docker officially launched in May 2025, claiming near-zero CVE and image size reduction of 95%. I looked at the technical approach - it uses distroless runtime, and it’s indeed very promising. But because it just launched, the ecosystem is still being built, worth keeping an eye on.
If you’re a small or medium team or individual developer, use Trivy directly - free, easy to use, sufficient functionality. Install with one command, scan with one command, 10 minutes to get started. If you’re a large enterprise with high security compliance requirements and sufficient budget, consider Snyk . Its vulnerability database updates timely, support team is professional, and it can deeply integrate with various development tools.
If your team has dedicated security engineers and wants a deeply customizable open-source solution, Clair is worth studying. But be prepared to spend time fiddling with configuration. For pursuing extreme security and minimal images, keep an eye on Docker Hardened Images development - it might be the future standard solution.
My own practice: use Trivy for daily development and CI/CD for quick feedback; before production deployment, use Harbor-integrated Clair for a second scan - double insurance. Trivy’s installation is so simple I couldn’t believe it the first time. If you use macOS: Linux users can directly download binary files or use package managers to install. GitHub releases page has detailed instructions: https://github.com/aquasecurity/trivy/releases The first time you run it, Trivy will automatically download the vulnerability database (trivy-db), about several tens of MB, need to wait a moment. After download completes, scanning speed is very fast.
Each vulnerability displays CVE number, affected package name, current version, and fixed version (if available). In actual work, you might not want to see all vulnerabilities, especially those “unfixable” low-risk ones that just annoy you. That’s when you need some advanced options: I commonly use this in CI/CD. After all, requiring all vulnerabilities to be fixed is unrealistic - solving the high-risk ones first is the priority.
Some vulnerabilities officially haven’t released patches for yet - no use rushing. Adding this parameter, Trivy only shows vulnerabilities with existing fix solutions, letting you focus energy on solvable problems. 3. Software Implementation, Frameworks & Protocols This is super useful! In CI/CD pipeline, if critical vulnerabilities are found, this command returns non-zero exit code, causing build failure. It’s like adding a security gate to your images - vulnerable images can’t enter production at all.
If you want to import scan results into security platforms or do further automation processing, JSON format is convenient. Some company internal network environments can’t access the external network. You can first download the vulnerability database on a machine that can connect to the internet, then copy it to the internal network machine and add this parameter so it won’t try to update.
The first time I scanned a production image, results filled the screen with over 100 vulnerabilities. My heart sank, thinking how long would this take to fix? Prioritize vulnerabilities with fix versions . If the “Fixed Version” column shows “none” or is empty, it means there’s currently no patch, and you can’t do anything about it. Solve vulnerabilities with fix solutions first.
Focus on CRITICAL and HIGH . LOW and MEDIUM level vulnerabilities, if not public-facing services, can be appropriately delayed. But CRITICAL must be fixed immediately - these vulnerabilities often have public exploit code that hackers can directly utilize. Check CVE details . If you’re uncertain about a vulnerability, go to https://cve.mitre.org/ and check that CVE number to see exactly what the problem is, scope of impact, and difficulty of exploitation. Sometimes seemingly scary vulnerabilities actually require very harsh exploitation conditions.
Understand Trivy’s working principle . Trivy downloads a vulnerability database (actually just a JSON file recording known vulnerabilities of various software packages), then compares it with your image’s software package list (obtained by analyzing package manager databases). As long as package name and version number match a known vulnerability, it gets reported. So sometimes there are false positives. For example, your image has a vulnerable package, but the actual code doesn’t call that problematic function at all, and Trivy will still alert. In these situations you need to judge risk combined with actual code.
Fixing vulnerabilities, honestly, often isn’t about “fixing” but “replacing.” Found dozens of system package vulnerabilities? Don’t upgrade them one by one - directly replacing with a more secure base image is much more efficient. My previous team was used to using Alpine Linux as base image because it’s only 5.87MB, particularly compact. But later we found Alpine has its own problems: it uses the muslc standard library instead of the common glibc, sometimes having compatibility issues. And small as it is, vulnerabilities are still there.
KiloClaw - Managed OpenClaw for enterprise, enabling AI Agent orchestration and smart model routing Now I’m more inclined to use Distroless images. This thing is only 3.06MB, smaller than Alpine, and the key is it’s extremely streamlined: no Shell, no package manager, no unnecessary tools whatsoever. Why is this more secure? Simple - even if hackers discover a vulnerability in your application, they can’t execute shell commands in the container because there simply isn’t one. Attack surface compressed to minimum.
Of course, Distroless also has inconveniences: debugging is troublesome because there aren’t even basic commands like ls and cat. My approach is to use regular images in development environment for easier debugging, switch to Distroless in production environment to ensure security. Docker officially launched Hardened Images (DHI) in 2025 is even more aggressive, claiming near-zero CVE and can further shrink images by 95%. Although the ecosystem isn’t mature now, it’s very worth attention - might be the next generation standard solution.
Replacing base image isn’t enough - application layer dependencies also need managing. Here are some practical tips: Many people like using latest tag for convenience, but that’s a bad habit. latest might not update for months, with system packages inside already outdated. Use specific version numbers, then actively check monthly if there are updated minor versions.
Note the trick here: putting update, upgrade, clean in one RUN instruction can reduce image layers. Finally deleting apt cache can save another several tens of MB space. This is the most common scenario. Trivy finds Flask vulnerable, you go to requirements.txt and change the version number: But there’s a pitfall here: directly upgrading Flask might bring compatibility issues. So best to run it in test environment first, confirm no problems before pushing to production.
A more stable approach is to only upgrade patch versions. For example, if Flask 2.0.1 has vulnerability, first try the latest version of 2.0.x rather than directly jumping to 2.3.0. Besides fixing specific vulnerabilities, there are some good habits that can keep your images secure long-term: This way the final image won’t contain Go compiler, source code, or intermediate files - clean and neat, much smaller attack surface.
Many images default run applications as root, which is basically suicidal. After hackers breach the application they directly get root permissions, can do whatever they want. Create a regular user, let the application run with that identity - much safer. This is easily overlooked. Your code might not have changed in half a year, but base image system packages are constantly updating patches. Rebuild at least once a month to include the latest security patches.
Our team set up a scheduled task to automatically rebuild all production images every Sunday, scan them once, and problems found Monday can be discovered and fixed. Accidentally packaging .env file into the image and database password leaks. .dockerignore is like .gitignore, preventing sensitive files from being packaged.
I need to emphasize this again. FROM python:latest is a ticking bomb - you have no idea what version you’re pulling or if it has vulnerabilities. Use explicit tags like FROM python:3.11.7-slim - predictable and traceable. Manually scanning images is too troublesome and easy to forget. The most reliable way is to integrate scanning into CI/CD, automatically checking every code commit or image build.
GitHub Actions integrating Trivy is unbelievably simple. Create .github/workflows/docker-scan.yml in your repository: After first-time configuration, push code once to try. You’ll see scan results in GitHub Actions tab. If there are vulnerabilities, this build will be marked red and won’t be merged into main branch. It’s like adding an automatic security gate to your code repository.
If you use GitLab, integration is similar. Create or modify .gitlab-ci.yml in repository root: Note the allow_failure: false line, meaning if security scan fails, let the entire pipeline fail. If you don’t want to be this strict, can change to allow_failure: true , then vulnerabilities found are just warnings, not blocking deployment. But I suggest production environment pipeline must be set to false. Development environment can be looser, but production environment can’t compromise.
If your company uses Harbor as private image registry (many large companies do), it’s even more worry-free. Harbor from v1.2 onwards has integrated Trivy and Clair, can automatically scan pushed images. This way even if someone bypasses CI/CD directly deploys, Harbor will intercept at the last checkpoint. Stringing together the previous content, a complete image security process should look like this: This process looks complex, but after configuring once it’s fully automated. Our team took about one Sprint (two weeks) from configuration to stable operation, but gained long-term security assurance.
Honestly, since configuring this process, I sleep much more soundly at night. At least don’t have to worry about someday suddenly a big vulnerability erupts and discovering my images were already hit. Back to the Log4Shell story at the article beginning. If we had this image security scanning process back then, vulnerabilities would have been discovered in CI/CD stage and never entered production environment. There wouldn’t have been that heart-pounding morning or the boss’s soul-searching question.
Honestly, the 76% figure for Docker Hub images containing vulnerabilities did initially shock me. But thinking about it now, this also shows most teams haven’t taken it seriously yet. If you start acting now, you’ll at least do better than 76% of people - isn’t that quite a sense of achievement? My suggestion is: don’t think about fixing all vulnerabilities at once, that’s unrealistic. Start from the simplest: Container security is a continuous process, not a one-time thing. But as long as you establish the process, subsequent maintenance really isn’t burdensome. Our team now scans automatically weekly, glances at issues in weekly meetings, basically can handle it in half an hour.
Emphasizing one more time: production environment images must be scanned! Images pulled from Docker Hub must be scanned! Don’t wait until something happens to regret, by then it’s too late. If you have any Docker security practical experience or stories, welcome to share in comments. Let’s progress together, making containerized applications more secure.
If you landed here from search, the fastest way to build context is to jump to the previous or next post in this same series. Complete Guide to Docker Nginx: Configuration File Mounting, HTTPS Setup, and Reverse Proxy Complete tutorial on Docker Nginx deployment covering configuration file mounting, HTTPS certificate setup, and reverse proxy. Solves common issues like config not taking effect and container communication, includes Let's Encrypt auto-renewal and production best practices.
Running Docker containers as root creates serious security risks. This comprehensive guide explains container escape vulnerabilities, provides complete security solutions including Dockerfile USER directive, --user parameter, Capabilities fine-grained permission control, and AppArmor configuration for production-grade secure containers. Docker vs Virtual Machines: A 5-Minute Guide to Performance Differences and When to Use Each Containers are at the heart of modern DevOps workflows, but they’re not immune to vulnerabilities. That’s where Trivy comes in! Trivy is a powerful, open-source vulnerability scanner that makes securing your container images straightforward and effective. In this post, we’ll explore how to use Trivy to scan Docker images and ensure your applications are secure.
1.Update the Vulnerability Database Keep the database current to ensure the latest vulnerabilities are detected: 4. Practical Deployment, Analysis & Case Studies 2.Focus on Fixing Critical Issues Prioritize addressing CRITICAL and HIGH vulnerabilities first to minimize risk. 3.Integrate Scanning Early Shift security left by integrating Trivy scans into your CI/CD pipelines.
Trivy makes vulnerability scanning easy, fast, and effective. Whether you're working with container images, IaC, or application dependencies, it’s a must-have tool for your DevSecOps toolkit. Want to explore more about Trivy? Check out the official documentation . Start scanning today and keep your applications secure! A comprehensive guide to using Trivy for scanning container images, detecting vulnerabilities, and integrating security checks into your CI/CD pipeline.
"Security scanning should not be an afterthought. By integrating Trivy into your workflow, you catch vulnerabilities before they reach production - shifting security left where fixes are cheapest." Trivy is an open-source vulnerability scanner developed by Aqua Security. It scans container images, filesystems, git repositories, and Kubernetes clusters for known vulnerabilities, misconfigurations, and exposed secrets. Unlike heavier alternatives, Trivy runs as a single binary with no database setup required - it downloads vulnerability databases automatically and caches them locally.
Trivy supports multiple installation methods depending on your operating system and preferences. In CI/CD pipelines, you typically want to fail builds only for serious vulnerabilities. Sometimes you need to suppress known vulnerabilities that are false positives or accepted risks. Integrating Trivy into your CI/CD pipeline ensures every image is scanned before deployment.
For per-registry credential pairs, prefer trivy registry login , which writes credentials to ~/.docker/config.json and is then picked up automatically. Scan Early and Often : Integrate Trivy into your CI/CD pipeline to catch vulnerabilities before they reach production. Scan on every pull request and before every deployment.
Set Appropriate Severity Thresholds : Use --severity HIGH,CRITICAL in production pipelines. Do not block builds on LOW severity issues - they create alert fatigue. Use --ignore-unfixed : Filter out vulnerabilities that have no available fix. You cannot patch what does not have a patch yet. Maintain an Ignore File : Document accepted risks in .trivyignore with comments explaining why each CVE is ignored. Review this file regularly.
Update Trivy Regularly : New vulnerability definitions are added daily. Run trivy image --download-db-only to update the database, or use the latest Trivy Docker image in CI. Generate SBOMs : Use CycloneDX or SPDX output formats to generate Software Bills of Materials. These help with compliance and incident response.
Scan Base Images Separately : Know the vulnerabilities in your base images (alpine, debian, ubuntu) before adding your application layer. Use Minimal Base Images : Distroless, Alpine, or scratch-based images have fewer packages and therefore fewer potential vulnerabilities.
Fail Fast in Development : Use stricter thresholds in development ( --exit-code 1 --severity MEDIUM,HIGH,CRITICAL ) to catch issues early. Monitor Continuously : Vulnerabilities are discovered after images are built. Use Trivy in scheduled scans of running containers, not just at build time.
Container security is a continuous process, not a one-time check. By integrating Trivy into your development workflow and CI/CD pipelines, you establish a security baseline that grows stronger with every scan. For monitoring your containerized applications after deployment, OneUptime provides comprehensive observability to detect anomalies and ensure your services remain healthy and secure in production.
Every OneUptime blog post is open source. Found a typo, an inaccuracy, or have a clearer way to explain something? Anyone can contribute — your edits make this post better for everyone who reads it next. Your complete reliability stack unified: infrastructure monitoring, incident management, status pages, and APM. Open-source and self-hostable.
"Manual scanning finds yesterday’s risks, automated scanning protects tomorrow’s releases As DevOps and security merge into DevSecOps, automation becomes key to maintaining secure and fast software delivery. One tool that has become essential in this space is Trivy, an open-source vulnerability scanner that detects security issues in container images, file systems, IaC (Infrastructure as Code) templates, and more.
This guide walks you through how to automate vulnerability scans using Trivy, integrate it into CI/CD pipelines, and ensure your software stays secure — without slowing down your delivery cycle. In 2025, over 85% of security breaches are linked to vulnerabilities in third-party components. With continuous deployment cycles, vulnerabilities can slip into production unnoticed. Automated scanning ensures: You’ll get a detailed vulnerability report with severity levels: LOW, MEDIUM, HIGH, and CRITICAL.
"Trivy turns vulnerability scanning from a task into a habit and from a habit into a safety net If any critical vulnerability is detected, the pipeline will fail, preventing unsafe code from deploying. You can even automate this using CronJobs in Kubernetes to perform daily scans and push results to Slack or email. 1. Slow vulnerability scans This usually happens when Trivy is using an outdated local cache. Refreshing the cache resolves the issue. Solution: Run trivy --refresh to update the data.
2. False positives during scans This problem occurs if the vulnerability database is old or outdated. Solution: Always update the database before running scans by executing a Trivy DB update command. 3. CI/CD pipeline failures caused by Trivy If the pipeline keeps failing during scans, it often means the severity thresholds are too strict. Solution: Adjust the exit-code configuration or relax the severity filters to match your risk tolerance.
4. Missing or unreported CVEs This can happen if the base image uses an OS that Trivy doesn't fully support. ** Solution:** Check the container image’s base OS for compatibility or enable debug mode using --debug to identify the issue. Q1: Is Trivy free to use? Yes, Trivy is completely open-source under the Apache 2.0 license. Q2: How often should I scan images? Ideally, before every deployment — or at least daily in production environments.
Q3: Can Trivy scan for secrets? Yes, it detects secrets and sensitive credentials in code and configurations. Q4: Does Trivy work offline? Yes, after downloading its vulnerability database locally. Q5: How do I export Trivy reports? Use the -f json -o report.json flag for JSON reports or --format template for custom ones. Security isn’t a one-time task — it’s a continuous process. By automating vulnerability scans with Trivy, DevOps teams can shift security left, identifying and fixing issues before deployment. Trivy’s speed, accuracy, and ease of integration make it one of the best tools for DevSecOps automation in 2025 and beyond. Start small, automate often, and let your pipelines protect your production.
About the Author: Narendra is a DevOps Engineer at AddWebSolution , specializing in automating infrastructure to improve efficiency and reliability. Shipping containers without verifying their contents is a security liability that no modern engineering team can afford. Container image scanning with Trivy provides a fast, open-source mechanism to identify OS package vulnerabilities, application dependencies, embedded secrets, and infrastructure-as-code misconfigurations before deployment. Whether you are securing a Laravel application or a complex microservices platform, integrating this scanner into your workflow is the first line of defense against supply chain attacks.
Trivy operates as a standalone binary that unpacks container layers and indexes their contents against multiple upstream vulnerability databases, including NVD, Red Hat, Debian, and GitHub Advisory. Unlike older scanners that only checked OS packages, Trivy also parses language-specific lock files (like composer.lock , package-lock.json , or go.mod ) to detect application-level dependencies. This dual-layer inspection is critical because a base image might be patched while the application layer contains a vulnerable library version.
The scanner maintains a local cache of these databases, typically stored in ~/.cache/trivy , which allows subsequent scans to run in seconds rather than minutes. For teams building Docker containers for Laravel applications , this means you can validate every build artifact locally before pushing to a registry. The tool also supports scanning filesystems directly, git repositories, and even running Kubernetes clusters, making it a versatile component in a broader CI/CD security strategy .
Installation is straightforward across all major platforms. On macOS, use Homebrew; on Linux, the official install script or package managers work reliably. Avoid downloading random binaries from unverified sources—always use the official Aqua Security release channels. A common mistake in 2026 is ignoring the database update step in air-gapped or restricted network environments. If your development machines lack direct internet access, you must manually download the trivy-db.tgz and trivy-java-db.tgz artifacts and place them in the cache directory. Without current databases, the scanner will produce false negatives, giving you a dangerous sense of security.
Not every vulnerability requires immediate action. Configure Trivy to focus on actionable findings by setting severity filters and using .trivyignore files for accepted risks. This prevents alert fatigue during development. Document every ignored CVE with a justification and expiration date. During SOC 2 or ISO 27001 audits, reviewers will examine these exceptions. An undocumented ignore file is a compliance finding itself.
Local scanning catches issues early, but pipeline integration enforces standards consistently. The goal is to fail builds when critical vulnerabilities exist while allowing warnings to pass with visibility. This balance prevents security from becoming a blocker while maintaining accountability. For GitHub Actions users, the official aquasecurity/trivy-action simplifies integration. GitLab CI and Jenkins have equivalent plugins or shell execution patterns. The key is outputting results in SARIF format for native platform integration and JSON for archival.
5. Performance Evaluation & Extended Technical Observations Set exit-code: '1' only for severities you genuinely intend to block. Starting with CRITICAL-only failures and expanding to HIGH after team buy-in prevents pipeline breakage from legacy debt. Track metrics over time: if your team consistently produces images with zero CRITICAL findings, tighten the threshold. Security maturity is incremental, not binary.
Vulnerability scanning is table stakes. Modern container image scanning with Trivy extends to three additional categories that often pose greater operational risk than known CVEs. For teams managing secrets with HashiCorp Vault , Trivy serves as a validation layer: if a secret appears in a scan, your injection mechanism failed. Treat every secret finding as a process defect, not just a cleanup task.
Choosing a scanner depends on your team's constraints: budget, ecosystem integration, compliance requirements, and maintenance tolerance. No tool is universally superior. In practice, many organizations run Trivy alongside a cloud-native scanner. Trivy catches issues pre-push in CI, while ECR or GCR scanning provides continuous monitoring of stored artifacts. This defense-in-depth approach aligns with AWS Well-Architected security pillars and similar frameworks. Grype is excellent for quick local checks but lacks IaC and secret coverage. Snyk offers superior developer experience and fix guidance but introduces vendor dependency and cost at scale.
Adopting container image scanning with Trivy is not a one-time setup—it is an ongoing engineering discipline. Start by integrating scans into your CI pipeline with CRITICAL-only blocking. Establish a weekly review cadence for HIGH-severity findings, assigning ownership and remediation timelines. Maintain your .trivyignore file as living documentation, not a graveyard of unaddressed risks. Automate database updates in air-gapped environments using scheduled jobs or artifact mirroring.
Security tooling only delivers value when teams trust and act on its output. False positives erode trust faster than any vulnerability exploits a system. Invest time tuning policies, documenting exceptions, and celebrating reductions in vulnerability counts. If your team needs help establishing a sustainable container security program or preparing for compliance audits, reach out to discuss your specific infrastructure challenges .
A container image that ships to production with an unpatched critical CVE is not a rare event. It is the default outcome unless someone builds a gate to stop it. Trivy container scanning gives teams that gate: an open-source scanner from Aqua Security that reads a container image, a filesystem, a Dockerfile, or a running Kubernetes cluster and reports exactly which packages carry known vulnerabilities, which secrets got baked in by accident, and which infrastructure-as-code files are misconfigured.
This tutorial builds a working Trivy container scanning pipeline from a blank terminal to a CI/CD gate that blocks a bad merge, plus a cross-check against Grype and a continuous scan of a live Kubernetes cluster. Every command below was tested against Trivy v0.74.0 (released August 14, 2026) and Grype v0.119.0 (released September 17, 2026), the current stable releases as of this writing. By the end you will have a repeatable workflow, not just a one-off scan.
Add Shattered once in the Google app and our stories show up in your news suggestions. Software supply chain attacks stopped being a theoretical risk years ago, and the numbers from 2025 back that up. Sonatype’s Attacking the Assembly Line research logged 3,430 malware advisories tied to open source packages in 2025, a 3.69x jump over the roughly 931-advisory-per-year baseline recorded before generative AI tooling accelerated both attacks and defenses. Of the advisories Sonatype could classify, 47.3% were targeted attacks aimed at specific organizations or supply chains, up from just 2 to 4% a year during 2021 through 2024. Malicious packages built specifically to compromise a developer’s machine during install, not after deployment, made up 53% of the malware Sonatype tracked.
Runtime data tells a slightly better story. Sysdig’s 2025 Cloud-Native Security and Usage Report found that fewer than 17% of analyzed container images carried a high or critical vulnerability, and fewer than 6% of packages with a critical or high flaw were actually loaded into memory at runtime. That gap matters: it means most of what a scanner flags never gets executed, which is exactly why a scanning pipeline needs sane severity filtering rather than a blanket “fail on anything” rule. Get the filtering wrong and engineers start ignoring the scanner altogether.
Those figures explain why container image scanning moved from “nice to have” to a hard gate in most CI/CD pipelines. A tool that scans one image is a demo. A pipeline that scans every image, every Dockerfile, and every dependency, then blocks a merge automatically, is a control. The gap between the two is the difference between a security team that finds out about a vulnerable image from an auditor and one that finds out from its own build log.
None of this requires a large security team or an expensive platform. Trivy and Grype both run as free, open-source binaries, and the workflow this tutorial builds fits inside a standard CI runner with no additional infrastructure. That accessibility is part of why container image scanning shows up in nearly every modern DevSecOps checklist now, regardless of company size. Trivy and Grype solve the same core problem from different starting points. Trivy, built by Aqua Security, scans container images, filesystems, git repositories, Kubernetes clusters, Terraform, and CloudFormation from one binary, and it bundles secret detection and misconfiguration checks alongside CVE matching. Grype, built by Anchore, focuses tightly on vulnerability matching against images and filesystems, and it pairs naturally with Syft, Anchore’s SBOM generator, when you want a two-tool pipeline with a clean separation between “generate the inventory” and “check the inventory against a CVE database.” Running both in the same pipeline is not redundant. Vulnerability databases disagree at the margins because they pull from different upstream feeds and apply different matching logic, so a package that Trivy flags as fixed might still show up in Grype’s output for a day or two until its database syncs, or vice versa. Treat disagreement between scanners as a signal to double-check the advisory manually rather than a bug in either tool.
Grype’s database updates are fast and its output format is simple to parse, which makes it a good second opinion in a CI step that only needs a pass/fail signal. It also integrates cleanly with Syft-generated SBOMs, so if your pipeline already produces a CycloneDX or SPDX file for compliance reasons, Grype can scan that file directly instead of re-pulling the image. For most teams the practical answer is to run Trivy as the primary gate because it covers images, IaC, and secrets in one pass, then run Grype as a lightweight cross-check on the final image before it ships. This tutorial builds exactly that setup.
You do not need a large environment to follow along, but pin these versions so your output matches the examples below. Check the Trivy release notes and the Grype release notes before you start, since both projects ship updates frequently. Nothing here requires a paid tier. Trivy and Grype are both fully open source under Apache 2.0, and the vulnerability databases they pull from are free to query, though heavy CI usage benefits from the caching step covered later.
Step 1: Install Trivy. On Linux or macOS, the fastest path is the official install script, which drops a pinned binary into your path. Full install options, including package manager repositories for every major distribution, live in the official Trivy documentation . Avoid piping curl straight into a root shell in production. Download the script, read it, then run it with a pinned version.
On macOS with Homebrew, brew install trivy pulls the current formula. On Debian or Ubuntu, add Aqua Security’s apt repository instead of relying on the distro’s default package, which often lags several versions behind. If you would rather not install anything locally, the containerized form works everywhere Docker runs: Step 2: Run your first image scan. Point Trivy at any public image to confirm the install works and to watch it pull its vulnerability database on first run, which takes a minute or two depending on your connection.
That single command already tells you more than most teams check before a deploy: what’s installed, what’s vulnerable, and whether a fix exists. Step 3: Interpret severity levels and exit codes. Trivy classifies findings as UNKNOWN, LOW, MEDIUM, HIGH, or CRITICAL, pulled from the CVSS score reported by the upstream advisory. By default the CLI exits with code 0 no matter what it finds, which is useless in CI. You control the gate with two flags.
Now the process exits with 1 if any HIGH or CRITICAL finding shows up, and 0 otherwise, which is exactly the signal a CI job needs to fail a build. Trivy also supports --format json , --format sarif , --format cyclonedx , and --format table (the human-readable default), so pick the format the next tool in your pipeline expects rather than parsing plain text with regex. Step 4: Filter noise with –ignore-unfixed. Given that Sysdig’s data shows under 6% of high/critical findings actually load at runtime, and a meaningful share of the rest have no available patch yet, blocking a build on every unfixed CVE just trains engineers to bypass the check. Add --ignore-unfixed so the gate only fires on vulnerabilities you can actually remediate today.
Track the unfixed findings separately in a dashboard rather than discarding them. A patch shipping next week can turn today’s “can’t fix it” into tomorrow’s blocked build if you never revisit the list. A simple weekly job that re-scans your currently deployed images against the latest database catches exactly this case, surfacing a fix that didn’t exist when you first shipped the image without requiring a new build to trigger the check.
Step 5: Scan your Dockerfile for misconfigurations. A clean image can still ship from an insecure Dockerfile, running as root, exposing an unnecessary port, or baking a build argument into a layer where it persists after the build finishes. Trivy’s config scanner checks the Dockerfile itself, not just the built image. A typical finding flags a missing USER directive, meaning the container runs as root by default, or a COPY instruction with overly broad permissions. Fixing this class of issue at the Dockerfile level is cheaper than catching it after deploy, since it enforces container security posture before an image ever gets built. This ties directly into broader hardening practices, and if you have not locked down runtime privileges yet, our container security hardening walkthrough covers the cluster-side controls that complement image-level scanning.
Step 6: Catch hardcoded secrets before they ship. Trivy’s secret scanner runs against the same target and looks for patterns matching API keys, private keys, and cloud credentials accidentally committed into a layer. If this step ever finds a live cloud access key baked into a layer, rotate that key immediately, because rebuilding the image without the secret does not invalidate a key that already leaked. Leaked cloud credentials remain a routine finding in CI pipelines, which is exactly why one hardcoded key in a Dockerfile layer can turn a routine scan into an incident report.
Step 7: Generate a software bill of materials. An SBOM is a structured inventory of every package, library, and dependency in your image, and it has become the standard artifact regulators, auditors, and downstream customers ask for. Trivy generates one directly, in either the CycloneDX or SPDX formats, both maintained as open standards. Store both files as build artifacts alongside the image tag they describe. An SBOM without a clear link back to the exact image digest it covers is close to useless during an incident, when the first question is always “which of our running images contains this package.” Tag the SBOM filename with the image SHA, not just a version string, so a latest retag six months from now cannot orphan the record.
SBOMs also pay off outside a single incident response scenario. When a new zero-day drops in a widely used library, most teams’ first move is a frantic search through every repository asking “do we use this package, and where.” An archive of per-build SBOMs turns that into a single grep or a database query instead of a days-long audit across dozens of services, which is exactly the scenario CISA and other national cybersecurity agencies had in mind when they started pushing SBOM requirements into procurement rules.
Step 8: Add Trivy to GitHub Actions with SARIF upload. The official action, aquasecurity/trivy-action, wraps the CLI and can upload results directly to GitHub’s code scanning tab in SARIF format, which surfaces findings inline on pull requests without a separate dashboard. Notice the if: always() on the upload step. Without it, a failed scan (which is the whole point of the job) skips the upload too, so you get a red build with no detail on why it failed. Pin the action to a specific version tag like 0.36.0 rather than @master , since a moving tag on a security-critical action is exactly the kind of dependency a supply-chain attacker targets.
Step 9: Add Trivy to GitLab CI. GitLab’s own container scanning template wraps a Trivy-based analyzer, but you can also invoke Trivy directly for tighter control over flags and output format. GitLab maintains its own container scanning documentation if you want the fully managed template instead of a hand-rolled job. The hand-rolled version above gives you the exact same severity filtering and exit-code behavior you already tested locally, which keeps local and CI results consistent, a detail that matters more than it sounds like when a developer says a build passed on their own machine.
Step 10: Cache the vulnerability database for faster builds. Every fresh Trivy run without a cache pulls the full vulnerability database, which adds 30 to 90 seconds to every CI job depending on network conditions. Persisting the cache directory between runs turns that into a small incremental update. For high-volume pipelines running dozens of scans a day, standing up Trivy in client/server mode avoids redundant database downloads entirely, since every job talks to one shared server instead of maintaining its own local copy. That setup is covered in the advanced tips section below.
Step 11: Suppress false positives with .trivyignore and VEX. Not every finding deserves a block. If your team has manually verified that a flagged package is not reachable in your code path, or a patch genuinely does not exist and the risk is accepted, record that decision instead of silently working around the gate. For a more auditable approach than a flat ignore file, use a VEX (Vulnerability Exploitability eXchange) document, which records not just that a CVE is suppressed but why, in a machine-readable format Trivy can consume with --vex . VEX matters more as your SBOM output starts feeding external audits, since “we ignored it” and “we assessed it as not exploitable, documented, and reviewed” are very different answers to give a customer’s security team.
Step 12: Scan a running Kubernetes cluster continuously. A scan at build time catches problems in the image you’re about to deploy, but it says nothing about the images already running, some of which may be months old and vulnerable to CVEs disclosed after they shipped. Trivy Operator v0.34.0 closes that gap by running scans continuously inside the cluster and exposing results as native Kubernetes resources.
If you already run an EKS cluster , the operator works the same way against managed control planes as it does against self-managed nodes, since it runs as a normal in-cluster workload rather than depending on cloud-provider-specific APIs. Watch the reports for images running with severities you already gate against in CI, since a running image that fails your build-time policy but somehow made it into production usually points to a gap in deployment controls, not the scanner.
Step 13: Cross-check results with Grype. Before a release candidate ships, run Grype against the same image as a second opinion. Discrepancies are rare but worth catching before, not after, a customer’s security team finds them independently. Grype’s --fail-on high flag mirrors Trivy’s exit-code behavior, and --only-fixed is the Grype equivalent of Trivy’s --ignore-unfixed . Keeping the flag logic symmetric between the two tools makes the pipeline easier to reason about months from now when someone who didn’t write it has to debug why a build failed.
Step 14: Tie every piece into one working project. Individually, each command above is a script. Together, they form a workflow: build, scan the Dockerfile, scan the image for CVEs and secrets, generate an SBOM, cross-check with a second scanner, and only then push to a registry. A Makefile keeps the sequence consistent whether a developer runs it locally or CI runs it on every push.
Replace the individual scan steps in the GitHub Actions and GitLab CI jobs shown earlier with a single make ship call, and the exact same sequence runs whether a developer tests it on a laptop or a runner executes it in the cloud. That consistency is the real payoff of building a project instead of copy-pasting individual scan commands into a pipeline: nobody debugs a CI-only failure they can’t reproduce locally.
Run make ship once against a deliberately outdated base image (try node:16 instead of node:20-alpine ) to confirm every gate actually fires before you trust it in production. If scan-config or scan-secrets passes silently when it shouldn’t, check that the exit code from each Trivy invocation is actually propagating, since a swallowed non-zero exit code in a shell pipeline is one of the most common ways teams discover their working gate never blocked anything.
Once the basic gate is running reliably, a few refinements pay off at scale. Track findings over time rather than treating each scan as a one-off pass/fail event, since a security posture that’s improving matters more to stakeholders than a single green checkmark. Export JSON output to a time-series store and chart the trend of open HIGH/CRITICAL findings per service. Set a base image update cadence too, since a stale base image accumulates new CVEs even when your own application code never changes. Rebuilding weekly against the latest patched base image, even with zero code changes, closes a class of vulnerabilities that a scan-only workflow can flag but never actually fixes on its own. Pair that cadence with automated dependency update tooling so the rebuild also picks up patched application-level packages, not just a refreshed base layer.
For organizations running hundreds of scans a day across many repositories, standing up a shared Trivy server avoids each job downloading its own database copy. Start the server once, then point every client at it. Harvested Online Documentation & Reference Sources • https://trivy.dev/docs/latest/guide/target/container_image/ • https://blog.gntech.me/posts/2026-05-26-docker-trivy-vulnerability-scanning/ • https://hub.docker.com/r/aquasec/trivy • https://trivy.dev/docs/latest/guide/references/configuration/cli/trivy/ • https://betterstack.com/community/guides/scaling-docker/trivy-container/ • https://eastondev.com/blog/en/posts/dev/20251218-docker-security-scanning/ • https://dev.to/arunranu/secure-your-docker-images-with-trivy-a-step-by-step-guide-2ihb • https://oneuptime.com/blog/post/2026-01-27-trivy-container-scanning/view • https://dev.to/addwebsolutionpvtltd/how-to-automate-vulnerability-scans-with-trivy-3b14 • https://khimananda.com/blog/container-image-scanning-with-trivy
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Docker Container Vulnerability Scanning Tool Using Trivy.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Docker Container Vulnerability Scanning Tool Using Trivy... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |