Complete Technical Paper Content — Drone Communication Security And Anti Hijacking System
Overview & System Context
Drone Communication Security And Anti Hijacking System: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9544 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Shahed drones are Iranian unmanned combat aerial vehicles (UCAVs) and loitering munitions developed by Shahed Aviation Industries. Shahed drones are manufactured both in Iran and in Russia, with the Russian variant building upon Iranian plans.
Following the 2022 Russian invasion of Ukraine, both variants have been deployed by Russian forces against Ukraine during the Russo-Ukrainian war and by Iranian forces during the 2026 Iran war. During the seventy-eighth session of the United Nations General Assembly in September 2023, the United States accused Iran of supplying Russia with drones during the Russian invasion of Ukraine, and aiding Russia in the development of a drone production plant. Iranian president Ebrahim Raisi denied the allegations, responding, "We are against the war in Ukraine." Months earlier, Sky News received purported document evidence dated 14 September 2022 from an informed source that Russia had purchased over US$1 million of artillery and tank shells and rockets. In June 2023, a U.S. intelligence finding released by the White House reported Iran was supplying Russia with materials to construct a drone manufacturing plant. In February 2024, additional document evidence was leaked revealing Russia's purchases of drones and an arrangement for Iran to assist Russia in developing a manufacturing facility, both purchased for a total of US$1.75 billion, paid in gold ingots.
According to the document submitted to the G7, the Iranian government is trying to "disassociate itself from providing Russia with weapons" and that "[it] cannot cope with Russian demand and the intensity of use in Ukraine." Consequently, the Yelabuga drone factory was established with Iranian assistance in Alabuga Special Economic Zone, part of the Republic of Tatarstan, an autonomous region of Russia, more than 1,300 km (810 mi) from the Russia–Ukraine border. The manufactory is next to the Kama River, permitting transportation by ship directly from Iran via the Caspian Sea, and is operated by the company Albatross, which employs students as young as 15 years old from Alabuga Polytechnic College to construct the combat drones. Russia aims to build 6,000 UCAVs by summer 2025 at a rate of 310 drones per month if the factory operates 24 hours a day, predicting the cost of production of one Geran-2 to be US$48,000. However, Russia has upgraded the drones over several iterations and has consequently increased the unit production cost to around US$80,000 as of April 2024. Iranian drone technology was deployed in combat during the Russian invasion of Ukraine. Russia used Iranian Shahed 136 drones in an attack on Kyiv on 17 October 2022, during which four civilians were killed, including one woman who was six months pregnant. Another Russian attack using Iranian drones took place on 28 May 2023. Ukraine said it shot down all but one of the drones, but one person was killed. Another strike on 20 June used 35 Shahed drones, 32 of which were claimed to have been shot down by Ukraine. On 22 November 2024, Russia attacked a residential area in Sumy, Ukraine, using Shahed drones. Two civilians were killed in the attack and 12 were injured. On 17 May 2025, Russia conducted multiple attacks across Ukraine involving Shahed drones, killing at least 13 civilians and injuring 32. In July 2025, there were multiple reports, including a documentary by Russian defense ministry channel Zvezda, indicating that Russia was using children and teenagers to assemble Shahed drones used to attack Ukraine.
The Shahed 121 was first noticed in 2016 when it flew over USS Harry S. Truman, a nuclear-powered aircraft carrier, in international airspace. The US Navy regarded this as a security breach which had not happened since 2014. The incident occurred after a nuclear deal that Iran signed with world powers, including the US. A US Navy Seahawk helicopter filmed the incident. The flight of Shahed 121 was considered by Iranian authorities to be safe as its wings were all "clean", implying that the drone did not carry weapons and was not dangerous to ships, but the high command of the US Navy described it as "abnormal" and "unprofessional." The Shahed 129, sometimes S129, is an Iranian single-engine medium-altitude long-endurance UCAV designed for the Islamic Revolutionary Guard Corps. It is capable of combat and reconnaissance missions. It has an endurance of 24 hours; it is similar in size, shape, and role to the American MQ-1 Predator. The Shahed 129 has been used for airstrikes in the Syrian Civil War and for border patrol on Iran's eastern border. As of 2017, the Shahed 129 and Shahed Saeqeh are expected to form the backbone of Iran's high-end UAV fleet for at least the next decade.
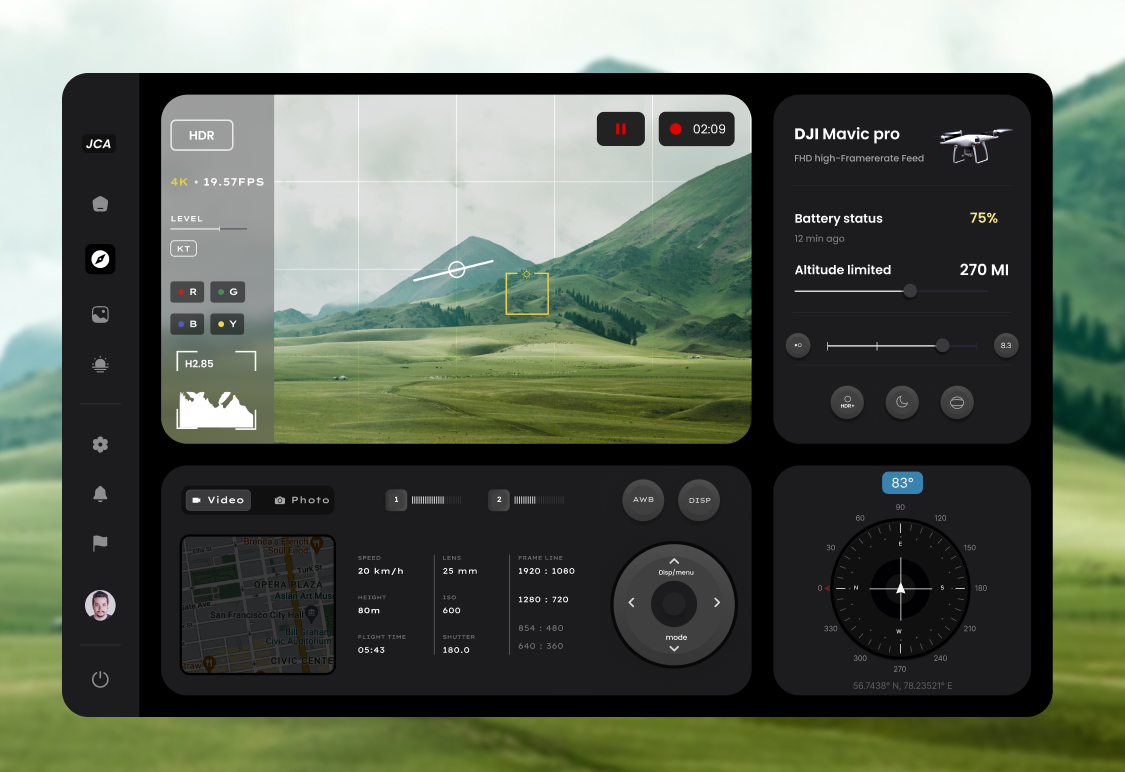
Figure 1: Agricultural drone surveillance system user interface – Artofit The Shahed 131, also called Geran-1 (Russian: IIIIII-1, literally "Geranium-1") in Russian service, came to prominence in October 2022 during the Russo-Ukrainian war. It is powered by a Wankel engine model Shahed-783/788. The Shahed-131 flight control unit was found to be able to connect with Iridium satellites, which in theory allows the flight path to be altered mid-flight. The flight controller has a backup inertial navigation system by MEMS gyroscope. Its primary instructions are derived from a commercial-grade GPS unit. The Shahed 131 is visually distinguished by vertical stabilisers that extend only upwards from the ends of the wings, while on the larger Shahed 136 they extend both up and down. It has a 15 kg (33 lb) warhead and has a range of 900 km (559 mi).
The HESA Shahed 136, or simply Shahed 136, known also as the Geran-2 (Russian: IIIIII-2) in Russian service, is a loitering munition in the form of an autonomous pusher-prop UCAV. It is designed and manufactured by Iran Aircraft Manufacturing Industrial Company, or HESA, in association with Shahed Aviation Industries. Its first appearance was 13 September 2022, when photos of the remains of a drone used by Russian forces during the invasion of Ukraine were publicly released. The wings were inscribed with "M412 IIIIII-2" ("M412 Geran-2" in Russian) as a means of disguising the drone and concealing Iran's part in the invasion of Ukraine, but it was recognized by its wing design, and Geran-2 drones are considered by Ukraine and its Western allies to be redesignated Iranian-made Shahed 136 drones. Experts have estimated a Shahed 136 costs between US$20,000 to US$50,000 to make. A series of leaked emails and documents revealed Russia had purchased 6,000 Shahed 136s for US$193,000 each in 2023. Russia is reported to be manufacturing a version of the Shahed 136, and Ukraine was also planning to produce its own version. The drones were used in the October 2022 missile strikes on Kyiv.
The Shahed 147 is a twin-boom, high-altitude long-endurance (HALE) surveillance UAV powered by a turboprop engine. It possesses a wingspan of 26 m (85 ft) and a maximum flight altitude of 60,000 feet (18,288 metres). The drone also possesses Synthetic Aperture Radar imaging for surveillance. The Shahed 147 was revealed during the 19 November 2023 Iranian Aerospace Force Exhibition, attended by Iranian Supreme Leader Ali Khamenei.
The Shahed 149 Gaza was unveiled on 21 May 2021 and named after the Gaza Strip in honor of Palestinians' struggle amid the 2021 Israel–Palestine crisis. The drone is a high-altitude, long-endurance UAV similar in size, shape and role to the American MQ-9 Reaper. It is larger and heavier than the earlier Shahed 129. It has a flight duration of 24 hours, a maximum operating radius of 2,500 km (1,600 mi), 21 m (69 ft) wingspan, 340 km/h (210 mph) maximum speed and is capable of carrying 13 bombs and 500 kg (1,100 lb) of electronic equipment. It was the first Iranian UAV powered by a turboprop engine.
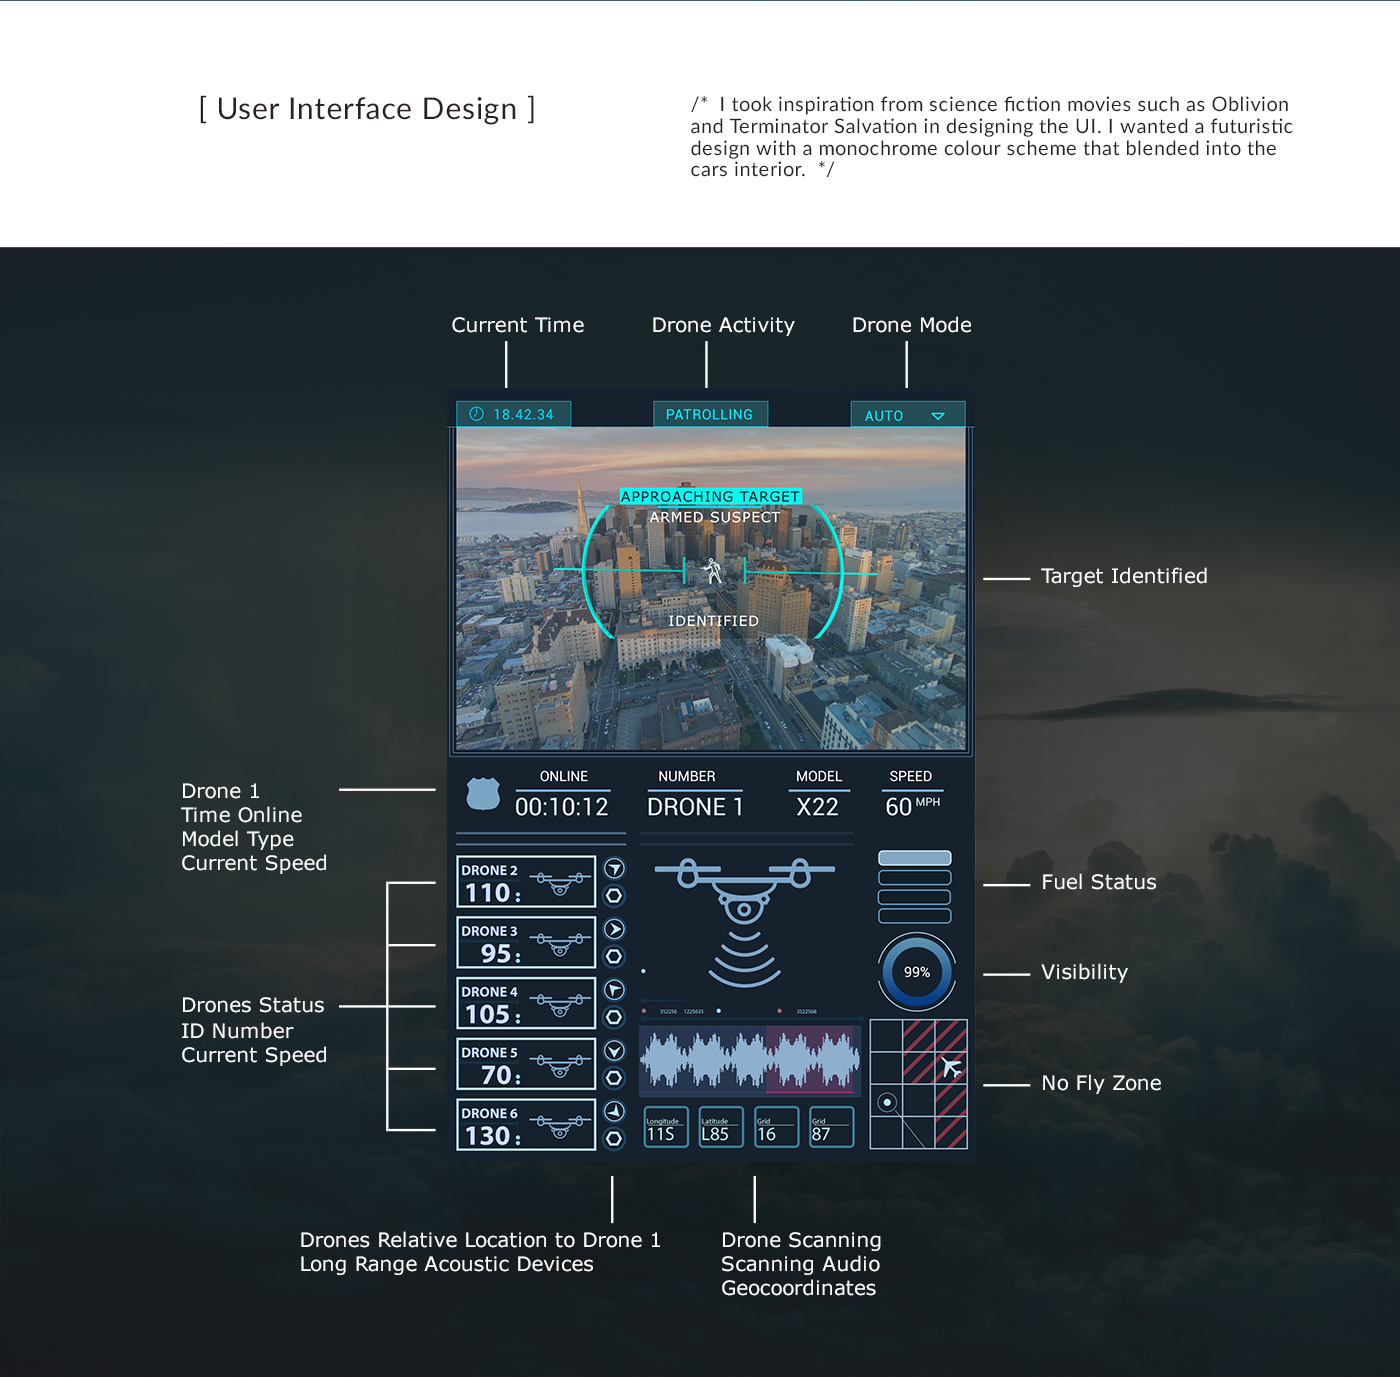
Figure 2: Police Drone User Interface on Behance The Shahed 171 Simorgh, named after a benevolent bird of Persian mythology, and called IRN-170 by the US government, is a jet-powered flying wing UCAV. It is based on an American Lockheed Martin RQ-170 Sentinel UAV that was seized by Iran in 2011 and reverse-engineered.
The Shahed 191, also called the Shahed Saeqeh, sometimes spelled "Saeqeh," was first revealed at an Iranian arms expo in October 2016. The name comes from the Persian word for "thunderbolt." Like the Shahed 171 Simorgh, the Shahed 191 is based on the seized Lockheed Martin RQ-170 Sentinel. The Shahed 191 has two variants, the Saeqeh-1 and the Saeqeh-2. The Geran-4 is based on the Geran-3 design, featuring an improved airframe and a Chinese-made turbojet engine producing 160 kgf (1,600 N; 350 lbf) of thrust. According to Ukrainian intelligence, the drone can fly at a speed of 500 km/h (310 mph) while carrying a 50 kg (110 lb) warhead and has a maximum range of 600 to 850 km (370 to 530 mi). Geran-4 drones were first employed during attacks on Ukraine in May 2026.
Just as with Western support for Ukraine, the Iranian drone build-up will have implications that go beyond this specific conflict. Iranian drones are increasing not only in number, but also sophistication and lethality, a development that concerns the United States and Europe. In response, we can expect Western actors to prioritise the production and export of low-cost defence systems able to counter the mass-produced drones directed by Iran, Iranian proxies, and other adversaries.
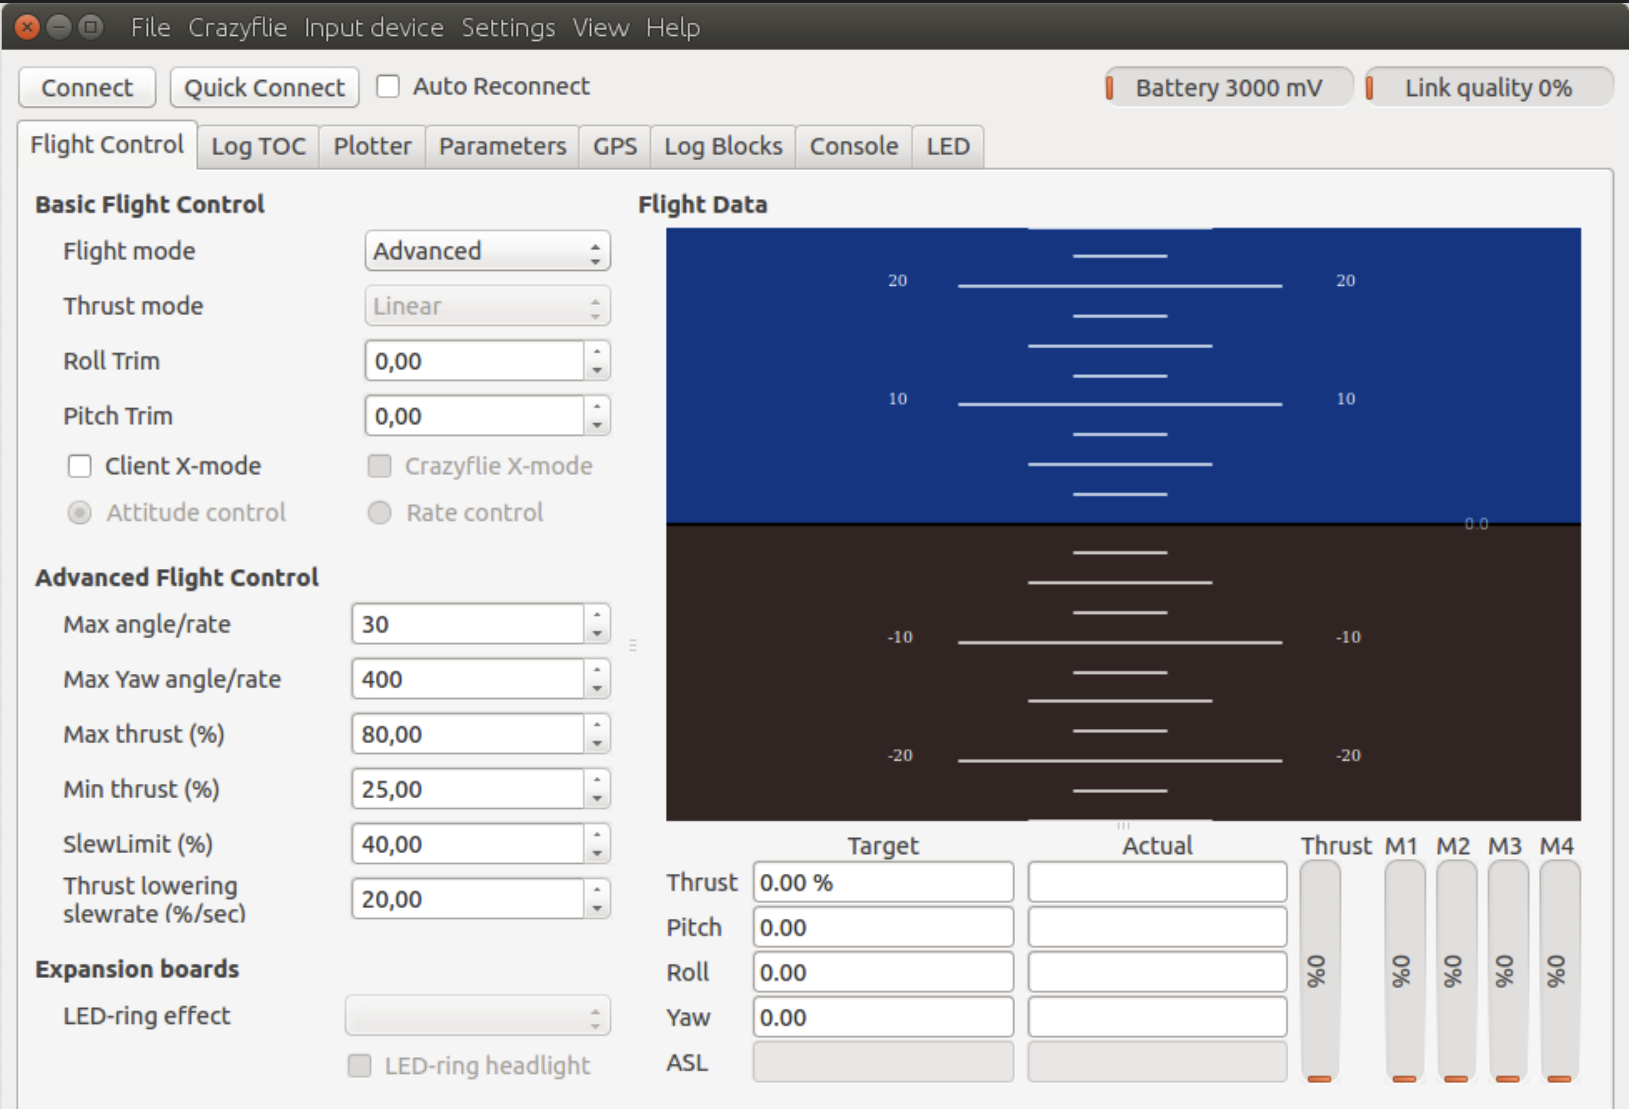
Figure 3: Wireless Attacks against Micro Aerial Drones | Cyber-Physical Systems ... Foreign involvement in the Russian invasion of Ukraine Iran and the Russian invasion of Ukraine Low-cost Uncrewed Combat Attack System – a US system partially derived from the Shahed 136 Drone security is crucial due to their widespread adoption in industries such as military, construction, and community services.
With the increasing use of drone swarms, even minor security lapses can lead to significant risks. This cheat sheet provides an overview of vulnerable endpoints in drone systems and strategies to mitigate security threats. The communication between the drone and the GCS is vulnerable to interception and attacks. This will be made evident in the future sections as well. It is important to understand that peripherals attached to drone may be vulnerable too! To explain this, we have made a list of vulnerable endpoints below.
Insecure Communication Links – Data transmitted between the drone and GCS can be intercepted if not properly encrypted. Use standard protocols for encryption of any data being sent over. Command Spoofing and Replay Attacks – Authenticate command messages and reject replayed messages using the protocol's freshness checks. For MAVLink, use message signing and timestamp validation ; encryption alone does not provide these controls.
Wi-Fi Weaknesses – Weak authentication or unprotected channels can allow unauthorized access. This is even possible through simple microcontrollers like ESP8266 ! An additional SoC (called the companion computer ) to manage peripherals (like the cameras, LiDARs etc.) and send telemetry data.
Thus, it becomes very important to maintain their security as well. The possible risks in this case are: Companion Computers – Open ports (e.g., SSH, FTP) can be exploited if not securely configured. User Error and Misconfiguration – Misconfigured security settings can expose the drone to risks. Drones often handle sensitive information (e.g., mission details, sensor logs, or edge AI models) and face a high risk of being lost or captured. Therefore, it's important to protect the onboard data: If your drone is ever captured or lost, you should ensure that it's not physically possible to steal data from it. This may happen under the following conditions: Insufficient Physical Security – Unsecured USB ports or exposed hardware can lead to data theft or tampering.
Insecure Supply Chain – Compromised components from suppliers can introduce hidden vulnerabilities. End-of-Life Decommissioning Risks – Improperly decommissioned drones may retain sensitive data or be repurposed maliciously. A drone shares many properties with a classical IoT device when it comes to protecting integrity against unauthorized modifications of firmware, software, or configuration. Without these protections, attackers could inject malicious firmware or modify the control stack, gaining persistent and often invisible access - especially if the device is physically accessible to them (e.g., while it is in storage).
Measured Boot – Measured Boot takes Secure Boot further by recording what software was loaded at each stage. This allows remote systems (like a fleet manager or ground station) to verify that the drone is running only trusted code. It also allows to authorize actions locally, such as releasing decryption keys only when the device boots properly. 2. System Architecture & Core Working Principles Firmware Signing – Ensures that firmware and configuration updates are signed with cryptographic signatures. Implement rollback protection to prevent attackers from loading older, vulnerable firmware versions. It's also a good idea to encrypt firmware packages, especially if they contain sensitive IP.
With drones implementing control logic depending on how close they are to other drones or aerial vehicles, manipulating sensor data can be disastrous! Attackers can manipulate drone sensors (GPS, cameras, altimeters) to feed incorrect data. Think of this more like how stuxnet changed the speed of the Uranium centrifuges in Iran while still reporting the speed as normal.
To prevent this, there is new research being developed involving watermarked signals whose entropy can be used to determine if the sensor values are correct of not. Read more about this method here . Inadequate Logging and Monitoring – Without sufficient monitoring, security breaches or operational anomalies may go undetected.
Integration Issues – Some cameras require webserver configurations, and if poorly integrated, these web servers on cameras or telemetry systems may expose vulnerabilities that can be used to gather sensitive information. Below are some protocols used by drone systems to communicate. This can be either between each other (if in a horde) or with the ground stations. We have mentioned what can go wrong with each protocol and also provided recommendations.
Require valid MAVLink 2 message signatures for commands received over untrusted links. Reject unsigned or incorrectly signed commands. Protect the shared signing key and persist signing timestamps across restarts so replay checks remain effective. Heartbeat messages advertise a component's presence, type, and state. Treat heartbeat receipt as a liveness signal, not authorization to execute commands.
Tools like ArduPilot and PX4 support MAVLink 2.0 security enhancements. They have been thoroughly tested and are therefore recommended. Recent CVEs underscore the risk of unauthenticated MAVLink. The absence of default authentication is not theoretical — it has produced critical, remotely-reachable vulnerabilities across both dominant open-source autopilots: CVE-2026-1579 (PX4, CVSS 9.8, CISA ICSA-26-090-02, CWE-306): with MAVLink 2 message signing disabled, an unauthenticated party can send SERIAL_CONTROL to obtain interactive shell access.
CVE-2026-38971 (ArduPilot ArduPlane ≤ 4.6.3, CVSS 9.1, CWE-125): an out-of-bounds read in the SERIAL_CONTROL handler (GCS_serial_control.cpp), reachable over MAVLink by an unauthenticated attacker — flight-controller memory disclosure and denial of service. CVE-2026-32743 and related PX4 issues (CWE-121): MAVLink-reachable stack buffer overflows in the log handler cause denial of service.
CVE-2020-10283 (MAVLink): an earlier authentication downgrade issue — the weakness is long-standing, not new. Defense-in-depth beyond message signing. Because signing is frequently disabled in the field and any software mitigation runs in the same trust domain an attacker may have compromised, consider enforcing protocol integrity out-of-band: Header validation — use system-ID allowlists and packet sequence numbers to detect unexpected senders and packet loss.
These fields do not authenticate unsigned messages; they cannot replace signature and timestamp validation. Typed-payload validation — reject non-finite parameter values (PARAM_SET) and bound FTP path lengths to defeat malformed-value and buffer-overflow classes. Hardware-enforced enforcement point — where the autopilot firmware cannot be modified or trusted, a bump-in-the-wire validation device placed between the companion computer and the flight controller can apply the above checks in a separate hardware domain, independent of a potentially compromised software stack.
Most attacks require physical access to exploit CAN. It works on a differential signal and hardware hacking may be possible by tapping into them. Do not rely on DroneCAN alone to authenticate CAN senders. Its multi-frame cyclic redundancy check (CRC) is an unkeyed checksum, not a message authentication code. Protect physical bus access and isolate the bus from untrusted components.
This has a way to enable AES-128 encryption to secure transmissions. Make sure you do that. Deploy network keys with frequent rotation to prevent key compromise. Read more about key rotations here . Monitor for ZigBee packet sniffing attacks using SDR-based tools like HackRF or YARD Stick One . You must enforce Strict Pairing Modes that is LE (Low Energy) Secure Connections over Bluetooth 4.2+. This uses the Elliptic curve Diffie-Hellman cryptosystem to generate keys. Essentially, its state of the art.
Pairing methods such as Just works are vulnerable to MITM attacks! Do not use them if you're setting up your own Bluetooth adapters. Make sure that you are using WPA3 encryption for the highest level of security. Note that protocols like WEP are vulnerable! Use 802.11w Management Frame Protection (MFP) to mitigate deauthentication attacks (these are crafted packets that emulate a server and cause deauthentication).
Do not rely on hiding the Wi-Fi network name or filtering media access control (MAC) addresses to prevent unauthorized access: hidden networks remain discoverable and MAC addresses can be spoofed . Use Wi-Fi authentication and encryption as described above. By implementing these security measures, drone operators can significantly reduce the risks of cyberattacks and unauthorized access to UAV communication systems.
3. Software Implementation, Frameworks & Protocols The table maps common attacks to relevant controls. Choose controls for the interfaces actually present on the drone and GCS; the impact depends on the implementation. Radio interference, forged messages, and software vulnerabilities require different defenses.
There are multiple GitHub repos that help with drone attack simulations and actual exploits . Be sure to check them out too for a deeper understanding of drone security. Recent technological advancements have seen the integration of unmanned aerial networks (UAVs) into various sectors, from civilian missions to military operations. In this context, ensuring security, precisely authentication, is essential to prevent data theft and manipulation. A Man-in-the-Middle attack not only compromises network integrity but also threatens the original data, potentially leading to theft or alteration. In this work, we proposed an authentication method to secure UAV data exchange over an insecure communication channel. Our solution combines Diffie-Hellman (DH) key exchange and Hash-based Message Authentication Code (HMAC) within ROS communication channels to authenticate exchanged UAV data. We evaluated our method by measuring transmission time and simulating key tampering, finding acceptable performance for DH key sizes below 4096 bits but longer times for larger sizes due to increased complexity. Both drones successfully detected tampered keys, affirming our method’s efficacy in protecting UAV communication. However, scalability challenges in resource-constrained environments warrant further research.
Widely recognized as drones, unmanned aerial vehicles (UAVs) networks have attracted a lot of research attention in the past few years as they facilitate network communication. As indicated by the name, UAVs are aircrafts that are automatically piloted using computers instead of having a human pilot. UAVs belong to the non-terrestrial network category as they move from land to space providing many advantages unlike terrestrial networks. First, thanks to their mobility, they provide enhanced connectivity by easily moving in the environment allowing network connection to reach the less fortunate rural areas where people do not have optical fibers and can only use 3G networks [ 1 ] . In addition to that, various algorithms were also proposed to optimize and increase mobility using factors such as coverage maximization and power control [ 2 ] and the optimal 3D trajectory of each UAV [ 3 ] . Secondly, UAVs enhance energy efficiency, particularly for Internet of Things devices that suffer from limited battery capacity. Acting as relays between sensors in remote and urban areas that have energy shortages, UAVs collect the IoT data to ease their transmission to unreachable areas [ 4 ] .
The previously discussed features position UAVs as a perfect candidate for integration with beyond 5G and 6G networks where millions of interconnected devices are communicating with each other requiring very high throughput, low latency, connectivity, and energy [ 5 ] . However,ensuring the security of these networks is crucial to create a complete system. Indeed, security remains a significant challenge in futuristic non-terrestrial communication networks, often overlooked in the development of UAV intelligent applications given their constrained computing capabilities [ 6 ] . Prioritizing 6G security is crucial, with concepts such as blockchain, quantum computing and communication technology, security protocols, and others being considered to enhance resilience against cyberattacks [ 7 ] .
UAV applications range from using communication between UAVs and base stations to novel approaches utilizing a swarm network of UAVs and employing UAV-to-UAV communication to create an interactive environment where data and/or communication is exchanged between these devices. According to this, various drone networking security solutions have been proposed by researchers. In this article, we focus on two of the security triad components which are authentication and integrity by proposing a secure communication approach that combines the Diffie-Hellman key exchange method for authentication and the use of the HMAC algorithm for integrity. Our contribution is highlighted in three aspects: The simplicity and flexibility of the authentication method make it well-suited for UAV communication environments.
The proposed method adds another security layer that suits the low energy capacity of UAVs. Robustness is enhanced by leveraging ROS (Robotic Operating System) communication channels, which provide standardized and reliable communication for UAV systems. The rest of the paper is organized as follows: section II presents related works and research solutions in the field of drone security as well as innovations in UAV architecture designs. Section III describes the proposed system, its architecture, and the simulation environment. In section IV, we discuss the simulation results and the performance evaluation. Finally, we conclude and present future works.
A work in [ 8 ] addressed the security of an Internet of Drone environment (IoD) where a drone is traveling a long distance to deliver goods to the designated customer location and then must return safely escaping all network attacks. The proposed system uses the asymmetric Elliptic-curse-cryptography (ECC) algorithm to encrypt the sent data, it uses a shared key for encryption and a secret one for decryption, furthermore, the combination of symmetric and asymmetric encryption is proposed to increase security, a hybrid encryption and decryption mechanism are realized at the transmitter and receiver nodes respectively [ 8 ] . Results show that the data sent from attackers acting as fake nodes are verified by SHA-256 and easily ignored [ 8 ] . Researchers in [ 9 ] divided UAV security into 03 main categories: Protocol-based security: Including UranusLink protocol that identifies packet loss using sequence numbers to optimize UAV long-distance communication and improve link performance by up to 33%, UAVCAN that improves communication abstraction to support diverse applications by enhancing the medium support, and MavLink protocol, which is used for bidirectional communication between UAVs and base stations with a secondary security layer to protect against attacks like DDoS and eavesdropping.
Agent-based security: two methods are discussed, the self-protective UAV Network method (ASP-UAS) using the Hierarchical Immune System (HIS) and multi-agent systems that enhance security against drone attacks and the HFA algorithm that ensures cybersecurity defense, focusing on secure communication through trust-building and node removal. Trajectory-design-based security: employing deep reinforcement learning, UAV trajectory, and sub-carrier power allocation’s performance has improved by 10.29% thanks to using a deep Q-network algorithm.
Furthermore, in UAV-to-vehicle communication, authors in [ 9 ] studied a case where a UAV is acting as a base station trying to communicate with a vehicle on the highway with the existence of another malicious vehicle on the same highway to eavesdrop on the communication between them. Results are shown below: High influence: has a weak influence on downlink secrecy outage and a minimal impact on uplink performance.
Transmit SNR: has a weak impact on downlink secrecy outage and does not significantly affect uplink performance. Ground Coverage Radius: negatively affects secrecy outage in both uplink and downlink scenarios while the radius of the destination’s ground coverage has minimal influence. Network security fundamentals are summarized in the CIA acronym, representing Confidentiality, Integrity, and availability.
Being the first pillar of the security triad, Confidentiality aims to protect the network from unauthorized access and data theft, it is implemented through access control applications, secure communication protocols, and encryption. According to this, some research works focused on building systems and applications for securing UAV communication by ensuring confidentiality. In [10] a customized Kerberos system was implemented for UAV authentication, it contained a Ground Station, an Authentication Server (AS), and a Ticket Granting Server as a secondary security layer. For the user to communicate with UAVs, they must pass through several phases: Phase 1: It has two steps, firstly, the user initiates the authentication process by sending a request (message-1) to the Authentication Server (AS) including ID, password, and Ticket-Granting Server (TGS) ID in the secure channel [step 1].
Secondly, the AS verifies the user’s credentials using its database, if authorized, the AS responds (message-2) with the user’s private key and an encrypted ticket for TGS access [step 2]. Phase 2: It also has two steps, firstly the user having the TGT, sends a request (message-3) to TGS containing user ID, UAV ID, and TGS ticket [step 3]. Secondly, TGS responds (message-4) with a ticket allowing the user access to the UAV [step 4].
Phase 3: Again, two last steps, firstly, the user sends an access request (message-5) to the Ground Station Radio Transceiver, including user ID and TGS ticket, the latter forwards this information (message-6) to the UAV in the Wireless Sensor Network area [step 5]. Secondly, if the user information is correct, the UAV responds with an authorized access message (message-7) to the radio transceiver, the information is then relayed to the user via radio transceiver in message-8 format, containing a notation for UAV access [step 6].
This system resulted in increased speed which is advantageous for enhancing security and defense against intrusion in UAV networks. Additionally, it aims to address shortcomings in power consumption and intrusion for the future [ 10 ] . Another research in [ 11 ] proposed a global and secured authentication system that aims to address UAV communication security challenges by using secure sensor values to defend against attacks and ensure integrity. It is resistant to tampering, especially against remote attacks ensuring availability, authenticity, and confidentiality while being adapted to the acceptance criteria of authorities to attract manufacturers. The system operates against physical and remote attacks by the integration of a Hardware Security Module (HSM) coupled with secure storage for key material, however, it suffers from latency and high power consumption [ 11 ] . Moreover, authors in [ 12 ] proposed a decentralized authentication method to avoid the single point of failure, the system relies on the reliability evaluation of the physical layer fingerprints that divide UAV nodes into selected and unselected nodes, and then a soft authentication judgment is set on the selected ones. When a node whether it was malicious or legitimate tries to send a message to the cluster head (CH), the other node judges if she should be granted access or not [ 12 ] . This method has proven to successfully increase the authentication accuracy while mitigating the wrong estimations that categorize a legitimate UAV as a malicious one and the opposite [ 12 ] . As a complement to network security, the architectural design must be adapted and well-studied to create a flexible environment for UAV implementation, the SDN technology responds to that by separating the control function from the data layer centralizing the network management, and making the network flexible, programmable and scalable for future implementations [ 13 ] . Several researchers have worked on the integration of UAV-based SDN systems such as SDN-based flying ad hoc network models(FANET), and SDN-based NFV for SDUAV security, others have used this infrastructural combination to prevent collision, reduce end-to-end delay, establish authentication and even in response to COVID-19 challenges [ 14 ] . Over the years more research focused on security for SDN-based UAV networks, for instance, We proposed in an earlier research work [ 15 ] a new design that relies on using UAV nodes both as controllers and switches at the same time in SDN, this work consisted of simulating a network pollution attack and using the network coding paradigm (NC) to protect data from being tampered with in case if the attacker gained control over one of the UAV nodes, a verification method of the legitimate IP address was also implemented. While results demonstrated more flexibility and less loss rate, it is still necessary to explore more security methods because IP addresses alone are not enough [ 15 ] .
the difference between our authentication method and those mentioned lies in its simplicity, efficiency, and autonomy. While the Kerberos system introduced in [ 10 ] involves multiple steps and relies on centralized servers, our method operates directly within the UAV network without the need for external servers. Similarly, the authentication system proposed in [ 11 ] may suffer from latency and high power consumption due to its reliance on secure sensor values and hardware security modules. In contrast, our method offers a lightweight solution that balances security requirements with the resource constraints of UAVs, making it more suitable for practical implementation in UAV networks. While the aforementioned studies contribute significantly to UAV communication security, they primarily focus on specific aspects such as encryption techniques, protocol-based security, and architectural design. In contrast, our proposed method offers a unique approach that addresses multiple security concerns simultaneously including secure authentication and data integrity, safeguarding against unauthorized access, and tampering in UAV communication environments.
In an open environment such as the aerial territory in which UAV networks operate, there is no apparent security channel for communicating which makes UAV endangered and exposed to attackers trying to intercept the exchanged information to steal it or manipulate it by changing the original packets. Consequently, research have focused on inter-UAV communication due to the lack of existing security approaches that protect the inter-communication flow from malicious parties. Fig. 1 describes the communication flow from one UAV to another over an insecure communication channel and how Man-In-The-Middle attacks could interfere.
According to this, and as one of the actors of the scientific research community, we proposed a solution based on using the combination of the Diffie-Hellman and the HMAC algorithms focusing on applying authentication and integrity in the UAV communication environment. Both algorithms were used in our system to complete the shortenings of each other. Fig. 2 illustrates the way they perform.
On the left, we have the Diffie-Hellman algorithm which allows two users (user A and user B) to choose a private key that will not be shared over the network (Pa for A and Pb for B), this key is used in a function to calculate a public key (a for A and b for B), the latter is then exchanged between the two parties and combined with their original private keys to calculate a shared secret key. The used function is described in 2 where p is prime. This method prevents an attacker from knowing the shared secret key, even if they intercept the exchanged public keys.
On the right, we have the HMAC algorithm that authenticates the exchanged data and verifies their integrity. When two entities, such as user A and user B want to exchange a message, the message along with a secret key known to both entities only (in our case, the one calculated from Diffie-Hellman) are combined using a hash algorithm to create a hash that will be added to the original message. When user B receives the authenticated data, it will check against the same calculated hash to see whether data has been altered.
The architecture focuses on using two drones communicating in a ROS/Gazebo environment as shown in Fig. 3 . 4. Practical Deployment, Analysis & Case Studies The implementation was based on an existing px4-mavros-gazebo-simulation which focuses on establishing a testing and experimentation environment for robotic vehicles like UAVs and Rovers. The four components of this system are explained as follows: PX4 Autopilot: PX4 is an open-source flight control software designed for unmanned vehicles such as UAVs, drones, and other unmanned vehicles. It offers an all-encompassing platform for the management and navigation control of aerial vehicles.
Gazebo Simulator: Gazebo is a multi-robot simulator that enables the testing and experimenting of robotic algorithms in a simulated setting. It replicates diverse robotic systems by incorporating a realistic physics engine and 3D graphics. MAVROS: MAVROS (Micro Air Vehicle Communication and Control ROS package) is a communication link between the Robot Operating System (ROS) and MAVLink-based flight controllers. It uses the MAVLink communication protocol to streamline the integration of ROS with UAVs.
ROS (Robot Operating System): ROS is an open-source middleware framework that aims to control and develop robotic systems. It offers tools and libraries for tasks such as hardware abstraction, device drivers, communication between processes, package management, and others. Fig. 4 illustrates how the four components are related and describes the role of each one of them in our solution. For instance: ROS enables UAV communication channels, hardware abstraction, and other functionalities.
The proposed solution lies in the combination of both the Diffie-Hellman key exchange algorithm and the HMAC algorithm. The latter is used to ensure effective authentication and data integrity due to the well-known Diffie-Hellman weakness against Man in the Middle attacks. When the key exchange is done and the shared key is calculated, HMAC joins the game by using the secret shared key to calculate its hash and authenticate the exchanged data. This operation is explained in detail in the sequence diagram in Fig. 5 .
In this scenario we used two drones (Drone 0 and Drone 1), both drones are displayed in a Gazebo simulator with similar physical characteristics, they perform a Diffie-Hellman key exchange and then exchange authenticated data using ROS. The process goes as follows: Both drones generate Diffie-Hellman Parameters (the generator and the key size) using the cryptography library.
Both drones generate their private and public keys using the generated Diffie-Hellman parameters. Drone 0 and Drone 1 initialize their ROS nodes which are called ’drone0_authentication_and_send’ & ’drone1_authentication_and_receive’ respectively.
Drone 0 and Drone 1 log and publish their public keys to respectively the ’/drone0/dh_public_key’ & the ’/drone1/dh_public_key’ ROS topics then wait for the other drone’s public key. Drone 0 generates authenticated data and an HMAC using the shared key obtained from Diffie-Hellman key exchange. Drone 0 publishes the authenticated data and HMAC to the ’/drone1/authenticated_data’ ROS topic.
If drone 1 does not find a matching HMAC it displays an error and discards data. This communication flow ensures secure key exchange and data transfer between the two drones in a ROS environment. HMAC provides a mean for drones to authenticate each other by ensuring that the exchanged data has not been altered during the communication. In this section, we identified the parameters that could potentially influence our solution either positively or negatively.Subsequently, we evaluated these parameters to propose enhancements for future work. We used two different evaluation methods: the first based on the time taken for the process to finish, and the second involving a key tampering scenario to simulate man-in-the-middle attacks.
In this approach, we considered various values for both the Diffie-Hellman and HMAC keys. We conducted tests by varying the keys each time. The chosen values are the following: For Diffie-Hellman: The test was conducted by repeating the key calculation, exchange, and authentication processes from start to finish using a different key each time. Each DH value is tested with all HMAC values until all DH values had been tested. Results were then illustrated in Figs. 6 and 7 respectively, representing a scatter plot and a histogram.
From the representation, we observe that the Time Taken increases as the HMAC key size increases. However, it remains significantly below 1 or 2 seconds, which is a promising result considering the efficient resources utilized in the environment, contributing to the reduced time. During testing, when a larger DH key size, such as 4096, was employed, the program execution slowed considerably, taking over 10 minutes. Despite not obtaining a result with this key size, 2048 remains a highly suitable and secure choice, making it challenging for attackers to decrypt information once encrypted.” The scatter plot illustrates the relationship between HMAC Key Size, DH Key Size, and the Time Taken, with each point representing a combination of HMAC Key Size and DH Key Size. The color gradient indicates the DH Key Size, with lighter shades representing larger keys and darker shades indicating smaller key sizes.
From the representation, we observe that the Time Taken increases as the HMAC key size increases. However, it remains significantly below 1 or 2 seconds, which is a promising result considering the efficient resources utilized in the environment. The latter, usually adds computing complexity thus the Time taken to finish the process which did not happen in our scenario. However, when we reached higher values, such as DH key sizes equal to or higher than 4096, the program execution slowed significantly, taking over 10 minutes. Despite not obtaining results with these higher values, 2048 remains a highly suitable and secure key size. It effectively complicates attackers’ attempts to decrypt encrypted information.
The second illustration presents the results of another series of tests conducted with the same parameters. We reran the program to ensure that results are consistent and have not been altered. The distribution of Time Taken across all test cases reveals that the majority fall within a specific range of time while cases with exceptionally high or low Time Taken are identified as outliners. This suggest that the overall results positively impact performance, as the Time Taken remains within the range previously depicted in the scatter plot.
It is well known that Man in the Middle attacks significantly compromise data exchange security. despite being a secure algorithm, the Diffie-Hellman key exchange lacks the ability to verify the integrity of exchanged data, making it vulnerable to such attacks. Incorporating the HMAC algorithm has bolstered authentication and added data integrity to our system. However, during the public key exchange phase, attackers can still intercept and manipulate the keys before injecting them back into the communication channel. Thus, UAVs must possess the capability to detect tampering to ensure data authenticity.
For testing and evaluation, we simulated a Man in the Middle attack by targeting the exchanged public keys. Our approach was simple and straightforward: we implemented two functions for each Drone0 and Drone1. The first function simulates tampering by altering a portion of the key, while the second function simulates key replacement.To determine the detection process, we incorporated a function that randomly decides whether to simulate tampering or key replacement.Both drones have this function, and each independently makes its own random decision. Consequently, the outcome could vary: both drones may detect tampering, both may detect key replacement, or one may detect tampering while the other detects key replacement. The results were recorded in a log file for each drone, as depicted in Figs. 8 and 9 for Drone 0 and Drone 1, respectively.
As demonstrated above, the tests yielded successful results; both drones detected alterations and manipulations, showcasing the algorithm’s effectiveness in guarding against Man-in-the-Middle attacks. The application of security and reliability in UAV networks presents a huge challenge for researchers, especially as when these integrate with futuristic 6G communication networks operating in complex environments. Thus, novel data exchange mechanisms and protocols are required to ensure efficiency, reliability and security. In this paper, we proposed a secure mechanism for inter-UAV communication to prevent attacks while maintaining resilience in untrusted environments and being flexible. We proposed the combination of the Diffie-Hellman key exchange algorithm and HMAC for UAV authentication and ensuring data integrity. We conducted two testing scenarios to asses the algorithm’s performance and its limits.The first test focused on evaluating the processing time by varying key sizes, with results showing that processing time remained below one second and exceeded 10 minutes for for sizes above 4096. In the second test, we simulated a Man-in-the-Middle attack by incorporating key replacement, tampering, and detection functions. Results demonstrated the system’s scalability and resilience, indicating potential for additional security implementations to further enhance its robustness.
Our work aims to achieve optimal reliability for UAV communications, particularly in the context of futuristic 6G networks that handle vast and complex amounts of data. To maximize and facilitate UAV integration, we are exploring novel paradigms and innovative approaches to leverage existing and emerging technologies. Future works will focus on: Drones rely heavily on wireless communication, often operating over the 2.4 GHz RF spectrum, making them susceptible to signal hijacking, jamming, and man-in-the-middle attacks. This article explores practical methods to secure drone control channels, including RF hardening techniques, encryption, and real-world vulnerability testing.
Drones often use unencrypted or weakly secured control signals. A simple GNU Radio script can help detect and analyze these transmissions: 5. Performance Evaluation & Extended Technical Observations The increasing use of drones in military, logistics, and surveillance demands robust RF security. While techniques like FHSS and AES mitigate risks, attackers continuously evolve. Future drone systems must integrate quantum-resistant encryption and AI-based anomaly detection to stay ahead.
By 2027, AI-driven RF fingerprinting will become standard for drone authentication, reducing reliance on traditional encryption. However, state-sponsored hackers will likely develop deep learning-based signal spoofing, escalating the arms race in wireless security. Reported By: Milchis Catalin – Hackers Feeds Extra Hub: Undercode MoN Basic Verification: Pass I We do not sell your personal data. If you wish to exercise your rights under applicable privacy laws, please visit our Do Not Sell My Personal Information page.
Recent advancements in drone technology have shown that commercial off-the-shelf Micro Aerial Drones are more effective than large-sized drones for performing flight missions in narrow environments, such as swarming, indoor navigation, and inspection of hazardous locations. Due to their deployments in many civilian and military applications, safe and reliable communication of these drones throughout the mission is critical. The Crazyflie ecosystem is one of the most popular Micro Aerial Drones and has the potential to be deployed worldwide. In this paper, we empirically investigate two interference attacks against the Crazy Real Time Protocol (CRTP) implemented within the Crazyflie drones. In particular, we explore the feasibility of experimenting two attack vectors that can disrupt an ongoing flight mission: the jamming attack, and the hijacking attack. Our experimental results demonstrate the effectiveness of such attacks in both autonomous and non-autonomous flight modes on a Crazyflie 2.1 drone. Finally, we suggest potential shielding strategies that guarantee a safe and secure flight mission. To the best of our knowledge, this is the first work investigating jamming and hijacking attacks against Micro Aerial Drones, both in autonomous and non-autonomous modes.
Defense Advanced Research Projects Agency (DARPA) originally introduced the concept of Micro Aerial Vehicle (MAV) for defense applications, with requirements including a maximum wingspan length of 15 cm and a weight of up to 100 g [ 1 ] . These micro-sized devices can be carried easily, and they are best suited for specific applications (e.g., indoor navigation, warehouse operations, drone swarming). Recently, many companies, government laboratories, and researchers from academia have been active in the design and development of MAVs [ 2 , 3 ] . The Crazyflie quadcopter is one of the most popular Micro Aerial Drones and is ideal for applications in different fields, and swarming on a larger scale [ 4 ] . However, the threats posed by the nature of wireless communications at the physical layer trigger a series of interference attacks, which are the most common types of attacks targeting MAVs [ 5 ] . Indeed, the limited resources of such devices make it very challenging to integrate software or hardware-based security solutions. In this paper, we empirically explore two interference attacks against the CRTP protocol that manages radio communication over the physical layer. Specifically, we investigate whether the jamming and hijacking attacks hold for the Crazyflie drones in autonomous and non-autonomous flight modes.
First, we perform constant jamming of the signal transmission by continuously broadcasting high-power interference signals [ 6 ] . Second, we perform a hijacking attack, in which we aim to control the Crazyflie drone. Then, we validate the effectiveness of each attack to gain insight into real-world applications. Finally, we suggest potential defense mechanisms and show the challenges that must be considered while integrating such solutions in practical settings.
Difference from existing work: Different from prior works, we perform practical and cost-efficient interference attacks against Micro Aerial Drones, focusing on the CRTP communication protocol. These drones have several unique features that distinguish them from other types of off-the-shelf drones in terms of security and performance. With respect to the existing literature that targets only medium and small drones, this is the first work focusing on interference attacks on Micro Aerial Drones. From a security standpoint, Micro Aerial Drones have limited wireless capabilities as one can suspect their vulnerability at the physical layer. Thus, the need to provide comprehensive security investigations for such types of drones.
On the other hand, our study considers both autonomous and non-autonomous flight modes to analyze our wireless attacks, whereas most of the prior studies have focused only on the non-autonomous flight mode. We experiment the feasibility of two wireless attacks against the CRTP communication protocol: (i) the jamming attack, and (ii) the hijacking attack.
In a controlled and safe environment, we showcase the real-world consequences of jamming and hijacking attacks and how they can be performed in practical settings. Moreover, we plan to publicly release our research artifacts for the transparency and reproducibility of our results. We suggest potential shielding strategies to mitigate the security risks posed by the attacks. Then, we discuss the various challenges regarding implementing such solutions.
In this section, we present the background information on the Crazyflie platform and its communication protocol. The Crazyflie platform consists of the Crazyflie drone , the Ground Control Station (GCS), and the Crazyradio module . The Crazyflie drone is connected to the GCS through the Crazyradio module. This module not only facilitates the exchange of control and telemetry data between the drone and the GCS but also has broadcasting capabilities for multiple Crazyflie drones communicating on the same radio channel. The Crazyflie ecosystem offers a wide range of features through its client software for the GCS, including real-time logging data, setting flight parameters, and command-based flight control. This enables the Crazyflie drone to be easily integrated into various applications. The availability of the Crazyradio module, the integrated IMU and pressure sensor, and the feature-rich client software for the GCS make the Crazyflie drone an attractive option for deployment in various settings.
The exchanged control and telemetry data between the GCS, and the Crazyflie drones are encoded into CRTP packets and sent via the radio through the ESB protocol. The CRTP protocol enables packet ordering for real-time control of the Crazyflie drone. We note that the payload of the CRTP packets provides the data buffer of the message (up to 31 bytes). The header of the CRTP packets is divided into three segments: (i) the port , (ii) the link , and (iii) the channel number . The port segment ranges between 0 and 15 (4 bits) and identifies the functionality of the message (e.g., port number 3 defines the commander and port number 5 for data logging). The link segment is a reserved field for future use and ranges between 0 and 3 (2 bits), while the channel number ranges between 0 and 3 (2 bits), and is used to determine the sub-functionality of the message that is defined in the application layer. As part of the CRTP protocol, each drone has a Unique Radio Identifier (URI) that is handled by the Crazyradio module. It includes four segments described as follows: Medium: Defines the nature of communication between the Crazyflie drone and the GCS (e.g., radio, serial).
Radio Channel: Identifies the radio channel between the GCS and the Crazyflie drone that is operating (i.e., the radio channel operates from 0 to 125). Communication speed: Refers to the bandwidth during the Air-2-Ground communication and operates under three communication data rates: 250kbit/s, 1Mbit/s, and 2Mbit/s.
Address: Determines the radio address of the Crazyflie drone communicating with the GCS. We mention that the default radio address of the Crazyflie drone provided by the manufacturer is E7:E7:E7:E7:E7 and can be changed by the operator. In our study, we consider an attacker within the range of the radio space of the drones (i.e., 1 km range line-of-sight with the Crazyflie drone) without physical access. The attacker’s goal is to compromise the flight mission. As illustrated in Figure 1 , the adversary can remotely transmit malicious traffic from his device to the Crazyflie drone and the Crazyradio module. Here, we consider an active attacker who can prevent the Air-2-Ground communication link, thus threatening the availability of the flight mission by taking over the drone mid-flight through a jamming or a hijacking attack. Regarding the attacker capabilities, we assume that the adversary can purchase similar or identical devices (e.g., Crazyflie drone, Crazyradio module) to develop and test the attacks.
In this section, we present our experimental setup. Then, we provide the implementation of our attacks. Afterward, we discuss the practicality and cost analysis of our attacks. In our experiments, we consider a centralized network architecture [ 5 ] , where we used one Crazyflie 2.1 drone flashed with the latest firmware version (v2022.09), which communicates with the GCS through the Crazyradio Power Amplifier module (i.e., USB dongle [ 7 ] ). The GCS is a laptop computer with an Intel Core i7-9750H CPU clocked at 2.60 GHz and 16 GB of memory. We note that the Crazyradio module is also flashed with the latest firmware version (v0.53). First, we setup the radio address of the Crazyflie drone on 01:E7:E7:E7:E7 . Then, we setup the Crazyradio module on channel 81 with a 2 Mbits/s radio bandwidth.
To demonstrate the feasibility and effectiveness of our attacks against the Crazyflie ecosystem, we performed two physical layer attacks, where it is sufficient for the adversary to compromise the availability of the ongoing flight mission, and then ultimately take over control of the drone. We performed all our attacks against the Crazyflie drone by considering two different flight mode scenarios: (i) autonomous flight mode and (ii) non-autonomous flight mode. In the autonomous flight mode, the Crazyflie drone operates autonomously via a client Python-based API [ 8 ] . In the non-autonomous flight mode, the user manually operates the Crazyflie drone via a real-time command-based flight control. It is worth mentioning that regardless of the considered attacks, the scanning phase is a prerequisite to gathering the radio address and the operating channel of the flying drone.
Scanning: To target a specific drone, we first start by scanning the network to identify the active drones and their communication channels. Therefore, in the scanning phase, we look for connected Crazyflie drones promiscuously by sweeping all possible channels under different radio bandwidths. Then, we display the active radio addresses of the Crazyflie drones with their corresponding radio channels and the received packets. According to Shannon’s information theory, we mathematically quantify the amount of data scanned I s I_{s} . In fact, given a continuous Air-2-Ground communication system, the transmitted signal x I ( t ) x(t) from the GCS to the drone can be modeled as a continuous signal with a probability density function p I ( x ) p(x) , where its entropy density H H can be defined as follows: Similarly, the received signal y I ( t ) y(t) by the drone from the GCS can be described as a continuous signal with a probability density function p I ( y ) p(y) , with its entropy density H I ( Y ) H(Y) . can be defined as: To quantify the amount of information shared between the drone and the GCS, we define I I ( X : Y ) I(X:Y) as the mutual information between the transmitted signal and the received signal, which can be expressed as: where p I ( x , y ) p(x,y) is the joint probability distribution of the transmitted and received signals x I ( t ) x(t) and y I ( t ) y(t) , respectively. Here, the scanning device aims to gather information about the transmitted signal x I ( t ) x(t) by observing the received signal y I ( t ) y(t) . To determine the amount of data scanned, we subtract the entropy density of the transmitted signal from the mutual information as follows: Figure 2 illustrates the result of the scanning phase by considering three active drones with the radio addresses 01:E7:E7:E7:E7 , 02:E7:E7:E7:E7 , and 03:E7:E7:E7:E7 operating on three different channels: 81, 82, and 83, respectively.
For the sake of clarity, we set the target drone on channel 81. We note that network scanning cannot be simply prevented as the device identifier and channel information data is inherently available to the public, similar to the MAC address and channel information in WiFi. It is worth mentioning that regardless of the implemented attacks, we scan the network to gather the radio address and the operating channel of the flying drone. We note that network scanning is a base for all implemented attacks in our study.
Attack 1 - Jamming: We launched the jamming attack against the running Crazyflie drone by jamming the signal going to and coming from the GCS. This attack consists of blocking the Air-2-Ground communication link and consequently disrupting the availability of the flight mission. Given a wireless communication system transmitting a benign signal x I ( t ) x(t) to a receiver over a period of time t t . The adversary transmits jamming signal j I ( t ) j(t) , which is added to the benign signal, such that where y I ( t ) y(t) is the received signal. We mention that the jamming signal is effective if and only if the received signal is corrupted. In other words, the jamming signal can be described as an additive noise that corrupts the benign signal. To evaluate the effectiveness of the corrupted signal, the adversary decreases the Signal-to-Noise Ratio (SNR) (i.e., the metric that measures the quality of the received signal). The SNR is the ratio of signal power to the noise power and can be defined as follows: such that | | . | | ||.|| refers to the Euclidean norm of the signal. Given the affordability of low-cost Software Defined Radios, we performed the jamming attack using HackRF One, one of the commercially available Software Defined Radios, and its open-source software development toolkit such as GNU radio. In the literature, there exist several types of jamming attacks, such as constant, reactive, or random jamming attacks [ 6 ] . In our case, we conducted a constant jamming attack, where we broadcast high-power interference signals (i.e., Gaussian noise) continuously over the operating radio frequency. We mention that the operating frequency of the Crazyflie drone can be inferred from its corresponding radio channel. For example, the Crazyflie drone operating on radio channel 81 has a radio frequency of 2481 MHz (i.e., the sum of 2.4 GHz and 81 MHz). We illustrate in Figure 3 the captured frequency sink flow graph of a Crazyflie drone with a radio frequency range centered at 2481 MHz. We set the frequency bandwidth to 10 MHz and the Fast Fourier Transform (FFT) size to 1024. The pick of the relative gain from the center frequency can be clearly shown in Figure 3 , which means that we can perfectly transmit interference signals to prevent the Crazyflie drone from accessing the radio channel.
After gathering the radio frequency of the Crazyflie drone, we continuously broadcast a Gaussian noise signal over the radio channel to jam the Air-2-Ground communication. In this case, the transmitted signal is in the form of a complex source that is divided into real and imaginary parts. We consider a constant jamming signal that is characterized by a high sampling rate of up to 10 million samples per second (i.e., 10MHz) to guarantee high accuracy in capturing and processing the signal. We amplify the jamming signal by setting the Radio Frequency (RF) gain to 14 dB, and we believe that the strength of our RF gain is fair enough to make the legitimate signal from the malicious one indistinguishable. To adequately filter out the generated jamming signal, we set a high cutoff frequency of 4MHz, with a transition width of 1MHz. In the Intermediate Frequency (IF) domain, we consider the IF gain of 47dB and the baseband gain of 0 dB. The working of the transmitted jamming signal with an amplitude of 1 is shown in Figure 4 . After performing the jamming attack against the Crazyflie drone in both autonomous and non-autonomous flight modes, we observe that the GCS cannot establish Air-2-Ground communication. Moreover, the Crazyflie drone crashes down in the autonomous flight mode while it remains stable over the air in the non-autonomous flight mode.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Shahed%20drones • https://cheatsheetseries.owasp.org/cheatsheets/Drone_Security_Cheat_Sheet.html • https://arxiv.org/html/2410.09085v1 • https://undercodetesting.com/securing-drone-communication-rf-vulnerabilities-and-layered-defense-techniques/ • https://arxiv.org/html/2403.03858v1
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Drone Communication Security And Anti Hijacking System.
[*] Metasploit Scan Running on Target Subnet for Drone Communication Security And Anti Hijacking System... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |