Complete Technical Paper Content — Dynamic Analysis Tool For Desktop Application Security
Overview & System Context
Dynamic Analysis Tool For Desktop Application Security: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9550 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Linux ( LIN-uuks) is a family of free and open-source software Unix-like operating systems based on the Linux kernel, which was first released on 17 September 1991 by Linus Torvalds. Some members of the family are typically packaged as a distribution (a.k.a. distro), which includes the kernel alongside supporting system software and libraries developed by third parties—such as GNU, Red Hat, and X.Org—to create a complete operating system; however, not all Linux-based operating systems are considered distros, with Android being an example. Linux was originally designed as a clone of Unix and is distributed under the copyleft GPL license. There are many thousands of Linux distributions, many based directly or indirectly on other distributions; popular Linux distros include Debian, Fedora Linux, Linux Mint, Arch Linux, and Ubuntu, while commercial distributions include Red Hat Enterprise Linux, SUSE Linux Enterprise, and ChromeOS. Linux distributions are frequently used in server platforms. Many Linux distributions use the word "Linux" in their name, but the Free Software Foundation uses and recommends the name "GNU/Linux", to emphasize the use and importance of GNU software in many distributions. There is controversy surrounding this. Other than the Linux kernel, key components that make up a distribution may include a display server (windowing system), a package manager, a bootloader, and a Unix shell.
Linux is one of the most prominent examples of free and open-source software collaboration. The Linux kernel is considered by many to be the largest free and open source project. While originally developed for x86-based personal computers, it has since been ported to more platforms than any other operating system. When combined with Android, which uses a Linux-based kernel and is designed for smartphones, they have the largest installed base of all general-purpose operating systems.
The Unix operating system was conceived of and implemented in 1969, at AT&T's Bell Labs in the United States, by Ken Thompson, Dennis Ritchie, Douglas McIlroy, and Joe Ossanna. First released in 1971, Unix was written entirely in assembly language, as was common practice at the time. In 1973, in a key pioneering approach, it was rewritten in the C programming language by Dennis Ritchie (except for some hardware and I/O routines). The availability of a high-level language implementation of Unix made its porting to different computer platforms easier. As a 1956 antitrust case forbade AT&T from entering the computer business, AT&T provided the operating system's source code to anyone who asked. As a result, Unix use grew quickly and it became widely adopted by academic institutions and businesses. In 1984, AT&T divested itself of its regional operating companies, and was released from its obligation not to enter the computer business; freed of that obligation, Bell Labs began selling Unix as a proprietary product, where users were not legally allowed to modify it. Onyx Systems began selling early microcomputer-based Unix workstations in 1980. Later, Sun Microsystems, founded as a spin-off of a student project at Stanford University, also began selling Unix-based desktop workstations in 1982. While Sun workstations did not use commodity PC hardware, for which Linux was later originally developed, it represented the first successful commercial attempt at distributing a primarily single-user microcomputer that ran a Unix operating system. With Unix increasingly "locked in" as a proprietary product, the GNU Project, started in 1983 by Richard Stallman, had the goal of creating a "complete Unix-compatible software system" composed entirely of free software. Work began in 1984. Later, in 1985, Stallman started the Free Software Foundation and wrote the GNU General Public License (GNU GPL) in 1989. By the early 1990s, many of the programs required in an operating system (such as libraries, compilers, text editors, a command-line shell, and a windowing system) were completed, although low-level elements such as device drivers, daemons, and the kernel, called GNU Hurd, were stalled and incomplete. Minix was created by Andrew S. Tanenbaum, a computer science professor, and released in 1987 as a minimal Unix-like operating system targeted at students and others who wanted to learn operating system principles. Although the complete source code of Minix was freely available, the licensing terms prevented it from being free software until the licensing changed in April 2000.
In a later study, the same analysis was performed for Debian version 4.0 (etch, which was released in 2007). This distribution contained close to 283 million lines of source code, and the study estimated that it would have required about seventy three thousand man-years and cost US$10.4 billion (in 2024 dollars) to develop by conventional means. Figure 1: Cyber Security Admin Dashboard UI Design :: Behance In the United States, the name Linux is a trademark registered to Linus Torvalds. Initially, nobody registered it. However, on 15 August 1994, William R. Della Croce Jr. filed for the trademark Linux, and then demanded royalties from Linux distributors.
In 1996, Torvalds and some affected organizations sued him to have the trademark assigned to Torvalds, and, in 1997, the case was settled. The licensing of the trademark has since been handled by the Linux Mark Institute (LMI). Torvalds has stated that he trademarked the name only to prevent someone else from using it. LMI originally charged a nominal sublicensing fee for use of the Linux name as part of trademarks, but later changed this in favor of offering a free, perpetual worldwide sublicense. The Free Software Foundation (FSF) prefers GNU/Linux as the name when referring to the operating system as a whole, because it considers Linux distributions to be variants of the GNU operating system initiated in 1983 by Richard Stallman, president of the FSF. The foundation explicitly takes no issue over the name Android for the Android OS, which is also an operating system based on the Linux kernel, as GNU is not a part of it. A minority of public figures and software projects other than Stallman and the FSF, notably distributions consisting of only free software, such as Debian (which had been sponsored by the FSF up to 1996), also use GNU/Linux when referring to the operating system as a whole.
Most media and common usage, however, refers to this family of operating systems simply as Linux, as do many large Linux distributions (for example, SUSE Linux and Red Hat Enterprise Linux). As of May 2011, about 8% to 13% of the lines of code of the Linux distribution Ubuntu (version "Natty") is made of GNU components (the range depending on whether GNOME is considered part of GNU); meanwhile, 6% is taken by the Linux kernel, increased to 9% when including its direct dependencies.
The adoption of Linux in production environments, rather than being used only by hobbyists, started to take off first in the mid-1990s in the supercomputing community, where organizations such as NASA started replacing their increasingly expensive machines with clusters of inexpensive commodity computers running Linux. Commercial use began when Dell and IBM, followed by Hewlett-Packard, started offering Linux support to escape Microsoft's monopoly in the desktop operating system market. Today, Linux systems are used throughout computing, from embedded systems to virtually all supercomputers, and have secured a place in server installations such as the popular LAMP application stack. The use of Linux distributions in home and enterprise desktops has been growing. Linux distributions have also become popular in the netbook market, with many devices shipping with customized Linux distributions installed, and Google releasing their own ChromeOS designed for netbooks. Linux's greatest success in the consumer market is perhaps the mobile device market, with Android being the dominant operating system on smartphones and very popular on tablets and, more recently, on wearables, and vehicles. Linux gaming is also on the rise with Valve showing its support for Linux and rolling out SteamOS, its own gaming-oriented Linux distribution, which was later implemented in their Steam Deck platform. Linux distributions have also gained popularity with various local and national governments, such as the federal government of Brazil.
Linus Torvalds is the lead maintainer for the Linux kernel and guides its development, while Greg Kroah-Hartman is the lead maintainer for the stable branch. Zoë Kooyman is the executive director of the Free Software Foundation, which in turn supports the GNU components. Finally, individuals and corporations develop third-party non-GNU components. These third-party components comprise a vast body of work and may include both kernel modules and user applications and libraries. Linux vendors and communities combine and distribute the kernel, GNU components, and non-GNU components, with additional package management software in the form of Linux distributions.
Many quantitative studies of free/open-source software focus on topics including market share and reliability, with numerous studies specifically examining Linux. The Linux market is growing, and the Linux operating system market size is expected to see a growth of 19.2% by 2027, reaching $15.64 billion, compared to $3.89 billion in 2019. Analysts project a Compound Annual Growth Rate (CAGR) of 13.7% between 2024 and 2032, culminating in a market size of US$34.90 billion by the latter year. Analysts and proponents attribute the relative success of Linux to its security, reliability, low cost, and freedom from vendor lock-in.
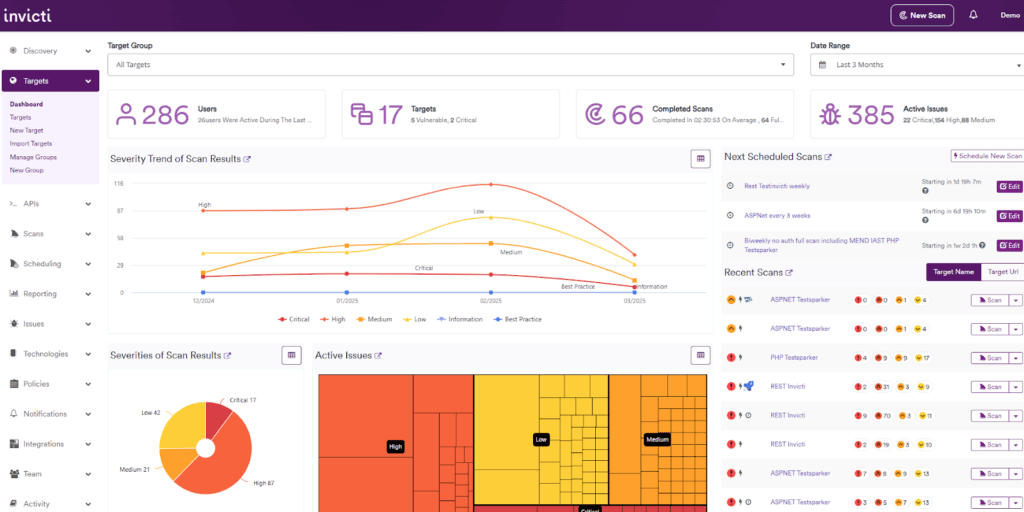
Figure 2: Top 10 Dynamic Application Security Testing (DAST) Tools for 2025 Desktops and laptops According to web server statistics (that is, based on the numbers recorded from visits to websites by client devices), in October 2024, the estimated market share of Linux on desktop computers was around 4.3%. In comparison, Microsoft Windows had a market share of around 73.4%, while macOS covered around 15.5%. Web servers W3Cook publishes stats that use the top 1,000,000 Alexa domains, which as of May 2015 estimate that 96.55% of web servers run Linux, 1.73% run Windows, and 1.72% run FreeBSD. W3Techs publishes stats that use the top 10,000,000 Alexa domains and the top 1,000,000 Tranco domains, updated monthly and as of November 2020 estimate that Linux is used by 39% of the web servers, versus 21.9% using Microsoft Windows. 40.1% used other types of Unix. IDC's Q1 2007 report indicated that Linux held 12.7% of the overall server market at that time; this estimate was based on the number of Linux servers sold by various companies, and did not include server hardware purchased separately that had Linux installed on it later. As of 2024, estimates suggest Linux accounts for at least 80% of the public cloud workload, partly thanks to its widespread use in platforms like Amazon Web Services (AWS), Microsoft Azure, and Google Cloud Platform. ZDNet reports that 96.3% of the top one million web servers are running Linux. W3Techs states that Linux powers at least 39.2% of websites whose operating system is known, with other estimates saying 55%. Mobile devices Android, which is based on the Linux kernel, has become the dominant operating system for smartphones. In April 2023, 68.61% of mobile devices accessing websites using StatCounter were from Android. Android is also a popular operating system for tablets, being responsible for more than 60% of tablet sales as of 2013. According to web server statistics, as of October 2021 Android has a market share of about 71%, with iOS holding 28%, and the remaining 1% attributed to various niche platforms. Film production For years, Linux has been the platform of choice in the film industry. The first major film produced on Linux servers was 1997's Titanic. Since then major studios including DreamWorks Animation, Pixar, Weta Digital, and Industrial Light & Magic have migrated to Linux. According to the Linux Movies Group, more than 95% of the servers and desktops at large animation and visual effects companies use Linux. Use in government Linux distributions have also gained popularity with various local and national governments. News of the Russian military creating its own Linux distribution has also surfaced, and has come to fruition as the G.H.ost Project. The Indian state of Kerala has gone to the extent of mandating that all state high schools run Linux on their computers. China uses Linux exclusively as the operating system for its Loongson processor family to achieve technology independence. In Spain, some regions have developed their own Linux distributions, which are widely used in education and official institutions, like gnuLinEx in Extremadura and Guadalinex in Andalusia. France and Germany have also taken steps toward the adoption of Linux. In April 2026 France ordered its ministries to begin to replace 2.5 million Windows desktops with Linux. North Korea's Red Star OS, developed as of 2002, is based on a version of Fedora Linux.
A bootloader, for example GNU GRUB, LILO, SYSLINUX or systemd-boot. This is a program that loads the Linux kernel into the computer's main memory, by being executed by the computer when it is turned on and after the firmware initialization is performed. An init program, such as the traditional sysvinit and the newer systemd, OpenRC and Upstart. This is the first process launched by the Linux kernel, and is at the root of the process tree. It starts processes such as system services and login prompts (whether graphical or in terminal mode). Software libraries, which contain code that can be used by running processes. On Linux systems using ELF-format executable files, the dynamic linker that manages the use of dynamic libraries is known as ld-linux.so. If the system is set up for the user to compile software themselves, header files will also be included to describe the programming interface of installed libraries. Besides the most commonly used software library on Linux systems, the GNU C Library (glibc), there are numerous other libraries, such as SDL and Mesa. The C standard library is the library necessary to run programs written in C on a computer system, with the GNU C Library being the standard. It provides an implementation of the POSIX API, as well as extensions to that API. For embedded systems, alternatives such as musl, EGLIBC (a glibc fork once used by Debian) and uClibc (which was designed for uClinux) have been developed, although the last two are no longer maintained. Android uses its own C library, Bionic. However, musl can additionally be used as a replacement for glibc on desktop and laptop systems, as seen on certain Linux distributions like Void Linux. Basic Unix commands, with GNU coreutils being the standard implementation. Alternatives exist for embedded systems, such as the copyleft BusyBox, and the BSD-licensed Toybox. Widget toolkits are the libraries used to build graphical user interfaces (GUIs) for software applications. Numerous widget toolkits are available, including GTK and Clutter developed by the GNOME Project, Qt developed by the Qt Project and led by The Qt Company, and Enlightenment Foundation Libraries (EFL) developed primarily by the Enlightenment team. A package management system, such as dpkg and RPM. Alternatively packages can be compiled from binary or source tarballs. User interface programs such as command shells or windowing environments.
The user interface, also known as the shell, is either a command-line interface (CLI), a graphical user interface (GUI), or controls attached to the associated hardware, which is common for embedded systems. For desktop systems, the default user interface is usually graphical, although the CLI is commonly available through terminal emulator windows or on a separate virtual console. CLI shells are text-based user interfaces, which use text for both input and output. The dominant shell used in Linux is the Bourne-Again Shell (bash), originally developed for the GNU Project; other shells such as Zsh are also used. Most low-level Linux components, including various parts of the userland, use the CLI exclusively. The CLI is particularly suited for automation of repetitive or delayed tasks and provides very simple inter-process communication. On desktop systems, the most popular user interfaces are the GUI shells, packaged together with extensive desktop environments, such as KDE Plasma, GNOME, MATE, Cinnamon, LXDE, Pantheon, and Xfce, though a variety of additional user interfaces exist. Most popular user interfaces are based on the X Window System, often simply called "X" or "X11". It provides network transparency and permits a graphical application running on one system to be displayed on another where a user may interact with the application; however, certain extensions of the X Window System are not capable of working over the network. Several X display servers exist, with the reference implementation, X.Org Server, being the most popular. Several types of window managers exist for X11, including tiling, dynamic, stacking, and compositing. Window managers provide means to control the placement and appearance of individual application windows, and interact with the X Window System. Simpler X window managers such as dwm, ratpoison, or i3wm provide a minimalist functionality, while more elaborate window managers such as FVWM, Enlightenment, or Window Maker provide more features such as a built-in taskbar and themes, but are still lightweight when compared to desktop environments. Desktop environments include window managers as part of their standard installations, such as Mutter (GNOME), KWin (KDE), or Xfwm (xfce), although users may choose to use a different window manager if preferred. Wayland is a display server protocol intended as a replacement for the X11 protocol; as of 2022, it has received relatively wide adoption. Unlike X11, Wayland does not need an external window manager and compositing manager. Therefore, a Wayland compositor takes the role of the display server, window manager, and compositing manager.
Weston is the reference implementation of Wayland, while GNOME's Mutter and KDE's KWin are being ported to Wayland as standalone display servers. Enlightenment has already been successfully ported since version 19. Additionally, many window managers have been made for Wayland, such as Sway or Hyprland, as well as other graphical utilities such as Waybar or Rofi.
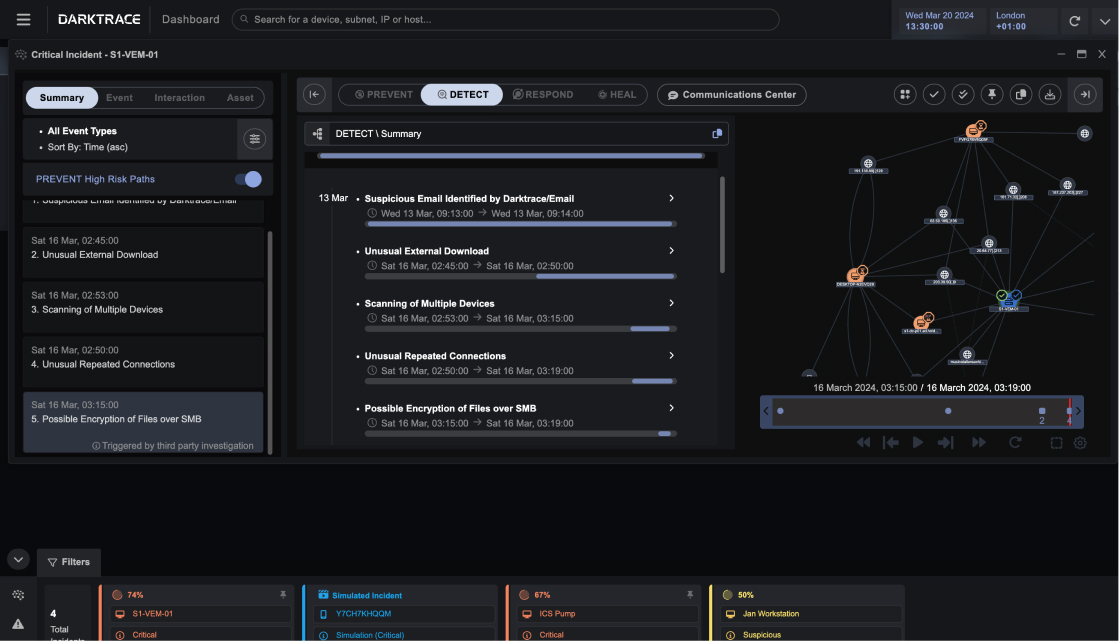
Figure 3: ActiveAI Security Platform | Darktrace Linux currently has two modern kernel-userspace APIs for handling video input devices: V4L2 API for video streams and radio, and DVB API for digital TV reception. The diversity of hardware standards and data formats requires continuous architectural refinement to maintain compatibility across different device classes. Development focuses on providing robust userspace libraries to abstract device complexity, ensuring that applications can interface with varying formats without specialized hardware-specific drivers.
The primary difference between Linux and many other popular contemporary operating systems is that the Linux kernel and other components are free and open-source software. Linux is not the only such operating system, although it is by far the most widely used. Some free and open-source software licenses are based on the principle of copyleft, a kind of reciprocity: any work derived from a copyleft piece of software must also be copyleft itself. The most common free software license, the GNU General Public License (GPL), is a form of copyleft and is used for the Linux kernel and many of the components from the GNU Project. Linux-based distributions are intended by developers for interoperability with other operating systems and established computing standards. Linux systems adhere to POSIX, Single UNIX Specification (SUS), Linux Standard Base (LSB), ISO, and ANSI standards where possible, although to date only one Linux distribution has been POSIX.1 certified, Linux-FT. The Open Group has tested and certified at least two Linux distributions as qualifying for the Unix trademark, EulerOS and Inspur K-UX. Free software projects, although developed through collaboration, are often produced independently of each other. The fact that the software licenses explicitly permit redistribution, however, provides a basis for larger-scale projects that collect the software produced by stand-alone projects and make it available all at once in the form of a Linux distribution. Many Linux distributions manage a remote collection of system software and application software packages available for download and installation through a network connection. This allows users to adapt the operating system to their specific needs. Distributions are maintained by individuals, loose-knit teams, volunteer organizations, and commercial entities. A distribution is responsible for the default configuration of the installed Linux kernel, general system security, and more generally integration of the different software packages into a coherent whole. Distributions typically use a package manager such as apt, yum, zypper, pacman or portage to install, remove, and update all of a system's software from one central location.
A distribution is largely driven by its developer and user communities. Some vendors develop and fund their distributions on a volunteer basis, Debian being a well-known example. Others maintain a community version of their commercial distributions, as Red Hat does with Fedora, and SUSE does with openSUSE. In many cities and regions, local associations known as Linux User Groups (LUGs) seek to promote their preferred distribution and by extension free software. They hold meetings and provide free demonstrations, training, technical support, and operating system installation to new users. Many Internet communities also provide support to Linux users and developers. Most distributions and free software / open-source projects have IRC chatrooms or newsgroups. Online forums are another means of support, with notable examples being Unix & Linux Stack Exchange, LinuxQuestions.org and the various distribution-specific support and community forums, such as ones for Ubuntu, Fedora, Arch Linux, Gentoo, etc. Linux distributions host mailing lists; commonly there will be a specific topic such as usage or development for a given list. There are several technology websites with a Linux focus. Print magazines on Linux often bundle cover disks that carry software or even complete Linux distributions. Although Linux distributions are generally available without charge, several large corporations sell, support, and contribute to the development of the components of the system and free software. An analysis of the Linux kernel in 2017 showed that well over 85% of the code was developed by programmers who are being paid for their work, leaving about 8.2% to unpaid developers and 4.1% unclassified. Some of the major corporations that provide contributions include Intel, Samsung, Google, AMD, Oracle, and Facebook. Several corporations, notably Red Hat, Canonical, and SUSE have built a significant business around Linux distributions. The free software licenses, on which the various software packages of a distribution built on the Linux kernel are based, explicitly accommodate and encourage commercialization; the relationship between a Linux distribution as a whole and individual vendors may be seen as symbiotic. One common business model of commercial suppliers is charging for support, especially for business users. A number of companies also offer a specialized business version of their distribution, which adds proprietary support packages and tools to administer higher numbers of installations or to simplify administrative tasks.
Another business model is to give away the software to sell hardware. This used to be the norm in the computer industry, with operating systems such as CP/M, Apple DOS, and versions of the classic Mac OS before 7.6 freely copyable (but not modifiable). As computer hardware standardized throughout the 1980s, it became more difficult for hardware manufacturers to profit from this tactic, as the OS would run on any manufacturer's computer that shared the same architecture.
Most programming languages support Linux either directly or through third-party community based ports. The original development tools used for building both Linux applications and operating system programs are found within the GNU toolchain, which includes the GNU Compiler Collection (GCC) and the GNU Build System. Among others, GCC provides compilers for Ada, C, C++, Go and Fortran. Many programming languages have a cross-platform reference implementation that supports Linux, for example PHP, Perl, Ruby, Python, Java, Go, Rust and Haskell. First released in 2003, the LLVM project provides an alternative cross-platform open-source compiler for many languages. Proprietary compilers for Linux include the Intel C++ Compiler, Sun Studio, and IBM XL C/C++ Compiler. BASIC is available in procedural form from QB64, PureBasic, Yabasic, GLBasic, Basic4GL, XBasic, wxBasic, SdlBasic, and Basic-256, and in object oriented through Gambas, FreeBASIC, B4X, Basic for Qt, Phoenix Object Basic, NS Basic, ProvideX, Chipmunk Basic, RapidQ and Xojo. Pascal is implemented through GNU Pascal, Free Pascal, Virtual Pascal, and graphically via Lazarus, PascalABC.NET, or Delphi using FireMonkey (formerly through Borland Kylix). A common feature of Unix-like systems, Linux includes traditional specific-purpose programming languages targeted at scripting, text processing and system configuration and management in general. Linux distributions support shell scripts, AWK, sed and make. Many programs also have an embedded programming language to support configuring or programming themselves. For example, regular expressions are supported in programs like grep and locate, the traditional Unix message transfer agent Sendmail contains its own Turing complete scripting system, and the advanced text editor GNU Emacs is built around a general purpose Lisp interpreter. Most distributions also include support for PHP, Perl, Ruby, Python and other dynamic languages. While not as common, Linux also supports C# and other CLI languages (via Mono), Vala, and Scheme. Guile Scheme acts as an extension language targeting the GNU system utilities, seeking to make the conventionally small, static, compiled C programs of Unix design rapidly and dynamically extensible via an elegant, functional high-level scripting system; many GNU programs can be compiled with optional Guile bindings to this end. Many Java virtual machines and development kits run on Linux, including the original Sun Microsystems JVM (HotSpot), IBM's J2SE RE, and many open-source projects like Kaffe and Jikes RVM; Kotlin, Scala, Groovy and other JVM languages are also available. GNOME and KDE are popular desktop environments and provide a framework for developing applications. These projects are based on the GTK and Qt widget toolkits, respectively, which can also be used independently of the larger framework. Both support a wide variety of languages. There are a number of Integrated development environments available including Anjuta, Code::Blocks, CodeLite, Eclipse, Geany, ActiveState Komodo, KDevelop, Lazarus, MonoDevelop, NetBeans, and Qt Creator, while the long-established editors Vim, nano and Emacs remain popular.
The Linux kernel is a widely ported operating system kernel, available for devices ranging from mobile phones to supercomputers; it runs on a highly diverse range of computer architectures, including ARM-based Android smartphones and the IBM Z mainframes. Specialized distributions and kernel forks exist for less mainstream architectures; for example, the ELKS kernel fork can run on Intel 8086 or Intel 80286 16-bit microprocessors, while the µClinux kernel fork may run on systems without a memory management unit. The kernel also runs on architectures that were only ever intended to use a proprietary manufacturer-created operating system, such as Macintosh computers (with PowerPC, Intel, and Apple silicon processors), PDAs, video game consoles, portable music players, and mobile phones. Linux has a reputation for supporting old hardware very well by maintaining standardized drivers for a long time. There are several industry associations and hardware conferences devoted to maintaining and improving support for diverse hardware under Linux, such as FreedomHEC. Over time, support for different hardware has improved in Linux, resulting in any off-the-shelf purchase having a "good chance" of being compatible. In 2014, a new initiative was launched to automatically collect a database of all tested hardware configurations.
One commonly expressed attribute about Linux (or open source software in general) is that through regular vetting by many individuals the software is progressively made more secure, a process referred to as being called "Linus's law". Linux is often highlighted for its share of the estimated global servers market share. Besides many volunteers, the not-for-profit bodies such as the Open Source Security Foundation and Linux Foundation actively pursue ways to promote security in the Linux platform as well.
Graphical map of Linux Internals (archived) Linux kernel website and archives The History of Linux in GIT Repository Format 1992–2010 (archived) Here’s the uncomfortable truth: your code review passed, your SAST tools gave you the green light, and you still shipped a critical vulnerability. Why? Because some of the most exploitable security flaws only exist when your application is actually running.
Modern applications are API-first architectures where the real attack surface only materializes at runtime. AI and LLM components introduce endpoints that don’t exist in your source code. Authentication flows, rate limiting, business logic vulnerabilities—none of these can be detected by static analysis. They only surface when the application is executing. For years, DAST was written off as too slow, too clunky, too late to matter. Traditional tools acted as final security gates, flagging issues only after code was deployed or about to be. Every finding became an emergency fire drill. So teams doubled down on static analysis instead.
But here’s the irony: just as we collectively decided dynamic testing was outdated, the application landscape changed in ways that make it more essential than ever. The answer isn’t to skip runtime testing. It’s to reimagine it. Modern approaches integrate dynamic analysis directly into CI/CD pipelines, catching exploitable vulnerabilities before production while developers still have context. Runtime security that actually scales with AI-driven development velocity.
In this guide, we will look at what dynamic analysis is, why the traditional security model is flawed, and how teams are addressing this issue by putting runtime testing directly into developers’ hands. We’ll cover when dynamic analysis catches stuff that static tools miss, how to integrate it without becoming everyone’s least favorite bottleneck, and why the future of AppSec means developers owning security from the first commit.
The first and most important thing to note is that dynamic analysis tests software while it’s running. It’s a blackbox approach that requires no source code scanning, and no theoretical vulnerabilities just because code matches a potential pattern. These tools just watch what your application actually does when it executes and reports back any issues that occurred. The key difference is that you need a live, running instance. You’re observing a real system processing data, managing state, interacting with APIs, and communicating with databases. This is where runtime behavior reveals vulnerabilities that appear to be fine in code review or vulnerabilities that appear in the code but could never actually be exploited.
2. System Architecture & Core Working Principles Depending on exactly what tool you are using for the dynamic analysis, what gets monitored could include everything from memory allocation and cleanup, network requests and API calls, authentication flows, how the app handles malicious inputs, resource usage and state management, and database queries built from user input.
Dynamic analysis identifies problems that only exist within a specific context. Race conditions that need precise timing. Injection vulnerabilities that depend on how three services handle a specific input sequence. Configuration errors that only show up in deployed environments. What it finds are the exploitable flaws attackers actually use, the ones that should truly be patched before a production deployment.
It wouldn’t be a complete guide without bringing up this subject. The industry loves the “ SAST vs. DAST ” debate like you have to pick a side. That’s a false choice that misses the entire point. Static analysis tools, like SAST, don’t need running code and instead look for particular patterns that could potentially signal a vulnerability or performance issue. On the flip side, as we mentioned earlier, dynamic analysis is performed against the running application and finds those vulnerabilities that are truly exploitable. As you can probably see, both are quite complementary, especially when looked at side-by-side: In short, static analysis catches patterns while dynamic analysis catches actual behavior.
This means that static tools are great for obvious stuff early on, like finding SQL queries built from unsanitized strings, hardcoded secrets, and deprecated functions. They’re fast, some can run in your IDE or terminal, and catch problems before you even commit. But they can’t tell you if that SQL injection is actually exploitable in your running app, or whether those auth checks actually work when someone tries to bypass them.
Dynamic analysis flips this. It only tests code that executes, meaning untested paths are blind spots. However, it catches runtime-specific problems that no amount of code review can find, such as authentication and authorization bypasses and configuration mismatches between environments, such as CORS misconfigurations. So, the actual question really isn’t which one to use; rather, it’s how to use both without killing your velocity.
Good teams run static analysis continuously during development (using IDE plugins, CLI’s, and pre-commit hooks) to catch obvious flaws quickly. Then they run dynamic analysis on local builds, in CI/CD and staging to validate that the running application is actually secure, not just theoretically secure based on code patterns. For modern API-first applications running in CI/CD pipelines, Dynamic Application Security Testing (DAST) is the foundation.
It’s the only approach that tests your running APIs exactly as attackers see them, finding exploitable vulnerabilities in authentication flows, authorization logic, and business logic, i.e. the stuff that matters most for today’s development teams. That said, the dynamic analysis landscape includes several specialized techniques that complement DAST for specific use cases. Here’s how they fit together: Traditional DAST tools were built for security teams to run quarterly scans—a model that died years ago. Modern DAST is designed for developers to run continuously, both locally and in CI/CD pipelines.
A modern, shift-left DAST solution like StackHawk automatically discovers API endpoints, tests for OWASP Top 10 vulnerabilities , and delivers findings in formats developers understand with no security expertise required to configure. This is where most teams should start and where the majority of exploitable vulnerabilities get caught. Fuzz Testing sends malformed and unexpected inputs to your APIs to uncover edge cases and vulnerabilities that standard testing misses. Modern API fuzzers can work from OpenAPI specifications to generate test cases that deliberately violate expected structures. StackHawk’s DAST platform complements API fuzzing efforts by confirming whether bugs found during fuzzing are exploitable security vulnerabilities. Most teams run fuzzing for high-risk endpoints handling sensitive data, integrating it into CI/CD alongside their DAST testing.
IAST (Interactive Application Security Testing) sits inside your application runtime, tracking data flow from entry to exploit. It provides detailed vulnerability traces but requires deploying agents into your application stack. The overhead and integration complexity make sense for staging environments where you need deep analysis, but DAST catches most runtime issues without the deployment burden.
Behavioral Analysis establishes baselines of normal behavior and flags deviations, which are useful for detecting API abuse patterns and novel attacks in production. Think of it as runtime monitoring rather than pre-deployment testing. It complements DAST by watching for threats after deployment, not replacing the testing that should happen before code ships. If you’re building modern applications with APIs and microservices, start with DAST integrated into your CI/CD pipeline . It catches the vast majority of exploitable runtime vulnerabilities without requiring specialized infrastructure or security expertise.
Add the other techniques only when you have specific needs that DAST doesn’t address, and even then, DAST remains your foundation. For dynamic analysis to be holistic, integration into CI/CD is critical. That said, some common challenges with dynamic analysis in CI/CD is that it needs running infrastructure, it takes time to configure, and can be noisy. Get it wrong and you’ve created the gate that slows everything down. Two ways to make sure this integration is successful is to use a tiered testing approach and to be aware of the environments to run testing within.
Running a comprehensive dynamic analysis on every commit sounds amazing. It doesn’t work in practice for high-velocity development teams. Here, I’m talking about everything under the dynamic analysis umbrella, not just DAST. Using this approach, you can see that the fastest tests should run frequently and comprehensive tests run less often. Both matter, but attempting to conduct comprehensive testing on every commit can hinder your pipeline velocity, including if developers are running massive testing operations on their local machines every time they create even a little bit of code.
Certain types of testing make sense to run frequently while others can be used more strategically so you don’t eat up developer time and your build minutes. You need somewhere to run this stuff. Local development gives fast feedback but limited infrastructure. Staging environments strike a balance between realism and safety, where comprehensive dynamic testing typically occurs. Production offers ultimate realism but needs guardrails for runtime monitoring and RASP. Containers plus service mocks work as a compromise: run your app in Docker with mocked dependencies for something faster than full staging but more realistic than local-only. The best setups maintain staging environments that mirror production architecture, accepting the infrastructure cost as the price of identifying and addressing vulnerabilities before they become exploitable.
There are plenty of tools out there that can round out a dynamic analysis stack. Of course, at StackHawk we believe the main hub is DAST since it can give truly comprehensive feedback on exploitable vulnerabilities. That said, layering on the other techniques we discussed is also critical if you want to cover your attack surface from as many angles as possible. When it comes to DAST, StackHawk represents the modern approach: Dynamic security testing designed for developers, not just security specialists. We believe that DAST should cover all aspects of the running application, including one of the more critical components: your APIs.
StackHawk’s API Discovery tool uses source code to reveal your complete API landscape, including shadow APIs before deployment. This enables automatic testing that discovers endpoints without a whole bunch of manual setup and complex integrations. On top of these capabilities, our developer-native workflows run naturally in CI/CD, integrating seamlessly with GitHub, GitLab, and Jenkins. The feedback from the tool can easily be digested in reports and translated into actionable findings, even allowing developers to generate cURL commands to reproduce vulnerabilities and showing potential fixes to guide developers down the right path.
Best suited for teams implementing DevSecOps , organizations with API-first architectures, and companies that want developers to own security even if they don’t have dedicated AppSec personnel. This follows our belief in shifting security left by making testing as natural for developers as running their functional test suites. When it comes to measuring how effective tools are, there are a few core metrics to focus on. Here’s what actually indicates whether dynamic analysis is working: Vulnerability detection effectiveness measures whether you’re finding real problems. Track severity and count, but more importantly, track false positive rates. A tool generating 500 alerts with 95% false positives is worse than one generating 50 alerts with 90% accuracy. In short, more alerts doesn’t necessarily mean the tool is working well.
3. Software Implementation, Frameworks & Protocols Integration efficiency measures how smoothly it fits into workflows. Monitor test execution time and the percentage of builds that include dynamic analysis, versus those that skip it. Measure the mean time to remediate: how long from detection to deployment of a fix? Business impact connects testing to outcomes executives care about. Measure the reduction in security incidents reaching production and the cost avoided by catching vulnerabilities before production. After all, security is about ensuring that customer and internal data is safe so that the business can grow confidently without the burden of breaches or other security incidents that undermine growth.
Dynamic analysis alone is not a silver bullet, as with any testing method used in isolation. What dynamic analysis is good for: Finding exploitable runtime vulnerabilities before attackers do. Validating that security controls are effective in operational environments. Catching configuration issues that only surface during execution. Testing APIs and auth flows as attackers see them. What it’s not good for: Finding every possible vulnerability (since coverage depends on what you test). Replacing static analysis or code review (they catch different things), and trying to cover up a fundamentally insecure architecture. It is simply one piece of the security puzzle.
The real goal of dynamic analysis (and other security tools and techniques) is to ship measurably more secure software at a pace your business can sustain. Dynamic analysis helps you find and fix vulnerabilities faster than you introduce them. Ready to see how modern dynamic analysis and DAST fits into your workflow? Try StackHawk free and start testing your APIs in minutes, or schedule a demo to see how teams are shifting security left without slowing down delivery.
The Smartest People in AI Are Telling Us to Fix Everything. Now There Is a Way to Do It. Seven months of warnings from Anthropic, OpenAI, and Microsoft say the same thing: the bugs you deprioritized are exploitable, and the window is short. Wingman is broadly available today. Here is why we built it. Compare eight of the best API security testing tools in 2026, including StackHawk, ZAP, Burp Suite, and more. See how they compare on API coverage, authentication, CI/CD integration, pricing, and authorization testing.
Learn how broken access control vulnerabilities like IDOR and privilege escalation happen, how code review can detect them, and how runtime testing verifies authorization across users, roles, and resources. Dynamic Analysis is the runtime evaluation of software and systems to observe actual behavior under real or simulated conditions. Analogy: like a cardiologist monitoring a patient during exercise rather than relying on a single snapshot. Formal: the continuous collection and analysis of runtime telemetry to infer correctness, performance, security, and reliability.
Dynamic Analysis inspects systems while they run. It is not static code review or design-time verification. It observes behavior: requests, resource usage, errors, latencies, concurrency patterns, and environmental interactions. Dynamic Analysis includes active testing (load, chaos), passive observability (traces, metrics, logs), and runtime security checks (RASP, runtime policy enforcement).
Dynamic Analysis is the continuous practice of observing and testing systems in operation to identify performance, reliability, functional, and security issues that only appear at runtime. 1) Prerequisites – Service inventory with owners and SLAs. – Instrumentation libraries and sidecar options chosen. – Observability pipeline and storage capacity planning. – Access controls and privacy directives for telemetry.
2) Instrumentation plan – Map core transactions and business-critical paths. – Add correlation IDs and semantic spans. – Standardize metric names and units. – Establish cardinality limits and tagging strategy. 3) Data collection – Deploy collectors and configure sampling. – Enforce scrubbers for PII and secrets. – Validate end-to-end ingestion and retention.
4) SLO design – Define SLIs aligning with user experience. – Choose SLO periods and error budget policies. – Publish SLOs to stakeholders. 5) Dashboards – Build executive, on-call, and debug dashboards. – Template dashboards per service and reuse panels. 6) Alerts & routing – Define page vs ticket thresholds. – Configure notification routing and escalation policies.
7) Runbooks & automation – Create runbooks for common alerts with step-by-step remediation. – Automate rollback, scaling, and throttling remediation where safe. 8) Validation (load/chaos/game days) – Run load tests in staging and shadow environments. – Execute chaos experiments with rollback safety. – Run game days with on-call to validate runbooks.
9) Continuous improvement – Postmortem-driven instrumentation and SLO refinement. – Monthly telemetry cost and retention review. – Quarterly chaos engineering maturity assessment. 1) Latency regression detection – Context: Public API begins responding slower. – Problem: SLO at risk and customer complaints. – Why DA helps: Detects tail latencies and isolates offending service. – What to measure: P95/P99, trace spans, DB query latencies. – Typical tools: Tracing backend, APM, synthetic monitors.
2) Autoscaler correctness validation – Context: Autoscaling rules produce oscillation. – Problem: Thundering herd and resource thrash. – Why DA helps: Observes scaling under realistic load and tunes policies. – What to measure: Pod startup time, CPU utilization, scaling events. – Typical tools: Kubernetes metrics, load generators. 3) Runtime security detection – Context: Application probed for injection attacks. – Problem: Unknown exploitation attempts. – Why DA helps: RASP and anomaly detection catch runtime exploitation. – What to measure: Unusual request patterns, blocked events. – Typical tools: RASP, WAF telemetry.
4) Cold-start mitigation for serverless – Context: Functions introduce latency spikes. – Problem: High tail latency for sporadic endpoints. – Why DA helps: Measures cold start rate and informs warmers or provisioned concurrency. – What to measure: Invocation latency, initialization time. – Typical tools: Function metrics, synthetic invocations. 5) Dependency regression root cause – Context: Third-party service update causes errors. – Problem: Partial failures and cascading errors. – Why DA helps: Correlates traces and isolates failing external calls. – What to measure: External call latency and error codes. – Typical tools: Tracing, distributed logs.
6) Capacity planning and cost optimization – Context: Increasing cloud spend with unknown source. – Problem: Overprovisioned clusters and telemetry cost growth. – Why DA helps: Identifies inefficiencies and informs rightsizing. – What to measure: Resource utilization per request and telemetry ingestion rates. – Typical tools: Metrics, cost allocation telemetry. 4. Practical Deployment, Analysis & Case Studies 7) Biz logic correctness under concurrency – Context: Race conditions lead to inconsistent state. – Problem: Data discrepancies and customer complaints. – Why DA helps: Observes real concurrent traces and reproduces via load tests. – What to measure: Transaction conflicts, retries, invariants. – Typical tools: Tracing, DB transaction logs.
8) Deployment impact analysis – Context: New release shows increased error rate. – Problem: Hard to distinguish code vs infra cause. – Why DA helps: Canary comparisons and side-by-side telemetry show differences. – What to measure: Canary vs baseline SLIs and trace differences. – Typical tools: Canary orchestration, tracing. Context: E-commerce API deployed on Kubernetes shows intermittent high latency during sale events. Goal: Detect and mitigate tail latency and prevent revenue loss. Why Dynamic Analysis matters here: Real traffic patterns, autoscaler behavior, and node eviction cause issues only at scale. Architecture / workflow: Ingress -> API pods with sidecar tracing -> DB and cache. Prometheus collects metrics, Jaeger collects traces, Grafana dashboards. Step-by-step implementation: Context: A serverless image-resizing function has inconsistent response times. Goal: Reduce cold start impact and ensure consistent latencies. Why Dynamic Analysis matters here: Cold starts depend on runtime environment and invocation patterns. Architecture / workflow: CDN -> Function platform with cloud-managed metrics -> S3 for input/output. Synthetic monitors and function logs feed observability. Step-by-step implementation: Context: An incident where cache misconfiguration caused DB overload and outages. Goal: Root cause identification and future prevention. Why Dynamic Analysis matters here: Live telemetry uncovers cascading failure timeline and contributing factors. Architecture / workflow: Services rely on cache layer; failing cache causes higher DB traffic. Traces show cache misses and burst of DB calls. Step-by-step implementation: Context: Observability costs balloon as retention increases. Goal: Balance debugging needs with cost constraints. Why Dynamic Analysis matters here: Retention policy directly affects post-incident analysis capability. Architecture / workflow: Telemetry ingest flows into long-term storage with tiered retention. Sampling and rollups reduce volume. Step-by-step
Implementation
Dynamic Analysis includes active testing as well as passive observability; observability focuses on collecting signals to answer questions about system state. Partially via black-box tests and network captures, but instrumentation provides richer, contextual signals. It can if intrusive tests are run without guardrails; use shadow traffic and canary approaches to minimize risk.
Implementation Synonym
High-value and customer-facing services should; smaller internal tools can be exempt temporarily. Yes for runtime exploits and anomalies, but it should complement static and penetration testing. Start conservative based on user tolerance; example 99.9% for critical APIs but varies by business need. Reduced incidents, faster MTTD/MTTR, and fewer postmortem action items tied to missing telemetry.
Implementation Meaning
Yes SDKs vary by language but standards like OpenTelemetry provide cross-language conventions. A sampling approach that keeps error or anomalous traces while downsampling common successful traces to save cost. They are complementary; synthetic detects availability from external vantage points and early regressions. Dynamic Analysis is essential to understand and improve software behavior in real-world conditions. It bridges testing and production by providing continuous feedback that reduces incidents, informs SLOs, and supports resilient architectures.
Implementation Science
#Automation #CareerGrowth #CICD #CI_CD #CloudAutomation #CloudComputing #CloudDevOps #CloudNative #DataScience #DevOps #DevOpsAutomation #DevOpsCareer #DevOpsCareers #DevOpsSkills #DevOpsTools #DevOpsTraining #DevSecOps #EnterpriseDevOps #InfrastructureAsCode #ITTraining #Kubernetes #MachineLearning #Microservices #Observability #SiteReliabilityEngineering #SoftwareDelivery #SoftwareDevelopment #SRE #TechSkills #TechTraining Applications now sit at the center of daily life, powering everything from online shopping to digital banking. That makes them prime targets for attackers who exploit weak points such as unpatched code, misconfigurations, or poor authentication to steal data or gain access. To stay ahead, organizations need security measures that replicate how real attackers operate. This is where Dynamic Application Security Testing (DAST) proves its value.
Implementation Specialist
DAST evaluates a live, running application from the outside – just as an attacker would – by sending requests, analyzing responses, and flagging vulnerabilities such as SQL injection, cross-site scripting (XSS), or broken authentication. Unlike static code analysis, it doesn’t require access to source code, which makes it a powerful complement to other testing methods.
Implementation Definition
Applications now sit at the core of business operations, which makes them a top target for attackers. The threat landscape continues to evolve rapidly, with complex architectures and high stakes that range from data breaches to regulatory fines and lasting damage to reputation. Weak authentication, misconfigured APIs, and injection flaws remain among the most common vulnerabilities exploited.
Implementation Manager
To counter these risks, organizations rely on application security testing to find and fix issues before they can be abused. Techniques like SAST, DAST, and IAST work best together – covering different stages of the application lifecycle, from development to runtime. Combined, they give businesses a stronger defense and a way to stay ahead of increasingly sophisticated attacks.
Implementation Consultant
Dynamic Application Security Testing (DAST) is essential for protecting web applications because it examines security the same way an attacker would. Instead of reviewing source code, DAST interacts with a live application to expose vulnerabilities such as SQL injection, cross-site scripting (XSS), and broken authentication. This black-box approach makes it especially effective at catching issues like misconfigurations, runtime errors, and hidden weaknesses that often slip through during development. In practice, DAST complements other testing methods by showing whether an application can truly withstand real-world attacks.
Implementation Intentions
Dynamic Application Security Testing (DAST) is a black-box testing approach that evaluates applications in their running state. Instead of examining the source code, it mimics real-world attacks by sending requests and analyzing responses to uncover vulnerabilities such as SQL injection, cross-site scripting (XSS), and authentication flaws. DAST tests from an external perspective, it doesn’t require access to the code itself. This makes it especially useful for third-party, legacy, or cloud-based applications where source code may not be available. By focusing on runtime behavior, DAST provides practical insight into how attackers could exploit weaknesses in a live environment.
Implementation Engineers
While DAST is highly effective in detecting runtime vulnerabilities, it is one of several approaches to application security testing: 5. Performance Evaluation & Extended Technical Observations Dynamic Application Security Testing (DAST) evaluates an application while it’s running to uncover vulnerabilities that attackers could exploit. Rather than reviewing the source code, it treats the application as a black box, sending inputs, simulating attacks, and analyzing how the system responds.
Because it focuses on runtime behavior, DAST mirrors real-world attack scenarios. This makes it effective at catching issues – such as authentication flaws, misconfigurations, or unintended data exposure – that often surface only after an application has been deployed. Dynamic Application Security Testing (DAST) is often called a black-box testing approach because it examines applications from the outside, much like an attacker would. Instead of inspecting internal code or architecture, DAST interacts with the running application – sending requests, simulating attacks, and analyzing responses. This provides a realistic view of how the application holds up under hostile conditions and whether vulnerabilities could be exploited in real-world scenarios.
The key advantages of black-box testing with DAST is that it’s language-agnostic – it works no matter what programming language or framework was used. It’s also effective at uncovering issues such as injection flaws, authentication gaps, and misconfigurations that only appear once the application is live. Dynamic Application Security Testing (DAST) works, breaking the scan into simple steps. Unlike static code analysis, DAST exercises the application while it’s running – just as an attacker would. A typical run starts by crawling and mapping the app, then launches realistic attack payloads, and finally analyzes the responses to spot weaknesses.
This step-by-step approach shows how vulnerabilities surface at runtime. It pinpoints risky areas and illustrates how they could be exploited in the real world, giving teams clear, actionable guidance on what to fix first. The DAST tool first crawls the application, systematically discovering and mapping all available pages, endpoints, forms, APIs, and resources. This process is akin to following every hyperlink and filling each form to understand all surface areas accessible to users – and potential attackers.
Next, the tool sends various crafted requests – some benign, others malicious – to the identified entry points, often mimicking common attack patterns like SQL injection, cross-site scripting (XSS), and authentication bypass attempts. The goal is to trigger security flaws under realistic attack scenarios using payloads representative of actual threats. DAST scrutinizes the application’s responses, looking for telltale signs of vulnerabilities, such as error messages, unexpected disclosures, or abnormal system reactions. Any anomalous output hinting at insecure behavior is flagged for review, and the findings are presented in detailed vulnerability reports for remediation.
Dynamic Application Security Testing (DAST) is an essential way to protect modern applications against real-world cyber threats. Unlike static testing, which reviews code without running it, DAST evaluates applications in their live state, simulating attacks from the outside to reveal vulnerabilities. When used strategically, DAST gives organizations clear, actionable insights into security gaps, supports compliance with industry regulations, and integrates smoothly into DevSecOps pipelines. By making DAST part of the development cycle, businesses can strengthen security without slowing down the speed and agility their teams rely on.
The biggest strengths of Dynamic Application Security Testing (DAST) are its ability to find vulnerabilities in live, running applications. Unlike static testing, which only looks at source code, DAST interacts with the application the way an attacker would. This allows it to catch runtime issues – such as SQL injection, cross-site scripting (XSS), authentication flaws, and session management weaknesses – that static scans often miss.
By exposing these risks in real-world conditions, DAST gives security teams a clearer view of the actual threats facing the application. With that insight, they can prioritize fixes based on verified vulnerabilities instead of theoretical ones, reducing the chance of costly breaches or service disruptions. DAST goes beyond flagging theoretical risks – it actively simulates the tactics, techniques, and procedures attackers use in the real world. By sending crafted inputs and malicious requests, it tests how an application behaves under hostile conditions.
This not only confirms whether the app can resist exploitation attempts but also shows security teams exactly how a vulnerability could be abused. With this simulation-based approach, organizations move past compliance-driven checkbox testing and adopt a truly proactive security stance. Developers and security teams gain a clearer understanding of how attackers might break in, giving them the chance to fix weaknesses before they are exploited in production.
DAST evaluates applications in their deployed state, it works regardless of the programming language or framework behind them. Whether your systems run on Java, .NET, Python, PHP, Ruby, or a mix of modern technologies, DAST can scan them without requiring access to the source code. This makes it especially useful for organizations with diverse tech stacks or third-party components.
Its language independence ensures every application gets the same level of security testing. By eliminating the need for multiple specialized tools, DAST simplifies the testing process while still delivering consistent coverage across the board. Dynamic Application Security Testing (DAST) is a practical way to support compliance with standards like PCI DSS, SOC 2, and ISO 27001. Frameworks require regular testing and evidence that vulnerabilities are being managed to protect sensitive data. By running DAST scans, organizations can show auditors – and themselves – that application-level risks are being found and addressed on an ongoing basis.
DAST also helps streamline compliance by mapping vulnerabilities directly to regulatory requirements. For example, reports can be aligned with PCI DSS application security controls or SOC 2 system security criteria. This makes audits easier to prepare for while reinforcing a strong security posture to customers and stakeholders. Modern software development moves fast, with constant code changes and rapid release cycles. DAST fits naturally into DevSecOps pipelines by delivering automated, continuous security testing. When integrated into CI/CD workflows, it ensures every build and deployment is checked for vulnerabilities – without slowing down release timelines.
This ongoing monitoring helps teams catch issues the moment they appear, making them far cheaper and easier to fix. By embedding DAST into DevSecOps, organizations can keep up their development speed while ensuring applications stay resilient against evolving threats throughout their lifecycle. Learn how DAST fits into modern DevSecOps workflows in our comparison piece: AppSec vs DevSecOps: Navigating the Security Landscape.
Dynamic Application Security Testing (DAST) helps organizations identify vulnerabilities in live applications by simulating real-world attacks. Unlike static testing, it uses a black-box approach, assessing the application from the outside – so it doesn’t require access to the source code. As cloud-native platforms, APIs, and rapid DevSecOps workflows become the norm, DAST’s role has grown. Whether scanning web apps, APIs, or containerized environments, it delivers actionable insights that help teams strengthen defenses and keep security aligned with the pace of modern development.
Discover how different tools scan APIs, including DAST scanners, in our “Top 11 API Security Testing Tools” article: API Security Testing Tools . Web applications are often the first touchpoint between a business and its users, which also makes them a top target for attackers. DAST allows organizations to test these applications in real time, simulating how an attacker might exploit weaknesses in input fields, forms, or session handling. It’s especially effective at finding runtime vulnerabilities such as cross-site scripting (XSS), SQL injection, and broken access controls – issues that static code reviews can easily miss.
By integrating DAST into the development lifecycle, teams can continuously monitor web apps for new risks introduced with each update. This proactive approach helps protect sensitive user data, maintain customer trust, and support compliance with standards like PCI DSS and GDPR. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Linux • https://www.stackhawk.com/blog/dynamic-analysis/ • https://devsecopsschool.com/blog/dynamic-analysis/ • https://blog.securelayer7.net/dast/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Dynamic Analysis Tool For Desktop Application Security.
[*] Metasploit Scan Running on Target Subnet for Dynamic Analysis Tool For Desktop Application Security... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |