Complete Technical Paper Content — Dynamic ARP Inspection Tool For Ethernet Switches
Overview & System Context
Dynamic Arp Inspection Tool For Ethernet Switches: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~6885 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background In computer networking, ARP spoofing (also ARP cache poisoning or ARP poison routing) is a technique by which an attacker sends (spoofed) Address Resolution Protocol (ARP) messages onto a local area network. Generally, the aim is to associate the attacker's MAC address with the IP address of another host, such as the default gateway, causing any traffic meant for that IP address to be sent to the attacker instead. ARP spoofing may allow an attacker to intercept data frames on a network, modify the traffic, or stop all traffic. Often, the attack is used as an opening for other attacks, such as denial of service, man in the middle, or session hijacking attacks. The attack can only be used on networks that use ARP, and requires the attacker to have direct access to the local network segment to be attacked.
The techniques that are used in ARP spoofing can also be used to implement redundancy of network services. For example, some software allows a backup server to issue a gratuitous ARP request in order to take over for a defective server and transparently offer redundancy. Circle and CUJO are two companies that have commercialized products centered around this strategy. ARP spoofing is often used by developers to debug IP traffic between two hosts when a switch is in use: if host A and host B are communicating through an Ethernet switch, their traffic would normally be invisible to a third monitoring host M.
The developer configures A to have M's MAC address for B, and B to have M's MAC address for A; and also configures M to forward packets. M can now monitor the traffic, exactly as in a man-in-the-middle attack. Dell Networking is the portfolio of computer networking products produced by Dell. This brand name originated in the first half of 2013 when Dell started to rebrand their former networking-related product brand known as Dell PowerConnect (including the Force10 portfolio).
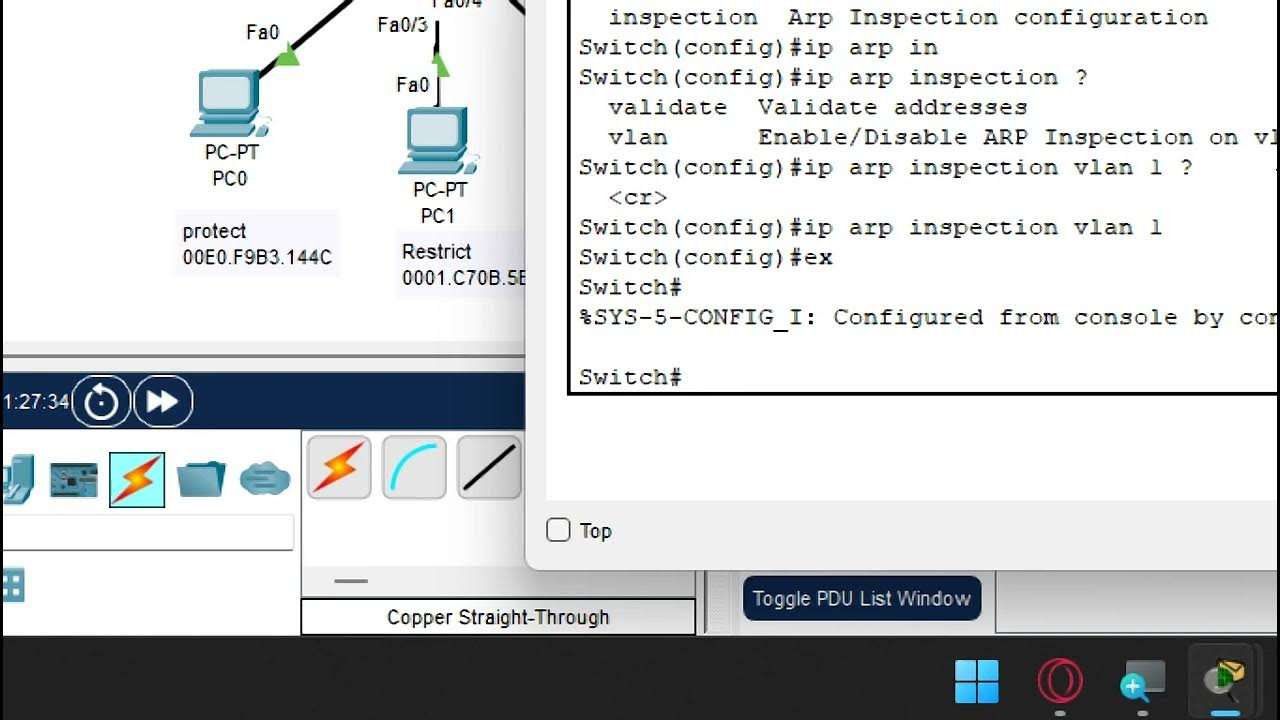
Z series: Datacenter distributed core switches: 3 models, the original Z9000, 2 RU high with 32 x 40 Gbit/s QSFP+ Ethernet ports and its follow up Z9500, 3RU high with up to 132 x 40 Gb QSFP+ slots. and the Z9100 including 100 Gb interfaces. C series: Chassis based campus access/core switches: 2 original models, C150 (9RU) and C300 (13RU) for 1 and 10 Gbit/s and the new C9010 system supporting external port-extenders, where specific N-series models can be (re)used as chassis managed port extender. E series: Virtualized core chassis-based switches. campus, office or data center aggregation/core switches: 3 models for 1 and 10 Gbit/s aggregation. S series: Fixed form-factor datacenter switches for 1, 10 and 40 Gbit/s Ethernet. X series: simple web-managed layer2 or l2+ campus switches based on Marvell networks chipset. W series: existing PowerConnect Wireless range which are OEM-versions of the Aruba Networks portfolio. M series: MXL and MIO modules running DNOS9.x and the existing PowerConnect M blade switches for the Dell M1000e chassis system including smaller versions of the MIOA/MXL switches for the FX2 mini chassis. N series: Campus access and aggregation switches with models for PoE+ offering 10 Gb or 40 Gb uplinks to the core. N-series switches run DNOS6.x on a Linux kernel. Legacy Powerconnect switches Figure 1: Tutorial Dynamic ARP Inspection pada Cisco Packet Tracer - YouTube Power connect 2800 series: web-managed(only) 10/100/1000 Ethernet switches Power connect 3500 series: managed 10/100 Mb layer 2 switches Power connect 5500 series: managed 10/100/1000 Mb layer 2 switches (with limited layer3 options) Power connect 6200 series: managed multi-layer gigabit Ethernet switches Power connect 7000 series: managed multi-layer gigabit Ethernet switches Power connect 8100 series: managed multi-layer ten gigabit Ethernet switches The PowerConnects 2800, 3500 and 5500 are based on Marvell Technology Group equipment while the PowerConnect 6200, 7000, 8100 and the blade-switches PCM6220, PCM6348 and PCM8024(-k) are powered by Broadcom.
The PCT7000 also offers a dual 10GbaseT copper 10 Gbit uplink module where the 6200 series only offers an SFP+ uplink module The PCT6200 stacking module can also be configured to run as a 10 Gbit Ethernet module with CX4 interfaces On the PCT7000 series, a stack can be combined with the PCM6348 blade switch in a Dell M1000e chassis The PCT7000 series offer an 'out of band' management interface which keeps management traffic out of the main switching/routing part of the switches. The PCT7048R and PCT7048RA is a switch with redundant power-supply (without need for external RPS module) and the RA offers reverse-air flow (back to ports direction, compared to ports to 'power supply side' in normal airflow). The PCT6200 series has only standard airflow; for a redundant power supply, a separate (1 RU) RPS module is required. The PCT7000 series offers a wider range of supported SFP+ optics, including some long-range multi-mode 10 Gb optics Up to 6 units in the 8100 series can be stacked to form one logical switch and any type of interface (10 Gb or 40 Gb, fiber-optical, or UTP copper) can be used for stacking. Similar to the rack-switches PCT7000 and PCT8024 series the switch offers an out-of-band Fast-Ethernet port for management as well as a serial console connection, required for initial configuration. The switch is built around the Broadcom Trident+ ASIC: the same ASIC as can be found in Cisco Nexus 5000 switches or Force10 models. The PowerConnect 8100 is initially released with firmware 5.0 of the switch-firmware which offers the same features as the PowerConnect 7000 and 8024 rack-switches and the different M-series Ethernet switches.
The underlying operating system of the PCT8100 is based on Linux 2.6 where all other 'Broadcom powered' PowerConnects run on VxWorks. Private VLAN, also known as port isolation, is a technique in computer networking where a VLAN contains switch ports that are restricted such that they can only communicate with a given uplink. The restricted ports are called private ports. Each private VLAN typically contains many private ports, and a single uplink. The uplink will typically be a port (or link aggregation group) connected to a router, firewall, server, provider network, or similar central resource. The concept was primarily introduced as a result of the limitation on the number of VLANs in network switches, a limit quickly exhausted in highly scaled scenarios. Hence, there was a requirement to create multiple network segregations with a minimum number of VLANs. The switch forwards all frames received from a private port to the uplink port, regardless of VLAN ID or destination MAC address.
Frames received from an uplink port are forwarded in the normal way (i.e. to the port hosting the destination MAC address, or to all ports of the VLAN for broadcast frames or for unknown destination MAC addresses). As a result, direct peer-to-peer traffic between peers through the switch is blocked, and any such communication must go through the uplink. While private VLANs provide isolation between peers at the data link layer, communication at higher layers may still be possible depending on further network configuration. A typical application for a private VLAN is a hotel or Ethernet to the home network where each room or apartment has a port for Internet access. Similar port isolation is used in Ethernet-based ADSL DSLAMs.
Allowing direct data link layer communication between customer nodes would expose the local network to various security attacks, such as ARP spoofing, as well as increase the potential for damage due to misconfiguration. Another application of private VLANs is to simplify IP address assignment. Ports can be isolated from each other at the data link layer (for security, performance, or other reasons), while belonging to the same IP subnet. In such a case, direct communication between the IP hosts on the protected ports is only possible through the uplink connection by using MAC-Forced Forwarding or a similar Proxy ARP based solution.
Figure 2: Cómo Configura Dynamic ARP Inspection (DAI) en Cisco Packet Tracer ... Dynamic-access port VLAN membership. Dynamic Trunking Protocol (DTP) Port Aggregation Protocol (PAgP) Link Aggregation Control Protocol (LACP) Multicast VLAN Registration (MVR) Voice VLAN Web Cache Communication Protocol (WCCP) Ethernet ring protection (ERP) Flexible VLAN tagging Egress VLAN firewall filters Integrated routing and bridging (IRB) interface Multichassis link aggregation groups (MC-LAGs) Q-in-Q tunneling Routing between sub-VLANs (Secondary) and Primary VLAN Juniper, does not support IGMP snooping Cisco Systems' Private VLANs have the advantage that they can function across multiple switches. A Private VLAN divides a VLAN (Primary) into sub-VLANs (Secondary) while keeping existing IP subnet and layer 3 configuration. A regular VLAN is a single broadcast domain, while private VLAN partitions one broadcast domain into multiple smaller broadcast subdomains.
Primary VLAN: Simply the original VLAN. This type of VLAN is used to forward frames downstream to all Secondary VLANs. Secondary VLAN: Secondary VLAN is configured with one of the following types: Isolated: Any switch ports associated with an Isolated VLAN can reach the primary VLAN, but not any other Secondary VLAN. In addition, hosts associated with the same Isolated VLAN cannot reach each other. There can be multiple Isolated VLANs in one Private VLAN domain (which may be useful if the VLANs need to use distinct paths for security reasons); the ports remain isolated from each other within each VLAN. Community: Any switch ports associated with a common community VLAN can communicate with each other and with the primary VLAN but not with any other secondary VLAN. There can be multiple distinct community VLANs within one Private VLAN domain. There are mainly two types of ports in a Private VLAN: Promiscuous port (P-Port) and Host port. Host port further divides in two types – Isolated port (I-Port) and Community port (C-port).
Promiscuous port (P-Port): The switch port connects to a router, firewall or other common gateway device. This port can communicate with anything else connected to the primary or any secondary VLAN. In other words, it is a type of a port that is allowed to send and receive frames from any other port on the VLAN. Host Ports: Isolated Port (I-Port): Connects to the regular host that resides on isolated VLAN. This port communicates only with P-Ports. Community Port (C-Port): Connects to the regular host that resides on community VLAN. This port communicates with P-Ports and ports on the same community VLAN. Example scenario: a switch with VLAN 100, converted into a Private VLAN with one P-Port, two I-Ports in Isolated VLAN 101 (Secondary) and two community VLANs 102 and 103 (Secondary), with 2 ports in each. The switch has one uplink port (trunk), connected to another switch. The diagram shows this configuration graphically. The following table shows the traffic which can flow between all these ports.
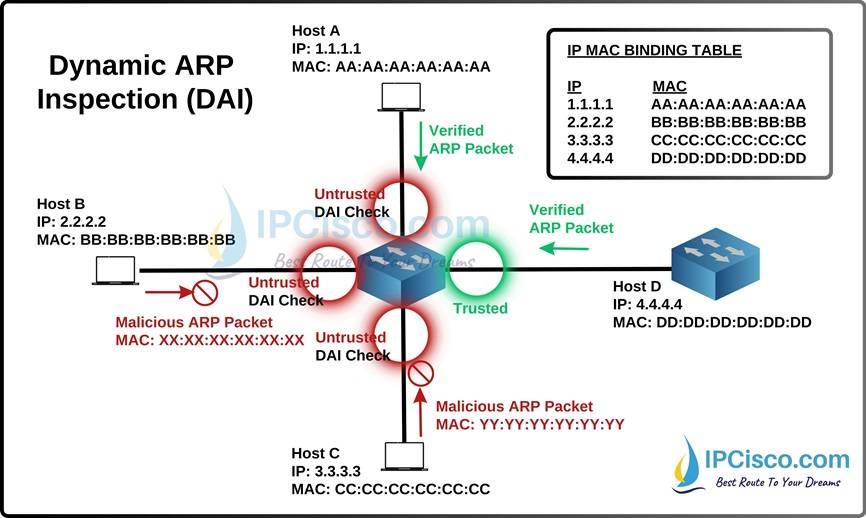
Figure 3: What Is Dynamic ARP Inspection (DAI)? Configuration + Examples Traffic from an Uplink port to an Isolated port will be denied if it is in the Isolated VLAN. Traffic from an Uplink port to an isolated port will be permitted if it is in the primary VLAN. Moving from a flat network to a segregated network without changing the IP addressing of the hosts. A firewall can replace a router, and then hosts can be slowly moved to their secondary VLAN assignment without changing their IP addresses. There is a need for a firewall with many tens, hundreds or even thousands interfaces. Using Private VLANs the firewall can have only one interface for all the segregated networks. There is a need to preserve IP addressing. With Private VLANs, all Secondary VLANs can share the same IP subnet. Overcome license fees for number of supported VLANs per firewall. There is a need for more than 4095 segregated networks. With Isolated VLAN, there can be endless number of segregated networks.
No need for separate IP subnet for each customer. Using Isolated VLAN, there is no limit on the number of customers. No need to change firewall's interface configuration to extend the number of configured VLANs. Dynamic ARP inspection (DAI) protects switching devices against Address Resolution Protocol (ARP) packet spoofing (also known as ARP poisoning or ARP cache poisoning).
DAI inspects ARPs on the LAN and uses the information in the DHCP snooping database on the switch to validate ARP packets and to protect against ARP spoofing. ARP requests and replies are compared against entries in the DHCP snooping database, and filtering decisions are made based on the results of those comparisons. When an attacker tries to use a forged ARP packet to spoof an address, the switch compares the address with entries in the database. If the media access control (MAC) address or IP address in the ARP packet does not match a valid entry in the DHCP snooping database, the packet is dropped ARP packets are sent to the Routing Engine and are rate-limited to protect the switching device from CPU overload.
Sending IP packets on a multi-access network requires mapping an IP address to an Ethernet MAC address. The switching device maintains this mapping in a cache that it consults when forwarding packets to network devices. If the ARP cache does not contain an entry for the destination device, the host (the DHCP client) broadcasts an ARP request for that device's address and stores the response in the cache.
ARP spoofing is one way to initiate man-in-the-middle attacks. The attacker sends an ARP packet that spoofs the MAC address of another device on the LAN. Instead of the switching device sending traffic to the proper network device, it sends the traffic to the device with the spoofed address that is impersonating the proper device. If the impersonating device is the attacker's machine, the attacker receives all the traffic from the switch that must have gone to another device. The result is that traffic from the switching device is misdirected and cannot reach its proper destination.
One type of ARP spoofing is gratuitous ARP, which is when a network device sends an ARP request to resolve its own IP address. In normal LAN operation, gratuitous ARP messages indicate that two devices have the same MAC address. They are also broadcast when a network interface card (NIC) in a device is changed and the device is rebooted, so that other devices on the LAN update their ARP caches. In malicious situations, an attacker can poison the ARP cache of a network device by sending an ARP response to the device that directs all packets destined for a certain IP address to go to a different MAC address instead.
To prevent MAC spoofing through gratuitous ARP and through other types of spoofing, the switches examine ARP responses through DAI. DAI examines ARP requests and responses on the LAN and validates ARP packets. The switch intercepts ARP packets from an access port and validates them against the DHCP snooping database. If no IP-MAC entry in the database corresponds to the information in the ARP packet, DAI drops the ARP packet and the local ARP cache is not updated with the information in that packet. DAI also drops ARP packets when the IP address in the packet is invalid. ARP probe packets are not subjected to dynamic ARP inspection. The switch always forwards such packets.
Junos OS for EX Series switches and the QFX Series uses DAI for ARP packets received on access ports because these ports are untrusted by default. Trunk ports are trusted by default, and therefore ARP packets bypass DAI on them. You configure DAI for each VLAN, not for each interface (port). By default, DAI is disabled for all VLANs. 2. System Architecture & Core Working Principles If you set an interface to be a DHCP trusted port, it is also trusted for ARP packets.
If your switching device is an EX Series switch and uses Junos OS with support for the Enhanced Layer 2 Software (ELS) configuration style, see Enabling a Trusted DHCP Server (ELS) for information about configuring an access interface to be a DHCP trusted port. For packets directed to the switching device to which a network device is connected, ARP queries are broadcast on the VLAN.
The ARP responses to those queries are subjected to the DAI check. For DAI, all ARP packets are trapped to the Packet Forwarding Engine. To prevent CPU overloading, ARP packets destined for the Routing Engine are rate-limited. If the DHCP server goes down and the lease time for an IP-MAC entry for a previously valid ARP packet runs out, that packet is blocked.
Prioritizing inspected packets is not supported on the QFX Series and the EX4600 switch. You can use class-of-service (CoS) forwarding classes and queues to prioritize DAI packets for a specified VLAN. This type of configuration places inspected packets for that VLAN in the egress queue, that you specify, ensuring that the security procedure does not interfere with the transmission of high-priority traffic.
This task uses Junos OS for EX Series switches with support for the Enhanced Layer 2 Software (ELS) configuration style. If your switch runs software that does not support ELS, see Enabling Dynamic ARP Inspection (non-ELS) . Dynamic ARP inspection (DAI) protects switches against ARP spoofing. DAI inspects ARP packets on the LAN and uses the information in the DHCP snooping database on the switch to validate ARP packets and to protect against ARP cache poisoning.
Before you can enable DAI on a VLAN, you must configure the VLAN. See Configuring VLANs for EX Series Switches with ELS Support (CLI Procedure) . This task uses Junos OS for EX Series switches that do not support the Enhanced Layer 2 Software (ELS) configuration style. If your switch runs software that does support ELS, see Enabling Dynamic ARP Inspection (ELS) . For ELS details, see Using the Enhanced Layer 2 Software CLI .
Dynamic ARP inspection (DAI) protects switches against ARP spoofing. DAI inspects ARP packets on the LAN and uses the information in the DHCP snooping database on the switch to validate ARP packets and to protect against ARP cache poisoning. You configure DAI for each VLAN, not for each interface (port). By default, DAI is disabled for all VLANs.
You might need to use class of service (CoS) to protect packets from critical applications from being dropped during periods of network congestion and delay and you might also need the port security features of DHCP snooping on the same ports through which those critical packets are entering and leaving. The sample output shows the number of ARP packets received and inspected per interface, with a listing of how many packets passed and how many failed the inspection on each interface. The switch compares the ARP requests and replies against the entries in the DHCP snooping database. If a MAC address or IP address in the ARP packet does not match a valid entry in the database, the packet is dropped.
This article explains how to configure Dynamic ARP Inspection (DAI) on MS switches. DAI protects your network against man-in-the-middle ARP spoofing attacks. DAI is a security feature in MS switches. It inspects Address Resolution Protocol (ARP) packets on the LAN. It uses the information in the DHCP snooping table to validate them.
It compares the packet's MAC and IP information against the MAC-IP bindings in the DHCP snooping table. Network devices need the IP and MAC address of the hosts they communicate with. ARP determines the MAC address associated with an IP address. Each device stores these IP-to-MAC bindings in its ARP cache. ARP spoofing is a form of man-in-the-middle attack. It lets an attacker intercept traffic intended for other hosts.
The attacker sends crafted ARP packets that poison the ARP cache on network devices. The attacker poisons the ARP caches of end hosts, switches, and firewalls on a LAN segment. This redirects traffic to the attacker's machine. Host C has now inserted itself into the traffic stream from Host A to Host B. This is a classic man-in-the-middle attack. DAI compares the IP-to-MAC binding information in ARP packets to the DHCP snooping table. If no IP-to-MAC entry in the table matches the ARP packet, DAI drops the packet. DAI does not update the local ARP cache with that information.
Configure only ports facing end hosts as untrusted ( Trusted: disabled ). Configure ports connecting network devices such as switches or wireless access points as trusted. This avoids connectivity issues. MS Classic switches implement DAI with the IP validation feature enabled. Classic switches check the IP in the ARP packet to confirm it is a valid address. Cloud-managed Catalyst switches perform basic DAI with no validation options enabled.
DAI is supported on the following models. The minimum required firmware is the oldest version that supports this functionality on the platform. It is not the same as the recommended firmware. Meraki recommends using the latest GA or RC firmware release for this feature. 3. Software Implementation, Frameworks & Protocols If the switch has no corresponding entry in its DHCP snooping table, and an ARP packet arrives on an untrusted port, DAI validation fails. The switch drops the ARP packet. Use DAI only for DHCP-enabled subnets.
Configure trusted ports before enabling DAI. Navigate to Switching > Monitor > Switch ports . By default, all ports are marked untrusted (disabled). DAI relies on DHCP snooping table information to perform validation. If a switch does not have a corresponding entry in its DHCP Snooping table, and an ARP packet arrives on an untrusted port, DAI validation will fail and the ARP packet will be dropped. It is therefore recommended to use DAI only for DHCP enabled subnets.
Confirm that DAI is working by reviewing DAI Blocked Events. When a client device attempts to spoof an IP address, traffic on the switch port fails validation. DAI then takes action. DAI blocks static IP addresses configured directly on devices. This is expected behavior. These events are tracked in the DHCP Tracker folder.
DAI may flag a client incorrectly. In this case, add the entry to the Allow list so the traffic is not dropped. Allowing an entry adds it to the DHCP snooping table as a valid snoop entry. This ties the MAC address of the client to the IP address in the table. DAI no longer flags the traffic as invalid or malicious. The selected entry now appears under the Allow listed snoop entries section. Traffic from this MAC address using this IP address is no longer blocked by DAI.
The Allow listed snoop entries section is expected to be empty during normal operation. IP-to-MAC bindings learned via the DHCP snooping table do not appear here. The section populates only after a client is manually moved or added. Layer 2 attacks hit fast because they live where most people assume the network is already “safe.” In a campus switch block, a rogue laptop can hand out bad IP settings, or a spoofed ARP reply can redirect traffic without touching a firewall. DHCP Security and ARP Inspection on Cisco switches close that gap by creating trust boundaries at the access layer and by validating who is allowed to claim an address.
Learn essential networking skills and gain hands-on experience in configuring, verifying, and troubleshooting real networks to advance your IT career. DHCP Snooping and Dynamic ARP Inspection are Cisco Layer 2 security features that stop rogue DHCP servers and ARP spoofing by tracking valid IP-to-MAC bindings and blocking suspicious traffic. Used together, they strengthen Network Defense on access switches, especially in campus, office, and dorm-style networks where CCNA -level switching skills matter most.
DHCP Snooping and Dynamic ARP Inspection are Cisco switch security features that verify DHCP lease activity and ARP traffic at Layer 2. Together, they prevent unauthorized hosts from poisoning address resolution or distributing incorrect network settings. This is not an academic feature pair. It is practical switch hardening for networks where users plug in whatever they want, and where the switch must decide what traffic is legitimate before it reaches the rest of the LAN. That is why these controls show up so often in Cisco® access-layer designs and in real CCNA troubleshooting labs.
For official Cisco documentation, the feature behavior and command syntax are covered in Cisco’s product and configuration references at Cisco . For the switching and address-resolution concepts behind these controls, Cisco’s learning materials and standards-backed references are the right place to verify details before rolling anything into production. A rogue DHCP server is a device that answers DHCP requests without authorization and gives clients the wrong gateway, DNS server, or IP scope. That sounds simple, but it can break an entire floor of users in seconds. One bad lease can send traffic to a malicious gateway, or make name resolution fail by pushing a poisoned DNS address.
ARP spoofing is a Layer 2 attack where an attacker sends forged ARP messages to make their MAC address look like the MAC address for a trusted IP. Once that mapping is accepted, the attacker can intercept traffic, redirect sessions, or create intermittent outages that are hard to diagnose. A poisoned ARP cache can enable man-in-the-middle access with nothing more than a laptop on the same VLAN.
Traditional switching does not validate control-plane trust by default. A switch forwards frames based on learned MAC addresses, but it does not automatically know whether a DHCP offer came from a legitimate server or whether an ARP reply matches a valid lease. That is why Network Defense at Layer 2 must be explicit instead of assumed. For workforce context, the U.S. Bureau of Labor Statistics notes continuing demand for network and security roles in its occupational outlook materials at BLS , which aligns with why Cisco® access security still matters in day-to-day operations.
DHCP Snooping is a Cisco switch security feature that filters DHCP messages and builds a binding database of trusted client information. It watches DHCP exchanges, decides which messages are allowed on untrusted ports, and records the lease details needed to identify a host later. The logic is simple, but the implementation must be precise. A switch should trust only the path that truly leads to the DHCP server or relay chain. In a campus network, that usually means the distribution uplink or a server segment interface, not a random access port or a trunk to an unmanaged device.
Think of DHCP Snooping as the source of truth for “who got which IP on which port.” If that binding table is wrong, every feature that depends on it becomes less reliable. On Cisco platforms, official behavior and configuration guidance are documented in Cisco’s support and configuration references at Cisco . For broader protocol context, DHCP behavior is standardized in IETF RFCs, including DHCPv4 and DHCPv6 references at RFC Editor .
Planning DHCP Snooping starts with deciding where the risk actually is. In most enterprises, that means user-facing VLANs, guest VLANs, and voice access networks. Core-only VLANs that never see endpoint DHCP activity may not need the same treatment, but access and distribution layers almost always do. Enable the feature on VLANs that carry client traffic and that could be abused by a rogue server. Guest WLAN VLANs, office floor VLANs, and student networks are usually top priorities. If a VLAN carries only infrastructure devices with static addressing, the design may be different, but you still need to think about whether that VLAN could ever receive rogue DHCP packets.
Trusted interfaces should line up with legitimate DHCP sources or relay paths. That may include uplinks to distribution switches, links to a server farm, or interfaces facing a DHCP relay device. On a trunk, trust does not mean “everything is safe”; it means the interface is part of the approved path for DHCP messages. 4. Practical Deployment, Analysis & Case Studies Voice VLANs and mixed-user trunks require extra attention. A phone and a PC may share one physical switchport while receiving addresses from different VLANs. If your trunk allowances, helper-address path, or trust model is wrong, phones can fail to register even while PCs appear normal.
DHCP starvation attacks try to exhaust the available scope by generating many fake requests. Rate limiting on untrusted ports reduces the chance that one endpoint can flood the segment. Cisco configuration planning should decide where rate limits are low enough to stop abuse but high enough not to interfere with legitimate client renewals. The NIST Cybersecurity Framework is useful here because it pushes organizations to identify assets, protect them, and validate changes systematically. That same discipline is what keeps switch security from becoming a messy, undocumented exception list.
Configuring DHCP Snooping on Cisco switches is usually a three-part job: enable it globally, enable it on the right VLANs, and then classify interfaces correctly. Get those three pieces right and the feature does its job quietly in the background. Access ports should remain untrusted unless there is a very specific reason to do otherwise. Uplinks to distribution switches, interfaces toward DHCP servers, and approved relay paths are the usual trusted candidates. EtherChannels and stacked switches need extra care because trust must be consistent across member links and across the stack domain.
Those commands help confirm that the feature is enabled, that bindings are being learned, and that the trust state matches your design. If clients are not getting leases, check whether the VLAN is enabled, whether the uplink is trusted, and whether trunk allowances include the correct VLANs. The CCNA certification path often reinforces these same switch behaviors through lab practice. Cisco’s official CCNA exam overview at Cisco CCNA is the best place to verify current exam objectives and expectations. For candidates comparing price or timing, always use Cisco’s current exam page because exam details can change.
For broader networking structure, DHCP Snooping fits naturally into topics such as layers of network , layer 2 vs layer 3 , layer 3 OSI , and address planning concepts like CIDR IP address and a CIDR chart . Those ideas matter because the switch is enforcing policy at Layer 2 while the design may span multiple subnets, helper addresses, and routed boundaries. Validation is where this feature either proves itself or exposes a design mistake. A clean deployment should show active snooping on the right VLANs, trusted uplinks, and a binding table that fills as clients renew leases. If that does not happen, the issue is usually in trust placement, VLAN scope, or relay path design.
Symptoms are usually obvious once you know what to look for. If a client gets no address at all, you may see 0.0.0.0 behavior during boot or repeated DHCP Discover attempts without a matching Offer. If only some VLANs fail, the problem is often a partial trust or trunk configuration issue rather than a global feature failure. Logging and debugging can help when packets are being dropped for valid reasons that are hard to see. Syslog, SNMP traps, and switch logs should be correlated with user reports and lease changes. In larger environments, centralized monitoring makes it easier to spot a pattern, such as one access closet dropping every DHCP packet after a topology change.
Operationally, this aligns with guidance from CIS Controls and the NIST identify/protect model , both of which emphasize baseline configuration and control validation. That is exactly what good DHCP Snooping troubleshooting is: confirm the baseline, then isolate the deviation. Dynamic ARP Inspection is a Cisco switch feature that validates ARP packets against trusted data sources before allowing them to influence the LAN. It is designed to block invalid ARP replies, suspicious gratuitous ARP activity, and spoofed mappings that do not match expected IP-to-MAC relationships.
DAI usually depends on the DHCP Snooping binding table. That matters because the switch needs a reliable source of truth for which MAC address belongs to which IP address on which VLAN and interface. If the data says a device on access port 18 is bound to 10.20.30.45, then an ARP reply that claims to be that same IP from a different port should be questioned or dropped.
Trusted versus untrusted behavior is the heart of DAI. On untrusted access ports, the switch inspects ARP traffic. On trusted uplinks or infrastructure-facing ports, it forwards ARP without the same inspection path. That reduces the chance of an attacker poisoning neighbors while keeping legitimate infrastructure traffic moving normally. This is especially valuable on VLANs with many dynamically addressed endpoints, such as office floors, student housing, conference areas, and shared lab spaces. The larger the user population, the greater the chance that one malicious host can affect many neighbors if Layer 2 controls are absent.
For standards-based guidance on address poisoning threats, the OWASP ARP Spoofing material is a useful reference point. For vendor-specific implementation details, Cisco’s official documentation remains the primary source. Configuring Dynamic ARP Inspection starts after DHCP Snooping is already working. That sequence matters. DAI needs the binding database, so enabling it first is a common mistake that leads to dropped traffic and confused operators.
Static-address devices are the main planning issue. Printers, building controllers, surveillance systems, and some servers may not obtain leases from DHCP, which means they will not automatically appear in the snooping table. In those cases, you can use ARP ACLs or static inspection entries where supported, or place those devices in a dedicated VLAN with a more controlled trust model.
Keep trust narrow. An uplink to a routed distribution device may need to be trusted. A user-facing access port should not be trusted just because it belongs to a switch. The operational rule is simple: trust infrastructure, inspect endpoints. When the feature is working, you should see legitimate ARP traffic pass and invalid claims dropped. In Cisco environments, verification commands typically include the DAI status and interface statistics, along with drop counters that show whether the switch is suppressing suspicious packets. That visibility is what makes DAI practical in real operations, not just in labs.
For the broader security model, NIST CSF emphasizes protection and detection controls that reduce trust in unauthenticated traffic. DAI is a very direct example of that philosophy at Layer 2. Static IP devices can fail DAI validation if they are not explicitly accounted for. That is because DAI often expects to confirm IP-to-MAC ownership from the DHCP Snooping binding database, and a static host may never create a lease record.
This is a common operational problem with printers, building automation devices, storage controllers, and management interfaces. If a switch is enforcing DAI too aggressively and no exception exists, those devices may look like spoofers even when they are legitimate. The result is unnecessary packet loss and a support ticket that feels like a security incident. The safest pattern is to reduce exceptions rather than grow them. If a VLAN is full of fixed-IP infrastructure, consider whether it belongs on the same segment as users at all. Good ARP Inspection design is about narrowing the blast radius of trust, not creating a long list of carve-outs.
ISC2 research and workforce materials regularly highlight how security operations depend on disciplined exception handling, and that principle is easy to see here. Security controls fail fastest when nobody owns the exception list. 5. Performance Evaluation & Extended Technical Observations Verification should be part of normal operations, not something you do only after an outage. Once DHCP Snooping and DAI are live, the switch should become a monitored source of truth for binding activity, interface trust state, and drop counters.
High drop counts are not always an attack, but they always deserve a look. A sudden ARP spike may indicate spoofing, or it may indicate a misconfigured static host, a trunk pruning issue, or an interface that was moved without updating the control list. The pattern matters more than the raw number. Operational best practice is to re-audit after every switch replacement, VLAN expansion, closet re-cabling, or topology redesign. If you treat DHCP Snooping and DAI as “set and forget,” they eventually drift out of alignment with reality. That is how security controls become outages.
For governance and operational discipline, many teams map this work to controls in the CIS Critical Security Controls and to asset/trust validation concepts in the NIST Cybersecurity Framework . Both support the same operational truth: if you do not verify it, you do not really control it. The biggest mistakes with DHCP Snooping and DAI are usually design mistakes, not syntax mistakes. The config may look fine, but the trust model is wrong or the feature order is wrong, and that is enough to break the network.
Another common issue is assuming relay support is automatic. If DHCP requests must cross a routed boundary, the helper path and trust placement need to match the actual traffic flow. Otherwise, the switch may block what looks like valid behavior from the client’s point of view. Do not roll out DHCP Snooping and DAI across every access VLAN at once unless you have already tested trunking, relay behavior, and static device exceptions in a lab or pilot site.
This is where CCNA -level switch troubleshooting pays off. The same habits used to verify tftp tcp port , telnet ip port , type 2 nat type , or even jumbo packet behavior in other labs apply here too: identify the path, verify the port state, then confirm the traffic is really flowing where you think it is. For broader incident-analysis context, references such as the Verizon Data Breach Investigations Report continue to show that internal misuse, credential theft, and misconfiguration play major roles in compromises. Layer 2 controls do not solve every problem, but they do remove a very common attack path.
Learn essential networking skills and gain hands-on experience in configuring, verifying, and troubleshooting real networks to advance your IT career. DHCP Snooping gives Cisco switches a trustworthy record of who received which address, on which VLAN, and from which interface. Dynamic ARP Inspection uses that record to stop fake ARP messages from rewriting the LAN’s trust model.
Together, they defend against rogue DHCP servers and ARP spoofing without requiring endpoint software on every device. That combination matters because Layer 2 attacks are effective precisely where users expect the network to be invisible. In access switches, campus networks, and shared environments, DHCP Security and ARP Inspection create the trust boundary that traditional switching does not provide on its own. If you are working through Cisco® CCNA v1.1 (200-301) topics, this is one of the clearest examples of practical network hardening you will use in the real world.
The right way to deploy it is straightforward: stage the change, trust only legitimate paths, document exceptions, and keep monitoring after go-live. That is how strong Network Defense stays strong after the lab is over. If you are building Cisco switching skills for operations or certification, use the official Cisco exam page and Cisco documentation for current details, then practice the configuration in a controlled lab before pushing it into production.
CompTIA®, Cisco®, Microsoft®, AWS®, EC-Council®, ISC2®, ISACA®, and PMI® are trademarks of their respective owners. DHCP Snooping is a security feature implemented on Cisco switches that helps prevent unauthorized or rogue DHCP servers from distributing IP address information within a network. By monitoring DHCP traffic, it creates a trusted database of legitimate DHCP servers and their assigned addresses.
This feature ensures that only trusted DHCP servers can assign IP addresses to clients, thereby reducing the risk of IP address conflicts, man-in-the-middle attacks, or network disruptions caused by rogue DHCP servers. It also enables the switch to enforce policies like DHCP rate limiting and logging suspicious activities, which enhances overall network security and stability.
Dynamic ARP Inspection (DAI) works in tandem with DHCP Snooping by validating ARP packets against the trusted DHCP snooping database. When a device sends an ARP reply, DAI checks whether the IP-to-MAC address mapping matches the entries learned via DHCP Snooping. If an ARP reply contains inconsistent or suspicious information, DAI blocks the packet, preventing ARP spoofing attacks that can redirect network traffic or intercept sensitive data. This combined approach effectively enforces trust boundaries at the access layer, safeguarding the network from common Layer 2 attacks like ARP poisoning.
To maximize security, start by enabling DHCP Snooping globally and specify trusted interfaces connected to legitimate DHCP servers. Configure the DHCP Snooping database to store binding information persistently across reboots. For DAI, enable it on all VLANs where ARP spoofing could occur, and ensure that DHCP Snooping is correctly configured to provide trusted bindings. It’s also important to fine-tune the rate limits for DHCP and ARP traffic to prevent denial-of-service attacks, and regularly monitor logs for suspicious activities.
A common misconception is that enabling DHCP Snooping alone is sufficient for network security. In reality, DAI should be configured simultaneously to effectively prevent ARP spoofing attacks. Another misunderstanding is that these features are only necessary in large enterprise networks. In fact, even small or campus networks can benefit from deploying DHCP Snooping and DAI to prevent common Layer 2 attacks, especially in environments with unmanaged or guest devices.
Start by verifying that DHCP Snooping and DAI are enabled on the correct VLANs and interfaces. Use commands like ‘show ip dhcp snooping’ and ‘show ip arp inspection’ to check the status and trusted bindings. If clients are not receiving IP addresses or ARP packets are being blocked unexpectedly, review the switch logs for error messages. Ensure that trusted interfaces are correctly configured and that no misconfigurations exist in the DHCP snooping database or ARP inspection policies. Adjust rate limits and trusted bindings as needed to resolve issues.
You reached this page when trying to access http://networklessons.com/switching/dai-dynamic-arp-inspection from 34.24.219.195 on October 19 2026, 09:25:56 UTC Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/ARP%20spoofing • https://en.wikipedia.org/wiki/Dell%20Networking • https://en.wikipedia.org/wiki/Private%20VLAN • https://www.juniper.net/documentation/us/en/software/junos/security-services/topics/topic-map/understanding-and-using-dai .html • https://documentation.meraki.com/Switching/MS_-_Switches/Operate_and_Maintain/How-Tos/How_to_Configure_Dynamic _ARP_Inspection • https://www.ituonline.com/blogs/implementing-dhcp-snooping-and-dynamic-arp-inspection-on-cisco-switches/ • https://networklessons.com/switching/dai-dynamic-arp-inspection • https://docs.fortinet.com/document/fortiswitch/7.2.10/administration-guide/500016/dynamic-arp-inspection
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Dynamic ARP Inspection Tool For Ethernet Switches.
[*] Metasploit Scan Running on Target Subnet for Dynamic ARP Inspection Tool For Ethernet Switches... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |