Complete Technical Paper Content — Elliptical Curve Cryptography Implementation For Key Exchange
Overview & System Context
Elliptical Curve Cryptography Implementation For Key Exchange: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9446 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background This is a potential security issue, you are being redirected to https://csrc.nist.gov .
Official websites use .gov A .gov website belongs to an official government organization in the United States. Secure .gov websites use HTTPS A lock ( ) or https:// means you’ve safely connected to the .gov website. Share sensitive information only on official, secure websites. Elliptic curve cryptography is critical to the adoption of strong cryptography as we migrate to higher security strengths. NIST has standardized elliptic curve cryptography for digital signature algorithms in FIPS 186 and for key establishment schemes in SP 800-56A .
Figure 1: Elliptic curve cryptography for digital signing and verification ... In FIPS 186-4 , NIST recommends fifteen elliptic curves of varying security levels for use in these elliptic curve cryptographic standards. However, more than fifteen years have passed since these curves were first developed, and the community now knows more about the security of elliptic curve cryptography and practical implementation issues. Advances within the cryptographic community have led to the development of new elliptic curves and algorithms whose designers claim to offer better performance and are easier to implement in a secure manner. Some of these curves are under consideration in voluntary, consensus-based Standards Developing Organizations.
In 2015, NIST hosted a Workshop on Elliptic Curve Cryptography Standards to discuss possible approaches to promote the adoption of secure, interoperable and efficient elliptic curve mechanisms. Workshop participants expressed significant interest in the development, standardization and adoption of new elliptic curves. In 2015, NIST solicited comments on possible improvements to FIPS 186-4. In particular, comments were requested on the possibility of adding new elliptic curves to the current recommended set, as well as on digital signature schemes. Throughout 2016, NIST began resolving the comments received and revising FIPS 186-4.
NIST published Federal Information Processing Standard (FIPS) 186-5, Digital Signature Standard (DSS) , along with NIST Special Publication (SP) 800-186, Recommendations for Discrete Logarithm-based Cryptography: Elliptic Curve Domain Parameters . Please see the CSRC News item for full details. A Federal Register Notice (FRN) was also issued announcing the issuance of FIPS 186-5, Digital Signature Standard.
Figure 2: Implementation of Elliptic Curve Cryptography (ECC) in ns-2. An implementation of Elliptic Curve Cryptography (ECC) from scratch in Python, covering the full mathematical foundation — from point arithmetic on curves over real numbers and finite fields, to real-world cryptographic protocols like ECDH key exchange , AES encryption , ECDSA signatures , and Bitcoin address generation .
Bitcoin demo (address generation, transaction signing, signature verification on secp256k1): A complete paper covering the theory and implementation details of this project is available in the repository: IntroductionToECC.pdf . It covers elliptic curve definitions, group theory, point addition, scalar multiplication, finite field curves, cyclic subgroups, ECDH, ECDSA, El Gamal on elliptic curves, and the Baby Step Giant Step attack.
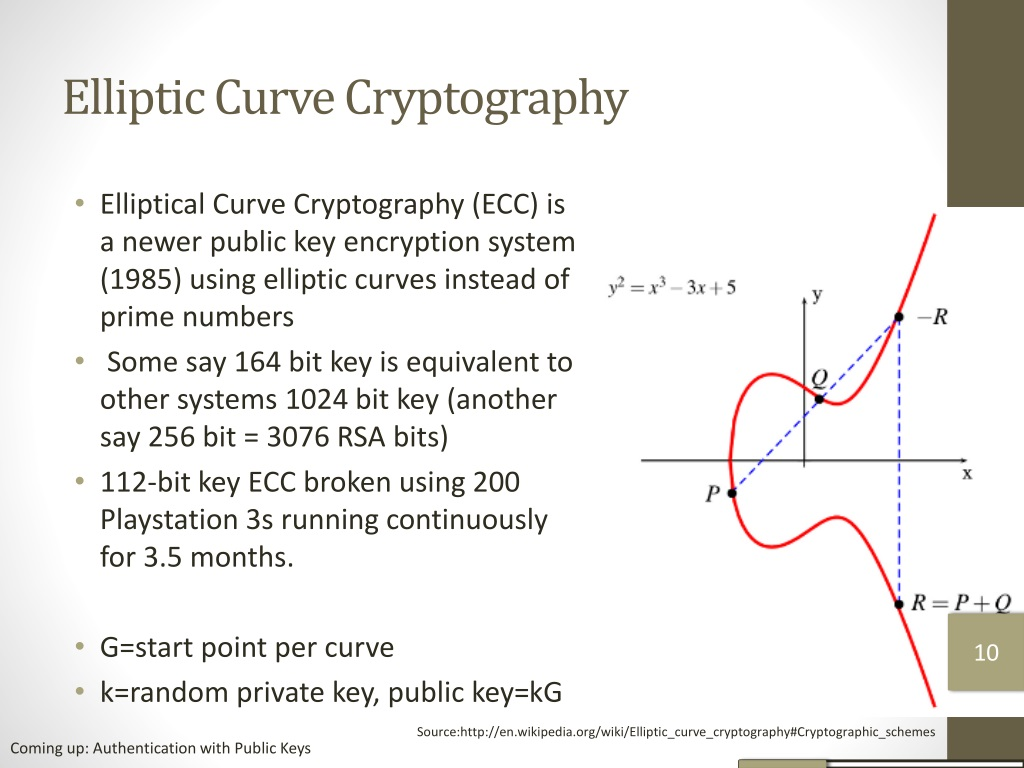
From-scratch implementation of elliptic curve arithmetic, ECDH key exchange, AES encryption, and a full Bitcoin simulation including address generation, ECDSA transaction signing, and verification on secp256k1. Figure 3: PPT - An Introduction to Public Key Encryption and Its Importance in ... The Elliptic Curve Cryptography (ECC) is modern family of public-key cryptosystems , which is based on the algebraic structures of the elliptic curves over finite fields and on the difficulty of the Elliptic Curve Discrete Logarithm Problem (ECDLP) .
ECC implements all major capabilities of the asymmetric cryptosystems: encryption , signatures and key exchange . The ECC cryptography is considered a natural modern successor of the RSA cryptosystem, because ECC uses smaller keys and signatures than RSA for the same level of security and provides very fast key generation , fast key agreement and fast signatures .
The private keys in the ECC are integers (in the range of the curve's field size, typically 256-bit integers). Example of 256-bit ECC private key (hex encoded, 32 bytes, 64 hex digits) is: 0x51897b64e85c3f714bba707e867914295a1377a7463a9dae8ea6a8b914246319 .
The key generation in the ECC cryptography is as simple as securely generating a random integer in certain range, so it is extremely fast. Any number within the range is valid ECC private key. The public keys in the ECC are EC points - pairs of integer coordinates { x , y }, laying on the curve. Due to their special properties, EC points can be compressed to just one coordinate + 1 bit (odd or even). Thus the compressed public key , corresponding to a 256-bit ECC private key, is a 257-bit integer. Example of ECC public key (corresponding to the above private key, encoded in the Ethereum format, as hex with prefix 02 or 03 ) is: 0x02f54ba86dc1ccb5bed0224d23f01ed87e4a443c47fc690d7797a13d41d2340e1a . In this format the public key actually takes 33 bytes (66 hex digits), which can be optimized to exactly 257 bits.
ECC crypto algorithms can use different underlying elliptic curves . Different curves provide different level of security (cryptographic strength), different performance (speed) and different key length , and also may involve different algorithms. ECC curves , adopted in the popular cryptographic libraries and security standards, have name (named curves, e.g. secp256k1 or Curve25519 ), field size (which defines the key length, e.g. 256-bit ), security strength (usually the field size / 2 or less), performance (operations/sec) and many other parameters.
ECC keys have length , which directly depends on the underlying curve. In most applications (like OpenSSL, OpenSSH and Bitcoin) the default key length for the ECC private keys is 256 bits , but depending on the curve many different ECC key sizes are possible: 192-bit (curve secp192r1 ), 233-bit (curve sect233k1 ), 224-bit (curve secp224k1 ), 256-bit (curves secp256k1 and Curve25519 ), 283-bit (curve sect283k1 ), 384-bit (curves p384 and secp384r1 ), 409-bit (curve sect409r1 ), 414-bit (curve Curve41417 ), 448-bit (curve Curve448-Goldilocks ), 511-bit (curve M-511 ), 521-bit (curve P-521 ), 571-bit (curve sect571k1 ) and many others.
Elliptic-curve cryptography (ECC) provides several groups of algorithms, based on the math of the elliptic curves over finite fields: ECC digital signature algorithms like ECDSA (for classical curves) and EdDSA (for twisted Edwards curves). ECC encryption algorithms and hybrid encryption schemes like the ECIES integrated encryption scheme and EEECC (EC-based ElGamal).
All these algorithms use a curve behind (like secp256k1 , curve25519 or p521 ) for the calculations and rely of the difficulty of the ECDLP (elliptic curve discrete logarithm problem). All these algorithms use public / private key pairs, where the private key is an integer and the public key is a point on the elliptic curve (EC point). Let's get into details about the elliptic curves over finite fields.
In mathematics elliptic curves are plane algebraic curves, consisting of all points { x , y }, described by the equation: Cryptography uses elliptic curves in a simplified form (Weierstras form), which is defined as: For example, the NIST curve secp256k1 (used in Bitcoin) is based on an elliptic curve in the form: To learn more about the equations of the elliptic curves and how they look like, play a bit with this online elliptic curve visualization tool : https://www.desmos.com/calculator/ialhd71we3 .
The elliptic curve cryptography (ECC) uses elliptic curves over the finite field Ip (where p is prime and p > 3) or I2 m (where the fields size p = 2_ m _). This means that the field is a square matrix of size p x p and the points on the curve are limited to integer coordinates within the field only. All algebraic operations within the field (like point addition and multiplication) result in another point within the field. The elliptic curve equation over the finite field Ip takes the following modular form: Unlike RSA , which uses for its key space the integers in the range [0... p -1] (the field Ip), the ECC uses the points { x , y } within the Galois field Ip (where x and y are integers in the range [0... p -1]).
Note that the elliptic curve over finite field y2 ≡ x3 + 7 (mod 17 ) consists of the blue points at the above figure, i.e. in practice the " elliptic curves " used in cryptography are " sets of points in square matrix ", not classical " curves ". The above curve is " educational ". It provides very small key length (4-5 bits). In the real world developers typically use curves of 256-bits or more.
It is pretty easy to calculate whether certain point belongs to certain elliptic curve over a finite field. For example, a point { x , y } belongs to the curve y2 ≡ x3 + 7 (mod 17 ) when and only when: The point P { 5 , 8 } belongs to the curve, because (5**3 + 7 - 8**2) % 17 == 0 . The point { 9 , 15 } does not belong to the curve, because (9**3 + 7 - 15**2) % 17 != 0 . These calculations are in Python style. The above mentioned elliptic curve and the points { 5 , 8 } and { 9 , 15 } are visualized below: Two points over an elliptic curve (EC points) can be added and the result is another point. This operation is known as EC point addition . If we add a point G to itself, the result is G + G = 2 * G . If we add G again to the result, we will obtain 3 * G and so on. This is how EC point multiplication is defined.
A point G over an elliptic curve over finite field (EC point) can be multiplied by an integer k and the result is another EC point P on the same curve and this operation is fast : The above operation involves some formulas and transformations, but for simplicity, we shall skip them. The important thing to know is that multiplying EC point by integer returns another EC point on the same curve and this operation is fast . Multiplying an EC point by 0 returns a special EC point called " infinity ".
The formulas for EC multiplication differ for the different forms of representation of the curve . In this example, we shall use an elliptic curve in the classical Weierstrass form . For example let's take the EC point G = { 15 , 13 } on the elliptic curve over finite field y2 ≡ x3 + 7 (mod 17 ) and multiply it by k = 6 . We shall obtain an EC point P = { 5 , 8 }: In elliptic curve over a finite field can form a finite cyclic algebraic group , which consists of all the points on the curve. In a cyclic group, if two EC points are added or an EC point is multiplied to an integer, the result is another EC point from the same cyclic group (and on the same curve). The order of the curve is the total number of all EC points on the curve. This total number of points includes also the special point called " point at infinity ", which is obtained when a point is multiplied by 0.
2. System Architecture & Core Working Principles Some curves form a single cyclic group (holding all their EC points), while others form several non-overlapping cyclic subgroups (each holding a subset of the curve's EC points). In the second scenario the points on the curve are split into h cyclic subgroups (partitions), each of order r (each subgroup holds equal number of points). The order of entire group is n = h * r (the number of subgroups, multiplied by the number of points in each subgroup). The number of subgroups h holding the EC points is called cofactor .
h is the curve cofactor (the number of non-overlapping subgroups of points, which together hold all curve points) r is the order of the subgroups (the number of points in each subgroup, including the infinity point for each subgroup) In other words, the points over an elliptic curve stay in one or several non-overlapping subsets, called cyclic subgroups . The number of subgroups is called " cofactor ". The total number of points in all subgroups is called " order " of the curve and is usually denoted by n . If the curve consists of only one cyclic subgroup , its cofactor h = 1 . If the curve consists of several subgroups, its cofactor > 1 .
For the elliptic curves over finite fields, the ECC cryptosystems define a special pre-defined (constant) EC point called generator point G ( base point ), which can generate any other point in its subgroup over the elliptic curve by multiplying G by some integer in the range [0... r ]. The number r is called " order " of the cyclic subgroup (the total number of all points in the subgroup).
For curves with cofactor = 1 there is only one subgroup and the order n of the curve (the total number of different points over the curve, including the infinity ) is equal to the number r . When G and n are carefully selected, and the cofactor = 1 , all possible EC points on the curve (including the special point infinity ) can be generated from the generator G by multiplying it by integer in the range [1... n ]. This integer n is known as " order of the curve ".
It is important to know that the order r of the subgroup , obtained from certain EC generator point G (which may be different from the order of the curve) defines the total number of all possible private keys for this curve: r = n / h (curve order, divided by the curve cofactor). Cryptographers select carefully the elliptic curve domain parameters (curve equation, generator point, cofactor, etc.) to ensure that the key space is large enough for certain cryptographic strength.
To summarize, in the ECC cryptography the EC points, together with the generator point G form cyclic groups (or cyclic subgroups ), which means that a number r exists ( r > 1), such that r * G = 0 * G = infinity and all points in the subgroup can be obtained by multiplying G by integer in the range [1... r ]. The number r is called order of the group (or subgroup ). Elliptic curve subgroups usually have many generator points , but cryptographers carefully select one of them, which generates the entire group (or subgroup) and is suitable for performance optimizations in the computations. This is the generator known as " G ".
It is known that for some curves different generator points generate subgroups of different order. More precisely, if the group order is n , for each prime d dividing n , there is a point Q such that d * Q = infinity . This means that some points used as generators for the same curve will generate smaller subgroups than others. if the group is small, the security is weak. This is known as "small-subgroup" attacks . This is the reason why cryptographers usually choose the subgroup order r to be a prime number .
For elliptic curves with cofactor h > 1, different base points can generate different subgroups of EC points on the curve. By choosing a certain generator point , we choose to operate over a certain subgroup of points on the curve and most EC point operations and ECC crypto algorithms will work well. Still in some cases, special attention should be given, so it is recommended to use only proven ECC implementations, algorithms and software packages.
At the above example (the EC over finite field y2 ≡ x3 + 7 mod 17 ), if we take the point G = { 15 , 13 } as generator , any other point from the curve can be obtained by multiplying G by some integer in the range [1...18]. Thus the order of this EC is n = 18 and its cofactor h = 1 . Note that the curve has 17 normal EC points (shown at the above figures) + one special " point at infinity ", all staying in a single subgroup, and the curve order is 18 (not 17).
Note also, that if we take the point {5, 9} as generator , it will generate just 3 EC points : {5, 8}, {5, 9} and infinity . Because the curve order is not prime number, different generators may generate subgroups of different order. This is a good example why we should not "invent" our own elliptic curves for cryptographic purposes and we should use proven curves. In the ECC , when we multiply a fixed EC point G (the generator point) by certain integer k ( k can be considered as private key ), we obtain an EC point P (its corresponding public key ).
It is very fast to calculate P = k * G , using the well-known ECC multiplication algorithms in time log_2( k _), e.g. the " double-and-add algorithm ". For 256-bit curves, it will take just a few hundreds simple EC operations. This asymmetry (fast multiplication and infeasible slow opposite operation) is the basis of the security strength behind the ECC cryptography, also known as the ECDLP problem .
The Elliptic Curve Discrete Logarithm Problem (ECDLP) in computer science is defined as follows: By given elliptic curve over finite field Ip and generator point G on the curve and point P on the curve, find the integer k (if it exists), such that P = k * G For carefully chosen (by cryptographers) finite fields and elliptic curves, the ECDLP problem has no efficient solution .
The multiplication of elliptic curve points in the group Ip is similar to exponentiation of integers in the group Ip (this is known as multiplicative notation ) and this is how the ECDLP problem is similar to the DLP problem (discrete logarithm problem). In the ECC cryptography, many algorithms rely on the computational difficulty of the ECDLP problem over carefully chosen field Ip and elliptic curve, for which no efficient algorithm exists .
Because the fastest known algorithm to solve the ECDLP for key of size k needs k \sqrt{k} k I steps, this means that to achieve a k -bit security strength , at least 2*k -bit curve is needed. Thus 256-bit elliptic curves (where the field size p is 256-bit number) typically provide nearly 128-bit security strength . In fact, the strength is slightly less , because the order of the curve ( n ) is typically less than the fields size ( p ) and because the curve may have cofactor h > 1 (and subgroup order r = n / h , smaller than n ) and because the number of steps is not exactly k \sqrt{k} k I , but is 0.886 ∗ k 0.886 * \sqrt{k} 0.886 ∗ k I . A precise security strength estimation for the most popular standard elliptic curves is given here: http://safecurves.cr.yp.to/rho.html .
For example, the secp256k1 ( p = 256) curve provides ~ 128-bit security (127.8 bits to be precise) and the Curve448 ( p = 448) provides ~ 224-bit security (222.8 bits to be precise). Now, after all the concepts, let's write some code . We shall use the Python library tinyec , which provides ECC primitives, such as cyclic groups (the SubGroup class), elliptic curves over finite fields (the Curve class) and EC points (the Point class).
First, install the package tinyec : We shall play with the educational curve from our previous examples y2 ≡ x3 + 7 (mod 17 ), with the generator point G = {15, 13}, which has order of n = 18 . We shall name it p1707 . Run the above code example: https://repl.it/@nakov/EC-points-in-Python . The above code demonstrates the EC multiplication . It multiplies the generator point G by 0, 1, 2, ..., 24. The output from the above program is as follows: It is visible that 0 * G = infinity . It is also clearly visible, that the EC group is cyclic and the order of the EC group is n = 18 , because starting from k = 18 , the next points repeat the first ones: The EC points, generated by multiplying the generator point G by 2, 3, 4, ..., 17 are shown on the figure below: Let's modify a bit the above example and change the generator point to be G' = { 5 , 9 }. This will change significantly the output: Run the above code example: https://repl.it/@nakov/EC-points-by-generator-point-in-Python . The output shows that the subgroup order of the new generator point is not 18, but is 3 . This is possible, because 18 is not prime . It is clear from the output, that 3 * G' = infinity and the obtained subgroup order is 3 : The above example again confirms that designing an elliptic curve for cryptography should be done by cryptographers, not by developers. Developers should rely on well established crypto-standards and proven crypto-libraries.
Now, let's write a real-world example . Instead of using our educational curve p1707 (4-5-bit curve, p = 17), we shall use the 192-bit cryptographic curve secp192r1 (192-bit, p = 6277101735386680763835789423207666416083908700390324961279). The below example is similar to the previous: Run the above code example: https://repl.it/@nakov/EC-points-in-real-world-in-Python . The output is also similar to the previous example: The curve secp192r1 uses a cyclic group of very large order n = 6277101735386680763835789423176059013767194773182842284081 (prime number) with cofactor h = 1, and as we can expect, n * G = infinity , just like at the previous example with our educational curve.
Now, let's generate a random private key privKey (integer in the range [0...n-1]) and its corresponding public key pubKey = privKey * G : Run the above code example: https://repl.it/@nakov/EC-points-private-public-keys-in-Python . The above code will produce output like this: Later we shall use such pairs of ECC keys {private key, public key} to encrypt data, sign messages and verify signatures.
Note that in real projects, 192-bit curves are considered weak , so 256-bit curves are recommended (or more bits), where the keys are also 256-bits (or respectively more). We use 192-bit curve in the above example just to make the sample output smaller. 3. Software Implementation, Frameworks & Protocols Elliptic curves over finite fields Ip (in the Weierstrass form) have at most 2 points per y coordinate (odd x and even x ). This property comes from the nature of the elliptic curve equation and is illustrated at the below graph: Due to this property, an elliptic curve point (and respectively an ECC public key) P { x , y } can be compressed as C { x , odd / even ). This means to erase the y coordinate from the point and represent it as 1 bit (odd y or even y ).
Compressed EC point is an EC point { x , y } represented in its shorter form { x , odd / even }. ECC public keys are EC points, so they can also be compressed in the same way. To decompress a point , we can calculate its two possible y coordinates by the formulas: Then we take the odd or even from the above coordinates (according to the additional parity bit in the compressed representation).
The modular square root (mod_sqrt) can be calculated using the Tonelli–Shanks algorithm . Let's take an example : at the elliptic curve y2 ≡ x3 + 7 (mod 17 ) the point P { 10 , 15 } can be compressed as C { 10 , odd }. For decompression , we first calculate the two possible y coordinates for x = 10 using the above formulas: y1 = 2 and y2 = 15. Then we choose the odd one: y = 15 . The decompressed point is { 10 , 15 }.
The code below implements public key compression and decompression in Python. It uses a library called nummaster for the " modular square root " function, which is unavailable in Python. First install the nummaster package: Finally, compress and decompress the point {10, 15} on the curve y2 ≡ x3 + 7 (mod 17 ), just as an example: Run the above code example: https://repl.it/@nakov/EC-point-compression-decompression-in-Python . The output of the above code is: ECC elliptic curves are described by a set of elliptic curve domain parameters , such as the curve equation parameters, the field parameters and the generator point coordinates. These parameters are specified in cryptography standards , such as: These standards define the parameters for a set of named curves , such as secp256k1 , P-521 and brainpoolP512t1 . The elliptic curves over finite fields, described in these crypto standards are well researched and analysed by cryptographers and are considered to have certain security strength , also described in these standards.
Some cryptographers (like Daniel Bernstein ) believe that most of the curves, described in the official crypto-standards are " unsafe " and define their own crypto-standards , which consider the ECC security in much broader level. The Bernstein's SafeCurves standard lists the curves, which are safe according to a set of ECC security requirements. The standard is available at https://safecurves.cr.yp.to .
To use ECC all communicating parties should agree on the EC domain parameters (all the elements defining the elliptic curve). It is highly recommended to use a named curve from the above standards with at least 256-bit modulus. Standard curves are well studied by cryptographers to guarantee their security strength. Don't use own elliptic curve (with non-standard domain parameters), unless you are experienced cryptographer and you know very well what are you doing! Many curves have weaknesses , which make the ECDLP problem not so difficult and compromise the security. If you are afraid of backdoored curves, use a standard safe curve from the SafeCurves list .
In ECC cryptography, elliptic curves over the finite fields are used, where the modulus p and the order n are very large integers ( n is usually prime number), e.g. 256-bit number. The finite field of the curve is of square form of size p x p , which is incredibly large, and all possible EC points on the curve (the order of the curve n ) is also a very big integer, e.g. 256-bit. For example, the domain parameters for the curve secp256k1 (the Bitcoin curve) are defined as follows: n (order; size; the count of all possible EC points) = 0xFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFFEBAAEDCE6AF48A03BBFD25E8CD0364141 a (the constant "a" in y^2 ≡ x^3 + a*x + b (mod p)) = 0x0000000000000000000000000000000000000000000000000000000000000000 b (the constant "b" in y^2 ≡ x^3 + a*x + b (mod p)) = 0x0000000000000000000000000000000000000000000000000000000000000007 g (the curve generator point G {x, y}) = ( 0x79BE667EF9DCBBAC55A06295CE870B07029BFCDB2DCE28D959F2815B16F81798 , 0x483ada7726a3c4655da4fbfc0e1108a8fd17b448a68554199c47d08ffb10d4b8 ) We already know that a 256-bit curve (which means that p and n are 256-bit numbers) provides 128-bit security strength , which means that to find the private key from the public key or signature, the best known non-quantum algorithm will take approximately 2128 operations. The above-defined ECC curve secp256k1 has 128-bit strength.
Now let's put in action the above domain parameters for the secp256k1 curve. Let's define the EC and calculate the public key for certain private key: Run the above code example: https://repl.it/@nakov/secp256k1-curve-in-Python . The above code defines the secp256k1 curve through its domain parameters and calculates a public key by given private key . This is done by multiplying the curve generator G by the private key. The result is correct, like it is visible from the program output: The public key is compressed and encoded in the standard format (encode the y coordinate as prefix 02 or 03 ).
Elliptic curves in the elliptic curve cryptography (ECC) may be presented in several forms (representations), which are proven to be birationally equivalent (isomorphic): Example Montgomery curve used in ECC is Curve25519 , which has the form y2 = x3 + _ 486662 _x2 + x Example Edwards curve used in ECC is Curve448 , which has the form x2 + y2 = 1 - _ 39081 _x2y2 For performance reasons elliptic curve cryptography (ECC) sometimes uses Edwards curves , which are elliptic curves in the following form: Every Edwards curve is birationally equivalent to an elliptic curve in Weierstrass form (y2 = x3 + _ a _x + b ) and thus has the same properties like the classical elliptic curves.
Edwards curves over a finite prime field Ip (where p is large prime number) provide fast integer to EC point multiplication, which has similar cryptographic properties like the classical elliptic curves, and the ECDLP problem has the same computational difficulty, suitable for cryptographic purposes. Examples of well-known cryptographic elliptic Edwards curves over finite prime fields are: Curve1174 (251-bit), Curve25519 (255-bit), Curve383187 (383-bit), Curve41417 (414-bit), Curve448 (448-bit), E-521 (521-bit) and others.
With carefully selected curve parameters, the Edwards curves over finite fields can implement ECC cryptosystems capable to provide ECDH key agreement schemes, digital signatures and hybrid encryption schemes, with very high performance . For example, the Curve25519 is the Edwards curve , defined by the following elliptic curve equation in Montgomery form : In fact, the above equation does not match directly the Edwards curve equation, but it is proven to be birationally equivalent to the following twisted Edwards curve (known as edwards25519 ): -x2 + y2 = 1 + _ 37095705934669439343138083508754565189542113879843219016388785533085940283555 _x2y2 The elliptic curve Curve25519 consists of all points { x , y } with integer coordinates, defined by the modular equation: The above equation has its equivalent in the classical Weierstrass form for the elliptic curves (y2 = x3 + _ a _x + b ), but the above form is designed especially for speed optimizations.
The Curve25519 is carefully engineered, by a team of cryptographers, led by Daniel Bernstein, at several levels of design and implementation to achieve very high speeds without compromising security. The Curve25519 has order (in its underlying cyclic group) n = 2252 + 0x14def9dea2f79cd65812631a5cf5d3ed and cofactor h = 8 and provides 125.8-bit security strength (it is sometimes referred as ~ 128-bit security). The private keys for the Curve25519 are 251 bits and are usually encoded as 256-bit integers (32 bytes, 64 hex digits). The public keys are typically encoded also as 256-bit integers (255-bit y-coordinate + 1-bit x-coordinate) and this is very convenient for developers.
Based on the Curve25519 an ECDH function is derived, called X25519 (used for elliptic-key Diffie–Hellman key agreement schemes) and fast digital signature scheme is derived, called Ed25519 , based on the the EdDSA algorithm. These schemes are very fast , because they involve multiplications and other simple operations with small integers (mostly 32-bit arithmetic), which can be efficiently implemented in the modern microprocessors (CPUs). Note that X25519 and Ed25519 use different encodings for the EC points , so they are not directly compatible and require conversion if you want to use the same public-private key pairs.
4. Practical Deployment, Analysis & Case Studies The Curve448 ( Curve448-Goldilocks ) is an untwisted Edwards curve , defined by the equation: over the finite prime field Ip , where p = 2448 - 2224 - 1.
It has order of n = 2446 - 0x8335dc163bb124b65129c96fde933d8d723a70aadc873d6d54a7bb0d and cofactor h = 4. Like any other Edwards curve, the Curve448 has equivalent in the Weierstrass form (y2 = x3 + _ a _x + b ), but the above Edwards form provides significant optimizations in the EC point calculations and improved performance.
The Curve448 provides ~ 224-bit security level (more precisely 222.8-bits ). The private keys for the Curve448 are 446 bits and are typically encoded as 448-bit integers (56 bytes, 112 hex digits). The public keys are also encoded as 448-bit integers . The Curve448 is suitable for ECDH key agreement (ECDH function, known as X448 ) and for fast digital signatures (EdDSA algorithm, known as Ed448 or edwards448 ). Note that X448 and Ed448 use different encodings for the EC points , so they are not directly compatible and require conversion if you want to use the same public-private key pairs.
Prefer Curve448 to Curve25519 when your application needs a higher level of security , but have in mind that Curve448 is about 3 times slower than Curve25519 and uses longer key length and signature length. Prefer Curve25519 to Curve448 when you need better performance and smaller keys and signatures. RFC 7748 - Elliptic Curves for Security - the Internet technical standard for implementing the X25519 and X448 key exchange protocols.
RFC 8032 - Edwards-Curve Digital Signature Algorithm (EdDSA) - the Internet technical standard for implementing the the Ed25519 and EdDSA-Ed448 signature schemes. In the general case, have in mind that Curve25519 is faster than secp256k1 and the other 256-bit standard NIST curves and is considered more secure, so it is the recommended choice for ~ 128-bit security. Similarly, the Curve448 has better performance than the classical curves with similar key length, so it is the recommended curve for ~ 224-bit security.
To demonstrate the elliptic curve Curve25519 in practice, we shall first install the pynacl crypto library for Python: The Python binding to the Networking and Cryptography (NaCl) library (PyNaCl) implements many modern cryptographic algorithms, including the EC point arithmetic over the Curve25519 and Ed25519 signatures. Next, generate a random 252-bit private key and its corresponding public key (EC point) on the Curve25519 (both keys will be encoded internally as 256-bit integers ): Run the above code example: https://repl.it/@nakov/Curve25519-in-Python . The sample output from the above code shows that both the public and the private (secret) keys on the Curve25519 are encoded as 256-bit integers (64 hex digits, 32 bytes) and this simplifies the developers: In fact, different crypto libraries may use different key encodings and typically X25519 ECDH keys are encoded differently than Ed25519 keys (Montgomery curve coordinates vs. twisted Edwards curve coordinates).
This program implements elliptic curve encryption and decryption using the Diffie-Hellman key exchange technique. The code performs operations such as point addition, scalar multiplication, and modular arithmetic over a finite field. It is designed for educational purposes to demonstrate basic elliptic curve cryptography (ECC). Elliptic Curve Cryptography (ECC): Worked on ECC for secure encryption and key exchange To recap the basic math, an elliptic curve over a finite field has points $(x, y)$ which satisfy the equation $$y^2 = x^3 + a x + b \text{ mod } q.$$When points are added to themselves multiple times we write the multiplication as $$Y = k P$$where $k$ is an integer. Since the number of points is finite, after a while we get to a value of $k = n$ such that $$\mathscr O = n P.
$$Where $\mathscr O$ is the point at infinity. We call $n$ the order of the point $P$. (See part 2 for more details.) The best curves for cryptographic use have the order of the curve $\#E$ (that is, the total number of points on the curve) equal to the order of every point, and that number is a prime. The relationship between the field prime of the elliptic curve equation and the order of the curve is given by Hasse's theorem:$$\#E = q +1 - t$$and the value of $t$ is in the range $$2\sqrt q \ge t \ge -2\sqrt q$$ We can find curves for which $\#E = n$ is a prime. For details on how to do that, look at chapter 6 in Elliptic Curve Cryptography for Developers.
As shown in part 3, we can find a good cryptographic curve for which the ECDLP is too hard to solve. We can use that curve to create a secret key for message encryption. To do that we set up values which are private to each person and public for each person. The private values are never shown, and given the way elliptic curves work, they don't need to be stored either. The public values are either exchanged between parties, or published in some fashion. It's better to get a key from someone every time and compare it with previous times to help build trust that you are talking to the same person - but that is cyber security, not cryptographic security.
The best way to create a private key is to enter a phrase into a hash function and spit out a bunch of garbage bits. As long as the entered phrase is the same each time, the private key does not change. Remembering a phrase can be a problem - but again, that's not cryptographic security. Making cryptographic security user friendly is hard, but the more all the details can be hidden from users the more they will use real security without thinking about it.
Let's assume we have a good cryptographic elliptic curve over a field $F_q$ with a prime number of points $n$. We pick a random point on the curve $G = (G_x, G_y)$ and publish the curve parameters $a$, $b$ and the point $G$. What this means is that the arithmetic for the curve is done modulo $q$, the values of $a$ and $b$ are modulo $q$, and the mathematics of the curve are modulo $n$. Every person who wants to use this curve selects a private key $r$ which is modulo $n$.
Let's suppose Albert and Barbara want to communicate using AES to encrypt and decrypt private messages. They need to create a secret key using public channels that anyone can eavesdrop on. The simplest way to create a secret is to use the elliptic curve version of the Diffie-Hellman protocol. Albert creates a private key $r_a$ using some method, and Barbara creates a private key $r_b$. They each then use point $G$ to create public keys with$$P_a = r_a G$$$$P_b = r_b G.$$Albert sends $P_a$ to Barbara and Barbara sends $P_b$ to Albert.
Using his private key, Albert computes $$S = r_a P_b$$and using her private key Barbara computes$$S = r_b P_a.$$ The value $S_x$ is then the shared secret key they can both use to encrypt messages using AES. In part 3 I explained the elliptic curve discrete log problem (ECDLP). For good curves finding the values of $r_a$ or $r_b$ is not possible (yet - see using quantum computers to break ECC ) so the public transmission of the points $P_a$ and $P_b$ hide the private key values.
The reason both Albert and Barbara get the same value $S_x$ is because $$S = r_a P_b = r_a r_b G$$and$$S = r_b P_a = r_b r_a G$$are the same points. Only the $x$ portion of the result is used for the AES key because $y$ is a simple function of $x$, and finding $x$ is the crux of the security. Another fundamental algorithm that relies on the intractability of solving the ECDLP is digital signature. The idea is to lock a specific document to a specific person. If the document changes or someone tries to spoof a signature, the verification process will fail.
The signing process uses a random number. For real security, this should be created using a hardware source. A different random number should be created for every signature, even if it is the same person and the same document on a different date. Let's call the random number $k$. We use the same curve and base point $G$ as in the key exchange to create the point$$Q = k G.$$The point $Q$ becomes a public key for the digital signature. The value of $k$ should be taken modulo $n$, and $Q$ should not be $\mathscr O$ - but the odds of a random value being $n$ is astronomically small.
Let's call the document to be signed $M$. The details of making sure everyone has the same $M$ on different platforms requires care. Some documents will have carriage return, line feed at the end of a line, some will have just carriage return, and others will have just line feed . It is absolutely essential that the signing operation and the verification operation use the exact same set of bits for $M$ or verification won't work.
A hash function is used to combine the point $Q$ with the document $M$. With the description $||$ meaning "concatenate" the value$$e = \text{ hash}(Q_x || Q_y || M)$$is computed. Let's now take Albert as the person signing the document. The digital signature Albert computes is$$s = k - e r_a \text{ mod }n.$$ The published value for the signature is $(s, Q)$. The value $e$ can be computed by anyone, and in fact that is required as part of the verification process. But nobody knows $r_a$ nor $k$, so using $s$ to find either one of those is more difficult than finding $k$ directly from $Q$. For even more security, the value of $k$ should be destroyed once $s$ is computed so no matter what happens, the signature can not be changed.
To verify that Albert signed the document $M$, you gather the document and the three values of the signature (the point $Q$ is two values $(Q_x, Q_y)$) along with Albert's public key $P_a$. You then compute$$e' = \text{ hash}(Q_x || Q_y || M)$$and check to see if$$Q' = s G + e' P_a \stackrel{?}{=} Q.$$If $Q' = Q$ the signature is verified, otherwise it fails. The whole idea of a hash function is that if one bit changes on the input, half the bits change on the output. So the value of $M$ must be the exact same set of bits for $e$ and $e'$. Let's see how this works by expanding $s$:$$Q' = s G + e' P_a $$ $$= (k - e r_a) G + e' P_a$$ $$ = k G - e r_a G + e' P_a $$ $$= Q + (e' - e)P_a.$$ As long as the value computed for $e'$ is exactly the same value computed in the original signature $e$, the last term is eliminated and result is a match. The value of $k$ is not known to anyone once the signature is finished, and is never required to be known again. Only the public key $Q$ is required to compute the hash of the document.
There are other algorithms which are more sophisticated than these to prevent specific types of attacks from threatening security. They are similar in construction, so the basic ideas here should give you a good grounding in how the compute engine is working in the background when you use things like SSH or TLS with elliptic curve cryptography. To post reply to a comment, click on the 'reply' button attached to each comment. To post a new comment (not a reply to a comment) check out the 'Write a Comment' tab at the top of the comments.
Otherwise, please use this form to register (free) an join one of the largest online community for Electrical/Embedded/DSP/FPGA/ML engineers: I love math and physics, learned DSP and embedded systems to do math and physics, and found FPGA's a hell of a lot of fun.
I graduated in 1982 with a PhD in nuclear engineering and have been programming in assembler and C ever since. The Diffie-Hellman key exchange algorithm is a method to securely establish a shared secret between two parties (Alice and Bob). Elliptic-curve Diffie–Hellman (ECDH) allows the two parties, each having an elliptic-curve public–private key pair, to establish the shared secret. This shared secret may be directly used as a key, or to derive another key. The key, or the derived key, can then be used to encrypt subsequent communications using a symmetric-key cipher. It is a variant of the Diffie–Hellman protocol using elliptic-curve cryptography.
The Diffie-Hellman key exchange is a way for people to secretly share information. When two people want to use cryptography, they often only have an insecure channel to exchange information. Martin Hellman, Whitfield Diffie and Ralph Merkle developed a protocol that allows this information exchange over an insecure channel. The resulting protocol has become known as Diffie-Hellman key exchange. Sometimes it is called Diffie-Hellman key agreement, Diffie-Hellman key establishment, Diffie-Hellman key negotiation or Exponential key exchange. Using this protocol, both parties agree on a secret key. They use this key to encrypt their communication using a symmetric-key cipher.
The scheme was first published by Whitfield Diffie and Martin Hellman in 1976. Diffie-Hellman key agreement itself is an anonymous (non-authenticated) key-agreement protocol, it provides the basis for a variety of authenticated protocols, and is used to provide perfect forward secrecy in Transport Layer Security’s short-lived modes. 5. Performance Evaluation & Extended Technical Observations We can find elliptic curves cryptosystems in TLS , PGP and SSH , which are just three of the main technologies on which the modern web and IT world are based. Not to mention Bitcoin and other cryptocurrencies .
Elliptic-curve cryptography (ECC) is an approach to public-key cryptography based on the algebraic structure of elliptic curves over finite fields. ECC requires smaller keys compared to non-EC cryptography (based on plain Galois fields) to provide equivalent security. In mathematics, an elliptic curve is a plane algebraic curve defined by an equation of the form: y² = x³ + ax + b .
The primary advantage of using Elliptic Curve based cryptography is reduced key size and hence speed. Elliptic curve based algorithms use significantly smaller key sizes than their non elliptic curve equivalents. The difference in equivalent key sizes increases dramatically as the key sizes increase. The approximate equivalence in security strength for symmetric algorithms compared to standard asymmetric algorithms and elliptic curve algorithms is shown in the table below.
As can be seen, to get equivalent strength to a 256 bit symmetric key, a standard asymmetric algorithm would have to use an enormous key of 15360 bits. Keys of this size are typically not practical due to the amount of processing power that would be required, and therefore the speed of the operations. However, with elliptic curve algorithms, the equivalent key length is 512 bits, which is entirely practical.
If you want to know more about the curves you can go here: SafeCurves: choosing safe curves for elliptic-curve cryptography . Provides a Cryptography Next Generation (CNG) implementation of the Elliptic Curve Diffie-Hellman (ECDH) algorithm. This class is used to perform cryptographic operations. A basic example could be as follows: After running this code, aliceKey and bobKey are both 32 bytes long and match each other. Now, Alice could use this as a symmetric key: Easy! right? right! the problem here is that ECDiffieHellmanCng is not available (yet) on mono either on linux or macos , look here https://github.com/mono/mono/issues/9037 and here: https://github.com/mono/mono/issues/9463 .
Originally, in the late 1990s, the Legion of the Bouncy Castle was simply a number of individuals united both in their interests of Cryptography and Open Source. The first official release of the Bouncy Castle APIs appeared in May 2000 and was about 27,000 lines long. The project grew steadily with a C# version of the Java APIs being added in 2006. By 2012 with the Java code base well past 300,000 lines and the C# one over 140,000 it started becoming obvious that a bit more organisation was required to maintain both progress and the quality of the APIs.
On 18 October 2013, a not-for-profit association, the Legion of the Bouncy Castle Inc. was established in the state of Victoria, Australia, by the core developers and others to take ownership of the project and support the ongoing development of the APIs. The association was recognised as an Australian charity with a purpose of advancement in education and a purpose that is beneficial to the community by the Australian Charities and Not-For-Profits Commission on 7 November 2013. The association was authorised to fundraise to support its purposes on 29 November 2013 by Consumer Affairs Victoria.
While I was trying to reduce the minimum .NET required version for SILENTTRINITY I realized that it could be possible to run the stager by replacing the ECDiffieHellmanCng implementation for a portable one. I most admit this was really hard, but I finally did it after a lot of reading and thanks to the BouncyCastle c# libraries. P-521 reffers to secp521r1 , it’s the default curve for the ECDiffieHellmanCng class. With those values we can create the domain parameters.
We’ll need the aliceKeyPair to share the public key to Bob and then be able to derive the Bob’s public key: Now, we’re going deep into the funny part… The whole idea of this is to find a secure shared key, so Bob needs to send me his public keys. Bob can acheive this by several ways. I would prefer to wait a binary stream from Bob, but it seems this is not a common practice. The common practice is to send a xml file with X and Y coordinates and receive the same.
First, in GetBobCoords we’re building a xml to send our coordinates ( GetXmlString )… so Bob responds with his public key’s coordinates and we’re returning the coordinates; from these coordinates, we’re creating a Point : CreatePoint will throws an exception if the point isn’t inside the curve which it is good, because we’re going to know if we’re doing something wrong. Now, we have both public keys and Alice ’s private key. We need to generate a shared key to encrypt/decrypt the communication; for this, we’re going to derive the Bob s key using a SHA256 function based on Alice ’s private key.
In cryptography, a key-agreement protocol is a protocol whereby two or more parties can agree on a key in such a way that both influence the outcome. If properly done, this precludes undesired third parties from forcing a key choice on the agreeing parties. Protocols that are useful in practice also do not reveal to any eavesdropping party what key has been agreed upon. Many key exchange systems have one party generate the key, and simply send that key to the other party – the other party has no influence on the key. Using a key-agreement protocol avoids some of the key distribution problems associated with such systems. Protocols where both parties influence the final derived key are the only way to implement perfect forward secrecy.
We’re using ECDH and initializing the agreement using Alice ’s private key. After getting the shared key’s bytes we’re getting a symmetric key: Well, this is awesome! This implementation should run on Linux, MacOS and Xamarin (Android and iOS). Also we can obfuscate the code using ConfuserEx from Linux. Using HTTPS between Alice and Bob should be the standard. I’m going to keep learning more about this topic. I’m glad to hear a better way to do this.
In this section we shall explain how to implement elliptic-curve based public-key encryption / decryption (asymmetric encryption scheme based on ECC). This is non-trivial and usually involves a design of hybrid encryption scheme, involving ECC cryptography, ECDH key exchange and symmetric encryption algorithm. Assume we have a ECC private-public key pair . We want to encrypt and decrypt data using these keys. By definition, asymmetric encryption works as follows: if we encrypt data by a public key , we will be able to decrypt the ciphertext later by the corresponding private key : The above process can be directly applied for the RSA cryptosystem, but not for the ECC . The elliptic curve cryptography (ECC) does not directly provide encryption method. Instead, we can design a hybrid encryption scheme by using the ECDH (Elliptic Curve Diffie–Hellman) key exchange scheme to derive a shared secret key for symmetric data encryption and decryption.
Let's get into details how to design and implement an ECC-based hybrid encryption scheme . Assume we have a cryptographic elliptic curve over finite field, along with its generator point G . We can use the following two functions to calculate a shared a secret key for encryption and decryption (derived from the ECDH scheme): Return both the sharedECCKey + ciphertextPubKey . Use the sharedECCKey for symmetric encryption. Use the randomly generated ciphertextPubKey to calculate the decryption key later.
The above calculations use the same math, like the ECDH algorithm (see the previous section ). Recall that EC points have the following property: Now, assume that a = privKey, a * G = pubKey, b = ciphertextPrivKey, b * G = ciphertextPubKey. This is what exactly the above two functions calculate, directly following the ECDH key agreement scheme. In the hybrid encryption schemes the encapsulated ciphertextPubKey is also known as " ephemeral key ", because it is used temporary, to derive the symmetric encryption key, using the ECDH key agreement scheme.
The below Python code uses the tinyec library to generate a ECC private-public key pair for the message recipient (based on the brainpoolP256r1 curve) and then derive a secret shared key (for encryption) and ephemeral ciphertext public key (for ECDH) from the recipient's public key and later derive the same secret shared key (for decryption) from the recipient's private key and the generated earlier ephemeral ciphertext public key : Run the above code example: https://repl.it/@nakov/ECC-based-secret-key-derivation-in-Python .
The code is pretty simple and demonstrates that we can generate a pair { secret key + ciphertext public key } from given EC public key and later we can recover the same secret key from the pair { ciphertext public key + private key }. The above code produces output like this: It is clear from the above output that the encryption key (derived from the public key) and the decryption key (derived from the corresponding private key) are the same . This is due to the above discussed property of the ECC: pubKey * ciphertextPrivKey = ciphertextPubKey * privKey . These keys will be used for data encryption and decryption in an integrated encryption scheme. The above output will be different if you run the code (due to the randomness used to generate ciphertextPrivKey , but the encryption and decryption keys will always be the same (the ECDH shared secret).
The above demonstrated mechanism for generating a shared ephemeral secret key, based on a ECC key pair, is an example of KEM (key encapsulation mechanism), based on the ECC and ECDH. Once we have the secret key , we can use it for symmetric data encryption , using a symmetric encryption scheme like AES-GCM or ChaCha20-Poly1305. Let's implement a fully-functional asymmetric ECC encryption and decryption hybrid scheme. It will be based on the brainpoolP256r1 curve and the AES-256-GCM authenticated symmetric cipher.
We shall use the tinyec and pycryptodome Python libraries respectively for ECC calculations and for the AES cipher: Run the above code example: https://repl.it/@nakov/ECC-based-hybrid-encryption-decryption-in-Python . The above example starts from generating an ECC public + private key pair for the message recipient: pubKey + privKey , using the tinyec library. These keys will be used to encrypt the message msg through the hybrid encryption scheme (asymmetric ECC + symmetric AES) and to decrypt is later back to its original form.
Next, we encrypt msg by using the pubKey and we obtain as a result the following set of output: { ciphertext , nonce , authTag , ciphertextPubKey }. The ciphertext is obtained by the symmetric AES-GCM encryption, along with the nonce (random AES initialization vector) and authTag (the MAC code of the encrypted text, obtained by the GCM block mode). Additionally, we obtain a randomly generated ephemeral public key ciphertextPubKey , which will be encapsulated in the encrypted message and will be used to recover the AES symmetric key during the decryption (using the ECDH key agreement scheme, as it was show before).
To decrypt the encrypted message, we use the data produced during the encryption { ciphertext , nonce , authTag , ciphertextPubKey }, along with the decryption privateKey . The result is the decrypted plaintext message. We use authenticated encryption (GCM block mode), so if the decryption key or some other parameter is incorrect, the decryption will fail with an exception .
Internally, the encrypt_ECC(msg, pubKey) function first generates an ephemeral ECC key-pair for the ciphertext and calculates the symmetric encryption shared ECC key sharedECCKey = ciphertextPrivKey * pubKey . This key is an EC point, so it is then transformed to 256-bit AES secret key (integer) though hashing the point's x and y coordinates. Finally, the AES-256-GCM cipher (from pycryptodome ) encrypts the message by the 256-bit shared secret key secretKey and produces as output ciphertext + nonce + authTag .
The decrypt_ECC(encryptedMsg{ciphertext, nonce, authTag, ciphertextPubKey}, privKey) function internally first calculates the symmetric encryption shared ECC key sharedECCKey = privKey * ciphertextPubKey . It is an EC point, so it should be first transformed to 256-bit AES secret key though hashing the point's x and y coordinates. Then the AES-256-GCM cipher is used to decrypt the ciphertext + nonce + authTag by the 256-bit shared secret key secretKey . The produced output is the original plaintext message (or an exception in case of incorrect decryption key or unmatching authTag ).
Harvested Online Documentation & Reference Sources • https://csrc.nist.gov/Projects/Elliptic-Curve-Cryptography • https://github.com/Arkww/Elliptic-Curve-Cryptography • https://cryptobook.nakov.com/asymmetric-key-ciphers/elliptic-curve-cryptography-ecc • https://github.com/Marina-Abdallah/ECC-Algorithm-Code • https://www.embeddedrelated.com/showarticle/1595.php • https://davidtavarez.github.io/2019/implementing-elliptic-curve-diffie-hellman-c-sharp/ • https://cryptobook.nakov.com/asymmetric-key-ciphers/ecc-encryption-decryption
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Elliptical Curve Cryptography Implementation For Key Exchange.
[*] Metasploit Scan Running on Target Subnet for Elliptical Curve Cryptography Implementation For Key Exchange... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |