Complete Technical Paper Content — Email Spoofing Detection Tool Using Spf Dkim Dmarc
Overview & System Context
Email Spoofing Detection Tool Using Spf Dkim Dmarc: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9543 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Email spoofing is the creation of email messages with a forged sender address. The term applies to email purporting to be from an address which is not actually the sender's; mail sent in reply to that address may bounce or be delivered to an unrelated party whose identity has been faked. Disposable email address or "masked" email is a different topic, providing a masked email address that is not the user's normal address, which is not disclosed (for example, so that it cannot be harvested), but forwards mail sent to it to the user's real address. The original transmission protocols used for email do not have built-in authentication methods: this deficiency allows spam and phishing emails to use spoofing in order to mislead the recipient. More recent countermeasures have made such spoofing from internet sources more difficult but they have not eliminated it completely; few internal networks have defences against a spoof email from a colleague's compromised computer on that network. Individuals and businesses deceived by spoof emails may suffer significant financial losses; in particular, spoofed emails are often used to infect computers with ransomware.
MAIL FROM: generally presented to the recipient as the Return-path: header but not normally visible to the end user, and by default no checks are done that the sending system is authorized to send on behalf of that address. RCPT TO: specifies which email address the email is delivered to, is not normally visible to the end user but may be present in the headers as part of the "Received:" header. Together, these are sometimes referred to as the "envelope" addressing – an analogy to a traditional paper envelope. Unless the receiving mail server signals that it has problems with either of these items, the sending system sends the "DATA" command, and typically sends several header items, including: From: Joe Q Doe
Alice is sent an infected email which she opens, running the worm code. The worm code searches Alice's email address book and finds the addresses of Bob and Charlie. From Alice's computer, the worm sends an infected email to Bob, but is forged to appear as if it was sent by Charlie. In this case, even if Bob's system detects the incoming mail as containing malware, he sees the source as being Charlie, even though it really came from Alice's computer. Meanwhile, Alice may remain unaware that her computer has been infected, and Charlie does not know anything about it at all, unless he receives an error message from Bob.
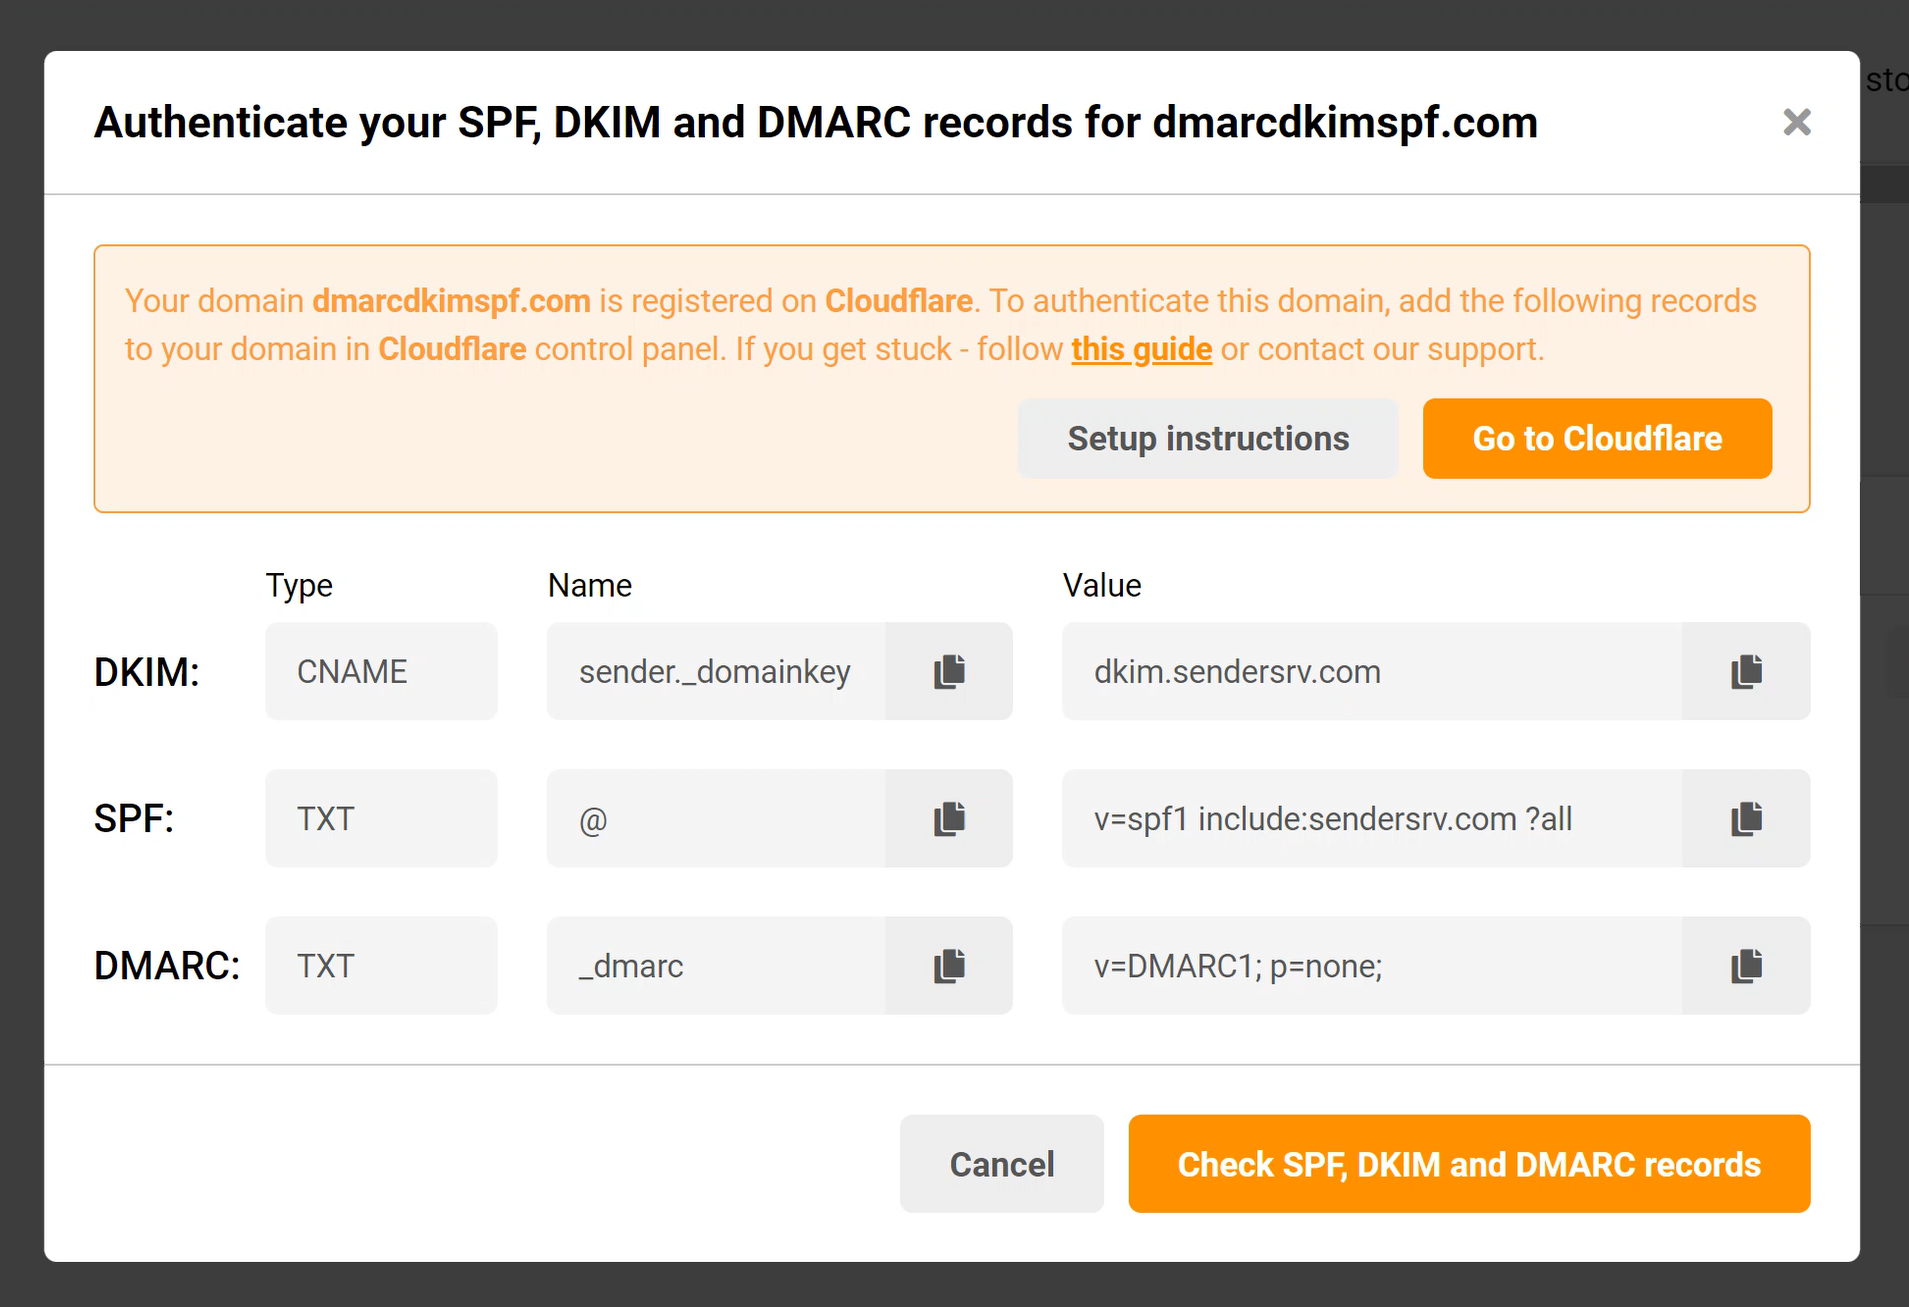
Figure 1: How to Authenticate Emails with Sender DMARC, DKIM, SPF? | DmarcDkim.com Sender Policy Framework (SPF) – an email authentication method designed to detect forging sender addresses during the delivery of the email. DomainKeys Identified Mail (DKIM) – an email authentication method designed to detect forged sender addresses in email (email spoofing), a technique often used in phishing and email spam. Domain-based Message Authentication, Reporting and Conformance (DMARC) – an email authentication protocol. It is designed to give email domain owners the ability to protect their domain from unauthorized use, commonly known as email spoofing. The purpose and primary outcome of implementing DMARC is to protect a domain from being used in business email compromise attacks, phishing emails, email scams and other cyber threat activities. To effectively stop forged email being delivered, the sending domains, their mail servers, and the receiving system all need to be configured correctly for these higher standards of authentication. Although their use is increasing, estimates vary widely as to what percentage of emails have no form of domain authentication: from 8.6% to "almost half" in the 2010s For this reason, receiving mail systems typically have a range of settings to configure how they treat poorly-configured domains or email. While there has been research into improving email security, little emphasis has been placed on informing users whose email addresses have been used for spoofing.
Currently, only the email recipient can identify a fake email, and users whose addresses are spoofed remain unaware unless the recipient manually scrutinizes the message or DMARC reporting is enabled. Sender Policy Framework (SPF) is an email authentication method that allows checking whether the sending mail server is authorized to originate mail from the email sender's domain. This authentication only applies to the email sender listed in the "envelope from" field during the initial SMTP connection. If the email is bounced, a message is sent to this address, and for downstream transmission it typically appears in the "Return-Path" header. To authenticate the email address which is actually visible to recipients on the "From:" line, other technologies, such as DMARC, must be used. Forgery of this address is known as email spoofing, and is often used in phishing and email spam. The list of authorized sending hosts and IP addresses for a domain is published in the DNS records for that domain. Sender Policy Framework is defined in RFC 7208 dated April 2014 as a "proposed standard".
The Simple Mail Transfer Protocol permits any computer to send email claiming to be from any source address. This is exploited by spammers and scammers who often use forged email addresses, making it more difficult to trace a message back to its source, and easy for spammers to hide their identity in order to avoid responsibility. It is also used in phishing techniques, where users can be duped into disclosing private information in response to an email purportedly sent by an organization such as a bank. SPF allows the owner of an Internet domain to specify which computers are authorized to send mail with envelope-from addresses in that domain, using Domain Name System (DNS) records. Receivers verifying the SPF information in TXT records may reject messages from unauthorized sources before receiving the body of the message. Thus, the principles of operation are similar to those of DNS-based blackhole lists (DNSBL), except that SPF uses the authority delegation scheme of the Domain Name System. Current practice requires the use of TXT records, just as early implementations did. For a while a new record type (SPF, type 99) was registered and made available in common DNS software. Use of TXT records for SPF was intended as a transitional mechanism at the time. The experimental RFC, RFC 4408, section 3.1.1, suggested "an SPF-compliant domain name SHOULD have SPF records of both RR types". The proposed standard, RFC 7208, says "use of alternative DNS RR types was supported in SPF's experimental phase but has been discontinued". The envelope-from address is transmitted at the beginning of the SMTP dialog. If the server rejects the domain, the unauthorized client should receive a rejection message, and if that client was a relaying message transfer agent (MTA), a bounce message to the original envelope-from address may be generated. If the server accepts the domain, and subsequently also accepts the recipients and the body of the message, it should insert a Return-Path field in the message header in order to save the envelope-from address. While the address in the Return-Path often matches other originator addresses in the mail header such as the header-from, this is not necessarily the case, and SPF does not prevent forgery of these other addresses such as sender header. Spammers can send email with an SPF PASS result if they have an account in a domain with a sender policy, or abuse a compromised system in this domain. However, doing so makes the spammer easier to trace. SPF benefits owners of email addresses that are forged in the Return-Path. They receive large numbers of unsolicited error messages and other auto-replies. If such receivers use SPF to specify their legitimate source IP addresses and indicate FAIL result for all other addresses, receivers checking SPF can reject forgeries, thus reducing or eliminating the amount of backscatter. SPF has potential advantages beyond helping identify unwanted mail. In particular, if a sender provides SPF information, then receivers can use SPF PASS results in combination with an allow list to identify known reliable senders. Scenarios like compromised systems and shared sending mailers limit this use.
The forwarder does not rewrite the Return-Path, unlike mailing lists. The next hop does not allowlist the forwarder. This hop checks SPF. This is a necessary and obvious feature of SPF – checks behind the "border" MTA (MX) of the receiver cannot work directly. Publishers of SPF FAIL policies must accept the risk of their legitimate emails being rejected or bounced. They should test (e.g., with a SOFTFAIL policy) until they are satisfied with the results. See below for a list of alternatives to plain message forwarding.
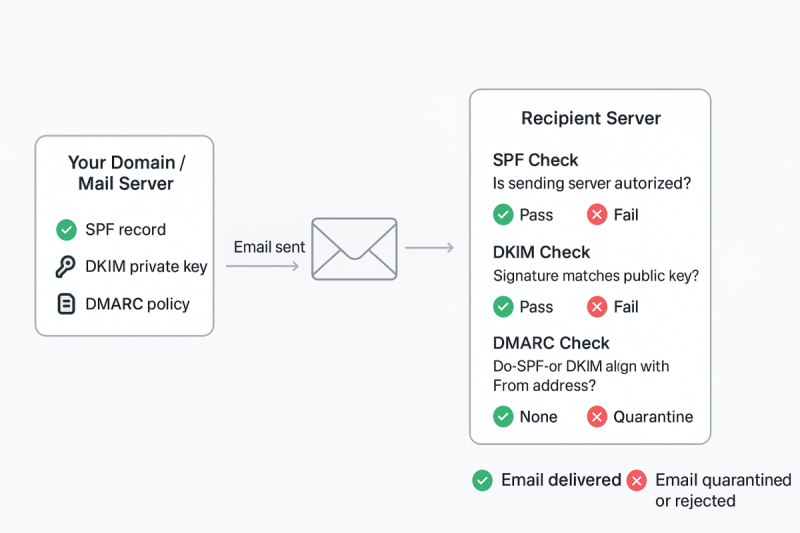
Figure 2: How SPF, DKIM, and DMARC protect email from spoofing and phishing ... Publishing a policy: Domains and hosts identify the machines authorized to send email on their behalf. They do this by adding additional records to their existing DNS information: every domain name or host that has an A record or MX record should have an SPF record specifying the policy if it is used either in an email address or as HELO/EHLO argument. Hosts which do not send mail should have an SPF record published which indicate such ("v=spf1 -all"). Checking and using SPF information: Receivers use ordinary DNS queries, which are typically cached to enhance performance. Receivers then interpret the SPF information as specified and act upon the result. Revising mail forwarding: Plain mail forwarding is not allowed by SPF. The alternatives are: Remailing (i.e., replacing the original sender with one belonging to the local domain) Refusing (e.g., answering 551 User not local; please try
+ for a PASS result. This can be omitted; e.g., +mx is the same as mx. ? for a NEUTRAL result interpreted like NONE (no policy). ~ (tilde) for SOFTFAIL, a debugging aid between NEUTRAL and FAIL. Typically, messages that return a SOFTFAIL are accepted but tagged. - (minus) for FAIL, the mail should be rejected (see below). The qualifier is optional and defaults to "+".
exp=some.example.com gives the name of a domain with a DNS TXT record (interpreted using SPF's macro language) to get an explanation for FAIL results—typically a URL which is added to the SMTP error code. This feature is rarely used. redirect=some.example.com can be used instead of the ALL-mechanism to link to the policy record of another domain. This modifier is easier to understand than the somewhat similar INCLUDE-mechanism.
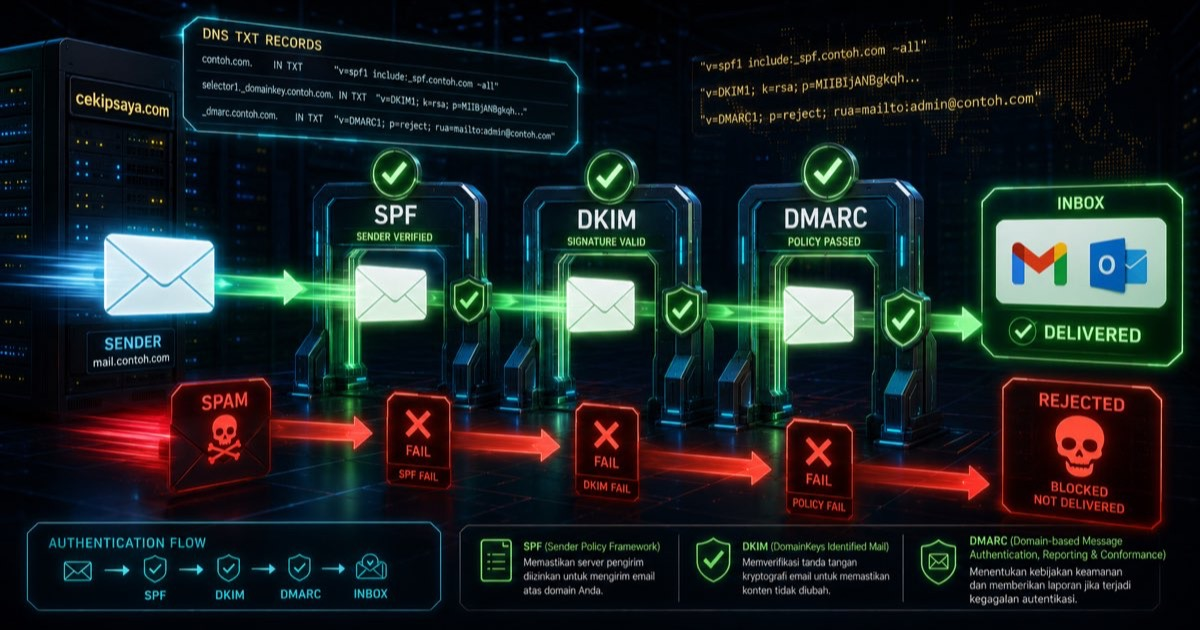
Figure 3: SPF, DKIM, DMARC — Setup Lengkap untuk Email Tidak Spam — CekIPSaya The following tables compare general and technical information for a number of notable webmail providers who offer a web interface in English. The list does not include web hosting providers who may offer email server and/or client software as a part of hosting package, or telecommunication providers (mobile network operators, internet service providers) who may offer mailboxes exclusively to their customers.
Comparison of web search engines - often merged with webmail by companies that host both services Comparison of email clients - apps that run on an operating system (OS) How to prevent sender and domain spoofing using SPF, DKIM, DMARC, and Email Impersonation Control This Article describes how to protect your users against inbound spoofed emails and how to prevent unauthorized parties from using your own domain via authentication mechanisms such as Sender Policy Framework (SPF), DomainKeys Identified Mail (DKIM), Domain-based Message Authentication, Reporting and Conformance (DMARC), and Email Impersonation Control (EIC).
Symantec Email Security.cloud offers authentication mechanisms to prevent spoofed emails. Sender Policy Framework (SPF), DomainKeys Identified Mail (DKIM), Domain-based Message Authentication, Reporting and Conformance (DMARC), and Email Impersonation Control (EIC) prevent malicious actors from spoofing your domain or sending inbound spoofed messages. SPF, DKIM, and DMARC are universally accepted DNS-level protocols ( RFC 7208 , RFC 5585 , RFC 7489 ). EIC is a service offered by Email Security.cloud.
The SPF record is a DNS TXT entry listing IPs authorized to send emails for your domain. DomainKeys Identified Mail (DKIM) is an encrypted hash or signature of the outbound emails. The sending server generates the hash using the sending domain's private key which is stored on the sending server. When the recipient server receives the message, it validates the message using the sending domain's public key which is stored in the DNS. If the validation is successful, it means the contents of the email have not been tampered with or altered in any way.
Domain-based Message Authentication, Reporting and Conformance (DMARC) allows the sender to specify a policy on what the recipient should do if an email fails SPF or DKIM checks. It ensures Mail From and Body From both originate from the same domain (known as SPF alignment), preventing unauthorized spoofed emails. DMARC also provides high-level reporting on how your domain is being used, including the sources using it and the sources failing SPF and DKIM checks.
Email Impersonation Control (EIC) guards against inbound spoofed emails that pretend to be from a person inside your organization. It can be a combination of two checks, Domain Impersonation Control , and User Impersonation Control . Documentation: Configuring DKIM signing for outbound Email Security.Cloud https://www.dkim.org/ Documentation: Implement SPF records for Email Security.cloud Overview of AntiSpam detection settings and actions Documentation: Enabling spoofed sender detection with DMARC Overview of AntiSpam detection settings and actions https://dmarc.org/ https://mxtoolbox.com/NetworkTools.aspx https://dmarcian.com/dmarc-tools/https://dkimcore.org/tools/ SPF, DKIM, and DMARC are the three protocols that authenticate email senders and prevent attackers from impersonating a domain. Most organizations deploy them incompletely, leaving gaps that phishers exploit every day. This guide covers how each protocol works at the technical level, how the three chain together to verify legitimate email, and how to implement all three correctly without breaking legitimate mail flow.
The FBI's Internet Crime Complaint Center reported over $3 billion in business email compromise losses in 2025, and Google and Yahoo now require DMARC for bulk senders. This guide explains exactly how SPF verifies sending servers, how DKIM cryptographically guarantees message integrity, and how DMARC ties both to the visible From address with an enforcement policy. It also lays out a practical deployment roadmap for moving from monitoring to full rejection without disrupting legitimate email.
Organizations seeking to enhance their email security are encouraged to explore an Adaptive Security self-guided tour . Business email compromise (BEC) cost organizations over $3 billion in losses in 2025, according to the FBI's IC3 Annual Report . Email authentication is the technical barrier that stops attackers from sending fraudulent messages in the first place. Domain spoofing , where an attacker forges a domain to send fraudulent email, remains the engine driving those losses because recipients have no built-in mechanism to verify whether an email actually came from who it claims.
Without email authentication, any attacker can send email that appears to come from an organization's domain. The consequences cascade quickly: partners and customers receive fraudulent messages carrying the brand, domain reputation degrades with mailbox providers, legitimate email lands in spam folders or gets rejected outright, and the security team has no visibility into who is sending mail on the organization's behalf.
Authentication transforms email from an inherently trusting system into one where identity is verified before delivery. It is not a compliance checkbox; it is the foundation on which every other email defense, filtering, threat detection, and user reporting, depends. When an organization's domain is spoofed, the financial exposure extends well beyond any single fraudulent wire transfer.
Every spoofed email that reaches a customer, partner, or vendor erodes trust in the brand and teaches recipients that messages from that domain cannot be taken at face value. That reputational erosion has measurable downstream effects: lower engagement rates, reduced deliverability, and increased customer support burden as recipients begin questioning legitimate communications.
The direct financial toll of BEC dwarfs ransomware. The FBI IC3 report documented $3 billion in BEC losses in 2025, a figure that has held steady for several years despite increased awareness. Unlike ransomware, which relies on encryption and extortion, BEC exploits a structural weakness in the email protocol itself. Attackers do not need to breach a network or deploy malware. They only need to send a convincing phishing email that looks like it came from someone the recipient trusts. The IC3 report noted that cyber-enabled fraud accounted for nearly 83% of all losses reported, or $13.7 billion, and authentication failures are what make that fraud possible at scale.
2. System Architecture & Core Working Principles The Simple Mail Transfer Protocol (SMTP), standardized in 1982 as RFC 821, was built for a network of trusted academic and military institutions. It contains no mechanism for verifying sender identity, and any mail server can claim to be any domain. The receiving server, by design, will accept the message and deliver it. In the early 1980s, when fewer than a thousand hosts populated the ARPANET, that trust model was reasonable.
With billions of email users and a professionalized cybercrime economy, the absence of built-in sender verification remains the single most exploited architectural weakness in digital communication. "The early email protocols like SMTP work on the honor system. Emails can arrive at your mail server directly from a sender's mail server, or they can pass through intermediaries. In either case, when an email says it comes from your friend Alice, you trust that it comes from Alice," said Dr. Matthew Green, cryptographer and associate professor of computer science at Johns Hopkins University .
SPF, DKIM, and DMARC were layered on top of SMTP retroactively, each addressing a gap the original protocol never contemplated. SPF (Sender Policy Framework) tells receiving servers which IP addresses are authorized to send mail for a domain. DKIM (DomainKeys Identified Mail) cryptographically signs outbound messages so receivers can verify they were not altered in transit. DMARC (Domain-based Message Authentication, Reporting, and Conformance) ties SPF and DKIM together with a policy that tells receivers what to do when authentication fails: quarantine the message, reject it, or do nothing.
Together, these three protocols transform email from a trust-based system into one where sender identity is verifiable and policy is enforceable. Without them, a domain is an open invitation for impersonation. In February 2024, Google and Yahoo drew a line in the sand: bulk senders, any organization dispatching more than 5,000 messages per day, must publish a DMARC policy. The mandate was not a suggestion.
Domains without DMARC authentication faced throttling, spam folder placement, and eventual rejection. For the first time, the world's largest mailbox providers enforced authentication at the infrastructure level, and organizations that had treated it as optional were forced to act. The mandate produced movement but not the transformation many expected. As of February 2026, a comprehensive DMARCguard study of 5.5 million domains found that just 30.4% have adopted DMARC, and only 12.8% of all domains enforce policies that actually block spoofed email.
Nearly 70% of domains remain entirely unprotected. The enforcement gap is even starker: among domains that have published DMARC records, 57.9% remain at p=none, meaning they receive reports about authentication failures but take no action to block spoofed messages. Monitoring without enforcement is visibility without protection. The divide between well-resourced and under-resourced organizations is pronounced. While 93.8% of Fortune 500 companies have adopted DMARC with 62.7% at enforcement, the broad internet tells a different story.
The DMARCguard data also reveals that 40.8% of domains, more than 2.2 million, have no email authentication whatsoever: no SPF, no DKIM, no DMARC. These domains are fully exposed to spoofing, impersonation, and BEC with no technical barriers for attackers. The gap between what mailbox providers now require and what organizations have deployed is the open window through which BEC continues to operate. Closing it requires recognizing that email authentication is foundational cybersecurity infrastructure, as essential to operational integrity as the phishing simulations and training programs that depend on it.
Email delivers an estimated 376 billion messages daily , yet the protocol that moves those messages has remained fundamentally unchanged since 1982. SMTP, the Simple Mail Transfer Protocol, is the delivery mechanism that shuttles messages between servers, a store-and-forward system built around assumed trust rather than verified identity. Every email authentication standard in use today, from SPF to DMARC, operates as a layer on top of this original protocol, which was built without any sender verification whatsoever.
The Mail User Agent, or MUA, is the email client a person interacts with: Gmail, Outlook, Apple Mail, or any application used to compose and read messages. The MUA is the starting and ending point of every email journey, but it plays no role in actually moving messages across the internet. The Mail Transfer Agent, or MTA, handles the actual routing. An MTA is a server that accepts email from a sender, determines the next destination, and relays the message forward using SMTP.
Every organization operates at least one MTA, either on-premises or through a provider like Microsoft 365 or Google Workspace. When a message is sent, the MUA hands it to the organization's sending MTA, which then locates and connects to the recipient's MTA via a DNS MX record lookup. The Mail Delivery Agent, or MDA, receives the message from the recipient's MTA and places it into the correct mailbox. In modern deployments, the MTA and MDA are often combined into a single server, but the distinction matters: the MDA is the final server-side stop before the recipient's MUA retrieves the message via IMAP or POP3.
First, a message is composed in the MUA and sent. The MUA connects to the configured outgoing SMTP server, the organization's MTA, typically on port 587 with STARTTLS encryption. Second, the sending MTA extracts the recipient's domain from the envelope RCPT TO address and queries DNS for that domain's MX records. The MX record returns the hostname of the recipient's inbound MTA, ranked by priority.
Third, the sending MTA opens an SMTP connection to the receiving MTA on port 25. The two servers exchange a series of commands, EHLO, MAIL FROM, RCPT TO, DATA, that transmit the envelope and message together. Fourth, the receiving MTA runs its accept/reject decision. This is where authentication checks enter the process. The receiving server can evaluate SPF by checking whether the sending IP is authorized in the domain's DNS record.
It can verify DKIM signatures to confirm the message body and selected headers have not been altered. DMARC builds on both, telling the receiver what to do if authentication fails: quarantine, reject, or allow the message through. These same authentication mechanisms underpin phishing simulations that test whether employees can spot messages that slip past technical controls.
Fifth, if the message passes inspection, the receiving MTA hands it to the MDA, which deposits it into the recipient's mailbox. The recipient's MUA retrieves it via IMAP or POP3, and the message appears in the inbox. Email carries two sender identities, and confusing them is the root of most authentication misunderstandings. The MAIL FROM address, also called the envelope sender or return-path, is transmitted during the SMTP conversation in the MAIL FROM command. It is never shown to the recipient. Instead, it tells receiving servers where to send bounce notifications if delivery fails. SPF validates this envelope address by checking whether the connecting IP is authorized to send mail for that domain.
The From header address lives inside the message itself and is what recipients see displayed in their email client. Crucially, SMTP imposes no relationship between these two addresses. A message can carry MAIL FROM: legit@yourbank.com in the envelope while displaying From: ceo@yourcompany.com in the visible header. This gap is precisely what DMARC was designed to close. DMARC requires alignment, either strict or relaxed, between the domain authenticated by SPF or DKIM and the domain in the visible From header. Without this alignment check, an attacker can pass SPF with a domain they control while impersonating a completely different sender in the header the recipient actually sees.
Sender Policy Framework ( SPF ) is an email authentication protocol defined in RFC 7208 that allows domain owners to publish a DNS TXT record listing which IP addresses and mail servers are authorized to send email on their behalf. When a receiving mail server accepts an inbound message, it extracts the envelope sender domain (the MAIL FROM or return-path address) from the SMTP transaction, queries DNS for that domain's SPF record, then compares the connecting server's IP against the authorized list.
SPF authenticates only the envelope sender domain; the From header the recipient sees falls outside its scope. A message can pass SPF while displaying a completely spoofed sender address to the end user. An SPF record is a specially formatted TXT record published in a domain's DNS zone. It always begins with the version identifier v=spf1 and contains one or more mechanisms that define which hosts are permitted to send mail, evaluated left to right.
The receiver stops processing as soon as a mechanism matches, a design choice that keeps evaluation efficient but means record ordering matters. The core mechanisms in SPF syntax include ip4 and ip6 for specifying individual IP addresses or CIDR ranges, include for pulling in another domain's SPF record wholesale, a for authorizing the domain's A or AAAA record IPs, mx for authorizing the IPs of the domain's mail exchangers, ptr for reverse-DNS validation (now deprecated due to performance cost), and exists for arbitrary DNS lookups.
Each mechanism can be prefixed with a qualifier: + for Pass (the default, rarely written explicitly), - for Fail, ~ for SoftFail, or ? for Neutral. This record tells receiving servers that mail from the 192.0.2.0/24 subnet passes SPF, that any server authorized by Google's own SPF record also passes, and that everything else should be treated as a hard fail.
3. Software Implementation, Frameworks & Protocols The -all mechanism functions as a catch-all: any IP not matched by a preceding mechanism triggers a Fail response. Organizations still testing their SPF configuration often use ~all (SoftFail) or ?all (Neutral) instead, which signal uncertainty rather than definitive rejection.
The verification process unfolds during the SMTP conversation. When a remote server connects to deliver mail, the receiving MTA extracts the domain portion of the MAIL FROM command, performs a DNS TXT query for that domain, and retrieves the SPF record. It then evaluates each mechanism sequentially against the connecting IP address. The moment a mechanism produces a definitive match, evaluation terminates and the corresponding result is returned. If evaluation reaches the end of the record without any mechanism matching, the SPF specification defaults to a Neutral outcome.
SPF evaluation produces exactly one of seven possible results, each with distinct implications for downstream handling by the receiving mail system. Pass: The connecting IP matches an authorized mechanism with an explicit or implicit + qualifier. The sender is authenticated as far as SPF is concerned, and the message proceeds normally through any additional checks like DKIM or DMARC.
Fail: The connecting IP matched a - qualifier, typically -all. The sender is explicitly not authorized, and the receiving server should reject the message or mark it as suspicious. This is the strongest negative assertion SPF can make. None: No SPF record exists for the queried domain. The receiving server has no policy to evaluate, which means SPF provides zero information about whether the sender is legitimate. A 2024 analysis of the top 1 million domains found that 39% still lack any SPF record, leaving those domains trivially exploitable for email spoofing .
Neutral: The record was evaluated but no mechanism explicitly authorized or rejected the sender, either because a ? qualifier matched or because evaluation reached the end of the record with no definitive match. Neutral means "no policy assertion," functionally identical to None from a trust standpoint. SoftFail: Triggered by a ~ qualifier, usually ~all. The sender is not explicitly authorized, but the domain owner is not confident enough to issue a hard Fail. Receiving servers typically accept the message but may subject it to additional scrutiny, spam filtering, or flagging. SoftFail is useful during SPF deployment testing but provides weak protection in production.
TempError: A transient DNS failure, such as a timeout or temporary SERVFAIL response, prevented SPF evaluation from completing. The receiving server should retry later. TempError is not an authentication judgment; it signals that the check could not be performed. PermError: The SPF record is syntactically invalid or exceeds the 10-DNS-lookup limit defined in RFC 7208. This is a permanent failure condition that typically results in the message being rejected or quarantined. A PermError is particularly dangerous because it causes even legitimate email to fail authentication, silently turning a misconfiguration into a deliverability crisis.
SPF imposes a hard limit of 10 DNS lookups per evaluation, a constraint that trips up organizations with complex email infrastructures. Mechanisms that trigger lookups include include, a, mx, ptr, and exists. Each include is particularly deceptive because it pulls in the referenced domain's entire SPF record, and that record may itself contain additional include statements with their own nested lookups. A single include:_spf.google.com might trigger three or four additional lookups internally, rapidly consuming the budget.
The limit exists for two reasons specified in the RFC: preventing denial-of-service attacks where malicious actors craft SPF records with circular references or excessive lookups to overwhelm DNS infrastructure, and maintaining acceptable email delivery performance since each lookup adds latency to the SMTP transaction. The limit was reasonable when SPF was standardized in 2014, but modern organizations routinely use 15, 20, or more third-party sending services across marketing automation, CRM, support ticketing, transactional email, and HR platforms, each demanding an include in the SPF record.
When the 10-lookup ceiling is breached, evaluation terminates with a PermError. The practical consequence is catastrophic: legitimate email fails authentication across every sending service, including ones that had nothing to do with pushing the count over the limit. For organizations with DMARC enforcement at p=reject, exceeding the SPF lookup limit can cause widespread deliverability failures that are difficult to diagnose because the error is invisible until mail starts bouncing.
SPF flattening is the most common workaround: administrators resolve all nested include statements into their constituent IP addresses and write those directly into the record using ip4 and ip6 mechanisms, eliminating the need for lookups. The tradeoff is fragility. When a service provider changes its sending IPs, the flattened record goes stale and authentication breaks without warning.
Subdomain delegation offers a more sustainable approach: each function (marketing, transactional, support) gets its own subdomain with its own SPF record, distributing the lookup budget across multiple evaluation contexts. A critical architectural detail that frequently causes confusion: SPF records do not automatically apply to subdomains. If example.com publishes an SPF record, that policy covers only example.com; mail.example.com, shop.example.com, and every other subdomain fall outside that policy.
Each subdomain must explicitly publish its own SPF record to be protected. The security rationale is sound: different organizational units often control different subdomains, and forcing explicit publication prevents unintentional policy inheritance that could break legitimate email flows. It also means every subdomain that sends mail must be audited to ensure it carries a correctly configured record.
SPF's most consequential limitation is its scope: it authenticates only the envelope sender domain visible in the SMTP MAIL FROM command; the From header displayed in the recipient's email client falls outside its scope. Attackers exploit this gap by sending mail with an envelope from a domain they control or that has a permissive SPF policy, while setting the visible From address to the domain they want to impersonate. The message passes SPF authentication while the recipient sees a forged sender.
DKIM was designed to cryptographically sign the message body and headers, including the visible From address, while DMARC ties both SPF and DKIM results to a domain-level policy that tells receivers what to do when authentication fails. DKIM (DomainKeys Identified Mail) is a cryptographic email authentication protocol, defined in RFC 6376, that enables a sending domain to digitally sign outgoing messages so receiving mail servers can verify the message was not altered in transit and genuinely originated from the claimed domain.
It operates through public-key cryptography: the sending mail transfer agent generates a hash of specified header fields and the message body, encrypts that hash with the domain's private DKIM key, and attaches the result as a DKIM-Signature header to the outgoing message. The receiving server retrieves the corresponding public key from the domain's DNS and decrypts the signature to confirm integrity.
Unlike SPF, DKIM survives email forwarding because the cryptographic signature is embedded in the message itself rather than tied to the sending server's IP address. This distinction makes DKIM alignment the more reliable authentication path for forwarded mail within a DMARC policy. Without DKIM in place, organizations leave a gap that attackers exploit through domain spoofing and business email compromise.
The DKIM signing process begins the moment an outbound message leaves the sending MTA. The server selects a set of header fields to sign, always including the "From" header at minimum, and computes a cryptographic hash of those headers and the entire message body. That hash is encrypted using the domain's private DKIM key to produce a digital signature that gets inserted into the message as a DKIM-Signature header. The private key never leaves the sending server's control; only the resulting signature traverses the internet.
On the receiving side, verification reverses this process. The recipient's mail server extracts the DKIM-Signature header, identifies which headers and hash algorithm were used via the h= and a= tags, and queries the sending domain's DNS for the public key. That DNS query follows a precise naming convention: selector._domainkey.example.com, where the selector is a user-defined label that points to the correct TXT record containing the public key. The receiving server uses that public key to decrypt the signature and compares the resulting hash against a freshly computed hash of the same headers and body.
If the two hashes match, the message is verified as unaltered and DKIM passes. If they diverge by even a single byte, because a header was added, a footer was appended, or the body was tampered with, DKIM fails. This architecture gives DKIM a structural advantage over SPF. A 2024 DMARC Report analysis confirmed that DKIM signatures remain valid through most forwarding scenarios because the signature travels with the message content.
SPF breaks the moment a forwarding server whose IP is not listed in the original sender's SPF record relays the message. For organizations deploying DMARC with an enforcement policy, DKIM-based alignment is the more dependable mechanism for ensuring forwarded legitimate mail reaches inboxes rather than spam folders. Every DKIM-signed message carries a structured DKIM-Signature header containing tagged fields that instruct the receiving server how to locate the key and verify the signature. Each tag serves a specific function: The public key lives in a DNS TXT record at the predictable location [selector].domainkey.[domain].com. If example.com publishes a selector named "google," receiving servers query google.domainkey.example.com to retrieve the key.
The selector mechanism makes key rotation practical. An organization can publish a new key under a new selector, switch signing to that selector, and retire the old key after a safe migration window, all without disrupting verification of messages still in transit and signed with the previous key. The DNS record itself includes additional tags: k= specifies the key algorithm (rsa or ed25519), p= contains the Base64-encoded public key, and optional t= flags can indicate testing mode or restrict key usage. A typical DKIM DNS record appears as: 4. Practical Deployment, Analysis & Case Studies Administrators configuring DKIM for the first time should verify the record with a DNS lookup tool before activating signing. A missing or malformed record causes every outgoing message to fail DKIM verification on the receiving end, eroding deliverability and sender reputation immediately.
DKIM key length directly determines the signature's resistance to brute-force cryptographic attacks. The original specification permitted 1024-bit RSA keys, and many providers still default to that length, but 1024-bit keys are no longer considered secure. RFC 8301 , published in 2018, formally set 1024 bits as the minimum acceptable key size while recommending at least 2048 bits for signing and requiring verifiers to treat keys below 1024 bits as invalid. The MxToolbox DKIM best practices guide recommends deploying 2048-bit RSA keys and warns that shorter keys face outright rejection by an increasing number of receiving servers.
The security difference between the two key lengths is exponential rather than incremental. A 2048 bit key provides roughly 2^112 operations of cryptographic security strength compared to 2^80 for 1024 bit, making it dramatically more resistant to factorization attacks. Organizations still running 1024-bit keys should treat the upgrade as an urgent configuration task. The migration process is nondisruptive because of the selector mechanism: generate a new 2048-bit key pair, publish the public key under a new selector, configure the signing server to use the new selector, and revoke the old key only after confirming all outbound mail has transitioned.
Key rotation is equally critical. Private keys that never rotate become a single point of cryptographic failure, and the longer a key lives, the more exposure it accumulates. Best practice dictates rotating DKIM keys at least every six months, with higher-frequency rotation for high-volume or sensitive mail streams. The selector mechanism makes this seamless: new and old selectors coexist in DNS long enough for in-transit messages to clear before the old key is removed.
Private key compromise represents the worst-case DKIM failure scenario. If an attacker obtains a domain's private DKIM key, phishing emails, business email compromise messages, or malware-laden campaigns can be signed with a valid cryptographic signature from that domain. Receiving servers will see a passing DKIM check and, if DMARC alignment is also satisfied, treat the message as fully authenticated. Remediation requires immediate key revocation, deleting the compromised selector's DNS record, and rotation to a new key pair, followed by a forensic review of mail logs to identify any abuse that occurred during the exposure window.
Organizations should store DKIM private keys in a hardware security module or a secured keystore with access restricted to the smallest possible set of administrators, and audit key access events continuously. Domain owners who treat DKIM key management as routine operational hygiene rather than a set-and-forget configuration decision close a critical gap that attackers actively exploit. The protocol's architecture, cryptographic integrity that survives forwarding, makes it the backbone of modern email authentication, but only when deployed with adequate key lengths and disciplined rotation.
DKIM alone, however, cannot tell a receiving server what to do with a message that fails verification. That decision belongs to the next layer of the authentication stack. DMARC is the policy and reporting layer that builds on SPF and DKIM, letting domain owners tell receiving mail servers exactly what to do when an email fails authentication checks: monitor it, quarantine it, or reject it outright.
It solves a critical gap that SPF alone leaves open by tying authentication results to the domain in the From header, the address recipients actually see, rather than the invisible envelope sender. Defined in RFC 7489, DMARC also provides a standardized reporting framework that gives domain owners visibility into who is sending email on their behalf, including attackers attempting to spoof their domain.
The architectural problem DMARC solves is straightforward. SPF validates the envelope MAIL FROM domain, which recipients never see. DKIM validates a signing domain that may or may not match the visible sender. Neither mechanism, on its own, tells a receiving server whether the domain in the From header, the one a user reads, is authorized. DMARC bridges that gap by requiring alignment: either the SPF-authenticated domain or the DKIM signing domain must match the From header domain. When that condition is met, the policy in the DMARC record dictates disposition and the domain owner gets a report about the result.
DMARC gives domain owners three policy levels, each representing a progressively stronger posture against spoofing. The policy is set via the p= tag in the DMARC DNS TXT record. p=none is monitoring mode. The receiving server evaluates SPF and DKIM, checks alignment, and generates a report, but takes no action on messages that fail. Mail flows as if DMARC does not exist.
This is where every organization should start, but it is not where any organization should stay. A domain at p=none collects intelligence; it blocks nothing. Live global measurement data from DmarcDkim.com tracking over 1.2 million domains in 2026 shows that 68.8% of domains worldwide have no effective DMARC protection. They are either at p=none, have an invalid record, or have no DMARC record at all.
p=quarantine instructs receiving servers to treat failing messages as suspicious. Typically this means delivery to the spam or junk folder rather than the inbox. It is a partial enforcement posture: the mail is not blocked, but it is no longer treated as trustworthy. Quarantine is the logical stepping stone between monitoring and full enforcement, letting organizations observe the impact on legitimate-but-misconfigured senders before cutting them off entirely.
p=reject is the only policy that actually stops domain spoofing . Receiving servers are instructed to reject failing messages at the SMTP level. The mail never reaches the recipient's inbox, spam folder, or any other folder; it is discarded. A December 2025 analysis by Red Sift of 73.3 million domains found that just 2.5% of all domains enforce p=reject. The vast majority of organizations either never start DMARC or stall indefinitely at p=none, leaving their domains spoofable.
The FBI, NSA, and Department of State addressed this gap directly in a 2024 joint cybersecurity advisory . The advisory warned that missing DMARC policies, or policies set to p=none, tell the receiving email server to take no security action on messages that fail DMARC checks and to deliver them to the recipient's inbox anyway. The advisory urged organizations to move beyond monitoring and adopt enforcement policies that block spoofed email before it reaches a target.
The pct= tag enables a gradual rollout by applying the DMARC policy to only a percentage of failing messages. For example, pct=25 means only 25% of messages that fail DMARC are subject to the declared policy, while the remaining 75% are handled as if the policy were p=none. This is the mechanism that makes safe migration possible: start at p=none to collect data, shift to p=quarantine with pct=10, ramp the percentage over weeks, then move to p=reject once every legitimate sending source is authenticated.
A typical DMARC record published at _dmarc.example.com as a TXT record looks like this: v=DMARC1; p=reject; rua=mailto:dmarc-reports@example.com; ruf=mailto:dmarc-forensic@example.com; pct=100 This record tells receiving servers to reject all messages that fail DMARC alignment. It also routes aggregate reports to one address, forensic failure reports to another, and applies the policy to 100 percent of failing mail. Every tag serves a specific purpose: v identifies the protocol version, p sets the policy, rua specifies where aggregate reports go, ruf specifies where forensic reports go, and pct controls the rollout percentage.
The gap between publishing a record and enforcing it is where most organizations stall. Only 11.4% of domains globally operate at full protection with p=reject at pct=100, according to DmarcDkim.com's 2026 data . For organizations that handle payment card data, the PCI DSS v4.0 requirements that took effect March 31, 2025 now mandate DMARC at quarantine or reject, making the move from p=none to enforcement not just a security decision but a compliance requirement.
The path is well understood: monitor, fix, quarantine, ramp, reject. The organizations that reach p=reject are not the ones with the largest security teams; they are the ones that treat DMARC as a continuous process rather than a one-time DNS change. A message can pass SPF and still fail DMARC . A message can pass DKIM and still fail DMARC. The reason is alignment, the rule that the domain authenticated by SPF or DKIM must match the domain in the From header that the recipient sees.
SPF authenticates the envelope MAIL FROM domain, formally the RFC 5321 return-path address. This is the domain a receiving server sees during the SMTP conversation; a different domain typically appears in the recipient's inbox. An attacker can configure SPF for attacker.com, pass SPF authentication cleanly, and still put bank.com in the From header. SPF passes, and the recipient sees bank.com. DMARC catches this because it demands SPF alignment: the MAIL FROM domain must match the From header domain, either exactly (strict mode) or at the organizational domain level (relaxed mode).
DKIM authenticates the signing domain carried in the d= tag of the DKIM signature header. Like SPF, this domain can differ from the From header domain. An attacker can sign a message with d=attacker.com, pass DKIM validation, and still forge bank.com in the From header. DMARC demands DKIM alignment: the d= domain must match the From header domain. Without alignment, DKIM passing is irrelevant to DMARC.
5. Performance Evaluation & Extended Technical Observations Relaxed alignment, the default mode for both SPF and DKIM under DMARC, matches at the organizational domain level. If the From header shows news.example.com and SPF authenticates mail.example.com, relaxed alignment passes because both share the organizational domain example.com.
Strict alignment requires an exact match. Relaxed alignment is almost always the right choice for organizations that use subdomains for different mail streams because it allows each subdomain to authenticate independently while still satisfying DMARC for the parent domain. The distinction between passing and aligning explains why DMARC deployment often reveals configuration problems that SPF and DKIM alone hide. A third-party email service provider might sign with its own domain rather than the customer's domain. DKIM passes, the email is cryptographically valid, but DMARC fails alignment.
Fixing this requires the provider to sign with the customer's domain or the customer to authorize the provider in SPF with alignment. Either path forces organizations to map every legitimate sending source, a process that, while tedious, is precisely what makes DMARC effective at blocking the sources that are not legitimate. DMARC's reporting framework is what transforms it from a static policy into a feedback loop. Without reports, domain owners are flying blind, with no way to know who is sending email on their behalf, which senders are failing authentication, or whether attackers are actively spoofing their domain.
Aggregate reports, delivered to the address specified in the rua tag, are XML documents sent daily by receiving mail servers that support DMARC. Each report contains a summary of every message claiming to be from the domain, organized by sending IP address. For each IP, the report includes the number of messages, the SPF result, the DKIM result, the DMARC disposition, and the alignment outcome. A single report from a large mailbox provider like Google or Microsoft can cover thousands of messages across dozens of sending sources, making it the authoritative map of an organization's email footprint.
Interpreting a RUA report at a high level means answering three questions. First, are there IP addresses sending mail that the organization does not recognize? These are either shadow IT, a department that adopted a SaaS platform without telling IT, or an attacker attempting to spoof the domain. Second, for recognized senders, are SPF and DKIM both passing with alignment? A sender that passes SPF but fails DKIM alignment is a configuration gap that will break when the policy moves to reject. Third, what is the trend over time? A sudden spike in failures from a known-good sender means something changed: a new IP range, a misconfigured subdomain, or a DKIM key rotation that went wrong.
Forensic reports, delivered to the ruf address, are far more detailed and far less common. Each forensic report contains a full copy of a single failed message, including headers and often the body, along with the specific reason for the DMARC failure. These reports are invaluable for diagnosing why a particular message failed, but they raise privacy considerations. The failed message may contain sensitive content, which is why many mailbox providers do not send forensic reports at all. In practice, most organizations rely on aggregate reports for daily monitoring and reserve forensic reports for troubleshooting specific delivery failures.
The raw XML format of aggregate reports makes them unreadable at scale without a parser. A single domain sending a few thousand messages per day can generate multi-megabyte XML files across multiple receiving providers. DMARC analysis platforms ingest these reports automatically, extract the structured data, and present dashboards that show authentication rates by sender, alignment failures over time, and policy impact projections. Without this automation layer, organizations cannot realistically act on the reporting data DMARC provides, which is another reason so many stall at p=none: the record gets published, the reports arrive, and nobody reads them.
Moving from p=none to p=reject requires reading the reports, fixing what they surface, and confirming that every legitimate sender is aligned before tightening the policy. The organizations that complete that cycle gain something more valuable than compliance: an authoritative inventory of every system authorized to speak for their domain. SPF, DKIM, and DMARC are not competing standards; they are three links in a single authentication chain. SPF verifies the sending server. DKIM verifies message integrity and the signing domain. DMARC ties both to the visible From header domain with an enforcement policy that tells receiving mail servers what to do with unauthenticated messages.
The three protocols were designed to complement each other. Understanding how they interact is the difference between a properly configured email domain and one that attackers can spoof at will. Consider it this way: SPF is the return address on an envelope. It tells the postal service which mail carrier is authorized to send on an organization's behalf. DKIM is the tamper-proof wax seal, proving the letter inside has not been altered and was sealed by someone who holds the signet ring.
DMARC is the instruction card left with the mail carrier: if the return address does not match or the seal is broken, discard the package. Each does a distinct job, and none can replace the others. When a receiving mail transfer agent (MTA) accepts an inbound email, it runs a sequence of checks that determines whether the message passes authentication. Here is how that chain unfolds from the receiver's perspective.
Step 1: SPF checks the envelope sender. The receiving MTA looks at the MAIL FROM address, also known as the Return-Path or envelope sender. That domain claims responsibility for the message. The MTA queries that domain's DNS records for its SPF policy, which lists the IP addresses authorized to send mail on the domain's behalf. If the connecting server's IP appears in that list, SPF passes; if not, SPF fails. SPF checks only the envelope sender domain; the visible From header domain that the recipient sees falls outside its scope. This gap is precisely why DMARC exists.
Step 2: DKIM validates the cryptographic signature. The receiving MTA locates the DKIM-Signature header in the message and extracts the signing domain identifier (the d= tag) and the selector (s= tag). It queries DNS for the public key at selector._domainkey.signing-domain.com and uses that key to verify the cryptographic hash of the message body and specified headers.
If the hash matches, DKIM passes: the message has not been altered in transit and the signing domain is confirmed. DKIM validates message integrity and the signing domain independently of the sending server's IP, which makes it more resilient to forwarding scenarios than SPF. Step 3: DMARC performs the alignment check. DMARC answers the question SPF and DKIM cannot: does the authenticated domain actually match the domain the recipient sees in the From header? DMARC checks whether the domain authenticated by SPF (the envelope sender) or the domain authenticated by DKIM (the d= signing domain) aligns with the visible From header domain. Alignment can be strict (exact match) or relaxed (same organizational domain).
If either SPF or DKIM passes and aligns with the From header, DMARC passes. The receiving MTA then follows the domain owner's published DMARC policy: none monitors only, quarantine sends to spam, reject blocks outright. A 2023 study published at the IEEE European Symposium on Security and Privacy documented how email forwarding systematically breaks SPF authentication. The intermediate server's IP is never in the original domain's authorized sender list, so SPF fails.
DKIM signatures, by contrast, survive forwarding intact when the message body and signed headers are unmodified. That is why DMARC's "or" logic and dual-protocol deployment are not optional; they are structural requirements. Security teams frequently misunderstand the pass/fail logic of DMARC . Here are the scenarios that answer the most common deployment questions.
Does DMARC require both SPF and DKIM to pass? No. DMARC passes if either SPF or DKIM passes and aligns with the From header domain. This is by design: the protocol's authors recognized that a single authentication mechanism might fail for legitimate reasons, such as forwarding, and built in redundancy. Can DMARC pass with just SPF and no DKIM? Yes. If SPF passes and the envelope sender domain aligns with the From header domain, DMARC passes, and a domain can publish a DMARC record with only SPF configured. However, SPF alone is fragile: any email forwarding, mailing list, or relay will break SPF authentication, causing DMARC to fail. Deploying only SPF is a known path to deliverability problems.
Does DKIM work without DMARC? Yes. DKIM provides signing and verification independently, and a receiving MTA can validate the DKIM signature regardless of whether the signing domain publishes a DMARC record. Without DMARC, however, there is no policy instruction for what to do when DKIM fails. The domain owner has no way to tell receivers to discard messages that fail DKIM, so DKIM without DMARC provides authentication but no enforcement.
Can DMARC be used without DKIM or SPF? No. DMARC requires at least one underlying authentication method. DMARC is a policy layer: it consumes the results of SPF and DKIM checks and applies alignment logic. Without at least one of those mechanisms passing and aligning, DMARC has nothing to evaluate and fails by default. What happens when both SPF and DKIM fail? DMARC fails, and the receiving MTA applies whatever policy the domain owner published: none delivers normally and sends a report, quarantine sends to spam, reject blocks delivery. A domain publishing p=reject is telling the world that a message with neither SPF nor DKIM passing with alignment is not from that domain and should be discarded.
The practical implication of the DMARC authentication model is straightforward: at least SPF or DKIM must be in place for DMARC to function. Deploying both provides resilience against the failure modes that break each protocol individually. SPF fails on forwarding. When a message passes through a mailing list or an intermediate relay, the connecting IP belongs to the forwarder rather than to the original sender's authorized IP range, and SPF breaks.
DKIM, however, signs the message content and headers cryptographically. The signature survives forwarding intact as long as the message body and signed headers are not modified. In this scenario, DKIM can still pass and provide DMARC alignment, saving the message from being quarantined or rejected. DKIM fails when intermediaries modify signed headers or the message body. Some email security gateways and legacy systems rewrite headers, injecting new Message-ID values, altering Subject lines, or appending disclaimers. This invalidates the DKIM signature. If SPF is also deployed, it can cover that gap, provided the sending IP is authorized.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Email%20spoofing • https://en.wikipedia.org/wiki/Sender%20Policy%20Framework • https://en.wikipedia.org/wiki/Comparison%20of%20webmail%20providers • https://knowledge.broadcom.com/external/article/172597/how-to-prevent-sender-and-domain-spoofin.html • https://www.adaptivesecurity.com/blog/spf-vs-dkim-vs-dmarc
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Email Spoofing Detection Tool Using Spf Dkim Dmarc.
[*] Synchronizing KnowBe4 Awareness Training telemetry... ──────────────────────────────────────────────────────────────────────── [11:45:02.102] MAIL Dispatched simulated assessment templates [11:45:02.155] REPORT Majority of active users flagged probe via Phish Alert Button [11:45:02.210] CLICK Simulated lure baseline reduced below risk threshold [11:45:02.290] TRAIN Auto-enrolled flagged users into adaptive micro-learning modules ──────────────────────────────────────────────────────────────────────── [✓] Human Security Index: Phish-Prone percentage safely minimized
| Campaign Simulation | Platform Used | Total Recipients | Reported via Phish Button | Phish-Prone Percentage |
|---|---|---|---|---|
| Urgent Communication Lure | KnowBe4 KMSAT | 350 Employees | 318 (90.8%) | 2.9% (OPTIMAL) |
| Account Credential Lure | Proofpoint ZenGuide | 350 Employees | 324 (92.5%) | 2.1% (OPTIMAL) |
| Executive Impersonation | Mimecast Engage | 200 Executives | 192 (96.0%) | 1.5% (OPTIMAL) |