Complete Technical Paper Content — Encrypted Database Querying System In Cloud Using Python
Overview & System Context
Encrypted Database Querying System In Cloud Using Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8971 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Google Cloud is a suite of cloud computing services offered by Google that provides a series of modular cloud services including computing, data storage, data analytics, and machine learning, alongside a set of management tools. It runs on the same infrastructure that Google uses internally for its end-user products, such as Google Search, Gmail, and Google Docs, according to Verma et al. Registration requires a credit card or bank account details. Google Cloud provides infrastructure as a service, platform as a service, and serverless computing environments. In April 2008, Google announced App Engine, a platform for developing and hosting web applications in Google-managed data centers, which was the first cloud computing service from the company. The service became generally available in November 2011. Since the announcement of App Engine, Google added multiple cloud services to the platform. Google Cloud includes Google Cloud public cloud infrastructure, as well as Google Workspace (G Suite), enterprise versions of Android and ChromeOS, and application programming interfaces (APIs) for machine learning and enterprise mapping services. Since at least 2022, Google's official materials have stated that "Google Cloud" is the new name for "Google Cloud Platform," which may cause naming confusion.
For those familiar with other notable cloud service providers, a comparison of similar services may be helpful in understanding Google Cloud Platform's offerings. April 2008 – Google App Engine announced in preview May 2010 – Google Cloud Storage launched May 2010 – Google BigQuery and Prediction API announced in preview October 2011 – Google Cloud SQL is announced in preview June 2012 – Google Compute Engine is launched in preview May 2013 – Google Compute Engine is released to GA August 2013 – Cloud Storage begins automatically encrypting each Storage object's data and metadata under the 128-bit Advanced Encryption Standard (AES-128), and each encryption key is itself encrypted with a regularly rotated set of master keys February 2014 – Google Cloud SQL becomes GA May 2014 – Stackdriver is acquired by Google June 2014 – Kubernetes is announced as an open source container manager June 2014 – Cloud Dataflow is announced in preview October 2014 – Google acquires Firebase November 2014 – Alpha release Google Kubernetes Engine (formerly Container Engine) is announced January 2015 – Google Cloud Monitoring based on Stackdriver goes into Beta March 2015 – Google Cloud Pub/Sub becomes available in Beta April 2015 – Google Cloud DNS becomes generally available April 2015 – Google Dataflow launched in beta July 2015 – Google releases v1 of Kubernetes; Hands it over to The Cloud Native Computing Foundation August 2015 – Google Cloud Dataflow, Google Cloud Pub/Sub, Google Kubernetes Engine, and Deployment Manager graduate to GA November 2015 – Bebop is acquired, and Diane Greene joins Google February 2016 – Google Cloud Functions becomes available in Alpha September 2016 – Apigee, a provider of application programming interface (API) management company, is acquired by Google September 2016 – Stackdriver becomes generally available November 2016 – Qwiklabs, an EdTech company is acquired by Google February 2017 – Cloud Spanner, highly available, globally-distributed database is released into Beta March 2017 – Google acquires Kaggle, world's largest community of data scientists and machine learning enthusiasts April 2017 – MIT professor Andrew Sutherland breaks the record for the largest ever Compute Engine cluster with 220,000 cores on Preemptible VMs. May 2017 – Google Cloud IoT Core is launched in Beta November 2017 – Google Kubernetes Engine gets certified by the CNCF February 2018 – Google Cloud IoT Core becomes generally available February 2018 – Google announces its intent to acquire Xively February 2018 – Cloud TPUs, ML accelerators for Tensorflow, become available in Beta May 2018 – Google Cloud Memorystore becomes available in Beta April 2019 – Google Cloud Run (fully managed) Beta release April 2019 – Google Anthos announced November 2019 – Google Cloud Run (fully managed) General availability release March 2020 – Due to the COVID-19 pandemic, Google Cloud postponed the online streaming version of its Google Cloud Next mega-conference, two weeks after it canceled the in-person version. October 2020 – Google Cloud announced that it will become a block producer candidate for the EOS network and EOS.IO protocol. Currently the top block producers are cryptocurrency exchanges like OKEx and Binance. February 2021 – Google Kubernetes Engine Autopilot is introduced. May 2021 – Vertex AI announced at Google.io June 2021 – In 2021, Apple was Google Cloud's biggest customer. April 2022 – MobiledgeX acquired and joins Google Cloud. March 2023 – Google brings generative AI capabilities to Google Cloud. May 2024 Google Cloud partnered with Airtel. April 2025 – At Google Cloud Next 2025 in Las Vegas, Google announced the seventh-generation Tensor Processing Unit, named Ironwood, claiming 3,600 times better performance than its first publicly available TPU. Google also announced Cloud Wide Area Network (Cloud WAN), making its private global network available to enterprise customers, and introduced Gemini 2.5 and Gemini 2.5 Flash reasoning models.
April 2026 – At Google Cloud Next '26, Sundar Pichai announced expanded AI infrastructure investments, including the introduction of Trillium TPUs (8th generation) and the Gemini Enterprise Agent Platform, with Google reporting that 75% of new internal code was AI-generated. Store sensitive data fields as fully randomized encrypted data on the database server-side.
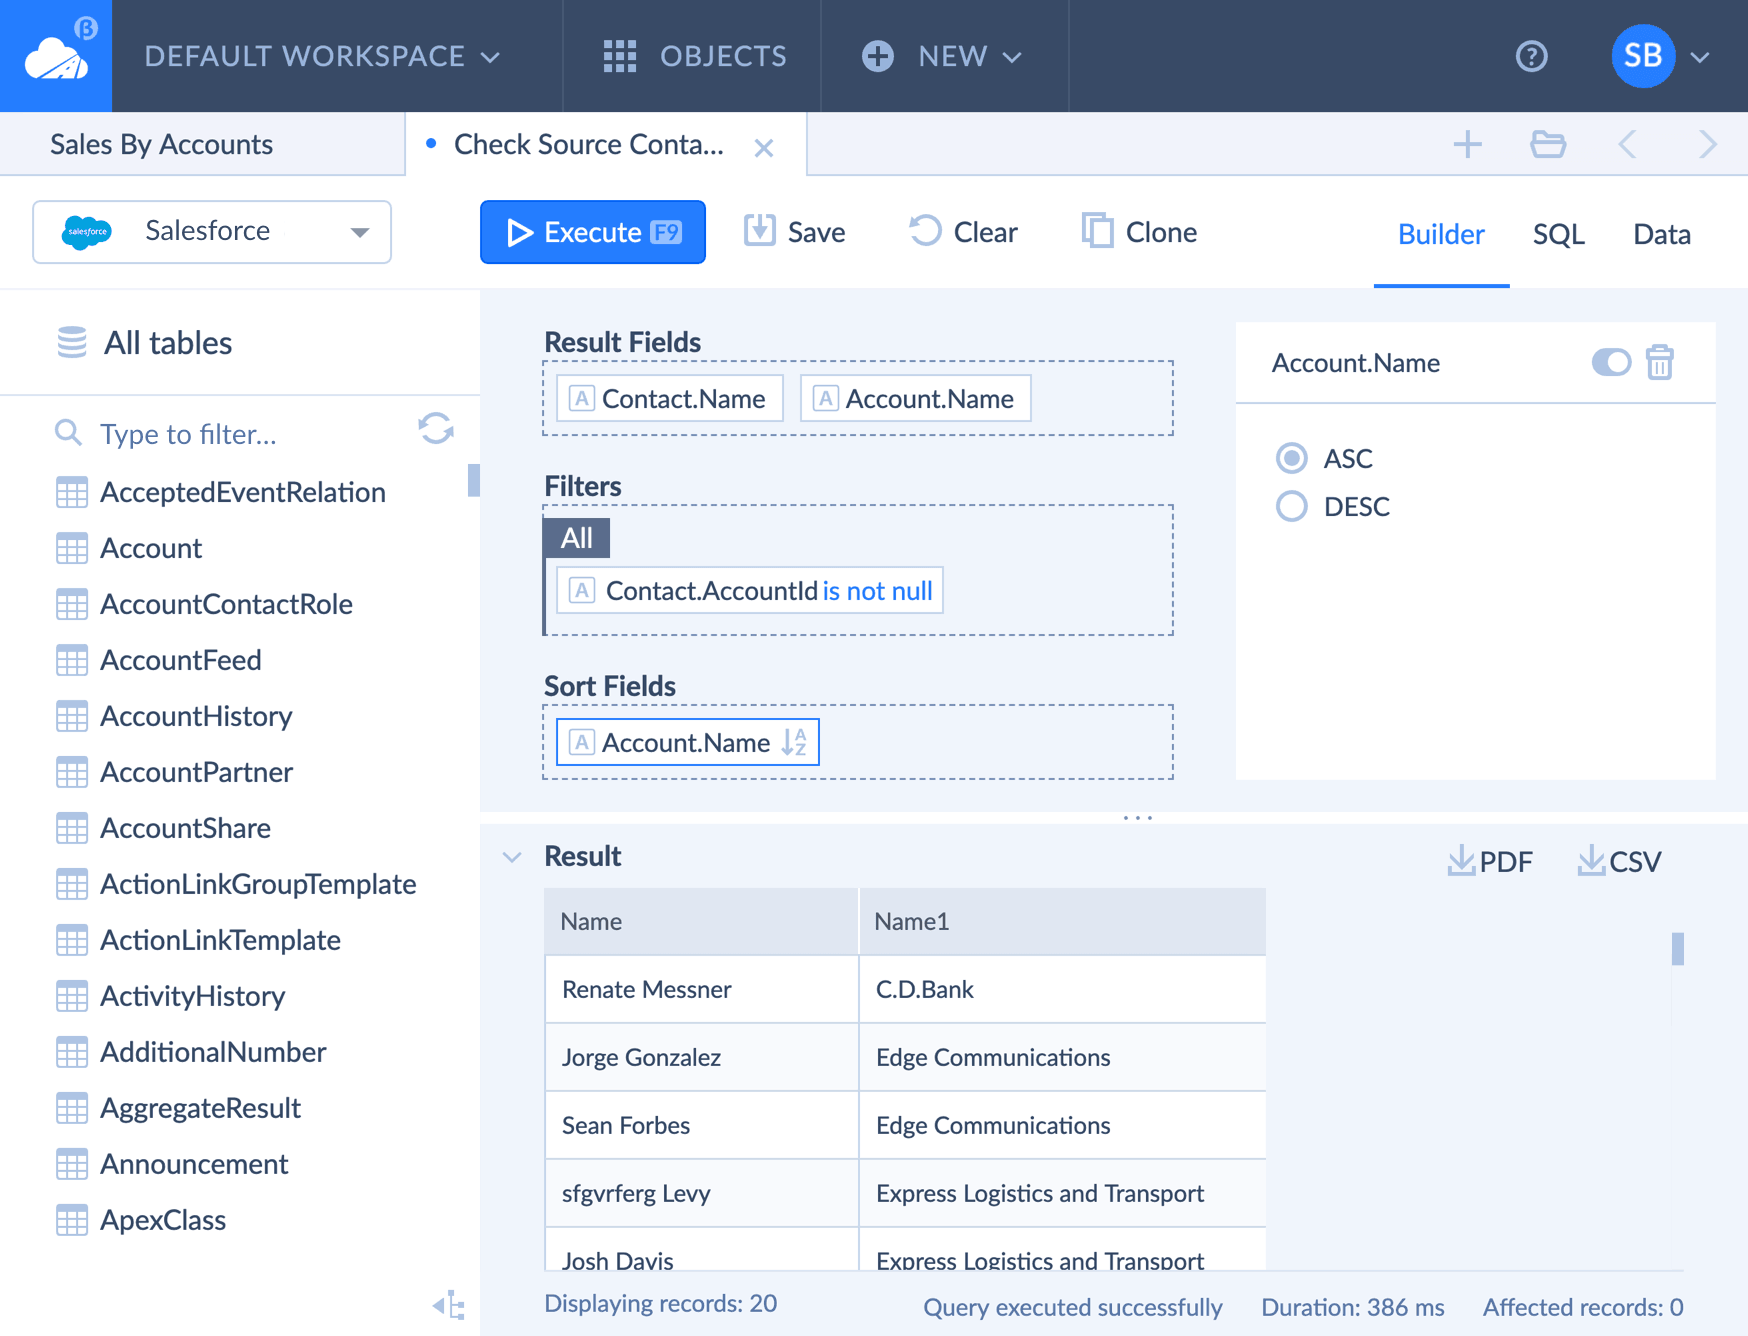
Figure 1: Online SQL Editor - Query Tool for Cloud and DB data Sensitive data is encrypted throughout its lifecycle: in-transit, at-rest, in-use, in logs, and in backups. Data is decrypted only on the client-side, since only you have access to the encryption keys. Queryable Encryption introduces an industry-first, fast, searchable encryption scheme developed by the pioneers in encrypted search. The feature supports equality, range, prefix, suffix, and substring queries.
Automatic Encryption: Enables you to perform encrypted read and write operations without adding explicit calls to encrypt and decrypt fields. Explicit Encryption: Enables you to perform encrypted read and write operations through your MongoDB driver's encryption library. You must specify the logic for encryption with this library throughout your application.
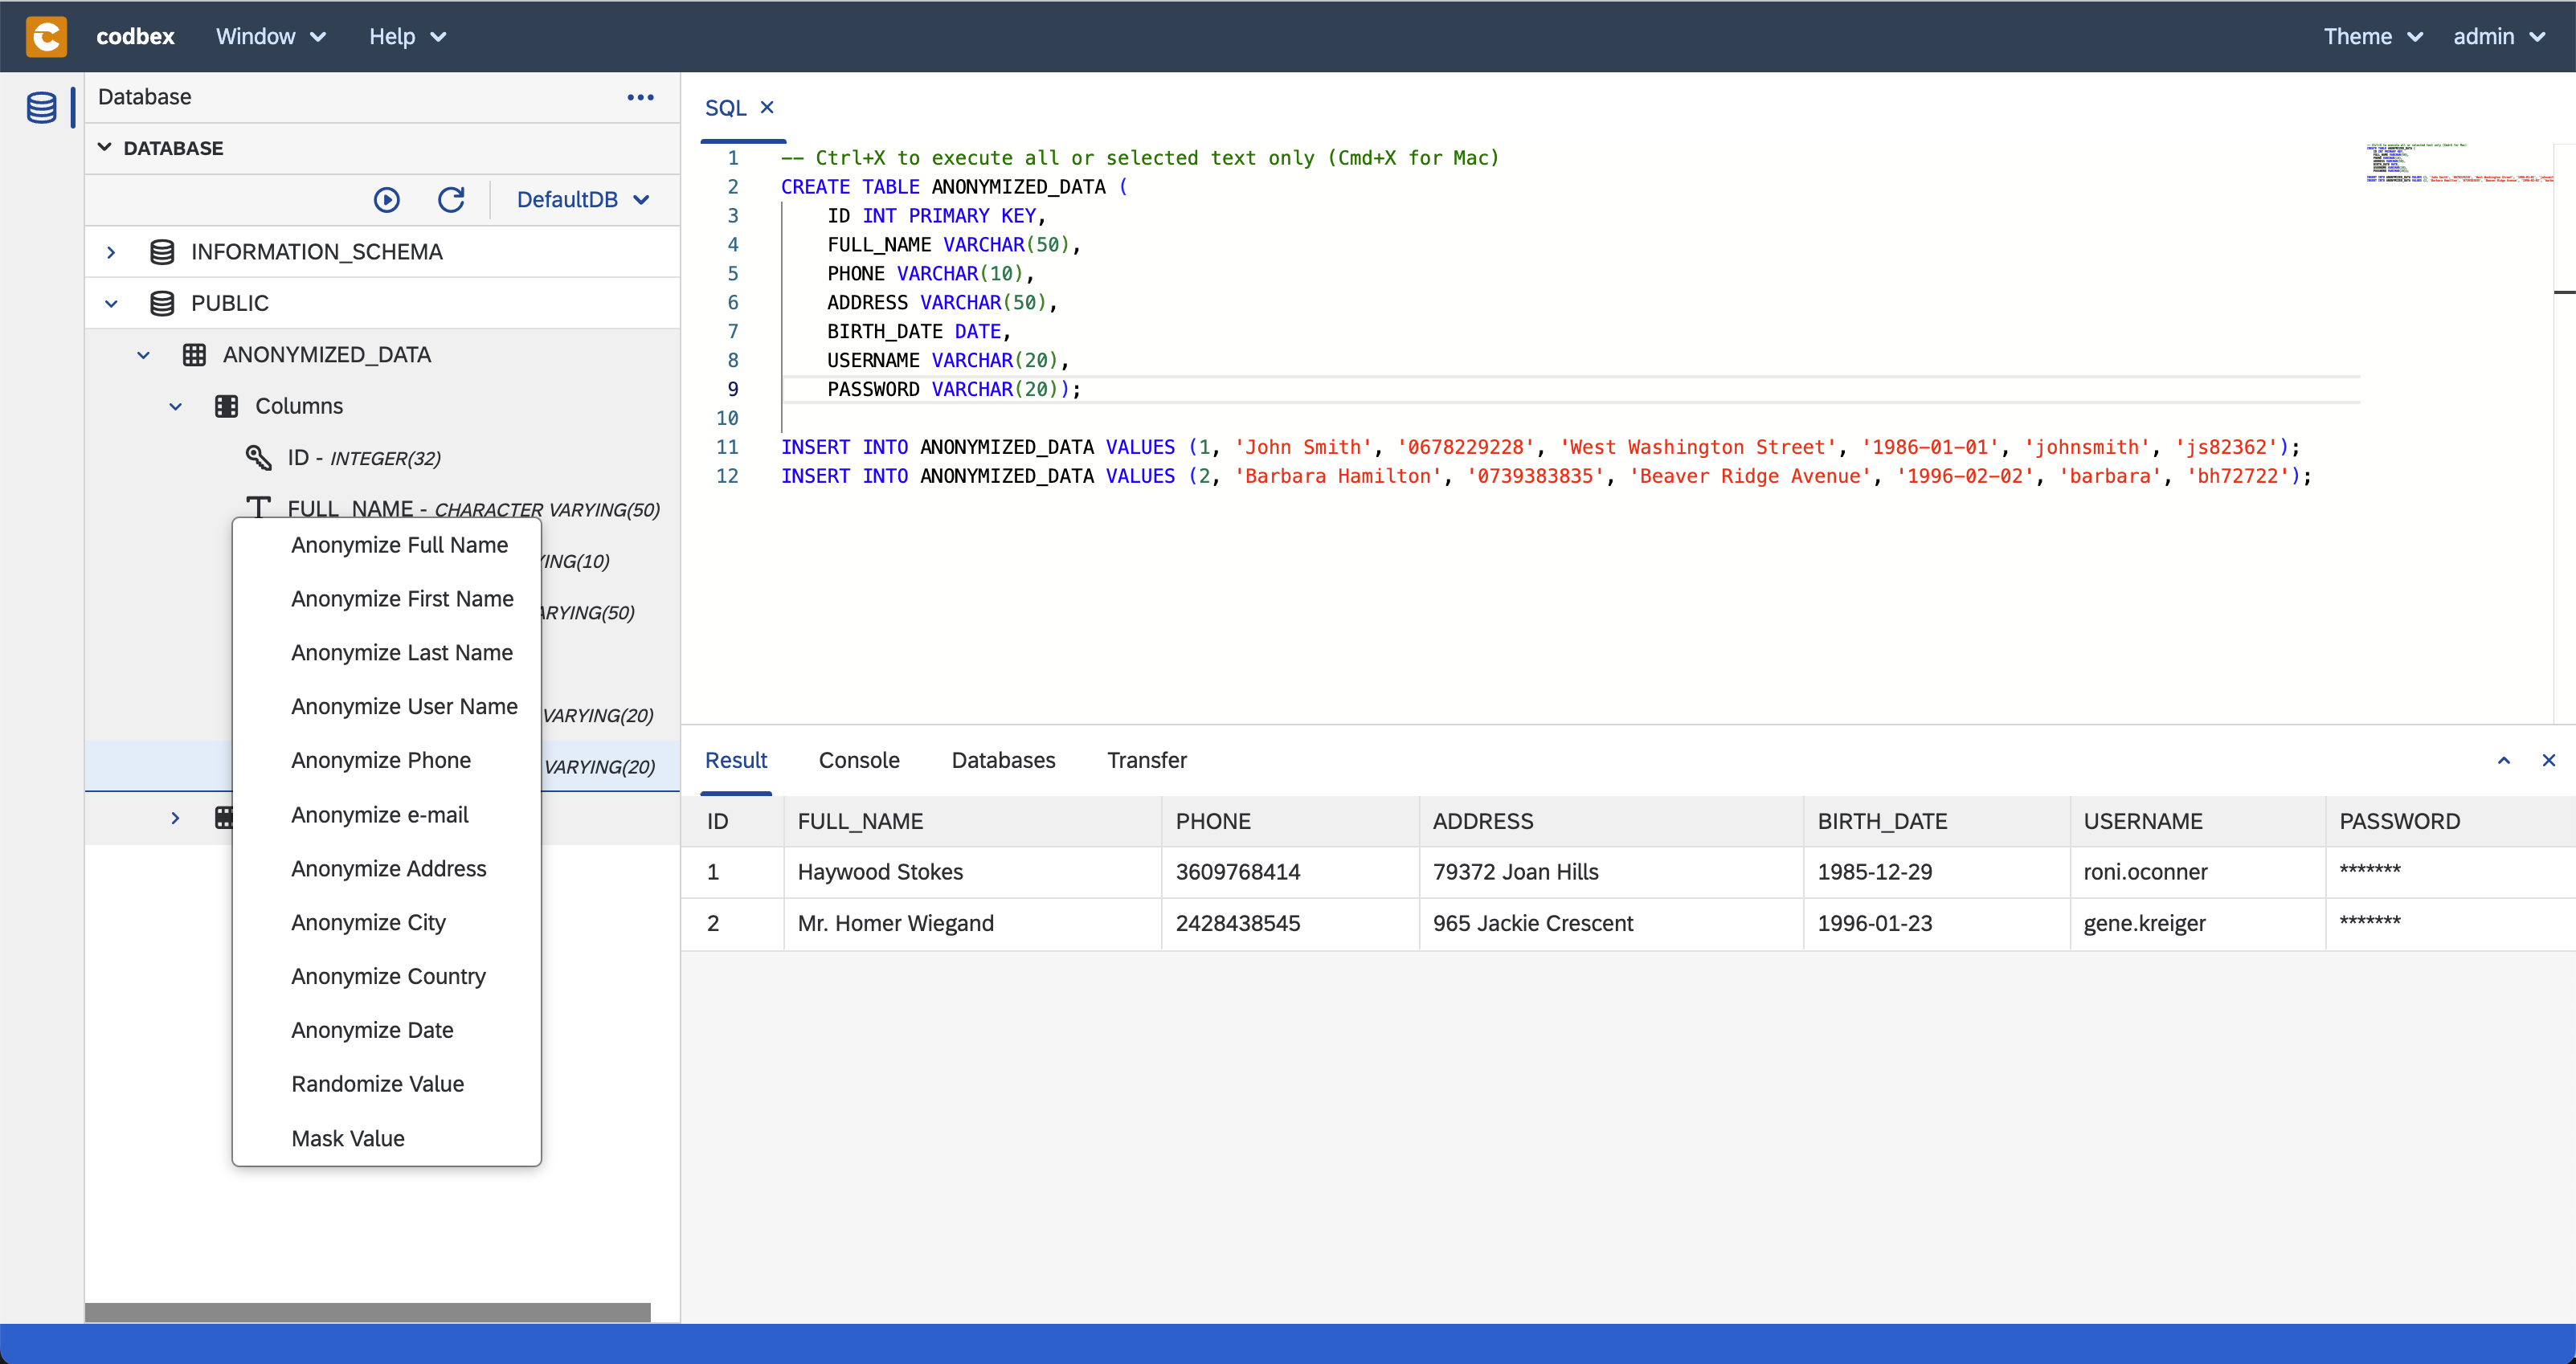
Figure 2: Screenshots When implementing an application that uses Queryable Encryption, consider the points listed in Security Considerations. To learn which MongoDB server products and drivers support Queryable Encryption, see Compatibility. Enabling Queryable Encryption on a collection redacts fields from some diagnostic commands and omits some operations from the query log. This limits the data available to MongoDB support engineers, especially when analyzing query performance. To measure the impact of operations against encrypted collections, use a third party application performance monitoring tool to collect metrics.
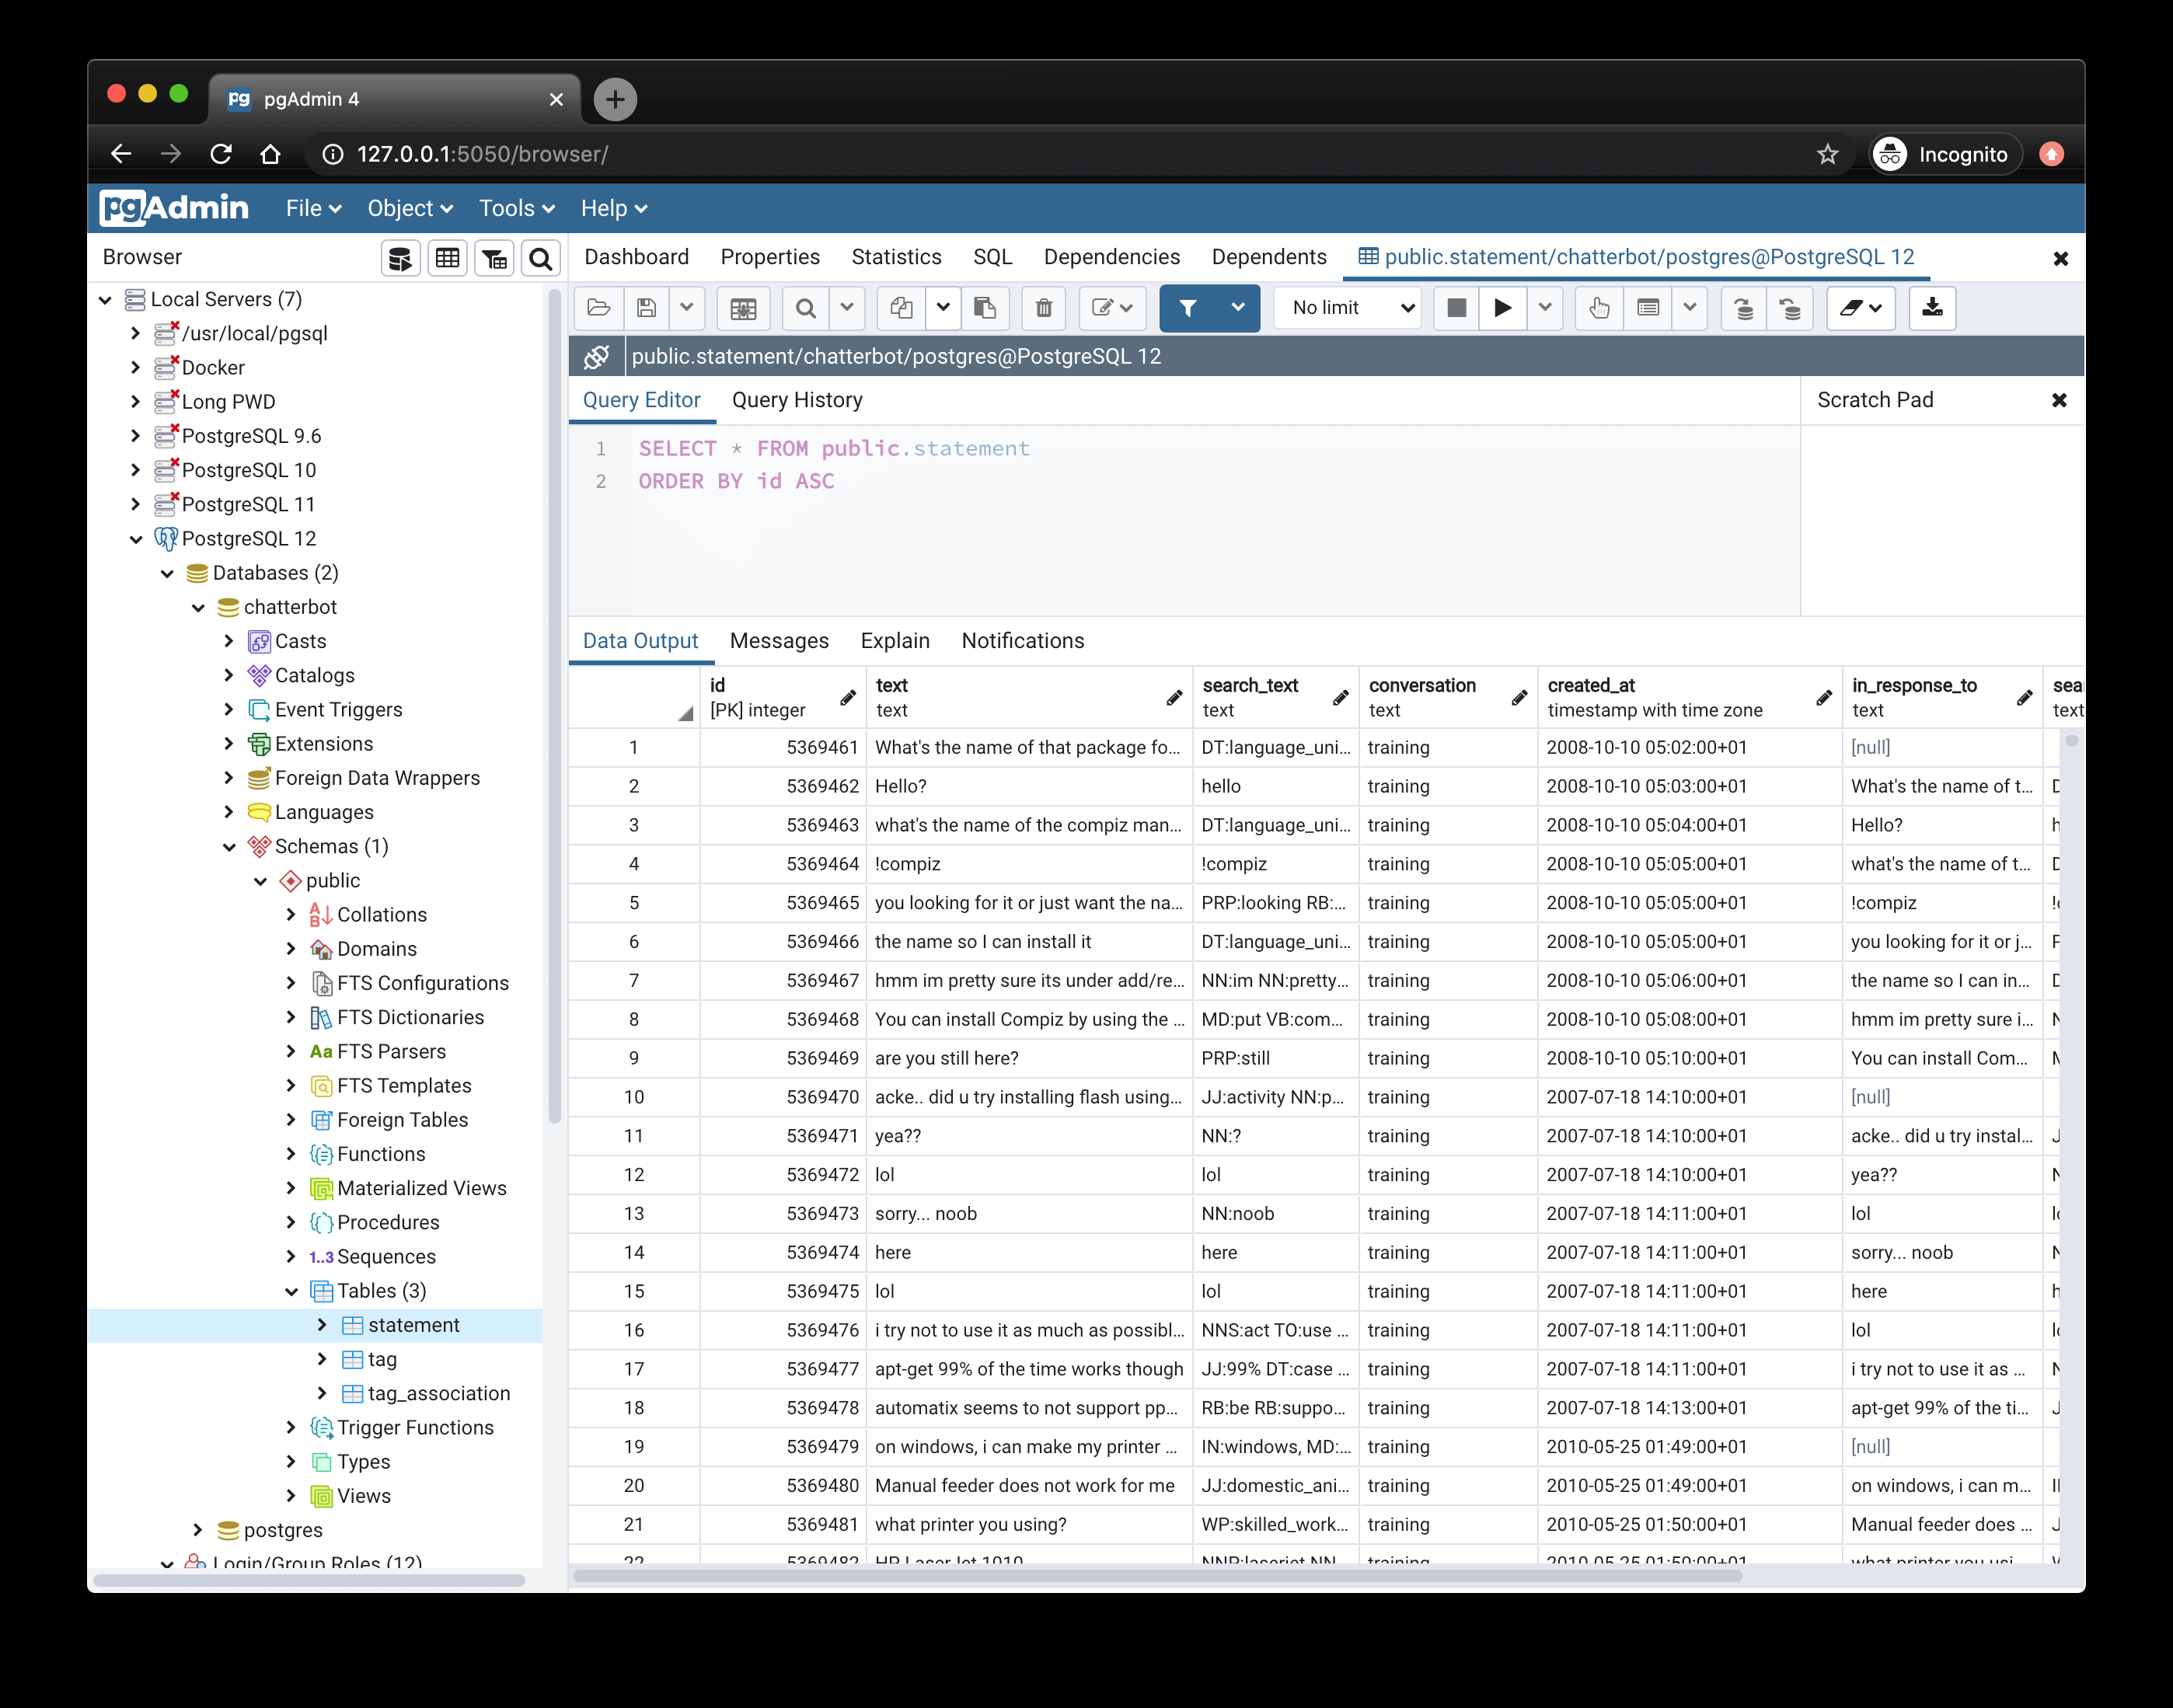
To learn about the security benefits of Queryable Encryption for your applications, see the Queryable Encryption Features page. Figure 3: Explore and Manage Databases in the Cloud To learn what you must install to use Queryable Encryption, see the Install a Queryable Encryption Compatible Driver and Dependencies and Install and Configure a Query Analysis Component pages.
To learn how Queryable Encryption works, see the Queryable Encryption Fundamentals section, which contains the following pages: To learn how to perform specific tasks with Queryable Encryption, see the Queryable Encryption Tutorials section. Access to this page requires authorization. You can try signing in or changing directories .
Always Encrypted is designed to safeguard sensitive information, including credit card numbers and national or regional identification numbers (such as U.S. social security numbers), in Azure SQL Database, Azure SQL Managed Instance, and SQL Server databases. Always Encrypted with secure enclaves expands the confidential computing capabilities of Always Encrypted by enabling in-place encryption and richer confidential queries. Always Encrypted with secure enclaves is available in SQL Server 2019 (15.x) and later, and in Azure SQL Database. You can encrypt sensitive data within client applications, ensuring that encryption keys are never exposed to the Database Engine. This approach provides a separation between those who own the data and can view it, and those who manage the data but should have no access: on-premises database administrators, cloud database operators, or other high-privileged unauthorized users. As a result, Always Encrypted allows customers to securely store their sensitive data in the cloud, reducing the risk of data theft by malicious insiders.
Always Encrypted has certain restrictions, such as the inability to perform operations on encrypted data, including sorting and filtering (except for point-lookups using deterministic encryption). This limitation means that some queries and applications might not be compatible with Always Encrypted or might require significant changes to the application logic. To address these limitations, Always Encrypted with secure enclaves enables the database engine to process encrypted data within a protected memory area called a secure enclave. Secure enclaves enhance the confidential computing capabilities of Always Encrypted by supporting pattern matching, various comparison operators, and in-place encryption.
Always Encrypted ensures that encryption is seamless for applications. On the client, the Always Encrypted-enabled driver encrypts sensitive data before sending it to the Database Engine and automatically rewrites queries to maintain application semantics. It also automatically decrypts query results from encrypted database columns. For applications that need to perform pattern matching, use comparison operators, sort, and index on encrypted columns, implement Always Encrypted with secure enclaves .
This section provides an overview of setting up Always Encrypted. For details and to get started, see Tutorial: Getting started with Always Encrypted . Provision cryptographic keys to protect your data . Always Encrypted uses two types of keys: A column encryption key encrypts the data within an encrypted column. A column master key is a key-protecting key that encrypts one or more column encryption keys.
Store column master keys in a trusted key store outside of the database system, such as Azure Key Vault , Windows certificate store , or a hardware security module. After this step, provision column encryption keys and encrypt each key with a column master key. Finally, save the metadata about the keys in your database. The column master key metadata includes the location of the column master key. The column encryption key metadata contains the encrypted value of the column encryption key. The Database Engine doesn't store or use any keys in plaintext.
For more information on managing Always Encrypted keys, see Overview of key management for Always Encrypted . Set up encryption for specific database columns that include sensitive information to ensure protection. This step might require creating new tables with encrypted columns or encrypting the existing columns and data. When configuring encryption for a column, specify details about the encryption algorithm, the column encryption key to safeguard the data, and the type of encryption. Always Encrypted supports two types of encryption: Deterministic encryption always generates the same encrypted value for a given plaintext value. By using deterministic encryption, you can perform point lookups, equality joins, grouping, and indexing on encrypted columns. However, unauthorized users might guess information about encrypted values by examining patterns in the encrypted column, especially if there's a small set of possible encrypted values, such as True/False, or North/South/East/West region.
Randomized encryption uses a method that encrypts data unpredictably. Each identical plaintext input results in a distinct encrypted output. This method improves the security of randomized encryption. To perform pattern matching by using comparison operators, sorting, and indexing on encrypted columns, adopt Always Encrypted with secure enclaves and apply randomized encryption. Always Encrypted ( without secure enclaves ) randomized encryption doesn't support searching, grouping, indexing, or joining on encrypted columns. Instead, for columns intended for search or grouping purposes, you must use deterministic encryption. This encryption type allows operations such as point lookups, equality joins, grouping, and indexing on encrypted columns.
Since the database system by design has no access to cryptographic keys, any column encryption requires moving and encrypting data outside of the database. The encryption process can take a long time and is vulnerable to network interruptions. Additionally, if you need to re-encrypt a column later, such as when rotating the encryption key or changing encryption types, you encounter the same difficulties again. Using Always Encrypted with secure enclaves eliminates the necessity of moving data out of the database. Because the enclave is trusted, a client driver within your application or a tool like SQL Server Management Studio (SSMS) can safely share the keys with the enclave during cryptographic operations. The enclave can then encrypt or re-encrypt columns in place, significantly decreasing the time required for these actions.
For details on Always Encrypted cryptographic algorithms, see Always Encrypted cryptography . To ensure Always Encrypted keys and protected sensitive data are never revealed in plaintext to the database environment, the Database Engine can't be involved in key provisioning and data encryption or decryption operations. Therefore, Transact-SQL (T-SQL) doesn't support key provisioning or cryptographic operations. For the same reason, encrypting existing data or re-encrypting it (with a different encryption type or a column encryption key) needs to be performed outside of the database (SQL tools can automate that).
After changing the definition of an encrypted column, execute sp_refresh_parameter_encryption to update the Always Encrypted metadata for the object. You can't perform computations on columns encrypted with randomized encryption. Deterministic encryption supports the following operations that involve equality comparisons. No other operations are allowed: For applications that need to perform pattern matching, use comparison operators, sort, and index on encrypted columns, implement Always Encrypted with secure enclaves .
You can't use query statements that trigger computations involving both plaintext and encrypted data. For example: Applications need to use query parameters to provide values for encrypted columns. For example, when you're inserting data into encrypted columns or filtering them by using deterministic encryption, use query parameters. Passing literals or T-SQL variables that correspond to encrypted columns isn't supported. For more information specific to a client driver you're using, see Develop applications using Always Encrypted .
In SSMS , it's essential to apply parameterization for Always Encrypted variables to execute queries that handle values associated with encrypted columns. This requirement includes scenarios such as inserting data into encrypted columns or applying filters on them (in cases where deterministic encryption is used). 2. System Architecture & Core Working Principles Stretch Database is deprecated in SQL Server 2022 (16.x) and Azure SQL Database. This feature will be removed in a future version of the Database Engine. Avoid using this feature in new development work, and plan to modify applications that currently use this feature.
Always Encrypted uses the following Transact-SQL statements, system catalog views, system stored procedures, and permissions. The VIEW ANY COLUMN MASTER KEY DEFINITION and VIEW ANY COLUMN ENCRYPTION KEY DEFINITION permissions are required when selecting encrypted columns. These permissions protect the columns even if the user doesn't have permission to the column master keys in their key stores, and they prevent access to plaintext.
In SQL Server, the public fixed database role grants both VIEW ANY COLUMN MASTER KEY DEFINITION and VIEW ANY COLUMN ENCRYPTION KEY DEFINITION permissions by default. A database administrator might choose to revoke or deny these permissions to the public role and grant them to specific roles or users to implement more restricted control. In SQL Database, the public fixed database role doesn't grant the VIEW ANY COLUMN MASTER KEY DEFINITION and VIEW ANY COLUMN ENCRYPTION KEY DEFINITION permissions by default. This change enables certain existing legacy tools that use older versions of DacFx to work properly. To work with encrypted columns (even if not decrypting them), a database administrator must explicitly grant the VIEW ANY COLUMN MASTER KEY DEFINITION and VIEW ANY COLUMN ENCRYPTION KEY DEFINITION permissions.
Access to this page requires authorization. You can try signing in or changing directories . This tutorial shows you how to get started with Always Encrypted . The tutorial covers: If you're looking for information on Always Encrypted with secure enclaves , see the following tutorials instead: Microsoft recommends using PowerShell 7 or later when running Always Encrypted PowerShell scripts. PowerShell 7 provides improved cross-platform support, better performance, and the latest compatibility with the SqlServer module (v22+), which is required for many Always Encrypted scenarios.
In this step, you'll create the HR schema and the Employees table. Then, you'll populate the table with some data. Connect to your database. For instructions on how to connect to a database from SSMS, see Quickstart: Connect and query an Azure SQL Database or an Azure SQL Managed Instance using SQL Server Management Studio (SSMS) or Quickstart: Connect and query a SQL Server instance using SQL Server Management Studio (SSMS) .
Paste in and execute the below statements to add a few employee records to the Employees table. In a PowerShell session, execute the following commands. Make sure you update the connection string with the address of your server and authentication settings that are valid for your database. In this step, you'll provision a column master key and a column encryption key for Always Encrypted. Then, you'll encrypt the SSN and Salary columns in the Employees table.
SSMS provides a wizard that helps you easily configure Always Encrypted by setting up a column master key, a column encryption key, and encrypt selected columns. Right-click the Employees table and select Encrypt Columns to open the Always Encrypted wizard. On the Master Key Configuration page, configure a new column master key that will be generated by the wizard. First, you need to select where you want to store your column master key. The wizard supports two key store types: In general, Azure Key Vault is the recommended option, especially if your database is in Azure.
Leave the default selection of Current User - this will instruct the wizard to generate a certificate (your new column master key) in the Current User store. On the In-Place Encryption Settings page, no additional configuration is required because the database does not have an enclave enabled. Select Next .
On the Run Settings page, you're asked if you want to proceed with encryption or generate a PowerShell script to be executed later. Leave the default settings and select Next . On the Summary page, the wizard informs you about the actions it will execute. Check all the information is correct and select Finish .
On the Results page, you can monitor the progress of the wizard's operations. Wait until all operations complete successfully and select Close . Expand ContosoHR > Security > Always Encrypted Keys to explore the metadata objects for the column master key and the column encryption that the wizard created.
You can also run the below queries against the system catalog views that contain key metadata. In Object Explorer , right-click the Employees table and select Script Table as > CREATE To > New Query Editor Window . This will open a new query window with the CREATE TABLE statement for the Employees table. Note the ENCRYPTED WITH clause that appears in the definitions of the SSN and Salary columns.
You can also run the below query against sys.columns to retrieve column-level encryption metadata for the two encrypted columns. If you're using Azure Key Vault, execute the below commands to create an asymmetric key in your key vault. Make sure you provide the correct ID of your subscription, the name of the resource group containing your key vault, and your key vault name.
If you're using Windows certificate store, execute the below commands to create a certificate in your Current User store. Connect to your database by using the SqlServer PowerShell module. Make sure you provide a valid connection string for your database. Create a column master key metadata object that references the physical column master key you created in your key store.
Generate a column encryption key, encrypt it with the column master key you've created, and create a column encryption key metadata object in the database. Encrypt SSN and Salary columns in the Employees Table. Choose deterministic encryption for the SSN column and randomized encryption for the Salary column. Deterministic encryption supports queries, such as point lookup searches that involve equality comparisons on encrypted columns. Randomized encryption doesn't support any computations on encrypted columns.
Run the below commands to query system catalog views that contain metadata about the column master key and the column encryption key that you created. Run the below commands to query sys.columns to retrieve column-level encryption metadata for the two encrypted columns. Paste in and execute the following query. The query should return binary encrypted data.
Rerun the same query. Since you're connected with Always Encrypted enabled for your database connection, the client driver in SSMS will attempt to decrypt data stored in both encrypted columns. If you use Azure Key Vault, you may be prompted to sign into Azure. Enable Parameterization for Always Encrypted . This feature allows you to run queries that filter data by encrypted columns (or insert data to encrypted columns).
Paste in and execute the below query, which filters data by the encrypted SSN column. The query should return one row containing plaintext values. Optionally, if you're using Azure Key Vault configured with the access policy permissions model, follow the below steps to see what happens when a user tries to retrieve plaintext data from encrypted columns without having access to the column master key protecting the data.
Connect to your database with Always Encrypted disabled and run a query to read data from encrypted columns. The query should return encrypted data as binary arrays. 3. Software Implementation, Frameworks & Protocols Connect to your database with Always Encrypted enabled and run a query to read data from encrypted columns. Since you have access to the column master key protecting your encrypted columns, the query should return plaintext data.
Invoke-SqlCmd doesn't support queries that can filter by or insert data to encrypted columns. Such queries need to be parameterized, and Invoke-SqlCmd doesn't support parameterized queries. Data security is a serious concern when we migrate data to a cloud DBMS. Database encryption, where sensitive columns are encrypted before they are stored in the cloud, has been proposed as a mechanism to address such data security concerns.
The intuitive expectation is that an adversary cannot “learn” anything about the encrypted columns, since she does not have access to the encryption key. However, query processing becomes a challenge since it needs to “look inside” the data. This tutorial explores the space of designs studied in prior work on processing queries over encrypted data. We cover approaches based on both classic client-server and involving the use of a trusted hardware module where data can be securely decrypted.
We discuss the security challenges that arise in both approaches and how they may be addressed. Briefly, supporting the full complexity of a modern DBMS including complex queries, transactions and stored procedures leads to significant challenges that we survey. Access to this page requires authorization. You can try signing in or changing directories .
Azure SQL Database is a fully managed platform as a service (PaaS) database engine that handles most database management functions, such as upgrading, patching, backups, and monitoring, without user involvement. Because it often stores critical business data, including customer records, financial information, and intellectual property, securing your Azure SQL Database is essential to protect against data breaches, unauthorized access, and compliance violations.
This article provides security recommendations to help protect your Azure SQL Database deployment. The security recommendations in this article implement Zero Trust principles: "Verify explicitly", "Use least privilege access", and "Assume breach". For comprehensive Zero Trust guidance, see the Zero Trust Guidance Center . Because Azure SQL Database is a managed PaaS engine, Microsoft hardens the operating system and infrastructure. Your responsibility centers on reducing the application and data surface exposed to attack and on detecting threats early.
Run SQL vulnerability assessments : Use SQL vulnerability assessment to discover, track, and remediate potential database misconfigurations and vulnerabilities. Schedule recurring scans and act on the baseline it establishes. For more information, see SQL vulnerability assessment . Protect against SQL injection : Use parameterized queries and stored procedures in your applications, and never concatenate user input into SQL statements. SQL injection remains one of the most common attack vectors against database applications.
For more information, see SQL injection . Apply defense in depth : Combine network isolation, identity controls, data protection, and monitoring so that no single control is a single point of failure. For more information, see Playbook for addressing common security requirements . Network security for Azure SQL Database helps prevent unauthorized connections and reduces exposure to attacks so that only trusted sources can reach your databases.
Use private endpoints : Connect to your Azure SQL Database over private IP addresses by using Azure Private Link to avoid exposing your database to the public internet. Private connectivity reduces the attack surface and the risk of data exfiltration. For more information, see Azure Private Link for Azure SQL Database . Disable public network access : When you rely on private endpoints, disable public network access entirely so all connections route through the private endpoint. For more information, see Deny public network access .
Configure server-level firewall rules : Control access to your logical server in Azure with IP firewall rules that specify which addresses or ranges can connect, following the principle of least privilege. For more information, see Azure SQL Database and Azure Synapse IP firewall rules . Configure database-level firewall rules : For more granular control, configure database-level firewall rules that apply to individual databases, enabling per-database access policies. For more information, see Database-level IP firewall rules .
Restrict traffic to specific virtual networks : Use virtual network rules to allow traffic only from specific subnets within your Azure virtual networks, adding network isolation beyond IP-based rules. For more information, see Virtual network rules for Azure SQL Database . Set the minimum TLS version : Configure the logical server's minimum TLS version to 1.2 or higher so connections that use older, weaker protocols are rejected. For more information, see Minimum TLS version .
Choose an appropriate connection policy : Use the Proxy connection policy when you want all traffic to flow through the gateway on a single port instead of exposing the range of back-end node ports, and use Redirect for lower latency from within Azure. Understand the tradeoffs before overriding the default. For more information, see Azure SQL Database connectivity architecture .
Strong identity and authentication controls limit access to your Azure SQL Database resources to authorized users and applications, with centralized identity management and easier account lifecycle control. Configure a Microsoft Entra admin : Designate a Microsoft Entra administrator for your logical server to enable centralized identity management and advanced authentication policies. For more information, see Configure Microsoft Entra authentication .
Use Microsoft Entra authentication : Prefer Microsoft Entra authentication over SQL authentication for centralized identity management and access to features like Conditional Access and multifactor authentication. For more information, see Microsoft Entra authentication . Disable SQL authentication when possible : For maximum security, require all connections to use Microsoft Entra authentication and turn off SQL authentication, eliminating the risk of weak or compromised SQL passwords. For more information, see Microsoft Entra-only authentication .
Create contained database users : Map contained database users to Microsoft Entra identities or groups instead of server-level logins when possible, simplifying permission management and reducing server-level access. For more information, see Contained database users . Enforce multifactor authentication : Require multifactor authentication (MFA) through Conditional Access for the Microsoft Entra identities that administer and connect to the logical server, adding a layer of protection beyond passwords. For more information, see How multifactor authentication works .
Apply Conditional Access policies : Use Conditional Access to control access based on user location, device compliance, and risk, providing adaptive security for each access attempt. For more information, see Conditional access . Use a managed identity for the logical server : Assign a system-assigned or user-assigned managed identity to the logical server so it can reach Azure Key Vault (for TDE customer-managed keys) and Azure Storage (for auditing) without stored secrets. For more information, see Managed identity in Microsoft Entra for Azure SQL .
Enforce strong password policies : If you use SQL authentication, require complex passwords that can't be easily guessed, rotate them regularly, and avoid reusing them across accounts. For more information, see Password policy . Grant least privilege : Give users only the minimum permissions required for their job functions, and review permissions regularly. For more information, see Getting started with database engine permissions .
Separate administrative roles : Avoid granting broad admin rights to all administrators. Use granular permissions and separation of duties across administrative functions. For more information, see Permissions . Assign access with database roles : Use built-in and custom database roles to implement role-based security, assigning users to roles instead of granting individual permissions. For more information, see Database-level roles .
Use Azure RBAC for management operations : Control access to Azure SQL Database management operations with Azure role-based access control, creating custom roles that grant only the permissions needed for specific tasks. For more information, see Azure built-in roles for databases . Provide just-in-time privileged access : Use Microsoft Entra Privileged Identity Management (PIM) to grant time-limited, approval-based access to administrative roles so users hold elevated privileges only when needed. For more information, see Privileged Identity Management .
Monitor privileged activities : Enable auditing to track actions performed by privileged accounts, review the logs for suspicious changes, and alert on sensitive operations. For more information, see Auditing for Azure SQL Database . Data protection safeguards your information through encryption, masking, and classification to prevent unauthorized disclosure, tampering, or loss of sensitive information.
Enable Transparent Data Encryption (TDE) : Encrypt your database, log, and backup files at rest. TDE is enabled by default for new databases; use customer-managed keys in Azure Key Vault for additional control over encryption keys. For more information, see Transparent data encryption (TDE) and TDE with customer-managed keys . Protect sensitive data with Always Encrypted : Use Always Encrypted to protect highly sensitive data in use, at rest, and in transit, so that even administrators can't view plaintext values. Use secure enclaves for richer functionality. For more information, see Always Encrypted .
Create tamper-evident data with ledger : Enable ledger to create an immutable, cryptographically verifiable record of changes to sensitive data, which can help meet regulatory requirements. For more information, see Ledger . Mask sensitive data with dynamic data masking : Apply dynamic data masking to obfuscate sensitive data for nonprivileged users while preserving functionality for applications, without changing application code. For more information, see Dynamic data masking .
Classify and label sensitive data : Use SQL Data Discovery and Classification to identify, classify, and label sensitive data so features like auditing and masking can use the metadata and you can report on where sensitive data resides. For more information, see Data discovery and classification . 4. Practical Deployment, Analysis & Case Studies Restrict access with column-level permissions : Grant or deny permissions at the column level so only users who need a sensitive column can read or modify it. For more information, see GRANT object permissions .
Restrict rows with Row-Level Security (RLS) : Implement RLS so users can access only the data rows relevant to them, providing application-level security ideal for multitenant scenarios. For more information, see Row-Level Security . Comprehensive logging and monitoring help you detect anomalous activity, investigate incidents, and demonstrate compliance for your databases.
Enable Microsoft Defender for SQL : Turn on Microsoft Defender for SQL to detect unusual and potentially harmful attempts to access or exploit your databases, including vulnerability assessment and advanced threat protection. For more information, see Microsoft Defender for SQL . Integrate with Microsoft Defender for Cloud : Use Microsoft Defender for Cloud for centralized security management, security recommendations, and integrated threat protection across your Azure resources. For more information, see Microsoft Defender for SQL in Defender for Cloud .
Configure threat protection alerts : Set up alerts for suspicious activity such as SQL injection attempts, anomalous access patterns, and brute-force authentication, and route notifications to the right recipients. For more information, see Advanced threat protection . Enable auditing : Configure auditing to track database events and write them to a Log Analytics workspace, Azure Storage, or Event Hubs. Audit both server-level and database-level events for full coverage. For more information, see Auditing for Azure SQL Database .
Stream diagnostic logs : Configure diagnostic settings to send logs, including security categories such as SQLSecurityAuditEvents , to Azure Monitor Logs, Event Hubs, or Azure Storage for retention and analysis. For more information, see Monitor Azure SQL Database with Azure Monitor . Review audit logs regularly : Establish a process to review audit logs for suspicious activity, focusing on privileged account actions, failed authentication attempts, and access to sensitive data. For more information, see Auditing for Azure SQL Database .
Governance controls help you demonstrate regulatory compliance and enforce consistent security configurations across your databases. Track regulatory compliance with Microsoft Defender for Cloud : Use the regulatory compliance dashboard to assess your databases against standards such as PCI DSS, ISO 27001, and SOC, and to track remediation of failing controls. For more information, see Regulatory compliance dashboard .
Enforce configurations with Azure Policy : Assign built-in Azure Policy definitions for Azure SQL Database to audit and enforce controls such as TDE, auditing, private endpoints, and Microsoft Entra-only authentication. For more information, see Azure Policy built-in definitions for Azure SQL Database . Govern sensitive data with Microsoft Purview : Register and scan Azure SQL Database in Microsoft Purview to catalog, classify, and govern sensitive data across your data estate. For more information, see Connect to and manage Azure SQL Database in Microsoft Purview .
Apply the Microsoft cloud security benchmark : Use the Microsoft cloud security benchmark as an Azure-wide baseline to prioritize and validate the controls you apply to Azure SQL Database. For more information, see Microsoft cloud security benchmark . Reliable backup and recovery processes protect your data from loss due to failures, disasters, or attacks. They also help you meet your recovery objectives.
Verify automated backup configuration : Confirm that automated backups are configured and that retention meets your requirements. Azure SQL Database provides automated backups by default with configurable retention from 1 to 35 days. For more information, see Automated backups . Configure backup storage redundancy : Choose the backup storage redundancy that matches your availability and disaster recovery needs: locally redundant (LRS), zone-redundant (ZRS), geo-redundant (GRS), or geo-zone-redundant (GZRS). For more information, see Backup storage redundancy .
Use long-term retention for compliance : Configure long-term retention (LTR) to store full backups for up to 10 years when compliance requires retention beyond the default period. For more information, see Long-term retention . Test backup and restore procedures : Regularly test restores to confirm they meet your recovery time objectives and that restored databases are fully functional with intact data. For more information, see Recover a database .
Implement geo-restore for disaster recovery : Use geo-restore to restore a database from geo-redundant backups to any Azure region, protecting against regional outages. For more information, see Geo-restore . Monitor backup activity : Track backup operations and configure alerts for failures by using Azure Monitor. For more information, see Monitor and troubleshoot backup storage consumption .
Database security involves using security measures and techniques to protect databases from unauthorized access, data breaches, data loss and other threats. They help safeguard sensitive information while maintaining the confidentiality, integrity and availability of database systems. Physical security protects database servers and infrastructure from unauthorized physical access, theft, tampering and damage.
Development and testing environments should be separated from production environments to prevent accidental or unauthorized access to production data. Secure connections help protect data exchanged between applications, users and database servers from interception. Database credentials should be stored and managed securely to prevent attackers from obtaining unauthorized access.
SQL injection occurs when attackers insert malicious SQL statements through application inputs. Secure query practices help prevent attackers from manipulating database operations. Regular security testing helps identify vulnerabilities and weaknesses in database systems before attackers can exploit them. Secure database configuration reduces unnecessary exposure and prevents attackers from exploiting weak default settings.
Data masking hides sensitive information while allowing authorized users to work with realistic-looking data. The HIPAA Security Rule is technology-neutral and risk-based. You must safeguard electronic protected health information (ePHI) so its confidentiality, integrity, and availability are preserved. Encryption is an “ addressable ” control, meaning you should implement it when reasonable and appropriate—or document why an alternative, equally effective safeguard is used.
In practice, you should treat strong encryption as the default for all ePHI at rest and in transit. Use the AES-256 Encryption standard for stored data and the TLS 1.2 Protocol or newer for all connections between apps, databases, and integrations. Combine encryption with access controls, audit logging, and incident response so queries touching ePHI are secure, observable, and recoverable.
To keep queries HIPAA-aligned, map your data flows , classify PHI, and decide where to apply encryption: storage-level (e.g., Transparent Data Encryption), application/field-level, and transport-level. Document your risk analysis , policies, and procedures, and ensure Business Associate Agreements (BAAs) cover encryption, key management, and logging expectations.
Adopt proven, widely implemented standards. For data at rest, favor AES-256 Encryption with authenticated modes such as GCM or XTS, implemented via FIPS-validated cryptographic modules. For data in motion, use the TLS 1.2 Protocol or TLS 1.3 with modern cipher suites, certificate pinning where applicable, and strict certificate lifecycle management. For keys and handshakes, use ephemeral key exchange (e.g., ECDHE) and modern curves (such as P-256 or higher).
Hashing should rely on SHA-256 or better, paired with salted, memoryIhard algorithms (e.g., scrypt/Argon2) for secrets. Validate vendor libraries, disable legacy ciphers, and continuously test protocol configurations as part of your secure build pipeline. Transparent Data Encryption (TDE) protects database files, backups, and snapshots without changing application queries. It encrypts pages on write and decrypts on read, so you get broad protection against media loss while your SQL remains the same. TDE does not secure data in memory or over the network, so pair it with TLS for connections and additional controls for granular fields.
Use TDE as your baseline at-rest control. Where teams need to limit what specific users can read inside columns (e.g., SSNs or diagnoses), layer Field-Level Encryption on top. Field-Level Encryption narrows exposure by encrypting only sensitive columns. You decrypt data only when the application genuinely needs it, reducing blast radius from over-privilege or SQL misuse.
Field-Level Encryption complements, not replaces, TDE. Use both to cover storage media, granular access, and insider risk simultaneously. Join thousands of organizations that trust Accountable to manage their compliance needs. 5. Performance Evaluation & Extended Technical Observations Keys are your ultimate crown jewels. Treat them with stricter controls than the data they protect, and centralize lifecycle operations in a KMS.
Encryption prevents disclosure, but only auditing proves appropriate use. Capture who queried what, when, from where, and why—then centralize the evidence. Even perfect encryption fails if everyone can decrypt. Role-Based Access Control (RBAC) confines decrypt rights and query scope to job duties, tightening the loop around PHI.
Bringing it all together, you can run encrypted queries confidently by combining TDE for broad atIrest protection, Field-Level Encryption for sensitive columns, AES-256 Encryption and the TLS 1.2 Protocol for strong cryptography, KMSIbacked key lifecycle controls, SIEMIdriven visibility, and strict RBAC. The result is resilient, auditable access to PHI without sacrificing clinical performance.
HIPAA does not mandate specific algorithms; it requires safeguards appropriate to your risks. In healthcare, the de facto standards are AES-256 Encryption for data at rest and the TLS 1.2 Protocol or newer for data in transit, implemented with FIPSIvalidated cryptographic modules and documented in your security policies . Transparent Data Encryption (TDE) encrypts database files and backups automatically, so most applications require no code changes. It reduces exposure from lost media or snapshots and centralizes key control. Because TDE doesn’t protect data in memory or on the wire—or limit what privileged users can query—you should pair it with Field-Level Encryption and TLS.
Manage keys in a Key Management Service (KMS) with envelope encryption, HSMIbacked master keys, strict leastIprivilege policies, and audited change control. Rotate keys on a schedule, rewrap data keys transparently, isolate duties between DB and KMS admins, secure key backups, and test recovery and revocation procedures regularly. Comprehensive audit logs prove that PHI access is appropriate and controlled. Capture query activity, authentication events, privilege changes, and key operations; forward them to a Security Information and Event Management (SIEM) platform for correlation, alerting, immutable retention, and regular review during security and compliance audits.
Join thousands of organizations that trust Accountable to manage their compliance needs. Strong dental compliance training protects patients, your team, and your practice. This guide tur... Choosing among HIPAA-compliant telehealth tools comes down to how well each platform fits your cl... You rely on cloud storage to keep Protected Health Information (PHI) available and secure, yet a ...
As cloud computing gains traction, data owners are outsourcing their data to cloud service providers (CSPs) for Database Service (DBaaS), bringing in a deviation of data ownership and usage, and intensifying privacy concerns, especially with potential breaches by hackers or CSP insiders. To address that, encrypted database services propose encrypting every tuple and query statement before submitting to the CSP, ensuring data confidentiality when the CSP is honest-but-curious, or even compromised. Existing solutions either employ property preserving cryptography schemes, which can perform certain operations over ciphertext without decrypting the data over the CSP, or utilize trusted execution environment (TEE) to safeguard data and computations from the CSP. Based on these efforts, we introduce Enc2DB, a novel secure database system, following a hybrid strategy on PostgreSQL and openGauss. We present a micro-benchmarking test and self-adaptive mode switch strategy that can dynamically choose the best execution path (cryptography or TEE) to answer a given query.
Besides, we also design and implement a ciphertext index compatible with native cost model and query optimizers to accelerate query processing. Empirical study over TPC-C test justifies that Enc2DB outperforms pure TEE and cryptography solutions, and our ciphertext index implementation also outperforms the state-of-the-art cryptographic-based system. Cloud computing has become an essential infrastructure for efficient data management systems. Migrating workloads to the cloud brings many advantages, such as lower cost, higher flexibility, greater scalability, higher reliability and so on. More and more enterprises and institutions are tending to rely on third-party database service providers for storing and managing their data services.
However, while storage and computing in the cloud bring great convenience, the deviation of data ownership and usage also brings privacy risks that can not be ignored. When users outsource data to cloud service providers (CSP), they lose physical control over data. The security and privacy of data depend on the security policy provided by the CSP. If the security policies are breached by external hackers or even rogue employees from the CSP itself, users’ sensitive data can be leaked, seriously compromising data security and privacy.
To ensure confidentiality, data can be kept encrypted over the CSP. Traditional data encryption [ 6 , 40 ] preserves confidentiality of data at rest. Securing data at rest allows users to utilize cloud storage without exposing sensitive information, but it prevents users from performing SQL queries effectively or efficiently. A possible solution to this problem is homomorphic encryption, which can provide data operability while preserving data confidentiality. The fully homomorphic encryption (FHE) [ 18 ] scheme allows algebraic computations over encrypted data, but it suffers from high overhead for complex analytical queries. Partially homomorphic encryption (PHE) [ 35 ] allows computations over encrypted data with respect to some specific operations and have practical performance.
Property-Preserving Encryption (PPE) [ 30 ] can preserve some attributes of plaintext data, such as comparisons. Another alternative is to utilize trusted execution environment to ensure the confidentiality of data. The trusted execution environment (TEE) [ 37 ] constructs a secure area in the CPU (called an enclave) through software and hardware methods, ensuring that the programs and data loaded inside are protected in terms of confidentiality and integrity. Therefore, the encrypted data can be decrypted and calculated in TEE, such that the OS knows nothing about the content inside. Due to recent advancements in TEE, many enclave-based encrypted databases and storage systems have emerged [ 5 , 8 , 16 , 21 , 24 , 34 , 42 , 45 , 39 ] . For example, EnclaveDB [ 34 ] protects the confidentiality and integrity of data and queries by placing sensitive data (tables, indexes and other metadata) in enclaves protected by trusted hardware (such as SGX).
In this paper, we propose a hybrid and adaptive encryption query processing solution, namely Enc 2 DB, implemented in our openGauss, an open-source database proposed by Huawei, as well as in PostgreSQL. Based on the cryptography technologies such as symmetric PHE, order preserving encryption (OPE), and AES we establish the ciphertext storage model of relational database and the corresponding query processing framework. Enc 2 DB proposes a hybrid solution make use of both software (cryptography) and hardware (TEE) to improve the efficiency of ciphertext data query, and realizes the fully encrypted storage and execution of query workload, as well as the transparent processing of user-side query requests. Our main contributions are as follows: We use full ciphertext-based storage, support user defined column-level choice of plaintext or ciphertext state.
We propose a ciphertext-aware indexing mechanism over ORE, to further improve query efficiency. We combine SGX with software-only solutions and propose a hybrid self-adaptive strategy towards range queries. In the rest of the paper, we first present background information and related work in section 2 and then explores system architecture in section 3 , as well as the implementation details of software and TEE-enabled modes. In section 4 , we introduce a series of optimizations. Empirical study is provided in section 5 , and we conclude in section 6 .
Homomorphic encryption is proposed for mathematical calculation of ciphertext without obtaining the key. According to the types of ciphertext calculation, it can be divided into FHE and PHE. FHE allows any algebraic operation on encrypted data, and the result obtained after decryption preserves the calculation result. In 2009, Gentry [ 18 ] implemented the first fully homologous encryption scheme. Although over the years, the algorithm of FHE has experienced significant improvement in the aspect of efficiency, it is impractical for real-world usage. In comparison, PHE only supports limited types of ciphertext calculation, but provide practical efficiency. PHE is mainly divided into additive homomorphic encryption (AHE) and multiplicative homomorphic encryption (MHE). Examples of AHE include Paillier [ 29 ] , benaloh [ 17 ] , Okamoto–Uchiyama [ 27 ] , Naccache stern [ 25 ] , Damgård-Jurik [ 14 ] ,etc. Examples of MHE include ElGamal [ 15 ] and RSA [ 36 ] . At present, we adopt the state-of-the-art symmetric AHE and MHE solution, namely SAHE and SMHE proposed in Symmetria [ 38 ] . They retain the full range of homomorphic operations that asymmetric schemes support while offering the same level of security (semantic security, (IND-CPA)).
For operations such as range queries involving comparisons that HE cannot support, we turn to the Property Preserving Encryption (PPE), which has been used in systems such as CryptDB [ 33 ] , Monomi [ 40 ] and Seabed [ 31 ] . The ciphertext of the PPE scheme retains some attributes of the plaintext. For the same plaintext data, the ciphertext encrypted by deterministic encryption (DET) is also the same. There are other schemes that can preserve the order relationship of the underlying plaintext values, which is called Order Preserving Encryption (OPE) [ 4 ] . The relative order of the plaintext values can be directly obtained by comparing the encrypted values. Boldyreava [ 9 ] proposes an attribute-preserving encryption scheme, but it’s a deterministic scheme that preserves frequency information of plaintext data.
At present, the Order-Revealing Encryption scheme (ORE) [ 10 , 11 , 12 ] and its branch scheme are non-deterministic solutions, which can reveal less information under the premise of guaranteeing higher operation efficiency, thus providing better security than OPE. Trusted Execution Environment(TEE) [ 37 , 44 ] builds a secure area in the central processing unit through software and hardware methods to ensure that the programs and data loaded in it are protected in terms of confidentiality and integrity. The principle of TEE is to divide the hardware and software resources of the system into two execution environments-trusted execution environment and common execution environment. The two environments are securely isolated, with independent internal data paths and storage space required for computing. Applications in a common execution environment cannot access the TEE. Even within the TEE, multiple applications run independently and cannot access each other without authorization. All major CPU vendors have rolled out their TEE ( e.g., ARM TrustZone, Intel SGX, and AMD SEV) to provide a secure execution environment, commonly referred to as an enclave [ 3 , 1 , 20 ] .
Encrypted database systems can employ TEE to preserve the confidentiality in query processing, by decrypting the ciphertext and performing complex calculations over plaintext within TEE. SGX is a representative TEE framework proposed by Intel, which encapsulates the security operations of legitimate software in an enclave to protect it from malware attacks. That is, even the OS or the VMM (Hypervisor) cannot access or affect the code and data inside the enclave.
EnclaveDB [ 34 ] relies on SGX and processes encrypted queries in an enclave, which allows only pre-compiled queries and assumes that all data can fit in the memory. Always encrypted Azure database [ 5 ] uses a few enclave-based defined function for computation over ciphertext. However, such non-intrusive design leads to possible information leakage and performance degradation. FE-in-GaussDB [ 46 ] combines encryption algorithms with TEE to securely perform various operations on ciphertext data, including matching, comparison and etc.
In this section, we introduce the basic structure of Enc 2 DB (Encrypted Database with Enclave), which provides two deployment modes, i.e., software-only and TEE-enabled. To start with, we first propose the software-only mode, namely EncDB (Encrypted Database). After that, we discuss how TEE can co-operate with EncDB by enabling complex tasks to run inside the Enclave, which leads to the second mode, Enc 2 DB (detailed in subsection 3.2 ).
The complete system is divided into two parts: the application server (trusted client) and the untrusted server. Its architecture is shown in Fig. 1 , which includes the following components deployed over both the client and the cloud. Encryption and Decryption Engine: holds the encryption key, encrypts plaintext data, and decrypts the result received from the cloud. The encryption module also generates and stores meta-encryption data, i.e., the mapping of plaintext operators to the relevant ciphertext ones, the supported encryption schemes towards different data types in the database.
Query rewriter: convert plaintext queries into the ones in ciphertext, which are sent through the network to the server. Database Driver: PostgreSQL supports multiple database application programming interfaces (such as libpq, JDBC, ODBC, etc.) to submit query requests. The application driver helps the client to send the rewritten encrypted SQL to the server and receive the encrypted result from the cloud.
Server-side Computing Services: Leverage a set of user-defined functions (UDFs) to perform operations on encrypted data. The pipeline for answering a SQL query under the architecture is as follows: The data provider uploads plaintext data, and the client encrypts each column under one or more encryption schemes according to the expected operations, replacing the original column name with a random string for anonymization. The user enters a plaintext query, which is rewritten and sent to the server in the form of a ciphertext counterpart. The server implements the relevant operation logic for ciphertext calculation in advance, performs query and operation on the encrypted SQL, and returns the obtained encrypted result to the client. The client decrypts the received ciphertext to obtain the plaintext query result. The whole process is completely transparent to the user, and the server is unaware about the content of either the query or the result.
In our software-only implementation mode, a column in a table is to be stored in ciphertext form under one (or more) of AHE, MHE, ORE, and AES. Given a SQL statement, the column names and operands are respectively replaced using desensitized names and ciphertext under a predefined encryption logic. This process takes place at the user’s local trusted end and is deployed by a small connection pool, which has many advantages such as transparency to the upper layers, no client awareness, and easy migration. After receiving the encrypted query statements, the server will perform the relevant ciphertext calculation according to the pre-configured user-defined functions, and finally returns the encrypted query results to the user, and the local trusted end will decrypt and obtain the plaintext results, which is completely transparent to the application.
Advantages . A major benefit of the software-only implementation mode is that it exert no hardware requirement, and it also has less deployment costs. Disadvantages . The obvious disadvantage of the software-only mode is the large redundancy of data, as a data column is copied and encrypted into many ciphertext columns under different encryption schemes, resulting in a huge space and time overhead. In addition, the query work is done using UDFs with a huge computational overhead. Besides, some complex expressions are hard to compute under this mode. For example, none of current encryption schemes can support both addition/multiplication homomorphic and comparison in ciphertext space. For queries containing both operations over the same operands, another round of interaction between the client and server is extraly required. This solution introduces network communication latency, which is unacceptable for a real-time online transaction processing system.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Google%20Cloud%20Platform • https://www.mongodb.com/docs/manual/core/queryable-encryption/ • https://learn.microsoft.com/en-us/sql/relational-databases/security/encryption/always-encrypted-database-engine?view=sql- server-ver17 • https://learn.microsoft.com/en-us/sql/relational-databases/security/encryption/always-encrypted-tutorial-getting-started?view =sql-server-ver17 • https://www.microsoft.com/en-us/research/publication/querying-encrypted-data-tutorial/ • https://learn.microsoft.com/en-us/azure/azure-sql/database/secure-database?view=azuresql • https://www.geeksforgeeks.org/blogs/database-security-practices/ • https://www.accountablehq.com/post/how-to-run-encrypted-database-queries-in-healthcare-hipaa-compliant-methods-and-b est-practices • https://arxiv.org/html/2404.06819v1
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Encrypted Database Querying System In Cloud Using Python.
[*] Metasploit Scan Running on Target Subnet for Encrypted Database Querying System In Cloud Using Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |