Complete Technical Paper Content — Encrypted Log Search Mechanism
Overview & System Context
Encrypted Log Search Mechanism: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9502 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background An HTTP cookie (also called web cookie, Internet cookie, browser cookie, or simply cookie) is a small block of data created by a web server while a user is browsing a website and placed on the user's computer or other device by the user's web browser.
Cookies are placed on the device used to access a website, and more than one cookie may be placed on a user's device during a session. Cookies serve useful and sometimes essential functions on the web. They enable web servers to store stateful information (such as items added in the shopping cart in an online store) on the user's device or to track the user's browsing activity (including clicking particular buttons, logging in, or recording which pages were visited in the past). They can also be used to save information that the user previously entered into form fields, such as names, addresses, passwords, and payment card numbers for subsequent use. Authentication cookies are commonly used by web servers to authenticate that a user is logged in, and with which account they are logged in. Without the cookie, users would need to authenticate themselves by logging in on each page containing sensitive information that they wish to access. The security of an authentication cookie generally depends on the security of the issuing website and the user's web browser, and on whether the cookie data is encrypted. Security vulnerabilities may allow a cookie's data to be read by an attacker, used to gain access to user data, or used to gain access (with the user's credentials) to the website to which the cookie belongs (see cross-site scripting and cross-site request forgery for examples). Tracking cookies, and especially third-party tracking cookies, are commonly used as ways to compile long-term records of individuals' browsing histories — a potential privacy concern that prompted European and U.S. lawmakers to take action in 2011. European law requires that all websites targeting European Union member states gain "informed consent" from users before storing non-essential cookies on their device.
A zombie cookie is data and code that has been placed by a web server on a visitor's computer or other device in a hidden location outside the visitor's web browser's dedicated cookie storage location, and that automatically recreates a HTTP cookie as a regular cookie after the original cookie had been deleted. The zombie cookie may be stored in multiple locations, such as Flash Local shared object, HTML5 Web storage, and other client-side and even server-side locations, and when absence is detected in one of the locations, the missing instance is recreated by the JavaScript code using the data stored in other locations.
Name Value Zero or more attributes (name/value pairs). Attributes store information such as the cookie's expiration, domain, and flags (such as Secure and HttpOnly). Tracking cookies are used to track users' web browsing habits. This can also be done to some extent by using the IP address of the computer requesting the page or the referer field of the HTTP request header, but cookies allow for greater precision.
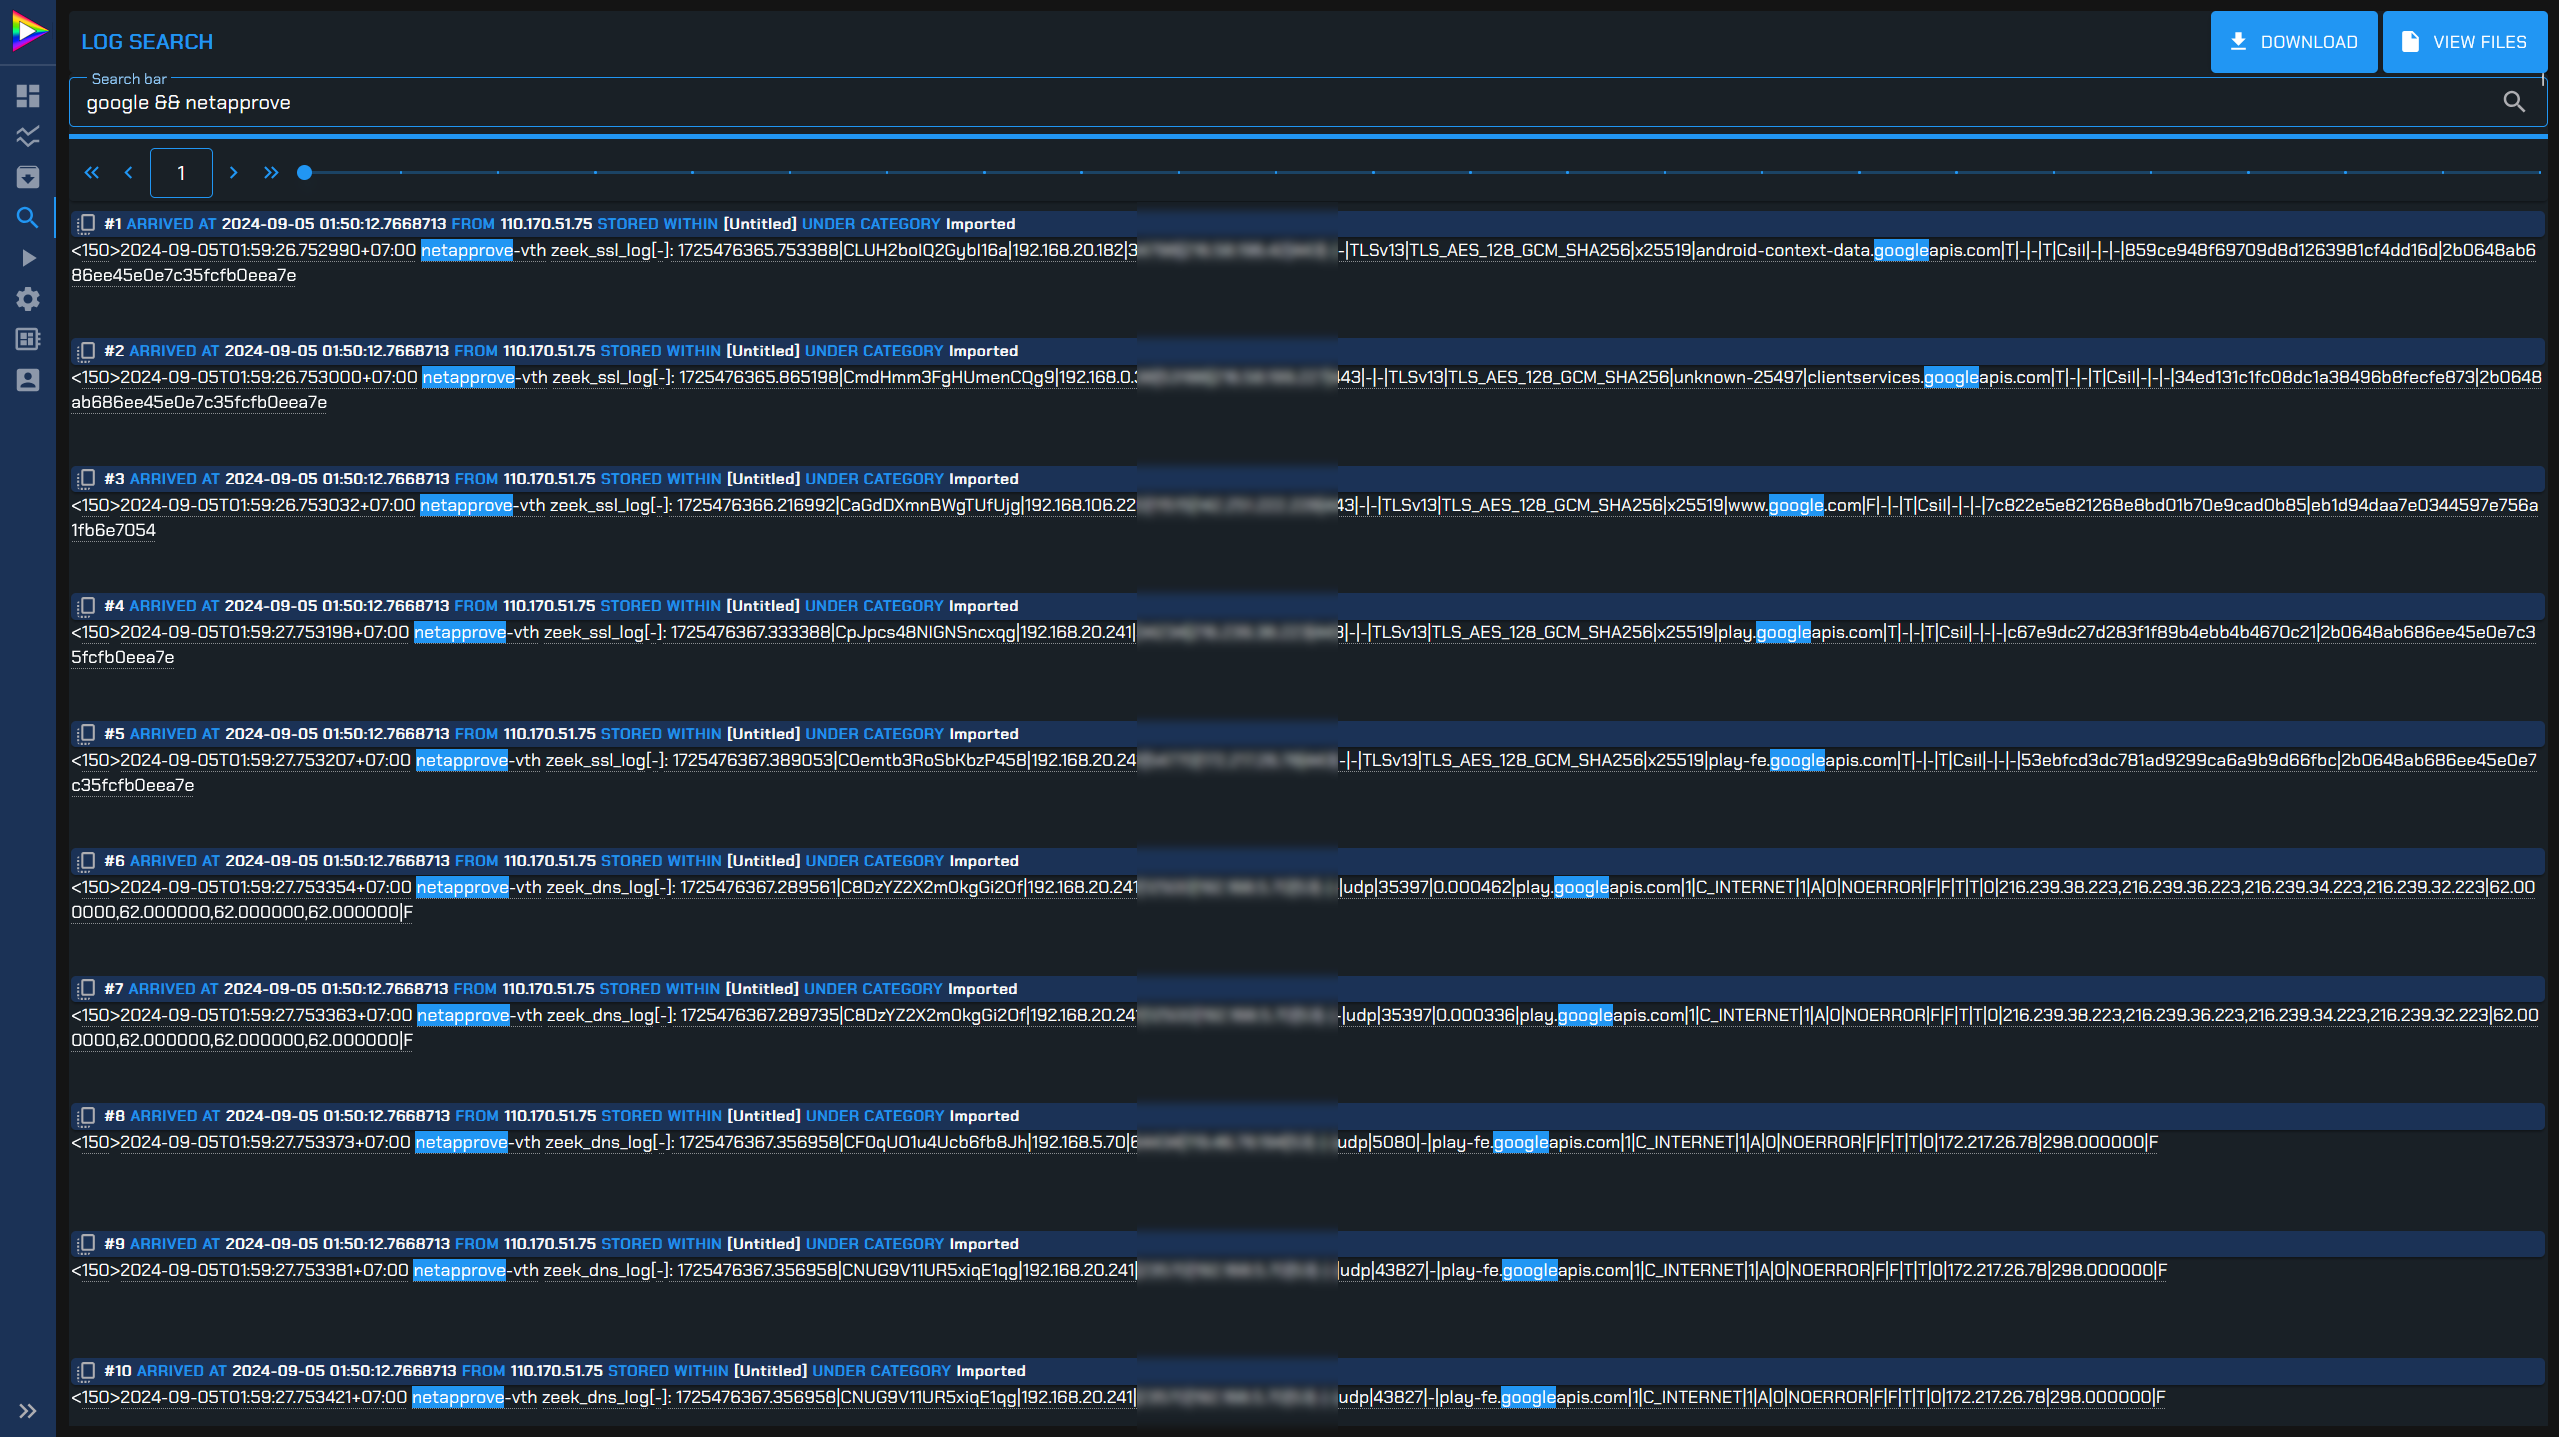
This can be demonstrated as follows: Figure 1: Guywanyatum Pooncharoen - Software Engineer If the user requests a page of the site, but the request contains no cookie, the server presumes that this is the first page visited by the user. So the server creates a unique identifier (typically a string of random letters and numbers) and sends it as a cookie back to the browser together with the requested page. From this point on, the cookie will automatically be sent by the browser to the server every time a new page from the site is requested. The server not only sends the page as usual but also stores the URL of the requested page, the date/time of the request, and the cookie in a log file. By analyzing this log file, it is then possible to discover which pages the user has visited, in what sequence, and for how long. Corporations exploit users' web habits by tracking cookies to collect information about buying habits. The Wall Street Journal found that America's top fifty websites installed an average of sixty-four pieces of tracking technology onto computers, resulting in a total of 3,180 tracking files. The data can then be collected and sold to bidding corporations.
Cookies are arbitrary pieces of data, usually chosen and first sent by the web server, and stored on the client computer by the web browser. The browser then sends them back to the server with every request, introducing states (memory of previous events) into otherwise stateless HTTP transactions. Without cookies, each retrieval of a web page or component of a web page would be an isolated event, largely unrelated to all other page views made by the user on the website. Although cookies are usually set by the web server, they can also be set by the client using a scripting language such as JavaScript (unless the cookie's HttpOnly flag is set, in which case the cookie cannot be modified by scripting languages). The cookie specifications require that browsers meet the following requirements in order to support cookies: Can support cookies as large as 4,096 bytes in size. Can support at least 50 cookies per domain (i.e. per website). Can support at least 3,000 cookies in total.
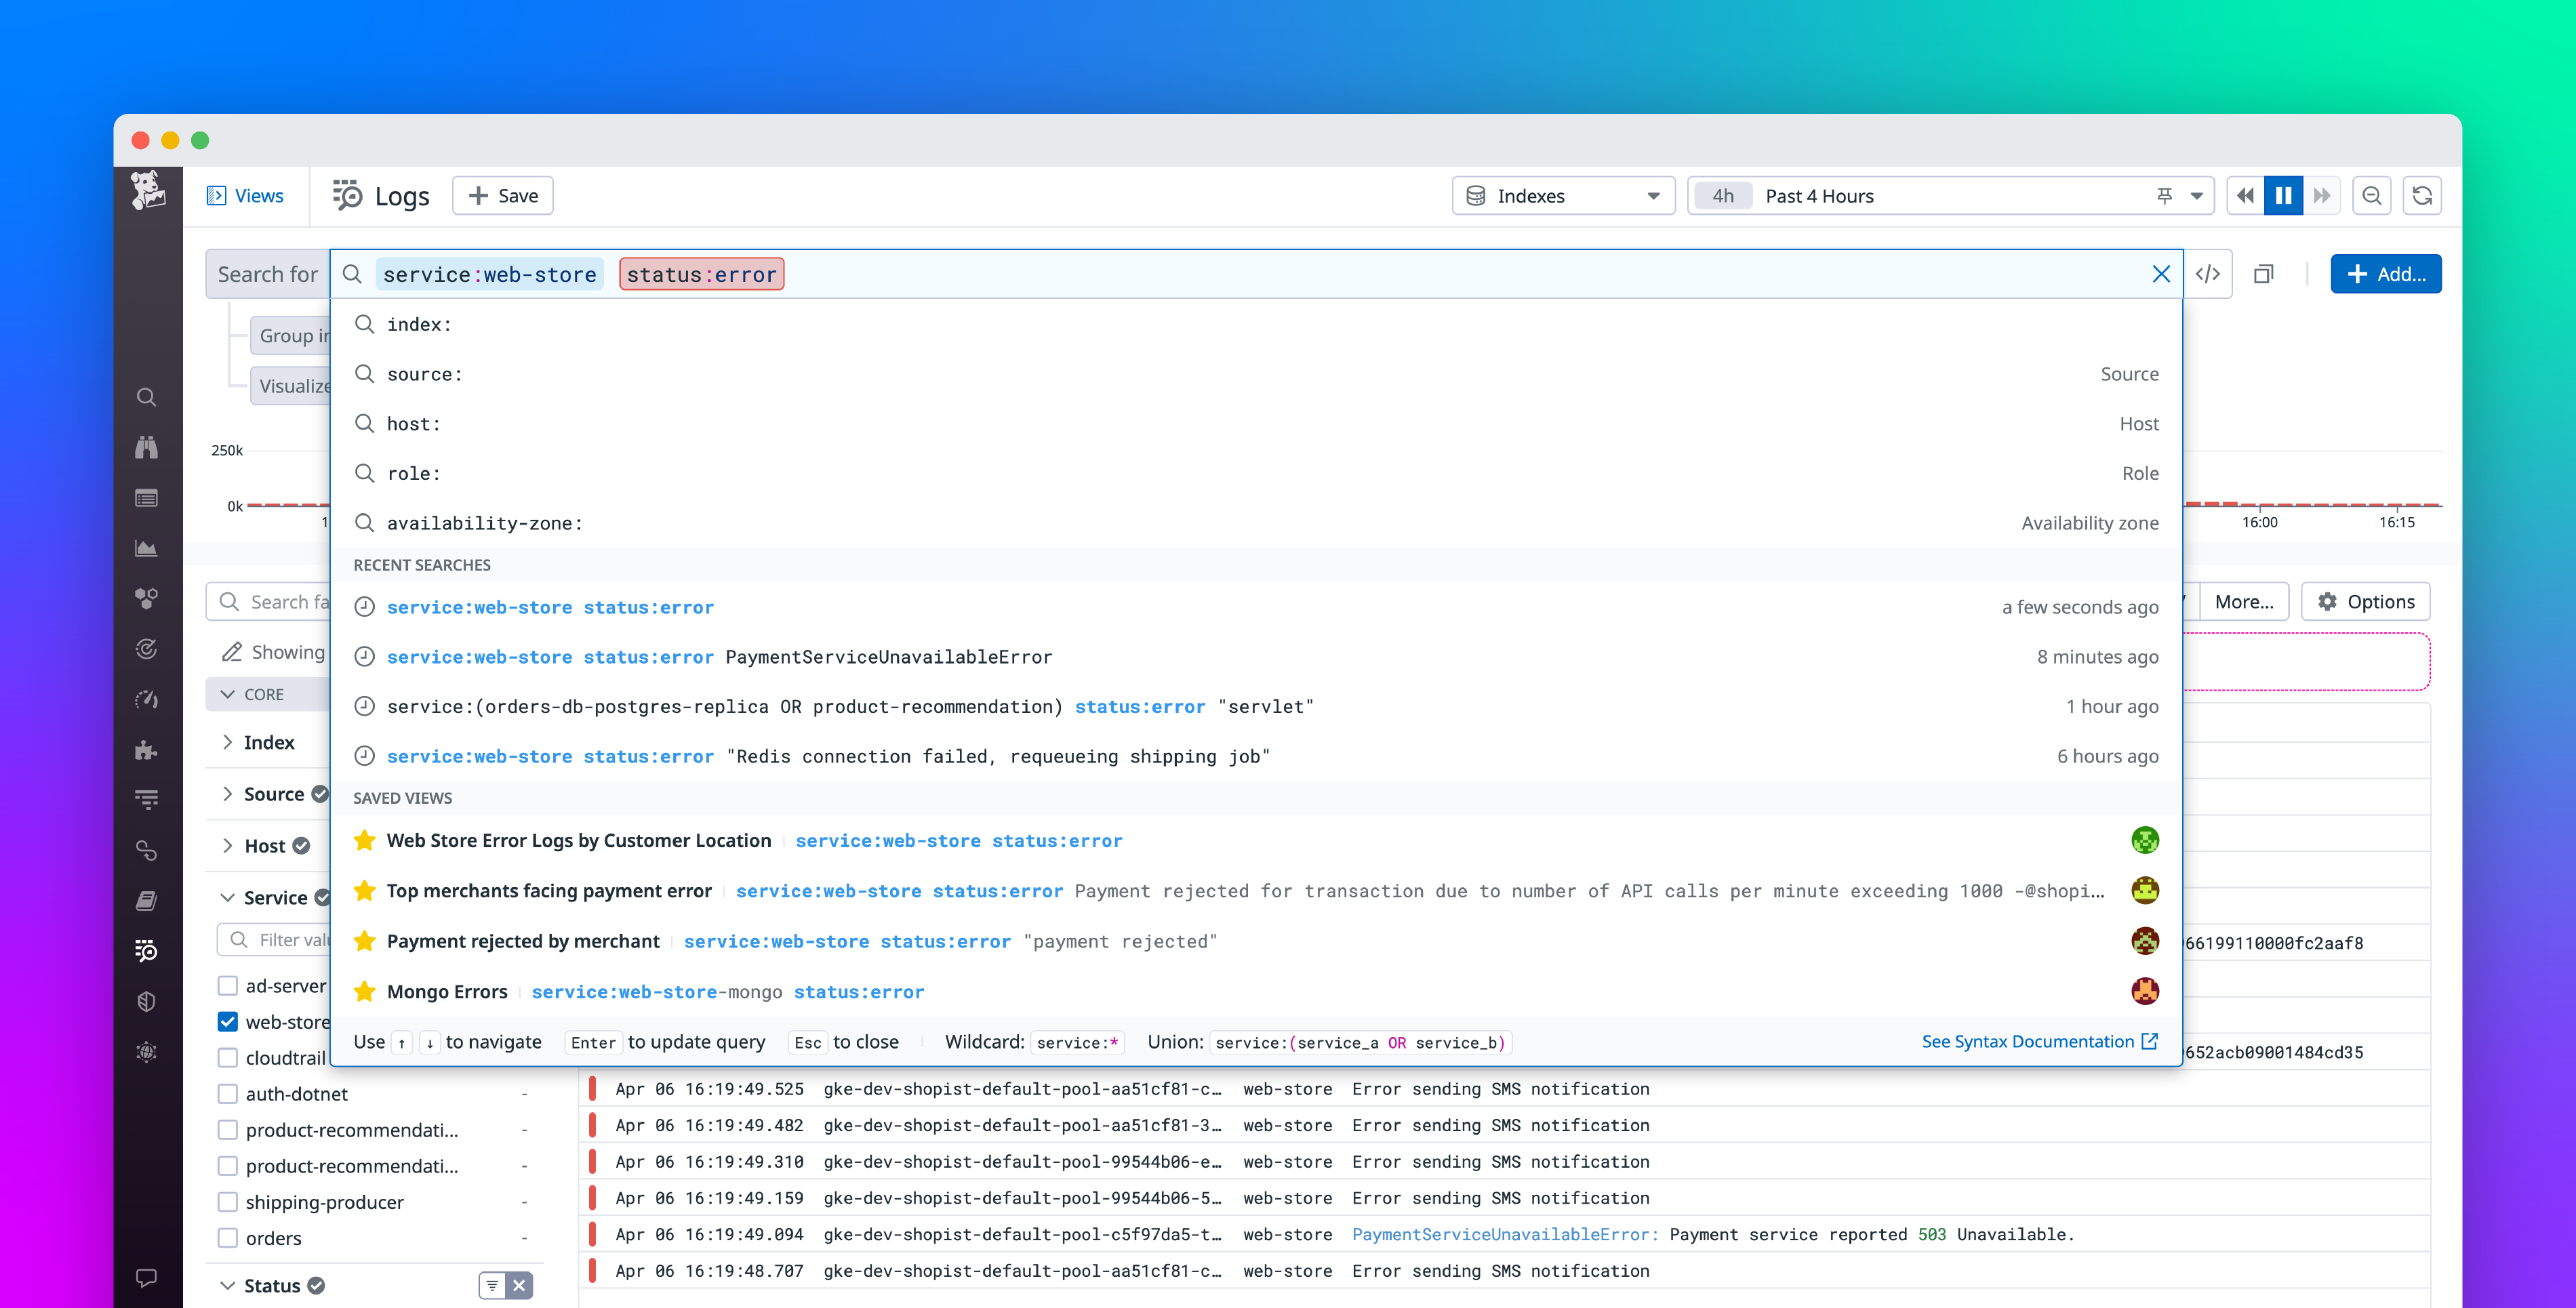
The server's HTTP response contains the contents of the website's homepage. But it also instructs the browser to set two cookies. The first, theme, is considered to be a session cookie since it does not have an Expires or Max-Age attribute. Session cookies are intended to be deleted by the browser when the browser closes. The second, sessionToken, is considered to be a persistent cookie since it contains an Expires attribute, which instructs the browser to delete the cookie at a specific date and time. Next, the browser sends another request to visit the spec.html page on the website. This request contains a Cookie header field, which contains the two cookies that the server instructed the browser to set: Figure 2: Search your logs efficiently with Datadog Log Management | Datadog This way, the server knows that this HTTP request is related to the previous one. The server would answer by sending the requested page, possibly including more Set-Cookie header fields in the HTTP response in order to instruct the browser to add new cookies, modify existing cookies, or remove existing cookies. To remove a cookie, the server must include a Set-Cookie header field with an expiration date in the past. The value of a cookie may consist of any printable ASCII character (! through ~, Unicode \u0021 through \u007E) excluding ,and; and whitespace characters. The name of a cookie excludes the same characters, as well as =, since that is the delimiter between the name and value. The cookie standard RFC 2965 is more restrictive but not implemented by browsers. The term cookie crumb is sometimes used to refer to a cookie's name–value pair. Cookies can also be set by scripting languages such as JavaScript that run within the browser. In JavaScript, the object document.cookie is used for this purpose. For example, the instruction document.cookie = "temperature=20" creates a cookie of name temperature and value 20.
The first cookie, LSID, has no Domain attribute, and has a Path attribute set to /accounts. This tells the browser to use the cookie only when requesting pages contained in docs.foo.com/accounts (the domain is derived from the request domain). The other two cookies, HSID and SSID, would be used when the browser requests any subdomain in .foo.com on any path (for example www.foo.com/bar). The prepending dot is optional in recent standards, but can be added for compatibility with RFC 2109 based implementations.
The first cookie, lu, is set to expire sometime on 15 January 2013. It will be used by the client browser until that time. The second cookie, made_write_conn, does not have an expiration date, making it a session cookie. It will be deleted after the user closes their browser. The third cookie, reg_fb_gate, has its value changed to deleted, with an expiration time in the past. The browser will delete this cookie right away because its expiration time is in the past. Note that cookie will only be deleted if the domain and path attributes in the Set-Cookie field match the values used when the cookie was created. As of 2016 Internet Explorer did not support Max-Age.
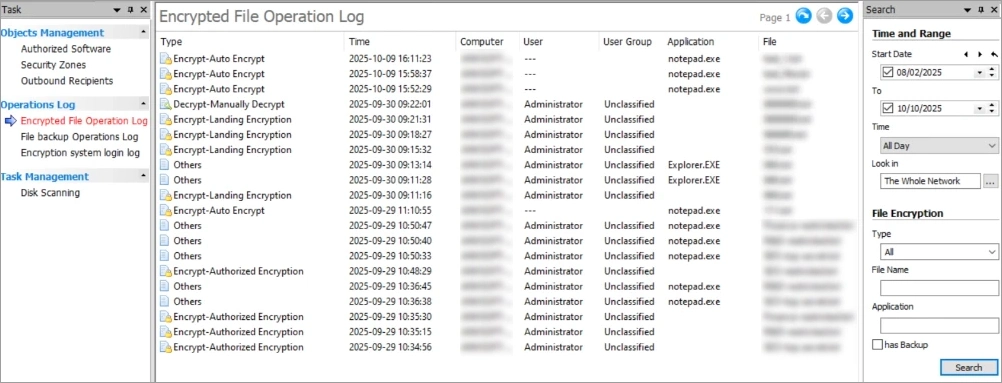
To enable or disable cookies completely, so that they are always accepted or always blocked. To view and selectively delete cookies using a cookie manager. To fully wipe all private data, including cookies. Add-on tools for managing cookie permissions also exist. Figure 3: Top 12 Data Security Software for Businesses in 2026 Cookies have some important implications for the privacy and anonymity of web users. While cookies are sent only to the server setting them or a server in the same Internet domain, a web page may contain images or other components stored on servers in other domains. Cookies that are set during retrieval of these components are called third-party cookies. A third-party cookie, belongs to a domain different from the one shown in the address bar. This sort of cookie typically appears when web pages feature content from external websites, such as banner advertisements. This opens up the potential for tracking the user's browsing history and is used by advertisers to serve relevant advertisements to each user.
As an example, suppose a user visits www.example.org. This website contains an advertisement from ad.foxytracking.com, which, when downloaded, sets a cookie belonging to the advertisement's domain (ad.foxytracking.com). Then, the user visits another website, www.foo.com, which also contains an advertisement from ad.foxytracking.com and sets a cookie belonging to that domain (ad.foxytracking.com). Eventually, both of these cookies will be sent to the advertiser when loading their advertisements or visiting their website. The advertiser can then use these cookies to build up a browsing history of the user across all the websites that have ads from this advertiser, through the use of the HTTP referer header field. As of 2014, some websites were setting cookies readable for over 100 third-party domains. On average, a single website was setting 10 cookies, with a maximum number of cookies (first- and third-party) reaching over 800. The older standards for cookies, RFC 2109 and RFC 2965, recommend that browsers should protect user privacy and not allow sharing of cookies between servers by default. However, the newer standard, RFC 6265, explicitly allows user agents to implement whichever third-party cookie policy they wish. Most modern web browsers contain privacy settings that can block third-party cookies. Since 2020, Apple Safari, Firefox, and Brave block all third-party cookies by default. Safari allows embedded sites to use Storage Access API to request permission to set first-party cookies. In May 2020, Google Chrome 83 introduced new features to block third-party cookies by default in its Incognito mode for private browsing, making blocking optional during normal browsing. The same update also added an option to block first-party cookies. In April 2024, Chrome postponed third-party cookie blocking by default to 2025. In July 2024, Google announced plan to avoid blocking third-party cookies by default and instead prompt users to allow third-party cookies.
The possibility of building a profile of users is a privacy threat, especially when tracking is done across multiple domains using third-party cookies. For this reason, some countries have legislation about cookies. Website operators who do not disclose third-party cookie use to consumers run the risk of harming consumer trust if cookie use is discovered. Having clear disclosure (such as in a privacy policy) tends to eliminate any negative effects of such cookie discovery. The government of the United States set strict rules on setting cookies in 2000 after it was disclosed that the White House drug policy office used cookies to track computer users viewing its online anti-drug advertising. In 2002, privacy activist Daniel Brandt found that the CIA had been leaving persistent cookies on computers that had visited its website. When notified it was violating policy, CIA stated that these cookies were not intentionally set and stopped setting them. On 25 December 2005, Brandt discovered that the National Security Agency (NSA) had been leaving two persistent cookies on visitors' computers due to a software upgrade. After being informed, the NSA immediately disabled the cookies.
In 2002, the European Union launched the Directive on Privacy and Electronic Communications (e-Privacy Directive), a policy requiring end users' consent for the placement of cookies, and similar technologies for storing and accessing information on users' equipment. In particular, Article 5 Paragraph 3 mandates that storing technically unnecessary data on a user's computer can only be done if the user is provided information about how this data is used, and the user is given the possibility of denying this storage operation. The Directive does not require users to authorise or be provided notice of cookie usage that are functionally required for delivering a service they have requested, for example to retain settings, store log-in sessions, or remember what is in a user's shopping basket. In 2009, the law was amended by Directive 2009/136/EC, which included a change to Article 5, Paragraph 3. Instead of having an option for users to opt out of cookie storage, the revised Directive requires consent to be obtained for cookie storage. The definition of consent is cross-referenced to the definition in European data protection law, firstly the Data Protection Directive 1995 and subsequently the General Data Protection Regulation (GDPR). As the definition of consent was strengthened in the text of the GDPR, this increased the quality of consent required by those storing and accessing information such as cookies on users devices. In a case decided under the Data Protection Directive however, the Court of Justice of the European Union later confirmed however that the previous law implied the same strong quality of consent as the current instrument. In addition to the requirement of consent which stems from storing or accessing information on a user's terminal device, the information in many cookies will be considered personal data under the GDPR alone, and will require a legal basis to process. This has been the case since the 1995 Data Protection Directive, which used an identical definition of personal data, although the GDPR in interpretative Recital 30 clarifies that cookie identifiers are included. While not all data processing under the GDPR requires consent, the characteristics of behavioural advertising mean that it is difficult or impossible to justify under any other ground. Consent under the combination of the GDPR and e-Privacy Directive has to meet a number of conditions in relation to cookies. It must be freely given and unambiguous: preticked boxes were banned under both the Data Protection Directive 1995 and the GDPR (Recital 32). The GDPR is specific that consent must be as 'easy to withdraw as to give', meaning that a reject-all button must be as easy to access in terms of clicks and visibility as an 'accept all' button. It must be specific and informed, meaning that consent relates to particular purposes for the use of this data, and all organisations seeking to use this consent must be specifically named. The Court of Justice of the European Union has also ruled that consent must be 'efficient and timely', meaning that it must be gained before cookies are laid and data processing begins instead of afterwards. The industry's response has been largely negative. Robert Bond of the law firm Speechly Bircham describes the effects as "far-reaching and incredibly onerous" for "all UK companies". Simon Davis of Privacy International argues that proper enforcement would "destroy the entire industry". However, scholars note that the onerous nature of cookie pop-ups stems from an attempt to continue to operate a business model through convoluted requests that may be incompatible with the GDPR. Academic studies and regulators both describe widespread non-compliance with the law. A study scraping 10,000 UK websites found that only 11.8% of sites adhered to minimal legal requirements, with only 33.4% of websites studied providing a mechanism to reject cookies that was as easy to use as accepting them. A study of 17,000 websites found that 84% of sites breached this criterion, finding additionally that many laid third party cookies with no notice at all. The UK regulator, the Information Commissioner's Office, stated in 2019 that the industry's 'Transparency and Consent Framework' from the advertising technology group the Interactive Advertising Bureau was 'insufficient to ensure transparency and fair processing of the personal data in question and therefore also insufficient to provide for free and informed consent, with attendant implications for PECR [e-Privacy] compliance.' Many companies that sell compliance solutions (Consent Management Platforms) permit them to be configured in manifestly illegal ways, which scholars have noted creates questions around the appropriate allocation of liability. A W3C specification called P3P was proposed for servers to communicate their privacy policy to browsers, allowing automatic, user-configurable handling.
However, few websites implement the specification, and the W3C has discontinued work on the specification. Third-party cookies can be blocked by most browsers to increase privacy and reduce tracking by advertising and tracking companies without negatively affecting the user's web experience on all sites. Some sites operate 'cookie walls', which make access to a site conditional on allowing cookies either technically in a browser, through pressing 'accept', or both. In 2020, the European Data Protection Board, composed of all EU data protection regulators, stated that cookie walls were illegal.In order for consent to be freely given, access to services and functionalities must not be made conditional on the consent of a user to the storing of information, or gaining of access to information already stored, in the terminal equipment of a user (so called cookie walls).Many advertising operators have an opt-out option to behavioural advertising, with a generic cookie in the browser stopping behavioural advertising. However, this is often ineffective against many forms of tracking, such as first-party tracking that is growing in popularity to avoid the impact of browsers blocking third party cookies. Furthermore, if such a setting is more difficult to place than the acceptance of tracking, it remains in breach of the conditions of the e-Privacy Directive.
Most websites use cookies as the only identifiers for user sessions, because other methods of identifying web users have limitations and vulnerabilities. If a website uses cookies as session identifiers, attackers can impersonate users' requests by stealing a full set of victims' cookies. From the web server's point of view, a request from an attacker then has the same authentication as the victim's requests; thus the request is performed on behalf of the victim's session. Listed here are various scenarios of cookie theft and user session hijacking (even without stealing user cookies) that work with websites relying solely on HTTP cookies for user identification.
Traffic on a network can be intercepted and read by computers on the network other than the sender and receiver (particularly over unencrypted open Wi-Fi). This traffic includes cookies sent on ordinary unencrypted HTTP sessions. Where network traffic is not encrypted, attackers can therefore read the communications of other users on the network, including HTTP cookies as well as the entire contents of the conversations, for the purpose of a man-in-the-middle attack. An attacker could use intercepted cookies to impersonate a user and perform a malicious task, such as transferring money out of the victim's bank account. This issue can be resolved by securing the communication between the user's computer and the server by employing Transport Layer Security (HTTPS protocol) to encrypt the connection. A server can specify the Secure flag while setting a cookie, which will cause the browser to send the cookie only over an encrypted channel, such as a TLS connection.
Cookies can also be stolen using a technique called cross-site scripting. This occurs when an attacker takes advantage of a website that allows its users to post unfiltered HTML and JavaScript content. By posting malicious HTML and JavaScript code, the attacker can cause the victim's web browser to send the victim's cookies to a website the attacker controls. As an example, an attacker may post a message on www.example.com with the following link: 2. System Architecture & Core Working Principles When another user clicks on this link, the browser executes the piece of code within the onclick attribute, thus replacing the string document.cookie with the list of cookies that are accessible from the current page. As a result, this list of cookies is sent to the attacker.com server. If the attacker's malicious posting is on an HTTPS website https://www.example.com, secure cookies will also be sent to attacker.com in plain text. It is the responsibility of the website developers to filter out such malicious code. Such attacks can be mitigated by using HttpOnly cookies. These cookies will not be accessible by client-side scripting languages like JavaScript, and therefore, the attacker will not be able to gather these cookies.
For example, Bob might be browsing a chat forum where another user, Mallory, has posted a message. Suppose that Mallory has crafted an HTML image element that references an action on Bob's bank's website (rather than an image file), e.g., If Bob's bank keeps his authentication information in a cookie, and if the cookie hasn't expired, then the attempt by Bob's browser to load the image will submit the withdrawal form with his cookie, thus authorizing a transaction without Bob's approval.
Because ETags are cached by the browser, and returned with subsequent requests for the same resource, a tracking server can simply repeat any ETag received from the browser to ensure an assigned ETag persists indefinitely (in a similar way to persistent cookies). Additional caching header fields can also enhance the preservation of ETag data. ETags can be flushed in some browsers by clearing the browser cache.
The browser cache can also be used to store information that can be used to track individual users. This technique takes advantage of the fact that the web browser will use resources stored within the cache instead of downloading them from the website when it determines that the cache already has the most up-to-date version of the resource. For example, a website could serve a JavaScript file with code that sets a unique identifier for the user (for example, var userId = 3243242;). After the user's initial visit, every time the user accesses the page, this file will be loaded from the cache instead of downloaded from the server. Thus, its content will never change.
A browser fingerprint is information collected about a browser's configuration, such as version number, screen resolution, and operating system, for the purpose of identification. Fingerprints can be used to fully or partially identify individual users or devices even when cookies are turned off. Basic web browser configuration information has long been collected by web analytics services in an effort to accurately measure real human web traffic and discount various forms of click fraud. With the assistance of client-side scripting languages, collection of much more esoteric parameters is possible. Assimilation of such information into a single string constitutes a device fingerprint. In 2010, EFF measured at least 18.1 bits of entropy possible from browser fingerprinting. Canvas fingerprinting, a more recent technique, claims to add another 5.7 bits.
Some web browsers support persistence mechanisms which allow the page to store the information locally for later use. The HTML5 standard (which most modern web browsers support to some extent) includes a JavaScript API called Web storage that allows two types of storage: local storage and session storage. Local storage behaves similarly to persistent cookies while session storage behaves similarly to session cookies, except that session storage is tied to an individual tab/window's lifetime (AKA a page session), not to a whole browser session like session cookies. Internet Explorer supports persistent information in the browser's history, in the browser's favorites, in an XML store ("user data"), or directly within a web page saved to disk. Some web browser plugins include persistence mechanisms as well. For example, Adobe Flash has Local shared object and Microsoft Silverlight has Isolated storage.
HTTP Strict Transport Security § Privacy issues Secure cookie – Type of HTTP cookie Session (computer science) – Temporary context for interactive information interchangePages displaying short descriptions of redirect targets RFC 6265, the current official specification for HTTP cookies HTTP cookies, Mozilla Developer Network Using cookies via ECMAScript, Mozilla Developer Network How Internet Cookies Work at HowStuffWorks Cookies at the Electronic Privacy Information Center (EPIC) Mozilla Knowledge-Base: Cookies Cookie Domain, explain in detail how cookie domains are handled in current major browsers Cookie Stealing - Michael Pound Check cookies for compliance with EU cookie directive Signal is an open-source, encrypted messaging service for instant messaging, voice calls, and video calls. The instant messaging function includes sending text, voice notes, images, videos, and other files. Communication may be one-to-one between users or may involve group messaging. The application uses a centralized computing architecture and is cross-platform software. It is developed by the nonprofit Signal Foundation and its subsidiary Signal Messenger LLC. Signal's software is free and open-source. Its mobile clients, desktop client, and server are all published under the AGPL-3.0-only license. The official Android app generally uses the proprietary Google Play Services, although it is designed to be able to work without them. Signal is also distributed for iOS and desktop programs for Windows, macOS, and Linux. Registration for desktop use requires an iOS or Android device. Signal uses mobile telephone numbers to register and manage user accounts, though configurable usernames were added in March 2024 to allow users to hide their phone numbers from other users. After removing support for SMS on Android in 2023, the app now secures all communications with end-to-end encryption. The client software includes mechanisms by which users can independently verify their contacts' identities and the data channel's integrity. The nonprofit Signal Foundation was launched in February 2018 with initial funding of $50 million from WhatsApp co-founder Brian Acton. As of January 2025, the platform had approximately 70 million monthly active users. As of January 2025, it had been downloaded more than 220 million times.
Open Whisper Systems' website was launched in January 2013. In February 2014, Open Whisper Systems introduced the second version of their TextSecure Protocol (now Signal Protocol), which added end-to-end encrypted group chat and instant messaging capabilities to TextSecure. Toward the end of July 2014, they announced plans to merge the RedPhone and TextSecure applications as Signal. This announcement coincided with the initial release of Signal as a RedPhone counterpart for iOS. The developers said that their next steps would be to provide TextSecure instant messaging capabilities for iOS, unify the RedPhone and TextSecure applications on Android, and launch a web client. Signal was the first iOS app to enable end-to-end encrypted voice calls for free. TextSecure compatibility was added to the iOS application in March 2015.
From its launch in May 2010 until March 2015, the Android version of Signal (then called TextSecure) included support for encrypted SMS/MMS messaging. From version 2.7.0 onward, the Android application only supported sending and receiving encrypted messages via the data channel. Reasons for this included security flaws of SMS/MMS and problems with the key exchange. Open Whisper Systems' abandonment of SMS/MMS encryption prompted some users to create a fork named Silence (initially called SMSSecure) that is meant solely for the exchange of encrypted SMS and MMS messages. In November 2015, the TextSecure and RedPhone applications on Android were merged to become Signal for Android. A month later, Open Whisper Systems announced Signal Desktop, a Chrome app that could link with a Signal mobile client. At launch, the app could only be linked with the Android version of Signal. On 26 September 2016, Open Whisper Systems announced that Signal Desktop could now be linked with the iOS version of Signal as well. On 31 October 2017, Open Whisper Systems announced that the Chrome app was deprecated. At the same time, they announced the release of a standalone desktop client (based on the Electron framework) for Windows, macOS and certain Linux distributions. On 4 October 2016, the American Civil Liberties Union (ACLU) and Open Whisper Systems published a series of documents revealing that OWS had received a subpoena requiring them to provide information associated with two phone numbers for a federal grand jury investigation in the first half of 2016. Only one of the two phone numbers was registered on Signal, and because of how the service is designed, OWS was only able to provide "the time the user's account had been created and the last time it had connected to the service". Along with the subpoena, OWS received a gag order requiring OWS not to tell anyone about the subpoena for one year. OWS approached the ACLU, and they were able to lift part of the gag order after challenging it in court. OWS said it was the first time they had received a subpoena, and that they were "committed to treating any future requests the same way". In March 2017, Open Whisper Systems transitioned Signal's calling system from RedPhone to WebRTC, also adding the ability to make video calls with the mobile apps.
On 21 February 2018, Moxie Marlinspike and WhatsApp co-founder Brian Acton announced the formation of the Signal Technology Foundation, a 501(c)(3) nonprofit organization whose mission is "to support, accelerate, and broaden Signal's mission of making private communication accessible and ubiquitous". Acton started the foundation with $50 million in funding and became the foundation's executive chairman after leaving WhatsApp's parent company Facebook in September 2017.
Marlinspike continued as Signal Messenger's first CEO. As of 2020, Signal ran entirely on donations, as a nonprofit. Between November 2019 and February 2020, Signal added iPad support, view-once images and videos, stickers, and reactions. They also announced plans for a new group messaging system and an "experimental method for storing encrypted contacts in the cloud." Signal was reportedly popularized in the United States during the George Floyd protests. Heightened awareness of police monitoring led protesters to use the platform to communicate. Black Lives Matter organizers had used the platform "for several years". During the first week of June, the encrypted messaging app was downloaded over five times more than it had been during the week prior to the murder of George Floyd. In June 2020, Signal Foundation announced a new feature that enables users to blur faces in photos, in response to increased federal efforts to monitor protesters. On 7 January 2021, Signal saw a surge in new user registrations, which temporarily overwhelmed Signal's capacity to deliver account verification messages. CNN and MacRumors linked the surge with a WhatsApp privacy policy change and a Signal endorsement by Elon Musk and Edward Snowden via Twitter. The surge was also tied to the attack on the United States Capitol. International newspapers reported similar trends in the United Arab Emirates. Reuters reported that more than 100,000 people had installed Signal between 7 and 8 January. Between 12 and 14 January 2021, the number of Signal installations listed on Google Play increased from over 10 million to over 50 million. On 15 January 2021, due to the surge of new users, Signal was overwhelmed with the new traffic and was down for all users. On the afternoon of 16 January, Signal announced via Twitter that service had been restored. On 10 January 2022, Moxie Marlinspike announced that he was stepping down from his role as CEO of Signal Messenger. He continues to remain on the Signal Foundation's board of directors and Brian Acton has volunteered to serve as interim CEO during the search for a new CEO. In August 2022, Signal notified 1900 users that their data had been affected by the Twilio breach including user phone numbers and SMS verification codes. At least one journalist had his account re-registered to a device he did not control as a result of the attack. In September 2022 Signal Messaging LLC announced that AI researcher and noted critic of big tech Meredith Whittaker would fill the newly created position of president. In August 2024, Reuters reported on the blocking of Signal in Venezuela and Russia. In Venezuela, the blocking was a result of protests after the controversial presidential elections in which Nicolas Maduro declared his victory. In Russia, the reason was that Signal did not meet the requirements of legislation in the field of countering terrorism and extremism. In May 2026, Signal threatened to leave Canada because of the Lawful Access Act, stating that "Bill C-22 could potentially allow hackers to exploit these very vulnerabilities engineered into electronic systems, with private messaging services serving as an ideal target for foreign adversaries".
Signal messages are encrypted with the Signal Protocol (formerly known as the TextSecure Protocol). The protocol combines the Double Ratchet Algorithm, prekeys, and an Extended Triple Diffie–Hellman (X3DH) handshake. It uses Curve25519, AES-256, and HMAC-SHA256 as primitives. The protocol provides confidentiality, integrity, authentication, participant consistency, destination validation, forward secrecy, backward secrecy (a.k.a. future secrecy), causality preservation, message unlinkability, message repudiation, participation repudiation, and asynchronicity. It does not provide anonymity preservation, and requires servers for the relaying of messages and storing of public key material. The Signal Protocol also supports end-to-end encrypted group chats. The group chat protocol is a combination of a pairwise double ratchet and multicast encryption. In addition to the properties provided by the one-to-one protocol, the group chat protocol provides speaker consistency, out-of-order resilience, dropped message resilience, computational equality, trust equality, subgroup messaging, as well as contractible and expandable membership. According to a 2023 technical report, Signal adopted a protocol called Sender Keys for group messaging, and favors the protocol where possible (rather than the double ratchet) for group messaging, even in small groups. In October 2014, researchers from Ruhr University Bochum (RUB) published an analysis of the Signal Protocol. Among other findings, they presented an unknown key-share attack on the protocol, but in general, they found that it was secure. In October 2016, researchers from UK's University of Oxford, Queensland University of Technology in Australia, and Canada's McMaster University published a formal analysis of the protocol. They concluded that the protocol was cryptographically sound. In July 2017, researchers from RUB found during another analysis of group messengers a purely theoretic attack against the group protocol of Signal: A user who knows the secret group ID of a group (due to having been a group member previously or stealing it from a member's device) can become a member of the group.
Since the group ID cannot be guessed and such member changes are displayed to the remaining members, this attack is likely to be difficult to carry out without being detected. As of August 2018, the Signal Protocol has been implemented into WhatsApp, Facebook Messenger, Skype, and Google Allo, making it possible for the conversations of "more than a billion people worldwide" to be end-to-end encrypted. In Google Allo, Skype and Facebook Messenger, conversations are not encrypted with the Signal Protocol by default; they only offer end-to-end encryption in an optional mode. Up until March 2017, Signal's voice calls were encrypted with SRTP and the ZRTP key-agreement protocol, which was developed by Phil Zimmermann. In March 2017, Signal transitioned to a new WebRTC-based calling system that introduced the ability to make video calls. Signal's voice and video calling functionalities use the Signal Protocol channel for authentication instead of ZRTP.
In December 2016, Egypt blocked access to Signal. In response, Signal's developers added domain fronting to their service. This allows Signal users in a specific country to circumvent censorship by making it look like they are connecting to a different internet-based service. As of May 2022, Signal's domain fronting is enabled by default in Egypt, UAE, Oman, Qatar, Iran, Cuba, Pakistan and Uzbekistan. As of January 2018, Signal was blocked in Iran. Signal's domain fronting feature relies on the Google App Engine (GAE) service. This does not work in Iran because Google has blocked Iranian access to GAE in order to comply with U.S. sanctions. In early 2018, Google App Engine made an internal change to stop domain fronting for all countries. Due to this issue, Signal made a public change to use Amazon CloudFront for domain fronting. However, AWS also announced that they would be making changes to their service to prevent domain fronting. As a result, Signal said that they would start investigating new methods/approaches. Signal switched from AWS back to Google in April 2019. In January 2021, Iran removed the app from app stores, and blocked Signal. Signal was later blocked by China in March 2021, followed by its removal from the App Store in China on 19 April 2024. On August 9, 2024, Signal was blocked in Russia. Roskomnadzor claimed that this was due to "violations of the law on combating terrorism and extremism". Around the same time, Signal was also blocked in Venezuela following the contested 2024 presidential election and subsequent protests.
In March 2025, it was revealed that senior members of the Trump administration—including vice president JD Vance, secretary of state Marco Rubio, and defense secretary Pete Hegseth—were using Signal to discuss sensitive information, including details of military attack plans in Yemen. The existence of the chat was disclosed by The Atlantic editor-in-chief Jeffrey Goldberg, who was accidentally added to the chat. Brian Hughes of the National Security Council later confirmed the authenticity of Goldberg's account. On October 4, 2025, The Minnesota Star Tribune reported that Deputy Homeland Security Advisor Anthony Salisbury had been seen in public exchanging information on Signal with other government officials. Subjects discussed included potential troop deployments to Portland, Oregon, upcoming Immigration and Customs Enforcement (ICE) operations in Chicago, Vice President JD Vance's desire to prosecute two unnamed Florida influencers, and Federal Bureau of Investigation director Kash Patel's firing of FBI employees.
Comparison of cross-platform instant messaging clients Comparison of VoIP software Internet privacy List of video telecommunication services and product brands Secure communication In cryptography, encryption is the process of transforming information in a way that, ideally, only authorized parties can decode. This process converts the original representation of the information, known as plaintext, into an alternative form known as ciphertext. Encryption does not itself prevent interference but denies the intelligible content to a would-be interceptor. For technical reasons, an encryption scheme usually uses a pseudo-random encryption key generated by an algorithm. For a well-designed modern encryption scheme, decrypting ciphertext without the appropriate key should be computationally infeasible. An authorized recipient can easily decrypt the message with the key provided by the originator to recipients but not to unauthorized users. Historically, various forms of encryption have been used to aid in cryptography. Early encryption techniques were often used in military messaging. Since then, new techniques have emerged and become commonplace in all areas of modern computing. Modern encryption schemes use the concepts of public-key and symmetric-key.
Conventional methods for permanently deleting data from a storage device involve overwriting the device's whole content with zeros, ones, or other patterns – a process which can take a significant amount of time, depending on the capacity and the type of storage medium. Cryptography offers a way of making the erasure almost instantaneous. This method is called crypto-shredding. An example implementation of this method can be found on iOS devices, where the cryptographic key is kept in a dedicated 'effaceable storage'. Because the key is stored on the same device, this setup on its own does not offer full privacy or security protection if an unauthorized person gains physical access to the device.
The question of balancing the need for national security with the right to privacy has been debated for years, since encryption has become critical in today's digital society. The modern encryption debate started around the '90s when US government tried to ban cryptography because, according to them, it would threaten national security. The debate is polarized around two opposing views. Those who see strong encryption as a problem making it easier for criminals to hide their illegal acts online and others who argue that encryption keep digital communications safe. The debate heated up in 2014, when Big Tech like Apple and Google set encryption by default in their devices. This was the start of a series of controversies that puts governments, companies and internet users at stake.
3. Software Implementation, Frameworks & Protocols Even when encryption effectively conceals a message’s content and prevents tampering, the length of the ciphertext remains a form of metadata that can leak sensitive information. For instance, the well-known CRIME and BREACH attacks against HTTPS exploited information leakage through encrypted message length as a side-channel attack. Traffic analysis more broadly refers to techniques that use metadata—such as message size and timing—to infer information about communication patterns. Applying padding to a message before encryption can help obscure its true plaintext length, though this increases the ciphertext size and adds bandwidth overhead. Padding may be applied randomly or deterministically, each approach involving different trade-offs. Encrypting and padding data to produce padded uniform random blobs (PURBs) ensures that the ciphertext reveals no metadata about the plaintext’s structure, leaking only asymptotically minimal O ( log I log I M ) {\displaystyle O(\log \log M)} information through its length.
Existing systems fail to securely protect and search audit logs without compromising their privacy, authentication, and integrity, especially in the presence of active attackers who can modify or erase records. The implementation of searchable encrypted log files with forward-secure encryption, authentication, and integrity, using a key management system that allows for encrypted searches while preserving confidentiality, even if the logging machine is compromised, by employing distinct cryptographic keys for encryption and authentication, and requiring interaction with a trusted third party for decryption.
If audit logs are stored in plaintext for easy searching and access, then search efficiency and access speed are improved, but confidentiality and integrity are compromised to active attackers The patent replaces plaintext storage with cryptographic encryption, substituting a mechanical/search-based access system with a cryptographic system that enables searching without decryption. The searchable encryption scheme allows the auditor to search encrypted log messages using cryptographic operations rather than plaintext comparison, maintaining search efficiency while ensuring confidentiality against active attackers.
If encryption is applied to protect log confidentiality, then confidentiality is improved, but the ability to perform searches without decryption is worsened The patent substitutes traditional plaintext searching with cryptographic searching. The searchable encryption scheme enables the auditor to perform searches on encrypted data by using cryptographic operations that work directly on ciphertext, eliminating the need to decrypt logs for search purposes while maintaining full search functionality.
The patent transforms the search operation from a plaintext-based string matching operation to a cryptographic operation that works on encrypted data. By changing the parameter space from plaintext to ciphertext, the system enables searching while maintaining confidentiality, as the search operations are performed in the encrypted domain. If a single cryptographic key is used for both encryption and authentication, then system complexity is reduced, but forward security and compromise resilience are worsened The patent segments the cryptographic key into two distinct keys: an encryption key for confining log message confidentiality and an authentication key for verifying integrity. This segmentation ensures that if one key is compromised, the other remains secure, providing forward security and compromise resilience without significantly increasing overall system complexity.
The patent introduces asymmetry in the key management system by using different cryptographic keys for encryption and authentication purposes. This asymmetric key structure ensures that the compromise of one key does not affect the security properties provided by the other key, enhancing forward security while maintaining manageable system complexity through clear separation of concerns.
If the logging machine is compromised and keys are recovered, then attacker access to future logs is improved, but the security of past logs is worsened The patent applies preliminary action by pre-establishing forward security through distinct key separation before any compromise occurs. The authentication key is designed to remain secure even if the encryption key is compromised, so past log messages remain protected. This preliminary key separation ensures that even if an attacker compromises the logging machine and obtains the encryption key, they cannot authenticate or tamper with past logs without the separate authentication key.
Audit logs are a fundamental digital forensic mechanism for providing security in computer systems. In one embodiment, a system that enables the verification of log data integrity and that provides searchable encryption of the log data by an auditor includes a key generation center, logging machine, and an auditor computing device. The system enables Compromise- Resilient Searchable Encryption, Authentication and Integrity, Per-item QoF with E&A for Searchable Encrypted Audit Logs, and a Key Management and System Model.
Centralized Logging Systems collect, store, and manage log data from multiple servers, applications, and services in one central location. They help in monitoring, analyzing, and troubleshooting distributed systems more efficiently. Examples: Popular centralized logging tools include ELK Stack, Splunk, and Graylog. Organizations use these tools to detect errors quickly, monitor system health, and troubleshoot issues across distributed systems.
Logging systems have one main place for storing logs. There are different ways to collect logs and send them there. Agent-Based Collection uses software agents installed on servers or devices to collect logs and send them to a centralized logging system. It supports real-time log collection and processing. Example: Fluentd, Logstash, and Splunk Universal Forwarder are popular agent-based log collection tools.
Syslog is a standard protocol used to send log messages from devices and applications to a central log server. It includes details such as timestamp, source, and severity level. 4. Practical Deployment, Analysis & Case Studies File-Based Collection gathers logs from local log files and transfers them to a centralized storage location. It is commonly used when agents cannot be installed.
Example: Tools such as SCP, FTP, and rsync are commonly used for file-based log collection. Logs contain the story of your application. When that story includes sensitive data, encryption transforms logs from a security liability into a protected asset that satisfies compliance requirements while preserving debugging capability. Modern applications generate logs containing user IDs, IP addresses, request payloads, and error details. Without encryption, this data sits exposed in log files, storage systems, and monitoring platforms. Regulations like GDPR, HIPAA, and PCI-DSS increasingly require protection of log data at rest and in transit. This guide walks through practical encryption strategies you can implement today.
The challenge is balancing security with usability. Over-encrypted logs become impossible to debug. Under-encrypted logs expose your users and organization to risk. Before writing code, understand where encryption fits in your logging pipeline. This diagram shows the key decision points. Each layer protects against different threats. Field-level encryption protects data even from administrators with storage access. Transport encryption prevents network interception. Storage encryption protects against physical theft or cloud provider access.
Field-level encryption gives you the most control. You decide exactly which data gets encrypted and who can decrypt it. This approach uses AES-256-GCM, which provides both confidentiality and integrity verification. This encryptor handles individual field values. Next, integrate it with your logging framework to automatically encrypt sensitive fields.
Encryption is only as strong as your key management. Poor key handling undermines the entire system. Never hardcode encryption keys. Use a secrets manager like AWS Secrets Manager, HashiCorp Vault, or Azure Key Vault. For key rotation, maintain multiple key versions. Tag encrypted data with the key version used, and update your decrypt path to select the matching key version.
Field encryption protects data content. Transport encryption protects data in transit. Configure your log shipper to use TLS when sending logs to collectors. Your cloud provider likely offers storage encryption. Enable it as a baseline, but remember it only protects against physical theft or provider-level access.
Encrypted logs need a way to decrypt them for debugging. Build a controlled access tool. Wrap this tool with proper access controls. Audit every decryption request to maintain accountability. Log encryption protects sensitive data throughout its lifecycle. Field-level encryption gives you precise control over what gets protected. Transport encryption secures data in motion. Storage encryption adds a final layer of defense at rest.
Start with identifying your sensitive fields and implementing field-level encryption. Add transport and storage encryption as additional layers. Build controlled decryption tools with audit logging. Together, these layers transform your logging system from a potential vulnerability into a security asset. The investment pays off during security audits, compliance reviews, and the inevitable day when you need to prove that a data breach did not expose user information stored in your logs.
Need help implementing secure logging with encryption? OneUptime provides enterprise-grade log management with built-in security controls, helping you maintain compliance while keeping full observability into your systems. 5. Performance Evaluation & Extended Technical Observations Every OneUptime blog post is open source. Found a typo, an inaccuracy, or have a clearer way to explain something? Anyone can contribute — your edits make this post better for everyone who reads it next.
Your complete reliability stack unified: infrastructure monitoring, incident management, status pages, and APM. Open-source and self-hostable. In cryptography, frequency analysis is the study of the frequency of letters or groups of letters in a ciphertext. The method is used as an aid to breaking substitution ciphers (e.g. mono-alphabetic substitution cipher , Caesar shift cipher , Vatsyayana cipher ).
Frequency analysis consists of counting the occurrence of each letter in a text. Frequency analysis is based on the fact that, in any given piece of text, certain letters and combinations of letters occur with varying frequencies. For instance, given a section of English language, letters E, T, A and O are the most common, while letters Z, Q and X are not as frequently used. The following chart shows the frequency of each letter of the alphabet for the English language: We can assume that most samples of text written in English would have a similar distribution of letters. However this is only true if the sample of text is long enough. A very short text may lead to a significantly different distribution.
When trying to decrypt a cipher text based on a substitution cipher, we can use a frequency analysis to help identify the most recurring letters in a cipher text and hence make hypothesis of what these letters have been encoded as (e.g. E, T, A, O, etc). This will help us decrypt some of the letters in the text. We can then recognise patterns/words in the partly decoded text to identify more substitutions.
You can perform a frequency analysis on the following text to try to decrypt this text step by step: Your Task: Complete a frequency analysis to decrypt the following ciphers. Cipher #1 Cipher #2 Cipher #3 Cipher #4 Cipher #5 Cipher #6 Cipher #7 Cipher #8 “DJ DK C QLXDWI WF SDGDU PCX. XLRLU KQCSLKBDQK, KJXDHDET FXWZ C BDIILE RCKL, BCGL PWE JBLDX FDXKJ GDSJWXO CTCDEKJ JBL LGDU TCUCSJDS LZQDXL. IYXDET JBL RCJJUL, XLRLU KQDLK ZCECTLI JW KJLCU KLSXLJ QUCEK JW JBL LZQDXL’K YUJDZCJL PLCQWE, JBL ILCJB KJCX, CE CXZWXLI KQCSL KJCJDWE PDJB LEWYTB QWPLX JW ILKJXWO CE LEJDXL QUCELJ. QYXKYLI RO JBL LZQDXL’K KDEDKJLX CTLEJK, QXDESLKK ULDC XCSLK BWZL CRWCXI BLX KJCXKBDQ, SYKJWIDCE WF JBL KJWULE QUCEK JBCJ SCE KCGL BLX QLWQUL CEI XLKJWXL FXLLIWZ JW JBL TCUCVO…” View Hint Star wars opening crawl “JVUI LUMNCJUIG KCL GIXVGEIS XO KPL KOYI AJCEIX OQ XCXOOPEI PE CE CXXIYAX XO GILWVI KPL QGPIES KCE LOJO QGOY XKI WJVXWKIL OQ XKI DPJI TCETLXIG BCHHC XKI KVXX. JPXXJI SOIL JVUI UEON XKCX XKI TCJCWXPW IYAPGI KCL LIWGIXJM HITVE WOELXGVWXPOE OE C EIN CGYOGIS LACWI LXCXPOE IDIE YOGI AONIGQVJ XKCE XKI QPGLX SGICSIS SICXK LXCG. NKIE WOYAJIXIS, XKPL VJXPYCXI NICAOE NPJJ LAIJJ WIGXCPE SOOY QOG XKI LYCJJ HCES OQ GIHIJL LXGVTTJPET XO GILXOGI QGIISOY XO XKI TCJCZM…” View Hint Star wars opening crawl “OK OH R WRFD KOIS QPF KNS FSTSJJOPX. RJKNPAGN KNS WSRKN HKRF NRH TSSX WSHKFPCSW, OIBSFORJ KFPPBH NRYS WFOYSX KNS FSTSJ QPFMSH QFPI KNSOF NOWWSX TRHS RXW BAFHASW KNSI RMFPHH KNS GRJREC. SYRWOXG KNS WFSRWSW OIBSFORJ HKRFQJSSK, R GFPAB PQ QFSSWPI QOGNKSFH JSW TC JADS HDCVRJDSF NRH SHKRTJOHNSW R XSV HSMFSK TRHS PX KNS FSIPKS OMS VPFJW PQ NPKN. KNS SYOJ JPFW WRFKN YRWSF, PTHSHHSW VOKN QOXWOXG CPAXG HDCVRJDSF, NRH WOHBRKMNSW KNPAHRXWH PQ FSIPKS BFPTSH OXKP KNS QRF FSRMNSH PQ HBRMS…” View Hint Star wars opening crawl “ZRTFT IH PQFTHZ IQ ZRT XBGBOZIO HTQBZT. HTWTFBG ZRLPHBQV HLGBF HYHZTSH RBWT VTOGBFTV ZRTIF IQZTQZILQH ZL GTBWT ZRT FTEPKGIO. ZRIH HTEBFBZIHZ SLWTSTQZ, PQVTF ZRT GTBVTFHRIE LD ZRT SYHZTFILPH OLPQZ VLLAP, RBH SBVT IZ VIDDIOPGZ DLF ZRT GISIZTV QPSKTF LD CTVI AQIXRZH ZL SBIQZBIQ ETBOT BQV LFVTF IQ ZRT XBGBJY.
HTQBZLF BSIVBGB, ZRT DLFSTF NPTTQ LD QBKLL, IH FTZPFQIQX ZL ZRT XBGBOZIO HTQBZT ZL WLZT LQ ZRT OFIZIOBG IHHPT LD OFTBZIQX BQ BFSY LD ZRT FTEPKGIO ZL BHHIHZ ZRT LWTFMRTGSTV CTVI…” View Hint Star wars opening crawl “FX IWBBJX PB NB PB PWX GBBD. VSP FWO, JBGX JRO, PWX GBBD? FWO IWBBJX PWUJ RJ BSA NBRK? RDL PWXO GRO FXKK RJM FWO IKUGV PWX WUNWXJP GBSDPRUD? FWO, 35 OXRAJ RNB, EKO PWX RPKRDPUI? FWO LBXJ AUIX CKRO PXQRJ? FX IWBBJX PB NB PB PWX GBBD UD PWUJ LXIRLX RDL LB PWX BPWXA PWUDNJ, DBP VXIRSJX PWXO RAX XRJO, VSP VXIRSJX PWXO RAX WRAL, VXIRSJX PWRP NBRK FUKK JXATX PB BANRDUZX RDL GXRJSAX PWX VXJP BE BSA XDXANUXJ RDL JMUKKJ, VXIRSJX PWRP IWRKKXDNX UJ BDX PWRP FX RAX FUKKUDN PB RIIXCP, BDX FX RAX SDFUKKUDN PB CBJPCBDX, RDL BDX FWUIW FX UDPXDL PB FUD, RDL PWX BPWXAJ, PBB.” View Hint Destination Moon – Most frequent letters: letter “E” and letter “O” “ZE KYV KFNE NYVIV Z NRJ SFIE CZMVU R DRE NYF JRZCVU KF JVR REU YV KFCU LJ FW YZJ CZWV ZE KYV CREU FW JLSDRIZEVJ JF NV JRZCVU LG KF KYV JLE ‘KZC NV WFLEU R JVR FW XIVVE REU NV CZMVU SVEVRKY KYV NRMVJ ZE FLI PVCCFN JLSDRIZEV NV RCC CZMV ZE R PVCCFN JLSDRIZEV PVCCFN JLSDRIZEV, PVCCFN JLSDRIZEV NV RCC CZMV ZE R PVCCFN JLSDRIZEV PVCCFN JLSDRIZEV, PVCCFN JLSDRIZEV REU FLI WIZVEUJ RIV RCC RSFRIU DREP DFIV FW KYVD CZMV EVOK UFFI REU KYV SREU SVXZEJ KF GCRP NV RCC CZMV ZE R PVCCFN JLSDRIZEV PVCCFN JLSDRIZEV, PVCCFN JLSDRIZEV NV RCC CZMV ZE R PVCCFN JLSDRIZEV PVCCFN JLSDRIZEV, PVCCFN JLSDRIZEV (WLCC JGVVU RYVRU DI. GRIBVI, WLCC JGVVU RYVRU WLCC JGVVU RYVRU ZK ZJ, JVIXVREK RTKZFE JKRKZFE, RTKZFE JKRKZFE RPV, RPV, JZI, WZIV TRGKRZE, TRGKRZE) RJ NV CZMV R CZWV FW VRJV VMVIPFEV FW LJ YRJ RCC NV EVVU (YRJ RCC NV EVVU) JBP FW SCLV (JBP FW SCLV) REU JVR FW XIVVE (REU JVR FW XIVVE) ZE FLI PVCCFN JLSDRIZEV (ZE FLI PVCCFN, JLSDRIZEV, YR YR) NV RCC CZMV ZE R PVCCFN JLSDRIZEV PVCCFN JLSDRIZEV, PVCCFN JLSDRIZEV NV RCC CZMV ZE R PVCCFN JLSDRIZEV PVCCFN JLSDRIZEV, PVCCFN JLSDRIZEV NV RCC CZMV ZE R PVCCFN JLSDRIZEV PVCCFN JLSDRIZEV, PVCCFN JLSDRIZEV NV RCC CZMV ZE R PVCCFN JLSDRIZEV PVCCFN JLSDRIZEV, PVCCFN JLSDRIZEV” View Hint A song by The Beattles “WAOUWBS HVSFS’G BC QCIBHFWSG WH WGB’H VOFR HC RC BCHVWBU HC YWZZ CF RWS TCF OBR BC FSZWUWCB, HCC WAOUWBS OZZ HVS DSCDZS ZWJWBU ZWTS WB DSOQS MCI, MCI AOM GOM W’A O RFSOASF PIH W’A BCH HVS CBZM CBS W VCDS GCASROM MCI KWZZ XCWB IG OBR HVS KCFZR KWZZ PS OG CBS WAOUWBS BC DCGGSGGWCBG W KCBRSF WT MCI QOB BC BSSR TCF UFSSR CF VIBUSF O PFCHVSFVCCR CT AOB WAOUWBS OZZ HVS DSCDZS GVOFWBU OZZ HVS KCFZR MCI, MCI AOM GOM W’A O RFSOASF PIH W’A BCH HVS CBZM CBS W VCDS GCASROM MCI KWZZ XCWB IG OBR HVS KCFZR KWZZ ZWJS OG CBS” View Hint A song by John Lennon “SBRL ZRFDHSRLY OHZ YLABYULK AV OPZ OVTL WSHULA VM AHAVVPUL PU HU HAALTWA AV YLZJBL OPZ MYPLUK OHU ZVSV MYVT AOL JSBAJOLZ VM AOL CPSL NHUNZALY QHIIH AOL OBAA.
SPAASL KVLZ SBRL RUVD AOHA AOL NHSHJAPJ LTWPYL OHZ ZLJYLASF ILNBU JVUZAYBJAPVU VU H ULD HYTVYLK ZWHJL ZAHAPVU LCLU TVYL WVDLYMBS AOHU AOL MPYZA KYLHKLK KLHAO ZAHY. DOLU JVTWSLALK, AOPZ BSAPTHAL DLHWVU DPSS ZWLSS JLYAHPU KVVT MVY AOL ZTHSS IHUK VM YLILSZ ZAYBNNSPUN AV YLZAVYL MYLLKVT AV AOL NHSHEF…” View Hint Star wars opening crawl Cybersecurity Log Analysis Workflow Explained – From Log Collection to Incident Response Log analysis is the backbone of modern cybersecurity operations. Every attack, misconfiguration, and system failure leaves traces in logs. Organizations that cannot collect and analyze logs effectively are operating blind .
This post provides a deep, textbook-style explanation of the Cybersecurity Log Analysis Workflow, based on the visual diagram above. It is written for: Log analysis is the process of collecting, processing, correlating, and analyzing log data generated by systems, networks, applications, and cloud platforms to identify security threats and operational issues.
Modern attacks often bypass traditional perimeter defenses. Logs provide visibility after initial compromise . Each stage builds on the previous one. If collection or normalization fails, investigation becomes ineffective. Log collection is the process of gathering raw events from multiple sources across the IT environment in real time. Attackers often try to delete or modify logs. Centralized collection reduces this risk and preserves evidence.
Normalization converts raw logs from different formats into a consistent, structured, and searchable format. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/HTTP%20cookie • https://en.wikipedia.org/wiki/Signal%20%28software%29 • https://en.wikipedia.org/wiki/Encryption • https://eureka.patsnap.com/triz-case/searchable-encrypted-audit-logs • https://www.geeksforgeeks.org/system-design/centralized-logging-systems-system-design/ • https://oneuptime.com/blog/post/2026-01-30-log-encryption/view • https://www.101computing.net/frequency-analysis/ • https://www.learncyber.in/2026/01/cybersecurity-log-analysis-workflow.html
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Encrypted Log Search Mechanism.
[*] Metasploit Scan Running on Target Subnet for Encrypted Log Search Mechanism... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |