Complete Technical Paper Content — End To End Zero Knowledge Secure Vault
Overview & System Context
End To End Zero Knowledge Secure Vault: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8526 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Bitwarden is a freemium open-source password management service that is used to store sensitive information, such as website credentials, in an encrypted vault. It is owned and developed by Bitwarden, Inc.
No critical issues were discovered during the two audits. Two security issues that Cure53 rated high were discovered during the source code audit and penetration testing. These were fixed quickly by Bitwarden and the third-party HubSpot. All other issues were either rated low or informational only. In January, Bitwarden announced the acquisition of Swedish startup Passwordless.dev for an undisclosed amount.
Passwordless.dev provided an open-source solution allowing developers to easily implement passwordless authentication based on the standards WebAuthn and FIDO2. Bitwarden also launched a beta software service allowing third-party developers the use of biometric sign-in technologies – including Apple's Touch ID and Face ID, and Microsoft's Windows Hello – in their apps.
Shamir's secret sharing (SSS) is an efficient secret sharing algorithm for distributing private information (the "secret") among a group, first developed by Adi Shamir in 1979. The secret cannot be revealed unless a minimum number of the group's members act together to pool their knowledge. To achieve this, the secret is mathematically divided into parts (the "shares") from which the secret can be reassembled only when a sufficient number of shares are combined. SSS has the property of information-theoretic security, meaning that even if an attacker steals some shares, it is impossible for the attacker to reconstruct the secret unless they have stolen a sufficient number of shares. Shamir's secret sharing is used in some applications to share the access keys to a master secret.
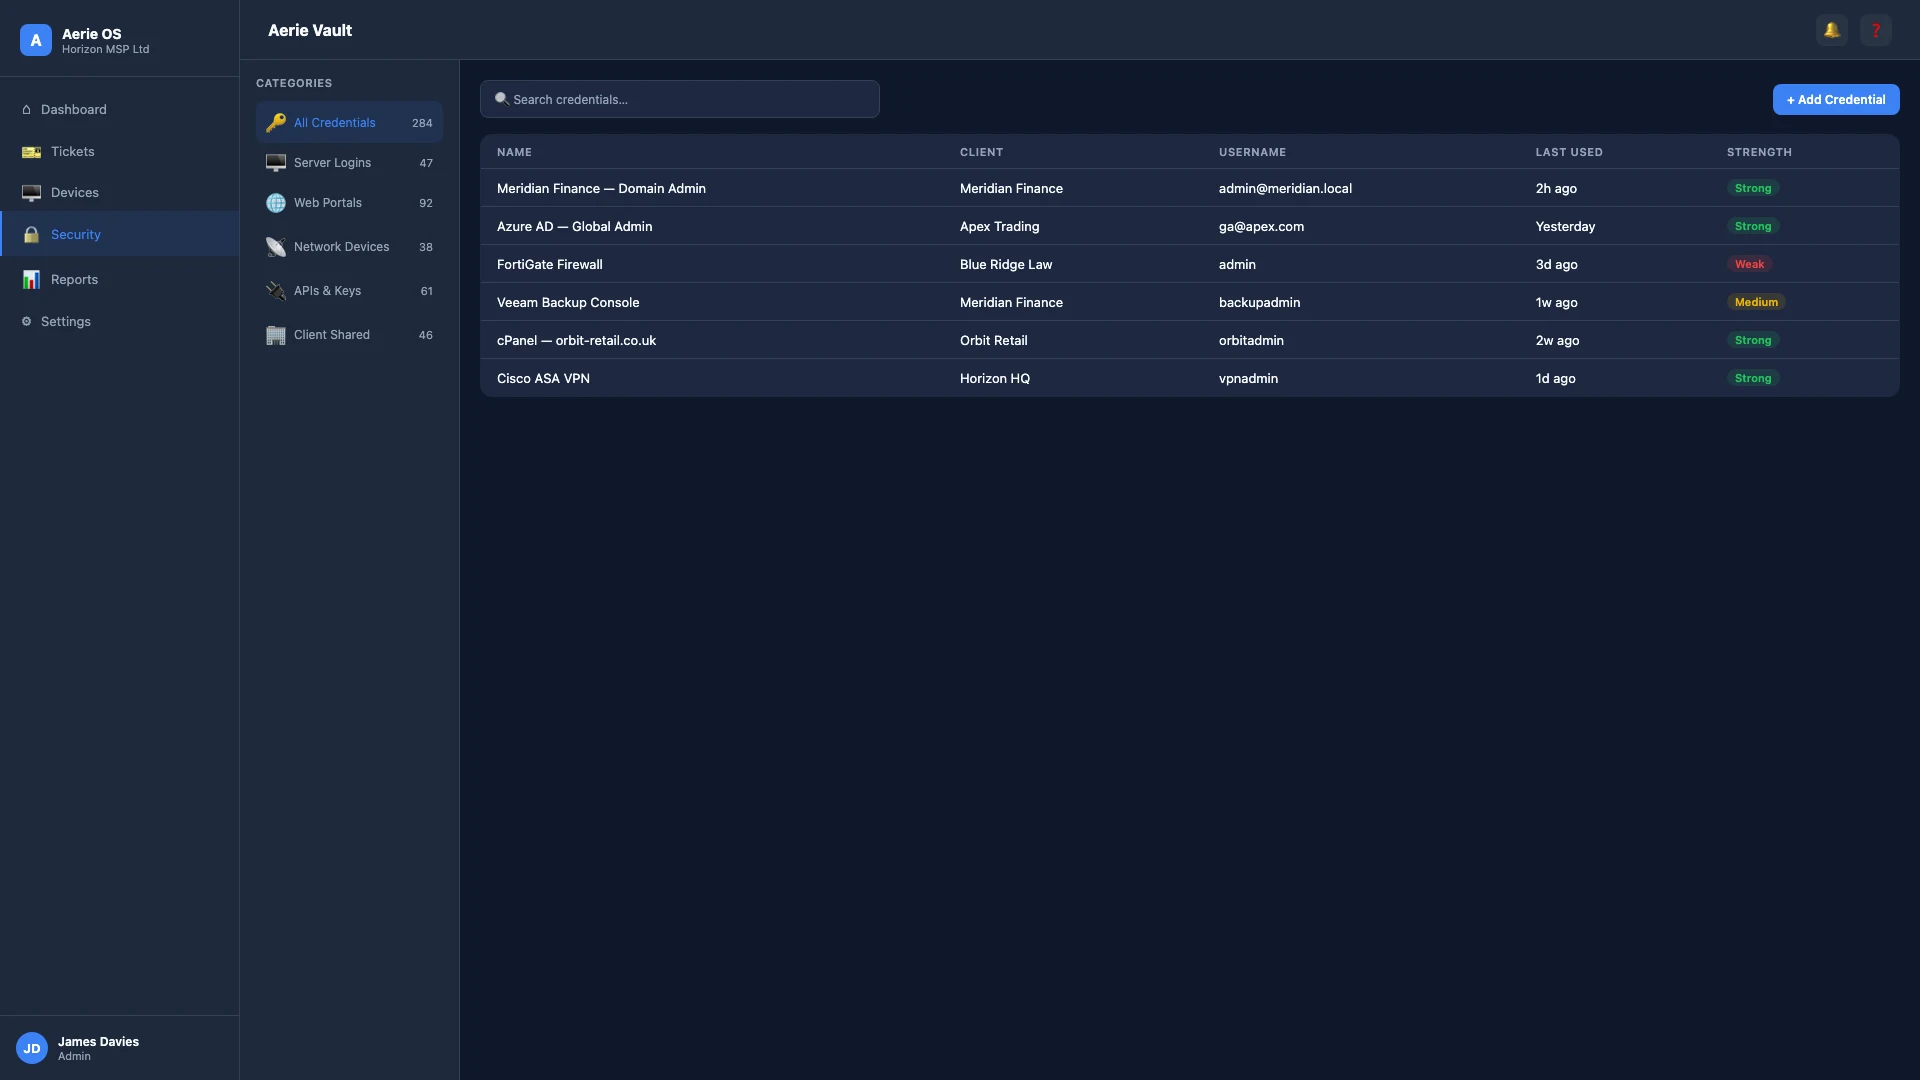
Figure 1: Aerie Vault | Zero-Knowledge MSP Password Manager share a key for decrypting the root key of a password manager, recover a user key for encrypted email access, share the passphrase used to recreate a master secret, which is in turn used to access a cryptocurrency wallet and recover the combination to a physical safe.
Secure: The scheme has information-theoretic security. Minimal: The size of each piece does not exceed the size of the original data. Extensible: For any given threshold, shares can be dynamically added or deleted without affecting existing shares Dynamic: Security can be enhanced without changing the secret, but by changing the polynomial occasionally (keeping the same free term) and constructing a new share for each of the participants. Flexible: In organizations where hierarchy is important, each participant can be issued different numbers of shares according to their importance inside the organization. For instance, with a threshold of 3, the president could unlock the safe alone if given three shares, while three secretaries with one share each must combine their shares to unlock the safe. Weaknesses include: No verifiable secret sharing: During the share reassembly process, SSS does not provide a way to verify the correctness of each share being used. Verifiable secret sharing aims to verify that shareholders are honest and not submitting fake shares.
Single point of failure: The secret must exist in one place when it is split into shares, and again in one place when it is reassembled. These are attack points, and other schemes including multisignature eliminate at least one of these single points of failure. Knowledge of any k {\displaystyle k} or more shares S i {\displaystyle S_{i}} makes S {\displaystyle S} computable. That is, the entire secret S {\displaystyle S} can be reconstructed from any combination of k {\displaystyle k} shares. Knowledge of any k − 1 {\displaystyle k-1} or fewer shares S i {\displaystyle S_{i}} leaves S {\displaystyle S} completely undetermined, in the sense that the possible values for S {\displaystyle S} remain as likely with knowledge of up to k − 1 {\displaystyle k-1} shares as with knowledge of 0 {\displaystyle 0} shares. The secret S {\displaystyle S} cannot be reconstructed with fewer than k {\displaystyle k} shares. If n = k {\displaystyle n=k} , then all of the shares are needed to reconstruct the secret S {\displaystyle S} . Assume that the secret S {\displaystyle S} can be represented as an element a 0 {\displaystyle a_{0}} of a finite field G F ( q ) {\displaystyle \mathrm {GF} (q)} (where q {\displaystyle q} is greater than the number n {\displaystyle n} of shares being generated). Randomly choose k − 1 {\displaystyle k-1} elements, a 1 , I , a k − 1 {\displaystyle a_{1},\cdots ,a_{k-1}} , from G F ( q ) {\displaystyle \mathrm {GF} (q)} and construct the polynomial f ( x ) = a 0 + a 1 x + a 2 x 2 + a 3 x 3 + I + a k − 1 x k − 1 {\displaystyle f\left(x\right)=a_{0}+a_{1}x+a_{2}x^{2}+a_{3}x^{3}+\cdots +a_{k-1}x^{k-1}} . Compute any n {\displaystyle n} points out on the curve, for instance set i = 1 , … , n {\displaystyle i=1,\ldots ,n} to find points ( i , f ( i ) ) {\displaystyle \left(i,f\left(i\right)\right)} . Every participant is given a point (a non-zero input to the polynomial, and the corresponding output).
Given any subset of k {\displaystyle k} of these pairs, a 0 {\displaystyle a_{0}} can be obtained using interpolation, with one possible formula for doing so being a 0 = f ( 0 ) = ∑ j = 0 k − 1 y j ∏ m = 0 m ≠ j k − 1 x m x m − x j {\displaystyle a_{0}=f(0)=\sum _{j=0}^{k-1}y_{j}\prod _{\begin{smallmatrix}m\,=\,0\\m\,\neq \,j\end{smallmatrix}}^{k-1}{\frac {x_{m}}{x_{m}-x_{j}}}} , where the list of points on the polynomial is given as k {\displaystyle k} pairs of the form ( x i , y i ) {\displaystyle (x_{i},y_{i})} . Note that f ( 0 ) {\displaystyle f(0)} is equal to the first coefficient of polynomial f ( x ) {\displaystyle f(x)} . More generally, any value f ( α ) {\displaystyle f(\alpha )} , where α ∈ G F ( q ) {\displaystyle \alpha \in \mathrm {GF} (q)} , may be used as the secret instead of f ( 0 ) {\displaystyle f(0)} . The leading coefficient a k − 1 {\displaystyle a_{k-1}} may similarly be interpreted as the value f ( ∞ ) {\displaystyle f(\infty )} on the projective line and can also be used as the secret.
These are precisely the polynomial-derived quantities that remain perfectly hidden from every coalition of fewer than k {\displaystyle k} participants. In contrast, other linear combinations of the polynomial coefficients, including the intermediate coefficients, a 1 , … , a k − 2 {\displaystyle a_{1},\ldots ,a_{k-2}} , may be determined by some coalitions of fewer than k {\displaystyle k} participants.
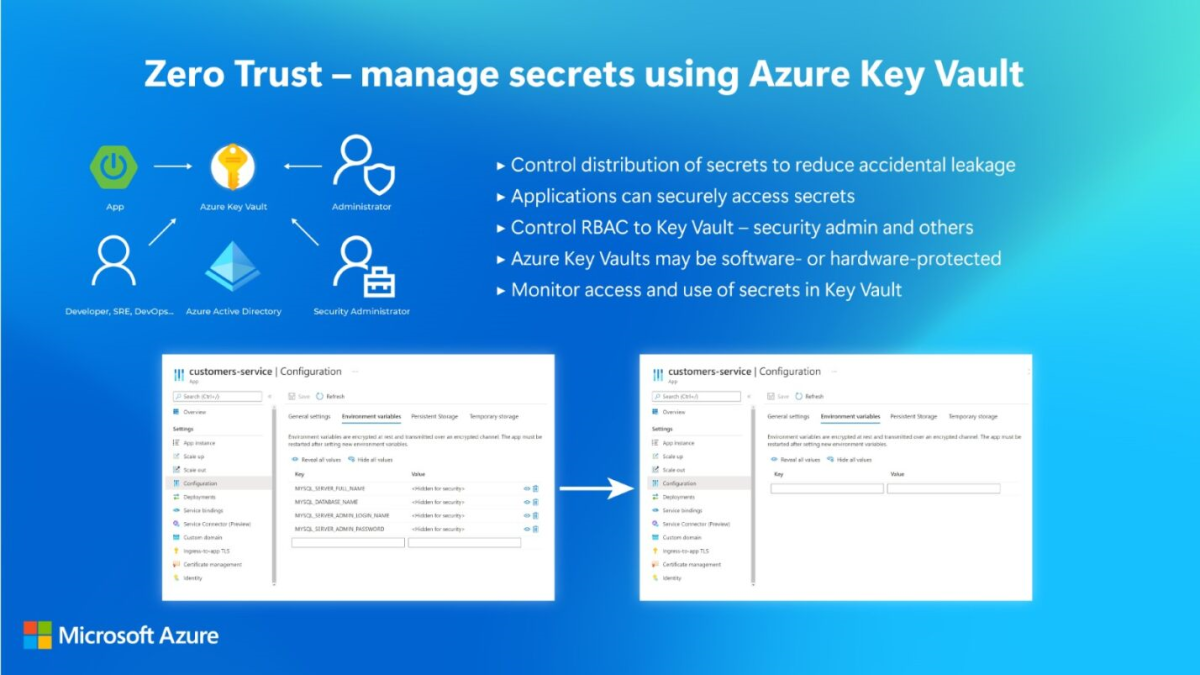
Figure 2: Scale with End-to-End Security, Monitoring, and Automation - Azure ... This yields coefficients ( a 0 = 1234 ; a 1 = 166 ; a 2 = 94 ) , {\displaystyle (a_{0}=1234;a_{1}=166;a_{2}=94),} where a 0 {\displaystyle a_{0}} is the secret The polynomial to produce secret shares (points) is therefore: f ( x ) = 1234 + 166 x + 94 x 2 {\displaystyle f(x)=1234+166x+94x^{2}} Six points D x − 1 = ( x , f ( x ) ) {\displaystyle D_{x-1}=(x,f(x))} from the polynomial are constructed as: D 0 = ( 1 , 1494 ) ; D 1 = ( 2 , 1942 ) ; D 2 = ( 3 , 2578 ) ; D 3 = ( 4 , 3402 ) ; D 4 = ( 5 , 4414 ) ; D 5 = ( 6 , 5614 ) {\displaystyle D_{0}=(1,1494);D_{1}=(2,1942);D_{2}=(3,2578);D_{3}=(4,3402);D_{4}=(5,4414);D_{5}=(6,5614)} Figure 3: From Now On Users Will Have End-to-End Zero Knowledge Encryption ...
Each participant in the scheme receives a different point (a pair of x {\displaystyle x} and f ( x ) {\displaystyle f(x)} ). Because D x − 1 {\displaystyle D_{x-1}} is used instead of D x {\displaystyle D_{x}} the points start from ( 1 , f ( 1 ) ) {\displaystyle (1,f(1))} and not ( 0 , f ( 0 ) ) {\displaystyle (0,f(0))} . This is necessary because f ( 0 ) {\displaystyle f(0)} is the secret. I 0 ( x ) = x − x 1 x 0 − x 1 ⋅ x − x 2 x 0 − x 2 = x − 4 2 − 4 ⋅ x − 5 2 − 5 = 1 6 x 2 − 3 2 x + 10 3 {\displaystyle \ell _{0}(x)={\frac {x-x_{1}}{x_{0}-x_{1}}}\cdot {\frac {x-x_{2}}{x_{0}-x_{2}}}={\frac {x-4}{2-4}}\cdot {\frac {x-5}{2-5}}={\frac {1}{6}}x^{2}-{\frac {3}{2}}x+{\frac {10}{3}}} I 1 ( x ) = x − x 0 x 1 − x 0 ⋅ x − x 2 x 1 − x 2 = x − 2 4 − 2 ⋅ x − 5 4 − 5 = − 1 2 x 2 + 7 2 x − 5 {\displaystyle \ell _{1}(x)={\frac {x-x_{0}}{x_{1}-x_{0}}}\cdot {\frac {x-x_{2}}{x_{1}-x_{2}}}={\frac {x-2}{4-2}}\cdot {\frac {x-5}{4-5}}=-{\frac {1}{2}}x^{2}+{\frac {7}{2}}x-5} I 2 ( x ) = x − x 0 x 2 − x 0 ⋅ x − x 1 x 2 − x 1 = x − 2 5 − 2 ⋅ x − 4 5 − 4 = 1 3 x 2 − 2 x + 8 3 {\displaystyle \ell _{2}(x)={\frac {x-x_{0}}{x_{2}-x_{0}}}\cdot {\frac {x-x_{1}}{x_{2}-x_{1}}}={\frac {x-2}{5-2}}\cdot {\frac {x-4}{5-4}}={\frac {1}{3}}x^{2}-2x+{\frac {8}{3}}} Using the formula for polynomial interpolation, f ( x ) {\displaystyle f(x)} is: f ( x ) = ∑ j = 0 2 y j ⋅ I j ( x ) = y 0 I 0 ( x ) + y 1 I 1 ( x ) + y 2 I 2 ( x ) = 1942 ( 1 6 x 2 − 3 2 x + 10 3 ) + 3402 ( − 1 2 x 2 + 7 2 x − 5 ) + 4414 ( 1 3 x 2 − 2 x + 8 3 ) = 1234 + 166 x + 94 x 2 {\displaystyle {\begin{aligned}f(x)&=\sum _{j=0}^{2}y_{j}\cdot \ell _{j}(x)\\[6pt]&=y_{0}\ell _{0}(x)+y_{1}\ell _{1}(x)+y_{2}\ell _{2}(x)\\[6pt]&=1942\left({\frac {1}{6}}x^{2}-{\frac {3}{2}}x+{\frac {10}{3}}\right)+3402\left(-{\frac {1}{2}}x^{2}+{\frac {7}{2}}x-5\right)+4414\left({\frac {1}{3}}x^{2}-2x+{\frac {8}{3}}\right)\\[6pt]&=1234+166x+94x^{2}\end{aligned}}} Recalling that the secret is the free coefficient, which means that S = 1234 {\displaystyle S=1234} , and the secret has been recovered.
f ( 0 ) = ∑ j = 0 k − 1 y j ∏ m = 0 m ≠ j k − 1 x m x m − x j {\displaystyle f(0)=\sum _{j=0}^{k-1}y_{j}\prod _{\begin{smallmatrix}m\,=\,0\\m\,\neq \,j\end{smallmatrix}}^{k-1}{\frac {x_{m}}{x_{m}-x_{j}}}} Fill the formula for f ( x ) {\displaystyle f(x)} with S {\displaystyle S} and the value of k : f ( x ) = S + a 1 x + I + a k − 1 x k − 1 ⇒ f ( x ) = S + a 1 x + a 2 x 2 {\displaystyle k:f(x)=S+a_{1}x+\cdots +a_{k-1}x^{k-1}\Rightarrow {}f(x)=S+a_{1}x+a_{2}x^{2}} Fill (1) with the values of D {\displaystyle D} 's x {\displaystyle x} and f ( x ) : 1942 = S + a 1 2 + a 2 2 2 ⇒ S = 1942 − 2 a 1 − 4 a 2 {\displaystyle f(x):1942=S+a_{1}2+a_{2}2^{2}\Rightarrow {}S=1942-2a_{1}-4a_{2}} The above attack exploits constraints on the values that the polynomial may take by virtue of how it was constructed: the polynomial must have coefficients that are integers, and the polynomial must take an integer as value when evaluated at each of the coordinates used in the scheme. This reduces its possible values at unknown points, including the resultant secret, given fewer than k {\displaystyle k} shares. This problem can be remedied by using finite field arithmetic. A finite field always has size q = p r {\displaystyle q=p^{r}} , where p {\displaystyle p} is a prime and r {\displaystyle r} is a positive integer. The size q {\displaystyle q} of the field must satisfy q > n {\displaystyle q>n} , and that q {\displaystyle q} is greater than the number of possible values for the secret, though the latter condition may be circumvented by splitting the secret into smaller secret values, and applying the scheme to each of these. In our example below, we use a prime field (i.e. r = 1). The figure shows a polynomial curve over a finite field. In practice this is only a small change. The order q of the field (i.e. the number of values that it has) must be chosen to be greater than the number of participants and the number of values that the secret a 0 = S {\displaystyle a_{0}=S} may take. All calculations involving the polynomial must also be calculated over the field (mod p in our example, in which p = q {\displaystyle p=q} is taken to be a prime) instead of over the integers. Both the choice of the field and the mapping of the secret to a value in this field are considered to be publicly known. For this example, choose p = 1613 {\displaystyle p=1613} , so the polynomial becomes f ( x ) = 1234 + 166 x + 94 x 2 mod 1613 {\displaystyle f(x)=1234+166x+94x^{2}{\bmod {1613}}} which gives the points: ( 1 , 1494 ) ; ( 2 , 329 ) ; ( 3 , 965 ) ; ( 4 , 176 ) ; ( 5 , 1188 ) ; ( 6 , 775 ) {\displaystyle (1,1494);(2,329);(3,965);(4,176);(5,1188);(6,775)} This time Eve doesn't gain any information when she finds a D x {\displaystyle D_{x}} (until she has k {\displaystyle k} points).
Suppose again that Eve finds D 0 = ( 1 , 1494 ) {\displaystyle D_{0}=\left(1,1494\right)} and D 1 = ( 2 , 329 ) {\displaystyle D_{1}=\left(2,329\right)} , and the public information is: n = 6 , k = 3 , p = 1613 , f ( x ) = a 0 + a 1 x + I + a k − 1 x k − 1 mod p , a 0 = S , a i ∈ N {\displaystyle n=6,k=3,p=1613,f(x)=a_{0}+a_{1}x+\dots +a_{k-1}x^{k-1}\mod {p},a_{0}=S,a_{i}\in \mathbb {N} } . Attempting the previous attack, Eve can: Fill the f ( x ) {\displaystyle f(x)} -formula with S {\displaystyle S} and the value of k {\displaystyle k} and p {\displaystyle p} : f ( x ) = S + a 1 x + I + a 3 − 1 x 3 − 1 mod 1613 {\displaystyle f(x)=S+a_{1}x+\dots +a_{3-1}x^{3-1}\mod 1613} Fill (1) with the values of D 0 {\displaystyle D_{0}} 's x {\displaystyle x} and f ( x ) : 1494 ≡ S + a 1 1 + a 2 1 2 ( mod 1613 ) ⇒ 1494 ≡ S + a 1 + a 2 ( mod 1613 ) {\displaystyle f(x):1494\equiv S+a_{1}1+a_{2}1^{2}{\pmod {1613}}\Rightarrow {}1494\equiv S+a_{1}+a_{2}{\pmod {1613}}} Fill (1) with the values of D 1 {\displaystyle D_{1}} 's x {\displaystyle x} and f ( x ) : 1942 ≡ S + a 1 2 + a 2 2 2 ( mod 1613 ) ⇒ 1942 ≡ S + 2 a 1 + 4 a 2 ( mod 1613 ) {\displaystyle f(x):1942\equiv S+a_{1}2+a_{2}2^{2}{\pmod {1613}}\Rightarrow {}1942\equiv S+2a_{1}+4a_{2}{\pmod {1613}}} Subtract (3)-(2): ( 1942 − 1494 ) ≡ ( S − S ) + ( 2 a 1 − a 1 ) + ( 4 a 2 − a 2 ) ( mod 1613 ) ⇒ 448 ≡ a 1 + 3 a 2 ( mod 1613 ) {\displaystyle (1942-1494)\equiv (S-S)+(2a_{1}-a_{1})+(4a_{2}-a_{2}){\pmod {1613}}\Rightarrow {}448\equiv a_{1}+3a_{2}{\pmod {1613}}} and rewrite this as a 1 ≡ 448 − 3 a 2 ( mod 1613 ) {\displaystyle a_{1}\equiv 448-3a_{2}{\pmod {1613}}} There are p {\displaystyle p} possible values for a 1 {\displaystyle a_{1}} . She knows that [ 448 , 445 , 442 , … ] {\displaystyle [448,445,442,\ldots ]} always decreases by 3, so if p {\displaystyle p} were divisible by 3 {\displaystyle 3} she could conclude a 1 ∈ [ 1 , 4 , 7 , … ] {\displaystyle a_{1}\in [1,4,7,\ldots ]} . However, p {\displaystyle p} is prime, so she can not conclude this.
Thus, using a finite field avoids this possible attack. Also, even though Eve can conclude that S ≡ 1046 + 2 a 2 ( mod 1613 ) {\displaystyle S\equiv 1046+2a_{2}{\pmod {1613}}} , it does not provide any additional information, since the "wrapping around" behavior of modular arithmetic prevents the leakage of "S is even", unlike the example with integer arithmetic above. Tokenization, when applied to data security, is the process of substituting a sensitive data element with a non-sensitive equivalent, referred to as a token, that has no intrinsic or exploitable meaning or value. The token is a reference (i.e. identifier) that maps back to the sensitive data through a tokenization system. The mapping from original data to a token uses methods that render tokens infeasible to reverse in the absence of the tokenization system, for example using tokens created from random numbers. A one-way cryptographic function is used to convert the original data into tokens, making it difficult to recreate the original data without obtaining entry to the tokenization system's resources. To deliver such services, the system maintains a vault database of tokens that are connected to the corresponding sensitive data. Protecting the system vault is vital to the system, and improved processes must be put in place to offer database integrity and physical security. The tokenization system must be secured and validated using security best practices applicable to sensitive data protection, secure storage, audit, authentication and authorization. The tokenization system provides data processing applications with the authority and interfaces to request tokens, or detokenize back to sensitive data. The security and risk reduction benefits of tokenization require that the tokenization system is logically isolated and segmented from data processing systems and applications that previously processed or stored sensitive data replaced by tokens. Only the tokenization system can tokenize data to create tokens, or detokenize back to redeem sensitive data under strict security controls. The token generation method must be proven to have the property that there is no feasible means through direct attack, cryptanalysis, side channel analysis, token mapping table exposure or brute force techniques to reverse tokens back to live data. Replacing live data with tokens in systems is intended to minimize exposure of sensitive data to those applications, stores, people and processes, reducing risk of compromise or accidental exposure and unauthorized access to sensitive data. Applications can operate using tokens instead of live data, with the exception of a small number of trusted applications explicitly permitted to detokenize when strictly necessary for an approved business purpose. Tokenization systems may be operated in-house within a secure isolated segment of the data center, or as a service from a secure service provider. Tokenization may be used to safeguard sensitive data involving, for example, bank accounts, financial statements, medical records, criminal records, driver's licenses, loan applications, stock trades, voter registrations, and other types of personally identifiable information (PII). Tokenization is often used in credit card processing. The PCI Council defines tokenization as "a process by which the primary account number (PAN) is replaced with a surrogate value called a token. A PAN may be linked to a reference number through the tokenization process. In this case, the merchant simply has to retain the token and a reliable third party controls the relationship and holds the PAN. The token may be created independently of the PAN, or the PAN can be used as part of the data input to the tokenization technique. The communication between the merchant and the third-party supplier must be secure to prevent an attacker from intercepting to gain the PAN and the token. De-tokenization is the reverse process of redeeming a token for its associated PAN value. The security of an individual token relies predominantly on the infeasibility of determining the original PAN knowing only the surrogate value". The choice of tokenization as an alternative to other techniques such as encryption will depend on varying regulatory requirements, interpretation, and acceptance by respective auditing or assessment entities. This is in addition to any technical, architectural or operational constraint that tokenization imposes in practical use.
The application sends the tokenization data and authentication information to the tokenization system. It is stopped if authentication fails and the data is delivered to an event management system. As a result, administrators can discover problems and effectively manage the system. The system moves on to the next phase if authentication is successful. Using one-way cryptographic or random generation techniques, a token is generated and kept in a highly secure data vault. The new token is provided to the application for further use, replacing the sensitive data for processing and storage. Tokenization systems share several components according to established standards.
Token generation is the process of producing a token using any means, such as one-way nonreversible cryptographic functions (e.g., a hash function with a strong, secret salt) or assignment via a randomly generated number. Random number generator (RNG) techniques are often the best choice for generating token values. Token mapping – this is the process of assigning the created token value to its original value. To enable permitted look-ups of the original value using the token as the index, a secure cross-reference database must be constructed. Token data store – this is a central repository for the token mapping process that holds the original sensitive values and their related token values. Sensitive data and token values must be securely kept in an encrypted format. Management of cryptographic keys. Strong key management procedures are required for sensitive data encryption on token data stores.
2. System Architecture & Core Working Principles Before comparing price, limits and features, compare the companies themselves: which legal entity you sign with, where it is based, how long it has operated and how you reach support. Compare authenticator apps by the codes they hold, the vault protection they use, the price and term they charge, their platform reach, their audit record and their ownership, with worked examples from NordPass, Bitwarden and Sinew Software Systems.
Compare background check and people search services on price, free search access, record opt-out, regulatory posture and support reach, and see where each one fits your search. Compare identity theft protection on price, device limits, monitoring quotas, features and the jurisdiction and support each provider gives you.
Parental control apps differ most in billing period, device counts, feature coverage and how much the vendor can read, so compare those lines before reading reviews. A step-by-step way to weigh price, device limits, encryption and support across password managers, with worked examples from the brands we track.
Comparing privacy tools comes down to four checks: the plan and period behind the price, the limits inside the tier, the encryption and logging claims, and the company standing behind the service. A hardware security key is judged on four things: what it costs, what it plugs into, what it protects, and who you call when it stops working.
Compare VPN pricing, device limits, trial terms and privacy claims section by section, using Apple Inc. and ESET Brasil as worked examples and the market ranges to benchmark them against. Every identity protection brand wraps a legal company, and the entity name, base country, company age and support routes tell you who you are really buying from before you weigh price.
Compare password manager companies through their legal entities, headquarters, founding years, support routes and product reviews. Ten privacy and ad blocking brands differ in founding year, legal entity, headquarters and support routes, and those four details tell you who you are actually contracting with.
Device limits and platform lists separate VPN providers faster than price alone, and here is how to read both side by side. Every VPN is a company before it is an app, and this guide lines up the founding year, headquarters, legal entity and support channels of the leading providers so you know who you are paying before you compare plan price … Here is how to compare the core features of eight VPNs, from device limits and platform coverage to protocols, privacy features and server reach.
Brands with a free tier set very different limits on it, so the free plan, the trial length and the refund window are separate numbers to check before you pick. Monthly rates, long-term discounts, plan lengths, renewal prices and currencies differ enough across these VPNs that price is best compared line by line rather than at a glance.
A workable way to compare VPNs on where they are registered, who owns them, what they log and whether an outside auditor has checked their claims. Most VPN listings lead with a discounted long-term rate, so the comparison that matters is the renewal price each brand charges once that rate runs out.
A zero-knowledge encrypted vault system setup script for Linux. Uses LUKS for hardware level USB protection and Rclone Crypt for file level cloud encryption. Includes one click automation scripts to open, sync, and lock your data without exposing your keys to Google. A zero-knowledge encrypted file sharing system with end-to-end encryption, built with Python and Flask. This application provides secure file storage and sharing capabilities with features like file versioning, access control, and comprehensive audit logging.
Zero-knowledge encrypted file sharing system with end-to-end encryption. Features include file versioning, access control, and audit logging. Built with modern cryptographic standards and security best practices. GhostVault keeps your files, notes, and records locked with keys only you control. Share selectively, audit instantly, and sleep soundly.
Files are encrypted before they leave your device using modern, vetted algorithms. Your private keys never touch our servers. Organize work into Spaces with roleIbased access (Owner, Admin, Contributor, Viewer). Invite with timeIboxed, linkIlimited sharing. Automatic version history and softIdelete let you roll back mistakes. Optional geoIredundant backups.
Every access, share, and edit is recorded with timestamp, device, and IP for complete visibility. Use the REST API or dropIin SDK. Webhooks notify your systems of changes in real time. No trackers, no ad tech. Minimal telemetry with on/off toggles and clear data retention controls. Note: Replace algorithm & compliance details with your actual implementation before launch.
Your data is encrypted locally with keys only you control. Our servers handle ciphertext and metadata necessary for sync/sharing, not plaintext contents. Yes, if you enable the recovery kit. Store it offline. Without recovery enabled, we cannot restore access. Business plan customers can request a DPA. A BAA is possible if your implementation meets HIPAA requirements. Replace this with your policy.
In a true zero-knowledge design, encryption keys derive from secrets controlled by the user and are not available to the storage provider. This improves confidentiality but makes password and recovery design critical because the provider may be unable to restore access. Zero knowledge means the service cannot read your files because it never receives or stores your decryption keys. Content encrypts entirely on your device, travels across the internet encrypted, and remains encrypted on the server. Only you and people you authorize can decrypt the content. The entire architecture is designed to eliminate the need to trust the service provider with your plaintext data.
Most security overviews gloss over the crucial elements: key recovery, who holds the encryption keys, and the privacy risk posed by filename leaks. They frequently mix up provider-encrypted-at-rest with true end-to-end setups. This overview explains what is actually private, shows you real-world settings, and provides fixes for common errors without risking your valuable data. Understanding who possesses the key is the single most important metric for evaluating true privacy.
Client Side Keys: The unique encryption key is derived from your passphrase and is created and stored exclusively on your device. The service never learns, transmits, or stores the key itself. 3. Software Implementation, Frameworks & Protocols Blind Storage: Servers hold only cipher-text. This means the content is useless to the provider’s staff, useless for internal search and indexing, and inaccessible in response to routine legal requests.
Local Compromise: It does not protect against local malware. If your device is compromised while the vault is unlocked and mounted, the malware can access the unencrypted files. Cloud Secure (developed by Newsoftwares.net) is a powerful example of a client-side encryption overlay for mainstream cloud providers like Google Drive, Dropbox, and iCloud. You create a secure vault on your local machine, put sensitive files inside, and let your normal cloud sync client move only the resulting ciphertext. The provider simply stores unreadable blobs.
You keep the sole key and control all recovery options. You require individual file encryption , which ensures that changing one file only re-syncs that single file, unlike monolithic containers (like VeraCrypt). This is the clean path that balances security and convenience for desktop users on a mainstream cloud.
Test on a Second Device: On a second device, install Cloud Secure and connect the same cloud account. Unlock with your passphrase or recovery key. Version History: Your provider stores the version history of the ciphertext , not the files inside. For document history, use your document editor’s internal versioning before moving files into the vault.
SMB Admin: Keep regulated documents in a client-side vault. For team editing, use a dedicated end-to-end provider. Document the recovery process and test it quarterly. No. Encrypted at rest uses provider keys . Zero knowledge keeps keys only on your devices . This is the fundamental difference in who controls the data.
No. If a vendor says they can reset content access without your recovery key, it is not truly zero knowledge. You must rely on your recovery key and backups. Export a copy and wrap it in a 7z archive with AES 256 and encrypted filenames . Send the link and passphrase by different channels .
Yes. Full disk encryption protects local copies and temporary files while the vault is unlocked and open. It adds a second wall of defense if your laptop is lost. Timing, sizes, and IP addresses. Your content stays private, but your metadat, the digital breadcrumb exists. Use a VPN if required by policy.
No. Server search cannot read ciphertext. You must unlock the vault and search locally on your device. A file that is merely “encrypted-at-rest” is safe only until the provider is subpoenaed or breached because they still hold the key. Zero knowledge encryption, whether through a client-side vault like Cloud Secure or a dedicated end-to-end service, flips that threat model entirely.
The answer to “Who holds the key?” determines your content’s ultimate fate. By committing to local encryption, turning on header privacy, and treating your recovery code like a passport, you ensure the answer is you and only you . Stop relying on the cloud provider’s policies. Start controlling your own data. Join millions of users who trust Folder Lock to password protect their most sensitive photos, videos, and documents.
Keeper is a Zero Knowledge security provider. Zero Knowledge is a system architecture that guarantees the highest levels of security and privacy. Encryption and decryption of data always occurs locally on the user's device. Each vault record is encrypted by a unique and client-side generated 256-bit AES encryption key in GCM mode. Each record-level key is wrapped by a 256-bit AES Shared Folder key if it is contained within a Shared Folder.
For Vault users, the Record and Folder Keys are encrypted with another AES-256 key called the Data Key. For Secrets Manager users, the Record and Folder Keys are encrypted with a 256-bit AES Application Key. For users who login with a Master Password, the keys to decrypt and encrypt data are derived from the user’s master password.
For users who login with SSO or Passwordless technology, Elliptic Curve cryptography is used to encrypt and decrypt data at the device level. All encrypted payloads sent to the Keeper servers are additionally wrapped by a 256-bit AES transmission key in addition to TLS, to protect against MITM attacks. The transmission key is generated on the client device and transferred to the server using ECIES encryption via the server's public EC key.
Starting in Q1 2026, Keeper has started the rollout of Quantum-Resistant Cryptography (QRC) as an additional encryption wrapper on the transmission key. Sharing of secrets between users uses Elliptic Curve Cryptography for secure key distribution. Data is encrypted locally on the user’s device before it is transmitted and stored in Keeper’s Cloud Security Vault. When data is synchronized to another device, the data remains encrypted until it is decrypted on the other device.
Keeper is the most secure, certified, tested and audited password security platform in the world. Keeper has the longest-standing SOC 2 and ISO certifications in the industry. Keeper is ISO 27001, 27017 and 27018 certified. Keeper is GDPR compliant, CCPA compliant, HIPAA compliant, FedRAMP High Authorized and StateRAMP Authorized, PCI DSS certified and certified by TrustArc for privacy.
Keeper complies with the EU-U.S. Data Privacy Framework (“EU-U.S. DPF”), the UK Extension to the EU-U.S. DPF and the Swiss-U.S. Data Privacy Framework (“Swiss-U.S. DPF”) as set forth by the U.S. Department of Commerce. Not only do we implement the most secure levels of encryption, we also adhere to very strict internal practices that are continually audited by third parties to help ensure that we continue to develop secure software and provide the world’s most secure cybersecurity platform.
Keeper is GDPR compliant and we are committed to ensuring our business processes and products continue to maintain compliance for our customers in the European Union. Keeper's desktop applications, web applications and mobile applications do not contain any trackers or 3rd party libraries which perform tracking. As an example, see this link for information on Keeper's Android app which shows that no trackers are installed.
Keeper is a fully SaaS platform and currently hosts data in the following Amazon AWS data centers. Customer may host their Keeper tenant in any preferred primary region. Customer data (stored ciphertext) and access to the platform is isolated to the specific region. The Keeper Security Cryptographic Module is FIPS 140-3 validated under certificate #4976. This FIPS 140-3 validation is valid through July 29, 2029. This enables Keeper to meet crypto validation requirements for US Federal and DoD organizations. FIPS 140-3 also aligns with security standards defined by ISO 19790 ensuring consistency with international encryption standards.
Keeper has been issued certificate #4976 under the NIST CMVP. To view the certificate click the link below: Keeper Security Government Cloud Password Manager and Privileged Access Manager is a FedRAMP Authorized provider at the High Impact Level, hosted in AWS GovCloud (US). Keeper Security can be found on the FedRAMP Marketplace . The Federal Risk and Authorization Management Program (FedRAMP) is a U.S. federal government program that provides a standardized approach to security assessment, authorization and continuous monitoring for cloud products and services.
FedRAMP enables government agencies to use modern cloud technologies, with an emphasis on security and protection of federal information and helps accelerate the adoption of secure, cloud solutions. For more information about FedRAMP, please visit https://www.gsa.gov/technology/government-it-initiatives/fedramp . 4. Practical Deployment, Analysis & Case Studies KSGC supports compliance with the United States International Traffic in Arms Regulations (ITAR). Companies that are subject to ITAR export regulations must control unintended exports by restricting access to protected data to U.S. Citizens and by restricting physical location of protected data to the U.S.
Zero-knowledge and zero-trust security, in conjunction with granular permissions, allows organizations to ensure that only approved personnel can access sensitive data. Robust compliance reporting features provide a traceable, electronic audit trail of all actions performed and data entered. Sequestered Customer Success team is comprised of U.S. Persons specifically trained in safe handling of Export Controlled and ITAR-governed data.
The Keeper FedRAMP environment has been audited by an independent third-party assessment organization (3PAO) to validate that proper controls are in place to support customer export compliance programs. Keeper's platform is built with End-to-End Encryption (E2EE) across all devices and endpoints. As described in this technical architecture document: Data stored in the platform is encrypted locally and encrypted in transit between the user's devices Data at rest is encrypted with multiple layers, starting with AES-256 encryption at the record level Data in transit is encrypted with TLS and additional layers of transmission encryption which protects against access MITM, service providers and untrusted networks.
Keeper implements a multi-layered encryption system based on client-side generated keys. Record-level keys and Folder-level keys are generated on the local device which encrypt each stored Vault record (e.g. Password). For example, if you have 10,000 records in your vault, you also have 10,000 AES Record Keys protecting the data. Keys are generated locally on the device to preserve Zero Knowledge and to support advanced features such as record and folder sharing. Record and Folder Keys are wrapped by other keys, such as the Data Key and Client Key.
A Master Password Key is derived from the Master Password using PBKDF2 with 1,000,000 rounds and used to unwrap the AES-256 Data Key, which is then used to unwrap the AES-256 Record Keys and Folder Keys. Record Keys are then used to decrypt the stored record information in the vault. A locally stored Elliptic Curve (EC) key pair is generated locally to encrypt and decrypt the user's Data Key, which then unwraps the Record and Folder keys.
Additional details about the key wrapping is described in the Encryption of Stored Data section below. Master Password Hashes and 256-bit AES Master Password Keys are generated by the on-premise SSO Cloud application. Business and Enterprise customers can manage many different capabilities of the Keeper platform, such as role-based enforcement policies, provisioning, authentication and team management.
Administrative functions are protected in the Keeper platform by encryption, in addition to authorization. Authorization allows an Admin to access certain capabilities of the platform, but Encryption is used in many ways to ensure that only designated users are able to physically perform functionality or view sensitive information. Many features within the Administrative features require decryption of keys in order to function and to preserve Zero-Knowledge and Zero-Trust. For example: Role policies for Vault Transfer and Device Approvals utilize public and private encryption key pairs Enterprise-level key pairs are used for sharing usage data from the individual user to the Admin Auditing of Password Strength and other sensitive usage data is encrypted with Enterprise Public Keys that can only be decrypted by the Admin.
Keeper's platform as a whole can be thought of as a key management platform, where the keys are in full control of the users and the Keeper Administrators. The underlying complexity of key management is abstracted from users by the friendly front-end interface. Keeper has created an advanced cloud authentication and network communications model that has been built for the highest levels of privacy, security and trust. A few key features of the authentication model are: Master Password is never transmitted over the network layer Unlike most SaaS services, the login credentials never leave the device. PBKDF2 is utilized on the local device to derive a 256-bit AES key used for decryption. A second PBKDF2 key is generated locally and then hashed with HMAC_SHA256 to derive an authentication token. Keeper’s Cloud Security vault has zero knowledge of the user’s decryption key.
Traffic between client device and Keeper Cloud cannot be intercepted or decrypted Keeper utilizes Key Pinning and additional layers of network-level encryption (Transmission Keys) between the device and the Keeper servers, to ensure that MITM attacks are prevented. New devices cannot login to an account without a device verification step No login attempts can be made on an account without passing this step. Keeper supports several types of device verification methods that depend on the authentication scheme being used.
2FA is performed after device verification, prior to Master Password entry If a user has 2FA configured or enforced, this step must pass prior to the Master Password entry. Master Password entry cannot be performed until the Device Verification and 2FA step succeeds The user is unable to proceed to the Master Password entry step without first performing a device verification and 2FA authentication. This advanced authentication flow provides protection against several attack vectors including brute force attack, password spraying, enumeration and MITM.
A user cannot attempt to login to an account without a device approval and verification step. For customers logging in with a Master Password, device verification can be performed using several new methods including: For customers who authenticate with Keeper SSO Connect Cloud, device approval performs a key transfer, in which the user's encrypted data key is delivered to the device, which is then decrypted locally using their elliptic curve private key.
Device approval methods include the following: 2FA can be added to any consumer or business account. Business customers can enforce the use of 2FA with various levels of control and security options. Starting with version 3 of the Keeper backend API (which corresponds to version 15+ of the Keeper client applications), the 2FA step comes before the Master Password entry. Performing the device verification and 2FA step prior to the Master Password entry phase offers mitigation of several attack vectors including brute force attack, password testing and account enumeration.
The user's vault records are encrypted locally with a 256-bit AES-GCM "Record Key" that is randomly generated on the device. The record keys are encrypted with a 256-bit AES-GCM "Data Key" that is also generated randomly on the user's device and unique to each user. For users who login with a Master Password, the Data Key is encrypted with a key derived from the user's Master Password using PBKDF2-HMAC-SHA256 with a 128-bit random salt and 1,000,000 iterations. The encrypted vault ciphertext is stored in the Keeper cloud.
For authentication, a second PBKDF2 key is generated locally on the user's device using 1,000,000 iterations and a 128-bit randomly generated salt. This key is then hashed with SHA256 to derive an authentication token. In the Keeper cloud, the authentication token is super-encrypted with a "user authentication" key. The user authentication key is randomly generated by the server and encrypted with a hardware security module (with a non-exportable key) prior to storage. The user authentication key is used to encrypt the salt, authentication token, user’s encrypted data key and other authentication related fields for alternate authentication methods like biometrics, etc.
Keeper's SSO Cloud capability provides authentication against a SAML 2.0 identity provider, while retaining full Zero Knowledge encryption with the user's vault. An Elliptic Curve (secp256r1) private key key pair is generated on the device. The Data Key of the user is decrypted with the device private key, and the Encrypted Data Key is provided to the user upon successful authentication from their designated identity provider.
For users who authenticate to Keeper with a SAML 2.0 identity provider, Keeper SSO Connect software is hosted in the customer's environment. The SSO Connect software generates and manages the user's Master Password. The Generated Master Password is then processed with PBKDF2 to derive a key which decrypts the user's other keys such as the Data Key. 5. Performance Evaluation & Extended Technical Observations Customers who normally login to their Keeper Vault using Enterprise SSO Login (SAML 2.0) can also login to Keeper Web Vault, Browser Extension and Keeper Commander using an "Alternate Master Password". To make use of this capability, it must be enabled by the Keeper Administrator in the role policy and then configured by the user. Offline access can also be achieved with a Master Password for SSO-enabled users when this feature is activated.
PBKDF2 is used to derive a key from the Alternate Master Password. A hash of the key performs authentication, and the key decrypts the user's Data Key locally on the device. More information is available on SSO Master Password at this link . Keeper natively supports Windows Hello, Touch ID, Face ID and Android biometrics. Customers who normally login to their Keeper Vault using a Master Password or Enterprise SSO Login (SAML 2.0) can also login to their devices using a biometric.
Biometrics must be enabled by the Keeper Administrator in the role policy. Offline access can also be achieved with a biometric for both Master Password and SSO-enabled users when this feature is activated. When biometric login is enabled on a device, a key is randomly generated locally and stored in the secure enclave (e.g. Keychain or Keystore) of the device. The user's Data Key is encrypted with the biometric key. Upon successful biometric authentication, the key is retrieved and the user is able to decrypt their vault.
Keeper does NOT store or process biometric data of users. Keeper integrates with the existing biometrics capabilities of the operating system to authenticate the user and retrieve the encryption key protected by the device secure enclave. Keeper’s passkey-based authentication leverages the FIDO2 WebAuthn standard with platform-bound credentials to deliver a phishing-resistant, cryptographically secure login experience. When a passkey is created, a unique key pair is generated and stored securely on the user’s device, protected by the device’s biometric or PIN-based local authentication. During login, Keeper uses challenge-response authentication to validate the user without transmitting any secrets over the network.
Because the private key never leaves the device and the authentication process requires both device possession and biometric presence, passkey login fulfills the requirements for both primary and secondary authentication factors. This approach eliminates reliance on passwords and one-time codes, significantly reducing the attack surface for credential-based threats while maintaining Keeper’s zero-knowledge encryption architecture.
For password-based authentication, when users create their account profile, they are required to select a “Master Password”. Users are also able to configure a second factor of authentication using FIDO2 WebAuthn, TOTP, Duo Security, RSA SecurID, SMS or SmartWatch. If the user is authenticated via Keeper SSO Connect™ Cloud, a 256-bit Elliptic Curve (EC secp256r1) private key is generated and stored locally on each device. The EC device private key is used to decrypt the AES-256 Data Key, and the Data Key decrypts the user's vault record keys and folder keys. No Master Passwords are utilized in this encryption model.
If the user is authenticated via Keeper SSO Connect™ On-Prem (integration with SAML 2.0 identity provider), the Master Password and AES-256 key is auto-generated by the SSO Connect software (hosted and operated by the Enterprise customer on-premise). The EC Device Private Key is not directly utilized to encrypt or decrypt vault data. Upon successful authentication from the Identity Provider, a separate key (that is not stored) is utilized for decryption of the vault data. Offline extraction of the local Device Private Key cannot decrypt a user's vault.
The Master Password is used to derive an encryption key on the client device using a Password Based Key Derivation Function (PBKDF2) with 1,000,000 rounds. On the client device, a 256-bit AES “Data Key” and “Client Key” are generated, as well as the User's EC Private/Public Key Pair for the purpose of sharing records between users and teams. (For legacy compatibility with older shared records, a 2048-bit RSA Private/Public Key Pair is also generated).
The “Data Key” is used to encrypt data that is synchronized to the Cloud Security Vault. For Master Password-based authentication, the “Data Key” is encrypted with the “Master Password Key” (derived from the Master Password using PBKDF2 with 1,000,000 iterations) and this ciphertext is super-encrypted and stored in the Cloud Security Vault. For SSO Cloud-based authentication, the local Device EC (secp256r1) private key is used to decrypt the Data Key. The Data Key decrypts the user's vault cipher record keys The “Client Key” is used to encrypt data that is stored locally on the user’s device. The “Client Key” is encrypted with the “Data Key” and this ciphertext is stored in the Cloud Security Vault. For Master Password-based authentication, the “Client Key” is also encrypted with the “Master Password Key” and this ciphertext is stored locally on the device for offline use. Offline mode can be controlled by the Enterprise administrator through role enforcement policies .
The vault data stored offline is AES-GCM encrypted with a 256-bit “Client Key” that is generated randomly and protected by PBKDF2-HMAC-SHA512 with a 128-bit random salt and 1,000,000 iterations. The salt and iterations are stored locally. When the user enters their Master Password, a key is derived using the salt and iterations and an attempt is made to decrypt the Client Key. The Client Key is then used to decrypt the stored record cache.
The “Device EC Private Key” is stored locally on the device and never leaves the device. This is used for Cloud SSO authentication models. The “User EC Private Key” is encrypted with the “Data Key” and the ciphertext is stored in the Cloud Security Vault. For each record (e.g. Website Password or File) that is created, a 256-bit AES “Record Key” is generated on the client device.
The “Record Key” is used to encrypt and decrypt the record content. The “Record Key” is encrypted with the user’s “Data Key” and the ciphertext is stored in the Cloud Security Vault. The Record Key and record data is also encrypted with the “Client Key” and the ciphertext is stored locally on the device. When a user logs into a device (with their master password), they first decrypt their Client Key from the Master Password-derived key.
The data key unwrapped locally or retrieved from the Cloud Security Vault upon successful authentication is decrypted with the user’s Master Password derived key. Record Key ciphertext is synchronized from the Cloud Security Vault then decrypted locally with the user’s Data Key. Shared Folder keys are decrypted with the respective Shared Folder Key from each folder. Record content is decrypted with the respective Record Key from each record. Record Keys and content are then encrypted with the client key and stored locally.
Keeper Privileged Access Management (KeeperPAM) provides centralized management of privileged credentials and access to protected systems. This document describes how KeeperPAM can be deployed in environments with restricted network connectivity, including environments commonly described as air-gapped. It also outlines the infrastructure requirements necessary for KeeperPAM to operate within supported parameters.
At the current state of the product, KeeperPAM requires AWS cloud infrastructure to function. An air-gapped environment is typically defined as an environment with limited or controlled connectivity to external networks. KeeperPAM does not support fully disconnected or offline deployments. Network connectivity between customer-deployed PAM components and Keeper-managed cloud services is required for normal operation.
Environments with restricted or tightly controlled network access may be supported, provided required connectivity is available. KeeperPAM uses a cloud-based architecture where core services are hosted and managed by Keeper Security. Customer environments deploy PAM components that interact with protected systems and communicate with Keeper cloud services.
At this time, AWS is the only supported cloud provider for KeeperPAM backend services. KeeperPAM relies on Keeper Security cloud services hosted in AWS. These services are required for the operation of the product and are managed by Keeper Security. Customers do not deploy or manage these cloud services. These components must have network connectivity to the Keeper cloud in order to function.
For KeeperPAM to operate within supported parameters, the following connectivity requirements must be met: Network connectivity from customer-deployed PAM components to Keeper cloud services hosted in AWS Connectivity sufficient to allow required communication between PAM components and Keeper cloud services KeeperPAM may be deployed in environments with restricted or controlled network access, provided that required connectivity to AWS-hosted Keeper services is available.
Deployments that prohibit all external network connectivity are not supported at this time. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Bitwarden • https://en.wikipedia.org/wiki/Shamir%27s%20secret%20sharing • https://en.wikipedia.org/wiki/Tokenization%20%28data%20security%29 • https://shieldcue.com/blog/password-manager-bitwarden-setup-guide/ • https://github.com/zeroxv6/encrypted-vault-script • https://github.com/Klima42/secure-file-vault • https://ghostvault.org/ • https://www.newsoftwares.net/blog/zero-knowledge-encryption-explained/ • https://docs.keeper.io/enterprise-guide/keeper-encryption-model • https://bitwarden.com/blog/end-to-end-encryption-and-zero-knowledge/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for End To End Zero Knowledge Secure Vault.
[*] Metasploit Scan Running on Target Subnet for End To End Zero Knowledge Secure Vault... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |