Complete Technical Paper Content — Endpoint Detection And Response Simulation Using Python
Overview & System Context
Endpoint Detection And Response Simulation Using Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9503 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Managed detection and response (or MDR) is a type of cybersecurity service providing customers with a cyberdefense technology and the associated remotely delivered human expertise. Those services help organizations monitor, detect, analyze and respond to advanced cyber threats. MDR is a form of managed security service (MSS).
Access to this page requires authorization. You can try signing in or changing directories . Endpoint detection and response capabilities in Defender for Endpoint provide advanced attack detections that are near real-time and actionable. Security analysts can prioritize alerts effectively, gain visibility into the full scope of a breach, and take response actions to remediate threats.
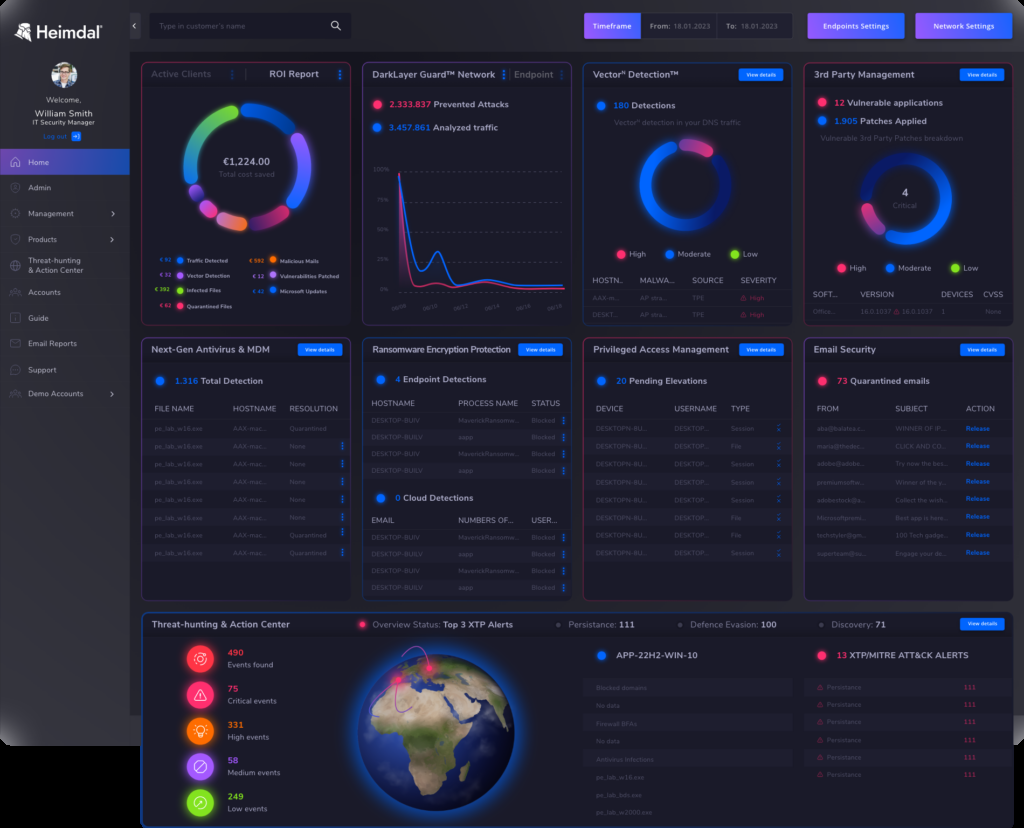
When a threat is detected, alerts are created in the system for an analyst to investigate. Alerts with the same attack techniques or attributed to the same attacker are aggregated into an entity called an incident . Aggregating alerts in this manner makes it easy for analysts to collectively investigate and respond to threats. Figure 1: The Complete Guide: How to Create an Endpoint Detection and Response ...
Defender for Endpoint detection is not intended to be an auditing or logging solution that records every operation or activity that happens on a given endpoint. Our sensor has an internal throttling mechanism, so the high rate of repeat identical events don't flood the logs. Defender for Endpoint Plan 1 and Microsoft Defender for Business include only the following manual response actions: Inspired by the "assume breach" mindset, Defender for Endpoint continuously collects behavioral cyber telemetry. This includes process information, network activities, deep optics into the kernel and memory manager, user login activities, registry and file system changes, and others. The information is stored for six months, enabling an analyst to travel back in time to the start of an attack. The analyst can then pivot in various views and approach an investigation through multiple vectors.
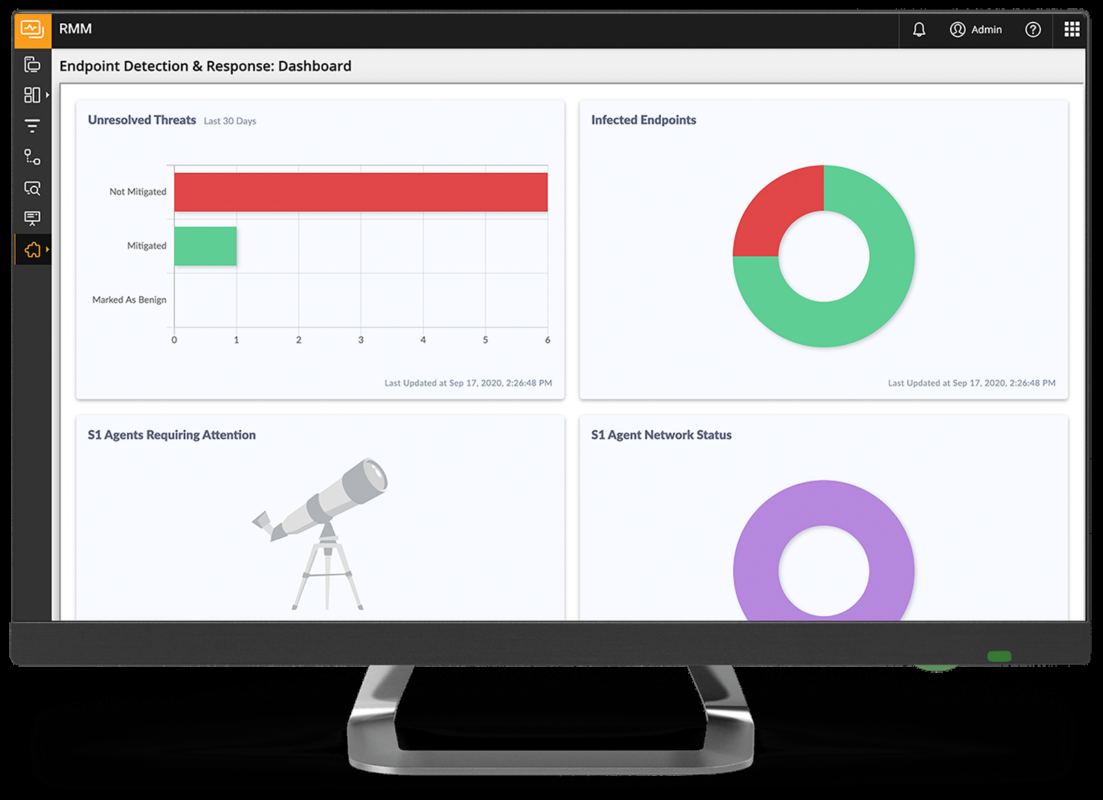
The response capabilities give you the power to promptly remediate threats by acting on the affected entities. Figure 2: Endpoint Detection and Response (EDR) N-ABLE RMM IIIIII — Monster Online Defender for Endpoint signals contribute to automatic attack disruption in Microsoft Defender XDR. Attack disruption uses signal correlation and AI to automatically contain active attacks in progressâIIsuch as ransomware, business email compromise, and adversary-in-the-middle attacksâIIlimiting lateral movement and reducing overall impact. Automatic attack disruption works with other Defender XDR sources to contain compromised assets, including automatically disabling compromised user accounts and isolating affected devices.
Endpoint detection and response (EDR) is an endpoint security solution that continuously monitors laptops, servers, and mobile devices to detect and respond to cyber threats in real time. This guide covers how EDR works, key capabilities like threat hunting and forensic analysis, the EDR vs XDR vs MDR decision framework, the 2026 AI-powered detection landscape, evaluation criteria, deployment best practices, and how to build EDR into a layered security stack.
Endpoint detection and response (EDR) is an endpoint security tool that always watches endpoint activities on laptops, desktops, servers, and mobile devices to detect and respond to cyber threats in real time. But, that one-line definition only scratches the surface. In use, EDR tools go far beyond what AV software can do. They record every process and file change. They also log every link on each device. Then they check that data using behavior-based rules, machine learning, and threat intelligence to spot odd activity before it becomes a breach.
The term was coined by Gartner analyst Anton Chuvakin in 2013. Since then, EDR has grown a lot. It went from a niche tool to a core layer of cybersecurity . Also, the EDR market is projected to reach $10.63 billion (Stratistics MRC). So, understanding how EDR works, what EDR features matter most, and how to choose the right EDR tools is now essential for every security team. Put simply, endpoint detection and response edr is no longer optional. EDR security and complex threat detection have become the backbone of modern endpoint security — it is the backbone of modern endpoint security.
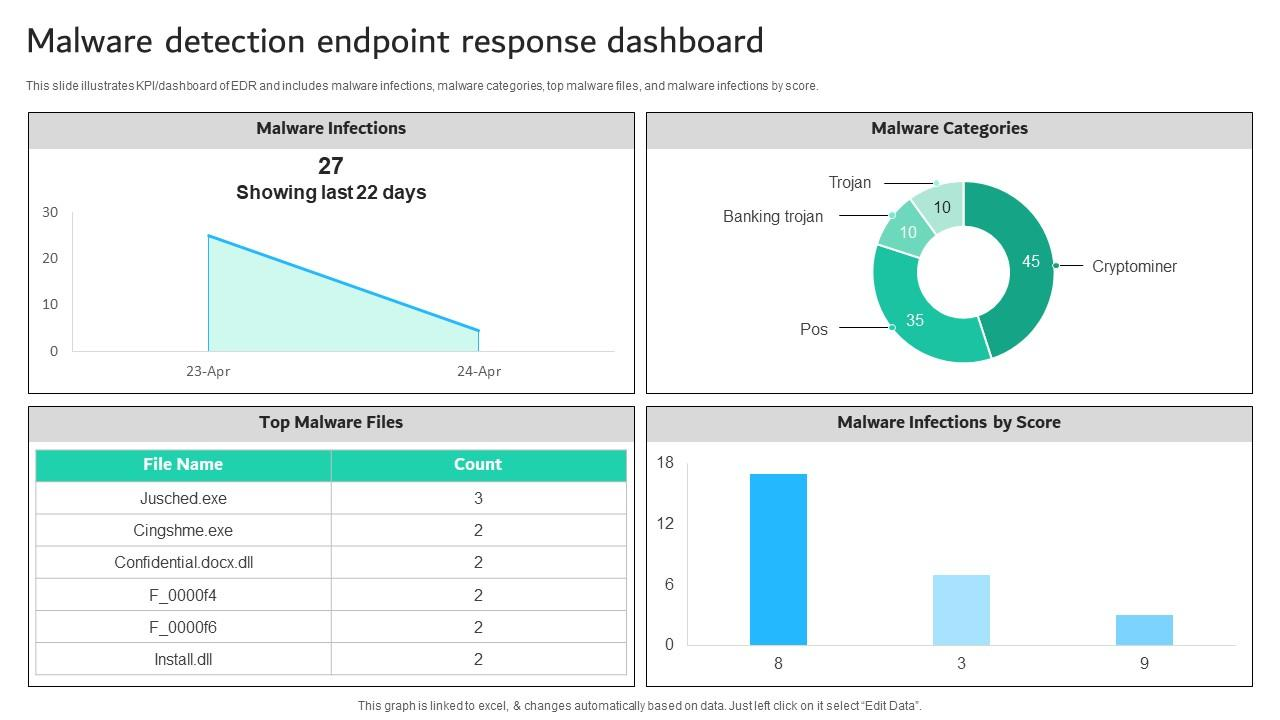
Figure 3: Malware Detection Endpoint Response Dashboard PPT Template Endpoints are the front door for most cyber attacks. In fact, over 70% of successful breaches start at an endpoint . This could be a laptop, a phone, or a server (IDC). Meanwhile, the average cost of a data breach reached $4.88 million (IBM). Standard AV uses signature databases. It catches known threats that match. But, it misses zero-day exploits, fileless attacks, and complex threat techniques that have no known signature. EDR fills this gap. It is built for this. It sees what AV cannot.
Also, the shift to remote work and cloud-first systems has expanded the attack surface. Firms now manage thousands of devices. These span offices, homes, and data centers. The old walls are gone. The risk is real. So, security staff need tools that provide unified view across every endpoint — not just the ones inside the corporate network. EDR gives that view. It always watches every managed device, no matter of location, and feeds alerts to the security operations center in real time.
Also, audit rules now mandate endpoint monitoring. HIPAA, PCI-DSS, SOX, and GDPR all require proof that firms can detect and respond to threats on endpoint devices. EDR gives the audit trail — continuous data, timestamped alerts, and loged response actions — that auditors expect. So, EDR is not just a security tool. It is also a audit enabler that shows due diligence in the event of a breach or audit.
Every EDR rollout starts with an agent — a lightweight software component installed on each endpoint. This agent always watches endpoint activities: processes launched, files created or modified, registry changes, network connections made, and user logins. All of this data flows to a central console — either cloud based or on-premise — where it is stored and checkd. The volume of data is enormous. One device can make thousands of events per hour. So, EDR tools must filter, compress, and prioritize this data so that security staff can focus on what matters. Most modern EDR tools retain 30 to 90 days of data, giving teams enough history for detection probe and forensic analysis when an incident occurs.
Also, the quality of data matters as much as the volume. The best EDR tools add rich context to each event — not just what happened, but who triggered it, from which device, using which logins, and through which network connections. This context is what splits an actionable alert from raw noise. Without it, security staff waste hours linking data manually. With it, they can triage and respond in minutes.
Once data is collected, EDR applies many detection layers. First, it checks for known IOCs (IOCs) . These include file hashes, IP addresses, and domains linked to known threats. Second, it watches for odd patterns . These include odd process chains, privilege jumps, or lateral movement. Third, complex EDR tools map observed behaviors to the MITRE ATT&CK framework, spoting the exact tactics techniques and procedures ttps an attacker is using.
When EDR spots a threat, it acts on its own. Say, it may isolate the affected endpoint from the network, kill the harmful process, or quarantine a suspicious file. At the same time, it alerts security staff with a ranked alert that includes context . It shows what happened, which device, what process fired, and how bad the risk is. This combination of auto-response and human review is what makes EDR so strong. It buys time for the security team while containing the threat before it spreads.
Also, modern EDR tools use machine learning models trained on millions of attack samples to classify threats with high accuracy. These models detect subtle patterns in endpoint activities that rule-based systems would miss — such as a valid Windows process being used to download and execute code from an unusual source. This is how EDR catches living-off-the-land attacks, where attackers abuse trusted system tools instead of rolling out custom malware. So, EDR security extends far beyond file scanning. It watches behavior, not just signatures.
The core EDR features fall into two categories: reactive detection and proactive threat hunting. Reactive detection fires when EDR spots odd activity — an odd process, a known IOC match, or a behavior-based pattern that matches an complex threat profile. The system raises an alert and, depending on the rule, takes auto action. Threat hunting goes further. Staff actively search the data for hidden threats. They do not wait for alerts. A hunter might search all devices for a process linked to new malware. Or they might look for unusual network connections to external IP addresses during off-hours. Threat hunting turns EDR from a reactive alarm system into an active defense tool. So, firms that combine auto detection with regular threat hunting catch threats faster and reduce dwell time — the window from compromise and findy.
When a breach occurs, EDR gives the post-breach data needed to understand what happened. Security staff can replay the full timeline of endpoint activities . They see which process launched first, what files it touched, which links it made, and how it spread. This detection probe feature is critical for post-incident reviews, legal reporting, and root cause review. Modern EDR tools also link with other security tools. EDR feeds alerts into SIEM platforms. SIEM links data from many sources. It also ties into SOAR platforms for planned response — on its own triggering playbooks that contain, review, and fix threats without manual steps. Also, threat intelligence feeds enrich EDR alerts with context: is this IOC linked to a known group? Is this TTP associated with ransomware or espionage? These links make EDR more than a standalone tool — they make it the nerve center of a layered security stack.
Another critical feature is cloud based data storage. Early EDR tools stored data locally, which limited scalability and made it hard to manage spread-out endpoints. Today, most EDR platforms send data to a cloud console where it is aggregated, linked, and retained at scale. This cloud based design also enables global search — a security analyst in one location can query every endpoint worldwide in seconds. For firms with remote workers, branch offices, or multi-cloud setups, cloud based EDR is now the default rollout model.
The MITRE ATT&CK framework is the field standard for classifying attacker behavior. It maps known tactics techniques and procedures ttps into a matrix of attack stages — from initial access and execution through persistence, privilege escalation, lateral movement, and exfiltration. Modern EDR tools use this framework to classify the odd patterns they detect. Say, when EDR detects a PowerShell script downloading a payload from an external server, it can map that behavior to MITRE ATT&CK technique T1059.001 (Command and Scripting Interpreter: PowerShell). This mapping gives security staff immediate context — they know exactly what stage of the attack chain they are looking at, and they can predict what the attacker is likely to do next.
Also, MITRE publishes annual ATT&CK Evaluations that test EDR tools against real-world attack scenarios. These evaluations are the most objective benchmark available for comparing EDR tools. They score each tool on detection scope, analytic quality, and view — with results mapped to exact tactics techniques and procedures ttps. So, when evaluating EDR tools, always check their MITRE ATT&CK Evaluation results alongside vendor marketing claims.
Understanding where EDR fits needs comparing it to the tools it builds on. AV (AV) is the oldest layer. It uses signature databases to catch known threats — viruses, trojans, and worms with recognized file hashes. But, AV misses zero-day threats, fileless attacks, and any harmful activity that does not match a known signature. It is a needed baseline, but not enough on its own.
Endpoint protection platforms (EPP) extend AV with extra prevention layers — firewall, device control, app whitelisting, and basic behavior-based rules. EPP focuses on blocking threats before they execute. But, EPP still lacks the always-on watching, detection probe, and response features that modern threats demand. EDR adds what EPP and AV lack: continuous data, behavior-based detection, auto-response, threat hunting, and forensic analysis. In short, AV blocks known threats. EPP prevents known and some unknown threats. EDR detects, reviews, and responds to everything else — such as the complex threat techniques that bypass the first two layers.
XDR (Extended Detection and Response) builds on EDR by linking signals across many sources . It covers endpoints, email, cloud, network, and identity. While EDR gives deep view into endpoint activities, XDR gives breadth across the entire setup. So, XDR can spot attack chains that span many domains — for instance, a phishing email that gives malware to an endpoint, which then uses stolen logins to access a cloud database.
But, XDR is not a replacement for EDR. Instead, it is an extension. Most XDR platforms include EDR as their endpoint layer. The value of XDR is linking — connecting dots across data sources that EDR alone cannot see. So, firms that already run EDR can upgrade to XDR for broader view without replacing their endpoint agent. In use, XDR shines in complex attack chains. Say, think of an attack that starts with a phishing email (caught by the email layer), gives malware to an endpoint (caught by EDR), uses stolen logins to access a cloud database (caught by the identity layer), and exfiltrates data over an encrypted tunnel (caught by network detection). No single tool sees the full chain. But, XDR links signals from all four sources and presents security staff with a unified timeline. This is why XDR grows fast. It fills a real gap. Firms of all sizes use it now.
MDR (Managed Detection and Response) is not a tech — it is a service. An MDR provider runs EDR tools (or XDR tools) on your behalf, staffing a 24/7 security operations center with skilld security staff who monitor, review, and respond to threats for you. For firms that lack the staff, budget, or expertise to run EDR in-house, MDR is often the most hands-on path to strong endpoint security.
The decision framework is straightforward. Firms with a mature security team and want deep endpoint view, deploy EDR. For cross-domain linking, add XDR. Firms that lack the staff to operate either, engage an MDR provider. Many firms combine all three — EDR as the agent, XDR as the platform, and MDR as the service layer. In short, these are not competing tools. Instead, they are complementary layers of a modern endpoint security tool.
Modern EDR looks corely other from the first-generation tools of 2015. The biggest shift is AI. Modern EDR tools use machine learning to baseline normal endpoint activities for each device, then flag deviations on its own. This approach catches odd patterns that rule-based systems miss — such as a valid process being hijacked by fileless malware, or an authorized user account behaving in ways that suggest compromise.
Also, AI-powered EDR reduces false positives by learning what is normal for each setup. A process that looks suspicious in a law firm might be routine in a software development shop. So, security staff spend less time chasing noise and more time on real threats. But, attackers are also using AI — making polymorphic malware that changes its signature with every infection, and crafting social engineering lures that bypass human judgment. This arms race means EDR must evolve always, not just at annual product releases.
Also, generative AI is creating new challenges for EDR. Attackers now use large language models to craft convincing phishing lures, make custom exploit code, and create polymorphic payloads that change their shape with every execution. Standard signature-based tools cannot keep up with this volume of unique threats. But, AI-powered EDR fights fire with fire — using the same machine learning advances to classify odd patterns faster and with fewer false positives. The result is an arms race where both sides iterate at machine speed. So, when evaluating EDR tools, ask vendors how their detection models are trained, how often they update, and how they handle adversarial AI techniques. The answer reveals if the tool is built for modern threats or still fighting past battles.
The rollout model has shifted too. Early EDR tools needed on-premise servers to store and check data. Today, most EDR platforms are cloud based — the agent sits on the endpoint, but all data flows to a cloud console for review. This model scales better, costs less, and enables global view for firms with spread-out workforces. Also, managed EDR services have grown rapidly. The cyber defense skills shortage — over 4 million unfilled roles globally (ISC2) — means many firms cannot staff a SOC to operate EDR tools around the clock. MDR providers fill this gap by offering 24/7 monitoring, threat hunting, and incident response as a plan service. So, even small and mid-sized firms can access firm-grade EDR features without building an in-house security ops team.
Every firm that manages endpoints needs EDR. But, some face higher urgency. Say, healthcare firms store protected health records on endpoints — and HIPAA needs proof of endpoint monitoring and incident response. In the same way, financial services firms handle high-value transactions and face legal pressure from PCI-DSS and SOX to show continuous endpoint security.
2. System Architecture & Core Working Principles Manufacturing firms run daily tech (OT) alongside IT — and ransomware that crosses from an IT endpoint to an OT controller can shut down a production line for weeks. Also, government agencies face nation-state threats that namely target endpoints with complex threat techniques designed to evade basic defenses.
But, the fastest-growing segment for EDR adoption is small and mid-sized businesses . These firms face the same threats as firms but lack dedicated security staff. Managed EDR services make firm-grade threat detection accessible at a fraction of the cost of building an in-house SOC. In short, EDR is not a luxury for large firms. It is a baseline control for any firm that connects devices to a network.
Also, firms undergoing digital transformation face rising endpoint risk. Moving workloads to the cloud, adopting SaaS apps, and enabling remote work all increase the number of connections and devices that need monitoring. Every new device is a possible entry point. So, EDR adoption should scale alongside digital transformation — not lag behind it. The firms that deploy EDR early in their cloud journey catch threats that would otherwise go unnoticed until the damage is done.
Also, cyber insurance providers now require EDR as a must-have for scope. Insurers view endpoint detection and response as a baseline control — without it, many will not issue a policy or will charge sharply higher premiums. So, rolling out EDR is not just a security decision. It is also a financial decision that affects insurance costs, audit posture, and audit readiness. Not all EDR tools are equal. When evaluating options, security teams should assess these criteria: Detection quality matters most. Does the tool detect and respond to fileless attacks, living-off-the-land techniques, and zero-day threats — not just known malware? Check independent test results from MITRE ATT&CK Evaluations, which score EDR tools against real-world attack scenarios and map results to exact tactics techniques and procedures ttps.
Response automation is the second priority. Can the tool on its own isolate an endpoint, kill a process, or block a network connection without waiting for a human? In fast-moving attacks, minutes matter. Auto-response buys time for security staff to review while the threat is already contained. Data storage and post-breach depth decide how far back your team can review. Some EDR tools retain 7 days of data. Others keep 90. For detection probe and audit reporting, longer storage is better. Also, evaluate if the tool links with your existing SIEM, SOAR, and threat intelligence platforms. An EDR that operates in isolation misses the cross-domain signals that reveal full attack chains.
Finally, think of rollout model . Do you need cloud based EDR for a spread-out workforce? On-premise for air-gapped setups? Or a hybrid? Also, assess the vendor’s roadmap — is the tool evolving toward XDR, or will you need to replace it in two years? The best EDR tools are the ones that fit your setup today and grow with your needs tomorrow. A successful EDR rollout starts with planning — not purchasing. First, inventory every endpoint in your setup: laptops, desktops, servers, mobile devices, and any connections and devices that touch your network. You cannot protect what you cannot see. Second, define your detection policies. What odd activity should trigger an alert? What odd patterns should trigger auto containment? These decisions should align with your risk profile, not with vendor defaults.
Third, roll out the EDR agent in phases. Start with a pilot group — often IT and security staff — to tune detection rules and reduce false positives. Then expand to high-risk groups: finance, executive, and IT admin endpoints. Finally, deploy to the full firm. This phased approach catches setup issues early and builds confidence before full-scale rollout. Rollout is not the finish line — it is the starting line. EDR needs ongoing ops. Security staff must review alerts daily, triage by risk level, and review confirmed threats. Also, tuning is critical. Every setup makes unique patterns of normal behavior. If EDR flags too many false positives, analysts suffer alert fatigue and start ignoring real threats. So, dedicate time each week to refining detection rules, updating allowlists, and adding lessons from recent incidents.
Also, link EDR into your broader security ops workflow. Feed EDR alerts into your security information and event management platform for cross-source linking. Connect it to your SOAR platform for auto playbooks. And enrich alerts with threat intelligence feeds so analysts see context — not just raw data. The firms that get the most from EDR are the ones that treat it as an running discipline, not a set-and-forget product.
Also, schedule regular threat hunting exercises. Instead of waiting for alerts, have your security staff actively search endpoint data for hidden threats. Say, hunt for beacon patterns — repeated network connections to external IP addresses at regular intervals — which often indicate command-and-control traffic. In the same way, search for processes that should not be running during off-hours, or user accounts accessing systems they have never touched before. Proactive threat hunting catches threats that auto detection misses, and it builds institutional knowledge within your security team about how your setup normally behaves.
EDR is powerful, but it comes with challenges that security teams must manage. First, alert fatigue is the most common problem. A poorly tuned EDR rollout can make hundreds of alerts per day — most of them false positives. So, security staff start ignoring alerts, and real threats slip through. The fix is aggressive tuning: baseline normal endpoint activities, suppress known-good patterns, and prioritize alerts by risk level and business impact.
Second, skills shortage is a persistent barrier. EDR needs trained security staff who can interpret behavior-based alerts, conduct threat hunting, and perform detection probe. Most firms do not have enough of these professionals. So, managed EDR services — where an external provider handles monitoring and response — have become the default for firms under 500 employees.
Third, endpoint scope gaps undermine the entire rollout. If EDR agents are not installed on every endpoint — such as BYOD mobile devices, contractor laptops, and shadow IT — attackers will find and exploit the unmonitored gaps. Also, legacy systems that cannot run modern EDR agents need compensating controls like network segmentation and enhanced logging. Finally, integration complexity can slow adoption. EDR must feed data to SIEM, SOAR, and threat intelligence platforms to deliver full value. If these links are broken or incomplete, security staff lack the cross-domain view they need. So, plan integration design before rollout, not after.
Fifth, privacy and data sovereignty concerns can complicate cloud based EDR rollouts. EDR agents collect detailed data about user activity on endpoint devices . This includes processes, file access, and network links. In regions with strict data protection laws (GDPR, India’s DPDPA), firms must ensure that this data is stored and processed in audit with local rules. Some EDR vendors offer regional data residency options. Others do not. So, evaluate data handling uses as part of your EDR tool selection — not as an afterthought.
EDR is one layer in a broader security stack. It works best when combined with other tools that cover other parts of the attack surface. Start by combining EDR with email security to stop phishing — the top delivery method for malware that targets endpoints. Then layer in IAM to enforce identity-based access controls and catch credential misuse that starts at the endpoint level. Add network detection to spot lateral movement that EDR alone might miss if the attacker moves from managed and unmanaged segments.
Also, feed EDR data into your security information and event management platform. SIEM links endpoint data with logs from firewalls, cloud platforms, and identity providers — revealing attack chains that no single tool can see alone. Also, connect EDR to a SOAR platform for auto-response playbooks that contain threats in seconds rather than hours. The goal is defense in depth. EDR handles the endpoint layer. Email security handles the inbox. IAM handles access.
Network detection handles traffic. SIEM handles linking. Each layer covers a gap the others miss. So, an attacker must bypass every layer — not just one — to succeed. Also, establish clear handoff procedures from layers. When EDR detects odd activity on an endpoint, who decides if it is part of a broader attack? When SIEM links an EDR alert with a failed cloud login from an unusual location, who reviews? These workflow questions matter as much as the tools themselves. So, log your detection-to-response workflow before rolling out EDR — not after the first real incident forces you to improvise.
Also, measure your EDR program’s performance. Track mean time to detect (MTTD), mean time to respond (MTTR), false positive rate, and the share of endpoints with active agents. These metrics show if your EDR security investment is delivering results or drifting. Firms that measure and improve consistently outperform those that deploy and forget. For help building your layered stack, explore our cybersecurity services and our cyber defense services and cloud security guides.
Key Takeaway EDR is the backbone of endpoint security — but it works best as part of a layered stack. Pair it with email security, IAM, network detection, SIEM, and SOAR. Each layer covers a gap the others miss. Endpoint detection and response has moved from a niche security tool to the backbone of modern cyber defense. With threats moving at machine speed and the skills gap widening, EDR is the layer that gives security staff the view, automation, and post-breach depth they need to detect and respond before a compromise becomes a breach.
The key decisions are clear. Choose EDR tools that deliver behavior-based detection, auto-response, and deep data storage. Evaluate against MITRE ATT&CK results. Decide if you need EDR alone, XDR for cross-domain view, or MDR for managed ops. Then deploy in phases, tune always, and link into your broader security stack. For leaders building their endpoint security plan, the path forward starts with one rule: you cannot protect what you cannot see. EDR gives you the view. The rest is discipline — tuning, hunting, responding, and improving with every incident.
The endpoint is where attacks land. It is where logins are stolen, where malware executes, and where data leaves the network. Endpoint detection and response is the discipline that watches this critical layer around the clock. Firms that invest in strong EDR security, train their security staff, and link EDR into a layered stack will consistently outperform those that rely on AV alone. The threat detection gap from these two groups widens every year.
Join 1 million+ technology professionals. Weekly digest of new terms, threat intelligence, and architecture decisions. Arctic Wolf® Managed Detection and Response (MDR) provides 24×7 monitoring to help you detect, respond, and recover from modern cyber attacks. Arctic Wolf ingests telemetry generated from industry-leading Endpoint Detection and Response (EDR) providers for advanced investigation into potential threats and correlation with logs from your other tools, such as cloud services, network devices, and identity and access management (IAM) tools.
For more information about the importance of EDR telemetry, see Arctic Wolf Exploring Endpoint Telemetry . You're probably dealing with some version of the same problem most SOC teams face. Alerts are firing from the firewall, identity platform, email gateway, cloud logs, vulnerability scanner, and a half-configured SIEM rule someone forgot to tune. Meanwhile, the device that launched PowerShell, spawned a suspicious child process, or reached out to a strange destination is where the story really started.
That's why endpoint detection response became such a core part of modern defense. It gives analysts direct visibility into what happened on the device, not just what crossed a perimeter control. In practice, that means better context for triage, faster containment when a host goes bad, and a cleaner path from detection to investigation. The hard part is that many teams stop there. They deploy EDR, forward a few alerts, and assume the endpoint problem is handled. It isn't. EDR is foundational, but it's no longer enough on its own. The mature approach is to treat endpoint telemetry as one part of a larger detection fabric that also includes response workflows, proactive exposure reduction, and normalized data across the rest of the environment.
A common shift starts like this. The SOC gets an alert from Microsoft Sentinel or Splunk. The analyst pivots to email logs, then identity logs, then a ticketing system note, then a spreadsheet someone keeps for asset ownership. Ten minutes later, the team still doesn't know what ran on the laptop. That visibility gap is why EDR moved from nice-to-have to baseline control. A widely cited historical statistic is that as many as 90% of successful cyberattacks and 70% of successful data breaches originate at endpoint devices , according to IBM's overview of EDR . If compromise often starts on the device, then device-level telemetry has to be part of the first response, not an afterthought.
Legacy antivirus was built for a world where known malware files were the main problem. That model still has value, but it isn't enough when the activity looks like a living-off-the-land chain, a malicious script, a stolen session, or an abused admin tool. Analysts need to know which process started first, what it touched, which account launched it, and whether it spread. That's the operational reason EDR matters. It continuously collects endpoint telemetry, analyzes it in real time, and supports actions such as containment, remediation, and threat hunting. It's built for the assumption that something will get through.
Practical rule: If your team can't reconstruct host activity without asking the user what they clicked, you don't have enough endpoint visibility. The need gets sharper in distributed environments. Laptops work off-network. Servers run in hybrid environments. Mobile devices and connected assets don't fit the old castle-and-moat model. Perimeter controls still matter, but they no longer tell the whole story.
For teams in regulated environments, endpoint visibility also ties directly to data protection workflows. Healthcare is a strong example because sensitive records move across endpoints, apps, and staff workflows. RiverAxe has a useful guide to health IT data protection that helps frame why endpoint controls have to support broader handling of sensitive data, not just malware blocking.
3. Software Implementation, Frameworks & Protocols What works is treating EDR as a foundation for investigation and containment. What doesn't work is treating it like a drop-in replacement for every other security function. EDR matters now because modern incidents are messy. The endpoint is where mess becomes evidence.
The simplest way to understand EDR is to think of it as an always-on flight data recorder for endpoints. It doesn't just look for one bad file. It records operational activity continuously so analysts can reconstruct what happened, decide whether it's malicious, and act before the compromise spreads. Modern EDR platforms are described as analyzing billions of events in real time and using endpoint agents to collect processes, network connections, activity volume, file transfers, and user behavior for centralized investigation, as described in CrowdStrike's EDR overview .
The first component is the agent . This is the lightweight software running on the laptop, server, or other managed asset. Its job is to observe system activity in real time and send relevant telemetry upstream. That telemetry usually includes process execution, network connections, file operations, and user-linked activity. The agent may also support local response actions such as process kill, host isolation, or script execution for remediation.
Deployment quality holds significant importance. If the agent is unstable, inconsistently configured, or disabled on key systems, the rest of the architecture can't compensate. A fancy console won't fix missing endpoint truth. The second component is the central analysis layer , usually cloud-based, sometimes hybrid. In this layer, telemetry from many endpoints gets normalized, correlated, and evaluated against behavioral logic, threat intelligence, and detection rules.
Then comes data storage . Good EDR doesn't just alert. It preserves enough event history for triage, retrospective analysis, and hunting. Analysts need to pivot backward in time, not just react to the current alert. Finally, there's the management console where responders live day to day, searching process trees, reviewing timelines, isolating devices, suppressing noisy detections, and handing off evidence to incident response.
The architecture only works when the parts reinforce each other. Collection without correlation becomes noise. Correlation without retention weakens forensics. Response without analyst context creates risk. Teams that want to mature further usually connect this architecture into broader operations. That includes detection lifecycle work, content tuning, and escalation design. ThreatCrush has a helpful article on security operations workflows that aligns well with how endpoint telemetry should feed the wider SOC rather than sit in a separate tool island.
EDR serves as a telemetry and correlation system. It continuously collects endpoint events such as process execution, file changes, network connections, user activity, and registry or configuration changes, then applies behavioral analytics to separate normal activity from suspicious patterns. Palo Alto Networks describes this model in its EDR explainer , and that's the right lens to use operationally.
Traditional AV asks, “Have I seen this bad file before?” EDR asks, “Does this chain of behavior look wrong for this host, user, or process?” That distinction matters because many serious incidents don't arrive as a neat malware sample. They show up as unusual command execution, suspicious parent-child process relationships, odd account behavior, file staging, persistence changes, or lateral movement patterns.
A good analyst doesn't look at one row in isolation. They stack these signals. A PowerShell launch by itself might be normal. PowerShell spawned by a document viewer, followed by a new scheduled task and an outbound network connection, isn't normal until proven otherwise. What works in practice is combining these capabilities with tuned detections and clear investigation paths. What fails is leaving every vendor default enabled and assuming the platform will magically know your environment.
Analyst habit: Spend time on process trees, not just alert titles. The title tells you what triggered. The tree tells you what happened. Detection engineering also matters more than is commonly acknowledged. Generic detections catch common patterns, but mature coverage comes from adapting logic to your tools, admin behaviors, and known risk paths. If your team is building that discipline, ThreatCrush has a relevant piece on detection engineering practice .
There's also an important limitation to remember. EDR sees endpoint behavior well, but it won't explain every upstream cause. It may show that a browser launched a suspicious chain. It may not tell you, by itself, whether the original lure came through email, chat, a cloud app, or a stolen token. That's why endpoint detection response has to be connected to the rest of the telemetry stack.
An EDR tool by itself improves visibility. An EDR tool wired properly into the SOC improves outcomes. A practical requirement of EDR is agent-based, real-time monitoring with response actions such as isolating a host or terminating a malicious process. Illumio also positions EDR as a complement to SIEM because it provides granular endpoint data that SIEM alone typically doesn't capture, as described in its EDR reference .
Some teams forward only high-confidence EDR alerts. That keeps costs and noise lower, but it limits deeper correlation. Other teams send much richer endpoint telemetry, which helps hunting and cross-source analysis but increases storage and tuning demands. There isn't one right answer. The right choice depends on analyst capacity, retention strategy, and use cases.
The last point is where many teams are still weak. They treat all endpoint alerts as equal even when asset criticality and exposure context clearly say otherwise. If your EDR rollout is judged only by whether the agent installed successfully, you're measuring deployment, not defense. Useful measures are operational. Analysts usually start with Mean Time to Detect and Mean Time to Respond because they show whether the team can identify and contain endpoint-driven incidents fast enough to matter. You don't need inflated dashboards full of vanity metrics. You need to know where the queue slows down.
ThreatCrush has a practical article on incident response automation that fits this part of the workflow well, especially for teams trying to move from manual handoffs to repeatable playbooks. Good integration reduces analyst decisions during the first minutes of an incident. Bad integration creates more tabs, more swivel-chair work, and more uncertainty.
Most EDR failures aren't product failures. They're operating model failures. The tool works, the telemetry exists, and the SOC still struggles because the deployment created noise, blind spots, or brittle automation. Lansweeper makes an important point in its discussion of EDR operations . Mainstream explanations talk a lot about continuous monitoring and automated isolation, but they rarely explain the tradeoff between speed and alert fatigue or what share of detections should drive containment. That gap shows up in real SOC work every day.
A noisy EDR deployment can make a team feel covered while also reducing its ability to respond. Analysts start bulk-closing low-context detections. Senior staff build mental allowlists no one documents. Eventually a real attack hides inside familiar noise. A quiet console can mean good tuning. It can also mean your team suppressed the only breadcrumbs that mattered.
The second major pitfall is overconfidence in automatic response. Host isolation sounds great until it hits a jump box, a production server, or an executive laptop in the middle of a board meeting. EDR can terminate a process quickly, but the operational consequences still belong to humans. A safer path is staged automation. Start with alert-only or notify-and-approve flows for sensitive assets. Use full auto-containment where confidence is high and business impact is low enough to tolerate mistakes.
After teams get the basics right, this short walkthrough is worth watching because it reinforces where response workflows need judgment, not just tooling: The market has shifted beyond endpoint-only thinking. Recent guidance increasingly frames EDR as one sensor in a broader detection fabric that overlaps with XDR, SIEM, and exposure-management workflows, as noted in Cybereason's EDR fundamentals .
That shift matters because classic endpoint detection response is still mostly reactive. It tells you what happened on the host and helps you respond. It usually doesn't tell you enough about why that host was vulnerable in the first place, how exposed similar assets are, or whether the same pattern exists elsewhere across cloud, identity, and network layers. An analyst investigating a suspicious process often needs more than process data. They may need to know whether the asset was internet-exposed, whether a weak service configuration existed, whether the account had excessive privilege, whether the same pattern appeared in network telemetry, and whether similar detections already exist in the SIEM.
This broader model also lines up well with Zero Trust work. If your team is building that architecture in practical stages, EnvManager's pragmatic Zero Trust roadmap for teams is useful because it focuses on operational sequencing rather than abstract slogans. A unified approach works best when telemetry is normalized, detections are portable, and response actions can flow across tools without custom glue everywhere. Open standards matter here. Sigma helps with portable detection logic. MITRE ATT&CK helps classify behaviors and investigation paths. Common event schemas make correlation less painful.
That's also where modern platforms are trying to reduce friction by combining proactive and reactive functions. Instead of running one product for endpoint signals, another for exposure review, another for SIEM enrichment, and several scripts for handoffs, teams increasingly want a single workflow where the analyst can see the attack path, the asset context, and the available response options together.
The practical takeaway is simple. Keep EDR. Mature it. Integrate it tightly. But don't stop there. Endpoint telemetry tells you what the device did. Unified detection and response tells you how the incident fits into the environment. 4. Practical Deployment, Analysis & Case Studies When teams reach that point, investigations get cleaner. Triage gets faster. Response decisions improve because they're based on more than one sensor. That's the direction endpoint detection response is heading, and it's the right one.
If you want to see how a unified approach can connect EDR, SIEM, CTEM, and SOC workflows in one platform, take a look at ThreatCrush . It's built for teams that need endpoint visibility, normalized telemetry, proactive exposure context, and response actions without stitching together separate products for every part of the workflow. Real-time threat intelligence, CTEM, and exposure management — built for security teams that move fast.
This repository contains three self-contained simulation tools that mimic common attacker behaviors for EDR/SIEM detection testing and security training labs . They are not real malware — all actions are simulated and safe for isolated environments. I WARNING : Run only in a controlled lab or virtual machine. Do not use on production systems or against unauthorized targets.
Detection Goal: Test security controls for obfuscated code execution and AMSI tampering. File: task2_privilege_escalation_credential_access.cpp Binary: task2_privilege_escalation_credential_access.exe Detection Goal: Trigger alerts for high-privilege commands and credential theft behavior . File: task3_ransomware_behavior_simulation.cpp Binary: task3_ransomware_behavior_simulation.exe MIT License – You are free to use, modify, and share for research, training, and defensive testing .
The author is not responsible for misuse. These programs are intended solely for educational and security testing purposes . Windows-based attacker behavior simulations for security research and detection engineering. Access to this page requires authorization. You can try signing in or changing directories . This article outlines the process to create incidents with attack simulations and tutorials and use Microsoft Defender to investigate and respond. Before starting this process, be sure you've reviewed the overall process for piloting and deploying Microsoft Defender and you have at least piloted some of the components of Microsoft Defender.
An incident in Microsoft Defender is a collection of correlated alerts and associated data that make up the story of an attack. Microsoft 365 services and apps create alerts when they detect a suspicious or malicious event or activity. Individual alerts provide valuable clues about a completed or ongoing attack. However, attacks typically employ various techniques against different types of entities, such as devices, users, and mailboxes. The result is multiple alerts for multiple entities in your tenant.
If you're brand new to security analysis and incident response, see the Respond to your first incident walkthrough to get a guided tour of a typical process of analysis, remediation, and post-incident review. This is article 6 of 6 in a series to help you deploy the components of Microsoft Defender XDR, including investigating and responding to incidents.
The articles in this series correspond to the following phases of end-to-end deployment: At any time during your pilot and deployment, you can test Microsoft Defender's incident response and automated investigation and remediation capabilities by creating an incident with a simulated attack and using the Microsoft Defender portal to investigate and respond.
Here's the workflow for investigating and responding to incidents using Microsoft Defender XDR in your production environment. Microsoft Threat Intelligence in Microsoft Defender XDR provides indicators of compromise (IOCs), threat research, and analysis from Microsoft experts and other sources. You can review threat intelligence articles or search for threat actors, vulnerabilities, and other indicators to support your investigations. You can read articles or search for threat actors, vulnerabilities, and other IOCs to gain insight on the types of threats that you might want to investigate.
The Microsoft Defender portal has built-in capabilities to create simulated attacks on your pilot environment: In the Microsoft Defender portal, select Email & collaboration > Attack simulation training . Defender for Office 365 with Microsoft 365 E5 or Microsoft Defender for Office 365 Plan 2 includes attack simulation training for phishing attacks. The basic steps are: For step-by-step instructions on how to create and launch a new simulation, see Simulate a phishing attack .
For step-by-step instructions on how to create a payload for use within a simulation, see Create a custom payload for attack simulation training . For step-by-step instructions on how to gain insights with reporting, see Gain insights through attack simulation training . There are additional simulations from third-party sources. There's also a set of tutorials.
Download the simulation file. You can choose to download the file or script on the test device but it's not mandatory. Run the simulation file or script on the test device as instructed in the walk-through document. For more information, see Experience Microsoft Defender for Endpoint through simulated attack . In this optional incident response exercise, you'll simulate an attack on an isolated Active Directory Domain Services (AD DS) domain controller and Windows device using a PowerShell script and then investigate, remediate, and resolve the incident.
First, you need to add an isolated AD DS domain controller and a Windows device to your pilot environment. If you use tenant and device groups, create a dedicated device group for the test device and push it to top level. One alternative is to host your AD DS domain controller and test device as virtual machines in Microsoft Azure infrastructure services. You can use the instructions in Phase 1 of the simulated enterprise Test Lab Guide , but skip the creation of the APP1 virtual machine.
You'll simulate an advanced attack that uses stealth techniques to hide from detection. The attack lists open Server Message Block (SMB) sessions on domain controllers. It also retrieves recent IP addresses of users' devices. Fileless in-memory attacks like this one don't drop files on the victim's device. Instead, they run only in memory. They "live off the land" by using built-in system and admin tools. They also inject code into system processes to hide what they're doing. This behavior helps them evade detection and persist on the device.
In this simulation, the scenario starts with a PowerShell script. In the real world, a user might be tricked into running a script. The script might also run from a remote connection to another computer from a previously infected device. This behavior suggests the attacker is trying to move laterally in the network. These scripts are hard to detect because admins also run scripts remotely for routine tasks.
During the simulation, the attack injects shellcode into a seemingly innocent process. The scenario requires the use of notepad.exe. We chose this process for the simulation, but attackers would more likely target a long-running system process, such as svchost.exe. The shellcode then goes on to contact the attacker's command-and-control (C2) server to receive instructions on how to proceed. The script attempts executing reconnaissance queries against the domain controller (DC).
Reconnaissance allows an attacker to get information about recent user login information. Once attackers have this information, they can move laterally in the network to get to a specific sensitive account. For optimum results, follow the attack simulation instructions as closely as possible. Ensure that your pilot environment includes the isolated AD DS domain controller and Windows device.
If you open this article on a web browser, you might encounter problems copying the full text without losing certain characters or introducing extra line breaks. If this is the case, download this document and open it on Adobe Reader. If you're running PowerShell using remote desktop protocol (RDP), use the Type Clipboard Text command in the RDP client because the CTRL-V hotkey or right-click-paste method might not work. Recent versions of PowerShell sometimes will also not accept that method, you might have to copy to Notepad in memory first, copy it in the virtual machine, and then paste it into PowerShell.
A few seconds later, the Notepad app will open. A simulated attack code will be injected into Notepad. Keep the automatically generated Notepad instance open to experience the full scenario. 5. Performance Evaluation & Extended Technical Observations The simulated attack code will attempt to communicate to an external IP address (simulating the C2 server) and then attempt reconnaissance against the domain controller through SMB.
The following console output confirms that the simulated reconnaissance action completed successfully against the domain controller: To see the Automated Incident and Response feature in action, keep the notepad.exe process open. You'll see Automated Incident and Response stop the Notepad process.
Before we walk you through this simulation, watch the following video to see how incident management helps you piece the related alerts together as part of the investigation process, where you can find it in the portal, and how it can help you in your security operations: Switching to the SOC analyst point of view, you can now start to investigate the attack in the Microsoft Defender portal.
Microsoft Defender correlates analytics and aggregates all related alerts and investigations from different products into one incident entity. By doing so, Microsoft Defender shows a broader attack story, allowing the SOC analyst to understand and respond to complex threats. The alerts generated during this simulation are associated with the same threat, and as a result, are automatically aggregated as a single incident.
Select the newest item by selecting the circle to the left of the incident name. A side panel displays additional information about the incident, including all the related alerts. Each incident has a unique name that describes it based on the attributes of the alerts it includes. The alerts that are shown in the dashboard can be filtered based on service resources: Microsoft Defender for Identity, Microsoft Defender for Cloud Apps, Microsoft Defender for Endpoint, Microsoft Defender XDR, and Microsoft Defender for Office 365.
In the Incident page, you can see all the alerts and information related to the incident. The information includes the entities and assets that are involved in the alert, the detection source of the alerts (such as Microsoft Defender for Identity or Microsoft Defender for Endpoint), and the reason they were linked together. Reviewing the incident alert list shows the progression of the attack. From this view, you can see and investigate the individual alerts.
You can also select Manage incident from the right-hand menu, to tag the incident, assign it to yourself, and add comments. We'll walk through only a few of the alerts generated during the simulated attack. Depending on the version of Windows and the Microsoft Defender products running on your test device, you might see more alerts that appear in a slightly different order.
Advanced attackers use sophisticated and stealthy methods to persist in memory and hide from detection tools. One common technique is to operate from within a trusted system process rather than a malicious executable, making it hard for detection tools and security operations to spot the malicious code. To allow the SOC analysts to catch these advanced attacks, deep memory sensors in Microsoft Defender for Endpoint provide our cloud service with unprecedented visibility into various cross-process code injection techniques. The following figure shows how Defender for Endpoint detected and alerted on the attempt to inject code to notepad.exe .
Microsoft Defender for Endpoint detections often target the most common attribute of an attack technique. This method ensures durability and raises the bar for attackers to switch to newer tactics. We employ large-scale learning algorithms to establish the normal behavior of common processes within an organization and worldwide and watch for when these processes show anomalous behaviors. These anomalous behaviors often indicate that extraneous code was introduced and is running in an otherwise trusted process.
For this scenario, the process notepad.exe is exhibiting abnormal behavior, involving communication with an external location. The detection of this abnormal external communication is independent of the specific method used to introduce and execute the malicious code. Because this alert is based on machine learning models that require additional backend processing, it might take some time before you see this alert in the portal.
Notice that the alert details include the external IP addressâIIan indicator that you can use as a pivot to expand investigation. When you select an IP address in the alert process tree, the IP address details page opens and shows additional information about the address.
Enumeration using Server Message Block (SMB) protocol enables attackers to get recent user sign-in information that helps them move laterally through the network to access a specific sensitive account. In this detection, an alert is triggered when the SMB session enumeration runs against a domain controller. After exploring the various alerts in this incident, return to the incident's main Incident page in the Microsoft Defender portal.
Select the Devices tab in the incident page to review the devices involved in this incident as reported by Microsoft Defender for Endpoint and Microsoft Defender for Identity. Select the name of the device where the attack was conducted, to open the entity page for that specific device. In that page, you can see alerts that were triggered and related events.
Select the Timeline tab to open the device timeline and view all events and behaviors observed on the device in chronological order, interspersed with the alerts raised. Expanding some of the more interesting behaviors provides useful details, such as process trees. For example, scroll down until you find the alert event Suspicious process injection observed . Select the powershell.exe injected to notepad.exe process event below it, to display the full process tree for this behavior under the Event entities graph on the side pane. Use the search bar for filtering if necessary.
On the incident page, select the Users tab to display the list of users involved in the attack. The table contains additional information about each user, including each user's Investigation Priority score. Select the user name to open the user's profile page where further investigation can be conducted. For more information, see Investigate risky users in Defender for Cloud Apps .
Before we walk you through this simulation, watch the following video to get familiar with what automated self-healing is, where to find it in the portal, and how it can help in your security operations: Navigate back to the incident in the Microsoft Defender portal. The Investigations tab in the Incident page shows the automated investigations that were triggered by Microsoft Defender for Identity and Microsoft Defender for Endpoint. In the following screenshot, only the automated investigation triggered by Defender for Endpoint is displayed. By default, Defender for Endpoint automatically remediates the artifacts found in the queue, which requires remediation.
Select the alert that triggered an investigation to open the Investigation details page. You'll see the following details: Depending on timing, the automated investigation might still be running. Wait a few minutes for the process to complete before you collect and analyze the evidence and review the results. Refresh the Investigation details page to get the latest findings.
During the automated investigation, Microsoft Defender for Endpoint identified the notepad.exe process, which was injected as one of the artifacts requiring remediation. Defender for Endpoint automatically stops the suspicious process injection as part of the automated remediation. You can see notepad.exe disappear from the list of running processes on the test device.
After the investigation is complete and confirmed to be remediated, you resolve the incident. From the Incident page, select Manage incident . Set the status to Resolve incident and select True alert for the classification and Security testing for the determination. When the incident is resolved, it resolves all of the associated alerts in the Microsoft Defender portal and the related portals.
This wraps up attack simulations for incident analysis, automated investigation, and incident resolution. You get to the incident queue from Incidents & alerts > Incidents on the quick launch of the Microsoft Defender portal . Here's an example. The Most recent incidents and alerts section shows a graph of alerts and incidents from the last 24 hours.
Select Choose columns to show details about each incident or its affected entities. Use these details to decide which incidents to analyze first. Apply filters to focus on a specific threat or scenario. Filters help you spot which incidents need quick action. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Managed%20detection%20and%20response • https://learn.microsoft.com/en-us/defender-endpoint/overview-endpoint-detection-response • https://www.signisys.com/learn/endpoint-detection-and-response/ • https://docs.arcticwolf.com/en-us/active-response-log-forwarding-and-security-monitoring/endpoint-detection-and-response-i ntegrations/endpoint-detection-and-response-overview • https://www.threatcrush.com/blog/endpoint-detection-response • https://github.com/sameerwire/Endpoint-Detection-Response-Simulation-Toolkit • https://learn.microsoft.com/en-us/defender-xdr/pilot-deploy-investigate-respond
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Endpoint Detection And Response Simulation Using Python.
[*] Metasploit Scan Running on Target Subnet for Endpoint Detection And Response Simulation Using Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |