Complete Technical Paper Content — Enterprise Data Loss Prevention Tool
Overview & System Context
Enterprise Data Loss Prevention Tool: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9501 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Data loss prevention (DLP) is a set of strategies and technologies that prevent the unauthorized transmission or disclosure of sensitive data in an information system, including data in motion (across networks), at rest (in storage), or in use (on endpoints). This concept is part of information privacy, data security and data governance. DLP systems have traditionally relied upon a variety of classification and enforcement mechanisms to reduce the risk of data loss but increasingly incorporate machine learning and behavioral analytics to enhance detection accuracy. DLP is used in on-premises systems, cloud applications, and hybrid environments. Data loss incidents (unauthorized disclosure or deletion of sensitive data) may turn into data leak incidents (data breaches) when media containing sensitive information are lost and then acquired by an unauthorized party, including via data theft. However, a data leak is possible without losing the data on the originating side.
There are limitations to the effectiveness of DLP systems in reducing risk of data loss. Other terms associated with data leakage prevention include information leak detection and prevention (ILDP), information leak prevention (ILP), content monitoring and filtering (CMF), information protection and control (IPC), and extrusion prevention system (EPS), as opposed to an intrusion prevention system.
The definition of Data Loss Prevention encompasses a set of practices and tools meant to prevent data leakage (also known as data exfiltration) by intentional and unintentional misuse. These practices and tools include encryption, detection, preventative measures, educational pop ups (for unintentional movements), and even machine learning to assess user risk scores. Over time, DLP has evolved into the realm of data protection and has become a premier feature of data protection deployment.
Netskope provides a comprehensive data loss prevention (DLP) enforcement solution for cloud applications and public cloud resources that is ideal for addressing regulatory compliance requirements and protecting sensitive data in your enterprise. The DLP profiles that enforce compliance and protect sensitive data consist of DLP rules that specify data identifiers. These data identifiers find content that should not be present in cloud app transactions or public cloud storage.
Data Classification with Large Language Models (LLM) and Context-Aware Machine Learning Figure 1: 8 Best Data Loss Prevention Software in 2026 Access to this page requires authorization. You can try signing in or changing directories . Every organization plans for and implements data loss prevention (DLP) differently. Why? Because every organization's business needs, goals, resources, and situation are unique. However, there are elements that are common to all successful DLP implementations. This article presents the best practices for planning a DLP deployment.
Get started with Microsoft Security Copilot to explore new ways to work smarter and faster using the power of AI. Learn more about Microsoft Security Copilot in Microsoft Purview . Many organizations choose to implement DLP to comply with various governmental or industry regulations. For example, the European Union's General Data Protection Regulation (GDPR), or the Health Insurance Portability and Accountability Act (HIPAA), or the California Consumer Privacy Act (CCPA). They also implement data loss prevention to protect their intellectual property. However, the starting place and ultimate destination in the DLP journey vary.
Figure 2: Top 10 Data Loss Prevention Software for 2026: Essential Security ... These are just some examples of how customers can approach DLP. It doesn't matter where you start from; DLP is flexible enough to accommodate various types of information protection journeys from start to a fully realized data loss prevention strategy.
The Learn about Microsoft Purview Data Loss Prevention introduces the three different aspects of the DLP planning process . We go into more detail here on the elements that are common to all DLP plans. When implemented, DLP policies can be applied across large portions of your organization. Your IT department can't develop a broad ranging plan on their own without negative consequences. You need to identify the stakeholders who can: In general, these needs tend to be 85% regulatory and compliance protection, and 15% intellectual property protection. Here are some suggestions on roles to include in your planning process: Figure 3: Top 10 Data Loss Prevention Software for 2026: Essential Security ...
Once identified, the stakeholders then describe the categories of sensitive information to be protected and the business processes that they're used in. For example, DLP defines these categories: Stakeholders might identify the sensitive information as "We are a data processor, so we have to implement privacy protections on data subject information and financial information".
Once you have identified your stakeholders, know which sensitive information needs protection, and where it's used, the stakeholders can set their protection goals and IT can develop an implementation plan. Documenting how your organization is going to get from its starting state to the desired end state is essential to communicating with your stakeholders and setting the project scope. Here's a set of steps that are commonly used to deploy DLP. You'll want more detail than the graphic shows, but you can use it to frame your DLP adoption path.
There are multiple ways to discover what individual sensitive items are and where they're located. You may have sensitivity labels already deployed or you may have decided to deploy a broad DLP policy to all locations that only discovers and audits items. To learn more, see Know your data . As you begin your DLP adoption, you can use these questions to focus your policy design and implementation efforts.
Because many organizations come to DLP with the goal of regulatory compliance, answering this question is a natural starting place for planning your DLP implementation. But, as the IT implementer, you're probably not positioned to answer it. Instead, you should consult your legal team and business executives for an answer. Example To get started quickly, you might pick the preconfigured U.K. Financial Data policy template, which includes the Credit Card Number , EU Debit Card Number , and SWIFT Code sensitive information types.
If your organization has implemented administrative units , you can scope your DLP policies by administrative unit or leave the scope default, which applies policies to the full directory. For more information, see Policy Scoping . The items that contain your organization's sensitive information are used every day in the course of doing business. You need to know where instances of that sensitive information may occur and what business processes they're used in. Knowing this helps you choose the right locations to apply your DLP policies. DLP policies can be applied to the following locations: Example Your organization's internal auditors are tracking a set of credit card numbers. They keep a spreadsheet of them in a secure SharePoint site. Several of the employees make copies and save them to their work OneDrive site, which is synced to their Windows 10 device. One of these employees pastes a list of 14 credit card numbers into an email and tries to send it to the outside auditors for review. In this case, you'd want to apply the policy to the secure SharePoint site, all the internal auditors OneDrive accounts, their Windows 10 devices, and Exchange email.
Different groups in your organization may have different views on what counts as an acceptable level of sensitive item leakage. Achieving the perfection of zero leakage may come at too high a cost to the business. Example Your organization's security group and legal team both feel that there should be no sharing of credit card numbers with anyone outside the org. They insist on zero leakage. However, as part of their regular review of credit card number activity, the internal auditors must share some credit card numbers with third-party auditors. If your DLP policy prohibits all sharing of credit card numbers outside the org, there will be a significant business process disruption and added cost to mitigate the disruption in order for the internal auditors to complete their tracking. This extra cost is unacceptable to the executive leadership. To resolve this issue, there needs to be an internal conversation to decide an acceptable level of leakage. Once that is decided, the policy can provide exceptions for certain individuals to share the information, or, it can be applied in audit-only mode.
To learn how to create a policy intent statement and map it to policy configurations see, Design a data loss prevention policy Before you can monitor some DLP locations, there are prerequisites that must be met. See the Before you begin sections of the following articles: When you create your DLP policies, you should consider rolling them out gradually, so you can assess their impact and test their effectiveness before fully enforcing them. For example, you don't want a new DLP policy to unintentionally block access to thousands of documents or to break an existing business process.
If you're creating DLP policies with a large potential impact, we recommend following this sequence: Run the policy in simulation mode, without Policy Tips and then use the DLP reports, and any incident reports, to assess the impact of the policies. You can use DLP reports to view the number, location, type, and severity of policy matches. Based on the results, you can fine-tune your policies as needed. In simulation mode, DLP policies won't impact the productivity of people working in your organization. It's also good to use this stage for testing out your workflow for DLP event review and issue remediation.
Run the policy in simulation mode with notifications and Policy Tips so that you can begin to teach users about your compliance policies and prepare them for when the policies are applied. It's useful to have a link to an organization policy page that provides more details about the policy in the Policy Tip. At this stage, you can also ask users to report false positives, so that you can further refine the conditions and reduce the number of false positives. Move to this stage once you have confidence that the results of applying the policies match what they stakeholders had in mind.
Start full policy enforcement so that the actions in the rules are applied and the content is protected. Continue to monitor the DLP reports and any incident reports or notifications to make sure that the results are what you intend. You can configure your policies so that, when a DLP policy is triggered, email notifications are sent automatically, and policy tips are shown to admins and end users. Policy tips are useful ways to raise awareness of risky behaviors on sensitive items and train users to avoid those behaviors in the future.
The regulations, laws, and industry standards that your organization is subject to will change over time, as will your business goals for DLP. Be sure to include regular reviews of all these areas so that your organization stays in compliance and so your DLP implementation continues to meet your business needs. Dive into DLP architecture essentials and discover how Strac enhances data security with advanced solutions, ensuring compliance and proactive risk mitigation.
Most sensitive data lived in email, file servers, databases, and employee laptops. Security teams deployed endpoint agents, created policies for p ersonally identifiable information (PII) and payment card data , and monitored email traffic for suspicious activity. Customer information flows through SaaS applications , support platforms , cloud storage , browsers, GenAI, Endpoints, and increasingly, AI agents connected to business systems through Model Context Protocol (MCP) . Employees paste information into ChatGPT or Claude , developers connect AI coding assistants to source code repositories, and autonomous agents retrieve data from systems like Salesforce, Slack , Google Drive, and Jira without human intervention.
This is why DLP architecture has become one of the most important components of a modern security program. DLP architecture is the collection of technologies, policies, and processes organizations use to discover, classify, monitor, and protect sensitive information. The objective is straightforward: understand where sensitive data exists, determine who can access it, monitor how it moves, and prevent unauthorized exposure before it becomes a security incident.
A modern DLP architecture must follow the data itself rather than relying on traditional network boundaries. A customer submits a support request and accidentally includes a Social Security Number. The ticket is automatically synchronized to Salesforce. A support agent shares part of the conversation in Slack to get assistance from a colleague. Later, another employee asks ChatGPT to summarize the case and generate a response. An AI agent connected to Salesforce retrieves the same ticket through MCP to create a customer success report.
Within a matter of minutes, sensitive information has moved through multiple applications, multiple users, and potentially multiple AI systems. They may identify the data after it reaches storage. They may generate an alert after exposure has already occurred. But they rarely provide visibility into how the information moved between systems in the first place.
One of the biggest surprises organizations encounter when implementing DLP is discovering how much sensitive data exists outside approved systems. A healthcare provider may believe patient data only exists in its electronic health record platform. A fintech company may assume customer financial information is restricted to Salesforce and internal databases.
Then a discovery scan reveals PHI inside Slack conversations, screenshots stored in Google Drive, attachments in Zendesk tickets, exported spreadsheets in SharePoint, and AI conversations containing customer information. Employees share files, copy information between systems, upload screenshots, and use AI tools to accelerate work. Over time, information appears in places nobody expected.
This is why every modern DLP architecture starts with continuous data discovery and classification. Before an organization can protect sensitive information, it needs visibility into where that information exists and how it is being used. A few years ago, Data Security Posture Management (DSPM) and DLP were often treated as separate security categories. Imagine a Snowflake environment containing millions of customer records. No breach has occurred. No policy has been violated. No data has been exfiltrated.
However, an access review reveals that hundreds of employees have access to data they don't actually need. DSPM helps organizations identify these exposures before they become incidents. It answers questions such as: DLP focuses on protecting data while it moves. DSPM focuses on understanding the risks associated with data where it resides.
2. System Architecture & Core Working Principles The most effective security programs now combine both approaches into a single architecture. For many organizations, work no longer happens on managed devices. It happens inside the browser. Employees spend their day working in Salesforce, Google Workspace , Slack, Notion , Microsoft 365 , ChatGPT, Claude , and countless other web applications.
A contractor using a personal laptop may never install an endpoint agent. A remote employee may never connect to a corporate network. Yet both users can still access sensitive company information through a browser. As a result, browser-based protection has become a critical layer of modern DLP architecture. Security teams increasingly monitor browser uploads, downloads, copy-and-paste activity, form submissions, and AI interactions because the browser has effectively become the primary workspace for modern employees.
A product manager uploads customer feedback into Claude to identify patterns. A developer shares source code with an AI coding assistant. A finance analyst uploads spreadsheets to generate forecasts. A support representative asks ChatGPT to summarize customer conversations. Traditional DLP solutions were designed to inspect email traffic and file transfers. They were not built to inspect prompts, responses, uploaded documents, generated code, or AI conversations.
Modern AI DLP architectures provide visibility into how data moves through AI systems. They inspect prompts before they reach the model, monitor responses before they reach users, and help organizations enforce policies around what information can and cannot be shared with AI platforms. As AI adoption accelerates, these controls are rapidly becoming a standard requirement rather than an optional feature.
Model Context Protocol allows AI agents to connect directly to business applications such as Slack, Salesforce, Google Drive, Jira, Confluence, GitHub, Zendesk, and countless other systems. To complete the task, the agent might access customer records in Salesforce, retrieve files from Google Drive, analyze support tickets in Zendesk, review conversations in Slack, and generate a final report.
This is why MCP security, AI governance, and agentic security have become increasingly important parts of enterprise security strategies. One of the biggest limitations of traditional DLP is that it often stops at detection. Modern DLP architecture increasingly focuses on remediation rather than detection alone.
The objective is to reduce risk immediately rather than simply documenting that a violation occurred. The strongest DLP architectures in 2026 are designed around one simple principle: protect data wherever it moves. Data discovery provides visibility into where sensitive information exists. DSPM identifies exposures and posture risks. SaaS DLP protects business applications. Browser DLP secures web activity. Endpoint DLP protects local devices. AI DLP governs interactions with AI systems. MCP DLP secures agentic workflows. Real-time remediation prevents exposure before it becomes a breach.
Organizations that combine them create a comprehensive view of how data moves throughout the business. They need a platform capable of protecting sensitive information across the environments where work actually happens. Strac combines DSPM and DLP into a single platform that discovers, classifies, monitors, and remediates sensitive data across SaaS applications, cloud platforms, browsers, endpoints, AI systems, and MCP-connected workflows.
For example, a healthcare provider can automatically redact PHI from Zendesk tickets before it spreads across other systems. A fintech company can detect and remediate PCI data inside Slack conversations. A SaaS company can prevent developers from exposing secrets and customer information through AI coding assistants. An enterprise can inspect and govern data flowing through AI agents connected to Salesforce, Google Drive, Jira, and other MCP-enabled applications.
Instead of focusing on a single channel, Strac follows sensitive information wherever it moves and applies protection at the point of risk. As organizations adopt more AI, deploy more SaaS applications, and introduce autonomous agents into business workflows, the number of ways sensitive information can move will continue to increase.
The organizations that succeed will be those that build architectures capable of discovering, understanding, and protecting data across every environment where work happens. Data Loss Prevention (DLP) architecture is the framework organizations use to discover, classify, monitor, and protect sensitive information across SaaS applications, cloud platforms, endpoints, browsers, AI tools, and AI agents. In 2026, modern DLP architectures must go beyond email and endpoints to address new risks introduced by generative AI, Model Context Protocol (MCP), shadow AI, and autonomous agent workflows. Without a modern DLP architecture, organizations face increased exposure to data breaches, compliance violations, and unauthorized data sharing.
AI has fundamentally changed how sensitive data moves inside organizations. Employees now routinely share information with tools like ChatGPT, Claude, Gemini, Copilot, and AI coding assistants to improve productivity. Traditional DLP solutions were not designed to inspect prompts, responses, uploaded documents, or AI-generated content. Modern AI DLP architectures provide visibility into AI interactions, inspect prompts and responses in real time, and prevent sensitive data from being exposed through AI workflows while enabling safe AI adoption.
DSPM (Data Security Posture Management) focuses on discovering where sensitive data lives, identifying overexposed data, and assessing access risks across SaaS, cloud, and data warehouse environments. DLP focuses on monitoring and preventing sensitive data from leaving approved systems. In practice, the two technologies are increasingly converging. Modern platforms combine DSPM and DLP to provide complete visibility into where sensitive data exists, who can access it, and how it moves throughout the organization.
Model Context Protocol (MCP) allows AI agents to connect directly to business applications such as Slack, Salesforce, Google Drive, Jira, GitHub, Zendesk, and Notion. While MCP dramatically improves AI capabilities, it also creates new pathways for sensitive data exposure. Modern DLP architectures now include MCP security controls that inspect AI agent tool calls, govern access permissions, monitor agent activity, and prevent sensitive information from being exposed to AI models or unauthorized systems.
The best DLP solutions in 2026 provide more than detection. Organizations should look for platforms that combine data discovery, DSPM, SaaS DLP, cloud DLP, browser DLP, endpoint DLP, AI DLP, and MCP security within a single platform. Advanced capabilities such as content-aware detection, OCR, machine learning, real-time redaction, masking, blocking, quarantine actions, and support for AI and agentic workflows are becoming essential for protecting sensitive data across today's distributed environments.
The Only Data Discovery (DSPM) and Data Loss Prevention (DLP) for SaaS, Cloud, Gen AI and Endpoints. Access to this page requires authorization. You can try signing in or changing directories . To help protect this sensitive data, and to reduce the risk from oversharing, they need a way to help prevent their users from inappropriately sharing sensitive data with people who shouldn't have it. This practice is called data loss prevention (DLP).
In Microsoft Purview, you implement data loss prevention by defining and applying DLP policies. A DLP policy can help you identify, monitor, and automatically protect sensitive in Enterprise applications & devices and Inline web traffic data. DLP policies act on a variety of locations, methods of data transmission, and types of user activities. DLP monitors and protects against oversharing in enterprise apps and on devices. It targets Microsoft 365 locations, like Exchange and SharePoint, and locations you add, like on-premises file shares, endpoint devices, and non-Microsoft cloud apps. These locations and sources include: DLP, with collection policies , monitors and protects against oversharing to Unmanaged cloud apps by targeting data transmitted on your network and in Microsoft Edge for Business. Use Data Loss Prevention for Cloud Apps in Edge for Business and network data security to cover locations like: DLP is just one of the Microsoft Purview tools that you use to help protect your sensitive items wherever they live or travel.
You should understand the other tools in the Microsoft Purview tool set, how they interrelate, and work better together. See, Microsoft Purview tools to learn more about the information protection process. DLP policies monitor the activities that users take on sensitive items and, if the policy conditions are met, take protective actions. For example, when a user attempts a prohibited action, like copying a sensitive item to an unapproved location or sharing medical information in an email, DLP can: All DLP monitored activities are recorded to the Microsoft 365 Audit log by default and routed to Activity explorer .
DLP monitoring and protection are native to the applications that users use every day. This helps to protect your organization's sensitive items from risky activities, even if your users are unaccustomed to data loss prevention thinking and practices. If your organization and your users are new to data loss prevention practices, the adoption of DLP might require a change to your business processes, and there will be a culture shift for your users. But, with proper planning, testing and tuning, your DLP policies protect your sensitive items while minimizing any potential business process disruptions.
Keep in mind that DLP as a technology can monitor and protect your data at rest, data in use and data in motion across Microsoft 365 services, Windows 10, Windows 11, and macOS (three latest released versions) devices, on-premises file shares, and on-premises SharePoint. There are planning implications for the different locations, the type of data you want to monitor and protect, and the actions to be taken when a policy match occurs.
DLP policies can block users from performing prohibited activities, like inappropriate sharing of sensitive information via email. As you plan your DLP policies, you must identify the business processes that touch your sensitive items. The business process owners can help you identify appropriate user behaviors that should be allowed and inappropriate user behaviors that should be protected against. You should plan your policies and deploy them in simulation mode , and evaluate their impact, before running them in more restrictive modes.
A successful DLP implementation is as much dependent on getting your users trained and acclimated to data loss prevention practices as it is on well planned and tuned policies. Since your users are heavily involved, be sure to plan for training for them too. You can strategically use policy tips to raise awareness with your users before changing the policy status from simulation mode to more restrictive modes.
You can apply DLP policies to data at rest, data in use, and data in motion in locations such as: Each one has different prerequisites. Sensitive items in some locations, like Exchange online, can be brought under the DLP umbrella by just configuring a policy that applies to them. Others, such as on-premises file repositories, require a deployment of Microsoft Purview Information Protection scanner . You'll need to prepare your environment, code draft policies, and test them thoroughly before activating any blocking actions.
Start by defining your control objectives, and how they apply across each respective workload. Draft a policy that embodies your objectives. Feel free to start with one workload at a time, or across all workloads - there's no impact yet. For more information, see Create and deploy data loss prevention policies . Evaluate the impact of the controls by implementing them with a DLP policy in simulation mode . Actions defined in a policy aren't applied while the policy is in simulation mode. It's ok to apply the policy to all workloads in simulation mode, so that you can get the full breadth of results, but you can start with one workload if you need to. For more information, see Policy Deployment .
While in simulation mode, monitor the outcomes of the policy and fine-tune it so that it meets your control objectives while ensuring you aren't adversely or inadvertently impacting valid user workflows and productivity. Here are some examples of things to fine-tune: Once the policy meets all your objectives, turn it on. Continue to monitor the outcomes of the policy application and tune as needed.
You have flexibility in how you create and configure your DLP policies. You can start from a predefined template and create a policy in just a few clicks or you can design your own from the ground up. No matter which you choose, all DLP policies require the same information from you. Choose what you want to monitor - DLP comes with many predefined policy templates to help you get started or you can create a custom policy.
Choose administrative scoping - DLP supports assigning Administrative Units to some Enterprise applications & devices policies. Administrators who are assigned to an administrative unit can only create and manage policies for the users, groups, distribution groups, accounts, and sites that they're assigned to. So, policies can be applied to all users, groups, and sites by an unrestricted administrator, or they can be scoped to administrative units. See, Policy Scoping for more DLP specific details.
See, Administrative units for the details on administrative units across Microsoft Purview Information Protection. Choose where you want to monitor - You pick one or more locations that you want DLP to monitor for sensitive information. You can monitor: The users and groups mentioned above should be Online users and M365, Exchange online, and Microsoft Entra groups 3. Software Implementation, Frameworks & Protocols Choose the conditions that must be matched for a policy to be applied to an item - You can accept preconfigured conditions or you can define custom conditions. Some examples are: Choose the action to take when the policy conditions are met - The actions depend on the location where the activity is happening. Some examples are: All DLP policies are created and maintained in the Microsoft Purview portal. See, Create and Deploy data loss prevention policies for more information.
After you create a DLP policy, it's stored in a central policy store, and then synced to the various content sources, including: After the policy is synced to the right locations, it starts to evaluate content and enforce actions. DLP reports a vast amount of information to Microsoft Purview from monitoring policy matches and actions, to user activities. You need to consume and act on that information to tune your policies and triage actions taken on sensitive items. The telemetry goes into the Microsoft 365 audit Logs first, is processed, and makes its way to different reporting tools. Each reporting tool has a different purpose.
The DLP Overview page gives you quick access to important information about your DLP policies, including: You can investigate incidents for Microsoft Purview Data Loss Prevention (DLP) from the Microsoft Defender portal Incidents & alerts > Incidents . See Investigate data loss incidents with Microsoft Defender XDR and Investigate alerts in Microsoft Defender XDR .
DLP can generate alerts when a user(s) performs an activity that meets the criteria of a rule in a DLP policy, and you have incident reports configured to generate alerts. Depending on your subscription level, alerts can be aggregated on a time window/rule basis or on a time windows/user basis(preview) . DLP posts the alert for investigation in the DLP Alerts dashboard . Use the DLP Alerts dashboard to view alerts, triage them, set investigation status, and track resolution. Alerts are also routed to Microsoft Defender portal where you can do all the alert dashboard tasks plus more.
DLP alerts are available in the Microsoft Defender portal for six months. They're only available in the Microsoft Purview DLP alerts dashboard for 30 days. If you're an administrative unit restricted admin, you'll only see the DLP alerts for your administrative unit. Here's an example of alerts generated by policy matches and activities from Windows 10 devices.
You can also view details of the associated event with rich metadata in the same dashboard. Alerts are generated differently for emails than they are for SharePoint or OneDrive items. In SharePoint and OneDrive, DLP scans existing items as well as new ones and generates an alert whenever a match is found. In Exchange, new email messages are scanned and an alert is generated if there's a policy match. DLP does not scan or match previously existing email items that are stored in a mailbox or archive.
The Activity explorer tab on the DLP page has multiple filters you can use to view DLP events. Use this tool to review activity related to content that contains sensitive info or has labels applied, such as what labels were changed, files were modified, and matched a rule. You can view the last 30 days of DLP information in Activity Explorer using these preconfigured filters: You can also access DLP report using via these cmdlets in the Security & Compliance PowerShell.
However, DLP reports need to pull data from across Microsoft 365, including Exchange. For this reason, the following cmdlets for DLP reports are available in Exchange PowerShell. To use the cmdlets for these DLP reports, take the following steps: A DLP Rule Undo event occurs when a previously matched DLP rule no longer applies to a document, causing the rule to be effectively reversed. This can happen in two main scenarios: when a user modifies content so it no longer meets the rule conditions, or when a policy or rule is changed and triggers re-evaluation of already-classified content. During this re-evaluation, if a document no longer satisfies the rule criteria, a DLP Rule Undo event is generated. For example, if a policy is configured to detect documents containing at least five Social Security numbers and a user uploads a document with ten, the rule will initially match. If the user later removes the sensitive data so the document no longer meets the threshold, the rule is undone. Similarly, if an administrator updates the policy to require fifteen Social Security numbers, the same document will no longer meet the criteria upon re-evaluation, resulting in a DLP Rule Undo event.
You can see the text that surrounds the matched content, like a credit card number in a DLPRuleMatch event in Activity explorer. DLPRuleMatch events are paired with user egress activities such as "CopyToClipboard" or "CloudEgress". They should be right next to (or at least very close to) each other in Activity explorer. You want to look at both because the user activity contains details about the matched policy and the DLPRuleMatch event contains the details about the text that surrounds the matched content.
For endpoint, be sure that you have applied KB5016688 for Windows 10 devices and KB5016691 for Windows 11 devices or above. To learn how to use data loss prevention to comply with data privacy regulations, see Deploy information protection for data privacy regulations with Microsoft Purview (aka.ms/m365dataprivacy).
Learn how to build a successful DLP implementation strategy for 2026. Discover best practices, deployment steps, common challenges, and how to protect sensitive data across SaaS, cloud, AI, browsers, and endpoints. · A successful DLP implementation starts withdiscovering and classifying sensitive data across SaaS apps, cloud storage,endpoints, browsers, and AI tools.
· Roll out DLP in phases by identifying criticaldata, creating policies, testing them, and gradually automating enforcement. · Modern DLP solutions should go beyond alerts byautomatically redacting, masking, blocking, or quarantining sensitive data inreal time. · Choose a platform with broad integrations,AI-powered detection, and built-in support for compliance frameworks like GDPR,HIPAA, PCI DSS, SOC 2, and ISO 27001.
· Strachelps organizations implement modern DLP with agentless deployment, unifiedDSPM and DLP, AI protection, and real-time remediation across cloud, SaaS,endpoints, browsers, and AI applications. Data no longer stays in one place. Employees work across SaaS apps , cloud storage , AI tools , browsers , and endpoints , creating more opportunities for sensitive information to be exposed. That's why implementing Data Loss Prevention (DLP) today is about much more than deploying security software. It requires a strategy that protects data wherever it moves without disrupting productivity.
This guide explains how to build a modern DLP implementation strategy, the key stages of a successful rollout, common mistakes to avoid, and what to look for in a DLP solution. A DLP implementation strategy is a plan for discovering, classifying, monitoring, and protecting sensitive data across your organization. The goal is to understand where sensitive data lives, who can access it, how it's being shared, and automatically prevent unauthorized exposure.
Instead of simply detecting risks, modern DLP solutions help stop them before they become data breaches. Traditional DLP focused on email and network traffic. Modern businesses need visibility across cloud applications, AI tools, and endpoints. Most organizations implement DLP in phases instead of trying to secure everything at once. A typical rollout includes: Rolling out a DLP solution isn't just about installing software. The most successful implementations start by understanding where sensitive data lives and then gradually applying policies that reduce risk without disrupting the business.
Before you can protect data, you need to know where it exists. Start by scanning your SaaS applications, cloud storage, endpoints, databases, and AI tools to identify sensitive information such as PII, PHI, PCI data, financial records, source code, and intellectual property. Automated data discovery and classification gives security teams visibility into what needs protection and helps prioritize the highest-risk areas.
Once sensitive data has been identified, create policies based on your business and compliance requirements. These policies determine what data should be monitored, who can access it, and what happens when a policy is violated. For example, you may want to block payment card data from being shared in Slack, automatically redact personal information from support tickets, or prevent confidential documents from being uploaded to AI applications.
Rather than enforcing policies immediately, begin by monitoring user activity. This allows you to understand how data moves through your organization and fine-tune policies before blocking legitimate work. Running in monitor mode first also helps reduce false positives and improves user adoption. Your environment will constantly change as employees adopt new SaaS applications, AI tools, and workflows. DLP policies should be reviewed regularly to account for new risks, changing compliance requirements, and evolving business needs.
Organizations that continuously monitor and refine their DLP strategy are far better prepared to prevent data loss over time. Even with the right technology, DLP projects can fail if they're rolled out too aggressively or without clear planning. Overly broad policies generate unnecessary alerts and quickly lead to alert fatigue. AI-powered classification and policy tuning help improve accuracy.
Many organizations protect email but overlook SaaS applications, cloud storage, AI tools, browsers, and endpoints where sensitive data is also shared. If security controls interrupt everyday work, employees often look for workarounds. Modern DLP should work quietly in the background while only intervening when necessary.
Meeting requirements for GDPR, HIPAA, PCI DSS, SOC 2, ISO 27001, and other regulations becomes difficult without centralized visibility and automated policy enforcement. Using separate tools for data discovery, classification, DLP, and AI security creates complexity and operational overhead. A unified platform simplifies management while providing consistent protection across the organization.
Not all DLP platforms offer the same level of protection. As organizations adopt more SaaS applications, AI tools, and cloud services, it's important to choose a solution that protects data wherever it lives without adding unnecessary complexity. A modern DLP platform should automatically discover and classify sensitive data across SaaS applications, cloud storage, endpoints, browsers, AI tools, and databases. Look for support for PII, PHI, PCI, financial data, source code, secrets, and custom data types.
Detecting sensitive data isn't enough. The platform should automatically respond by masking, redacting, blocking, quarantining, encrypting, or deleting sensitive information before it can be exposed. 4. Practical Deployment, Analysis & Case Studies Traditional regex-based detection often creates false positives. AI and machine learning improve accuracy by understanding context and identifying sensitive information in text, documents, images, PDFs, spreadsheets, screenshots, and other unstructured content.
Choose a platform that integrates with the applications your teams already use, including Microsoft 365, Google Workspace, Slack, Salesforce, Jira, Zendesk, SharePoint, OneDrive, Box, Dropbox, ChatGPT, Claude, Gemini, Microsoft Copilot, and endpoint devices. If your business operates in a regulated industry, look for built-in policies that support frameworks such as GDPR, HIPAA, PCI DSS, SOC 2, ISO 27001, CCPA, and NIST.
Strac is a modern DSPM and DLP platform that helps organizations discover, classify, monitor, and protect sensitive data across cloud, SaaS, endpoints, browsers, and AI applications from a single platform. Whether you're implementing DLP for the first time or replacing a legacy solution, Strac helps security teams reduce data exposure while keeping deployment simple and productivity high.
A successful DLP implementation is an ongoing process, not a one-time project. The right strategy starts with understanding where sensitive data lives, building policies around business risk, and automating protection across every environment where data moves. As organizations continue to adopt SaaS applications, AI tools, and cloud services, choosing a modern DLP platform with broad visibility, real-time remediation, and built-in compliance support is essential. Solutions like Strac help organizations simplify DLP implementation while protecting sensitive data wherever employees work.
A DLP implementation strategy is a structured plan for discovering, classifying, monitoring, and protecting sensitive data across your organization. It typically includes data discovery, policy creation, monitoring, automated remediation, and ongoing optimization to reduce the risk of data loss and ensure compliance. The timeline depends on the size and complexity of your environment. Many modern, cloud-native DLP platforms can be deployed within days, while larger enterprise rollouts may take several weeks as policies are tested and refined.
A DLP solution should protect any sensitive or regulated data, including personally identifiable information (PII), protected health information (PHI), payment card data (PCI), financial records, source code, intellectual property, credentials, API keys, and confidential business documents across SaaS, cloud, endpoints, browsers, and AI applications. Look for automated data discovery, AI-powered classification, real-time remediation, broad SaaS and cloud integrations, endpoint and browser protection, AI security, compliance templates, and centralized visibility across your entire data environment.
Strac combines DSPM and DLP in a single, agentless platform that discovers, classifies, and protects sensitive data across SaaS applications, cloud storage, endpoints, browsers, and AI tools. With AI-powered detection, real-time remediation, and built-in compliance policies, organizations can deploy DLP quickly while reducing operational overhead. The Only Data Discovery (DSPM) and Data Loss Prevention (DLP) for SaaS, Cloud, Gen AI and Endpoints.
In the digital economy, data is the most critical asset for any organization. Data Loss Prevention (DLP) has evolved from a niche compliance tool into a foundational component of enterprise risk management and business resilience. With the average cost of a data breach reaching millions and regulatory fines under laws like GDPR amounting to up to 4% of global revenue, a proactive DLP strategy is essential.
This definitive guide provides a comprehensive overview of DLP, from core concepts and cutting-edge tools to a step-by-step implementation framework, empowering you to build an effective defense for your organization’s most valuable information. Data Loss Prevention is a cohesive set of technologies, policies, and processes designed to detect and prevent the unauthorized access, use, or transfer of sensitive data.
Unlike traditional security that guards the perimeter, DLP takes a data-centric approach, focusing on protecting the content itself, whether it’s at rest, in motion, or in use. Modern DLP solutions use advanced techniques like contextual analysis, fingerprinting, and machine learning to accurately identify sensitive information based on regulatory templates (GDPR, HIPAA) or custom-defined criteria, enforcing protection through alerts, encryption, or blocking.
2019-Present: Evolution into integrated, intelligent platforms featuring AI/ML, cloud-native architecture, and automated response, reflecting data’s movement beyond the corporate network into SaaS apps and personal devices. This is data stored on any medium: databases, file servers, cloud storage (AWS S3, Google Drive), laptops, and USB drives. Protection Tools: Full Disk Encryption (FDE), File-Level Encryption, Database Activity Monitoring (DAM), and strict access controls.
Data actively moving through networks, whether via email, web uploads, cloud app syncing (Slack, Teams), or instant messaging. Protection Tools: Network-based DLP, secure email gateways, Cloud Access Security Brokers (CASB), and encrypted transfer protocols.
Data being actively viewed or processed by users on endpoints, such as in applications, during copy-paste actions, or while being printed. Protection Tools: Endpoint DLP agents, application controls, digital rights management (DRM), and user behavior analytics. Selecting the right architecture depends on your organization’s primary data pathways and risks.
DAM solutions provide granular, real-time oversight of database transactions, offering specialized capabilities like sensitive data discovery within databases, session recording for privileged users, and compliance reporting tailored to structured data environments. The DLP market offers solutions ranging from broad enterprise suites to specialized, cloud-native platforms. Selecting the right one requires matching vendor strengths to your specific environment and needs.
Map Your Environment: Identify where your sensitive data lives and flows—Microsoft 365, Google Workspace, endpoints, SaaS apps. Your primary data repository dictates the tool’s core competency needed.
Define Primary Use Cases: Is the driver compliance reporting (need templated policies), insider threat prevention (need endpoint forensics), or cloud/GENAI data security (need API integrations)? Prioritize accordingly. Assess Operational Model: Enterprise suites (Symantec, Forcepoint) are powerful but require significant resources. Cloud-native platforms (Nightfall, Cyberhaven) often offer faster deployment and easier management.
Plan for Convergence: Consider how the DLP tool will integrate with your existing Security Information and Event Management (SIEM), Extended Detection and Response (XDR), or Cloud Security Posture Management (CSPM) tools for a unified security posture. A successful Data Loss Prevention program is a business initiative, not just an IT project. Follow this phased approach.
Secure Executive Buy-In: Present a business case with quantified risk and ROI. Form a cross-functional steering committee with IT, legal, compliance, and business unit leaders. Identify & Classify Critical Data: Conduct discovery workshops. Create an inventory with a classification schema (e.g., Public, Internal, Confidential, Restricted) and tag data accordingly.
Perform a Risk Assessment: Map data flows and identify risk scenarios (accidental leak, malicious insider). Assess current controls using frameworks like NIST CSF. Evaluate & Select a Solution: Use the criteria in Section 4.2. Run proof-of-concept trials with shortlisted vendors to test detection accuracy and management overhead.
Pilot: Deploy in “monitor-only” mode to a low-risk department. Tune policies based on findings. Refine & Expand: Begin limited enforcement, then roll out to additional departments with tailored policies. Enterprise Rollout: Achieve full deployment with comprehensive, department-specific policy enforcement. Develop Clear Policies: Start with high-impact, low-false-positive rules (e.g., blocking unencrypted Social Security numbers via email). Establish a formal exception and override process.
Integrate into SOC Workflows: Feed DLP alerts into your Security Operations Center (SOC) and create specific incident response playbooks. Establish Metrics & Review Cycles: Track technical metrics (false positives), business metrics (incidents prevented), and operational metrics (response time). Review and refine policies quarterly.
High False Positives: Combat this with machine-learning-based classification, regular policy tuning cycles, and incorporating user feedback on alerts. Performance Impact: Deploy lightweight agents, use selective scanning instead of full-disk scans, and leverage cloud-based analysis where possible.
Shadow IT & Cloud Sprawl: Integrate DLP with Cloud Access Security Broker (CASB) solutions and conduct regular discovery audits to maintain visibility. User Resistance: Implement progressive enforcement (monitor, then warn, then block), communicate transparently about the “why,” and provide easy, approved channels for secure data sharing.
Siloed Departments: Establish a DLP governance committee with shared goals and a RACI matrix to clarify roles and responsibilities across teams. DLP tools will increasingly use predictive analytics to score user risk based on behavior, employ natural language processing (NLP) for more accurate content classification, and automate incident investigation and response workflows.
The principle of “never trust, always verify” will extend to data. DLP will enable data-centric micro-segmentation (isolating data based on sensitivity) and require continuous authentication for access to critical datasets. A new frontline for DLP is securing data flowing into and out of Large Language Models (LLMs) like ChatGPT. Future DLP tools will natively monitor API calls to GenAI services to prevent the exposure of proprietary code, strategic documents, or PII.
Next 30 Days: Perform a sensitive data discovery pilot. Draft a one-page business case for executive review. Next 90 Days: Form a DLP working group. Finalize your data classification policy. Evaluate 2-3 vendors. 5. Performance Evaluation & Extended Technical Observations Next 12 Months: Complete a phased deployment of your chosen solution. Establish quarterly review cycles and measure your program’s maturity against initial goals.
Data Loss Prevention is a strategic business enabler . A well-executed DLP program does more than prevent breaches. It builds customer trust, protects intellectual property, and ensures operational resilience. By adopting a data-centric approach, choosing the right tools for your environment, and following a structured implementation framework, your organization can turn data security from a vulnerability into a competitive advantage.
I'm Kevin James, and I'm passionate about writing on Security and cybersecurity topics. Here, I'd like to share a bit more about myself.I hold a Bachelor of Science in Cybersecurity from Utica College, New York, which has been the foundation of my career in cybersecurity.As a writer, I have the privilege of sharing my insights and knowledge on a wide range of cybersecurity topics. You'll find my articles here at Cybersecurityforme.com, covering the latest trends, threats, and solutions in the field.
Information technology (IT) security and cybersecurity are the building blocks of any organization’s data protection plan. Some people use these… In a world where cyberattacks are constantly increasing in frequency, severity, and sophistication, cybersecurity professionals need to start thinking about… In today’s digital world, cyberattacks are not a matter of “if” but “when.” Organizations invest heavily in firewalls, antivirus software,… Data Loss Prevention (DLP) Strategy Steps: Guide to Building an Effective Data Loss Prevention Plan A well-designed DLP strategy is no longer optional. As organizations expand across cloud platforms, remote work environments, and third-party ecosystems, sensitive data moves faster and farther than ever before. At the same time, stricter data sovereignty laws and cross-border data […] A well-designed DLP strategy is no longer optional. As organizations expand across cloud platforms, remote work environments, and third-party ecosystems, sensitive data moves faster and farther than ever before. At the same time, stricter data sovereignty laws and cross-border data transfer regulations are placing greater pressure on organizations to maintain control over where data is stored, processed, and accessed. Without a structured data loss prevention strategy, businesses risk regulatory penalties, reputational damage, and operational disruption.
Start your DLP strategy by clearly defining what sensitive data you must protect and why. Align your data loss prevention plan with regulatory requirements such as GDPR , HIPAA , or industry mandates, and tie it directly to business priorities like customer trust and operational continuity. Next, conduct a focused security risk assessment. Identify where sensitive data is stored, who can access it, how it is shared, and where controls are weak. Pay special attention to remote access, third-party collaboration, and legacy systems.
Finally, document your primary risk scenarios. Include both insider risks such as oversharing or misconfigured permissions and external threats like phishing or ransomware. Prioritizing these risks will help you build a practical and effective DLP implementation strategy instead of a theoretical one. Gain visibility before enforcing controls. Identify where sensitive data lives across endpoints, cloud platforms, shared drives, and on-prem systems. Focus on high-risk data types such as PII , financial records, intellectual property, and healthcare information.
Map how this data moves across departments, regions, and external collaborators. Understanding data flows helps you apply DLP controls where exposure risk is highest and strengthens your overall data governance framework. Once data is identified, classify it. Create clear categories such as public, internal, confidential, and restricted. Align these classifications with your information security strategy and compliance requirements.
Use automated tagging and metadata to scale classification across large volumes of files. Apply read-only metadata where necessary to preserve audit integrity and prevent tampering. Classification should directly trigger enforcement actions such as access restrictions, retention rules, or DLP policies. Learn how data sovereignty differs from data residency and why the distinction is critical for regulatory compliance. Click to explore the full breakdown.
Limit access to sensitive data based on role and business need. Implement role-based access control and enforce file and folder-level permissions to reduce unnecessary exposure. Actively review external sharing permissions and remove excessive access. Apply Zero Trust pillars so access is continuously verified and never assumed. This reduces insider risk and prevents oversharing across internal and third-party environments.
Extend protection across hybrid environments. Monitor file uploads, downloads, and transfers on endpoints and in cloud storage platforms. Ensure sensitive data is encrypted at rest and in transit. Apply controls to external sharing, including expiration dates, password protection, and restricted permissions. Endpoint DLP controls should work together to protect remote and distributed workforces.
Reduce risk by limiting how long sensitive data is stored. Implement automated data retention policies and deletion policies aligned with regulatory requirements. Use automated workflows to enforce policy rules consistently. Enable temporary or transient file sharing when required, and ensure expired access is revoked automatically. Automation reduces manual oversight and strengthens compliance enforcement.
Visibility is critical to an effective DLP roll out strategy. Track user activity, file access, permission changes, and sharing behavior. Integrate with SIEM systems to centralize alerts and correlate suspicious activity. Configure automated alerts for unusual behavior such as bulk downloads or repeated failed login attempts. Detailed audit trails help demonstrate regulatory compliance and support incident response.
Start with pilot DLP projects to validate policies before full deployment. Measure outcomes such as policy violations, reduced oversharing, and improved response times. Refine controls to balance security and usability. As your organization grows, ensure your data loss prevention project plan scales across users, departments, and geographic regions without increasing administrative complexity.
Many DLP initiatives fail due to overly complex tools that reduce user adoption. Choose solutions that integrate smoothly into existing workflows. Another common issue is poor visibility into unstructured data. Invest in automated classification and discovery tools. Finally, ensure technical controls directly enforce your data protection policy. A documented policy without enforcement creates compliance gaps.
A modern DLP strategy should align with Zero Trust principles. Require continuous verification for users and devices, enforce least privilege access, and strictly control external collaboration. Encrypt sensitive data beyond the network perimeter and assume no user or device is automatically trusted. Zero Trust strengthens DLP enforcement across distributed environments and remote workforces.
FileCloud provides the technical foundation required to support a comprehensive data loss prevention strategy. Organizations can enforce granular file and folder permissions, apply metadata-driven classification, and implement Zero Trust File Sharing® for secure external collaboration. Built-in retention policies, audit-ready logging, and integration with DLP, SIEM, and identity systems support regulatory compliance and insider threat mitigation. Flexible deployment options including on-prem, hybrid , and regionally hosted environments help organizations address stricter data sovereignty requirements and maintain control over where sensitive data resides.
A strong DLP implementation strategy includes structured data discovery, classification controls, granular access enforcement, real-time monitoring, and automated policy execution. It should align directly with regulatory requirements and business risk priorities while integrating with identity management and security systems. Successful implementation also requires clear ownership, executive support, phased deployment, and measurable performance indicators to ensure long-term effectiveness.
An effective DLP roll out strategy succeeds when it prioritizes high-risk data first, applies clear classification standards, and introduces enforcement controls in controlled phases rather than all at once. Organizations that balance usability with security see higher adoption and fewer workarounds. Ongoing monitoring, policy refinement, and user education are critical to maintaining effectiveness as the environment evolves.
A comprehensive data loss prevention plan should clearly define sensitive data categories, document how data flows across systems and teams, establish access control policies, enforce encryption standards, and implement retention and deletion rules. It should also outline monitoring procedures, incident response protocols, and accountability structures. The plan must connect governance requirements with enforceable technical controls.
A DLP project should begin with stakeholder alignment and risk assessment, followed by data discovery and classification. From there, organizations should design enforcement policies, test them in a pilot environment, and refine controls before scaling. Enterprise-level DLP projects require coordination between security, compliance, IT, and legal teams to ensure policies are enforceable and aligned with regulatory obligations.
A data loss prevention project plan must map each technical control to a specific regulatory or internal policy requirement. It should define how sensitive data is classified, how access is controlled, how retention is enforced, and how audit evidence is collected. This approach ensures compliance is built into the architecture rather than treated as a separate documentation exercise.
A data protection policy establishes the rules and expectations for handling sensitive information, while a DLP strategy enforces those rules through technology and process controls. The policy defines what should happen, and the DLP implementation strategy ensures it happens consistently through monitoring, classification, access restrictions, and automated enforcement.
Cloud DLP should operate as part of a unified security framework that includes endpoint protections, identity management, and access control systems. It must monitor data movement within cloud storage environments, enforce encryption, and restrict external sharing. For organizations operating in hybrid environments, cloud DLP must provide visibility and enforcement that align with on-prem systems to eliminate blind spots.
DLP supports a data governance framework by acting as the enforcement layer that ensures governance policies are consistently applied. Governance defines how data is categorized, stored, accessed, and retained. DLP ensures those rules are executed automatically through classification, monitoring, and access controls. Together, they provide structured oversight of sensitive data across departments, jurisdictions, and regulatory environments.
Data is a precious resource for businesses, but losing it can also have disastrous consequences. To avoid this, it’s best to implement a DLP strategy. What is DLP? What’s the point? And how can it be implemented? Find out the answers. DLP stands for Data Loss Prevention . The idea is to prevent data loss , especially by preventing employees from sending critical information outside the company’s network. To achieve this, organizations can implement a series of measures aimed at ensuring the security of sensitive information.
Often, DLP solutions are software used by IT security managers to control what can or cannot be transferred. For this purpose, DLP solutions classify different data based on their level of confidentiality. This allows defining what can or cannot leave the network (and by whom). In addition to enhancing control over network activity, DLP software can also filter data streams within the network itself, thereby protecting data in motion.
To optimize the use of these tools, companies have a significant interest in defining a comprehensive data leak prevention strategy. 43% of data breaches in an organization originate from an internal employee. Therefore, while human error is a factor, in the realm of IT security and data protection, these errors can sometimes have disastrous consequences for organizations.
Indeed, an employee who inadvertently shares a file on a public cloud and discloses confidential information can hold the company liable or tarnish its reputation. Not to mention the financial losses required to mitigate the damage. The purpose of DLP (Data Loss Prevention) software is precisely to prevent unauthorized users from sharing information that should remain on the network (potentially harming the company).
In addition to internal threats, companies across all sectors of activity are also subject to the GDPR (General Data Protection Regulation). In this regard, organizations are considered responsible for all their data, whether it concerns the company itself, customers, partners, and so on. And when the organization holds information related to third parties, it must be doubly vigilant regarding the risk of data exfiltration.
To successfully implement your data loss prevention strategy, you need to follow a series of best practices. Here’s what you need to know: First and foremost, it is essential to define critical data-those that would genuinely harm the company in the event of theft or cyberattacks.
Network administrators should focus their attention on these sensitive data sets, as they are more likely to be targeted by cyberattacks. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Data%20loss%20prevention%20software • https://docs.netskope.com/en/data-loss-prevention • https://docs.paloaltonetworks.com/enterprise-dlp/getting-started/about-enterprise-data-loss-prevention • https://learn.microsoft.com/en-us/purview/dlp-overview-plan-for-dlp • https://www.strac.io/blog/understanding-data-loss-prevention-architecture • https://learn.microsoft.com/en-us/purview/dlp-learn-about-dlp • https://www.strac.io/blog/data-loss-prevention-implementation-strategy • https://cybersecurityforme.com/data-loss-prevention-dlp-complete-guide/ • https://www.filecloud.com/blog/dlp-strategy/ • https://liora.io/en/dlp-data-loss-prevention-principles-and-implementation
Extracted Research Figures & Simulation Topologies
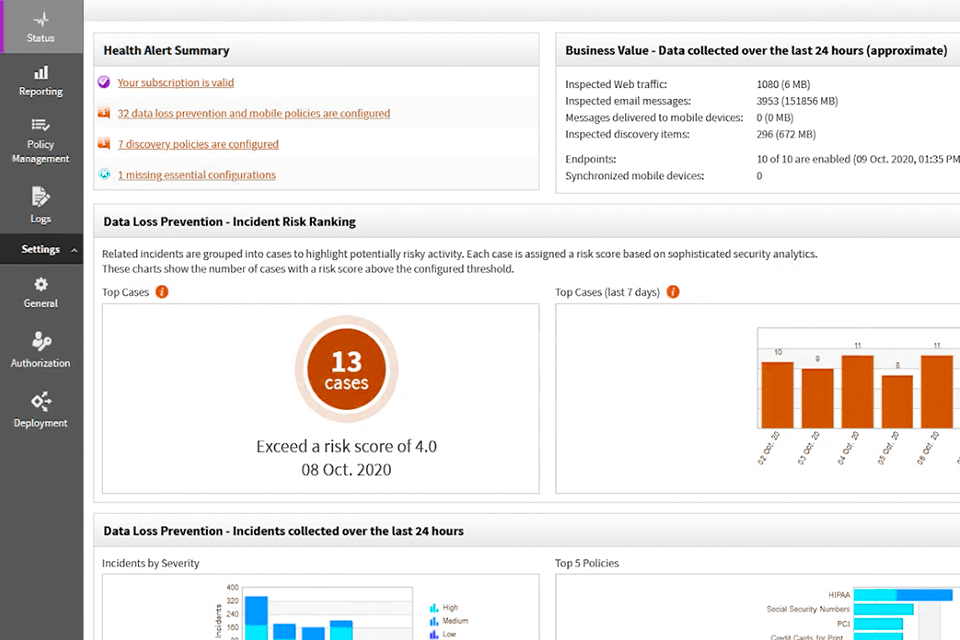
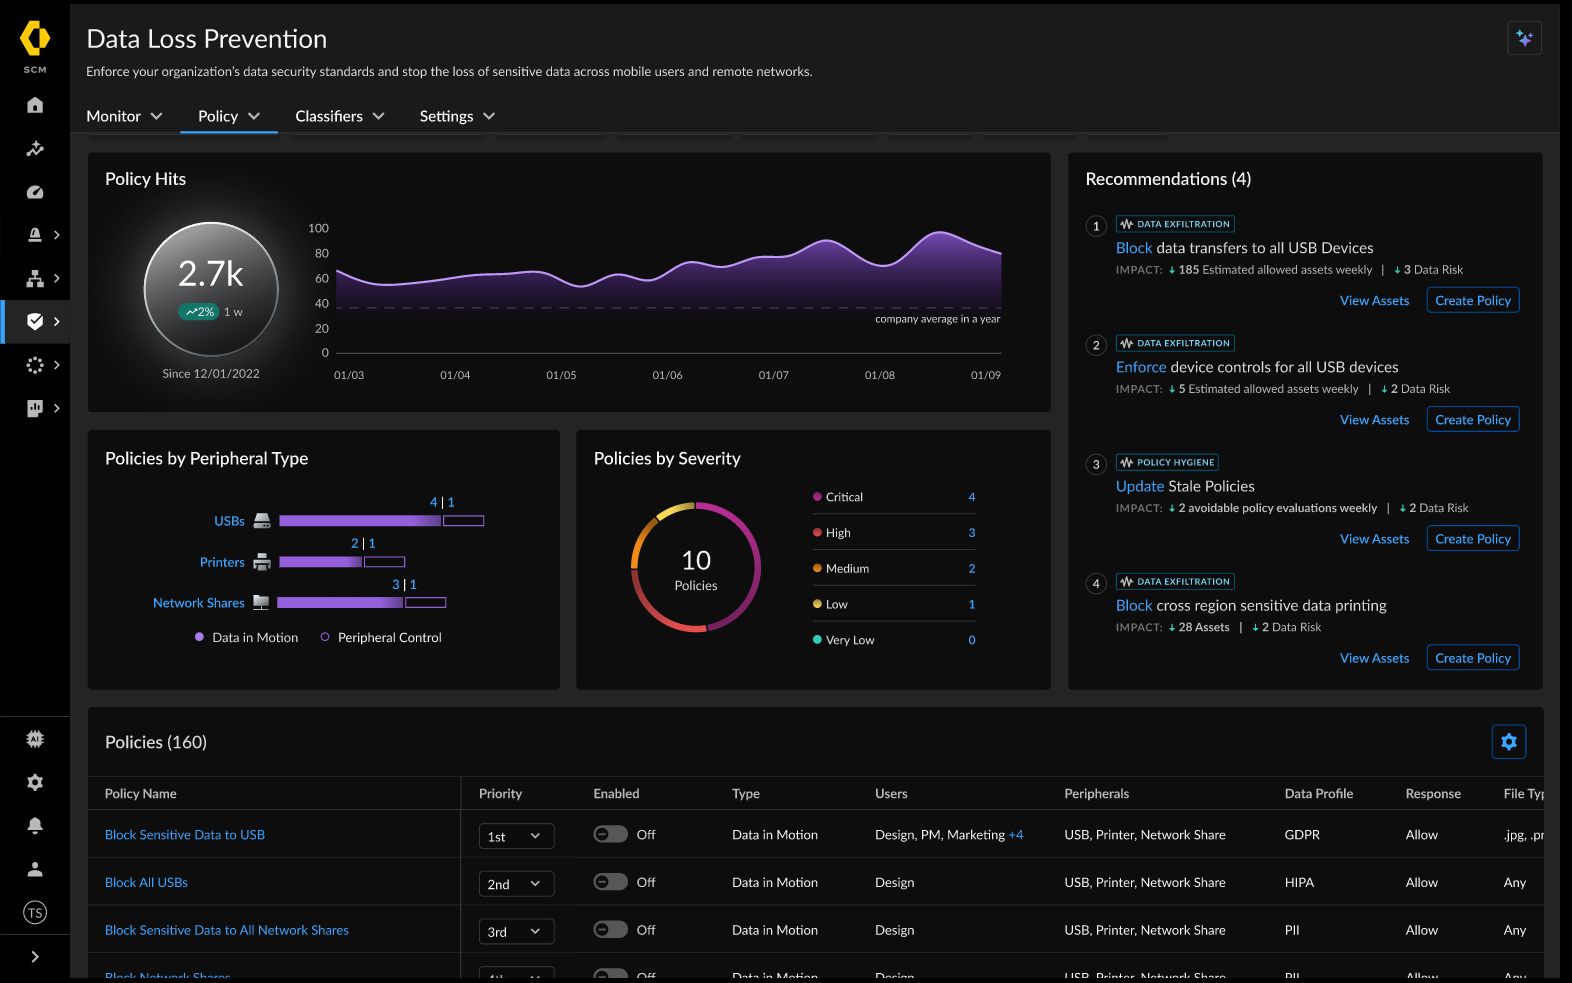
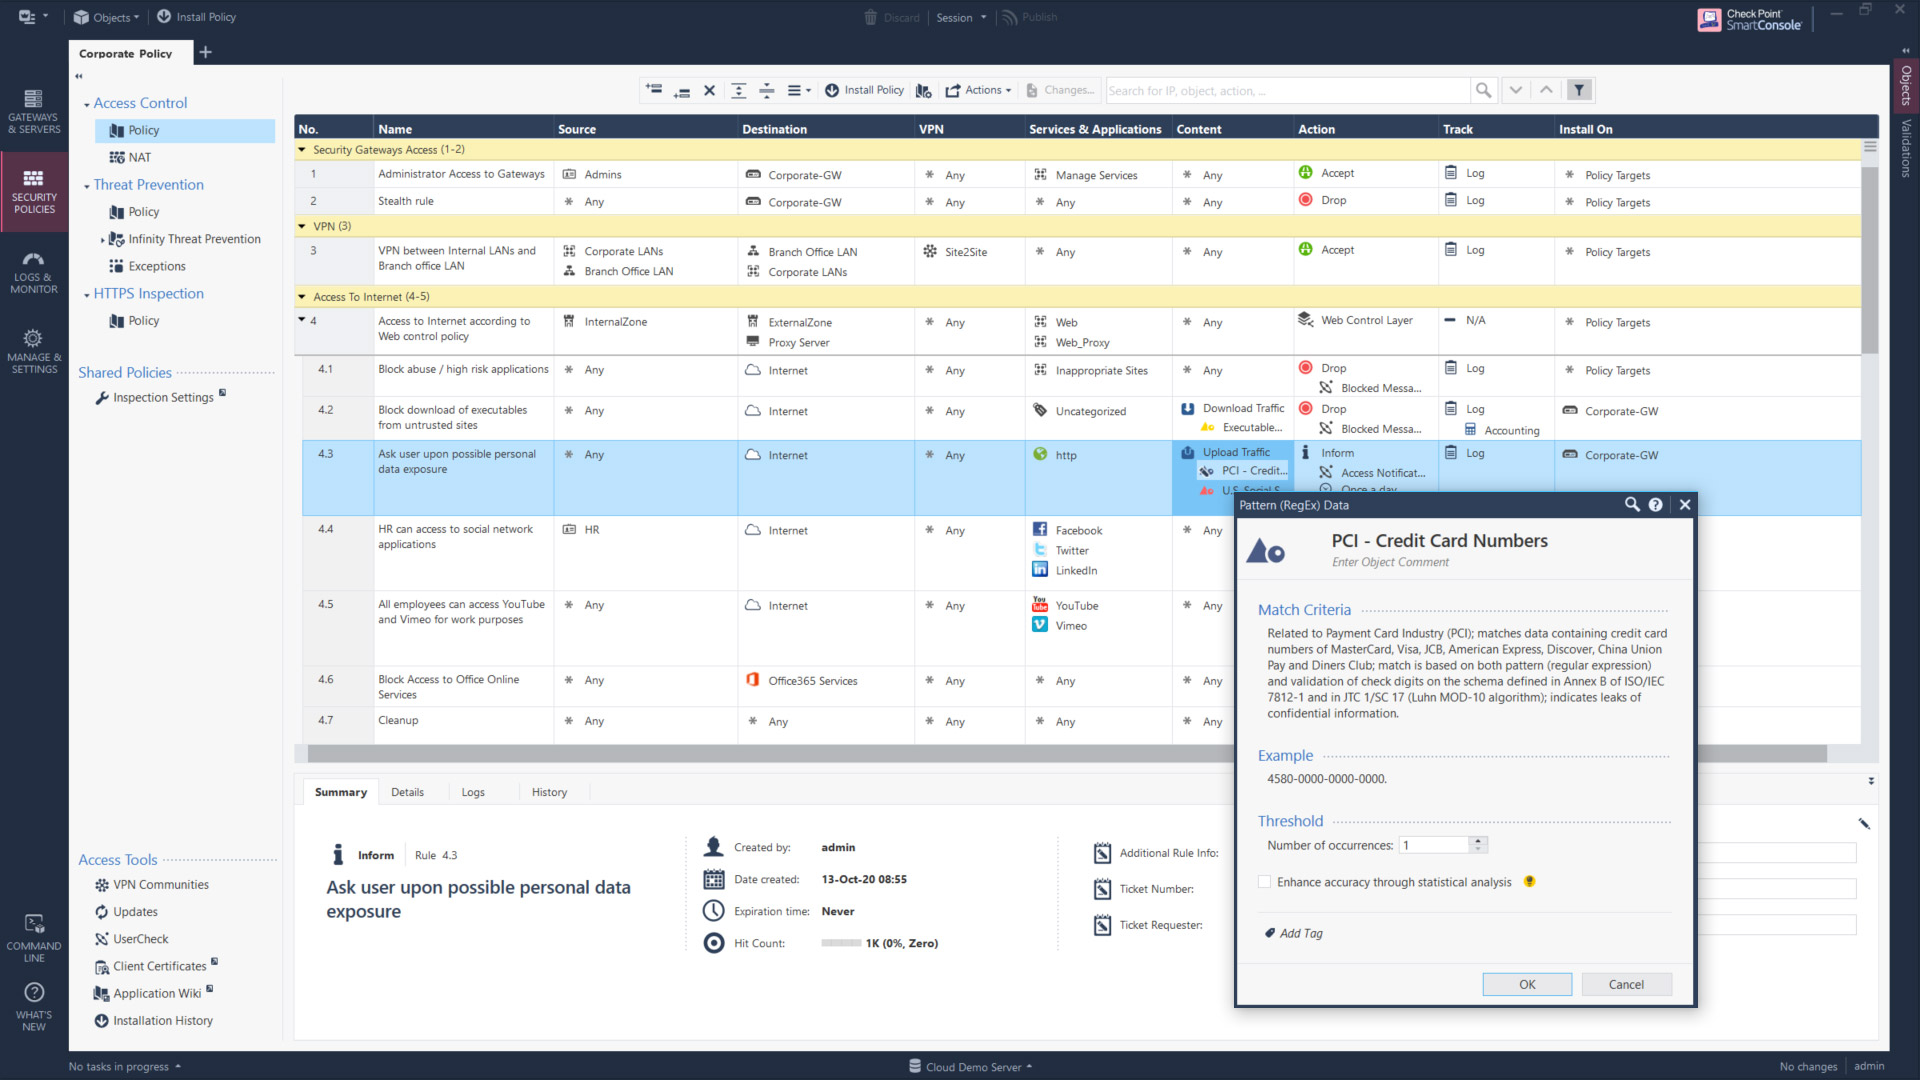
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Enterprise Data Loss Prevention Tool.
[*] Metasploit Scan Running on Target Subnet for Enterprise Data Loss Prevention Tool... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |