Complete Technical Paper Content — Federated Learning For Fraud Detection
Overview & System Context
Federated Learning For Fraud Detection: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~2588 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Fraud detection is a shared problem across banks payment processors and fintech partners yet high quality models often require cross institution signals that cannot be centralized due to privacy regulation contractual constraints and competitive boundaries. Federated learning enables collaborative model training without moving raw data by sending model updates rather than records. However practical deployment in financial networks requires more than basic model averaging. It requires robust privacy protection against inference, strong security controls against malicious participants, a design that addresses non independent data distributions and a governance model that aligns with risk and compliance. This paper proposes an architecture led framework for privacy preserving federated fraud detection across financial institutions. We describe system components for horizontal and vertical federation, secure aggregation to protect individual client updates and differential privacy to bound leakage. We present model design options including tabular models representation learning and federated graph learning for transaction relationship signals. We then define an operational lifecycle that covers onboarding, auditability, drift detection, incident response and model rollback. Finally we outline an evaluation plan that measures detection lift, fairness, privacy, resilience and cost. The goal is a blueprint that allows banks and fintech partners to share learning value while preserving customer privacy and supporting regulatory defensibility [1] P. Kairouz et al., "Advances and Open Problems in Federated Learning," Foundations and Trends in Machine Learning, [2] K. Bonawitz et al., "Practical Secure Aggregation for Privacy Preserving Machine Learning," in Proceedings of the ACM [3] Wang, L., Jia, R., & Song, D. (2020). D2PIFed: Differentially private federated learning with efficient communication.
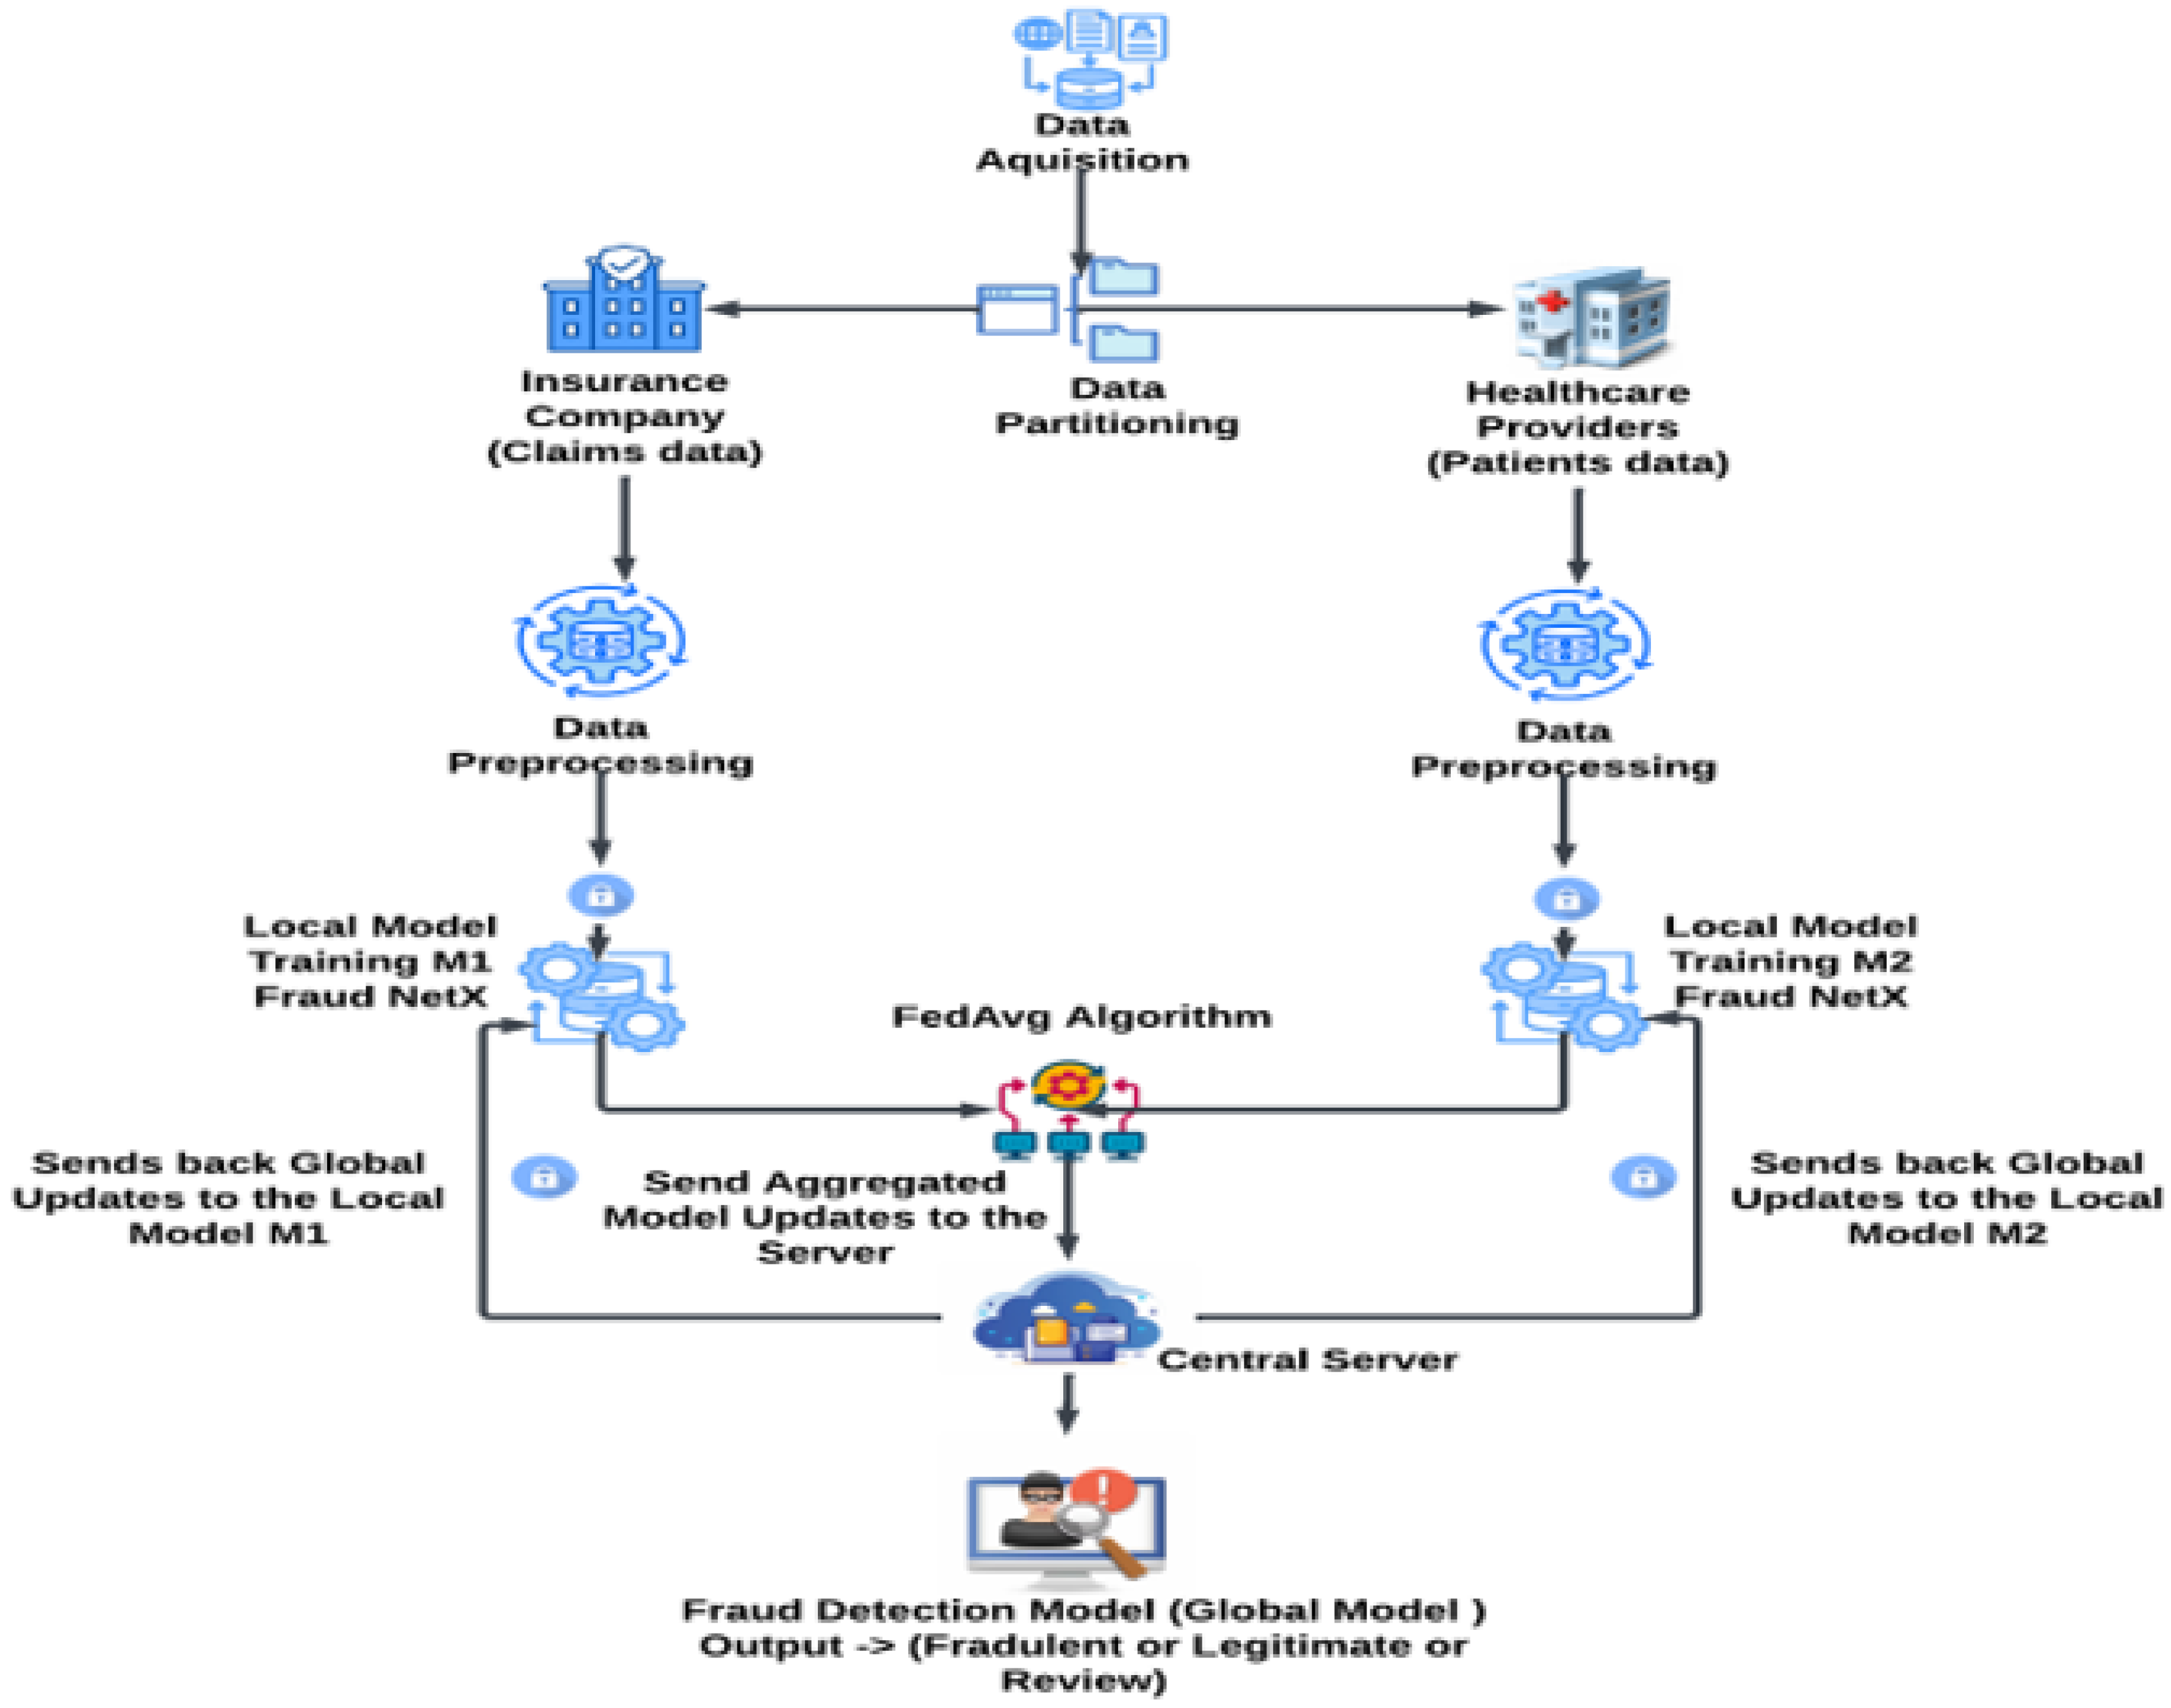
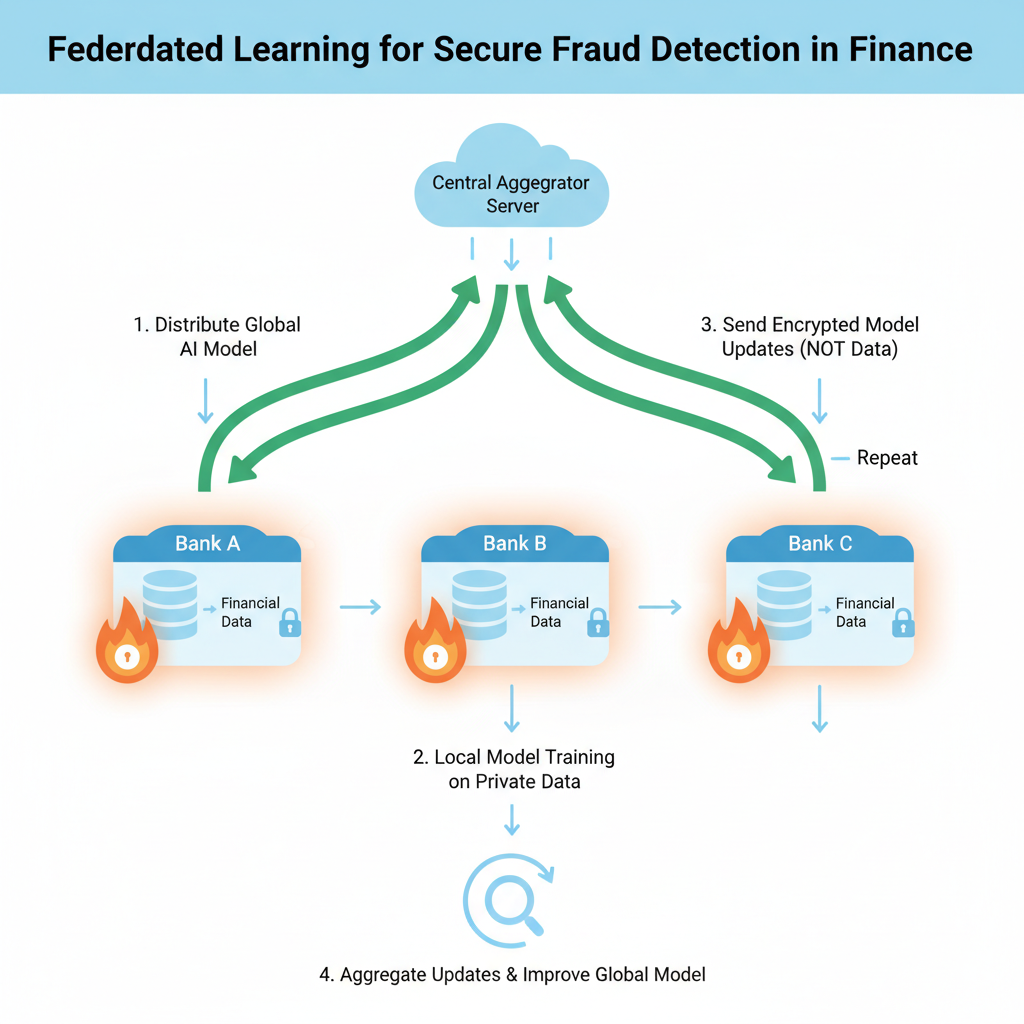
arXiv. https://doi.org/10.48550/arXiv.2006.13039 Figure 1: A Privacy-Preserving Approach to Health Insurance Fraud Detection Using ... of Emerging Research in Engineering and Technology, 4(2), 126-129. https://doi.org/10.63282/3050-922X.IJERET-V4I2P113 [5] W. Yang et al., "FFD: A Federated Learning Based Method for Credit Card Fraud Detection," in Advances in Knowledge [6] Zheng, W., Yan, L., Gou, C., & Wang, F.IY. (2020). Federated metaIlearning for fraudulent credit card detection. In Proceedings of the TwentyINinth International Joint Conference on Artificial Intelligence (IJCAI) (pp. 4654–4660).
https://doi.org/10.24963/ijcai.2020/642 [7] Pan, Z., Wang, G., Li, Z., Chen, L., Bian, Y., & Lai, Z. (2023). 2SFGL: A simple and robust protocol for federated graphIbased fraud detection. arXiv. https://doi.org/10.48550/arXiv.2310.08335 Figure 2: Conversational AI & Federated Learning in Finance: Secure Fraud Detection [8] N. F. Aurna et al., "Federated Learning Based Credit Card Fraud Detection: Performance Analysis with Sampling Methods 10.1109/CSR57506.2023.10224978.
[9] Gunda SK, Yettapu SDR, Bodakunti S, Bikki SB. Decision Intelligence Methodology for AI-Driven Agile Software Lifecycle Governance and
Architecture
Centered Project Management, 2023 Mar.
Architecture Tour Chicago
30;4(1):102-8. https://doi.org/10.63282/3050-9262.IJAIDSML-V4I1P112 [10] H. Brendan McMahan et al., "Learning Differentially Private Recurrent Language Models," in International Conference on [11] R. Shokri, M. Stronati, C. Song and V. Shmatikov, "Membership Inference Attacks Against Machine Learning Models," in Figure 3: AI-Powered Fraud Detection System for a FinTech Startup - Case Study [12] L. Song, R. Shokri and P. Mittal, "Privacy Risks of Securing Machine Learning Models Against Adversarial Examples," in [13] J. KoneIný, H. B. McMahan, D. Ramage and P. Richtárik, "Federated Optimization: Distributed Machine Learning for On [14] Alsaeedi, A., & Khan, M. (2019). Software defect prediction using supervised machine learning and ensemble techniques: A comparative study.
Architecture Boat Tour Chicago
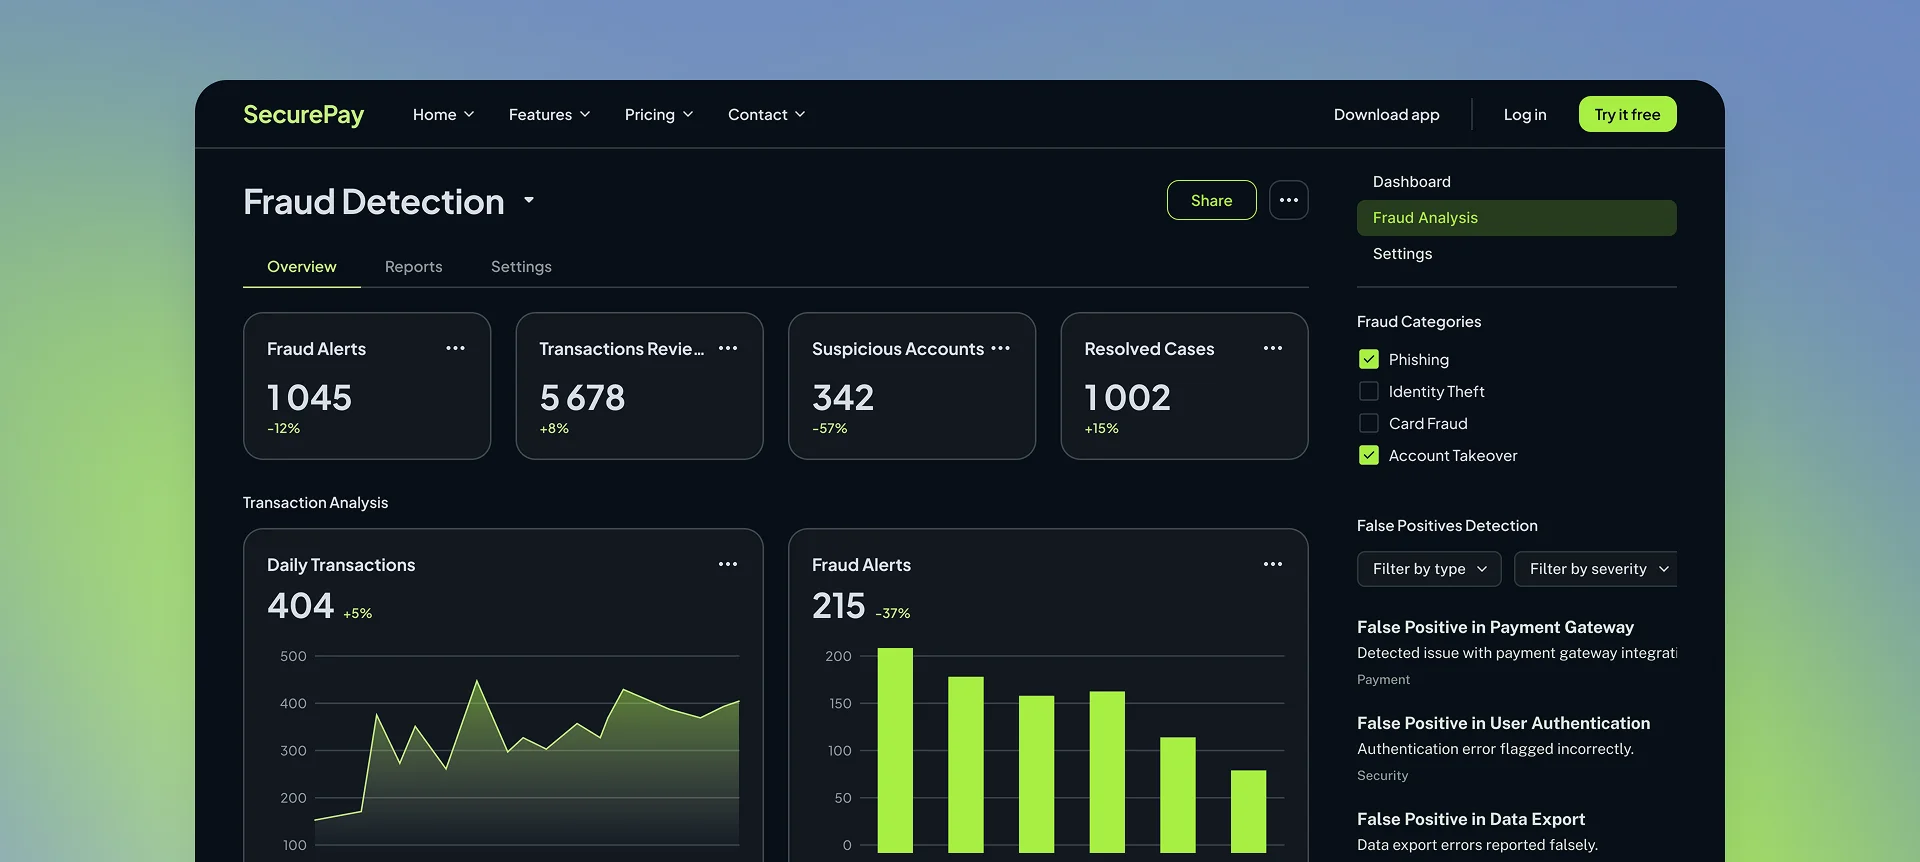
Journal of Software Engineering and Applications, 12, 85–100.
Architecture Salary
https://doi.org/10.4236/jsea.2019.125007 2. System Architecture & Core Working Principles [15] M. Jagielski et al., "Manipulating Machine Learning: Poisoning Attacks and Countermeasures for Regression Learning," in [16] P. Blanchard, E. M. El Mhamdi, R. Guerraoui and J. Stainer, "Machine Learning with Adversaries: Byzantine Tolerant [17] E. Bagdasaryan, A. Veit, Y. Hua, D. Estrin and V. Shmatikov, "How To Backdoor Federated Learning," in Proceedings of [18] Shah, H., & Sahatiya, P. (2022). A comparative analysis study of software defect prediction using machine learning algorithms on NASA datasets.
Architecture Degree
Journal of Harbin Institute of Technology, 54(9), 67–76.
Architecture Styles
Retrieved from http://hebgydxxb.periodicales.com/index.php/JHIT/article/view/1301 [19] S. Ramaswamy, R. Mathews, K. Rao, and F. Beaufays, "Federated Learning for Emoji Prediction in a Mobile Keyboard," [20] H. Li, K. Ota, and M. Dong, "Learning IoT in Edge: Deep Learning for the Internet of Things with Edge Computing," IEEE [21] AlINawaiseh, O., & Hammad, M. (2022). Software defect prediction using stacking generalization of optimized treeIbased ensembles. Applied Sciences, 12(9), 4577. https://doi.org/10.3390/app12094577 [22] Z. Ma, H. Hu, Y. Li, and J. Liu, "Privacy-Enhancing Technologies in Federated Learning: A Survey," Information Fusion, [23] L. Xu, W. Wang, and Z. Qin, "FedSafe: A Federated Learning Framework for Secure and Fair Model Training," IEEE [24] A. G. Howard et al., "MobileNets: Efficient Convolutional Neural Networks for Mobile Vision Applications," arXiv preprint, [25] S. Wang, T. Tuor, T. Salonidis, K. Leung, C. Makaya, T. He, and K. Chan, "Adaptive Federated Learning in Resource [26] M. Chen, Z. Yang, W. Saad, C. Yin, and M. Shikh-Bahaei, "A Joint Learning and Communications Framework for [27] Shah, H., & Sahatiya, P. (2022). A comparative analysis study of software defect prediction using machine learning algorithms on NASA dataset. Harbin Gongye Daxue Xuebao/Journal of Harbin Institute of Technology, 54(9), 67–76.
Architecture Schools
Retrieved from http://hebgydxxb.periodicales.com/index.php/JHIT/article/view/1301 A privacy-preserving fraud detection system using federated learning to analyze transaction patterns across distributed financial institutions without sharing raw data. 3. Software Implementation, Frameworks & Protocols This project introduces a novel approach to fraud detection in the financial sector using federated learning , allowing multiple banks or payment processors to collaboratively train AI models without exposing sensitive customer data. The system is built with real-time applicability and regulatory compliance in mind, providing a modern, secure framework for cross institutional fraud intelligence.
Architecture Boat Tour
This is one of the first open-source prototypes to simulate real-time fraud detection in a federated learning context for the financial industry. It avoids data centralization by keeping customer data on-device or on-prem , aligning with GDPR and financial compliance standards. The architecture and algorithms were fully designed and developed by Rahul Autade . This work addresses a critical challenge in global fintech operations: how to collaborate on fraud prevention without violating data privacy laws .
Architecture Design
fraud-detection-federated/ I III I src/ # Core source code I III client_simulator.py # Federated client logic (local training) I III model_builder.py # Fraud detection model definition I III model_inference.py # Fraud detection model interface I III main.py # Fraud Main funcation I III data_loader.py # Data loading and preprocessing I III utils.py # Utility functions (e.g., data split, logging) I III data_loader.py # Data loading and preprocessing I III preprocessing.py # Preprocessing I III test_main.py # Fraud test funcation I III trainer.py # Utility functions (e.g., data split, logging) I III I data/ # Data assets I III high_fraud_data.csv # High Hit Rated Fraud Data I III low_fraud_data.csv # Low Hit Rated Fraud Data I III merchant_pattern_data.csv # Merchant Pattern Fraud Data I III synthetic_data.csv # Synthetic Fraud Data I III I notebooks/ # Jupyter notebooks for demo or experiments I III explore_fraud_data.ipynb I III federated_training_demo.ipynb I III fraud_detection_demo.ipynb I III model_inference_demo.ipynb I III I docs/ # repository documentation I III fraud_detection_presentation.pptx # Fraud Detection Presentation I III fraud_flowchart.png # Fraud flow flowchart I III fraud_model_metrics.png # Fraud Model Metrics I III high_fraud_data_preview.png # High rated Fraud data preview I III industry_standards.md # Inductry Standard Fraud detection I III low_fraud_data_preview.png # Low rated Fraud data preview I III merchant_pattern_data_preview.png # Mechant Patteren Fraud Data preview I III project_roadmap.md # Project Roadmap I III project_slide_deck.md # Project Structure I III synthetic_data_preview.png # Synthetic Data Fraud Data preview I III system_architecture.png # Fraud Detection System Architecture I III requirements.txt # Python package dependencies III README.md # Project description, usage, and documentation III LICENSE # License file (e.g., MIT, Apache 2.0) III .gitignore # Files/folders to ignore in Git tracking A privacy-preserving fraud detection system using federated learning to analyze transaction patterns across distributed financial institutions without sharing raw data.
Architecture Jobs
Putting our long-tenured investment teams on the line to earn the trust of institutional investors. Direct access to market leading liquidity harnessed through world-class research, tools, data, and analytics. Helping institutional investors, traditional and alternative asset and fund managers, broker dealers and equity issuers meet the demands of a rapidly evolving market.
Leveraging cutting-edge technology and innovative tools to bring clients industry-leading analysis and investment advice. Helping hedge funds, asset managers and institutional investors meet the demands of a rapidly evolving market. Global short-term fixed income strategies designed to help clients manage liquidity through the cycle. With J.P. Morgan Wealth Management, you can invest on your own or work with an advisor to design a personalized investment strategy. We have opportunities for every investor.
Invest with J.P. Morgan Personal Investing, a platform for UK-based clients with the human expertise, intuitive app and tools to help you work towards your long-term goals. Enhance your equity compensation offering with solutions designed to empower your employees and bring your reward strategy to life.
4. Practical Deployment, Analysis & Case Studies We aim to be the most respected financial services firm in the world, serving corporations and individuals in more than 100 countries. A proof-of-concept completed by Kinexys by J.P. Morgan , the firm’s industry-leading blockchain business unit, BNY, RBC, DeepTempo and NVIDIA has demonstrated how federated learning enables institutions to collaboratively train AI fraud detection models without sharing sensitive transaction data. The raw data is kept within an institution’s own environment which helps to support privacy and regulatory compliance.
Instead of pooling transaction data into a centralized database, each institution trained a locally hosted AI model on its own data. The models then shared encrypted insights and updates, enabling the federated learning system to learn patterns across institutions without exposing sensitive information. NVIDIA FLARE (NVIDIA Federated Learning Application Runtime Environment), a domain-agnostic, open-source software development kit, powered the tests on a multi-site federated environment provided by NVIDIA DGX Cloud .
As AI adoption expands across financial services – from predictive analytics to large language models – data diversity increasingly drives model performance. However, privacy, security and regulatory considerations limit direct data sharing between institutions. Federated learning addresses this barrier by enabling organizations to collaboratively train models while keeping raw data within their own secure environments, allowing insights to be shared while maintaining required guardrails.
The proof-of-concept showed clear improvements in fraud detection, outperforming models trained on data from a single institution and nearly matching the performance of centralized models trained on pooled data. Performance gains also appeared quickly, with models stabilizing within a few federated learning training rounds which outperformed models trained only on a single institution’s data.
For institutions, this indicates federated learning can help detect more fraudulent transactions while reducing missed cases, without requiring cross-institution data sharing. The proof-of-concept also demonstrated the ability to detect fraud patterns that may be difficult for a single institution to identify alone. Certain fraud scenarios referred to as “Type 1” patterns, such as location-based fraud, may appear rarely within a single dataset but become more visible when signals are combined across institutions. In the proof-of-concept, these patterns were better detected by the models after federated training, demonstrating that cross-institution learning could help banks identify emerging fraud types earlier and limit their spread.
For this proof-of-concept, NVIDIA FLARE ran in a secure sandbox on NVIDIA DGX Cloud, which provides an isolated environment for each participant bank so that data can’t be seen or accessed by other participants. The project used privacy-enhancing technologies (PETs), including differential privacy, and GPU-accelerated training, enabling banks to efficiently collaborate while meeting strict security and compliance requirements.
This collaboration highlights how privacy-preserving AI frameworks can help financial institutions work together against shared threats such as fraud. As fraud networks become more sophisticated and cross borders, approaches like federated learning may help create a unified, privacy-first protection layer for the financial ecosystem.
An earlier whitepaper involving a subset of the participating institutions, including Kinexys by J.P. Morgan, a part of J.P. Morgan Payments , along with supporting coding information , has been published here . J.P. Morgan’s website and/or mobile terms, privacy and security policies don’t apply to the site or app you're about to visit. Please review its terms, privacy and security policies to see how they apply to you. J.P. Morgan isn’t responsible for (and doesn’t provide) any products, services or content at this third-party site or app, except for products and services that explicitly carry the J.P. Morgan name.
A PyTorch-based federated learning prototype for cross-bank fraud detection, comparing FedAvg vs FedProx , with a roadmap to privacy-preserving training via differential privacy . This repository demonstrates a federated learning (FL) workflow for fraud detection across multiple peer “banks” (clients). Instead of pooling sensitive transaction data into a central dataset, each bank trains a model locally and only shares model updates with a central server, which aggregates them to form a global model.
5. Performance Evaluation & Extended Technical Observations Centralized training is often infeasible in regulated domains like banking due to privacy, security, and compliance constraints. Federated learning enables: Train a fraud detection model collaboratively across multiple banks and evaluate how FL strategies behave when client data distributions differ.
Evaluation is performed per client , and results are summarized to compare FedAvg and FedProx. This highlights performance variation across heterogeneous clients and how optimization affects convergence and stability. Federated learning reduces raw data sharing, but does not automatically guarantee privacy —model updates can still leak information under certain threat models. The next phase of this project will introduce explicit privacy guarantees and quantify the privacy–utility trade-off.
A PyTorch-based federated learning prototype for cross-bank fraud detection, comparing FedAvg vs FedProx and outlining a roadmap to privacy-preserving training with differential privacy. A privacy-preserving approach to fraud detection using federated learning on messaging platform data Simulating distributed machine learning for fraud detection without centralizing sensitive user data Note: This project is under active development with planned improvements to model architecture, visualization, and potential LLM integration.
This project demonstrates how federated learning can be applied to fraud detection in messaging platforms while preserving user privacy. Instead of collecting all user data in one central location, the system trains machine learning models locally on each client's device and only shares model updates with a central server. The simulation creates realistic scenarios with different types of users (normal users, bots, business accounts, influencers, and dormant accounts) and shows how a global fraud detection model can be trained collaboratively across multiple clients using the FedAvg (Federated Averaging) algorithm.
This project is designed to run entirely in Google Colab - no local installation required. Figure: Model performance metrics across 10 federated learning rounds showing consistent improvement in fraud detection accuracy. This project demonstrates practical implementation of federated learning for fraud detection, showcasing expertise in privacy-preserving ML, distributed systems, and synthetic data generation.
A privacy-preserving federated learning system that enables multiple financial institutions to collaboratively train fraud detection models without sharing raw transaction data. Built with PyTorch, Flower framework, and comprehensive MLOps monitoring. Harvested Online Documentation & Reference Sources • https://ijeret.org/index.php/ijeret/article/view/394 • https://github.com/rahul2287/fraud-detection-federated • https://www.jpmorgan.com/payments/newsroom/project-aikya-federated-learning-fraud-detection • https://github.com/charchitd/Federated-Learning-for-fraud-detection • https://github.com/agr1maa/Fraud-Detection-using-Federated-Learning • https://github.com/durvibangera/federated-learning-fraud-detection
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Federated Learning For Fraud Detection.
[*] Metasploit Scan Running on Target Subnet for Federated Learning For Fraud Detection... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |