Complete Technical Paper Content — File Integrity Checker With Email Alert Using Python
Overview & System Context
File Integrity Checker With Email Alert Using Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9541 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A cybersecurity tool that detects unauthorized file tampering using SHA-256 cryptographic hashing — the same concept used by enterprise Intrusion Detection Systems like Tripwire and AIDE .
Built a File Integrity Checker using SHA-256 cryptographic hashing to detect unauthorized file tampering — implementing the same baseline comparison model used by enterprise IDS tools like Tripwire, with a dark-themed GUI, automated scheduling, Gmail alerts, and persistent logging. II SHA-256 based file tamper detection tool with GUI, email alerts & auto-scheduler | Cybersecurity Portfolio Project File integrity monitoring serves as a critical layer of defense, ensuring the integrity and security of files and folders within systems and networks. File integrity monitoring tools provide early alerts on potential security breaches, malware infections, and insider threats by monitoring changes to critical files and detecting unauthorized modifications. For a file integrity monitoring tool to be effective, an organization should plan its architecture and implementation correctly.
Figure 1: File integrity monitoring (FIM) software | Log360 The architecture usually entails placing monitoring agents on separate servers or systems, with important data being aggregated and managed by a centralized management server. Configuring the tool to monitor particular files or folders, creating thresholds, continuously monitoring for changes, identifying unauthorized alterations, and putting in place suitable response mechanisms like alerts and workflows are all part of the implementation process for a file integrity monitoring tool.
Organizations are protected from potential breaches and data tampering by the proactive security measures that a file integrity monitoring tool's architecture and implementation together offer. These measures identify and mitigate unwanted changes to files. In order to use a file integrity monitoring tool more effectively in today's cybersecurity landscape, it is imperative to understand its architecture and implementation.
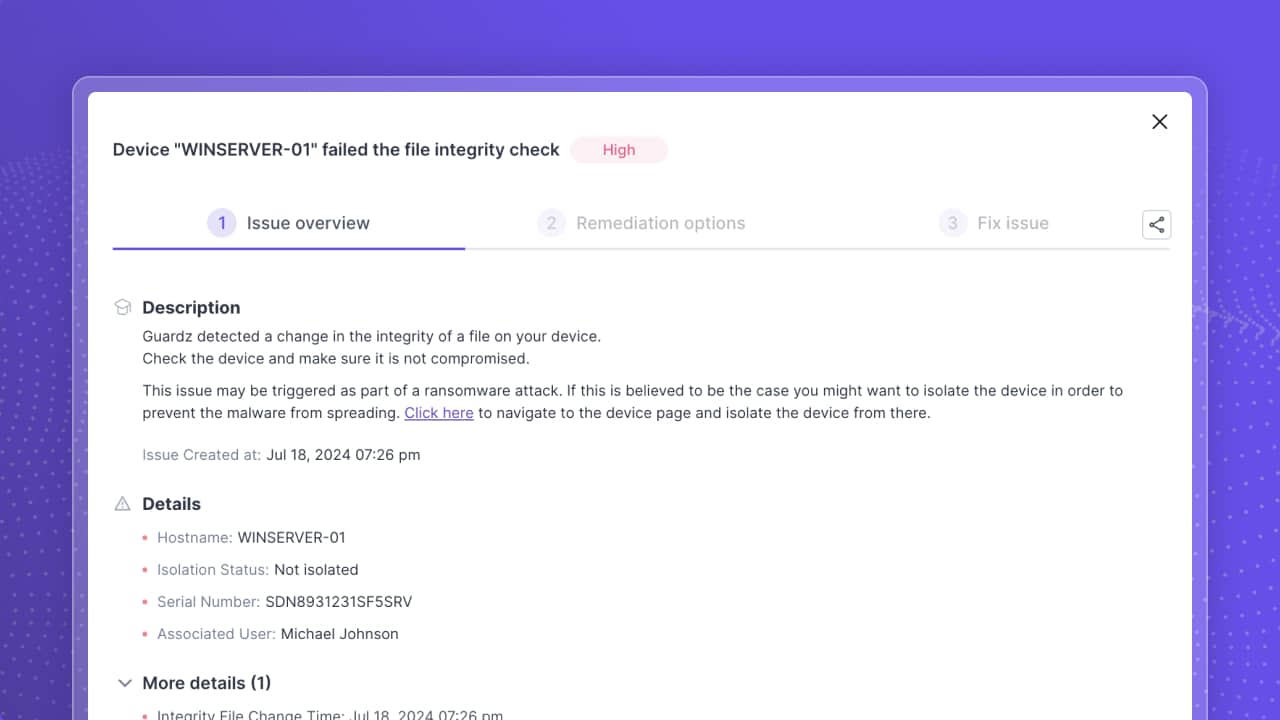
Figure 1 shows a general overview of the architecture of file integrity monitoring systems. The following is a list of the file integrity monitoring system components that are necessary to create the whole architecture: Figure 2: Guardz Enhances MSP Security with AI-Powered Email Protection ... The overall goal of file integrity monitoring systems is to give enterprises visibility into the changes made to important files and directories, enabling them to quickly identify and address security events.
A typical workflow for implementing a file integrity monitoring tool is shown in Figure 2: Find a file integrity monitoring tool that meets your needs by doing some research. Every choice, both open-source and commercial, has different features. Refer to the "10 things to take into account when choosing a FIM tool" section of this page to gain insights into how to choose a suitable file integrity monitoring solution for your organization.
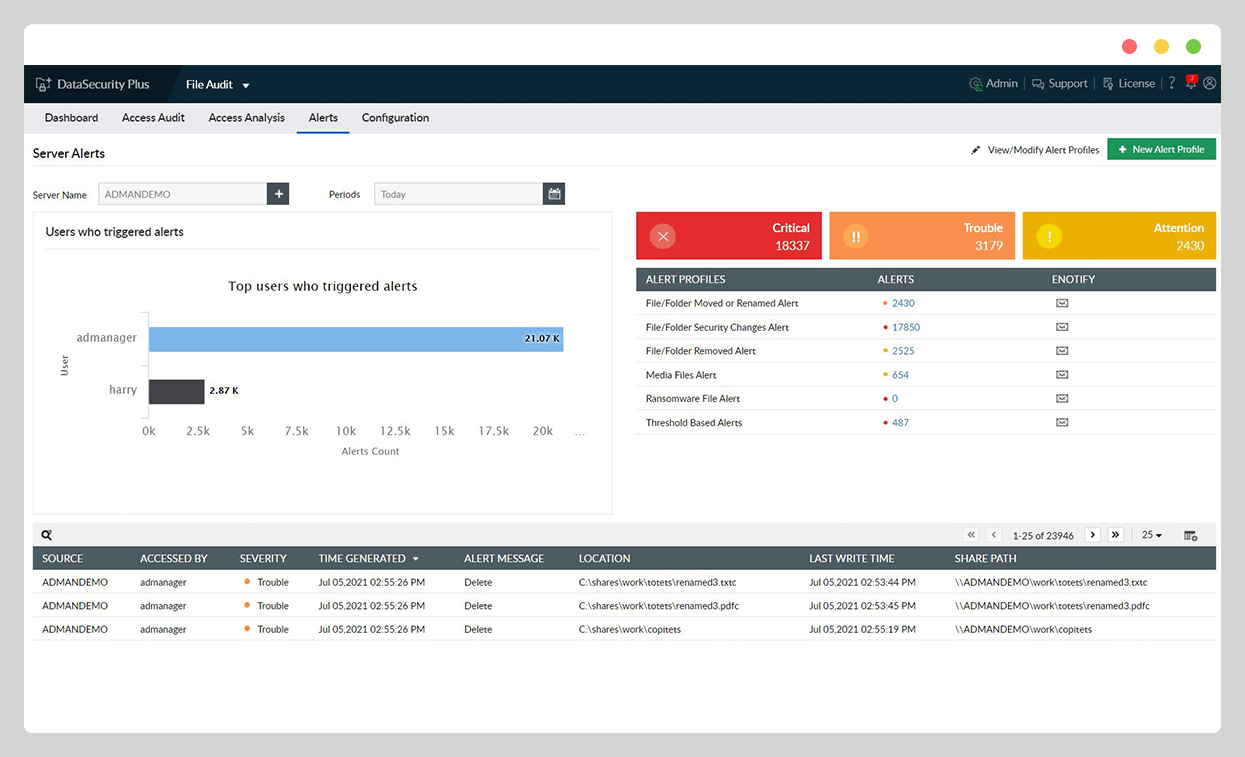
Install agents in the systems that the file integrity monitoring solution needs to monitor. The central server or console gathers the data collected by the agents. This data is collected by the database that is maintained within the file integrity monitoring solution. Figure 3: File integrity checker | ManageEngine DataSecurity Plus Next, ensure that the tool has appropriate permissions to access the files and directories being monitored. For quicker monitoring and response procedures, integrate the file integrity monitoring tool into your current infrastructure, such as centralized logging and alerting systems.
File integrity monitoring configuration with ManageEngine Log360 is very user-friendly. It is effortless to configure multiple devices at once, and these devices immediately install the necessary file integrity monitoring agents. Agent updates, SACL settings, and all the relevant audit policies are updated automatically. Choose the files and folders that need to be monitored. These could include any files necessary for the proper operation of your system, such as executables, libraries, configuration files, and vital system files.
With Log360, you can configure individual devices and also create templates to indicate the locations of files and folders that need to be monitored for multiple devices (Fig. 3). These features help reduce redundancy and increase efficiency. You can also choose to include or exclude subfolders, specific files, or file types. Make sure you understand the objectives of your file integrity monitoring, such as detecting unauthorized changes, ensuring compliance with regulations, or identifying potential security breaches.
Ascertain users' regular usage patterns and behaviors to set alert criteria. Then, using this alert criteria as a guide, the file integrity monitoring tool analyzes events in real time. When an event crosses the predetermined alert threshold, a notification is generated and forwarded to the appropriate authority, who then analyzes the issue and takes appropriate actions to rectify it. These alerts include details such as the type of change, the affected files or directories, and the time of the event.
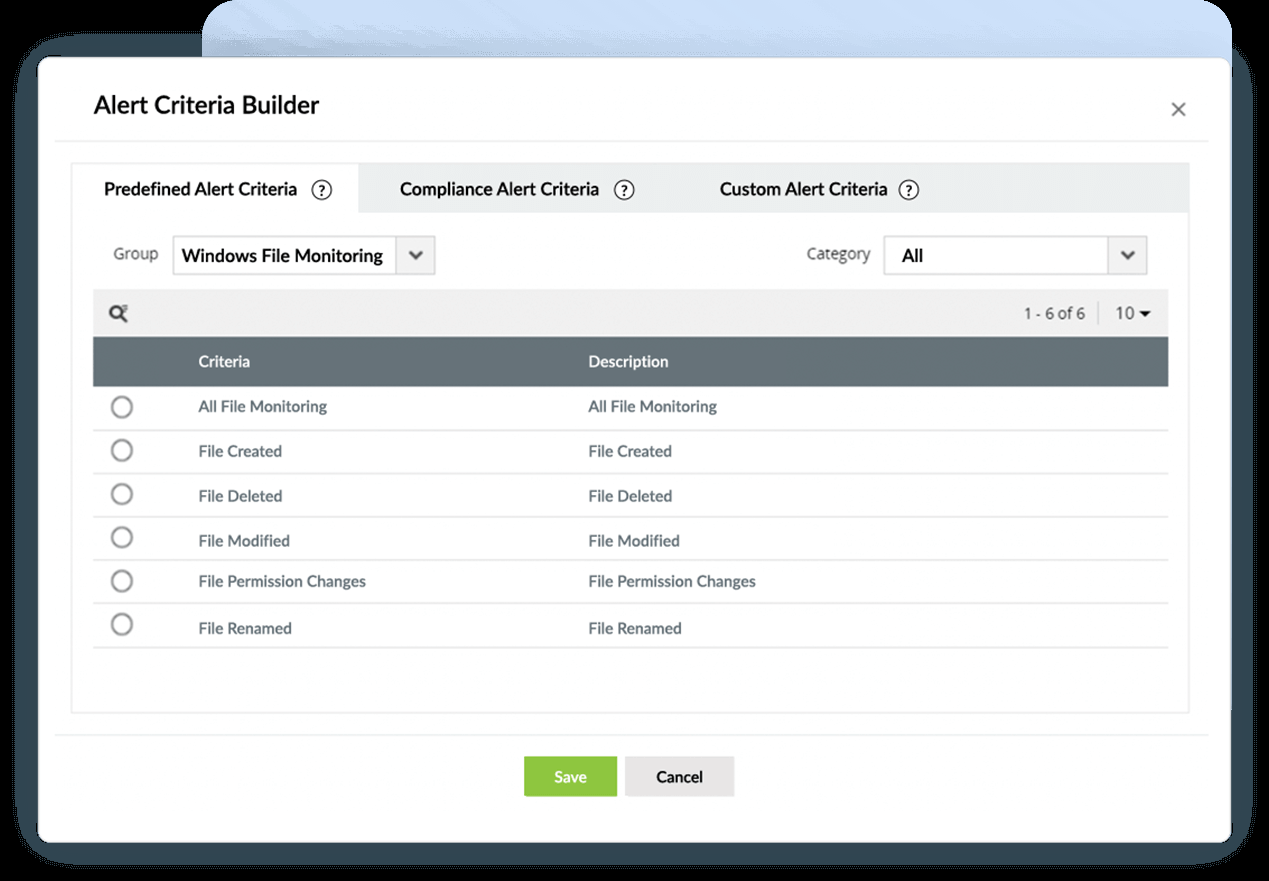
Log360 provides real-time event alerts for important updates, including changes made to files and folders. You can set up alerts by configuring the alert criteria according to your needs (Fig. 4). Alert criteria can also be created based on custom thresholds and user actions. Regularly generate reports summarizing file integrity monitoring activities, including the detected changes, alerts, and compliance statuses. Use these reports to demonstrate compliance with regulations and evaluate your overall security posture.
As shown in Figure 5, Log360 generates thorough reports (file monitoring reports, correlation reports, compliance reports, and more) with accurate integrity information (file creations, deletions, modifications, permission changes, and more). These reports can be exported in multiple formats, including CSV and PDF. You can automatically receive the reports at regular intervals with the help of flexible report scheduling.
Upon receiving alerts, make sure to promptly investigate the detected changes to determine their nature and impact. This may involve reviewing logs, analyzing file contents, and assessing the severity of incidents. To reduce any security risks or restore the integrity of impacted files, take the necessary remedial actions. This can entail undoing unauthorized changes, applying patches, or implementing additional security controls.
Log360 enables you to create and execute incident workflows and automate common incident response steps (Fig. 6). When alerts are triggered, these workflows get executed automatically to remediate the incidents. Review and update your file integrity monitoring tool's rules and configurations on a regular basis to keep up with evolving threats and changes in your environment.
Log360 allows you to view dashboards and reports on all file and folder creations, deletions, changes, owner alterations, and permission modifications (Fig. 7). All failed attempts to access files are also recorded. For your security team, these capabilities offer several advantages, including early detection of possible dangers like ransomware, malware, and IT sabotage. This helps your organization reduce its mean time to detect incidents.
Review the actions performed on files and folders to determine whether any new threats are emerging. Ensure that the file integrity monitoring tool's alert rules and configurations are updated appropriately in order prevent such threats from occurring again. Conduct regular audits and assessments to make sure your file integrity monitoring tool's implementation is efficient and compliant with security best practices.
By adhering to this procedure, you can set up a strong file integrity monitoring system that can help you identify unauthorized modifications while protecting the security and integrity of your systems and data. Are you looking for ways to protect your organization's sensitive information from being misused? Sign up for a personalized demo of Log360, a comprehensive SIEM solution that can help you detect, prioritize, investigate, and respond to security threats.
You can also explore on your own with a free, fully functional, 30-day trial of Log360 . ManageEngine named in 2022 Gartner MQ for SIEM Gartner Peer Insights Customers' choice for SIEM FIM is a high-performance File Integrity Monitoring tool written in Rust. It runs silently in the background, watching your files and alerting you the instant anything changes — creating a complete, searchable history of every modification.
Think of it as a 24/7 security camera for your filesystem . If someone modifies a config file, drops a malicious script, or accidentally deletes something important, FIM catches it all. FIM is an Open Source Host-based file integrity monitoring tool that performs file system analysis, file integrity checking, real time alerting and provides Audit daemon data.
File Integrity Monitoring (FIM) helps in auditing sensitive files and meeting regulatory compliance requirements. Wazuh has an inbuilt FIM module that monitors file system changes to detect the creation, modification, and deletion of files. This use case uses the Wazuh FIM module to detect changes in monitored directories on Ubuntu and Windows endpoints. The Wazuh FIM module enriches alert data by fetching information about the user and process that made the changes using who-data audit .
The Wazuh FIM module monitors a directory on this endpoint to detect file creation, changes, and deletion. The Wazuh FIM module monitors a directory on this endpoint to detect file creation, changes, and deletion. Perform the following steps to configure the Wazuh agent to monitor filesystem changes in the /root directory. Edit the Wazuh agent /var/ossec/etc/ossec.conf configuration file. Add the directories for monitoring within the
Edit the C:\Program Files (x86)\ossec-agent\ossec.conf configuration file on the monitored Windows endpoint. Add the directories for monitoring within the
You can visualize the alert data in the Wazuh dashboard. To do this, go to the File Integrity Monitoring module and add the filters in the search bar to query the alerts: Access to this page requires authorization. You can try signing in or changing directories . The file integrity monitoring feature in Microsoft Defender for Cloud's Defender for Servers Plan 2 , scans operating system files, Windows registries, application software, and Linux system files. It analyzes these files for changes that might indicate an attack.
File integrity monitoring examines operating system files, Windows registries, application software, and Linux system files to detect suspicious activity such as: File integrity monitoring uses the Microsoft Defender for Endpoint agent and agentless scanning to collect data from machines.
To ensure proper file integrity monitoring functionality, machines must run the Defender for Servers Windows client (Microsoft Defender for Endpoint agent) version 10.8799 or above . This requirement is especially important for: Due to a pipeline change in Microsoft Defender for Endpoint, users with existing FIM deployments on legacy Windows machines must update their MDE agent to version 10.8799 or above to continue receiving file integrity monitoring data.
If you're currently using file integrity monitoring with legacy agent-based methods (Log Analytics agent/Microsoft Monitoring Agent (MMA) or Azure Monitor Agent (AMA)), you need to migrate to the MDE-based (Microsoft Defender for Endpoint) approach. This migration ensures continued functionality and access to enhanced capabilities. Learn how to migrate file integrity monitoring from legacy AMA/MMA clients to the MDE-based solution.
After enabling Defender for Servers Plan 2, you enable and configure file integrity monitoring. It isn't enabled by default. Defender for Cloud recommends entities to monitor with file integrity monitoring. You can choose items from the recommendations. When choosing which files to monitor: When using file integrity monitoring with the Defender for Endpoint agent, we recommend monitoring these items with based on known attack patterns.
You can create custom rules to monitor specific files or folders as long as they meet the following validation criteria: A maximum of three asterisks * are allowed in the path (maximum depth). Wildcards ( * ) are allowed only at the start or end of a path segment. Windows registry paths must start with HKLM or hklm and may only contain letters, numbers, spaces, _ , . , \ , : . Wildcards ( * ) are allowed only at the start or end of a path segment.
Windows file paths may only contain letters, numbers, spaces, _ , . , \ , * , ? , : and must not contain / . Wildcards ( * ) are allowed only at the start or end of a path segment. Linux file paths must be absolute (start with / ) and may only contain letters, numbers, spaces, _ , . , / , * , : . Wildcards ( * ) are allowed only at the start or end of a path segment.
All paths must meet the systemâIIs maximum path length (260 characters) and maximum depth (three asterisks) rules. A rule name must contain only letters (aâIIz, AâIIZ), digits (0âII9), and underscores (_), and can be up to 128 characters. At least one change type (from change management and documentation rRequest (CMDR)) must be selected.
Qualys File Integrity Monitoring (FIM) is a cloud-based security solution that detects and reports changes in files, directories, and registry settings across IT environments. It helps organizations ensure security, maintain compliance, and streamline auditing by identifying unauthorized or suspicious modifications that could indicate security breaches. FIM detects unauthorized or suspicious changes to critical system files, helping to reduce the time to respond to potential breaches.
Example : If a critical configuration file on a server is modified unexpectedly, FIM sends an alert with details on who made the change, when, and how. 2. System Architecture & Core Working Principles FIM is a cloud-based solution, offering centralized visibility and management of file change events.
Example : A company with a mix of AWS, Azure, and on-premise servers can monitor file changes across all locations using a FIM dashboard. FIM automatically alerts you when it detects unauthorized or suspicious changes. You can also generates reports to capture events and incidents occurring in your files.
Example : A financial services firm receives an immediate alert when an unauthorized registry key is modified, triggering an investigation that reveals a compromised account, preventing further damage. FIM can identify and alert if someone is impersonating a privileged user to gain unauthorized access. Example : A healthcare organization discovered via FIM that an IT admin account was impersonated to access sensitive patient files, prompting a revamp of its identity and access controls.
FIM can capture file access attempts, providing detailed information about who, what, when, and where access attempts occur. Example : An employee attempts to access a confidential file. FIM logs who accessed it, when, and what actions they tried. FIM helps organizations meet compliance requirements like PCI DSS, HIPAA, GDPR, and others.
Example : A healthcare provider uses FIM reports during a HIPAA audit to demonstrate continuous monitoring of electronic health records. FIM can monitor network devices (such as routers and firewalls) for configuration changes, even without requiring agents to be on the devices.
For more infromation on supported technologies on Agentless FIM, see Platform Availability Matrix for Agentless FIM . Example : An employee accidentally changes a firewall setting, exposing internal systems. FIM detects and alerts the change without the agent. This PowerShell script serves as a file integrity monitor that continuously checks for changes in files within a specified folder and sends email alerts if any unauthorized modifications or file additions occur. It provides an extra layer of security by maintaining a baseline of file hashes and notifying you by email when discrepancies are detected.
Usage: Configure the script by setting the following variables at the beginning of the script: $EmailFrom: Your email address for sending alerts. $EmailTo: The recipient's email address for receiving alerts. $Subject: The subject line of the email alerts. $AppPassword: Your email account's application-specific password. Run the script and choose one of the following options: A) Collect new Baseline: Creates a new baseline of file hashes in the specified folder. Use this option when first setting up the monitor. B) Begin monitoring files with saved Baseline: Initiates real-time monitoring using the previously collected baseline. This option continuously checks for file changes and sends email alerts if any unauthorized modifications or file additions occur.
Complete guide to setting up Tripwire file integrity monitoring on Ubuntu for security compliance. File integrity monitoring (FIM) is a critical security practice that helps detect unauthorized changes to system files, configuration files, and other important data. Tripwire is one of the most established and trusted open-source tools for implementing FIM on Linux systems. This comprehensive guide walks you through setting up Tripwire on Ubuntu to protect your server from unauthorized modifications.
File Integrity Monitoring (FIM) is a security technique that validates the integrity of operating system and application files by comparing their current state against a known, trusted baseline. When changes are detected, FIM systems generate alerts, allowing security teams to investigate potential security incidents. Before installing Tripwire, update your system packages to ensure you have the latest security patches.
During installation, you will be prompted to configure Tripwire. Answer the prompts as follows: Important : Store these passphrases securely. You will need them for any policy or database updates. Tripwire's main configuration file is /etc/tripwire/twcfg.txt . Let's examine and customize it. After modifying the configuration, you need to regenerate the encrypted configuration file: The policy file defines which files and directories Tripwire monitors and what changes to report. The default policy at /etc/tripwire/twpol.txt is comprehensive but often needs customization for your specific environment.
The database stores the baseline state of all monitored files. Initialize it after configuring the policy: This process may take several minutes depending on the number of files being monitored. You will see output indicating which files are being processed. After legitimate system changes (updates, configuration modifications), update the database to accept the new state: Tripwire provides robust file integrity monitoring that is essential for maintaining security and compliance on Ubuntu systems.
By following this guide, you have learned how to: File integrity monitoring is a fundamental security control that helps detect breaches, ensure compliance, and maintain system integrity. Regular monitoring and prompt investigation of alerts are key to maximizing the security benefits of Tripwire. While Tripwire provides excellent file integrity monitoring at the system level, comprehensive infrastructure monitoring requires visibility across your entire stack. OneUptime complements your Tripwire deployment by providing: Integrate your Tripwire alerts with OneUptime to create a comprehensive security monitoring solution that provides complete visibility into your infrastructure's health and security posture. Visit oneuptime.com to start your free trial today.
Every OneUptime blog post is open source. Found a typo, an inaccuracy, or have a clearer way to explain something? Anyone can contribute — your edits make this post better for everyone who reads it next. Your complete reliability stack unified: infrastructure monitoring, incident management, status pages, and APM. Open-source and self-hostable.
Before jumping into the configuration, it is essential to understand what makes FIM a foundational pillar of modern cybersecurity infrastructure. In a standard enterprise network, thousands of files are accessed and modified daily. However, critical system files, application configurations, and sensitive data directories should rarely change. When an attacker successfully breaches a system, one of their primary objectives is to establish persistence, escalate privileges, or modify logs to hide their tracks. They often achieve this by altering binaries or injecting malicious code into trusted files.
In this step-by-step tutorial, we are setting up a practical lab to demonstrate Wazuh's FIM capabilities. We will cover: Open your preferred web browser and navigate to your Wazuh server's IP address (e.g., https://
Open Windows PowerShell as an Administrator on your target endpoint. Run the following command to open the main configuration file ( ossec.conf ) in Notepad for editing: After saving your directory modifications inside the configuration file, apply the changes by restarting the Wazuh agent service. Run the following command in your administrative PowerShell window: Return to your Wazuh Dashboard main overview screen. Under the Endpoint Security section on the bottom left, locate and click on the File Integrity Monitoring card to view the dedicated FIM alerts, tracking metrics, and integrity event summaries.
Inside the ossec.conf file, find the
Navigate to the Events tab within the FIM module to see incoming alerts. As shown in Screenshot (523).png , the dashboard successfully captures the file creation event with Rule ID 554 ("File added to the system") pointing directly to the path c:\wazuhtest\new text document.txt . If a monitored file is altered, Wazuh generates a higher severity alert. As observed in Screenshot (524).png , modifying the text inside test.txt triggers Rule ID 550 ("Integrity checksum changed"), providing a clear timeline of file tampering events under the syscheck.path details.
Implementing File Integrity Monitoring (FIM) is one of the most effective ways to secure your endpoints against unauthorized changes, malware deployment, and unexpected configuration drift. By leveraging Wazuh’s native syscheck engine, we successfully built a real-time file auditing system with minimal configuration. I Looking for the complete setup? Check out the Wazuh Installation and Agent Deployment Guide If you need enterprise-grade, centralized change detection across physical, virtual, and cloud servers that your security team already manages, choose Trend Micro Deep Security File Integrity Monitoring , whereas Lansweeper File Integrity Monitoring fits teams that want file-change signals tied to their existing asset records.
Three quick recommendations before you dive into the full comparison below — each one leads on a different dimension. A single Deep Security policy can combine path rules with Windows registry-key monitoring for mixed workload estates. Built for fits when security teams already manage Windows and Linux servers through Deep Security and need centralized change detection..
Datadog Agent file events retain host and process context inside the same investigation and automation environment as security telemetry. Built for fits when security teams already use Datadog and need host changes connected to broader investigations.. Asset-linked file change records connect modified paths with Lansweeper device inventory during investigations.
Built for fits when security teams need file changes connected to existing Lansweeper asset records.. Server security platform with file integrity monitoring for physical, virtual, and cloud servers. A single Deep Security policy can combine path rules with Windows registry-key monitoring for mixed workload estates. Predefined rules cover common operating-system and application locations, while custom rules target application-specific configuration paths. Content and metadata comparisons provide more detail than filename-only detection. The REST API supports administration and event retrieval, which helps connect findings with ticketing, orchestration, and reporting workflows.
Deployment requires installing and maintaining Deep Security Agents across protected hosts, followed by policy tuning to reduce expected-change noise. Deep Security File Integrity Monitoring fits server estates that already use Deep Security for workload protection and need centralized change records. It documents modifications but does not provide file restoration, source version management, or approval workflow management.
Rules watch selected registry keys and values alongside filesystem paths on Windows servers. Deep Security Agents apply consistent monitoring policies across supported virtual and cloud-hosted servers. Best for: Fits when security teams already manage Windows and Linux servers through Deep Security and need centralized change detection.
Cloud-scale monitoring platform with file integrity monitoring for infrastructure and applications. Datadog Agent file events retain host and process context inside the same investigation and automation environment as security telemetry. Security teams already deploying the Datadog Agent across servers can add monitored paths through centralized configuration. Rules can focus on application directories, system binaries, and sensitive configuration files. Datadog tags and host metadata help analysts group changes by service, environment, or ownership.
3. Software Implementation, Frameworks & Protocols The main tradeoff is dependence on the Datadog Agent and Datadog’s broader security configuration model. High-change directories require exclusion rules and alert tuning. The product fits incident response teams investigating unexpected changes alongside logs, metrics, and security signals.
Operators collect file-change events for selected system paths and connect them to centralized dashboards. Best for: Fits when security teams already use Datadog and need host changes connected to broader investigations. IT asset management platform with file integrity monitoring capabilities for tracked assets. Asset-linked file change records connect modified paths with Lansweeper device inventory during investigations.
Integration with Lansweeper’s inventory links a changed path to device identity, operating system, and installed software records. That relationship helps teams scope monitored assets and investigate changes without maintaining a separate host list. Administrators can apply path-based monitoring to sensitive files and directories. The setup requires selecting paths and maintaining exclusions as systems change. Lansweeper is less suitable for teams that need process identity on every change or remediation playbooks inside the same console. It fits investigations where analysts already rely on Lansweeper inventory and need file changes connected to known assets.
Operations teams compare reported changes with approved maintenance activity using existing device records. Best for: Fits when security teams need file changes connected to existing Lansweeper asset records. ManageEngine EventLog Analyzer includes file integrity monitoring for critical files, folders, and system changes. Use of EventLog Analyzer correlation rules to link file-related changes to surrounding authentication and system events.
ManageEngine EventLog Analyzer focuses on aggregating Windows and Linux event logs and turning them into actionable change and security signals. For file integrity monitoring workflows, it supports baseline-based integrity checks and alerting around file-related events collected from monitored endpoints. Admins can tune detection logic with rules, exclusions, and severity mappings so the alert stream reflects operational priorities. Reporting and investigation views are built around event context, change attribution fields, and audit-style timelines.
Best for: Fits when teams need file-change auditing signals derived from event logs with centralized investigation. Cloud-native file integrity monitoring for workloads across hybrid and multi-cloud environments. Cloud One console management of FIM baselines and alert workflows across enrolled endpoints in one governance surface. Trend Micro Cloud One File Integrity Monitoring continuously detects file changes on monitored endpoints and raises alerts when integrity deviates from a baseline. It integrates FIM monitoring into Trend Micro Cloud One management so configuration and reporting can be handled from a central console.
Host-agent coverage supports both scheduled integrity checks and real-time file change events, which reduces the gap between drift and detection. Change events can be filtered with exclusion rules to reduce noise from expected file churn. Best for: Fits when teams want cloud-managed file integrity monitoring with centralized reporting and practical tuning controls. InsightIDR-integrated file change events feed the same detection and triage pipeline as other InsightIDR signals.
Rapid7 InsightIDR File Integrity Monitoring targets security operations teams that already run InsightIDR and want file change auditing tied to broader detection workflows. The solution performs host-based integrity monitoring with scheduled baselines, real-time file change detection, and alerting routed into the InsightIDR event pipeline. It focuses on configuration and governance through InsightIDR integration points, including automation hooks for enrichment and response orchestration. It is most distinct where file integrity signals must co-exist with existing SIEM-style triage and case management workflows.
Best for: Fits when teams need host file change auditing integrated into InsightIDR investigations. Open-source file integrity monitoring and host-based intrusion detection for multi-platform deployments. Samhain’s baseline database and diff reporting workflow is designed for repeatable integrity verification on the same host across scans.
Samhain focuses on host-based file integrity monitoring by building a baseline inventory and then tracking deviations on an agent host. Its core workflow centers on hashing file content and recording file attributes to produce a change report for later review. The configuration model supports include and exclude rules so monitored paths can be narrowed to sensitive binaries, configuration, and directories. Scheduled integrity scans and change reports make it suitable for continuous compliance checks without depending on network traffic visibility.
Best for: Fits when teams need host-local integrity baselines and scheduled file change auditing for compliance. Firmware and hardware integrity platform extending file integrity monitoring to device firmware. Baseline-driven integrity assessment built around known-good OS and application artifacts, with change history for investigation workflows.
Eclypsium focuses on file integrity monitoring for enterprise endpoints and cloud workloads using an agent-based collection model tied to a known-good baseline. It emphasizes integrity checks for system binaries, configuration files, and OS artifacts so change auditing can support incident response and compliance workflows. The platform’s reporting and change history are designed for governance, including change attribution signals and alerting tied to observed modifications. Eclypsium also supports automation through integrations and APIs so integrity findings can flow into existing security operations workflows.
Best for: Fits when security teams need baseline-driven integrity findings with governance controls across managed endpoints. CimTrak Integrity Suite monitors file, configuration, memory, and endpoint changes in real time. Configuration change auditing for monitoring rules and scopes with clear accountability for integrity policy updates.
CimTrak Integrity Suite monitors file changes on endpoints by hashing monitored paths and comparing results to a known-good baseline. It supports change auditing with alerting, evidence capture, and rule-driven inclusion or exclusion to manage noise from expected updates. Administration centers on managing monitored scopes, controlling who can view reports and alert details, and maintaining an audit trail for governance reviews. Integration depth is focused on exporting findings and interfacing with existing security workflows rather than replacing SIEM or EDR entirely.
Best for: Fits when security teams need baseline-based file change auditing with controlled scopes and governance reporting. Tripwire Enterprise monitors file, configuration, and system changes across enterprise environments. File integrity monitoring built around controlled baselines and policy objects that generate defensible audit artifacts. Tripwire Enterprise targets organizations that need host-based file change monitoring with audit-ready reporting for compliance and incident triage. Core capabilities include baseline management with cryptographic hash verification, continuous or scheduled integrity scans, and policy-driven change detection with file and directory scope controls.
Tripwire Enterprise also supports alert workflows that can feed downstream systems through integrations built for security operations and SIEM use cases. Governance is handled through role separation, change control around monitored targets, and an audit trail that tracks configuration and reporting outcomes. Best for: Fits when regulated teams need controlled baselines, hash-verified change monitoring, and audit-oriented reporting.
After evaluating 10 cybersecurity information security, Trend Micro Deep Security File Integrity Monitoring stands out as our overall top pick — it scored highest across our combined criteria of features, ease of use, and value, which is why it sits at #1 in the rankings above. Use the comparison table and detailed reviews above to validate the fit against your own requirements before committing to a tool.
File integrity monitoring software watches for unauthorized changes to files and directories by comparing observed content against a baseline of stored hashes. The strongest options in this guide include Trend Micro Deep Security File Integrity Monitoring, which can combine path rules with Windows registry-key monitoring in a single Deep Security policy. Datadog File Integrity Monitoring and Tripwire Enterprise both connect integrity findings to investigation pipelines through their broader telemetry and policy-based change detection.
Across deployments, governance determines whether findings turn into actionable alerts. Trend Micro Cloud One File Integrity Monitoring centralizes baseline and alert workflow management for enrolled endpoints, while Rapid7 InsightIDR File Integrity Monitoring routes file change events into InsightIDR’s triage workflows. File Integrity Monitoring software for baseline-driven change detection, alerting, and audit trails File integrity monitoring software establishes a known-good baseline, then evaluates file system changes through stored hashes and integrity checks for tamper-evident audit trails. Tools like Tripwire Enterprise focus on controlled baselines and policy objects that generate defensible audit artifacts, using include and exclude targeting to reduce noise. Samhain emphasizes host-local repeatable integrity verification with stored hashes and diff reporting across scheduled scans.
Integration depth varies by product, especially where file events need to land inside existing investigation workflows. DataDog File Integrity Monitoring captures file events with host and process context inside the same Datadog Agent environment, while Rapid7 InsightIDR File Integrity Monitoring feeds file change events into InsightIDR’s detection and triage pipeline. ManageEngine EventLog Analyzer pairs baseline-driven integrity checking with correlation rules that link file-related changes to surrounding authentication and system event context.
In file integrity monitoring, alert quality depends on how baselines and change evidence are produced, stored, and compared over time. These capabilities decide whether findings stay actionable when endpoints churn, apps update frequently, or identities and processes change. Trend Micro Deep Security File Integrity Monitoring lets one Deep Security policy combine path rules with Windows registry-key monitoring for mixed workload estates. CimTrak Integrity Suite applies rule-based inclusion and exclusion to keep monitored scopes aligned with governance boundaries.
Trend Micro Cloud One File Integrity Monitoring uses the Cloud One console to manage FIM baselines and alert workflows across enrolled endpoints. Rapid7 InsightIDR File Integrity Monitoring routes file change events into the same InsightIDR detection and triage pipeline used for other signals. DataDog File Integrity Monitoring keeps file events inside the same investigation and automation environment as broader security telemetry in the Datadog Agent. Lansweeper File Integrity Monitoring links modified paths to Lansweeper device inventory so triage starts with the already-managed asset context.
ManageEngine EventLog Analyzer correlates file-related changes with surrounding authentication and system events using EventLog Analyzer correlation rules. InsightIDR-focused monitoring also reduces noise by relying on baseline-driven integrity scans before events enter the triage workflow. Samhain stores baseline hashes and runs scheduled integrity scans with diff reporting for repeatable host-local verification.
Tripwire Enterprise uses controlled baselines and policy objects that generate defensible audit artifacts with cryptographic integrity checks. The fastest path to reliable alerts starts with matching change evidence generation to how the security team investigates incidents. Some platforms send file change findings into existing telemetry workflows, while others emphasize offline repeatable baselines and audit artifacts.
Governance also varies. Some tools centralize baseline and alert workflow management in a single console, while others require distributed agent policy tuning and disciplined baseline lifecycle operations. If file changes need to appear inside Datadog investigations with host and process context from the same Datadog Agent environment, DataDog File Integrity Monitoring fits that workflow. If file changes must feed InsightIDR detections and triage alongside other InsightIDR signals, Rapid7 InsightIDR File Integrity Monitoring matches that routing model.
If FIM baselines and alert workflows should be managed from a centralized Cloud One console, Trend Micro Cloud One File Integrity Monitoring provides that single governance surface across enrolled endpoints. If the organization already standardizes on Deep Security policies across Windows and Linux, Trend Micro Deep Security File Integrity Monitoring aligns with that existing policy control plane.
For repeatable host-local verification with stored hashes and diff reporting, Samhain is built around a baseline database and scan-by-scan diff workflow. For controlled baselines that generate defensible audit artifacts through policy objects and cryptographic verification, Tripwire Enterprise fits audit-oriented evidence needs. For estates with frequent routine updates across sensitive paths, tools that rely on baseline-driven integrity scans with include and exclude targeting reduce noise through scoping rules. CimTrak Integrity Suite and Tripwire Enterprise both rely on rule-based inclusion and exclusion to manage scoped monitoring without flooding alerts.
If file-change findings must be tied to authentication and system event context using correlation rules, ManageEngine EventLog Analyzer adds that correlation layer. If trusted asset context already exists in an inventory system, Lansweeper File Integrity Monitoring can speed triage by linking modified paths to existing device records. Different teams optimize for different failure modes. Some teams lose time when file events arrive without identity and process context, while others lose time when baselines drift across large fleets.
The tools also split by governance preference. Some options concentrate baseline and workflow control in a console, while others require baseline discipline on each host or through policy tuning across agents. DataDog File Integrity Monitoring embeds file events inside the same Datadog Agent investigation and automation environment, including host and process details.
Enterprises already running Deep Security policy across mixed Windows and Linux workloads 4. Practical Deployment, Analysis & Case Studies Trend Micro Deep Security File Integrity Monitoring supports centralized change detection through a single Deep Security policy that can combine path rules with Windows registry-key monitoring.
Organizations needing cloud-managed baseline and alert workflow governance across enrolled endpoints Trend Micro Cloud One File Integrity Monitoring manages FIM baselines and alert workflows from the Cloud One console, paired with both real-time detection and scheduled integrity scanning. Tripwire Enterprise uses controlled baselines and policy objects with cryptographic verification to support audit-oriented reporting.
Teams that want host-local repeatable verification and scan diffs for compliance checks Samhain is designed for scheduled integrity scans with a stored baseline database and diff reporting workflow on the same host. Most deployment issues come from treating monitoring scope and baseline lifecycle as one-time setup work. Alert noise, missing coverage, and weak attribution often trace back to path selection and governance discipline.
Another frequent issue is assuming integration is automatic. File events may require the right collector, agent coverage, or correlation inputs before they become reliable in investigations. Monitoring every path without scoping include and exclude rules for high-change directories Rule tuning becomes labor-intensive in large heterogeneous estates for Trend Micro Deep Security File Integrity Monitoring, so broad rules usually require iterative refinement.
DataDog File Integrity Monitoring depends on installing and maintaining the Datadog Agent for host coverage, so unmaintained endpoints silently reduce integrity visibility. Relying on baseline checks without aligning change attribution to the available event fidelity ManageEngine EventLog Analyzer can only correlate file-related changes as well as the endpoint event logs and collector configuration provide surrounding authentication and system context.
Skipping baseline management discipline and letting known-good artifacts drift into the monitored baseline Eclypsium requires disciplined baseline management because its detection depends on known-good OS and application artifacts and on installed agent visibility for scope coverage. We evaluated Trend Micro Deep Security File Integrity Monitoring, DataDog File Integrity Monitoring, Lansweeper File Integrity Monitoring, ManageEngine EventLog Analyzer, Trend Micro Cloud One File Integrity Monitoring, Rapid7 InsightIDR File Integrity Monitoring, Samhain, Eclypsium, CimTrak Integrity Suite, and Tripwire Enterprise on feature coverage at 40% weight. Ease of deployment and ongoing operations plus value outcomes each contributed 30% of the total score.
Trend Micro Deep Security File Integrity Monitoring stood out because a single Deep Security policy can combine path rules with Windows registry-key monitoring for mixed workload estates. That combination reduces the need for separate policy surfaces when both file system and registry changes must be detected under one governance workflow. See head-to-head software comparisons with feature breakdowns, pricing, and our recommendation for each use case.
See side-by-side comparisons of cybersecurity information security tools and pick the right one for your stack. Our best-of pages are how many teams discover and compare tools in this space. If you think your product belongs in this lineup, we’d like to hear from you—we’ll walk you through fit and what an editorial entry looks like. Readers come to these pages to shortlist software—your product shows up in that moment, not in a random sidebar.
We describe your product in our own words and check the facts before anything goes live. You appear in the roundup the same way as other tools we cover: name, positioning, and a clear next step for readers who want to learn more. We refresh lists on a regular rhythm so the category page stays useful as products and pricing change.
A simple and powerful cybersecurity tool to monitor file changes using hashing (SHA-256). This project detects any modification, deletion, or addition of files and alerts the user via GUI and Email. I Monitor multiple files I Detect file modifications I Detect deleted files I Detect newly added files I GUI interface using Tkinter I Email alert system I Secure hashing using SHA-256 Tripwire Enterprise is the safest best pick if you run enterprise endpoints and need governed integrity policies with detailed, SIEM-ready change events, whereas ADAudit Plus fits Windows teams that want file change evidence tied to identity activity when staying in an AD-focused world.
Three quick recommendations before you dive into the full comparison below — each one leads on a different dimension. Centralized integrity policy management with controlled baseline snapshots for repeatable change detection at enterprise scale. Best for: Fits when enterprises need governed integrity policies, detailed change events, and SIEM-ready auditing across many endpoints.
Wazuh’s unified rules engine correlates file change detections with other host signals for context-rich alerts. Best for: Fits when file integrity signals must correlate with broader host detections and automated response workflows. Built-in Active Directory identity correlation on integrity events for clearer change attribution. Best for: Fits when Windows environments need file change evidence linked to identity activity.
Tripwire Enterprise monitors file, directory, configuration, and system changes across enterprise environments. Centralized integrity policy management with controlled baseline snapshots for repeatable change detection at enterprise scale. Tripwire Enterprise uses agent-based integrity checking on endpoints, where file attributes and cryptographic hashes are evaluated against a known-good baseline. Administrators can model integrity rules around protected paths, set action responses for detected changes, and generate audit-friendly reporting with change detail for investigators. The configuration workflow supports baseline snapshot creation and controlled re-baselining to reduce alert noise after planned changes.
A tradeoff appears in operational overhead, because maintaining accurate allowlists and keeping baselines current requires disciplined change management. The tool fits environments with defined operational ownership for endpoints, where security teams and system owners can approve baseline updates and review recurring change patterns during scheduled integrity scans.
System administrators apply a controlled baseline update after change windows, then validate detection behavior. Operators track changes to system binaries and configuration paths with detailed event records and scheduled scans. Best for: Fits when enterprises need governed integrity policies, detailed change events, and SIEM-ready auditing across many endpoints.
Wazuh provides host-based intrusion detection with file integrity monitoring for servers, endpoints, and cloud workloads. Wazuh’s unified rules engine correlates file change detections with other host signals for context-rich alerts. Wazuh’s file integrity checking is delivered through its agent, which collects file metadata and change events from monitored hosts and then runs them through a centralized detection and rules layer. Integrity activity can feed dashboards, alerts, and downstream workflows, so analysts do not rely on a separate FIM console to investigate. Configuration is policy-based, and the system can generate an audit trail of detected changes alongside related security signals from the same hosts.
A key tradeoff is operational overhead because reliable baselines and low-noise alerting require disciplined agent enrollment, policy distribution, and recurring verification of what files should change. Wazuh fits environments that already run or plan to run host security analytics, where file change signals need correlation with authentication events, vulnerability findings, and other host telemetry.
Use the Wazuh API to push integrity findings into ticketing and response orchestration. Best for: Fits when file integrity signals must correlate with broader host detections and automated response workflows. ADAudit Plus audits file access and change activity across Windows servers, shares, and Active Directory environments. Built-in Active Directory identity correlation on integrity events for clearer change attribution.
ADAudit Plus uses a Windows-focused monitoring model that couples integrity findings with directory and identity context, which helps when change attribution matters. It supports baselining and integrity verification through hash-based comparisons, then records results as audit log entries for investigation and reporting. The reporting output is oriented toward governance needs rather than only file-change notifications.
A key tradeoff is that AD-centric identity context can be wasted when the environment has minimal Active Directory usage or relies on non-Windows endpoints. It fits organizations that need integrity change evidence linked to user and group activity on Windows file servers and domain-joined endpoints. Regular baselined verification supports controlled monitoring windows and repeatable review.
Best for: Fits when Windows environments need file change evidence linked to identity activity. Qualys File Integrity Monitoring tracks changes to critical files, directories, and system configurations. Qualys-integrated integrity evaluation produces audit-ready change evidence tied to managed policies. Qualys File Integrity Monitoring pairs endpoint change detection with policy-driven integrity rules across operating systems. It builds baselines from known-good file states and evaluates current hashes against a maintained reference set.
Best for: Fits when security teams need centrally governed integrity monitoring with repeatable evidence for compliance and audit trails. OSSEC’s agent-centric architecture combines file integrity checks with log monitoring and HIDS detection on the same host. OSSEC performs host-based file integrity checking by computing hashes for monitored files and comparing them against a known baseline. It also supports host intrusion detection and log analysis in the same agent model, which helps produce unified host-change visibility.
Best for: Fits when an enterprise needs host-level integrity checking across many endpoints under central policy control. FIM findings route through Datadog’s alerting and event pipeline for correlation with metrics and logs across the same environment. Datadog File Integrity Monitoring targets teams that already run Datadog for operations and need file change signals folded into existing monitoring workflows. It uses an endpoint agent to compute file baselines and then flags new or modified files, routing alerts through Datadog’s alerting, dashboards, and event streams.
Best for: Fits when Datadog is already the monitoring hub and file-change alerts must correlate with other telemetry. AIDE creates a database of file attributes and detects changes through cryptographic checksums. AIDE’s standalone baseline and compare cycle updates trust by regenerating its local integrity database rather than using continuous agent telemetry.
AIDE is a host-based file integrity checker that uses a locally maintained database of cryptographic hashes for change detection. It generates baselines, compares current file states against known-good records, and reports mismatches for targeted files and directories. Best for: Fits when teams need scheduled file integrity checking on Linux hosts with simple local reporting and external alerting.
5. Performance Evaluation & Extended Technical Observations CimTrak provides real-time file integrity monitoring for systems, applications, databases, and network devices. Audit-oriented change review workflow that centers expected baselines and administrator handling of detected differences. CimTrak delivers file integrity checking with an audit-oriented workflow that ties detected changes to what is expected on each monitored system. It focuses on baseline management and repeatable integrity scans so administrators can track unauthorized file changes and configuration drift across endpoints.
Best for: Fits when a team needs audit-friendly integrity checks with disciplined baseline management. Baseline and verification are centered on stored file inventories and deterministic scan comparisons rather than live enforcement. AFICK is an open source file integrity checking utility that compares current filesystem state against a stored known-good inventory. It uses per-file attributes and checksums to detect changes, then reports differences for triage.
Best for: Fits when teams need scheduled integrity scans on a small set of hosts without a full HIDS stack. Configurable baselines for monitored directory trees with hash comparison and file-level change evidence in scan results. Samhain from la-samhna.de targets file integrity checking through host-side integrity baselining and ongoing change detection. It uses a baseline snapshot approach where hashes are computed for configured paths and then compared during scheduled or triggered scans.
Best for: Fits when teams need filesystem integrity verification with clear scan evidence and controlled scope. After evaluating 10 file integrity checking software, Tripwire Enterprise stands out as our overall top pick — it scored highest across our combined criteria of features, ease of use, and value, which is why it sits at #1 in the rankings above. Use the comparison table and detailed reviews above to validate the fit against your own requirements before committing to a tool.
File integrity checking software monitors file and configuration changes by comparing current file attributes and cryptographic hashes against a managed baseline snapshot. This guide covers Tripwire Enterprise, Wazuh, and SANS alongside other tools that use agent-based collection or scheduled local scans for integrity verification. The coverage focuses on how each product handles baseline lifecycle, how detected changes get enriched for investigation, and how alerts and reports fit into existing operations. The toolset spans centralized policy management in Tripwire Enterprise, unified rules correlation in Wazuh, and audit-oriented change review workflows in SANS-style HIDS deployments.
File Integrity Checking Software for baseline-driven tamper detection and change attribution File integrity checking software detects unauthorized file changes by hashing monitored files and comparing those hashes and attributes to a known-good baseline. Tripwire Enterprise emphasizes centralized integrity policy management with controlled baseline snapshots for repeatable change detection, which supports consistent investigations across many endpoints.
Wazuh routes file change detections through its unified rules engine so integrity events gain context alongside other host signals, which affects alert quality and downstream automation. Some tools instead rely on local or scheduled baseline compare cycles, where scan runs generate file-level evidence that external workflows must triage and act on. File integrity checking succeeds when baseline handling is governed end to end, not when detection works only in a lab environment. The baseline lifecycle affects repeatability, forensic value, and how quickly legitimate changes stop triggering alerts.
Alert investigation needs more than a changed filename. It requires change event detail that supports attribution, correlation with other host signals, and audit-ready reporting for compliance workflows. Tripwire Enterprise provides centralized integrity policy management with controlled baseline snapshots and re-baselining workflows for enterprise repeatability. CimTrak also emphasizes baseline-driven integrity scans but centers audit-style change review around expected baselines and administrator handling.
Wazuh routes file integrity detections through a unified rules engine so integrity events gain context with other host detections. Datadog File Integrity Monitoring routes findings into Datadog’s alerting and event pipeline for correlation with metrics and logs in the same environment. ManageEngine ADAudit Plus adds Active Directory identity correlation on integrity events to connect file modifications to identity activity. OSSEC combines file integrity checks with log monitoring and HIDS detection on the same host, but change attribution still needs extra tuning for clarity.
Qualys File Integrity Monitoring includes scoping and scheduling controls that reduce alert noise across large fleets while keeping centrally governed integrity monitoring. AIDE focuses on scheduled baseline compare cycles with local integrity database updates, which shifts noise management to external scheduling and alert triage. Tripwire Enterprise and Wazuh both rely on agent-based deployment, which supports broad coverage but adds endpoint rollout coordination. AIDE and AFICK focus on scheduled local scans or deterministic offline baseline compare cycles, which lowers central fleet complexity at the cost of limited central agent management.
How to choose File Integrity Checking Software by baseline governance and operational fit The first choice is not hashing strength. It is the baseline operating model that determines how changes become “known good” without erasing forensic meaning. The second choice is where change events should land for action. Some tools feed an integrated rules engine for automated response workflows, while others generate scan evidence that external processes must triage and enforce.
Select Tripwire Enterprise when baseline snapshots must be centrally governed with controlled re-baselining workflows for repeatable change detection at scale. Select AIDE or AFICK when scheduled integrity checks on Linux hosts or small host sets work better with local baseline creation and external alerting. Decide where file-change decisions happen: unified rules correlation versus external triage Choose Wazuh when file integrity detections must be correlated through a unified rules engine with other host signals for context-rich alerts and automated response workflows. Choose Samhain or Qualys File Integrity Monitoring when scan runs and managed policies produce file-level evidence that security teams route through existing ticketing, SIEM, or review workflows.
Choose ManageEngine ADAudit Plus when Windows fleets require Active Directory identity correlation tied to integrity events for clearer investigation of file modifications. Choose OSSEC when a combined host monitoring stack is acceptable, with integrity checks and log monitoring on endpoints under central policy control, even if attribution needs extra tuning. Expect Tripwire Enterprise and Wazuh to require ongoing admin workload for baseline lifecycle and tuning because managed policies and rules correlation depend on careful configuration. Expect Qualys File Integrity Monitoring and AIDE to require workload shifts toward scoping, scheduling, include and exclude patterns, and exception handling to keep alert volume manageable.
Choose Tripwire Enterprise when governed integrity policy management must align with investigation-ready change events and audit-friendly reporting across many endpoints. Choose CimTrak when audit-oriented change review centered on expected baselines is the primary workflow and external automation fills enforcement gaps. File integrity checking tools fit organizations that treat integrity evidence as an operational input to investigations, ticketing, and compliance reporting. The best match depends on whether baseline governance needs to be centralized or whether scheduled evidence generation is enough.
Some deployments focus on fleet-level correlation and automation, while others focus on scheduled scans with controlled scope and audit-ready scan outputs. Tripwire Enterprise fits when centralized integrity policy management and controlled baseline snapshots are required to keep investigations consistent across many endpoints.
Wazuh fits when a unified rules engine must correlate integrity events with other host signals to improve alert context and support automated response workflows. ManageEngine ADAudit Plus fits when Active Directory identity correlation on integrity events must clarify change attribution for investigations.
Datadog File Integrity Monitoring fits when file-change findings must route through Datadog’s alerting and event pipeline alongside metrics and logs. AIDE fits when scheduled baseline and compare cycles can update a local integrity database and produce evidence for external alert routing.
Most rollout failures come from baseline lifecycle mistakes and from mismatched expectations about how much correlation and enforcement is built in. A tool can detect changes, but governance gaps can turn detection into a chronic alert workload. The second pitfall is assuming every environment can use the same attribution workflow, especially when identity and OS alignment differs.
Tripwire Enterprise and Wazuh require baseline lifecycle and tuning discipline, because neglect can create drift and inflate alert volume over time. Expecting scan evidence to automatically produce investigation context and enforcement AIDE and AFICK produce deterministic scan comparisons and integrity evidence, but enforcement workflows like quarantine require external automation and separate triage steps.
Qualys File Integrity Monitoring includes scoping and scheduling controls, but operational tuning is still needed to manage file churn and exceptions without overwhelming analysts. ManageEngine ADAudit Plus provides built-in Active Directory identity correlation on integrity events, while OSSEC can require extra tuning to make change attribution clear.
We evaluated file integrity checking tools by measuring baseline lifecycle feature depth, detection event usefulness for investigation, and operational fit for baseline maintenance and tuning. Features accounted for 40% of the score by focusing on baseline snapshot governance, change evidence detail, and workflow support for re-baselining or policy-controlled scans. Ease and value each accounted for 30% by assessing deployment overhead for agent-based coverage and how quickly teams could reduce noisy alerts through scoping, scheduling, or tuning. Tripwire Enterprise separated itself with centralized integrity policy management and controlled baseline snapshots that produced repeatable change detection across many endpoints.
See head-to-head software comparisons with feature breakdowns, pricing, and our recommendation for each use case. See side-by-side comparisons of cybersecurity information security tools and pick the right one for your stack. Our best-of pages are how many teams discover and compare tools in this space. If you think your product belongs in this lineup, we’d like to hear from you—we’ll walk you through fit and what an editorial entry looks like.
Readers come to these pages to shortlist software—your product shows up in that moment, not in a random sidebar. We describe your product in our own words and check the facts before anything goes live. You appear in the roundup the same way as other tools we cover: name, positioning, and a clear next step for readers who want to learn more.
We refresh lists on a regular rhythm so the category page stays useful as products and pricing change. Written by Tatiana Kuznetsova · Edited by James Mitchell · Fact-checked by Helena Strand Published June 19, 2026 Updated October 12, 2026 Next review: within 42 days 16 min read Includes paid placements · ranking is editorial. Worldmetrics may earn a commission through links on this page. This does not influence our rankings — products are evaluated through our verification process and ranked by quality and fit. Read our editorial policy → AFICK is the best fit if scheduled host integrity checks and straightforward human triage are enough, whereas Samhain is the cleaner pick for administrators who need deterministic per-file change output on Unix and Linux systems.
AFICK keeps integrity logic centered on baseline hash comparisons and mismatch reporting, with minimal workflow complexity. Samhain’s change detection is driven by a file and hash baseline with per-file discrepancy reporting, not only aggregated events.
Best for: Fits when administrators need deterministic host integrity checks with clear per-file change output. Tripwire’s change validation workflow ties detected file events to controlled baseline expectations and retained evidence. Best for: Fits when security teams need audit-ready file change evidence across mixed server fleets. A document search collects the original publication and places each number next to its sentence.
Scores are calculated across three dimensions: Features (depth and breadth of capabilities, verified against official documentation), Ease of use (aggregated sentiment from user reviews, weighted by recency), and Value (pricing relative to features and market alternatives). Each dimension is scored 1–10. Harvested Online Documentation & Reference Sources • https://github.com/Anujadhav23/file-integrity-checker • https://www.manageengine.com/log-management/cyber-security/file-integrity-monitoring-architecture-implementation-workin g.html • https://github.com/Achiefs/fim • https://documentation.wazuh.com/current/proof-of-concept-guide/poc-file-integrity-monitoring.html • https://learn.microsoft.com/en-us/azure/defender-for-cloud/file-integrity-monitoring-overview • https://docs.qualys.com/en/fim/latest/get_started/get_started.htm • https://github.com/andreitrcv/File-Integrity-Monitor_Email-Alert-System • https://oneuptime.com/blog/post/2026-01-15-setup-tripwire-file-integrity-monitoring-ubuntu/view • https://learn.edwhere.com/blog/wazuh-file-integrity-monitoring-guide • https://gitnux.org/best/file-integrity-monitoring-software/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for File Integrity Checker With Email Alert Using Python.
[*] Synchronizing KnowBe4 Awareness Training telemetry... ──────────────────────────────────────────────────────────────────────── [11:45:02.102] MAIL Dispatched simulated assessment templates [11:45:02.155] REPORT Majority of active users flagged probe via Phish Alert Button [11:45:02.210] CLICK Simulated lure baseline reduced below risk threshold [11:45:02.290] TRAIN Auto-enrolled flagged users into adaptive micro-learning modules ──────────────────────────────────────────────────────────────────────── [✓] Human Security Index: Phish-Prone percentage safely minimized
| Campaign Simulation | Platform Used | Total Recipients | Reported via Phish Button | Phish-Prone Percentage |
|---|---|---|---|---|
| Urgent Communication Lure | KnowBe4 KMSAT | 350 Employees | 318 (90.8%) | 2.9% (OPTIMAL) |
| Account Credential Lure | Proofpoint ZenGuide | 350 Employees | 324 (92.5%) | 2.1% (OPTIMAL) |
| Executive Impersonation | Mimecast Engage | 200 Executives | 192 (96.0%) | 1.5% (OPTIMAL) |