Complete Technical Paper Content — File Integrity Monitoring System Using Sha 256 Hashing
Overview & System Context
File Integrity Monitoring System Using Sha 256 Hashing: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8354 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background In cryptography, SHA-1 (Secure Hash Algorithm 1) is a hash function which takes an input and produces a 160-bit (20-byte) hash value known as a message digest – typically rendered as 40 hexadecimal digits. It was designed by the United States National Security Agency, and is a U.S. Federal Information Processing Standard. The algorithm has been cryptographically broken but is still widely used. Since 2005, SHA-1 has not been considered secure against well-funded opponents; as of 2010 many organizations have recommended its replacement. NIST formally deprecated use of SHA-1 in 2011 and disallowed its use for digital signatures in 2013, and declared that it should be phased out by 2030. As of 2020, chosen-prefix attacks against SHA-1 are practical. As such, it is recommended to remove SHA-1 from products as soon as possible and instead use SHA-2 or SHA-3. Replacing SHA-1 is urgent where it is used for digital signatures. All major web browser vendors ceased acceptance of SHA-1 SSL certificates in 2017. In February 2017, CWI Amsterdam and Google announced they had performed a collision attack against SHA-1, publishing two dissimilar PDF files which produced the same SHA-1 hash.
However, SHA-1 is still secure for HMAC. Microsoft has discontinued SHA-1 code signing support for Windows Update on August 3, 2020, which also effectively ended the update servers for versions of Windows that have not been updated to SHA-2, such as Windows 2000 up to Vista, as well as Windows Server versions from Windows 2000 Server to Server 2003. SHA-1 is based on principles similar to those used by Ronald L. Rivest of MIT in the design of the MD4 and MD5 message digest algorithms, but generates a larger message digest (160 bits vs. 128 bits).
SHA-1 was developed as part of the U.S. Government's Capstone project. The original specification of the algorithm was published in 1993 under the title Secure Hash Standard, FIPS PUB 180, by U.S. government standards agency NIST (National Institute of Standards and Technology). This version is now often named SHA-0. It was withdrawn by the NSA shortly after publication and was superseded by the revised version, published in 1995 in FIPS PUB 180-1 and commonly designated SHA-1. SHA-1 differs from SHA-0 only by a single bitwise rotation in the message schedule of its compression function. According to the NSA, this was done to correct a flaw in the original algorithm which reduced its cryptographic security, but they did not provide any further explanation. Publicly available techniques did indeed demonstrate a compromise of SHA-0, in 2004, before SHA-1 in 2017 (see §Attacks).
SHA-1 forms part of several widely used security applications and protocols, including TLS and SSL, PGP, SSH, S/MIME, and IPsec. Those applications can also use MD5; both MD5 and SHA-1 are descended from MD4. SHA-1 and SHA-2 are the hash algorithms required by law for use in certain U.S. government applications, including use within other cryptographic algorithms and protocols, for the protection of sensitive unclassified information. FIPS PUB 180-1 also encouraged adoption and use of SHA-1 by private and commercial organizations. SHA-1 is being retired from most government uses; the U.S. National Institute of Standards and Technology said, "Federal agencies should stop using SHA-1 for...applications that require collision resistance as soon as practical, and must use the SHA-2 family of hash functions for these applications after 2010", though that was later relaxed to allow SHA-1 to be used for verifying old digital signatures and time stamps. A prime motivation for the publication of the Secure Hash Algorithm was the Digital Signature Standard, in which it is incorporated. The SHA hash functions have been used for the basis of the SHACAL block ciphers.
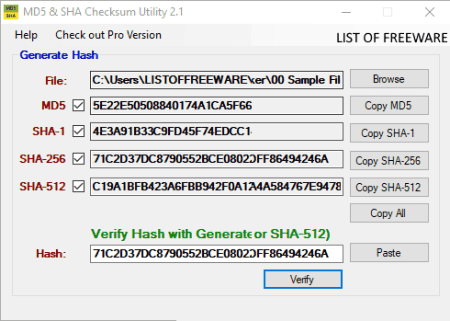
Figure 1: 18 Best Free File Integrity Checker Software For Windows If you have disk corruption, if you have DRAM corruption, if you have any kind of problems at all, Git will notice them. It's not a question of if, it's a guarantee. You can have people who try to be malicious. They won't succeed. [...] Nobody has been able to break SHA-1, but the point is the SHA-1, as far as Git is concerned, isn't even a security feature. It's purely a consistency check. The security parts are elsewhere, so a lot of people assume that since Git uses SHA-1 and SHA-1 is used for cryptographically secure stuff, they think that, Okay, it's a huge security feature. It has nothing at all to do with security, it's just the best hash you can get. ... I guarantee you, if you put your data in Git, you can trust the fact that five years later, after it was converted from your hard disk to DVD to whatever new technology and you copied it along, five years later you can verify that the data you get back out is the exact same data you put in. [...] One of the reasons I care is for the kernel, we had a break in on one of the BitKeeper sites where people tried to corrupt the kernel source code repositories. However Git does not require the second preimage resistance of SHA-1 as a security feature, since it will always prefer to keep the earliest version of an object in case of collision, preventing an attacker from surreptitiously overwriting files. The known attacks (as of 2020) also do not break second preimage resistance.
Implementations of all FIPS-approved security functions can be officially validated through the CMVP program, jointly run by the National Institute of Standards and Technology (NIST) and the Communications Security Establishment (CSE). For informal verification, a package to generate a high number of test vectors is made available for download on the NIST site; the resulting verification, however, does not replace the formal CMVP validation, which is required by law for certain applications.
As of December 2013, there are over 2000 validated implementations of SHA-1, with 14 of them capable of handling messages with a length in bits not a multiple of eight (see SHS Validation List Archived 2011-08-23 at the Wayback Machine). SHA1("The quick brown fox jumps over the lazy dog") Outputted hexadecimal: 2fd4e1c67a2d28fced849ee1bb76e7391b93eb12 Outputted Base64 binary to ASCII text encoding: L9ThxnotKPzthJ7hu3bnORuT6xI= Even a small change in the message will, with overwhelming probability, result in many bits changing due to the avalanche effect. For example, changing dog to cog produces a hash with different values for 81 of the 160 bits: SHA1("The quick brown fox jumps over the lazy cog") Outputted hexadecimal: de9f2c7fd25e1b3afad3e85a0bd17d9b100db4b3 Outputted Base64 binary to ASCII text encoding: 3p8sf9JeGzr60+haC9F9mxANtLM= The hash of the zero-length string is: Figure 2: File Hash Verification Guide Using SHA-256 Local Client-Side Tool ...
SHA1("") Outputted hexadecimal: da39a3ee5e6b4b0d3255bfef95601890afd80709 Outputted Base64 binary to ASCII text encoding: 2jmj7l5rSw0yVb/vlWAYkK/YBwk= Note 1: All variables are unsigned 32-bit quantities and wrap modulo 232 when calculating, except for ml, the message length, which is a 64-bit quantity, and hh, the message digest, which is a 160-bit quantity. Note 2: All constants in this pseudo code are in big endian. Within each word, the most significant byte is stored in the leftmost byte position Pre-processing: append the bit '1' to the message e.g. by adding 0x80 if message length is a multiple of 8 bits. append 0 ≤ k < 512 bits '0', such that the resulting message length in bits is congruent to −64 ≡ 448 (mod 512) append ml, the original message length in bits, as a 64-bit big-endian integer. Thus, the total length is a multiple of 512 bits.
Process the message in successive 512-bit chunks: break message into 512-bit chunks for each chunk break chunk into sixteen 32-bit big-endian words w[i], 0 ≤ i ≤ 15 Figure 3: How To Check The SHA-256 Hash of a File in Windows - YouTube Message schedule: extend the sixteen 32-bit words into eighty 32-bit words: for i from 16 to 79 Note 3: SHA-0 differs by not having this leftrotate. w[i] = (w[i-3] xor w[i-8] xor w[i-14] xor w[i-16]) leftrotate 1 Initialize hash value for this chunk: a = h0 b = h1 c = h2 d = h3 e = h4 Main loop: for i from 0 to 79 if 0 ≤ i ≤ 19 then f = (b and c) or ((not b) and d) k = 0x5A827999 else if 20 ≤ i ≤ 39 f = b xor c xor d k = 0x6ED9EBA1 else if 40 ≤ i ≤ 59 f = (b and c) or (b and d) or (c and d) k = 0x8F1BBCDC else if 60 ≤ i ≤ 79 f = b xor c xor d k = 0xCA62C1D6 temp = (a leftrotate 5) + f + e + k + w[i] e = d d = c c = b leftrotate 30 b = a a = temp Add this chunk's hash to result so far: h0 = h0 + a h1 = h1 + b h2 = h2 + c h3 = h3 + d h4 = h4 + e Produce the final hash value (big-endian) as a 160-bit number: hh = (h0 leftshift 128) or (h1 leftshift 96) or (h2 leftshift 64) or (h3 leftshift 32) or h4 The number hh is the message digest, which can be written in hexadecimal (base 16). The chosen constant values used in the algorithm were assumed to be nothing up my sleeve numbers: The four round constants k are 230 times the square roots of 2, 3, 5 and 10. However they were incorrectly rounded to the nearest integer instead of being rounded to the nearest odd integer, with equilibrated proportions of zero and one bits. As well, choosing the square root of 10 (which is not a prime) made it a common factor for the two other chosen square roots of primes 2 and 5, with possibly usable arithmetic properties across successive rounds, reducing the strength of the algorithm against finding collisions on some bits. The first four starting values for h0 through h3 are the same with the MD5 algorithm, and the fifth (for h4) is similar. However they were not properly verified for being resistant against inversion of the few first rounds to infer possible collisions on some bits, usable by multiblock differential attacks. Instead of the formulation from the original FIPS PUB 180-1 shown, the following equivalent expressions may be used to compute f in the main loop above: Bitwise choice between c and d, controlled by b. (0 ≤ i ≤ 19): f = d xor (b and (c xor d)) (alternative 1) (0 ≤ i ≤ 19): f = (b and c) or ((not b) and d) (alternative 2) (0 ≤ i ≤ 19): f = (b and c) xor ((not b) and d) (alternative 3) (0 ≤ i ≤ 19): f = vec_sel(d, c, b) (alternative 4) [premo08] Bitwise majority function. (40 ≤ i ≤ 59): f = (b and c) or (d and (b or c)) (alternative 1) (40 ≤ i ≤ 59): f = (b and c) or (d and (b xor c)) (alternative 2) (40 ≤ i ≤ 59): f = (b and c) xor (d and (b xor c)) (alternative 3) (40 ≤ i ≤ 59): f = (b and c) xor (b and d) xor (c and d) (alternative 4) (40 ≤ i ≤ 59): f = vec_sel(c, b, c xor d) (alternative 5) This transformation keeps all operands 64-bit aligned and, by removing the dependency of w[i] on w[i-3], allows efficient SIMD implementation with a vector length of 4 like x86 SSE instructions.
2. System Architecture & Core Working Principles Botan Bouncy Castle cryptlib Crypto++ Libgcrypt Mbed TLS Nettle LibreSSL OpenSSL GnuTLS Hardware acceleration is provided by the following processor extensions: Intel SHA extensions: Available on some Intel and AMD x86 processors. VIA PadLock IBM z/Architecture: Available since 2003 as part of the Message-Security-Assist Extension CSRC Cryptographic Toolkit – Official NIST site for the Secure Hash Standard FIPS 180-4: Secure Hash Standard (SHS) RFC 3174 (with sample C implementation) Interview with Yiqun Lisa Yin concerning the attack on SHA-1 Explanation of the successful attacks on SHA-1 (3 pages, 2006) Cryptography Research – Hash Collision Q&A Lecture on SHA-1 (1h 18m) on YouTube by Christof Paar. Archived 2017-04-24 at the Wayback Machine KeePass Password Safe is a free and open-source password manager primarily for Windows. It officially supports macOS and Linux operating systems through the use of Mono. Additionally, there are several unofficial ports for Windows Phone, Android, iOS, and BlackBerry devices, which normally work with the same copied or shared (remote) password database.
KeePass stores usernames, passwords, and other fields, including free-form notes and file attachments, in an encrypted file. This file can be protected by any combination of a master password, a key file, and the current Windows account details. By default, the KeePass database is stored on a local file system (as opposed to cloud storage). KeePass comes in two different variants: KeePass 1.x and KeePass 2.x. Although the 1.x variant is the former variant it is supported indefinitely: Dominik Reichl: "2.x isn't the successor of 1.x, and 1.x isn't dead". KeePass 2.x has a different software basis in C# instead of the former C++. Mainly communication features are extended in KeePass 2.x: authentication with the Windows user account, remote and shared database editing as well as many plugins allowing communication and authentication with different web browsers, databases and more. KeePass 1.x and 2.x support a number of plugins, although 2.x allows more plugins. It has a password generator and synchronization function, supports two-factor authentication, and has a Secure Desktop mode. It can use a two-channel auto-type obfuscation feature to offer additional protection against keyloggers. KeePass can import from over 30 other most commonly used password managers. A 2017 Consumer Reports article described KeePass as one of the four most widely used password managers (alongside 1Password, Dashlane and LastPass), being "popular among tech enthusiasts" and offering the same level of security as non-free competitors. A 2019 Independent Security Evaluators study described KeePass as well as other widely used password managers as being unable to control Windows 10's tendency to leave passwords in cleartext in RAM after they are displayed using Windows controlled GUI. In addition, several GitHub projects (KeeFarce, KeeThief, Lazanga) specifically attack a running KeePass to steal all data when the host is compromised.
KeePass cannot prevent password theft and, as Dominik Reichl, the administrator of KeePass, states, "neither KeePass nor any other password manager can magically run securely in a spyware-infected, insecure environment." KeePass can minimize itself and type the information of the currently selected entry into dialogs, webforms, etc. KeePass has a global auto-type hot key. When KeePass is running in the background (with an unlocked database) and user presses down the hotkey, it looks up the selected (or correct) entry and enters every login and/or password characters sequence. All fields, such as title, username, password, URL, and notes, can be drag and dropped into other windows. Windows clipboard handling allows double-clicking on any field of the password list to copy its value to the Windows clipboard. KeePass may be configured to randomize characters' input sequence to make it harder to log keystrokes. The features is called Two-Channel Auto-Type Obfuscation (TCATO).
KeePass features a built-in password generator that generates random passwords. Random seeding can be done through user input (mouse movement and random keyboard input). According to the utility's author, KeePass was one of the first password management utilities to use security-enhanced password edit controls, in this case one called CSecureEditEx. The author makes several claims regarding the security of the control and its resistance to password revealing utilities; however, the author does not cite or make any references to any third-party testing of the control to corroborate the claims of its security. Passwords are protected in memory while KeePass is running. On Windows Vista and later versions, passwords are encrypted in process memory using Windows Data Protection API, which allows storing the key for memory protection in a secure, non-swappable memory area. On previous Windows systems, KeePass falls back to using the ARC4 cipher with a temporary, random session key.
Access to the database is restricted by a master password or a key file. Both methods may be combined to create a "composite master key". If both methods are used, then both must be present to access the password database. KeePass version 2.x introduces a third option—dependency upon the current Windows user. KeePass encrypts the database with the AES, Twofish or ChaCha20 symmetric cipher, where the first two are used in CBC/PKCS7 mode. AES is the default option in both KeePass editions, Twofish is available in KeePass 1.x, ChaCha20 is available only in KeePass 2.35 and higher.
However, a separate plugin provides Twofish as an encryption algorithm in KeePass 2.x. In KeePass 1.x (KDB database format), the integrity of the data is checked using a SHA-256 hash of the plaintext, whereas in KeePass 2.x (KDBX database format), the authenticity of the data is ensured using a HMAC-SHA-256 hash of the ciphertext (Encrypt-then-MAC construction).
BitTorrent is a communication protocol for peer-to-peer file sharing (P2P), which enables users to distribute data and electronic files over the Internet in a decentralized manner. The act of downloading and uploading data via BitTorrent is also labeled "torrenting". The protocol is developed and maintained by Rainberry, Inc., and was first released in 2001. To send or receive files, users use a BitTorrent client on their Internet-connected computer, which are available for a variety of computing platforms and operating systems, including an official client. BitTorrent trackers provide a list of files available for transfer and allow the client to find peer users, known as "seeds", who may transfer the files. BitTorrent downloading is considered to be faster than HTTP ("direct downloading") and FTP due to the lack of a central server that could limit bandwidth. BitTorrent is one of the most common protocols for transferring large files, such as digital video files containing TV shows and video clips, or digital audio files. BitTorrent accounted for a third of all internet traffic in 2004, according to a study by Cachelogic. As recently as 2019 BitTorrent remained a significant file sharing protocol according to Sandvine, generating a substantial amount of Internet traffic, with 2.46% of downstream, and 27.58% of upstream traffic, although this share has declined significantly since then.
Programmer Bram Cohen, a University at Buffalo alumnus, designed the protocol in April 2001 with the idea of speeding up download time by enabling files to be downloaded from many sources. He then released the first available version on 2 July 2001. Cohen and Ashwin Navin founded BitTorrent, Inc. (later renamed Rainberry, Inc.) to further develop the technology in 2004. The first release of the BitTorrent client had no search engine and no peer exchange. Up until 2005, the only way to share files was by creating a small text file called a "torrent", that they would upload to a torrent index site. The first uploader acted as a seed, and downloaders would initially connect as peers. Those who wish to download the file would download the torrent, which their client would use to connect to a tracker which had a list of the IP addresses of other seeds and peers in the swarm. Once a peer completed a download of the complete file, it could in turn function as a seed. These files contain metadata about the files to be shared and the trackers which keep track of the other seeds and peers. In 2005, first Vuze and then the BitTorrent client introduced distributed tracking using distributed hash tables which allowed clients to exchange data on swarms directly without the need for a torrent file. In 2006, peer exchange functionality was added allowing clients to add peers based on the data found on connected nodes. In 2017, BitTorrent, Inc. released the BitTorrent v2 protocol specification.
BitTorrent v2 is intended to work seamlessly with previous versions of the BitTorrent protocol. The main reason for the update was that the old cryptographic hash function, SHA-1, is no longer considered safe from malicious attacks by the developers, and as such, v2 uses SHA-256. To ensure backwards compatibility, the v2 .torrent file format supports a hybrid mode where the torrents are hashed through both the new method and the old method, with the intent that the files will be shared with peers on both v1 and v2 swarms. Another update to the specification is adding a hash tree to speed up time from adding a torrent to downloading files, and to allow more granular checks for file corruption. In addition, each file is now hashed individually, enabling files in the swarm to be deduplicated, so that if multiple torrents include the same files, but seeders are only seeding the file from some, downloaders of the other torrents can still download the file. In addition, file hashes can be displayed on tracker, torrent indexing services, to search for swarms by searching for hashes of files contained in them. These hashes are different from the usual SHA-256 hash of files and can be obtained using tools. Magnet links for v2 also support a hybrid mode to ensure support for legacy clients.
The BitTorrent protocol can be used to reduce the server and network impact of distributing large files. Rather than downloading a file from a single source server, the BitTorrent protocol allows users to join a "swarm" of hosts to upload and download from each other simultaneously. The protocol is an alternative to the older single source, multiple mirror sources technique for distributing data, and can work effectively over networks with lower bandwidth. Using the BitTorrent protocol, several basic computers, such as home computers, can replace large servers while efficiently distributing files to many recipients. This lower bandwidth usage also helps prevent large spikes in internet traffic in a given area, keeping internet speeds higher for all users in general, regardless of whether or not they use the BitTorrent protocol. The file being distributed is divided into segments called pieces. As each peer receives a new piece of the file, it becomes a source (of that piece) for other peers, relieving the original seed from having to send that piece to every computer or user wishing a copy. With BitTorrent, the task of distributing the file is shared by those who want it; it is entirely possible for the seed to send only a single copy of the file itself and eventually distribute to an unlimited number of peers. Each piece is protected by a cryptographic hash contained in the torrent descriptor. This ensures that any modification of the piece can be reliably detected, and thus prevents both accidental and malicious modifications of any of the pieces received at other nodes. If a node starts with an authentic copy of the torrent descriptor, it can verify the authenticity of the entire file it receives. Pieces are typically downloaded non-sequentially, and are rearranged into the correct order by the BitTorrent client, which monitors which pieces it needs, and which pieces it has and can upload to other peers. Pieces are of the same size throughout a single download (for example, a 10 MB file may be transmitted as ten 1 MB pieces or as forty 256 KB pieces). Due to the nature of this approach, the download of any file can be halted at any time and be resumed at a later date, without the loss of previously downloaded information, which in turn makes BitTorrent particularly useful in the transfer of larger files. This also enables the client to seek out readily available pieces and download them immediately, rather than halting the download and waiting for the next (and possibly unavailable) piece in line, which typically reduces the overall time of the download. This eventual transition from peers to seeders determines the overall "health" of the file (as determined by the number of times a file is available in its complete form). The distributed nature of BitTorrent can lead to a flood-like spreading of a file throughout many peer computer nodes. As more peers join the swarm, the likelihood of a successful download by any particular node increases. Relative to traditional Internet distribution schemes, this permits a significant reduction in the original distributor's hardware and bandwidth resource costs. Distributed downloading protocols in general provide redundancy against system problems, reduce dependence on the original distributor, and provide sources for the file which are generally transient and therefore there is no single point of failure as in one way server-client transfers. Though both ultimately transfer files over a network, a BitTorrent download differs from a one way server-client download (as is typical with an HTTP or FTP request, for example) in several fundamental ways: BitTorrent makes many small data requests over different IP connections to different machines, while server-client downloading is typically made via a single TCP connection to a single machine. BitTorrent downloads in a random or in a "rarest-first" approach that ensures high availability, while classic downloads are sequential. Taken together, these differences allow BitTorrent to achieve much lower cost to the content provider, much higher redundancy, and much greater resistance to abuse or to "flash crowds" than regular server software. However, this protection, theoretically, comes at a cost: downloads can take time to rise to full speed because it may take time for enough peer connections to be established, and it may take time for a node to receive sufficient data to become an effective uploader. This contrasts with regular downloads (such as from an HTTP server, for example) that, while more vulnerable to overload and abuse, rise to full speed very quickly, and maintain this speed throughout. In the beginning, BitTorrent's non-contiguous download methods made it harder to support "streaming playback". In 2014, the client Popcorn Time allowed for streaming of BitTorrent video files. Since then, more and more clients are offering streaming options.
Web "seeding" was implemented in 2006 as the ability of BitTorrent clients to download torrent pieces from an HTTP source in addition to the "swarm". The advantage of this feature is that a website may distribute a torrent for a particular file or batch of files and make those files available for download from that same web server; this can simplify long-term seeding and load balancing through the use of existing, cheap web hosting setups. In theory, this would make using BitTorrent almost as easy for a web publisher as creating a direct HTTP download. In addition, it would allow the "web seed" to be disabled if the swarm becomes too popular while still allowing the file to be readily available. This feature has two distinct specifications, both of which are supported by Libtorrent and the 26+ clients that use it. The first was created by John "TheSHAD0W" Hoffman, who created BitTornado. This first specification requires running a web service that serves content by info-hash and piece number, rather than filename. The other specification is created by GetRight authors and can rely on a basic HTTP download space (using byte serving). In September 2010, a new service named Burnbit was launched which generates a torrent from any URL using webseeding. There are server-side solutions that provide initial seeding of the file from the web server via standard BitTorrent protocol and when the number of external seeders reach a limit, they stop serving the file from the original source.
A technique called broadcatching combines RSS feeds with the BitTorrent protocol to create a content delivery system, further simplifying and automating content distribution. Steve Gillmor explained the concept in a column for Ziff-Davis in December 2003. The discussion spread quickly among bloggers (Ernest Miller, Chris Pirillo, etc.). In an article entitled Broadcatching with BitTorrent, Scott Raymond explained: I want RSS feeds of BitTorrent files. A script would periodically check the feed for new items, and use them to start the download. Then, I could find a trusted publisher of an Alias RSS feed, and "subscribe" to all new episodes of the show, which would then start downloading automatically – like the "season pass" feature of the TiVo. The RSS feed will track the content, while BitTorrent ensures content integrity with cryptographic hashing of all data, so feed subscribers will receive uncorrupted content. One of the first and popular software clients (free and open source) for broadcatching is Miro. Other free software clients such as PenguinTV and KatchTV are also now supporting broadcatching. The BitTorrent web-service MoveDigital added the ability to make torrents available to any web application capable of parsing XML through its standard REST-based interface in 2006, though this has since been discontinued. Additionally, Torrenthut is developing a similar torrent API that will provide the same features, and help bring the torrent community to Web 2.0 standards. Alongside this release is a first PHP application built using the API called PEP, which will parse any Really Simple Syndication (RSS 2.0) feed and automatically create and seed a torrent for each enclosure found in that feed.
Since BitTorrent makes up a large proportion of total traffic, some ISPs have chosen to "throttle" (slow down) BitTorrent transfers. For this reason, methods have been developed to disguise BitTorrent traffic in an attempt to thwart these efforts. Protocol header encrypt (PHE) and Message stream encryption/Protocol encryption (MSE/PE) are features of some BitTorrent clients that attempt to make BitTorrent hard to detect and throttle. As of November 2015, Vuze, BitComet, KTorrent, Transmission, Deluge, µTorrent, MooPolice, Halite, qBittorrent, rTorrent, and the latest official BitTorrent client (v6) support MSE/PE encryption. In August 2007, Comcast was preventing BitTorrent seeding by monitoring and interfering with the communication between peers. Protection against these efforts is provided by proxying the client-tracker traffic via an encrypted tunnel to a point outside of the Comcast network. In 2008, Comcast called a "truce" with BitTorrent, Inc. with the intention of shaping traffic in a protocol-agnostic manner. Questions about the ethics and legality of Comcast's behavior have led to renewed debate about net neutrality in the United States. In general, although encryption can make it difficult to determine what is being shared, BitTorrent is vulnerable to traffic analysis. Thus, even with MSE/PE, it may be possible for an ISP to recognize BitTorrent and also to determine that a system is no longer downloading but only uploading data, and terminate its connection by injecting TCP RST (reset flag) packets.
Poorly implemented clients may contact multiple trackers, leading to more overhead-traffic. Torrents from closed trackers suddenly become downloadable by non-members, as they can connect to a seed via an open tracker. The BitTorrent specification is free to use and many clients are open source, so BitTorrent clients have been created for all common operating systems using a variety of programming languages. The official BitTorrent client, µTorrent, qBittorrent, Transmission, Vuze, and BitComet are some of the most popular clients. Some BitTorrent implementations such as MLDonkey and Torrentflux are designed to run as servers. For example, this can be used to centralize file sharing on a single dedicated server which users share access to on the network. Server-oriented BitTorrent implementations can also be hosted by hosting providers at co-located facilities with high bandwidth Internet connectivity (e.g., a datacenter) which can provide dramatic speed benefits over using BitTorrent from a regular home broadband connection. Services such as ImageShack can download files on BitTorrent for the user, allowing them to download the entire file by HTTP once it is finished. The Opera web browser supports BitTorrent natively. Brave web browser ships with an extension which supports WebTorrent, a BitTorrent-like protocol based on WebRTC instead of UDP and TCP. BitLet allowed users to download Torrents directly from their browser using a Java applet (until browsers removed support for Java applets). An increasing number of hardware devices are being made to support BitTorrent. These include routers and NAS devices containing BitTorrent-capable firmware like OpenWrt. Proprietary versions of the protocol which implement DRM, encryption, and authentication are found within managed clients such as Pando.
Although the protocol itself is legal, problems stem from using the protocol to traffic copyright infringing works, since BitTorrent is often used to download otherwise paid content, such as movies and video games. There has been much controversy over the use of BitTorrent trackers. BitTorrent metafiles themselves do not store file contents. Whether the publishers of BitTorrent metafiles violate copyrights by linking to copyrighted works without the authorization of copyright holders is controversial.
Various jurisdictions have pursued legal action against websites that host BitTorrent trackers. As a result, the use of BitTorrent may sometimes be limited by ISPs due to legal or copyright grounds. Users may choose to run seedboxes or virtual private networks (VPNs) to circumvent these restrictions. High-profile examples include the closing of Suprnova.org, TorrentSpy, LokiTorrent, BTJunkie, Mininova, Oink's Pink Palace and What.cd. BitTorrent search engine The Pirate Bay torrent website, formed by a Swedish group, is noted for the "legal" section of its website in which letters and replies on the subject of alleged copyright infringements are publicly displayed. On 31 May 2006, The Pirate Bay's servers in Sweden were raided by Swedish police on allegations by the MPAA of copyright infringement; however, the tracker was up and running again three days later.
In the study used to value NBC Universal in its merger with Comcast, Envisional examined the 10,000 torrent swarms managed by PublicBT which had the most active downloaders. After excluding pornographic and unidentifiable content, it was found that only one swarm offered legitimate content. In the United States, more than 200,000 lawsuits have been filed for copyright infringement on BitTorrent since 2010. In the United Kingdom, on 30 April 2012, the High Court of Justice ordered five ISPs to block The Pirate Bay. In June 2025, the court ruled partially in favor of Meta for the class-action lawsuit Kasey et al v. Meta Platforms, Inc. regarding the use of copyrighted works for training AI under fair use. However, Meta's alleged use of BitTorrent both to download and seed pirated copyrighted content remains a live issue in both this case and the Strike 3 Holdings, LLC v. Meta Platforms, Inc. lawsuit filed in July 2025. In March 2026 Meta argued that BitTorrent was essential for the fair use training of its LLM, thus their alleged uploading of content as a part of using BitTorrent should also be considered fair use. As of May 2026, no known decision has been made by the court regarding this defense.
A Python-based file integrity monitoring system that uses SHA-256 hashing to detect unauthorized or unexpected changes in protected files. During an integrity check or continuous monitoring session, the current file hashes are compared with the baseline. This project demonstrates the basic principles of file integrity monitoring and can be used as a learning project for understanding file security, cryptographic hashing, and security event detection.
3. Software Implementation, Frameworks & Protocols The GUI allows you to create a baseline, check file integrity, start or stop continuous monitoring, and view security reports. The continuous monitor checks the protected files periodically and records detected security events. A Python-based file integrity monitoring system using SHA-256 hashing to detect new, modified, and deleted files.
A beginner-friendly cybersecurity project that detects unauthorized changes to critical files using SHA-256 cryptographic hashing. File Integrity Monitoring (FIM) is a defensive security mechanism used to detect changes to important files. This project creates a trusted baseline by calculating the SHA-256 hash of monitored files. During subsequent integrity checks, the current hash of each file is compared with its baseline hash.
A Python-based File Integrity Monitoring system using SHA-256 hashing to detect modified, deleted, and newly introduced files. You just downloaded a Linux ISO, a firmware update, or a release binary from GitHub. The SHA-256 checksum is sitting right there on the download page. You glance at it, think “I should probably check that,” and then… don’t. We’ve all done it. But knowing how to verify file integrity with a hash checksum is the difference between running verified software and running whatever your network happened to deliver.
With YouTube rolling out AI-generated content labels and LLMs disagreeing on basic facts, the question “is this thing what it claims to be?” has never been more relevant. Hashing won’t tell you if content was AI-generated — but it will tell you, with mathematical certainty, whether a file has been tampered with in transit. This guide walks through the complete verification workflow: from understanding what a checksum proves, to actually checking one on every major platform, to knowing when hashing alone isn’t enough.
File integrity verification answers one question: is this file identical to the file the author published? A cryptographic hash function takes any input — a 4KB config file or a 6GB ISO — and produces a fixed-length fingerprint. SHA-256 always outputs 64 hexadecimal characters. Change a single bit in the input, and the output changes completely. When a software author publishes a checksum alongside a download, they’re saying: “If you hash this file and get the same value, you have exactly what I uploaded.” If the values don’t match, something changed — corruption during download, a CDN serving stale cache, or an attacker substituting a modified binary.
The gap: GitHub release binaries, direct downloads from project websites, and anything shared outside a package manager. That’s where manual verification matters. If you’d rather not open a terminal, you can hash files directly in your browser using the Web Crypto API. The file never leaves your machine — it’s processed entirely client-side using crypto.subtle.digest() .
Try it yourself with our Hash Generator — drag a file in and get SHA-256, SHA-512, or MD5 instantly. Don’t eyeball it. A 64-character hex string is easy to misjudge visually. Use programmatic comparison: If diff produces no output, the hashes match. Any output means mismatch — don’t run the file. Let’s walk through verifying a real download. Here’s the pattern most open-source projects follow: The --ignore-missing flag is useful when the checksums file lists all platform builds but you only downloaded one.
Here’s the uncomfortable truth: a checksum only proves the file matches the published hash. It doesn’t prove the hash itself is legitimate. If an attacker compromises the download page, they can replace both the binary and the checksum simultaneously. You’d verify a tampered file against a tampered hash and get a “match.” 4. Practical Deployment, Analysis & Case Studies For most developer workflows — downloading a CLI tool, verifying a package — hash + HTTPS is sufficient. The checksum catches corruption and CDN issues. HTTPS ensures you’re reading the real checksum from the real server.
For operating system images and security-critical software, verify the GPG signature on the checksums file too: If the project only provides MD5, that’s a yellow flag — it protects against accidental corruption but not intentional tampering. Prefer SHA-256 or SHA-512 when available. For CI/CD pipelines, most download steps should include checksum verification. If you’re fetching binaries in a Dockerfile or GitHub Action, pin both the version and the expected hash.
Most developers should operate at level 2 (hash verification) by default, stepping up to level 3 for security-sensitive software. Level 4 is for the paranoid — and sometimes, being paranoid is appropriate. The tools are already on your machine. sha256sum (Linux), shasum (macOS), and Get-FileHash (Windows) are all built in. For browser-based verification without installing anything, our Hash Generator processes files entirely client-side — your data never leaves your browser.
The next time you download a binary with a checksum sitting right there on the page, take the 10 seconds to verify it. Future you — the one who didn’t run a compromised binary — will be grateful. Verifying a file's integrity means hashing the downloaded file locally with SHA-256 and comparing the resulting 64-character hexadecimal digest against the publisher's official published checksum. If even a single bit was tampered with by malware or corrupted by network packet loss, the hashes will fail to match, warning you before you execute the software.
Never run critical downloaded binaries without verification. Publishers post official SHA-256 checksums alongside their software. Running a quick terminal command ( shasum -a 256 filename on macOS/Linux or Get-FileHash on Windows) proves whether the binary in your downloads folder is byte-for-byte identical to the original release. Imagine receiving a high-security shipping crate containing critical aircraft parts. Rather than dismantling all 5,000 internal precision gears to ensure no one tampered with the crate in transit, the factory placed a serialized, holographic tamper-evident tape across all box seams.
The factory publishes that exact serial code on their corporate security board. When the crate arrives at your hangar, you verify that the holographic tape is intact and matches the serial number. If an eavesdropper cut the tape or substituted a counterfeit part, the seal fractures visibly. A SHA-256 checksum is an unforgeable digital holographic seal: altering even one byte out of ten billion bits irreversibly fractures the hash into an entirely different 64-character string.
This is the authentic published release hash from Canonical for the official Ubuntu 24.04 Noble Numbat LTS desktop installation media: If an attacker intercepted your download and inserted a keylogger into the kernel, the resulting hash would change entirely. Checking this hash takes 4 seconds and protects your entire machine.
Reality: HTTPS only guarantees that the file was encrypted between your computer and the download server. If the server itself, a regional download mirror, or a third-party CDN is breached (as occurred during the Linux Mint incident in 2016), HTTPS cheerfully delivers a backdoored ISO with a valid green padlock. Reality: Skimming only the beginning or end of a hash leaves you vulnerable to chosen-prefix attacks or lazy visual spoofing.
Always compare the full 64 characters or let the shell compare them automatically ( echo "$EXPECTED $FILE" | sha256sum -c ). Reality: CRC32 is not a cryptographic hash; it is an error-detecting code designed solely for accidental line noise. MD5 was mathematically broken for collisions in 2004. Attackers can easily craft a malicious executable that produces the identical MD5 or CRC32 checksum as a clean binary. Only SHA-256 or SHA-512 are cryptographically secure against intentional modification.
What if an attacker hacks the main website and changes both the download link and the published SHA-256 hash? Defense-in-depth requires signed checksum files : Proves cryptographically that the list of checksums was created by the publisher's offline master PGP key. Proves that the multi-gigabyte ISO you downloaded matches the signed checksum byte-for-byte.
A Python-based File Integrity Monitor (FIM) that uses SHA-256 hashing to detect unauthorised changes to files — just like enterprise tools Tripwire and AIDE. Supports both snapshot-based scanning and real-time live monitoring. SHA-256 is a one-way cryptographic function. Even a single character change produces a totally different hash — making tampering immediately detectable.
This tool is for educational and defensive use only . Use it to monitor directories you own or have permission to monitor. 5. Performance Evaluation & Extended Technical Observations Hash algorithms are mathematical functions that map input data of arbitrary length to fixed-length output values, commonly used for file integrity checking. In this context, the algorithm takes a file as input and generates a unique digital fingerprint, known as a checksum. For instance, MD5 produces a 128-bit (16-byte) hash value, while SHA-256 generates a 256-bit (32-byte) hash value. This process does not involve encryption, as theoretically, an infinite number of inputs can yield the same hash, although collisions are extremely rare in practice. The primary role of a checksum is to detect accidental modifications during file transmission or storage by verifying if the hash values of the original and received files match.
In terms of computational efficiency, MD5 is generally faster than SHA-256. Based on performance benchmarks, SHA-256 operates at approximately 40% the speed of MD5, meaning MD5 can significantly reduce time overhead when processing large volumes of files. For example, in a backup program where time is not critical, MD5's speed may make it a more suitable choice. However, this speed difference stems from algorithmic complexity: SHA-256 employs more intricate operations to enhance security, whereas MD5 optimizes for speed at the cost of certain security properties. From a resource consumption perspective, MD5's 128-bit output is more compact than SHA-256's 256-bit output, offering slight advantages in storing numerous hash values, though this is often negligible for modern storage systems.
Although MD5 is considered obsolete in cryptographic security, it retains practical value in pure file integrity checking scenarios. MD5 does generate a checksum, a standard technique for verifying data integrity. In non-security-sensitive applications, such as backup software or file synchronization tools, MD5's low collision rate is sufficient for most needs. Collisions occur when two different inputs produce the same hash value; for MD5, while there are known constructive attacks, natural collisions are exceedingly rare in random file checking. Thus, if the primary goal is to detect non-malicious modifications (e.g., transmission errors), MD5 is a viable option. However, in highly sensitive or adversarial environments, MD5's vulnerabilities could be exploited, warranting preference for more secure algorithms.
Beyond SHA-256 and MD5, other algorithms are designed specifically for high-speed file hashing, such as Murmur and XXHash. These are not cryptographic hashes and do not meet strict security requirements (e.g., randomness), but they offer low collision rates and extremely fast computation for large messages. They are suitable for scenarios requiring efficient integrity checks, like image deduplication systems where identical user-uploaded files can be uniquely identified to avoid duplicate storage. Compared to MD5, these algorithms may provide superior speed while maintaining acceptable collision rates. When selecting an algorithm, assess specific needs: if speed is critical and security is not a primary concern, Murmur or XXHash might be better choices; conversely, if both security and integrity are needed, SHA-256 is more appropriate.
Reference resources, such as technical Q&A sites, offer detailed comparisons to aid decision-making. In practical applications, algorithm selection requires balancing multiple factors. For backup programs, if the checking process does not impede core operations and file volumes are large, MD5's speed can enhance efficiency; but if backups involve sensitive data, even with low collision risks, using SHA-256 adds an extra security layer. For general file integrity checking, MD5 is often adequate, but it is advisable to periodically evaluate if the algorithm still meets needs, especially in evolving security environments. Additionally, implementations should ensure proper integration of hash calculations to avoid common errors, such as mishandling file boundaries. In code examples, computing a file hash with MD5 might involve reading a file stream and applying the algorithm, while SHA-256 implementation is similar but more complex. In summary, best practices involve weighing speed, collision probability, and security based on specific contexts, consulting up-to-date technical guidelines as necessary to maintain solution effectiveness.
Copyright Notice: All rights in this article are reserved by the operators of DevGex. Reasonable sharing and citation are welcome; any reproduction, excerpting, or re-publication without prior permission is prohibited. A Python-based file integrity monitoring tool that detects unauthorized file system changes using SHA-256 cryptographic hashing. This is a lightweight implementation inspired by enterprise-grade tools like OSSEC and Tripwire, designed for security monitoring and incident detection.
File integrity monitoring is a critical security control recommended by frameworks such as PCI DSS, NIST 800-53, and CIS Controls. The process works in two phases: Baseline Generation - The tool scans designated directories, computes a SHA-256 cryptographic hash for every file, and records metadata (size, permissions, modification time). This snapshot represents the known-good state.
Integrity Checking - On subsequent runs, the tool re-scans the same directories and compares each file against the stored baseline. Any discrepancy - whether a changed hash, a new file, a missing file, or altered permissions - triggers an alert. Because SHA-256 is a one-way cryptographic hash function, even a single-byte change in a file produces a completely different hash value. This makes it virtually impossible for an attacker to modify a file without detection.
Sean Ibeziako is a cybersecurity student with a 3.8 GPA, currently pursuing CompTIA A+ and Security+ certifications. With hands-on IT support experience and a passion for defensive security, Sean is building practical tools and projects to prepare for a career as a SOC analyst. This File Integrity Monitor demonstrates core security monitoring concepts used in real-world enterprise environments.
Python-based file integrity monitoring tool using SHA-256 cryptographic hashing - detects unauthorized file modifications, additions, deletions, and permission changes A Python-based File Integrity Monitoring (FIM) tool that detects unauthorized modifications to files using SHA-256 cryptographic hashing . The tool establishes a trusted baseline for files and compares future scans against it to identify potential tampering.
This project was developed as a cybersecurity project to demonstrate the concepts of file integrity monitoring, cryptographic hashing, and log file tampering detection . This project is intended for educational purposes and demonstrates the principles of File Integrity Monitoring (FIM). It is not intended to replace enterprise-grade security monitoring solutions.
This project idea was inspired from https://roadmap.sh/projects/file-integrity-checker , where along with their requirements, I have added many more features in this FIM.
Python-based File Integrity Monitoring (FIM) tool using SHA-256 hashing to detect file tampering. This study investigates cryptographic methods to ensure data integrity within cloud environments, with a particular focus on comparing the security, performance, and efficiency of MD5 and SHA-256 hash algorithms. Data integrity is critical for protecting sensitive information, especially in sectors like healthcare, where cloud storage solutions are increasingly prevalent.
Through a theoretical analysis, the study evaluates the advantages and limitations of MD5 and SHA-256, emphasizing SHA-256’s stronger security capabilities in preventing collision attacks compared to MD5, albeit with higher resource consumption. The literature review draws from recent advancements in cryptography, blockchain, and artificial intelligence (AI) technologies, presenting a comprehensive view of the current landscape. Findings show that while MD5 offers faster processing times, its vulnerability to attacks renders it unsuitable for high-security applications. SHA-256, although more computationally intensive, provides robust protection against data integrity threats and is therefore recommended for applications requiring enhanced security.
The study concludes with recommendations for future research, proposing the exploration of blockchain and AI-driven solutions to further improve data integrity protocols. Additional suggestions include the development of hybrid cryptographic hash functions, systematic reevaluation of existing cryptographic techniques, and the implementation of Data Loss Prevention (DLP) systems tailored for Internet of Things (IoT) devices. These recommendations aim to address emerging cybersecurity challenges and advance the effectiveness of data integrity solutions within cloud computing and beyond.
Garcia Martinez, Haryam, "EXPLORING SECURE METHODS FOR ENSURING DATA INTEGRITY: A THEORETICAL ANALYSIS OF CRYPTOGRAPHIC AND DETECTION TECHNIQUES" (2024). Electronic Theses, Projects, and Dissertations . 2094. https://scholarworks.lib.csusb.edu/etd/2094 Cybersecurity Commons , Databases and Information Systems Commons , Information Security Commons , Other Computer Sciences Commons Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/SHA-1 • https://en.wikipedia.org/wiki/KeePass • https://en.wikipedia.org/wiki/BitTorrent • https://github.com/TriveniRN/File-Integrity-Monitor • https://github.com/surve21/File-Integrity-Monitor • https://blog.kestreltools.com/blog/file-integrity-verification-hash-checksum-guide-2026/ • https://www.hashmama.com/guides/verify-file-integrity-sha256 • https://devpost.com/software/file-integrity-monitor • https://devgex.com/en/article/00039707 • https://github.com/seanibeziako/file-integrity-monitor
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for File Integrity Monitoring System Using Sha 256 Hashing.
[*] Metasploit Scan Running on Target Subnet for File Integrity Monitoring System Using Sha 256 Hashing... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |