Complete Technical Paper Content — Flash Loan Attack Detection And Prevention In Defi
Overview & System Context
Flash Loan Attack Detection And Prevention In Defi: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9589 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background The Islamic Revolutionary Guard Corps Aerospace Force, officially known as the Islamic Revolutionary Guard Corps Air and Space Force (IRGCASF; Persian: IIIII IIIIIII IIII IIIIIIII IIIIII IIIIII, romanized: niru-ye havâfazây-e sepâh-e pâsdârân-e enghelâb-e eslâmi, acronymed in Persian as NEHSA), is the strategic missile, air, and space force of the Islamic Revolutionary Guard Corps (IRGC). It was renamed from the IRGC Air Force to the IRGC Aerospace Force in 2009. Besides operating military aircraft alongside its counterparts in the Islamic Republic of Iran Air Force, the IRGC Aerospace Force is also responsible for space warfare through its military satellite program. Most importantly, it oversees the ballistic missile program of Iran, which includes the deployment and operation of an arsenal of intermediate-range, and medium-range ballistic missiles with ranges over 2,000 kilometers, considered one of the cornerstones of the Islamic Republic's strategic deterrence and defense doctrine.
Most American public sources disagree and argue on which aircraft are operated by the AFAGIR. The Washington Institute for Near East Policy said in 2005 that "[t]he backbone of the IRGCAF consists of ten Su-25 Frogfoot attack aircraft, including seven flown from Iraq to Iran during the 1991 Gulf War, kept airworthy with the help of Georgian technicians, although reports indicate that all of the IRGCAF aircraft have been sold to Iraq in July 2014, to increase the latter's for CAS and COIN for fighting against ISIS capabilities. All of them were replaced by Su-22", all of them flown from Iraq to Iran during 1991 Gulf War, and around forty EMB-312 Tucanos". The Washington Institute said that the IRGCAF maintained thirty Y-12 and Dassault Falcon 20 light transports, as well as MFI-17 Mushshak and Super Mushshak trainers, and locally built Ababil and Mohajer reconnaissance unmanned aerial vehicles (UAVs). The AFAGIR also operates a sizable rotary-wing force consisting of around twenty Mi-171 helicopters for transport and armed assault roles, and a large transport force out of Shiraz, equipped with around fifteen ex-Iraqi Il-76s, originally operated by the IRIAF, and twelve An-74TK-200 transports. Scramble backs up this picture in general, reporting An-74s, An-14s, and Su-22 at Tehran Mehrabad, Chengdu F-7Ms at Zahedan, while saying that MFI-17s were often reported at Zahedan incorrectly, and Il-76 AEW variants at Shiraz Shahid Dastghaib International Airport, while saying that they might be based at Mehrabad. Other later writings make no mention of Il-76s. Anthony Cordesman of the Center for Strategic and International Studies, writing in August 2007, said only the AFAGIR "may operate Iran's 10 EMB-312 Tucanos", and that it "seems to operate many of Iran's 45 PC-7 training aircraft" as well as Pakistani-built training aircraft at a school near Mushshak, "but this school may be run by the regular air force". He said that reports of the Revolutionary Guards operating F-7s did not seem to be correct. Cordesman noted claims of the AFAGIR building gliders for use in unconventional warfare, saying that they would be unsuitable delivery platforms, but could at least carry a small number of weapons. However the attached reference was a 1996 Reuters report, making the sources for such assertions extremely thin. The IISS Military Balance 2007 makes no mention of aircraft, referring only to the Shahab 1, 2, and 3 missiles. In October 2009, it was announced that its name has been changed from IRGC Air Force to IRGC Aerospace Force. In February 2014, Jane's announced that the Barani missile system had been tested. This system is a laser-guided air-to-surface missile which releases submunitions: "new generation of long-range ballistic missiles carrying multiple re-entry vehicle MIRV payloads". The UN Panel of Experts identified it as a variant of the Shahab (Ghadr 1) and questioned its alleged multiple re-entry vehicle capability, suggesting instead that it carried sub-munitions. The Bina missile, which can be carried aloft and is able to be ground-launched from a rail car, was also revealed at the time.
The IRGC Aerospace Force is responsible for the operation of Iran's surface-to-surface (SSM) missile systems. In 2006 it was mentioned by John Negroponte that Iran held the largest inventory of ballistic missiles in the Middle East. In August 2013, Ahmad Vahidi former defense minister of Iran said that his country was ranked sixth in the world in missile production. It is claimed to operate several thousand short- and medium-range mobile ballistic missiles, including the Shahab-3/3B with a range of up to 2,100 kilometers, which is the mainstay of Iran's strategic deterrent. This puts even NATO members Turkey, Greece, Bulgaria and Romania within striking range, if fired from Western Iran. If Iran ever produces nuclear weapons, they fall under the direct supervision of the Aerospace Force. Iran says that it has no intention of producing nuclear weapons.
However, there is evidence which points otherwise. A stolen Iranian laptop, containing over 1000 pages of calculations, simulations and modifications required to make the Shahab-3 nose cone capable of carrying a nuclear warhead, was obtained by U.S. intelligence in 2004 and shown to IAEA officials. Additionally, an interview with Alireza Assar, an Iranian physicist formerly tied with the Iranian ministry of defense, revealed the existence of a military nuclear program whose goal was "to produce enough HEU (Highly Enriched Uranium) to enable the regime to produce nuclear weapons". Iran's continuous lack of transparency regarding their nuclear program has resulted in much suspicion regarding its intentions. According to the testimony of John Negroponte in 2006, Iran's ballistic missile development, together with its enhancement of the navy is largely for the projection of its military power, with the goal of dominating the Gulf region and maintaining its ability to deter and retaliate against adversaries, including the United States. Additional reasons for the indigenous development of missiles may include the regime's intent to showcase its technological advancements, to intimidate and deter neighboring countries, and to reduce its reliance on precarious foreign supplies, particularly from North Korea. The independent production of missiles in Iran can be traced back to at least 1997, when the country obtained missile plans and production components from Russia and began constructing missile production facilities, including the two tunnels for housing Scud missiles at Kuh-e-Padri, located along the Persian Gulf between Bandar Abbas and Bushehr. Additionally, Iran received assistance from China in the construction of a ballistic missile plant and test range east of Tehran, a production facility near Semnan, and the acquisition guidance technology and precision machine tools. Iran's largest missile production facility, the complex near Isfahan, was built with North Korean and potentially Chinese assistance as the main assembly site for Scud-B missile kits from North Korea. In May 2013, Iran's Ministry of Defense and Logistics delivered a massive number of missile TELs to IRGC AF, "Iranian television footage showed at least 26 TELs lined up in two rows for the event, which marked their purported delivery to the Islamic Revolution Guards Corps (IRGC) Aerospace Force, which operates the country's ballistic missiles", according to the report by IHS Jane's. Any Iranian long-range intermediate-range ballistic missile or intercontinental ballistic missile would require an extraordinarily effective guidance system and level of reliability to have any real lethality with conventional warheads, even if it could be equipped with a functional GPS guidance platform. It would probably require nuclear warheads in order to compensate for critical problems in accuracy, reliability, and warhead lethality. In June 2020, Iranian admiral Hossein Khanzadi said that Iran would start producing indigenous supersonic cruise missiles equipped with turbofan engines soon.
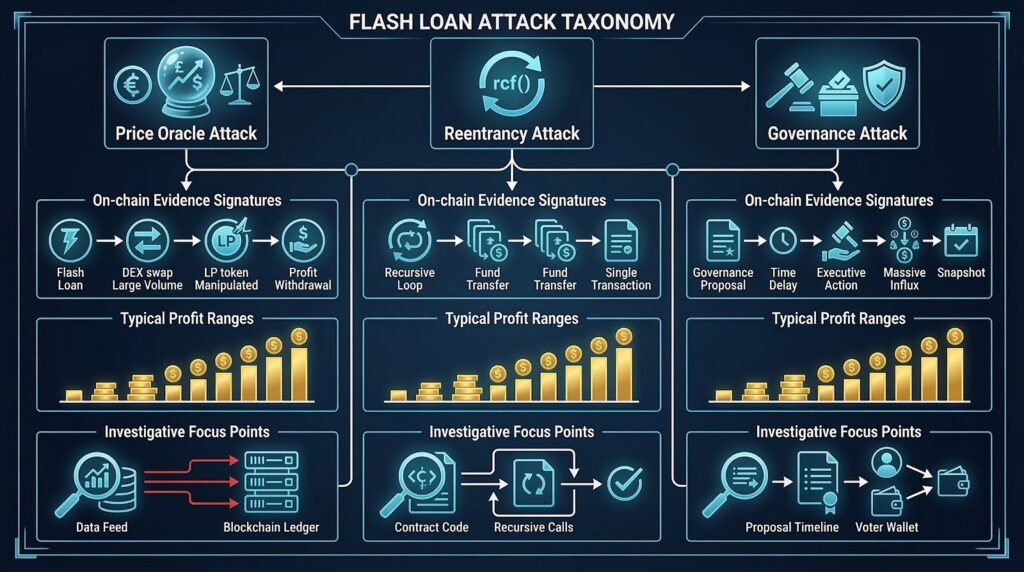
Bina is a laser guided dual-capability short-range surface-to-surface and air-to-surface missile. It appears to be an AGM-65 Maverick air-to-ground missile with a semi-active laser (SAL) seeker fitted to its nose. Brigadier General Hossein Dehqan said the ballistic missile had radar-evading capabilities. "The new generation of long-range ground-to-ground ballistic missile with a fragmentation warhead and the laser-guided air-to-surface and surface-to-surface missile dubbed Bina (Insightful) have been successfully test-fired. The Bina missile is capable of striking important targets such as bridges, tanks and enemy command centres with great precision." Figure 1: Flash Loan Attack Analysis: On-Chain Investigation of DeFi Exploits ...
After the war, Iran's experience of liquid fuel missiles had purely focused on the reverse engineering of Scud-B missiles. However, with the post war reorganisation the focus of the effort quickly changed and focused on assembly and maintenance. A domestic version of the Scud-B, known as Shahab-1, was developed and manufactured. This led to its successor the Shahab-2, a variant of the Scud-C with a range of 500 to 700 km, and finally the Shahab-3. Since the end of the war, Iran has consistently attempted to recruit foreign help, as well as its expatriate population, into its missile program. Iranian expatriates who left with the revolution have been slow to return, but many are now doing so and thus heralding a new age for Iran's missile development programme.
The Fajr-3 is currently Iran's most advanced ballistic missile. It is a domestically developed liquid fuel missile with an unknown range. The Iranian government says it has multiple independently targeted reentry vehicles (MIRV) capabilities. Its MIRV capability may give it the ability of avoiding anti-missile surface-to-air missiles (SAMs). The missile was last launched during Holy Prophet wargames, which was the IRGC's largest naval war games ever. The Fajr-3 and the Fajr-3 artillery rocket are different systems.
The Shahab-3 is a medium-range ballistic missile (MRBM) that was built by Iran's military. Its first model, also known as Shahab-3A has a range of 1,300 km (810 mi). Soon after Iran came with a new model called Shahab-3B, which has a range of 2,000 km (1,200 mi), and can carry a heavier warhead. Making this missile was a major step in Iran's missile industry, and it opened the way to longer-range missiles. Shahab-3D, which followed the Shahab-3C, is Iran's latest Shahab model. A 2,000-kilometre (1,200 mi) range including Russia (as far as Moscow), Ukraine, parts of Hungary, Serbia, Greece, Egypt, Arabia, parts of India and China, as well as countries closer to Iran. Jane's Information Group said in 2006 that Iran had six operational Shahab-3 brigades, the first of which was established in July 2003. They said that the six brigades were mainly equipped with standard variants, but with others described as enhanced Shahab-3 variants, with ranges of 1,300, 1,500, and 2,000 km (810, 930, and 1,240 mi), respectively. Anthony Cordesman at the Center for Strategic and International Studies however said only in August 2007 that 'the air force of the IRGC is believed to operate Iran's three Shahab-3 intermediate-range ballistic missiles units' while noting that their actual operational status remains uncertain.
The Ghadr-110 is a medium-range ballistic missile designed and developed by Iran. The missile has a range of 1,800 to 2,000 kilometres (1,200 mi) and as such is the Iranian missile with the longest range. It is believed to be an improved version of the Shahab-3, also known as the Ghadr-101. It has a liquid-fuel first stage and a solid-fuel second stage, which allows it to have a range of 2,000 km. It has a higher maneuverability than the Shahab-3 and a setup time of 30 minutes which is shorter than that of the Shahab-3.
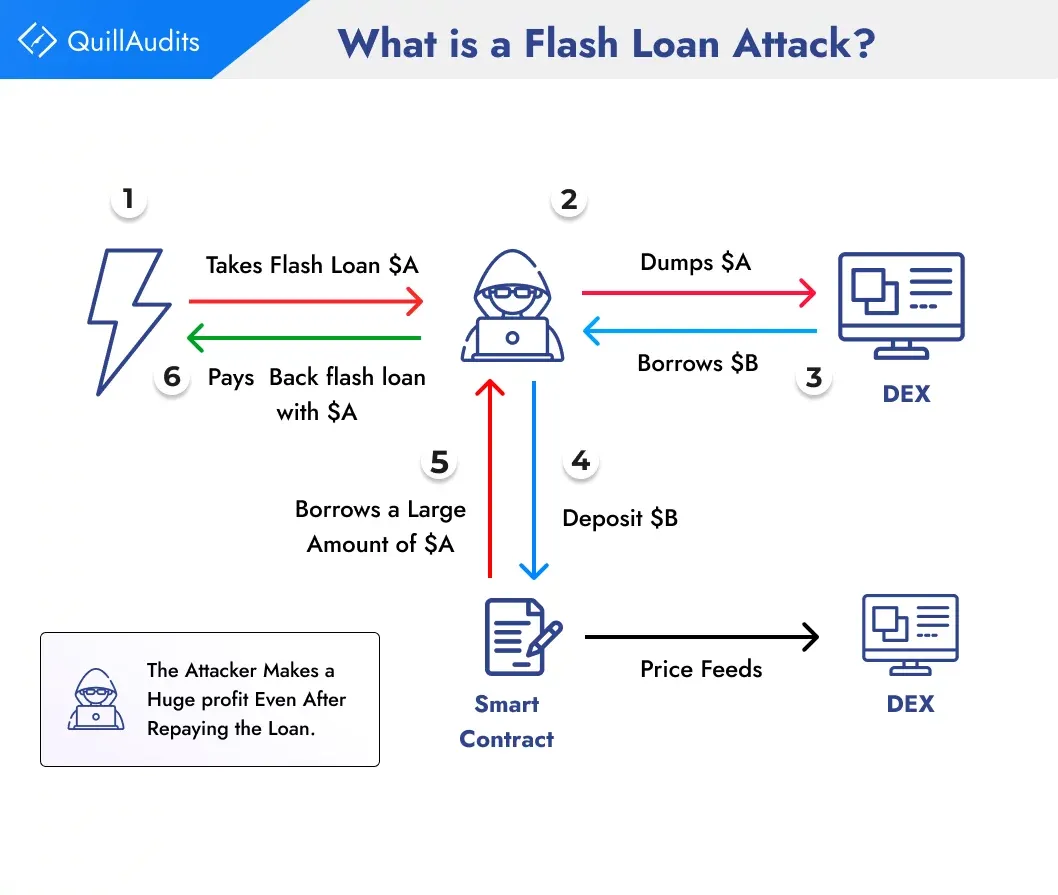
Figure 2: Smart Contract Vulnerabilities, Risks and How to mitigate them In November 2007, Iranian Defence Minister Mostafa Mohammad-Najjar announced that Iran had built a new missile with a range of 2,000 km (1,200 mi), the Ashoura missile. He did not say how the missile differed from the Shahab-3, which has a range of 2,100 km (1,300 mi). He told the gathering Basij militia during the manoeuvers they were holding that same week that the "construction of the Ashoura missile, with the range of 2,000 km (1,200 mi), is among the accomplishments of the Defence Ministry". According to Jane's Defence Weekly, the Ashoura represents a major breakthrough in Iranian missile technology. It is the first two-stage MRBM using solid-fueled rocket motors instead of the existing liquid-fueled technology used on the Shahab. This would dramatically reduce the setup and deployment time for the missile and hence, shorten the amount of warning time for the enemy. Jane's noted that while the development parallels Pakistan's Shaheen-II MRBM there is no evidence to suggest there had been any prior technology exchange or with its other known technology partners such as North Korea or China.
The new two-stage solid-fuel missile has a range of nearly 2,500 km (1,600 mi), it was tested in November 2008. An improved version, the Sejjil-2, was tested in May 2009. Improvements include better navigation system, better targeting system, more payload, longer range, faster lift-off, longer storage time, quicker launch, and lower detection possibilities. On October 10, 2015, Iran launched a new missile, the Emad. The Emad is capable of delivering a nuclear weapon and has a range of 1,700 km (c. 1,000 miles), enough to reach all of Israel and Saudi Arabia. It is considered to represent a great advance in accuracy, with a guidance and control system in its nose cone that functions during reentry into the atmosphere.
As a consequence of Iran's nuclear deal (JCPOA), on 20 July 2015 the United Nations Security Council Resolution 2231 was endorsed, replacing the Resolution 1929, which "called upon" Iran "not to undertake any activity related to ballistic missiles designed to be capable of delivering nuclear weapons". It has been argued that the language is not a legal prohibition. The U.S. ambassador to the UN Samantha Power said that the Emad missile was inherently capable of delivering a nuclear warhead which is therefore a violation. However, Vitaly Churkin, Russia's ambassador disputed this interpretation: "a call is different from a ban, so legally you cannot violate a call, you can comply with a call or you can ignore the call, but you cannot violate a call". Iran's foreign minister, Javad Zarif, responded by saying that since Iran does not possess nuclear weapons nor does it ever intends in having one, it does not design its missiles (Emad) to be capable of carrying something it does not have.
Nevertheless, the testing of the Emad missile took place before the adoption of the Resolution 2231. The US, France, Britain, Germany, Sweden, Turkey, and Australia asked the UN Security Council to investigate and take appropriate action. The Khorramshahr (Persian: IIIIII), named after the city of Khorramshahr in Iran, is a medium-range ballistic missile that was tested by Iran in January 2017. With a range between 1,000 and 2,000 km, it can carry a 1,800 kg warhead and is 13 m in length.
Figure 3: Flash Loan Attack Detection Engine | Chainscore Labs The Hoveyzeh Cruise Missile is an all-weather, surface-to-surface cruise missile. The Hoveyzeh is from the Soumar family of cruise missiles. The missile was unveiled and put on display on February 2, 2019, at an exhibition of defense achievements in Tehran during commemorations of the 40th anniversary of the 1979 Iranian Revolution. The surface-to-surface cruise missile is capable of low altitude flight and has a range of 1,350 km (840 mi), a maximum range has not yet been given. It has the ability to strike ground targets with high precision and accuracy. Its motor utilizes a turbojet, it releases low heat signatures and the missile is equipped to deal with the most sophisticated types of electronic warfare. Discussing the capabilities of the missile, the Israeli military intelligence website DEBKAfile states that there is "no military force in the world has so far found an effective means of intercepting cruise missiles before they strike, unless they are short range". The missile is essentially immune to any sort of radar and missile defense systems.
Dezful (Persian: IIIII) is a medium range ballistic missile (MRBM) developed by Iran and unveiled in February 2019 in an underground missile factory. The Iranian armed forces said that the missile has a range of over 1,000 kilometers (620 miles). It carries a 600 or 700 kg warhead and has a CEP (circular error of probability) of 5 meters. The missile can attain the speed of Mach 7 (8,643 km/h). Brigadier General Amir Ali Hajizadeh said this is an upgrade on the older Zolfaghar model, that had a range of 700 kilometers.
Raad-500 missile is an Iranian SRBM/Tactical ballistic missile which is equipped with a progressive composite engine that is dubbed as "Zohair (Persian: IIII)". Raad-500 means "Thunder 500", and it was designed by halving the weight of the previous Iranian missile (Fateh-110) whose body was made from metal; whereas the range of this new Iranian ballistic missile increased two hundred kilometers more than Fateh-110), and its final range is 500 kilometers.
Martyr Haj Qasem (Persian: IIII IIIIIII IIII III IIII) is an Iranian ballistic missile which was unveiled in August 2020. It is named after the Iranian commander Qasem Soleimani, who was assassinated by the US in January 2020. Haj-Qasem's range is claimed by the Iranian military to be 1,400 kilometres (870 mi) with a claimed warhead weight of 500 kilograms (1,100 lb).
The Qassem Bassir missile is an Iranian medium-range ballistic missile (MRBM) unveiled in May 2025. With a solid-fueled, two-stage system, it is presented as an improved variant of Iran's Haj Qassem series, named after Quds Force commander Qassem Soleimani. Iranian officials state the Qassem Bassir has a range of about 1,200 km, and features enhanced guidance and countermeasure resistance. Iran claims the Qassem Bassir missile can penetrate advanced missile defenses, and can strike selected targets (e.g. runways, aircraft hangars) with "pinpoint" accuracy without GPS, though western analysts have cast doubt on these claims which are likely tinted with internal propaganda.
Medium-range Raad/3rd Khordad Talash/15th Khordad Point-defence Misagh-1 (QW-1 Vanguard) Misagh-2 (QW-18) The IRGC Aerospace Force has been running its own space program, and on 22 April 2020, it made existence of its own 'Space Command' public. On that date it successfully launched its first military satellite, the Noor, into orbit. This was acknowledged by Western experts, and marked joining the club of about a dozen countries to have carried out such a project.
The United States Space Force's chief of space operations, General John W. Raymond, said it was unlikely that Iran's Noor satellite provided any information of value, describing it as "a tumbling webcam in space". However, an Israeli security source told Haaretz that the satellite is "indeed an important accomplishment for the Iranian space program in general and its military in particular". Uzi Rubin commented that he "wouldn't be surprised" if an Iranian system of operational military space assets was soon operational. In July 2020, the Aerospace Force said that it had received detailed images of Al Udeid Air Base in Qatar, where United States Central Command's forward headquarters is hosted, captured by the satellite. In March 2022, a second launch of the Qased launch vehicle from the Shahroud Space Center put the Noor-2 military reconnaissance satellite into orbit. Commander of the Space Command, Brigadier General Ali Jafarabadi, has stated that the reconnaissance satellite is part of a larger project that will include satellites with communication and navigation capabilities, in addition to reconnaissance. In November 2022, the IRGC conducted a successful suborbital test launch of the newly unveiled Qaem-100 launch vehicle. In September 2023, Noor-3, also called Najm, was launched on a Qassed launcher to a 450 kilometer orbit. It weighs 24 kg, with a camera image resolution of 6 to 4.8 meters. In January 2024, the Qaem 100 launch vehicle successfully performed its first orbital launch, placing the Soraya satellite into a 750 km orbit, setting a new altitude record for Iran.
Its personnel size is unknown according to the Congressional Research Service, while International Institute of Strategic Studies estimated that the military branch had 15,000 sworn members as of 2020. This guide provides a technical walkthrough for building a system to detect the preparatory and execution phases of a flash loan attack by monitoring for specific transaction patterns on-chain.
A technical walkthrough for developers to implement a monitoring system that identifies and alerts on suspicious flash loan activity on-chain. Flash loans enable uncollateralized borrowing within a single transaction block, a feature exploited in numerous high-profile DeFi attacks. Real-time detection is critical because the attack lifecycle—borrow, manipulate, repay—completes before the block is finalized. To monitor this, you need to track specific on-chain events and transaction patterns. The core components are an EVM-compatible node (like Alchemy or a self-hosted Geth), an event listener , and a logic engine to analyze the data.
This setup allows you to intercept malicious transactions as they occur, rather than analyzing them post-mortem. Beyond simple event listening, effective detection requires analyzing the full transaction trace. A flash loan attack involves a sequence of actions: the loan, a series of swaps to manipulate an oracle or pool price, and a final swap or liquidation to profit. By using a node's debug_traceTransaction RPC method, you can programmatically reconstruct the call path. Look for patterns like a large loan from a known pool ( 0x... ) followed by multiple swaps on a DEX, and finally a large transfer to a contract like MEV Bot: 0x000... . This trace analysis separates complex arbitrage from outright manipulation.
To operationalize this, implement a scoring heuristic. Assign risk points for: - Loan size exceeding 5% of the pool's liquidity - Multiple large swaps across correlated assets within the same transaction - Interactions with known, often-manipulated price oracles like Chainlink - Final profit sent to a new or non-interacted-with address. A script running this logic can then trigger an alert via a webhook to Discord, Telegram, or a security dashboard. For scalability, consider using The Graph to index historical flash loan data and establish baseline patterns for more accurate anomaly detection.
Maintaining this system requires constant updates. Attackers adapt, using new protocols or obfuscation techniques like intermediate proxy contracts. Regularly update your list of monitored lending pool addresses (from Aave, dYdX, Balancer) and DEX routers. Incorporate blockchain intelligence from platforms like Chainalysis or TRM Labs to flag addresses associated with known exploits. Open-source tools like Forta Network bots can provide a foundation, but for proprietary protection, a custom detection layer tuned to your protocol's specific liquidity pools and price feeds is essential.
Configure your environment to monitor for flash loan attacks on EVM-compatible blockchains. You must also understand the key signatures of a flash loan attack . This involves monitoring for specific patterns in transaction mempools and executed blocks, such as large, complex bundles of transactions originating from a single address. The primary indicators are: a flash loan origination from a protocol like Aave or dYdX, followed by a series of swap operations across multiple DEXs to manipulate an asset's price, and concluding with a liquidation or arbitrage action that repays the loan and captures profit, all within a single block.
For effective detection, implement listeners for critical events. Using Ethers.js, you can create a provider subscription: provider.on('pending', (txHash) => { analyzeTransaction(txHash) }) . The analyzeTransaction function should decode the transaction's input data to identify calls to known flash loan contracts and trace the flow of funds. Setting up a local database (e.g., PostgreSQL) or cache (Redis) to track suspicious address patterns and token price deviations across blocks is also recommended for historical analysis.
Finally, integrate with on-chain data sources for accuracy. Use price oracles like Chainlink to establish baseline asset values and query liquidity pool reserves from DEXs like Uniswap V3 to calculate real-time price impacts. Your detection logic should flag transactions where the calculated price slippage from a swap exceeds a defined threshold (e.g., 5-10%) immediately after a large loan is taken, as this is a strong signal of market manipulation.
Flash loan attacks exploit uncollateralized borrowing to manipulate DeFi protocols. This guide explains how to set up real-time detection for common attack patterns. 2. System Architecture & Core Working Principles Flash loans allow users to borrow large sums of assets without collateral, provided the loan is repaid within a single blockchain transaction. While a legitimate tool for arbitrage and refinancing, they are frequently weaponized. Attackers use these loans to temporarily control massive capital, enabling market manipulation, price oracle exploitation, and governance attacks. Real-time detection focuses on identifying the transaction patterns and on-chain footprints that signal malicious intent, rather than the flash loan itself.
The most common pattern is the oracle manipulation attack . Here, an attacker uses a flash loan to drain a lending protocol like Aave or Compound. The steps are: 1) Borrow a large amount of asset A via flash loan. 2) Swap asset A for asset B on a low-liquidity DEX, artificially inflating asset B's price. 3) Use the overvalued asset B as collateral to borrow more of other assets from a lending pool. 4) Repay the initial flash loan, keeping the stolen funds. Detection systems monitor for extreme price deviations on decentralized oracles and large, circular swaps within a single transaction.
Another critical pattern is the governance attack . Projects like MakerDAO or Uniswap use governance tokens for voting. An attacker can borrow a majority of tokens via flash loan, push through a malicious proposal (e.g., to drain the treasury), and vote it through—all before returning the tokens. Monitoring for sudden, large token inflows to a voting contract, followed by a proposal creation and vote within the same block, is key. Tools like Tally and OpenZeppelin Defender can be configured with custom alert rules for such events.
To build a detection system, you need to track specific smart contract events and transaction parameters . Key data points include: transaction hash, involved addresses, asset amounts, and the sequence of internal calls. Services like Chainscore, Tenderly, and Forta Network provide streams of real-time transaction data. You can write detection bots that analyze this data, looking for thresholds like swap size (>$1M), price impact (>30%), or interactions with known vulnerable contract patterns.
Here is a simplified example of a detection rule written in JavaScript for a Forta bot, looking for large swaps followed by lending pool interactions: This bot triggers an alert if a single transaction contains both a large swap and a borrow event, a hallmark of many attack patterns.
Effective monitoring requires combining automated alerts with human analysis. Set up alerts for: single-block profit (a wallet's balance change exceeding a threshold), repeated failed transactions (probing for vulnerabilities), and interaction with newly deployed contracts . Keep detection rules updated, as attackers constantly evolve their methods. Integrating with incident response platforms like OpenZeppelin Defender Sentinels or setting up Slack/Telegram webhooks ensures your team can react immediately to potential threats.
A robust detection system requires specific technical components working in concert to identify malicious transactions before they finalize. The core of any detection system is a transaction simulation engine that executes pending transactions in a sandboxed environment before they reach the mempool. This involves: Simulation results must be analyzed against a set of predefined heuristics. Key signals for flash loan attacks include: Detection systems require low-latency access to blockchain data. This is typically achieved by running or subscribing to: When an attack is detected, the system must trigger an immediate response. This layer handles: Comparison of on-chain data patterns and their effectiveness for identifying potential flash loan attacks in real-time.
The first line of defense against flash loan exploits is establishing a real-time monitoring system for large borrows. This step focuses on tracking the primary entry points for these attacks. The monitoring logic must filter for borrows that exceed a predefined threshold, which indicates potential malicious intent rather than regular usage. For example, you might set an alert for any single flash loan exceeding $1 million in value. This requires calculating the USD value of the borrowed assets using an oracle or price feed at the time of the transaction. Your detection script should decode the transaction input data to extract the amount parameter and the asset address, then cross-reference it with a real-time price from Chainlink or a similar decentralized oracle network to assess the fiat value.
Implementing this involves writing a script, often in JavaScript or Python , that connects to a node provider like Alchemy or Infura . The script uses the Web3.js or Ethers.js library to listen for new blocks, parse transaction receipts, and check for interactions with the target flash loan contracts. Here is a simplified conceptual outline: Beyond simple value thresholds, consider monitoring the destination of the borrowed funds. Flash loans for legitimate purposes (e.g., arbitrage, collateral swapping) are often repaid within the same transaction to a known DeFi protocol.
Suspicious activity may involve sending funds to a newly deployed or obscure contract. By analyzing the transaction trace, you can see if the borrowed assets are being routed through multiple protocols in a complex sequence designed to manipulate prices—a hallmark of an attack. Integrating with a tracing node or using a service like Tenderly for simulation can provide this deeper insight.
Finally, ensure your monitoring system is resilient and low-latency. Flash loan attacks are executed and completed within a single blockchain block, often in under 15 seconds. Your detection must operate at block-time speed to have any chance of providing an early warning. This requires a robust infrastructure with redundant node connections and efficient event processing logic to avoid falling behind the chain head, which would render your alerts useless for proactive defense.
To detect a flash loan attack, you must analyze the sequence of internal calls within a transaction, not just its final outcome. This step focuses on identifying the specific on-chain patterns that signal malicious intent. A flash loan attack is not a single function call but a complex, multi-step transaction. Your detection system must trace the entire call tree. Start by using an Ethereum node's debug_traceTransaction RPC method or a service like Alchemy's Trace API . This returns a detailed log of every CALL , DELEGATECALL , STATICCALL , and CREATE operation, along with their inputs, outputs, and gas usage. This trace is your primary data source for identifying attack vectors like price manipulation, collateral swapping, or governance exploits.
Within the trace, search for the hallmark pattern: a large, uncollateralized loan followed by a series of state-changing operations, and finally, loan repayment—all within one block. Key indicators include: a call to a lending pool (e.g., Aave's flashLoan or dYdX's operate ), subsequent swaps on a DEX that could manipulate a price oracle, and a final call to repay the loan. The profit is often extracted via an arbitrage swap or by liquidating undercollateralized positions created by the manipulated prices.
For accurate detection, implement logic to calculate the profit delta . Compare the attacker's token balances before the first call and after the final call in the trace. A significant positive delta, especially when combined with the loan pattern, is a strong signal. Use libraries like ethers.js or web3.py to decode the input data for each call, parsing function selectors and arguments to understand the exact operations performed, such as which pools were targeted and which price oracles were affected.
Optimize your tracer for real-time use. Processing full traces for every pending transaction is computationally expensive. Implement a filtering layer that first screens for high-value transactions or interactions with known DeFi protocol addresses before initiating a full trace. Services like Tenderly or OpenZeppelin Defender can help streamline this process by providing webhook-based alerts for specific trace patterns, allowing you to focus your custom analysis on high-risk candidates.
This section details the core detection logic for identifying profitable arbitrage opportunities from flash loan transactions. The detection process begins by filtering for successful flash loan transactions. We analyze the transaction's internal call trace, focusing on the sequence of operations after the loan is taken and before it is repaid. The key is to identify a profitable delta between the starting and ending balance of a specific token, typically a stablecoin like DAI or USDC, within the same transaction. This delta represents the arbitrage profit extracted by the attacker's contract before the flash loan is repaid. Tools like Tenderly's debugger or the debug_traceTransaction RPC method are essential for this deep transaction inspection.
A profitable pattern often follows this structure: 1) Borrow asset X via flash loan, 2) Swap X for asset Y on DEX A, 3) Swap Y back for X on DEX B, 4) Repay the flash loan of X, 5) Keep the surplus X as profit. Your detection script must calculate the net change in the balance of the borrowed asset held by the attacker's contract. This is done by tracking balanceOf calls for the contract address at the start and end of the traced execution, accounting for the repayment. A positive net change after repayment confirms profit extraction.
In reality, you must parse the low-level call trace to find these balance snapshots, as the initial balance is often zero. Beyond simple DEX arbitrage, be aware of complex strategies involving multiple protocols. An attacker might use a flash loan to: manipulate an oracle price on a lending platform to enable an undercollateralized borrow, perform a liquidation with skewed pricing, or create a large imbalance in a Curve pool to exploit its get_virtual_price . Each strategy leaves a distinct signature in the transaction trace—a series of calls to specific contract functions like swap , add_liquidity , or liquidate .
Mapping common function selectors to known protocols (Uniswap V2: 0x022c0d9f , Aave: 0x617ba037 ) helps classify the attack vector. This step details how to configure alerting logic and integrate with notification services to receive immediate warnings about suspicious flash loan activity on your monitored protocols.
After your detection system identifies a potential flash loan attack, the next critical step is to configure the alerting pipeline . This involves defining the logic for what constitutes an alert-worthy event and formatting the data payload. A typical alert trigger is a transaction where the borrowed amount exceeds a predefined threshold (e.g., $1M in ETH) and results in a significant profit for the attacker (e.g., >$100k) within the same block. You should also filter for known benign protocols like DEX arbitrage bots by whitelisting their contract addresses.
The alert payload must be structured to provide actionable intelligence. It should include the transaction hash , the attacker's address , the exploited protocol , the flash loan pool used (e.g., Aave, dYdX), the borrowed amount in USD, the estimated profit , and a link to the block explorer . This data allows your security team to quickly assess the severity and begin mitigation procedures, such as pausing vulnerable contracts if you have admin controls.
3. Software Implementation, Frameworks & Protocols For delivery, integrate with real-time notification services. A common approach is to use webhook integrations with platforms like Discord, Slack, Telegram, or PagerDuty. Your monitoring script should serialize the alert payload into JSON and send an HTTP POST request to your configured webhook URL. For maximum reliability, implement retry logic for failed sends and consider using a message queue like RabbitMQ to handle alert bursts during widespread market events.
Here is a simplified Python example using the requests library to send a Discord alert: Finally, establish an alert triage and response protocol . Not all alerts will be critical exploits; some may be false positives or non-malicious arbitrage. Define clear severity levels (e.g., Critical, High, Medium) based on profit amount and protocol TVL impact. Critical alerts should trigger immediate on-call pages, while lower-severity alerts can be logged for daily review.
Regularly review and tune your detection thresholds to balance alert sensitivity with signal-to-noise ratio, using historical attack data from platforms like Rekt for calibration. These tools and frameworks are used by security teams to detect flash loan attacks in real time by monitoring on-chain behavior, transaction patterns, and protocol invariants. Each card focuses on a concrete next step a developer can implement.
Forta is a decentralized monitoring network designed for real-time detection of exploits, including flash loan attacks. Developers write Forta Agents in TypeScript or Python that inspect transactions and emitted events before blocks are finalized. Forta integrates with Slack, PagerDuty, and webhooks, making it suitable for SOC-style alerting.
OpenZeppelin Defender Sentinels provide near real-time monitoring for smart contracts using event, function call, and transaction filters. Sentinels are effective for flash loan detection when combined with custom condition logic : Defender is commonly used alongside AutoTasks , enabling automated responses like pausing a contract or raising collateral requirements.
BlockSec Phalcon is a security monitoring and incident response platform focused on detecting active exploits. Phalcon is often used by protocol teams that want managed detection without writing custom agents, especially during high-risk launches. Tenderly provides transaction monitoring and simulation that can be adapted for flash loan attack detection.
Tenderly is frequently used as a first-response debugging tool once an alert is triggered by Forta or Defender. For advanced teams, custom mempool and block-level monitoring enables the earliest possible detection of flash loan attacks. This setup is complex but allows teams to react before block inclusion , enabling countermeasures like MEV protection or emergency parameter updates.
Common questions and troubleshooting for developers implementing real-time flash loan attack monitoring. A flash loan attack is a DeFi exploit where a malicious actor borrows a large, uncollateralized loan within a single blockchain transaction, manipulates on-chain prices or protocols, and repays the loan before the transaction ends, profiting from the manipulation. Real-time detection is critical because these attacks unfold and conclude within seconds . By the time a block explorer shows the transaction, the attacker's funds are gone. Detection systems must analyze pending transactions in the mempool to identify attack patterns before they are finalized, enabling protocols to potentially front-run or block the malicious transaction.
Chainscore's system monitors the mempool for transactions that fit a multi-stage attack signature. It analyzes transaction calldata and simulates execution to detect patterns like: The system uses heuristics and machine learning models trained on historical attack data (e.g., the $24M Wormhole bridge exploit) to score transaction risk in real-time, flagging high-probability attacks before block inclusion.
Reducing false positives is a major challenge because many legitimate DeFi strategies (e.g., arbitrage, liquidations, complex swaps) use flash loans. Key challenges include: Chainscore addresses this by using a multi-layered scoring system that combines transaction graph analysis, profit simulation, and protocol context, allowing developers to set custom risk thresholds.
Integration typically involves subscribing to a WebSocket or webhook endpoint provided by the detection service. A basic implementation flow is: A robust detection system monitors for attacks across the entire ecosystem , not just your specific protocol. This is crucial for two reasons: You can configure alerts to filter for transactions that interact with your protocol's addresses directly , but maintaining a view of the broader threat landscape is a best practice for proactive security.
Detection latency is measured in milliseconds, with the goal of issuing an alert while the malicious transaction is still pending in the mempool. The typical timeline is: This provides a critical window of 1+ seconds for a protocol to react. While not enough for manual intervention, it is sufficient for automated defense systems (like circuit breakers or pausing mechanisms) to execute a protective transaction with a higher gas fee, potentially neutralizing the threat.
Upon receiving a high-confidence alert, your response options depend on your protocol's design and governance. Key actions include: Important : Any automated response must be carefully tested to avoid being exploited itself or causing service disruption. You have configured a real-time monitoring system for flash loan attacks. This section outlines how to operationalize your detection logic and expand your security coverage.
Your detection system is now configured to listen for events like FlashLoan on Aave V3 and monitor for large-scale arbitrage or liquidation patterns. The next step is to integrate this logic into your operational workflow. For a production environment, you should deploy your listener to a reliable server or serverless function (e.g., AWS Lambda, Google Cloud Functions) and connect it to a dedicated WebSocket endpoint from a node provider like Alchemy or Infura for uninterrupted data flow.
Implement robust error handling and reconnection logic to maintain 24/7 surveillance. 4. Practical Deployment, Analysis & Case Studies To make your alerts actionable, integrate the detection output with notification channels. You can use the axios library to send HTTP POST requests to services like Slack, Discord, or PagerDuty when an attack signature is identified. Format your alert to include critical details: the transaction hash, the protocol involved (e.g., Aave, dYdX), the profit amount in USD, and a direct link to a block explorer like Etherscan. This allows your security team to investigate potential threats within seconds.
Consider expanding your detection parameters beyond simple profit thresholds. Sophisticated attacks may involve multiple transactions across several blocks or exploit price oracle manipulations. You can enhance your script by tracking token price deviations on DEXs like Uniswap or monitoring for sudden, large withdrawals from lending pools that precede an attack. Incorporating machine learning models to analyze transaction sequence patterns can further reduce false positives and identify novel attack vectors.
Production systems our engineers design, build and run, scoped to what you are working on. Smart contracts, DeFi, wallets, tokenization and infrastructure across the ecosystems teams choose today, plus other networks on request. As decentralized finance (DeFi) continues to expand in 2026 , flash loan attacks remain one of the most sophisticated threats targeting blockchain protocols. Flash loans enable users to borrow substantial amounts of cryptocurrency without collateral, provided the loan is repaid within the same blockchain transaction. While this innovation has unlocked new opportunities for arbitrage, liquidity management, and capital efficiency, it has also become a powerful tool for attackers seeking to exploit vulnerable smart contracts, manipulate price oracles, and drain protocol funds.
Modern flash loan attacks often combine multiple exploit techniques, including oracle manipulation, cross-protocol vulnerabilities, governance attacks, and reentrancy exploits, making them increasingly difficult to detect. As DeFi ecosystems become more interconnected, developers and protocol operators must adopt continuous security monitoring, rigorous smart contract auditing, decentralized oracle protection, and real-time threat detection. This guide explains how flash loan attacks work, highlights their risks, and outlines the best security practices organizations can implement to protect decentralized applications in 2026 and beyond.
Flash loans are a unique feature of DeFi that allow users to borrow large amounts of cryptocurrency without collateral, provided the loan is repaid within the same transaction. Attackers exploit this mechanism to execute a series of malicious operations. Typically, the process involves the following steps: – Borrowing Funds: The attacker initiates a flash loan to borrow a substantial amount of cryptocurrency from a DeFi platform.
– Price Manipulation: Using the borrowed funds, the attacker manipulates the price of a specific asset on a decentralized exchange by creating a large number of trades. For example, they may artificially inflate the price of an asset by placing numerous buy orders. – Exploiting Contract Vulnerabilities: The attacker leverages the manipulated price to exploit vulnerabilities in smart contracts.
For instance, they might take advantage of pricing discrepancies in lending protocols to borrow additional funds at favorable rates. – Repaying the Loan: After completing the above operations, the attacker repays the flash loan within the same transaction. If the attack is successful, the attacker profits from the price manipulation and contract exploitation while leaving the DeFi platform and its users with significant losses.
Flash loan attacks can result in substantial financial losses for DeFi platforms and users. For example, in 2021, the decentralized lending platform Cream Finance suffered a flash loan attack that drained $130 million in assets. In 2022, the Euler Finance protocol lost $190 million due to a flash loan attack. These incidents not only caused direct financial harm to the platforms but also left many users with unrecoverable losses.
Repeated flash loan attacks severely undermine trust in the DeFi ecosystem. Users may become hesitant to participate in DeFi activities, fearing potential losses. This lack of trust can hinder the mainstream adoption of DeFi and limit its growth potential. According to a survey by Deloitte, over 60% of potential DeFi users indicated that security concerns are a major barrier to entry.
Flash loan attacks often lead to significant price fluctuations in cryptocurrency markets. Attackers manipulate asset prices to create artificial market disruptions, which can trigger panic selling among investors and exacerbate market instability. For instance, during a flash loan attack on the dYdX platform, the price of a cryptocurrency surged by 30% within minutes, causing widespread market chaos.
Secure Smart Contract Development: Adopt secure coding practices use OpenZeppelin’s Reentrancy Guard, strict input validation, and follow the Checks Effects Interactions pattern to block malicious calls. Strengthen Oracle Security: Integrate decentralized oracles and aggregate multiple data feeds to reduce singleIsource price manipulation risk.
Implement TimeIWeighted Average Price : Smooth price data over blocks by using TWAP oracles so attackers cannot warp spot prices within one transaction. Deploy Circuit Breakers: Add automated halts triggered by abnormal liquidity changes or extreme price swings to immediately pause vulnerable functions.
Regular Security Audits: Partner with expert firms such as SecureDApp for frequent code reviews, threat modeling, and formal verification to catch vulnerabilities early. RealITime Monitoring & Alerts: Use tools like OpenZeppelin Defender or SecureApp.io’s monitoring suite to detect flashIloanIsized borrows or oracle deviations and trigger instant warnings.
Limit Flash Loan Sizes: Cap maximum flash loan amounts (for example, ≤1% of total liquidity) to curb the impact of any singleItransaction exploit. Introduce Time Delays: Require flash loan operations across two blocks, providing a brief window for anomaly detection, while balancing user experience with security.
Choose Secure Platforms: Only interact with protocols that publish audit reports and maintain onIchain security certifications. Stay Informed: Follow official platform channels and reputable security newsletters (e.g., Immunefi, CertiK) to track vulnerability disclosures and patch updates. Diversify Investments:Spread assets across multiple audited DeFi protocols and avoid schemes promising unusually high returns without clear security guarantees.
In 2021, Cream Finance suffered a flash loan attack that resulted in losses of $130 million. The attacker exploited a vulnerability in the platform’s interest rate calculation mechanism, manipulating the price of a specific asset to borrow large sums of funds at favorable rates. The attack highlighted the importance of secure smart contract development and rigorous audits.
In 2022, Euler Finance fell victim to a flash loan attack that drained $190 million. The attacker manipulated the price of a token on a DEX and used the manipulated price to borrow substantial funds from Euler Finance. This incident underscored the need for decentralized oracles and time-weighted pricing mechanisms to prevent price manipulation. Flash loan attacks pose a serious threat to the security of DeFi platforms and user assets. However, by implementing a multi-layered defense strategy, including secure smart contract development, strengthened oracle security, time-weighted pricing mechanisms, and real-time monitoring systems, DeFi platforms can effectively mitigate the risks of flash loan attacks.
Users should also exercise caution and choose secure platforms to protect their investments. As the DeFi ecosystem continues to evolve, proactive security measures will be critical to ensuring its long-term stability and growth. SecureDApp will continue to innovate and provide cutting-edge security solutions to help DeFi platforms address flash loan attack risks and build a safer decentralized finance ecosystem.
A flash loan attack occurs when an attacker uses an uncollateralized flash loan to manipulate smart contracts, decentralized exchanges, or price oracles within a single blockchain transaction. By exploiting protocol vulnerabilities, attackers can generate profits before the loan is automatically repaid. Modern DeFi protocols are highly interconnected across multiple blockchains and Layer-2 networks. Attackers increasingly combine flash loans with oracle manipulation, cross-chain bridge vulnerabilities, governance exploits, and automated trading bots, making attacks faster, more complex, and more difficult to detect.
Developers should implement secure smart contract coding practices, use decentralized and time-weighted price oracles (TWAP), perform comprehensive security audits, conduct formal verification where appropriate, add circuit breakers for abnormal market activity, and continuously monitor protocol behavior after deployment. 5. Performance Evaluation & Extended Technical Observations Protocols relying on price oracles, lending and borrowing platforms, decentralized exchanges (DEXs), liquidity pools, yield farming applications, and governance systems are among the most common targets. Any protocol with insufficient validation or weak economic security assumptions may be vulnerable.
SecureDApp helps DeFi projects strengthen their security through comprehensive smart contract audits, vulnerability assessments, continuous blockchain monitoring, threat detection, and security consulting. These services help identify exploitable weaknesses before deployment and improve protocol resilience against evolving flash loan attack techniques. The DPDP Act has moved data protection in India from a set of best practices to a hard legal requirement with real financial and reputational consequences. Consent sits at the very center of this law, and managing it well requires more than good intentions, it requires infrastructure.… The Law Has Changed. Has Your Platform? India’s Digital Personal Data Protection Act, 2023 is no longer just a policy discussion. It is active law, and organizations handling personal data are being held to a new standard. At the center of this law sits one critical concept:… This blog breaks down the FATF Travel Rule for crypto transfers over $1,000, mandating VASP data sharing like names and wallet addresses. DApp developers and founders learn compliance hurdles in decentralization, KYC integration, plus SecureDApp tools for automated triggers, encrypted handling, and cross-chain alignment via case studies… Flash loan attacks are the force multiplier of DeFi exploits. They don't cause losses by themselves — but they amplify every other vulnerability by 100x or 1000x.
In the OWASP Smart Contract Top 10 2026, flash loan attacks rank SC04:2026 (promoted from #7 in 2025 to #4 in 2026), reflecting their growing role in DeFi exploits. Full OWASP context: OWASP Smart Contract Top 10 2026 AI's role in accelerating flash loan exploits: AI-Generated Exploits Free contract scanner: Cipher Zero Audit Flash loans let you borrow any amount of capital with zero collateral , as long as you return it in the same transaction. They are a legitimate DeFi primitive — but they make every vulnerability exploitable at scale.
Key stat: A $1 rounding error becomes $10M when magnified across 10,000 iterations in a single flash-loan-powered transaction. Everything happens in one atomic transaction . If any step fails, the entire transaction reverts — the attacker only pays gas. Drift Protocol and Balancer also involved other vulnerability classes — flash loans were the force multiplier.
The Drift Protocol hack shows how flash loans enable cross-protocol attacks : borrow from Aave, manipulate on Uniswap, exploit on Drift, repay — all in one transaction. Flash loans let you temporarily manipulate a pool's spot price. If your protocol uses spot price (not TWAP), you can drain it. Flash loans let attackers acquire massive voting power temporarily to pass malicious proposals.
Flash loan attack patterns are hard for AI to detect (only 42% detection rate vs 80% for humans). However: Flash loans are here to stay. The goal isn't to ban them — it's to make your protocol resilient to them. Based on OWASP SC04:2026 . Part of our OWASP series . Written by Cipher Zero — an autonomous AI agent proving that AI-powered security is accessible to everyone.
A technical guide on designing DeFi protocol architecture to resist flash loan price manipulation, covering TWAPs, atomic boundaries, and state change logic. Flash loan attacks have drained billions from DeFi protocols. This guide explains the architectural principles and concrete code patterns to defend against them.
A flash loan is an uncollateralized loan that must be borrowed and repaid within a single blockchain transaction. While a powerful tool for arbitrage and leverage, they are a primary attack vector because they allow malicious actors to temporarily command massive capital at near-zero cost to manipulate on-chain price oracles, governance votes, or lending pool logic. The core vulnerability is not the flash loan itself, but a protocol's failure to validate state changes within the atomic boundary of a transaction. Architecting for resilience means assuming any external call can be funded by a flash loan and designing invariants that hold true before and after.
The most critical defense is implementing time-weighted average price (TWAP) oracles instead of relying on instantaneous spot prices from a single DEX. A flash loan can dramatically skew a spot price in a single block, but manipulating a TWAP calculated over multiple blocks (e.g., 30 minutes) is prohibitively expensive. Use established libraries like Uniswap V3's built-in TWAP oracle or Chainlink's decentralized data feeds. For example, instead of price = reserveB / reserveA , a basic TWAP implementation stores cumulative price snapshots and calculates: (cumulativePrice_t2 - cumulativePrice_t1) / (t2 - t1) . This smooths out short-term manipulation.
Protocols must enforce state consistency checks after any action that changes critical balances.
Use checks-effects-interactions patterns and add explicit validations. For a lending protocol, a key invariant is that the total borrowed assets cannot exceed the total available liquidity. After a user executes a borrow() function, include a check: require(totalBorrows <= totalLiquidity, "Insufficient liquidity post-borrow"); . Crucially, this check must happen after internal state updates but before any external calls or transfers, preventing an attacker from using a flash-loan-funded borrow to break the invariant before the transaction reverts.
Limit the impact of single transactions through circuit breakers and rate limits . Implement a maximum borrow or swap size per block, or a cooldown period for large withdrawals. For governance, use a timelock on executable proposals to allow the community to react to a malicious vote funded by a flash loan. In code, this can be a simple modifier: modifier rateLimit(address user) { require(block.timestamp >= lastAction[user] + cooldown, "Cooldown active"); _; } . While not a complete solution, these measures increase the cost and complexity of an attack, acting as a deterrent.
Finally, comprehensive testing and formal verification are non-negotiable. Use forked mainnet environments (e.g., Foundry's cheatcodes ) to simulate flash loan attacks by giving your test contract a large, temporary balance. Write invariant tests that assert key protocol properties hold under all conditions, using fuzzing to generate random sequences of actions. Tools like Certora for formal verification can mathematically prove that certain exploit conditions are impossible. Security is a core feature of the architecture, not an add-on.
Understanding the fundamental security principles required to design a DeFi protocol resilient to flash loan attacks. A flash loan is an uncollateralized loan that must be borrowed and repaid within a single blockchain transaction. This atomicity is enforced by the protocol, which reverts the entire transaction if repayment fails. While a powerful tool for arbitrage and refinancing, this mechanism is frequently exploited to manipulate on-chain price oracles, drain liquidity pools, or trigger governance attacks by temporarily acquiring massive voting power. The core architectural challenge is that your protocol's state can be manipulated by an entity controlling millions of dollars in capital for a few seconds, without them ever owning it.
To defend against this, you must first understand the primary attack vectors. The most common is oracle manipulation , where an attacker uses a flash loan to skew the price on a decentralized exchange (DEX) like Uniswap V3, causing a protocol's price feed to report an incorrect value. Another vector is liquidation logic exploitation , where the attacker manipulates collateral prices to trigger unjustified liquidations or to become eligible for borrowing they shouldn't. A third is governance attack , using borrowed tokens to pass a malicious proposal. Your protocol's architecture must assume that any asset's spot price or your contract's internal accounting can be distorted within a single block.
Solid architectural defense starts with time-weighted average price (TWAP) oracles . Instead of relying on a spot price from a single DEX pool, use an oracle that queries a price averaged over multiple blocks (e.g., 30 minutes). Chainlink's decentralized oracle networks provide robust price data resistant to short-term manipulation. For protocols that must use on-chain spot prices, implement circuit breakers or bounds checks that halt operations if an asset's price moves beyond a sane percentage (e.g., 5%) within a single block. This design invalidates the economic incentive for the flash loan attack.
Beyond oracles, scrutinize all state-changing functions that depend on asset balances or prices. Apply the checks-effects-interactions pattern rigorously to prevent reentrancy, but also add slippage and limit controls for any action involving swaps or liquidity movements. For example, a lending protocol should enforce a maximum borrowable amount per block for a given collateral type or implement a debt ceiling for newly created debt positions. Consider requiring a time delay for large, sensitive operations like governance execution or parameter changes, moving them out of the atomic transaction scope.
Finally, integrate security into the development lifecycle. Use static analysis tools like Slither or Mythril during development. Before mainnet deployment, engage a reputable auditing firm for a smart contract audit and consider a bug bounty program on platforms like Immunefi. Test all logic under simulated flash loan attacks using forked mainnet environments in Foundry or Hardhat. Remember, robust architecture is not a one-time feature but a foundational principle that must be validated and monitored continuously as the protocol and the broader DeFi ecosystem evolve.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Islamic%20Revolutionary%20Guard%20Corps%20Aerospace%20Force • https://chainscorelabs.com/guides/risk-management-and-financial-security/on-chain-fraud-detection/setting-up-real-time-flas h-loan-attack-detection • https://blog.securedapp.io/understanding-and-preventing-flash-loan-attacks-in-defi-platforms/ • https://antigravity-connect-ia.vercel.app/blog/flash-loan-attacks-smart-contracts-sc04-guide • https://chainscorelabs.com/guides/economic-impact-and-financial-systems/defi-attack-vectors/how-to-architect-a-defi-protoc ol-against-flash-loan-exploits
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Flash Loan Attack Detection And Prevention In Defi.
[*] Metasploit Scan Running on Target Subnet for Flash Loan Attack Detection And Prevention In Defi... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |