Complete Technical Paper Content — Ftp Attack Monitoring And Automatic IP Blocking Tool
Overview & System Context
Ftp Attack Monitoring And Automatic Ip Blocking Tool: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9120 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Simple Network Management Protocol (SNMP) is an Internet Standard protocol for collecting and organizing information about managed devices on IP networks and for modifying that information to change device behavior. Devices that typically support SNMP include cable modems, routers, network switches, servers, workstations, printers, and more. SNMP is widely used in network management for network monitoring. SNMP exposes management data in the form of variables on the managed systems organized in a management information base (MIB), which describes the system status and configuration.
These variables can then be remotely queried (and, in some circumstances, manipulated) by network management applications. Three significant versions of SNMP have been developed and deployed. SNMPv1 is the original version of the protocol. More recent versions, SNMPv2c and SNMPv3, feature improvements in performance, flexibility and security. SNMP is a component of the Internet Protocol Suite as defined by the Internet Engineering Task Force (IETF). It consists of a set of standards for network management, including an application layer protocol, a database schema, and a set of data objects.
In typical uses of SNMP, one or more administrative computers called managers have the task of monitoring or managing a group of hosts or devices on a computer network. Each managed system executes a software component called an agent that reports information via SNMP to the manager. An SNMP-managed network consists of three key components: Managed devices Agent – software that runs on managed devices Network management station (NMS) – software that runs on the manager A managed device is a network node that implements an SNMP interface that allows unidirectional (read-only) or bidirectional (read and write) access to node-specific information. Managed devices exchange node-specific information with the NMSs. Sometimes called network elements, the managed devices can be any type of device, including, but not limited to, routers, access servers, switches, cable modems, bridges, hubs, IP telephones, IP video cameras, computer hosts, and printers. An agent is a network-management software module that resides on a managed device. An agent has local knowledge of management information and translates that information to or from an SNMP-specific form. A network management station executes applications that monitor and control managed devices. NMSs provide the bulk of the processing and memory resources required for network management. One or more NMSs may exist on any managed network.
SNMP agents expose management data on the managed systems as variables. The protocol also permits active management tasks, such as configuration changes, through remote modification of these variables. The variables accessible via SNMP are organized in hierarchies. SNMP itself does not define which variables a managed system should offer. Rather, SNMP uses an extensible design that allows applications to define their own hierarchies. These hierarchies are described as a management information base (MIB). MIBs describe the structure of the management data of a device subsystem; they use a hierarchical namespace containing object identifiers (OID). Each OID identifies a variable that can be read or set via SNMP.
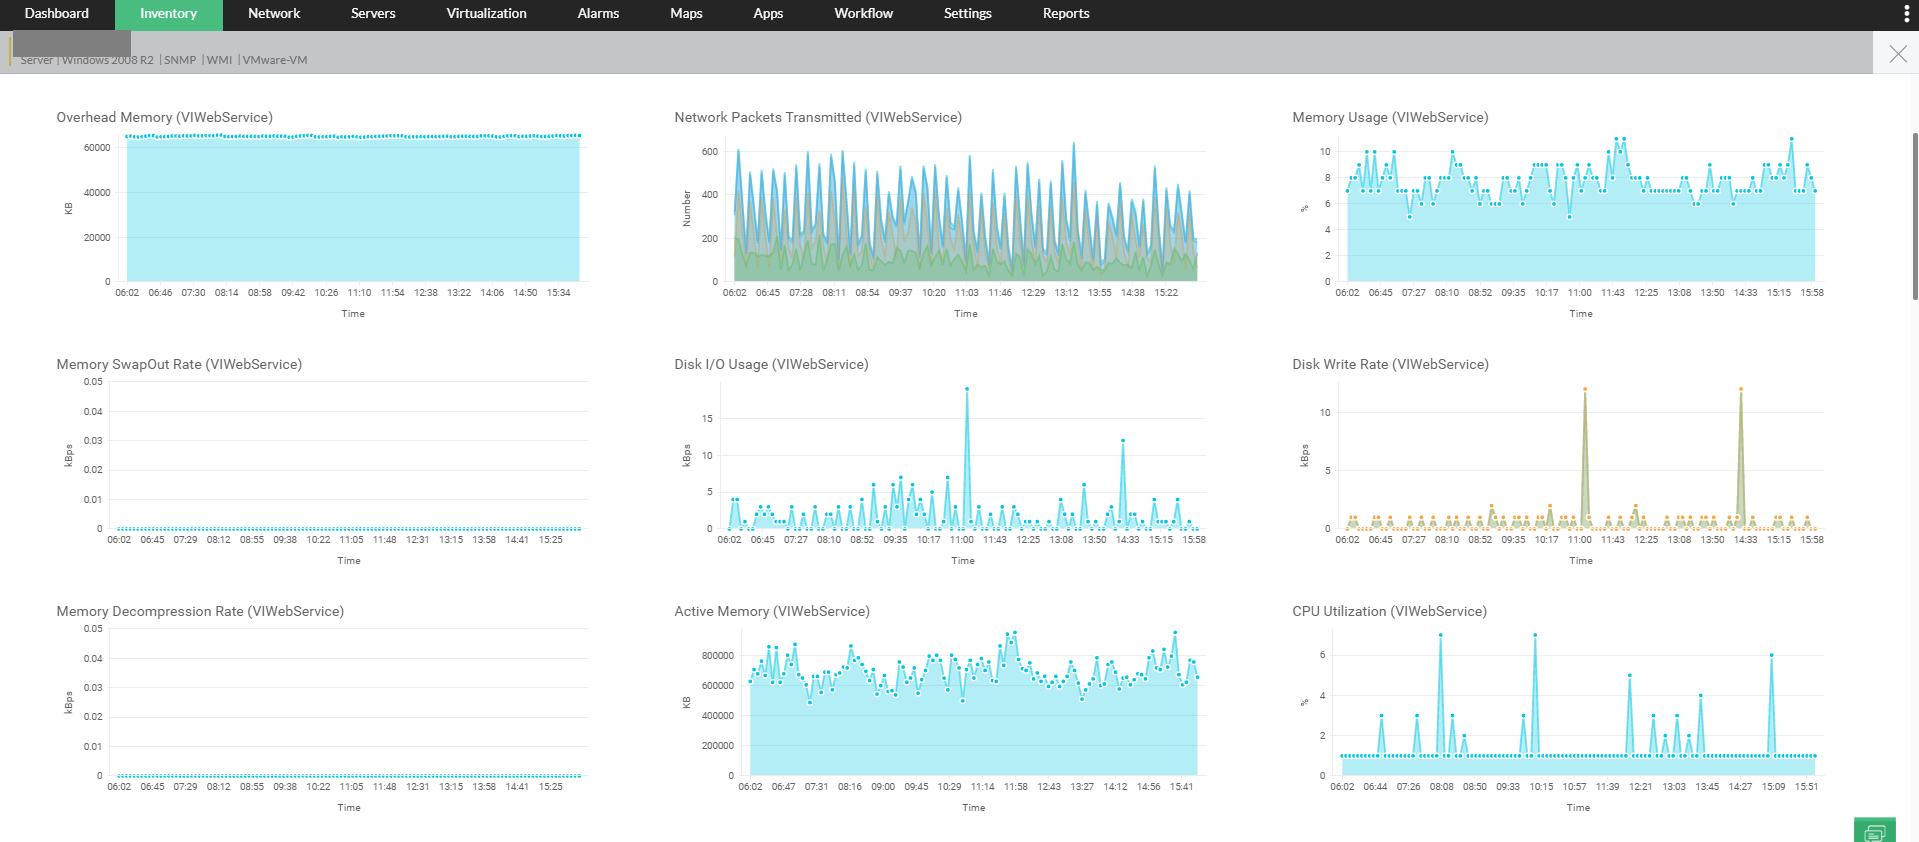
MIBs use the notation defined by Structure of Management Information Version 2.0 (SMIv2, RFC 2578), a subset of ASN.1. Figure 1: Monitor FTP Server | FTP Monitoring Software & Tool - ManageEngine ... GetRequest A manager-to-agent request to retrieve the value of a variable or list of variables. Desired variables are specified in variable bindings (the value field is not used). Retrieval of the specified variable values is to be done as an atomic operation by the agent. A Response with current values is returned. SetRequest A manager-to-agent request to change the value of a variable or list of variables. Variable bindings are specified in the body of the request. Changes to all specified variables are to be made as an atomic operation by the agent. A Response with (current) new values for the variables is returned.
GetNextRequest A manager-to-agent request to discover available variables and their values. Returns a Response with variable binding for the lexicographically next variable in the MIB. The entire MIB of an agent can be walked by iterative application of GetNextRequest starting at OID 0. Rows of a table can be read by specifying column OIDs in the variable bindings of the request. GetBulkRequest A manager-to-agent request for multiple iterations of GetNextRequest. An optimized version of GetNextRequest. Returns a Response with multiple variable bindings walked from the variable binding or bindings in the request. PDU specific non-repeaters and max-repetitions fields are used to control response behavior. GetBulkRequest was introduced in SNMPv2. Response Returns variable bindings and acknowledgement from agent to manager for GetRequest, SetRequest, GetNextRequest, GetBulkRequest and InformRequest. Error reporting is provided by error-status and error-index fields. Although it was used as a response to both gets and sets, this PDU was called GetResponse in SNMPv1. Trap Asynchronous notification from agent to manager. While in other SNMP communication, the manager actively requests information from the agent, these are PDUs that are sent from the agent to the manager without being explicitly requested. SNMP Traps enable an agent to notify the management station of significant events by way of an unsolicited SNMP message. Trap PDUs include current sysUpTime value, an OID identifying the type of trap and optional variable bindings. Destination addressing for traps is determined in an application-specific manner, typically through trap configuration variables in the MIB. The format of the trap message was changed in SNMPv2 and the PDU was renamed SNMPv2-Trap.
InformRequest Acknowledged asynchronous notification. This PDU was introduced in SNMPv2 and was originally defined as manager to manager communication. Later implementations have loosened the original definition to allow agent to manager communications. Manager-to-manager notifications were already possible in SNMPv1 using a Trap, but as SNMP commonly runs over UDP where delivery is not assured and dropped packets are not reported, delivery of a Trap was not guaranteed.
InformRequest fixes this as an acknowledgement is returned on receipt. RFC 1157 specifies that an SNMP implementation must accept a message of at least 484 bytes in length. In practice, SNMP implementations accept longer messages. If implemented correctly, an SNMP message is discarded if the decoding of the message fails and thus malformed SNMP requests are ignored. A successfully decoded SNMP request is then authenticated using the community string. If the authentication fails, a trap is generated indicating an authentication failure and the message is dropped. SNMPv1 and SNMPv2c use communities to establish trust between managers and agents. Most agents support three community names, one each for read-only, read-write and trap. These three community strings control different types of activities. The read-only community applies to get requests. The read-write community string applies to set requests. The trap community string applies to receipt of traps. SNMPv3 also uses community strings, but allows for secure authentication and communication between SNMP manager and agent.
RFC 1065 — Structure and identification of management information for TCP/IP-based internets RFC 1066 — Management information base for network management of TCP/IP-based internets RFC 1067 — A simple network management protocol In 1990, these documents were superseded by: RFC 1155 — Structure and identification of management information for TCP/IP-based internets RFC 1156 — Management information base for network management of TCP/IP-based internets RFC 1157 — A simple network management protocol In 1991, RFC 1156 (MIB-1) was replaced by the more often used: RFC 1213 — Version 2 of management information base (MIB-2) for network management of TCP/IP-based internets SNMPv1 is widely used and is the de facto network management protocol in the Internet community. SNMPv1 may be carried by transport layer protocols such as User Datagram Protocol (UDP), OSI Connectionless-mode Network Service (CLNS), AppleTalk Datagram Delivery Protocol (DDP), and Novell Internetwork Packet Exchange (IPX). Version 1 has been criticized for its poor security. The specification does, in fact, allow room for custom authentication to be used, but widely used implementations "support only a trivial authentication service that identifies all SNMP messages as authentic SNMP messages." The security of the messages, therefore, becomes dependent on the security of the channels over which the messages are sent. For example, an organization may consider their internal network to be sufficiently secure that no encryption is necessary for its SNMP messages. In such cases, the community name, which is transmitted in cleartext, tends to be viewed as a de facto password, in spite of the original specification.
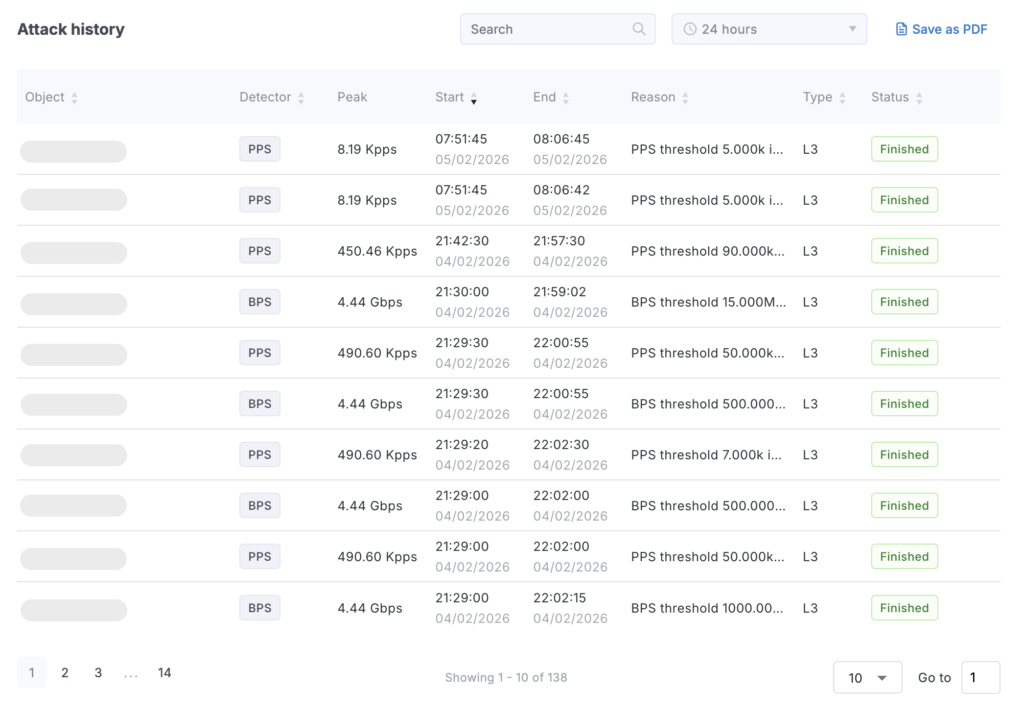
Figure 2: Monitoring Tools (Network Protection) | StormWall 2. System Architecture & Core Working Principles Although SNMPv3 makes no changes to the protocol aside from the addition of cryptographic security, it looks very different due to new textual conventions, concepts, and terminology. The most visible change was to define a secure version of SNMP, by adding security and remote configuration enhancements to SNMP. The security aspect is addressed by offering both strong authentication and data encryption for privacy. For the administration aspect, SNMPv3 focuses on two parts, namely notification originators and proxy forwarders. The changes also facilitate remote configuration and administration of the SNMP entities, as well as addressing issues related to large-scale deployment, accounting, and fault management. Features and enhancements included: Identification of SNMP entities to facilitate communication only between known SNMP entities – Each SNMP entity has an identifier called the SNMPEngineID, and SNMP communication is possible only if an SNMP entity knows the identity of its peer. Traps and Notifications are exceptions to this rule. Support for security models – A security model may define the security policy within an administrative domain or an intranet. SNMPv3 contains the specifications for a user-based security model (USM). Definition of security goals where the goals of message authentication service include protection against the following: Modification of Information – Protection against some unauthorized SNMP entity altering in-transit messages generated by an authorized principal. Masquerade – Protection against attempting management operations not authorized for some principal by assuming the identity of another principal that has the appropriate authorizations. Message stream modification – Protection against messages getting maliciously re-ordered, delayed, or replayed to affect unauthorized management operations. Disclosure – Protection against eavesdropping on the exchanges between SNMP engines.
Specification for USM – USM consists of the general definition of the following communication mechanisms available: Communication without authentication and privacy (NoAuthNoPriv). Communication with authentication and without privacy (AuthNoPriv). Communication with authentication and privacy (AuthPriv). Definition of different authentication and privacy protocols – MD5, SHA and HMAC-SHA-2 authentication protocols and the CBC_DES and CFB_AES_128 privacy protocols are supported in the USM. Definition of a discovery procedure – To find the SNMPEngineID of an SNMP entity for a given transport address and transport endpoint address. Definition of the time synchronization procedure – To facilitate authenticated communication between the SNMP entities. Definition of the SNMP framework MIB – To facilitate remote configuration and administration of the SNMP entity. Definition of the USM MIBs – To facilitate remote configuration and administration of the security module. Definition of the view-based access control model (VACM) MIBs – To facilitate remote configuration and administration of the access control module. Security was one of the biggest weaknesses of SNMP until v3.
Authentication in SNMP Versions 1 and 2 amounts to nothing more than a password (community string) sent in clear text between a manager and agent. Each SNMPv3 message contains security parameters that are encoded as an octet string. The meaning of these security parameters depends on the security model being used. The security approach in v3 targets: Confidentiality – Encryption of packets to prevent snooping by an unauthorized source. Integrity – Message integrity to ensure that a packet has not been tampered with while in transit, including an optional packet replay protection mechanism.
Authentication – to verify that the message is from a valid source. Version 3 also defines the USM and VACM, which were later followed by a transport security model (TSM) that provided support for SNMPv3 over SSH and SNMPv3 over TLS and DTLS. USM (User-based Security Model) provides authentication and privacy (encryption) functions and operates at the message level. VACM (View-based Access Control Model) determines whether a given principal is allowed access to a particular MIB object to perform specific functions and operates at the PDU level. TSM (Transport Security Model) provides a method for authenticating and encrypting messages over external security channels. Two transports, SSH and TLS/DTLS, have been defined that make use of the TSM specification. As of 2004 the IETF recognizes Simple Network Management Protocol version 3 as defined by RFC 3411–RFC 3418 (also known as STD0062) as the current standard version of SNMP. The IETF has designated SNMPv3 a full Internet standard, the highest maturity level for an RFC. It considers earlier versions to be obsolete (designating them variously Historic or Obsolete).
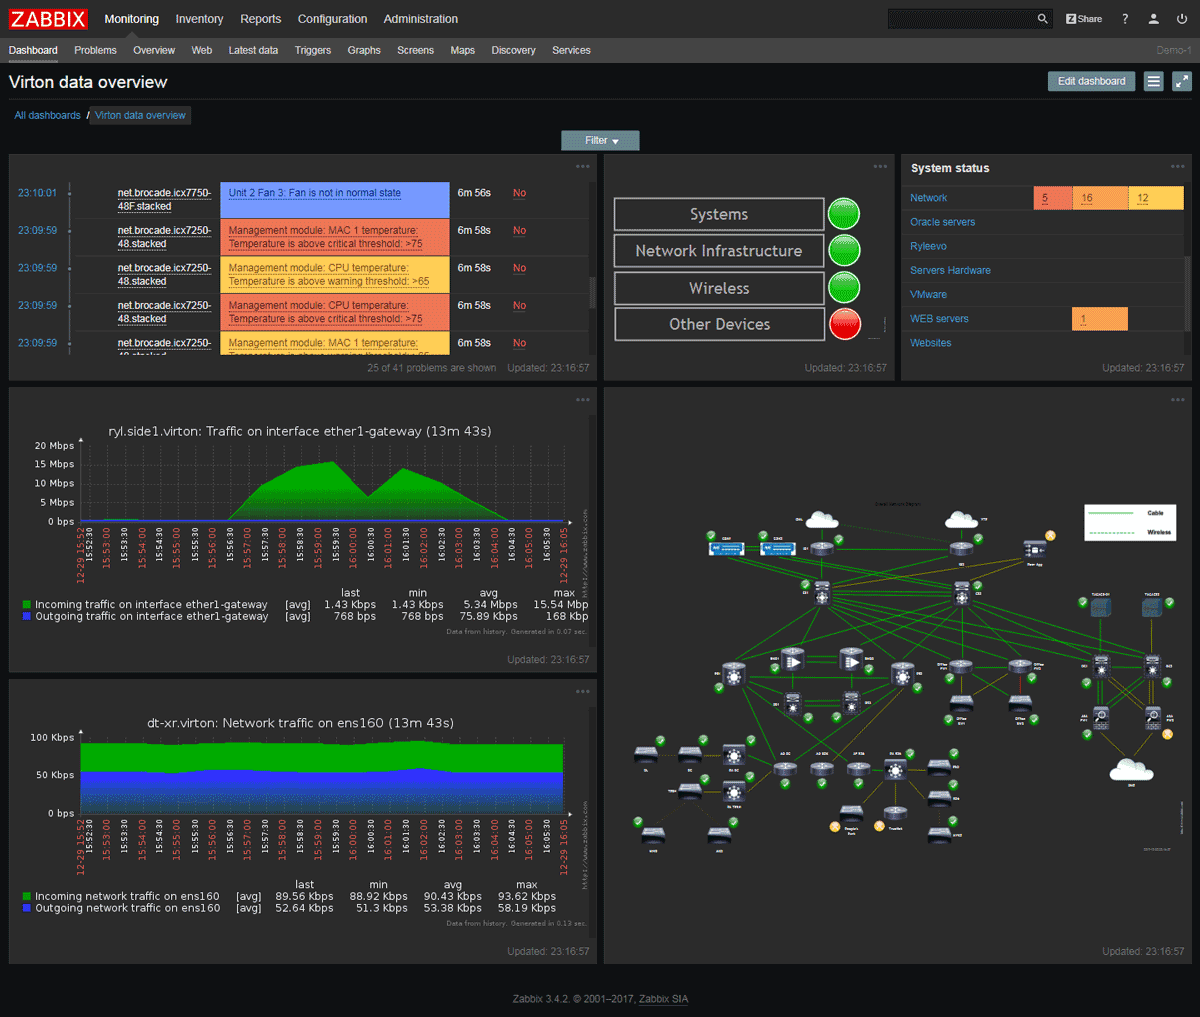
Figure 3: Best IP Monitoring Software for 2025 Internet censorship is the legal control or suppression of what can be accessed, published, or viewed on the Internet. Censorship is most often applied to specific internet domains (such as Wikipedia.org, for example) but exceptionally may extend to all Internet resources located outside the jurisdiction of the censoring state. Internet censorship may also put restrictions on what information can be made internet accessible. Organizations providing internet access – such as schools and libraries – may choose to preclude access to material that they consider undesirable, offensive, age-inappropriate or even illegal, and regard this as ethical behavior rather than censorship. Individuals and organizations may engage in self-censorship of material they publish, for moral, religious, or business reasons, to conform to societal norms, political views, due to intimidation, or out of fear of legal or other consequences. The extent of Internet censorship varies on a country-to-country basis. While some countries have moderate Internet censorship, other countries go as far as to limit the access of information such as news and suppress and silence discussion among citizens. Internet censorship also occurs in response to or in anticipation of events such as elections, protests, and riots. An example is the increased censorship due to the events of the Arab Spring. Other types of censorship include the use of copyrights, defamation, harassment, and various obscene material claims as a way to deliberately suppress content. Support for and opposition to Internet censorship also varies. In a 2012 Internet Society survey, 71% of respondents agreed that "censorship should exist in some form on the Internet". In the same survey, 83% agreed that "access to the Internet should be considered a basic human right" and 86% agreed that "freedom of expression should be guaranteed on the Internet". According to GlobalWebIndex, over 400 million people use virtual private networks to circumvent censorship or for increased user privacy. Age verification as a form of internet censorship is expanding to more jurisdictions, particularly since Australia passed its Online Safety Amendment on 27 November 2024, which came into force on 10 December 2025.
A 1993 Time magazine article quotes computer scientist John Gilmore, one of the founders of the Electronic Frontier Foundation, as saying "The Net interprets censorship as damage and routes around it". In November 2007, "Father of the Internet" Vint Cerf stated that he sees government control of the Internet failing because the Web is almost entirely privately owned. A report of research conducted in 2007 and published in 2009 by the Berkman Klein Center for Internet & Society at Harvard University stated that: "We are confident that the [censorship circumvention] tool developers will for the most part keep ahead of the governments' blocking efforts", but also that "...we believe that less than two percent of all filtered Internet users use circumvention tools". In contrast, a 2011 report by researchers at the Oxford Internet Institute published by UNESCO concludes "... the control of information on the Internet and Web is certainly feasible, and technological advances do not therefore guarantee greater freedom of speech". Blocking and filtering can be based on relatively static blacklists or be determined more dynamically based on a real-time examination of the information being exchanged. Blacklists may be produced manually or automatically and are often not available to non-customers of the blocking software. Blocking or filtering can be done at a centralized national level, at a decentralized sub-national level, or at an institutional level, e.g., in libraries, universities or Internet cafés. Blocking and filtering may also vary within a country across different ISPs. Countries may filter sensitive content on an ongoing basis and/or introduce temporary filtering during key time periods such as elections. In some cases, the censoring authorities may surreptitiously block content to mislead the public into believing that censorship has not been applied. This is achieved by returning a fake "Not Found" error message when an attempt is made to access a blocked website. Unless the censor has total control over all Internet-connected computers, such as in North Korea (who employs an intranet that only privileged citizens can access), or Cuba, total censorship of information is very difficult or impossible to achieve due to the underlying distributed technology of the Internet. Pseudonymity and data havens (such as Hyphanet) protect free speech using technologies that guarantee material cannot be removed and prevents the identification of authors.
Technologically savvy users can often find ways to access blocked content. Nevertheless, blocking remains an effective means of limiting access to sensitive information for most users when censors, such as those in China, are able to devote significant resources to building and maintaining a comprehensive censorship system. The term "splinternet" is sometimes used to describe the effects of national firewalls. The verb "rivercrab" colloquially refers to censorship of the Internet, particularly in Asia.
Internet backbone, including Internet exchange points (IXP) with international networks (Autonomous Systems), operators of submarine communications cables, satellite Internet access points, international optical fibre links etc. In addition to facing huge performance challenges due to large bandwidths involved, these do not give censors access to information exchanged within the country. Internet service providers, which involves installation of voluntary (such as in the UK) or mandatory (such as in Russia) Internet surveillance and blocking equipment. Individual institutions, which in most cases implement some form of Internet access controls to enforce their own policies, but, especially in case of public or educational institutions, may be requested or coerced to do this on the request from the government. Personal devices, whose manufacturers or vendors may be required by law to install censorship software. Application service providers (e.g. social media companies), who may be legally required to remove particular content. Foreign providers with business presence in given country may be also coerced into restricting access to specific contents for visitors from the requesting country. Certificate authorities may be required to issue counterfeit X.509 certificates controlled by the government, allowing man-in-the-middle surveillance of TLS encrypted connections. Content Delivery Network providers who tend to aggregate large amounts of content (e.g. images) may be also an attractive target for censorship authorities.
Internet Protocol (IP) address blocking: Access to a certain IP address is denied. If the target Web site is hosted in a shared hosting server, all websites on the same server will be blocked. This affects IP-based protocols such as HTTP, FTP and POP. A typical circumvention method is to find proxies that have access to the target websites, but proxies may be jammed or blocked, and some Web sites, such as Wikipedia (when editing), also block proxies. Some large websites such as Google have allocated additional IP addresses to circumvent the block, but later the block was extended to cover the new addresses.
Due to challenges with geopositioning, geo-blocking is normally implemented via IP address blocking. Domain name system (DNS) filtering and redirection: Connections to blocked domain names are not resolved, or an incorrect IP address is returned via DNS hijacking or other means. This affects all IP-based protocols such as HTTP, FTP and POP. A typical circumvention method is to find an alternative DNS resolver that resolves domain names correctly, but domain name servers are subject to blockage as well, especially IP address blocking. Another workaround is to bypass DNS if the IP address is obtainable from other sources and is not itself blocked. Examples are modifying the Hosts file or typing the IP address instead of the domain name as part of a URL given to a Web browser. Uniform Resource Locator (URL) filtering: URL strings are scanned for target keywords regardless of the domain name specified in the URL. This affects the HTTP protocol. Typical circumvention methods are to use escaped characters in the URL, or to use encrypted protocols such as VPN and TLS/SSL. Packet filtering: Terminate TCP packet transmissions when a certain number of controversial keywords are detected. This affects all TCP-based protocols such as HTTP, FTP and POP, but Search engine results pages are more likely to be censored. Typical circumvention methods are to use encrypted connections – such as VPN and TLS/SSL – to escape the HTML content, or by reducing the TCP/IP stack's MTU/MSS to reduce the amount of text contained in a given packet. Connection reset: If a previous TCP connection is blocked by the filter, future connection attempts from both sides can also be blocked for some variable amount of time. Depending on the location of the block, other users or websites may also be blocked, if the communication is routed through the blocking location. A circumvention method is to ignore the reset packet sent by the firewall. Network disconnection: A technically simpler method of Internet censorship is to completely cut off all routers, either by software or by hardware (turning off machines, pulling out cables). A circumvention method could be to use a satellite ISP to access Internet. Portal censorship and search result removal: Major portals, including search engines, may exclude web sites that they would ordinarily include. This renders a site invisible to people who do not know where to find it. When a major portal does this, it has a similar effect to censorship. Sometimes this exclusion is done to satisfy a legal or other requirement, other times it is purely at the discretion of the portal. For example, Google.de and Google.fr remove Neo-Nazi and other listings in compliance with German and French law. Computer network attacks: Denial-of-service attacks and attacks that deface opposition websites can produce the same result as other blocking techniques, preventing or limiting access to certain websites or other online services, although only for a limited period of time. This technique might be used during the lead up to an election or some other sensitive period. It is more frequently used by non-state actors seeking to disrupt services.
3. Software Implementation, Frameworks & Protocols Writing in 2009, Ronald Deibert, professor of political science at the University of Toronto and co-founder and one of the principal investigators of the OpenNet Initiative, and, writing in 2011, Evgeny Morzov, a visiting scholar at Stanford University and an op-ed contributor to The New York Times, explain that companies in the United States, Finland, France, Germany, Britain, Canada, and South Africa are in part responsible for the increasing sophistication of online content filtering worldwide.
While the off-the-shelf filtering software sold by Internet security companies are primarily marketed to businesses and individuals seeking to protect themselves and their employees and families, they are also used by governments to block what they consider sensitive content. Among the most popular filtering software programs is SmartFilter by Secure Computing in California, which was bought by McAfee in 2008. SmartFilter has been used by Tunisia, Saudi Arabia, Sudan, the UAE, Kuwait, Bahrain, Iran, and Oman, as well as the United States and the UK. Myanmar and Yemen have used filtering software from Websense. The Canadian-made commercial filter Netsweeper is used in Qatar, the UAE, and Yemen. The Canadian organization CitizenLab has reported that Sandvine and Procera products are used in Turkey and Egypt. On 12 March 2013, in a Special Report on Internet Surveillance, Reporters Without Borders named five "Corporate Enemies of the Internet": Amesys (France), Blue Coat Systems (U.S.), Gamma (UK and Germany), HackingTeam (Italy), and Trovicor (Germany). The companies sell products that are liable to be used by governments to violate human rights and freedom of information. RWB said that the list is not exhaustive and will be expanded in the coming months. In a U.S. lawsuit filed in May 2011, Cisco is accused of helping the Chinese government build a firewall, known widely as the Golden Shield, to censor the Internet and keep tabs on dissidents. Cisco said it had made nothing special for China. Cisco is also accused of aiding the Chinese government in monitoring and apprehending members of the banned Falun Gong group. Many filtering programs allow blocking to be configured based on dozens of categories and subcategories. For example, Websense uses over 90 categories, including "abortion", "adult material", "advocacy groups", "drugs", "games", "job search", and "religion". However, these blocking categories can contain errors that lead to the unintended blocking of websites. According to the OpenNet Initiative, the 2007 blocking of Dailymotion in Tunisia resulted from Secure Computing wrongly categorizing Dailymotion as "pornography" in its SmartFilter software. While initial reports suggested the block was due to satirical videos about human rights violations in Tunisia, access was gradually restored after Secure Computing corrected the categorization error.
Organizations such as the Global Network Initiative, the Electronic Frontier Foundation, Amnesty International, and the American Civil Liberties Union have successfully lobbied some vendors such as Websense to make changes to their software, to refrain from doing business with repressive governments, and to educate schools who have inadvertently reconfigured their filtering software too strictly. Nevertheless, regulations and accountability related to the use of commercial filters and services are often non-existent, and there is relatively little oversight from civil society or other independent groups.
Vendors often consider information about what sites and content is blocked valuable intellectual property that is not made available outside the company, sometimes not even to the organizations purchasing the filters. Thus by relying upon out-of-the-box filtering systems, the detailed task of deciding what is or is not acceptable speech may be outsourced to the commercial vendors.
Internet content is also subject to censorship methods similar to those used with more traditional media. For example: Laws and regulations may prohibit various types of content and/or require that content be removed or blocked either proactively or in response to requests. Publishers, authors, and ISPs may receive formal and informal requests to remove, alter, slant, or block access to specific sites or content. Publishers and authors may accept bribes to include, withdraw, or slant the information they present. Publishers, authors, and ISPs may be subject to arrest, criminal prosecution, fines, and imprisonment. Publishers, authors, and ISPs may be subject to civil lawsuits. Equipment may be confiscated and/or destroyed. Publishers and ISPs may be closed or required licenses may be withheld or revoked. Publishers, authors, and ISPs may be subject to boycotts. Publishers, authors, and their families may be subject to threats, attacks, beatings, and even murder. Publishers, authors, and their families may be threatened with or actually lose their jobs. Individuals may be paid to write articles and comments in support of particular positions or attacking opposition positions, usually without acknowledging the payments to readers and viewers. Censors may create their own online publications and Web sites to guide online opinion. Access to the Internet may be limited due to restrictive licensing policies or high costs. Access to the Internet may be limited due to a lack of the necessary infrastructure, deliberate or not. Access to search results may be restricted due to government involvement in the censorship of specific search terms, content may be excluded due to terms set with search engines. By allowing search engines to operate in new territory they must agree to abide to censorship standards set by the government in that country.
Internet censorship circumvention is one of the processes used by technologically savvy Internet users to bypass the technical aspects of Internet filtering and gain access to the otherwise censored material. Circumvention is an inherent problem for those wishing to censor the Internet because filtering and blocking do not remove content from the Internet, but instead block access to it. Therefore, as long as there is at least one publicly accessible uncensored system, it will often be possible to gain access to the otherwise censored material. However circumvention may not be possible by non-tech-savvy users, so blocking and filtering remain effective means of censoring the Internet access of large numbers of users. Different techniques and resources are used to bypass Internet censorship, including proxy websites, virtual private networks, sneakernets, the dark web and circumvention software tools. Solutions have differing ease of use, speed, security, and risks.
Most, however, rely on gaining access to an Internet connection that is not subject to filtering, often in a different jurisdiction not subject to the same censorship laws. According to GlobalWebIndex, over 400 million people use virtual private networks to circumvent censorship or for an increased level of privacy. The majority of circumvention techniques are not suitable for day to day use. There are risks to using circumvention software or other methods to bypass Internet censorship. In some countries, individuals that gain access to otherwise restricted content may be violating the law and if caught can be expelled, fired, jailed, or subject to other punishments and loss of access. In June 2011, The New York Times reported that the U.S. is engaged in a "global effort to deploy 'shadow' Internet and mobile phone systems that dissidents can use to undermine repressive governments that seek to silence them by censoring or shutting down telecommunications networks." Another way to circumvent Internet censorship is to physically go to an area where the Internet is not censored. In 2017, a so-called "Internet refugee camp" was established by IT workers in the village of Bonako, just outside an area of Cameroon where the Internet is regularly blocked.
Internet controls and censorship directed at political opposition to the ruling government have been associated with higher authoritarianism. Internet controls can be categorized in pervasive internet control and more subtle internet influence operations. Examples include: Political blogs and websites religion and minority groups, when these movements represent a threat to the ruling regime Falun Gong and Tibetan exile group sites in China or Buddhist, Cao Dai faith, and indigenous hill tribes sites in Vietnam Sites aimed at religious conversion from Islam to Christianity Sites that comment on minorities or LGBTQ issues Lèse-majesté sites, sites with content that offends the dignity of or challenges the authority of a reigning sovereign or of a state 50 Cent Party, or "50 Cent Army" that worked to sway negative public opinion on the Chinese Communist Party Russian web brigades Sites criticizing the government or an authority in the country Sites that comment on political parties that oppose the current government of a country Sites that accuse authorities of corruption Communist symbols and imagery in Poland, Lithuania, Ukraine, Georgia, Latvia, Moldova, Hungary, and Indonesia Neo-Nazi and similar websites, particularly in France and Germany Sites that include hate speech inciting racism, sexism, homophobia, transphobia or other forms of bigotry Sites seen as promoting illegal drug use (such as Erowid) Sex and erotic, fetishism, prostitution, and pornographic sites Child pornography and pedophile-related sites (see also CIRCAMP) Gambling sites Sites encouraging or inciting violence Sites promoting criminal activity Sites that contain blasphemous content, particularly when directed at a majority or state supported religion Sites that contain defamatory, slanderous, or libelous content Sites that include political satire Sites that contain information on social issues or "online protests, petitions and campaign" Blocking of pro–North Korean sites by South Korea Blocking of sites of groups that foment domestic conflict in India Blocking of sites of the Muslim Brotherhood in some countries in the Middle East Blocking of sites such as 4chan thought to be related to the internet hacker group Anonymous 4. Practical Deployment, Analysis & Case Studies File sharing and peer-to-peer (P2P) related websites such as The Pirate Bay Sites that sell or distribute music, but are not 'approved' by rights holders, such as AllOfMP3 In 2011, the government of the United States proposed the SOPA and PIPA laws, which would have required entire websites blocked or shut down if they hosted material that violated copyright. On 18 January 2012, many websites including Wikipedia blacked out for the day to protest against these proposed laws. The bills were eventually killed off. On 9 June 2019, the EU passed UploadFilter which would have infringed on user-generated content, but excluded in Article 13 of the law due to similar large outcry over concerns that the filter might destroy user-generated content.
Media sharing websites (e.g. Flickr and YouTube) Social networks (e.g. Facebook and Instagram) Translation sites and tools E-mail providers Web hosting sites Blog hosting sites such as Blogspot and Medium Microblogging sites such as Twitter and Weibo Wikipedia Censorship circumvention sites Anonymizers Proxy avoidance sites Search engines such as Bing and Google – particularly in Mainland China and Cuba The right to be forgotten is a concept that has been discussed and put into practice in the European Union. In May 2014, the European Court of Justice ruled against Google in Costeja, a case brought by a Spanish man who requested the removal of a link to a digitized 1998 article in La Vanguardia newspaper about an auction for his foreclosed home, for a debt that he had subsequently paid. He initially attempted to have the article removed by complaining to Spain's data protection agency—Agencia Española de Protección de Datos—which rejected the claim on the grounds that it was lawful and accurate, but accepted a complaint against Google and asked Google to remove the results. Google sued in Spain and the lawsuit was transferred to the European Court of Justice. The court ruled in Costeja that search engines are responsible for the content they point to and thus, Google was required to comply with EU data privacy laws. It began compliance on 30 May 2014 during which it received 12,000 requests to have personal details removed from its search engine. Index on Censorship claimed that "Costeja ruling ... allows individuals to complain to search engines about information they do not like with no legal oversight.
This is akin to marching into a library and forcing it to pulp books. Although the ruling is intended for private individuals it opens the door to anyone who wants to whitewash their personal history....The Court's decision is a retrograde move that misunderstands the role and responsibility of search engines and the wider internet. It should send chills down the spine of everyone in the European Union who believes in the crucial importance of free expression and freedom of information." From 1995 to 2002, the government of South Korea passed the Telecommunications Business Act (TBA), the first internet censorship law in the world. As more people in more places begin using the Internet for important activities, there is an increase in online censorship, using increasingly sophisticated techniques. The motives, scope, and effectiveness of Internet censorship vary widely from country to country. The countries engaged in state-mandated filtering are clustered in three main regions of the world: east Asia, central Asia, and the Middle East/North Africa. Countries in other regions also practice certain forms of filtering. In the United States, state-mandated Internet filtering occurs on some computers in libraries and K–12 schools. Content related to Nazism or Holocaust denial is blocked in France and Germany. Child pornography and hate speech are blocked in many countries throughout the world. In fact, many countries throughout the world, including some democracies with long traditions of strong support for freedom of expression and freedom of the press, are engaged in some amount of online censorship, often with substantial public support. Internet censorship in China is among the most stringent in the world. The government blocks Web sites that discuss the Dalai Lama, the 1989 crackdown on Tiananmen Square protesters, the banned spiritual practice Falun Gong, as well as many general Internet sites. The government requires Internet search firms and state media to censor issues deemed officially "sensitive," and blocks access to foreign websites including Facebook, Twitter, and YouTube. According to a study in 2014, censorship in China is used to muzzle those outside government who attempt to spur the creation of crowds for any reason—in opposition to, in support of, or unrelated to the government. There are international bodies that oppose internet censorship, for example "Internet censorship is open to challenge at the World Trade Organization (WTO) as it can restrict trade in online services, a forthcoming study argues". On 28 November 2024, Australia passed a social media ban for users under 16, this, along with The Anxious Generation by Johnathan Haidt and the UK's Online Safety Act have led to many other countries and subdivisions to enact or propose similar social media bans, with similar actions following in Brazil and Indonesia in March 2026, Malaysia in June 2026 and Florida by mid-June 2026. As a result of these proposals, some online platforms such as Roblox have made their age verification policies global in order to close loopholes around these policies because if they fail to comply, they could face heavy fines.
Since 2023, many countries and subdivisions across the globe have passed or proposed laws to require age verification for parts of the internet, including social media services, social networks, devices, and other digital services with the intention of protecting young people from harmful and illegal content. Most of the passed laws or bills have the age verification process done through handing over a government-issued ID, a facial scan or credit card, in order to prove that they are not underage, with the process often done with third-party age verification providers. These laws and proposals vary greatly, with some of them restricting access only to certain features or distinguishing between different users online, which could lead to companies requiring age verification to comply with such restrictions as the Kids Online Safety Act, or banning users under a certain age, which is the approach of the Online Safety Amendment in Australia which fully prohibits anyone under 16 years old from holding social media accounts. A few nations, such as Pakistan, have proposed punishing those who allow minors to access these services. These laws have received criticism from some, including organizations that focus on digital and civil rights (such as the Electronic Frontier Foundation, Access Now, the V-Dem Institute and the American Civil Liberties Union in the United States) for normalizing surveillance and restricting freedom of speech through the elimination of anonymous accounts. The New Zealand Council for Civil Liberties, UNICEF, and the Council of Europe Commissioner for Human Rights have also opposed such laws on the basis that they constitute violations of the rights to freedom of speech and privacy, that such laws may backfire, and that there are better ways of protecting children online. These laws can also be bypassed by loopholes, such as VPNs, which have seen a significant increase in users in countries where such laws are enforced. While these laws typically only apply in their respective countries, some online platforms (such as Roblox) made their age verification policies global, and Discord, which require age verification for certain features to close said loopholes to avoid receiving a lawsuit. Despite these laws being mainly used for requiring social media services to verify the age of their users, critics even believe that these laws would silently expand beyond the internet and create a realm of digital censorship, with devices, apps, games, and websites being required to age verify their users with intrusive methods such as with a facial scan or the presentation of a government ID as a result of mission creep. Despite recent online protests over Internet censorship, there have been no physical protests related to age verification despite recent protest over internet censorship. Critics worry that media outlets such as BBC and CNN will silence these views. On 6 August 2026, a Texas man, Joseph Roy Ozment became the first person to be arrested for using voicemail to threaten the Texas Governor's Office over age verification on Crunchyroll.
Several governments have resorted to shutting down most or all Internet connections in all or part of the country. This appears to have been the case on 27 and 28 January 2011 during the 2011 Egyptian revolution, in what has been widely described as an "unprecedented" internet block. About 3500 Border Gateway Protocol (BGP) routes to Egyptian networks were shut down from about 22:10 to 22:35 UTC 27 January. This full block was implemented without cutting off major intercontinental fibre-optic links, with Renesys stating on 27 January, "Critical European-Asian fiber-optic routes through Egypt appear to be unaffected for now." Full blocks also occurred in Myanmar/Burma in 2007, Libya in 2011, Iran in 2019, and Syria during the Syrian civil war. Almost all Internet connections in Sudan were disconnected from 3 June to 9 July 2019, in response to a political opposition sit-in seeking civilian rule. and since the beginning of the civil war in April 2023 between the Sudanese Armed Forces (SAF) and the Rapid Support Forces (RSF), there have been series of Internet shutdowns in Sudan. A near-complete shutdown in Ethiopia lasted for a week after the Amhara Region coup attempt. A week-long shutdown in Mauritania followed disputes over the 2019 Mauritanian presidential election. Other country-wide shutdowns in 2019 include Zimbabwe after a gasoline price protests triggered police violence, Gabon during the 2019 Gabonese coup attempt, and during or after elections in Democratic Republic of the Congo, Benin, Malawi, and Kazakhstan. Local shutdowns are frequently ordered in India during times of unrest and security concerns. Some countries have used localized Internet shutdowns to combat cheating during exams, including Iraq, Ethiopia, India, Algeria, and Uzbekistan. The Iranian government imposed a total internet shutdown from 16 to 23 November 2019, in response to the fuel protests. Doug Madory, the director of Internet analysis at Oracle, has described the operation as "unusual in its scale" and way more advanced. Beginning Saturday afternoon on 16 November 2019, the government of Iran ordered the disconnection of much of the country's internet connectivity as a response to widespread protests against the government's decision to raise gas prices. While Iran is no stranger to government-directed interference in its citizens’ access to the internet, this outage is notable in how it differs from past events. Unlike previous efforts at censorship and bandwidth throttling, the internet of Iran is presently experiencing a multi-day wholesale disconnection for much of its population – arguably the largest such event ever for Iran.
The 2014 report assessed 65 countries and reported that 36 countries experienced a negative trajectory in Internet freedom since the previous year, with the most significant declines in Russia, Turkey and Ukraine. According to the report, few countries demonstrated any gains in Internet freedom, and the improvements that were recorded reflected less vigorous application of existing controls rather than new steps taken by governments to actively increase Internet freedom. The year's largest improvement was recorded in India, where restrictions to content and access were relaxed from what had been imposed in 2013 to stifle rioting in the northeastern states. Notable improvement was also recorded in Brazil, where lawmakers approved the bill Marco Civil da Internet, which contains significant provisions governing net neutrality and safeguarding privacy protection.
When the "Enemies of the Internet" list was introduced in 2006, it listed 13 countries. From 2006 to 2012 the number of countries listed fell to 10 and then rose to 12. The list was not updated in 2013. In 2014 the list grew to 19 with an increased emphasis on surveillance in addition to censorship. The list has not been updated since 2014. When the "Countries under surveillance" list was introduced in 2008, it listed 10 countries. Between 2008 and 2012 the number of countries listed grew to 16 and then fell to 11. The number grew to 12 with the addition of Norway in 2020. The list was last updated in 2020.
5. Performance Evaluation & Extended Technical Observations a list of "State Enemies of the Internet", countries whose governments are involved in active, intrusive surveillance of news providers, resulting in grave violations of freedom of information and human rights; and a list of "Corporate Enemies of the Internet", companies that sell products that are liable to be used by governments to violate human rights and freedom of information. The five "State Enemies of the Internet" named in March 2013 are: Bahrain, China, Iran, Syria, and Vietnam. The five "Corporate Enemies of the Internet" named in March 2013 are: Amesys (France), Blue Coat Systems (U.S.), Gamma Group (UK and Germany), HackingTeam (Italy), and Trovicor (Germany).
Despite worries about privacy and fraud, people around the world see access to the internet as their fundamental right. They think the web is a force for good, and most don't want governments to regulate it. Findings from the poll include: Nearly four in five (78%) Internet users felt that the Internet had brought them greater freedom. Most Internet users (53%) felt that "the internet should never be regulated by any level of government anywhere". Opinion was evenly split between Internet users who felt that "the internet is a safe place to express my opinions" (48%) and those who disagreed (49%). Users in Germany and France agreed the least, followed by users in a highly filtered country such as China, while users in Egypt, India and Kenya agreed more strongly. The aspects of the Internet that cause the most concern include: fraud (32%), violent and explicit content (27%), threats to privacy (20%), state censorship of content (6%), and the extent of corporate presence (3%).
Almost four in five Internet users and non-users around the world felt that access to the Internet was a fundamental right (50% strongly agreed, 29% somewhat agreed, 9% somewhat disagreed, 6% strongly disagreed, and 6% gave no opinion). And while there is strong support for this right in all of the countries surveyed, it is surprising that the United States and Canada were among the top five countries where people most strongly disagreed that access to the Internet was a fundamental right of all people (13% in Japan, 11% in the U.S., 11% in Kenya, 11% in Pakistan, and 10% in Canada strongly disagree).
Saudi Arabia and the United Arab Emirates (UAE) are among the few states that publish detailed information about their filtering practices and display a notification to the user when attempting to access a blocked website. The websites that are blocked are mostly pornographic or considered un-Islamic. In contrast, countries such as China and Tunisia send users a false error indication. China blocks requests by users for a banned website at the router level and a connection error is returned, effectively preventing the user's IP address from making further HTTP requests for a varying time, which appears to the user as "time-out" error with no explanation. Tunisia has altered the block page functionality of SmartFilter, the commercial filtering software it uses, so that users attempting to access blocked websites receive a fake "File not found" error page. In Uzbekistan, users are frequently sent block pages stating that the website is blocked because of pornography, even when the page contains no pornography. Uzbeki ISPs may also redirect users' request for blocked websites to unrelated websites, or sites similar to the banned websites, but with different information.
During the Arab Spring of 2011, media jihad (media struggle) was extensive. Internet and mobile technologies, particularly social networks such as Facebook and Twitter, played and are playing important new and unique roles in organizing and spreading the protests and making them visible to the rest of the world. An activist in Egypt tweeted, "we use Facebook to schedule the protests, Twitter to coordinate, and YouTube to tell the world". This successful use of digital media in turn led to increased censorship including the complete loss of Internet access for periods of time in Egypt and Libya in 2011. In Syria, the Syrian Electronic Army (SEA), an organization that operates with at least tacit support of the government, claims responsibility for defacing or otherwise compromising scores of websites that it contends spread news hostile to the Syrian government. SEA disseminates denial of service (DoS) software designed to target media websites including those of Al Jazeera, BBC News, Syrian satellite broadcaster Orient TV, and Dubai-based Al Arabiya TV. In response to the greater freedom of expression brought about by the Arab Spring revolutions in countries that were previously subject to very strict censorship, in March 2011, Reporters Without Borders moved Tunisia and Egypt from its "Internet enemies" list to its list of countries "under surveillance" and in 2012 dropped Libya from the list entirely. At the same time, there were warnings that Internet censorship might increase in other countries following the events of the Arab Spring. However, in 2013, Libyan communication company LTT blocked the pornographic websites. It even blocked the family-filtered videos of ordinary websites like Dailymotion.
Accountability software – Type of surveillance software Block (Internet) – a technical measure intended to restrict access to information or resources Cleanfeed – a content blocking system in use in the UK and Canada Computer and network surveillance – Monitoring of computer or network activity Content moderation – System to sort undesirable contributions Anti-copyright – Dissenting views of copyright lawPages displaying short descriptions of redirect targets Copyleft – Preservation of legal rights in the reuse of a work Criticism of copyright Cyber-dissident – Person who voices political dissent on the Internet The Digital Imprimatur – a 2003 article about Internet censorship and digital rights management by John Walker, co-founder of the computer-aided design software company Autodesk Digital rights – Type of human and legal rights Firewall (computing) – Software or hardware-based network security system Great Firewall – Chinese internet regulations Internet censorship circumvention – Methods to bypass internet censorship Internet filter – Software that restricts or controls the content an Internet user is capable to access Internet police – Term describing governmental and official involvement in cyber policing Internet activism – Use of the internet to facilitate activism National Information Network of Iran 2019 Internet blackout in Iran Internet safety Online age verifcation laws by country Censorship Wikia, an anti-censorship site that catalogs past and present censored works, using verifiable sources, and a forum to discuss organizing against and circumventing censorship. "Index on Censorship", website of Index on Censorship, a London-based organization and magazine that promotes freedom of expression. Internet censorship wiki (Archived 2017-06-07 at the Wayback Machine) provided information about different methods of access filtering and ways to bypass them. "Online Survival Kit", We Fight Censorship project of Reporters Without Borders. "Media Freedom Internet Cookbook" by the OSCE Representative on Freedom of the Media, Vienna, 2004. How to Bypass Internet Censorship Archived 2 February 2016 at the Wayback Machine, also known by the titles: Bypassing Internet Censorship or Circumvention Tools, a FLOSS Manual, 10 March 2011, 240 pp. RFC 9505: A Survey of Worldwide Censorship Techniques The Secure Shell Protocol (SSH Protocol) is a cryptographic network protocol for operating network services securely over an unsecured network. Its most notable applications are remote login and command-line execution. SSH was designed for Unix-like operating systems as a replacement for Telnet and unsecured remote Unix shell protocols, such as the Berkeley Remote Shell (rsh) and the related rlogin and rexec protocols, which all use insecure, plaintext methods of authentication, such as passwords. Since mechanisms like Telnet and Remote Shell are designed to access and operate remote computers, sending the authentication tokens (e.g. username and password) for this access to these computers across a public network in an unsecured way poses a great risk of third parties obtaining the password and achieving the same level of access to the remote system as the telnet user. Secure Shell mitigates this risk through the use of encryption mechanisms that are intended to hide the contents of the transmission from an observer, even if the observer has access to the entire data stream. Finnish computer scientist Tatu Ylönen designed SSH in 1995 and provided an implementation in the form of two commands, ssh and slogin, as secure replacements for rsh and rlogin, respectively. Subsequent development of the protocol suite proceeded in several developer groups, producing several variants of implementation. The protocol specification distinguishes two major versions, referred to as SSH-1 and SSH-2. The most commonly implemented software stack is OpenSSH, released in 1999 as open-source software by the OpenBSD developers. Implementations are distributed for all types of operating systems in common use, including embedded systems. SSH applications are based on a client–server architecture, connecting an SSH client instance with an SSH server. SSH operates as a layered protocol suite comprising three principal hierarchical components: the transport layer provides server authentication, confidentiality, and integrity; the user authentication protocol validates the user to the server; and the connection protocol multiplexes the encrypted tunnel into multiple logical communication channels.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Simple%20Network%20Management%20Protocol • https://en.wikipedia.org/wiki/Internet%20censorship • https://en.wikipedia.org/wiki/Secure%20Shell
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Ftp Attack Monitoring And Automatic IP Blocking Tool.
[*] Metasploit Scan Running on Target Subnet for Ftp Attack Monitoring And Automatic IP Blocking Tool... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |