Complete Technical Paper Content — Gdpr Compliance Tracking System
Overview & System Context
Gdpr Compliance Tracking System: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9523 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background An HTTP cookie (also called web cookie, Internet cookie, browser cookie, or simply cookie) is a small block of data created by a web server while a user is browsing a website and placed on the user's computer or other device by the user's web browser.
Cookies are placed on the device used to access a website, and more than one cookie may be placed on a user's device during a session. Cookies serve useful and sometimes essential functions on the web. They enable web servers to store stateful information (such as items added in the shopping cart in an online store) on the user's device or to track the user's browsing activity (including clicking particular buttons, logging in, or recording which pages were visited in the past). They can also be used to save information that the user previously entered into form fields, such as names, addresses, passwords, and payment card numbers for subsequent use. Authentication cookies are commonly used by web servers to authenticate that a user is logged in, and with which account they are logged in. Without the cookie, users would need to authenticate themselves by logging in on each page containing sensitive information that they wish to access. The security of an authentication cookie generally depends on the security of the issuing website and the user's web browser, and on whether the cookie data is encrypted. Security vulnerabilities may allow a cookie's data to be read by an attacker, used to gain access to user data, or used to gain access (with the user's credentials) to the website to which the cookie belongs (see cross-site scripting and cross-site request forgery for examples). Tracking cookies, and especially third-party tracking cookies, are commonly used as ways to compile long-term records of individuals' browsing histories — a potential privacy concern that prompted European and U.S. lawmakers to take action in 2011. European law requires that all websites targeting European Union member states gain "informed consent" from users before storing non-essential cookies on their device.
A zombie cookie is data and code that has been placed by a web server on a visitor's computer or other device in a hidden location outside the visitor's web browser's dedicated cookie storage location, and that automatically recreates a HTTP cookie as a regular cookie after the original cookie had been deleted. The zombie cookie may be stored in multiple locations, such as Flash Local shared object, HTML5 Web storage, and other client-side and even server-side locations, and when absence is detected in one of the locations, the missing instance is recreated by the JavaScript code using the data stored in other locations.
Name Value Zero or more attributes (name/value pairs). Attributes store information such as the cookie's expiration, domain, and flags (such as Secure and HttpOnly). Tracking cookies are used to track users' web browsing habits. This can also be done to some extent by using the IP address of the computer requesting the page or the referer field of the HTTP request header, but cookies allow for greater precision.
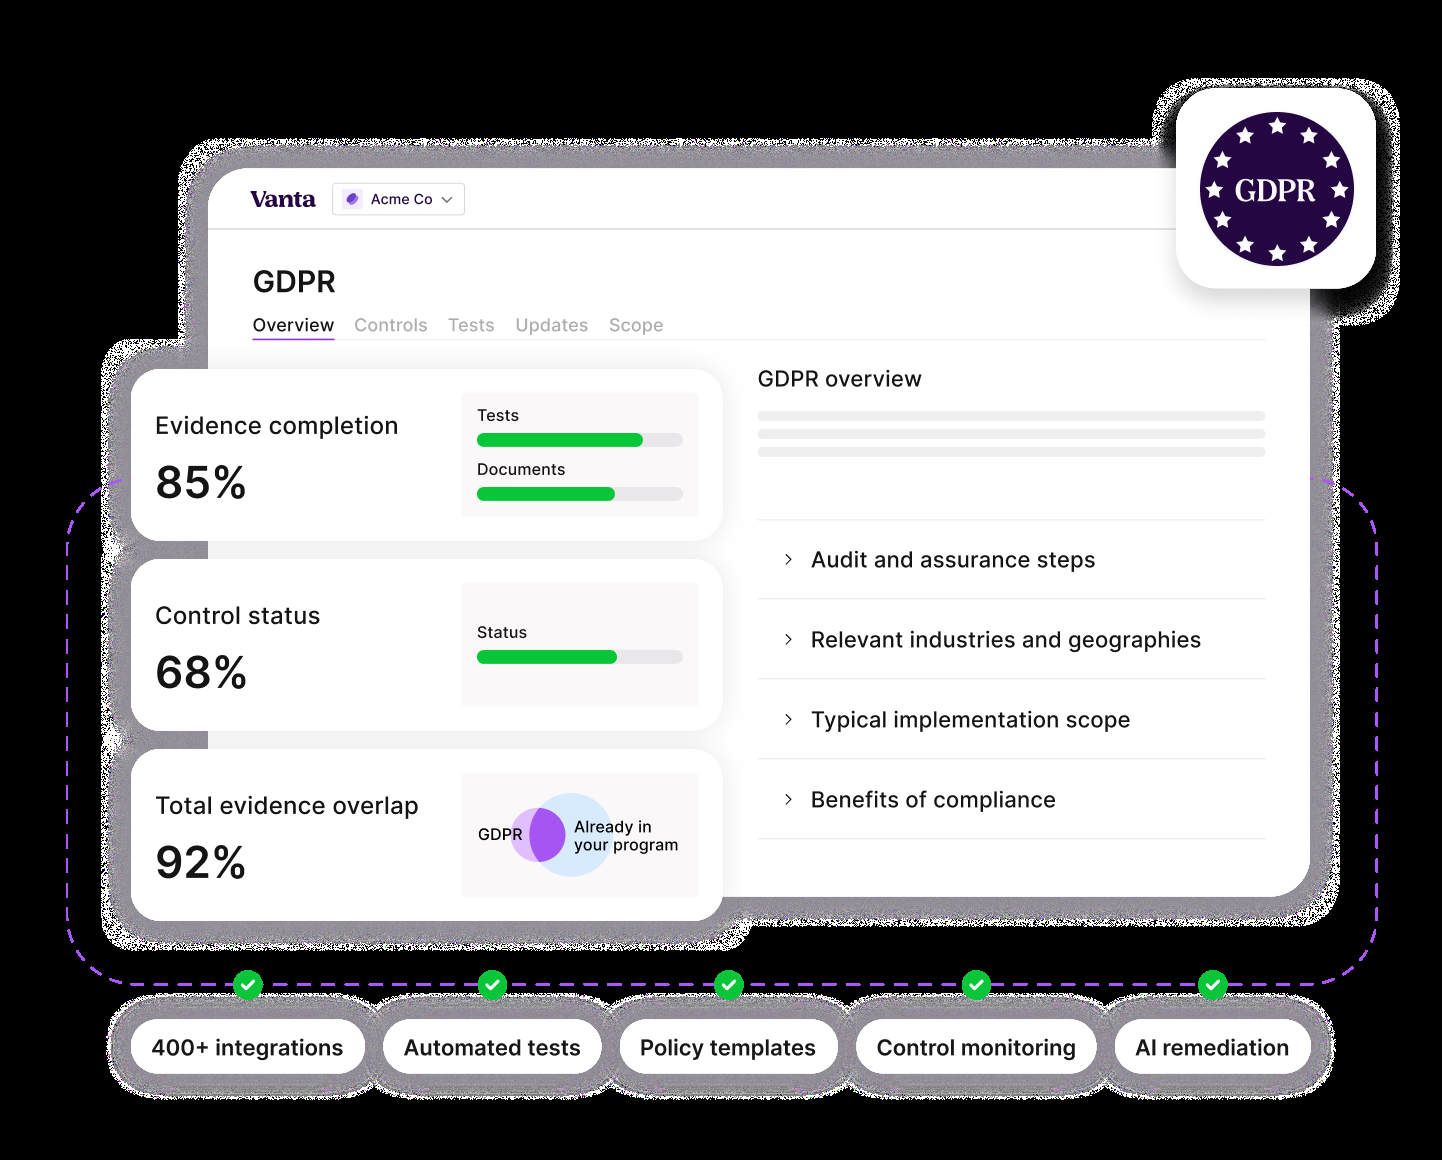
This can be demonstrated as follows: Figure 1: GDPR compliance software If the user requests a page of the site, but the request contains no cookie, the server presumes that this is the first page visited by the user. So the server creates a unique identifier (typically a string of random letters and numbers) and sends it as a cookie back to the browser together with the requested page. From this point on, the cookie will automatically be sent by the browser to the server every time a new page from the site is requested. The server not only sends the page as usual but also stores the URL of the requested page, the date/time of the request, and the cookie in a log file. By analyzing this log file, it is then possible to discover which pages the user has visited, in what sequence, and for how long. Corporations exploit users' web habits by tracking cookies to collect information about buying habits. The Wall Street Journal found that America's top fifty websites installed an average of sixty-four pieces of tracking technology onto computers, resulting in a total of 3,180 tracking files. The data can then be collected and sold to bidding corporations.
Cookies are arbitrary pieces of data, usually chosen and first sent by the web server, and stored on the client computer by the web browser. The browser then sends them back to the server with every request, introducing states (memory of previous events) into otherwise stateless HTTP transactions. Without cookies, each retrieval of a web page or component of a web page would be an isolated event, largely unrelated to all other page views made by the user on the website. Although cookies are usually set by the web server, they can also be set by the client using a scripting language such as JavaScript (unless the cookie's HttpOnly flag is set, in which case the cookie cannot be modified by scripting languages). The cookie specifications require that browsers meet the following requirements in order to support cookies: Can support cookies as large as 4,096 bytes in size. Can support at least 50 cookies per domain (i.e. per website). Can support at least 3,000 cookies in total.
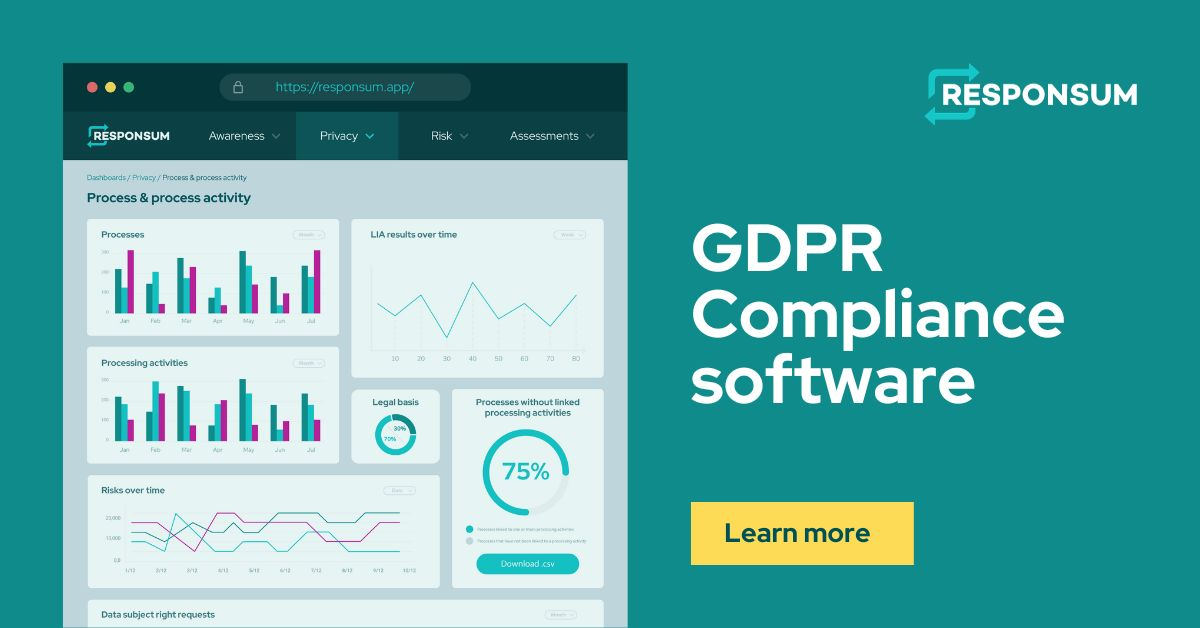
The server's HTTP response contains the contents of the website's homepage. But it also instructs the browser to set two cookies. The first, theme, is considered to be a session cookie since it does not have an Expires or Max-Age attribute. Session cookies are intended to be deleted by the browser when the browser closes. The second, sessionToken, is considered to be a persistent cookie since it contains an Expires attribute, which instructs the browser to delete the cookie at a specific date and time. Next, the browser sends another request to visit the spec.html page on the website. This request contains a Cookie header field, which contains the two cookies that the server instructed the browser to set: Figure 2: GDPR Compliance Software | Responsum This way, the server knows that this HTTP request is related to the previous one. The server would answer by sending the requested page, possibly including more Set-Cookie header fields in the HTTP response in order to instruct the browser to add new cookies, modify existing cookies, or remove existing cookies. To remove a cookie, the server must include a Set-Cookie header field with an expiration date in the past. The value of a cookie may consist of any printable ASCII character (! through ~, Unicode \u0021 through \u007E) excluding ,and; and whitespace characters. The name of a cookie excludes the same characters, as well as =, since that is the delimiter between the name and value. The cookie standard RFC 2965 is more restrictive but not implemented by browsers. The term cookie crumb is sometimes used to refer to a cookie's name–value pair. Cookies can also be set by scripting languages such as JavaScript that run within the browser. In JavaScript, the object document.cookie is used for this purpose. For example, the instruction document.cookie = "temperature=20" creates a cookie of name temperature and value 20.
The first cookie, LSID, has no Domain attribute, and has a Path attribute set to /accounts. This tells the browser to use the cookie only when requesting pages contained in docs.foo.com/accounts (the domain is derived from the request domain). The other two cookies, HSID and SSID, would be used when the browser requests any subdomain in .foo.com on any path (for example www.foo.com/bar). The prepending dot is optional in recent standards, but can be added for compatibility with RFC 2109 based implementations.
The first cookie, lu, is set to expire sometime on 15 January 2013. It will be used by the client browser until that time. The second cookie, made_write_conn, does not have an expiration date, making it a session cookie. It will be deleted after the user closes their browser. The third cookie, reg_fb_gate, has its value changed to deleted, with an expiration time in the past. The browser will delete this cookie right away because its expiration time is in the past. Note that cookie will only be deleted if the domain and path attributes in the Set-Cookie field match the values used when the cookie was created. As of 2016 Internet Explorer did not support Max-Age.
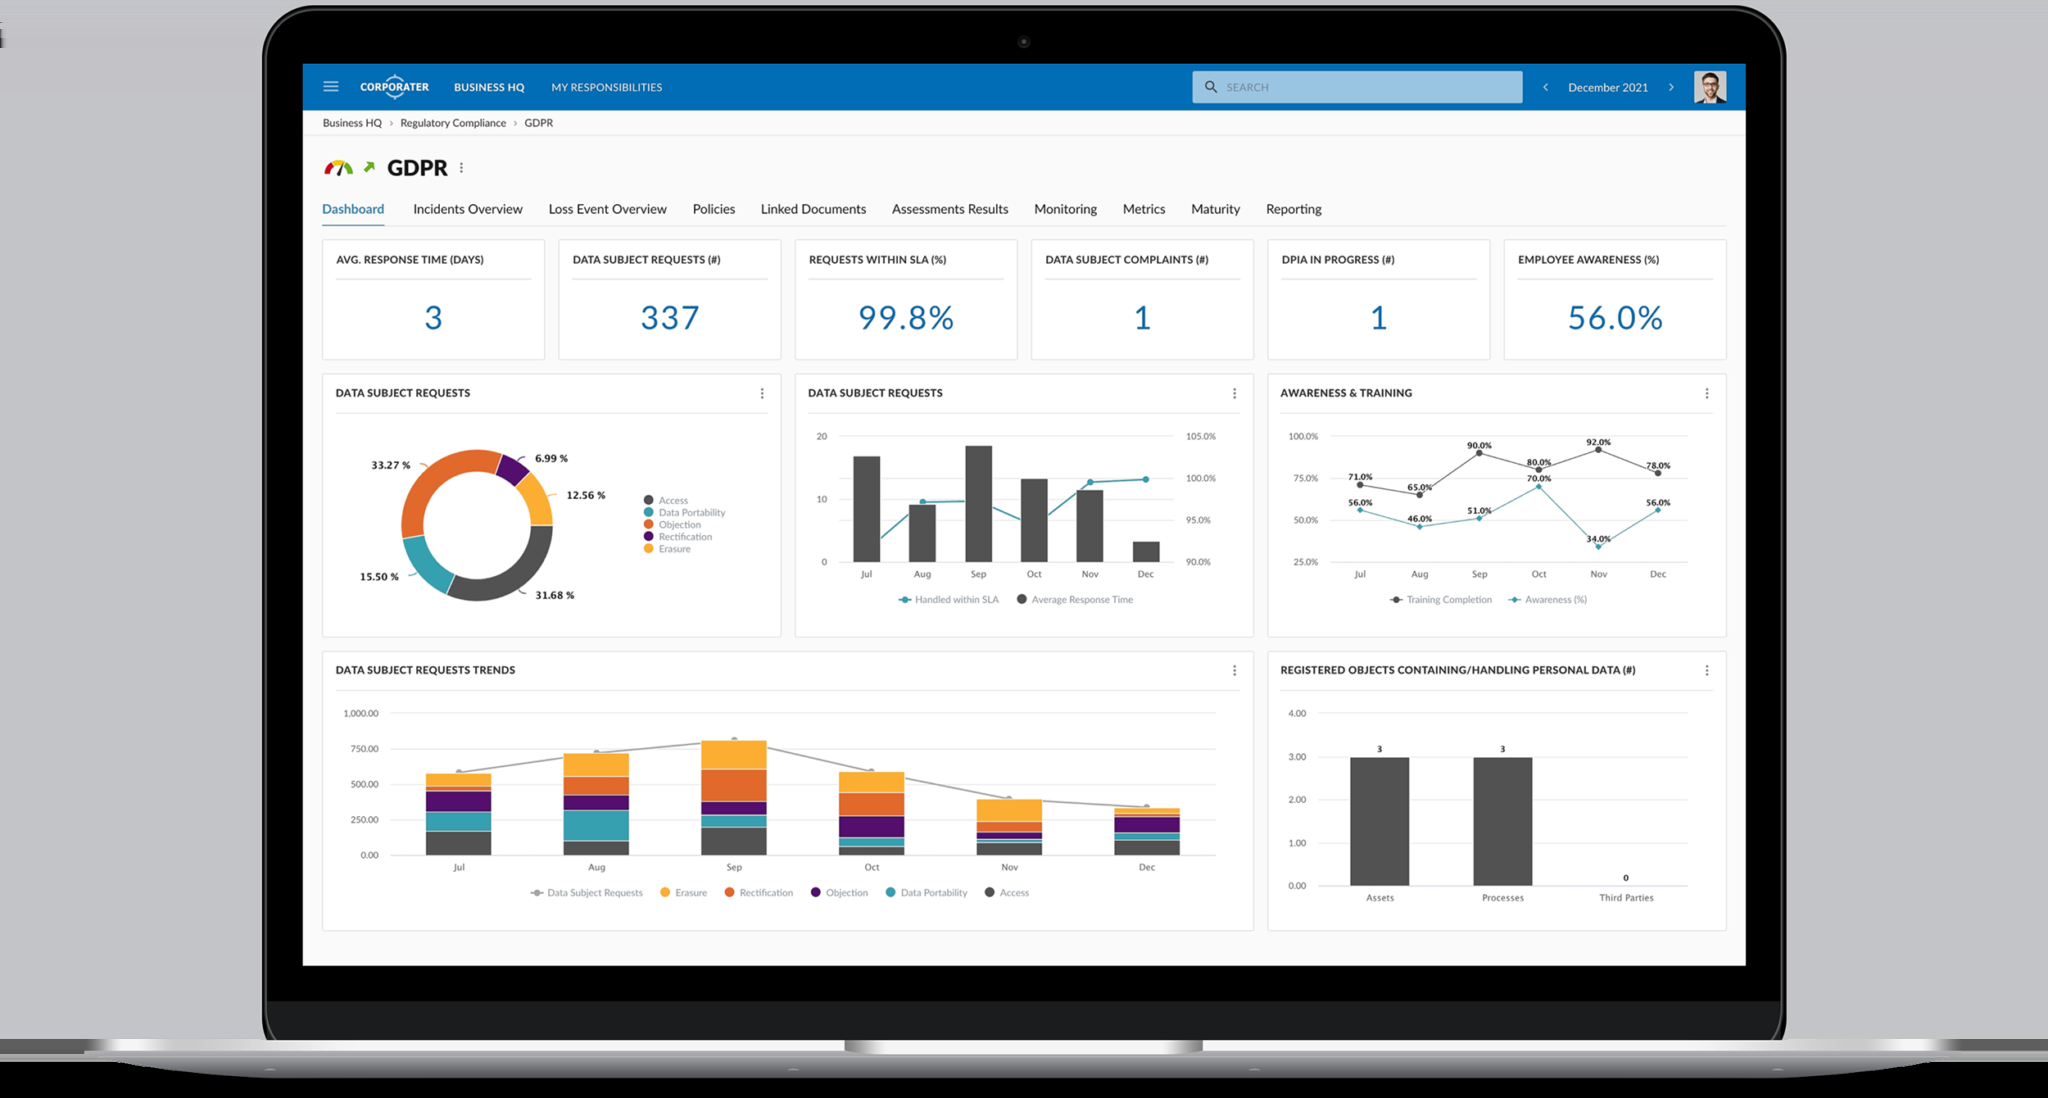
To enable or disable cookies completely, so that they are always accepted or always blocked. To view and selectively delete cookies using a cookie manager. To fully wipe all private data, including cookies. Add-on tools for managing cookie permissions also exist. Figure 3: GDPR Compliance Software | Compliance Management Solutions | Corporater Cookies have some important implications for the privacy and anonymity of web users. While cookies are sent only to the server setting them or a server in the same Internet domain, a web page may contain images or other components stored on servers in other domains. Cookies that are set during retrieval of these components are called third-party cookies. A third-party cookie, belongs to a domain different from the one shown in the address bar. This sort of cookie typically appears when web pages feature content from external websites, such as banner advertisements. This opens up the potential for tracking the user's browsing history and is used by advertisers to serve relevant advertisements to each user.
As an example, suppose a user visits www.example.org. This website contains an advertisement from ad.foxytracking.com, which, when downloaded, sets a cookie belonging to the advertisement's domain (ad.foxytracking.com). Then, the user visits another website, www.foo.com, which also contains an advertisement from ad.foxytracking.com and sets a cookie belonging to that domain (ad.foxytracking.com). Eventually, both of these cookies will be sent to the advertiser when loading their advertisements or visiting their website. The advertiser can then use these cookies to build up a browsing history of the user across all the websites that have ads from this advertiser, through the use of the HTTP referer header field. As of 2014, some websites were setting cookies readable for over 100 third-party domains. On average, a single website was setting 10 cookies, with a maximum number of cookies (first- and third-party) reaching over 800. The older standards for cookies, RFC 2109 and RFC 2965, recommend that browsers should protect user privacy and not allow sharing of cookies between servers by default. However, the newer standard, RFC 6265, explicitly allows user agents to implement whichever third-party cookie policy they wish. Most modern web browsers contain privacy settings that can block third-party cookies. Since 2020, Apple Safari, Firefox, and Brave block all third-party cookies by default. Safari allows embedded sites to use Storage Access API to request permission to set first-party cookies. In May 2020, Google Chrome 83 introduced new features to block third-party cookies by default in its Incognito mode for private browsing, making blocking optional during normal browsing. The same update also added an option to block first-party cookies. In April 2024, Chrome postponed third-party cookie blocking by default to 2025. In July 2024, Google announced plan to avoid blocking third-party cookies by default and instead prompt users to allow third-party cookies.
The possibility of building a profile of users is a privacy threat, especially when tracking is done across multiple domains using third-party cookies. For this reason, some countries have legislation about cookies. Website operators who do not disclose third-party cookie use to consumers run the risk of harming consumer trust if cookie use is discovered. Having clear disclosure (such as in a privacy policy) tends to eliminate any negative effects of such cookie discovery. The government of the United States set strict rules on setting cookies in 2000 after it was disclosed that the White House drug policy office used cookies to track computer users viewing its online anti-drug advertising. In 2002, privacy activist Daniel Brandt found that the CIA had been leaving persistent cookies on computers that had visited its website. When notified it was violating policy, CIA stated that these cookies were not intentionally set and stopped setting them. On 25 December 2005, Brandt discovered that the National Security Agency (NSA) had been leaving two persistent cookies on visitors' computers due to a software upgrade. After being informed, the NSA immediately disabled the cookies.
In 2002, the European Union launched the Directive on Privacy and Electronic Communications (e-Privacy Directive), a policy requiring end users' consent for the placement of cookies, and similar technologies for storing and accessing information on users' equipment. In particular, Article 5 Paragraph 3 mandates that storing technically unnecessary data on a user's computer can only be done if the user is provided information about how this data is used, and the user is given the possibility of denying this storage operation. The Directive does not require users to authorise or be provided notice of cookie usage that are functionally required for delivering a service they have requested, for example to retain settings, store log-in sessions, or remember what is in a user's shopping basket. In 2009, the law was amended by Directive 2009/136/EC, which included a change to Article 5, Paragraph 3. Instead of having an option for users to opt out of cookie storage, the revised Directive requires consent to be obtained for cookie storage. The definition of consent is cross-referenced to the definition in European data protection law, firstly the Data Protection Directive 1995 and subsequently the General Data Protection Regulation (GDPR). As the definition of consent was strengthened in the text of the GDPR, this increased the quality of consent required by those storing and accessing information such as cookies on users devices. In a case decided under the Data Protection Directive however, the Court of Justice of the European Union later confirmed however that the previous law implied the same strong quality of consent as the current instrument. In addition to the requirement of consent which stems from storing or accessing information on a user's terminal device, the information in many cookies will be considered personal data under the GDPR alone, and will require a legal basis to process. This has been the case since the 1995 Data Protection Directive, which used an identical definition of personal data, although the GDPR in interpretative Recital 30 clarifies that cookie identifiers are included. While not all data processing under the GDPR requires consent, the characteristics of behavioural advertising mean that it is difficult or impossible to justify under any other ground. Consent under the combination of the GDPR and e-Privacy Directive has to meet a number of conditions in relation to cookies. It must be freely given and unambiguous: preticked boxes were banned under both the Data Protection Directive 1995 and the GDPR (Recital 32). The GDPR is specific that consent must be as 'easy to withdraw as to give', meaning that a reject-all button must be as easy to access in terms of clicks and visibility as an 'accept all' button. It must be specific and informed, meaning that consent relates to particular purposes for the use of this data, and all organisations seeking to use this consent must be specifically named. The Court of Justice of the European Union has also ruled that consent must be 'efficient and timely', meaning that it must be gained before cookies are laid and data processing begins instead of afterwards. The industry's response has been largely negative. Robert Bond of the law firm Speechly Bircham describes the effects as "far-reaching and incredibly onerous" for "all UK companies". Simon Davis of Privacy International argues that proper enforcement would "destroy the entire industry". However, scholars note that the onerous nature of cookie pop-ups stems from an attempt to continue to operate a business model through convoluted requests that may be incompatible with the GDPR. Academic studies and regulators both describe widespread non-compliance with the law. A study scraping 10,000 UK websites found that only 11.8% of sites adhered to minimal legal requirements, with only 33.4% of websites studied providing a mechanism to reject cookies that was as easy to use as accepting them. A study of 17,000 websites found that 84% of sites breached this criterion, finding additionally that many laid third party cookies with no notice at all. The UK regulator, the Information Commissioner's Office, stated in 2019 that the industry's 'Transparency and Consent Framework' from the advertising technology group the Interactive Advertising Bureau was 'insufficient to ensure transparency and fair processing of the personal data in question and therefore also insufficient to provide for free and informed consent, with attendant implications for PECR [e-Privacy] compliance.' Many companies that sell compliance solutions (Consent Management Platforms) permit them to be configured in manifestly illegal ways, which scholars have noted creates questions around the appropriate allocation of liability. A W3C specification called P3P was proposed for servers to communicate their privacy policy to browsers, allowing automatic, user-configurable handling.
However, few websites implement the specification, and the W3C has discontinued work on the specification. Third-party cookies can be blocked by most browsers to increase privacy and reduce tracking by advertising and tracking companies without negatively affecting the user's web experience on all sites. Some sites operate 'cookie walls', which make access to a site conditional on allowing cookies either technically in a browser, through pressing 'accept', or both. In 2020, the European Data Protection Board, composed of all EU data protection regulators, stated that cookie walls were illegal.In order for consent to be freely given, access to services and functionalities must not be made conditional on the consent of a user to the storing of information, or gaining of access to information already stored, in the terminal equipment of a user (so called cookie walls).Many advertising operators have an opt-out option to behavioural advertising, with a generic cookie in the browser stopping behavioural advertising. However, this is often ineffective against many forms of tracking, such as first-party tracking that is growing in popularity to avoid the impact of browsers blocking third party cookies. Furthermore, if such a setting is more difficult to place than the acceptance of tracking, it remains in breach of the conditions of the e-Privacy Directive.
2. System Architecture & Core Working Principles Most websites use cookies as the only identifiers for user sessions, because other methods of identifying web users have limitations and vulnerabilities. If a website uses cookies as session identifiers, attackers can impersonate users' requests by stealing a full set of victims' cookies. From the web server's point of view, a request from an attacker then has the same authentication as the victim's requests; thus the request is performed on behalf of the victim's session. Listed here are various scenarios of cookie theft and user session hijacking (even without stealing user cookies) that work with websites relying solely on HTTP cookies for user identification.
Traffic on a network can be intercepted and read by computers on the network other than the sender and receiver (particularly over unencrypted open Wi-Fi). This traffic includes cookies sent on ordinary unencrypted HTTP sessions. Where network traffic is not encrypted, attackers can therefore read the communications of other users on the network, including HTTP cookies as well as the entire contents of the conversations, for the purpose of a man-in-the-middle attack. An attacker could use intercepted cookies to impersonate a user and perform a malicious task, such as transferring money out of the victim's bank account. This issue can be resolved by securing the communication between the user's computer and the server by employing Transport Layer Security (HTTPS protocol) to encrypt the connection. A server can specify the Secure flag while setting a cookie, which will cause the browser to send the cookie only over an encrypted channel, such as a TLS connection.
Cookies can also be stolen using a technique called cross-site scripting. This occurs when an attacker takes advantage of a website that allows its users to post unfiltered HTML and JavaScript content. By posting malicious HTML and JavaScript code, the attacker can cause the victim's web browser to send the victim's cookies to a website the attacker controls. As an example, an attacker may post a message on www.example.com with the following link: When another user clicks on this link, the browser executes the piece of code within the onclick attribute, thus replacing the string document.cookie with the list of cookies that are accessible from the current page. As a result, this list of cookies is sent to the attacker.com server. If the attacker's malicious posting is on an HTTPS website https://www.example.com, secure cookies will also be sent to attacker.com in plain text. It is the responsibility of the website developers to filter out such malicious code. Such attacks can be mitigated by using HttpOnly cookies. These cookies will not be accessible by client-side scripting languages like JavaScript, and therefore, the attacker will not be able to gather these cookies.
For example, Bob might be browsing a chat forum where another user, Mallory, has posted a message. Suppose that Mallory has crafted an HTML image element that references an action on Bob's bank's website (rather than an image file), e.g., If Bob's bank keeps his authentication information in a cookie, and if the cookie hasn't expired, then the attempt by Bob's browser to load the image will submit the withdrawal form with his cookie, thus authorizing a transaction without Bob's approval.
Because ETags are cached by the browser, and returned with subsequent requests for the same resource, a tracking server can simply repeat any ETag received from the browser to ensure an assigned ETag persists indefinitely (in a similar way to persistent cookies). Additional caching header fields can also enhance the preservation of ETag data. ETags can be flushed in some browsers by clearing the browser cache.
The browser cache can also be used to store information that can be used to track individual users. This technique takes advantage of the fact that the web browser will use resources stored within the cache instead of downloading them from the website when it determines that the cache already has the most up-to-date version of the resource. For example, a website could serve a JavaScript file with code that sets a unique identifier for the user (for example, var userId = 3243242;). After the user's initial visit, every time the user accesses the page, this file will be loaded from the cache instead of downloaded from the server. Thus, its content will never change.
A browser fingerprint is information collected about a browser's configuration, such as version number, screen resolution, and operating system, for the purpose of identification. Fingerprints can be used to fully or partially identify individual users or devices even when cookies are turned off. Basic web browser configuration information has long been collected by web analytics services in an effort to accurately measure real human web traffic and discount various forms of click fraud. With the assistance of client-side scripting languages, collection of much more esoteric parameters is possible. Assimilation of such information into a single string constitutes a device fingerprint. In 2010, EFF measured at least 18.1 bits of entropy possible from browser fingerprinting. Canvas fingerprinting, a more recent technique, claims to add another 5.7 bits.
Some web browsers support persistence mechanisms which allow the page to store the information locally for later use. The HTML5 standard (which most modern web browsers support to some extent) includes a JavaScript API called Web storage that allows two types of storage: local storage and session storage. Local storage behaves similarly to persistent cookies while session storage behaves similarly to session cookies, except that session storage is tied to an individual tab/window's lifetime (AKA a page session), not to a whole browser session like session cookies. Internet Explorer supports persistent information in the browser's history, in the browser's favorites, in an XML store ("user data"), or directly within a web page saved to disk. Some web browser plugins include persistence mechanisms as well. For example, Adobe Flash has Local shared object and Microsoft Silverlight has Isolated storage.
HTTP Strict Transport Security § Privacy issues Secure cookie – Type of HTTP cookie Session (computer science) – Temporary context for interactive information interchangePages displaying short descriptions of redirect targets RFC 6265, the current official specification for HTTP cookies HTTP cookies, Mozilla Developer Network Using cookies via ECMAScript, Mozilla Developer Network How Internet Cookies Work at HowStuffWorks Cookies at the Electronic Privacy Information Center (EPIC) Mozilla Knowledge-Base: Cookies Cookie Domain, explain in detail how cookie domains are handled in current major browsers Cookie Stealing - Michael Pound Check cookies for compliance with EU cookie directive The General Data Protection Regulation (Regulation (EU) 2016/679), abbreviated GDPR, is a European Union regulation on information privacy in the European Union (EU) and the European Economic Area (EEA). The GDPR is an important component of EU privacy law and human rights law, in particular Article 8(1) of the Charter of Fundamental Rights of the European Union. It also governs the transfer of personal data outside the EU and EEA. The GDPR's goals are to enhance individuals' control and rights over their personal information and to simplify the regulations for international business. It supersedes the Data Protection Directive 95/46/EC and, among other things, simplifies the terminology. The European Parliament and Council of the European Union adopted the GDPR on 14 April 2016, to become effective on 25 May 2018. As an EU regulation (instead of a directive), the GDPR has direct legal effect and does not require transposition into national law.
However, it also provides flexibility for individual member states to modify (derogate from) some of its provisions. As an example of the Brussels effect, the regulation became a model for many other laws around the world, including in Brazil, Japan, Singapore, South Africa, South Korea, Sri Lanka, and Thailand. After leaving the European Union, the United Kingdom enacted its "UK GDPR", identical to the GDPR. The California Consumer Privacy Act (CCPA), adopted on 28 June 2018, has many similarities with the GDPR.
Article 5 sets out six principles relating to the lawfulness of processing personal data. The first of these specifies that data must be processed lawfully, fairly and in a transparent manner. Article 6 develops this principle by specifying that personal data may not be processed unless there is at least one legal basis for doing so. The other principles refer to "purpose limitation", "data minimisation", "accuracy", "storage limitation", and "integrity and confidentiality". Article 6 states that the lawful purposes are: (a) If the data subject has given consent to the processing of his or her personal data; (b) To fulfill contractual obligations with a data subject, or for tasks at the request of a data subject who is in the process of entering into a contract; (c) To comply with a data controller's legal obligations; (d) To protect the vital interests of a data subject or another individual; (e) To perform a task in the public interest or in official authority; (f) For the legitimate interests of a data controller or a third party, unless these interests are overridden by interests of the data subject or her or his rights according to the Charter of Fundamental Rights (especially in the case of children). If informed consent is used as the lawful basis for processing, consent must have been explicit for data collected and each purpose data is used for. Consent must be a specific, freely given, plainly worded, and unambiguous affirmation given by the data subject; an online form which has consent options structured as an opt-out selected by default is a violation of the GDPR, as the consent is not unambiguously affirmed by the user. In addition, multiple types of processing may not be "bundled" together into a single affirmation prompt, as this is not specific to each use of data, and the individual permissions are not freely given. (Recital 32). Data subjects must be allowed to withdraw this consent at any time, and the process of doing so must not be harder than it was to opt in. A data controller may not refuse service to users who decline consent to processing that is not strictly necessary in order to use the service. Consent for children, defined in the regulation as being less than 16 years old (although with the option for member states to individually make it as low as 13 years old), must be given by the child's parent or custodian, and verifiable. If consent to processing was already provided under the Data Protection Directive, a data controller does not have to re-obtain consent if the processing is documented and obtained in compliance with the GDPR's requirements (Recital 171).
Legal or official authority is being carried out "Legitimate interest", where the organisation needs to process data in order to provide the data subject with a service they signed up for A task being carried out for public interest. GDPR is also clear that the data controller must inform individuals of their right to object from the first communication the controller has with them. This should be clear and separate from any other information the controller is providing and give them their options for how best to object to the processing of their data. There are instances the controller can refuse a request, in the circumstances that the objection request is "manifestly unfounded" or "excessive", so each case of objection must be looked at individually.
Other countries such as Canada are also, following the GDPR, considering legislation to regulate automated decision making under privacy laws, even though there are policy questions as to whether this is the best way to regulate AI. Data controllers must clearly disclose any data collection, declare the lawful basis and purpose for data processing, and state how long data is being retained and if it is being shared with any third parties or outside of the EEA. Firms have the obligation to protect data of employees and consumers to the degree where only the necessary data is extracted with minimum interference with data privacy from employees, consumers, or third parties. Firms should have internal controls and regulations for various departments such as audit, internal controls, and operations. Data subjects have the right to request a portable copy of the data collected by a controller in a common format, as well as the right to have their data erased under certain circumstances. Public authorities, and businesses whose core activities consist of regular or systematic processing of personal data, are required to employ a data protection officer (DPO), who is responsible for managing compliance with the GDPR. Data controllers must report data breaches to national supervisory authorities within 72 hours if they have an adverse effect on user privacy. In some cases, violators of the GDPR may be fined up to €20 million or up to 4% of the annual worldwide turnover of the preceding financial year in case of an enterprise, whichever is greater. To be able to demonstrate compliance with the GDPR, the data controller must implement measures that meet the principles of data protection by design and by default. Article 25 requires data protection measures to be designed into the development of business processes for products and services. Such measures include pseudonymising personal data, by the controller, as soon as possible (Recital 78). It is the responsibility and the liability of the data controller to implement effective measures and be able to demonstrate the compliance of processing activities even if the processing is carried out by a data processor on behalf of the controller (Recital 74). When data is collected, data subjects must be clearly informed about the extent of data collection, the legal basis for the processing of personal data, how long data is retained, if data is being transferred to a third-party and/or outside the EU, and any automated decision-making that is made on a solely algorithmic basis. Data subjects must be informed of their privacy rights under the GDPR, including their right to revoke consent to data processing at any time, their right to view their personal data and access an overview of how it is being processed, their right to obtain a portable copy of the stored data, their right to erasure of their data under certain circumstances, their right to contest any automated decision-making that was made on a solely algorithmic basis, and their right to file complaints with a Data Protection Authority. As such, the data subject must also be provided with contact details for the data controller and their designated data protection officer, where applicable.
Data protection impact assessments (Article 35) have to be conducted when specific risks occur to the rights and freedoms of data subjects. Risk assessment and mitigation is required and prior approval of the data protection authorities is required for high risks. Article 25 requires data protection to be designed into the development of business processes for products and services. Privacy settings must therefore be set at a high level by default, and technical and procedural measures shall be taken by the controller to make sure that the processing, throughout the whole processing lifecycle, complies with the regulation. Controllers shall also implement mechanisms to ensure that personal data is not processed unless necessary for each specific purpose. This is known as data minimisation. A report by the European Union Agency for Network and Information Security elaborates on what needs to be done to achieve privacy and data protection by default. It specifies that encryption and decryption operations must be carried out locally, not by remote service, because both keys and data must remain in the power of the data owner if any privacy is to be achieved. The report specifies that outsourced data storage on remote clouds is practical and relatively safe if only the data owner, not the cloud service, holds the decryption keys.
3. Software Implementation, Frameworks & Protocols employing more than 250 people; the processing it carries out is likely to result in a risk to the rights and freedoms of data subjects; the processing is not occasional; processing includes special categories of data as referred to in Article 9(1) or personal data relating to criminal convictions and offences referred to in Article 10. Such requirements may be modified by each EU country. The records shall be in electronic form and the controller or the processor and, where applicable, the controller's or the processor's representative, shall make the record available to the supervisory authority on request. Records of controller shall contain all of the following information: the name and contact details of the controller and, where applicable, the joint controller, the controller's representative and the data protection officer; the purposes of the processing; a description of the categories of data subjects and of the categories of personal data; the categories of recipients to whom the personal data have been or will be disclosed including recipients in third countries or international organisations; where applicable, transfers of personal data to a third country or an international organisation, including the identification of that third country or international organisation and, in the case of transfers referred to in the second subparagraph of Article 49(1), the documentation of suitable safeguards; where possible, the envisaged time limits for erasure of the different categories of data; where possible, a general description of the technical and organisational security measures referred to in Article 32(1). Records of processor shall contain all of the following information: the name and contact details of the processor or processors and of each controller on behalf of which the processor is acting, and, where applicable, of the controller's or the processor's representative, and the data protection officer; the categories of processing carried out on behalf of each controller; where applicable, transfers of personal data to a third country or an international organisation, including the identification of that third country or international organisation and, in the case of transfers referred to in the second subparagraph of Article 49(1), the documentation of suitable safeguards; where possible, a general description of the technical and organisational security measures referred to in Article 32(1).
Article 37 requires appointment of a data protection officer. If processing is carried out by a public authority (except for courts or independent judicial authorities when acting in their judicial capacity), or if processing operations involve regular and systematic monitoring of data subjects on a large scale, or if processing on a large scale of special categories of data and personal data relating to criminal convictions and offences (Articles 9 and Article 10) a data protection officer (DPO)—a person with expert knowledge of data protection law and practices—must be designated to assist the controller or processor in monitoring their internal compliance with the Regulation. A designated DPO can be a current member of staff of a controller or processor, or the role can be outsourced to an external person or agency through a service contract. In any case, the processing body must make sure that there is no conflict of interest in other roles or interests that a DPO may hold. The contact details for the DPO must be published by the processing organisation (for example, in a privacy notice) and registered with the supervisory authority. The DPO is similar to a compliance officer and is also expected to be proficient at managing IT processes, data security (including dealing with cyberattacks) and other critical business continuity issues associated with the holding and processing of personal and sensitive data. The skill set required stretches beyond understanding legal compliance with data protection laws and regulations. The DPO must maintain a living data inventory of all data collected and stored on behalf of the organization. More details on the function and the role of data protection officer were given on 13 December 2016 (revised 5 April 2017) in a guideline document. Organisations based outside the EU must also appoint an EU-based person as a representative and point of contact for their GDPR obligations. This is a distinct role from a DPO, although there is overlap in responsibilities that suggest that this role can also be held by the designated DPO.
Article 42 and 43 of the GDPR set the legal basis for formal GDPR certifications. They set the basis for two categories of certifications: National certification schemes, whose application is limited to a single EU/EEA country; European Data Protection Seals, which are recognized by all EU and EEA jurisdictions. According to Art. 42 GDPR, the purpose of this certification is to demonstrate “compliance with the GDPR of processing operations by controllers and processors”. There are over 70 references to certification in the GDPR, encompassing various obligations such as: Adequacy of the technical and organizational measures; Data sharing with data processors; Data protection by design and by default; International data transfers. The GDPR certification also contributes to reduce the legal and financial risks of applicants, as well as of data controllers using certified data processing services. The adoption of the European Data Protection Seals is under the responsibility of the European Data Protection Board (EDPB) and is recognized across all EU and EEA Member States. In October 2022, the Europrivacy certification criteria were officially recognized by the European Data Protection Board (EDPB) to serve as European Data Protection Seal. Europrivacy was developed by the European research programme and is managed by the European Centre for Certification and Privacy (ECCP) in Luxembourg.
Besides the definitions as a criminal offence according to national law following Article 83 GDPR the following sanctions can be imposed: a warning in writing in cases of first and non-intentional noncompliance regular periodic data protection audits a fine up to €10 million or up to 2% of the annual worldwide turnover of the preceding financial year in case of an enterprise, whichever is greater, if there has been an infringement of the following provisions (Article 83, Paragraph 4): the obligations of the controller and the processor pursuant to Articles 8, 11, 25 to 39, and 42 and 43 the obligations of the certification body pursuant to Articles 42 and 43 the obligations of the monitoring body pursuant to Article 41(4) a fine up to €20 million or up to 4% of the annual worldwide turnover of the preceding financial year in case of an enterprise, whichever is greater, if there has been an infringement of the following provisions (Article 83, Paragraph 5 & 6): the basic principles for processing, including conditions for consent, pursuant to Articles 5, 6, 7, and 9 the data subjects' rights pursuant to Articles 12 to 22 the transfers of personal data to a recipient in a third country or an international organisation pursuant to Articles 44 to 49 any obligations pursuant to member state law adopted under Chapter IX noncompliance with an order or a temporary or definitive limitation on processing or the suspension of data flows by the supervisory authority pursuant to Article 58(2) or failure to provide access in violation of Article 58(1) Personal or household activities Law enforcement National security Conversely, an entity or more precisely an "enterprise" has to be engaged in "economic activity" to be covered by the GDPR. Economic activity is defined broadly under European Union competition law.
All processing of personal data requires consent of the data subject In fact, data can be processed without consent if one of the other five lawful bases for processing applies, and obtaining consent may often be inappropriate. Individuals have an absolute right to have their data deleted (right to be forgotten) Whilst there is an absolute right to opt out of direct marketing, data controllers can continue to process personal data where they have a lawful basis to do so, as long as the data remain necessary for the purpose for which it was originally collected. Removing individuals' names from records takes them out of scope of GDPR "Pseudonymous" data where an individual is identified by a number can still be personal data if the data controller is capable of tying that data back to an individual in another way. GDPR applies to anyone processing personal data of EU citizens anywhere in the world In fact, it applies to non-EU established organizations only where they are processing data of data subjects located in the EU (irrespective of their citizenship) and then only when supplying goods or services to them, or monitoring their behaviour.
Academic experts who participated in the formulation of the GDPR wrote that the law "is the most consequential regulatory development in information policy in a generation. The GDPR brings personal data into a complex and protective regulatory regime." Despite having had at least two years to prepare and do so, many companies and websites changed their privacy policies and features worldwide directly prior to GDPR's implementation, and customarily provided email and other notifications discussing these changes. This was criticised for resulting in a fatiguing number of communications, while experts noted that some reminder emails incorrectly asserted that new consent for data processing had to be obtained for when the GDPR took effect (any previously obtained consent to processing is valid as long as it met the regulation's requirements). Phishing scams also emerged using falsified versions of GDPR-related emails, and it was also argued that some GDPR notice emails may have actually been sent in violation of anti-spam laws. In March 2019, a provider of compliance software found that many websites operated by EU member state governments contained embedded tracking from ad technology providers. The deluge of GDPR-related notices also inspired memes, including those surrounding privacy policy notices being delivered by atypical means (such as a Ouija board or Star Wars opening crawl), suggesting that Santa Claus's "naughty or nice" list was a violation, and a recording of excerpts from the regulation by a former BBC Radio 4 Shipping Forecast announcer. A blog, GDPR Hall of Shame, was also created to showcase unusual delivery of GDPR notices, and attempts at compliance that contained egregious violations of the regulation's requirements. Its author remarked that the regulation "has a lot of nitty gritty, in-the-weeds details, but not a lot of information about how to comply", but also acknowledged that businesses had two years to comply, making some of its responses unjustified. Research indicates that approximately 25% of software vulnerabilities have GDPR implications. Since Article 33 emphasizes breaches, not bugs, security experts advise companies to invest in processes and capabilities to identify vulnerabilities before they can be exploited, including coordinated vulnerability disclosure processes. An investigation of Android apps' privacy policies, data access capabilities, and data access behaviour has shown that numerous apps display a somewhat privacy-friendlier behaviour since the GDPR was implemented, although they still retain most of their data access privileges in their code. An investigation of the Norwegian Consumer Council into the post-GDPR data subject dashboards on social media platforms (such as Google dashboard) has concluded that large social media firms deploy deceptive tactics in order to discourage their customers from sharpening their privacy settings. On the effective date, some websites began to block visitors from EU countries entirely (including Instapaper, Unroll.me, Tubi and Tribune Publishing-owned newspapers, such as the Chicago Tribune and the Los Angeles Times) or redirect them to stripped-down versions of their services (in the case of NPR and USA Today) with limited functionality and/or no advertising so that they will not be liable. Some companies, such as Klout, and several online video games, ceased operations entirely to coincide with its implementation, citing the GDPR as a burden on their continued operations, especially due to the business model of the former. The volume of online behavioural advertising placements in Europe fell 25–40% on 25 May 2018. In 2020, two years after the GDPR began its implementation, the European Commission assessed that users across the EU had increased their knowledge about their rights, stating that "69% of the population above the age of 16 in the EU have heard about the GDPR and 71% of people heard about their national data protection authority." The commission also found that privacy has become a competitive quality for companies which consumers are taking into account in their decisionmaking processes.
Facebook and subsidiaries WhatsApp and Instagram, as well as Google LLC (targeting Android), were immediately sued by Max Schrems's non-profit NOYB just hours after midnight on 25 May 2018, for their use of "forced consent". Schrems asserts that both companies violated Article 7(4) by not presenting opt-ins for data processing consent on an individualized basis, and requiring users to consent to all data processing activities (including those not strictly necessary) or would be forbidden from using the services. On 21 January 2019, Google was fined €50 million by the French DPA for showing insufficient control, consent, and transparency over use of personal data for behavioural advertising. In November 2018, following a journalistic investigation into Liviu Dragnea, the Romanian DPA (ANSPDCP) used a GDPR request to demand information on the RISE Project's sources. In July 2019, the British Information Commissioner's Office issued an intention to fine British Airways a record £183 million (1.5% of turnover) for poor security arrangements that enabled a 2018 web skimming attack affecting around 380,000 transactions. British Airways was ultimately fined a reduced amount of £20m, with the ICO noting that they had "considered both representations from BA and the economic impact of COVID-19 on their business before setting a final penalty". In December 2019, Politico reported that Ireland and Luxembourg – two smaller EU countries that have had a reputation as a tax havens and (especially in the case of Ireland) as a base for European subsidiaries of U.S. big tech companies – were facing significant backlogs in their investigations of major foreign companies under GDPR, with Ireland citing the complexity of the regulation as a factor. Critics interviewed by Politico also argued that enforcement was also being hampered by varying interpretations between member states, the prioritisation of guidance over enforcement by some authorities, and a lack of cooperation between member states. In November 2021, Irish Council for Civil Liberties lodged a formal complaint of the Commission that it is in breach of its obligation under EU Law to carefully monitor how Ireland applies the GDPR. Until January 2023, the Commission published a new commitment based on the complaint of ICCL. While companies are now subject to legal obligations, there are still various inconsistencies in the practical and technical implementation of GDPR. As an example, according to the GDPR's right to access, the companies are obliged to provide data subjects with the data they gather about them. However, in a study on loyalty cards in Germany, companies did not provide the data subjects with the exact information of the purchased articles. One might argue that such companies do not collect the information of the purchased articles, which does not conform with their business models. Therefore, data subjects tend to see that as a GDPR violation. As a result, studies have suggested for a better control through authorities. According to the GDPR, end-users' consent should be valid, freely given, specific, informed and active. However, the lack of enforceability regarding obtaining lawful consents has been a challenge. As an example, a 2020 study, showed that the Big Tech, i.e. Google, Amazon, Facebook, Apple, and Microsoft (GAFAM), use dark patterns in their consent obtaining mechanisms, which raises doubts regarding the lawfulness of the acquired consent. In March 2021, EU member states led by France were reported to be attempting to modify the impact of the privacy regulation in Europe by exempting national security agencies. After around 160 million Euros in GDPR fines were imposed in 2020, the figure was already over one billion Euros in 2021. In 2024 and early 2025, GDPR enforcement actions intensified. The Irish Data Protection Commission (DPC) imposed a €345 million fine on TikTok for violations related to children's data privacy and insufficient safeguards for young users. In January 2025, Meta was fined €1.2 billion for unlawful data transfers between the EU and the US, marking one of the largest GDPR fines to date.
On 12 February 2025, the European Commission abandoned proposed regulations on technology patents, AI liability, and privacy for messaging apps due to strong lobbying and a lack of consensus among EU lawmakers, with major tech firms opposing the changes. Chat Control Cyber Security and Resilience Bill – UK proposed legislation 2024. Data Act, proposed EU law from 2022 Data Governance Act, proposed EU law from 2020 Digital Markets Act Digital Services Act EU–US Privacy Shield European Data Protection Board (EDPB) European Health Data Space Privacy and Electronic Communications Directive 2002 (ePrivacy Directive, ePD) Right to be forgotten law Transparency and targeting of political advertising Related concepts: Budapest Convention on Cybercrime Data portability Do Not Track legislation ePrivacy Regulation Privacy Impact Assessment Compliance tactics by certain companies: General Data Protection Regulation consolidated text General Data Protection Regulation initial legal act Data protection, European Commission Procedure 2012/0011/COD Procedure for the proposed revised legal framework (General Data Protection Regulation) Handbook on European data protection law, European Union Agency for Fundamental Rights Europrivacy Official Website ECCP – European Centre for Certification and Privacy GDPR Certification Consent or pay, also called pay-or-okay, is a compliance tactic used by certain companies, most notably Meta, to drive up the rates at which users consent to data processing under the European Union's General Data Protection Regulation (GDPR). It consists of presenting the user with a tracking consent notice, but only allowing a binary choice: either the user consents to the data processing, or they are required to pay to use the service, which is otherwise free to use if data processing is consented to. The tactic has been criticised by privacy advocates and non-governmental organisations such as NOYB and Wikimedia Europe, which claim that it is illegal under the GDPR. On 17 April 2024, the European Data Protection Board released a non-binding opinion stating that in most cases, consent-or-pay models do not constitute valid consent within the meaning of the GDPR.
4. Practical Deployment, Analysis & Case Studies GDPR requires a lawful basis for all personal data processing. The six available bases are: Privacy by Design requires embedding data protection into your software’s core architecture rather than bolting it on afterward. This means: GDPR requires breach notification to supervisory authorities within 72 hours and affected individuals “without undue delay” when high risk exists.
The General Data Protection Regulation (GDPR) fundamentally changed how enterprises handle personal data. For software companies processing EU residents’ information, compliance isn’t optional—it’s a legal requirement that can impact your bottom line with fines up to €20 million or 4% of global annual revenue. This comprehensive guide walks you through implementing GDPR compliance in your enterprise software, from initial assessment to ongoing monitoring.
GDPR applies to any organization processing personal data of EU residents, regardless of where your company is located. If your enterprise software collects, stores, or processes data like names, email addresses, IP addresses, or behavioral analytics from EU users, you’re subject to GDPR. The regulation covers both data controllers (who determine processing purposes) and data processors (who process data on behalf of controllers). Most enterprise software companies act as both, depending on the specific use case.
Visualize how personal data moves through your enterprise software ecosystem. Document every touchpoint from collection to deletion, including integrations with third-party services, backup systems, and analytics platforms. This mapping exercise often reveals forgotten data repositories and unexpected data transfers that require immediate attention.
GDPR requires a lawful basis for all personal data processing. The six available bases are: Most enterprise software relies on contract, legal obligation, or legitimate interests rather than consent, which must be freely withdrawable. Privacy by Design requires embedding data protection into your software’s core architecture rather than bolting it on afterward. This means: Data minimization : Collect only necessary personal data for specified purposes. Configure your systems to automatically limit data collection and processing scope.
Purpose limitation : Use personal data only for declared purposes. Implement access controls preventing unauthorized data use across different business functions. Storage limitation : Delete personal data when no longer needed. Build automated retention and deletion workflows into your enterprise software.
GDPR grants individuals eight rights regarding their personal data. Your enterprise software must facilitate these rights within strict timeframes: Right of access : Provide individuals with copies of their personal data and processing information within one month. Right to data portability : Provide personal data in structured, machine-readable formats.
Automate as many rights requests as possible while maintaining human oversight for complex cases. 5. Performance Evaluation & Extended Technical Observations Enterprise software typically integrates with numerous third-party services. Each integration creates potential GDPR compliance risks that require careful management.
Execute Data Processing Agreements (DPAs) with all vendors acting as data processors. These contracts must specify: GDPR requires breach notification to supervisory authorities within 72 hours and affected individuals “without undue delay” when high risk exists. GDPR compliance isn’t a one-time project—it requires ongoing attention. Schedule regular assessments to: Ensure all employees understand their GDPR obligations through regular training covering: A Data Controller determines the purposes and means of personal data processing, while a Data Processor processes personal data on behalf of the Controller. Enterprise software companies often act as both—as Controllers for their own customer data and as Processors when providing services to other organizations.
You must respond to most individual rights requests within one month, though this can be extended to three months for complex requests. The clock starts ticking when you receive a valid request, so implement efficient request handling procedures. No, consent is just one of six lawful bases for processing personal data. Many enterprise software use cases rely on contract performance, legal obligations, or legitimate interests instead of consent. Choose the most appropriate legal basis for each processing purpose.
You must notify the relevant supervisory authority within 72 hours if the breach is likely to result in risk to individuals’ rights and freedoms. High-risk breaches also require notification to affected individuals without undue delay. Document all breaches regardless of notification requirements. International transfers require appropriate safeguards such as adequacy decisions, Standard Contractual Clauses (SCCs), or certification schemes. The UK now has its own adequacy decision from the EU, but transfers to other countries require careful legal analysis and appropriate transfer mechanisms.
Implementing GDPR compliance for enterprise software requires extensive documentation, policies, and procedures. Rather than starting from scratch, leverage our comprehensive library of ready-to-use compliance templates designed specifically for software companies. Our template collection includes privacy notices, consent forms, Data Processing Agreements, breach response procedures, and staff training materials—all crafted by compliance experts and regularly updated for regulatory changes.
Get immediate access to professional compliance templates and accelerate your GDPR implementation timeline. Visit our template library today and transform your compliance program from overwhelming obligation to competitive advantage. Blog Iompliance Continuous GDPR Software Compliance Monitoring: A Step-by-Step Implementation Guide Striking off the last row of your compliance to-do list isn’t the end of the road. The real work begins in maintaining this complex system and quickly implementing the regulatory changes required to stay compliant.
And this is where most companies hit a wall because compliance requires continuous strategic planning, budgeting, and attention to resources. You can avoid most of the issues by treating GDPR compliant software management as an ongoing process, embedding accountability into daily operations, and replacing static documentation with dynamic visibility.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/HTTP%20cookie • https://en.wikipedia.org/wiki/General%20Data%20Protection%20Regulation • https://en.wikipedia.org/wiki/Consent%20or%20pay • https://www.complianceautomator.com/compliance/gdpr-implementation-guide-for-enterprise-software • https://corpsoft.io/2026/02/27/continuous-gdpr-software-compliance-monitoring/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Gdpr Compliance Tracking System.
[*] Metasploit Scan Running on Target Subnet for Gdpr Compliance Tracking System... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |