Complete Technical Paper Content — Git Leaks Scanner And Sensitive Credential Detector
Overview & System Context
Git Leaks Scanner And Sensitive Credential Detector: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9557 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Heartbleed is a security bug in some outdated versions of the OpenSSL cryptography library, which is a widely used implementation of the Transport Layer Security (TLS) protocol. It was introduced into the software in 2012 and publicly disclosed in April 2014. Heartbleed could be exploited regardless of whether the vulnerable OpenSSL instance is running as a TLS server or client. It resulted from improper input validation (due to a missing bounds check) in the implementation of the TLS heartbeat extension. Thus, the bug's name derived from heartbeat. The vulnerability was classified as a buffer over-read, a situation where more data can be read than should be allowed. Heartbleed was registered in the Common Vulnerabilities and Exposures database as CVE-2014-0160. A fixed version of OpenSSL was released on 7 April 2014, on the same day Heartbleed was publicly disclosed. TLS implementations other than OpenSSL, such as GnuTLS, Mozilla's Network Security Services, and the Windows platform implementation of TLS, were not affected because the defect existed in the OpenSSL's implementation of TLS rather than in the protocol itself. System administrators were frequently slow to patch their systems. As of 20 May 2014, 1.5% of the 800,000 most popular TLS-enabled websites were still vulnerable to the bug, and by 21 June 2014, 309,197 public web servers remained vulnerable. According to a 23 January 2017 report from Shodan, nearly 180,000 internet-connected devices were still vulnerable to the bug, but by 6 July 2017, the number had dropped to 144,000 according to a search performed on shodan.io for the vulnerability. Around two years later, 11 July 2019, Shodan reported that 91,063 devices were vulnerable. The U.S. had the most vulnerable devices, with 21,258 (23%), and the 10 countries with the most vulnerable devices had a total of 56,537 vulnerable devices (62%). The remaining countries totaled 34,526 devices (38%).
The report also broke the devices down by 10 other categories such as organization (the top 3 were wireless companies), product (Apache httpd, Nginx), and service (HTTPS, 81%). At the time of disclosure, some 17% (around half a million) of the Internet's secure web servers certified by trusted authorities were believed to be vulnerable to the attack, allowing theft of the servers' private keys and users' session cookies and passwords. The Electronic Frontier Foundation, Ars Technica, and Bruce Schneier all deemed the Heartbleed bug "catastrophic". Forbes cybersecurity columnist Joseph Steinberg wrote:Some might argue that Heartbleed is the worst vulnerability found (at least in terms of its potential impact) since commercial traffic began to flow on the Internet. An unidentified UK Cabinet Office spokesman recommended that: People should take advice on changing passwords from the websites they use. Most websites have corrected the bug and are best placed to advise what action, if any, people need to take. On the day of disclosure, The Tor Project advised: If you need strong anonymity or privacy on the Internet, you might want to stay away from the Internet entirely for the next few days while things settle. The Sydney Morning Herald published a timeline of the discovery on 15 April 2014, showing that some organizations had been able to patch the bug before its public disclosure. In some cases, it is not clear how they found out.
By reusing the same private key, a site that was affected by the Heartbleed bug still faces exactly the same risks as those that have not yet replaced their SSL certificates. eWeek said, "[Heartbleed is] likely to remain a risk for months, if not years, to come." Cloudflare revoked all TLS certificates and estimated that publishing its certificate revocation list would cost the issuer, GlobalSign, $400,000 per month that year.
The RFC 6520 Heartbeat Extension tests TLS/DTLS secure communication links by allowing a computer at one end of a connection to send a Heartbeat Request message, consisting of a payload, typically a text string, along with the payload's length as a 16-bit integer. The receiving computer then must send exactly the same payload back to the sender. The affected versions of OpenSSL allocate a memory buffer for the message to be returned based on the length field in the requesting message, without regard to the actual size of that message's payload. Because of this failure to do proper bounds checking, the message returned consists of the payload, possibly followed by whatever else happened to be in the allocated memory buffer. Heartbleed is therefore exploited by sending a malformed heartbeat request with a small payload and large length field to the vulnerable party (usually a server) in order to elicit the victim's response, permitting attackers to read up to 64 kibibytes of the victim's memory that was likely to have been used previously by OpenSSL. Where a Heartbeat Request might ask a party to "send back the four-letter word 'bird'", resulting in a response of "bird", a malicious "Heartbleed request" of "send back the 500-letter word 'bird'" would cause the victim to return "bird" followed by whatever 496 subsequent characters the victim happened to have in active memory. Attackers in this way could receive sensitive data, compromising the confidentiality of the victim's communications. Although an attacker has some control over the disclosed memory block's size, it has no control over its location, and therefore cannot choose what content is revealed.
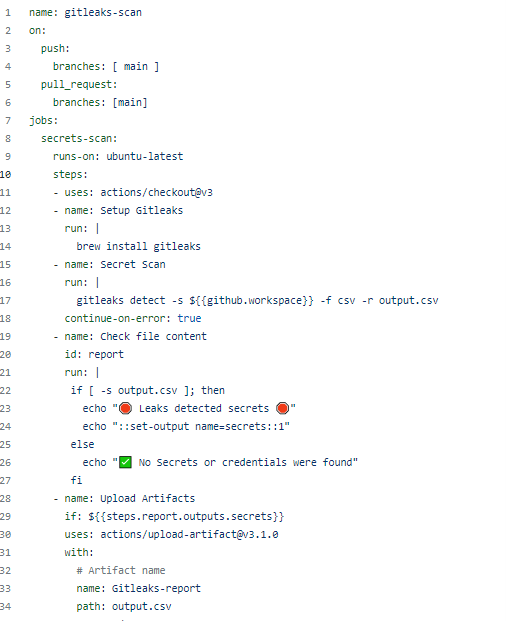
Figure 1: Protect and discover secrets using Git-leaks - Canarys The Canadian federal government temporarily shut online services of the Canada Revenue Agency (CRA) and several government departments over Heartbleed bug security concerns. Before the CRA online services were shut down, a hacker obtained approximately 900 social insurance numbers. Another Canadian Government agency, Statistics Canada, had its servers compromised due to the bug and also temporarily took its services offline. Platform maintainers like the Wikimedia Foundation advised their users to change passwords. The servers of LastPass were vulnerable, but due to additional encryption and forward secrecy, potential attacks were not able to exploit this bug. However, LastPass recommended that its users change passwords for vulnerable websites. The Tor Project recommended that Tor relay operators and hidden service operators revoke and generate fresh keys after patching OpenSSL, but noted that Tor relays use two sets of keys and that Tor's multi-hop design minimizes the impact of exploiting a single relay. 586 relays later found to be susceptible to the Heartbleed bug were taken off-line as a precautionary measure. Game-related services including Steam, Minecraft, Wargaming, League of Legends, GOG.com, Origin, Sony Online Entertainment, Humble Bundle, and Path of Exile were affected and subsequently fixed.
Several Hewlett-Packard server applications, such as HP System Management Homepage (SMH) for Linux and Windows. Some versions of FileMaker 13 LibreOffice 4.2.0 to 4.2.2 (fixed in 4.2.3) LogMeIn claimed to have "updated many products and parts of our services that rely on OpenSSL". Multiple McAfee products, in particular some versions of software providing anti-viral coverage for Microsoft Exchange, software firewalls, and McAfee Email and Web Gateways Oracle MySQL Connector/C 6.1.0-6.1.3 and Connector/ODBC 5.1.13, 5.2.5-5.2.6, 5.3.2 Oracle Big Data Appliance (includes Oracle Linux 6) Primavera P6 Professional Project Management (includes Primavera P6 Enterprise Project Portfolio Management) WinSCP (FTP client for Windows) 5.5.2 and some earlier versions (only vulnerable with FTP over TLS/SSL, fixed in 5.5.3) Multiple VMware products, including VMware ESXi 5.5, VMware Player 6.0, VMware Workstation 10 and the series of Horizon products, emulators and cloud computing suites Several other Oracle Corporation applications were affected.
Android 4.1.1, used in various portable devices. Chris Smith writes in Boy Genius Report that just this one version of Android is affected but that it is a popular version of Android (Chitika claim 4.1.1 is on 50 million devices; Google describe it as less than 10% of activated Android devices). Other Android versions are not vulnerable as they either have heartbeats disabled or use an unaffected version of OpenSSL. Firmware for some AirPort base stations Firmware for some Cisco Systems routers Firmware for some Juniper Networks routers pfSense 2.1.0 and 2.1.1 (fixed in 2.1.2) DD-WRT versions between and including 19163 and 23881 (fixed in 23882) Western Digital My Cloud product family firmware Tripwire SecureScan AppCheck – static binary scan and fuzzing, from Synopsys Software Integrity Group (formerly Codenomicon) Arbor Network's Pravail Security Analytics Norton Safeweb Heartbleed Check Tool Heartbleed testing tool by a European IT security company Heartbleed test by Italian cryptographer Filippo Valsorda Heartbleed Vulnerability Test by Cyberoam Critical Watch Free Online Heartbleed Tester Metasploit Heartbleed scanner module Heartbleed Server Scanner by Rehmann Lookout Mobile Security Heartbleed Detector, an app for Android devices that determines the OpenSSL version of the device and indicates whether the vulnerable heartbeat is enabled Heartbleed checker hosted by LastPass Online network range scanner for Heartbleed vulnerability by Pentest-Tools.com Official Red Hat offline scanner written in the Python language Qualys SSL Labs' SSL Server Test which not only looks for the Heartbleed bug, but can also find other SSL/TLS implementation errors. Browser extensions, such as Chromebleed and FoxBleed SSL Diagnos CrowdStrike Heartbleed Scanner – Scans routers, printers and other devices connected inside a network including intranet web sites. Netcraft Site Report – indicates whether a website's confidentiality could be jeopardized due to a past exploitation of Heartbleed by checking data from Netcraft's SSL Survey to determine whether a site offered the heartbeat TLS Extension prior to the Heartbleed disclosure. The Netcraft Extensions for Chrome, Firefox and Opera also perform this check, whilst looking for potentially compromised certificates. Other security tools have added support for finding this bug. For example, Tenable Network Security wrote a plugin for its Nessus vulnerability scanner that can scan for this fault. The Nmap security scanner includes a Heartbleed detection script from version 6.45. Sourcefire has released Snort rules to detect Heartbleed attack traffic and possible Heartbleed response traffic. Open source packet analysis software such as Wireshark and tcpdump can identify Heartbleed packets using specific BPF packet filters that can be used on stored packet captures or live traffic.
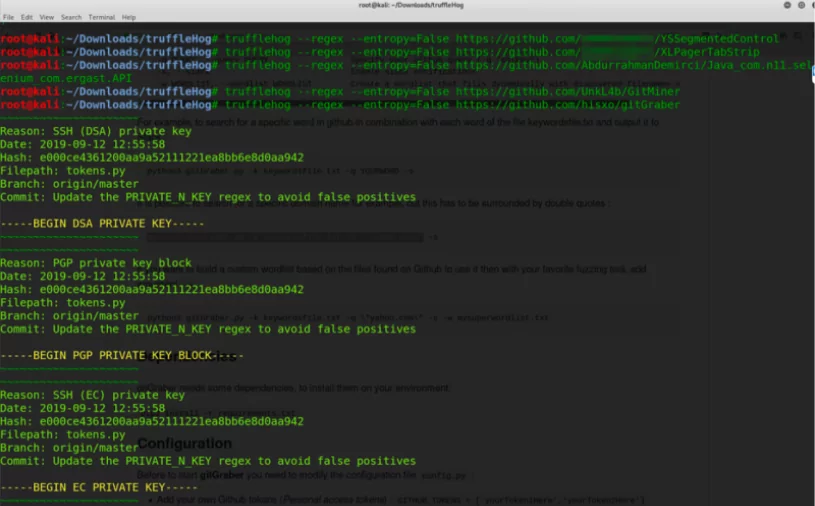
Figure 2: Tools and Features That Can Be Used To Detect Sensitive Data OpenSSL core developer Ben Laurie claimed that a security audit of OpenSSL would have caught Heartbleed. Software engineer John Walsh commented: Think about it, OpenSSL only has two [fulltime] people to write, maintain, test, and review 500,000 lines of business critical code. The OpenSSL foundation's president, Steve Marquess, said "The mystery is not that a few overworked volunteers missed this bug; the mystery is why it hasn't happened more often." David A. Wheeler described audits as an excellent way to find vulnerabilities in typical cases, but noted that "OpenSSL uses unnecessarily complex structures, which makes it harder to both humans and machines to review." He wrote: There should be a continuous effort to simplify the code, because otherwise just adding capabilities will slowly increase the software complexity. The code should be refactored over time to make it simple and clear, not just constantly add new features. The goal should be code that is "obviously right", as opposed to code that is so complicated that "I can't see any problems". According to security researcher Dan Kaminsky, Heartbleed is sign of an economic problem which needs to be fixed. Seeing the time taken to catch this simple error in a simple feature from a "critical" dependency, Kaminsky fears numerous future vulnerabilities if nothing is done. When Heartbleed was discovered, OpenSSL was maintained by a handful of volunteers, only one of whom worked full time. Yearly donations to the OpenSSL project were about US$2,000. The Heartbleed website from Codenomicon advised money donations to the OpenSSL project. After learning about donations for the 2 or 3 days following Heartbleed's disclosure totaling US$841, Kaminsky commented "We are building the most important technologies for the global economy on shockingly underfunded infrastructure." Core developer Ben Laurie has qualified the project as "completely unfunded". Although the OpenSSL Software Foundation has no bug bounty program, the Internet Bug Bounty initiative awarded US$15,000 to Google's Neel Mehta, who discovered Heartbleed, for his responsible disclosure. Mehta later donated his reward to a Freedom of the Press Foundation fundraiser. Paul Chiusano suggested Heartbleed may have resulted from failed software economics. The industry's collective response to the crisis was the Core Infrastructure Initiative, a multimillion-dollar project announced by the Linux Foundation on 24 April 2014 to provide funds to critical elements of the global information infrastructure. The initiative intends to allow lead developers to work full time on their projects and to pay for security audits, hardware and software infrastructure, travel, and other expenses. OpenSSL is a candidate to become the first recipient of the initiative's funding. After the discovery Google established Project Zero which is tasked with finding zero-day vulnerabilities to help secure the Web and society.
Summary and Q&A about the bug by Codenomicon Ltd Information for Canadian organizations and individuals List of all security notices Archived 19 July 2018 at the Wayback Machine Gitleaks is a command-line secret scanner for Git history, directories/files, and stdin. The principal workflow selects an input mode, turns input into fragments, applies configured detection rules (including decoding), filters findings, and emits a report.
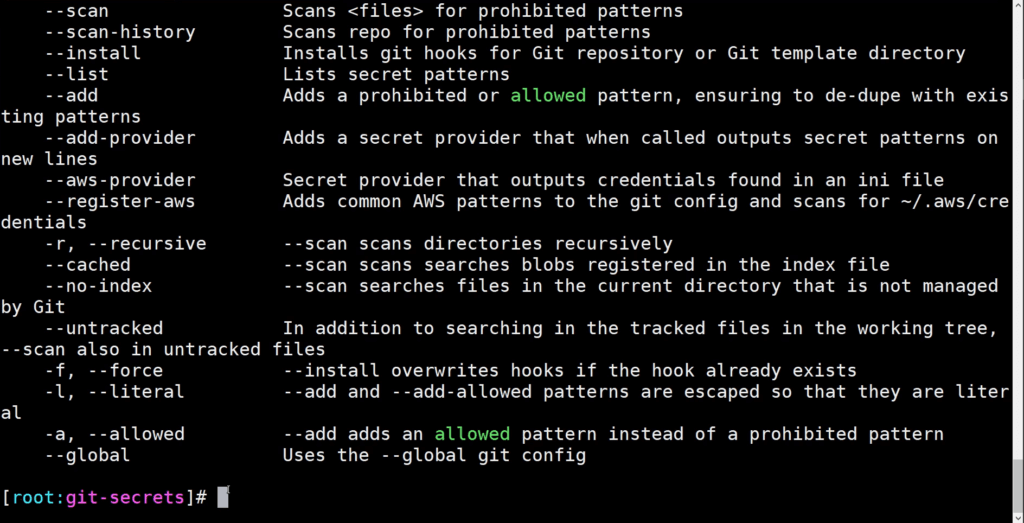
The README documents the scanning modes and report formats; sampled sources establish the detector, source adapters, rule configuration, and SARIF reporting. Some command wiring and unsampled directory/stdin handlers are not shown, so uncertain runtime links are omitted or marked unverified. Drawn by GitDiagram on October 5, 2026 from the repository's file tree, README and source files. Read as Markdown Figure 3: Top 9 Git Secret Scanning Tools for DevSecOps - Check Point Blog Gitleaks is feature complete. I'm not merging new features into Gitleaks. Future releases will be security patches only. I'm shifting my focus to Betterleaks Gitleaks is a tool for detecting secrets like passwords, API keys, and tokens in git repos, files, and whatever else you wanna throw at it via stdin . If you wanna learn more about how the detection engine works check out this blog: Regex is (almost) all you need .
Gitleaks can be installed using Homebrew, Docker, or Go. Gitleaks is also available in binary form for many popular platforms and OS types on the releases page . In addition, Gitleaks can be implemented as a pre-commit hook directly in your repo or as a GitHub action using Gitleaks-Action . Create a .pre-commit-config.yaml file at the root of your repository with the following content: for a native execution of gitleaks or use the gitleaks-docker pre-commit ID for executing gitleaks using the official Docker images Auto-update the config to the latest repos' versions by executing pre-commit autoupdate Note: to disable the gitleaks pre-commit hook you can prepend SKIP=gitleaks to the commit command and it will skip running gitleaks II v8.19.0 introduced a change that deprecated detect and protect . Those commands are still available but are hidden in the --help menu. Take a look at this gist for easy command translations. If you find v8.19.0 broke an existing command ( detect / protect ), please open an issue.
The git command lets you scan local git repos. Under the hood, gitleaks uses the git log -p command to scan patches. You can configure the behavior of git log -p with the log-opts option. For example, if you wanted to run gitleaks on a range of commits you could use the following command: gitleaks git -v --log-opts="--all commitA..commitB" path_to_repo . See the git log documentation for more information. If there is no target specified as a positional argument, then gitleaks will attempt to scan the current working directory as a git repo.
The dir (aliases include files , directory ) command lets you scan directories and files. Example: gitleaks dir -v path_to_directory_or_file . If there is no target specified as a positional argument, then gitleaks will scan the current working directory. You can also stream data to gitleaks with the stdin command. Example: cat some_file | gitleaks -v stdin When scanning large repositories or repositories with a long history, it can be convenient to use a baseline. When using a baseline, gitleaks will ignore any old findings that are present in the baseline. A baseline can be any gitleaks report. To create a gitleaks report, run gitleaks with the --report-path parameter.
After running the detect command with the --baseline-path parameter, report output (findings.json) will only contain new issues. You can run Gitleaks as a pre-commit hook by copying the example pre-commit.py script into your .git/hooks/ directory. Gitleaks offers a configuration format you can follow to write your own secret detection rules: Refer to the default gitleaks config for examples or follow the contributing guidelines if you would like to contribute to the default configuration. Additionally, you can check out this gitleaks blog post which covers advanced configuration setups.
In v8.28.0 Gitleaks introduced composite rules, which are made up of a single "primary" rule and one or more auxiliary or required rules. To create a composite rule, add a [[rules.required]] table to the primary rule specifying an id and optionally withinLines and/or withinColumns proximity constraints. A fragment is a chunk of content that Gitleaks processes at once (typically a file, part of a file, or git diff), and proximity matching instructs the primary rule to only report a finding if the auxiliary required rules also find matches within the specified area of the fragment.
Proximity matching: Using the withinLines and withinColumns fields instructs the primary rule to only report a finding if the auxiliary required rules also find matches within the specified proximity. You can set: If you are knowingly committing a test secret that gitleaks will catch you can add a gitleaks:allow comment to that line which will instruct gitleaks to ignore that secret. Ex: You can ignore specific findings by creating a .gitleaksignore file at the root of your repo. In release v8.10.0 Gitleaks added a Fingerprint value to the Gitleaks report. Each leak, or finding, has a Fingerprint that uniquely identifies a secret. Add this fingerprint to the .gitleaksignore file to ignore that specific secret. See Gitleaks' .gitleaksignore for an example. Note: this feature is experimental and is subject to change in the future.
Sometimes secrets are encoded in a way that can make them difficult to find with just regex. Now you can tell gitleaks to automatically find and decode encoded text. The flag --max-decode-depth enables this feature (the default value "0" means the feature is disabled by default). Recursive decoding is supported since decoded text can also contain encoded text. The flag --max-decode-depth sets the recursion limit. Recursion stops when there are no new segments of encoded text to decode, so setting a really high max depth doesn't mean it will make that many passes. It will only make as many as it needs to decode the text. Overall, decoding only minimally increases scan times.
Sometimes secrets are packaged within archive files like zip files or tarballs, making them difficult to discover. Now you can tell gitleaks to automatically extract and scan the contents of archives. The flag --max-archive-depth enables this feature for both dir and git scan types. The default value of "0" means this feature is disabled by default. Recursive scanning is supported since archives can also contain other archives. The --max-archive-depth flag sets the recursion limit. Recursion stops when there are no new archives to extract, so setting a very high max depth just sets the potential to go that deep. It will only go as deep as it needs to.
The findings for secrets located within an archive will include the path to the file inside the archive. Inner paths are separated with ! . This means a secret was detected on line 4 of files/.env.prod. which is in archives/files.tar which is in testdata/archives/nested.tar.gz .
The compression and archive formats supported by mholt's archives package are supported. Gitleaks has built-in support for several report formats: json , csv , junit , and sarif . If none of these formats fit your need, you can create your own report format with a Go text/template .tmpl file and the --report-template flag. The template can use extended functionality from the Masterminds/sprig template library .
You can always set the exit code when leaks are encountered with the --exit-code flag. Default exit codes below: > your AI agent picks dependencies from memory; give it dated facts — try starlog.dev I vet your agent's deps I vibe-coding is fine. vibe-importing isnâIIt. — try starlog.dev I vibe-importing isnâIIt fine I your agent has never seen your private packages — try starlog.dev I facts for private packages I a linter for the dependencies your AI agent picks — try starlog.dev I a linter for agent deps I whois is redacted, cdns mask the rest âII get the real operator — try whoisgeni.us I who really runs that domain I domain attribution that shows its work âII full evidence chain — try whoisgeni.us I domain intel w/ evidence I 2. System Architecture & Core Working Principles Metrics below are heuristic approximations computed from repository structure, not authoritative measurements.
Every minute, developers accidentally push AWS keys, API tokens, and database credentials to GitHubâIIand it takes an average of just 4 seconds for automated bots to find and exploit them. The traditional approach to preventing credential leaks was code review and developer vigilance, both of which fail at scale. A single distracted engineer can expose production secrets in a late-night commit, and by the time the mistake is discovered during code review, the damage is doneâIIcredentials must be rotated, incident reports filed, and security teams scrambled.
Pre-commit hooks and CI/CD scanners emerged as the solution, but early tools relied on simple pattern matching that either missed novel secret formats or flooded teams with false positives. Gitleaks entered this landscape as a Go-based CLI tool designed to be fast enough for pre-commit hooks yet comprehensive enough for deep repository audits. Unlike its predecessors, it combines regex-based rules with entropy analysisâIIa statistical technique that identifies high-randomness strings characteristic of cryptographic material. This dual approach means Gitleaks can catch both known secret formats (like AWS access keys with their distinctive AKIA prefix) and unknown formats that exhibit the mathematical properties of secure tokens. With over 26,000 GitHub stars and adoption across enterprises and open-source projects, it's become the de facto standard for Git-based secret scanning.
Gitleaks' architecture centers on a detection engine that processes Git objects (commits, diffs, file contents) through a configurable rule set. Each rule is defined in TOML configuration files and specifies regex patterns, entropy thresholds, file path filters, and allowlists. When you run Gitleaks against a repository, it walks the commit history, extracts text content, and applies every active rule to every line.
The entropy-based detection is where Gitleaks differentiates itself from simpler pattern-matching tools. Entropy measures the randomness of a stringâIIa high-entropy string like xAmzAws3K3yH4sH1ghR4nd0mn3ss has approximately 4.7 bits of entropy per character, while a low-entropy string like password123 hovers around 3.2 bits. Gitleaks calculates Shannon entropy for each token and flags those exceeding a configurable threshold (typically 3.5-4.0 bits per character for base64-encoded secrets).
This rule targets API keys with a specific prefix ( myapp_api_key ), requires the captured group (secretGroup = 1) to have at least 3.7 bits of entropy per character, and explicitly ignores test files and example credentials. The allowlist mechanism is critical for production useâIIwithout it, documentation examples, test fixtures, and intentionally fake credentials generate noise that trains developers to ignore scanner output.
Gitleaks operates in several modes, each optimized for different security gates. In detect mode, it scans the current state of files without considering Git historyâIIideal for pre-commit hooks where speed matters more than comprehensiveness. In protect mode, it analyzes staged changes (the Git index) to prevent secrets from ever entering the repository. In default mode, it traverses the entire Git history, which is expensive but necessary for initial repository audits or compliance requirements.
The scanning logic uses goroutines to parallelize rule evaluation across files and commits. For a repository with thousands of commits, Gitleaks spawns worker pools that process commits concurrently while maintaining bounded memory usageâIIit doesn't load the entire repository into RAM but streams commit objects from Git's object database. This is why Gitleaks can scan multi-gigabyte repositories in minutes on modest hardware.
Findings are enriched with contextual metadata that makes remediation practical. Each secret detection includes the commit hash, file path, line number, matched rule ID, and a "fingerprint"âIIa hash of the secret value and location that enables tracking whether a specific secret has been fixed across multiple scans. This fingerprinting system is essential for baseline management: you can run an initial scan, acknowledge certain findings as false positives or accepted risks, and then focus subsequent scans on net-new secrets.
Integration with CI/CD pipelines leverages Gitleaks' exit codes: it returns 0 if no secrets are found, 1 if secrets are detected. This makes pipeline integration trivial: The SARIF output format deserves special mentionâIIit's a standardized JSON schema for static analysis results that integrates natively with GitHub's security tab, Azure DevOps, and other platforms. When Gitleaks outputs SARIF, findings appear as code scanning alerts with inline annotations on pull requests, complete with severity levels and remediation guidance.
The regex-plus-entropy approach sounds bulletproof in theory but hits walls with real-world code patterns. Base64-encoded JSON configuration blocks, cryptographic hashes in documentation, and machine-generated IDs all exhibit high entropy and trigger false positives. A particularly frustrating case is encoded test fixturesâIIyour test suite might include base64-encoded sample data that Gitleaks flags as potential secrets. You'll spend significant time building allowlists that capture these patterns without creating blind spots for actual credential leaks.
Multi-line secrets are Gitleaks' Achilles heel. If a developer splits an API key across multiple string concatenations or embeds it in a multi-line YAML block with specific indentation, the regex engine won't match because it processes line-by-line. Similarly, secrets constructed at runtime through string manipulation ( api_key = prefix + middle + suffix ) are invisible to static analysis. Obfuscation techniques like hex encoding, ROT13, or even simple character substitution will evade detection. This isn't a Gitleaks-specific limitationâIIit's fundamental to static analysisâIIbut it means Gitleaks is one layer in a defense-in-depth strategy, not a silver bullet. You'll still need runtime secret detection, network monitoring, and secret management platforms to catch what slips through.
Use Gitleaks if you need a fast, zero-configuration secret scanner for Git repositories and you're willing to invest upfront effort in tuning allowlists for your codebase. It's the right choice for open-source projects where transparency demands free tools, for CI/CD pipelines where sub-minute scan times are non-negotiable, and for pre-commit hooks where developer experience depends on instant feedback. The entropy-based detection genuinely catches secrets that pure regex tools miss, and the active development community means detection rules stay current with emerging secret formats. Skip Gitleaks if you're dealing with codebases that have unusual encoding patterns or generate excessive false positivesâIIthe tuning tax might outweigh the security benefits. Also skip it if you need secret rotation workflows, runtime detection, or integration with enterprise secret vaults; Gitleaks is purely a detection tool and you'll need to build or buy remediation capabilities separately.
For organizations already invested in commercial platforms like GitGuardian or cloud-native tools with managed rulesets, Gitleaks' additional value may not justify maintaining yet another tool in your security stack. FreeLLMAPI: A 7.4-Billion-Token Proxy That Aggregates 34 Free LLM Providers Behind One Endpoint Surgical Model Modification: How Blackfrost's DWM Rewrites LLM Behavior Without Breaking Intelligence FreeLLMAPI: A 7.4-Billion-Token Proxy That Aggregates 34 Free LLM Providers Behind One Endpoint Surgical Model Modification: How Blackfrost's DWM Rewrites LLM Behavior Without Breaking Intelligence Credential leaks remain one of the most common and costly security failures in software delivery, often originating from a single hardcoded API key buried in commit history. Implementing secrets scanning in Git and CI with gitleaks provides an automated, open-source defense layer that catches these exposures before they reach production or public repositories. This guide covers practical installation, configuration, and pipeline integration strategies that work for teams ranging from solo developers to enterprise DevOps organizations managing compliance frameworks like SOC 2 or ISO 27001.
Getting started requires minimal overhead. Gitleaks is a single binary written in Go, making it trivial to add to any environment without complex dependencies. For teams adopting CI/CD best practices for small teams , this low-friction setup is critical because security tooling that slows down development gets disabled. Choose the installation method that matches your team's standardization level. On macOS, Homebrew is typically fastest: For Linux environments or containerized build agents, downloading the release binary directly ensures version pinning: Create a .gitleaks.toml file in your repository root. This configuration file travels with your code, ensuring consistent secrets scanning in Git and CI with gitleaks across all environments: The useDefault = true directive inherits over 100 community-maintained rules covering AWS, GitHub, Stripe, Slack, and dozens of other providers. Only add custom rules when your organization uses internal token formats or proprietary API schemas.
Understanding detection mechanics prevents both false negatives (missed leaks) and false positives (developer fatigue). Gitleaks employs two complementary techniques that work together during secrets scanning in Git and CI with gitleaks . Deterministic patterns match known credential structures. AWS access keys always start with AKIA followed by 16 alphanumeric characters. GitHub personal access tokens follow ghp_ prefix conventions. These rules have near-zero false positive rates because they target specific, documented formats.
Shannon entropy measures randomness in strings. A string like aHR0cHM6Ly9leGFtcGxlLmNvbQ== scores high entropy because character distribution is uniform and unpredictable—characteristic of encoded secrets. English prose scores low entropy due to predictable letter frequencies. In practice, entropy detection catches secrets that don't match known patterns but still look suspicious. The tradeoff is noise: UUIDs, hashes, and compressed data also score high. Configure entropy thresholds carefully in your .gitleaks.toml : Local scanning alone is insufficient. Developers can bypass hooks, and historical commits may contain secrets pushed before tooling was adopted. Pipeline enforcement guarantees coverage. If you're evaluating automation platforms, compare options in our GitHub Actions vs GitLab CI comparison to choose the right fit.
The fetch-depth: 0 parameter is non-negotiable. Shallow clones omit historical commits where secrets often hide. I've audited teams that ran scanning for months on shallow clones, only to discover leaked production database passwords three commits deep. This catches issues at the earliest possible stage. However, never treat pre-commit hooks as your only line of defense—they're a convenience layer, not a security boundary.
What are common mistakes when implementing secrets scanning in Git and CI with gitleaks? After helping multiple organizations achieve SOC 2 compliance and remediate credential exposure incidents, I've seen the same anti-patterns repeatedly. Avoiding these saves weeks of rework. This tells gitleaks to ignore previously identified findings while catching new ones. Rotate every secret in the baseline immediately—baselines are for reducing noise, not accepting risk.
Effective secrets scanning in Git and CI with gitleaks is not a set-and-forget checkbox—it's an ongoing practice that combines tooling, process discipline, and incident response readiness. Start with local pre-commit hooks for immediate feedback, enforce pipeline scanning with full history, manage baselines responsibly for legacy codebases, and integrate secret rotation into your remediation workflow. Teams handling regulated workloads should pair this with centralized secrets management; see our guide on secrets management with HashiCorp Vault for architecture patterns that complement scanning. If your team needs help designing audit-ready security controls or integrating scanning into existing infrastructure, reach out to discuss your specific requirements .
A Comprehensive Educational Tool for Developers, DevOps Engineers, and Security Professionals II Important Update (Mid-2026): Zach Rice, the original creator of Gitleaks, has launched a successor tool called Betterleaks . Gitleaks remains stable and will continue to receive security patches, but active feature development has shifted to Betterleaks. See Section 19 at the end of this guide for full details and a migration guide.
Gitleaks is a powerful, open-source static analysis tool designed to detect and prevent secrets (API keys, passwords, tokens, certificates) from being exposed in Git repositories. Developed in Go, it provides fast, accurate scanning capabilities that integrate seamlessly into modern development workflows. The latest stable version of Gitleaks is v8.30.1 (released March 21, 2026), built with Go 1.24. It is considered feature complete by its original author, Zach Rice. Future releases will focus on security patches only. For new features and continued active development, see Section 19: Betterleaks of this guide.
The Solution: Gitleaks provides proactive security by scanning your entire Git history, current files, and incoming changes for sensitive information before it becomes a vulnerability. Note: Earlier versions of this command used gitleaks detect --source . --no-git --verbose . As of v8.19.0+, the filesystem-only scan moved to its own dir subcommand. See Section 5 for the full command-naming change.
Note: The detect and protect commands were deprecated in v8.19.0. They still work but are hidden from --help . The modern equivalents are below. The rest of this guide uses the current syntax throughout. 3. Software Implementation, Frameworks & Protocols Note: The Fingerprint field (used for .gitleaksignore , covered in Section 7) was added in a later release and may not appear in output from very old Gitleaks versions.
Note: The original version of this guide recommended git filter-branch --force --index-filter ... --prune-empty --tag-name-filter cat -- --all . The Git project itself now discourages filter-branch for performance and safety reasons. git-filter-repo is the current best practice and is what’s used above. Scans directories and files without git context, only the current state on disk, not history. Useful for non-git folders or for the fastest possible scan when history doesn’t matter.
Scans content piped from stdin. This is the modern way to wire Gitleaks into pre-commit hooks, replacing the old protect command. Note: The GITLEAKS_VERBOSE environment variable from older versions has been removed; use the --verbose flag instead.
Composite rules allow you to require multiple patterns to match in proximity before flagging a finding. This dramatically reduces false positives. For example, it only flags an AWS access key if a matching secret key also appears nearby. You can suppress specific findings by adding their fingerprints to a .gitleaksignore file at the root of your repo. The fingerprint is included in every finding’s output (see the Fingerprint field in Section 5).
Add // gitleaks:allow (or # gitleaks:allow for Python/Bash/YAML) at the end of a line to suppress findings for that specific line. This is useful for one-off documented exceptions without editing the global allowlist. Note: The GitHub Action above uses gitleaks-action@v3 , not the older v2 . See Section 10 for why this matters. v2 stops working September 16, 2026.
Situation: Security team needs to audit hundreds of repositories across the organization. The simplest and most maintainable way to run Gitleaks as a pre-commit hook today is via the pre-commit framework, which Gitleaks officially supports: Note: The original Neovim snippet called gitleaks protect --staged --source %s , mixing a stdin-style hook with a file argument.
The corrected version above uses gitleaks dir to scan the saved file directly, which is the right tool for a “scan this one file on save” use case. Note: If you’d rather not maintain this script by hand, the pre-commit framework hook shown above handles the Gitleaks portion automatically and is easier to keep updated. But the custom script here is still useful if you want the extra .env and TODO/FIXME checks bundled in.
Important: gitleaks-action@v2 will stop working on September 16, 2026 , when Node 20 is removed from GitHub-hosted runners. Migrate to gitleaks-action@v3 now. It requires GitHub Actions runner v2.327.1 or later (the default on all current hosted runners). Every example below uses v3 . Note: actions/upload-artifact@v3 and actions/github-script@v6 , used in the original version of this guide, were deprecated by GitHub in early 2025; v4 and v7 respectively are the current versions and are used throughout this section.
Note: The original config used gitleaks detect --report-format json with artifacts: reports: junit: . The command has been updated to gitleaks git , and the report format switched to sarif (with a matching gitleaks-report.sarif path) since SARIF integrates more cleanly with GitLab’s native vulnerability reporting UI. If you need JUnit output for a test-results dashboard instead, --report-format junit still works identically to before.
Cause: Scanning a repository with a very long and complex history. Solution: Limit the scan depth. Use the --log-opts flag to scan only recent history. For example, --log-opts="--since='1 year ago'" or --log-opts="--max-count=1000" . Cause: Scanning very large files. Solution: Skip large files by setting a size limit. Use the --max-target-megabytes flag to exclude files larger than a certain size.
Cause: Insufficient system resources. Solution: Increase memory available to Gitleaks, especially when running in a container. For Docker, you can adjust memory limits. Cause: Legitimate test/example data that matches a secret pattern. Solution: Add the fingerprint to .gitleaksignore , add an allowlist entry to gitleaks.toml , or use an inline // gitleaks:allow comment. See Section 7 for all three approaches.
If you’re following old scripts or documentation that use gitleaks detect or gitleaks protect --staged , note that they still work (they’re hidden from --help as of v8.19.0+) but should be updated to the current equivalents used throughout this guide: For any complex issue, the --verbose or -v flag is your best friend. It provides detailed output on which files are being scanned and which rules are being applied.
This will give you insight into the entire process, helping you pinpoint where the issue might be. When scanning large repositories or running Gitleaks in resource-constrained environments, performance can become a critical factor. Here are some strategies to optimize your Gitleaks scans. Large repositories can be slow to scan due to the sheer volume of commits and files. Here’s how to speed things up: Shallow Clones: When cloning a repository for scanning, use a shallow clone to limit the history.
Limit Scan Depth: Use the --log-opts flag to restrict the scan to a recent number of commits. Scan Specific Timeframes: If you only need to audit recent activity, specify a date range. Use a Baseline: Once you’ve done a full initial scan, use --baseline-path on subsequent runs so Gitleaks only needs to report new findings rather than re-presenting everything each time.
A large number of branches can also slow down scans. It’s good practice to regularly prune stale branches. For very large repositories where Git history is not the primary concern, run Gitleaks with the dir command, which only scans the current state of the files and skips walking through git history entirely. This is often dramatically faster. If your repository contains large binary files, using Git LFS can improve performance by keeping those large files out of the main Git repository.
Beyond just running Gitleaks, here are some best practices to build a robust secret management strategy. The “shift-left” approach involves integrating security early in the development lifecycle. Relying on a single tool is not enough. A layered security approach is more effective: Remember: Rotation alone is not enough if the repository is or was ever public. Automated bots scrape newly pushed secrets within minutes. The secret needs to be both rotated and removed from history. Step 1 (revoke) should never wait on Step 2 (clean history), since cleaning history takes longer and the credential is compromised the moment it’s pushed.
Train your team on the importance of not hardcoding secrets and how to use approved secret management tools. For large organizations, Gitleaks offers several advanced and enterprise-grade features. You can use a baseline report to only show new leaks since the last scan. This is useful for integrating Gitleaks into an existing project with a large number of findings.
Automatic Decoding (v8.27+): Decode base64, hex, and percent-encoded text to find hidden secrets. Composite Rules (v8.28+): Require multiple patterns to match in proximity before flagging a finding, dramatically reducing false positives. See Section 7 for full configuration examples. Gitleaks is a powerful tool, but it’s important to understand how it compares to other secret scanning tools in the ecosystem, including its own successor.
With the launch of Betterleaks by Gitleaks’ original author in early 2026, this is the most relevant comparison for anyone choosing a tool today: 4. Practical Deployment, Analysis & Case Studies Without Gitleaks: The code is committed and pushed to a public repository. Within minutes, automated scanners find the key, and the AWS account is compromised, leading to a costly data breach.
Scenario: A company acquires a new business and needs to audit a large, legacy monorepo with years of commit history. To keep Gitleaks effective, it’s important to perform regular maintenance and stay up to date. For Binary Installations: Periodically re-run the installation script to get the latest version. For Gitleaks-Action: Make sure you’re pinned to gitleaks-action@v3 (not @v2 , which stops working September 16, 2026, see Section 10).
For the pre-commit framework: Run pre-commit autoupdate to bump the pinned rev automatically. The default ruleset was actively updated with each release through v8.30.0 (which added Airtable and Looker token detection). Since Gitleaks is now feature-complete, expect future rule updates to be infrequent and security-driven rather than expansive. If you need the ruleset to keep pace with new secret formats from cloud providers, Betterleaks (Section 19) is where that active development is now happening. Its rules are largely compatible with Gitleaks configs.
As your codebase evolves, your allowlists may become outdated. It’s a good practice to periodically review your allowlist rules to ensure they are still relevant and not hiding real leaks. The Gitleaks community is active and welcoming. Here are some resources to help you on your journey. Gitleaks is an open-source project, and contributions are welcome, particularly for security patches, bug fixes, and documentation improvements, since the project is now feature-complete. You can contribute by: New feature contributions and significant rule-set expansions are now generally directed toward Betterleaks instead. See below.
In early February 2026, Zach Rice, the original creator of Gitleaks, joined Aikido Security as Head of Secrets Scanning. He then launched Betterleaks on February 3, 2026, as the official spiritual successor to Gitleaks. Rice has been transparent about the reason: he no longer holds full administrative control over the Gitleaks repository and name. Rather than work around governance friction indefinitely, he started fresh. As he put it: “Betterleaks is the successor to Gitleaks. We’re dropping the ‘git’ and slapping ‘better’ on it because that’s what it is, better.” He has confirmed that Gitleaks will remain stable and continue to receive security patches, so existing users are not forced to migrate. This guide treats Gitleaks (Sections 1–18) as the stable, current-day default and Betterleaks as the option for teams who want the newest detection technology and active development.
The most significant technical change. Instead of measuring how “random” a string looks character-by-character (Shannon entropy, the method Gitleaks uses, described in Section 3), Betterleaks uses Byte Pair Encoding (BPE) tokenization , the same compression technique used by GPT-4 and other large language models. The logic: natural language compresses efficiently into long tokens (high token efficiency). Secrets and random strings compress poorly into many short tokens (low token efficiency). BPE tokenization turns this into a far more reliable signal than raw entropy.
This 28-percentage-point recall improvement means dramatically fewer real secrets slip through undetected, while precision more than doubles. That means far fewer false positives to triage as well. Betterleaks can fire live HTTP requests against detected credentials to verify they are still active. Validation logic is written in Common Expression Language (CEL) , giving rule authors fine-grained programmatic control over what constitutes a confirmed secret. For example, it can distinguish a still-active AWS key from one that was already rotated and revoked.
Betterleaks is fully backwards-compatible with Gitleaks. Existing config files, allowlists, and CLI flags all work without modification, which is why the migration guide below is so short. Simpler installation with no native library requirements, which also simplifies cross-platform builds and container images. Processes multiple commits simultaneously instead of walking history linearly, the way Gitleaks does (see Section 3, Phase 1). Benchmarks show significantly faster scans on large repositories with deep history.
Betterleaks includes tight output controls and flag-based output suppression, making it easy for AI coding agents (like Claude Code or Cursor) to integrate as a subprocess without excessive token overhead. That’s a use case that didn’t really exist when Gitleaks’ CLI was originally designed. The same applies to every example in Sections 8-14 of this guide. Anywhere you see gitleaks git , gitleaks dir , or gitleaks stdin , the Betterleaks equivalent is simply betterleaks in place of gitleaks , with identical flags.
Betterleaks is open-source under the MIT license and is maintained by four core contributors: Zach Rice (project lead), plus contributors from the Royal Bank of Canada, Red Hat, and Amazon. Aikido Security acts as a sponsor, not an owner, and Rice retains project ownership. That’s a deliberate structural difference from how Gitleaks’ governance evolved. Either way, if you’re currently using neither tool, start somewhere. Even Gitleaks at 70.4% recall stops the vast majority of real secrets from reaching production, and migrating later is, by design, nearly frictionless.
This guide was last updated June 2026. For the latest information, consult the official repositories at github.com/gitleaks/gitleaks and github.com/betterleaks/betterleaks ._ Kokil Thapa is an experienced full-stack web developer focused on building fast, secure, and scalable web applications. He helps businesses and individuals create SEO-friendly, user-focused digital platforms designed for long-term growth.
Hardcoded credentials remain one of the most common and damaging security failures in production web systems. Implementing secrets scanning in Git and CI with gitleaks catches API keys, database passwords, and private tokens before they reach your repository history or deployment pipeline. This guide provides the exact configuration I use on production Laravel and legal-tech projects to enforce this safety net without disrupting legitimate development workflows.
The first line of defense is always local. Relying solely on CI means secrets have already been pushed to the remote, requiring history rewriting if caught. For developers working on sensitive projects like legal-tech portals handling client data , preventing the leak at the source is non-negotiable. Gitleaks v8.21+ (current stable in 2026) supports native Git hook integration that validates staged changes before the commit object is created.
Install gitleaks via Homebrew, apt, or direct binary download. For team consistency, pin the version in your project documentation or DevContainer configuration. On Ubuntu 24.04 servers I maintain, I install it globally so all users share the same scanner version: The --staged flag is critical. Without it, gitleaks scans the entire working directory including untracked files and build artifacts, producing excessive false positives. With --staged , it only examines what you are about to commit. The --pre-commit flag installs the hook script into .git/hooks/pre-commit automatically.
Real projects contain placeholder credentials in test suites, example configurations, and documentation. Blocking these halts development unnecessarily. Create a .gitleaksignore file in your repository root to allowlist specific false positives by their SHA256 fingerprint: Generate fingerprints for legitimate secrets using gitleaks detect --verbose on the offending commit, then copy the Fingerprint value. Never allowlist by file path alone — paths change during refactoring, but content hashes remain stable. Review the allowlist quarterly as part of your CI/CD maintenance routine .
Local hooks can be bypassed. A determined developer can skip them with --no-verify , or a misconfigured environment might not have the hook installed. CI integration serves as the authoritative enforcement point. In my experience managing shared infrastructure for multiple Nepal-based legal and translation service sites, the CI job is where most real-world catches happen after initial adoption.
Add this job to your .gitlab-ci.yml . It runs early in the pipeline, fails fast, and uploads results as an artifact for audit trails. This configuration works with GitLab CI runner images that include curl and tar: The when: always directive ensures the report uploads even when secrets are found. Without it, a failed job produces no artifact, making triage impossible. Set expire_in according to your compliance requirements — 30 days covers most audit windows while avoiding storage bloat.
Full-history scans on mature projects with thousands of commits take minutes. For monorepos or legacy codebases, restrict scanning to the merge request diff range: This reduces scan time from minutes to seconds on active branches. Reserve full-history scans for nightly scheduled pipelines or initial baseline assessments. On a legal document management system I maintained, switching to diff-based scanning reduced CI feedback time from 4 minutes to 18 seconds per merge request.
Gitleaks ships with 100+ built-in rules covering AWS, GitHub, Stripe, and other major providers. However, PHP and Laravel ecosystems have unique secret patterns that default rules miss. Custom rules catch framework-specific leaks like APP_KEY values, Sanctum tokens, and Nepal payment gateway credentials. Create .gitleaks.toml in your project root. Extend the default rules rather than replacing them to retain upstream provider coverage: The Sanctum token rule deserves explanation. Sanctum formats tokens as {id}|{hash} where both segments are fixed-length alphanumeric strings. The pipe character combined with exact lengths makes this pattern highly specific. Generic base64 detectors miss this format entirely because the pipe breaks standard encoding assumptions.
Never deploy untested regex rules. False positives erode trust and lead developers to disable scanning. Validate against known-good and known-bad samples: If a rule triggers more than 5 times on legitimate code during validation, refine the regex or add contextual keywords. Precision matters more than recall in custom rules — let the default high-confidence rules handle generic cases.
5. Performance Evaluation & Extended Technical Observations Finding a secret is only half the problem. Remediation requires revoking the compromised credential, removing it from Git history, and verifying no downstream systems cached the old value. Skipping any step leaves residual risk. This ordering is counterintuitive but essential. If you rewrite Git history first, the old secret remains valid in production systems during the cleanup window. An attacker who cloned the repository before the force-push retains access. Always rotate the credential immediately upon discovery, then proceed to history cleanup.
For Laravel projects, regenerate APP_KEY with php artisan key:generate and re-encrypt any data encrypted with the old key. For API integrations like those described in Laravel API best practices , generate new tokens and update environment variables across all deployed instances simultaneously. Avoid git filter-branch — it is deprecated and error-prone. Use git-filter-repo (installed via pip or package manager) for reliable history rewriting: Coordinate force-pushes with your team. Every contributor must re-clone or reset their local branches. Document the incident timestamp and affected commit ranges so future bisect operations account for the discontinuity. On shared infrastructure like the Deployer 7 + GitLab CI setup I use for sister sites, schedule rewrites during low-traffic windows to minimize deployment disruption.
Implementing secrets scanning in Git and CI with gitleaks transforms credential security from reactive incident response to proactive prevention. Start with local pre-commit hooks for immediate developer feedback, enforce mandatory CI gates for authoritative protection, extend default rules for your specific technology stack, and establish clear remediation procedures before your first real leak occurs. The configuration patterns in this guide reflect battle-tested setups from production Laravel applications and legal-tech platforms serving real clients.
If your team needs help integrating secrets scanning into existing CI/CD pipelines, configuring custom rules for PHP/Laravel projects, or remediating historical leaks safely, reach out to discuss your specific requirements . Proper secrets management is foundational infrastructure, not optional compliance theater. Your email is not published. Comments appear once they have been read. Sign in to have your details filled in.
Learn how to use gitleaks to detect hardcoded secrets, API keys, and credentials in your Git repositories before they become security incidents. A single leaked API key can cost millions. Secrets accidentally committed to Git spread through clones, forks, and backups faster than you can rotate them. gitleaks scans Git history for credentials, preventing leaks before they reach remote repositories. This guide covers installation, configuration, CI/CD integration, and remediation workflows.
Once pushed, secrets persist in Git history even if "deleted" in a later commit. Attackers scrape public repositories specifically looking for these patterns. gitleaks is a single binary written in Go. Install it using your package manager or download directly: gitleaks uses regular expressions and entropy analysis to detect secrets. The default configuration covers: Secret scanning is a safety net, not a primary defense. Use secret management tools (Vault, AWS Secrets Manager) and environment variables to keep credentials out of code. gitleaks catches the mistakes that slip through, preventing a configuration error from becoming a breach.
Every OneUptime blog post is open source. Found a typo, an inaccuracy, or have a clearer way to explain something? Anyone can contribute — your edits make this post better for everyone who reads it next. Your complete reliability stack unified: infrastructure monitoring, incident management, status pages, and APM. Open-source and self-hostable.
In today's development environment, maintaining the security of your code is as crucial as ensuring its functionality. One of the key aspects of security is managing and safeguarding your secrets, such as API keys, passwords, and tokens. Accidentally committing these secrets to your repository can lead to severe security breaches. Implementing secret scanning in your Continuous Integration (CI) pipelines is essential to mitigate this risk. This blog will guide you through setting up secret scanning in GitLab CI pipelines using Gitleaks and a pre-commit hook .
Before diving into the technical setup, let's briefly discuss why secret scanning is important: Prevent Data Leaks: Secrets embedded in the code can be easily exposed if not managed properly, leading to unauthorized access. Compliance: Many organizations have compliance requirements that mandate the protection of sensitive data.
Early Detection: Scanning for secrets early in the CI pipeline helps catch issues before they make it to production. Faster Time to Market through Accelerated Releases: Automated secret scanning ensures that security checks do not become bottlenecks in the release process, allowing for faster and more frequent releases. Gitleaks : An open-source tool that scans your codebase for secrets, providing a comprehensive way to detect and prevent leaks.
Git Hooks: This is a git functionality. It's a way to run custom scripts when certain actions occur. OWASP Juice Shop : The application code to be used for this demonstration. It is probably the most modern and sophisticated insecure web application. Juice Shop encompasses vulnerabilities from the entire OWASP Top Ten and many other security flaws in real-world applications! Gitlab: A web-based DevOps lifecycle tool that provides a Git repository manager with features like source code management (SCM), continuous integration (CI), continuous deployment (CD), and more.
STEP 2: Create a .gitlab-ci.yml file in the repository. This file is the configuration file that GitLab CI/CD uses to define the pipeline and its various stages, jobs, and actions. IMAGE_NAME and IMAGE_TAG : These variables define the name and tag of the Docker image that will be built and pushed. cache : Stage for caching dependencies. test : Stage for running tests and performing secret scanning. build : Stage for building and pushing the Docker image.
create_cache : This job uses the node:18-bullseye image to install dependencies with Yarn. Caching : The node_modules/, yarn.lock, and .yarn directories are cached based on the yarn.lock file to speed up future pipeline runs. gitleaks : This job uses the zricethezav/gitleaks image to scan the source code for secrets. Report : The results are saved to gitleaks-report.json.
yarn_test : This job installs dependencies and runs tests using the node:18-bullseye image. Caching : Similar to the create_cache job, it caches dependencies to speed up future runs. build_image : This job uses the docker:24 image and the Docker-in-Docker (dind) service to build and push the Docker image. Docker Login : The DOCKER_PASS and DOCKER_USER variables are used to log in to Docker Hub. Build and Push : The Docker image is built with the specified IMAGE_NAME and IMAGE_TAG, and then pushed to the Docker registry.
After running the pipeline, the job at the gitleak job failed due to leaks found in the repository. PRE_COMMIT HOOK Implementing a pre-commit hook to scan for potential leaks in your code can prevent sensitive credentials from being committed to the repository. This proactive measure ensures sensitive information remains secure and never makes it to the repository commits, mitigating the risk of exposure to attackers.
Open your terminal and navigate to the root directory of your Git repository. cd /path/to/your/repository Create the pre-commit hook file: Inside the .git/hooks directory, create a file named pre-commit. vi .git/hooks/pre-commit Configuration: Defined variables for image name, host folder, container folder, and report file for easy configuration and readability.
Error Handling: The function exit_with_error was added to handle errors gracefully and provide meaningful error messages. Docker Pull: Added error handling for the docker pull command to ensure the script exits if pulling the Gitleaks image fails. Docker Run: It is used to configure variables to run the Gitleaks container and capture its exit code. Check Gitleaks Exit Code: Checked the exit code of the Gitleaks run and displayed the report if secrets were detected, preventing the commit.
The pre-commit hook has helped enforce secret protection by preventing commits until any leaked secrets are removed. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Heartbleed • https://gitdiagram.com/gitleaks/gitleaks • https://github.com/gitleaks/gitleaks • https://starlog.is/articles/llm-engineering/gitleaks-gitleaks • https://khimananda.com/blog/secrets-scanning-in-git-and-ci-with-gitleaks • https://laoutaris.org/blog/gitleaks/ • https://kokil.com.np/blog/secrets-scanning-in-git-and-ci-with-gitleaks • https://oneuptime.com/blog/post/2026-01-25-secret-scanning-gitleaks/view • https://dev.to/sirlawdin/secret-scanning-in-ci-pipelines-using-gitleaks-and-pre-commit-hook-1e3f • https://blog.gnomeitsolutions.com/git-secrets-scanning-gitleaks/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Git Leaks Scanner And Sensitive Credential Detector.
[*] Synchronizing KnowBe4 Awareness Training telemetry... ──────────────────────────────────────────────────────────────────────── [11:45:02.102] MAIL Dispatched simulated assessment templates [11:45:02.155] REPORT Majority of active users flagged probe via Phish Alert Button [11:45:02.210] CLICK Simulated lure baseline reduced below risk threshold [11:45:02.290] TRAIN Auto-enrolled flagged users into adaptive micro-learning modules ──────────────────────────────────────────────────────────────────────── [✓] Human Security Index: Phish-Prone percentage safely minimized
| Campaign Simulation | Platform Used | Total Recipients | Reported via Phish Button | Phish-Prone Percentage |
|---|---|---|---|---|
| Urgent Communication Lure | KnowBe4 KMSAT | 350 Employees | 318 (90.8%) | 2.9% (OPTIMAL) |
| Account Credential Lure | Proofpoint ZenGuide | 350 Employees | 324 (92.5%) | 2.1% (OPTIMAL) |
| Executive Impersonation | Mimecast Engage | 200 Executives | 192 (96.0%) | 1.5% (OPTIMAL) |