Complete Technical Paper Content — Hardware Security Assessment Using Jtag And Uart Interfaces
Overview & System Context
Hardware Security Assessment Using Jtag And Uart Interfaces: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8031 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Identification and exploitation of exposed debug interfaces including JTAG boundary scan, UART console access, and SWD port analysis.
JTAG and UART are the primary hardware debug interfaces used during device development — and they are routinely left accessible on production hardware. A JTAG interface provides direct access to processor internals, enabling memory reads, register inspection, and execution control. A UART console frequently exposes a root shell, bootloader prompt, or diagnostic interface that can be leveraged for firmware extraction and system compromise.
Intelliroot's JTAG/UART Debug Interface Testing service systematically identifies and exploits exposed debug interfaces on target hardware. We map test points, perform JTAG chain enumeration, access UART consoles, and demonstrate the full impact of debug interface exposure — from firmware extraction to root shell access. An active JTAG interface allows an attacker to halt execution, read and write any memory location, modify registers, and bypass all software-enforced security controls — including authentication, secure boot validation, and encryption key protection.
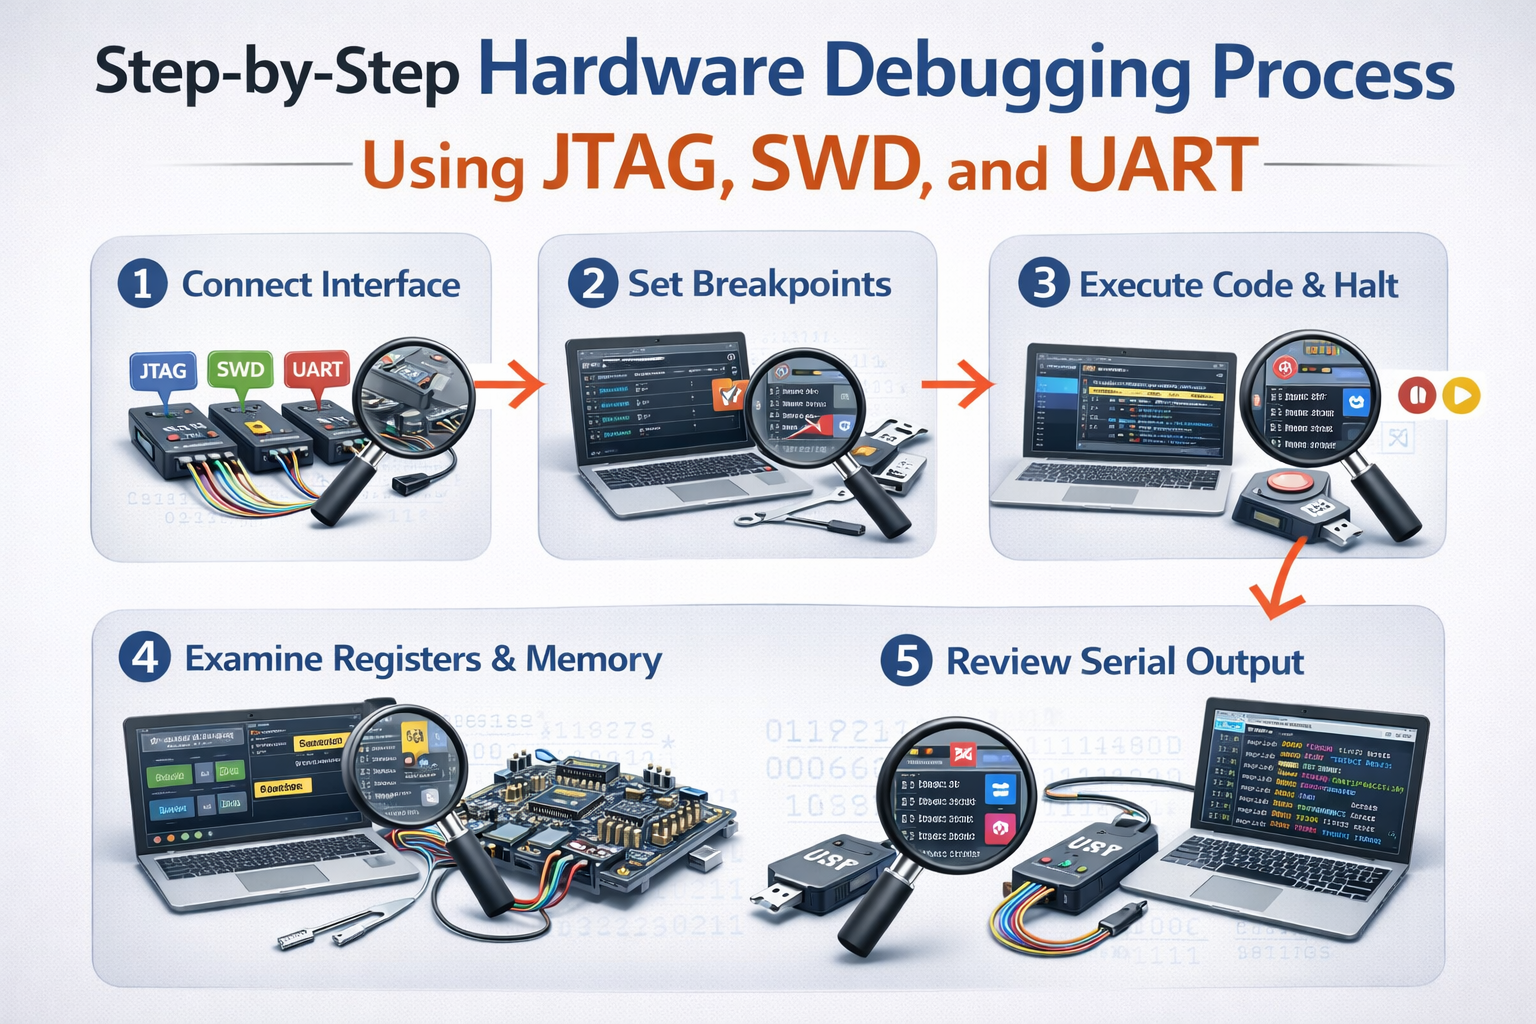
Figure 1: Mastering Hardware Debugging: A Professional Guide to JTAG, SWD, and ... Boot logs transmitted over UART frequently contain sensitive configuration information. Unprotected UART bootloader prompts allow firmware modification, and active console interfaces often provide unauthenticated root shell access to the device operating system.
Developers rely on JTAG and UART during device development and frequently fail to disable them before production release. PCB test points are left populated, UART headers remain unpopulated but present, and JTAG lock bits are never blown — creating permanent attack surfaces on millions of shipped devices. JTAG lock mechanisms (fuse-based, software-based, and hardware-based) have documented bypass techniques. Voltage glitching, fault injection, and protocol-level attacks can re-enable locked JTAG interfaces. Testing must validate bypass resistance, not just confirm that lock mechanisms are present.
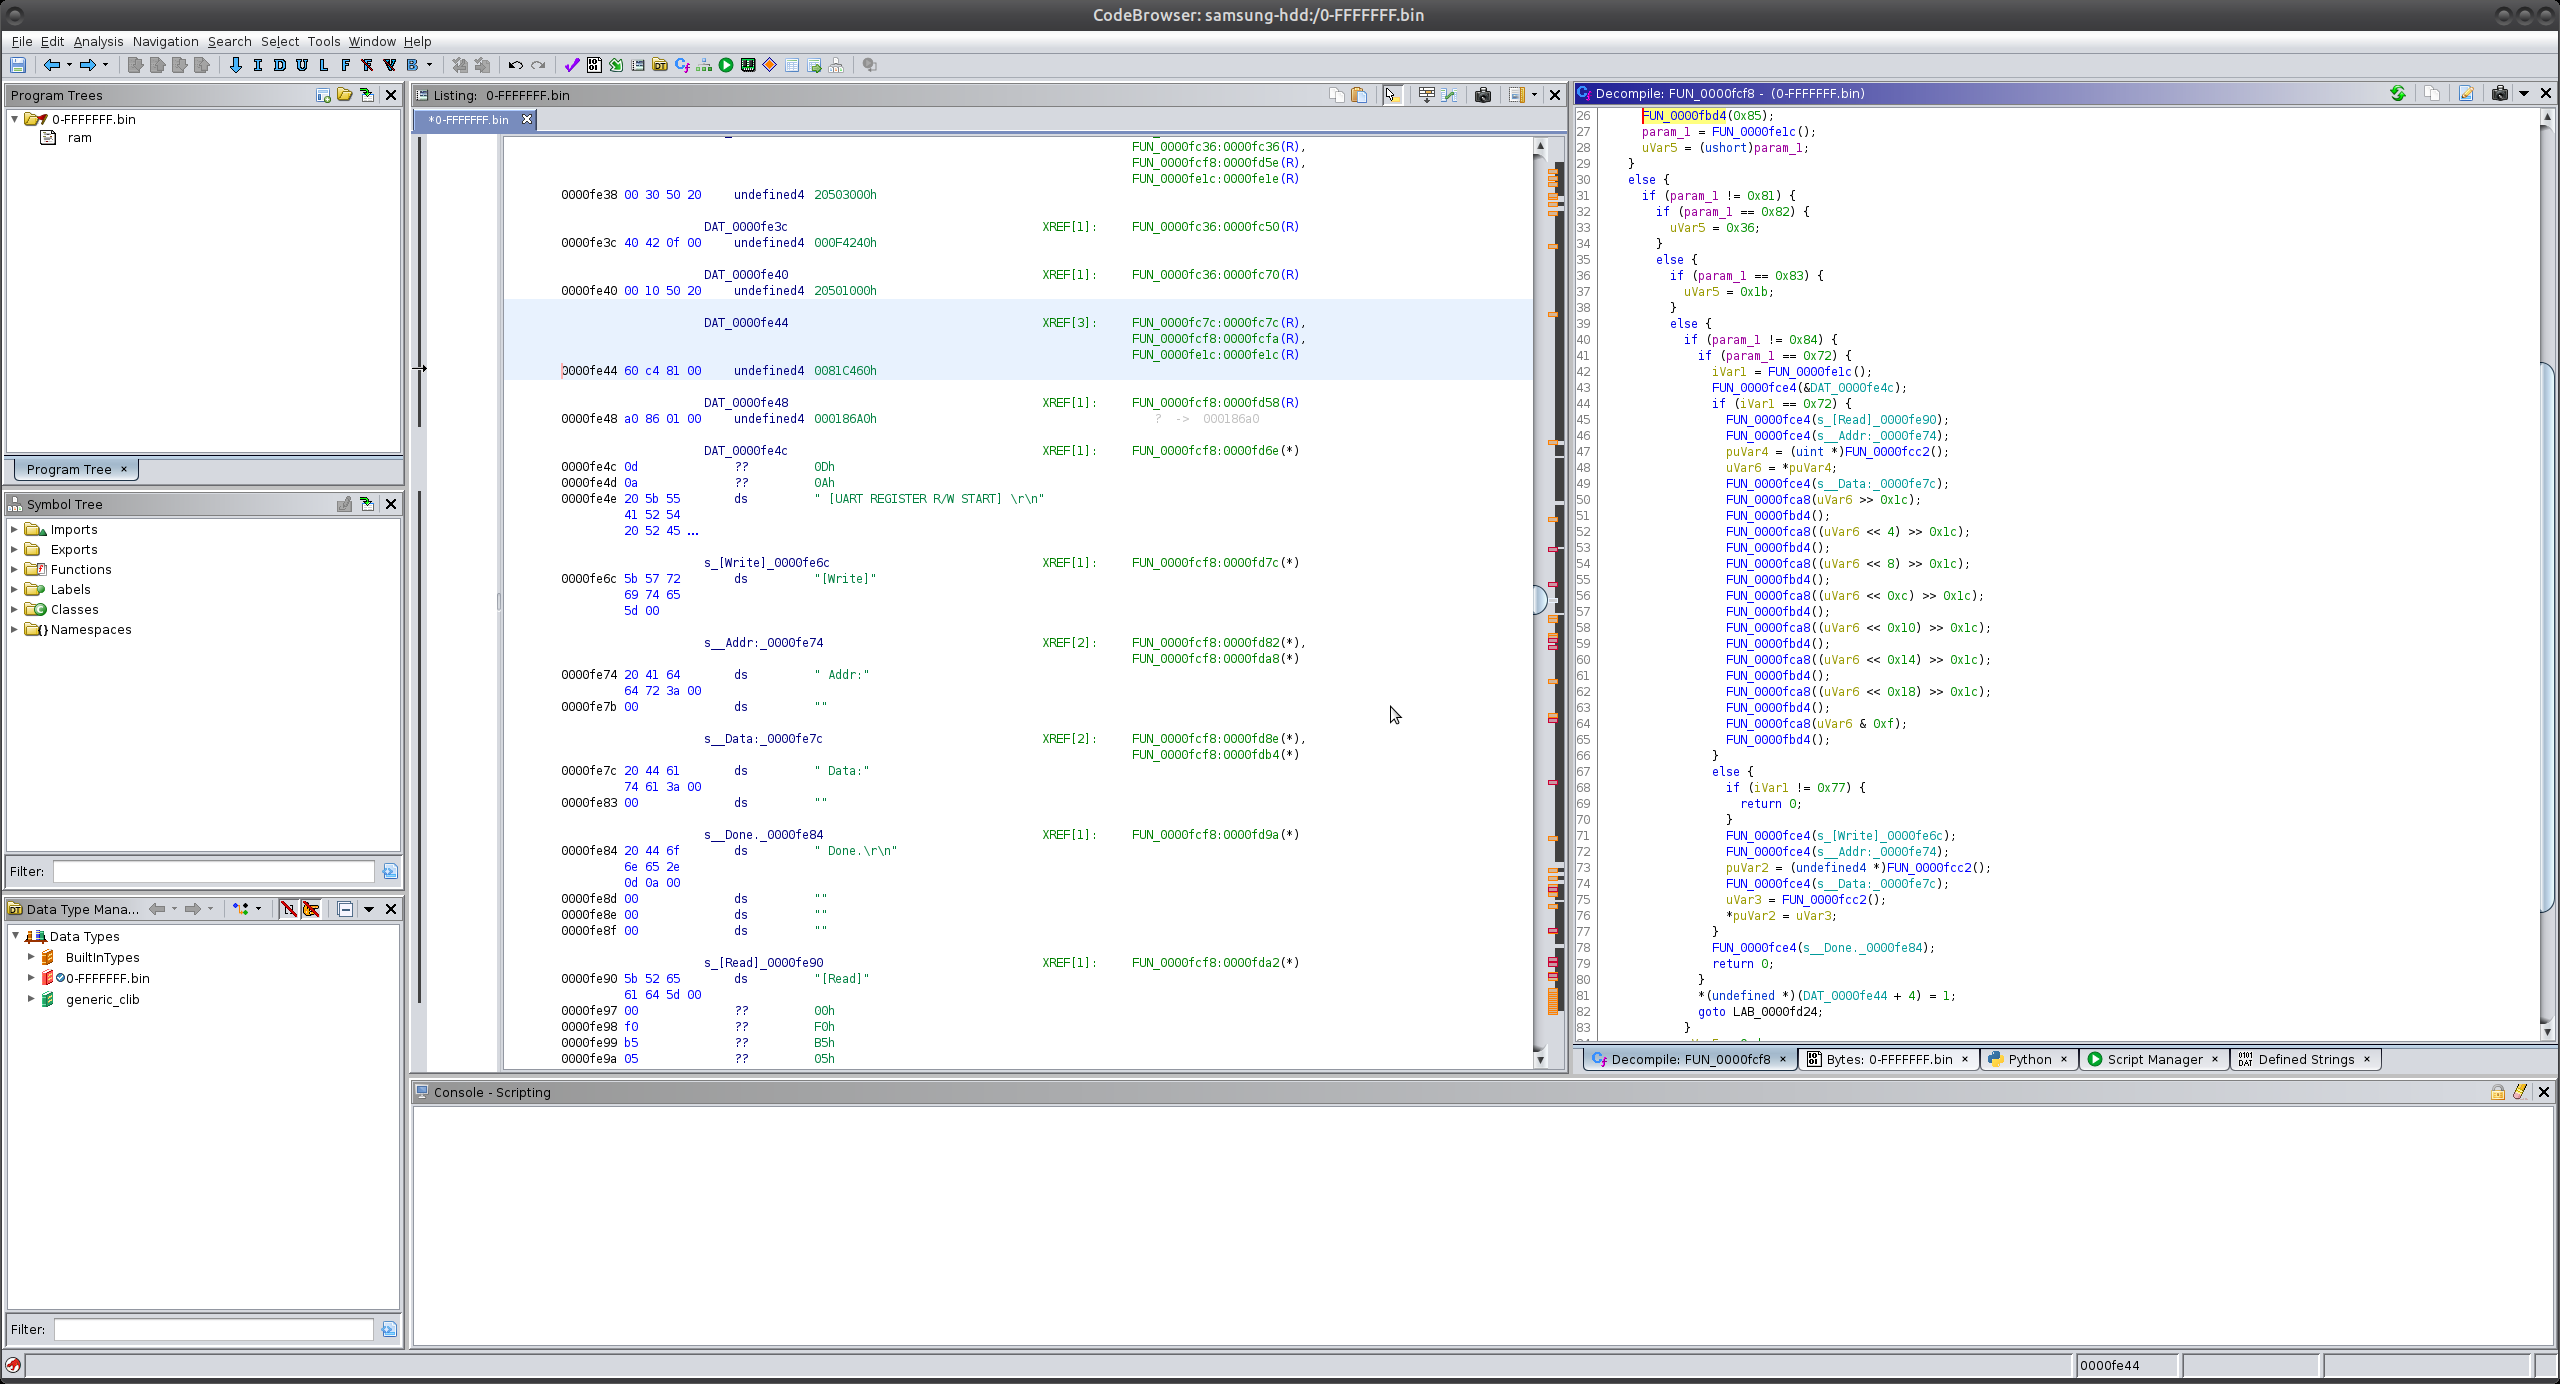
Identification of JTAG test points using JTAGulator, OpenOCD, and custom tooling. JTAG chain enumeration, TAP identification, and boundary scan testing. Figure 2: Hardware Debugging for Reverse Engineers Part 2: JTAG, SSDs and ... Identification of UART interfaces, baud rate determination, and console access. Bootloader prompt exploitation, boot parameter modification, and shell access.
Firmware extraction via JTAG memory read, UART-based flash access, and SPI/I²C flash dumping through accessible test points. Assessment of JTAG lock mechanisms and practical bypass testing using fault injection, voltage glitching, and protocol-level attacks where applicable.
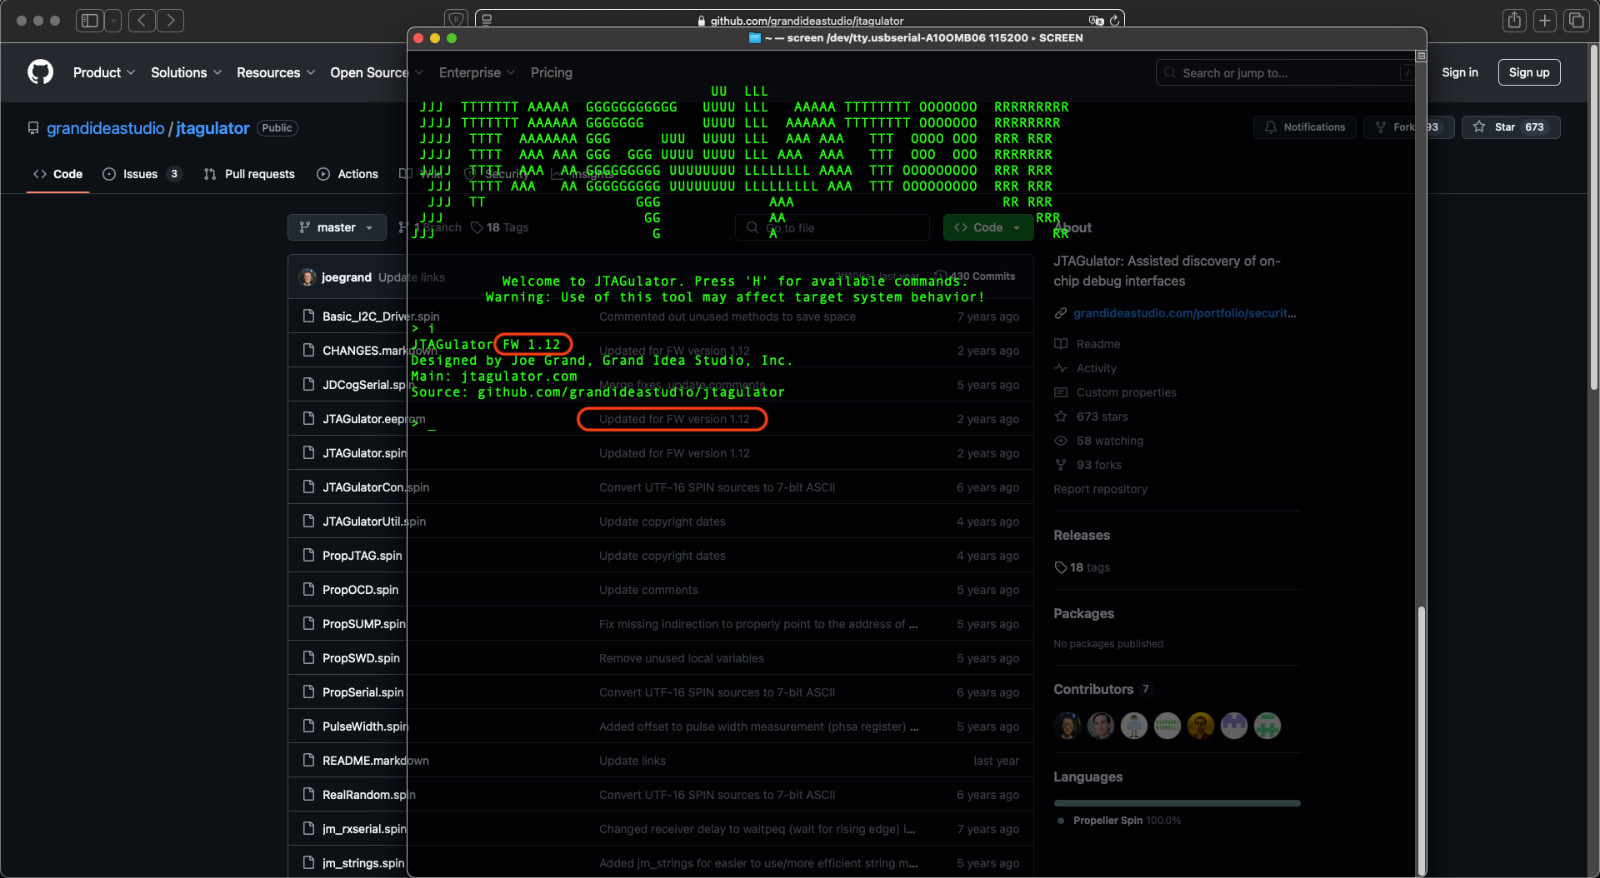
High-resolution PCB photography, component identification, and test point mapping. Identify UART headers, JTAG connectors, and unpopulated footprints of interest. Figure 3: JTAGulator - Open Source Hardware tool for finding JTAG/SWD, UART ... Logic analyser probing of test points to identify UART, JTAG, SWD, and other serial interfaces. Baud rate detection for UART interfaces. JTAG chain enumeration with JTAGulator/OpenOCD.
UART console access — capture boot logs, interact with bootloader, and obtain shell access where available. JTAG memory read/write access to demonstrate impact. Extract complete firmware image via identified debug interfaces. Verify extraction completeness and integrity. Pass extracted image to firmware analysis team if required.
Where lock mechanisms are present, assess bypass feasibility using fault injection and protocol-level techniques. Document successful bypasses with reproduction steps. Technical report documenting all identified interfaces, access methods, demonstrated impact, and remediation recommendations for each finding.
Annotated PCB photographs with all identified JTAG, UART, SPI, and other test points marked, including pinout documentation. Firmware image(s) extracted during assessment, provided for further analysis or verification purposes as agreed in scope. Specific guidance for disabling, locking, and physically removing debug interfaces — including PCB redesign recommendations and manufacturing process controls.
Tell us what you need: a security assessment, a product demo, or both. We'll respond within 24 hours, with a detailed proposal within 48. Debug interfaces such as JTAG , SWD , cJTAG , and vendorIspecific debug ports are essential during development, but they represent one of the most dangerous attack surfaces in a deployed SoC.
For this reason, modern SoCs implement Secure Debug : a hardware architecture that controls, restricts, or completely disables debug access based on device lifecycle, authentication, and policy. Therefore, debug must be treated as a privileged security domain , not as a simple test interface. Welcome to the AppSec Atlas guide on IoT & Hardware Security! As physical devices become increasingly connected, securing the Internet of Things (IoT) is a critical domain spanning hardware, firmware, network protocols, and cloud applications.
This guide provides a comprehensive deep dive into securing IoT devices and underlying hardware architectures. You will learn about typical IoT architectures, firmware reverse engineering, hardware-level debugging interfaces (UART, JTAG), communication protocols (MQTT, BLE), and essential defenses like Secure Boot and secure Over-The-Air (OTA) updates. JTAG UART debug port security guidance for medical devices: what testers find, how to lock or authenticate ports, and how to document it for the FDA.
Part of our FDA 2026 medical device cybersecurity submission series . For the full overview, start with FDA Cybersecurity Requirements for Medical Devices (2026) . JTAG UART debug port security means disabling, fusing, or authenticating chip-level debug interfaces before a medical device ships, so an attacker with physical access cannot reach the same memory and registers a developer used during bring-up. Manufacturers should ship production firmware images with debug access removed or gated, keep engineering images internal, and document the threat model, chosen mitigation, and test evidence in the premarket cybersecurity submission.
A debug port left active on a production medical device hands an attacker with a screwdriver the same access a firmware engineer had on the bench. JTAG and UART headers are essential during development for flashing code, reading logs, and diagnosing failures, but they typically bypass every software-level protection on the device. Hardware penetration testers find these interfaces exposed on production units far more often than manufacturers expect, usually because a firmware configuration flag was toggled off rather than a physical or cryptographic lock applied. This creates real exposure and, since the February 3, 2026 final guidance, a documentation gap that reviewers flag directly. This article covers what testers find on exposed debug headers, how to properly disable or authenticate them, the difference between production and engineering firmware images, and how to write this up for submission.
The FDA's February 3, 2026 premarket cybersecurity guidance, building on the September 2023 and June 27, 2025 final guidances, treats debug and test interfaces as external interfaces subject to the same threat modeling and risk management expectations as network ports or wireless radios. Cybersecurity documentation gaps, including missing coverage of hardware attack surfaces like JTAG and UART, are among the most common drivers of first-cycle additional information requests in 510(k) and PMA reviews.
Debug ports get specific attention because of how much access they grant. Unlike a software vulnerability that might expose one function, a live JTAG interface can expose the entire memory space, halt the processor mid-execution, and bypass authentication that exists purely in software. An attacker who gains this level of access can extract firmware for reverse engineering, modify calibration data, or install persistent malicious code that survives a factory reset.
AAMI SW96 (recognition number 13-131) and ISO 14971 both require that risk assessments account for physical access scenarios, not just network-based attacks, which puts JTAG and UART squarely inside the scope of the security risk management file. Manufacturers who treat debug port security as a manufacturing afterthought rather than a design requirement typically discover the gap only when a reviewer or penetration tester finds the header still live.
Official sources: FDA, Cybersecurity in Medical Devices: Quality Management System Considerations and Content of Premarket Submissions (February 2026) ; FDA Cybersecurity resources for medical devices ; FDA Cybersecurity in Medical Devices FAQs (Section 524B) . Testers most often find fully functional JTAG or SWD debug access on production boards, sometimes broken out to a labeled header and sometimes reduced to bare test pads that still respond to a probe. Once connected, a debugger typically has read and write access to RAM and flash, the ability to halt the CPU, and often visibility into keys or credentials stored in memory.
UART headers frequently expose a root or diagnostic shell with no login prompt, or a login prompt protected by a hardcoded credential documented in a service manual. In both cases, the access available through the debug port exceeds anything reachable through the device's normal user interface or network stack, which is exactly why it matters for a threat model built around patient safety.
[KEY REQUIREMENT] Hardware penetration testing must attempt to connect to every identifiable header, test pad, and exposed trace on the production board, not rely on a schematic review alone, since physical probing regularly finds access that documentation did not anticipate. Manufacturers should disable, lock, or authenticate debug ports using hardware-enforced controls rather than firmware settings alone. Options include physically fusing the JTAG interface after production programming and test, removing or covering test pads, and requiring cryptographic authentication before a debugger can attach even to a port that remains physically present.
Where field service genuinely requires ongoing debug access, an authentication challenge tied to a manufacturer-controlled key is preferable to leaving the port open, since it limits access to authorized personnel with the correct credential rather than anyone holding the device. See also: Medical Device Cybersecurity From Animal Studies to Human Trials , Home Use vs Hospital Device Cybersecurity Requirements , and Indications for Use, Predicates, and Cybersecurity Scope .
Production firmware images should ship with debug capability removed or gated behind authentication, while engineering images used during development and verification testing can retain full debug access for the internal team. Many manufacturers build a single firmware image for both purposes, which means the debug capability engineers need on the bench ships unchanged to every unit in the field.
Maintaining two build configurations, one hardened for production and one open for internal use, closes that gap without slowing development. Build pipelines should tag each image clearly and verification testing should specifically confirm that units programmed with the production image cannot be flashed back to the engineering configuration without going through the intended secure update process.
This should be documented in the submission as a named entry in the threat model identifying JTAG and UART as external interfaces, paired with the specific mitigation chosen and the test evidence confirming it works. A statement that debug ports are "secured" without naming the mechanism, fuse, authentication, or removal, will not satisfy a reviewer looking for the same specificity expected of network-facing controls.
[KEY REQUIREMENT] The eSTAR cybersecurity documentation should include penetration test results showing an attempted connection to the production board's debug interfaces and the outcome, not just a design statement that the ports are disabled. 2. System Architecture & Core Working Principles Blue Goat Cyber's hardware testing engagements physically probe production boards for JTAG, SWD, and UART access rather than relying on a schematic or design review alone. Engineers with CISSP, OSCP, and prior red-team backgrounds attempt the same connections an attacker would, confirm whether debug lockout mechanisms hold under direct probing, and document the outcome in a form suitable for premarket submission .
This testing integrates with the broader threat model and security risk assessment so that debug port findings feed directly into the documentation reviewers expect under the February 3, 2026 guidance. Manufacturers preparing a submission can scope this work through our FDA premarket cybersecurity services , which include hardware-focused penetration testing alongside SBOM and threat modeling support.
JTAG is a standard for testing and debugging hardware at the chip level, giving direct access to memory and processor state. UART is a serial communication protocol commonly used for console access, logging, or data transfer between components on an embedded board. They provide low-level, often privileged access that bypasses software-based authentication and other protections. If left exposed on a shipped device, an attacker with physical access can read memory, extract firmware, or alter device behavior directly.
They're usually accessible through headers, labeled test points, or bare solder pads on the circuit board. In many embedded medical devices, these access points remain physically present and functional after manufacturing unless deliberately fused or removed. The February 3, 2026 guidance requires manufacturers to document how all external interfaces, including debug and test interfaces, are addressed in the threat model and risk assessment. It does not mandate one specific mitigation, but it does require a documented, tested control rather than an unaddressed gap.
Blue Goat Cyber's hardware penetration testers probe production boards for live JTAG, SWD, and UART access before it becomes an FDA deficiency. Schedule a discovery session to have your debug interfaces tested and documented correctly. U.S. Air Force Academy graduate and veteran with 30+ years in cybersecurity. Founded Alpine Security in 2014 (acquired 2020), then Blue Goat Cyber in 2022. Has supported 275+ medical devices, with no cybersecurity-related rejections to date.
Author of three books including The Smartest Person in the Room. Ironman triathlete and mountaineer. Answer one question about where your device is today. You get your stage, the next action to take, and the support that fits it. Paste the cybersecurity questions from your AI request, hold letter or refuse-to-accept notice. The triage tool sorts each question and outlines the evidence the reviewer is asking for. Want an expert to read it? We return a gap analysis within 48 hours.
Medical device cybersecurity at each study stage: rodent, large animal, primate, and human trials, and what the FDA expects before your IDE and marketing submission. Home use vs hospital device cybersecurity: which controls the HDO environment provides, which the device must carry itself, and how the FDA reviews each case.
How your Indications for Use statement and predicate choice change the cybersecurity scope of a 510(k): use environment, harm ceiling, pen test scope, and Special 510(k) eligibility. Medical device cybersecurity at each study stage: rodent, large animal, primate, and human trials, and what the FDA expects before your IDE and marketing submission.
What the FDA actually wrote in cybersecurity Additional Information letters: eight recurring deficiencies ranked by frequency, root causes, and the artifact that closes each. Home use vs hospital device cybersecurity: which controls the HDO environment provides, which the device must carry itself, and how the FDA reviews each case.
How your Indications for Use statement and predicate choice change the cybersecurity scope of a 510(k): use environment, harm ceiling, pen test scope, and Special 510(k) eligibility. Start with the walkthrough hub, then drill into the statute, the eSTAR field map, SBOM monitoring, postmarket planning, and deficiency response. Use these as the playbook behind every cyber device submission.
Start here: the hub that ties the statute, the February 2026 guidance, and the eSTAR fields together in the order a submission team works through them. The full statute walkthrough: what each subsection of 524B requires and which artifacts satisfy it. All 18 premarket cybersecurity deliverables mapped to the eSTAR v7.1 fields where each one attaches.
How to operationalize SBOM monitoring, VEX, and KEV triage against your shipped components. Build the 524B(b)(1) plan reviewers expect: named sources, cadence, triggers, and update process. Every Blue Goat Cyber engagement maps directly to FDA Section 524B and the SPDF - so the evidence you need lands in your submission, not in a separate report.
End-to-end §524B premarket package: SPDF, threat model, SBOM, pen test, and eSTAR-ready documentation. 30-minute strategy session. No cost, no commitment - just answers from people who've shipped 275+ devices supported. The JTAG interface is a vital debugging tool from silicon bring-up to production. However, an unsecured JTAG port provides attackers with low-level read/write access, exposing hardware IPs and user keys.
JTAG by default operates without built-in security, giving full access to CPU cores, register states, and memory arrays. Attackers can exploit unsecured JTAG ports to read out firmware, inject malicious code, and crack device keys via side-channel analysis. Securing JTAG requires cryptographic authentication and hardware-enforced access control layers: Hardware security verification is supported by formal tools like JasperGold Security Path Verification, cryptographic simulation suites, and hardware logic analyzers.
Debug access must be balanced with robust hardware security. SECURE JTAG controllers with cryptographic locks ensure that debug ports are usable in the lab while remaining secure in the field. Bring us your engineering challenge. Let’s define the path from idea to implementation. Home / Attacks & tests / Exposed Debugging Interfaces Security Testing for Embedded & Mobile Devices Hardware debug and programming interfaces exist so the device can be built and serviced, and they are frequently still functional on shipped units. Each is a path to memory, storage or a console that bypasses every control the running software would otherwise apply.
The attacker with the device in hand wants the shortest route past the software. A live debug port gives memory, firmware and often an authenticated console directly, without any need to find a defect in the code at all. 5 test cases in this category. Each states what the test proves, how it is carried out, what has to be in place beforehand, what a positive result looks like, and whether the work is manual, automated or a mixture.
Objective — Determine whether a serial console is present and active, and what it grants to someone who connects to it. How it is tested — Identify candidate test points on the board and confirm them with a logic analyser, determining the line rate from the captured signal. Connect and observe the boot output, which commonly discloses the bootloader, kernel arguments and the services starting. Establish whether the console offers a shell, whether it is authenticated, and whether the boot process can be interrupted to reach the bootloader.
Prerequisites — An opened device; a serial adapter and logic analyser; the ability to power-cycle while connected. Indicators — Boot output disclosing configuration and credentials; an unauthenticated shell; a bootloader prompt reachable by interrupting boot; the console accepting input at all. Depth — Manual Physical probing and signal analysis; nothing about this is reachable without the board.
Objective — Determine whether the processor's debug interface remains enabled, giving direct control of execution and memory. How it is tested — Identify the debug pads from the board layout and component datasheets, and probe to confirm which are active, since production boards frequently retain the pads while removing the connector. Attempt to attach a debugger and establish whether the interface responds, whether debug authentication is required, and whether readout protection has been set at manufacture. Where the interface is live, establish what it grants: memory read, memory write, halting and single-stepping execution, and extraction of the firmware in full.
Prerequisites — An opened device; a debug probe and adapters; datasheets identifying the debug pins; authorisation for irreversible work. 3. Software Implementation, Frameworks & Protocols Indicators — The debug interface responding; no debug authentication; readout protection unset; memory readable or writable; execution haltable.
Objective — Determine whether the external flash holding firmware and configuration can be read or written directly on the bus. How it is tested — Identify the flash component and its bus, and attach a programmer either in place or after removing the component. Read the contents and establish whether they are encrypted. Attempt to write modified contents and establish whether the device validates them at boot. Capture bus traffic during boot, which reveals what is read and in what order.
Prerequisites — An opened device; a programmer and clip or rework tools; a logic analyser for bus capture; authorisation to remove components. Indicators — Flash contents readable in place; contents unencrypted; modified contents accepted at boot; secrets visible on the bus during boot.
Objective — Determine what the device's external ports expose beyond their documented purpose. How it is tested — Enumerate the interfaces the device presents on each external port, including any that appear only in recovery or during boot. Establish whether a console, storage, network or debug interface is presented in addition to the documented function. Where the device acts as a host, test how it handles unexpected devices and malformed descriptors.
Establish whether firmware can be loaded through the port. Prerequisites — A device with external ports; a computer able to enumerate and emulate devices; the ability to observe the device during boot and recovery. Indicators — A console or storage interface presented on an external port; a debug interface appearing in recovery; firmware loadable through the port; the device mishandling malformed descriptors.
Depth — Hybrid Enumeration automates; the recovery-state and host-mode behaviours have to be provoked deliberately. Objective — Determine whether peripheral buses expose components holding secrets or controlling security-relevant behaviour. How it is tested — Identify the bus lines on the board and enumerate the components responding on each. Establish what each holds — configuration memory, a secure element, sensors, power control — and whether it can be read or written directly. Capture bus traffic during boot and operation to establish whether secrets cross it unprotected, and whether responses from a component can be substituted.
Prerequisites — An opened device; probes and a bus adapter; a logic analyser; datasheets for the components found. Indicators — Configuration memory readable or writable on the bus; keys crossing the bus unprotected; a component's responses substitutable; security decisions depending on an unauthenticated bus device. A device that may be opened and, if necessary, destroyed; probes, a logic analyser and adapters for each interface; component datasheets and board photographs; and written authorisation, since this work leaves visible traces.
Every identifier below is quoted from the published control list it belongs to. Where a test has no defensible mapping, none is given rather than an approximate one. The proliferation of Internet of Things (IoT) devices has created a vast new attack surface, making hardware security a critical frontier in cybersecurity. Establishing a dedicated home lab is the first step toward understanding and mitigating the unique vulnerabilities present in embedded systems, from smart home gadgets to industrial control systems.
A robust lab starts with the right physical tools. The core items include a JTAGulator for identifying debug interfaces, a Bus Pirate for universal serial communication, a logic analyzer like the Salae for signal inspection, and a variety of oscilloscopes and multimeters. This process is crucial for accessing console interfaces on devices. After connecting a USB-to-Serial adapter (e.g., FTDI chip), use `dmesg` to identify the assigned TTY device (e.g., ttyUSB0 ). The `screen` command then opens a serial connection at a specific baud rate (common rates are 9600, 115200). If the correct rate is used, you will gain interactive access to the device’s command shell.
The first step in analyzing a device is obtaining its firmware, which can often be done through software means before resorting to hardware methods. `Binwalk` is a vital tool for firmware analysis. The `-e` flag automatically extracts known file systems embedded within the binary, and `-M` performs a recursive extraction to get all layers. Once extracted, the `strings` command pipes all human-readable text from the binary into `grep` to search for hardcoded credentials, API keys, or other sensitive information, which are common critical vulnerabilities.
JTAG (Joint Test Action Group) is a standard interface for debugging embedded systems. Unsecured JTAG ports can provide full control over a device. OpenOCD is a driver for interacting with JTAG interfaces. The command `-f` specifies configuration files for your specific hardware adapter (e.g., an FTDI cable) and the target chip. This opens a debugging server. UrJTAG’s `detect` command attempts to identify the Instruction Register (IR) length of the target chip, which is a key step in establishing a working connection for reading and writing memory.
Many devices store firmware on SPI (Serial Peripheral Interface) flash chips. Dumping this memory is a primary hardware exploitation technique. This command uses flashrom , a universal flash programming utility, with the Bus Pirate ( -p buspirate_spi ) specified as the programmer. The `-r` flag reads the contents of the connected SPI flash chip and writes it to firmware_dump.bin . Always generate a SHA256 hash of the dumped file to verify its integrity for later analysis and to compare against multiple reads.
UART (Universal Asynchronous Receiver-Transmitter) is a common serial console interface on PCBs that can provide a root shell. Finding the correct baud rate is essential. Tools like `baudrate.py` automate this by monitoring the receive pin and testing common rates. Once the baud rate is identified (e.g., 115200), a terminal program like `minicom` is used to connect. The `-D` flag specifies the device, and `-b` sets the baud rate. If the serial interface is unprotected, this often grants immediate administrative access.
IoT devices often communicate wirelessly. SDR tools like the RTL-SDR and HackRF allow you to capture and analyze radio frequencies. The `hackrf_transfer` command is used to capture raw RF signals. `-r` specifies the output file, `-f` sets the center frequency to listen on (e.g., 433.9 MHz), `-s` is the sample rate, and -g / -l control gain settings. The resulting `.raw` file can be imported into Audacity as “Raw IQ Data” to visualize the modulation and decode the signal manually, which is key for replay attacks.
As mentioned in the source post, Proxmox provides a scalable platform for hosting vulnerable IoT images, analysis VMs, and tool suites. This set of commands prepares a Debian host for a Proxmox VE installation. It adds the official Proxmox repository GPG key for authentication, adds the package repository to the system’s sources list, and then updates the package list and performs a full system upgrade. After a reboot, the Proxmox VE kernel is loaded, and the web management interface becomes available for building and managing virtual machines and containers.
Analysis: The post from Debanjan Saha highlights a growing trend where accessibility to hardware hacking tools and knowledge is democratizing a field once reserved for highly funded labs. The planned integration of Proxmox for virtualization and fault injection tools for advanced attacks shows a clear and effective path for skill development. This move from simple interface interaction to sophisticated fault and side-channel analysis is exactly how serious researchers build deep, practical expertise that is directly applicable to real-world IoT security assessments.
The increasing complexity and connectivity of consumer and industrial IoT devices will outpace manufacturers’ security practices. Within the next 3-5 years, we will see a significant rise in automated worms specifically targeting hardware-level vulnerabilities in IoT device families, moving beyond simple weak credential attacks. This will make the skills developed in labs like this one critical for both offensive red teams and defensive blue teams tasked with protecting critical infrastructure.
Reported By: Debanjansaha360 Iot – Hackers Feeds Extra Hub: Undercode MoN Basic Verification: Pass I We do not sell your personal data. If you wish to exercise your rights under applicable privacy laws, please visit our Do Not Sell My Personal Information page. Google Tensor SoCs, found in Pixel devices, represent a significant leap in mobile processing, integrating custom silicon designed for AI and advanced security. While software-based analysis provides valuable insights, truly understanding and auditing the low-level security posture of these complex systems necessitates direct hardware access. JTAG (Joint Test Action Group) and UART (Universal Asynchronous Receiver-Transmitter) interfaces are indispensable tools for security researchers aiming to delve into the boot process, firmware execution, and TrustZone environments that protect critical data on Tensor chips. This guide outlines the intricate steps required to set up a hardware debugging environment for Tensor SoCs, focusing on the practical aspects of pinout identification, soldering, and software configuration.
The first critical step involves gaining physical access to the SoC and identifying the elusive debug pads. Carefully disassemble your Pixel device. This typically involves applying heat to loosen adhesive (e.g., around the screen), then using prying tools to separate components. Once the mainboard is exposed, visually inspect areas around the Tensor SoC, memory modules, and power management ICs for groups of unmarked test pads. These are often small, circular or square gold-plated pads.
Google does not publicly release schematics for its Tensor SoCs, making pinout identification a reverse engineering challenge. Successfully connecting to these tiny pads requires precision. Clean the target pads thoroughly with isopropyl alcohol. Apply a small amount of flux. Use fine-gauge Kynar wire (AWG 30 is common) and pre-tin the ends. Solder one end of each wire to its respective debug pad with minimal heat and solder, ensuring no bridges. Route the wires carefully to avoid stress points.
Once the wires are soldered to the device, connect them to your JTAG/SWD and UART adapters. Ensure proper voltage levels; most modern SoCs operate at 1.8V. The JTAG adapter should typically sense the target voltage. Here’s a general wiring concept: OpenOCD acts as the bridge between your JTAG adapter and GDB. Tensor SoCs, being custom ARMv8.2-A designs, will require a carefully crafted OpenOCD configuration. Start with a generic ARM Cortex-A configuration and adapt it. You’ll need to identify the Debug Access Port (DAP) and specific CoreSight components. The example below is a starting point and likely needs significant customization based on your findings: To monitor boot logs and potentially interact with the bootloader, connect your UART adapter. Assuming your adapter is /dev/ttyUSB0 and the baud rate is 115200: The UART output is invaluable for understanding the boot sequence, identifying different boot stages, and observing any error messages. With JTAG, you can pause execution at critical points (e.g., before secure boot validation), dump memory regions, and even modify registers or inject code to bypass checks or gain more control. This is crucial for discovering vulnerabilities in the initial stages of device bring-up.
4. Practical Deployment, Analysis & Case Studies Google Tensor SoCs heavily leverage ARM TrustZone for their Trusted Execution Environment (TEE), which handles sensitive operations like fingerprint authentication and cryptographic key management. While direct JTAG access into the secure world is often restricted, you can still use JTAG to observe transitions between the normal and secure worlds by monitoring specific ARM core registers (e.g., SCR_EL3). Researchers might attempt to dump TEE OS firmware or analyze memory patterns during secure operations, looking for information leakage or execution flow anomalies. Overcoming TEE protections often involves exploiting vulnerabilities in the normal world that allow elevation to secure world privileges.
One of the primary goals of hardware debugging is to extract firmware components that are not accessible via software means. Using JTAG, you can dump the primary bootloader, secondary bootloaders, TEE OS images, modem firmware, and other proprietary components directly from flash memory or RAM. These extracted binaries can then be loaded into tools like Ghidra or IDA Pro for static analysis, uncovering hidden functionalities, cryptographic routines, or potential attack surfaces.
Debugging Tensor SoCs comes with significant challenges. Google implements robust security features, including debug fuses (which can permanently disable JTAG/SWD after device manufacturing or tampering), secure boot mechanisms, and sophisticated anti-tampering measures. Bypassing these often requires advanced techniques or identifying specific hardware vulnerabilities. Ethical considerations are paramount: research should always be conducted on your own devices, and any discovered vulnerabilities should be responsibly disclosed.
Hardware debugging Google Tensor SoCs provides an unparalleled level of insight into their security architecture, far beyond what purely software-based methods can achieve. While challenging, the ability to directly interact with the silicon, observe low-level boot processes, and extract proprietary firmware is invaluable for advanced security research, vulnerability discovery, and understanding the future of mobile platform security. As Tensor SoCs evolve, so too will the methods required to audit their security, necessitating continuous innovation in hardware reverse engineering techniques and tools.
Are you researching mobile hardware properties, processor SoCs, GPU chipsets, or RAM configurations? Access our complete specs catalog to compare up to 5 devices side-by-side! "Software vulnerabilities live in code. Hardware vulnerabilities live in the physical device — in a header on the PCB that the manufacturer left exposed, in a debug interface that was never disabled, in a bootloader that trusts a UART console before authentication. Before you can attack an IoT device, you have to understand the hardware. Today we open the box." Understand the UART and JTAG debug interfaces found on embedded devices. Learn how to identify them on a PCB without documentation. Understand the firmware extraction workflow from hardware interfaces. Apply the methodology to a development board target.
Prerequisites: Day 700 (Module 10 Gate passed). Days 250, 432. Estimated study time: 4 hours. The physical interfaces are often the fastest path to full control: many consumer IoT devices have an active UART root shell that requires only a UART adapter and a few capacitors to access. UART (Universal Asynchronous Receiver/Transmitter) is a serial communication protocol. On embedded Linux devices, it is almost always connected to the kernel's serial console — meaning it outputs boot logs and provides a root shell when the device boots.
JTAG (Joint Test Action Group) is a hardware debugging standard (IEEE 1149.1) present on almost all modern processors. It provides: JTAG is the most powerful hardware interface for security research — it effectively gives you a hardware debugger equivalent to GDB.
When UART is password-protected and JTAG is not accessible, the firmware can be read directly from the SPI flash chip: Target: Use a spare development board (Raspberry Pi, ESP32 dev board, any OpenWRT router dev board, or a Banana Pi). Do NOT practise on production devices or devices you do not own. ← Previous: Day 700 — Module 10 Competency Check → Next: Day 702 — Firmware Analysis: binwalk, Squashfs, and Backdoor Hunting I spent the day mapping the physical debug interface attack surface on a production Cortex-M4 board. The target had UART, JTAG, and USB DFU exposed on a header. Within 20 minutes of probing with a logic analyzer, I had the bootloader baud rate, found an unlocked JTAG TAP, and dumped the first 64KB of flash over SWD. Today’s deep dive: how to systematically enumerate, assess, and harden every debug port on an embedded device.
Debug ports are the crown jewels of an embedded attack surface. They provide direct, authenticated (or often unauthenticated) access to CPU registers, memory, and peripheral configuration. The threat model is simple: if an attacker can physically connect to a debug interface, they can extract firmware, patch execution flow, or permanently brick the device. The key insight is that debug interfaces are rarely disabled in production firmware . Many teams leave JTAG/SWD enabled “just in case” for field updates, or they rely on obfuscation (e.g., hiding the header under a heatsink) rather than actual access control. A determined attacker with a 10 l o g i c ana l yzer an d a 20 JTAG adapter will find and exploit these ports.
1. “RDP Level 1 means secure” False. RDP Level 1 (read protection) only prevents flash reads over SWD/JTAG. It does not prevent: 2. UART is “just a debug console” UART is often the easiest entry point. Many bootloaders expose a shell with md (memory display), mw (memory write), and reset commands. If you can interrupt autoboot, you can dump the entire flash over XMODEM. Always disable the UART console in production builds.
3. USB composite devices leak interfaces A device that presents as a HID keyboard for input and DFU for firmware update is a single USB descriptor. An attacker can re-enumerate the device and talk to the DFU interface even if the application code never uses it. Always check lsusb -v for unexpected interfaces. UART discovery challenge : Take any dev board with a serial header. Use a logic analyzer (or oscilloscope) to capture the boot sequence. Identify the baud rate by measuring the shortest pulse width (1 bit period). Calculate: baud = 1 / (pulse_width_in_seconds) . Verify with a terminal at that rate.
JTAG lock verification : On an STM32 board, write a firmware that sets RDP Level 1. After programming, attempt to connect with OpenOCD and read flash. Observe the error. Then try to halt the CPU and read R0 — note that this still works. Document the difference between “read protected” and “debug disabled.” USB descriptor audit : Connect any embedded device to your Linux machine. Run lsusb -v and count all interfaces. For each interface, identify the class (HID, CDC, DFU, etc.). If you find a DFU interface, try dfu-util -l to see if upload is allowed. If it is, that’s a vulnerability.
Tomorrow we map the OWASP Embedded/IoT Top 10 to real firmware vulnerabilities. We’ll take each category (Insecure Interfaces, Lack of Secure Update, etc.) and show exactly which CVE patterns and code smells to look for in your codebase. Bring your threat model — we’re going to cross-reference it against the industry standard. Authorization: Written consent, chain-of-custody, data handling plan. Define what’s in-scope (read/modify firmware? boundary-scan only?). Non-destructive first: No mass-erase, no reprogramming unless explicitly allowed. ESD & power safety: Use an ESD mat/wrist strap. Bench PSU with current limit (start ~50–150 mA above idle). CWE mapping: Track against CWE-1191 — Improper Control of Debug Interface for severity rationale.
Pins: TCK, TMS, TDI, TDO, (nTRST), (nSRST), GND , Vref (target I/O voltage reference). Flavors: IEEE-1149.1 boundary-scan vs CPU debug (ARM DAP/JTAG, RISC-V Debug, MIPS EJTAG). SWD is a 2-wire ARM alt; many boards expose either JTAG or SWD (sometimes both). Goal: Determine if debug is (a) present, (b) reachable, (c) authenticated/locked, and (d) abusable for halt/run control, memory readout, or code exec .
Interfaces: FT2232H-based (Tigard/GreatFET/Bus Blaster/Shikra), J-Link, Black Magic Probe, ST-Link. Discovery: JTAGulator (or GreatFET apps), continuity multimeter, logic analyzer (Saleae-class), microscope. Support: Level shifter (1.2–5 V), pogo/Tag-Connect leads, fine wire + flux, isopropyl, camera for docs. Software: OpenOCD, urJTAG, pyOCD/Segger tools (vendor), flashrom (sometimes), hex editors, hash tools.
Photograph everything : PCB sides, shields, stickers/labels, test pads. Identify silicon : SoC/MCU markings → grab datasheet/pinout (often hints at JTAG/SWD pins). Map candidates : Look for 4–7 clustered pads, unpopulated headers, “Jx/TPx” silk. Continuity : Trace pads to SoC pins; verify GND . Power domains : With device on , measure likely Vref pad to ground (1.2/1.8/2.5/3.3/5.0 V). Never guess— match your adapter I/O to Vref .
Remove or isolate batteries where possible. Never back-power through I/O: connect GND → Vref → (signals) ; power target from its own supply unless the ROE says otherwise. Current-limit your bench PSU and watch for abnormal draw. Connect JTAGulator (or GreatFET) with GND and Vref set correctly. Run auto-scan for JTAG/SWD; capture any IDCODE hits and the resolved pin mapping.
Use logic analyzer during boot: TCK is a clean clock, TMS toggles often; TDO shows activity only when clocked. Try common header orders (e.g., Tag-Connect, ARM 10/20-pin). With OpenOCD + FT2232H , iterate wiring hypotheses until scan_chain returns valid TAP/IDCODE . Expect a TAP and IDCODE . If nothing: swap TDI/TDO, verify Vref, reduce speed (e.g., 100–500 kHz), check TRST/SRST pull states If success: JTAG grants run-control and memory access → High severity . If denied/locked: Note error/status; proceed to protection evaluation (next step).
3. Boundary-scan only? Use SAMPLE/EXTEST carefully to avoid driving sensitive nets. This still leaks PCB design and strap states; rate as info–medium depending on abuse potential (e.g., toggling bootmode pins). Level 1: memory read blocked but mass erase allowed. Level 2: debug fully disabled (irreversible). Secure JTAG / Challenge-response (NXP SJC, Qualcomm Sec JTAG, TI ICEPick, RISC-V Debug Auth) Critical/High: Unauthenticated halt or full flash read/write in production state. Medium: Boundary-scan controllable I/O with plausible abuse (e.g., boot strap forcing), or partial memory access. Low/Info: IDCODE only, or authenticated debug that’s properly enforced.
Boot-window attach: Script reset halt with tight timing to see if a brief window exists before locks apply. Strap manipulation (EXTEST or clips): Enter factory bootloader modes that unintentionally expose flashing interfaces (e.g., UART/USB DFU). Fault-tolerant attempts: Observe and stop here unless ROE explicitly allows FI/glitching (this moves into destructive/unstable territory).
Photo set: board, headers, wiring, instrument screens. Pin map diagram (pad → signal). Logs: full OpenOCD/urJTAG transcripts, scan_chain, targets, errors. Firmware dumps + cryptographic hashes. BSDL/datasheets used. Timing notes (attach windows, adapter speeds). Device/Rev: Result: (e.g., “Unauthenticated JTAG permits CPU halt + full flash readout.”) Impact: IP/keys extraction, secure boot bypass, runtime tamper, persistent implant. Severity: (map to CWE-1191; justify). Evidence: (IDs, logs, hashes, photos).
Likelihood/Exploitability: (lab vs field—access time, required skills, tool cost). Remediation: (see checklist). Re-test: Attach logs showing closure. Set production fuses / lifecycle to CLOSED; enable authenticated JTAG where possible. Disable or remove pads/headers: depopulate headers, use via-in-pad under BGAs; add tamper-evident barriers. Gate JTAG behind secure boot complete + policy; require cryptographic unlock with per-device keys and rate-limit attempts. Wipe secrets on debug entry (key ladders, session keys); partition secrets off the main CPU if feasible. Manufacturing split: separate DEV/TEST images from PROD; automated post-program fuse-burn + verify step with signed logs. Field service plan: vetted unlock tokens, time-bound & audited; disable after use.
Tie every exploit path to business impact (e.g., “exposes patient data,” “enables firmware cloning,” “permits bypass of immobilizer”). Execs act on impact, not just “JTAG open.” Start with observe-only tests (IDCODE, scan). Always log raw outputs and hash artifacts. If you confirm unauthenticated debug, stop, document, and move to remediation discussion before deeper exploitation unless your ROE explicitly says continue.
5. Performance Evaluation & Extended Technical Observations The Emerging Security Risk of AI-Enabled Endpoints, Wearables, and Personal Devices The cybersecurity model… When Refrigeration Controllers Become Cyber Weapons: Lessons from the Danfoss Incident for OT and Product Security A compromised controller is not just an IT incident when it has the authority to change the physical world. The… Why cybersecurity leaders must move beyond authentication to verifiable integrity, bounded authority, and accountable… The 1BitSquared BitMagic Basic is a Sigrok-compatible, FX2-based digital logic analyzer with eight digital channels, a… Zero-Trust Content Ingestion: Building a Pre-Ingestion Prompt-Injection Defense for RAG and Agentic AI The next major AI security boundary is not only the model. It is the content entering the model's context.
The most important lesson from RatHat isn't simply that malware is using AI. It's that attackers can compose legitimate… When the Trusted Hardware Becomes Inspectable: What the PS2 MechaCon Breakthrough Teaches Embedded Product Security A… The biggest AI coding risk isn't that AI will write bad code. It's that humans will stop questioning code because AI… The biggest AI security risk may not be a hacked model. It may be a model with permission to make decisions.
Windows Sticky Keys Exploitation: A Critical Security Vulnerability in Windows Authentication Mechanisms Pico Hacking (Part 18 - "FOR 800 YEARS HAVE I TRAINED JEDI!", The FORCE That IS Input...) Hardware Security Assessment and Hardware Penetration Testing: Perform teardowns, fault injection/EMFI, side-channel analysis, and secure element evaluation. Cybersecurity impact: expose hardware Trojans, tamper paths, and key extraction risks, then recommend countermeasures and production tests to prevent exploitation.
The materials within this course focus on the NICE Framework Task, Knowledge, and Skill statements identified within the indicated NICE Framework component(s): If you would like to provide feedback on this course, please e-mail the NICCS team at NICCS@cisa.dhs.gov . Please keep in mind that NICCS does not own this course or accept payment for course entry. If you have questions related to the details of this course, such as cost, prerequisites, how to register, etc., please contact the course training provider directly. You can find course training provider contact information by following the link that says “Visit course page for more information...” on this page.
In an era where every toaster, camera, and lightbulb is connected to the internet, the “physical” is no longer separate from the “digital.” While most security professionals focus on cloud APIs and web vulnerabilities, the true gatekeepers of the IoT revolution are the printed circuit boards (PCBs) humming quietly in our homes and critical infrastructure. I Hardware hacking is the art of peeling back the silicon seal. By interacting directly with a device’s circuitry, researchers can bypass software-defined security, extract sensitive keys, and understand the logic that keeps our world running. In this guide, we will navigate the essential interfaces—JTAG and UART—and explore the methodology behind firmware extraction.
Whether you are an IoT security researcher or a curious engineer, understanding these physical attack surfaces is non-negotiable in 2026. When we pick up a device, we aren’t just looking at plastic and metal; we are looking at a roadmap. Most embedded devices rely on a System-on-Chip (SoC) architecture, where the CPU, memory, and I/O controllers coexist on a single die.
Recent trends from the CISA Cybersecurity Strategic Plan highlight that “secure by design” must include physical tamper-resistance. Many manufacturers still rely on “security through obscurity,” leaving debug ports exposed, which is essentially leaving a digital front door unlocked. Before you can hack, you must map the terrain. Hardware hackers typically look for specific footprints on a PCB: UART is often the “low-hanging fruit” of hardware security. Many development boards and commercial products leave UART interfaces active in production, providing a root shell without requiring any authentication. I Always match the voltage levels of your adapter to the device. Connecting a 5V adapter to a 3.3V logic line can fry the chip instantly! If UART is a window, JTAG is the master key. Originally designed for manufacturing testing, JTAG allows you to halt the processor, inspect registers, and read or write directly to memory. When a device has “JTAG Locking” disabled, you can effectively dump the entire flash memory, including encrypted firmware components. I If you find that JTAG is locked, don’t give up! Look for “Glitching” attacks (Voltage or Clock glitching) to bypass the fuse-bit check that disables JTAG.
Once you have established a bridge to the hardware, your goal is to extract the firmware binary. This file is the “operating system” of the device, and once extracted, the real research begins—static analysis. Be aware of Anti-Tamper mechanisms . Many modern smart meters and high-security devices utilize mesh circuits or light sensors that trigger a “factory reset” or “data wipe” if the casing is opened. Always inspect the enclosure for micro-switches before prying it open.
Hardware hacking is a relentless game of cat and mouse. As manufacturers harden their devices with better encryption and physical tamper-detection, researchers develop new, creative ways to peer into the silicon. By understanding UART, JTAG, and the fundamental process of firmware extraction, you are not just learning how to break devices; you are learning how to build them better.
The next time you look at a circuit board, don’t just see resistors and capacitors—see a story waiting to be told. Keep exploring, keep probing, and always stay curious. The future of security is being written on the board. Build a reproducible hardware debug and bus-sniffing rig with a documented methodology for firmware extraction and hardware attack-surface assessment.
UART (Universal Asynchronous Receiver-Transmitter) console access is a critical yet often overlooked attack vector in embedded systems. Many production devices leave serial debugging ports enabled, allowing attackers to gain root shells and full system control. This article explores UART exploitation, key commands, and mitigation strategies. Despite advancements in IoT security, UART remains a neglected attack surface. Manufacturers often prioritize cost over security, leaving debug interfaces exposed. Red teams should include UART testing in hardware assessments, while blue teams must enforce physical security and disable unnecessary ports.
As IoT adoption grows, UART-based exploits will rise, leading to more firmware-level attacks. Vendors will eventually adopt secure boot and encrypted firmware, but legacy devices will remain vulnerable for years. Reported By: Sam Bent – Hackers Feeds Extra Hub: Undercode MoN Basic Verification: Pass I We do not sell your personal data. If you wish to exercise your rights under applicable privacy laws, please visit our Do Not Sell My Personal Information page.
Comprehensive guide to hardware security testing covering hardware attack methodologies, car hacking, IoT device exploitation, radio frequency attacks, and DIY hardware toolkit development for security professionals and researchers. Connected devices, embedded controllers, industrial equipment, IoT platforms, and custom hardware introduce security risks that traditional assessments often overlook. Digisecuritas independently assesses hardware and embedded systems to identify weaknesses across device architecture, firmware, communication interfaces, and supporting infrastructure before deployment or production.
Many security programmes focus on applications, networks, and cloud infrastructure. Embedded devices introduce different risks because software and hardware work together. Assess operating systems and embedded software for security weaknesses that could affect device integrity. Review exposed interfaces such as UART, JTAG, SWD, USB, and other accessible debugging or communication ports where applicable.
Review wired and wireless communications for encryption, authentication, and protocol security. Evaluate overall device design, trust boundaries, and security controls supporting long-term resilience. Hardware security decisions often remain invisible until devices reach production or deployment. Digisecuritas provides an independent assessment that complements internal engineering and product development teams by identifying security weaknesses before they affect operations, customers, or regulatory obligations.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/List%20of%20computing%20and%20IT%20abbreviations • https://www.intelliroot.com/services/embedded-security/jtag-uart-testing • https://www.dexterlab.io/theory/security-overview/hardware-security-modules-and-pufs/system-security-architecture/secure- debug-and-jtag-lockdown/ • https://www.appsecatlas.com/docs/specialized/iot-security • https://bluegoatcyber.com/blog/navigating-the-intersection-of-jtag-uart-debug-ports-and-fda-compliance-in-medical-device-c ybersecurity • https://avecas.in/securing-jtag-debug-interfaces/ • https://appsec-labs.com/attack-and-tests/exposed-debugging-interfaces-security-testing-for-embedded-mobile-devices/ • https://undercodetesting.com/building-your-iot-hardware-pentesting-home-lab-a-pro-guide/ • https://androidmobiles.org/hardware-debugging-tensor-socs-jtag-uart-setup-and-advanced-low-level-security-research/ • https://github.com/ducminhgd/learn-security/blob/main/11-GhostLevel/DAY-0701-Hardware-Security-UART-JTAG.md
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Hardware Security Assessment Using Jtag And Uart Interfaces.
[*] Metasploit Scan Running on Target Subnet for Hardware Security Assessment Using Jtag And Uart Interfaces... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |