Complete Technical Paper Content — Honeynet Setup For Enterprise Network Attack Monitoring
Overview & System Context
Honeynet Setup For Enterprise Network Attack Monitoring: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9513 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Organisations implement Integrated Honeynet by connecting multiple decoy systems and services into the production security architecture so activity can be observed and correlated centrally. Segment the honeynet from real assets, instrument it for detailed logging, and alert on any interaction. Use it to detect reconnaissance, lateral movement, and attacker tooling without exposing internal systems.
An integrated honeynet is more than a single trap host. It is a coordinated set of decoys, telemetry, and response hooks that sits inside the wider security environment so interaction with one decoy can inform monitoring, correlation, and escalation across the rest. The point is not just to lure attackers, but to turn their touchpoints into useful detection signals. The practical design choice is to make the honeynet look coherent without letting it become a bridge to real assets. That means the decoys should resemble the production environment closely enough to attract recon and tooling, while the monitoring stack treats any interaction as suspicious and worth correlation. Deception Technology Guide is the natural reference point for honeypots, honeynets, and connected deception architectures.
Because the value comes from visibility, an integrated honeynet should be instrumented as if it were a high-priority sensor, not a forgotten sandbox. The logging should be detailed enough to preserve command traces, network paths, and suspicious follow-on actions, so analysts can tell reconnaissance apart from active exploitation and can see whether a single probe is part of a broader intrusion pattern.
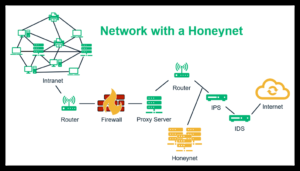
Figure 1: What Is a Honeypot in Network Security? Definition, Types & Uses ... The first implementation principle is segmentation. A honeynet should be isolated from genuine workloads, accounts, and data so an attacker who gains access to a decoy cannot pivot into the production estate. In practice, that means network separation, tightly controlled routing, restricted outbound paths, and explicit monitoring of any attempted cross-boundary movement.
The second principle is believable integration. The decoys should fit the same naming, service, and protocol patterns that defenders expect to see in the environment, but they should not contain real business data or reusable credentials. If the deception is too shallow, it will be ignored; if it is too connected, it becomes a liability. NIST Cybersecurity Framework 2.0 is a useful organizing lens for placing the honeynet inside the detect and respond functions of a broader programme.
The third principle is correlation. One isolated alert from a decoy is useful, but integrated honeynet design should allow multiple observations to be joined across sensors, logs, and alerting rules. That is what makes the environment valuable for spotting reconnaissance, lateral movement attempts, and repeated tooling behavior rather than one-off noise. A well-run deployment also needs lifecycle discipline. Decoys should be maintained so they continue to look plausible, but their identities, services, and telemetry paths should remain under change control. If a honeynet is left stale, attackers may disregard it, and defenders may lose confidence in the signals it produces.
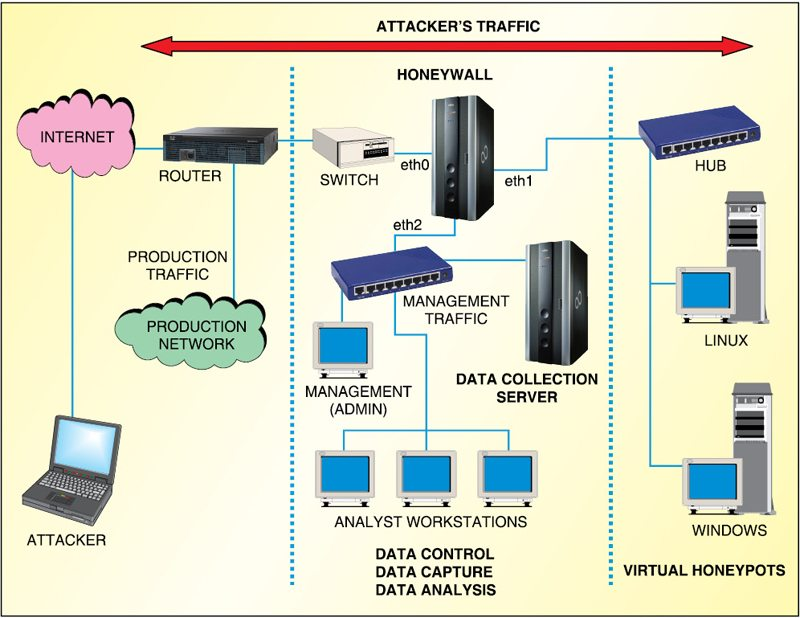
Figure 2: Monitoring and Tracking Hackers’ Activities Using Honeynets Integrated honeynets are strongest when they are treated as an evidence source, not just an alarm source. The central question is not only “did someone touch the decoy?” but also “what did they do next, what did they try to enumerate, and which controls or network paths did they probe?” That makes them especially useful for exposing early-stage adversary behavior that might otherwise look like ordinary scanning.
They are also good at revealing assumptions in the rest of the environment. If a decoy is accessed through a route you did not expect, that may indicate weak internal segmentation, overbroad visibility, or mistaken trust between zones. If an attacker immediately tries to authenticate, reuse tooling, or enumerate services, the honeynet is telling you something about the way your environment appears from the inside.
For more advanced deployments, organisations often pair deception with detective controls that already understand attacker behaviour. MITRE ATT&CK Enterprise Matrix helps teams map what they observe in the honeynet to reconnaissance, credential access, lateral movement, and persistence techniques. That improves triage because the response can be based on observed behaviour, not just on the fact that a decoy was contacted.
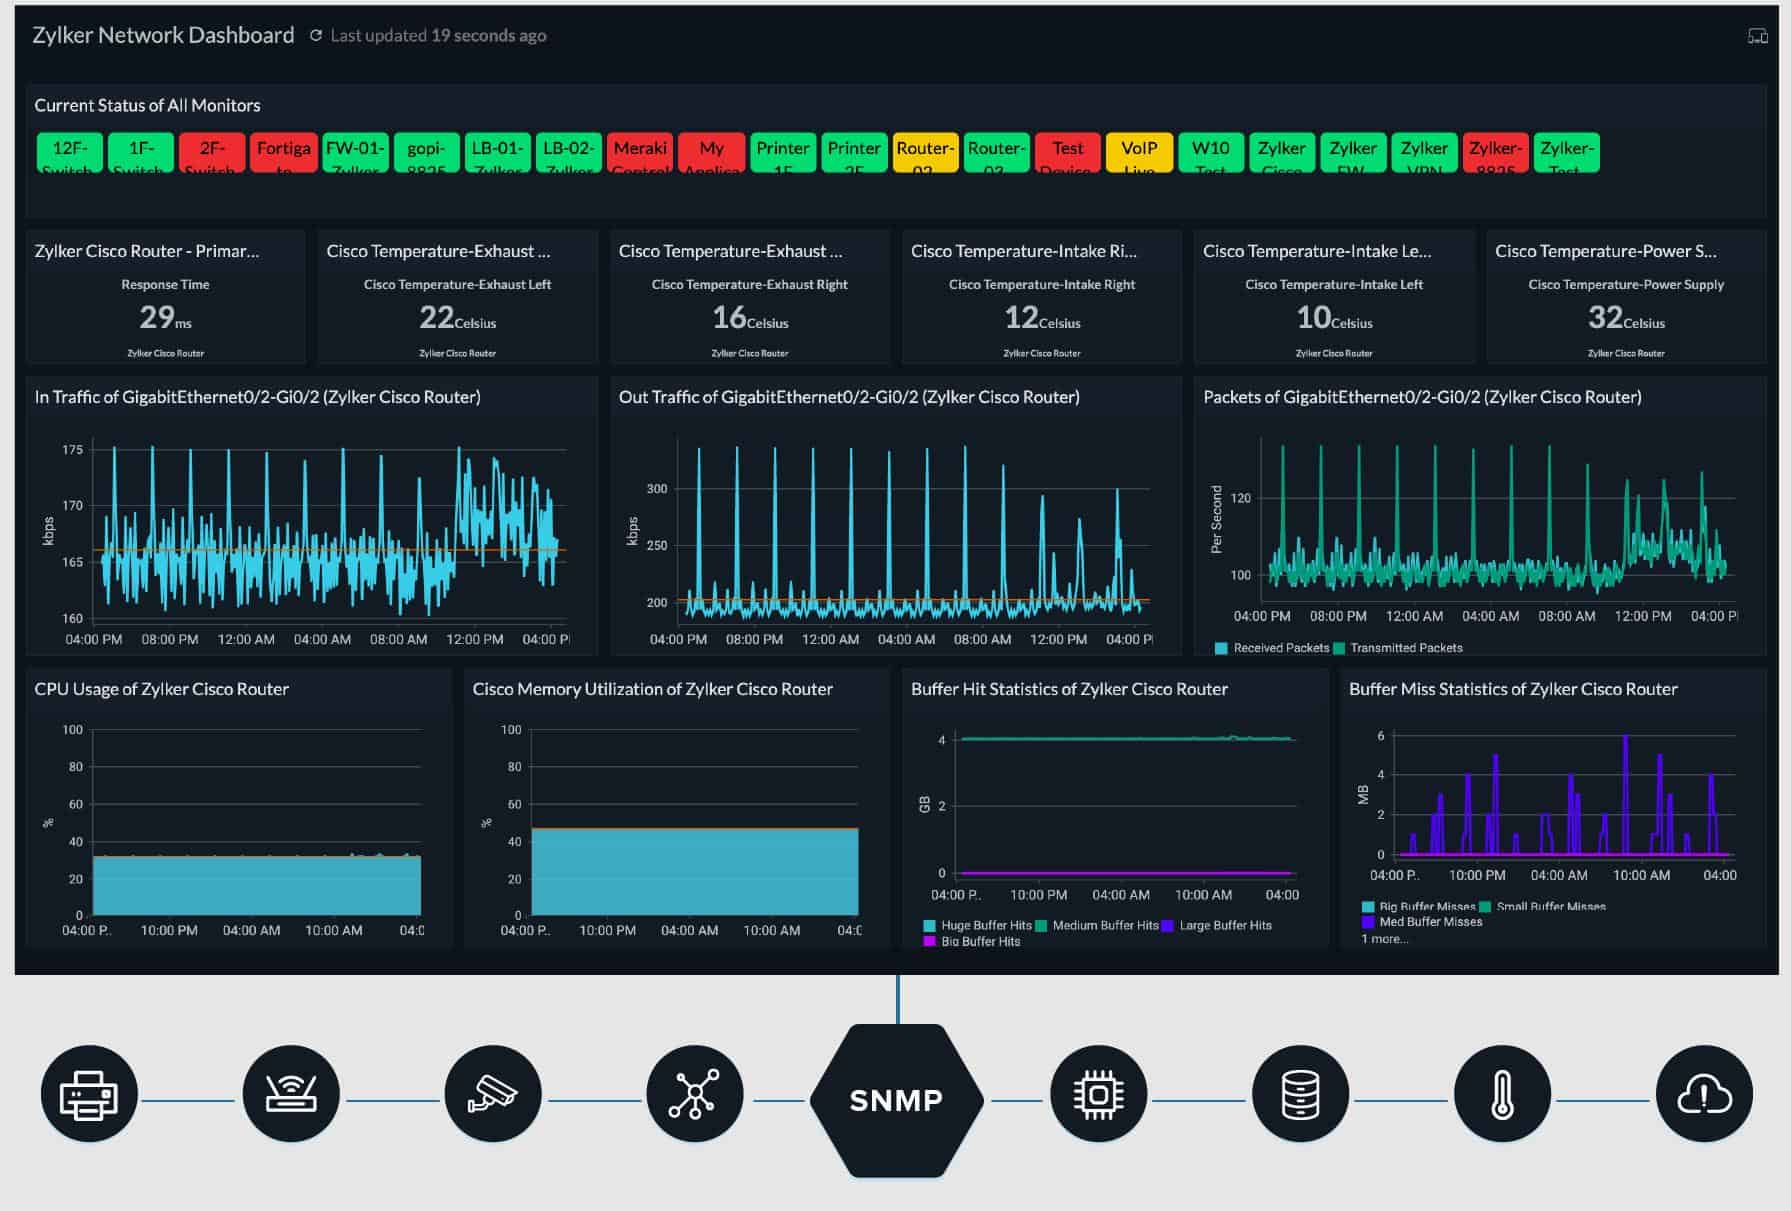
An integrated honeynet creates value only if it stays safely separated from real systems and generates trustworthy telemetry. The main risk is misconfiguration, where a decoy is either too exposed, too trusted, or too weakly monitored to provide reliable detection value. Figure 3: Network Optimization - A Quick Guide & Top Tools for 2025 Failure mechanism: An attacker uses the honeynet to test routes, enumerate services, or stage follow-on activity, and weak segmentation or poor logging fails to contain or explain that behavior.
Impact: The organisation can lose containment confidence, miss early intrusion indicators, or create a false sense of security around assets that are supposed to be non-production traps. This section maps relevant standards and security frameworks to the operational risks and controls described in this guidance.
MITRE ATT&CK addresses the attack and risk surface, while NIST CSF 2.0 sets the governance and control requirements practitioners need to meet. What to verify: Confirm that every decoy has a defined owner, logging path, and alert rule before it goes live. If the team cannot show where honeynet telemetry lands, who reviews it, and how it triggers response, the deployment is not yet operationally useful.
What good looks like: A good integrated honeynet produces high-fidelity alerts with clear context, such as source, sequence, and attempted action, while remaining unreachable from the real estate it is designed to protect. The strongest deployments make analyst triage easier, not noisier. Common mistake: Treating the honeynet as a one-time decoy project instead of a maintained detection capability. The environment must be periodically refreshed so it remains believable and so stale artifacts do not undermine trust in the signals it generates.
Practitioner takeaway: The best integrated honeynets are deliberately boring to the defender and convincing to the attacker, because their real value comes from safe isolation, consistent telemetry, and fast correlation across the rest of the security stack. The latest on NHI and Agentic AI security – articles, research, breaches, news and events every week.
The latest on NHI and Agentic AI security – articles, research, breaches, news and events every week. Developers and cybersecurity professionals often struggle to detect and analyze advanced cyber threats effectively. Traditional security tools may miss sophisticated attacks, leaving networks vulnerable. Understanding how attackers operate inside a network is crucial for improving defenses.
A honeynet is a network of decoy systems designed to attract attackers, allowing you to monitor their activities safely. Developers use honeynets to gather intelligence on attack methods, improve detection capabilities, and strengthen network security. A honeynet is a controlled network environment composed of multiple honeypotsâIIdecoy systems or services designed to appear vulnerable and attractive to attackers. Unlike a single honeypot, a honeynet simulates an entire network segment, enabling the observation of attacker behavior across multiple systems and services. This setup helps security teams analyze attack patterns, malware propagation, and intrusion techniques in a realistic context.
Honeynets are isolated from production networks to prevent actual damage. They collect detailed logs and data about attacker activities, which can be used to improve security measures and develop better detection tools. By deploying a honeynet, developers gain insights into emerging threats and attacker tactics that traditional defenses might miss. Setting up a honeynet involves creating a network of decoy systems that mimic real production environments. Begin by selecting hardware or virtual machines to host honeypots. Next, configure these systems with services and vulnerabilities that attract attackers without exposing your real network.
Isolation is critical; use firewalls and VLANs to separate the honeynet from your operational network. Deploy monitoring tools like Intrusion Detection Systems (IDS) and logging utilities to capture attacker behavior. Finally, ensure you have a secure management interface to analyze collected data without risking exposure. Proper setup requires careful planning to balance realism and security. The honeynet should appear genuine enough to deceive attackers but remain contained to avoid unintended breaches.
Determine the number of honeypots and the types of services to simulate. Decide on physical or virtual deployment and network segmentation strategies. Planning ensures your honeynet mimics realistic environments and maintains isolation from production systems. Create virtual machines using tools like VMware, VirtualBox, or KVM. Install operating systems and configure services that appear vulnerable.
This command creates a virtual machine named honeypot1 connected to the honeynet virtual network, providing a controlled environment for attacker interaction. Set up VLANs or firewall rules to isolate the honeynet from your production network, preventing attackers from reaching sensitive systems.
This iptables rule blocks forwarding traffic from the honeynet interface (eth1) to the production network interface (eth0), maintaining network separation. Deploy IDS like Snort or Suricata on the honeynet to capture and analyze attacker traffic. This command installs Snort, which monitors network traffic for suspicious activity within the honeynet.
Configure honeypots and network devices to log all interactions. Use centralized logging servers for easier analysis. 2. System Architecture & Core Working Principles Starting the rsyslog daemon enables centralized logging, helping collect data from multiple honeypots efficiently. Review logs and IDS alerts to identify attacker methods and update your defenses accordingly.
This command streams Snort alerts in real-time, allowing you to monitor ongoing attacks within the honeynet. Data analysis from a honeynet involves reviewing logs, network traffic captures, and IDS alerts to understand attacker behavior. Start by filtering noise and focusing on suspicious activities such as unauthorized access attempts, malware downloads, or lateral movement.
Use tools like Wireshark to inspect packet captures and log analysis platforms like ELK Stack (Elasticsearch, Logstash, Kibana) to visualize patterns. Correlate events across multiple honeypots to track attacker progression and tactics. Effective analysis helps identify zero-day exploits, malware signatures, and attack infrastructure. This intelligence can inform security policies, patch management, and incident response strategies.
Several tools assist in building and managing honeynets. Honeyd is a popular lightweight honeypot daemon that simulates multiple hosts on a network. The Modern Honey Network (MHN) provides a centralized platform for deploying and managing various honeypots. Other tools include Kippo for SSH honeypots, Dionaea for malware capture, and Snort or Suricata for network intrusion detection. Combining these tools helps create a comprehensive honeynet environment that captures diverse attacker activities.
Choosing the right tools depends on your goals, available resources, and the complexity of the threats you want to study. Honeynets are powerful tools in cybersecurity that help developers and security teams understand attacker behavior by simulating vulnerable network environments. They provide valuable intelligence on attack methods, malware, and intrusion techniques that traditional defenses may miss.
By carefully planning, isolating, and monitoring honeynets, developers can improve threat detection and response capabilities. Implementing best practices and using appropriate tools ensures honeynets remain effective and secure, making them essential for proactive cybersecurity strategies. A honeypot is a single decoy system designed to attract attackers, while a honeynet is a network of multiple honeypots simulating an entire network segment for more comprehensive attack analysis.
Honeynets do not prevent attacks directly but help detect and analyze attacks early, providing intelligence to strengthen overall security measures and prevent future incidents. Honeynets should be isolated from production networks to avoid risks. Proper network segmentation and security controls are necessary to ensure attacker activities do not impact real systems.
Managing a honeynet requires knowledge of networking, virtualization, security tools, and log analysis. Beginners may need training or assistance to deploy and maintain effective honeynets. Honeynets can detect various attacks including malware infections, scanning, brute force attempts, exploitation of vulnerabilities, and lateral movement within a network.
Network infrastructure in a production environment is increasingly targeted by attackers every day. Many resources and services now rely on the internet, making network infrastructure one of the most critical parts to protect, as it hosts numerous company resources and services. Several solutions have already been proposed to prevent attacks, minimize damage, and divert hackers and intruders. Among these, the honeypot stands out as a highly effective tool; it is designed to mimic both a scanner and an attacker, diverting and misleading them within a simulated, production-level environment. This paper will demonstrate the use of a honeynet where a honeypot acts like a real resource to deceive the attacker and analyze their behavior.
Security is a top priority in both social and corporate life. To maintain strong security, it is essential to understand data protection techniques and perform regular security checks [ 1 ] . The world is becoming more challenging in terms of security, making a safe environment a primary focus for individuals and companies. As technology advances, each new day brings fresh security challenges [ 2 ] .
In a production environment, network security is a significant challenge. Protecting the network is one of the most important factors, whether it’s operating over the internet, a LAN, or other methods, and this is true for any size of business. While no system is completely immune to attacks, a strong and effective security system is essential for safeguarding customer data. A good security system helps businesses reduce the risk of data theft and sabotage [ 3 ] . Digitally connected devices and applications are becoming a part of every aspect of our lives—homes, offices, cars, and even our bodies. All of these gadgets are becoming ”smarter” to take advantage of being connected to the internet.
The Internet of Things (IoT) is growing rapidly, which has expanded the attack surface far beyond traditional enterprise IT infrastructures. It is important to understand the security risks of IoT before discussing its features [ 4 ] . This study explains how Honeypots and Honeynets can be used to increase the security of a network’s infrastructure. Honeypots are designed to improve security by detecting unauthorized attempts to access a data system. Modern network security often includes firewalls, intrusion detection systems, and encryption. However, today’s environment requires more proactive methods to identify, redirect, and contain unwanted access. Honeypots offer a proactive approach to these network security concerns [ 5 ] . Honeypots are typically hosted on servers that simulate different environments to appear like a real network. An attacker can enter the honeynet from any machine, which allows the system to monitor the attacker’s behavior and divert threats away from the real network. A honeynet simulates a genuine network more accurately than a single honeypot, making it suitable for large or complex environments where attackers might be drawn to what seems like an authentic and appealing target [ 6 ] .
All network infrastructure resources—including hardware, software, systems, and devices—work together to enable connectivity, control, and communication. This ranges from servers to Wi-Fi routers. This infrastructure also includes the network protocols that allow users and systems to communicate and interact [ 7 ] . This study will propose a secure, hybrid-designed model for network infrastructure security to provide trusted communication and reliable service. The main challenge is to integrate honeypots and honeynets with firewalls and analyze hacker footprints to improve security. We will use two types of honeypots: one will be placed in front of the honeynet’s production router to act as a fake web server, tricking attackers into spending their time there. The other will be placed behind the router, where it can analyze attacker behavior in a controlled environment. The honeynet is set up before the main network infrastructure to ensure security and continuous service in a production environment.
New methods and technologies are needed for network security and forensics. Honeypots are widely used for network security, as these tools can track intruders and monitor hacker activity. Modern communication has connected the world and made the internet accessible to everyone. To maintain security, it is crucial to continuously develop new strategies and upgrade firewalls and intrusion detection systems [ 8 ] . Honeypot security solutions are constantly being improved and used in new ways. Even traditional decoy honeypots have many uses for security engineers and can sometimes help predict security vulnerabilities.
Cloud services and their user bases are growing rapidly. Companies are now more comfortable hosting their servers in the cloud to serve their clients. While internet and app services have made our lives easier, this expansion also increases vulnerability. To protect these services, Honeypot and Honeynet technologies must be improved by closely monitoring and analyzing attacker activity [ 9 ] .
This paper will implement a technique to create a Honeynet and Honeypot. This method is designed to deceive hackers with fake content, diverting them from the real network and potentially protecting it. However, if a hacker carefully examines the material and detects the deception, they might erase their traces before we can collect them and could even plan a larger attack. Poorly maintained or misused honeypots could also increase risks from hackers [ 10 ] .
Understanding hacker attack patterns is essential for network engineers and researchers. Engineers regularly review security reports and logs to measure these patterns, which is a key part of developing and maintaining security. By comparing an attacker’s habits and attack stages, researchers have noticed that attacks on weekdays can have different outcomes than those on weekends. Although some days stand out, attack patterns can vary. By studying these patterns, experts can better understand an attacker’s behavior and adjust the network’s security architecture to defend against it. Hackers can attack from outside the network or by compromising an internal user’s computer. Honeypots and Honeynets help security analysts by recording both external and internal threats and vulnerabilities [ 11 ] .
An employee’s lack of security awareness can make a company vulnerable. Employees with low awareness might accidentally reveal company secrets. Therefore, security awareness training is essential for network security. Many companies are now training their employees on security to help them manage risks and vulnerabilities. This training often focuses on basic communication, technical skills, and how to recognize threats like phishing and ransomware [ 12 ] .
Hackers attack individuals and corporations to steal data, often aiming to steal money or hold data for ransom in exchange for money or cryptocurrencies. Financial firms and organizations that hold public data are major targets, but this does not mean small businesses are immune. Hackers will also attack any network that appears insecure. As a result, security must be a top priority for any organization, regardless of its size.
In security research, a honeypot is a valuable tool for carefully examining hacker activity. It allows security experts to see how an attacker penetrates a system, elevates their privileges, and moves through the network. Security organizations, research institutions, and government agencies are all assessing these threats to find solutions. With a honeypot, an attacker’s actions can be examined in a secure environment, either physical or virtual, preventing a breach of the actual network [ 13 ] .
This section explains our methodology. We will introduce the topic, present the data we collected, analyze it, and then validate our findings to show the project’s reliability. The goal of this project is to implement a solution for real-time threats to network infrastructure. The analysis and project discussion will be illustrated with a diagram to clarify our method and structure. This paper will create a Honeypot within a Honeynet. A honeynet is a network where all devices are decoys but are designed to function like real ones. A honeypot is a single fake server or workstation that imitates a real resource [ 14 ] . Active protection is a relatively new concept in information technology. While some have tried to define this term, many definitions are incomplete or miss key features of this security approach. Some have blended active and offensive security strategies.
This study examines the features of active protection techniques like Honeypots and Honeynets, including their benefits and limitations [ 15 ] . Honeypot systems have been around for over a decade and have improved and adapted over time, thanks to programs like The Honeynet Project and Project Honeypot. Despite their benefits, honeypots are not commonly used in businesses. This may be due to the challenges of installing and managing a honeypot, as well as a lack of understanding of its advantages. Compared to traditional firewalls, honeypots and honeynets offer advanced security features and provide valuable support for security engineers [ 16 ] .
The foundation of network security management is the CIA triad: Confidentiality, Integrity, and Availability. Many network security tools are ineffective without a good strategy and proper administration. To manage a network without interruption and meet user needs, it’s important to handle fault management, configuration, and performance analysis of the security infrastructure [ 17 ] .
Confidentiality protects sensitive data from unauthorized users and attackers. Access to this data should be limited to authorized individuals. Integrity ensures that data is not altered by unauthorized people, maintaining its accuracy for providers. Availability ensures that authorized users can access the data when they need it. Any interruption that prevents users from accessing the service is considered a security violation. The service must be secure and consistently accessible to the right users [ 18 ] .
Security methods can be categorized based on the component level: hardware, software, and cloud. Hardware is the physical part of a network or connected device. It is necessary to safeguard hardware from physical and digital attacks, as a network attack can damage hardware by overusing its resources and shortening its lifespan. Software is the graphical interface that provides services. A direct software infection can damage the hardware or the entire network, so software security must always be kept up-to-date. Cloud services are hosted on the internet and can be used from anywhere. It’s crucial to protect this blended hardware and software environment in data centers using the CIA approach [ 19 ] .
Network security engineers are always focused on preventive measures to protect their network. Security surveillance is needed to prevent network breakdowns, unauthorized access, and malicious users. Securing a commercial network often requires expensive hardware and software. A security framework for a network is typically based on its core design [ 20 ] . 3. Software Implementation, Frameworks & Protocols Since this project uses open-source components, its security approach was designed to be adaptable to any network topology. Engineers choose hardware based on their network design. This article discusses our specific network design and compares it to standard and hybrid security models.
We will use the GNS3 open-source simulator to build a decoy network topology where some devices will behave like real ones. We will configure network protocols and connect them to the internet with a real routing engine to make the simulation more realistic. This network will be placed next to the main production network’s border router. A Windows-based Honeypot server will be configured behind the Honeynet router to analyze attacker activities and store logs. This honeypot will have defense and traceback systems to capture attacker footprints, trace them back to their source, and analyze them.
Tracing the attacker’s IP will help reveal their location, hop count, and route path. The connection state of each hop will be presented in milliseconds (ms) for measurement. We will also check the source IP’s domain information for identification [ 21 ] . An attacker will first try to find and enter the production network. To counter this, another honeypot will be set up in front of the Honeynet network router to deceive the attacker. It will present a fake message to make it seem like a legitimate web server.
The goal is to make the attacker think they are in a real service environment, which will distract them on the fake web server. This decoy device is placed before the Honeynet router to entice hackers. However, if poorly designed, attracting hackers into a fake network can be dangerous. A comprehensive Honeynet is therefore designed to prevent hackers from gaining access to more devices if they become more aggressive [ 10 ] .
Next, an attacker machine will be placed in the network topology to generate random attacks using Kali Linux tools to evaluate the system. The logs will then be analyzed to understand the attacker’s activity. This project offers a design that traps attackers, making it difficult for them to distinguish between real and fake networks. By searching the honeypot for resources, the attacker wastes time and leaves behind valuable footprints and logs, which helps us understand their attack patterns. This can reduce vulnerabilities and protect the real network infrastructure. The second honeypot will capture the attacker’s source to determine their network origin and system details, identifying any other potential vulnerabilities.
Cyber attacks are one of the biggest criminal risks today, and security engineers are constantly taking steps to prevent them. Security breaches often happen due to a lack of awareness or insufficient precautions. Security measures rely on hardware, software, and cloud components to be effective [ 22 ] . Different network security models use different tools. Most models include a firewall or a similar security device. Many security engineers believe a firewall is the most cost-effective solution for network security. A firewall offers services like intrusion detection and prevention, threat analysis, security logs, and more. The main goal of a firewall is to protect a network and provide uninterrupted service [ 23 ] .
However, a firewall alone cannot protect a network with critical services. Attackers today can bypass firewalls using methods like SQL injection, social engineering, application vulnerabilities, and exploiting IoT devices or employee ignorance. Once a firewall is breached, hackers can quickly infiltrate networks and access resources [ 24 ] . In addition to a firewall, other security control methods are needed. While a firewall is a crucial component, this traditional approach is well-known to everyone, including hackers.
The network model developed here uses a different security approach. As shown in the diagram, it features a three-layer security system: a decoy device that misleads the attacker, a fake network that manipulates them, and another decoy device that analyzes and tracks them. These three layers are placed before the firewall that protects the production network. This unique approach provides security engineers with extra reports on hackers trying to target network devices, giving them time to study logs, analyze threats, and prepare for an attack.
In this paper, the goal is to develop a secure network topology with two different Honeypots, each serving a different purpose. We used the GNS3 simulator for our lab to visualize the project in a virtual environment [ 25 ] . The Graphical Network Simulator-3 (GNS3) is a free, open-source network simulation platform. It provides a graphical interface where complex network labs can be created by importing various network equipment like routers, switches, firewalls, and servers. It works by emulating the images of the devices that do the actual job. Using this emulator, anyone can design a high-quality, complex network topology, including simulations of Ethernet, frame relay, and ATM switches. Virtual machines from VMWare or VirtualBox can be imported using the GNS3 VM. GNS3 has a built-in feature for packet capture using Wireshark. The main drawback of GNS3 is that while the platform itself doesn’t use many base machine CPU resources, the lab machines (routers, switches, firewalls) installed in GNS3 do consume CPU and RAM according to their allocated memory [ 26 ] .
Our lab was built with seven components, including a cloud, a distribution switch, and another switch from the GNS3 simulator. We also used a Cisco IOS router, a Pentbox Honeypot, a KFSensor Honeypot, and a Firewall in our topology. The Pentbox and KFSensor honeypots were run in VMWare, and the virtual machines were imported into the GNS3 environment as VMWare templates.
The entire lab was run in the GNS VM, with both GNS3 and GNS VM at version 2.2.5. The GNS VM was allocated 10 GB of RAM and 2 dual-core processors. Using the GNS VM is better than the standalone GNS3, especially when running Cisco IOS or Unix devices. Once installed, the GNS VM is simple to use as a plug-and-play OS. It can also be accessed remotely as a cloud by setting up internet connectivity [ 27 ] .
We ran two of our honeypots in VMWare and imported them as templates into the GNS3 VM environment. One honeypot was installed on Ubuntu, and the other on a Windows operating system. The Ubuntu-based Pentbox honeypot was used to mimic an attacker’s target. We lured the attacker with a fake banner on a web server using this honeypot, causing them to leave behind a footprint. This data is useful for forensic analysis of the attacker. Pentbox is a penetration testing tool with several features for penetration testing, network analysis, and monitoring [ 28 ] .
The Pentbox was set up as a web server with a fake message, and port 8080 was opened to fool the attacker. This honeypot serves as the first decoy in front of the network. This open-source program can be cloned from GitHub for learning purposes [ 29 ] . This honeypot is a good network decoy that can gather an attacker’s footprints before they can assault the main network.
The router connects and distributes the internet to all connected devices, routing IP packets between them. It translates network addresses and sends local network traffic to the wide area network and vice versa. Routers also have security features like access control lists, port filtering, and IP filtering. Although routers do not provide deep inspection services like firewalls, some can offer content filtering and bandwidth control [ 30 ] .
Our routing device handled LAN-to-WAN routing and acted as the network’s border gateway. Border routers manage Border Gateway Protocol (BGP) and internet traffic. With our CISCO IOS 7200 border router, we can filter traffic from specific sources and destinations. We can also set port restrictions for security. The border router can filter IP addresses, access control lists, and ports to prevent network attacks, allowing us to block any suspicious or vulnerable addresses. We used the CISCO 7200 border router because it provides these features and serves as a reliable routing system with security surveillance capabilities [ 31 , 32 ] .
KFSensor is an intrusion detection system for Windows that can be used as a honeypot in a network security model. It is known as an active intrusion detection tool and can identify attackers moving on a network and store logs to analyze their motives. KFSensor provides an interface where anyone can view a real-time threat report with detailed information [ 32 ] . In this research, we used KFSensor as a honeypot to analyze attacker behavior and attack patterns. KFSensor provides information about the attacker’s source, protocol, traffic, packet type, and more [ 33 ] . I generated threats from a testing computer and observed the results on its real-time threat interface. This interface showed TCP, UDP, and ICMP threats from other machines. TCP and UDP packets came from the testing attacker’s workstation, while ICMP packets came from the router. We found broadcast UDP packets and a ’sync scan’ TCP, which is caused by a Distributed Denial of Service (DDoS) attack from another machine on the network.
In this lab, we generated a DDoS attack from an attacker workstation to analyze the data collected by KFSensor. We used Slowloris in Kali Linux for the DDoS attack. Slowloris is an open-source tool available on GitHub that generates many HTTP session requests to a target location for an HTTP DDoS attack. The targeted system becomes unable to respond to other users due to the excessive HTTP requests, causing service interruptions [ yevsieieva2017analysis ] . Slowloris generated a DDoS attack by sending keep-alive header packets.
We sent a DDoS attack to the honeypot to test how we could collect data for analyzing the attacker’s patterns. This DDoS attack drains service resources such as bandwidth, CPU, and memory, causing service interruptions [ 34 ] . The Slowloris tool sent a large number of HTTP requests to our honeypot to verify that it captures the attacker’s data in real time. We measured the attack’s start and end times in the event description. The figure shows that the attack was a form of sniffing, which we measured. After reviewing multiple reports on the time frame and action type, we can determine the attacker’s timing and patterns, including when they choose to launch a new attack.
When more information about the attacker is needed, we can use the KFSensor Nmap feature to trace them. We tracked the path from the attacker’s IP information using Nmap and scanned it to get information about the operating system, system version, connectivity status, and packet travel time through a trace report [ 33 ] . With all this information, we measured the distance between our system and the attacker’s system and gathered details about the materials used to generate the attack.
Knowing the operating system and version helps us understand how dangerous the next attack could be. To find the attacker’s location on a global map, we used the Nmap topology to get the targeted IP address. The Nmap tool built into KFSensor can locate the vulnerable IP address by following the trace route step-by-step and provides graphical feedback about the attacker’s hop location [ 33 ] . At this point, it is clear that we have successfully back-traced the attacker using the KFSensor Honeypot. We used KFSensor Nmap to scan and capture information about the attacker’s system. With Nmap in KFSensor, we scanned every active IP address, performed a full network scan, identified network vulnerabilities, and developed a visual map of the attacker’s location, open ports, and other key information [ 33 ] .
The designed network security diagram set a benchmark, and we tested its performance. The goal was to reduce network vulnerability and challenge attackers by analyzing and observing the collected reports. Our first approach was to create a fake environment to trap the attacker. The first honeypot we set up was designed to mimic a fake web server on port 8080 to trick the intruder. The server would display a fake message upon entry.
The second honeypot was designed to attract the intruder to get their footprints and analyze scan reports. This device provides a brief report that allows us to identify and observe the intruder’s attitude and attack patterns. The performance was analyzed in a real-time attack scenario. We connected all devices to the internet to make them reachable globally and observed how attackers were more likely to find and attack our devices.
The result was that the first honeypot received the highest number of vulnerability scanning reports. This is because this honeypot is at the front of the network, and its information can be easily found by scanning the network surface. We analyzed this report using the built-in Wireshark on the Ubuntu operating system of that honeypot. Wireshark is a network vulnerability analysis tool available on most popular operating systems, and it can capture packets and traffic patterns going in and out of a specific machine.
We observed that Honeypot 2, which was used for analyzing intruders, received fewer hits from footprints and vulnerability scans from the internet. This was due to the Honeynet router, which has its own defense system against flooding and Denial of Service attacks to keep the routing engine running smoothly. Even though we did not set up any access control lists or port filtering, the router has a built-in protection system to prevent attacks from taking down its core operations.
While connected to the global internet, we discovered another major attack on our devices: a Distributed Denial of Service (DDoS) attack. Similar to the footprinting events, we found that Honeynet-1 received most of the attack events, while the Honeynet and the Firewall received the fewest. This attack caused higher bandwidth consumption and CPU usage on each device. The firewall has its own mechanism to protect against DoS attacks. In general, DDoS attacks are carried out by botnets that send a huge amount of traffic or service requests to the target, causing service interruptions by overwhelming the system’s processes.
By observing the scan and footprint data, it is clear that the first honeypot attracted the most attention from attackers, while the second honeypot received less, as it was inside the Honeynet. The Firewall attracted the least attention because attackers had already found access to two other devices before reaching it. The DDoS attack results were similar, suggesting that attackers performed some footprinting on the network before launching the attack. Generally, attackers gather information before an attack, searching for opportunities and weak points. This is the first phase of hacking any system.
It is likely that attackers spent more time on the honeypots, which is why they invested less time on the firewall. This gave security engineers enough time to analyze the risk by studying the data from the honeypots. The next step would be to apply filters or create limitations on the firewall. Keeping an eye on the attacker’s source and the ports they attack can also help security engineers prepare.
The goal of this work was to mislead attackers with a decoy and analyze their behavior before an attack. The results demonstrated the project’s success, as most of the major attacks were directed at the honeypots, and hackers remained on the Honeynet for a long time instead of the real infrastructure. Additionally, we received a detailed report on their attack methods, which helped us decide on the next stage of security. The hybrid security model showed that these decoys gave security engineers enough time to prepare before any security breach or service interruption. By tracing these reports, any security engineer can easily determine the next steps for improving defense. Tracing the attacker’s steps is highly recommended for protecting a network before experiencing a cyber attack.
Honeypots and Honeynets are among the most powerful tools for security research, and this study describes some aspects of a security project using them. However, the author intends to continue researching network security and a hybrid network architecture model to improve network infrastructure and security. Further study on this paper may include the following topics. The honeypots should be enhanced to resemble a real server with several services running in different VMs. The Honeynet will use a clustered, load-balanced network design with multiple routers for different internet service providers, merging internet traffic effectively. We will move beyond DDoS attacks to integrate intrusion protection into the honeypot along with an intrusion detection system. The Honeynet infrastructure will be automated to integrate with the main network infrastructure. This study discusses Honeynet and Honeypot solutions with practical examples. The author plans to add more sophisticated network scenarios and honeypot servers in future work.
Network security plays a vital role in protecting confidential data and important services from theft and can save any company from cyber robbery. By focusing on this subject, this paper provided a practical concept with a real-life attack scenario on network security. The solution showed how a honeypot can be a strong security tool by providing different services. When we need to misguide a hacker or collect their footprints from a safe system, a honeypot is undoubtedly one of the best solutions.
The Honeynet was presented as one of the most effective tools to protect a network, supplementing firewall security by using honeypot devices. Overall, this project discussed the importance of network security with a technique for implementing Honeypot and Honeynet services in a production network. This project implements a Security Operations Center (SOC) and a Honeynet in Microsoft Azure to monitor, detect, and analyze cybersecurity threats.
4. Practical Deployment, Analysis & Case Studies Implementation of a SOC and Honeynet in Azure for cybersecurity monitoring and analysis A honeynet is a network of intentionally vulnerable or instrumented systems deployed to attract, observe, and analyze malicious activity. In short, itâIIs a decoy network that looks real enough to lure attackers while recording their behavior for study.
Direct definition (concise): A honeynet is a collection of decoy hosts, services, and network infrastructure designed to appear operational but are isolated and monitored so defenders can capture attacker tactics, techniques, and procedures (TTPs). âI¢ In practice, a honeynet may include fake servers, workstations, routers, and simulated services that mimic production assets. âI¢ It often integrates logging, packet capture, and sandboxing to record attacker actions without exposing real systems. âI¢ In 2025, honeynets may span on-premises, cloud, and container platforms to reflect modern infrastructure.
According to top sources and common definitions, honeynets are typically built with the express purpose of intelligence gathering and vulnerability discovery rather than production use. They generally: âI¢ Emulate services (web, SSH, RDP) to entice attackers âI¢ Capture network traffic and forensic artifacts âI¢ Isolate attacker activity to prevent lateral movement into real assets âI¢ Support research, incident response, and threat-hunting efforts âI¢ Intentionally vulnerable or attractive to attackers âI¢ Highly instrumented for monitoring and capture âI¢ Isolated using network segmentation, virtualization, or air-gapping âI¢ Used for intelligence, not for serving real business functions âI¢ For defenders, a honeynet provides a safe environment to observe attacker behavior and test detection controls. âI¢ For researchers, it offers live telemetry about emerging exploits and malware trends. âI¢ For organizations, honeynets may support compliance, red-team testing, and threat-hunting programs.
In my experience, a well-designed honeynet yields richer contextual data than passive external logs, and in 2025 it often complements deception tooling and telemetry-driven detection strategies. Honeynets deliver several practical, measurable benefits when deployed properly. They are especially valuable for organizations seeking deeper visibility into active threats and validation of detection capabilities.
âI¢ Improved detection fidelity: Honeynets often reveal attacker behaviors that evade conventional sensors, helping refine alerts and reduce false positives. âI¢ Faster threat intelligence: By capturing real attack artifacts, defenders can more rapidly identify new malware samples and TTPs for sharing and mitigation.
âI¢ Validation of controls: Observing attacker attempts against the honeynet allows teams to test incident response playbooks and tune prevention mechanisms. Research indicates that threat intelligence derived from active traps complements passive logs; top sources highlight honeynets as a practical method for obtaining contextual telemetry. In 2025, trends show increased interest in deception technologies alongside centralized telemetry platforms.
âI¢ Security operations centers (SOCs): Use honeynets to enrich alerts and build use cases for SIEM/XDR tools. âI¢ Threat intelligence teams: Harvest indicators of compromise (IOCs) and behavior profiles to inform defensive feeds. âI¢ Incident response teams: Practice containment and remediation in a controlled setting by replaying attack scenarios. âI¢ Small-to-medium enterprises (SMEs): Lightweight honeynets or cloud-based decoys may offer risk-adjusted intelligence without heavy investment.
Based on practical use, honeynets typically yield richer, higher-fidelity data than simple honeypots because they simulate a network context. However, they require careful design, monitoring, and legal consideration. In my experience, the most valuable outcome is not just raw data but the ability to convert that data into improved detection rules, playbooks, and risk reductions.
Using a honeynet effectively requires planning, isolation, monitoring, and an operational model for analysis. Below is a step-by-step approach to implement one responsibly. âI¢ Clear objectives (threat intelligence, detection validation, research) âI¢ Staff or partners to monitor and analyze data âI¢ Legal review and acceptable-use policies âI¢ Segmented network and monitoring infrastructure Define goals: Decide what you want to learnâIIattack vectors, lateral movement, malware families, or cloud-based threats.
Design the environment: Choose hosts and services to emulate. In 2025, include cloud instances, containers, and service APIs that mirror your exposure. Isolate and instrument: Use virtualization, VLANs, or dedicated cloud accounts to isolate the honeynet. Add packet capture, full-disk logging, and process tracing.
Deploy decoys: Configure decoy systems with believable artifactsâIIuser accounts, sample data, open portsâIIwhile avoiding connection to production credentials. Implement monitoring: Stream logs to a central collector or SIEM/XDR. Use automated analysis to triage captured events. Capture and analyze: Extract artifactsâIIbinaries, logs, command historiesâIIand enrich them with threat-intel feeds for IOC development.
Iterate and tune: Adjust service emulation and monitoring based on observed attacker behavior and false positives. âI¢ Start small: A minimal, well-monitored honeynet is better than a large, poorly controlled one. âI¢ Use deception thoughtfully: Make decoys believable but avoid exposing real credentials or data. âI¢ Automate analysis: Build automated pipelines to extract IOCs and generate detection rules. âI¢ Maintain forensic readiness: Preserve chain-of-custody for captured artifacts if legal action is possible. âI¢ Engage cross-functional teams: Include legal, risk, and network teams early to align on containment and compliance.
âI¢ Use virtualization and container platforms for flexible isolation. âI¢ Integrate network packet capture and centralized logging. âI¢ Consider deception frameworks and open-source honeynet projects for templates and automation. âI¢ For cloud-focused threats: Deploy honeynet instances in separate cloud accounts and instrument cloud logs. âI¢ For IoT threats: Use hardware emulators or virtualized device images to mimic device behavior. âI¢ For malware collection: Sandbox captured binaries in an isolated environment for dynamic analysis.
In my experience, maintaining clear objectives and automated pipelines for analysis turns honeynet telemetry into operational value rather than a noisy data dump. Honeynets are powerful but can be misused. Below are common pitfalls, why they happen, and how to avoid them based on practical experience.
Lack of clear objectives âI¢ Why it happens: Teams deploy honeynets because they seem "cool" without specifying what intelligence they need. âI¢ Consequence: Collected data is unfocused and hard to action. âI¢ Solution: Define specific use cases (e.g., detect lateral movement, collect malware), and design decoys to meet those goals. Poor isolation and escape risk âI¢ Why it happens: Misconfigured segmentation or overly permissive network rules. âI¢ Consequence: An attacker could pivot from the honeynet into production systems. âI¢ Solution: Use strong network isolation, separate cloud accounts, strict egress controls, and monitoring to prevent lateral movement.
Exposing real credentials or sensitive data âI¢ Why it happens: Trying to make decoys convincing by including real artifacts. âI¢ Consequence: Real data compromise and legal/regulatory issues. âI¢ Solution: Use synthetic data and test accounts only; avoid reuse of production credentials. Insufficient monitoring and analysis capacity âI¢ Why it happens: Teams underestimate the workload of triaging captured artifacts. âI¢ Consequence: Signals pile up unexamined, reducing the programâIIs usefulness. âI¢ Solution: Automate triage, prioritize alerts, and ensure analysts have time to review and convert findings into detections.
Overly complex deployments early on âI¢ Why it happens: Trying to replicate an entire production network at once. âI¢ Consequence: Management overhead and misconfigurations. âI¢ Solution: Begin with a focused, small-scale honeynet and expand after demonstrating value. 5. Performance Evaluation & Extended Technical Observations Ignoring legal or policy constraints âI¢ Why it happens: Teams focus on technical setup and neglect legal review. âI¢ Consequence: Liability for entrapment, privacy violations, or data retention issues. âI¢ Solution: Consult legal and compliance teams before deployment; document policies and retention timelines.
âI¢ If you see attacker activity escalating beyond expected patterns, immediately verify isolation controls. âI¢ If the honeynet yields few interactions, adjust the attractivenessâIIopen believable services, publish decoy DNS names, or emulate known misconfigurations. âI¢ If noise overwhelms analysts, implement filters, scoring, and automation to surface high-confidence events.
Based on experience, watch out for "run-and-forget" honeynetsâIIthese become liabilities. Regular review, tuning, and integration with detection engineering are essential to sustain value. Generally, the best-performing programs maintain a small number of high-fidelity decoys and strong automation for analysis. Honeynets remain a practical, high-value tool for defenders in 2025 when deployed with purpose and discipline. Key takeaways: âI¢ A honeynet is a network of decoy systems designed to attract and monitor attackers for intelligence and detection validation.
âI¢ Benefits include improved detection fidelity, actionable threat intelligence, and practical validation of response playbooks. âI¢ Successful implementation requires clear objectives, strong isolation, robust monitoring, and automated analysis pipelines. âI¢ Common mistakesâIIsuch as weak isolation, real-data exposure, and lack of analysis capacityâIIare avoidable with planning and cross-functional alignment.
âI¢ Define a clear objective for your honeynet aligned to your SOC or threat-intel needs. âI¢ Start small with one or two decoy services and instrument them for logging and packet capture. âI¢ Automate artifact extraction and enrichment so analysts can quickly operationalize findings. In my experience, the most actionable return from a honeynet is not raw samples but improved detection rules, validated playbooks, and a deeper understanding of adversary behavior. As threats continue to evolve in 2025, integrating honeynets with telemetry-driven defense and automation can help teams stay ahead. If you want a practical next step, scope a pilot project focused on one high-risk attack vector and measure the improvements to detection and response workflows.
This project documents a fully deployed honeynet built on Microsoft Azure, designed to attract real-world attackers and analyze global malicious activity. I deployed an intentionally vulnerable Windows 10 VM, exposed it to the internet, collected security events using Microsoft Sentinel, enriched the attack data with geolocation metadata, and visualized global threat patterns through an interactive attack map.
Over a 24-hour period, the honeynet generated tens of thousands of failed login attempts, providing a real dataset for SIEM analysis, KQL querying, and threat visualization. A honeynet is a decoy network designed to mimic a real environment. It's a network with intentionally disabled security controls (like firewalls) so attackers are encouraged to interact with it.
To generate real attack traffic, I deployed a Windows 10 Virtual Machine on Azure, placed it inside a dedicated resource group, and configured it as a honeypot: All security logs were forwarded to a Log Analytics Workspace and processed through Microsoft Sentinel. Raw logs do not include geographic information, so I enriched attacker IP addresses using a 55,000-row GeoIP watchlist imported into Sentinel.
To visualize attack patterns, I built a custom Sentinel Workbook using a JSON-based map configuration. The map plotted each failed login attempt geographically, with clustering based on event volume. The honeynet recorded tens of thousands of brute-force attempts worldwide. Below are the top regions by unsuccessful login attempts (Event ID 4625): This project successfully demonstrates the end-to-end deployment of a honeynet, real-world data collection, security event enrichment, SIEM analysis, and threat visualization. It replicates a realistic SOC workflow, involving: The final dataset and attack map provide a clear, visual story of global attack behavior observed in a 24-hour window.
Documentation for a HoneyNet simulation project that I did on MS Azure, using MS Sentinel The escalating sophistication and variety of cyber threats have rendered static honeypots inadequate, necessitating adaptive, intelligence-driven deception. In this work, ADLAH is introduced: an Adaptive Deep Learning Anomaly Detection Honeynet designed to maximize high-fidelity threat intelligence while minimizing cost through autonomous orchestration of infrastructure. The principal contribution is offered as an end-to-end architectural blueprint and vision for an AI-driven deception platform. Feasibility is evidenced by a functional prototype of the central decision mechanism, in which a reinforcement learning (RL) agent determines, in real time, when sessions should be escalated from low-interaction sensor nodes to dynamically provisioned, high-interaction honeypots. Because sufficient live data were unavailable, field-scale validation is not claimed; instead, design trade-offs and limitations are detailed, and a rigorous roadmap toward empirical evaluation at scale is provided. Beyond selective escalation and anomaly detection, the architecture pursues automated extraction, clustering, and versioning of bot attack chains, a core capability motivated by the empirical observation that exposed services are dominated by automated traffic. Together, these elements delineate a practical path toward cost-efficient capture of high-value adversary behavior, systematic bot versioning, and the production of actionable threat intelligence.
The cybersecurity landscape has undergone a dramatic transformation, with cyber threats becoming increasingly sophisticated, persistent, and economically damaging [ 2 ] . Global cybercrime damages are projected to reach $10.5 trillion annually by 2025 [ 76 ] , driven by the proliferation of connected devices and the professionalization of cybercriminal organizations. Modern attacks are complex, multi-stage campaigns that can persist undetected for extended periods, with a median dwell time of 11 days [ 69 ] .
This research is situated within the strategic context of national cybersecurity agencies, such as the German Federal Office for Information Security (BSI), which are responsible for protecting critical digital infrastructure. A primary goal for such agencies is the rapid detection of novel threats to provide timely warnings. While existing sensor networks like the BSI’s MADCAT offer a valuable baseline, the increasing sophistication of application-layer attacks necessitates more advanced analysis capabilities. The Artificial Intelligence (AI)-driven, adaptive architecture presented in this paper aims to address this need, providing a significant leap in capability beyond static sensor grids and directly supporting the BSI’s mission to enhance the nation’s cyber resilience.
The work presented here has been conducted in collaboration with the German Federal Office for Information Security (BSI) and is designed to complement and extend the BSI’s operational capabilities. At the core of the current sensor layer stands MADCAT (Mass Attack Detection Connection Acceptance Tools) [ 15 ] , a low-interaction, honeypot-like suite purpose-built to capture Internet-scale, early-stage attack activity for situational awareness and mass-attack analytics.
In recent years, mass attacks on Internet users have increased markedly, with new procedures and attack patterns emerging continuously. Large-scale outages (e.g., in 2016, an incident affected roughly 900,000 consumer connections in Germany) illustrate how mass events can ripple into critical services [ 134 , 111 , 104 ] . Mass attacks often serve as a staging ground for later targeted operations against specific victims. Many attempts remain undetected or unreported to BSI because they cause no immediately visible impact.
To fulfill its legal mandate under § 7b Abs. 4 BSIG, BSI must therefore operate its infrastructure for collecting and analyzing data on attacks and attempted attacks. Honeypots are a widely used tool for this purpose. By operating its sensors, BSI reduces dependencies on third parties, enables faster and autonomous incident response in significant events, and accumulates longitudinal data to forecast evolving attack trends.
A prominent example is the Log4Shell vulnerability (CVE-2021-44228), disclosed on 10 December 2021. [ 136 ] Exploitation attempts are often detectable in the very first network request via malicious JNDI lookups, making them suitable for"First-Flight" analysis. Although the vulnerability is now well known, exploitation remains observable in current traffic, for instance, scanning activity on TCP port 25565 (popular in Minecraft servers) increased noticeably after disclosure and persists to this day.
MADCAT was developed by BSI (C 26) as a universal, low-interaction cyber threat detection suite. It is honeypot-like in that it records all contact attempts without binding itself to specific services."Low interaction" indicates that, in its current v2 deployment, responses are limited to the technically necessary minimum to establish a connection and capture attack vectors. Internally, an evolved version of MADCAT v2 is in operational use. The extensions proposed in this work enable the analysis of all layers above, including session, presentation, and application-layer behavior, thereby supporting scalable prioritization, advanced Layer 7 analytics, and triage across large sensor fleets and dynamically orchestrated honeypots.
Sensors are deployed both at consumer-grade, Internet-reachable access links and on leased servers (e.g., at mass hosters). In controlled test phases, small-scale deployments have recorded on the order of hundreds of thousands of events per day, exhibiting complex and constantly changing mass-attack activity. These observations empirically motivate an adaptive escalation layer that concentrates scarce high-interaction resources on the most valuable sessions. 1 1 1 Valuable sessions are defined as interactions that exhibit novel, complex, or persistent behavior, indicating a higher likelihood of yielding actionable intelligence about new threats or adversary TTPs.
The program serves BSI’s statutory tasks (e.g., § 3 Abs. 1 S. 2 Nr. 1 bis 4, 10, 14 BSIG) by building and maintaining expertise in the detection and analysis of attack patterns, and by enabling peer-level information exchange with ISPs, operators, and partner organizations. In the course of this work, an exchange between Telekom Security, BSI, and the author was conducted to explore whether T-Pot datasets could be made available for research. The contact at Telekom Security indicated that many similar requests are received and that corresponding approval processes can be lengthy. Access could therefore not be granted within the thesis timeline. To mitigate this, a self-hosted T-Pot instance was deployed and used to collect exploratory data. While this analysis is not central to the present results, the resulting dataset is expected to play a role in future iterations of the architecture, particularly for improving application-layer anomaly detection.
MADCAT focuses on recording initial contact attempts across all reachable ports and protocols with minimal response surface, enabling broad deployment at scale (e.g., consumer links and leased servers). In controlled deployments, MADCAT sensors have observed on the order of hundreds of thousands of events per day across a pretty limited number of sensors, underscoring the need for efficient downstream processing.
From an architectural standpoint, MADCAT provides a modular, ingest-ready telemetry layer: Capture Modules (TCP/UDP/ICMP/RAW): Protocol-specific collectors record first packets and flows. The TCP path includes a postprocessor that correlates SYN and connection objects and optionally leverages system conntrack; its status is summarized via ct_status (Found/Changed/Failed/None). The RAW path uses libpcap filters to quantify traffic classes (e.g., IPv6) 2 2 2 Attacks using IPv6 are yet relatively rare compared to IPv4, thus specialized IPv6-capable modules are still under development. beyond the core protocol set.
Enrichment Processor: Normalizes and augments events (e.g., external sensor IP resolution, geo-IP), performs optional payload splitting for large events using a consistent SPLIT tag, and writes structured logs for shipper ingestion. Harvested Online Documentation & Reference Sources • https://nhimg.org/faq/how-do-organisations-implement-integrated-honeynet/ • https://www.thelasttech.com/post/honeynet-in-cybersecurity • https://arxiv.org/html/2512.07180v1 • https://github.com/goro1408/SOC-Honeynet-Azure • https://www.shadecoder.com/topics/honeynet-a-comprehensive-guide-for-2025 • https://github.com/Adityarlama/honeynet • https://ar5iv.labs.arxiv.org/html/2512.07827
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Honeynet Setup For Enterprise Network Attack Monitoring.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |