Complete Technical Paper Content — Honeytoken Deployment And Alert
Overview & System Context
Honeytoken Deployment And Alert: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~7481 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background GitGuardian Honeytoken creates decoy credentials called honeytokens that do not grant access to customer resources or data. Instead, they act as tripwires that reveal information about the attacker, such as IP Address, User Agent, and Location.
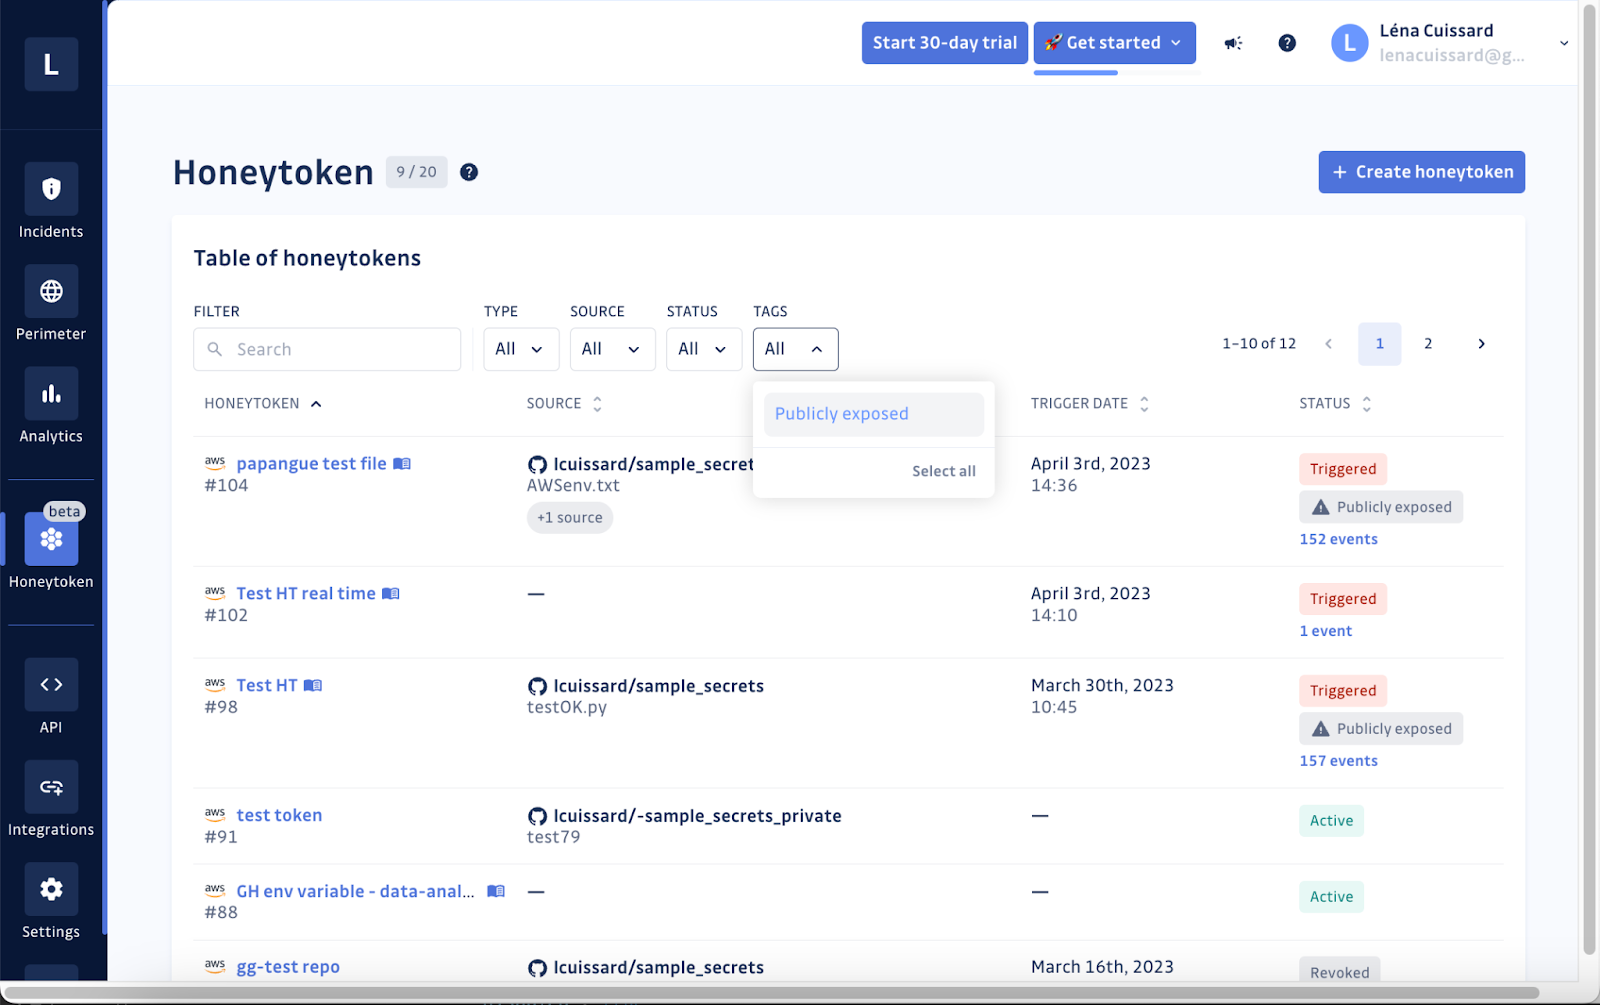
Our honeytokens are indistinguishable from real secrets to attackers . They are designed to be triggered by secret scanners like TruffleHog or Gitleaks, which are often misused by hackers. If a hacker uses a secret scanner to search for developer secrets, they will trigger the honeytoken and alert the security team of a potential security incident. There are several reasons why you should use honeytokens in the software development life cycle (SDLC) and software supply chain: Step 2: Create your honeytoken — click on " Create my first honeytoken " and provide a name and optional description . The description can include specific details about where and how the honeytoken will be placed. Additionally, you can use labels to categorize your honeytoken in a structured manner. Then click " Create my honeytoken ." Figure 1: Launching GitGuardian Honeytoken: your powerful ally to detect any ...
Congratulations! Your honeytoken creation has been confirmed, and you have received your honeytoken key. Step 3: Test your honeytoken — copy the aws sts get-caller-identity command displayed in the information box and paste it into your terminal to trigger the honeytoken: Step 4: Verify your honeytoken data — you can check by verifying the status on the dashboard, along with Events data (Timestamp, IP address, User-agent, and Action performed). Additionally, you should have received an email.
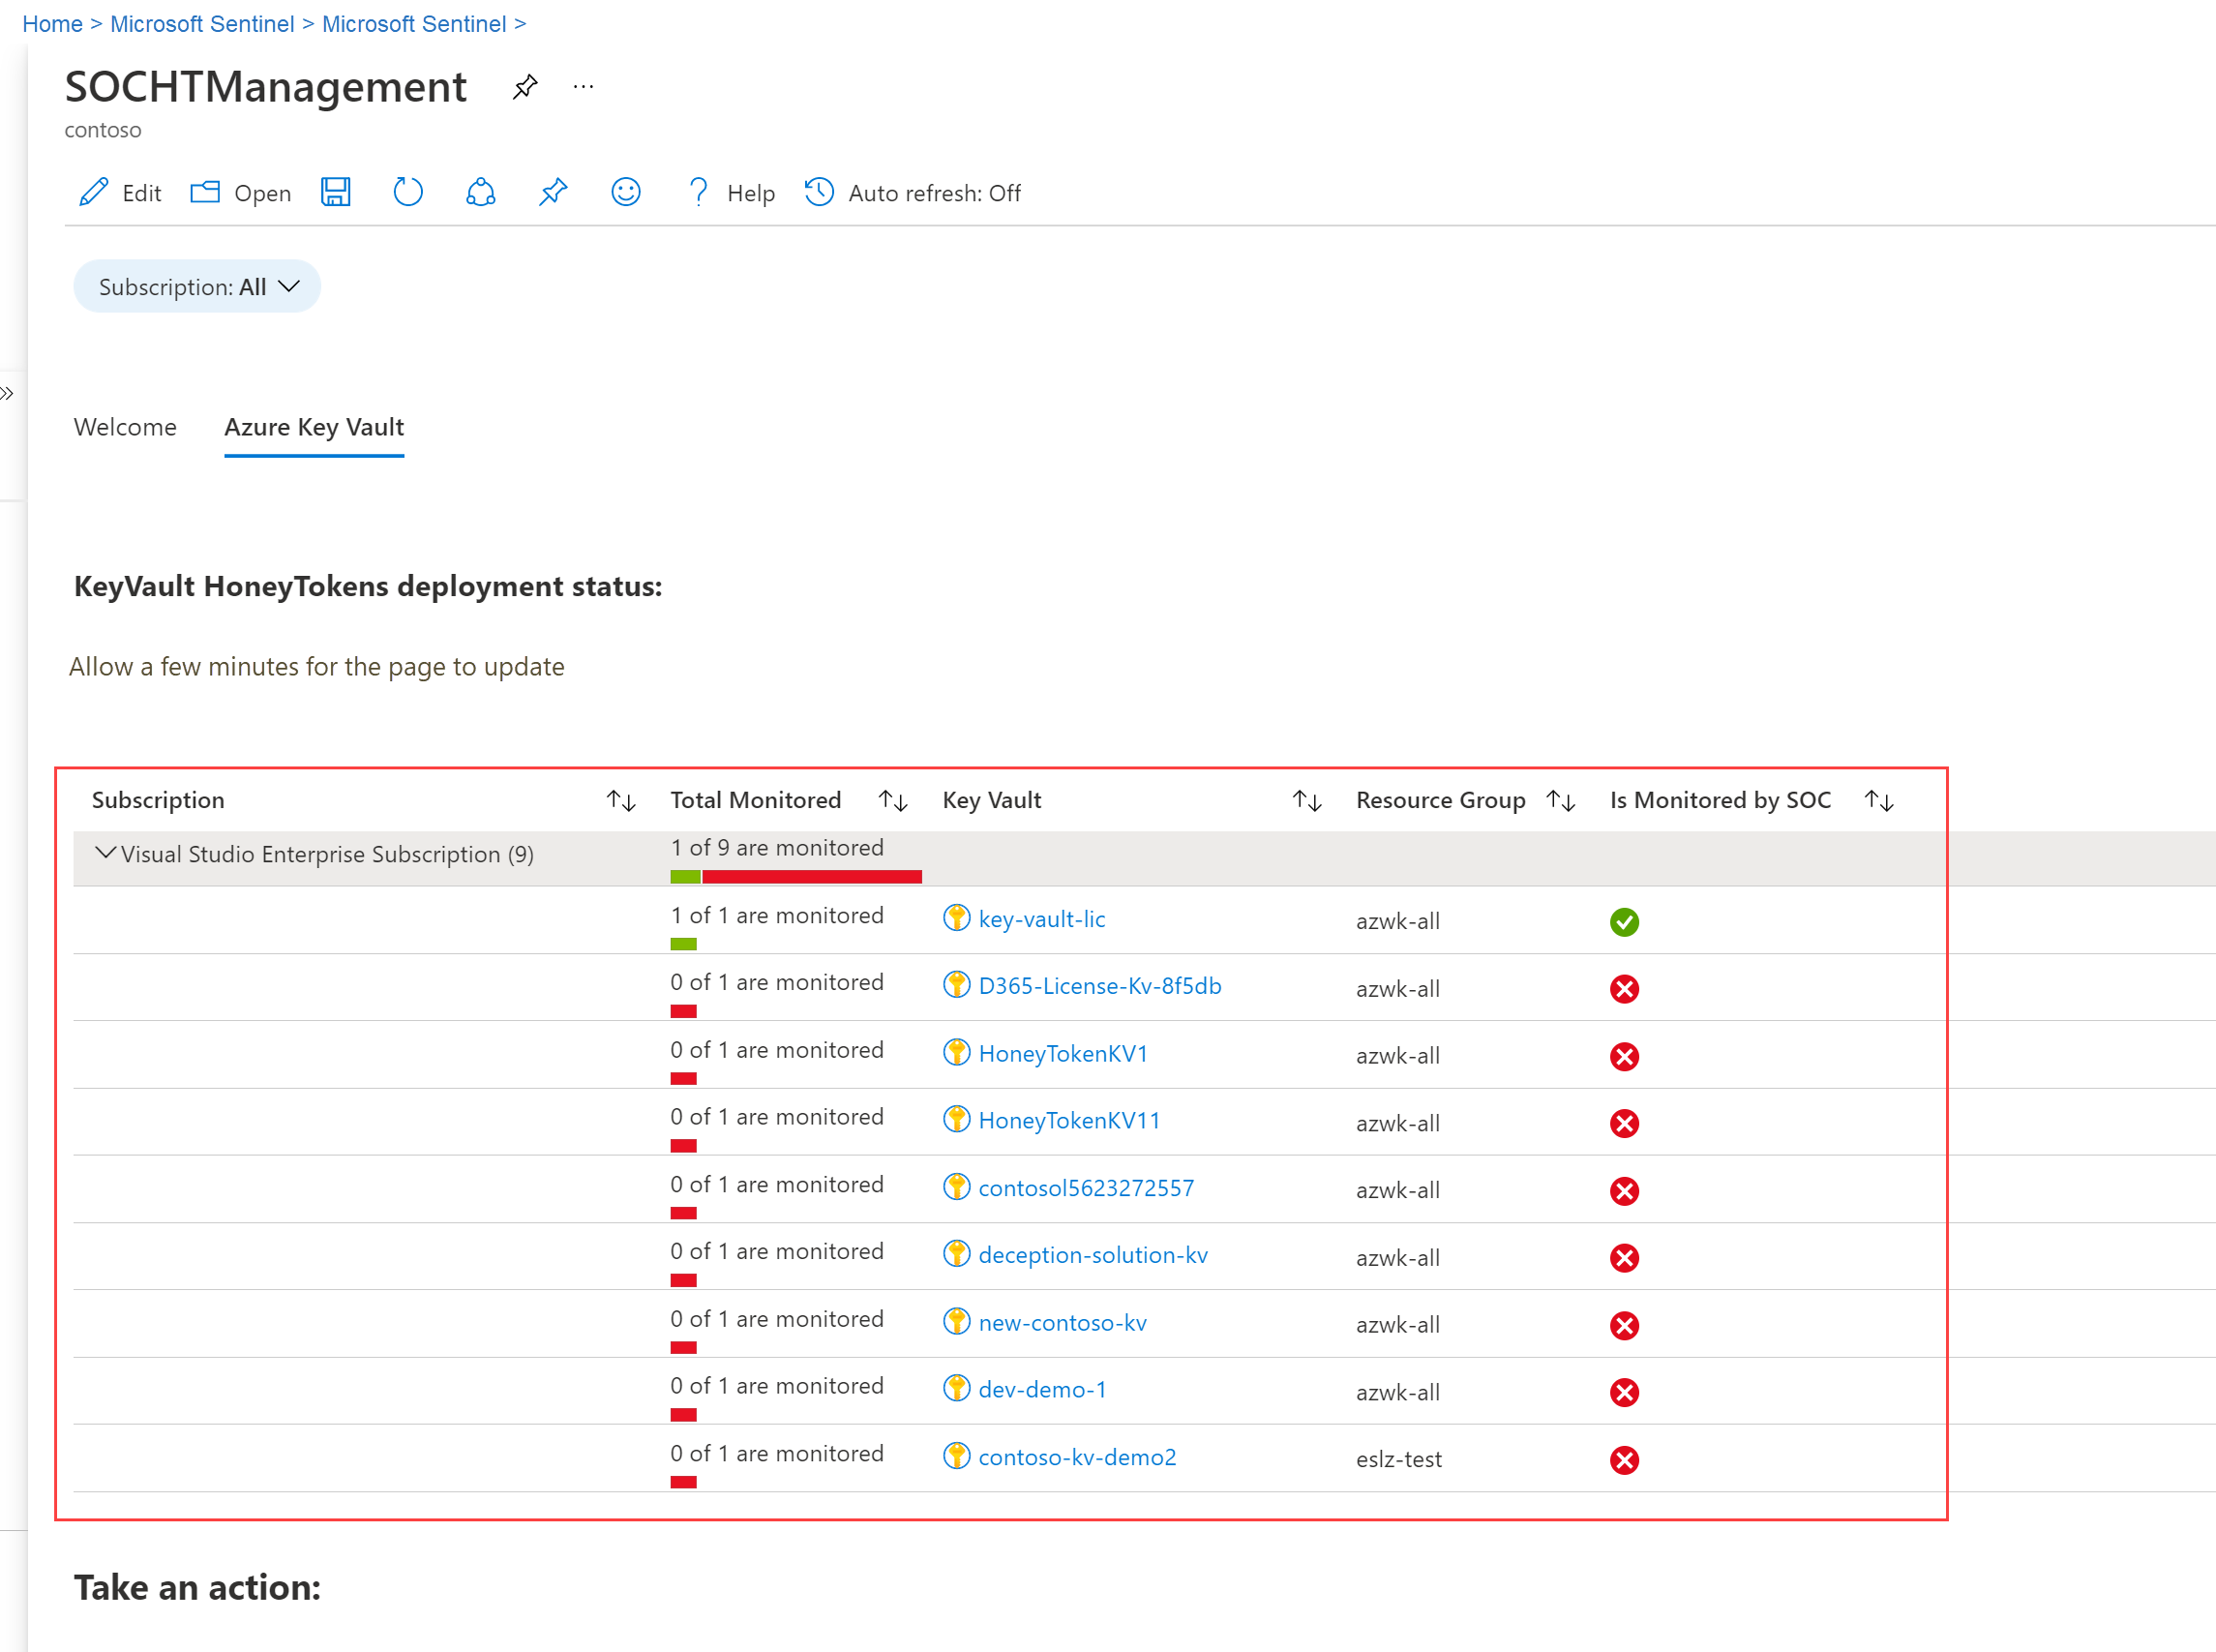
Step 5: Reset your honeytoken — resetting the honeytoken changes its status back to Active, allowing it to be triggered again on future attempts. After resetting, your honeytoken is as good as new! Figure 2: Deploy and monitor Azure Key Vault honeytokens with Microsoft Sentinel ... In a real-life scenario, if you confirm that a triggered honeytoken corresponds to a security incident, you should rather revoke the honeytoken after investigating and taking the necessary measures to protect your environment.
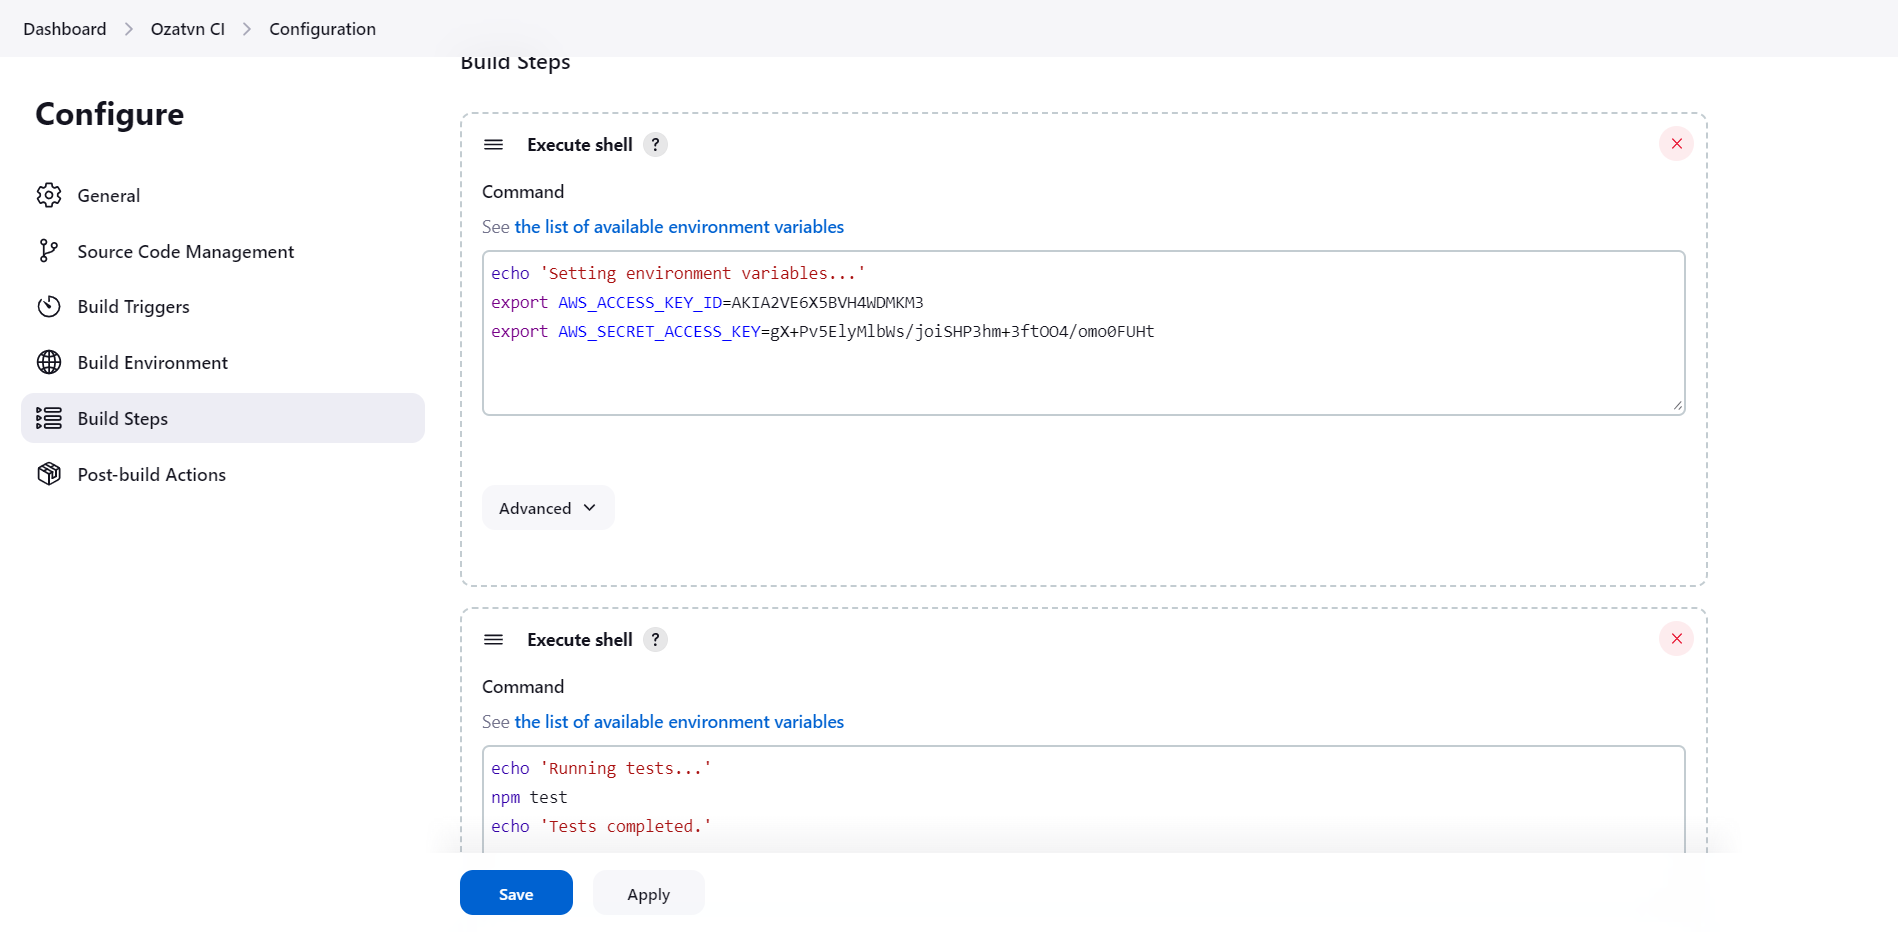
Step 6: Place your honeytoken — you are now ready to start using the honeytoken to protect any system. You can also further configure your alerts to receive instant notifications through custom webhooks, allowing you to customize your alerting workflow. If an attacker encounters these AWS credentials, they will likely try to use them. In consequence, you would be immediately notified of the unauthorized access attempt. With just a few lines of code, you can now effectively deceive attackers! * The trick matters less than the access. Three 2026 disclosures, GitLost, Claude Code's CVE-2026-21852, and Amazon Q's CVE-2026-12957, show agent manipulation determines less damage than the credentials and permissions the agent can reach. * Secrets exposure keeps Figure 3: Secure Your CI/CD Pipelines With Honeytokens Learn how to effectively respond to an AWS key honeytoken trigger with this step-by-step guide. Investigate the incident, identify the leak source, secure your environment, and leverage OSINT techniques to protect your AWS infrastructure.
Learn how GitGuardian Honeytoken's new feature, Deployment Jobs, revolutionizes early breach detection and code repository protection. Automate honeytoken deployment across multiple repositories with ease, ensuring ongoing security and peace of mind. GitGuardian is the code security platform for the DevOps generation. With automated secrets detection and remediation, our platform enables Dev, Sec, and Ops to advance together towards the Secure Software Development Lifecycle.
Today we are going to run through step by step how to create your own honeytokens using entirely open-source tools. With this method, you can create 1 - 5,000 tokens that you can manage using entirely your own infrastructure. To complete this tutorial you will need an AWS account and create a terraform backend, but don’t worry, even if you have no experience with these tools this tutorial will walk through each step.
What are honeytokens or canary tokens? Both are different names for essentially the same thing. You can find a much more detailed description in this blog post , but as a refresher, honeytokens are secrets (like AWS API keys, or other credentials) that are left in your infrastructure to tempt attackers to try and exploit them. Once an attacker uses a honeytoken, it sends an alert and this lets you know you have an intruder in your systems.
Enough about that, let's get started. To make this tutorial accessible to everyone, I am going to explain each step including creating an AWS user with the correct permissions and setting up a slack webhook for notifications. Advanced users may wish to skim over these steps if they are experienced in using these tools. When creating honeytokens I always recommend creating a fresh new AWS user to handle these. This way you can restrict scope easily and keep it separate from your everyday workings. If you have never used AWS here are some steps to create them. If you are familiar with these steps you can skip down to the permissions JSON file.
If you are brand new to AWS you can create an account here, you can use other cloud providers for this but will require a lot of modifications so today we will stick with AWS. Visit your IAM Dashboard and visit the IAM dashboard and click on the user's tab and follow the prompts. Next, we need to set the permissions of the user, it is always a best practice to specify the minimal possible permissions.
Permissions can be added to a group, this may be a good idea if you plan on creating multiple honeytoken users, or you can assign permissions directly to a user. For this tutorial, we will select "Assign policies directly" and click "Create policy". Now we have created a user, we need to create an access token for them. Select the user from the console, and under the "Security credentials" tab click "Create access key", at the next option select "CLI interface".
Now we have our REAL access keys. Next, we need to add them to our local environment. Be careful as these keys are sensitive so you do not want to lose track of them. Make sure you have the AWS CLI client installed - https://docs.aws.amazon.com/cli/latest/userguide/getting-started-install.html The command line will then prompt you to insert your access tokens and region. The region is the closest AWS data center to you, you can leave this blank if you are not sure. Leave the default output format blank. See the example below.
You can get alerts from your honeytokens in a number of places, the GitHub project comes with examples for Slack, SendGrid (email), SES and more. But we are going to be using Slack notifications because, in my opinion, they are the easiest to set up. For this, you will need a slack workspace with a webhook URL. If you know how to do this or want to use a different notification method you can skip this step.
Head over to https://slack.com , create an account if you don’t have one, choose the workspace you want to use or create a brand new workspace by clicking on “Create a new workspace” in the top right corner/ Next, create a new channel that you want the alerts to go to. Again for simplicity, I called my Canary-Token-Alerts Once the workspace has been set up, you need to add a new app to your workspace. Next to “Browse Slack” there are three dots, click this and select “Apps” on the menu During the setup of this app, select the channel you want it to post alerts to. In our case, it is the channel we just created "Canary-Token-Alerts" Finally, you will be able to retrieve your Slack WebHook, and store this somewhere safe as we will need it later.
Now that we have set up our AWS user and created our Slack webhook, we are ready to build our honeytoken. 2. System Architecture & Core Working Principles We are using the GGCanary GitHub project. This is a complete open-source solution so you can create all your own tokens using a terraform backend, it can be scaled from 1 to 5,000 tokens different so suitable for personal use all the way to large enterprises.
If you don’t already make sure you have terraform installed on your computer.
Instructions https://developer.hashicorp.com/terraform/tutorials/aws-get-started/install-cli For our tokens, we are using the open-source project GGCanary https://github.com/GitGuardian/ggcanary This is the file that establishes the connection between our terraform backend and our AWS account.
We now need to create a terraform.tfvars file which will connect with our Slack webhook to send us alerts. In the main project directory, create a file named terraform.tvars and copy the code below into that file. If you want to connect your tokens to email or other systems you can find examples of this file for connections to different services in the folder examples/tf_vars Next, we need to actually create each of our tokens, we can create 1 or 5,000 or any number in between. I am going to create two.
First the token name , the default is ggtoken1, you can name this whatever you want, it may help to give it a name that references where you will put this token. For example github-token-1. This will help you identify what token was triggered if you have multiple. Next Tags , these are tags you can add to the token which may help you in understanding more details. You can add multiple tags for example: Finally, the source is where you did leave the token, in my example this is GitHub so I will name this VCS-GitHub. Here is my finished file We are almost there! Now we just need to check we have all the dependencies available to run and prevent any annoying errors.
This applies the terraform state that we described in our terraform.tfvars file. Center yes when prompted to perform the next action, you should get the following message below. Next, we want to run the same command to initialize the terraform backend again in this directory. Just as we did in the backend we want to apply to terraform state in the main folder. Run the command Final step!!! We just now need to access our honeytokens that have been created. Use the command You can use these keys to make a call like you would with any other AWS credentials. We can also run the helpful command below to test one of our tokens.
In just a few minutes, you should get a notification in your slack channel saying that someone has tripped over your honeytoken! The message in your slack channel should look like the one below. Need more help? email me mackenzie.jackson@gitguardian.com and I will be happy to help debug them pesky error messages with you.
GitGuardian is the code security platform for the DevOps generation. With automated secrets detection and remediation, our platform enables Dev, Sec, and Ops to advance together towards the Secure Software Development Lifecycle. Deploy automated honeytokens in Kubernetes with Koney: set traps for attackers, detect file access with eBPF and Tetragon, and forward alerts to Dynatrace.
Imagine an attacker has breached your perimeter. They’ve gained access to a container in your Kubernetes cluster and are now searching through the file system, looking for secrets (credentials, tokens, keys) that they can use to further the attack. What if those secrets were fake? What if, the moment the attacker attempts to read a fake credential, you get an alert? That’s the idea behind honeytokens: small, realistic-looking files placed in strategic locations to catch unauthorized access attempts.
When someone touches them, you may have a very strong indicator of compromise (IoC) that warrants investigation because legitimate users would never interact with these decoys. In this blog post, we introduce Koney , an open source research project that integrates seamlessly with Dynatrace. Koney is a Kubernetes operator that automates the deployment of honeytokens across your cluster. We’ll walk through the setup from scratch: installing Koney, writing your first deception policy, watching it scale across containers, and forwarding alerts directly to Dynatrace.
Koney is a Kubernetes operator developed by the cloud-native security research team at Dynatrace, together with Matteo Golinelli from the University of Trento. It lets you define deception policies that describe which traps to deploy, where to deploy them, and how to monitor them. Currently, the open source version of Koney supports placing honeytokens in the file system. You can download or contribute on GitHub .
Traditional security approaches focus on building walls and closing gaps: scanning for vulnerabilities with Runtime Vulnerability Analytics (RVA) , blocking attacks in real-time with Runtime Application Protection (RAP) , and fixing misconfigurations with Security Posture Management (SPM) . These are all essential. But they share a common limitation: defenders must close every hole, while attackers need to find just one .
With the rise of Generative AI , this asymmetry is getting worse. Attackers can increasingly use AI-assisted tools and automation to accelerate portions of the attack lifecycle. Instead of trying to keep attackers out, cyber deception places traps on the inside. Now, the attacker, whether human or automated, must watch their steps to not trigger an alert. Honeytokens are one of the simplest deception techniques. Unlike noisy intrusion detection systems, a honeytoken generates a signal only when something truly suspicious happens: properly configured legitimate processes generally should not access a decoy credentials file planted by your security team.
Deception has a rich history in information security. Researchers like Lance Spitzner popularized the concept of honeypots in the early 2000s. Academic research has demonstrated that deception techniques can help detect and slow attacker activity in specific scenarios. But widespread industry adoption has been held back by the operational burden: manually creating, deploying, monitoring, and rotating honeytokens across dozens of containers is tedious and error prone. Koney solves this by letting you express your deception strategy as a Kubernetes custom resource (a DeceptionPolicy object) and handling everything else automatically.
When you update a policy, Koney updates the traps. When you delete a policy, Koney removes them. When you spawn new pods that match the policy, Koney automatically deploys traps there too. It’s deception-as-code for Kubernetes. That’s it. Koney is now watching for DeceptionPolicy custom resources in your cluster. Koney uses Tetragon for eBPF-based monitoring. Tetragon watches for file access events at the kernel level.
3. Software Implementation, Frameworks & Protocols The dnsPolicy=ClusterFirstWithHostNet setting is required so that Tetragon can resolve the addresses of Koney’s internal services to forward alerts. If you have Tetragon already installed, make sure to set this option. To see Koney in action, we need an application running in the cluster. Create and apply a demo-app.yaml manifest with label honeytoken: “ true ” set in the pod labels. Alternatively, you can also use any existing application in your cluster; just make sure the relevant pods carry the label honeytoken=true. We’ll use this in our deception policy to select which containers get honeytokens.
A DeceptionPolicy is a custom resource that describes what to deploy and where. We’ll place a decoy credentials file at /run/secrets/.aws/credentials . This is a common path that attackers look for when hunting for cloud provider secrets. Credential files in well-known paths are among the first things attackers look for after gaining a foothold. In the status conditions, you should see that the policy was found and both the decoy and captor have been deployed successfully.
You should see the decoy AWS credentials we defined. This file was injected by Koney; it wasn’t in the original container image. An attacker stumbling onto this file would see what looks like valid credentials and try to use them. The moment they read the file, an alert is already triggered. The deception policy applies to all matching containers. If you add new workloads or scale up your deployment, every new pod also automatically receives the honeytoken. This is one of the key advantages of expressing deception “as code.” Let’s test it by scaling up our deployment: Koney also tracks what it deployed using a koney/changes annotation. Let’s inspect it: Now let’s simulate an attacker finding and reading the honeytoken. Open a shell in the container and access the honeytoken: This tells you exactly where the access happened (pod, namespace, container), who did it (process binary, PID, UID), and which policy was triggered.
Seeing alerts in logs is fine for testing, but in production, you’ll want them in your security platform. Koney supports forwarding alerts to Dynatrace using a DeceptionAlertSink resource. To set this up, you’ll need a Dynatrace API token and environment URL stored in a Kubernetes secret. The detailed instructions for creating the token with the correct scopes are in Koney’s documentation on alert sinks .
Once you have the secret, create a DeceptionAlertSink (assuming your secret is named dynatrace-api-token ): When configured successfully, honeytoken access alerts can be forwarded to Dynatrace as security events . After setting up the alert sink, trigger a few more access events to generate findings in Dynatrace: Then open the Threats & Exploits app in Dynatrace. You’ll see the detection findings with all the contextual information.
Each finding includes structured fields like koney.deception_policy_name, koney.trap_type, k8s.pod.name, and process.executable.name . This means you can write Dynatrace Query Language (DQL) queries to further analyze and correlate events with Investigations . One of the most practical benefits of Koney is that deception policies are living resources. You can update them at any time.
Try changing the fileContent field in your honeytoken.yaml and re-apply the policy: kubectl apply -f honeytoken.yaml Koney will update the honeytoken across all matching containers. This enables dynamic deception strategies. Koney currently supports filesystem honeytokens, but the project is designed to support additional deception techniques in future versions. including deceptive HTTP endpoints and payloads that can lure vulnerability scanners and redirect them to honeypots.
Once alerts are flowing into Dynatrace, the possibilities go further. For example, you could build a Workflow that triggers on Koney alerts, looks up the owner of the affected namespace using the Ownership app, and creates a ticket for the security team. We previously demonstrated this kind of end-to-end security automation in the blog post, Context-aware security incident response with Dynatrace Automations and Tetragon , but now with Koney, even more steps are automated.
If you’re interested in the research behind Koney, we recommend reading the Koney paper , published in the 4th Workshop on Active Defense and Deception (AD&D), co-located with the 10th IEEE European Symposium on Security and Privacy (EuroS&P ’25). In a controlled study by Horizon3 researchers, models that explicitly identified a trap in their reasoning still attacked it 73.4% of the time. Read the findings and see what they mean for canaries, decoys, and early detection.
Deception technology occupies a unique position in the security tool landscape because it inverts the economics of detection. Every other detection mechanism works against the attacker's ability to hide: the defender tries to find malicious behavior in a sea of legitimate activity. Deception technology creates artifacts that have no legitimate use case: a fake AWS key that should never be accessed, a fake admin account that should never log in, a network service that no legitimate user would ever connect to. When any of these objects is touched, the alert has near-zero false positive probability because no legitimate operation should ever interact with them. This property makes deception one of the highest-fidelity detection mechanisms available, and it is deployable by teams with modest security budgets and limited SIEM infrastructure.
The fundamental asymmetry of deception technology is this: the defender must place deception artifacts correctly once, while the attacker must avoid every deception artifact every time. A single trip wire in a password manager, a code repository, an Active Directory OU, or a network segment generates an alert on first contact. The attacker who discovers a fake credential and uses it has identified themselves without knowing they have done so. The attacker who is sophisticated enough to identify and avoid the deception object must expend additional time and resources at each step, which increases dwell time, increases the probability of detection through other mechanisms, and may disrupt the attack timeline enough to enable a response.
Traditional detection mechanisms suffer from the problem of signal-to-noise ratio. A SIEM ingesting endpoint, network, and identity logs generates thousands to tens of thousands of events per day, and the detection rules that identify malicious behavior also match legitimate activity patterns that resemble malicious ones. The analyst workload of investigating false positives consumes the capacity that should be directed at real threats. Deception solves this problem architecturally: a honeytoken that generates exactly one alert type (this fake thing was accessed) produces a signal with effectively no noise.
The operational overhead argument against deception technology is typically overstated. The concern is that maintaining realistic-looking deception artifacts requires ongoing effort to keep them believable. In practice, the highest-value deception artifacts require minimal maintenance: a fake AWS key in a code repository does not need to be updated to remain functional as a trip wire. A fake admin account in Active Directory does not need to have its password changed or its group memberships updated to generate an alert when someone attempts to authenticate with it. A network honeypot emulating an RDP server does not need to be updated when Windows Server gets a new patch. The maintenance burden argument against deception is much stronger for enterprise deception platforms that attempt to build complete deceptive environments than for targeted honeytoken deployments, which is where most organizations should start.
The deception technology spectrum ranges from a single honeytoken costing nothing to deploy to a commercial enterprise deception fabric costing hundreds of thousands of dollars annually. Understanding what each tier of the spectrum provides helps match the investment to the organization's threat model and operational capacity. A honeytoken is a single fake data object with a monitoring mechanism attached. The simplest example is a URL that, when accessed, sends an HTTP request to a logging server. A more sophisticated example is an AWS access key that, when used in an API call, generates a CloudTrail event flagged as unauthorized access. Honeytokens can be deployed in minutes, cost nothing to maintain, and generate extremely high-confidence alerts on contact. Their limitation is that they only detect activity that directly contacts the specific object: an attacker who finds the fake AWS key and doesn't use it, or who finds the code repository but not the specific file containing the key, generates no alert.
A honeypot is a fake system or service that appears functional but captures and alerts on all connection attempts. A fake RDP server that looks like a real Windows Server, logs every connection attempt, and generates an alert on any inbound session is a network honeypot. Unlike a honeytoken, a honeypot provides network-level detection: any host that scans the honeypot's IP address generates an alert, even if the scanner never attempts to authenticate. Honeypots detect network reconnaissance and lateral movement probing that honeytokens miss.
Full deception platforms create an entire parallel deceptive environment: fake servers, fake network shares, fake Active Directory objects, fake credentials distributed across real endpoints, and full correlation of all deception interactions into a unified alert timeline. Commercial platforms like Attivo Networks (acquired by SentinelOne), Illusive Networks, and Acalvio automate the creation and distribution of deception objects at scale and provide an analyst interface for investigating deception alerts. They also include anti-deception analysis: the platform monitors for attacker behaviors that suggest they are identifying and avoiding deception objects, which is itself an indicator of sophisticated adversary tradecraft.
Canarytokens.org, operated by Thinkst, is the most accessible entry point to deception technology. The service is free and generates unique URLs, DNS names, or payloads that send an HTTP callback to Thinkst's logging infrastructure (or to your own server using the self-hosted version) when triggered, delivering an alert with the source IP address, user-agent, and timestamp of the access event.
The available canary token types cover most high-value placement scenarios. A DNS token generates an alert when a DNS query is made for a unique subdomain, which fires when a document embedding the token is opened and its DNS beacon resolves, even if the user is on an internal network. A Word document token embeds a DNS beacon in a .docx file that fires when the document is opened in Microsoft Word, making it a high-value trip wire for document stores. An AWS key token uses a real AWS IAM key with no permissions attached; any attempt to use the key in an AWS API call generates a CloudTrail event and a webhook alert, making it an ideal fake credential for code repositories. A Windows credential token creates a .URL file that, when opened by Windows Explorer, attempts to authenticate to a UNC path controlled by Canarytokens, capturing NTLM hashes in a way that resembles a credential capture attempt but alerts the defender instead.
4. Practical Deployment, Analysis & Case Studies For self-hosted environments where sending alert data to a third-party service is not acceptable, the Canarytokens open-source project provides the full platform for deployment on internal infrastructure. A self-hosted Canarytokens server on an internal host with alerting configured to your SIEM or email provides all the same token types with complete data sovereignty. The setup requires a Linux server with Docker, a DNS entry pointing a subdomain to the server, and a port 80/443 listener for HTTP callback tokens. The entire deployment takes two to three hours and provides ongoing high-fidelity detection infrastructure.
Deploying a portfolio of canary tokens across an environment should follow a placement strategy based on where attackers typically look for credentials and access paths during post-exploitation enumeration. File shares accessed by many users, source code repositories, password managers, cloud infrastructure credentials, and administrative tool configurations are the primary placement targets. Place at least one token in each category that applies to your environment before moving on to more complex deception techniques.
The value of a honeytoken is proportional to how likely an attacker who has achieved initial access is to encounter and interact with it during their post-exploitation workflow. Placing honeytokens in locations that attackers systematically search during the reconnaissance and credential harvesting phases of an intrusion maximizes the probability of early detection. A fake admin credential in a password manager is a high-priority placement because attackers who compromise a workstation frequently harvest credentials from browser-stored passwords and password managers. A KeePass database or browser password store that contains an entry labeled 'server-admin' or 'domain-admin' with a URL pointing to a canary token will fire when the attacker copies or attempts to use the credential. The account name should match the naming convention of real administrative accounts in the environment to be convincing.
A fake AWS access key embedded in a code repository is high-value because automated secret scanning tools used by attackers scan public and private repositories for AWS key patterns immediately after gaining access. A fake key with a name like 'aws-prod-backup-key' in a .env file or configuration file will be extracted and tested against the AWS API, generating a CloudTrail alert with the source IP of the system attempting to use the key. This alert fires before the attacker has gained any actual access, providing an extremely early warning signal.
A fake domain admin account in Active Directory is valuable for detecting Active Directory enumeration and credential stuffing attempts. Create an account with a name that fits the convention of real admin accounts, populate it with realistic AD attributes (description, department, manager), and configure the account to never expire and to require password at next login so it looks dormant. Any authentication attempt against this account, whether through Kerberoasting, password spray, or direct login attempt, should generate an alert via SIEM rule on the account name. This alert fires during the privilege escalation phase, well before the attacker has achieved their objective.
A fake database connection string in an application configuration file is valuable for detecting attackers who are searching for database credentials after compromising an application server. A connection string containing a canary DNS token in the server hostname will resolve the DNS token when any process attempts to connect to the fake database, identifying which process on which host is attempting the connection.
An entry labeled with an admin account name containing a canary token URL that fires on access. Detects credential harvesting from workstations. A real-format AWS access key with no permissions in a .env or config file. API usage generates a CloudTrail event with the attacker's source IP.
A convincing-looking AD account with realistic attributes that should never be authenticated against. Any auth attempt generates an alert. A connection string with a canary DNS hostname that fires when any process attempts to resolve the server address, identifying unauthorized database access attempts.
A document named to attract attention (passwords.xlsx, network-diagram.docx) containing a DNS canary token that fires when the file is opened. Active Directory is the primary target for privilege escalation in Windows environments, and deception objects within AD provide detection coverage for the reconnaissance and enumeration techniques attackers use to identify and target privileged accounts. AD deception operates at a different level than canary tokens: rather than detecting access to a specific object, AD deception detects the LDAP enumeration and authentication attempts that precede targeted credential attacks.
Fake service principal names (SPNs) attached to fake service accounts are a specific AD deception technique targeting Kerberoasting. Kerberoasting extracts Kerberos service tickets for accounts with SPNs and attempts to crack the service account password offline. Creating a fake service account with a compelling SPN (like HTTP/intranet-payroll.domain.com) and an extremely strong password, then monitoring for Kerberos TGS requests for that specific SPN in the domain controller event logs (Event ID 4769), detects Kerberoasting attempts that target the fake account. The fake SPN is never used for any legitimate service, so any TGS request for it is unambiguously an attack indicator.
Fake Group Policy Objects with names that suggest elevated privilege access (like 'Domain Admin Desktop Policy' or 'Privileged Access Workstation Configuration') attract attackers who enumerate GPOs looking for policy objects that reveal administrative workflows or contain embedded credentials. The GPO itself does not need to be functional as a detection mechanism: the detection comes from monitoring LDAP queries for the GPO's GUID in domain controller logs or from a canary token embedded in the GPO's script content.
OpenCanary is the leading open-source network honeypot platform for teams that want low-overhead network-level deception without a commercial platform. OpenCanary runs as a Python process on a Linux system and emulates a configurable set of network services: RDP, SSH, HTTP, HTTPS, SMB, FTP, Telnet, and SNMP. Any inbound connection to any of these services generates an alert with the source IP, protocol, and connection details. Deploy OpenCanary on a Linux host with a static IP address that has no legitimate business function, ensure the address is in the same subnet as servers or workstations to maximize the probability of encountering network scanners, and configure alert forwarding to your SIEM or email. T-Pot is an alternative honeypot distribution that packages multiple honeypot software projects into a Docker Compose deployment, providing higher-fidelity emulation at the cost of higher resource requirements.
A deception deployment that generates alerts nobody sees is worse than no deception deployment, because it creates a false sense of coverage. Routing honeytoken and honeypot alerts to a monitored channel with a dedicated high-priority rule is as important as the deception technology itself. The alert path should be: deception event fires, alert goes to SIEM with a specific rule that tags it as a deception alert at Critical or High severity, the SIEM rule triggers immediate notification to the on-call analyst via PagerDuty, Opsgenie, or equivalent paging system.
For Canarytokens, configure webhook delivery to your SIEM's HTTP input endpoint so that every token trigger creates a SIEM event. Add a SIEM detection rule that matches on the source type 'canarytoken' and generates a Critical alert with no additional conditions required. Unlike most SIEM rules that require multiple correlated events to reduce false positives, honeytoken alerts should trigger on a single event because the false positive probability is inherently near-zero. The single-event Critical alert rule for honeytokens is one of the rare cases where a SIEM rule with no baseline or correlation requirement is operationally appropriate.
Sophisticated attackers increasingly use anti-deception techniques to identify honeypots and avoid deception objects before interacting with them. Common honeypot identification techniques include checking whether the target system's network characteristics match what the emulated service would realistically produce (network timing, banner strings, error message formats), checking for inconsistencies between the emulated system's behavior and a real implementation (OpenCanary's SMB emulation differs from real Windows SMB in detectable ways), and testing whether the target system responds to unusual protocol edge cases in ways that real systems do not. To resist anti-deception analysis, deploy honeypots on hardware that matches the emulated system's resource profile, use realistic banner strings that match the specific software version being emulated, and periodically review public research on honeypot fingerprinting techniques to update your deployments accordingly.
Maintenance is the most common deception deployment failure. A fake admin credential in a password manager that has an expired password, a canary token whose webhook URL is no longer monitored, or a network honeypot that went offline six months ago provide zero detection value while creating a false belief in coverage. Implement a quarterly deception audit: verify every active token still generates an alert when triggered, verify every honeypot is online and its alert path is functional, and review the list of deployed deception objects against a register of what was intended to be deployed. Deception that has decayed into non-functionality is worse than no deception because it creates a coverage illusion.
Deception technology is one of the most cost-effective detection investments a security team can make, particularly for teams that lack the budget for comprehensive SIEM coverage or the analyst capacity to tune high-noise detection rules. Start with a portfolio of canary tokens placed at the locations attackers consistently target during post-exploitation: password managers, code repositories, Active Directory, and file shares. Add a network honeypot in each internal subnet. Connect every alert to your SIEM with a high-priority rule that bypasses the triage queue. The honeytoken that fires at 2 AM on a Tuesday with the source IP of a compromised workstation is worth more than a thousand SIEM rules that generate alerts an analyst never has time to review.
A honeytoken is a single fake data object (a credential, a document, an API key) that generates an alert when accessed or used. It requires no dedicated server or network infrastructure. A honeypot is a fake system or service that accepts network connections and generates alerts on connection attempts. Honeytokens detect attackers who interact with specific objects like credentials and files. Honeypots detect network reconnaissance and lateral movement probing. The two are complementary: deploy honeytokens for credential and data access detection, and honeypots for network-level lateral movement detection.
Yes. Canarytokens can deliver alerts directly to an email address or Slack channel, which is sufficient for small teams that review alerts manually. OpenCanary can log to a local file and be configured to send email on connection events. The limitation of SIEM-less deception is the absence of correlation with other security events, which reduces the analyst's ability to contextualize the deception alert with the broader attacker activity visible in other log sources. For organizations without a SIEM, direct email or Slack alerting from deception tools is a viable starting point that can be migrated to SIEM integration as the security infrastructure matures.
Placement and naming discipline prevent most accidental triggers. Do not place honeytokens in locations where legitimate work activity could encounter them: a canary token in a shared document that multiple users open for work purposes will generate constant alerts. Place tokens in locations that have no legitimate business purpose (an account named in a way that suggests it should never be used, a file named to attract an intruder's attention in a location administrators do not browse) and document the existence and placement of each token in your detection register. If a honeytoken placement generates a legitimate user false positive, treat it as a placement design failure and relocate the token.
The primary operational risk is a honeypot service that interferes with legitimate network traffic if deployed on an IP address or port combination that legitimate applications depend on. Mitigate this by assigning honeypots to IP addresses that have never been used for legitimate services and verifying that no existing network traffic targets the honeypot address before deployment. A secondary risk is that sophisticated attackers who identify your honeypot can use its characteristics to map your deception strategy, though this risk applies primarily to enterprise deception platforms rather than simple canary tokens.
How does deception technology compare to threat intelligence feeds for detection coverage? Deception technology and threat intelligence feeds detect different threat profiles. Threat intelligence feeds provide indicators of compromise (IOCs) for known malicious infrastructure and malware families, enabling detection of attacks using previously identified tools and infrastructure. Deception technology provides behavioral detection of attacker activity in your environment regardless of the tools used, which catches novel threats that have no threat intelligence coverage. The two approaches are complementary: threat intelligence catches known threats early, and deception technology catches unknown or novel threats that bypassed signature-based controls. The false positive profile of deception is substantially better than IOC-based detection, where IOC stale dates and IP address reuse generate significant noise.
25 actively exploited vulnerabilities with CVSS scores, exploit status, and patch availability. Print it, pin it, share it with your SOC team. Step-by-step 24-hour IR checklist covering detection, containment, eradication, and recovery. Built for SOC teams, IR leads, and CISOs.
50,000+ security professionals read Decryption Digest for early warnings on zero-days, ransomware, and nation-state campaigns. Free, daily, no spam. Cybersecurity professional with expertise in threat intelligence, vulnerability research, and enterprise security. Covers zero-days, ransomware, and nation-state operations for 50,000+ security professionals every morning.
Actionable threat intelligence for working practitioners. Free. No spam. Trusted by 50,000+ SOC analysts, CISOs, and security engineers. Cybersecurity insights by Amit Vijayan. Incident response, threat intelligence, detection engineering and practical learning for security professionals.
5. Performance Evaluation & Extended Technical Observations A honeytoken alert can give a SOC a focused starting point: an identity or process interacted with a deliberately synthetic asset. The investigation still has to explain what happened. This guide shows how to preserve the signal, separate benign access from suspicious behavior and document an evidence-led decision.
A decoy with no routine business purpose can be useful, but backup agents, content indexers, security scanners and authorized tests can still touch it. Treat the alert as a hypothesis to investigate rather than proof of compromise. This workflow concerns an approved existing decoy deployment; it does not instruct readers to plant real credentials or expose production systems.
Do not infer a person from an IP address alone. A proxy or shared service may be the observable source. Record which identifiers come directly from evidence and which relationships remain inferred. The following is illustrative, unexecuted pseudocode, not a ready-to-run KQL or SPL query. Map fields to your actual data sources. Test and adapt it only in environments you are authorized to investigate.
A shared username or matching timestamp alone is weak correlation. For endpoint process joins, retain process-instance context; see our KQL and Splunk PowerShell investigation examples . If the source lacks the required identifier, state the limitation instead of manufacturing a connection. A synthetic file triggers an alert during the backup window. The service identity, host, process and job record all match an approved backup task. The analyst records a supported benign explanation and proposes a narrow, reviewed exception for this exact workflow. This does not justify ignoring every event from the service account.
A decoy interaction appears under an employee account outside its expected workflow. Nearby identity events and endpoint observations suggest unusual access, but there is no reliable record proving data transfer. The analyst preserves the timeline, escalates the suspicious sequence and explicitly records that exfiltration is unproven. Measure which recurring events consume analyst time and validate their cause before tuning. Tie exceptions to a verified asset, process or job and an expiry or review date. Retest after collector, decoy or business-workflow changes. A detector that becomes silent after a broad exclusion may simply have lost visibility.
Where corroborating evidence indicates compromise, follow the incident-response process for account restriction, session revocation or endpoint isolation. Assess business impact, preserve evidence and involve the asset owner. Do not automate destructive action solely because a decoy fired. The decoy is a defensive mechanism, not itself an adversary technique. Select an ATT&CK mapping only after observed behavior supports it; do not assign credential theft or data exfiltration from the alert name alone. Record the scope, raw evidence references, correlation assumptions, benign alternatives, confidence, action owner and review deadline.
Context: CISA, Using Cyber Decoys to Strengthen Detection and Response, September 16, 2026 . This article's workflow and fictional examples are HackInvasion's instructional analysis. Continue with detection validation with benign tests and coverage gaps or browse the Knowledge Base . I Submitted as part of CSCI 32032 – Research Methodology and Scientific Communication at the University of Kelaniya, Sri Lanka.
Honeytokens are fake digital assets used to detect unauthorized access. This project proposes an automated framework for deploying honeytokens across enterprise systems using Ansible, with real-time alerting through SIEM platforms like Wazuh or ELK Stack. Theekshani Pramodya TheekshaniPramodya on GitHub Department of Computer Science University of Kelaniya, Sri Lanka T.P. Hettiarachchi, “Automating Honeytoken Deployment and Detection in Enterprise Networks,” 2025.
Research project on automating honeytoken deployment and detection in enterprise networks using Ansible and SIEM integration. Submitted for CSCI 32032 – Research Methodology and Scientific Communication. Traditional security boundaries are no longer enough. Discover how to transform your cloud VPS from a passive target into an active defense system using Honeytokens. This comprehensive guide walks you through the strategic deployment of digital tripwires, allowing you to detect, log, and neutralize sophisticated cyber threats the exact moment a breach occurs, long before critical assets are compromised.
Deploying honeytokens can be accomplished through various methods, each suited to different needs and scenarios: Deployment jobs are only available for workspaces under the Growth or Enterprise plan. Deployment jobs enable the automated deployment of honeytokens into code repositories that are integrated with GitGuardian. For an in-depth exploration of Deployment jobs, please refer to our detailed page on this topic .
This approach is highly recommended for broad coverage across numerous repositories, offering an efficient and streamlined process. If you use Endpoint Protection , ggshield can plant a honeytoken directly on each developer machine and keep it reconciled with GitGuardian. The decoy lands in the local credential file that credential harvesting malware reads first, so an attempt to steal it raises an alert naming the compromised machine.
This is the right method for extending honeytoken coverage to your fleet of laptops and workstations. Deployment runs through your MDM alongside endpoint scanning. See Protect endpoints with Honeytokens . Manual deployment of honeytokens is always an option. This involves creating a honeytoken from the GitGuardian dashboard, copying the AWS key, and then inserting it into the asset you wish to monitor. Detailed instructions for this process can be found on our Getting Started page.
This method is particularly useful for assets not under GitGuardian's monitoring or in scenarios where automation is not feasible. It is best suited for situations involving a smaller number of assets. When manually inserting honeytokens into assets not integrated with GitGuardian, it's crucial to assign them distinctive names and descriptions. This way, should the honeytoken be triggered, you'll be able to identify which asset was compromised. We recommend naming the honeytoken after the asset itself and using the description field to provide additional details about its precise location. Custom tags can also be utilized to categorize your honeytokens effectively.
For those with specific needs or seeking greater flexibility, creating custom deployment scripts is a viable option. You can craft scripts that generate honeytokens by leveraging GitGuardian's Honeytoken API , insert them into the desired context, and then deploy them to your target assets. This method offers a high degree of customization and control but requires a significant technical investment from the user. It is a good choice for covering a vast array of assets not supported by GitGuardian's integrations, or if you prefer to dictate the exact context in which your honeytokens are deployed.
This guide walks through honeytoken creation in the Trapster dashboard. Each type has its own deployment guide with placement examples. When you create a honeytoken, you pick a template from the catalog. Each template produces a different kind of decoy. Filter by All , File , Anti-phishing , or Other .
Use the search box or category filters ( All , File , Anti-phishing , Other ) to find the type you want. Click a template to select it. Every honeytoken requires a Note : a short reminder of where you placed it. This note appears in incidents when the honeytoken triggers. Click Create . After creation, you are given the honeytoken to download or copy and told what to do next: Harvested Online Documentation & Reference Sources • https://blog.gitguardian.com/how-to-create-and-use-honeytokens-step-by-step/ • https://blog.gitguardian.com/honeytoken-workshop/ • https://www.dynatrace.com/news/blog/cyber-deception-with-koney-and-dynatrace/ • https://www.decryptiondigest.com/blog/deception-technology-honeypot-deployment • https://hackinvasion.blogspot.com/2026/09/investigating-honeytoken-alerts-from.html • https://github.com/TheekshaniPramodya/honeytoken-deployment-detection • https://xylentis.com/blog/building-an-early-warning-system-how-to-deploy-honeytokens-on-your-vps-for-proactive-intrusion-d etection • https://docs.gitguardian.com/honeytoken/deploy-honeytokens/deployment-methods • https://docs.trapster.cloud/honeytokens/create-and-deploy/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Honeytoken Deployment And Alert.
[*] Metasploit Scan Running on Target Subnet for Honeytoken Deployment And Alert... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |