Complete Technical Paper Content — Http Request Smuggling Vulnerability Detector Tool
Overview & System Context
Http Request Smuggling Vulnerability Detector Tool: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9527 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Many entities have provided or promised military aid to Ukraine during the Russo-Ukrainian War, particularly since the 2022 Russian invasion of Ukraine. This includes weaponry, equipment, training, logistical support, as well as financial support, unless earmarked for humanitarian purposes. Weapons sent as a result of cooperation between multiple countries are listed separately under each country. The aid has mostly been coordinated through the Ukraine Defense Contact Group, whose 57 member countries include all 32 member states of NATO. The European Union co-ordinated weapons supplies through its institutions for the first time. The Russian invasion led several donor countries, including Germany and Sweden, to overturn their national policies on providing offensive military aid. By March 2024, the majority of Western governments had pledged more than $380 billion worth of aid to Ukraine since the invasion, including nearly $118 billion in direct military aid from individual countries. As of December 2024, European countries have provided €132 billion in aid (military, financial, and humanitarian), and the United States has provided €114 billion. Most of the US funding supports American industries that produce weapons and military equipment. Fearing escalation, NATO states have hesitated to provide heavier and more advanced weapons to Ukraine or have imposed limits such as forbidding Ukraine from using them to strike inside Russia.
Since June 2024, they have lifted some of these restrictions, allowing Ukraine to strike Russian military targets near the border in self-defence. According to defence expert Malcolm Chalmers, at the beginning of 2025, the US provided 20% of all military equipment Ukraine was using, with 25% supplied by Europe and 55% produced by Ukraine. However, the 20% provided by the US "is the most lethal and important." Individual EU member states have provided military, financial, and non-lethal material aid since 2014. The following list is the aid collectively provided by the EU. Most of this aid has been coordinated by the European Commission.
Around €17 billion in grants and loans from 2014 until 12 February 2022. €1.2 billion loan approved 16 February 2022 €450 million worth of lethal weapons, announced on 27 February 2022, under the European Peace Facility. €50 million worth of non-lethal aid, announced on 27 February 2022. Provision of satellite intelligence, notably through the European Union Satellite Centre, as part of 1 March 2022 resolution on the Russian aggression against Ukraine. Increase of military aid under the European Peace Facility to €1 billion, announced on 23 March 2022. Military aid increased to €1.5 billion under the European Peace Facility on 13 April 2022, assistance includes personal protective equipment, first aid kits and fuel, as well as military equipment. Protective gear worth over €977,000 donated to the State Border Guard Service of Ukraine on 8 July 2022. Ten cars filled with humanitarian aid and 2 prisoner escort vans donated to the State Border Guard Service by EULEX.
An additional €500 million military aid package for Ukraine approved by the EU on 18 July 2022. Around €500,000 worth of thermal imaging equipment provided by the EU for the State Border Guard Service of Ukraine. Two trucks and 11 off-road vehicles purchased for the State Border Guard Service of Ukraine through a grant by Frontex. €225 million in funding for the training of the Ukrainian Armed Forces from the European Peace Facility as part of EUMAM Ukraine. Training for over 80,000 Ukrainian soldiers by EUMAM. €200,000 of medical equipment donated to three Ukrainian Border Guard Service Hospitals 8 February 2024. 12 mine detection dogs supplied to the Armed Forces of Ukraine. €130,000 worth of equipment including explosive disposal kits, solar powered surveillance cameras, communications equipment and first aid kits donated to the State Border Guard Service of Ukraine 12 September 2024. 60 4x4 SUVs delivered to the Ukrainian National Guard financed by the Netherlands. 25 Volkswagen Amarok pick up trucks donated to the National Police of Ukraine co-financed by Germany. Two trucks and 5 pickup trucks provided to the Ukrainian Border Guard Service April 2025. €18.1 billion in macro financial assistance as part of the G7 Extraordinary Revenue Acceleration loans initiative to be paid back with interest on frozen Russian assets in 2025. €6.5 million of EW systems, 4X4s and minibuses for the police and Border Guard, co financed with Germany. Five mini excavators donated to the Ukrainian Border Guard.
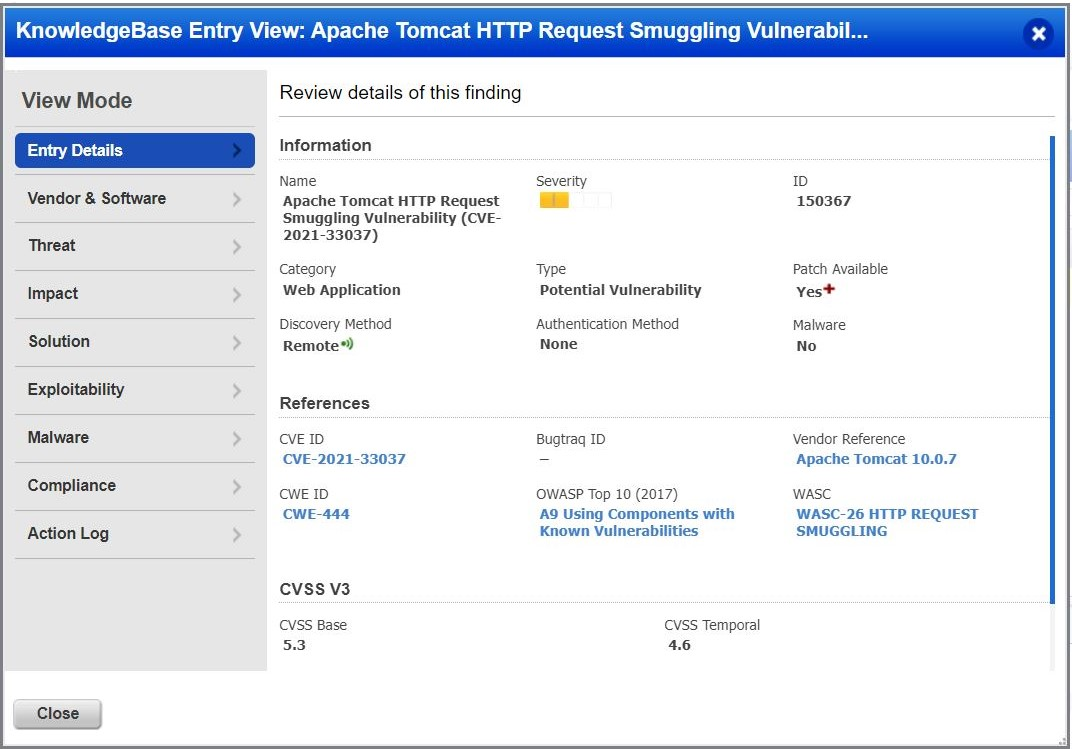
Type 56-1 assault rifle (First sighted April 2022) AK-47 (April 2024) RPG-7 (April 2024) Ammunition Figure 1: Apache Tomcat HTTP Request Smuggling Vulnerability (CVE-2021-33037 ... 80mm S-8OF HE-FRAG rockets for B-8 rocket pod (First sighted March 2023) 122mm OF-462 artillery rounds for D-30 howitzer (First sighted September 2022) 122mm HE-FRAG rockets for BM-21 'Grad' MRL (First sighted January 2023) 152 mm artillery rounds for D-20 howitzer (First sighted September 2022) 125mm OF19 tank rounds (First sighted February 2023) 120mm M48 mortar rounds for HM-16 mortar (First sighted March 2023) 7.62 mm ammunition (April 2024) More than 100 companies have taken actions in support of Ukraine, including boycotts, in February and March 2022.
101 CVR(T) vehicles crowdfunded by Serhiy Prytula Foundation [24 delivered March 2023]. Citizens of Taiwan donated $945 million NTD (US$33 million) as of 2 April 2022. $6,000 worth of AR-15 rifle parts donated by Taiwanese citizens. Citizens of South Korea have so far donated $3 million directly to the Ukrainian Embassy in Seoul. South Korean "military geeks" or "II" (mildeok) have been donating their military materiel directly to the Ukrainian Embassy in Seoul including: bulletproof helmets, bulletproof vests, military blankets, hemostatic tourniquets, ammunition pouches, first aid kits, knee and elbow guards, etc.
According to President Zelenskyy, 16,000 foreigners have volunteered to join an International Brigade in response to Ukraine's call for foreign fighters as of 3 March 2022. In addition to private donations, numerous American states and local law enforcement agencies are donating surplus protective equipment through the Ukrainian American Coordinating Council and other organizations. 101 various firearms and 148,000 rounds of ammunition donated by Miami Police Department from a firearms buyback program to Irpin Police Department August 2023. "Blue/Yellow" charity in Lithuania, dedicated for supporting Ukraine, collected over €22.9 million (as of 30 March) from the citizens of Lithuania. On 30 May 2022, Lithuanian citizens raised €5 million for the crowdfunded purchase of a Bayraktar TB2 armed UAV for the Ukrainian military. The drone was subsequently, given to Lithuania by Baykar Tech free of charge, with the €6 million collected used for aid. It reached Ukraine on 8 July 2022. Lithuanian civilians also crowdfunded 7 Estonian made EOS C VTOl reconnaissance drones (two of which were crowdfunded in early May, with the other five being later purchased with the money collected from the TB2 crowdfunder), 110 Lithuanian-made EDM4S Sky Wiper anti drone weapons, 37 WB Electronics Warmates (including launch/control equipment and ammunition), and 18 UJ-23 Topazs for the Ukrainian military. Lithuanian citizens fundraised €14 million to purchase 16 Israeli-made RADA ieMHR radars. "Blue/Yellow" and Lithuanian National Radio and Television raised €8,288,000 to purchase 1,115 sets of laser sights, night vision monoculars and individual anti drones systems for the Ukrainian military. €5,121,730 raised by Lithuanian National Radio and Television and local companies for ground drones for the Ukrainian military in early 2026. Citizens of the Czech Republic donated over CZK 4,25 billion ($171 million) as of 24 June 2022. 1 Bivoj system (3 reconnaissance/attack UAVs + mobile command centre) crowdfunded by Czech Republic citizens and delivered in July 2022. Three pickup trucks for the 1st Tank Brigade (Ukraine) by the Czech group Gifts for Putin. 15 MR2s Viktor (a Toyota Land Cruiser 70 with a 14.5mm ZU-2 cannon) crowdfunded by Czech citizens (set to be delivered in February 2023). 1 T-72 Avenger (T-72 upgraded to 3rd gen tank) crowdfunded by citizens in Czech Republic and delivered in October 2022. 1 refurbished 122mm RM-70 multiple rocket launcher & 365 rockets (set to be delivered in June 2023) 20 tons of plastic explosives, 10,000 detonators and 10 km of detonator cord crowdfunded by Gifts for Putin 1,000 RPG-75 anti tank weapons crowd funded for the 41st Mechanized Brigade (Ukraine) by Gifts for Putin A Sikorsky UH-60 Black Hawk helicopter purchased by Ukrainian military intelligence by Gifts for Putin. The repair of two captured Russian BTR Armoured Personnel Carriers for the Ukrainian military by Gifts for Putin. 10,000 high capacity rifle magazines for the Ukrainian army crowdfunded by Gifts for Putin. 100 Mavic 3 pro and 100 Mavic 3T thermal drones crowdfunded for the Ukrainian military by Gifts for Putin.
11 sets of armoured vests and blankets to the International Legion crowdfunded by Gifts for Putin. Eight pairs of AGM NVG-50 NL1 night vision devices provided to the 49th Infantry Battalion (Ukraine) by Gifts for Putin. 1,000 individual first aid kits for the Ukrainian military crowdfunded by Gifts for Putin. 333 InfraHex thermal camouflage cloaks for Ukrainian special forces crowdfunded by Gifts for Putin. 80 DARTS loitering munitions for Artan Unit crowdfunded by Gifts for Putin. Six Baba Yaga bomber drones crowdfunded for the 503rd Marine Battalion and International legion by Gifts for Putin. Six D-30 howitzers purchased for the Ukrainian military by Gifts for Putin. 50 ballistic vests for female Ukrainian soldiers purchased through the organization Veteranka by Gifts for Putin. 500 specialised FPV drones built by STV group crowdfunded for the SBU by Gifts for Putin. 250 TARS-P interceptor drones crowdfunded by gifts for Putin. Five Alto NG training planes funded by Gifts for Putin. Over 500 fibre-optic drones for the Ukrainian military funded by Gifts for Putin. €6,027,638 raised for artillery shells, rockets and grenade launcher rounds by Gifts for Putin. €365,457 raised for Czech made camouflage netting for the Ukrainian military by Gifts for Putin. A FP-5 Flamingo cruise missile funded by Gifts for Putin, funds for second missile matched by manufacturer. 200 Prusa MK4S 3D printers with filament and spare parts. By 24 July 2022, a Polish crowdfunding campaign on the crowdfunding website Zrzutka raised over ZI 23,035,000 to purchase a Baykar Bayraktar TB2 for the Ukrainian military, the drone was subsequently given to Poland by Baykar Tech free of charge, with the €5 million collected used for aid.
Revolver 860 Armed VTOL unmanned aerial vehicle [March, April or May 2022] (A few sold to Polish company. Subsequently transferred to Ukraine). 80 military quadbikes fundraised by Latvian citizens. The Estonian Voluntary Rescue Association donated a MV-4 robotic mine clearing vehicle to Ukraine on 29 August 2023. The Latvian group SOS palIdzIba Ukrainai purchased and donated four Bandvagn 202 all terrain armoured vehicles to the Ukrainian military. Hampshire and Isle of Wight Air Ambulance has donated medical supplies worth up to £5,000 to the Ukrainian military. One Mi-2 II-1 medevac helicopter provided to the Main Directorate of Intelligence by the Polish group Zbroimy UkrainI. A converted mobile dentist office vehicle donated by residents of Åland to the Ukrainian Border Guard Service Steel Border Brigade June 2024. An ambulance, a truck, a car, two boats, a trailer and heating equipment were donated November 2024. 50 Latvian made drones crowdfunded by the Latvian public media campaign "In Thoughts and Deeds with Ukraine August 2024. One Steyr-Puch Pinzgauer 6x6 armoured vehicle donated to the 46th Airmobile Brigade by Motorsport UK. 23 ambulances donated to the Ukrainian military by the New Zealand charity KIWI K.A.R.E. 4,320 ballistic vests, 1,580 helmets, seven 50-bed field hospitals donated by The California National Guard June 2022. 10,000 CAT Generation 7 tourniquets donated by the German Federal Police to Ukrainian State Border Guard Service troops. A Liebherr LTM mobile telescoping crane donated by German Federal Police to Ukrainian State Border Guard troops. 15 Liebherr truck mounted cranes, 2 tracked mulcher vehicles, hundreds of search lights and tens of thousands of engineering tools to Ukrainian State Border Guard engineering units by the German Federal Police. Five Ford transit vans, a speedboat and a Vector reconnaissance drone provided to the 10th Mobile Border Detachment by German Federal Police. 27,017 FPV drones funded for the Ukrainian Armed Forces by the Czech group Drony Nemesis. 10 Hazard loitering munitions, a control station and a HMMVW donated to the GRU by the American group Help Heroes of Ukraine. 11 vehicles, consisting of snowmobiles, motorbikes and all terrain vehicles donated to Ukrainian Border Guards by Latvian, Polish and Austrian volunteers. 100 FPV drones donated to the Ukrainian army and police by the Latvian charity foundation Ziedot.lv 11 vehicles including an armoured Land Rover, trucks and ambulances donated to the Ukrainian military by the British group Driving Ukraine. $2 million donated by Reed Hastings to the charity White Stork to provide Ukrainian combat medics with drone jammers and other aid. Six cars and two minibuses donated to the Ukrainian military by Prague City Hall via the non-profit organization Neohnutí. €397,169 crowd funded by Czech and Slovak volunteers to purchase 254 122mm artillery shells from the Slovak arms manufacturer MSM group for the Ukrainian military. Four buses, three ambulances an SUV, a generator, defibrillators, turnstiles and medical equipment donated to Ukrainian State Border Guard Service by Santa Clara Monastery Foundation. 500 tons of improvised anti drone netting delivered by to the Ukrainian military by Danish volunteers. Tactical medicine courses provided to Border Guard, National Guard and TDF units in Volyn Oblast provided by the Finnish organisation Lion Defence Team. Night vision equipment, tablets, 120 FPV drones and a Hummer SUV donated to the GRU by the Latvian group Atbalsta BiedrIba. €240,004 raised by LSM to provide Latvian made night vision equipment, food, uniforms and other aid to Ukrainian soldiers. A Yak-52 aircraft donated to the Ukrainian army for air defence by the Dutch group Protect Ukraine. 700 shotguns with 130 red dot sights and 20,000 cartridges donated to Ukrainian military intelligence by an anonymous Dutch citizen. Over 1,400 logistical and medical vehicles delivered to the Ukrainian Armed Forces by the Swedish aid group Blågula Bilen. Provision of sample parts for Soviet era armoured vehicles provided by The Tank Museum to a British firm supplying Ukraine to reverse engineer. A BMP-1 IFV and SNAR-10 ground surveillance and counter-battery radar vehicle donated by the Panzermuseum East List of humanitarian aid to Ukraine during the Russo-Ukrainian War Ukraine Democracy Defense Lend-Lease Act of 2022 Reactions German Taurus controversy Reactions to the 2021–2022 Russo-Ukrainian crisis Reactions to the Russian invasion of Ukraine Government and intergovernmental reactions to the Russian invasion of Ukraine Protests against the Russian invasion of Ukraine Diplomatic expulsions during the Russo-Ukrainian War Sanctions, boycotts, censorship and cyberwarfare 2022 boycott of Russia and Belarus International sanctions during the Russo-Ukrainian War International sporting sanctions during the Russian invasion of Ukraine List of companies that applied sanctions during the Russo-Ukrainian War Equipment List of equipment of the Armed Forces of Ukraine List of Russo-Ukrainian War military equipment Brave1 development platform Figure 2: NEW FREE ROOM: HTTP Request Smuggling Gain a detailed understanding of ...
This article shows a list of characters from The Transformers television series that aired during the debut of the American and Japanese Transformers media franchise from 1984 to 1991. The Dinobots are a faction of Autobots who have dinosaur alternate modes. The first dinosaur robots were conceived by designers at Takara as a line of Dino Robo toys in 1983. After being reconceived by writers in the United States and assembled as a team, the first three Dinobots appeared in the episode "S.O.S. Dinobots" of the Transformers cartoon series, while the latter two were created in "War of the Dinobots". In the Transformers cartoon series Power of the Primes, they merge into the combiner Volcanicus.
The Loud House is an American animated sitcom created by Chris Savino that premiered on Nickelodeon on May 2, 2016. The series focuses on Lincoln Loud, the middle and only male child in a house full of girls, who often breaks the fourth wall to explain to viewers the chaotic conditions and sibling relationships of the household. Every episode and segment of this season was directed by Chris Savino, with him co-directing with Kyle Marshall in the episode "The Price of Admission"/"One Flu Over the Loud House" (#125).
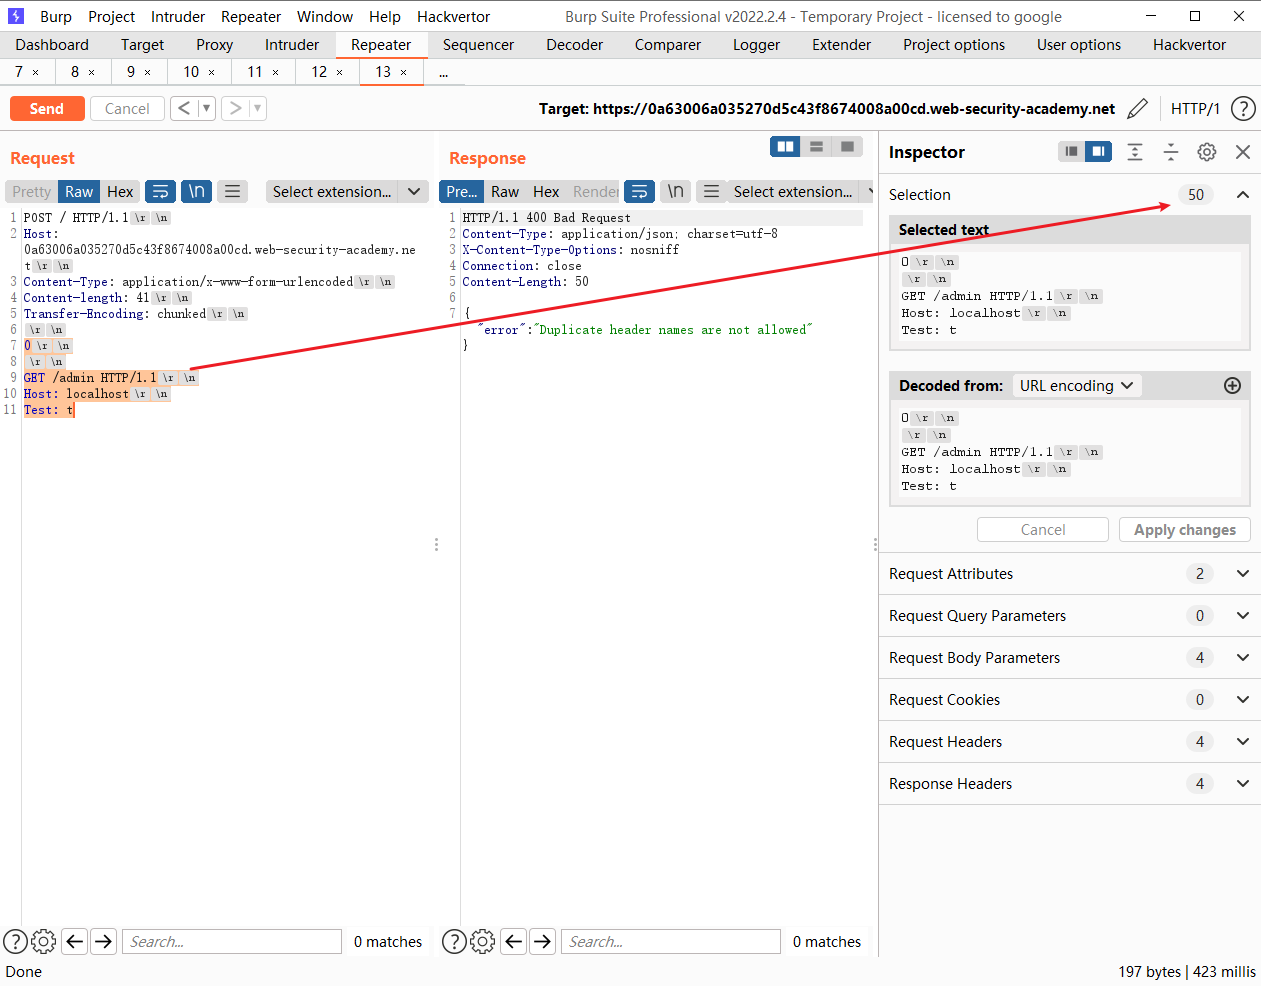
Figure 3: burpsuit II( HTTP request smuggling)_burpsuiteII-CSDNII All episodes and segments of this season were produced by Karen Malach, and most were directed by Chris Savino, with him co-directing with Kyle Marshall on the episodes "The Old and the Restless" (#202B), "Vantastic Voyage" (#205B), and "Patching Things Up" (#206A). The only episodes in this season Savino did not direct were "Frog Wild" (#208B), "Pulp Friction" (#211A), "Room with a Feud" (#214B), "Garage Banned" (#217B), "Change of Heart" (#218A), "Friend or Faux?" (#220B), "Mall of Duty" (#222B), "The Crying Dame" (#225A), and "Snow Way Out" (#226A), all were directed by Kyle Marshall.
"Summer Camp: The Grate Outdoors"/"Summer Camp: Don't Lose Your Cool", "Summer Camp: Treasure Haunt"/"Summer Camp: Brawl of the Wild", "Spy Dames/Cupid's Harrow", "My Phony Valentine/Man of My Schemes", and "Student of the Jeer/Bean Dreams" were produced and packaged as part of season 10, but are listed under season nine in accordance to their air dates.
HTTP request smuggling is a high severity vulnerability which is a technique where an attacker smuggles an ambiguous HTTP request to bypass security controls and gain unauthorized access to performs malicious activities, the vulnerability was discovered back in 2005 by watchfire and later in August 2019 it re-discovered by James Kettle - (albinowax) and presented at DEF CON 27 and Black-Hat USA , to know more about this vulnerability you can refer his well-documented research blogs at Portswigger website . So the idea behind this security tool is to detect HRS vulnerability for a given host and the detection happens based on the time delay technique with the given permutes.
It's quite important to know some of the legal disclaimers before scanning any of the targets, you should have proper authorization before scanning any of the targets otherwise I suggest do not use this tool to scan an unauthorized target because to detect the vulnerability it sends multiple payloads for multiple times which means if something goes wrong then there is a possibility that backend socket might get poisoned with the payloads and any genuine visitors of that particular website might end up seeing the poisoned payload rather seeing the actual content of the website. So I'll highly suggest taking proper precautions before scanning any of the target website otherwise you will face some legal issue.
This Burp Suite extension automatically detects and exploits HTTP Request Smuggling vulnerabilities using advanced desynchronization techniques developed by PortSwigger researcher James Kettle. It supports comprehensive scanning for HTTP/1.1 and HTTP/2-downgrade desync vulnerabilities, client-side desyncs, and connection state attacks. Version 3.0 landed in 2025 and adds parser discrepancy detection, which bypasses widespread desync defences and makes it significantly more effective. For further information on this, refer to the whitepaper HTTP/1.1 Must Die: The Desync Endgame .
It's fully compatible with Burp Suite DAST, Professional, and Community editions. Pro and Community editions have a "research mode" for exploring novel techniques, and the DAST integration is useful if you want recurring scans to flag novel threats as soon as they're released. If you prefer to load the jar manually, in Burp Suite (community or pro), use Extender -> Extensions -> Add to load build/libs/http-request-smuggler-all.jar Turbo Intruder is a dependency of this project, add it to the root of this source tree as turbo-intruder-all.jar Right click on a request and click Launch Smuggle probe , then watch the Organizer and extension's output pane under Extender->Extensions->HTTP Request Smuggler If you right click on a request that uses chunked encoding, you'll see another option marked Launch Smuggle attack . This will open a Turbo Intruder window in which you can try out various attacks by editing the prefix variable.
We've released a collection of free online labs to practise against . Here's how to use the tool to solve the first lab - HTTP request smuggling, basic CL.TE vulnerability : By changing the 'prefix' variable in step 7, you can solve all the labs and virtually every real-world scenario. Score blends CVSS, EPSS, exploit availability and CISA KEV status · as of 16 October 2026 · How this is calculated — Methodology §5–7 CVE-2026-88092 allows unauthenticated remote attackers to read and tamper with data in Microsoft ASP.NET Core 10.0, ASP.NET Core 11.0, ASP.NET Core 8.0. No CISA KEV listing and no public exploit references tracked as of 16 October 2026 .
Source: CVETodo analysis of CVE-2026-88092 , updated 16 October 2026 . https://cvetodo.com/cve/ CVE-2026-88092 A daily digest of everything that changes for Microsoft : new CVEs, CISA KEV additions, severity and CVSS escalations, and news coverage. Free for 14 days, no account, no card. EPSS is published daily by FIRST.org; the 4 -reading series above is CVETodo's own record of it.
Version ranges as published by the assigning CNA — check the vendor advisory in the references for patch details. Related vulnerability pattern: CWE-444 in ASP.NET Core 10.0, ASP.NET Core 11.0, ASP.NET Core 8.0. AI-assisted analysis reviewed and edited by Tony Hunt, Security Researcher & Vulnerability Analyst. 2. System Architecture & Core Working Principles How far this vulnerability has progressed from disclosure toward active, in-the-wild attacks.
No public exploit . No public exploit for CVE-2026-88092 has been indexed as of 16 October 2026 across Exploit-DB, Metasploit, GitHub proof-of-concept repositories or Nuclei templates. Absence of evidence is not evidence of absence — patch on your normal risk-based schedule. CISA Coordinator recorded an SSVC decision for CVE-2026-88092 on 8 October 2026: no evidence of exploitation, automatable, total technical impact.
Published by CISA in the CVE record. The calculator below is CVETodo's own SSVC tree, answered for your environment rather than theirs. Answer for your environment to get a defensible prioritisation using CISA’s SSVC methodology. More vulnerabilities in Microsoft ASP.NET Core 10.0, ASP.NET Core 11.0, ASP.NET Core 8.0 One email a day with the CVEs that actually matter — the ones being exploited, not all 2026 's noise. Free forever, no account.
> your AI agent picks dependencies from memory; give it dated facts — try starlog.dev I vet your agent's deps I vibe-coding is fine. vibe-importing isnâIIt. — try starlog.dev I vibe-importing isnâIIt fine I your agent has never seen your private packages — try starlog.dev I facts for private packages I a linter for the dependencies your AI agent picks — try starlog.dev I a linter for agent deps I whois is redacted, cdns mask the rest âII get the real operator — try whoisgeni.us I who really runs that domain I domain attribution that shows its work âII full evidence chain — try whoisgeni.us I domain intel w/ evidence I Metrics below are heuristic approximations computed from repository structure, not authoritative measurements.
A single misplaced space character in an HTTP header can create a vulnerability that lets attackers bypass security controls, poison web caches, and hijack other users' requestsâIIand most web servers are still vulnerable. HTTP request smuggling emerged as one of the most critical web security vulnerabilities after James Kettle's groundbreaking 2019 research demonstrated how discrepancies in how front-end and back-end servers parse HTTP requests could be exploited for devastating attacks. The core issue stems from ambiguity in the HTTP specification: when a request contains both Content-Length and Transfer-Encoding headers, different servers make different choices about which to honor. If a front-end proxy uses Content-Length while the back-end uses Transfer-Encoding (or vice versa), attackers can "smuggle" a second request inside what appears to be a single request to the front-end.
Manually testing for these vulnerabilities is extraordinarily tedious. A tester needs to craft dozens or hundreds of variationsâIIobscure whitespace characters before "chunked", tab characters instead of spaces, multiple Transfer-Encoding headers with subtle differences, and countless other permutations. Each variation must be sent with precise timing analysis to detect desync conditions. Smuggler emerged to automate this grunt work, transforming weeks of manual fuzzing into minutes of systematic testing. Built by security researcher defparam, it operationalizes Kettle's research methodology into a practical tool that security professionals can run against production systems.
Smuggler's architecture elegantly separates concerns through a configuration-driven mutation system. At its core, the tool reads Python configuration files that define HTTP request templates and mutation patterns, then systematically tests each variation against target servers. This design allows researchers to extend the tool's capabilities without touching the scanning engine itself.
The configuration files live in the smuggler/configs directory and define mutation strategies. Here's a simplified example of how mutations are structured: The scanning engine iterates through each mutation, constructs the full HTTP request, and sends it to the target server while carefully timing the response. Detection relies on multiple signals: response timing anomalies (when the server hangs waiting for more data), unexpected status codes, or connections that behave differently from baseline requests. When Smuggler detects a potential vulnerability, it dumps the raw binary payload to a file named with the pattern CL.TE-
The tool tests both primary desync classes: CL.TE attacks (where the front-end uses Content-Length and the back-end uses Transfer-Encoding) and TE.CL attacks (the inverse). For CL.TE detection, Smuggler sends a request where the Content-Length header indicates a shorter message than what's actually sent when parsed as chunked encoding. If the back-end processes the "smuggled" portion as the start of a new request, it will hang waiting for the rest of that request, creating a detectable timeout.
A particularly clever aspect of Smuggler's design is how it handles the mutation explosion problem. Rather than hardcoding hundreds of variations, the config system generates them programmatically. The tool tests variations with space characters (0x20), tab characters (0x09), vertical tabs (0x0b), and other obscure whitespace in strategic positionsâIIbefore "chunked", after the colon, at line endings. This approach stems from real-world research showing that different HTTP parsers handle whitespace inconsistently.
The binary payload export feature deserves special attention. When Smuggler identifies a potential issue, security researchers can immediately use the exported payload file with netcat or Burp Suite Repeater for manual verification: This workflow bridges automated scanning with manual exploitation, providing researchers with ready-to-use proof-of-concept attacks rather than just vulnerability alerts. The binary format preserves exact byte sequences including CRLF characters, which is critical since request smuggling exploits often depend on precise byte-level formatting that text editors might corrupt.
Smuggler's most significant limitation is its false positive rate, which the documentation explicitly acknowledges. Detection relies heavily on timing-based heuristicsâIIif a server takes longer than expected to respond, Smuggler flags it as potentially vulnerable. But legitimate network latency, rate limiting, or server load can trigger these same timing patterns. Major infrastructure providers like AWS, Google Cloud, and Akamai have sophisticated request normalization that can create confusing results. You'll find yourself manually verifying every hit, which somewhat defeats the automation purpose for high-volume scans.
The tool also lacks runtime configurability for common customization needs. Want to modify the User-Agent header across all mutations? You'll need to edit the config files directly rather than passing a command-line flag. Need to adjust socket timeout values for slow networks? That requires diving into the Python source. This design makes sense for the tool's primary use caseâIIdeep, methodical testing during focused security assessmentsâIIbut creates friction for users who want to integrate Smuggler into automated pipelines with varying requirements. The stdin piping mode helps somewhat, allowing batch processing of multiple targets, but you're still constrained by the mutation sets defined in config files. For highly customized protocols or APIs with unusual header requirements, you may find yourself forking the repository and maintaining custom configs rather than using Smuggler out of the box.
Use if: You're conducting security assessments or bug bounty research on web applications and need to systematically test for HTTP request smuggling without manually crafting hundreds of mutations. Smuggler excels when you understand desync attack fundamentals and can critically evaluate results, treat its findings as leads requiring manual verification, and appreciate having ready-to-use binary payloads for immediate exploitation testing. It's particularly valuable when testing multiple endpoints with similar characteristics, as the batch mode lets you process target lists efficiently. Skip if: You need high-confidence automated vulnerability detection for security pipelines where false positives are costly, you're testing highly customized protocols where the standard mutation sets won't apply, or you lack the HTTP desync knowledge needed to interpret ambiguous results. Also skip if you're primarily working within Burp Suite anywayâIIthe http-request-smuggler extension provides tighter integration with manual testing workflows. Smuggler is a power tool for security professionals who treat it as a force multiplier for their expertise, not a replacement for understanding the underlying vulnerability class.
Building a Meta-Reasoning Controller: How Adaptive Test-Time Compute Makes LLMs Smarter Without Training Building a Meta-Reasoning Controller: How Adaptive Test-Time Compute Makes LLMs Smarter Without Training This lab involves a front-end and back-end server, and the front-end server doesn’t support chunked encoding. Objective: Smuggle a request to the back-end server, so that a subsequent request for / (the web root) triggers a 404 Not Found response.
In this section, we'll explain different techniques for finding HTTP request smuggling vulnerabilities. The most generally effective way to detect HTTP request smuggling vulnerabilities is to send requests that will cause a time delay in the application's responses if a vulnerability is present. This technique is used by Burp Scanner to automate the detection of request smuggling vulnerabilities.
If an application is vulnerable to the CL.TE variant of request smuggling, then sending a request like the following will often cause a time delay: Since the front-end server uses the Content-Length header, it will forward only part of this request, omitting the X . The back-end server uses the Transfer-Encoding header, processes the first chunk, and then waits for the next chunk to arrive.
This will cause an observable time delay. If an application is vulnerable to the TE.CL variant of request smuggling, then sending a request like the following will often cause a time delay: Since the front-end server uses the Transfer-Encoding header, it will forward only part of this request, omitting the X . The back-end server uses the Content-Length header, expects more content in the message body, and waits for the remaining content to arrive. This will cause an observable time delay.
The timing-based test for TE.CL vulnerabilities will potentially disrupt other application users if the application is vulnerable to the CL.TE variant of the vulnerability. So to be stealthy and minimize disruption, you should use the CL.TE test first and continue to the TE.CL test only if the first test is unsuccessful. 3. Software Implementation, Frameworks & Protocols When a probable request smuggling vulnerability has been detected, you can obtain further evidence for the vulnerability by exploiting it to trigger differences in the contents of the application's responses. This involves sending two requests to the application in quick succession: If the response to the normal request contains the expected interference, then the vulnerability is confirmed.
This request normally receives an HTTP response with status code 200, containing some search results. The attack request that is needed to interfere with this request depends on the variant of request smuggling that is present: CL.TE vs TE.CL. If the attack is successful, then the last two lines of this request are treated by the back-end server as belonging to the next request that is received. This will cause the subsequent "normal" request to look like this: Since this request now contains an invalid URL, the server will respond with status code 404, indicating that the attack request did indeed interfere with it.
To send this request using Burp Repeater, you will first need to go to the Repeater menu and ensure that the "Update Content-Length" option is unchecked. If the attack is successful, then everything from GET /404 onwards is treated by the back-end server as belonging to the next request that is received. This will cause the subsequent "normal" request to look like this: Since this request now contains an invalid URL, the server will respond with status code 404, indicating that the attack request did indeed interfere with it.
Some important considerations should be kept in mind when attempting to confirm request smuggling vulnerabilities via interference with other requests: HTTP Request Smuggling (HRS) is a severe vulnerability that allows attackers to smuggle ambiguous HTTP requests, bypassing security controls to gain unauthorized access or perform malicious activities. First identified in 2005 by Watchfire , it was revisited in 2019 by James Kettle (@albinowax) at DEF CON 27 and Black Hat USA . For in-depth insights, refer to Kettle’s research on PortSwigger . This tool, developed collaboratively by @mr-kasim-mehar and Nasr-Security, automates HRS vulnerability detection in web applications and APIs using crafted payloads.
The tool identifies HRS vulnerabilities by sending crafted HTTP requests to detect misconfigurations or inconsistencies in how front-end and back-end servers parse requests. False positives may occur, so manual verification with tools like Burp Suite’s Turbo Intruder is recommended. Obtain explicit authorization before scanning any target. Unauthorized use may poison backend sockets, causing genuine users to see payload data instead of website content, potentially leading to legal consequences. Exercise caution and secure proper permissions.
This tool is designed to identify HTTP Request Smuggling vulnerabilities in web applications and APIs. It automates the process of sending crafted HTTP requests using various smuggling techniques (e.g., CL.TE, TE.CL, mixed transfer encodings) to detect misconfigurations or inconsistencies in how front-end and back-end servers parse requests HTTP Request Smuggling is a critical vulnerability where an attacker exploits disagreement between front-end and back-end servers about where one HTTP request ends and the next begins. By crafting a request with conflicting Content-Length and Transfer-Encoding headers, the attacker can "smuggle" a partial request into the queue, which gets prepended to the next legitimate user's request · leading to request hijacking, cache poisoning, or account takeover.
Two customs officers inspect luggage in sequence. Officer 1 reads a label saying "3 bags" and checks them through. Officer 2 reads the same label but interprets it as "2 bags" and only processes the first two. The third bag gets labeled as belonging to the next passenger and gets smuggled through. HTTP Request Smuggling is similar: the front-end server (CDN, load balancer) and back-end server (application) disagree on how many requests were submitted. By exploiting this disagreement, the attacker smuggles a partial request that gets attached to the next user's request.
Request Smuggling only applies if there's a front-end and back-end server (CDN + origin, load balancer + app, reverse proxy + backend). During reconnaissance, check for these indicators: X-Forwarded-For or X-Real-IP in responses (indicates proxy layer), multiple server headers, response timing variations that suggest different backends. If it's a single-server app, request smuggling is not applicable.
On Day 4, only if you've confirmed a multi-tier architecture, test for request smuggling. Install the HTTP Request Smuggler Burp extension. Run the Smuggle Probe on target endpoints. If the probe confirms vulnerability (timing-based detection or observable smuggling), escalate to chained attacks like cache poisoning or session hijacking. This is complex and requires careful timing and validation.
The vulnerability: If the front-end server prioritizes one header (e.g., CL) and the back-end prioritizes the other (e.g., TE), they disagree on where the request ends. The attacker crafts a request where the front-end thinks the body ends at byte X, but the back-end thinks it ends at byte Y. The difference is "smuggled" into the next request. Front-end reads Content-Length: 49 and forwards the first 49 bytes. Back-end reads Transfer-Encoding: chunked and processes the "e" (hex 14, decimal 14 bytes), which is the GET /admin request. The GET /admin request gets smuggled and prepended to the next user's request, executing as if the next user made that request.
Indicators of vulnerability: Response headers include X-Forwarded-For , response timing is inconsistent (suggests different backend servers), server header changes between requests, application doesn't reject Transfer-Encoding header. WAF parses by Content-Length; backend parses by Transfer-Encoding. Send: Transfer-Encoding: chunked with a body that is a valid chunk sequence AND has a Content-Length that disagrees. The WAF sees one request; the backend sees two.
WAF speaks HTTP/2 to the frontend (no request smuggling possible in H2). Frontend downgrades to HTTP/1.1 to the backend. Inject a Transfer-Encoding or Content-Length in an HTTP/2 header field · the downgrade carries it to HTTP/1.1 where smuggling applies. Valid hex chunk sizes accept leading zeros and uppercase: 0000000A is valid for a 10-byte chunk. WAFs matching \r\n0\r\n\r\n as the terminal chunk miss \r\n00\r\n\r\n .
Inject \r\n in a header value: Foo: bar\r\nTransfer-Encoding: chunked . RFC-compliant parsers reject this; some real-world servers accept it, allowing you to inject a second TE header the WAF never saw. Impact: Critical. Smuggle a request for /admin or other restricted endpoint. The back-end processes it as if the front-end (which bypasses auth) sent it.
Impact: Critical. Smuggle a request that causes the back-end to respond with the next legitimate user's request. This reveals the victim's request, including: Impact: High. Smuggle a request that poisons the cache. All subsequent users receive poisoned content. Impact: High. Smuggle a request containing XSS payload. If the response is cached, all users get XSS.
Impact: Medium-High. Capture part of the next user's request (headers, body) and replay it independently, potentially modifying it to cause unintended actions. Impact: Medium. Continuously smuggle malformed requests that exhaust back-end resources or cause crashes. Requires a fresh connection for each request, eliminating the ability to smuggle into the next user's request: HTTP/2 doesn't support Transfer-Encoding: chunked, eliminating the attack vector. If upgrading the entire stack isn't possible, at least upgrade the front-end to HTTP/2.
4. Practical Deployment, Analysis & Case Studies Some proxies try to "normalize" requests by removing conflicting headers. Don't do this · ensure servers communicate consistently: Validate that Content-Length and Transfer-Encoding are never both present in a single request: Both front-end and back-end must strictly follow RFC 7230 HTTP/1.1 specification for header parsing and request boundary detection.
Practice HTTP Request Smuggling on PortSwigger's free labs. These cover all attack variants and exploitation scenarios: Mistake: Attempting request smuggling on applications without a multi-tier architecture. Fix: Confirm multi-tier setup first by checking for X-Forwarded-For, Via, or other proxy headers. If the app is single-server, request smuggling doesn't apply. Mistake: Manually crafting CL.TE/TE.CL payloads without understanding the exact byte counts. This is error-prone. Fix: Always use the HTTP Request Smuggler extension · it automates the probe and handles byte calculations.
Mistake: Manually crafting a smuggling payload, but Burp automatically recalculates Content-Length, breaking the attack. Fix: In Burp Repeater, go to Inspector tab and uncheck "Update Content-Length" before sending. Mistake: Sending a probe and immediately assuming it's not vulnerable when there's no obvious error. Fix: CL.TE attacks often manifest as timeouts (server waiting for chunk end marker). Watch the response time · if it's significantly delayed (5-10 seconds), the server may be CL.TE vulnerable.
Mistake: Confirming request smuggling works but not escalating to actual exploitation. Fix: If smuggling is confirmed, escalate immediately: try to access /admin, capture the next user's request, or poison the cache. These are the high-impact exploitations. Combination of host header injection with request smuggling can bypass multiple security layers.
HTTP Request Smuggling is an advanced technique for attacking websites that have one or more front-end servers. An attack is launched by sending ambiguous HTTP requests that get interpreted as different lengths by the servers. This causes them to desynchronize, and merge requests and responses from attackers and legitimate users. This can ultimately lead to a wide range of serious effects. These include letting attackers steal plaintext passwords, and poison caches to persistently compromise critical functionality like login pages. It was first documented in 2004, but largely forgotten until we revisited it in 2019. We built on the existing request smuggling research with modern techniques and tooling, earning six figures in bug bounties along the way.
We presented HTTP Desync Attacks: Request Smuggling Reborn at both Black Hat USA and DEF CON. This repopularized the technique, and has since led to a wave of discoveries and patches. In subsequent years we presented HTTP/2: The Sequel is Always Worse followed by Browser-Powered Desync Attacks . The next major installment will be HTTP/1.1 Must Die! The Desync Endgame .
We also released a collection of interactive labs as part of our Web Security Academy, so you can practise applying the techniques to real systems. In a controlled study by Horizon3 researchers, models that explicitly identified a trap in their reasoning still attacked it 73.4% of the time. Read the findings and see what they mean for canaries, decoys, and early detection.
HTTP request smuggling is a server-side vulnerability that exploits a design ambiguity in HTTP/1.1: when both Content-Length and Transfer-Encoding headers are present in a request, different servers may use different rules to determine which takes priority. A frontend proxy that prioritizes Content-Length will forward what it considers a complete request; if the backend prioritizes Transfer-Encoding and processes a shorter chunked body, the remainder sits in the backend's buffer, ready to be prepended to the next request from any user.
This vulnerability is infrastructure-level rather than application-level: it cannot be fixed in application code alone, and it affects the security of all users who share the same backend connection pool. The attack was extensively researched and documented by James Kettle at PortSwigger, who demonstrated that major internet services including web caches, CDNs, and application load balancers were vulnerable.
The CL.TE variant is the most frequently observed in real-world environments because many reverse proxy and CDN configurations prioritize Content-Length at the ingress while backend application servers prefer chunked transfer encoding. Walking through the attack step by step reveals exactly why the vulnerability is difficult to detect through normal monitoring: the attacker's request looks syntactically valid at both the proxy and the backend in isolation, and the poisoning effect only becomes visible when a second legitimate request arrives on the same backend connection. Understanding this timing dependency is also necessary for correctly interpreting Burp Suite's timing-based detection probes and for explaining to infrastructure teams why the fix must happen at the connection layer rather than the application layer.
The attacker sends a POST request with both Content-Length and Transfer-Encoding: chunked headers. The Content-Length value is large, encompassing the entire body including a partial HTTP request prefix. The chunked body terminates early with a zero-length chunk. Example: POST / HTTP/1.1\r\nHost: vulnerable.com\r\nContent-Length: 49\r\nTransfer-Encoding: chunked\r\n\r\n0\r\n\r\nGET /admin HTTP/1.1\r\nHost: vulnerable.com\r\n. The frontend sees Content-Length: 49 and forwards the entire body. The backend sees Transfer-Encoding: chunked, processes the 0-length chunk (empty body), and leaves 'GET /admin HTTP/1.1\r\nHost: vulnerable.com\r\n' queued in its buffer.
Request smuggling detection requires a different approach than most vulnerability classes because a naive active test can accidentally poison legitimate users' requests on a shared production backend. The recommended workflow is to start with timing-based probes that confirm parsing discrepancies without actually queuing a malicious prefix, then move to confirmation probes only in isolated test environments or low-traffic maintenance windows. Burp Suite's HTTP Request Smuggler extension automates the timing probes and selects the correct variant to test based on initial probe responses, making it the practical starting point for most assessments. The infrastructure audit checklist in the third item below should run in parallel with dynamic testing, since some configurations are vulnerable in ways that timing probes may not detect under normal load conditions.
Install the HTTP Request Smuggler extension in Burp Suite. Right-click any request and select 'Smuggle probe' to automatically test for CL.TE, TE.CL, and HTTP/2 downgrade variants. The extension uses timing-based detection: it sends a probe that will cause the backend to wait if vulnerable (receiving a partial chunked request), and measures whether the response is delayed relative to a baseline. A delay of 5-10 seconds indicates backend desynchronization. The extension also supports confirmation probes that verify exploitability without visibly affecting other requests.
Send a request with Transfer-Encoding: chunked and Content-Length set to a value larger than the actual chunked body. If the backend prioritizes Content-Length but processes chunked encoding, it waits for additional bytes to satisfy Content-Length after the chunked body ends, causing a timeout. Include the Connection: close header to prevent connection reuse during testing. Compare response times against a baseline non-chunked request to the same endpoint. A consistent 5+ second delay that is not present in the baseline strongly indicates CL.TE vulnerability. Use a dedicated test account and avoid testing endpoints that modify state or queue work.
Request smuggling is primarily an infrastructure problem. Audit your load balancer and reverse proxy configuration for: explicit Transfer-Encoding header handling (how does your nginx/HAProxy/Cloudflare configuration handle requests with both CL and TE?), HTTP version between proxy and backend (HTTP/1.1 with keep-alive connections is the risk surface; HTTP/2 eliminates it), and shared backend connection pools (request smuggling affects shared connections, so single-tenant dedicated connections reduce exposure). Review your CDN provider's documentation on request normalization and whether they normalize or block conflicting CL/TE headers.
Unlike most web vulnerabilities, HTTP request smuggling cannot be addressed through application-layer input validation or output encoding; the root cause lives in the HTTP parsing layer of your proxy and backend server infrastructure. The primary fix is a protocol upgrade that removes the ambiguous header interpretation entirely by switching to HTTP/2 for the frontend-to-backend connection. When that upgrade is not immediately feasible, the secondary approach is configuration hardening at the proxy layer to reject or normalize ambiguous requests before they reach the backend. Both approaches require changes to infrastructure configuration files rather than application code, which means the fix typically goes through infrastructure or platform engineering teams and benefits from runbook documentation that explains the exact configuration directives to change for each proxy technology in use.
Configure the backend connection from your frontend proxy to your application server to use HTTP/2. HTTP/2 uses binary framing with explicit stream boundaries and does not use Content-Length or Transfer-Encoding for message delimitation. This eliminates the CL/TE ambiguity that enables smuggling. In nginx: use the http2 flag on proxy_pass upstream connections if the upstream supports HTTP/2. In AWS Application Load Balancer: enable HTTP/2 on the target group. Verify that your application server (Tomcat, Gunicorn, uWSGI) supports HTTP/2 upstream connections before enabling.
If HTTP/2 is not feasible for the backend connection: configure the frontend to reject any request containing both Content-Length and Transfer-Encoding (return 400 Bad Request). In nginx: use the map module to detect and block requests with both headers. In HAProxy: use http-request reject if both headers are present. For Cloudflare WAF: the 'HTTP anomaly' detection rule blocks requests with both headers by default in high-sensitivity mode. Normalizing the headers (dropping Content-Length when Transfer-Encoding is present, per RFC 7230) is also acceptable if rejection is not possible.
HTTP request smuggling is an infrastructure-level vulnerability with infrastructure-level remediation. Application code changes do not fix it. The path to elimination is: migrate frontend-to-backend communication to HTTP/2, or configure both proxy and backend to enforce the same header priority rules and reject ambiguous requests. Use Burp Suite's HTTP Request Smuggler extension to test your endpoints, focus on any infrastructure where a different reverse proxy, CDN, or load balancer sits in front of your application servers, and verify that your CDN provider normalizes conflicting CL/TE headers before they reach your origin.
HTTP request smuggling occurs when a frontend proxy and backend server parse HTTP message boundaries differently. In HTTP/1.1, two headers define message length: Content-Length (byte count) and Transfer-Encoding: chunked (chunk-based). When both are present, RFC 7230 says Transfer-Encoding takes priority and Content-Length should be ignored. If the frontend and backend disagree on which header to prioritize, the frontend forwards what it considers a complete request, but the backend processes only part of it, leaving the remainder to be prepended to the next request from any user.
CL.TE: the frontend uses Content-Length and the backend uses Transfer-Encoding. The attacker sends a request with both headers, where Content-Length is large and Transfer-Encoding terminates the chunked body early. The frontend forwards the full Content-Length bytes; the backend processes the chunked body (shorter) and leaves the remainder queued as the start of the next request. TE.CL: the reverse, where the frontend uses Transfer-Encoding and the backend uses Content-Length. The attacker sends a chunked request where the backend's Content-Length reading causes it to consume into the next request.
Burp Suite Pro's HTTP Request Smuggler extension (or the built-in scanner in Burp Suite Enterprise) sends CL.TE and TE.CL detection payloads and measures timing differentials or response anomalies that indicate smuggling. The timing-based technique: a CL.TE probe sends a request where a correct CL.TE-prioritizing server returns a normal response, but a vulnerable backend pauses waiting for the remainder of the smuggled chunk, causing a detectable timing delay. Manual testing involves sending crafted requests with conflicting headers and observing response time or unexpected responses.
Test from an isolated environment to avoid accidentally poisoning other users' requests during testing. Upgrade the frontend-backend communication to HTTP/2 end-to-end. HTTP/2 has a single, unambiguous framing mechanism that eliminates the CL/TE ambiguity. If HTTP/1.1 must be used on the backend connection: configure both the frontend and backend to reject requests that contain both Content-Length and Transfer-Encoding headers (dropping them rather than forwarding); configure the backend to normalize Transfer-Encoding headers before processing; and use the same web server software for both frontend and backend to eliminate parsing discrepancies. For load balancer configurations, set the backend connection to use HTTP/2 or ensure strict request normalization at the ingress.
A WAF positioned at the frontend is typically the attack surface for request smuggling, not a protection layer, because the smuggled content is already past the WAF when it reaches the backend. WAFs may help if they normalize ambiguous headers before forwarding, but many do not. The effective fix is at the infrastructure level: eliminating the parsing discrepancy between frontend and backend, not adding another intermediary. Some WAFs (Cloudflare, for example) have added specific request smuggling normalization, but verify that the specific WAF you use applies this to your traffic before relying on it.
5. Performance Evaluation & Extended Technical Observations HTTP/2 request smuggling (H2.CL and H2.TE) exploits the downgrade from HTTP/2 (used between client and frontend) to HTTP/1.1 (used between frontend and backend). HTTP/2 does not use Content-Length or chunked encoding for framing, but the frontend may rewrite HTTP/2 requests into HTTP/1.1 by adding Content-Length headers. If the frontend adds a Content-Length that the attacker can influence (for example, by including a content-length pseudo-header in an HTTP/2 request that overrides the automatically computed value), the frontend may forward a request with a misleading Content-Length to the HTTP/1.1 backend, creating smuggling conditions.
25 actively exploited vulnerabilities with CVSS scores, exploit status, and patch availability. Print it, pin it, share it with your SOC team. Step-by-step 24-hour IR checklist covering detection, containment, eradication, and recovery. Built for SOC teams, IR leads, and CISOs.
50,000+ security professionals read Decryption Digest for early warnings on zero-days, ransomware, and nation-state campaigns. Free, daily, no spam. Cybersecurity professional with expertise in threat intelligence, vulnerability research, and enterprise security. Covers zero-days, ransomware, and nation-state operations for 50,000+ security professionals every morning.
Actionable threat intelligence for working practitioners. Free. No spam. Trusted by 50,000+ SOC analysts, CISOs, and security engineers. In this section, we'll explain HTTP request smuggling attacks and describe how common request smuggling vulnerabilities can arise.
If you're already familiar with HTTP request smuggling and just want to practice on a series of deliberately vulnerable sites, check out the link below for an overview of all labs in this topic. HTTP request smuggling is a technique for interfering with the way a web site processes sequences of HTTP requests that are received from one or more users. Request smuggling vulnerabilities are often critical in nature, allowing an attacker to bypass security controls, gain unauthorized access to sensitive data, and directly compromise other application users.
Request smuggling is primarily associated with HTTP/1 requests. However, websites that support HTTP/2 may be vulnerable, depending on their back-end architecture. HTTP request smuggling was first documented in 2005, and repopularized by PortSwigger's extensive research on the topic. For details, check out the following whitepapers: Today's web applications frequently employ chains of HTTP servers between users and the ultimate application logic. Users send requests to a front-end server (sometimes called a load balancer or reverse proxy) and this server forwards requests to one or more back-end servers. This type of architecture is increasingly common, and in some cases unavoidable, in modern cloud-based applications.
When the front-end server forwards HTTP requests to a back-end server, it typically sends several requests over the same back-end network connection, because this is much more efficient and performant. The protocol is very simple; HTTP requests are sent one after another, and the receiving server has to determine where one request ends and the next one begins: In this situation, it is crucial that the front-end and back-end systems agree about the boundaries between requests.
Otherwise, an attacker might be able to send an ambiguous request that gets interpreted differently by the front-end and back-end systems: Here, the attacker causes part of their front-end request to be interpreted by the back-end server as the start of the next request. It is effectively prepended to the next request, and so can interfere with the way the application processes that request. This is a request smuggling attack, and it can have devastating results.
Most HTTP request smuggling vulnerabilities arise because the HTTP/1 specification provides two different ways to specify where a request ends: the Content-Length header and the Transfer-Encoding header. The Content-Length header is straightforward: it specifies the length of the message body in bytes. For example: The Transfer-Encoding header can be used to specify that the message body uses chunked encoding. This means that the message body contains one or more chunks of data. Each chunk consists of the chunk size in bytes (expressed in hexadecimal), followed by a newline, followed by the chunk contents. The message is terminated with a chunk of size zero.
For example: Many security testers are unaware that chunked encoding can be used in HTTP requests, for two reasons: As the HTTP/1 specification provides two different methods for specifying the length of HTTP messages, it is possible for a single message to use both methods at once, such that they conflict with each other. The specification attempts to prevent this problem by stating that if both the Content-Length and Transfer-Encoding headers are present, then the Content-Length header should be ignored. This might be sufficient to avoid ambiguity when only a single server is in play, but not when two or more servers are chained together. In this situation, problems can arise for two reasons: If the front-end and back-end servers behave differently in relation to the (possibly obfuscated) Transfer-Encoding header, then they might disagree about the boundaries between successive requests, leading to request smuggling vulnerabilities.
Websites that use HTTP/2 end-to-end are inherently immune to request smuggling attacks. As the HTTP/2 specification introduces a single, robust mechanism for specifying the length of a request, there is no way for an attacker to introduce the required ambiguity. However, many websites have an HTTP/2-speaking front-end server, but deploy this in front of back-end infrastructure that only supports HTTP/1. This means that the front-end effectively has to translate the requests it receives into HTTP/1. This process is known as HTTP downgrading. For more information, see Advanced request smuggling .
Classic request smuggling attacks involve placing both the Content-Length header and the Transfer-Encoding header into a single HTTP/1 request and manipulating these so that the front-end and back-end servers process the request differently. The exact way in which this is done depends on the behavior of the two servers: These techniques are only possible using HTTP/1 requests. Browsers and other clients, including Burp, use HTTP/2 by default to communicate with servers that explicitly advertise support for it during the TLS handshake.
As a result, when testing sites with HTTP/2 support, you need to manually switch protocols in Burp Repeater. You can do this from the Request attributes section of the Inspector panel. Here, the front-end server uses the Content-Length header and the back-end server uses the Transfer-Encoding header. We can perform a simple HTTP request smuggling attack as follows: The front-end server processes the Content-Length header and determines that the request body is 13 bytes long, up to the end of SMUGGLED . This request is forwarded on to the back-end server.
The back-end server processes the Transfer-Encoding header, and so treats the message body as using chunked encoding. It processes the first chunk, which is stated to be zero length, and so is treated as terminating the request. The following bytes, SMUGGLED , are left unprocessed, and the back-end server will treat these as being the start of the next request in the sequence.
Here, the front-end server uses the Transfer-Encoding header and the back-end server uses the Content-Length header. We can perform a simple HTTP request smuggling attack as follows: To send this request using Burp Repeater, you will first need to go to the Repeater menu and ensure that the "Update Content-Length" option is unchecked.
The front-end server processes the Transfer-Encoding header, and so treats the message body as using chunked encoding. It processes the first chunk, which is stated to be 8 bytes long, up to the start of the line following SMUGGLED . It processes the second chunk, which is stated to be zero length, and so is treated as terminating the request. This request is forwarded on to the back-end server.
The back-end server processes the Content-Length header and determines that the request body is 3 bytes long, up to the start of the line following 8 . The following bytes, starting with SMUGGLED , are left unprocessed, and the back-end server will treat these as being the start of the next request in the sequence. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/List%20of%20military%20aid%20to%20Ukraine%20during%20the%20Russo-Ukrainian%20war • https://en.wikipedia.org/wiki/List%20of%20The%20Transformers%20characters • https://en.wikipedia.org/wiki/List%20of%20The%20Loud%20House%20episodes • https://github.com/GuardianVigil/go-smuggler • https://github.com/PortSwigger/http-request-smuggler • https://cvetodo.com/cve/CVE-2026-88092 • https://starlog.is/articles/developer-tools/defparam-smuggler/ • https://pasindu-sd.github.io/writeups-blog/PortSwigger---Labs/HTTP-request-smuggling/HTTP-request-smuggling,-confirmin g-a-CL.TE-vulnerability-via-differential-responses • https://portswigger.net/web-security/request-smuggling/finding • https://github.com/Nasr-Security/http-smuggler
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Http Request Smuggling Vulnerability Detector Tool.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Http Request Smuggling Vulnerability Detector Tool... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |