Complete Technical Paper Content — Infrastructure As Code Security Scanner Using Tfsec
Overview & System Context
Infrastructure As Code Security Scanner Using Tfsec: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~6629 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Misconfigured infrastructure remains the leading cause of cloud breaches, yet most teams still treat IaC security as an afterthought during deployment rather than a shift-left validation step. Effective IaC security: scan with tfsec, Checkov, Terrascan integrates static analysis directly into your development workflow to catch exposed ports, missing encryption, and overly permissive IAM roles before you ever run terraform apply . This guide provides the exact configuration patterns and CI integration steps needed to enforce policy-as-code without slowing down delivery.
Implementing IaC security: scan with tfsec, Checkov, Terrascan requires more than installing binaries; it demands strategic placement within your DevSecOps shift-left strategy . In practice, I recommend a tiered approach where lightweight checks run locally via pre-commit hooks, while comprehensive scans execute in CI on every pull request. This prevents noise fatigue while ensuring no insecure code merges to main.
The key to sustainable adoption is treating scanner output as structured data, not just terminal noise. Configure each tool to emit SARIF or JSON so your CI platform can annotate pull requests directly. When developers see "S3 bucket missing versioning" inline on line 42 of their diff, fix rates increase dramatically compared to burying findings in a separate dashboard. For teams managing sensitive data, pair these scanners with proper secrets handling to ensure credentials never leak during the scan process itself.
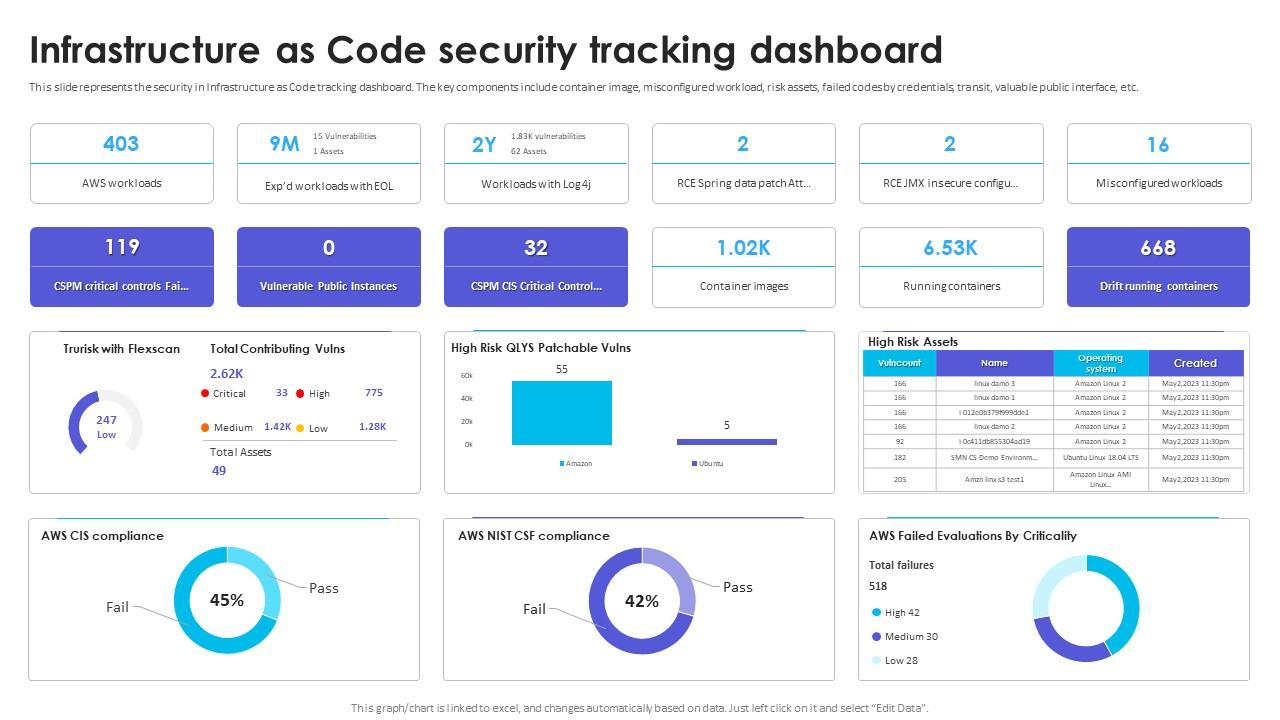
Catch issues before they enter version control using pre-commit. This reduces CI cycle time and gives immediate feedback: Figure 1: Infrastructure As Code Security Tracking Dashboard Infrastructure As ... Choosing the right tool depends on your specific compliance requirements, supported frameworks, and performance constraints. While there is overlap, each scanner has distinct strengths that make them complementary rather than redundant when implementing IaC security: scan with tfsec, Checkov, Terrascan .
In my experience helping Nepal-based fintechs achieve ISO 27001 compliance, Checkov's extensive built-in policy library (800+ checks) satisfies auditors fastest. However, for daily developer workflows on pure Terraform projects, tfsec's speed and low false-positive rate make it the superior first-line defense. Terrascan fills gaps with its curated vulnerability database, particularly useful when you need to explain why a finding matters to non-technical stakeholders.
Built-in rules cover generic cloud security, but every organization has unique constraints—specific tagging schemas, approved instance types, or region restrictions. Writing custom policies enforces these standards automatically. Below is a practical Rego example for tfsec that blocks any AWS S3 bucket lacking mandatory cost-allocation tags: For Checkov, custom Python policies offer lower barrier to entry for teams already comfortable with Python. Store custom policies in a shared repository and reference them via --external-checks-dir in CI. This centralizes governance while allowing individual teams to opt into stricter controls. Remember to version your policy repository independently from application code; policy changes should follow their own review cycle, especially when preparing for audits like SOC 2 evidence automation .
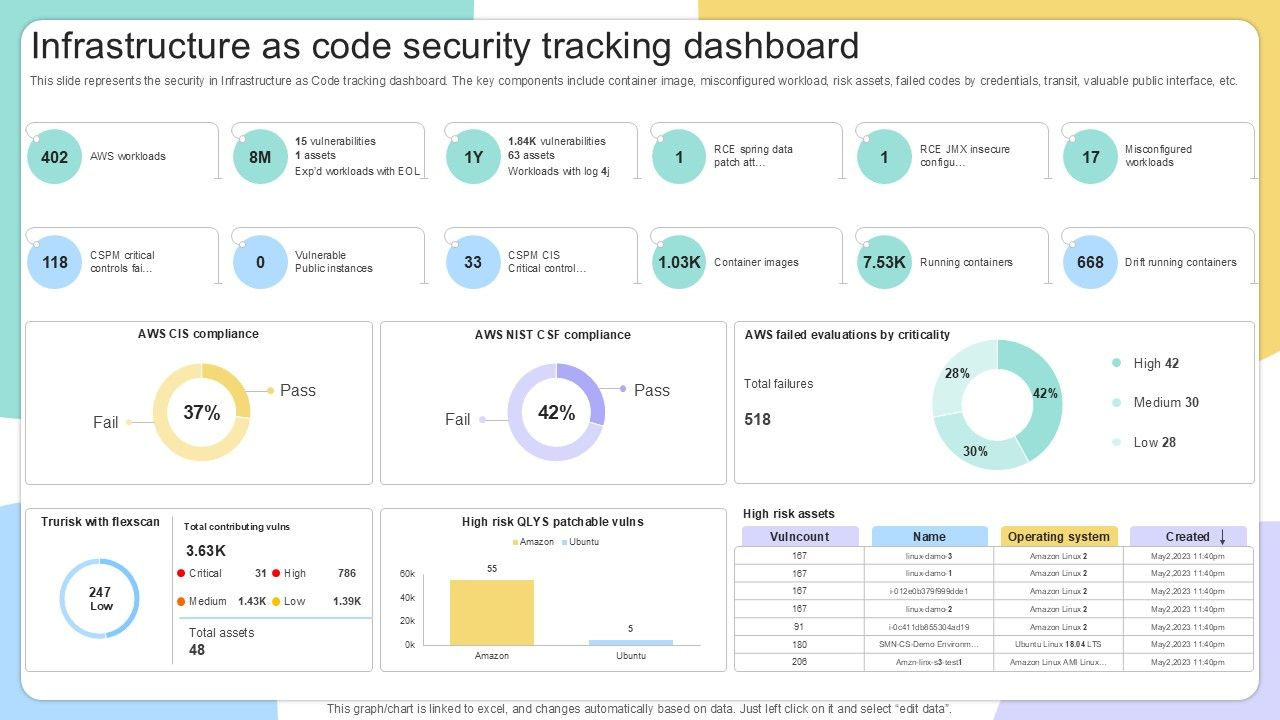
Figure 2: Infrastructure As Code Security IAC Tools For Performance Analysis PPT ... Scanner fatigue kills adoption faster than any technical limitation. A common mistake is enabling all rules at HIGH severity immediately. Instead, baseline your existing codebase first, then ratchet up enforcement. All three tools support inline suppression comments for legitimate exceptions, but use them sparingly and always require justification: Create an exception review process. Monthly, export all suppressed findings and validate they're still valid. Stale exceptions become security debt. In regulated environments, maintain an exception register mapping each suppression to a risk acceptance form signed by the system owner. This discipline separates mature IaC security: scan with tfsec, Checkov, Terrascan implementations from checkbox exercises.
If your stack extends beyond Terraform/AWS, tool selection shifts. Checkov leads for Kubernetes manifest scanning with native Helm chart support and pod security standard checks. Terrascan excels at detecting container image vulnerabilities referenced in IaC. For teams adopting Kubernetes security best practices , run Checkov against both Terraform modules generating K8s manifests AND the rendered YAML output to catch drift between intent and artifact.
For multi-cloud organizations, avoid forcing a single tool. Run tfsec for AWS/Terraform modules where it dominates, Checkov for Azure/GCP/K8s coverage, and aggregate results. The marginal CI time increase is worth avoiding blind spots. Document this matrix in your internal developer platform so teams self-select appropriate scanners based on their stack rather than guessing.
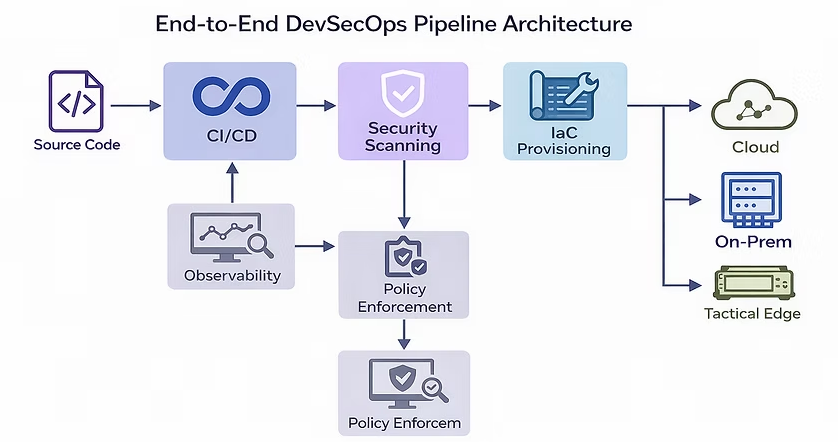
Figure 3: Infrastructure as Code Security Risks: The Silent Threat in Modern DevOps Effective IaC security: scan with tfsec, Checkov, Terrascan transforms infrastructure provisioning from a trust-based model to a verified, auditable process. Begin with tfsec in pre-commit hooks for immediate wins, layer Checkov for compliance reporting, and add Terrascan when you need deeper forensic context. Automate enforcement in CI, manage exceptions rigorously, and treat policy definitions as first-class code artifacts. If your team needs help designing a scanning strategy that balances security rigor with delivery speed, reach out to discuss your specific infrastructure challenges .
Kokil Thapa is an experienced full-stack web developer focused on building fast, secure, and scalable web applications. He helps businesses and individuals create SEO-friendly, user-focused digital platforms designed for long-term growth. Shipping infrastructure without automated validation is a liability I no longer accept on production projects. IaC Security: Scan with tfsec, Checkov, Terrascan provides the static analysis layer needed to catch open S3 buckets, overly permissive IAM roles, and unencrypted databases before they ever reach your cloud provider. In my experience managing deployments for legal-tech portals and eCommerce platforms, integrating these scanners into GitLab CI or local workflows prevents costly remediation cycles that often exceed the original development budget in Nepal's resource-constrained market.
Integrating scanners into your continuous integration workflow transforms security from an afterthought into a quality gate. On projects where I manage CI/CD pipeline setup , I treat infrastructure scans identically to application unit tests: if the scan fails, the merge request cannot be merged. This prevents "security debt" from accumulating silently in your Terraform modules. The most effective pattern uses a tiered approach. Run the fastest scanner first to provide immediate developer feedback, then run broader policy checks as secondary jobs. This balances developer velocity with comprehensive coverage. Below is a production-ready GitLab CI configuration that orchestrates all three tools without bloating the pipeline runtime.
A critical implementation detail often missed in tutorials is artifact retention and format standardization. All three tools support JUnit XML output, which GitLab (and Jenkins, GitHub Actions) can parse natively to display results directly in the merge request UI. Without this integration, developers must dig through raw log files, drastically reducing fix rates. I always set allow_failure: true for new scanner introductions, giving teams two weeks to triage existing violations before making the gate mandatory.
Choosing the right tool depends entirely on your stack, team size, and compliance requirements. After deploying these across multiple client environments—from Laravel-hosted infrastructure on AWS to Kubernetes clusters for SaaS products—I have found that each scanner occupies a distinct niche. No single tool covers every scenario adequately. In practice, tfsec wins for pure Terraform projects where speed matters most. Its parser understands HCL semantics deeply, catching issues like unresolved variable references that regex-based tools miss. Checkov dominates when you need compliance mapping out of the box; its Python-based custom policies are far more accessible than Rego for teams already writing Python backend code. Terrascan excels at post-deployment auditing and visualizing attack paths, though its slower scan time makes it less suitable as a pre-commit hook.
For Nepal-based clients operating under tight budgets, I typically start with tfsec alone. It catches 80% of critical misconfigurations with near-zero pipeline overhead. Only when compliance frameworks (like PCI-DSS for payment-integrated eCommerce sites) enter the picture do I add Checkov's heavier policy library. Understanding these trade-offs helps avoid over-engineering security processes that stall delivery—a topic I explore further in my guide on securing websites and servers in Nepal .
Built-in rules cover generic best practices, but every organization has unique constraints. Legal-tech platforms I build often require specific encryption standards or data residency rules that public policy libraries don't address. Writing custom policies bridges this gap. Checkov's Python-based policies are straightforward for developers already comfortable with the language. This example enforces that all S3 buckets must have a specific tag indicating Nepal data residency approval: For tfsec, Rego policies integrate with the OPA engine. This rule ensures all RDS instances use approved instance classes for cost control in Nepali SME projects: Store custom policies in version control alongside your infrastructure code. Both tools support loading policies from local directories via CLI flags ( --external-checks-dir for Checkov, --rego-policy-dir for tfsec). Never embed organizational rules in upstream forks; maintainability suffers immediately when upstream updates break your modifications.
No scanner is perfect. False positives erode trust faster than any other factor, leading teams to disable checks entirely. Equally dangerous is introducing scanners to legacy codebases with hundreds of pre-existing violations—developers ignore new failures buried in noise. Both problems require explicit baselining strategies. On a recent legal-tech portal migration, we inherited 340+ Checkov violations across 15 Terraform modules. Instead of blocking all merges, we baselined everything, fixed CRITICAL and HIGH severity issues within two sprints, and reduced the baseline by 60% in six weeks. The remaining LOW findings were accepted as documented technical debt with owner assignments. This pragmatic approach kept delivery moving while measurably improving security posture—a balance essential when working with Nepal-based teams where dedicated security staff are rare.
Catching issues in CI is good; catching them before commit is better. Developer experience determines whether security tooling gets adopted or bypassed. I configure local scanning to mirror CI behavior exactly, preventing the frustrating "works locally, fails in pipeline" cycle that plagues many DevOps implementations. The key insight is consistency. If your CI uses --minimum-severity HIGH but your local hook defaults to MEDIUM, developers waste time fixing issues CI won't enforce. Mirror configurations exactly. When updating scanner versions in CI, update pre-commit hooks simultaneously. This discipline prevents the configuration drift that makes security tooling feel arbitrary and hostile to developer workflow.
Effective IaC Security: Scan with tfsec, Checkov, and Terrascan requires treating them as complementary layers rather than competing alternatives. Start with tfsec for rapid developer feedback, add Checkov when compliance frameworks demand it, and reserve Terrascan for periodic deep audits and drift detection. Baseline existing violations pragmatically, mirror configurations across local and CI environments, and measure adoption through actual fix rates rather than scan counts.
The goal isn't perfect scores—it's sustainable security practices that survive contact with real project timelines and budget constraints. Whether you're building legal-tech portals in Kathmandu or SaaS infrastructure globally, these tools provide the automated guardrails that let teams move fast without accumulating catastrophic technical debt. If you need help implementing these scanners in your existing workflow or designing custom policies for Nepal-specific compliance requirements, reach out to discuss your infrastructure security needs .
2. System Architecture & Core Working Principles Your email is not published. Comments appear once they have been read. Sign in to have your details filled in. In a controlled study by Horizon3 researchers, models that explicitly identified a trap in their reasoning still attacked it 73.4% of the time. Read the findings and see what they mean for canaries, decoys, and early detection.
Terraform code that provisions an S3 bucket with public access, an RDS instance without encryption, or a security group with 0.0.0.0/0 ingress on all ports will create exactly that infrastructure when applied. Security scanning in CI/CD catches these before apply runs. This guide covers how to set up tfsec and Checkov in a GitHub Actions pipeline, the top misconfiguration patterns each tool catches, and how to handle suppression for legitimate exceptions without creating a blanket ignore policy.
This shows only High and Critical findings, giving you the most impactful starting point without overwhelming the team with hundreds of Medium and Low findings at once. These resource types produce the highest-frequency high-severity findings across AWS, Azure, and GCP: Set soft_fail: false once the existing finding backlog is resolved. With soft_fail: false , any High or Critical finding blocks the PR merge. Upload SARIF to the GitHub Security tab so findings are tracked as code scanning alerts alongside SAST results.
Some findings are intentional. A public S3 bucket hosting a static website, a security group allowing 443 from the world for a load balancer, or a non-encrypted bucket for cost optimization in a staging environment. Suppression must be documented and scoped. For custom organization rules that the public scanners do not cover (e.g., required tags on all resources, specific naming conventions), tfsec supports custom rule YAML files placed in a .tfsec/ directory in the repo.
Trivy is a broader security scanner that covers IaC, container images, and secrets in a single tool. For Terraform, Trivy replicates most tfsec and Checkov checks and adds secrets detection (hardcoded API keys, passwords, AWS access keys in Terraform variable files). Trivy is particularly useful for detecting hardcoded secrets in .tfvars files and in resource arguments that should reference variable inputs: For secrets in Terraform state files (a separate problem): Terraform state can contain sensitive values in plaintext. Always use remote state with encryption at rest (S3 + SSE, Terraform Cloud, or Azure Backend with customer-managed keys). Add state file locations to your .gitignore and run Trivy on your repository to ensure no .tfstate files are committed.
Every terraform apply without a prior security scan is a production deployment with no code review for the security properties that matter most. Add tfsec or Checkov to your CI/CD pipeline at the PR level, upload results as SARIF to the Security tab, set a policy that High and Critical findings block merge, and require ticket references for every suppression. The scanning takes 30-60 seconds per run and prevents the kind of S3 bucket public access exposure that shows up in breach post-mortems.
They overlap significantly on core rule coverage. tfsec is Terraform-specific and fast, with good HCL parsing. Checkov covers more frameworks (Terraform, Kubernetes, Dockerfiles, Ansible) and has a larger rule library including compliance framework mappings (CIS, SOC 2, PCI). Trivy adds secrets detection on top of misconfiguration scanning. Many teams run two tools in parallel: tfsec for fast PR feedback and Checkov for compliance-mapped reporting. Running all three is not unreasonable in high-compliance environments and takes under 2 minutes in CI.
Can IaC scanning detect runtime misconfigurations that are applied outside of Terraform? No. IaC scanners analyze the Terraform code; they cannot see what exists in cloud accounts that was deployed manually, through another tool, or that drifted from the Terraform state after apply. For runtime misconfiguration detection, use a CSPM tool (Defender for Cloud, Wiz, Prisma Cloud, AWS Security Hub). IaC scanning and CSPM are complementary: IaC scanning prevents new misconfigurations from being deployed; CSPM detects existing misconfigurations regardless of how they were created.
When tfsec or Checkov scans a root module that calls a public registry module, findings in the module code are typically surfaced with the module source path. You cannot modify the module source, but you can: (1) pass variables to the module that enable secure configuration, (2) fork the module and apply fixes in your fork, (3) suppress the finding with a documented justification, or (4) switch to a different module with better security defaults. Check the module's GitHub issues first -- many popular modules have accepted PRs for security fixes that are not yet in a released version.
Start with report-only mode (soft_fail: true) for the first 4-6 weeks to let the team understand the finding volume and resolve the existing backlog. Then switch Critical findings to blocking, then High findings. Medium and Low findings should remain advisory for most teams. The goal is to make the path of least resistance a secure one: if every PR fails due to 50 findings, engineers will configure blanket suppressions to unblock themselves, defeating the purpose.
Use inline suppression comments (tfsec, Checkov, and Trivy all support suppression directives with a reason field) for one-time exceptions. Enforce a policy that every suppression must include a reason string and a Jira or issue tracker reference. In your CI pipeline, run a script that counts active suppressions per repository and outputs a suppression inventory as a build artifact. Route suppressions beyond a defined threshold for mandatory security review. Set suppression expiry by convention: if the reason references a ticket, the ticket closure should trigger suppression removal. Review the suppression inventory quarterly as part of your IaC security posture assessment.
Terraform state files contain plaintext values for all resource attributes, including secrets, passwords, and private keys that were passed to resources during provisioning. Never store state locally on developer machines or in version control. Use remote state backends with encryption at rest and access controls: Terraform Cloud, AWS S3 with server-side encryption and a DynamoDB lock table, Azure Blob Storage with encryption, or GCS with a customer-managed key. Restrict state file access via IAM so only the CI/CD role and designated operators can read or write state. Enable state locking to prevent concurrent applies. For particularly sensitive state (containing database credentials or certificate private keys), consider using external secret references rather than passing secrets directly to resource arguments.
25 actively exploited vulnerabilities with CVSS scores, exploit status, and patch availability. Print it, pin it, share it with your SOC team. Step-by-step 24-hour IR checklist covering detection, containment, eradication, and recovery. Built for SOC teams, IR leads, and CISOs.
50,000+ security professionals read Decryption Digest for early warnings on zero-days, ransomware, and nation-state campaigns. Free, daily, no spam. Cybersecurity professional with expertise in threat intelligence, vulnerability research, and enterprise security. Covers zero-days, ransomware, and nation-state operations for 50,000+ security professionals every morning.
Actionable threat intelligence for working practitioners. Free. No spam. Trusted by 50,000+ SOC analysts, CISOs, and security engineers. Learn how to integrate tfsec into your Terraform workflow to catch security misconfigurations before they reach your cloud infrastructure.
Finding security issues in your Terraform code after deployment is painful and expensive. tfsec is a static analysis tool that scans your Terraform files and flags security problems before you ever run terraform apply . It catches things like unencrypted storage, overly permissive IAM policies, and public access to resources that should be private. This guide walks through installing tfsec, running it against your code, integrating it into CI/CD, and handling its output effectively.
tfsec reads your .tf files and checks them against a large set of built-in security rules. It understands Terraform's HCL syntax natively, so it can follow variable references, evaluate expressions, and understand module structures. This is a big advantage over generic pattern-matching tools. Each finding includes the severity, the specific code location, and a link to documentation explaining the issue and how to fix it.
Not every tfsec finding is a real problem. Sometimes you intentionally configure something that tfsec flags. You can suppress specific findings with inline comments: If the built-in rules do not cover your organization's requirements, you can write custom rules: 3. Software Implementation, Frameworks & Protocols It is worth noting that tfsec has been integrated into Trivy, another Aqua Security tool. Trivy provides a broader scanning capability that includes container images, file systems, and IaC. If you are already using Trivy, you get tfsec's rules for free. If you only need Terraform scanning, tfsec is a lighter-weight option.
tfsec is straightforward to set up and catches a significant percentage of common Terraform security mistakes. Start by running it locally, integrate it into your CI/CD pipeline, and gradually work through the findings. The goal is not to have zero findings from day one but to prevent new security issues from being introduced and steadily improve your baseline. For monitoring your infrastructure after deployment, OneUptime provides comprehensive observability including uptime monitoring, logs, and incident management.
Every OneUptime blog post is open source. Found a typo, an inaccuracy, or have a clearer way to explain something? Anyone can contribute — your edits make this post better for everyone who reads it next. Your complete reliability stack unified: infrastructure monitoring, incident management, status pages, and APM. Open-source and self-hostable.
Infrastructure as Code failures rarely stem from syntax errors alone; they usually result from subtle misconfigurations or security gaps that standard validation misses. Integrating tflint and tfsec in your pipeline provides the necessary defense layers by combining deep linting with dedicated security policy enforcement before you ever run a plan. This guide walks through the exact configuration needed to make these tools effective gatekeepers in your CI workflow, ensuring your infrastructure is both valid and secure.
A common mistake I see when teams adopt infrastructure as code with Terraform is assuming that terraform validate is sufficient quality control. It is not. Validate only checks HCL syntax and internal consistency; it does not know if your S3 bucket is public or if your security group allows unrestricted SSH access. You need specialized tooling to bridge this gap. TFLint focuses on correctness, style, and provider-specific best practices. It catches issues like invalid instance types, deprecated attributes, and naming convention violations that technically parse correctly but will fail during apply or cause operational debt. TFSec, conversely, is a security-first scanner that evaluates your configuration against compliance frameworks like CIS, NIST, and SOC 2. It identifies exposed secrets, missing encryption, and overly permissive network rules.
Using them together covers the full spectrum of pre-deployment risk. TFLint ensures your code works as intended; tfsec ensures it doesn't introduce unacceptable security posture. In my experience helping organizations achieve ISO 27001 certification, this combination is often the minimum viable control set for automated infrastructure governance. TFLint requires explicit plugin configuration to understand provider-specific resources. Without plugins, it can only lint core HCL syntax. Create a .tflint.hcl file in your repository root to define rules and enable provider inspection.
Before adding tflint to CI, verify your configuration locally. Install the binary and initialize plugins to download the correct rule sets: In practice, pin plugin versions explicitly as shown above. Floating versions can introduce breaking rule changes between developer machines and CI runners, causing frustrating "works on my machine" discrepancies. For teams managing multiple environments, consider storing this config in a shared module or using Terragrunt to inject consistent linting standards across repositories.
TFSec ships with hundreds of built-in checks. Running it without configuration on an existing codebase typically generates overwhelming noise. The key to sustainable adoption is aggressive tuning based on your actual risk profile and compliance requirements. Never globally disable high-severity security checks without documented justification. Instead, use inline ignores with explanatory comments directly in your Terraform code. This keeps the audit trail adjacent to the decision: This approach satisfies auditors because the rationale travels with the code. When reviewing PRs, engineers can immediately see why a check was bypassed rather than hunting through external documentation. For teams pursuing DevSecOps shift-left practices , this transparency is essential for maintaining security velocity without sacrificing governance.
Understanding the distinct roles of each tool prevents redundant configuration and ensures comprehensive coverage. While there is some overlap in basic checks, their primary functions serve different purposes in the validation chain. In production environments, I treat tflint as a mandatory quality gate that should block merges on any error-level finding. TFSec operates as a security advisory layer where HIGH and CRITICAL findings block deployment, but MEDIUM issues may generate warnings tracked in your backlog. This tiered approach balances safety with delivery velocity, especially important for teams managing multiple environments in IaC where risk tolerance varies between staging and production.
Automating these checks in CI removes human inconsistency from the review process. Below is a production-tested GitHub Actions workflow that runs both tools with proper caching and artifact generation. If your repository contains multiple Terraform roots, naive recursive scanning wastes time re-evaluating unchanged modules. Use directory filtering to target only modified paths: For organizations with strict compliance requirements, archive the SARIF outputs as build artifacts. These serve as timestamped evidence for audits, proving that security scanning occurred on every change. When preparing for SOC 2 or ISO 27001 assessments, having automated proof of continuous validation significantly reduces auditor questioning and evidence collection effort.
The technical setup of tflint and tfsec in your pipeline is straightforward; the organizational challenge is preventing tool fatigue. Start with permissive configurations that warn rather than fail, giving teams time to remediate existing debt. Establish a regular cadence—perhaps quarterly—to tighten rules as baseline quality improves. Track metrics like mean time to resolution for security findings and false positive rates to demonstrate value to stakeholders.
Remember that these tools augment, not replace, human judgment. They excel at catching known patterns and enforcing consistency at scale, but architectural decisions still require experienced engineers who understand business context. If you're building out your IaC validation strategy or need help tuning these tools for compliance frameworks, reach out to discuss your specific infrastructure challenges .
As part of our goal to provide a comprehensive open source security solution for all, we have been consolidating all of our scanning-related efforts in one place, and that is Trivy . Over the past year, tfsec has laid the foundations to Trivy's IaC & misconfigurations scanning capabilities, including Terraform scanning, which has been natively supported in Trivy for a long time now.
Going forward we want to encourage the tfsec community to transition over to Trivy. Moving to Trivy gives you the same excellent Terraform scanning engine, with some extra benefits: For further information on how Trivy compares to tfsec and moving from tfsec to Trivy, do have a look at the migration guide. tfsec uses static analysis of your terraform code to spot potential misconfigurations.
For our projects using Terraform, tfsec has quickly become a default static analysis tool to detect potential security risks. It's easy to integrate into a CI pipeline and has a growing library of checks against all of the major cloud providers and platforms like Kubernetes. Given its ease of use, we believe tfsec could be a good addition to any Terraform project. Please note that using go install will install directly from the master branch and version numbers will not be reported via tfsec --version .
The binaries on the releases page are signed with the tfsec signing key D66B222A3EA4C25D5D1A097FC34ACEFB46EC39CE tfsec will scan the specified directory. If no directory is specified, the current working directory will be used.
4. Practical Deployment, Analysis & Case Studies The exit status will be non-zero if tfsec finds problems, otherwise the exit status will be zero. As an alternative to installing and running tfsec on your system, you may run tfsec in a Docker container. A Visual Studio Code extension is being developed to integrate with tfsec results. More information can be found on the tfsec Marketplace page If you want to run tfsec on your repository as a GitHub Action, you can use https://github.com/aquasecurity/tfsec-pr-commenter-action .
You can now install the official tfsec task . Please raise any issues/feature requests on the task repository . You may wish to ignore some warnings. If you'd like to do so, you can simply add a comment containing tfsec:ignore:
If you're not sure which line to add the comment on, just check the tfsec output for the line number of the discovered problem. You can set expiration date for ignore with yyyy-mm-dd format. This is a useful feature when you want to ensure ignored issue won't be forgotten and should be revisited in the future. Ignore like this will be active only till 2025-01-02 , after this date it will be deactivated.
You may wish to exclude some checks from running. If you'd like to do so, you can simply add new argument -e check1,check2,etc to your cmd command You can include values from a tfvars file in the scan, using, for example: --tfvars-file terraform.tfvars . tfsec is designed for running in a CI pipeline. You may wish to run tfsec as part of your build without coloured output. You can do this using --no-colour (or --no-color for our American friends).
You can output tfsec results as JSON, CSV, Checkstyle, Sarif, JUnit or just plain old human-readable format. Use the --format flag to specify your desired format. If you want to integrate with Github Security alerts and include the output of your tfsec checks you can use the tfsec-sarif-action Github action to run the static analysis then upload the results to the security alerts tab.
When you click through the alerts for the branch, you get more information about the actual issue. If you need to support versions of terraform which use HCL v1 (terraform <0.12), you can use v0.1.3 of tfsec, though support is very limited and has fewer checks. We always welcome contributions; big or small, it can be documentation updates, adding new checks or something bigger.
Please check the Contributing Guide for details on how to help out. tfsec is an Aqua Security open source project. Learn about our open source work and portfolio here . Join the community, and talk to us about any matter in GitHub Discussion or Slack . tfsec uses static analysis of your terraform code to spot potential misconfigurations.
For our projects using Terraform, tfsec has quickly become a default static analysis tool to detect potential security risks. It's easy to integrate into a CI pipeline and has a growing library of checks against all of the major cloud providers and platforms like Kubernetes. Given its ease of use, we believe tfsec could be a good addition to any Terraform project. Please note that using go install will install directly from the master branch and version numbers will not be reported via tfsec --version .
The binaries on the releases page are signed with the tfsec signing key D66B222A3EA4C25D5D1A097FC34ACEFB46EC39CE tfsec will scan the specified directory. If no directory is specified, the current working directory will be used.
The exit status will be non-zero if tfsec finds problems, otherwise the exit status will be zero. As an alternative to installing and running tfsec on your system, you may run tfsec in a Docker container. A Visual Studio Code extension is being developed to integrate with tfsec results. More information can be found on the tfsec Marketplace page If you want to run tfsec on your repository as a GitHub Action, you can use https://github.com/aquasecurity/tfsec-pr-commenter-action .
You can now install the official tfsec task . Please raise any issues/feature requests on the task repository . You may wish to ignore some warnings. If you'd like to do so, you can simply add a comment containing tfsec:ignore:
If you're not sure which line to add the comment on, just check the tfsec output for the line number of the discovered problem. You can set expiration date for ignore with yyyy-mm-dd format. This is a useful feature when you want to ensure ignored issue won't be forgotten and should be revisited in the future. 5. Performance Evaluation & Extended Technical Observations Ignore like this will be active only till 2025-01-02 , after this date it will be deactivated.
You may wish to exclude some checks from running. If you'd like to do so, you can simply add new argument -e check1,check2,etc to your cmd command You can include values from a tfvars file in the scan, using, for example: --tfvars-file terraform.tfvars . tfsec is designed for running in a CI pipeline. You may wish to run tfsec as part of your build without coloured output. You can do this using --no-colour (or --no-color for our American friends).
You can output tfsec results as JSON, CSV, Checkstyle, Sarif, JUnit or just plain old human-readable format. Use the --format flag to specify your desired format. If you want to integrate with Github Security alerts and include the output of your tfsec checks you can use the tfsec-sarif-action Github action to run the static analysis then upload the results to the security alerts tab.
When you click through the alerts for the branch, you get more information about the actual issue. If you need to support versions of terraform which use HCL v1 (terraform <0.12), you can use v0.1.3 of tfsec, though support is very limited and has fewer checks. We always welcome contributions; big or small, it can be documentation updates, adding new checks or something bigger.
Please check the Contributing Guide for details on how to help out. tfsec is an Aqua Security open source project. Learn about our open source work and portfolio here . Join the community, and talk to us about any matter in GitHub Discussion or Slack . > your AI agent picks dependencies from memory; give it dated facts — try starlog.dev I vet your agent's deps I vibe-coding is fine. vibe-importing isnâIIt. — try starlog.dev I vibe-importing isnâIIt fine I your agent has never seen your private packages — try starlog.dev I facts for private packages I a linter for the dependencies your AI agent picks — try starlog.dev I a linter for agent deps I whois is redacted, cdns mask the rest âII get the real operator — try whoisgeni.us I who really runs that domain I domain attribution that shows its work âII full evidence chain — try whoisgeni.us I domain intel w/ evidence I Metrics below are heuristic approximations computed from repository structure, not authoritative measurements.
tfsec scanned over 6 million Terraform files before its creators made the bold decision to sunset it in favor of their own competing tool, Trivy. Here's why that was the right move. In the early days of Terraform adoption, security testing happened too lateâIIafter infrastructure was already deployed to the cloud. Teams would discover misconfigured S3 buckets, overly permissive security groups, or unencrypted databases only after cloud security posture management tools flagged them in production. The feedback loop was measured in days or weeks, and fixes required coordination between security and infrastructure teams.
tfsec emerged in 2019 to shift security left, bringing static analysis directly into the Terraform development workflow. Unlike simple pattern matchers that looked for hardcoded secrets, tfsec understood Terraform's HCL syntax deeply enough to evaluate expressions, follow variable references across files, and detect security issues in resource relationships. It could catch a security group allowing 0.0.0.0/0 access even when that CIDR block was constructed through string concatenation or passed through module variables. The tool gained rapid adoption because it was fast, required no agent or cloud credentials, and integrated seamlessly into existing CI/CD pipelines. By the time Aqua Security acquired the project and eventually merged it into Trivy, tfsec had become the de facto standard for pre-deployment Terraform security scanning.
What made tfsec architecturally interesting wasn't just that it parsed HCLâIIit's that it built an evaluation engine capable of reasoning about Terraform's execution model without actually running Terraform. When you write a Terraform security rule in most tools, you're pattern matching against static text. tfsec constructed an abstract syntax tree from your Terraform code and evaluated it with context about resource relationships, variable values, and even Terraform functions.
A naive pattern matcher would miss the security issue because "0.0.0.0/0" isn't directly in the resource block. tfsec's expression evaluator would execute the concat() function, recognize that the resulting array contains the dangerous CIDR block, and flag rule aws-ec2-no-public-ingress-sgr . This expression-aware analysis extended to understanding format() , join() , conditional expressions, and even locals that reference other locals.
The rule engine itself was plugin-based, with each check implemented as a Go function that received parsed resource data and returned violations. Rules were organized by provider (AWS, Azure, GCP) and resource type, with metadata including severity, description, remediation advice, and links to compliance frameworks. Here's a simplified version of what a rule looked like internally: Beyond built-in rules, tfsec supported custom policies written in Rego, the policy language from Open Policy Agent. This was crucial for organizations with specific compliance requirements not covered by the default rule set. You could write a policy that enforced your company's tagging standards, naming conventions, or architectural patterns: tfsec's performance characteristics made it viable for pre-commit hooks and fast feedback loops. It scanned typical Terraform codebases in under a second by avoiding the overhead of initializing Terraform providers or making API calls. The tool parsed HCL using HashiCorp's own hcl library, built a dependency graph, evaluated expressions in topological order, and ran all enabled checks in parallel across goroutines. This architecture meant scanning time scaled linearly with codebase size rather than exhibiting the exponential growth of tools that performed full Terraform plan operations.
The output flexibility was another strength. tfsec could emit findings in JSON for programmatic processing, SARIF for GitHub Code Scanning integration, JUnit XML for CI dashboards, or human-readable terminal output with color-coded severity levels and code snippets showing exactly where issues occurred. This made it easy to fail CI builds on high-severity findings while allowing warnings to pass through for visibility without blocking deployments.
The biggest gotcha with tfsec today is that it's officially deprecated. Aqua Security consolidated the scanning engine into Trivy, which means tfsec won't receive new cloud provider rules, bug fixes beyond critical security issues, or updates to support new Terraform language features. If you're using Terraform 1.8+ with new HCL syntax, tfsec might not parse it correctly. The deprecation isn't suddenâIIthe maintainers provided clear migration paths and Trivy inherited tfsec's entire rule setâIIbut it means any new adoption is technical debt you're deliberately taking on.
The more fundamental limitation is inherent to static analysis: tfsec has no runtime context. It can't tell you if an S3 bucket is genuinely public because your bucket policy might be managed outside Terraform, or permissions might be inherited from organizational SCPs. It can't detect if your RDS instance is actually exposed because it doesn't know your VPC's route tables or network ACLs. This creates false positives that require manual triage. The tool provides ignore comments ( #tfsec:ignore:aws-s3-enable-bucket-encryption ) to suppress findings, but these clutter your Terraform code and require discipline to document why each exception is acceptable. Additionally, tfsec scans what you've written, not what Terraform will actually createâIIif your Terraform provider has default values that secure a resource, tfsec might still flag it as misconfigured because those defaults aren't in your code.
Use if: You're already running tfsec in production pipelines and need time to plan a migrationâIIit still works fine for current Terraform versions and won't suddenly break. You're doing a security audit of legacy Terraform code and need a quick scan without setting up a new tool. You're evaluating Trivy and want to understand its Terraform scanning heritage by examining the original implementation. Skip if: You're starting a new project or greenfield infrastructureâIIgo directly to Trivy, which provides the same Terraform rules plus container scanning, Kubernetes manifests, and SBOM generation in a single actively maintained tool. You need the latest cloud provider security checksâIITrivy gets updated rules while tfsec does not. You want commercial support or long-term viability guaranteesâIItfsec is maintenance-mode open source while Trivy has Aqua Security's full backing. You're investing in a comprehensive DevSecOps pipelineâIITrivy's broader scope (IaC, containers, dependencies) gives you a unified security scanning interface rather than maintaining multiple specialized tools.
Inside the Uncensored AI Arsenal: A Critical Look at Offensive Security Model Repositories Flowsint: Building a Graph-Based OSINT Platform That Doesn't Choke on Async Enrichment Inside the Uncensored AI Arsenal: A Critical Look at Offensive Security Model Repositories Flowsint: Building a Graph-Based OSINT Platform That Doesn't Choke on Async Enrichment Designed to run locally and in your CI pipelines, developer-friendly output and fully documented checks mean detection and remediation can take place as quickly and efficiently as possible tfsec takes a developer-first approach to scanning your Terraform templates; using static analysis and deep integration with the official HCL parser it ensures that security issues can be detected before your infrastructure changes take effect.
tfsec is an Aqua Security open source project. Learn about our open source work and portfolio here . Contact us about any matter by opening a GitHub Discussion here Harvested Online Documentation & Reference Sources • https://khimananda.com/blog/iac-security-scan-with-tfsec-checkov-terrascan • https://kokil.com.np/blog/iac-security-scan-with-tfsec-checkov-terrascan • https://www.decryptiondigest.com/blog/terraform-iac-security-scanning-tfsec-checklist • https://oneuptime.com/blog/post/2026-02-23-how-to-use-tfsec-for-static-security-analysis/view • https://khimananda.com/blog/tflint-and-tfsec-in-your-pipeline • https://github.com/aquasecurity/tfsec • https://github.com/CyberFvde/tfsec • https://starlog.is/articles/cybersecurity/aquasecurity-tfsec/ • https://aquasecurity.github.io/tfsec/v1.28.1/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Infrastructure As Code Security Scanner Using Tfsec.
[*] Metasploit Scan Running on Target Subnet for Infrastructure As Code Security Scanner Using Tfsec... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |