Complete Technical Paper Content — Insider Threat Detection Using Machine Learning Python Github
Overview & System Context
Insider Threat Detection Using Machine Learning Python Github: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~1053 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Detects insider threats using machine learning by analyzing user behavior, system access, and anomalies. Includes simulated logs, anomaly detection models, a combined dashboard, explainability tools, graph analysis, and red team simulation.
Detects insider threats using machine learning by analyzing user behavior, system access, and anomalies. MSc Cybersecurity Thesis Project - Nottingham Trent University A comprehensive machine learning framework for behavioral anomaly detection and explainable insider threat identification This repository contains the complete implementation of an advanced insider threat detection system developed as part of an MSc Cybersecurity thesis at Nottingham Trent University. The project addresses critical gaps in current Security Information and Event Management (SIEM) systems by implementing explainable AI techniques to reduce "alert fatigue" while maintaining high precision in threat detection.
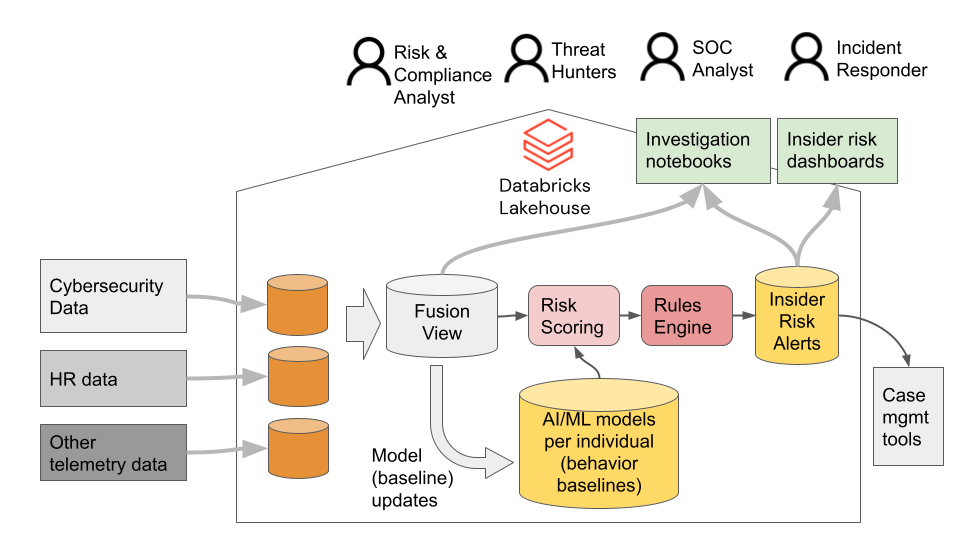
Figure 1: GitHub - databricks-industry-solutions/insider-threat-risk · GitHub This project represents ongoing research in cybersecurity and machine learning. Contributions are welcome in the following areas: If this project helps your research or interests you, please consider giving it a star! This project represents the culmination of advanced research in cybersecurity, machine learning, and explainable AI, specifically designed to address real-world challenges in insider threat detection while maintaining the highest standards of academic rigor and practical applicability.
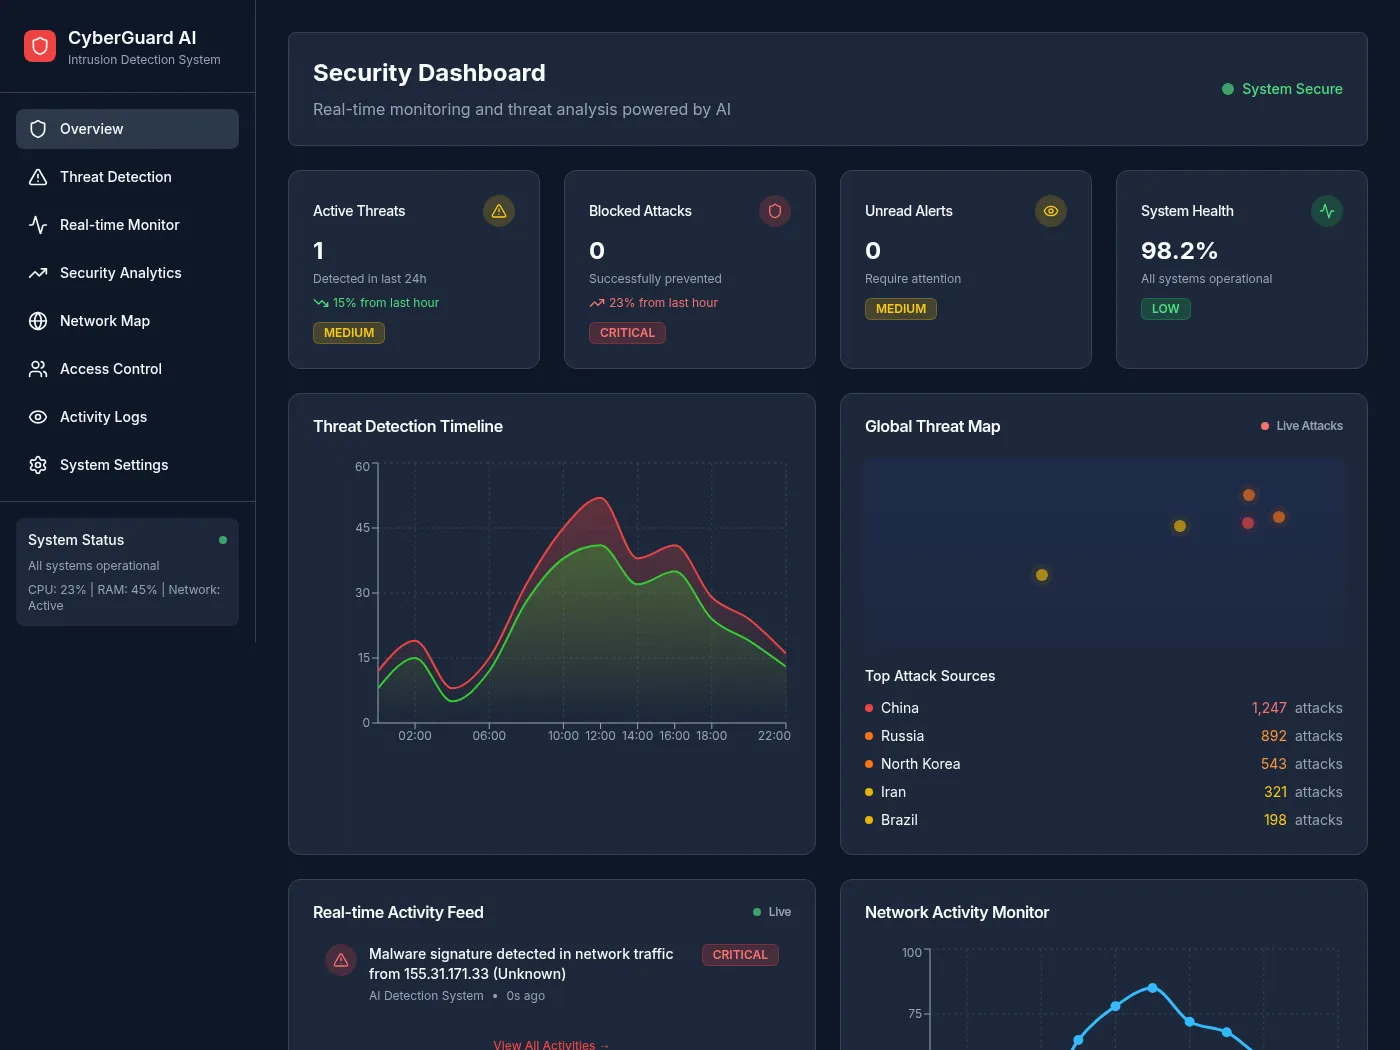
Explainable AI insider threat detection system with 100% precision. Isolation Forest + SHAP framework processing 26.2GB multi-modal behavioral data (CERT/TWOS datasets). Designed for SOC analyst workflow integration. Figure 2: AI-Powered Intrusion Detection System Dashboard | Built with Blink 2. System Architecture & Core Working Principles User Behavior Analytics (UBA) for Insider Threat Detection. A Python-based system that uses machine learning (Isolation Forest) to analyze user behavior logs, detect anomalies, and identify potential insider threats within an organization's network.
The project includes data preprocessing, model training, and a Flask API for anomaly detection. User Behavior Analytics (UBA) for Insider Threat Detection. A Python-based system that uses machine learning (Isolation Forest) to analyze user behavior logs, detect anomalies, and identify potential insider threats within an organization's network. The project includes data preprocessing, model training, and a Flask API for anomaly detection.
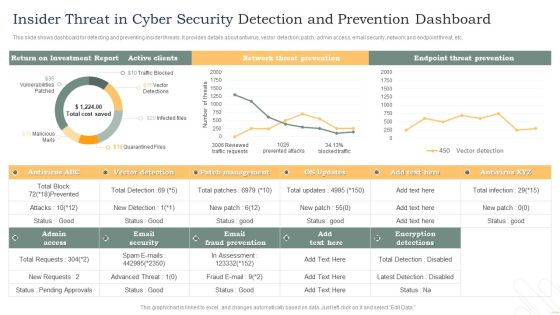
Artificial Intelligence (AI) is revolutionizing cybersecurity. In 2025, AI-driven threat detection helps identify complex attacks faster than traditional methods. This tutorial walks you through building an AI-powered threat detection system using Python, machine learning algorithms, and open-source tools. Before you begin, determine the objectives of your AI system. Decide what threats you want to detect, such as: Figure 3: Insider Threat In Cyber Security Detection And Prevention Dashboard ...
Clearly defining goals ensures your AI model is trained on the right data and produces actionable insights. AI models require high-quality data. Collect logs and telemetry from multiple sources: Store your data in a centralized data lake for further processing. Use tools like ELK (Elasticsearch, Logstash, Kibana) for ingestion and indexing.
Feature engineering is critical for making your AI model effective in detecting subtle attack indicators. 3. Software Implementation, Frameworks & Protocols Evaluate model performance using metrics like precision, recall, and F1-score. Adjust hyperparameters to reduce false positives.
Enrich your detection system by integrating threat intelligence feeds (STIX/TAXII) to detect known bad actors. Use dashboards for real-time visualization of anomalies. Kibana, Grafana, or Splunk can help display: Threat landscapes evolve. Regularly retrain your AI model with new data and update feature sets to stay ahead of emerging attack techniques.
AI-powered threat detection systems are a game-changer for cybersecurity. By combining machine learning with threat intelligence and automation, you can detect and respond to sophisticated attacks faster than ever. Whether you’re securing a small network or an enterprise infrastructure, implementing this system will significantly strengthen your defenses. A comprehensive machine learning and deep learning pipeline for detecting insider threats using the CERT r4.1 dataset. This project combines unsupervised anomaly detection, supervised machine learning, and advanced deep learning architectures to identify anomalous user behavior in enterprise environments.
Visual representation of the project's machine learning pipeline for insider threat detection Insider threats—security incidents perpetrated by individuals with legitimate access represent a critical challenge for enterprise security. This project develops an end-to-end detection system that: 4. Practical Deployment, Analysis & Case Studies This project uses the CERT Insider Threat Test Dataset v4.1 (r4.1) , a synthetic but realistic corpus designed to emulate enterprise user behavior and insider threat scenarios.
Purpose : Foundation of the pipeline - data loading, cleaning, and initial feature engineering When to use : Run after preprocessing to generate anomaly labels for supervised learning Purpose : Advanced behavioral feature engineering and traditional machine learning baselines When to use : Run after anomaly detection to establish baseline performance and identify important features When to use : Run last in the pipeline, after establishing baselines and consensus labels This project uses synthetic data designed to simulate realistic enterprise scenarios without exposing real user information.
When adapting this approach to real-world data: This project is for educational and research purposes. Please cite appropriately if using in academic work. 5. Performance Evaluation & Extended Technical Observations A comprehensive machine learning and deep learning pipeline for detecting insider threats using the CERT r4.1 dataset. This project combines unsupervised anomaly detection, supervised machine learning, and advanced deep learning architectures to identify anomalous user behavior in enterprise environments.
An AI-powered system for detecting insider threats using machine learning. This project combines unsupervised anomaly detection (Isolation Forest) with supervised classification (XGBoost) for comprehensive threat identification and explainability. This system analyzes user behavior within an organization to identify potential insider threats. It leverages: This repository does not include a Dockerfile . The commands below are example placeholders — add a Dockerfile at the repository root or adjust the build context before running them.
Note : The dataset is not included in this repository. Download from kilthub.cmu.edu and place in the dataset/ directory. The inference and deployment scripts expect trained model files at the following paths (relative to the repository root): Place your trained model pickle files at these locations, or update the paths in deployment/server.py and inference/02_inference_hybrid_approach/hybrid_inference.py .
Note: Notebooks and training scripts use DuckDB files for faster access. For example, several notebooks expect dataset/supervised_dataset.duckdb and specific table names (e.g., labeled_training_data_new_approach ). Use the scripts in data_transformation_and_preprocessing/02_load_to_duckdb/ and the preprocessing notebooks to generate the DuckDB files and tables before running the training notebooks.
Harvested Online Documentation & Reference Sources • https://github.com/flatmarstheory/AI-Powered-Insider-Threat-Detection-System • https://github.com/thekarunakarreddy/Automated-Detection-of-Insider-Threats-in-SOC-Using-SIEM-Data-and-Machine-Lear ning-Techniques • https://github.com/iamAgbaCoder/UBA-Insider-Threat-Detection • https://solutionviews.com/tutorial/how-to-build-ai-powered-threat-detection-system • https://github.com/RobertoDure/Insider_Threat_Detection_with_CERT • https://github.com/AmanJ4588/insider_threat_detection_ai
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Insider Threat Detection Using Machine Learning Python Github.
[*] Metasploit Scan Running on Target Subnet for Insider Threat Detection Using Machine Learning Python Github... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |