Complete Technical Paper Content — Insider Threat Detection Using User Behavior Analytics
Overview & System Context
Insider Threat Detection Using User Behavior Analytics: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8624 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Netskope Behavior Analytics looks at patterns of human behavior, and then applies algorithms and statistical analysis to detect meaningful anomalies from those patterns—anomalies that indicate potential threats. Instead of tracking devices or security events, behavior analytics tracks users. Analyzing this activity will help detect insider threats, compromised accounts, compromised devices, rogue insiders, data exfiltration, lateral movement, anomalous behavior, and advanced persistent threats.
The Insider Threats & Advanced Compromise page provides information about the various types of detected insider threats and compromised accounts. Use the Insider Threats & Advanced Compromise dashboard to address some common use cases, such as: Access to this page requires authorization. You can try signing in or changing directories .
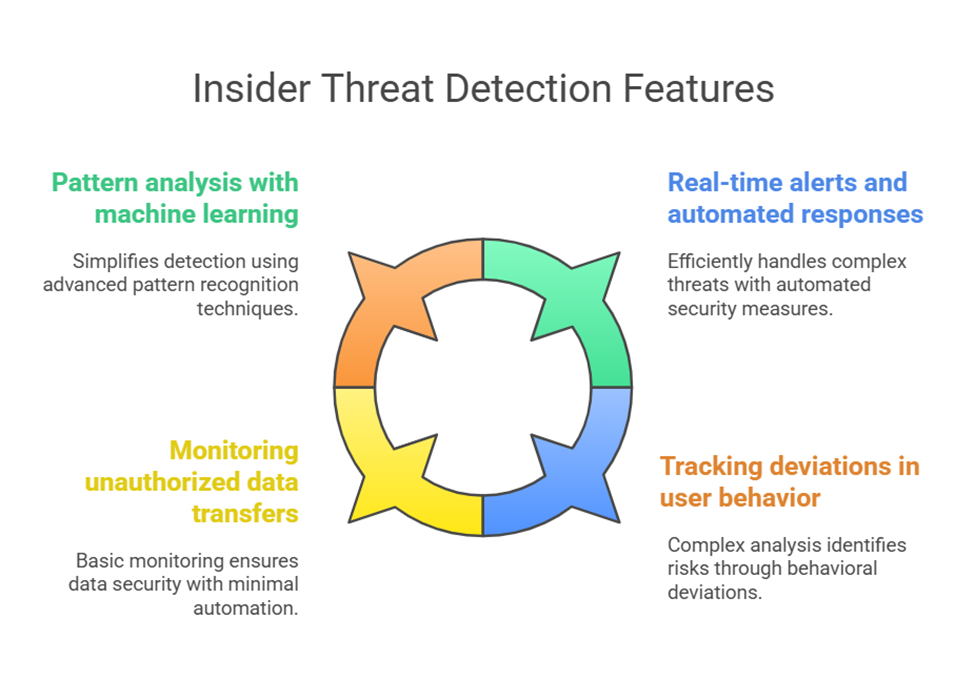
Detecting anomalous behavior within an organization is often complex and time-consuming. Microsoft Sentinel's User and Entity Behavior Analytics (UEBA) simplifies this challenge by continuously learning from your data to surface meaningful anomalies that help analysts detect and investigate potential threats more effectively. Figure 1: Top 10 Insider Threat Detection Software This article explains what Microsoft Sentinel User and Entity Behavior Analytics (UEBA) is, how it works, how to onboard to it, and how to use UEBA to detect and investigate anomalies to enhance your threat detection capabilities.
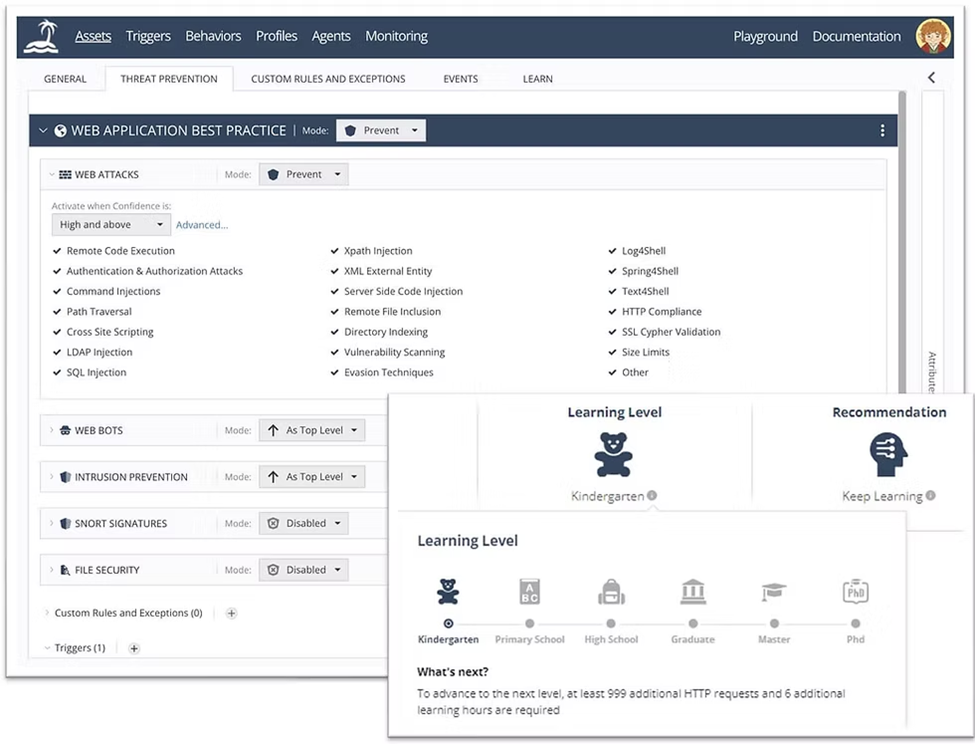
Microsoft Sentinel UEBA uses machine learning to build dynamic behavioral profiles for users, hosts, IP addresses, applications, and other entities. It then detects anomalies by comparing current activity to established baselines, helping security teams identify threats such as compromised accounts , insider attacks , and lateral movement . UEBA assigns risk scores to anomalous behaviors, taking into account the associated entities, severity of the anomaly, and context, including: This diagram shows how you enable UEBA, and how UEBA analyzes data and assigns risk scores to prioritize investigations: Figure 2: Top 10 Insider Threat Detection Software For more information about which anomalies UEBA detects, see Anomalies detected by the Microsoft Sentinel machine learning engine .
UEBA is natively integrated into Microsoft Sentinel and the Microsoft Defender portal, providing a seamless experience for security operations teams and embedded experiences that enhance threat investigation and response. Enable UEBA in Microsoft Sentinel and connect key data sources , such as Microsoft Entra ID, Defender for Identity, and Office 365. For more information, see Enable entity behavior analytics .
Install the UEBA Essentials solution , a collection of dozens of pre-built hunting queries curated and maintained by Microsoft security experts. The solution includes multi-cloud anomaly detection queries across Azure, Amazon Web Services (AWS), Google Cloud Platform (GCP), and Okta. Installing the solution helps you get started quickly with threat hunting and investigations using UEBA data, instead of building these detection capabilities from scratch.
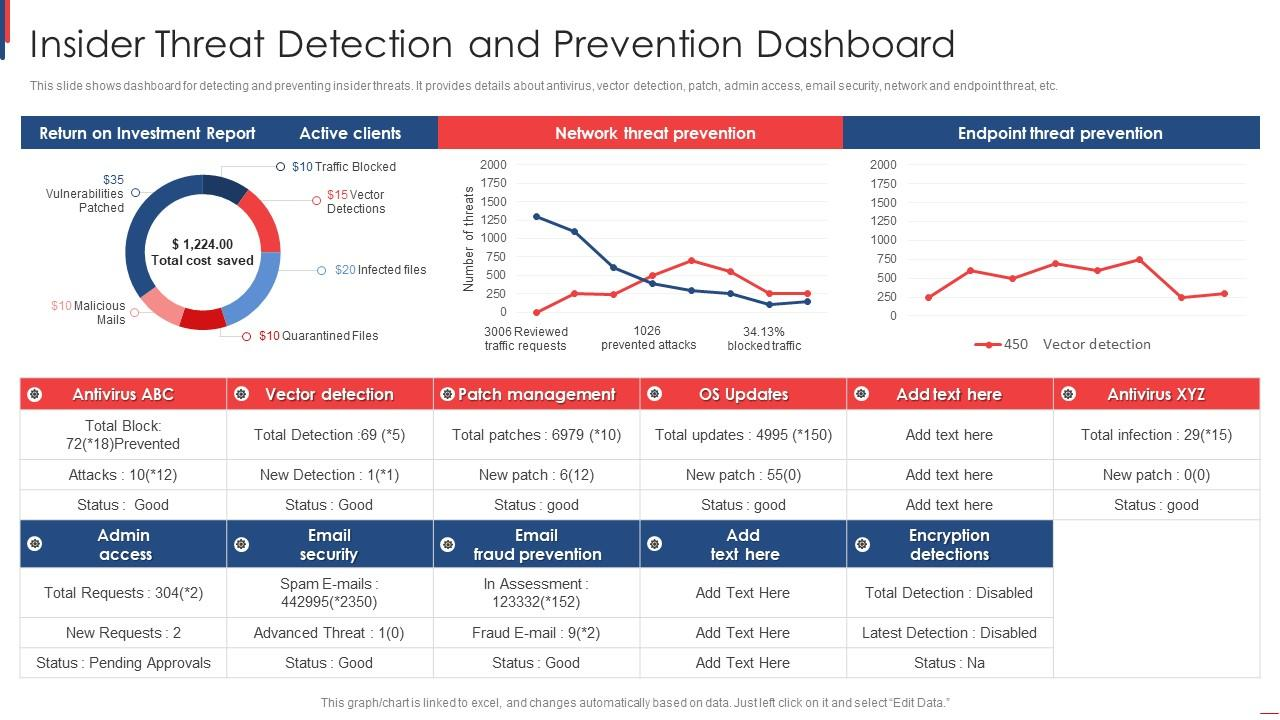
Figure 3: Insider Threat Detection And Prevention Dashboard PPT Slide For information about installing Microsoft Sentinel solutions, see Install or update Microsoft Sentinel solutions . Integrate UEBA insights into workbooks, incident workflows, and hunting queries to maximize their value across your SOC workflows.
Microsoft Sentinel stores UEBA insights across several tables, each optimized for a different purpose. Analysts commonly correlate data across these tables to investigate anomalous behavior end to end. The UEBA behaviors layer is a separate capability that you enable independently from UEBA. The SentinelBehaviorInfo and SentinelBehaviorEntities tables are only created in your workspace if you enable the behaviors layer.
This screenshot shows an example of data in the UserPeerAnalytics table with the eight highest-ranked peers for the user Kendall Collins. Sentinel uses the TF-IDF algorithm to normalize weights when calculating peer ranks. Smaller groups carry higher weight. UEBA provides two scores to help security teams prioritize investigations and detect anomalies effectively: While these scores serve different purposes, you can expect some correlation. High anomaly scores often align with high investigation priority, but not always. Each score provides unique insight for layered detection.
By surfacing anomalies in investigation graphs and user pages, and prompting analysts to incorporate anomaly data in hunting queries, UEBA facilitates faster threat detection, smarter prioritization, and more efficient incident response. This section outlines the key UEBA analyst experiences available in the Microsoft Defender portal. The Defender portal home page includes a UEBA widget where analysts immediately have visibility into anomalous user behavior and therefore accelerate threat detection workflows. If the tenant isn't onboarded yet to UEBA, this widget also provides security admins quick access to the onboarding process.
Analysts can quickly assess user risk using UEBA context displayed in side panels and the Overview tab on all user pages in the Defender portal. When unusual behavior is detected, the portal automatically tags users with UEBA anomalies helping prioritize investigations based on recent activity. For more information, see User entity page in Microsoft Defender . Each user page includes a Top UEBA anomalies section, showing the top three anomalies from the past 30 days, along with direct links to pre-built anomaly queries and the Sentinel events timeline for deeper analysis.
During incident investigations, analysts can launch built-in queries directly from incident graphs in the Defender portal to retrieve all user anomalies related to the case. When analysts write Advanced Hunting or custom detection queries using UEBA-related tables, the Microsoft Defender portal displays a banner that prompts them to join the Anomalies table. This enriches investigations with behavioral insights and strengthens the overall analysis.
While UEBA builds baseline profiles to detect anomalous activity, the new UEBA behaviors layer aggregates related events from high-volume raw security logs into clear, structured, meaningful behaviors that explain "who did what to whom" at a glance. By converting fragmented logs into coherent behavior objects, the behaviors layer accelerates threat hunting, simplifies detection authoring, and provides richer context for UEBA anomaly detection. Together, these capabilities help analysts quickly understand not just that something anomalous happened, but what happened and why it matters.
For more information, see Translate raw security logs to behavioral insights using UEBA behaviors in Microsoft Sentinel . UEBA is included with Microsoft Sentinel at no extra cost. UEBA data is stored in Log Analytics tables and follows standard Microsoft Sentinel pricing. For more information, see Microsoft Sentinel pricing . This article provides an in-depth analysis of the definition, architecture, and core mechanisms of User Behavior Analytics (UBA) technology, essential for enhancing an organization's insider threat response capabilities. Through practical configuration and operational strategies, it offers key insights for successful UBA adoption, contributing to strengthening detection capabilities against complex insider threats such as data exfiltration and privilege misuse.
Key answer: Insider threat detection with user behavior analytics (UBA) works by establishing a baseline of normal activity for users and entities within an organization. It then continuously monitors for deviations from these baselines, scoring anomalous behaviors based on their potential risk. High-risk patterns, such as unusual access to sensitive data or attempts at data exfiltration, are investigated to prevent or mitigate security incidents.
In an organization's security threat landscape, insider threats are persistently easy to overlook. While defense systems against external attacks are becoming more sophisticated, threats originating from users with legitimate access to internal systems and data are extremely difficult to detect. Industry reports, such as the Verizon DBIR report, indicate that a significant number of data breaches are caused by insiders or involve insider actions. User Behavior Analytics (UBA) is one of the key technologies for effectively countering such insider threats.
UBA transcends the limitations of simple rule-based detection, focusing on proactively identifying potential threats by learning users' normal behavior patterns and identifying anomalous activities through the use of machine learning and statistical analysis. This post provides in-depth insights, from the technical overview of UBA to architectural analysis, core mechanisms, performance comparisons, and practical configuration and operational strategies, guiding organizations to substantially strengthen their insider threat response capabilities.
UBA is a security technology that continuously monitors and analyzes user access patterns to systems, applications, and data to establish a baseline of normal behavior, then detects anomalous activities that deviate from this baseline. It particularly excels at identifying 'unknown unknowns' – threats that traditional signature-based or rule-based security solutions often miss. The core values of UBA can be summarized into three main points: 2. System Architecture & Core Working Principles UBA is often operated in conjunction with SIEM (Security Information and Event Management) or SOAR (Security Orchestration, Automation and Response) solutions. Platforms like Seekurity SIEM collect various logs and provide them to the UBA engine, which then generates anomaly detection alerts that are centrally managed, enabling faster and more systematic threat response. Furthermore, in cloud environments, cloud activity logs collected by solutions like FRIIM CNAPP can be utilized as a key data source for UBA, enhancing cloud insider threat detection capabilities.
The architecture of a UBA system typically consists of four main stages: data collection, data processing and storage, behavioral analysis, and risk scoring and alerting. Each component interacts organically to provide a sophisticated analysis environment for insider threat detection. The data flow is structured as a pipeline where logs are collected from each data source, stored via the data processing layer, analyzed by the behavioral analytics engine to assign risk scores, and finally, alerts are delivered to SIEM/SOAR. In this process, Seekurity SIEM is responsible for log collection and normalization, as well as the integrated management of UBA alerts, maximizing visibility across overall security operations.
The most fundamental mechanism of UBA is to learn users' normal behavior patterns to establish a baseline, and then detect activities that deviate from this baseline as anomalies. This process is carried out through statistical analysis and machine learning techniques. Initially, user activity data is collected over a specific period to learn each user's login times, accessed systems, data usage, and network traffic patterns.
A notable point is that this baseline is not static but dynamically updated. When a user's work patterns change or roles are altered, UBA re-learns the baseline based on new data to reduce false positives and increase detection accuracy. For instance, if a user typically accessed specific servers only during certain hours, but suddenly logs in from a different region late at night to download a large volume of files, this behavior can be immediately classified as anomalous through baseline learning.
Below is an example of a Sigma Rule that generates anomaly detection rules based on user login history in a typical UBA system. This illustrates logic similar to how a UBA engine processes data internally. The Sigma Rule above shows conceptual anomaly detection logic, but an actual UBA engine determines `unusual_time` or `unusual_ip` through dynamic behavioral pattern analysis rather than static rules. For example, the KYRA AI Guardrail can be used to develop complex sequence-based anomaly detection models and integrate them into the UBA engine. This strengthens the predictive capabilities against unknown attack techniques.
Beyond analyzing individual user behavior, UBA offers the capability to detect anomalies by comparatively analyzing the actions of peer groups – users belonging to similar roles or departments. If most users within a specific group do not access a particular resource, but one user repeatedly does, this can be considered a deviation from the normal behavioral pattern of that group.
For example, while the typical work of an accounting department is limited to accessing financial systems and specific spreadsheet files, an attempt by a user in that department to suddenly connect to a development server and download source code would be immediately classified as anomalous behavior through peer group analysis. This is identified as an anomaly when compared to the group's general behavior pattern, even if it wasn't part of the individual user's past behavior baseline.
The various detected anomalous behaviors are not simply listed; their risk is assessed through an integrated risk scoring mechanism. Each anomaly is assigned a predefined severity score, and these scores accumulate over time to calculate an overall risk score for each entity, such as user accounts, hosts, and applications. A higher score indicates a greater likelihood that the entity is exposed to a threat.
This risk scoring provides prioritization, allowing security teams to focus on the most critical threats amidst numerous alerts. An easily overlooked aspect is that multiple low-severity anomalies can accumulate to form a high-risk score. This is highly effective in identifying complex attack flows, such as Advanced Persistent Threats (APTs), which are difficult to detect through single events.
The detection accuracy and effectiveness of UBA depend on how richly and accurately data is integrated for analysis. Logs collected from various data sources are more than just records; they are essential for understanding the context of user activities and adding depth to threat analysis. The core of data source integration lies in the process of log normalization and enrichment. Logs originating from different systems have varying formats and field names, so they must be converted into a standardized format that the UBA engine can commonly understand. Seekurity SIEM strongly supports these log normalization and parsing capabilities.
Enrichment is the process of adding additional contextual information to raw log data to enhance its analytical value. For instance, geographical location, owning organization information, and reputation scores can be added to IP address information. User account information can be linked with details such as department, job title, privilege groups, and past security event history, providing deeper answers to questions like 'who, when, where, what, and how'.
Below is an example of rsyslog configuration for forwarding logs to Seekurity SIEM. This represents a basic step for data collection in a UBA system. Logs collected with such configurations are analyzed by the UBA engine to understand the context of user behavior, contributing to accurate threat detection. Cloud activity logs collected by cloud security solutions like FRIIM CNAPP can also be utilized as important enrichment data.
UBA exhibits characteristics that contrast with traditional rule-based SIEM detection methods in several aspects, showing prominent performance differences, especially in insider threat detection. The following table compares the main features of the two approaches. By learning dynamic user behavior patterns and building predictive models, UBA provides visibility into 'unknown' insider threats that are difficult to detect with traditional SIEM rules. This particularly shines in scenarios such as data exfiltration due to misused legitimate privileges, privilege escalation attempts, and anomalous activities after account compromise. It identifies statistically significant deviations from normal patterns using statistical anomaly detection techniques.
In contrast, traditional SIEM relies on predefined signatures or rules, thus having limitations in detecting new attack techniques or subtle behavioral changes. However, it remains efficient for quickly and accurately detecting known threats or specific compliance rule violations. Therefore, the most effective approach is to integrate UBA and Seekurity SIEM's rule-based detection to operate them complementarily. UBA detects early signs of anomalous behavior, and SIEM correlates this information with existing security events to provide a comprehensive threat context, thereby maximizing overall threat response capabilities.
Successful deployment and optimization of a UBA system require a systematic approach. The following are key steps for configuring and optimizing UBA in a production environment. First and foremost, it is essential to identify and integrate the core data sources required for UBA analysis. This includes logs generated by Active Directory, endpoint security solutions, VPNs, network devices, applications, databases, and cloud security platforms such as FRIIM CNAPP/CSPM. Centralizing logs to Seekurity SIEM through various methods like data collection agents, APIs, and Syslog forwarding is crucial.
After data integration, the UBA system learns each user's normal behavior baseline based on data collected over a certain period (e.g., 2 weeks to 1 month). During this initial learning phase, false positives may occur, so the security team must carefully review alerts and provide feedback to improve model accuracy. In this process, the KYRA AI Guardrail can be utilized to develop customized machine learning models for specific threat scenarios and integrate them into the UBA engine to enhance detection performance.
The risk scores and alert thresholds generated by UBA must be optimized to match the organization's security policies and threat tolerance levels. A threshold that is too low can lead to excessive alerts, increasing the security team's fatigue, while a threshold that is too high might miss actual threats. Continuous monitoring and feedback are crucial to finding the appropriate balance. It is particularly effective to apply stricter thresholds for users accessing critical data or systems.
One of the greatest advantages of UBA is its ability to automate threat response through tight integration with Seekurity SIEM and SOAR. When UBA detects an anomalous activity with a high-risk score, Seekurity SIEM integrates this for monitoring, and Seekurity SOAR executes predefined playbooks, enabling rapid response. The UBA alert example in JSON format above is sent to Seekurity SIEM, providing clear context to analysts, and enables automated actions such as user account lockout and network access blocking via Seekurity SOAR playbooks. Such practical integrated configuration is essential for reducing threat response times and maximizing security operations efficiency.
As important as the adoption of a UBA system is its continuous performance management through monitoring and operations. Maintaining the accuracy of the UBA model and proactively addressing potential issues are crucial for effective insider threat detection. Seekurity SIEM's dashboard visualizes these metrics, helping the operations team grasp the UBA system's status at a glance.
An easily overlooked aspect during UBA operations is 'Model Drift.' User behavior patterns naturally evolve with organizational changes (e.g., adoption of new systems, expansion of remote work, large-scale personnel transfers). If the model fails to adequately reflect these changes, false positives or false negatives may increase, making periodic model retraining and updates essential.
Furthermore, as UBA systems process sensitive user data, utmost attention must be paid to data privacy and regulatory compliance (e.g., personal information protection laws, GDPR). It is crucial to minimize data access privileges and establish measures for de-identification. Rapid response in the event of a UBA system failure is essential for service continuity. For example, if log ingestion is halted due to a data collection agent error, Seekurity SIEM's log collection monitoring function should immediately detect the failure, and the agent must be restarted or its settings checked. If the UBA engine itself malfunctions and analysis stops, Seekurity SOAR playbooks can be used to automate actions such as switching to a backup system or sending alerts to monitoring systems. This contributes to minimizing detection gaps caused by failures and maintaining the defense system against insider threats.
Insider threats are detected with behavior analytics by first establishing a baseline of normal user and entity behavior through machine learning and statistical analysis of activity data. The system then continuously monitors for deviations from this learned baseline, identifying anomalous activities that may indicate a threat. These anomalies are further evaluated through peer group analysis and aggregated into risk scores for prioritization.
Risk scoring in user behavior analytics is a mechanism where individual anomalous behaviors are assigned severity scores, which then accumulate to calculate an overall risk score for entities like user accounts or systems. This score considers factors such as the anomaly's severity, frequency, and the user's role. It helps security teams prioritize investigations, as a higher score indicates a greater likelihood of a threat, even from multiple low-severity events.
Behaviors indicating data exfiltration by an insider often involve significant deviations from established norms. Examples include a user downloading an unusually large volume of files, accessing file servers or sensitive data not typically associated with their role, or accessing resources from atypical locations or at unusual times. Such actions, especially when combined with attempts to transfer data off-network or to unauthorized cloud storage, suggest potential data exfiltration.
What should organizations evaluate when choosing an insider threat detection solution? When choosing an insider threat detection solution, organizations should evaluate its capability to integrate diverse data sources for comprehensive visibility. Key criteria include the solution's machine learning and statistical analysis methods for baseline learning and accurate anomaly detection, as well as its risk scoring mechanisms for prioritizing threats. The ability to integrate with existing security operations platforms, its adaptability to evolving user behaviors, and robust data privacy features are also essential considerations.
Balancing insider monitoring with employee privacy requires careful consideration of data collection, access, and usage policies. Organizations should focus monitoring efforts on behaviors directly related to security risks and minimize the collection of unnecessary personal data. Implementing strict access controls, data de-identification techniques, and adhering to relevant data privacy regulations are crucial steps to maintain privacy while ensuring effective threat detection.
3. Software Implementation, Frameworks & Protocols Insider threats are a persistent problem that can cause severe financial and reputational damage to organizations. UBA is establishing itself as an essential technology for effectively addressing these complex and difficult-to-detect insider threats. Through machine learning-based behavioral analysis, UBA overcomes the limitations of existing rule-based solutions and dramatically improves an organization's threat visibility by identifying unknown threats and subtle anomalies.
Key to UBA adoption are accurate data source integration, initial model learning and continuous tuning, and tight integration with unified security platforms like Seekurity SIEM/SOAR. This enables the establishment of a rapid and automated response system for detected threats. Furthermore, it is essential to actively leverage cloud activity logs provided by cloud security solutions like FRIIM CNAPP as data sources for UBA to strengthen insider threat detection capabilities in cloud environments.
Of course, UBA also has limitations, such as false positives during the initial learning period, resource consumption due to massive data processing, and the need for continuous model management. However, by acknowledging these limitations and approaching them with a systematic strategy, UBA will significantly strengthen an organization's crisis response capabilities against various insider threat scenarios, including data exfiltration, privilege misuse, and account takeover. Ultimately, the focus should be on protecting an organization's sensitive assets and ensuring business continuity through UBA.
In a controlled study by Horizon3 researchers, models that explicitly identified a trap in their reasoning still attacked it 73.4% of the time. Read the findings and see what they mean for canaries, decoys, and early detection. User and Entity Behavior Analytics (UEBA) detects threats by modeling what 'normal' looks like for each user, device, and service account, and alerting when behavior deviates significantly from that baseline. This fills the gap that signature-based SIEM rules cannot: a compromised account performing actions the legitimate user would never take, an employee slowly exfiltrating data over months, or a service account suddenly accessing hundreds of servers. This guide covers UEBA architecture, the detection use cases it addresses, data source requirements, vendor options, and the operational work required to get value from a UEBA deployment.
UEBA systems build statistical models of normal behavior for every entity they observe, users, devices, applications, and service accounts. Deviations from these baselines generate risk scores rather than binary alerts. Peer group analysis: Compares a user's behavior to that of their peer group (same department, role, or title). An accountant downloading 10GB of data is anomalous regardless of absolute thresholds, but it is especially anomalous if no other accountant has ever downloaded more than 500MB.
Time-based baselines: Models what is normal for a specific user at a specific time. A user logging in at 2am is only anomalous if that user never logs in at 2am, but for a SOC analyst with night shifts, 2am logins are expected. Entity stitching: Links events across data sources using common identifiers (username, IP, hostname) to build a unified timeline of what an entity did across all systems. This is how UEBA connects a VPN login, a file server access, and a cloud storage upload into a coherent story.
Risk score accumulation: Individual anomalies may be low-risk in isolation but combine to form a high-risk session. A user logging in from a new IP (+10 risk), accessing a file share they never access (+15 risk), and uploading to a personal cloud storage service (+30 risk) accumulates to a 55-point risk score that triggers an alert, even though no single event would have triggered a rule.
UEBA is not a general-purpose detection tool, it excels at specific threat scenarios that rule-based detection struggles with. An attacker with valid credentials behaves differently than the legitimate user, they access different systems, at different times, from different locations, and with different data access patterns. A malicious insider often acts within their legitimate access rights, making rule-based detection ineffective. UEBA detects the behavioral pattern even when individual actions are permitted.
Service accounts and admin accounts have broad access, UEBA establishes what each privileged account normally does and alerts on deviations. Successful credential stuffing produces a pattern: rapid logins from unusual IPs, failed logins preceding a successful one, access to account settings shortly after login.
Even when lateral movement uses legitimate credentials, the pattern is anomalous, a single account accessing dozens of systems in sequence is not normal user behavior. UEBA is only as good as the data fed into it. Missing data sources create blind spots that attackers can exploit. UEBA requires consistent timestamps (UTC synchronized), stable user identifiers (UPN or SAMAccountName, not display name), and reliable entity mapping (same user appearing as jsmith, john.smith, and J.Smith breaks entity stitching). Invest in data normalization before deploying UEBA, garbage in produces false positives and missed detections.
UEBA is available as a standalone product, as a SIEM add-on, or natively in cloud security platforms. Microsoft Entra ID Protection provides UEBA-style risk scoring for Azure AD identities, including: This is the fastest path to baseline UEBA for Microsoft-centric organizations, enable Entra ID Protection and configure risk-based Conditional Access policies immediately.
The most common UEBA failure mode is not technical, it is operational. Organizations deploy UEBA, get overwhelmed by alerts, and stop acting on them. Track how long analysts spend investigating each UEBA alert. Target: 15-20 minutes per alert. If investigations consistently take 45+ minutes, the alert is providing insufficient context, enrich alerts with entity timeline, peer comparison data, and historical risk score.
UEBA closes the detection gap that rule-based SIEM cannot address: slow account compromise, insider data theft within legitimate access boundaries, and lateral movement using valid credentials. The organizations that get value from UEBA invest first in data quality and normalization, start with 2-3 well-tuned use cases rather than enabling everything at once, and integrate UEBA risk scores into their SOAR workflows to automate first-response actions. Without this operational discipline, UEBA becomes another alert source that gets tuned out. With it, UEBA is one of the most effective detections for advanced threat actors.
A SIEM (Security Information and Event Management) collects and correlates logs, primarily using rules to generate alerts when specific conditions are met. UEBA (User and Entity Behavior Analytics) builds statistical models of normal behavior and alerts on deviations from those baselines. The key difference: SIEM rules require knowing what you are looking for in advance; UEBA detects unknown threats by recognizing that something is anomalous even if no rule matches it. In practice, most organizations deploy UEBA as an add-on to or integration with their SIEM, feeding UEBA risk scores back into SIEM correlation rules. They are complementary, not competing technologies.
Most UEBA platforms require 30-90 days of data ingestion to build statistically reliable behavioral baselines. During this period, anomaly detection is less accurate, the models do not yet know what 'normal' looks like for each entity. Plan for: 30 days minimum for basic user behavior patterns, 60 days for reliable peer group comparisons, 90 days for time-of-day and day-of-week seasonal patterns. Do not enable production alerting until baselines are established. Some platforms offer pre-built industry models as a starting point that accelerate baseline formation, but these should be treated as seeds, not replacements for organization-specific learning.
Yes, this is one of UEBA's strongest use cases. UEBA can detect the behavioral precursors to data exfiltration: unusual file access volume, access to data outside normal work scope, activity outside normal working hours, and searches for sensitive content. The critical requirement is integrating file access logs (from DLP, file servers, SharePoint, OneDrive) and HR data (termination dates, departing employees are the highest insider threat risk). With these data sources, UEBA can flag anomalous behavior days to weeks before data actually leaves, giving time to investigate and intervene before exfiltration occurs.
Is Microsoft Sentinel's UEBA feature sufficient or do we need a dedicated UEBA platform? Microsoft Sentinel's UEBA (entity behavior analytics) provides solid baseline functionality, entity risk scores, user and device timelines, anomaly detection for Azure AD sign-ins, and integration with Microsoft Defender signals. It is a good starting point for Microsoft-centric organizations and is included in the Sentinel pricing. Dedicated UEBA platforms like Exabeam or Securonix provide broader data source coverage (non-Microsoft environments), deeper pre-built use case libraries, more sophisticated insider threat models, and better visualization for analyst investigations. Choose Sentinel UEBA if you are primarily Microsoft-centric and want to avoid additional vendor spend; choose a dedicated platform if you have complex multi-vendor environments or specific regulatory insider threat requirements.
Entity stitching is the process of linking different identifiers for the same entity across data sources, for example, recognizing that 'jsmith', ' [email protected] ', 'CORP\\jsmith', and the IP address 10.0.1.45 all refer to the same person in different log sources. Without entity stitching, UEBA sees fragmented behavior and cannot build a coherent behavioral model. Entity stitching requires a reliable identity store (Active Directory) as the source of truth and consistent logging of user identifiers in each data source. Poorly stitched entities are the most common cause of UEBA false negatives, the anomalous behavior is in the logs, but it is attributed to different entity identities and never scores high enough to trigger an alert.
Key metrics for UEBA ROI reporting: (1) Mean Time to Detect (MTTD) for insider threat and compromised account scenarios, compare pre- and post-UEBA detection times using tabletop exercises with known scenarios; (2) True positive rate, percentage of UEBA alerts that result in confirmed security incidents; (3) Cases investigated that would not have been detected by rules, track alerts that did not match any SIEM rule; (4) Time to investigate per alert (target 15-20 minutes vs. 60+ minutes for manual log analysis); (5) Insider threat cases closed, if your program has an insider threat function, track cases originated by UEBA. Frame ROI in terms of breach cost avoidance using IBM or Ponemon data for your industry's average cost per incident.
25 actively exploited vulnerabilities with CVSS scores, exploit status, and patch availability. Print it, pin it, share it with your SOC team. Step-by-step 24-hour IR checklist covering detection, containment, eradication, and recovery. Built for SOC teams, IR leads, and CISOs.
50,000+ security professionals read Decryption Digest for early warnings on zero-days, ransomware, and nation-state campaigns. Free, daily, no spam. Cybersecurity professional with expertise in threat intelligence, vulnerability research, and enterprise security. Covers zero-days, ransomware, and nation-state operations for 50,000+ security professionals every morning.
4. Practical Deployment, Analysis & Case Studies Actionable threat intelligence for working practitioners. Free. No spam. Trusted by 50,000+ SOC analysts, CISOs, and security engineers. How to detect malicious insiders and compromised accounts using User and Entity Behavior Analytics. Practical implementation guide with real-world detection scenarios.
Insider threats account for 34% of all data breaches yet receive far less attention than external attacks. Whether malicious employees, negligent users, or compromised accounts—insiders have legitimate access that bypasses traditional perimeter defenses. Traditional security tools fail because insiders have authorized access . You need behavior-based detection.
UEBA establishes normal behavior baselines for users, then flags anomalies that indicate compromise or malicious activity. Insider threats require a fundamentally different detection approach. Traditional signature-based tools don't work when the attacker has legitimate credentials. Start small: Deploy UEBA for privileged users first, then expand to entire organization.
Need help implementing UEBA? Our threat detection team can assess your environment and design a phased deployment plan. S6 Security Labs has deployed UEBA solutions across 30+ enterprise environments, detecting insider threats averaging 12 days before traditional tools.
A first-hand account of A$250,000 in API-equivalent inference, a power-measured local compute cluster, 40-plus parallel agents, and why cheap AI is encouraging us to build the same things repeatedly. Modern supply chain attacks target package inputs, workflow code, CI/CD runners, release tokens and developer tooling. EDR is useful, but it cannot solve this alone. Security teams need to work with developers to build safer defaults across GitHub, Forgejo and Bitbucket pipelines.
S6SOC is the direction we are building toward: agentic security operations that sit around the tools organisations already run, prove telemetry and detections work, and make advanced SOC discipline available to smaller teams without taking control away from humans. Not all cyber threats come from outside your organization. Sometimes the biggest risk is already inside your network — a trusted employee going rogue, a compromised account, or a third-party contractor with too many access privileges.
As attack surfaces expand, those once-rare scenarios are becoming more common – and more expensive. According to the 2025 Ponemon Cost of Insider Risks Global Report , the average cost of insider threat incidents increased by more than 100% between 2018 and 2024. High-profile incidents have shown how damaging this can be in practice, from employees leaking sensitive internal data to attackers using stolen credentials to access millions of customer records. Verizon’s 2025 Data Breach Investigations Report estimates that compromised credentials were involved in 22% of all data breaches .
Even with intrusion prevention systems and antivirus software in place, these threats often go undetected until real damage has already been done. To address this growing risk, organizations are increasingly turning to User and Entity Behavior Analytics (UEBA) to identify suspicious activity that traditional security tools miss. Traditional security tools aren't designed to catch trusted users behaving maliciously. They're built to block known, external attackers, while allowing authorized users to go about their business.
However, this risk is more prevalent than many realize. According to Cybersecurity Insiders’ 2024 Insider Threat Report , 83% of organizations experienced at least one insider attack in the past year, up from 66% in 2019. Most organizations still rely on signature-based detection. These systems maintain a database of known attack patterns and block any traffic that matches them. If a hacker uses an exploit known to the system, it’s caught.
The problem is that insider threats rarely match known signatures. A legitimate employee accessing files they’re authorized to see doesn’t trigger alarms. An admin account downloading unusually large volumes of data may also go unnoticed — even though that behavior could indicate data exfiltration. In several widely reported breaches, attackers gained access using valid credentials and operated inside the network for extended periods without triggering traditional security controls.
In a breach disclosed in 2025, attackers used stolen credentials to access PowerSchool’s customer support systems , exposing personal data on more than 60 million students and teachers before the activity was detected. To address this gap, some organizations turn to behavioral detection systems such as IPS (Intrusion Prevention Systems) and IDS (Intrusion Detection Systems) . These tools establish a baseline of “normal” activity and flag deviations from it.
While more effective than signature-based tools, they often generate high volumes of false positives. A salesperson working late to close a deal might trigger alerts, or an engineer may need one-time access to production systems during an outage. Security teams end up spending valuable time investigating harmless anomalies instead of real threats. User and Entity Behavior Analytics (UEBA) addresses these limitations more directly. It builds on the behavioral approach of IPS and IDS but applies advanced analytics to reduce false positives and add context. Rather than flagging every deviation, UEBA builds risk profiles and prioritizes the alerts that matter.
UEBA uses machine learning to establish behavioral baselines for users and systems across your network. When activity deviates from those patterns — for example, an employee suddenly accessing files they’ve never touched before — the system calculates a risk score and alerts security teams to investigate. While UEBA is often associated with malicious insiders, it is just as effective at detecting compromised accounts. In many cases, unusual behavior is not intentional misuse, but the result of stolen credentials being used by someone else. Because UEBA focuses on behavior rather than intent, it can identify both scenarios when activity no longer matches established patterns.
Unlike User Behavior Analytics (UBA), which focuses only on people, UEBA also tracks entities such as devices, systems, and applications. This broader view allows security teams to spot abnormal behavior in infrastructure itself – like a compromised database acting out of character – not just suspicious user activity. For example, if an employee typically accesses 20 files per day but suddenly downloads 2,000 files at 3 a.m., UEBA would flag the behavior as suspicious and alert administrators before the data leaves the network.
UEBA begins by collecting activity data from across your network — including firewall logs, VPN connections, file access records, email activity, database queries, and application usage. It analyzes this data to build behavioral profiles for every user and entity. What files does an HR manager typically access? When does the marketing database usually see peak activity? Over time, these patterns form a baseline of what “normal” looks like.
Once those baselines are established, UEBA continuously compares current activity against them. Unusual behavior — for example, an accountant accessing HR files or a server making outbound connections to unfamiliar IP addresses — is flagged for manual review. Anomalies on their own don’t tell the full story. UEBA assigns risk scores by weighing multiple factors, including how unusual the behavior is, the user’s access privileges, the sensitivity of the data involved, and historical activity.
A low-level employee downloading gigabytes of customer data at 2 a.m. receives a higher risk score than a system administrator performing routine maintenance. When risk scores cross a defined threshold, alerts are escalated to security teams with all the details — what happened, who was involved, why it’s suspicious, and which systems or data may be at risk.
5. Performance Evaluation & Extended Technical Observations Analysts can then investigate the most concerning threats immediately. This allows them to act quickly if a threat is genuine — disabling compromised accounts, blocking suspicious connections, or isolating affected systems before damage spreads. UEBA is designed to complement existing security tools, not replace them. Its role is to add behavioral context, helping teams spot risky activity.
In practice, UEBA is often used alongside tools such as SIEM platforms and endpoint or network security controls. Those systems generate large volumes of alerts and logs. UEBA helps narrow them down by highlighting activity that looks genuinely unusual. UEBA is especially effective at detecting activity linked to compromised accounts, where valid credentials are used by someone other than the account owner. In these cases, behavior often changes suddenly — different access patterns, unusual data movement, or activity at odd times — making it easier to spot as a cause of concern.
Like any behavioral approach, UEBA depends on having enough consistent activity data to learn from. It is less effective in environments with very short-lived users or limited visibility. UEBA identifies risk rather than taking action itself. Investigation and response still rely on existing security controls and human judgment. UEBA addresses several persistent challenges that traditional security tools struggle to solve.
UEBA helps surface insider threats and compromised accounts that blend in with everyday activity — the kind of behavior traditional security tools are likely to miss because nothing seems overtly malicious. By continuously monitoring and ignoring lower-risk threats, UEBA reduces dwell time, giving security teams a better chance to contain incidents before damage spreads.
According to IBM’s 2025 Cost of a Data Breach Report , breaches involving stolen credentials take an average of 246 days to identify and contain, among the longest of any attack type, as attackers using valid credentials blend in with legitimate users. Security teams are often buried in alerts. UEBA’s contextual risk scoring highlights the activity most likely to represent real threats, so analysts spend less time chasing false alarms and more time investigating genuine incidents.
As environments grow more complex, UEBA can continuously analyze activity across large volumes of users, systems, and applications — something that simply isn’t possible to do manually at scale. This makes it easier to expand coverage without growing security teams at the same rate. UEBA systems require significant upfront configuration to establish accurate behavioral baselines — typically over a 30–90-day training period. During this time, organizations may see an excessively high volume of alerts as the system is fine-tuned towards what “normal” looks like.
Detection thresholds and risk scoring need tweaking regularly, though. Overly aggressive settings generate noise but being too lenient risks threats slipping through the cracks. UEBA is not a set-and-forget solution. While it automates detection and alert prioritization, security analysts must still review alerts, determine whether activity is genuinely malicious, and take action to contain incidents. This requires ongoing human judgment and incident response expertise.
Organizations have limited control over how third-party platforms generate and report data. Different tools use different APIs, schemas, and formats, which can make it harder for UEBA to analyze activity consistently across the environment. Gaps in data coverage can create blind spots where threats go undetected. Before deployment, organizations should verify that their UEBA solution supports all critical platforms and systems.
Behavioral monitoring can raise concerns among employees, who may see it as a lack of trust. Organizations need to clearly communicate why UEBA is being used and how it protects both the business and its employees, rather than monitoring individuals as a punishment. You may trust your employees — but insider threats often emerge from unexpected places. A long-standing staff member misusing access, a compromised account, or someone who unknowingly falls for a phishing attack can all introduce serious risk. By the time unusual behavior becomes obvious, the damage is often already done.
UEBA is designed to catch those signals earlier by flagging potential threats that other tools miss. For organizations ready to take insider risk more seriously, UEBA provides a more practical, scalable way to detect and respond before small issues turn into major incidents. Insider threats are no longer limited to disgruntled employees or corporate spies. They’ve evolved into something broader, and often-times harder to spot. From compromised user accounts to negligent mistakes and third-party overreach, insider incidents are shaped by behavior, not just intent.
For analysts and security practitioners, that means going beyond static rules and surface-level alerts. Understanding behavior patterns — what’s normal, what’s abnormal, and why it matters — is key to spotting early warning signs, reducing noise, and responding with confidence. When you can connect the dots between access, intent, and activity, you’re one step ahead of the threat.
This guide takes a closer look at the modern shape of insider threats: Who’s behind them, how threats and risk can slip through the cracks, and why identity alone isn’t enough to protect your organization. Discover how Splunk User and Entity Behavior Analytics uses machine learning to help security teams spot what they didn’t know to look for — from hidden threats to unusual user activity that could signal something’s wrong.
We're already getting value out of it! It was finding things on the OT side that we weren't even aware of previously with just Splunk Enterprise Security in terms of insider threats. In a controlled study by Horizon3 researchers, models that explicitly identified a trap in their reasoning still attacked it 73.4% of the time. Read the findings and see what they mean for canaries, decoys, and early detection.
Deployed a Splunk UBA instance last year in a 3,000-employee environment with what seemed like sufficient data sources: Active Directory authentication, Windows Security events, and web proxy logs. After the 30-day baseline period, the platform generated 40+ risk score alerts on the first day of live alerting — nearly all of them false positives caused by legitimate but unusual work patterns: the security team's own scanning activity appearing as reconnaissance, late-night deployments from the DevOps team appearing as anomalous after-hours access, and the help desk's cross-system access appearing as lateral movement.
The root causes were two deployment mistakes: the peer group configuration had placed all IT staff in a single group rather than separate groups for security, DevOps, and help desk (very different behavioral profiles), and the DLP data source was not connected (making the data movement model run on incomplete information that created spurious anomalies from normal file access patterns). Both issues were correctable, but they illustrate why UEBA deployments that produce noisy alerts for the first 90 days are the norm rather than the exception. The fixes are not difficult — they require accurate peer group definition and complete data source coverage — but they require understanding why the noise is happening before tuning.
UEBA behavioral models are only as good as the data they learn from. Missing data sources create blind spots in the behavioral profile that cause two problems: genuine insider threat indicators are not detected (because the relevant activity type has no data), and the behavioral models compensate with spurious correlations from available data that generate false positives. The data source integration phase is the most important phase of UEBA deployment and should not be rushed to get the platform into active alerting faster.
DLP policy violation events and file access logs are the highest-signal data sources for insider threat detection because they directly measure data handling behavior rather than inferring it from proxy indicators. If a DLP solution is not yet deployed in the environment, connect the cloud storage activity logs (Microsoft 365 purview audit, Google Workspace Drive audit) as a partial substitute that captures the most common cloud-based exfiltration channels. For file server access, enable Object Access auditing on Windows file servers for the file shares containing sensitive data (not all shares — the event volume from full file server auditing is prohibitive), configure them to forward to the SIEM, and connect the SIEM log source to UEBA. The combination of DLP events, cloud storage uploads, and file server access provides the three channels most commonly used for insider data exfiltration and enables the multi-indicator correlation that distinguishes genuine exfiltration from normal file access variation.
Physical badge access correlated with logical system access is a high-specificity insider threat indicator because the combination (working late and accessing sensitive systems with no physical presence on-site) is genuinely rare in normal work patterns. Many UEBA platforms support badge access log integration if the physical access control system can export events in a standard format (CSV, syslog, or API). Connect badge reader entry/exit events to UEBA and enable the after-hours logical access anomaly model, which flags users who access sensitive systems from unusual locations without corresponding badge records showing physical office presence. The false positive rate on this model is typically very low because the combination of anomalies is genuinely unusual — legitimate remote access from authorized WFH employees is recognized by the VPN context, distinguishing it from post-termination access using retained credentials.
A UEBA platform that generates 40 alerts per day in a team of three analysts is as ineffective as no UEBA at all — the alert volume exceeds analyst capacity and trains responders to ignore or batch-close alerts without investigation. Alert volume management through threshold tuning, peer group refinement, and exclusion rules is an ongoing operational process that requires structured feedback from analysts into the model configuration. Most UEBA platforms reach a stable, useful alert cadence after 90 days of tuning from the initial go-live.
Structure the UEBA alert workflow as a recurring risk score review meeting where security analysts review all users who crossed the alert threshold in the recent period, classify each as true positive (escalate to HR and legal for investigation), false positive (document the benign explanation and tune the model), or monitoring (behavior is anomalous but context suggests a benign explanation — watch for additional indicators in the next cycle). This structured review approach is more effective than individual analyst alert triage for UEBA because insider threat indicators often require knowledge of organizational context (a user with a resignation submitted, a pending M&A event, a specific project deadline) that is not visible in the UEBA data alone.
The security analyst who identified the alert and the HR business partner assigned to the relevant department should both attend the review meeting so that UEBA data is interpreted with full organizational context rather than in isolation. Configure the UEBA risk score decay rate to reduce a user's composite risk score over time when no new anomalous behavior is detected, preventing false positives from a one-time unusual event (working late on a product launch, accessing a new file share for a cross-departmental project) from keeping a user in high-risk status for weeks. Most UEBA platforms allow decay rate configuration as a half-life in days: a 7-day half-life means a risk contribution from a single anomaly decays to 50% after 7 days and to below 10% after 23 days. Set the decay rate based on the insider threat investigation SLA — if the team reviews high-risk users on a 7-day cadence, a 7-day decay ensures that stale anomalies age out within one review cycle. A user who returns to baseline behavior after a single unusual event should not remain on the analyst radar for more than two to three weeks without new supporting indicators.
UEBA insider threat detection is effective when three conditions are met: complete data source coverage including DLP, file access, authentication, communication metadata, and ideally physical badge access; a 30-60 day behavioral baseline period before alerting goes live; and structured feedback-driven threshold tuning for the first 90 days of active operation. Peer group configuration based on actual job function rather than org chart hierarchy is the single most impactful configuration decision for reducing false positive rates. Connect watchlist management to HR processes so that elevated-risk employees are monitored at lower thresholds without requiring analysts to track HR events manually. Build an investigation playbook reviewed by legal counsel before the first true positive alert arrives, so that evidence collection is legally defensible and investigation procedures are consistent. UEBA is a detection tool, not a conviction tool — its output is an investigation trigger, not a disciplinary action.
Effective UEBA insider threat detection requires a minimum of four data source categories to establish meaningful behavioral baselines. Identity and access data: Active Directory authentication events (Windows Event IDs 4624, 4625, 4648, 4768), VPN authentication logs, and privileged access management (PAM) session logs provide the who-logged-in-from-where behavioral baseline. File and data activity: DLP solution logs with data movement events, Windows file share access logs (Event ID 5145), and cloud storage activity logs (Microsoft 365 audit logs, Google Workspace admin logs, Box/SharePoint logs) provide the what-data-was-accessed behavioral baseline. Communication data: email metadata (sender, recipient, attachment size — not content), collaboration platform activity (Teams, Slack message volume patterns), and web proxy logs with category and upload volume data provide communication behavioral baselines. Physical access: badge reader entry and exit logs correlated with logical system access provide the working-hours and location baseline. Missing any of these categories significantly reduces UEBA detection coverage — a UEBA deployment with only authentication logs will detect account compromise but miss data exfiltration patterns.
Harvested Online Documentation & Reference Sources • https://docs.netskope.com/en/behavior-analytics • https://learn.microsoft.com/en-us/azure/sentinel/identify-threats-with-entity-behavior-analytics • https://seekerslab.com/en/resources/blog/strengthening-insider-threat-detection-a-practical-guide-and-success-strategies-fo r-user-behavior-analytics-uba-en-1773621675547 • https://www.decryptiondigest.com/blog/ueba-user-entity-behavior-analytics-guide • https://s6securitylabs.com/blog/2025-12-18-insider-threat-detection • https://www.splunk.com/en_us/blog/learn/user-entity-behavior-analytics-ueba.html • https://www.splunk.com/en_us/form/the-modern-guide-to-minimizing-insider-threats-user-and-entity-behavior-analytics.html • https://www.decryptiondigest.com/blog/ueba-insider-threat-detection-splunk-exabeam-deployment-guide • https://www.decryptiondigest.com/blog/how-to-detect-insider-threats-ueba-user-entity-behavior-analytics
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Insider Threat Detection Using User Behavior Analytics.
[*] Synchronizing KnowBe4 Awareness Training telemetry... ──────────────────────────────────────────────────────────────────────── [11:45:02.102] MAIL Dispatched simulated assessment templates [11:45:02.155] REPORT Majority of active users flagged probe via Phish Alert Button [11:45:02.210] CLICK Simulated lure baseline reduced below risk threshold [11:45:02.290] TRAIN Auto-enrolled flagged users into adaptive micro-learning modules ──────────────────────────────────────────────────────────────────────── [✓] Human Security Index: Phish-Prone percentage safely minimized
| Campaign Simulation | Platform Used | Total Recipients | Reported via Phish Button | Phish-Prone Percentage |
|---|---|---|---|---|
| Urgent Communication Lure | KnowBe4 KMSAT | 350 Employees | 318 (90.8%) | 2.9% (OPTIMAL) |
| Account Credential Lure | Proofpoint ZenGuide | 350 Employees | 324 (92.5%) | 2.1% (OPTIMAL) |
| Executive Impersonation | Mimecast Engage | 200 Executives | 192 (96.0%) | 1.5% (OPTIMAL) |