Complete Technical Paper Content — Jwt Token Vulnerability Detection Tool In Python
Overview & System Context
Jwt Token Vulnerability Detection Tool In Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8504 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background CVE-2026-102271 is an authentication bypass vulnerability in PyJWT affecting versions 2.4.0 to 2.14.0. Attackers can forge HMAC tokens using public keys when applications mix HMAC and asymmetric algorithms. This article covers technical details, affected versions, impact, and mitigation steps.
CVE-2026-102271 affects PyJWT, a Python implementation of JSON Web Token (JWT) standards. Versions from 2.4.0 up to 2.14.0 contain a flaw in HMACAlgorithm.prepare_key where the asymmetric-key guard relies on textual PEM markers absent from Distinguished Encoding Rules (DER) encoded keys. When an application mixes HMAC and asymmetric algorithms and supplies a DER public key as the shared verification key, PyJWT uses those public DER bytes as the HMAC secret. An attacker who knows the public key can then forge authenticated HMAC tokens. The issue is fixed in PyJWT 2.14.0 and is tracked as [CWE-347: Improper Verification of Cryptographic Signature].
Attackers with access to a public key can forge signed JWTs, bypassing authentication in applications that mix HMAC and asymmetric verification. PyJWT's HMACAlgorithm.prepare_key function is responsible for validating and normalizing the key material used for HMAC operations. Historically, the guard designed to reject asymmetric keys checked for textual PEM markers such as -----BEGIN PUBLIC KEY----- . DER-encoded keys carry no such ASCII markers because they are binary structures. As a result, a DER public key passes the guard and is treated as raw HMAC secret bytes.
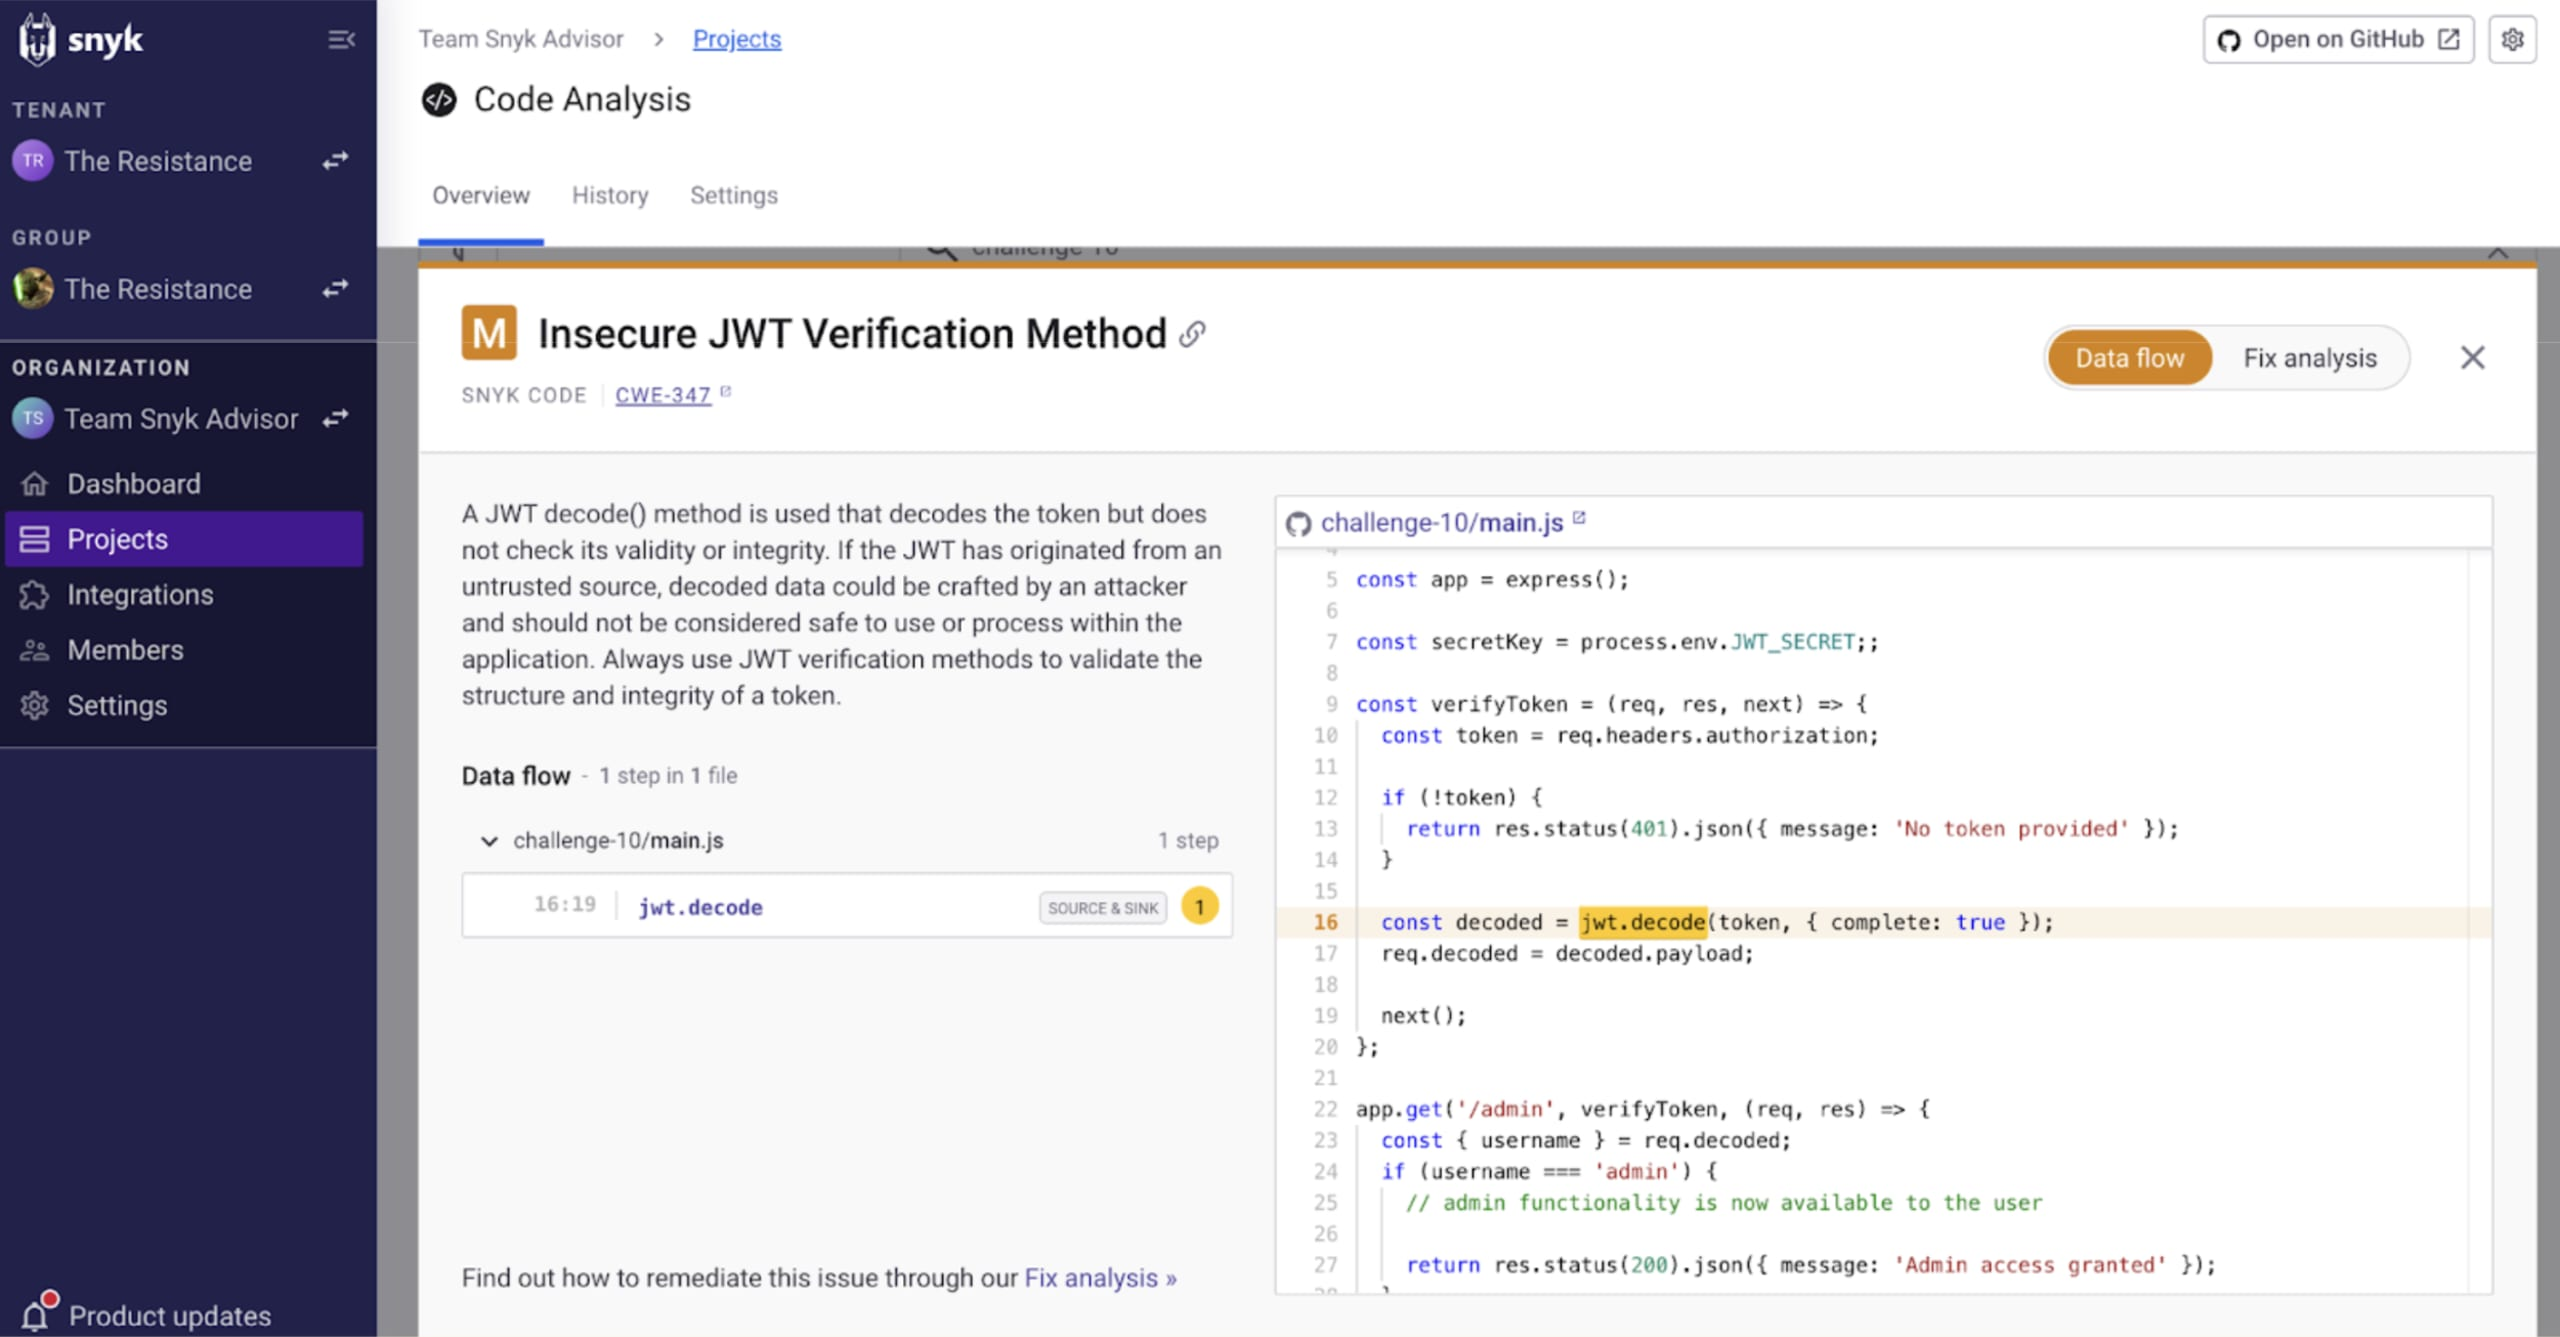
Figure 1: JWT Security Risk: Prevention & Best Practices | Detecting JWT Security ... This becomes exploitable in applications that permit algorithm confusion between asymmetric algorithms (for example, RS256 or ES256 ) and symmetric ones ( HS256 ). If the verifier passes the intended public key to jwt.decode while allowing HS256 , PyJWT computes an HMAC over the token using the public key bytes. Because public keys are, by definition, not secret, any attacker holding the key can produce a valid signature.
The root cause is an incomplete input classification check. The prepare-key logic distinguished PEM-encoded asymmetric keys but omitted DER detection, allowing binary-encoded public keys through as HMAC secrets [CWE-347]. Exploitation requires an application to accept a JWT algorithm list that includes an HMAC variant while configuring a DER public key as the verification key. The attacker crafts a JWT with the alg header set to HS256 , signs the token using the known public DER bytes, and submits it. The verifier reproduces the same HMAC and accepts the forged token as authentic.
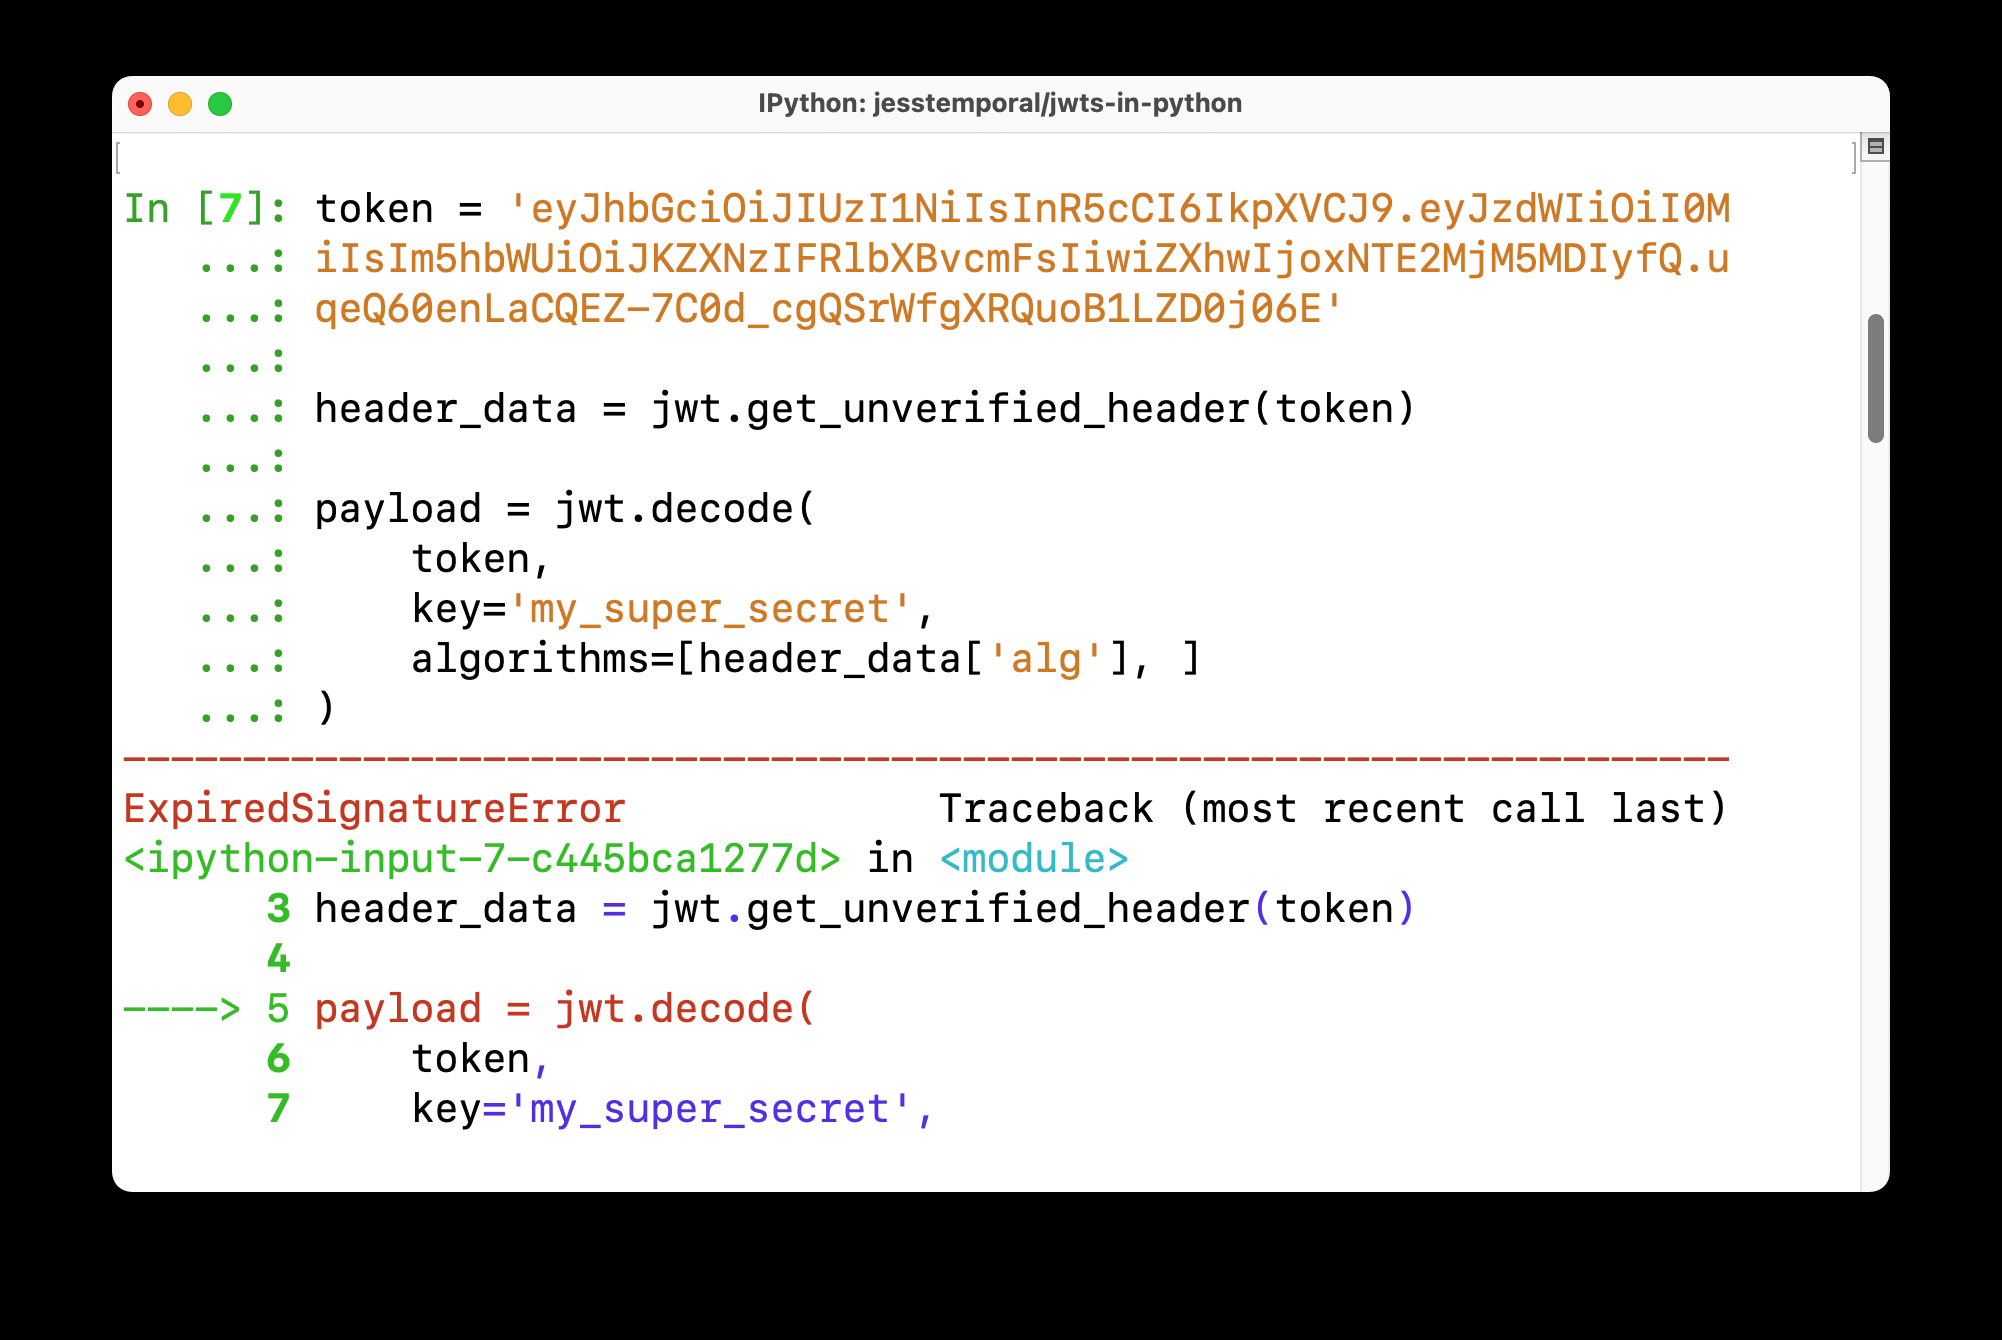
Source: GitHub Commit 2798504 . The fix imports cryptography.x509 and related primitives so prepare_key can parse DER blobs and reject any key that decodes as an asymmetric public key. Figure 2: How to Handle JWTs in Python The fix ships in PyJWT 2.14.0 via commit 2798504fa2663364573cf2d1043d8d7fef389499 . Additional context is available in GHSA-p4g4-x82p-q773 . The patched prepare_key uses the cryptography library to parse DER content and reject asymmetric public keys before they reach the HMAC path.
Disclaimer : This content was generated using AI. While we strive for accuracy, please verify critical information with official sources. See how the world’s most intelligent, autonomous cybersecurity platform can protect your organization today and into the future.
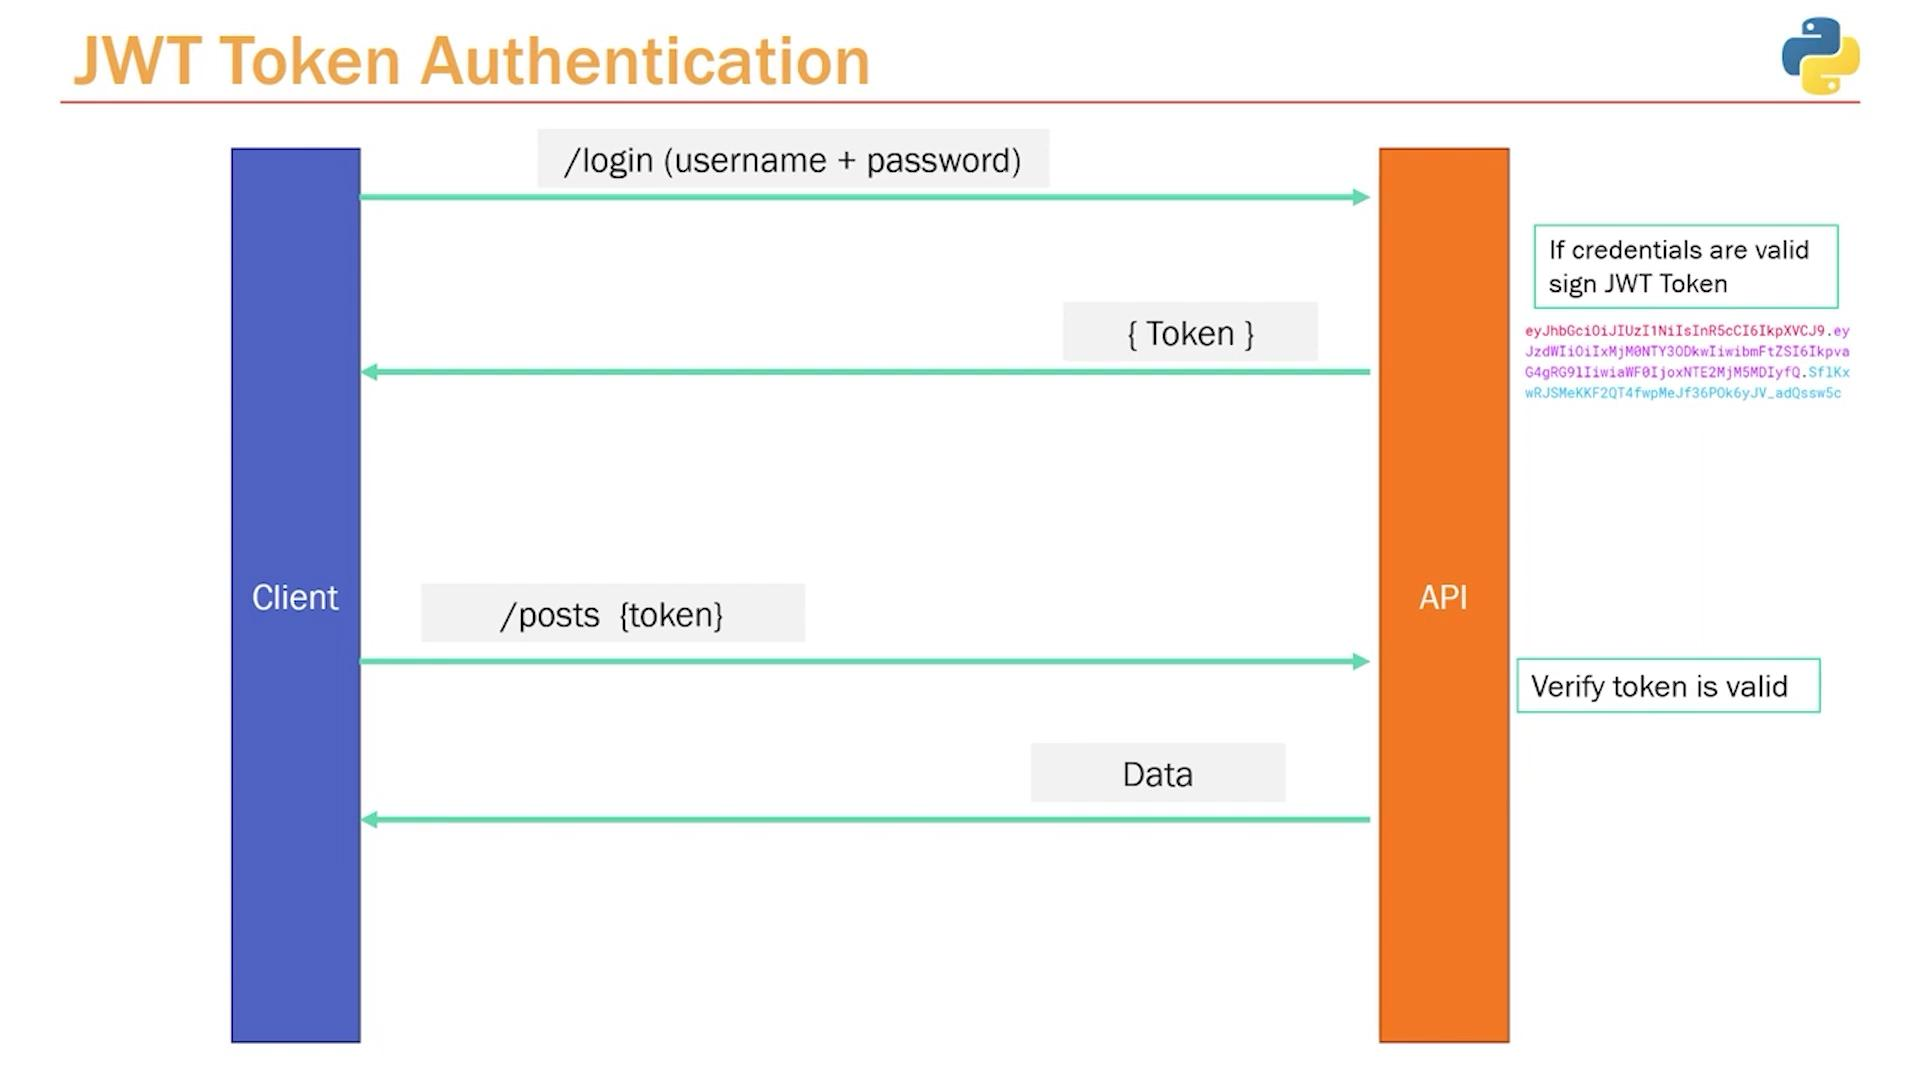
PyJWT is a Python library which allows you to encode and decode JSON Web Tokens (JWT). JWT is an open, industry-standard ( RFC 7519 ) for representing claims securely between two parties. Figure 3: Jwt Token Basics - KodeKloud If you want to quickly add secure token-based authentication to Python projects, feel free to check Auth0’s Python SDK and free plan at auth0.com/signup .
Before you read any further, study this JWT verification code and predict the vulnerability: This code has three critical vulnerabilities . By the end of this lesson, you will be able to identify all three and build JWT authentication that withstands real-world attacks. The payload is NOT encrypted. It is only Base64-encoded. Anyone can decode and read it. Never store passwords, credit card numbers, or other secrets in the payload.
Both the issuer and verifier use the same secret key . Simple, but the secret must be shared with every service that verifies tokens: The issuer signs with a private key . Verifiers only need the public key . This is essential for microservice architectures where you do not want to distribute the signing secret: Use HS256 when a single service both issues and verifies tokens. Use RS256 when separate services issue and verify tokens (microservices, Keycloak, Auth0). RS256 is the standard for production systems.
Every time a refresh token is used, it is invalidated and a new one is issued. If an attacker steals a refresh token and the legitimate user also uses it, the system detects the reuse and invalidates the entire token family: If your server accepts "alg": "none" or allows switching between algorithm families, an attacker can forge tokens: The alg: none attack : Some JWT libraries accept {"alg": "none"} in the header, meaning no signature is required. An attacker crafts a token with alg: none and an empty signature, and the server accepts it without any verification. Always specify exactly which algorithms you expect.
JWTs are stateless by design. Once issued, they remain valid until expiration. To support logout or forced revocation, you need a blacklist: For most applications, short-lived access tokens + database-backed refresh tokens is the best balance of security and performance. Only add access token blacklisting if compliance requirements demand immediate revocation (e.g., financial services, SOC 2).
In production with RS256, public keys are distributed via a JWKS (JSON Web Key Set) endpoint. Keycloak, Auth0, and other identity providers expose this at a well-known URL: This approach means your API servers never store private keys. They fetch the public key from the auth server's JWKS endpoint and cache it locally.
verify_signature: False - The signature is never verified. An attacker can forge any payload, impersonate any user, escalate to admin, or extend expiration indefinitely. Manual expiration check with no algorithm restriction - The code does not specify which algorithms are allowed. An attacker can submit a token with "alg": "none" and bypass all cryptographic verification.
No issuer, audience, or required-claims validation - The code accepts tokens from any source, for any audience, with any structure. A token issued by a compromised development environment would be accepted by production. The algorithm list includes "none" , which allows unsigned tokens. An attacker can send a token with {"alg": "none"} and an empty signature. The server will accept it with no cryptographic verification at all. Fix: algorithms=["HS256"] - never include "none" .
Question 2 : A developer stores the JWT signing key as SECRET_KEY = "mysecret" directly in their Python source code. What are the risks? Three risks: (1) The secret is committed to version control and visible to anyone with repository access. (2) An 8-character string like "mysecret" is trivially brute-forceable - HS256 keys should be at least 256 bits (32 bytes) of random data. (3) The same secret is likely used across all environments (dev, staging, prod), meaning a compromise in development compromises production. Store the key in environment variables or a secrets manager and generate it with os.urandom(32).hex() .
Question 3 : An API sets access token expiration to 24 hours to "reduce refresh token complexity." What is the security impact? A 24-hour access token means that if a token is stolen (via XSS, network interception, or log exposure), the attacker has up to 24 hours of access even after the user changes their password or the admin revokes access. With a 15-minute access token, the exposure window shrinks to 15 minutes. The operational complexity of refresh tokens is the necessary price for this drastically reduced attack surface.
This FastAPI authentication middleware has multiple flaws. Identify and fix all of them: Fixes applied: (1) Secret from environment. (2) Standard Authorization: Bearer header. (3) Single explicit algorithm. (4) Issuer validation. (5) Required claims. (6) Proper error handling instead of silent None . Document your design decisions for: signing algorithm, key distribution, token lifetimes, claim structure, revocation strategy, and multi-device session handling.
In the next lesson, OAuth 2.0 and OpenID Connect , you will learn how JWT tokens fit into the broader OAuth 2.0 authorization framework - implementing delegated authorization with Keycloak, Google, and other identity providers. Learn how to implement secure JWT authentication in Python with refresh token rotation, token revocation, and security best practices. This guide covers common pitfalls and production-ready patterns.
JWT authentication seems simple until you get it wrong. Tokens that never expire, secrets in code, no revocation mechanism - these mistakes turn your authentication into a security vulnerability. This guide shows you how to implement JWT authentication correctly. JWTs are powerful but require careful implementation. This guide covers the security aspects that are often overlooked.
This module provides the core JWT functionality: creating access tokens (short-lived for API authentication) and refresh tokens (longer-lived for obtaining new access tokens). Each token includes a unique identifier (jti) for tracking and revocation. Rotating refresh tokens on each use is a critical security measure. When a refresh token is used, it is immediately invalidated and a new one is issued. If an attacker steals a refresh token, they can only use it once before detection. The "token family" concept groups related tokens so that reuse of an old token invalidates all tokens in that session.
This schema stores refresh token metadata for revocation tracking. The family_id links related tokens from the same login session, enabling bulk revocation when suspicious activity is detected. This complete FastAPI authentication implementation includes login, token refresh with rotation, and logout endpoints. It uses FastAPI's dependency injection to validate tokens and protect routes.
Since access tokens are stateless, they remain valid until expiration even after logout. For immediate revocation (e.g., security incidents), maintain an in-memory blacklist of revoked token IDs. The blacklist automatically cleans up expired entries to prevent memory growth. 2. System Architecture & Core Working Principles Never use weak or predictable secrets. Generate a cryptographically secure random string of at least 256 bits (32 bytes).
Always validate all JWT claims, not just the signature. Check expiration, issued-at time (to detect tokens from the future), token type, and required claims. HS256 requires sharing the secret with all services that verify tokens. RS256 uses asymmetric keys: only the auth service needs the private key, other services only need the public key.
Add headers to prevent token leakage through referrers and browser caching of authenticated responses. Need to monitor authentication events? OneUptime provides security logging and alerting for authentication failures, suspicious activity, and token issues. Every OneUptime blog post is open source. Found a typo, an inaccuracy, or have a clearer way to explain something? Anyone can contribute — your edits make this post better for everyone who reads it next.
Your complete reliability stack unified: infrastructure monitoring, incident management, status pages, and APM. Open-source and self-hostable. Most Python JWT security implementations focus on signature verification and stop there. If jwt.decode() doesn't raise an exception, the engineer assumes the request is safe. This is a dangerous fallacy. Verification only proves that the token hasn't been tampered with; it says nothing about whether the user should be accessing the specific resource they requested.
In a standard FastAPI or Flask environment, failing to link the token's identity to the database query leads directly to BOLA (Broken Object Level Authorization) . Attackers don't need to forge tokens; they simply use their own valid token to request someone else's order_id . Without Autonomous Authorization logic, your API will happily serve the data, leading to a massive Audit failure .
While modern libraries like PyJWT and python-jose have patched the infamous "alg: none" exploit by default, Token Injection has evolved. Attackers now look for JWT-assertion-grant vulnerabilities where one service trusts a token from another service without validating the intended audience ( aud ) or issuer ( iss ). In Python microservices, BOLA often creeps in through generic decorators. An engineer might write a @require_auth decorator that populates request.user . However, the subsequent database call looks like this: This code is broken. A secure Python JWT security pattern requires a "Check-Before-Write" or "Check-Before-Read" logic that includes the user's unique identifier from the JWT: db.query(Models.Invoice).filter(Models.Invoice.id == invoice_id, Models.Invoice.owner_id == jwt_user_id).first() API Sprawl often leads to "Key Rot Drift." You rotate your RS256 private keys, but a legacy Shadow API is still running an old container with the previous public key. This creates a security gap where revoked credentials still grant access. Continuous Compliance requires an automated way to verify that every endpoint in your environment uses the current key-set and enforces mTLS where necessary.
You cannot solve Python JWT security issues by manually reviewing every PR. You need Evidence-based Remediation integrated into your CI/CD security flow. The goal is to catch hardcoded secrets or permissive token validation before the code reaches a staging environment. Automated Discovery: Use tools that perform eBPF-powered discovery to see which endpoints actually consume JWTs in the wild.
Static Analysis: Scan for PyJWT.decode calls that lack leeway , audience , or issuer validation. Runtime Protection: Monitor for LLM-driven bot evasion attempts where high-velocity requests attempt to iterate through UUIDs using a single valid JWT. Enterprise security platforms often require complex Machine IAM configurations and long setup times. For a Python developer, the overhead usually isn't worth the "robust" marketing promises. We need tools that respect the developer's time.
To pass your next Python API security audit , you must move beyond simple middleware. Implementing OpenAPI/Swagger validation is the first step, but the real work happens at the data layer. Ensure that your Remediation strategy includes: For more on the broader landscape of securing Python environments, check our Python API Security Ecosystem Guide . If you're struggling with Shadow & Zombie APIs , it's time to automate your discovery process and reclaim your Audit Trail Integrity .
Everything you need to know to implement and validate JWTs securely in Python — from signing to verifying with JWKS, with code examples and best practices throughout. Whether you're building a single-page application, a mobile backend, or a microservices architecture, JWTs allow you to authenticate users and transmit information securely between parties without maintaining session state on the server. They're compact, URL-safe, and can be easily verified using digital signatures — making them an ideal choice for many authentication and authorization scenarios.
This tutorial will walk you through the essentials of handling JWTs in Python — from decoding and verifying tokens to securing your APIs with best practices. We'll look at how to use the popular PyJWT library to handle token validation, manage claims like expiration and audience, and safely extract user information from JWTs. If you are tired of copying JWT code from StackOverflow and want to finally understand what’s actually happening and how to handle JWTs properly in your Python apps, keep reading.
!! Need to inspect a token? Use the WorkOS JWT Debugger to decode and inspect your JWTs directly in the browser. It's a quick way to verify your token's iss , aud , sub , and other claims while debugging.!! A JSON Web Token (JWT) is a compact, URL-safe token used for securely transmitting information between two parties. Typically, JWTs are used for authentication purposes, allowing a server to verify the identity of a user without needing to store session information.
JWTs are protected via JSON Web Signature (JWS) . JWS uses a signature algorithm and is used to share data between parties when confidentiality is not required . This is because claims within a JWS can be read as they are simply base64-encoded (but carry with them a signature for authentication).Some of the cryptographic algorithms JWS uses are HMAC, RSA, and ECDSA .
To work with JWTs in Python, you'll need the PyJWT , a popular library for creating and verifying JWTs: In this tutorial, we will be using RS256 . This asymmetric algorithm requires two keys: a private key to sign the token and a public key to verify it. If you already have them move along to the next section. !!Asymmetric algorithms use a pair of public and private keys to sign and verify the tokens. They are more secure, scalable, and better for secure, distributed systems but also more resource-intensive and complex. For more on the various algorithms see Which algorithm should you use to sign JWTs? !! There are many ways to generate your keys. You could generate your keys using OpenSSL and save them as raw PEM files that your code would read.
However, this is not a best practice. Instead, you should use JSON Web Key Sets (JWKS) , especially in distributed or cloud environments. !!JWKS simplifies key rotation by allowing services to fetch the latest keys from a central endpoint, making updates easier and reducing the risk of errors. In contrast, PEM files require manual distribution and updates, which can be cumbersome in large systems. JWKS also centralizes key distribution, ensuring that all services or clients always have the correct keys without the need for constant manual updates.!! If you are using a third-party identity provider (like WorkOS), they automatically generate and expose a JWKS endpoint for you. This allows clients to dynamically fetch the public keys needed for JWT verification without you having to manage the keys manually. WorkOS offers a public JWKS endpoint ( https://api.workos.com/sso/jwks/your-client_id ) that clients can use to retrieve keys to validate JWTs. These services handle key rotation, expiration, and key distribution automatically.
If you're not using a third-party identity provider and want to create and manage your own JWKS in Python, there are several steps you can follow to ensure you're doing so securely and effectively. Here’s a high-level overview: !!If you need something fast for a proof-of-concept, you can use a tool like mkjwk.org to generate a JWK.!! If you are using a vault to store your private key, now is the time to do it. For WorkOS Vault the API call looks like this: The response will contain an id which you can use whenever you want to retrieve the value in order to sign a JWT: Once you have your RSA keys, create a token and sign it using the private key. In this example, for simplicity reasons, we are reading the private key from a pem file. Remember that the best practice here is to use a key vault .
The Bearer prefix tells the server: “This is a bearer token — anyone who has it can use it, no need for anything else.” The payload of each JWT consists of claims. These are pieces of information that provide details about the user and can be either standard (as defined by RFC 7519) or custom. Standard claims serve common use cases for identifying the token, setting validity, and establishing trust, while custom ones are created by each app to add specific context or permissions.
These claims are technically optional, but several of them are very important during the token validation process, which we will see later. Custom claims let your application logic leverage token data directly without needing extra DB lookups (but balance that with token size and security).
The app or API that is on the receiving end needs to verify the JWT’s signature using the corresponding public key, and then validate the token's claims (like expiration, audience, etc.). In our example, we use RS256, which means that the receiving app needs to know the public key. The app will typically receive the public key in one of these ways: 3. Software Implementation, Frameworks & Protocols You should only care about this claim if, instead of using one static public key, you are using JWKS with rotating keys.
It tells your app which public key (from a set of keys) should be used to verify the signature. This is used when your authentication provider uses key rotation — i.e., they publish multiple public keys at a JWKS endpoint, and the JWT header includes kid to tell you which one was used to sign it. For example, let’s say your auth server exposes its JWKS at: https://auth.example.com/.well-known/jwks.json .
When your app receives a JWT, it extracts the kid from the header, it looks up the matching public key in the JWKS, and it uses that key to verify the signature. If you want to access the kid value, to log it or alert someone, you can get it like this: After the signature has been verified, you need to validate the claims. This includes both the standard and the custom ones.
For the standard claims, PyJWT does all of the job for you. All we need to do is pass the expected audience and issuer information. If they don’t match with the information included in the JWT, the library will throw an exception: The library will throw different exceptions depending on what went wrong, and you can handle each one the way you want: If you're building a REST API, you will want to wrap this in a function and raise specific exceptions or return HTTP responses accordingly.
Besides always validating the standard claims for optimal security, you will also want to validate the standard ones before using them. Things like roles , email_verified , or department : This way, you can implement your business logic checks and use the information included in the JWT’s payload. While handling JWTs with PyJWT is often necessary for verifying tokens at the API layer, it’s worth considering how those tokens are issued in the first place. If you're building authentication flows — especially ones involving Single Sign-On (SSO) , SCIM provisioning , or multi-tenant identity — WorkOS can take care of the heavy lifting.
WorkOS provides a modern API for enterprise-ready authentication features, letting you integrate SSO (SAML, OIDC, etc.), manage users and directories, and issue secure tokens — all without building a full auth stack from scratch. It's especially useful if you need to support enterprise customers or want to offer a “Login with your company” experience. And it costs nothing for up to 1,000,000 monthly active users.
If you’re tired of stitching together SSO flows or dealing with SAML metadata manually, it’s worth checking out. Even in 2025, I still review Python APIs where JSON Web Tokens (JWTs) are the weakest link. The code often looks modern—FastAPI or Django REST, async endpoints, type hints—but the JWT handling and secrets management feel stuck in 2017.
In my experience, teams rarely get hacked because they chose JWTs; they get hacked because they misuse them: weak or hardIcoded secrets, tokens that never expire, missing audience/issuer checks, or storing too much sensitive data in the payload. Add in copyIpasted Stack Overflow snippets, and suddenly you’ve got predictable signing keys or tokens that can be reused forever.
This article focuses on practical Python JWT security best practices that I rely on in real projects: how to generate and rotate strong keys, validate tokens correctly, avoid common library misconfigurations, and design safer token lifecycles. By the end, you’ll know exactly which pitfalls to eliminate and how to harden your existing Python JWT implementation without rewriting your whole auth stack.
Before we can talk about Python JWT security best practices, it helps to ground how JWTs actually work in a typical Python API. A JWT is just a signed JSON blob: a header (algorithm & type), a payload (claims like sub , exp , scope ), and a signature that proves the token was created by your server and not tampered with. In most Python stacks I work on, the flow looks like this: a user authenticates once (login, OAuth, etc.), the backend issues a JWT, the client sends that JWT on every request (usually in the Authorization: Bearer header), and the API verifies and decodes it for each call.
Where things usually go wrong in real projects is not the syntax but the details: hardIcoded or weak secrets, missing exp / aud / iss checks, overloading the payload with sensitive data, or trusting any algorithm the token declares. I’ve seen production APIs accept unsigned ( alg: none ) tokens simply because default verification options were never set. In the rest of this guide, I’ll walk through the specific checks and configuration I now treat as nonInegotiable whenever I review JWT usage in a Python codebase, and how to align your implementation with modern JSON Web Token for Java – OWASP Cheat Sheet Series rather than adIhoc snippets.
When I’m hardening an API, I start with token design before I touch any endpoints. The way you choose algorithms, claims, lifetimes, and audiences has more impact on real-world risk than most people expect. Here’s how I now approach Python JWT security best practices for creating tokens that are both safe and maintainable. In 2025, there’s rarely a good reason to let tokens dictate their own algorithm. I always lock the server to a specific, strong algorithm and never trust what comes from the header alone.
In Python with PyJWT, that means being explicit on both encode and decode. One mistake I see a lot is developers omitting the algorithms list on decode, which can open the door to algorithm confusion issues. In my own reviews, I treat “no algorithm allowlist” as a red flag worth fixing immediately, even before more subtle design tweaks.
JWTs are meant to carry identity and authorization context, not your entire user record. I’ve seen tokens stuffed with emails, addresses, feature flags, and even passwords (yes, still). That’s a gift to anyone who can log traffic or steal a token. This way, the token expresses what the caller is allowed to do in a compact way, and I can always re-query the database for anything sensitive or frequently changing. One thing I learned the hard way was that over-encoding state into tokens makes revocation and policy changes painful.
Token lifetime and audience scoping are where design decisions hit real risk. If a token leaks, its time window and where it’s valid determines how bad that leak is. In Python, I like to centralize lifetime and audience rules so they’re easy to review and update: By being strict about lifetimes and audience scoping from day one, I’ve avoided many of the ugly retrofits I’ve seen other teams go through when they realize old, long-lived tokens are still floating around in logs, caches, or compromised devices.
No matter how carefully you design your claims and lifetimes, your JWTs are only as strong as the keys that sign them. Most of the scary incidents I’ve seen with Python APIs came down to sloppy secrets management: hardIcoded keys in Git, shared keys across environments, or no plan for rotation. In my own projects, I now treat JWT secrets like any other highIvalue credential: isolated, shortIlived when possible, and never directly embedded in source code.
The bare minimum for Python JWT security best practices is to stop committing signing keys to your repo. Even private repos leak eventually (forks, logs, screenshots, contractors). I load secrets from the environment and keep separate keys per environment (dev, staging, prod) so a leak in one doesn’t automatically compromise the others. A simple pattern I like is a small config module that centralizes secret loading and fails fast if anything is missing: In my experience, this kind of guardrail catches a lot of misconfigurations early, especially when someone spins up a new environment and forgets to set secrets. I also avoid putting real secrets into .env.example files; I just document the variable names and requirements.
Environment variables are fine for local development and small setups, but once a service is public-facing I strongly prefer a real secrets manager: AWS Secrets Manager, GCP Secret Manager, HashiCorp Vault, etc. They give me audit logs, centralized rotation, and access policies that are much harder to replicate by hand. The exact client depends on your platform, but the Python pattern is similar: fetch once at startup, cache in memory, and never log the value. Here’s a trimmed-down example using a generic “vault_client” abstraction, which I’ve used as a starting point on a few teams: In a real system, I’d also bind permissions so that only the auth service can read this path, and I’d never grant write access from the app itself. When I first added a vault to an older Python stack, the biggest win wasn’t just security—it was finally being able to rotate keys without hunting through Ansible templates and handIedited config files. If your team is new to vaults, it’s worth reading up on production-grade patterns like Secrets management: essential when using Kubernetes – CNCF .
Key rotation is where many teams stumble. They generate a strong key once, deploy it, and then forget about it until a breach—or an audit—forces them to care. My rule of thumb now is to design for rotation from day one, even if you’re not rotating aggressively at first. Here’s a simplified pattern for symmetric keys where I keep a small keyset in the vault and select by kid : In practice, I store the keyset in a secure backend and treat ACTIVE_KID as a configuration value. During rotation, I add a new key, mark it as active for signing, but keep the old key around so already-issued tokens continue to work until they naturally expire. That way, rotation becomes a routine operation instead of an outageIrisking event you dread doing.
Once tokens are flying around your system, safe validation is where Python JWT security best practices either hold or collapse. In my own reviews, most issues show up here: half-configured libraries, missing checks, or adIhoc parsing in every view. I always centralize verification in middleware or dependency layers so there’s exactly one place to get this right. I never treat a JWT as trustworthy until its signature is verified with a known key and an explicit algorithm allowlist. Relying on defaults or parsing the payload without verification is a direct path to accepting forged tokens.
One thing I learned early on is to never call jwt.decode without the algorithms parameter; that tiny omission has real security implications if libraries ever relax defaults. Beyond the signature, I treat core claims as mandatory guardrails: if any check fails, the request is unauthorized. In production Python APIs I usually enforce: To avoid bugs, I centralize these checks in a single helper and only pass the resulting identity object to the rest of the app.
That way, view functions don’t have to remember the rules, they just get a trusted “current_user”. In FastAPI, Django, or Flask, I make JWT validation a reusable layer, not something each endpoint reIimplements. Here’s a simple FastAPI-style dependency I’ve used as a starting point: 4. Practical Deployment, Analysis & Case Studies From there, each route just declares current_user = Depends(get_current_user) . In my experience, this pattern dramatically reduces subtle mistakes, because any tightening of JWT rules happens in one place and automatically protects every protected endpoint.
Even when I’m confident in my server-side configuration, I always remind teams that stolen tokens are just as bad as stolen passwords. Python JWT security best practices don’t stop at the backend; how you send and store tokens on the client side has a big impact on real-world risk. Over the years, I’ve seen more incidents from sloppy client storage than from broken crypto.
First, I never allow JWTs to move over plain HTTP in production— HTTPS is mandatory . Without TLS, anyone on the network can capture tokens and replay them. On the wire, I strongly prefer this pattern: On the server side, that usually means pulling the JWT from the header in your framework of choice and running it through a single verification function. A simple Flask example I’ve used in smaller services looks like this: By handling the header consistently, I reduce the chances of someone inventing their own adIhoc way of passing tokens (like custom headers or query params) that end up leaking into logs or analytics tools.
The toughest discussions I’ve had with frontend teams are always about where to store JWTs. There’s no perfect answer, but some choices are clearly worse than others. When I’m advising teams, I focus on reducing exposure to XSS and theft: For mobile or native clients, I recommend platform-specific secure storage (Keychain, Keystore, encrypted storage libraries) rather than flat files or shared preferences. Whatever the platform, my rule is simple: assume an attacker will eventually get script execution somewhere and design your storage so that the impact of that moment is as small and short-lived as possible.
All of these Python JWT security best practices become real when they’re wired into a framework. In my own work, FastAPI and Django are where I apply these patterns day-to-day: centralized verification, strict claim checks, and secrets pulled from config instead of hard-coded constants. FastAPI makes it easy to wrap secure JWT handling into dependencies. I like to combine a settings object (fed by environment variables or a vault) with a shared verification helper and a get_current_user dependency.
In my experience, this structure keeps JWT logic in one place and makes reviews much easier—when I audit a service, I can focus on settings.py and security.py instead of hunting through handlers. Django needs a slightly different approach, but the principles are identical: load secrets from the environment, centralize verification, and plug into middleware or authentication backends. One pattern that’s worked well for me is a custom authentication backend that uses PyJWT.
From there, views can rely on Django’s standard request.user without knowing anything about JWT internals. When I combine this with a proper secrets manager feeding environment variables into Django’s settings, I get a setup that’s both familiar to Django developers and aligned with modern JWT Security Best Practices:Checklist for APIs | Curity . When I look back at the incidents I’ve helped debug, the root causes were almost always simple gaps: missing claim checks, weak secrets, or tokens stored in the wrong place. The good news is that a small, consistent checklist goes a long way toward hardening real Python APIs.
In my experience, if a team can honestly tick off each of these items, they’re in a much better place than most APIs I’m asked to review. The next step is to automate as much of this as possible—shared libraries, framework integrations, and security checks in CI—so these best practices aren’t just documentation, they’re guardrails your code can’t ignore. Hi, I’m Cary Huang — a tech enthusiast based in Canada. I’ve spent years working with complex production systems and open-source software. Through TechBuddies.io, my team and I share practical engineering insights, curate relevant tech news, and recommend useful tools and products to help developers learn and work more effectively.
A Python CLI tool that decodes a JWT and checks it for the most common real-world vulnerabilities, producing a severity-scored report in the console, as JSON, or as an HTML file. II For educational purposes only. Only use against systems you own or have explicit permission to test. Using this against third-party services without authorisation is illegal.
The process exits with status 1 when any Critical or High issue is found, so it can gate a CI pipeline. The tool decodes the token without verifying the signature (the point is to inspect potentially malicious tokens), then runs four families of checks: Adding a new check is a matter of writing a function that returns a list of finding dicts and wiring it into analyze() in jwt_analyzer.py .
The suite covers every vulnerability class with deliberately crafted vulnerable tokens. Test coverage is 85%+ . Python CLI tool for analyzing JWT tokens for common security vulnerabilities (alg=none, weak secrets, RS256→HS256 confusion) A Python-based security analysis tool that analyzes JSON Web Tokens (JWTs) and identifies common security misconfigurations, weak algorithms, missing claims, excessive expiration times, and sensitive data exposure.
Python-based JWT security analysis tool for detecting token misconfigurations, weak algorithms, missing claims, and security risks. If you've been building APIs with Python, you've probably realized that letting anyone access your endpoints is a recipe for disaster. That's where JSON Web Tokens (JWT) come in. They're not just some fancy tech buzzword—they're one of the most practical ways to secure your APIs without overcomplicating things.
When I first started working with APIs at PythonSkillset, I spent weeks trying to understand authentication methods. JWT turned out to be the sweet spot between security and simplicity. Let me show you how it actually works. Think of JWT as a digital ID card. When a user logs into your API, you create a token that contains their identity information. Instead of checking their password every single time they make a request, they just show you this token. You verify it's genuine, and that's it.
The beauty is in the structure. A JWT has three parts: - Header : Says what kind of token it is and how it's encrypted - Payload : The actual data (user ID, expiration time, etc.) - Signature : Digital proof that nobody tampered with the token All these parts are base64-encoded and separated by dots, making something that looks like eyJhbGciOiJIUzI1NiJ9.eyJ1c2VyX2lkIjoxMjN9.xxxxxxxx First, you need to install the library. I recommend PyJWT because it's actively maintained and works well with Flask and FastAPI: Now here's a common scenario from my work at PythonSkillset. We needed to protect a user dashboard API. Here's how we set up the token creation: The exp claim is crucial—it sets an expiration time. Never create tokens that last forever. One hour works well for most applications.
Here's where things get interesting. You need to verify tokens on every protected route. Let me show you how we do this at PythonSkillset with Flask: Notice how we handle the "Bearer" prefix? Many developers forget this and wonder why their tokens don't work. The Authorization header usually comes as Bearer eyJhbGci... , and you need to strip that prefix before decoding.
At PythonSkillset, we review a lot of API security implementations. Here are the three most common mistakes: 1. Storing secrets in code Never hardcode your JWT secret. Use environment variables or a secrets manager: 3. Not refreshing tokens Your tokens expire in an hour, but what if the user is actively using the app? Implement refresh tokens—short-lived access tokens paired with longer-lived refresh tokens.
The Depends(verify_token) pattern makes it incredibly easy to protect multiple routes without repeating code. JWT authentication doesn't have to be complicated. Start with the basics—create tokens, verify them, handle errors gracefully. As you get comfortable, add layers like refresh tokens and role-based access. Remember, security is a journey, not a destination. The APIs I build today at PythonSkillset are far more secure than what I wrote six months ago, and that's exactly how it should be. Keep learning, keep testing, and your users' data will stay safe.
Learn essential tips for using the JWT security scanner to identify and fix token vulnerabilities, enhancing your API security effectively. JSON Web Tokens (JWTs) have become a cornerstone of modern API authentication and authorization systems. However, their widespread adoption has also made them a prime target for security vulnerabilities. The introduction of jwt-security-scanner to PyPI represents a significant advancement in helping developers identify and remediate JWT-related security issues before they become critical problems.
JWT tokens are used extensively in web applications, microservices, and API-driven architectures to manage user authentication and authorization. Despite their popularity, many developers struggle to implement JWT security correctly. Common vulnerabilities include weak signing algorithms, improper token validation, expired token handling, and insufficient claim verification.
The complexity of JWT security stems from multiple factors. Developers must understand cryptographic principles, token lifecycle management, and proper validation techniques. Additionally, different JWT libraries implement security features differently, creating inconsistencies across applications. These challenges have led to numerous security breaches where attackers exploited JWT weaknesses to gain unauthorized access to sensitive systems and data.
The jwt-security-scanner is a specialized tool designed to analyze JWT tokens and configurations for potential security weaknesses. Available on PyPI, this scanner automates the detection of common JWT vulnerabilities that might otherwise go unnoticed during development and testing phases. This security tool examines multiple aspects of JWT implementation, including algorithm strength, signature validation, token expiration handling, and claim verification. By integrating jwt-security-scanner into development workflows, teams can catch security issues early in the development lifecycle, reducing the risk of deploying vulnerable code to production environments.
5. Performance Evaluation & Extended Technical Observations The jwt-security-scanner provides comprehensive vulnerability detection across several critical areas. The tool analyzes the algorithms used for token signing, identifying weak or deprecated cryptographic methods that could be exploited by attackers. It verifies that tokens include proper expiration claims and checks whether applications correctly validate these timeouts.
The scanner also examines the structure and content of JWT claims, ensuring that sensitive information isn't exposed in the token payload. Since JWT payloads are base64-encoded but not encrypted, any sensitive data included in claims is visible to anyone with access to the token. The tool helps identify instances where developers may have inadvertently included confidential information in JWT tokens.
Additionally, jwt-security-scanner checks for proper signature verification implementation, ensuring that applications validate token signatures before accepting them. It also identifies tokens that use the "none" algorithm, a critical vulnerability that allows attackers to forge valid tokens without knowing the signing secret. The jwt-security-scanner targets several well-known JWT vulnerabilities that have affected real-world applications. The "none" algorithm vulnerability remains one of the most dangerous, as it allows attackers to create valid tokens without any cryptographic key. Many JWT libraries support this algorithm for testing purposes, but developers sometimes accidentally enable it in production environments.
Weak signing algorithms represent another critical vulnerability. Algorithms like HS256 (HMAC with SHA-256) can be vulnerable if implemented with insufficient key entropy or if the key is exposed. The scanner identifies when applications use weaker algorithms that should be replaced with more robust options like RS256 (RSA with SHA-256) or ES256 (ECDSA with SHA-256).
Improper token validation is another common issue the scanner detects. Some applications fail to verify token signatures, accept expired tokens, or don't validate the issuer and audience claims. These validation failures can allow attackers to use forged or stolen tokens to gain unauthorized access. The scanner also identifies tokens that lack proper expiration claims or use excessively long expiration periods. Tokens without expiration times remain valid indefinitely, increasing the window of opportunity for attackers to exploit stolen tokens.
Similarly, tokens with very long expiration periods reduce the effectiveness of token rotation strategies. Implementing jwt-security-scanner in your development pipeline is straightforward. As a PyPI package, it can be installed using standard Python package management tools. Once installed, developers can integrate the scanner into their testing frameworks, continuous integration pipelines, and pre-commit hooks.
The tool can be used in multiple ways depending on your development workflow. Developers can run it locally during development to check their JWT implementations before committing code. Teams can integrate it into their CI/CD pipelines to automatically scan all JWT-related code changes. Security teams can use it as part of their code review process to ensure consistent JWT security standards across the organization.
While jwt-security-scanner is a valuable tool, it should be part of a comprehensive JWT security strategy. Developers should follow established best practices alongside using automated scanning tools. The availability of jwt-security-scanner on PyPI reflects the growing recognition of JWT security as a critical concern in modern application development. As APIs become increasingly central to business operations, the security of authentication mechanisms becomes paramount.
This tool contributes to a broader ecosystem of security-focused development practices. By making JWT vulnerability detection accessible to developers, it democratizes security expertise and helps organizations of all sizes implement stronger security controls. Teams without dedicated security specialists can now leverage automated scanning to identify and fix JWT vulnerabilities.
The scanner also supports organizational security compliance efforts. Many regulatory frameworks and security standards require organizations to demonstrate that they've implemented appropriate controls to protect authentication mechanisms. Using jwt-security-scanner provides evidence of proactive security measures. As JWT usage continues to evolve, security tools like jwt-security-scanner will need to adapt to new threats and best practices. The cybersecurity landscape constantly changes, with new vulnerabilities discovered and new attack techniques developed. Developers should stay informed about JWT security updates and ensure they're using the latest versions of security scanning tools.
Organizations should also consider how jwt-security-scanner fits into their broader security architecture. While the tool is valuable for identifying JWT vulnerabilities, it should be complemented by other security measures including API security gateways, rate limiting, authentication monitoring, and incident response procedures. The jwt-security-scanner represents an important advancement in making JWT security more accessible to development teams. By automating the detection of common JWT vulnerabilities, the tool helps developers identify and fix security issues before they reach production environments.
JWT tokens are fundamental to modern API security, but their complexity creates opportunities for security mistakes. The scanner addresses this by providing automated vulnerability detection that catches issues developers might otherwise miss. For any organization using JWTs in their applications, integrating jwt-security-scanner into development workflows is a practical step toward stronger security.
Developers should view this tool as part of a comprehensive security strategy that includes proper algorithm selection, thorough token validation, secure key management, and regular security updates. By combining automated scanning with security best practices, organizations can significantly reduce the risk of JWT-related security breaches and protect their applications and users from unauthorized access.
A JWT security scanner is a tool designed to identify vulnerabilities in JSON Web Tokens used for authentication and authorization in applications. The jwt-security-scanner analyzes JWT tokens for weaknesses such as weak signing algorithms, improper validation, and expiration issues, helping developers secure their applications.
JWT security is crucial because vulnerabilities can lead to unauthorized access to sensitive data and systems, making it essential to implement strong security measures. Yes, the jwt-security-scanner can be integrated into CI/CD pipelines to automatically scan for JWT vulnerabilities during the development lifecycle.
Best practices include using strong signing algorithms, implementing proper validation, minimizing sensitive data in claims, and regularly rotating signing keys. For further reading on JWT security, check out resources from OWASP and NIST for authoritative guidelines. Discover how the 42Crunch API Security Plugin enhances API security by integrating vulnerability detection and remediation into the development workflow.
Explore how the 42Crunch API security testing plugin for GitHub Copilot enhances security in development by identifying vulnerabilities early. Discover 10 proven strategies for effortless API protection using Fortinet's FortiWeb, ensuring your APIs are secure against various threats.
Explore essential tips for securing AI agents with the immunity agent on PyPI. Learn how to safeguard your AI projects from vulnerabilities effectively. JSON Web Tokens, or JWTs for short, are all over the web. They can be used to track bits of information about a user in a very compact way and can be used in APIs for authorization purposes. This post will cover what JSON Web Tokens are and how to create JWTs in Python using the most popular JWT library: PyJWT . We are also going to see how you can sign and verify JWTs in Python using asymmetric algorithms.
Before we get started, there's a collection of scripts with all the code I'm going to cover in this blog post available in this GitHub repository . If you prefer, you can also watch the videos below with me explaining all about JWTs! I JSON Web Tokens are a very compact way to carry information. They are defined as a 3 part structure consisting of a header, a payload, and a signature. The header and payload both have what we call claims, they are statements about an entity and all additional data that needs to be passed in the request: The final part is the signature, and it helps you ensure that a given token wasn't tampered with because signing JWTs requires either a secret or a public/private key pair agreed on previously. The signature itself is based on the header and payload, in combination with a secret, or private/public key pair, depending on the algorithm.
Claims follow the standard key-value pairing that you see in dictionaries and JSON objects, and most of the claims commonly used in JWTs have a standardized naming defined in the JWT specification (RFC7519) . In the RFC7519, you'll also find the description of what each claim means . If you want to know more about JWTs, you should check this page that talks about JSON web tokens in a very practical way, or if you want a more in-depth resource, I recommend the "JWT Handbook" available for free in the link below.
While it's nice to read definitions and explanations, it's sometimes more beneficial to actually see how something works. In the rest of this article, you'll learn the ins and outs of JSON Web Tokens by creating, signing, verifying, and decoding your very own JWT. To create an environment, you must create and navigate to your working folder. The way I like to do this is using the following commands: And after the environment gets created, I can activate it and install the latest version of pip : Note that the command for activating your environment will vary according to your operating system (OS). On this documentation page, you can find a list of all the ways you can activate an environment to see a way for activating the environment that works best for your OS in there.
To sign your tokens with an asymmetric algorithm like RS256, you'll need a public/private key pair. I'll explain more about what this is in the next section, but for now, if you'd like to follow the tutorial, you'll need to have an RSA key pair. It is possible you already got a pair you want to use but, in case you need to generate a new one, here's what I did for generating a key pair I used in this example: Note that if you are using Windows as an operating system, depending on the OS version, you'll need to install OpenSSH to have access to the ssh-keygen . In this tutorial you'll find all the ways you can generate a key pair on Windows.
And if you want to have the key pair inside the working directory, remember to pass the path to your directory when prompted for a path. The path must contain the name of the private key as well. In my case, I used the following path in case you want to copy it. Remember to update accordingly: Also, you'll be prompted for a passphrase. For simplicity's sake, the key pair I generated for the examples on this blog post do not have a passphrase. Keep in mind that you should always use passphrases when generating RSA keys to provide an extra level of security.
Now for doing all that I'll cover in this post, you'll need to install PyJWT with the cryptography package as a dependency. This dependency will give you the ability to sign and verify JWTs signed with asymmetric algorithms. I'm going to teach you how to create a JWT because by understanding how a token is created, you'll better understand how to use JWTs, so bear that in mind.
Remember that if you are using a service like Auth0 , you shouldn't create your tokens; the service will provide them to you. Because JWTs can be read by anyone as long as they have the secret or public key, it is really important to follow industry standards to avoid complications like data and security breaches. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/List%20of%20computing%20and%20IT%20abbreviations • https://www.sentinelone.com/vulnerability-database/cve-2026-102271/ • https://pyjwt.readthedocs.io/en/stable/ • https://engineersofai.com/docs/python/python-advanced/security-engineering/jwt-authentication • https://oneuptime.com/blog/post/2025-01-06-python-jwt-authentication • https://www.apiposture.com/blogs/api-security-posture-management-aspm/python-api-security-the-devsecops-ecosystem-g uide/python-jwt-security-guide/ • https://workos.com/blog/how-to-handle-jwt-in-python • https://www.techbuddies.io/2026/03/02/python-jwt-security-best-practices-for-safer-apis-in-2025/ • https://github.com/gimacorp/jwt-analyzer • https://github.com/ARahman2429/JWT-Configuration-Analyzer
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Jwt Token Vulnerability Detection Tool In Python.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Jwt Token Vulnerability Detection Tool In Python... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |