Complete Technical Paper Content — Kerberoasting Attack Detection System In Active Directory
Overview & System Context
Kerberoasting Attack Detection System In Active Directory: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9534 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background In a controlled study by Horizon3 researchers, models that explicitly identified a trap in their reasoning still attacked it 73.4% of the time. Read the findings and see what they mean for canaries, decoys, and early detection.
Kerberoasting requires no special tools, no elevated privileges, and triggers no account lockouts: any domain user can execute it using built-in Windows tools or Impacket. The technique exploits the Kerberos protocol's design: service tickets are encrypted with the target account's password hash, which means anyone who can request the ticket can attempt to crack the password offline.
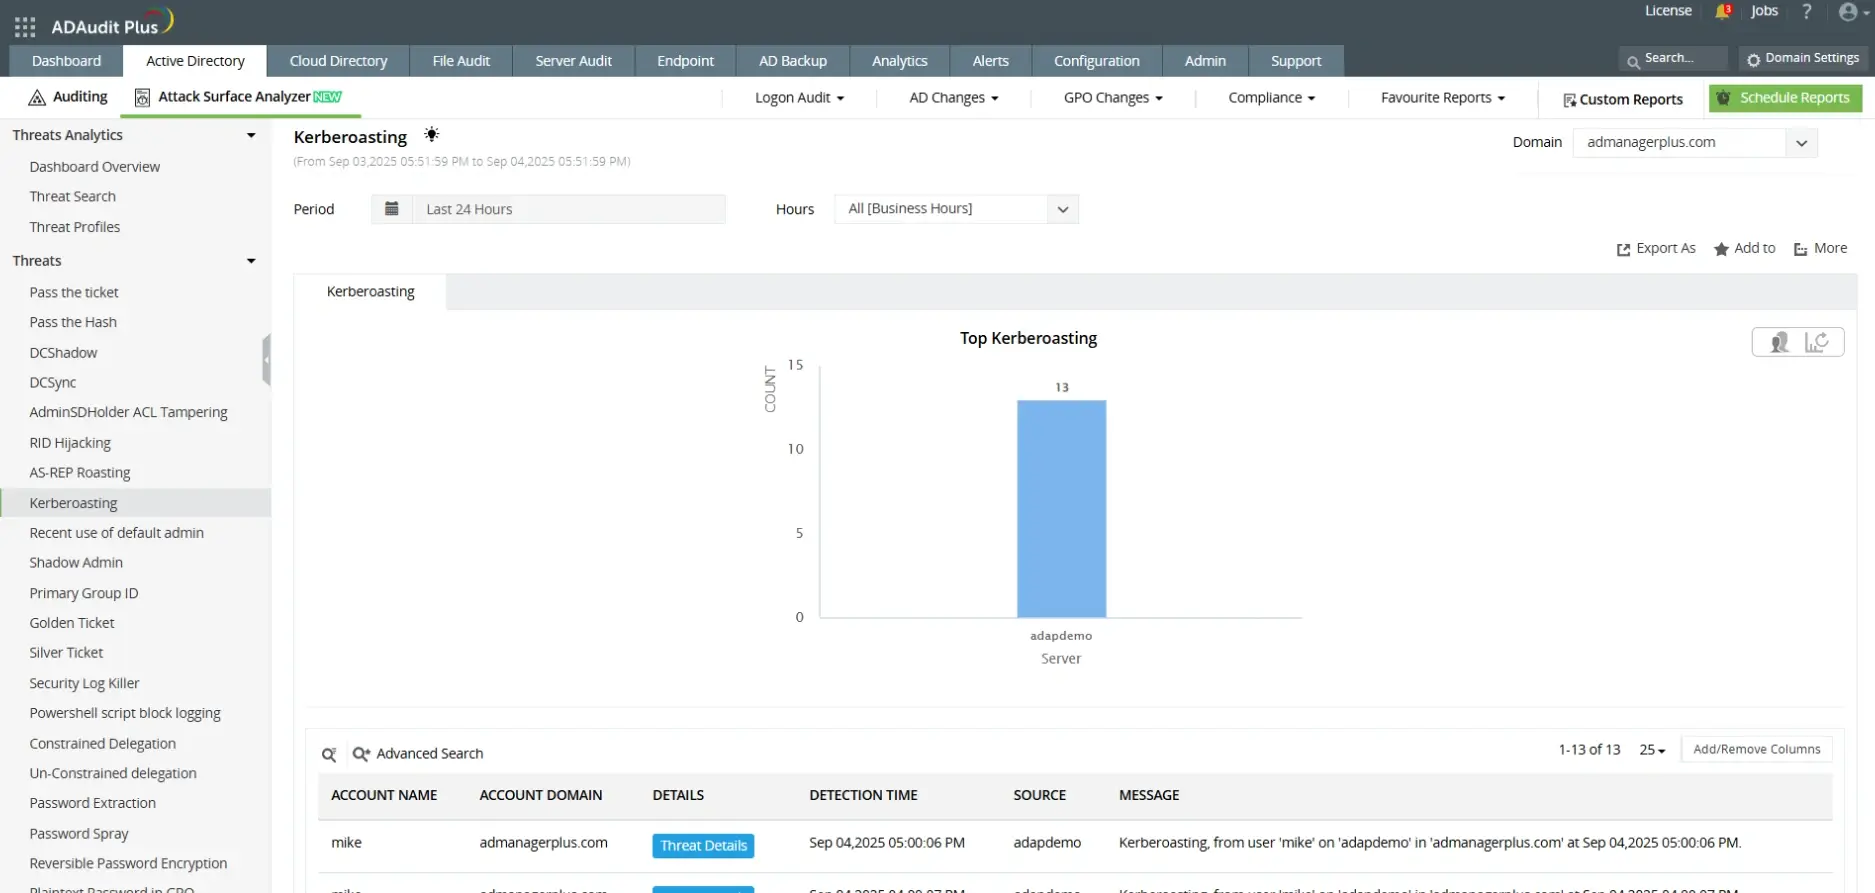
Detection is possible because Kerberoasting leaves a specific fingerprint: Event ID 4769 with RC4 encryption type, often from a user account requesting service tickets for accounts they have no legitimate reason to access. The attacker requests a Kerberos TGS (service ticket) for each SPN-registered account: Figure 1: Kerberos Auditing with ADAudit Plus | Active Directory Kerberos ...
The Domain Controller processes the request as legitimate: it is a standard Kerberos operation. The returned ticket is encrypted with the service account's NTLM hash. Weak passwords crack in seconds. Passwords under 15 characters using common patterns can crack in under an hour on a modern GPU. Long, random service account passwords (25+ characters) are computationally infeasible to crack.
Event ID 4769 fires on Domain Controllers when a Kerberos service ticket is requested. The critical field for Kerberoasting detection is the Ticket Encryption Type. Alert tuning: Some legitimate applications request RC4 tickets: legacy applications that do not support AES, and some third-party Kerberos clients. Baseline the normal count of RC4 4769 events per day; alert on deviations above 3 standard deviations, or alert specifically when a single account requests RC4 tickets for multiple SPNs in under 5 minutes.
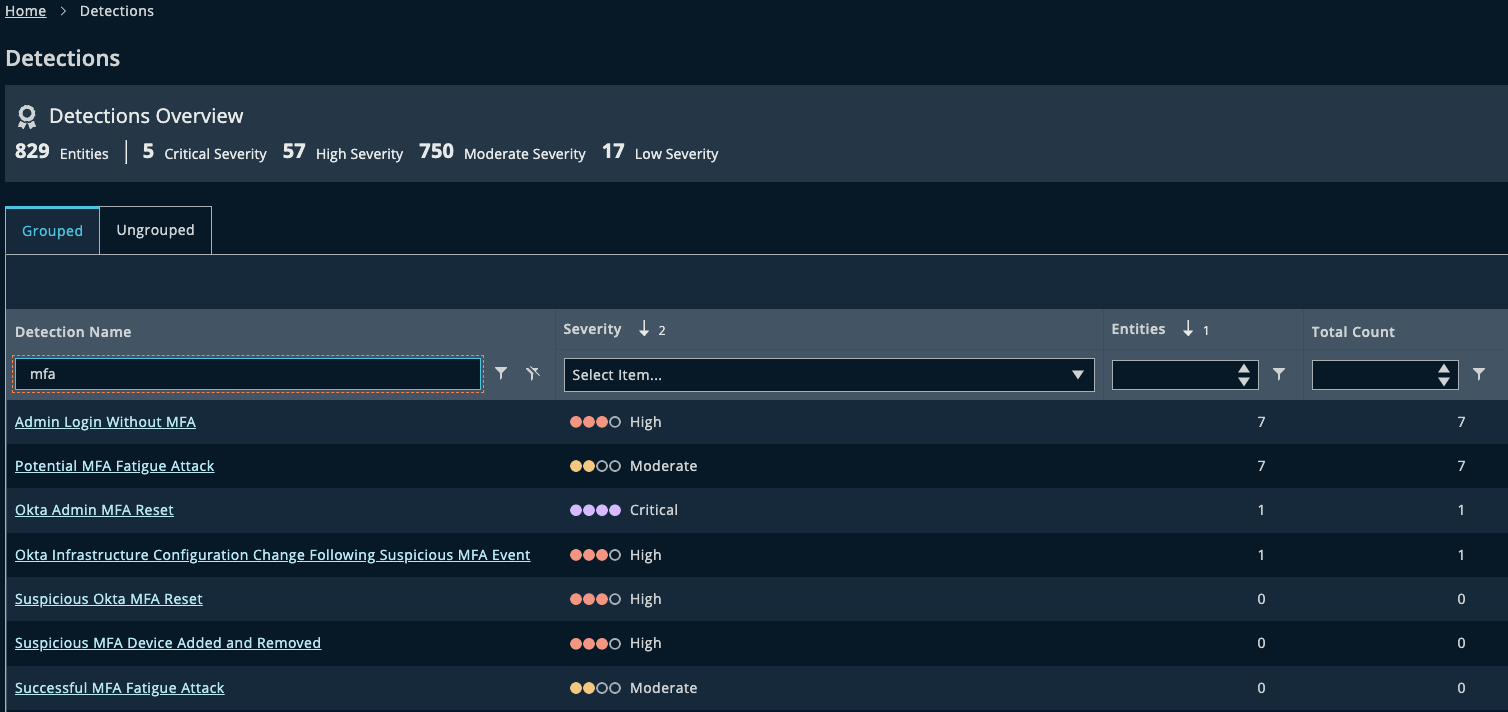
Figure 2: Kerberoasting | Detection and Mitigation Best practices | BeyondTrust Detection is important, but hardening service accounts makes successful cracking computationally infeasible even if the hash is obtained. A 25-character random password takes centuries to crack even with a GPU cluster. A 10-character password with common patterns cracks in seconds.
gMSAs automatically rotate their passwords to 120-character random strings managed by Active Directory: making Kerberoasting entirely infeasible: This does not prevent Kerberoasting (AES hashes can still be cracked) but significantly increases the GPU time required: AES hashes crack 100x slower than RC4.
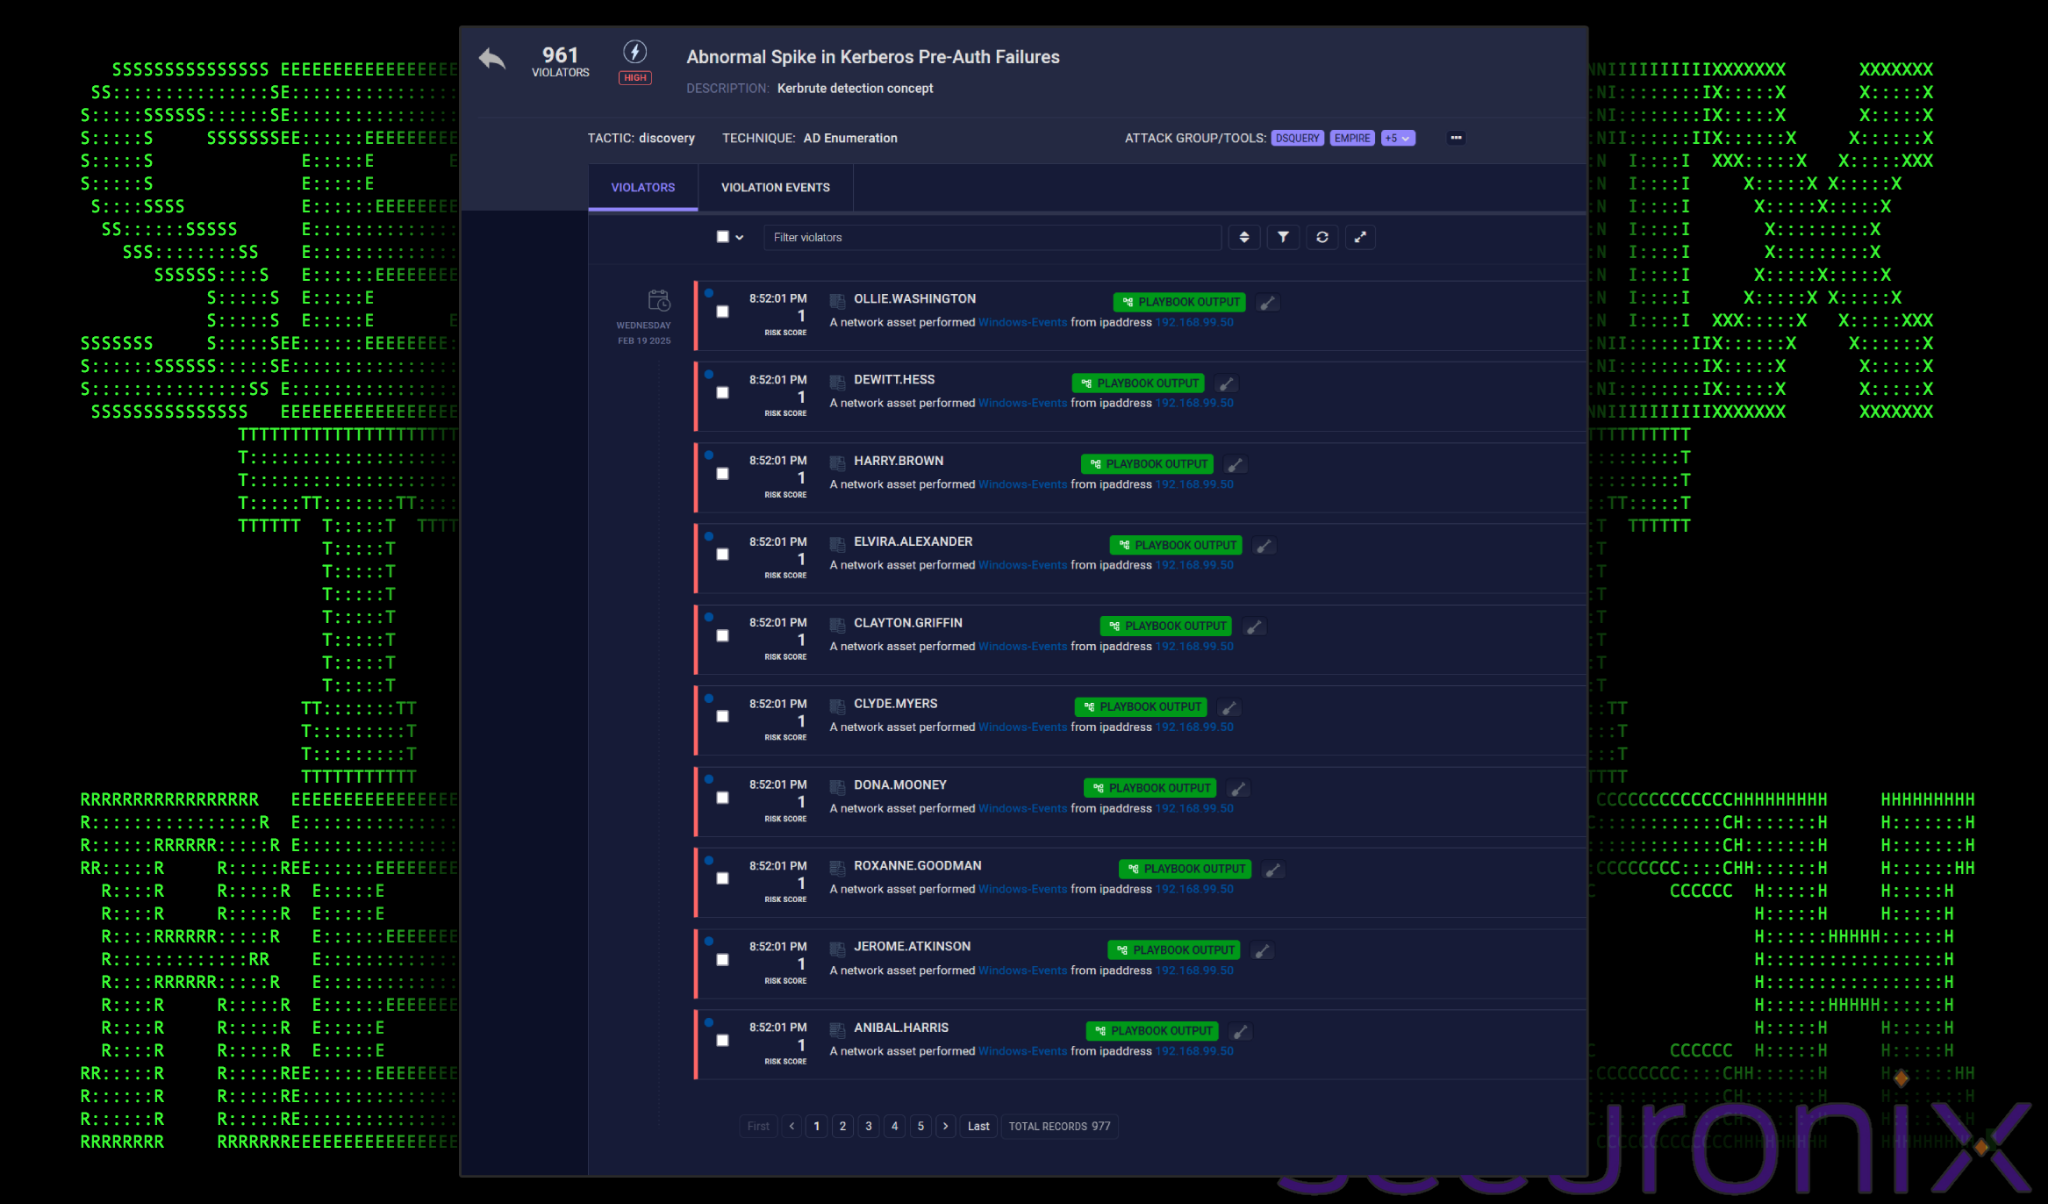
Figure 3: Hunting Kerbrute: Analysis, Detection and Mitigation of Kerberos ... Any account with a SPN and a password older than 90 days is a Kerberoasting target. Prioritize gMSA migration for these accounts. Kerberoasting requests service tickets for SPN-registered accounts using RC4 encryption (Event ID 4769, TicketEncryptionType 0x17) then cracks the returned hash offline: no lockouts, no elevated privileges required. Detection uses SIEM rules on Event 4769 filtering for RC4 encryption type from unexpected accounts. Hardening makes cracking infeasible: migrate service accounts to gMSAs (120-character auto-rotating passwords), enforce 25+ character random passwords for accounts that cannot use gMSAs, and require AES-only encryption on all service accounts.
Monitor Event ID 4769 (Kerberos service ticket request) on Domain Controllers for requests with Ticket Encryption Type 0x17 (RC4-HMAC). RC4 requests targeting SPN-registered user accounts (not machine accounts) from a single source in a short time window are high-confidence Kerberoasting indicators. Alert when a single account makes more than three RC4 service ticket requests targeting different SPNs within 10 minutes.
Migrate service accounts to Group Managed Service Accounts (gMSAs), which use automatically rotated 120-character random passwords that are computationally infeasible to crack. For accounts that cannot use gMSAs, set passwords of 25+ random characters and require AES-only Kerberos encryption (Set-ADUser -KerberosEncryptionType AES128,AES256). Audit all SPN registrations quarterly and prioritize migration of accounts with old passwords.
Primary detection: Windows Security Event ID 4769 with TicketEncryptionType 0x17 (RC4-HMAC) — this indicates an RC4 service ticket request, which is the type Kerberoasting tools request because RC4-encrypted tickets are faster to crack. Alert on multiple Event ID 4769 with RC4 from a single source account within a short window, or RC4 ticket requests for service accounts that do not normally receive such requests. Secondary detection: network signatures for unusually high volume TGS-REQ (Kerberos service ticket requests) from a single workstation. Note: if you have enforced AES-only on service accounts, any RC4 request for those accounts is an immediate high-confidence Kerberoasting indicator.
The most common tools: Rubeus (C#, runs in memory, can request RC4 tickets and output them in hashcat format in one command), Impacket's GetUserSPNs.py (Python, runs from a Linux attacker machine using domain credentials), and the original PowerSploit Invoke-Kerberoast.ps1 (PowerShell, often flagged by EDR). After obtaining the hashes, attackers use hashcat with mode 13100 (Kerberos 5 TGS-REP etype 23) against wordlists and rule sets. A service account with a common password pattern ('Winter2023!') can be cracked in minutes. An account with a 25-character random password would take longer than the age of the universe to crack.
A Group Managed Service Account (gMSA) is an Active Directory account type where the password is managed automatically by AD: it is 120 characters of random data, rotated every 30 days, and never stored as a human-readable password anywhere. The password is retrieved by authorized computer accounts via the Netlogon protocol and injected into the service at startup. This prevents Kerberoasting because even if an attacker obtains the Kerberos service ticket for the gMSA, cracking the 120-character random password is computationally infeasible with any current hardware. Create a gMSA with: New-ADServiceAccount -Name svc-webapp -DNSHostName webapp.domain.com -PrincipalsAllowedToRetrieveManagedPassword 'WebServer$'.
How do you identify which service accounts in Active Directory are Kerberoasting targets? Any domain user account with a registered Service Principal Name (SPN) is a Kerberoasting target. Run 'Get-ADUser -Filter {ServicePrincipalName -ne "$null"} -Properties ServicePrincipalName, PasswordLastSet, PasswordNeverExpires' to list all such accounts along with when their password was last changed. Prioritize based on two factors: password age and privilege level. Accounts with passwords older than 90 days and high-privilege group memberships (Domain Admins, Schema Admins, or local admin on servers) are the highest risk because cracking yields elevated access and the password has had more time to appear in breach databases or wordlists. Accounts with PasswordNeverExpires set are also higher priority since their hashes are stable targets. Cross-reference the SPN list against your actual running services to identify orphaned SPNs: accounts that have SPNs registered but are not actually running any service. Orphaned SPN accounts are often forgotten, still have old passwords, and are Kerberoasting targets with no operational reason to keep them active. Remove SPNs from accounts that no longer run services or disable the accounts entirely.
25 actively exploited vulnerabilities with CVSS scores, exploit status, and patch availability. Print it, pin it, share it with your SOC team. Step-by-step 24-hour IR checklist covering detection, containment, eradication, and recovery. Built for SOC teams, IR leads, and CISOs.
50,000+ security professionals read Decryption Digest for early warnings on zero-days, ransomware, and nation-state campaigns. Free, daily, no spam. Cybersecurity professional with expertise in threat intelligence, vulnerability research, and enterprise security. Covers zero-days, ransomware, and nation-state operations for 50,000+ security professionals every morning.
Actionable threat intelligence for working practitioners. Free. No spam. Trusted by 50,000+ SOC analysts, CISOs, and security engineers. A Kerberoasting attack exploits the Kerberos authentication protocol by extracting service account tickets from Active Directory to crack their passwords offline. Organizations can defend against this threat by enforcing long, complex passwords, implementing Managed Service Accounts, and utilizing real-time monitoring to detect unusual ticket requests.
A kerberoasting attack is one of the most common and effective post-exploitation techniques used to compromise Active Directory (AD). By exploiting how the Kerberos protocol handles service tickets, attackers can harvest account credentials without ever sending a single packet to the target system. Because kerberoasting targets service accounts, which often have high privileges and weak passwords, it is a high-priority threat for IT security teams.
In this guide, we break down the anatomy of the attack and provide actionable strategies for detecting kerberoasting before it leads to a full domain compromise. Active Directory (AD) is the beating heart of many organizations, IT infrastructures, managing user accounts, permissions, and access to critical resources. However, beneath its seemingly impenetrable exterior lies a vulnerability that attackers are increasingly exploiting: the Kerberoasting attack. Let’s take a look at this threat, understand its mechanics, and uncover why Active Directory is a prime target.
At its core, a Kerberoasting attack is an exploitation of the Kerberos authentication protocol , which is the backbone of Active Directory security . Here’s a simplified breakdown of a Kerberoasting attack: Over 80% of breaches involve brute force or the use of stolen credentials — Kerberoasting directly exploits weak service-account credentials.
2. System Architecture & Core Working Principles Active Directory, by design, is built on trust relationships due to its reliance on legacy Kerberos configurations. Kerberos relies on the security of passwords to protect service tickets. The exploit doesn’t require administrative rights to initiate, making it a “low-hanging fruit” for attackers.
The consequences of a successful Kerberoasting attack can be severe. Attackers can leverage compromised service accounts to move laterally within the network, gaining access to sensitive data, intellectual property, and financial information. In a worst-case scenario, they can elevate their privileges to domain administrator, effectively taking control of the entire Active Directory domain.
The fallout from such a breach can include financial losses, reputational damage, and regulatory fines. Furthermore, recovering from a Kerberoasting attack can be costly and time-consuming, disrupting business operations and eroding stakeholder trust. Understanding the threat of Kerberoasting is the first step toward protecting your Active Directory environment. Cayosoft Guardian offers extensive visibility into service account activities, enabling you to identify suspicious behavior and potential Kerberoasting attempts before they escalate.
While the stealthy nature of Kerberoasting attacks can make them difficult to detect, there are signs within Active Directory that can alert you to an ongoing breach. By proactively monitoring these indicators, you can catch attackers in the act and prevent them from inflicting significant damage. Event logs serve as your first line of defense in detecting Kerberoasting attacks. Active Directory logs various events, such as Kerberos service ticket requests ( Event ID 4769 ), which can be monitored to spot unusual patterns indicative of an attack in progress. Key indicators include: The median time attackers remain undetected is still measured in days . Proactive kerberos monitoring is the only way to shorten this window and stop a breach in progress.
Successful kerberoasting detection depends on your ability to distinguish a legitimate Ticket Granting Service (TGS) request from an exploit. Because the Kerberos protocol uses TGS tickets to authenticate users to specific services, an attacker must request these tickets before they can begin the offline cracking process. To catch them, you must monitor for an abnormal volume of TGS-REQ packets, particularly those targeting high-privilege service accounts with active Service Principal Names (SPNs).
Effective kerberoasting detection requires not only scheduled scans for extensive gap analysis in Active Directory and Entra ID but also real-time monitoring of changes that may indicate immediate threats. For example, if a standard user account suddenly requests dozens of tickets for SQL or Exchange services within seconds, it is a clear sign of a service account scan. Cayosoft Guardian ‘s threat module is specifically designed to address both needs effectively. It offers real-time alerts for suspicious activities, such as password spray attacks (a common component of Kerberoasting) by continuously monitoring for signs that indicate such exploits. This dual approach ensures that you are equipped to quickly respond to emerging threats and protect your critical assets.
Detecting Kerberoasting attacks is crucial, but prevention is the ultimate goal. Let’s explore some proven strategies to safeguard your Active Directory setup against Kerberoasting attacks. The simplest yet most effective defense against Kerberoasting is to enforce strong password policies for all service accounts, including the following specifics: While strong passwords may seem like a basic precaution, they are often overlooked in the context of service accounts. They represent a significant barrier to attackers attempting to crack service tickets.
Service accounts are often the “weakest link” in kerberoasting because they are frequently over-privileged and poorly monitored. Implementing proper service account hygiene is crucial but challenging, as they are essentially user accounts that may not be easily identifiable by native tools. Cayosoft Administrator provides robust user management and reporting functions that are vital for maintaining account hygiene. It helps to: Cayosoft Administrator not only assists in maintaining optimal service account hygiene but also provides seamless management across both Active Directory and Entra ID, ensuring a strong defense against potential security threats.
In healthcare organizations, Kerberoasting poses a unique and dangerous threat. Service accounts are often tied to essential clinical systems like EHRs, lab integrations, and imaging software, making them high-value targets for attackers. If compromised, these accounts could grant unauthorized access to sensitive patient data or disrupt care delivery. Cayosoft’s healthcare identity management solutions are purpose-built to address these challenges, helping IT teams enforce strong service account controls, identify misconfigurations, and monitor changes across Active Directory in real time, all while supporting compliance with data privacy regulations like HIPAA.
Compromised service accounts are a frequent cause of healthcare breaches. These accounts can expose EHRs and clinical systems if not tightly controlled. MSAs offer a technical solution to the challenge of managing service account passwords. Unlike standard service accounts, MSAs do not have a password that a human knows or manages. Windows automatically handles the password generation and rotation (using complex 240-byte passwords) at the Domain Controller level. This not only enhances security but also reduces the administrative burden on IT teams. While MSAs are not a silver bullet, they can be a valuable addition to your Kerberoasting defense strategy.
While the previous strategies focus on specific tactics to deter Kerberoasting attacks, a comprehensive approach to Active Directory security is essential for long-term resilience. A holistic perspective lets you create a multi-layered defense that both thwarts Kerberoasting and strengthens your overall security. Regular security audits and assessments are like routine checkups for your Active Directory environment. They provide valuable insights into potential vulnerabilities, including weak passwords, misconfigured service accounts, and excessive permissions.
By conducting both internal and external assessments, you can identify accounts with registered SPNs that haven’t been rotated in years. Identifying these weaknesses early allows you to remediate them before an attacker can request a service ticket for offline cracking. The principle of least privilege (PoLP) is a fundamental security concept that emphasizes granting users and service accounts only the minimum necessary permissions to perform their tasks. By adhering to PoLP, you minimize the potential damage an attacker can inflict if they compromise an account.
Review the permissions assigned to each service account and remove any unnecessary privileges. Implement role-based access control (RBAC) to further refine permissions and ensure that users and service accounts have access only to the resources they need. With RBAC, even if an attacker successfully cracks a service account password, their ability to move laterally or escalate to Domain Admin is strictly limited.
Despite your best efforts, there’s always a chance that an attacker may successfully execute a Kerberoasting attack. Having a well-defined incident response plan in place can significantly reduce the impact of a breach. The average cost of a U.S. data breach is in the multi-million-dollar range . Preventing Kerberoasting and account compromise is far cheaper than remediation.
Cayosoft Guardian not only helps with detecting and preventing Kerberoasting attacks but also provides tools and resources to streamline incident response and recovery, including granular and automated rollback capabilities that protect objects from unwanted changes and surpass native Active Directory rollback. By integrating Cayosoft Guardian into your security strategy, you can enhance your overall resilience to cyber threats.
Protecting your organization against Kerberoasting attacks is a critical component of Active Directory security, but it’s only one piece of the puzzle. To truly safeguard your organization’s data, you need a multi-faceted approach that addresses a wide range of threats and vulnerabilities. Cybersecurity is constantly evolving, with new threats and attack vectors emerging regularly. To maintain a robust defense, continuous monitoring and adaptation are essential. This means not only keeping abreast of the latest security trends and vulnerabilities but also proactively adjusting your security measures to address them.
Regularly review and update your security policies, procedures, and technologies to ensure that they remain effective against the latest threats. Implement a security information and event management (SIEM) solution to aggregate and analyze logs from various sources, providing a centralized view of your security posture. Cayosoft Guardian is your protection against Active Directory threats, including Kerberoasting attacks. It continuously monitors your identity infrastructure, providing automatic threat detection and enabling swift incident recovery. Cayosoft Guardian allows organizations to proactively identify and mitigate security risks, gain insights into suspicious activity, enforce strong password policies, and ensure compliance, all while streamlining security management.
Ready to see Cayosoft Guardian in action? Schedule a demo today and discover how it can elevate your Active Directory security posture. Kerberoasting attacks cleverly exploit a combination of factors inherent to Active Directory. First, the Kerberos authentication protocol, while robust, relies on the strength of passwords protecting service tickets. Second, Active Directory environments often house a multitude of service accounts, many with privileged access, making it challenging to maintain strong, unique passwords for each one. This creates fertile ground for attackers to request and crack these service tickets, ultimately gaining unauthorized access.
While completely eliminating the risk of Kerberoasting attacks is difficult, proactive measures can significantly reduce your vulnerability. Enforcing strong password policies for service accounts, implementing regular audits and assessments, and adhering to the principle of least privilege can create a multi-layered defense that makes it significantly harder for attackers to succeed. Solutions like Cayosoft that automate password management and provide real-time monitoring can further bolster your defenses.
3. Software Implementation, Frameworks & Protocols Early Kerberoasting detection is crucial for minimizing the impact of a Kerberoasting attack. Actively monitor Active Directory event logs to identify telltale signs of an attack, like unusual service ticket requests, repeated failed login attempts for service accounts, or an abnormal volume of TGS requests.
While Kerberoasting is a significant threat, it’s not the only one facing Active Directory. Other attacks (like Golden Ticket, Silver Ticket, and DCSync) also target Kerberos vulnerabilities. A comprehensive Active Directory security strategy should encompass a broad range of protective measures, including strong password policies, regular audits, access controls, and proactive monitoring.
Cayosoft offers a suite of Active Directory security solutions designed to mitigate the risk of Kerberoasting attacks. It offers automated password management for service accounts, real-time monitoring and alerting capabilities for suspicious Kerberos activity, and streamlined incident response. Through these and other capabilities, Cayosoft empowers organizations to proactively defend their Active Directory environments and minimize the potential damage from attacks.
Identity Threat Detection and Response for Active Directory, Entra ID, Intune & Microsoft 365. Kerberoasting is one of those AD techniques that shows up constantly, it’s usually one of the first things tried once someone’s got any foothold at all. Part of why it’s so popular is that it’s quiet, needs no special privileges, and just abuses how Kerberos authentication is designed to work in the first place. I ran the full attack in the lab and then built out detection and defense around it.
Kerberos uses Service Principal Names (SPNs) to link service instances to their logon accounts. Any authenticated domain user can request a Ticket Granting Service (TGS) ticket for any SPN in the domain. The ticket comes back encrypted with the service account’s NTLM hash. Once that ticket’s in hand you crack it completely offline, no more network noise, no lockout risk, and you never needed elevated privileges just to request it in the first place. That combination is exactly why it’s dangerous.
Rubeus queries the domain for all accounts with SPNs registered, requests a TGS ticket for each one, and dumps the hashes to a file. The output looks like a wall of Kerberos ticket data in hashcat-ready format. If Hashcat returns a hardware error, add --force . Once finished, the cracked output shows the plaintext password alongside the hash.
The primary detection signal is Event ID 4769 (Kerberos Service Ticket Operations). A Kerberoasting attempt will generate 4769 events with: Any activity against a honeypot SPN is suspicious by definition. No legitimate service should be requesting tickets for an account that does not actually run a service.
For two weeks, an attacker asked a domain controller for service account tickets and took them away to crack offline. The production identity server at the center of it ran no endpoint agent, so nothing on that machine recorded any of it. Every request succeeded because every request was a legitimate Kerberos operation. The attack is known as Kerberoasting: someone holding any ordinary user account in your domain asks a domain controller for a service ticket, then cracks a privileged service account's password out of that ticket offline. They exploit no flaw to do it.
Nothing fails, nothing locks out, and no alarm has to fire. The mechanism is ordinary Kerberos. Any authenticated user in an Active Directory domain can ask a domain controller for a service ticket, and the domain controller encrypts that ticket with a key derived from the service account's password. You don't need a special privilege to ask. Nothing about the request may look out of place. The attacker takes the ticket away and works on cracking the password on their own hardware, where none of your monitoring tools can detect their activity.
That two week case comes from Prophet Security's Q3 2026 threat report. What exposed it was the pattern of ticket requests arriving at the domain controller, reconstructed from authentication logs and from telemetry belonging to a different host. This guide details the assets an attacker steals during an attack and explains why monitoring the domain controller is essential for reliable Kerberoasting detection. Additionally, it addresses the evolving significance of the encryption type field, outlines step-by-step investigation procedures, and provides strategies to harden directory accounts against roasting. For foundational concepts on handling security alerts, refer to our overview on alert triage .
MITRE ATT&CK tracks Kerberoasting as T1558.003 , a sub-technique of Steal or Forge Kerberos Tickets (T1558). The target is any user account carrying a service principal name, or SPN, in its servicePrincipalName attribute. Computer accounts carry SPNs too, but their passwords are long and machine-generated, so nobody bothers. The SPN tells Kerberos which account a service runs as, and the key distribution center will issue a ticket for that account to anyone who asks.
The ticket is not the prize. The password behind it is. And a cracked service account password lasts, where a stolen session does not. These accounts usually have no person attached, no MFA in front of them, and a password nobody has changed in years. Most of them can do more than they need to, because whoever set the account up granted whatever made the application work instead of taking the time to scope the permission to least privilege.
Two things follow from that. An attacker who cracks one useful SPN account often does not need to escalate again. And there is no failed login burst to alert on, unlike the patterns behind a credential stuffing investigation , because every request in a Kerberoasting run is a legitimate, successful Kerberos operation. The request and the crack happen in two different places. One touches your domain controller. The other happens on hardware you do not own and cannot instrument. In between, the attacker's own machine still leaves evidence, though you rarely have visibility into it. Common Kerberoasting tools have known detections, and the LDAP enumeration and service ticket requests they generate can be tracked in domain controller event logs. That evidence can be hard to sort through, but it is still worth collecting.
You have very little endpoint telemetry to work with here, and that is a real departure from most of what arrives in the queue. The techniques in our guide to investigating EDR alerts assume the attacker's process did something on a host you are watching. Kerberoasting does not require that. In the case above, the machine under attack carried no agent, so there was nothing to investigate on the asset that mattered.
So the main event to collect is 4769, "A Kerberos service ticket was requested." It is written to the Security log on domain controllers only. The common gap is that the DCs generate it and nobody forwards it. Check what your SIEM is actually receiving before assuming the data is there. Microsoft also extended the event schema in the January 2025 cumulative update for Windows Server 2016 and later. It now carries the account's supported encryption types and the encryption types advertised in the request, both useful here.
The classic detection is the Ticket Encryption Type field on event 4769. These are the values you will see: Attackers target accounts with legacy encryption types, like 0x17. The RC4 key comes straight from the password, with no salting and no iteration, so an RC4 ticket cracks far faster than an AES one. Microsoft's own guidance says to expect only 0x11 and 0x12 in a current environment, and to treat DES or RC4 as odd.
Before relying on this indicator to build a detection, consider two factors that have already diminished its efficacy. The first is that Microsoft has already turned RC4 off. The change addresses CVE-2026-20833 , and it landed in three phases through 2026. January was audit only. From April, the KDC issued AES-only tickets for any account with no explicit msDS-SupportedEncryptionTypes value. In July the rollback option went away and enforcement became permanent.
So RC4 still works, but only where somebody has explicitly configured an account to accept it. What decides that now is the account's msDS-SupportedEncryptionTypes attribute, the domain controller's DefaultDomainSupportedEncTypes registry value (which is what the April 2026 change flipped to AES), and the Group Policy setting for allowed Kerberos encryption types. Domain functional level is not what decides whether RC4 is issued.
Plenty of environments still allow RC4 on purpose, usually for a legacy system that can't do AES, such as an old appliance, a storage array, a Java app or Linux keytab running an old Kerberos config, or a vendor product nobody has touched in years. A 0x17 rule fires every time those services authenticate, and the easy move is to suppress it . Don't. List the accounts that still allow RC4 and the hosts that normally request tickets for them, then alert on anything outside that list: RC4 for an account that isn't on it, or a ticket for a listed account requested from a host that has never asked before. Those accounts are also the easiest to crack in the domain, so put them first in line for the hardening steps below.
The second is that attackers were already declining the tell. Tools exist that ask for AES tickets on purpose, to get past RC4-based detections. AES tickets are slower to crack, not impossible. A weak password is still weak either way. And RC4-only detection fires on things that are not attacks, because until the April 2026 change, user accounts with SPNs defaulted to RC4 wherever msDS-SupportedEncryptionTypes was unset.
Keep the encryption type check. Before you rely on it, find out what your domain actually enforces, and pair it with detections that do not depend on the attacker choosing the noisy option. Rather than relying solely on encryption types, three stronger signals offer more reliable detection. Once a Kerberoasting alert fires, follow the steps below to understand what happened and what's at risk.
4. Practical Deployment, Analysis & Case Studies The Prophet Security case in the Q3 report is instructive in that the Kerberoasting ran for over two weeks against a production identity server with no endpoint coverage. Several of the longest-running intrusions in that dataset were surfaced through telemetry from a host other than the one the attacker worked from.
Building the picture from other machines is slow, and it may turn up nothing. So it gets skipped when four hundred other alerts are waiting. What came back in that investigation included something nobody asked for: a list of assets authenticating to the directory with no agent reporting on them. That list underscores the need to reconcile your endpoint agent coverage against your authentication logs rather than your asset inventory. An inventory tells you what someone wrote down. The authentication log tells you what is actually talking to your directory. That includes machines nobody ever inventoried, and ones whose agent went quiet months ago. Dormant and orphaned accounts sit in the same blind spot, which is what we found unmasking zombie credentials in an acquired subsidiary.
You cannot block Kerberoasting outright. Handing service tickets to authenticated users is what Kerberos is for. What you can do is make the stolen ticket worthless. Group managed service accounts are the strongest answer. A gMSA password is 120 characters, randomly generated, and rotated automatically on a schedule that defaults to 30 days. An attacker can still Kerberoast a gMSA and still request the ticket, but nobody will crack a 120-character random password before it rotates. Windows Server 2025 also introduced delegated managed service accounts, which bind authentication to specific machine identities and keep the secret on the domain controller. They are worth adopting, with the caveat that the BadSuccessor technique disclosed in 2025 showed that write access to a dMSA object can be abused for privilege escalation, so lock down who can create or modify them.
Where a gMSA will not work, length is what matters. Microsoft sets a 14 character floor for service accounts and wants much longer, fully random, and not a word from any dictionary. Microsoft says plainly that moving to AES is not enough on its own. It has to come with strong passwords. Then find out what you have. You can query the same attribute the attacker does. List every user object with a non-null servicePrincipalName, and for each one write down the password age, what it can do, and whether the service behind it still exists. Any account that fails the third check is the cheapest thing on this list to fix, since you can usually disable it rather than rotate it. That audit has a blind spot. An account with GenericWrite, GenericAll, or Validated-SPN rights over another user object can write an SPN onto it and roast it, so an account with no SPN today is still exposed if the wrong people can edit it.
Review who holds write rights over privileged user objects as part of the same exercise. Turning that audit into standing coverage is the job of an AI detection engineer . You cannot take the usual shortcuts with Kerberoasting. The alert that fires is a normal Kerberos operation. RC4 is gone as a default, and RC4 is what most existing detections key on. The offline half of the attack is invisible by design. And the assets where it runs longest are the ones carrying the least instrumentation. Answering it properly means pulling the full request set, mapping exposed accounts to their privilege, and reconstructing events from directory telemetry when the host has none.
That work is procedural and it takes time, which is why it competes badly against a queue. Prophet AI SOC Analyst investigates every alert to that depth without prioritizing. It scopes the request window, maps the exposed service accounts, and follows what those accounts did afterwards, recording the evidence behind each step. Request a demo of Prophet AI to see how it runs a full investigation against your own alerts.
Kerberoasting recovers a service account's plaintext password by cracking a Kerberos service ticket offline. Pass-the-hash reuses a stolen password hash directly for authentication without ever recovering the password. Kerberoasting needs no privilege to start and no access to the target host, only a valid domain account. Pass-the-hash requires first obtaining the hash, usually from memory on a compromised machine.
Event 4769, A Kerberos service ticket was requested, written to the Security log on domain controllers only. A default domain controller logs it on success, but Failure auditing is off by default and the event is only useful if it is being forwarded. Check that it is actually being collected before building any detection on it, because many environments generate it and never ship it anywhere.
No. AES tickets are slower to crack than RC4 tickets, not impossible, and a weak service account password remains crackable either way. Microsoft states that moving to AES is not sufficient on its own and must be paired with strong passwords. What did change is the RC4 signal: under CVE-2026-20833 Microsoft removed RC4 as a default through 2026, so alerting on encryption type 0x17 catches less than it used to.
Enumerate every user object with a non-null servicePrincipalName attribute, which is the same attribute an attacker queries. For each account, record the password age, the privilege it holds, and whether the service behind it still exists. Accounts supporting a service that no longer runs are the cheapest exposure to remove, since they can usually be disabled rather than rotated.
Not immune, but impractical to crack. A group managed service account with a service principal name can still be Kerberoasted and its ticket can still be requested. The password is 120 characters, randomly generated, and rotated automatically on a 30 day default schedule, so no practical cracking effort will recover it before the next rotation. You cannot observe the cracking, because it happens offline on the attacker's own hardware. The determination has to come from the exposed account's later behavior: authentication from sources or at times that do not match its history, new sessions on hosts it can reach, or changes made using it. Treat the account as compromised, since no available evidence would prove otherwise.
The attack patterns seen most across customer environments, and why some of those attacks succeeded where others were blocked. Josh is a senior security analyst at Prophet Security. Prior to Prophet, Josh was a detection and response analyst at Rapid7 Kerberoasting remains one of the most reliable privilege escalation paths in Active Directory environments — not because it’s sophisticated, but because the conditions enabling it are endemic to enterprise networks.
When a user authenticates to a service in Active Directory, the Kerberos Key Distribution Center (KDC) issues a Ticket Granting Service (TGS) ticket encrypted with the service account’s NTLM hash. Any authenticated domain user can request this ticket. The critical detail: the ticket is encrypted with the service account’s password hash . If the password is weak enough to crack offline, the attacker gains the cleartext password — no interaction with the service required, no network noise after the initial ticket request.
Run these commands only in an owned lab or a sanctioned assessment with written scope. Replace the placeholders with lab values; do not point broad authentication tests at production ranges without explicit approval. Event ID 4769 — A Kerberos service ticket was requested. High-volume TGS requests from a single account in a short time window is a reliable signal.
The encryption type is the key indicator. Modern environments should be using AES (0x12/0x18). RC4 requests for service tickets warrant investigation. Enforce AES encryption — Set msDS-SupportedEncryptionTypes on service accounts to require AES (value: 0x18 ). Managed Service Accounts (gMSA) — Automatically rotate passwords (240-character random), eliminating crackability.
Drop-in replacement for most service account use cases. Privileged account isolation — Service accounts with SPNs should never have domain admin rights. Scope permissions to what the service actually needs. Password length policy — If you can’t migrate to gMSA, enforce 25+ character passwords on all SPN accounts. 25+ characters with standard complexity makes offline cracking computationally infeasible with current hardware.
Kerberoasting’s longevity as an attack technique reflects a structural problem: service accounts are long-lived, often over-privileged, and their passwords rarely rotated. The fix is architectural, not just technical. Migrate to gMSAs, enforce AES, and segment service account privileges. The detection is straightforward — the hardening is what organizations avoid. Kerberoasting rarely operates in isolation. Once a service account is cracked, attackers typically chain to LSASS dumping for local credentials and ADCS abuse for certificate-based privilege escalation — often using LOLBins for lateral movement throughout. In hybrid environments, on-premises credential access is usually a stepping stone toward Entra ID and cloud resources.
Active Directory Certificate Services is installed in most enterprise networks — and almost always misconfigured. Here's how attackers exploit ESC1 through ESC8 with Certipy, and how to detect and stop them. The most dangerous defenders understand how attackers think. The best red teamers understand what defenders see. Here's why the divide between offense and defense is killing your security program.
DCSync abuses Active Directory replication to pull every password hash from a domain controller without touching it. Here's how the attack works, what it leaves in your logs, and how to build detections that catch it. 5. Performance Evaluation & Extended Technical Observations Kerberoasting has been sitting on the MITRE ATT&CK list since 2018, but 2026 is the year it finally forced Microsoft’s hand.
IBM’s own RC4 deprecation guidance, published in May 2026, points to exactly why: kerberoasting incidents doubled between 2022 and 2023 alone, and IBM X-Force’s July 2025 threat intelligence report found that stolen credentials, kerberoasting included, played a role in 30% of the intrusions it investigated that year. Microsoft didn’t move quickly on its own: as of September 2025, it still supported RC4 by default a full 11 months after first promising a fix, prompting Senator Ron Wyden’s office to point out that RC4 dates back to the 1980s and remains squarely exploitable for Kerberoasting; that same month Microsoft committed to having Windows Server 2025 disable RC4 by default in new AD domains starting in Q1 2026. In January 2026, Microsoft began shipping Kerberos protocol hardening updates tied to CVE-2026-20833 , a Windows Kerberos information disclosure flaw (CVSS 5.5) that exists precisely because RC4-HMAC is still allowed as a fallback encryption type on most domain controllers. The April 2026 updates flipped the default so that accounts without an explicit encryption setting now get AES-SHA1 tickets instead of RC4, and full enforcement became permanent after July 2026. If your Active Directory environment still has service accounts issuing RC4 tickets, an attacker with nothing more than a standard domain user account can request a ticket, take it offsite, and crack the service account password without ever touching your logs in a way that looks unusual.
This tutorial walks through detecting and stopping Kerberoasting the way security teams are actually doing it in August 2026: auditing which service accounts are exposed, reading the right Windows Event IDs, migrating to AES-only Kerberos tickets, rotating exposed credentials to Group Managed Service Accounts, and wiring up detection rules in Microsoft Defender for Identity and a SIEM. By the end you’ll have a working PowerShell audit script, a Splunk/Sentinel detection query, and a hardened AD environment that no longer hands attackers crackable password hashes on request.
Add Tech Insider once in the Google app and our stories appear in your news suggestions. Kerberoasting is a credential-theft technique cataloged as MITRE ATT&CK T1558.003 that abuses a completely legitimate feature of the Kerberos authentication protocol used by every Active Directory domain. Any authenticated domain user, even a low-privilege one, is allowed to request a Kerberos service ticket (a TGS, or ticket-granting service ticket) for any service that has a Service Principal Name (SPN) registered in AD. That ticket is encrypted with a key derived from the service account’s own password. The attacker doesn’t need to touch the domain controller’s memory or trigger an alert to get it, they just ask for it, which is a normal part of everyday Kerberos authentication. As BleepingComputer put it in a November 2025 report, that’s precisely what makes the technique so dangerous: it hands an attacker everything needed to crack a service account’s password completely offline, with no alert ever firing back on the domain controller.
Once the attacker has that ticket, they take it offline and try to crack the password hash with tools like Hashcat, completely outside the network where no defensive tooling can see it happening. Automated tooling has made that step almost instantaneous: research from Lyrie.ai published in May 2026 found that a single off-the-shelf Rubeus run can pull down hundreds of roastable ticket hashes in under two minutes, turning what used to be a slow, targeted attack into something an intruder can point at an entire domain before lunch. If the service account was still using RC4-HMAC encryption, cracking is fast because RC4’s key derivation is comparatively weak and doesn’t include the salting that AES tickets get. If the service account has a short or dictionary-guessable password, even AES tickets eventually fall. According to Microsoft’s own guidance on mitigating Kerberoasting , “administrators can use the techniques described below to detect Kerberoasting cyberattacks in their network,” specifically recommending teams check for ticket requests with unusual Kerberos encryption types and repeated service ticket requests as the two clearest signals. That’s the foundation this entire tutorial is built on: encryption-type auditing plus request-volume monitoring.
What makes Kerberoasting dangerous rather than merely theoretical is what service accounts tend to have access to. They’re frequently over-privileged (sometimes with Domain Admin rights inherited from years of “just make it work” IT decisions), rarely rotated because rotating a service account password used to mean an outage, and often set up with static, human-typed passwords instead of the long random secrets a properly configured account should have. Crack one SQL service account password and an attacker can move laterally into a database server, a backup system, or in the worst case, escalate straight to domain-wide control.
Kerberoasting rarely appears as the opening move in an attack. It shows up in the middle, after an attacker has already established a foothold through phishing, an exposed VPN credential, or exploitation of an internet-facing vulnerability, and needs a way to move from “one compromised laptop” to “control of the domain.” That middle-stage role is exactly what makes it so persistent: it doesn’t trigger endpoint antivirus, it doesn’t require malware, and from the domain controller’s point of view it looks like an ordinary Kerberos ticket request because, technically, it is one. The stakes of getting that stage wrong are not
Abstract
in a September 2025 statement, Senator Ron Wyden’s office cited a Kerberoasting-linked breach that exposed 5.6 million Ascension patient records as a real-world example of what happens once that privilege escalation succeeds. Threat intelligence coverage through 2025 and into 2026 consistently places Kerberoasting alongside NTLM relay and Pass-the-Hash as one of the small set of credential-abuse techniques that repeatedly turns a single-endpoint compromise into a full domain compromise, particularly in ransomware intrusions where the attacker’s entire goal is reaching Domain Admin fast enough to disable backups and deploy the encryptor before the SOC can respond. Microsoft’s own telemetry underscores just how large that pool of opportunity is: the company reported in May 2026 that it now tracks roughly 600 million identity attacks per day across its customer base, a volume that keeps Kerberos ticket abuse squarely in the credential-theft mix threat intel teams have to prioritize.
Abstract Art
The reason RC4 specifically matters so much in that chain comes down to time. An AES256 ticket for a strong, randomly generated password is not meaningfully crackable with commodity hardware in the hours an attacker typically has before detection. An RC4 ticket for a service account with a human-chosen, 12-character password can fall in minutes on a single modern GPU. But moving to AES doesn’t make the password problem disappear on its own: a Mine2 study released in April 2026, after the RC4 default flip had already rolled out, found that 78% of Active Directory environments it scanned still had at least one AES-ticketed service account crackable within a practical timeframe, almost always because the underlying password was still short or human-chosen rather than randomly generated. That gap between “minutes” and “computationally infeasible” is the entire reason Microsoft treated RC4 deprecation as urgent enough to force through CVE-2026-20833 rather than leaving it as an optional hardening recommendation buried in a best-practices document nobody reads. Every step in this tutorial exists to close that specific gap: remove RC4, remove weak static passwords, and reduce the standing privilege of the accounts an attacker would even bother targeting in the first place.
Abstract Definition
This tutorial assumes you’re working in a Windows Server-based Active Directory environment. You don’t need every tool listed to follow along, but the audit and hardening steps assume access to a domain admin or delegated AD-auditor account. Here’s what to have ready before you start. A note on Rubeus and Impacket’s GetUserSPNs.py: both are legitimate, widely used offensive-security tools built for exactly this kind of testing, and you should only run them against systems you own or have written authorization to test. Every command in this guide that touches those tools is meant for a lab domain controller or an authorized penetration test, not production.
Abstraction
You can’t protect what you haven’t found. The first step is a full inventory of every account in the domain that has a Service Principal Name registered, because every single one of those accounts is a valid Kerberoasting target. Run this from a domain-joined machine with the RSAT AD PowerShell module installed and an account that has read access to the domain. The msDS-SupportedEncryptionTypes column is the one to pay attention to first. A value of 0x18 (decimal 24) means the account is configured for AES128 and AES256 only, which is what you want. A blank value, a value of 0 , or anything that still includes RC4 in the bitmask means that account is currently exposed to weak-encryption Kerberoasting. Sort the CSV by IsPrivileged = True first; those are the accounts an attacker will target for maximum blast radius, and they’re the ones you fix today, not next sprint.
Abstraction Tadc
Kerberoasting detection lives almost entirely inside three Windows Security event IDs generated on your domain controllers. Get familiar with all three before you write a single detection rule, because they correlate with each other and a Kerberoasting attempt usually shows up as a specific pattern across all of them, not just one isolated log line. Event ID 4769 is where you’ll spend most of your time. Every time it fires, the log includes a Ticket Encryption Type field, and the values to know are 0x12 and 0x18 (AES256 and AES128, in the hex encoding most log tools display), versus 0x17 , which is RC4-HMAC. A domain controller logging bursts of 4769 events with etype 0x17 against multiple distinct SPNs, from one user account, in a short window, is close to the textbook definition of a Kerberoasting attempt. Security researcher Will Schroeder, whose ADSecurity.org research effectively defined how the industry detects this technique, put it plainly: “Looking for TGS-REQ packets with RC4 encryption is probably the best method, though false positives are likely.” That caveat about false positives matters, because some legacy line-of-business applications still request RC4 tickets legitimately, which is exactly why Step 1’s inventory work has to happen before you turn on aggressive alerting. Vendors have been working the same problem from the detection-engineering side: BeyondTrust tested a statistical Kerberos-detection framework in July 2025 specifically aimed at cutting down the false-positive rate on exactly this kind of etype-based alerting, reinforcing that a naive “alert on any RC4 request” rule isn’t where mature teams should land.
Abstract Meaning
None of the event-ID monitoring in Step 2 works if your domain controllers aren’t generating detailed Kerberos audit logs in the first place. Confirm the audit policy is enabled with this command, then push it through Group Policy if it isn’t already active domain-wide. Apply this through a Group Policy Object linked to the Domain Controllers OU rather than setting it locally on each DC, so new domain controllers inherit the policy automatically. Once this is active, confirm events are actually landing in the Security log on a test DC before moving on, an empty log after enabling audit policy usually means the GPO hasn’t replicated yet or the policy is being overridden by a higher-precedence GPO.
Abstract Noun
With audit logging confirmed, the next step is turning raw 4769 events into an actual alert. The pattern you’re hunting for is one account requesting tickets for an unusual number of distinct SPNs in a short window, especially with RC4 encryption types mixed in. Here’s a Splunk search that implements Microsoft’s guidance on monitoring 4769 volume and encryption type together, adaptable to Microsoft Sentinel’s KQL with minor syntax changes.
Abstract Painting
Tune the thresholds (5 distinct SPNs, 15 requests in 10 minutes) against your own baseline before enabling this as a page-worthy alert; a batch job or monitoring tool that legitimately enumerates services can trip a poorly tuned rule. If you want a tighter window suited to how fast modern tooling actually runs, a May 2026 ITDR playbook from Lyrie.ai recommends flagging any single principal that requests TGS tickets for more than five distinct services within a 60-second window, a threshold built specifically around how quickly automated Rubeus-style roasting completes. Run whichever version you choose in report-only mode for a week, review the accounts it flags, and add known-good service accounts to an allowlist before switching it to an active alert.
Abstract Expressionism
If your organization is already running Microsoft Defender for Identity, you get a meaningful chunk of Kerberoasting detection out of the box, but only if the sensor is deployed on every domain controller, not just the ones that seemed most important at rollout time. Defender for Identity raises alert ID 2410 for suspected Kerberos SPN exposure, and Defender XDR correlates that with wider identity telemetry to reduce false positives compared to a standalone SIEM rule.
Abstracted Jax
If your organization is weighing Defender for Identity against other endpoint and identity detection stacks, see our breakdown of CrowdStrike Falcon vs. Microsoft Defender XDR for a fuller pricing and capability comparison. To confirm coverage, go to Microsoft Defender XDR, open Settings, then Identities, and check that every domain controller in your forest shows a “Healthy” sensor status. Any DC marked as unmonitored is a blind spot an attacker can exploit specifically because it isn’t watched. Once coverage is confirmed, review the Kerberos-related alert policies under Defender for Identity’s alert tuning settings and make sure “Suspected Kerberoasting attack” and “Suspected SPN exposure” (the underlying detections behind alert 2410) are both set to notify your SOC rather than being logged silently. Microsoft has also been expanding coverage on the Entra ID side of the house: in April 2026 it added 14 new token risk signals to Entra ID Protection specifically aimed at catching credential abuse, kerberoasting included, which is worth enabling alongside Defender for Identity if your identity estate spans both on-prem AD and Entra ID.
SIEM rules and Defender for Identity alerts catch attacks in progress. PingCastle and Semperis Purple Knight catch the exposure before an attack ever starts, by scoring your domain against known weak configurations, including SPN accounts with legacy encryption enabled, accounts with AdminCount set to 1 that also carry an SPN, and Kerberos pre-authentication disabled on accounts (a related technique called AS-REP Roasting, tracked separately as T1558.004).
Run either tool quarterly at minimum, and immediately after any large service account provisioning push (a new ERP rollout, a new backup vendor, a new monitoring agent), since those are exactly the moments when a poorly configured SPN account with a weak password gets created and forgotten. Microsoft Defender for Identity, PingCastle, and Semperis Purple Knight all touch Kerberoasting detection, but they solve different halves of the problem, and most mature identity security programs end up running at least two of the three together rather than picking just one.
The practical pattern that works well: run Defender for Identity continuously as the real-time tripwire, and run PingCastle or Purple Knight quarterly (or after any major AD change) as the audit that catches exposure before it ever becomes an attack Defender for Identity has to alert on. Neither replaces the manual audit script from Step 1, since both tools score risk generically across many categories rather than giving you the specific, exportable, privilege-sorted list of every SPN account you need to actually work through the remediation backlog.
This is the single highest-leverage hardening step in this entire tutorial. The Hacker News reported in March 2026 that Windows Server 2025 had shipped a built-in Kerberoasting mitigation addressing this exact gap, and Microsoft’s current guidance for Windows Server 2025 domain controllers is now explicit: DES and RC4 encryption suites should not be used for Kerberos. Set this through Group Policy under Computer Configuration, Windows Settings, Security Settings, Local Policies, Security Options, “Network security: Configure encryption types allowed for Kerberos,” and enable only AES128_HMAC_SHA1 and AES256_HMAC_SHA1.
Before you flip this switch domain-wide, audit which accounts actually have AES keys generated. An account that has never had its password reset since before AES support was enabled may only have RC4 key material, and forcing AES-only encryption without first generating AES keys will break authentication for that account, not just make it more secure. This isn’t a hypothetical risk: Microsoft had to ship a fix in April 2025 after a round of security updates caused authentication problems on Windows Server 2025 domain controllers, a reminder that Kerberos encryption changes on DCs deserve a maintenance window and a rollback plan, not a same-day production rollout.
Microsoft’s own phased rollout illustrates why this matters as a 2026-specific action item: RC4 was quietly treated as an “assumed” fallback encryption type for years, meaning any account without explicit configuration silently got RC4 support. Starting in April 2026, that default changed to AES-SHA1, and after July 2026, the registry key that allowed reverting to the old assumed behavior ( RC4DefaultDisablementPhase ) stopped working entirely, so environments that never explicitly configured their service accounts are now the ones most exposed if they haven’t done the work in this step.
Encryption hardening protects tickets in transit and at rest, but it does nothing if the underlying password is short, static, and human-chosen. A Group Managed Service Account (gMSA) solves that by having Active Directory itself generate and automatically rotate a 240-byte random password, with no human ever knowing or typing it. That single property makes offline cracking of a Kerberoasted ticket practically infeasible, since brute-forcing a random 240-byte secret isn’t something Hashcat is going to finish in any usable timeframe.
Not every legacy application supports gMSAs, especially older third-party software with hardcoded service-account logon assumptions. For those, fall back to a very long, randomly generated password (32+ characters, stored in a secrets manager like HashiCorp Vault rather than a spreadsheet) rotated on a fixed schedule, combined with strict AES-only encryption from Step 7. It’s not as strong as a gMSA, but it closes most of the practical attack window.
Even a perfectly hardened, AES-only, gMSA-backed service account is still worth attacking if it happens to sit in Domain Admins. Go back to the CSV from Step 1, filter for accounts where IsPrivileged = True , and challenge every single one: does a SQL service account actually need Domain Admin, or does it need db_owner on three specific databases? In the overwhelming majority of legacy environments, the answer is that someone added the account to a high-privilege group years ago to unblock a deployment and nobody ever walked it back.
Use delegated, scoped permissions through Active Directory Users and Computers’ Delegation of Control wizard, or better, through fine-grained group membership tied to exactly the resource the service needs. Document why each privileged service account has the access it has; if nobody can produce a reason within five minutes, that’s a strong signal the access should be removed, not preserved out of caution. This same over-privileging pattern is why a well-run vulnerability management program tracks identity risk alongside unpatched software, not as a separate workstream.
A detection rule you haven’t tested is a detection rule you’re hoping works. In an isolated lab domain (never production), use Rubeus to simulate a Kerberoasting request and confirm your SIEM query from Step 4 and your Defender for Identity alert from Step 5 both fire as expected. Harvested Online Documentation & Reference Sources • https://www.decryptiondigest.com/blog/how-to-detect-kerberoasting-attacks-active-directory • https://www.cayosoft.com/blog/kerberoasting-attack/ • https://alchemestrum.github.io/soc/investigations/kerberoasting-attack-defense/ • https://www.prophetsecurity.ai/blog/kerberoasting-detection-in-active-directory • https://hivesecurity.gitlab.io/blog/kerberoasting-deep-dive/ • https://tech-insider.org/how-to-detect-stop-kerberoasting-active-directory-2026/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Kerberoasting Attack Detection System In Active Directory.
[*] Metasploit Scan Running on Target Subnet for Kerberoasting Attack Detection System In Active Directory... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |