Complete Technical Paper Content — Keylogger Detection And Prevention Software For Windows
Overview & System Context
Keylogger Detection And Prevention Software For Windows: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9572 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Keystroke logging, often referred to as keylogging or keyboard capturing, is the action of recording (logging) the keys pressed on a keyboard, typically covertly, so that a person using the keyboard is unaware that their actions are being monitored. Data can then be retrieved by the person operating the logging program. A keystroke recorder or keylogger can be either software or hardware. While the programs themselves are legal, with many designed to allow employers to oversee the use of their computers, keyloggers are most often used for stealing passwords and other confidential information. Keystroke logging can also be utilized to monitor activities of children in schools or at home and by law enforcement officials to investigate malicious usage. Keylogging can also be used to study keystroke dynamics or human-computer interaction. Numerous keylogging methods exist, ranging from hardware and software-based approaches to acoustic cryptanalysis.
A software-based keylogger is a computer program designed to record any input from the keyboard. Keyloggers are used in IT organizations to troubleshoot technical problems with computers and business networks. Families and businesspeople use keyloggers legally to monitor network usage without their users' direct knowledge. Microsoft publicly stated that Windows 10 has a built-in keylogger in its final version "to improve typing and writing services". However, malicious individuals can use keyloggers on public computers to steal passwords or credit card information. Most keyloggers are not stopped by HTTPS encryption because that only protects data in transit between computers; software-based keyloggers run on the affected user's computer, reading keyboard inputs directly as the user types. From a technical perspective, there are several categories: Hypervisor-based: The keylogger can theoretically reside in a malware hypervisor running underneath the operating system, which thus remains untouched. It effectively becomes a virtual machine. Blue Pill is a conceptual example. Kernel-based: A program on the machine obtains root access to hide in the OS and intercepts keystrokes that pass through the kernel. This method is difficult both to write and to combat. Such keyloggers reside at the kernel level, which makes them difficult to detect, especially for user-mode applications that do not have root access. They are frequently implemented as rootkits that subvert the operating system kernel to gain unauthorized access to the hardware. This makes them very powerful. A keylogger using this method can act as a keyboard device driver, for example, and thus gain access to any information typed on the keyboard as it goes to the operating system. API-based: These keyloggers hook keyboard APIs inside a running application. The keylogger registers keystroke events as if it was a normal piece of the application instead of malware. The keylogger receives an event each time the user presses or releases a key. The keylogger simply records it. This is usually done by inject a DLL to other processes. Windows APIs such as GetAsyncKeyState(), GetForegroundWindow(), etc. are used to poll the state of the keyboard or to subscribe to keyboard events. A more recent example simply polls the BIOS for pre-boot authentication PINs that have not been cleared from memory. Form grabbing based: Form grabbing-based keyloggers log Web form submissions by recording the form data on submit events. This happens when the user completes a form and submits it, usually by clicking a button or pressing enter. This type of keylogger records form data before it is passed over the Internet. IME-based: A malicious IME can do keylogging. JavaScript-based: A malicious script tag is injected into a targeted web page, and listens for key events such as onKeyUp(). Scripts can be injected via a variety of methods, including cross-site scripting, man-in-the-browser, man-in-the-middle, or a compromise of the remote website. Memory-injection-based: Memory Injection (MitB)-based keyloggers perform their logging function by altering the memory tables associated with the browser and other system functions. By patching the memory tables or injecting directly into memory, this technique can be used by malware authors to bypass Windows UAC (User Account Control). The Zeus and SpyEye trojans use this method exclusively.
Non-Windows systems have protection mechanisms that allow access to locally recorded data from a remote location. Remote communication may be achieved when one of these methods is used: Data is uploaded to a website, database or an FTP server. Data is periodically emailed to a pre-defined email address. Data is Wirelessly transmitted employing an attached hardware system. The software enables a remote login to the local machine from the Internet or the local network, for data logs stored on the target machine.
descriptions of writing strategies; the writing development of children (with and without writing difficulties), spelling, first and second language writing, and specialist skill areas such as translation and subtitling. Keystroke logging can be used to research writing, specifically. It can also be integrated into educational domains for second language learning, programming skills, and typing skills.
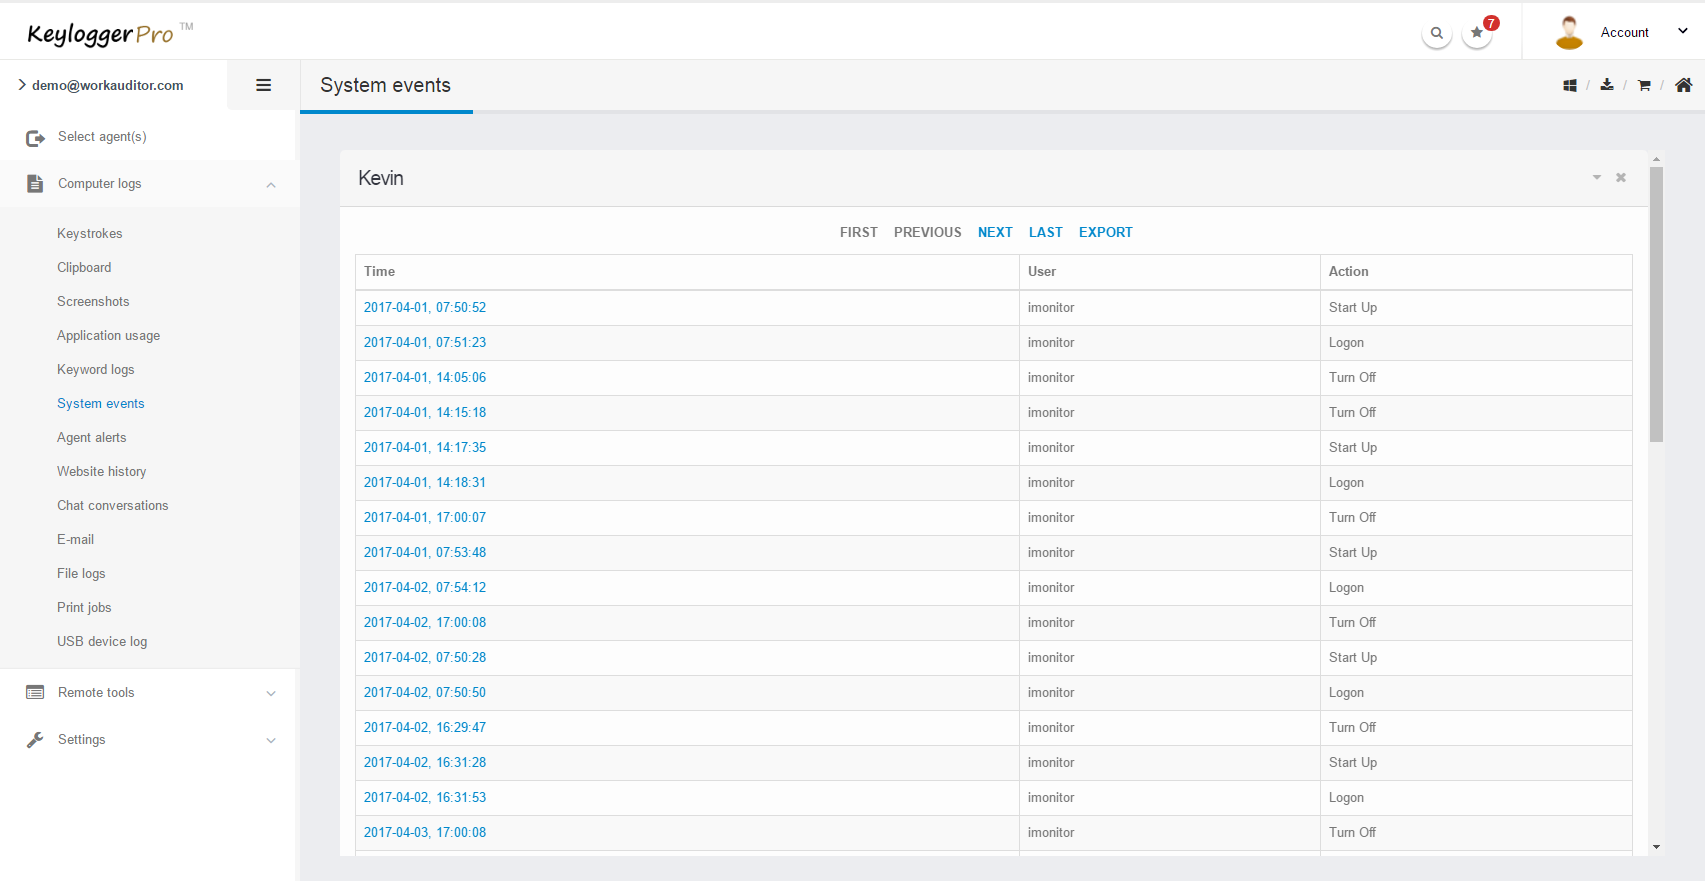
Figure 1: Como Detectar o Keylogger: os 5 Principais Softwares Anti-Keystroke ... This study also reported that machine learning models trained on genuine typing behavior achieved low false acceptance and false rejection rates in most instances, showing that the use of continuous authentication systems can operate with low error rates. They also found that the typing patterns of most people have enough discriminatory signals that you could create a personal profile based on the typing habits alone. This shows that the same core exploits used by malicious attackers can also form the basis of security systems designed to protect users from intrusions and impersonations. The authors concluded that while keystroke-dynamics authentication is promising, its deployment must carefully balance security, usability, and privacy considerations for the optimal user experience.
Clipboard logging. Anything that has been copied to the clipboard can be captured by the program. Screen logging. Screenshots are taken to capture graphics-based information. Applications with screen logging abilities may take screenshots of the whole screen, of just one application, or even just around the mouse cursor. They may take these screenshots periodically or in response to user behaviors (for example, when a user clicks the mouse). Screen logging can be used to capture data inputted with an on-screen keyboard. Programmatically capturing the text in a control. The Microsoft Windows API allows programs to request the text 'value' in some controls. This means that some passwords may be captured, even if they are hidden behind password masks (usually asterisks). The recording of every program/folder/window opened including a screenshot of every website visited. The recording of search engines queries, instant messenger conversations, FTP downloads and other Internet-based activities (including the bandwidth used).
Hardware-based keyloggers do not depend upon any software being installed as they exist at a hardware level in a computer system. Firmware-based: BIOS-level firmware that handles keyboard events can be modified to record these events as they are processed. Physical and/or root-level access is required to the machine, and the software loaded into the BIOS needs to be created for the specific hardware that it will be running on. Keyboard hardware: Hardware keyloggers are used for keystroke logging utilizing a hardware circuit that is attached somewhere in between the computer keyboard and the computer, typically inline with the keyboard's cable connector. There are also USB connector-based hardware keyloggers, as well as ones for laptop computers (the Mini-PCI card plugs into the expansion slot of a laptop). More stealthy implementations can be installed or built into standard keyboards so that no device is visible on the external cable. Both types log all keyboard activity to their internal memory, which can be subsequently accessed, for example, by typing in a secret key sequence. Hardware keyloggers do not require any software to be installed on a target user's computer, therefore not interfering with the computer's operation and less likely to be detected by software running on it. However, its physical presence may be detected if, for example, it is installed outside the case as an inline device between the computer and the keyboard. Some of these implementations can be controlled and monitored remotely using a wireless communication standard. Wireless keyboard and mouse sniffers: These passive sniffers collect packets of data being transferred from a wireless keyboard and its receiver. As encryption may be used to secure the wireless communications between the two devices, this may need to be cracked beforehand if the transmissions are to be read. In some cases, this enables an attacker to type arbitrary commands into a victim's computer. Keyboard overlays: Criminals have been known to use keyboard overlays on ATMs to capture people's PINs. Each keypress is registered by the keyboard of the ATM as well as the criminal's keypad that is placed over it. The device is designed to look like an integrated part of the machine so that bank customers are unaware of its presence. Acoustic keyloggers: Acoustic cryptanalysis can be used to monitor the sound created by someone typing on a computer. Each key on the keyboard makes a subtly different acoustic signature when struck. It is then possible to identify which keystroke signature relates to which keyboard character via statistical methods such as frequency analysis. The repetition frequency of similar acoustic keystroke signatures, the timings between different keyboard strokes and other context information such as the probable language in which the user is writing are used in this analysis to map sounds to letters. A fairly long recording (1000 or more keystrokes) is required so that a large enough sample is collected. Electromagnetic emissions: It is possible to capture the electromagnetic emissions of a wired keyboard from up to 20 metres (66 ft) away, without being physically wired to it. In 2009, Swiss researchers tested 11 different USB, PS/2 and laptop keyboards in a semi-anechoic chamber and found them all vulnerable, primarily because of the prohibitive cost of adding shielding during manufacture. The researchers used a wide-band receiver to tune into the specific frequency of the emissions radiated from the keyboards. Optical surveillance: Optical surveillance, while not a keylogger in the classical sense, is nonetheless an approach that can be used to capture passwords or PINs. A strategically placed camera, such as a hidden surveillance camera at an ATM, can allow a criminal to watch a PIN or password being entered. Physical evidence: For a keypad that is used only to enter a security code, the keys which are in actual use will have evidence of use from many fingerprints. A passcode of four digits, if the four digits in question are known, is reduced from 10,000 possibilities to just 24 possibilities (104 versus 4! [factorial of 4]). These could then be used on separate occasions for a manual "brute force attack". Smartphone sensors: Researchers have demonstrated that it is possible to capture the keystrokes of nearby computer keyboards using only the commodity accelerometer found in smartphones. The attack is made possible by placing a smartphone near a keyboard on the same desk. The smartphone's accelerometer can then detect the vibrations created by typing on the keyboard and then translate this raw accelerometer signal into readable sentences with as much as 80 percent accuracy. The technique involves working through probability by detecting pairs of keystrokes, rather than individual keys. It models "keyboard events" in pairs and then works out whether the pair of keys pressed is on the left or the right side of the keyboard and whether they are close together or far apart on the QWERTY keyboard. Once it has worked this out, it compares the results to a preloaded dictionary where each word has been broken down in the same way. Similar techniques have also been shown to be effective at capturing keystrokes on touchscreen keyboards while in some cases, in combination with gyroscope or with the ambient-light sensor. Body keyloggers: Body keyloggers track and analyze body movements to determine which keys were pressed. The attacker needs to be familiar with the keys layout of the tracked keyboard to correlate between body movements and keys position, although with a suitably large sample this can be deduced. Tracking audible signals of the user' interface (e.g. a sound the device produce to informs the user that a keystroke was logged) may reduce the complexity of the body keylogging algorithms, as it marks the moment at which a key was pressed.
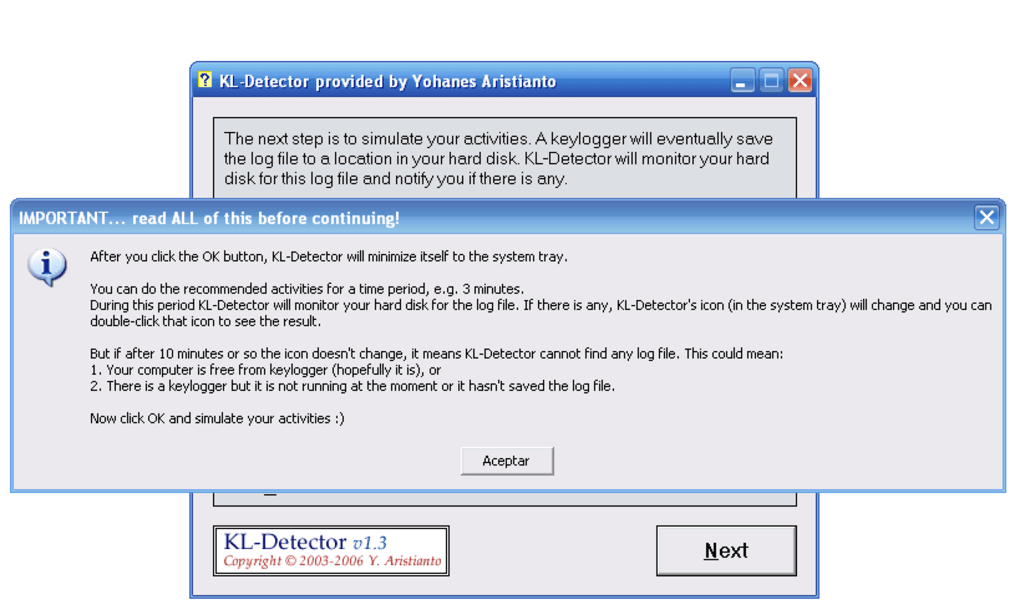
Figure 2: Best Keylogger Detector for Windows (2026) & Anti Keylogger Tools An anti-keylogger is a piece of software specifically designed to detect keyloggers on a computer, typically comparing all files in the computer against a database of keyloggers, looking for similarities which might indicate the presence of a hidden keylogger. As anti-keyloggers have been designed specifically to detect keyloggers, they have the potential to be more effective than conventional antivirus software; some antivirus software do not consider keyloggers to be malware, as under some circumstances a keylogger can be considered a legitimate piece of software.
Automatic form-filling programs may prevent keylogging by removing the requirement for a user to type personal details and passwords using the keyboard. Form fillers are primarily designed for Web browsers to fill in checkout pages and log users into their accounts. Once the user's account and credit card information has been entered into the program, it will be automatically entered into forms without ever using the keyboard or clipboard, thereby reducing the possibility that private data is being recorded. However, someone with physical access to the machine may still be able to install software that can intercept this information elsewhere in the operating system or while in transit on the network. (Transport Layer Security (TLS) reduces the risk that data in transit may be intercepted by network sniffers and proxy tools.) Malware (a portmanteau of malicious software) is any software intentionally designed to cause disruption or destruction to a computer, server, client, or computer network, leak private information, gain unauthorized access to information or systems, deprive access to information, or interfere with the user's computer security and privacy without their knowledge. Researchers tend to classify malware into one or more sub-types (i.e. computer viruses, worms, Trojan horses, logic bombs, ransomware, spyware, adware, rogue software, wipers and keyloggers). Malware poses serious threats to individuals and businesses on the Internet. According to Symantec's 2018 Internet Security Threat Report (ISTR), the number of malware variants increased to 669,947,865 in 2017, which is twice as many malware variants as in 2016. Cybercrime, which includes malware attacks as well as other crimes committed by computer, was predicted to cost the global economy US$6 trillion in 2021, and is increasing at a rate of 15% per year. Since 2021, malware has been designed to target computer systems that run critical infrastructure such as the electricity distribution network. The defense strategies against malware differ according to its type, but most can be prevented by installing antivirus software or firewalls, applying regular patches, securing networks, creating backups, and isolating infected systems. Malware can be designed to evade antivirus software detection algorithms.
The notion of a self-reproducing computer program can be traced back to initial theories about the operation of complex automata. John von Neumann showed that in theory a program could reproduce itself. This constituted a plausibility result in computability theory. Fred Cohen experimented with computer viruses and confirmed Neumann's postulate and investigated other properties of malware such as detectability and self-obfuscation using rudimentary encryption. His 1987 doctoral dissertation was on the subject of computer viruses. The combination of cryptographic technology as part of the payload of the virus, exploiting it for attack purposes was initialized and investigated from the mid-1990s, and includes initial ransomware and evasion ideas. Before Internet access became widespread, viruses spread on personal computers by infecting executable programs or boot sectors of floppy disks. By inserting a copy of itself into the machine code instructions in these programs or boot sectors, a virus causes itself to be run whenever the program is run or the disk is booted. Early computer viruses were written for the Apple II and Mac, but they became more widespread with the dominance of the IBM PC and MS-DOS. The first IBM PC virus in the wild was a boot sector virus dubbed (c)Brain, created in 1986 by the Farooq Alvi brothers in Pakistan. Malware distributors would trick the user into booting or running from an infected device or medium. For example, a virus could make an infected computer add autorunnable code to any USB stick plugged into it. Anyone who then attached the stick to another computer set to autorun from USB would in turn become infected, and also pass on the infection in the same way. Older email software would automatically open HTML email containing potentially malicious JavaScript code. Users may also execute disguised malicious email attachments. The 2018 Data Breach Investigations Report by Verizon, cited by CSO Online, states that emails are the primary method of malware delivery, accounting for 96% of malware delivery around the world. The first worms, network-borne infectious programs, originated not on personal computers, but on multitasking Unix systems. The first well-known worm was the Morris worm of 1988, which infected SunOS and VAX BSD systems. Unlike a virus, this worm did not insert itself into other programs. Instead, it exploited security holes (vulnerabilities) in network server programs and started itself running as a separate process. This same behavior is used by today's worms as well. With the rise of the Microsoft Windows platform in the 1990s, and the flexible macros of its applications, it became possible to write infectious code in the macro language of Microsoft Word and similar programs. These macro viruses infect documents and templates rather than applications (executables), but rely on the fact that macros in a Word document are a form of executable code. Many early infectious programs, including the Morris Worm, the first internet worm, were written as experiments or pranks. Today, malware is used by both black hat hackers and governments to steal personal, financial, or business information. Today, any device that plugs into a USB port – even lights, fans, speakers, toys, or peripherals such as a digital microscope – can be used to spread malware. Devices can be infected during manufacturing or supply if quality control is inadequate.
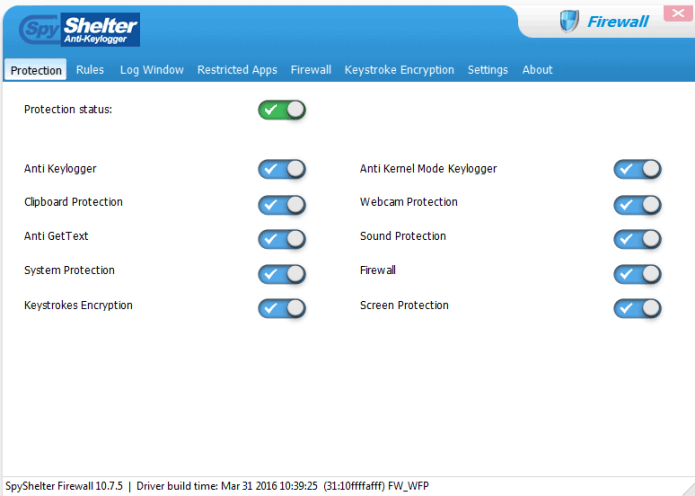
Figure 3: The 5 Best Keylogger Detectors For Windows 10 A computer virus is software usually hidden within another seemingly harmless program that can produce copies of itself and insert them into other programs or files, and that usually performs a harmful action (such as destroying data). They have been likened to biological viruses. An example of this is a portable execution infection, a technique, usually used to spread malware, that inserts extra data or executable code into PE files. A computer virus is software that embeds itself in some other executable software (including the operating system itself) on the target system without the user's knowledge and consent and when it is run, the virus is spread to other executable files.
A worm is a stand-alone malware software that actively transmits itself over a network to infect other computers and can copy itself without infecting files. These definitions lead to the observation that a virus requires the user to run an infected software or operating system for the virus to spread, whereas a worm spreads itself. Once malicious software is installed on a system, it is essential that it stays concealed, to avoid detection. Software packages known as rootkits allow this concealment, by modifying the host's operating system so that the malware is hidden from the user. Rootkits can prevent a harmful process from being visible in the system's list of processes, or keep its files from being read. Some types of harmful software contain routines to evade identification or removal attempts, not merely to hide themselves. An early example of this behavior is recorded in the Jargon File tale of a pair of programs infesting a Xerox CP-V time sharing system: Each ghost-job would detect the fact that the other had been killed, and would start a new copy of the recently stopped program within a few milliseconds. The only way to kill both ghosts was to kill them simultaneously (very difficult) or to deliberately crash the system.
A backdoor is a broad term for a computer program that allows an attacker persistent unauthorised remote access to a victim's machine often without their knowledge. The attacker typically uses another attack (such as a trojan, worm or virus) to bypass authentication mechanisms usually over an unsecured network such as the Internet to install the backdoor application. A backdoor can also be a side effect of a software bug in legitimate software that is exploited by an attacker to gain access to a victim's computer or network. The idea has often been suggested that computer manufacturers preinstall backdoors on their systems to provide technical support for customers, but this has never been reliably verified. It was reported in 2014 that US government agencies had been diverting computers purchased by those considered "targets" to secret workshops where software or hardware permitting remote access by the agency was installed, considered to be among the most productive operations to obtain access to networks around the world. Backdoors may be installed by Trojan horses, worms, implants, or other methods.
A Trojan horse misrepresents itself to masquerade as a regular, benign program or utility in order to persuade a victim to install it. A Trojan horse usually carries a hidden destructive function that is activated when the application is started. The term is derived from the Ancient Greek story of the Trojan horse used to invade the city of Troy by stealth. Trojan horses are generally spread by some form of social engineering, for example, where a user is duped into executing an email attachment disguised to be unsuspicious, (e.g., a routine form to be filled in), or by drive-by download. Although their payload can be anything, many modern forms act as a backdoor, contacting a controller (phoning home) which can then have unauthorized access to the affected computer, potentially installing additional software such as a keylogger to steal confidential information, cryptomining software or adware to generate revenue to the operator of the trojan. While Trojan horses and backdoors are not easily detectable by themselves, computers may appear to run slower, emit more heat or fan noise due to heavy processor or network usage, as may occur when cryptomining software is installed. Cryptominers may limit resource usage or only run during idle times in an attempt to evade detection. Unlike computer viruses and worms, Trojan horses generally do not attempt to inject themselves into other files or otherwise propagate themselves. Modern Trojans are often disguised within legitimate-looking applications, making them particularly effective at bypassing basic user awareness and simple antivirus measures. In spring 2017, Mac users were hit by the new version of Proton Remote Access Trojan (RAT) trained to extract password data from various sources, such as browser auto-fill data, the Mac-OS keychain, and password vaults.
Droppers are a sub-type of Trojans that solely aim to deliver malware upon the system that they infect with the desire to subvert detection through stealth and a light payload. It is important not to confuse a dropper with a loader or stager. A loader or stager will merely load an extension of the malware (for example a collection of malicious functions through reflective dynamic link library injection) into memory. The purpose is to keep the initial stage light and undetectable. A dropper merely downloads further malware to the system.
Ransomware prevents a user from accessing their files until a ransom is paid. There are two variations of ransomware, being crypto ransomware and locker ransomware. Locker ransomware just locks down a computer system without encrypting its contents, whereas crypto ransomware locks down a system and encrypts its contents. For example, programs such as CryptoLocker encrypt files securely, and only decrypt them on payment of a substantial sum of money. Lock-screens, or screen lockers is a type of "cyber police" ransomware that blocks screens on Windows or Android devices with a false accusation in harvesting illegal content, trying to scare the victims into paying up a fee. Jisut and SLocker impact Android devices more than other lock-screens, with Jisut making up nearly 60 percent of all Android ransomware detections.
Encryption-based ransomware, like the name suggests, is a type of ransomware that encrypts all files on an infected machine. These types of malware then display a pop-up ad informing the user that their files have been encrypted and that they must pay (usually in Bitcoin) to recover them. Some examples of encryption-based ransomware are CryptoLocker and WannaCry. According to Microsoft's Digital Crimes Unit in May 2025, Lumma Stealer ("Lumma"), which steals passwords, credit cards, bank accounts, and cryptocurrency wallets, is the favored info-stealing malware used by hundreds of cyber threat actors and enables criminals to empty bank accounts, hold schools for ransom, and disrupt critical services.
2. System Architecture & Core Working Principles Grayware is any unwanted application or file that can worsen the performance of computers and may cause security risks but which there is insufficient consensus or data to classify them as malware. Types of grayware typically include spyware, adware, fraudulent dialers, joke programs ("jokeware") and remote access tools. For example, at one point, Sony BMG compact discs silently installed a rootkit on purchasers' computers with the intention of preventing illicit copying.
Real-time protection: They can provide real time protection against the installation of malware software on a computer. This type of malware protection works the same way as that of antivirus protection in that the anti-malware software scans all incoming network data for malware and blocks any threats it comes across. Removal: Anti-malware software programs can be used solely for detection and removal of malware software that has already been installed onto a computer. This type of anti-malware software scans the contents of the Windows registry, operating system files, and installed programs on a computer and will provide a list of any threats found, allowing the user to choose which files to delete or keep, or to compare this list to a list of known malware components, removing files that match. Sandboxing: Sandboxing confines applications within a controlled environment, restricting their operations and isolating them from other applications on the host while limiting access to system resources. Browser sandboxing isolates web processes to prevent malware and exploits, enhancing security.
Further Reading: Research Papers and Documents about Malware on IDMARCH (Int. Digital Media Archive) Archived 22 September 2016 at the Wayback Machine Advanced Malware Cleaning – a Microsoft video A rootkit is a collection of typically malicious computer software designed to enable access to a computer or to part of its software that would not otherwise be allowed (for example, by an unauthorized user). Rootkits often mask their presence or that of other software. The term rootkit is a compound of "root" (the traditional name of the privileged account on Unix-like operating systems) and the word "kit" (which refers to the software components that implement the tool). The term "rootkit" has negative connotations through its association with malware. Rootkit installation can be automated, or an attacker can install a rootkit after having obtained root or administrator access. Obtaining this access is a result of a direct attack on a system, i.e., exploiting a vulnerability (such as privilege escalation) or a password (obtained by cracking or social engineering tactics like "phishing"). Once installed, it becomes possible to hide the intrusion as well as to maintain privileged access. Full control over a system means that existing software can be modified, including software that might otherwise be used to detect or circumvent it. Rootkit detection is difficult because a rootkit may be able to subvert the software that is intended to find it.
Detection methods include using an alternative and trusted operating system, behavior-based methods, signature scanning, difference scanning, and memory dump analysis. Removal can be complicated, especially in cases where the rootkit resides in the kernel; reinstallation of the operating system may be the only available solution to the problem. When dealing with firmware rootkits, removal may require hardware replacement, or specialized equipment.
Stuxnet, uncovered in 2010, was a highly sophisticated worm widely believed to have been developed in a joint U.S.–Israeli intelligence operation targeting Iran’s nuclear facilities. It notably included a Windows kernel-mode rootkit that concealed the malware’s files and processes, enabling the worm to silently sabotage industrial control systems. Stuxnet is often cited as the first known cyberweapon; it destroyed a significant part of Iran’s uranium centrifuges, while remaining difficult to detect.
In 2005, Sony BMG published CDs with copy protection and digital rights management software called Extended Copy Protection, created by software company First 4 Internet. The software included a music player but silently installed a rootkit which limited the user's ability to access the CD. Software engineer Mark Russinovich, who created the rootkit detection tool RootkitRevealer, discovered the rootkit on one of his computers. The ensuing scandal raised the public's awareness of rootkits. To cloak itself, the rootkit hid any file starting with "$sys$" from the user. Soon after Russinovich's report, malware appeared which took advantage of the existing rootkit on affected systems. One BBC analyst called it a "public relations nightmare." Sony BMG released patches to uninstall the rootkit, which exposed users to an even more serious vulnerability.
The company eventually recalled the CDs. In the United States, a class-action lawsuit was brought against Sony BMG. The 2004–2005 Greek wiretapping case, also referred to as Greek Watergate, involved the illegal telephone tapping of more than 100 mobile phones on the Vodafone Greece network belonging mostly to members of the Greek government and top-ranking civil servants. The taps began sometime near the beginning of August 2004 and were removed in March 2005 without discovering the identity of the perpetrators. The intruders installed a rootkit targeting Ericsson's AXE telephone exchange. According to IEEE Spectrum, this was "the first time a rootkit has been observed on a special-purpose system, in this case an Ericsson telephone switch." The rootkit was designed to patch the memory of the exchange while it was running, enable wiretapping while disabling audit logs, patch the commands that list active processes and active data blocks, and modify the data block checksum verification command. A "backdoor" allowed an operator with sysadmin status to deactivate the exchange's transaction log, alarms and access commands related to the surveillance capability. The rootkit was discovered after the intruders installed a faulty update, which caused SMS texts to be undelivered, leading to an automated failure report being generated. Ericsson engineers were called in to investigate the fault and discovered the hidden data blocks containing the list of phone numbers being monitored, along with the rootkit and illicit monitoring software.
Provide an attacker with full access via a backdoor, permitting unauthorized access to, for example, steal or falsify documents. One of the ways to carry this out is to subvert the login mechanism, such as the /bin/login program on Unix-like systems or GINA on Windows. The replacement appears to function normally, but also accepts a secret login combination that allows an attacker direct access to the system with administrative privileges, bypassing standard authentication and authorization mechanisms. Conceal other malware, notably password-stealing key loggers and computer viruses. Appropriate the compromised machine as a zombie computer for attacks on other computers. (The attack originates from the compromised system or network, instead of the attacker's system.) "Zombie" computers are typically members of large botnets that can–amongst other things–launch denial-of-service attacks, distribute email spam, and conduct click fraud. In some instances, rootkits provide desired functionality, and may be installed intentionally on behalf of the computer user: Detect attacks, for example, in a honeypot. Enhance emulation software and security software. Alcohol 120% and Daemon Tools are commercial examples of non-hostile rootkits used to defeat copy-protection mechanisms such as SafeDisc and SecuROM. Kaspersky antivirus software also uses techniques resembling rootkits to protect itself from malicious actions. It loads its own drivers to intercept system activity, and then prevents other processes from doing harm to itself. Its processes are not hidden, but cannot be terminated by standard methods. Anti-theft protection: Laptops may have BIOS-based rootkit software that will periodically report to a central authority, allowing the laptop to be monitored, disabled or wiped of information in the event that it is stolen. Bypassing Microsoft Product Activation There are at least five types of rootkit, ranging from those at the lowest level in firmware (with the highest privileges), through to the least privileged user-based variants that operate in Ring 3. Hybrid combinations of these may occur spanning, for example, user mode and kernel mode.
User-mode rootkits run in Ring 3, along with other applications as user, rather than low-level system processes. They have a number of possible installation vectors to intercept and modify the standard behavior of application programming interfaces (APIs). Some inject a dynamically linked library (such as a .DLL file on Windows, or a .dylib file on Mac OS X) into other processes, and are thereby able to execute inside any target process to spoof it; others with sufficient privileges simply overwrite the memory of a target application. Injection mechanisms include: Use of vendor-supplied application extensions. For example, Windows Explorer has public interfaces that allow third parties to extend its functionality. Interception of messages. Debuggers. Exploitation of security vulnerabilities. Function hooking or patching of commonly used APIs, for example, to hide a running process or file that resides on a filesystem. ...since user mode applications all run in their own memory space, the rootkit needs to perform this patching in the memory space of every running application. In addition, the rootkit needs to monitor the system for any new applications that execute and patch those programs' memory space before they fully execute.
Code signing uses public-key infrastructure to check if a file has been modified since being digitally signed by its publisher. Alternatively, a system owner or administrator can use a cryptographic hash function to compute a "fingerprint" at installation time that can help to detect subsequent unauthorized changes to on-disk code libraries. However, unsophisticated schemes check only whether the code has been modified since installation time; subversion prior to that time is not detectable. The fingerprint must be re-established each time changes are made to the system: for example, after installing security updates or a service pack. The hash function creates a message digest, a relatively short code calculated from each bit in the file using an algorithm that creates large changes in the message digest with even smaller changes to the original file. By recalculating and comparing the message digest of the installed files at regular intervals against a trusted list of message digests, changes in the system can be detected and monitored—as long as the original baseline was created before the malware was added.
More-sophisticated rootkits are able to subvert the verification process by presenting an unmodified copy of the file for inspection, or by making code modifications only in memory, reconfiguration registers, which are later compared to a white list of expected values. The code that performs hash, compare, or extend operations must also be protected—in this context, the notion of an immutable root-of-trust holds that the very first code to measure security properties of a system must itself be trusted to ensure that a rootkit or bootkit does not compromise the system at its most fundamental level.
Using software keyloggers to steal sensitive information, such as passwords, from computers has been a well-known technique for over 20 years, and reports indicate it continues to be employed in cyber attacks today. While keylogging itself does not directly damage a computer, early detection is critical to preventing subsequent, more invasive cyber attacks. In this presentation, I will begin by explaining four common types of user-mode keyloggers on Windows (Polling-based, Hooking-based, RawInputModel, and DirectInput) and then discuss detection methods for each. Specifically, I will explain how to detect keyloggers using Event Tracing for Windows (ETW), a logging feature built into Windows and utilized by modern Endpoint Detection and Response (EDR) platforms, including examples of actual detection rules.
In the latter part of the presentation, I will focus on a hotkey-based keylogging technique disclosed in 2024, examining its threats and discussing detection methods. I will specifically highlight the difficulties in detecting this keylogging technique through ETW and then propose a new method for detecting it without ETW using an undocumented hotkey table. Overall, this presentation will share information about both old and new keylogging techniques, along with useful tips and insights for successfully implementing detection methods.
Introduction
- This project involves both the development of a keylogger for the Windows operating system and the creation of detection mechanisms to identify and mitigate keylogger activities. The implementation phase will focus on creating a keylogger application capable of capturing keystrokes on a Windows system, utilizing various techniques such as hooking into the keyboard input events. The detection phase will involve researching and implementing methods to identify keylogger behavior, including signature-based detection, heuristic analysis, and monitoring system processes for suspicious activity.
Introduction Synonym
Domain of the Project :- Cybersecurity - Keylogging Expected Outcome :- The expected outcome of this project includes:
Conclusion
- This project offers a comprehensive exploration of both offensive and defensive aspects of cybersecurity related to keyloggers. Interns will gain hands-on experience in software development, system monitoring, and cybersecurity techniques, culminating in a detailed understanding of keylogger threats and protection strategies Keylogger Development and Detection System This project focuses on two main aspects: developing a Windows keylogger and designing detection mechanisms to identify and counter keylogging activities.
Conclusion Synonym
3. Software Implementation, Frameworks & Protocols In this article, we explore what hotkey-based keyloggers are and how to detect them. Specifically, we explain how these keyloggers intercept keystrokes, then present a detection technique that leverages an undocumented hotkey table in kernel space.
Conclusion Meaning
In May 2024, Elastic Security Labs published an article highlighting new features added in Elastic Defend (starting with 8.12) to enhance the detection of keyloggers running on Windows. In that post, we covered four types of keyloggers commonly employed in cyberattacks — polling-based keyloggers, hooking-based keyloggers, keyloggers using the Raw Input Model, and keyloggers using DirectInput — and explained our detection methodology. In particular, we introduced a behavior-based detection method using the Microsoft-Windows-Win32k provider within Event Tracing for Windows (ETW).
Conclusion Transition Words
Shortly after publication, we were honored to have our article noticed by Jonathan Bar Or , Principal Security Researcher at Microsoft. He provided invaluable feedback by pointing out the existence of hotkey-based keyloggers and even shared proof-of-concept (PoC) code with us. Leveraging his PoC code Hotkeyz as a starting point, this article presents one potential method for detecting hotkey-based keyloggers.
Conclusion Definition
Before delving into hotkey-based keyloggers, let’s first clarify what a hotkey is. A hotkey is a type of keyboard shortcut that directly invokes a specific function on a computer by pressing a single key or a combination of keys. For example, many Windows users press Alt + Tab to switch between tasks (or, in other words, windows). In this instance, Alt + Tab serves as a hotkey that directly triggers the task-switching function.
Conclusion Paragraph
(Note: Although other types of keyboard shortcuts exist, this article focuses solely on hotkeys. Also, all information herein is based on Windows 10 version 22H2 OS Build 19045.5371 without virtualization based security . Please note that the internal data structures and behavior may differ in other versions of Windows.) In addition to using the pre-configured hotkeys in Windows as shown in the previous example, you can also register your own custom hotkeys. There are various methods to do this, but one straightforward approach is to use the Windows API function RegisterHotKey , which allows a user to register a specific key as a hotkey. For instance, the following code snippet demonstrates how to use the RegisterHotKey API to register the A key (with a virtual-key code of 0x41) as a global hotkey: After registering a hotkey, when the registered key is pressed, a WM_HOTKEY message is sent to the message queue of the window specified as the first argument to the RegisterHotKey API (or to the thread that registered the hotkey if NULL is used).
Conclusion Starters
The code below demonstrates a message loop that uses the GetMessage API to check for a WM_HOTKEY message in the message queue , and if one is received, it extracts the virtual-key code (in this case, 0x41) from the message. In other words, imagine you're writing something in a notepad application. If the A key is pressed, the character won't be treated as normal text input — it will be recognized as a global hotkey instead.
Conclusion Sentence Starters
In this example, only the A key is registered as a hotkey. However, you can register multiple keys (like B, C, or D) as separate hotkeys at the same time. This means that any key (i.e., any virtual-key code) that can be registered with the RegisterHotKey API can potentially be hijacked as a global hotkey. A hotkey-based keylogger abuses this capability to capture the keystrokes entered by the user.
Conclusion Examples
Based on our testing, we found that not only alphanumeric and basic symbol keys, but also those keys when combined with the SHIFT modifier, can all be registered as hotkeys using the RegisterHotKey API. This means that a keylogger can effectively monitor every keystroke necessary to steal sensitive information. Let's walk through the actual process of how a hotkey-based keylogger captures keystrokes, using the Hotkeyz hotkey-based keylogger as an example.
Conclusion Words
In Hotkeyz, it first registers each alphanumeric virtual-key code — and some additional keys, such as VK_SPACE and VK_RETURN — as individual hotkeys by using the RegisterHotKey API. Then, inside the keylogger's message loop, the PeekMessageW API is used to check whether any WM_HOTKEY messages from these registered hotkeys have appeared in the message queue. When a WM_HOTKEY message is detected, the virtual-key code it contains is extracted and eventually saved to a text file. Below is an excerpt from the message loop code, highlighting the most important parts.
One important detail is this: to avoid alerting the user to the keylogger's presence, once the virtual-key code is extracted from the message, the key's hotkey registration is temporarily removed using the UnregisterHotKey API. After that, the key press is simulated with keybd_event so that it appears to the user as if the key was pressed normally. Once the key press is simulated, the key is re-registered using the RegisterHotKey API to wait for further input. This is the core mechanism behind how a hotkey-based keylogger operates.
Now that we understand what hotkey-based keyloggers are and how they operate, let's explain how to detect them. Following the approach described in an earlier article, we first investigated whether Event Tracing for Windows (ETW) could be used to detect hotkey-based keyloggers. Our research quickly revealed that ETW currently does not monitor the RegisterHotKey or UnregisterHotKey APIs. In addition to reviewing the manifest file for the Microsoft-Windows-Win32k provider, we reverse-engineered the internals of the RegisterHotKey API — specifically, the NtUserRegisterHotKey function in win32kfull.sys. Unfortunately, we found no evidence that these APIs trigger any ETW events when executed.
The image below shows a comparison between the decompiled code for NtUserGetAsyncKeyState (which is monitored by ETW) and NtUserRegisterHotKey . Notice that at the beginning of NtUserGetAsyncKeyState , there is a call to EtwTraceGetAsyncKeyState — a function associated with logging ETW events — while NtUserRegisterHotKey does not contain such a call.
Figure 1: Comparison of the Decompiled Code for **NtUserGetAsyncKeyState** and **NtUserRegisterHotKey** Although we also considered using ETW providers other than Microsoft-Windows-Win32k to indirectly monitor calls to the RegisterHotKey API, we found that the detection method using the "hotkey table" — which will be introduced next and does not rely on ETW — achieves results that are comparable to or even better than monitoring the RegisterHotKey API. In the end, we chose to implement this method.
After discovering that ETW cannot directly monitor calls to the RegisterHotKey API, we started exploring detection methods that don't rely on ETW. During our investigation, we wondered, "Isn't the information for registered hotkeys stored somewhere? And if so, could that data be used for detection?" Based on that hypothesis, we quickly found a hash table labeled gphkHashTable within NtUserRegisterHotKey . Searching Microsoft's online documentation revealed no details on gphkHashTable , suggesting that it's an undocumented kernel data structure.
Figure 2: The hotkey table (**gphkHashTable**), discovered within the **RegisterHotKey** function called inside **NtUserRegisterHotKey** 4. Practical Deployment, Analysis & Case Studies Through reverse engineering, we discovered that this hash table stores objects containing information about registered hotkeys. Each object holds details such as the virtual-key code and modifiers specified in the arguments to the RegisterHotKey API. The right side of Figure 3 shows part of the structure definition for a hotkey object (named HOT_KEY ), while the left side displays how the registered hotkey objects appear when accessed via WinDbg.
Figure 3: Hotkey Object Details. WinDbg view (left) and HOT_KEY structure details (right) We also determined that ghpkHashTable is structured as shown in Figure 4. Specifically, it uses the result of the modulo operation (with 0x80) on the virtual-key code (specified by the RegisterHotKey API) as the index into the hash table. Hotkey objects sharing the same index are linked together in a list, which allows the table to store and manage hotkey information even when the virtual-key codes are identical but the modifiers differ.
In other words, by scanning all HOT_KEY objects stored in ghpkHashTable , we can retrieve details about every registered hotkey. If we find that every main key — for example, each individual alphanumeric key — is registered as a separate hotkey, that strongly indicates the presence of an active hotkey-based keylogger. Now, let's move on to implementing the detection tool. Since gphkHashTable resides in the kernel space, it cannot be accessed by a user-mode application. For this reason, it was necessary to develop a device driver for detection. More specifically, we decided to develop a device driver that obtains the address of gphkHashTable and scans through all the hotkey objects stored in the hash table. If the number of alphanumeric keys registered as hotkeys exceeds a predefined threshold, it will alert us to the potential presence of a hotkey-based keylogger.
While developing the detection tool, one of the first challenges we faced was how to obtain the address of gphkHashTable . After some consideration, we decided to extract the address directly from an instruction in the win32kfull.sys driver that accesses gphkHashTable . Through reverse engineering, we discovered that within the IsHotKey function — right at the beginning — there is a lea instruction (lea rbx, gphkHashTable ) that accesses gphkHashTable . We used the opcode byte sequence (0x48, 0x8d, 0x1d) from that instruction as a signature to locate the corresponding line, and then computed the address of gphkHashTable using the obtained 32-bit (4-byte) offset.
Additionally, since IsHotKey is not an exported function, we also need to know its address before looking for gphkHashTable . Through further reverse engineering, we discovered that the exported function EditionIsHotKey calls the IsHotKey function. Therefore, we decided to compute the address of IsHotKey within the EditionIsHotKey function using the same method described earlier. (For reference, the base address of win32kfull.sys can be found using the PsLoadedModuleList API.) Once we finalized our approach to obtaining the address of gphkHashTable , we began writing code to access the memory space of win32kfull.sys to retrieve that address. One challenge we encountered at this stage was that win32kfull.sys is a session driver . Before proceeding further, here’s a brief, simplified explanation of what a session is.
In Windows, when a user logs in, a separate session (with session numbers starting from 1) is assigned to each user. Simply put, the first user to log in is assigned Session 1 . If another user logs in while that session is active, that user is assigned Session 2 , and so on. Each user then has their own desktop environment within their assigned session. Kernel data that must be managed separately for each session (i.e., per logged-in user) is stored in an isolated area of kernel memory called session space . This includes GUI objects managed by win32k drivers, such as windows and mouse/keyboard input data, ensuring that the screen and input remain properly separated between users.
(This is a simplified explanation. For a more detailed discussion on sessions, please refer to James Forshaw’s blog post .) Figure 6: Overview of Sessions. Session 0 is dedicated exclusively to service processes Based on the above, win32kfull.sys is known as a session driver . This means that, for example, hotkey information registered in the session of the first logged-in user (Session 1) can only be accessed from within that same session. So, how can we work around this limitation? In such cases, KeStackAttachProcess can be used.
KeStackAttachProcess allows the current thread to temporarily attach to the address space of a specified process. If we can attach to a GUI process in the target session — more precisely, a process that has loaded win32kfull.sys — then we can access win32kfull.sys and its associated data within that session. For our implementation, assuming that only one user is logged in, we decided to locate and attach to winlogon.exe , the process responsible for handling user logon operations.
Once we have successfully attached to the winlogon.exe process and determined the address of gphkHashTable , the next step is simply scanning gphkHashTable to check the registered hotkeys. Below is an excerpt of that code: The code itself is straightforward: it iterates through each index of the hash table, following the linked list to access every HOT_KEY object, and checks whether the registered hotkeys correspond to alphanumeric keys without any modifiers. In our detection tool, if every alphanumeric key is registered as a hotkey, an alert is raised, indicating the possible presence of a hotkey-based keylogger. For simplicity, this implementation only targets alphanumeric key hotkeys, although it would be easy to extend the tool to check for hotkeys with modifiers such as SHIFT .
The detection tool (Hotkey-based Keylogger Detector) has been released below. Detailed usage instructions are provided as well. Additionally, this research was presented at NULLCON Goa 2025 , and the presentation slides are available. The following is a demo video showcasing how the Hotkey-based Keylogger Detector detects Hotkeyz. We would like to express our heartfelt gratitude to Jonathan Bar Or for reading our previous article, sharing his insights on hotkey-based keyloggers, and generously publishing the PoC tool Hotkeyz .
5. Performance Evaluation & Extended Technical Observations Learn how to detect and prevent keyloggers from capturing your passwords and sensitive data. Complete guide covering software and hardware keyloggers, detection tools, and enterprise protection strategies. A keylogger is software or hardware that records every keystroke you make and sends it to an attacker, capturing passwords, messages, and card numbers as you type them. You detect a software keylogger by scanning with two or three anti- malware tools (Windows Defender, Malwarebytes, HitmanPro), reviewing running processes and startup entries, and watching for unexplained outbound network traffic; you detect a hardware keylogger only by physically inspecting the cable between keyboard and computer. You prevent both by using a password manager that auto-fills without typing, enabling multi-factor authentication, and — for credentials that must survive a full compromise — logging in with a FIDO2 /WebAuthn hardware key, which a keylogger cannot capture or replay.
That is the summary an AI Overview will give you. What it can't show you is where in the chain each defense actually intercepts — why keystroke encryption stops a browser keylogger but not a kernel one, why a captured TOTP code is already worthless, and why a hardware logger is invisible to every scanner you own. The diagram below traces a single keystroke from key press to attacker inbox and marks the exact point each control breaks the chain. Below it, a detectability-vs-defense table ranks the keylogger types by how much they should actually worry you, followed by the process, network, and physical checks that separate a real infection from a slow laptop.
Rule of thumb: detection catches the loggers you can see; encryption and FIDO2 defeat the ones you can't. In 2025, keyloggers remain one of the most effective attack tools. The Snake Keylogger campaign targeting banking and e-commerce users demonstrates their ongoing threat, while AI-enhanced variants are making detection increasingly difficult. Whether you're protecting personal accounts or enterprise systems, understanding how keyloggers work and how to defend against them is essential.
Not all keyloggers are equal. A commercial user-mode logger is trivially caught by any scanner; a firmware or hardware logger can defeat a full OS reinstall. This table ranks the types by how detectable they are and what actually stops each one. This guide covers software and hardware keyloggers, detection methods, prevention strategies, and what to do if you discover one on your system.
Keyloggers are surveillance tools that record keyboard input. While some have legitimate uses (parental monitoring, employee oversight with consent, law enforcement), they're commonly deployed by attackers for credential theft and espionage. Individual symptoms are weak evidence — every one has an innocent explanation. Use this table to decide whether a symptom is worth chasing and what to check next. Two or more rows lighting up at once is the real signal.
These indicators are subtle and often have other causes, but combined they warrant investigation — start with the process and network checks above before assuming the worst. A keylogger is surveillance software or hardware that records every keystroke made on a computer or mobile device. Software keyloggers run as hidden programs that intercept keyboard input, while hardware keyloggers are physical devices connected between the keyboard and computer. Both capture passwords, messages, searches, and all other typed content, sending it to whoever installed the keylogger.
Signs of keylogger infection include: slight input lag when typing, unexplained network activity, unfamiliar processes in Task Manager, unexpected system slowdowns, browser settings changing without your action, or accounts being accessed from unknown locations. However, sophisticated keyloggers leave few traces. Run anti-malware scans with multiple tools (Windows Defender, Malwarebytes, HitmanPro) and physically inspect your keyboard connection for hardware keyloggers.
Most antivirus software can detect known software keyloggers through signature matching, and modern solutions use behavioral analysis to catch unknown variants. However, sophisticated keyloggers using rootkit techniques, kernel-mode drivers, or fileless memory-only approaches may evade detection. Hardware keyloggers are completely invisible to software scanners. For best protection, use multiple security tools and conduct physical inspections.
Hardware keyloggers cannot be detected by any software—they operate at the physical layer between keyboard and computer. They can only be found through physical inspection. Look for unfamiliar USB adapters or dongles between your keyboard cable and computer. Some hardware keyloggers include WiFi capabilities for remote data retrieval and may be hidden inside USB ports or even keyboards themselves.
Virtual (on-screen) keyboards prevent standard software keyloggers that hook keyboard APIs, since no physical keystrokes occur. However, they don't protect against: screen capture keyloggers (screenshot every click), mouse movement loggers, form grabbers that intercept submitted data, or hardware keyloggers. Virtual keyboards are a helpful additional layer but not a complete solution.
Yes, most modern keyloggers include clipboard monitoring that captures everything you copy and paste. This is specifically designed to defeat users who copy passwords from password managers instead of typing them. Advanced password managers clear the clipboard shortly after paste operations, and some use techniques that bypass clipboard entirely to fill credentials.
Browser-based keyloggers are significant threats. They can be deployed through malicious browser extensions, cross-site scripting (XSS) attacks on legitimate websites, or compromised ad networks. These keyloggers only capture input within the browser but can steal credentials, credit card numbers, and personal information. Regularly audit your browser extensions and use reputable ad blockers.
Keystroke encryption protects your typing by encrypting keystrokes at the driver level before keyloggers can intercept them. Tools like KeyScrambler encrypt your input so that even if a keylogger captures it, the attacker receives meaningless encrypted data instead of readable text. The encryption is decrypted only at the application level where you're typing. Multi-factor authentication significantly reduces keylogger risk but doesn't eliminate it entirely. If a keylogger captures your password, the attacker still needs your second factor. TOTP codes (authenticator apps) rotate every 30 seconds, making captured codes useless. Hardware security keys (FIDO2/WebAuthn) provide the strongest protection—they use cryptographic challenges that keyloggers cannot replay.
Enterprise detection involves multiple layers: EDR solutions that detect API hooking and suspicious process behavior, network monitoring for unusual data exfiltration patterns, USB device control policies that block unauthorized hardware, application whitelisting that prevents unknown software from running, regular endpoint scans, and physical security inspections. Behavioral analytics can detect unusual account access patterns even if the keylogger itself goes undetected.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Keystroke%20logging • https://en.wikipedia.org/wiki/Malware • https://en.wikipedia.org/wiki/Rootkit • https://nullcon.net/talk/windows-keylogger-detection-targeting-past-and-present-keylogging-techniques/ • https://github.com/sruthiboda/Development-and-Detection-of-Keyloggers-for-Windows-OS • https://www.elastic.co/security-labs/threat-command/detecting-hotkey-based-keyloggers • https://inventivehq.com/blog/keylogger-detection-prevention-guide
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Keylogger Detection And Prevention Software For Windows.
[*] Metasploit Scan Running on Target Subnet for Keylogger Detection And Prevention Software For Windows... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |