Complete Technical Paper Content — Kubernetes Security Policy Enforcement Tool Project
Overview & System Context
Kubernetes Security Policy Enforcement Tool Project: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9532 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Kubernetes (), also known as K8s, is an open-source container orchestration system for automating software deployment, scaling, and management. Originally designed by Google, the project is now maintained by a worldwide community of contributors, and the trademark is held by the Cloud Native Computing Foundation. The name Kubernetes comes from the Ancient Greek term κυβερνIτης, kubernItIs (helmsman, pilot), which is also the origin of the words cybernetics and (through Latin) governor. "Kubernetes" is often abbreviated with the numerical contraction "K8s", meaning "the letter K, followed by 8 letters, followed by s". Kubernetes assembles one or more computers, either virtual machines or bare metal, into a cluster which can run workloads in containers. It works with various container runtimes, such as containerd and CRI-O. Its suitability for running and managing workloads of all sizes and styles has led to its widespread adoption in clouds and data centers. There are multiple distributions of this platform—from independent software vendors (ISVs) as well as hosted-on-cloud offerings from all the major public cloud vendors. The software consists of a control plane and nodes on which the actual applications run. It includes tools like kubeadm and kubectl which can be used to interact with its REST-based API.
Kubernetes was announced by Google on June 6, 2014. The project was conceived and created by Google employees Joe Beda, Brendan Burns, and Craig McLuckie. Others at Google soon joined to help build the project including Ville Aikas, Dawn Chen, Brian Grant, Tim Hockin, and Daniel Smith. Other companies such as Red Hat and CoreOS joined the effort soon after, with notable contributors such as Clayton Coleman and Kelsey Hightower. The design and development of Kubernetes was inspired by Google's Borg cluster manager and based on Promise Theory. Many of its top contributors had previously worked on Borg; they codenamed Kubernetes "Project 7" after the Star Trek ex-Borg character Seven of Nine and gave its logo a seven-spoked ship's wheel (designed by Tim Hockin). Unlike Borg, which was written in C++, Kubernetes is written in the Go language. Kubernetes was announced in June, 2014 and version 1.0 was released on July 21, 2015. Google worked with the Linux Foundation to form the Cloud Native Computing Foundation (CNCF) and offered Kubernetes as the seed technology.
Google was already offering a managed Kubernetes service, GKE, and Red Hat was supporting Kubernetes as part of OpenShift since the inception of the Kubernetes project in 2014. In 2017, the principal competitors rallied around Kubernetes and announced adding native support for it: VMware (proponent of Pivotal Cloud Foundry) in August, Mesosphere, Inc. (proponent of Marathon and Mesos) in September, Docker, Inc. (proponent of Docker) in October, Microsoft Azure also in October, AWS announced support for Kubernetes via the Elastic Kubernetes Service (EKS) in November. On March 6, 2018, Kubernetes Project reached ninth place in the list of GitHub projects by the number of commits, and second place in authors and issues, after the Linux kernel. Until version 1.18, Kubernetes followed an N-2 support policy, meaning that the three most recent minor versions receive security updates and bug fixes. Starting with version 1.19, Kubernetes follows an N-3 support policy.
Kubernetes defines a set of building blocks ("primitives") that collectively provide mechanisms that deploy, maintain, and scale applications based on CPU, memory or custom metrics. Kubernetes is loosely coupled and extensible to meet the needs of different workloads. The internal components as well as extensions and containers that run on Kubernetes rely on the Kubernetes API. The platform exerts its control over compute and storage resources by defining resources as objects, which can then be managed as such. Kubernetes follows the primary/replica architecture. The components of Kubernetes can be divided into those that manage an individual node and those that are part of the control plane.
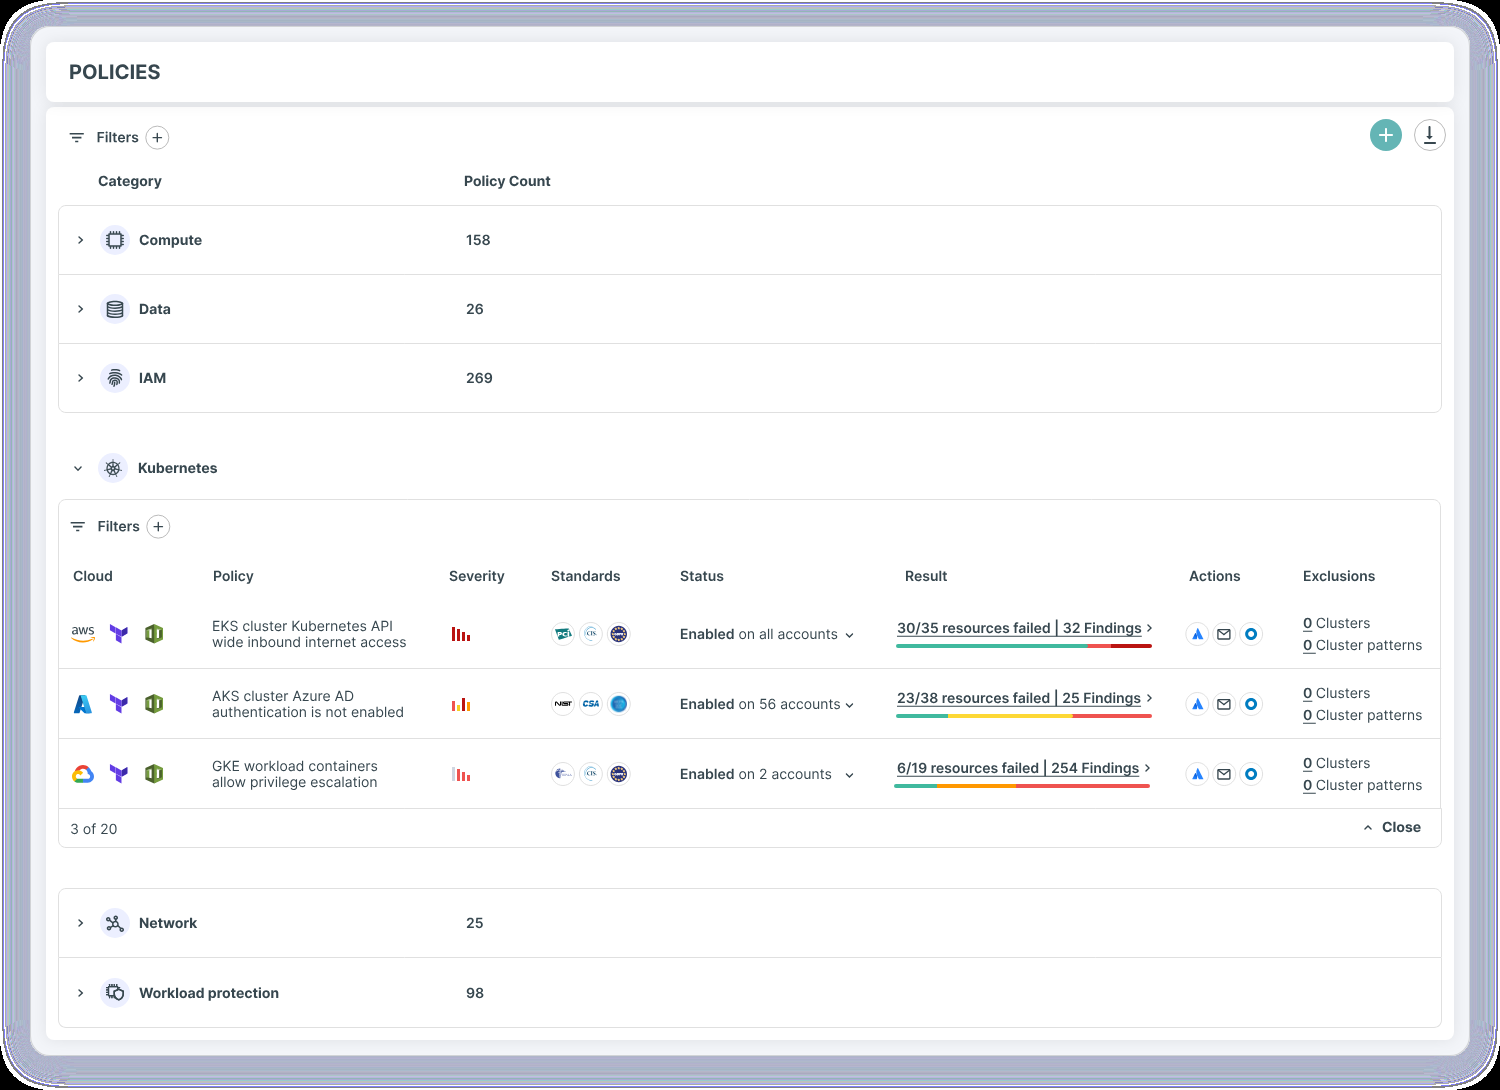
Figure 1: Mastering the Art of Kubernetes Security - Blog | Tenable® A Kubernetes service is a set of pods that work together, such as one tier of a multi-tier application. The set of pods that constitute a service are defined by a label selector. Kubernetes provides two modes of service discovery, using environment variables or using Kubernetes DNS. Service discovery assigns a stable IP address and DNS name to the service, and load balances traffic in a round-robin manner to network connections of that IP address among the pods matching the selector (even as failures cause the pods to move from machine to machine). By default a service is exposed inside a cluster (e.g., back end pods might be grouped into a service, with requests from the front-end pods load-balanced among them), but a service can also be exposed outside a cluster (e.g., for clients to reach front-end pods).
As environment variables, which will be consumed by kubelet from the ConfigMap when the container is launched; Mounted within a volume accessible within the container's filesystem, which supports automatic reloading without restarting the container. The biggest difference between a Secret and a ConfigMap is that Secrets are specifically designed for containing secure and confidential data, although they are not encrypted at rest by default, and requires additional setup in order to fully secure the use of Secrets within the cluster. Secrets are often used to store confidential or sensitive data like certificates, credentials to work with image registries, passwords, and ssh keys.
tier=backend AND release_track=canary Just like labels, field selectors also let one select Kubernetes resources. Unlike labels, the selection is based on the attribute values inherent to the resource being selected, rather than user-defined categorization. metadata.name and metadata.namespace are field selectors that will be present on all Kubernetes objects. Other selectors that can be used depend on the object/resource type.
DNS Cluster DNS is a DNS server, in addition to the other DNS server(s) in the environment, which serves DNS records for Kubernetes services. Containers started by Kubernetes automatically include this DNS server in their DNS searches. Web UI This is a general purpose, web-based UI for Kubernetes clusters. It allows administrators to manage and troubleshoot applications running in the cluster, as well as the cluster itself. Resource monitoring Container Resource Monitoring records metrics about containers in a central database, and provides a UI for browsing that data. Cost monitoring Kubernetes cost monitoring applications allow breakdown of costs by pods, nodes, namespaces, and labels. Cluster-level logging To prevent the loss of event data in the event of node or pod failures, container logs can be saved to a central log store with a search/browsing interface. Kubernetes provides no native storage for log data, but one can integrate many existing logging solutions into the Kubernetes cluster.
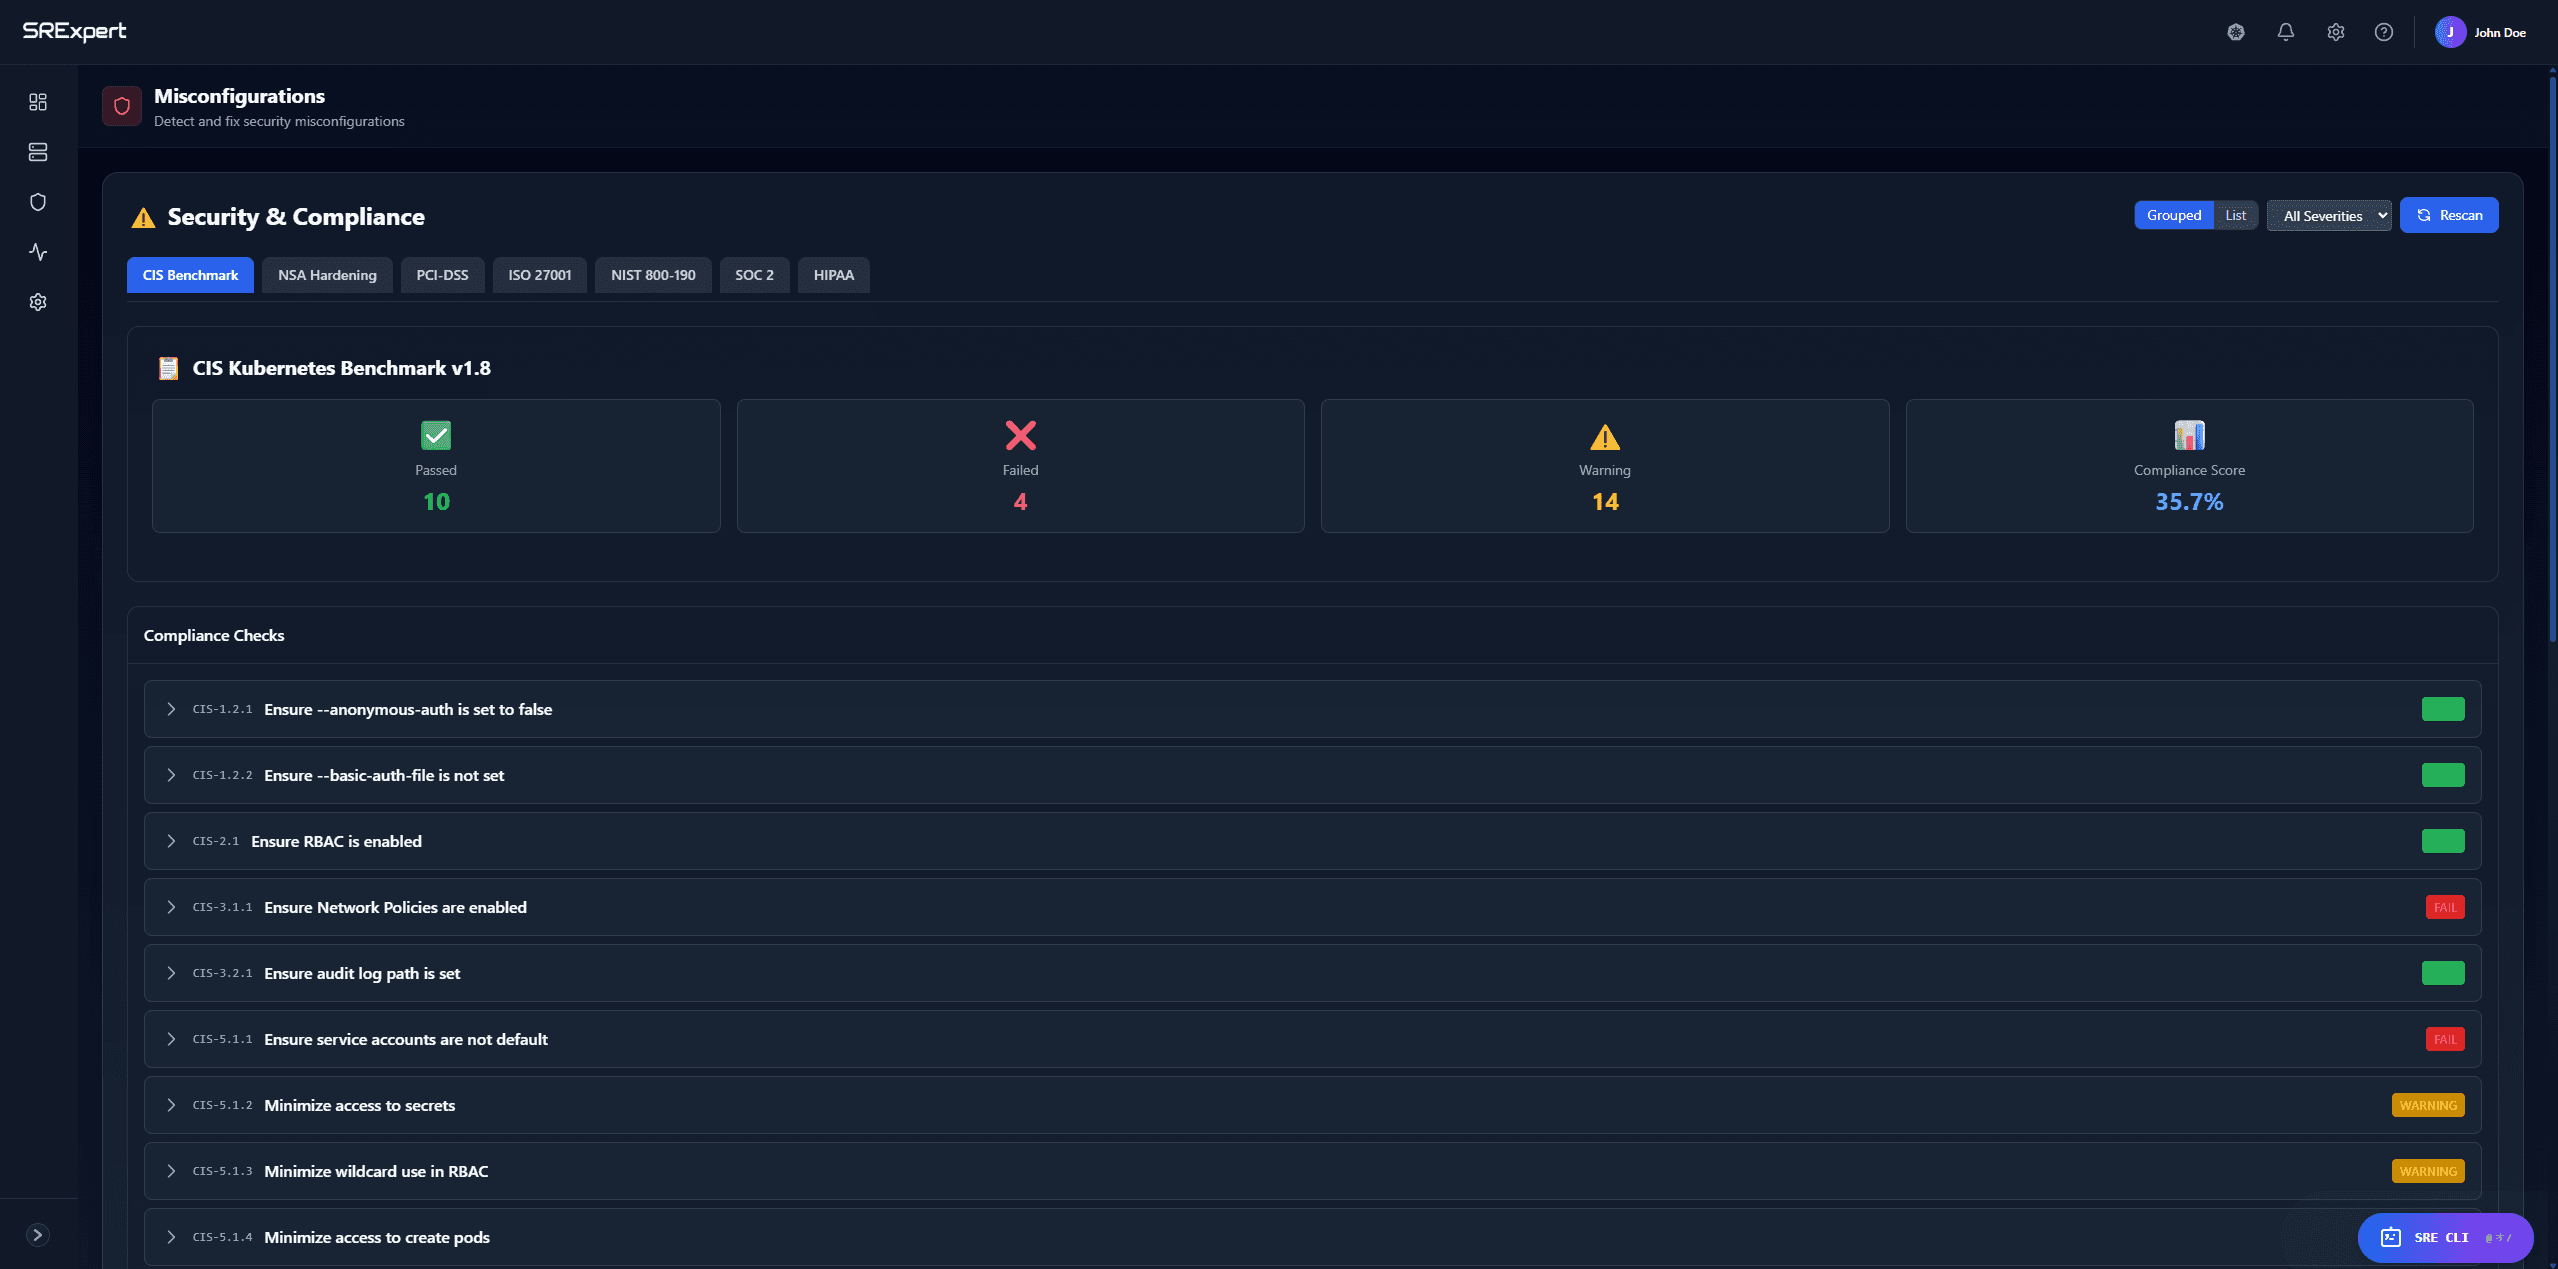
Figure 2: SRExpert — Kubernetes Management Platform: Dashboard, Security & AI spec: Describes the desired state of the resource, which can be controlled by end users, or other higher-level controllers; status: Describes the current state of the resource, which is actively updated by the controller of the resource. All objects in Kubernetes are subject to the same API conventions. Some of these include: Must have the following metadata under the nested object field metadata: namespace: a label that objects are subdivided into; name: a string that uniquely identifies the object within the defined namespace; uid: a string that uniquely identifies any API object in the cluster, regardless of type, name, namespace and time -- that is, even across deletions and recreations with the same type, name and namespace. May be managed by another controller, which is defined in the metadata.ownerReferences field: At most one other object shall be the managing controller of the controllee object, which is defined by the controller field.
May be garbage collected if the owner is deleted: When an object is deleted, all dependent objects may also be deleted in a cascading fashion. X.509 client certificates Bearer tokens Service account tokens, intended for programmatic API access Users are typically expected to indicate and define cluster URL details along with the necessary credentials in a kubeconfig file, which are natively supported by other Kubernetes tools like kubectl and the official Kubernetes client libraries.
Node authorization mode: Grants a fixed list of operations of API requests that kubelets are allowed to perform, in order to function properly. Attribute-based access control (ABAC) mode: Grants access rights to users through the use of defined access control policies which combine attributes together. Role-based access control (RBAC) mode: Grants access rights to users based on roles that are granted to the user, where each role defines a list of actions that are allowed. Webhook mode: Queries a REST API service to determine if a user is authorized to perform a given action.
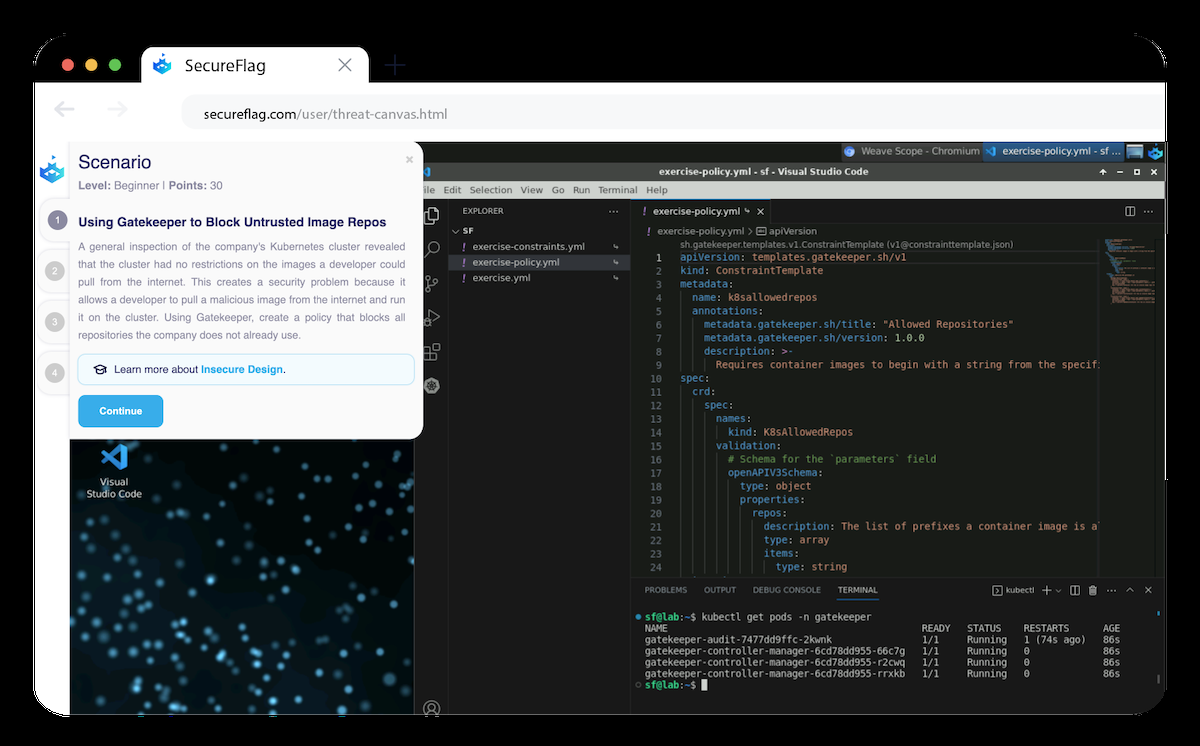
Figure 3: Securing Kubernetes: Using Gatekeeper to enforce effective security ... kubectl: Command-line for interacting with the Kubernetes control plane Official client libraries maintained by Kubernetes for C, .NET, Go, Haskell, Java, JavaScript, Perl, Python and Ruby Cilium is a cloud native technology for networking, observability, and security. It is based on the kernel technology eBPF, originally for better networking performance, and now leverages many additional features for different use cases. The core networking component has evolved from only providing a flat Layer 3 network for containers to including advanced networking features, like BGP and Service mesh, within a Kubernetes cluster, across multiple clusters, and connecting with the world outside Kubernetes. Hubble was created as the network observability component and Tetragon was later added for security observability and runtime enforcement. Cilium runs on Linux and is one of the first eBPF applications being ported to Microsoft Windows through the eBPF on Windows project.
December 2015 - Initial commit to the Cilium project May 2016 - Network policy was added, expanding the scope beyond just networking August 2016 - Cilium was initially announced during LinuxCon as a project providing fast IPv6 container networking with eBPF and XDP. Today, Cilium has been adopted by major cloud provider's Kubernetes offerings and is one of the most widely used CNIs. August 2017 - ebpf-go was created as a library to read, modify, and load eBPF programs and attach them to various hooks. April 2018 - Cilium 1.0 is the first stable release November 2019 - Hubble was launched to provide eBPF-based observability to network flows August 2020 - Chosen by Google as the basis for their Kubernetes Dataplane v2 September 2021 - AWS picks Cilium for Networking & Security on EKS Anywhere October 2021 - Pwru was launched for tracing network packets in the Linux kernel with advanced filtering capabilities October 2021 - Accepted into CNCF as an incubation level project December 2021 - Cilium Service Mesh launched to help manage traffic between services May 2022 - Tetragon open sourced to cover security observability and runtime enforcement October 2022 - Chosen as CNI for Azure April 2023 - Cilium Mesh launched to connect workloads and machines across cloud, on-prem, and edge April 2023 - First CiliumCon hosted as a part of KubeCon October 2023 - Cilium becomes a CNCF Graduated project Datadog uses Cilium as their CNI and kube-proxy replacement Ascend uses Cilium as their one CNI across multiple cloud providers Bell Canada uses Cilium and eBPF for telco networking Cosmonic uses Cilium for their Nomad-based PaaS IKEA uses Cilium for their self-hosted bare-metal private cloud S&P Global uses Cilium as its CNI Sky uses Cilium as their CNI and for network security The New York Times uses Cilium on EKS for multi-region multi-tenant shared clusters Trip.com uses Cilium both on premise and in AWS OpenAI uses Cilium as their CNI Palantir uses Cilium as their CNI across all major cloud providers TikTok uses Cilium as their CNI in their IPv6-only datacenters Cilium is the CNI for many cloud providers including Alibaba, APPUiO, Azure, AWS, DigitalOcean, Exoscale, Google Cloud, Hetzner, and Tencent Cloud.
Container Network Interface (CNI) - Provides networking for Kubernetes clusters Layer 4 Load Balancer - Based on Maglev and XDP for handling north/south traffic Cluster Mesh - Combines multiple Kubernetes clusters into one network Bandwidth and Latency Optimization - Fair Queueing, TCP Optimization, and Rate Limiting kube-proxy replacement - Replaces iptables with eBPF hash tables BGP - Integrates into existing networks and provides load balancing in bare metal clusters Egress Gateway - Provides a static IP for integration into external workloads Service Mesh - Includes ingress, TLS termination, canary rollouts, rate limiting, and circuit breaking Gateway API - Fully conformant implementation for managing ingress into Kubernetes clusters SRv6 - Defines packet processing in the network as a program BBR support for Pods - Allows for better throughput and latency for Internet traffic NAT 46/64 Gateway - Allows IPv4 services to talk with IPv6 ones and vice versa BIG TCP for IPv4/IPv6 - Enables better performance by reducing the number of packets traversing the stack Cilium Mesh - Connects workloads running outside Kubernetes to ones running inside it Service Map - Provides a UI for network flows and policy Network Flow Logs - Provides Layer 3/4 and DNS visibility connected to identity Network Protocol Visibility - Including HTTP, gRPC, Kafka, UDP, and SCTP Metrics & Tracing Export - Sends data to Prometheus, OpenTelemetry, or other storage system Transparent Encryption - Utilizes either IPSec or WireGuard Network Policy - Includes Layer 3 to Layer 7 and DNS-aware policies Runtime Enforcement - Stops processes outside of policies with default policies File Integrity Monitoring - Tracks modification to the system CiliumCon EU 2023, held in conjunction with KubeCon + CloudNativeCon EU 2023 CiliumCon NA 2023, held in conjunction with KubeCon + CloudNativeCon NA 2023 CiliumCon EU 2024, held in conjunction with KubeCon + CloudNativeCon EU 2024 CiliumCon NA 2024 held in conjunction with KubeCon + CloudNativeCon NA 2024 Cilium Annual Report 2022: Year of the CNI Cilium Annual Report 2023: Year of Graduation Cilium Annual Report 2024: Year of Kubernetes Networking Cilium Annual Report 2025: Decade of Cloud Native Networking Google Cloud is a suite of cloud computing services offered by Google that provides a series of modular cloud services including computing, data storage, data analytics, and machine learning, alongside a set of management tools. It runs on the same infrastructure that Google uses internally for its end-user products, such as Google Search, Gmail, and Google Docs, according to Verma et al. Registration requires a credit card or bank account details. Google Cloud provides infrastructure as a service, platform as a service, and serverless computing environments. In April 2008, Google announced App Engine, a platform for developing and hosting web applications in Google-managed data centers, which was the first cloud computing service from the company. The service became generally available in November 2011. Since the announcement of App Engine, Google added multiple cloud services to the platform. Google Cloud includes Google Cloud public cloud infrastructure, as well as Google Workspace (G Suite), enterprise versions of Android and ChromeOS, and application programming interfaces (APIs) for machine learning and enterprise mapping services. Since at least 2022, Google's official materials have stated that "Google Cloud" is the new name for "Google Cloud Platform," which may cause naming confusion.
For those familiar with other notable cloud service providers, a comparison of similar services may be helpful in understanding Google Cloud Platform's offerings. April 2008 – Google App Engine announced in preview May 2010 – Google Cloud Storage launched May 2010 – Google BigQuery and Prediction API announced in preview October 2011 – Google Cloud SQL is announced in preview June 2012 – Google Compute Engine is launched in preview May 2013 – Google Compute Engine is released to GA August 2013 – Cloud Storage begins automatically encrypting each Storage object's data and metadata under the 128-bit Advanced Encryption Standard (AES-128), and each encryption key is itself encrypted with a regularly rotated set of master keys February 2014 – Google Cloud SQL becomes GA May 2014 – Stackdriver is acquired by Google June 2014 – Kubernetes is announced as an open source container manager June 2014 – Cloud Dataflow is announced in preview October 2014 – Google acquires Firebase November 2014 – Alpha release Google Kubernetes Engine (formerly Container Engine) is announced January 2015 – Google Cloud Monitoring based on Stackdriver goes into Beta March 2015 – Google Cloud Pub/Sub becomes available in Beta April 2015 – Google Cloud DNS becomes generally available April 2015 – Google Dataflow launched in beta July 2015 – Google releases v1 of Kubernetes; Hands it over to The Cloud Native Computing Foundation August 2015 – Google Cloud Dataflow, Google Cloud Pub/Sub, Google Kubernetes Engine, and Deployment Manager graduate to GA November 2015 – Bebop is acquired, and Diane Greene joins Google February 2016 – Google Cloud Functions becomes available in Alpha September 2016 – Apigee, a provider of application programming interface (API) management company, is acquired by Google September 2016 – Stackdriver becomes generally available November 2016 – Qwiklabs, an EdTech company is acquired by Google February 2017 – Cloud Spanner, highly available, globally-distributed database is released into Beta March 2017 – Google acquires Kaggle, world's largest community of data scientists and machine learning enthusiasts April 2017 – MIT professor Andrew Sutherland breaks the record for the largest ever Compute Engine cluster with 220,000 cores on Preemptible VMs. May 2017 – Google Cloud IoT Core is launched in Beta November 2017 – Google Kubernetes Engine gets certified by the CNCF February 2018 – Google Cloud IoT Core becomes generally available February 2018 – Google announces its intent to acquire Xively February 2018 – Cloud TPUs, ML accelerators for Tensorflow, become available in Beta May 2018 – Google Cloud Memorystore becomes available in Beta April 2019 – Google Cloud Run (fully managed) Beta release April 2019 – Google Anthos announced November 2019 – Google Cloud Run (fully managed) General availability release March 2020 – Due to the COVID-19 pandemic, Google Cloud postponed the online streaming version of its Google Cloud Next mega-conference, two weeks after it canceled the in-person version. October 2020 – Google Cloud announced that it will become a block producer candidate for the EOS network and EOS.IO protocol. Currently the top block producers are cryptocurrency exchanges like OKEx and Binance. February 2021 – Google Kubernetes Engine Autopilot is introduced. May 2021 – Vertex AI announced at Google.io June 2021 – In 2021, Apple was Google Cloud's biggest customer. April 2022 – MobiledgeX acquired and joins Google Cloud. March 2023 – Google brings generative AI capabilities to Google Cloud. May 2024 Google Cloud partnered with Airtel. April 2025 – At Google Cloud Next 2025 in Las Vegas, Google announced the seventh-generation Tensor Processing Unit, named Ironwood, claiming 3,600 times better performance than its first publicly available TPU. Google also announced Cloud Wide Area Network (Cloud WAN), making its private global network available to enterprise customers, and introduced Gemini 2.5 and Gemini 2.5 Flash reasoning models.
April 2026 – At Google Cloud Next '26, Sundar Pichai announced expanded AI infrastructure investments, including the introduction of Trillium TPUs (8th generation) and the Gemini Enterprise Agent Platform, with Google reporting that 75% of new internal code was AI-generated. A comprehensive comparison of Open Policy Agent (OPA) and HashiCorp Sentinel for policy as code. Compare language, use cases, integrations, ecosystem, and enterprise features to choose the right solution.
A step-by-step tutorial on writing, testing, and deploying your first Open Policy Agent (OPA) Gatekeeper policy to enforce custom rules on your Kubernetes cluster. Explore complex policy design for dynamic, data-driven, and context-aware infrastructure governance. Build and enforce Zero Trust principles in your deployments using policy-as-code as the foundation.
A comprehensive comparison of Open Policy Agent (OPA) and HashiCorp Sentinel for policy as code. Compare language, use cases, integrations, ecosystem, and enterprise features to choose the right solution. A comprehensive troubleshooting guide for OPA Rego undefined decision errors. Learn why decisions are undefined, how to fix them, and best practices for robust policy writing.
A comprehensive guide to debugging Kubernetes NetworkPolicy issues. Learn how to troubleshoot connection failures, test policies, and fix common NetworkPolicy configuration problems. A comprehensive guide to reducing Kubernetes costs across AWS EKS, Google GKE, and Azure AKS. Learn rightsizing, autoscaling, spot instances, storage optimization, and cloud-specific cost strategies.
A comprehensive guide to reducing Kubernetes costs across AWS EKS, Google GKE, and Azure AKS. Learn rightsizing, autoscaling, spot instances, storage optimization, and cloud-specific cost strategies. Master Kubernetes network security by learning how to write, apply, and troubleshoot NetworkPolicy resources to control traffic flow between your pods.
A step-by-step guide to installing, configuring, and writing your first policies with Open Policy Agent (OPA) Gatekeeper on Kubernetes. Clarify the crucial distinctions between Policy-as-Code (PaC) and Infrastructure as Code (IaC) security scanning, and learn how they work together to create a robust cloud security posture.
2. System Architecture & Core Working Principles An in-depth, hands-on guide to learning Open Policy Agent and the Rego language for unified policy enforcement across your stack. Learn the fundamentals of Cedar, the high-performance policy language from AWS, for building secure and auditable application authorization.
Master the integration of Open Policy Agent (OPA) with Terraform to enforce security, compliance, and operational best practices on your infrastructure as code. A step-by-step tutorial on writing, testing, and deploying your first Open Policy Agent (OPA) Gatekeeper policy to enforce custom rules on your Kubernetes cluster.
Advanced techniques for detecting and managing configuration drift in your cloud environments. Explore complex policy design for dynamic, data-driven, and context-aware infrastructure governance. Build and enforce Zero Trust principles in your deployments using policy-as-code as the foundation. A misconfigured Kubernetes cluster doesn’t announce itself. It just sits there, quietly reachable, until someone finds an exposed dashboard, a default-allow network policy, or a service account with cluster-admin rights it never needed.
Kubernetes 1.36 “Haru” went GA in May 2026 and, for the first time, shipped Restricted Pod Security as the default in three or more core namespaces out of the box; Kubernetes 1.37.0 followed in late August 2026 running on Go 1.26.5, and the September 2026 patch release, 1.37.1, added further storage-hardening features including new bind-mount options — but the platform still ships with more open doors than most teams realize. This tutorial walks through hardening a real cluster from the ground up: RBAC, Pod Security Standards, network policies, secrets management, image signing, runtime detection, and node-level lockdown, with copy-pasteable YAML at every step.
By the end you’ll have a working, layered kubernetes security hardening baseline you can drop into a staging cluster today and promote to production once you’ve tested it against your own workloads. This isn’t a checklist you skim once. Kubernetes security hardening is a maintenance habit, and this guide is built to be re-run every quarter as your cluster grows. Add Tech Insider once in the Google app and our stories appear in your news suggestions.
The OWASP Kubernetes Top 10 (2025 edition) and the official Kubernetes security checklist now converge on the same five pillars for 2026: RBAC least privilege, Pod Security Standards enforcement, network segmentation, image provenance, and runtime detection — the same five-pillar framework this guide has used since our original August 2026 hardening research named the OWASP 2025 Top 10 as its baseline. That convergence matters because it means the industry has stopped debating what “secure Kubernetes” looks like. The open question left for most teams is simply whether they’ve actually implemented it.
Most breaches in container environments don’t start with a zero-day. They start with something mundane: a service account that automounts a token nobody uses, a namespace with no NetworkPolicy so a compromised pod can reach the entire cluster, or a Secret sitting unencrypted in etcd. That said, platform-level bugs still surface and compound misconfiguration risk — in September 2026, Kubernetes disclosed CVE-2026-19444, which let kubectl cp on Windows write arbitrary files, and CVE-2026-76654, where Windows subpath symlinks could be abused for NTLM coercion, both reminders that hardening has to cover client tooling and the OS layer, not just cluster config. Kubernetes security hardening closes those gaps systematically rather than reactively. Container security best practices in 2026 also increasingly assume a supply-chain angle: image scanning and signature verification catch compromised base images before they ever reach a node, which matters given how much of a typical container image is inherited from a public registry rather than written in-house.
The good news is that none of the steps below require ripping out your existing cluster. Every control here layers on top of a running deployment, and most can be rolled out namespace by namespace so you can validate behavior before enforcing it fleet-wide. Before starting, confirm you have the following. Version numbers below reflect what’s current and stable as of September 2026 — check each project’s release page before you install, since minor point releases ship frequently; note that Kubernetes 1.34 entered security-only maintenance in August 2026 and reaches end-of-life in October 2026, so clusters still on that branch should already have an upgrade path scheduled.
If you’re running managed Kubernetes (EKS, AKS, GKE, or Oracle Cloud Infrastructure’s OKE, which supported Kubernetes 1.34.10 alongside 1.36.1 and 1.35.2 as of August 2026), some of these steps — especially node hardening and control plane audit logging — are partially handled by the provider. We’ll flag where that applies. If you’re comparing managed options first, our EKS vs AKS vs GKE breakdown covers the control-plane security defaults each one ships with out of the box.
Don’t harden blind. Run a baseline scan first so you know what you’re actually fixing, and so you have a before/after comparison to show whoever signs off on the change window. Install kube-bench and run it against your nodes and control plane: kube-bench checks your cluster against the CIS Kubernetes Benchmark , flagging items as PASS, FAIL, WARN, or INFO.
Expect your first run on an unhardened cluster to return a long list of FAIL entries around file permissions, RBAC wildcards, and anonymous auth. That’s normal — treat it as your punch list for the rest of this guide, not a grade. Any service account bound to cluster-admin that isn’t a controller or your own CI/CD pipeline identity is worth investigating immediately. This is consistently the single highest-impact finding in a first-pass audit.
RBAC least privilege means every service account, user, and group has exactly the permissions it needs and nothing more. In practice, most clusters drift toward over-permissioning because it’s faster to grant cluster-admin during a debugging session and never revoke it. The risk isn’t theoretical: Kubernetes disclosed CVE-2026-2270 in September 2026, where overly broad StatefulSet permissions allowed cross-namespace pod creation — exactly the kind of blast-radius expansion namespace-scoped Roles are meant to prevent. Start by replacing broad ClusterRoleBindings with namespace-scoped Roles wherever the workload doesn’t genuinely need cross-namespace access.
Notice there’s no wildcard anywhere in that Role — every resource and verb is spelled out. Audit your RoleBindings on a recurring schedule, not just once: ThnkBig’s August 2026 security guide formalizes this as four RBAC reviews a year and pairs it with mandatory MFA for every user who can reach the cluster, a combination worth adopting even if you build your own cadence rather than following theirs verbatim. A quarterly review catches the permissions that got added “temporarily” six months ago and never removed. Teams running Kubecost alongside their cluster for cost attribution can piggyback the same quarterly cadence onto a permissions review, since both require walking every namespace anyway — see our Kubecost setup guide if you haven’t wired that up yet.
Pod Security Standards (PSS) replaced the deprecated PodSecurityPolicy and are enforced natively via the built-in Pod Security Admission controller — no extra installation required. There are three levels: Privileged (unrestricted), Baseline (blocks known privilege escalations), and Restricted (enforces current pod hardening best practice, including non-root and no privilege escalation). For 2026 production workloads, Restricted should be your default target — AppSecSanta’s May 2026 hardening guide, aligned with the OWASP Kubernetes Top 10 (2025), goes as far as enforcing Baseline or Restricted on 100% of workloads with no exceptions, which is the direction most mature teams are already heading.
Don’t flip straight to enforce on a namespace with existing workloads — you’ll break pods that aren’t compliant yet. Set audit and warn first, watch the API server logs and `kubectl` warnings for a week, fix what surfaces, then move to enforce . Full level definitions live in the official Pod Security Standards documentation . By default, every pod gets a Kubernetes API token mounted into its filesystem, whether or not the workload ever calls the API server. That token is a standing credential an attacker can lift the moment they get shell access to a container. Most workloads — a web server, a batch job, a static frontend — never need it. Orthogonal’s March 2026 guide goes further, mandating that application workloads never run under cluster-admin and defaulting to automountServiceAccountToken=false alongside runAsUser IDs of 1000 or higher; for AI and GPU-backed workloads specifically, BeyondScale’s May 2026 hardening guide recommends capping projected service account token lifetimes at 3,600 seconds and keeping the NVIDIA GPU Operator on version 25.3.1 or newer.
Setting it at both the ServiceAccount and pod spec level is redundant but cheap insurance — if someone forgets one, the other still catches it. For the handful of workloads that genuinely need API access (operators, controllers, CI runners), leave the token mounted but scope its RBAC role as tightly as described in Step 2. Without a NetworkPolicy, every pod in a namespace can talk to every other pod in the cluster by default. That’s convenient during development and disastrous during an incident, because it means a single compromised container can reach your database, your internal admin panel, and anything else on the flat network. Default-deny for both ingress and egress, with explicit allow rules layered on top, is now baseline practice.
That last policy matters more than it looks — teams frequently deploy a default-deny egress rule, forget DNS still needs to resolve, and spend an afternoon debugging why every pod suddenly can’t reach anything. Build the DNS allowance in from the start. Note that NetworkPolicy enforcement depends on your CNI plugin actually supporting it — Calico, Cilium, and most managed cluster CNIs do, but the default kubenet on some older setups doesn’t enforce policies at all, which means the YAML applies with no error and silently does nothing.
Kubernetes Secrets are base64-encoded, not encrypted, by default. Anyone with etcd read access — or a backup of etcd — can trivially decode every Secret in your cluster. Kubernetes has disabled the insecure, unauthenticated API port by default since 1.20, so this etcd exposure is now the more realistic attack path worth closing. Decryption Digest’s May 2026 checklist recommends AES-GCM as the preferred provider for etcd Secrets encryption, with AES-CBC as an acceptable fallback.
Enable encryption at rest at the API server level: Reference that file with --encryption-provider-config on the API server, then re-write existing Secrets so they get encrypted under the new config ( kubectl get secrets --all-namespaces -o json | kubectl replace -f - forces a rewrite). For mature teams, the 2026 recommendation goes a step further: migrate sensitive Secrets out of etcd entirely into an external manager like HashiCorp Vault, AWS Secrets Manager, or Azure Key Vault, and inject them at runtime via a CSI driver instead of storing them as native Kubernetes objects. We cover the full setup in our HashiCorp Vault tutorial if you’re starting from scratch, and if you’re choosing between managed secret stores our CSPM tool comparison covers how each platform surfaces exposed Secrets automatically.
The smaller and more restricted your container image, the less an attacker can do once they’re inside it. 2026 hardening guidance is explicit on this: use distroless or slim base images, run as a non-root user, drop unnecessary Linux capabilities, and make the root filesystem read-only wherever the app doesn’t need to write locally. Don’t stop at the image layer, either — Optibot’s April 2026 advisory flags three runc CVEs and urges upgrading to runc 1.2.8+ or 1.3.3+, and notes that Pod Security Admission’s Restricted level now requires an explicit seccompProfile of RuntimeDefault rather than treating it as optional.
The emptyDir mount for /tmp is a common gotcha: setting readOnlyRootFilesystem: true without it will crash-loop any application that writes temp files, logs, or cache data to disk, which is most of them. Mount a writable volume explicitly for whatever paths the app actually touches, and leave everything else locked. Hardening a pod’s runtime configuration doesn’t help if the image itself was compromised before it ever reached your cluster — a poisoned dependency in a public base image, a malicious CI step, or a supply-chain injection. Admission controllers close that gap by blocking anything that doesn’t meet policy before it’s scheduled. Kyverno 1.19 (current as of August 2026) is the most widely adopted policy engine for this, alongside OPA Gatekeeper.
Once Kyverno is running, add a ClusterPolicy that blocks unsigned images from being admitted: Sign your images at build time with Cosign (part of the Sigstore project ) so this policy has something to actually verify. Just like Pod Security Standards, deploy this in Audit mode first — flipping straight to Enforce on a policy engine you haven’t tested against your real image inventory is the single fastest way to take production down during a deploy.
Audit logs are your forensic trail — without them, you can’t answer “what happened” after an incident, only “what state we’re in now.” Configure a policy that captures request/response bodies for sensitive operations (Secrets access, exec into pods) while keeping noisier, lower-value requests at metadata-only level to control log volume. Point the API server at this policy with --audit-policy-file and --audit-log-path , then forward the resulting log file into whatever SIEM your security team already watches — Splunk, Elastic, or a cloud-native option. If you’re comparing SIEM platforms for this, our cloud security platform comparison breaks down ingestion pricing, which matters once you’re piping full RequestResponse-level Secrets access logs at scale.
Everything up to this point is static configuration — it prevents bad states from being created. Runtime detection catches bad behavior happening right now: a shell spawned inside a container that shouldn’t have one, a process reading /etc/shadow , an unexpected outbound connection. Falco 0.44.1 is the CNCF-graduated standard for this and reads directly from kernel syscalls via eBPF, so it sees activity that config auditing alone never will.
3. Software Implementation, Frameworks & Protocols Falco ships with a solid default ruleset (shell spawned in container, write below binary directory, unexpected network tool launched) but expect noisy false positives out of the box against your specific workloads. Tune the rules over your first two weeks rather than disabling categories wholesale — an ignored Falco alert is worse than no Falco at all, because it creates a false sense of coverage. Full rule syntax and tuning guidance is in the Falco documentation .
Pod-level and API-level hardening don’t help if the underlying node is soft. Node hardening in 2026 focuses on three things: disabling unnecessary kernel modules, isolating node roles so control-plane and worker responsibilities never share a machine, and locking SSH access down to break-glass only — or removing it outright, which is the direction cloud provider STACKIT is pushing: it announced that it will strip OpenSSH from Kubernetes nodes entirely starting November 2026 to shrink the attack surface. Watch the kubelet certificate story too: KEP-4872’s kubelet certificate hardening work entered alpha in Kubernetes 1.35 (per a December 2025 CNCF preview), and tightening kubelet’s own TLS material is likely to become a standard node-hardening checklist item as that KEP matures toward stable.
If you’re on managed Kubernetes, most of this is handled for you on the control plane side — GKE’s cluster hardening guide is a solid reference for what the provider covers versus what’s still your responsibility on worker nodes. AWS and Azure publish equivalent shared-responsibility breakdowns; check whichever cloud backs your EKS deployment before assuming node hardening is done for you.
Once RBAC, Pod Security Standards, network policies, and secrets are handled, a service mesh with mutual TLS is the next layer for teams operating at scale. mTLS encrypts and authenticates every service-to-service call inside the cluster, which matters because NetworkPolicies control who can talk to whom but not whether the traffic itself is encrypted and verified . Istio and Linkerd both support automatic mTLS with sidecar injection and require no application code changes.
Treat this as a Phase 3 control, not a Phase 1 one. A service mesh adds real operational complexity — sidecar resource overhead, an additional control plane to patch, and a new source of latency to debug. Deploy it after the foundational controls above are stable, not instead of them. Manual hardening decays. New nodes get added without the hardened base image, new namespaces get created without the Pod Security labels, and six months later half of what you did in Steps 1 through 12 has quietly drifted. Automate the kube-bench scan from Step 1 to run on a schedule, and alert when the pass rate drops.
Pipe the CronJob’s output into your SIEM or a Slack webhook so a failed run gets seen the same day, not discovered during the next annual audit. There’s no single tool that covers every layer of Kubernetes container security. Most production clusters run a combination of the categories below.
Open source covers every layer described in this tutorial at zero licensing cost, which is why most of the hands-on steps above use it. Commercial CNAPP platforms earn their price when you need a unified dashboard across dozens of clusters and multiple clouds rather than stitching together five open source projects yourself — see our CNAPP comparison for pricing at scale.
These are the mistakes that show up repeatedly in post-incident reviews, even on clusters that technically “did” a hardening pass. Here’s what typically goes wrong during and after a hardening rollout, and how to fix it. Once the baseline above is stable, a few additional practices separate a hardened cluster from a genuinely resilient one.
Etcd encryption keys, service account signing keys, and TLS certificates should rotate on a calendar cadence rather than only after a suspected compromise. Waiting for a trigger means your rotation process is untested exactly when you need it most. A NetworkPolicy that looks correct on paper isn’t verified until you’ve actually tried to violate it from inside the cluster. Periodically spin up a throwaway pod and attempt lateral movement, privilege escalation, and secrets access against your own hardened namespaces. If it succeeds, you’ve found a real gap before an attacker did.
A kube-bench score or Kyverno policy report that only lives on a dashboard gets ignored under deadline pressure. Wire the CI/CD pipeline to block a deploy if the target namespace fails its Pod Security or Kyverno checks — visibility alone doesn’t change behavior, but a failed pipeline does. Combining every step above into a single applyable bundle gives you a repeatable baseline for any new namespace. Save this as hardened-namespace-baseline.yaml and apply it as the first thing you do when standing up a new namespace, before any workload gets deployed into it.
From here, layer Kyverno’s image-signing policy, Falco, and the kube-bench CronJob from Step 13 on top of the cluster as a whole (they’re cluster-scoped, not per-namespace), and every new namespace inherits a hardened starting point instead of the wide-open Kubernetes default. Kubernetes security hardening is easy to declare “done” and hard to actually verify. A cluster can pass every step in this guide on the day you apply it and still drift back toward risk within a quarter as new namespaces, new engineers, and new third-party charts get added without the same rigor. Track a small set of metrics over time rather than relying on a one-time pass/fail from kube-bench.
None of these numbers matter in isolation — a 95% CIS pass rate on a cluster with three cluster-admin service accounts nobody can explain is not actually hardened, it just looks hardened on one dashboard. Review the full set together, monthly at minimum, and treat any metric moving in the wrong direction as equally urgent as a new CVE. Configuration drift is slower than a zero-day but just as reliable at eventually causing an incident.
Is Kubernetes secure by default? No. Out of the box, Kubernetes ships with permissive networking (no NetworkPolicy blocks anything unless one is created), unencrypted Secrets at rest, and service account tokens automounted into every pod whether needed or not. Security is opt-in and requires the explicit hardening steps covered in this guide. What’s the difference between Pod Security Standards and OPA Gatekeeper or Kyverno? Pod Security Standards are a built-in, Kubernetes-native admission control limited to pod-level security fields (privilege escalation, root user, capabilities).
Kyverno and OPA Gatekeeper are general-purpose policy engines that can enforce arbitrary rules across any resource type, including image signing, label requirements, and resource limits — they’re complementary, not competing. Do I need a service mesh for Kubernetes security? Not as a first step. mTLS via a service mesh adds meaningful protection against internal traffic interception, but it should come after RBAC, Pod Security Standards, network policies, and secrets management are already solid. Adding mesh complexity before the fundamentals are in place tends to create more operational risk than security benefit.
How often should I run a CIS Kubernetes Benchmark scan? Weekly at minimum via an automated CronJob, as shown in Step 13. Configuration drift happens continuously as new nodes, namespaces, and workloads get added — an annual audit alone will always be finding problems that existed for months. Does managed Kubernetes (EKS, AKS, GKE) handle security hardening for me? Partially. Managed providers secure the control plane — API server availability, etcd encryption keys, and control-plane audit logging are typically handled. Worker node OS hardening, RBAC configuration, Pod Security Standards, NetworkPolicies, and workload-level container hardening remain your responsibility regardless of which cloud you use.
What’s the single highest-impact first step if I can only do one thing? Audit and fix RBAC ClusterRoleBindings granting cluster-admin to service accounts that don’t need it (Steps 1 and 2). Over-permissioned service accounts are the most commonly exploited misconfiguration because they turn a single compromised pod into full cluster control. Can I use Trivy and Kyverno together? Yes, and most production setups do. Trivy scans images for known vulnerabilities during CI/CD, before an image is ever pushed to a registry. Kyverno enforces admission-time policy — including verifying that an image was actually signed — at the moment a pod tries to schedule. They cover different points in the pipeline.
Will enforcing Restricted Pod Security Standards break my existing workloads? Likely, if they weren’t built with it in mind. Legacy images that run as root or require specific Linux capabilities will fail under Restricted. Always deploy in audit and warn mode first (Step 3) to identify what breaks before switching to enforce . Elias Virtanen is the Cybersecurity Analyst at Tech Insider, bringing hands-on expertise from his background in penetration testing and security consulting. He previously worked as a security researcher at F-Secure in Helsinki, where he focused on threat intelligence and vulnerability disclosure. Elias covers ransomware trends, zero-trust architecture, and the evolving regulatory landscape including NIS2 and the EU Cyber Resilience Act. He holds a CISSP certification and an MSc in Information Security from Aalto University.
Tech Insider delivers in-depth coverage of the technologies shaping the future: AI, cybersecurity, cloud computing, hardware, and the trends that matter. Policy enforcement tools help ensure compliance and security standards across your Kubernetes clusters. They act as automated security guards that validate and enforce rules before resources are created or modified.
Policy enforcement uses admission controllers to validate Kubernetes resources against defined policies. Policies are written as code, making them: Open Policy Agent (OPA) is a general-purpose policy engine. Gatekeeper is a Kubernetes-specific implementation that uses OPA: Configure Pod Security Standards with baseline and restricted profiles, deploy OPA Gatekeeper admission controller with custom policies, and implement ValidatingAdmissionWebhooks for comprehensive security enforcement in production Kubernetes clusters.
Kubernetes Pod Security Standards provide a built-in framework for enforcing security policies at the namespace level, replacing deprecated Pod Security Policies. This tutorial shows you how to implement Pod Security Standards with baseline and restricted profiles, deploy OPA Gatekeeper for custom policy enforcement, and configure ValidatingAdmissionWebhooks to prevent insecure workloads from running in your cluster. You'll also set up comprehensive monitoring and alerting for security violations to maintain compliance in production environments.
Start by updating your system and installing necessary tools for Kubernetes security management. Configure namespaces with appropriate Pod Security Standard labels for baseline and restricted security profiles. 4. Practical Deployment, Analysis & Case Studies Set default Pod Security Standards at the cluster level by modifying the kube-apiserver configuration.
Define the admission control configuration file for Pod Security Standards enforcement. Define constraint templates for common security policies like required security contexts and resource limits. Apply constraints using the templates to enforce security context requirements in specific namespaces. Implement a custom ValidatingAdmissionWebhook for additional security checks beyond OPA Gatekeeper.
Create the ValidatingAdmissionWebhook configuration to intercept pod creation requests. Configure Prometheus monitoring for Pod Security Standards and Gatekeeper violations. This requires an existing Prometheus setup. Configure audit logging to track Pod Security Standards violations and admission webhook activity.
Build a production-grade Istio primary-remote multi-cluster topology with shared trust, locality-aware failover, and automated recovery testing. Covers cross-cluster service discovery, Kiali and Prometheus monitoring, and control plane backup procedures. Learn how to combine Ansible Vault with HashiCorp Vault using the community.hashi_vault collection, AppRole authentication, and least-privilege policies for production-grade secrets management in playbooks.
Build a primary-remote Istio multi-cluster mesh with shared trust domain, then run progressive canary rollouts using DestinationRule subsets, weighted VirtualServices and metrics-based promotion across clusters. We handle infrastructure for businesses that depend on uptime. Fully managed, with one fixed contact who knows your setup. This section of the Kubernetes documentation aims to help you learn to run workloads more securely, and about the essential aspects of keeping a Kubernetes cluster secure.
Kubernetes is based on a cloud-native architecture, and draws on advice from the CNCF about good practice for cloud native information security. Read Cloud Native Security and Kubernetes for the broader context about how to secure your cluster and the applications that you're running on it.
Kubernetes includes several APIs and security controls, as well as ways to define policies that can form part of how you manage information security. A key security mechanism for any Kubernetes cluster is to control access to the Kubernetes API . Kubernetes expects you to configure and use TLS to provide data encryption in transit within the control plane, and between the control plane and its clients. You can also enable encryption at rest for the data stored within Kubernetes control plane; this is separate from using encryption at rest for your own workloads' data, which might also be a good idea.
The Secret API provides basic protection for configuration values that require confidentiality. Enforce Pod security standards to ensure that Pods and their containers are isolated appropriately. You can also use RuntimeClasses to define custom isolation if you need it. Network policies let you control network traffic between Pods, or between Pods and the network outside your cluster.
You can deploy security controls from the wider ecosystem to implement preventative or detective controls around Pods, their containers, and the images that run in them. Admission controllers are plugins that intercept Kubernetes API requests and can validate or mutate the requests based on specific fields in the request. Thoughtfully designing these controllers helps to avoid unintended disruptions as Kubernetes APIs change across version updates. For design considerations, see Admission Webhook Good Practices .
Kubernetes audit logging provides a security-relevant, chronological set of records documenting the sequence of actions in a cluster. The cluster audits the activities generated by users, by applications that use the Kubernetes API, and by the control plane itself. If you are running a Kubernetes cluster on your own hardware or a different cloud provider, consult your documentation for security best practices. Here are links to some of the popular cloud providers' security documentation: You can define security policies using Kubernetes-native mechanisms, such as NetworkPolicy (declarative control over network packet filtering) or ValidatingAdmissionPolicy (declarative restrictions on what changes someone can make using the Kubernetes API).
However, you can also rely on policy implementations from the wider ecosystem around Kubernetes. Kubernetes provides extension mechanisms to let those ecosystem projects implement their own policy controls on source code review, container image approval, API access controls, networking, and more. Thanks for the feedback. If you have a specific, answerable question about how to use Kubernetes, ask it on Stack Overflow .
Open an issue in the GitHub Repository if you want to report a problem or suggest an improvement . Items on this page refer to third party products or projects that provide functionality required by Kubernetes. The Kubernetes project authors aren't responsible for those third-party products or projects. See the CNCF website guidelines for more details. You should read the content guide before proposing a change that adds an extra third-party link.
Learn how to create a Kubernetes security policy to safeguard your cluster. Explore key components, best practices, and SentinelOne solutions to enhance your security framework. Kubernetes has become the go-to platform for managing containerized applications. But its flexibility and scalability come with a huge responsibility: securing the infrastructure of your business. implementing a robust Kubernetes Security Policy is one of the most important steps to protect your cluster and workloads from the threats that abound in the wild.
In this post, we’ll cover the key components of a Kubernetes security policy, how to implement them, and the best practices for safeguarding your cluster. We’ll also touch on SentinelOne’s Kubernetes security solutions to give you an idea of the tools available to bolster your security framework. A Kubernetes security policy refers to the guidelines and rules that help you secure your Kubernetes clusters, ensuring that your workloads and the infrastructure itself are protected. A well-defined security policy mitigates risks like unauthorized access, data leaks, and runtime threats.
Without a proper security policy, Kubernetes clusters become prime targets for attackers. Security vulnerabilities can expose sensitive data, disrupt services, or even bring down the entire infrastructure. Since Kubernetes dynamically manages workloads and scales across multiple nodes, a breach at any level could have devastating consequences. Organizations often overlook Kubernetes security in favor of speed and innovation. However, leaving security as an afterthought exposes your clusters to potential threats. The complexity of Kubernetes makes securing it challenging, but setting up clear security policies will ensure you’re protected across all layers.
5. Performance Evaluation & Extended Technical Observations Kubernetes security is not just one-dimensional. A comprehensive security policy touches on multiple aspects, including pods, networking, access control, and multiple monitoring fronts. Let’s explore the key components of a Kubernetes security policy. Pod Security Policies are used to define the security-related conditions under which a pod can operate in a Kubernetes cluster. This includes setting rules around privileges escalation, host filesystem access, and running containers as root.
Network policies define how pods can communicate with each other and with external services. you can use them to limit inter-pod communication to only what is necessary, thereby reducing the attack surface of your cluster. RBAC allows you to control who can access and modify resources in your Kubernetes cluster. You can assign roles to users, service accounts, and other entities, ensuring that only authorized personnel have the ability to interact with sensitive resources.
Runtime security policies monitor the behavior of your containers and take action when anomalies are detected. This includes preventing container escapes, blocking malicious behavior, and quarantining compromised containers. Managing secrets (like API keys, passwords, and certificates) securely is crucial in security. Kubernetes provides a built-in mechanism to store secrets, but misconfigurations can lead to data exposure. Integrating robust secret management practices into your security policy helps prevent these issues.
Continuous security monitoring and auditing allow you to detect unusual activities, misconfigurations, and breaches. Setting up automated alerting and logging systems can help you respond quickly to incidents before they escalate. Now that we’ve discussed the key components of Kubernetes security policies, let’s dive deeper into how you can implement these policies within your cluster.
Pod Security Policies (PSP) are essential for controlling how pods are deployed within your cluster. PSPs allow administrators to enforce security configurations, such as: Pod Security Policies are being deprecated in favor of Pod Security Standards (PSS). PSS simplifies policy enforcement by introducing three predefined standards: privileged, baseline, and restricted. As PSPs are phased out, transitioning to PSS ensures continued security for your pods.
Network policies in Kubernetes help you define how pods interact with each other and external services. By default, Kubernetes allows unrestricted pod-to-pod communication, which can be dangerous in a multi-tenant environment. You can create network policies that specify which pods are allowed to communicate with each other and under what conditions. For example, you can restrict traffic between sensitive workloads and limit access to critical services.
RBAC allows you to define roles and assign permissions to users, groups, and service accounts. This ensures that only authorized users can perform specific actions within your cluster. To configure RBAC, you need to create Role or ClusterRole objects that define permissions, then bind these roles to users or service accounts using RoleBindings or ClusterRoleBindings.
Auditing RBAC policies regularly ensures that permissions are up-to-date and secure. Use tools like Open Policy Agent (OPA) to enforce and validate RBAC configurations. Even after securing pod deployment and network access, runtime threats like container escapes and privilege escalations can compromise your cluster. Implementing runtime security measures ensures that containers behave as expected and don’t become vectors for attacks.
Use runtime security tools to enforce security controls within containers. These tools monitor syscalls, detect anomalies, and prevent unauthorized actions in real-time. Mismanaged secrets can expose your sensitive data to attackers. Kubernetes provides the Secret object to securely store things like API keys and passwords, but there are additional best practices you should follow.
Kubernetes allows you to store secrets as base64-encoded strings. you can also integrate external tools like HashiCorp Vault or AWS Secrets Manager for more robust secrets management. Continuous monitoring tools like Prometheus and Grafana can help track the performance and security of your Kubernetes cluster. It’s important to set up alerts for unusual activities like failed authentication attempts or suspicious network traffic.
Audit logs provide valuable insight into the security state of your cluster. Tools like Fluentd can help you collect and analyze these logs to detect issues. If you detect a security breach, take immediate action to contain the damage. Isolate affected pods, revoke compromised credentials, and start forensic analysis to determine the cause of the breach.
To ensure long-term security in your Kubernetes environment, it’s important to follow best practices. Beyond what has been already described in the security policy section above, here are a few more important best practices to follow: SentinelOne is a cybersecurity platform that focuses on endpoint security , detection, and response. When it comes to Kubernetes security, SentinelOne offers a policy-based way to secure the environment on Kubernetes. Here is an overview of SentinelOne’s Kubernetes security policy in brief: The following are kinds of policies supported by SentinelOne to ensure security for Kubernetes The overall effectiveness of SentinelOne’s Kubernetes Security Policy is an end-to-end automated security solution for Kubernetes environments, guaranteeing compliance and instant threat detection with response in place.
AI-powered cloud workload protection (CWPP) for servers, VMs, and containers, that detects and stops runtime threats in real time. Kubernetes is a powerful platform, but it comes with security challenges. By defining and implementing a robust Kubernetes security policy, you can protect your cluster from various threats. From Pod Security Policies to continuous monitoring, each aspect of the policy works together to safeguard your workload.
Discover how AI-powered cloud security can protect your organization in a one-on-one demo with a SentinelOne product expert. Kubernetes security policies cover several aspects like Pod Security Policies (PSP), Network Policies, Role-Based Access Control (RBAC), Runtime Security Policies, Secrets Management, and Security Monitoring and Auditing.
A Kubernetes Pod Security Policy (PSP) is a security resource that controls the security-related aspects of how pods are deployed within a cluster. It restricts things like privilege escalation, root user access, and access to host files. Security in Kubernetes is about protecting your cluster, workloads, and data from threats. Kubernetes provides many security features, but security requires a defense-in-depth approachâIImultiple layers of protection working together. Think of it like a castle: you need strong walls (network policies), guards at the gates (authentication), careful access control (authorization), and monitoring for threats (audit logs).
Each layer provides protection, and together they create a comprehensive security posture. Secure Pods - Run containers as non-root, drop capabilities, use read-only filesystems Securing a Kubernetes cluster requires a layered approach -- no single mechanism provides complete protection. This guide covers the essential security layers for production clusters, from network segmentation to supply chain integrity.
The principle of defense in depth means that even if one security layer is bypassed, others continue to protect the system. In Kubernetes, the key layers are: Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Kubernetes • https://en.wikipedia.org/wiki/Cilium%20%28computing%29 • https://en.wikipedia.org/wiki/Google%20Cloud%20Platform • https://policyascode.dev/guides/kubernetes-governance/ • https://tech-insider.org/kubernetes-security-hardening-2026/ • https://k8s.guru/docs/security/policy-enforcement/ • https://binadit.com/tutorials/implement-kubernetes-pod-security-standards-and-admission-controllers • https://kubernetes.io/docs/concepts/security/ • https://www.sentinelone.com/cybersecurity-101/cloud-security/kubernetes-security-policy/ • https://k8s.guru/docs/security/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Kubernetes Security Policy Enforcement Tool Project.
[*] Metasploit Scan Running on Target Subnet for Kubernetes Security Policy Enforcement Tool Project... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |