Complete Technical Paper Content — Linux Privilege Escalation Auditing Script In Bash
Overview & System Context
Linux Privilege Escalation Auditing Script In Bash: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8148 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Linux malware includes viruses, Trojans, worms and other types of malware that affect the Linux family of operating systems.
Linux, Unix and other Unix-like computer operating systems are generally regarded as very well-protected against, but not immune to, computer viruses. [That argument] ignores Unix's dominance in a number of non-desktop specialties, including Web servers and scientific workstations. A virus/trojan/worm author who successfully targeted specifically Apache httpd Linux/x86 Web servers would both have an extremely target-rich environment and instantly earn lasting fame, and yet it doesn't happen. In 2008 the quantity of malware targeting Linux was noted as increasing. Shane Coursen, a senior technical consultant with Kaspersky Lab, said at the time, "The growth in Linux malware is simply due to its increasing popularity, particularly as a desktop operating system ... The use of an operating system is directly correlated to the interest by the malware writers to develop malware for that OS." Tom Ferris, a researcher with Security Protocols, commented on one of Kaspersky's reports, stating, "In people's minds, if it's non-Windows, it's secure, and that's not the case. They think nobody writes malware for Linux or Mac OS X. But that's not necessarily true." Some Linux users do run Linux-based anti-virus software to scan insecure documents and email which comes from or is going to Windows users. SecurityFocus's Scott Granneman stated: ...some Linux machines definitely need anti-virus software. Samba or NFS servers, for instance, may store documents in undocumented, vulnerable Microsoft formats, such as Word and Excel, that contain and propagate viruses. Linux mail servers should run AV software in order to neutralize viruses before they show up in the mailboxes of Outlook and Outlook Express users. Because they are predominantly used on mail servers which may send mail to computers running other operating systems, Linux virus scanners generally use definitions for, and scan for, all known viruses for all computer platforms. For example, the open source ClamAV "Detects ... viruses, worms and trojans, including Microsoft Office macro viruses, mobile malware, and other threats." Cases of malware intended for Microsoft Windows systems posing a danger to Linux systems when run through compatibility layers such as Wine, while uncommon, have been recorded.
The viruses listed below pose a potential, although minimal, threat to Linux systems. If an infected binary containing one of the viruses were run, the system would be temporarily infected, as the Linux kernel is memory resident and read-only. Any infection level would depend on which user with what privileges ran the binary. A binary run under the root account would be able to infect the entire system. Privilege escalation vulnerabilities may permit malware running under a limited account to infect the entire system. This is true for any malicious program that is run without special steps taken to limit its privileges. It is trivial to add a code snippet to any program that a user may download and let this additional code download a modified login server, an open mail relay, or similar program, and make this additional component run any time the user logs in. No special malware writing skills are needed for this. Special skill may be needed for tricking the user to run the (trojan) program in the first place. The use of software repositories significantly reduces any threat of installation of malware, as the software repositories are checked by maintainers, who try to ensure that their repository is malware-free. Subsequently, to ensure safe distribution of the software, checksums are made available. These make it possible to reveal modified versions that may have been introduced by e.g. hijacking of communications using a man-in-the-middle attack or via a redirection attack such as ARP or DNS poisoning. Careful use of these digital signatures provides an additional line of defense, which limits the scope of attacks to include only the original authors, package and release maintainers and possibly others with suitable administrative access, depending on how the keys and checksums are handled. Reproducible builds can ensure that digitally signed source code has been reliably transformed into a binary application.
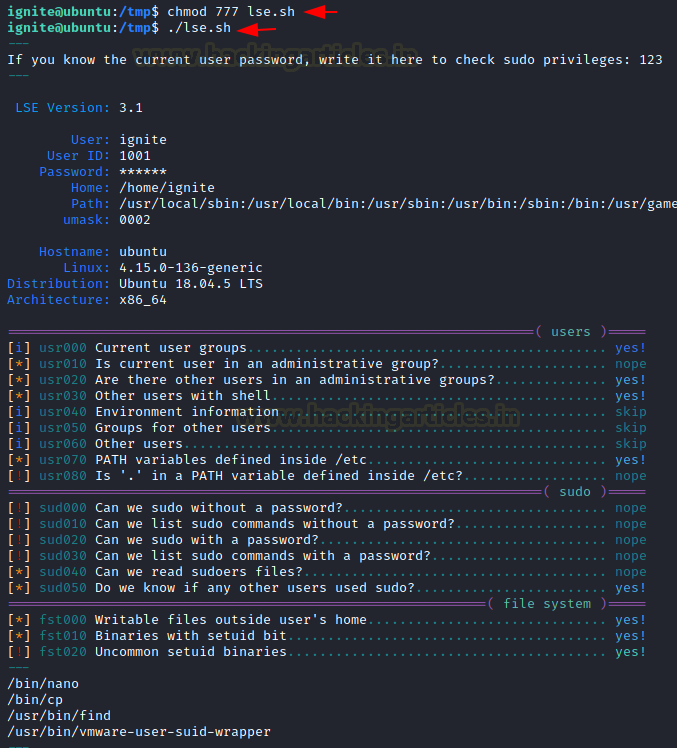
Figure 1: Linux Privilege Escalation: Automated Script - Hacking Articles The classical threat to Unix-like systems are vulnerabilities in network daemons, such as SSH and web servers. These can be used by worms or for attacks against specific targets. As servers are patched quite quickly when a vulnerability is found, there have been only a few widespread worms of this kind. As specific targets can be attacked through a vulnerability that is not publicly known there is no guarantee that a certain installation is secure. Also servers without such vulnerabilities can be successfully attacked through weak passwords.
Older Linux distributions were relatively sensitive to buffer overflow attacks: if the program did not care about the size of the buffer itself, the kernel provided only limited protection, allowing an attacker to execute arbitrary code under the rights of the vulnerable application under attack. Programs that gain root access even when launched by a non-root user (via the setuid bit) were particularly attractive to attack. However, as of 2009 most of the kernels include address space layout randomization (ASLR), enhanced memory protection and other extensions making such attacks much more difficult to arrange.
What makes this virus worth mentioning is that it illustrates how easily scripting platforms, extensibility, plug-ins, ActiveX, etc, can be abused. All too often, this is forgotten in the pursuit to match features with another vendor... The ability for malware to survive in a cross-platform, cross-application environment has particular relevance as more and more malware is pushed out via Web sites. How long until someone uses something like this to drop a JavaScript infecter on a Web server, regardless of platform? There are a number of anti-virus applications available which will run under the Linux operating system. Most of these applications are looking for exploits which could affect users of Microsoft Windows.
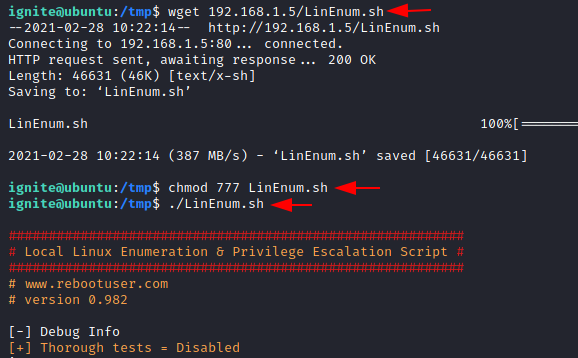
Figure 2: Linux Privilege Escalation: Automated Script - Hacking Articles chkrootkit (free and open source software) ClamAV (free and open source software) Comodo (proprietary) Crowdstrike (proprietary) Dr.Web (proprietary) ESET (proprietary) Kaspersky Virus Removal Tool (KVRT) for Linux (free) Linux Malware Detect lynis (open source auditing) rkhunter (free and open source software) Samhain (free and open source software) Sophos (proprietary) Linux malware can also be detected (and analyzed) using memory forensics tools, such as: Hydra, Aidra, LightAidra and NewAidra – another form of a powerful IRC botnet that infects Linux boxes. EnergyMech 2.8 overkill mod (Linux/Overkill) – a long-lasting botnet worm designed to infect servers with its bot and operated through IRC protocol, for the purposes of DDoSing and spreading itself.
BackTrack was a Linux distribution that focused on security, based on the Knoppix Linux distribution aimed at digital forensics and penetration test use. In March 2013, the Offensive Security team rebuilt BackTrack around the Debian distribution and released it under the name Kali Linux. WHAX: a Slax-based Linux distribution developed by Mati Aharoni, a security consultant. Earlier versions of WHAX were called Whoppix and were based on Knoppix. Auditor Security Collection: a Live CD based on Knoppix developed by Max Moser which included over 300 tools organized in a user-friendly hierarchy. On January 9, 2010, BackTrack 4 improved hardware support, and added official FluxBox support. The overlap with Auditor and WHAX in purpose and in collection of tools partly led to the merger. The overlap came about as Backtrack 5, released on May 10, 2011. This version also seen the base OS changed from Slackware to Ubuntu.
Figure 3: GitHub - xpinux/xpinaudit-tool: This is a Bash script that performs a ... Metasploit for integration Wi-Fi drivers supporting monitor mode (rfmon mode) and packet injection Aircrack-ng Reaver, a tool used to exploit a vulnerability in WPS Gerix Wifi Cracker Kismet Nmap Ophcrack Ettercap Wireshark (formerly known as Ethereal) BeEF (Browser Exploitation Framework) Hydra OWASP Mantra Security Framework, a collection of hacking tools, add-ons and scripts based on Firefox Cisco OCS Mass Scanner, a very reliable and fast scanner for Cisco routers to test default telnet and enabling password. A large collection of exploits as well as more commonplace software such as browsers.
Armitage - java-based front-end to Metasploit. BackTrack arranged tools into 12 categories: Information gathering Vulnerability assessment Exploitation tools Privilege escalation Maintaining access Reverse engineering RFID tools Stress testing Forensics Reporting tools Services Miscellaneous Whenever a new version of BackTrack was released, older versions would lose their support and service from the BackTrack development team. There are currently no supported versions of BackTrack.
OpenVMS, often referred to as just VMS, is a multi-user, multiprocessing and virtual memory-based operating system. It is designed to support time-sharing, batch processing, transaction processing and workstation applications. Customers using OpenVMS include banks and financial service providers, hospitals and healthcare providers, telecommunications operators, network information services, and industrial manufacturers. During the 1990s and 2000s, there were approximately half a million VMS systems in operation worldwide. It was first announced by Digital Equipment Corporation (DEC) as VAX/VMS (Virtual Address eXtension/Virtual Memory System) alongside the VAX-11/780 minicomputer in 1977. OpenVMS has subsequently been ported to run on DEC Alpha systems, the Itanium-based HPE Integrity Servers, and select x86-64 hardware and hypervisors. Since 2014, OpenVMS is developed and supported by VMS Software Inc. (VSI). OpenVMS offers high availability through clustering—the ability to distribute the system over multiple physical machines. This allows clustered applications and data to remain continuously available while operating system software and hardware maintenance and upgrades are performed, or if part of the cluster is destroyed. VMS cluster uptimes of 17 years have been reported.
In April 1975, Digital Equipment Corporation (DEC) embarked on a project to design a 32-bit extension to its PDP-11 computer line. The hardware component was code named Star; the operating system was code named Starlet. Roger Gourd was the project lead for VMS. Software engineers Dave Cutler, Dick Hustvedt, and Peter Lipman acted as technical project leaders. To avoid a repetition of PDP-11's many incompatible operating systems, the new operating system would be capable of real-time, time-sharing, and transaction processing. The Star and Starlet projects culminated in the VAX-11/780 computer and the VAX/VMS operating system. The Starlet project's code name survives in VMS in the name of several of the system libraries, including STARLET.OLB and STARLET.MLB. VMS was mostly written in VAX MACRO with some components written in BLISS. One of the original goals for VMS was backward compatibility with DEC's existing RSX-11M operating system. Prior to the V4.0 release, VAX/VMS included a compatibility layer named the RSX Application Migration Executive (RSX AME), which allowed user-mode RSX-11M software to be run unmodified on top of VMS. The RSX AME played an important role on early versions of VAX/VMS, which used certain RSX-11M user-mode utilities before native VAX versions had been developed. By the V3.0 release, all compatibility-mode utilities were replaced with native implementations. In VAX/VMS V4.0, RSX AME was removed from the base system, and replaced with an optional layered product named VAX-11 RSX.
By the early 1980s VAX/VMS was very successful in the market. Although created on Unix on DEC systems, Ingres ported to VMS believing that doing so was necessary for commercial success. Demand for the VMS version was so much greater that the company neglected the Unix version. A number of distributions of VAX/VMS were created: MicroVMS was a distribution of VAX/VMS designed for MicroVAX and VAXstation hardware, which had less memory and disk space than larger VAX systems of the time. MicroVMS split up VAX/VMS into multiple kits, which a customer could use to install a subset of VAX/VMS tailored to their specific requirements. MicroVMS releases were produced for each of the V4.x releases of VAX/VMS and was discontinued when VAX/VMS V5.0 was released. Desktop-VMS was a short-lived distribution of VAX/VMS sold with VAXstation systems. It consisted of a single CD-ROM containing a bundle of VMS, DECwindows, DECnet, VAXcluster support, and a setup process designed for non-technical users. Desktop-VMS could either be run directly from the CD or could be installed onto a hard drive. Desktop-VMS had its own versioning scheme beginning with V1.0, which corresponded to the V5.x releases of VMS. An unofficial derivative of VAX/VMS named MOS VP (Russian: IIIIIIIIIIIIIIIIIII IIIIIIIIIIII IIIIIII I IIIIIIIIIII IIIIIII, III II, lit.
'Multifunctional Operating System with Virtual Memory') was created in the Soviet Union during the 1980s for the SM 1700 line of VAX clone hardware. MOS VP added support for the Cyrillic script and translated parts of the user interface into Russian. Similar derivatives of MicroVMS known as MicroMOS VP (Russian: IIIIIIII II) or MOS-32M (Russian: III-32I) were also created. With the V5.0 release in April 1988, DEC began to refer to VAX/VMS as simply VMS in its documentation.
In July 1992, DEC renamed VAX/VMS to OpenVMS as an indication of its support of open systems industry standards such as POSIX and Unix compatibility, and to drop the VAX connection since a migration to a different architecture was underway. The OpenVMS name was first used with the OpenVMS AXP V1.0 release in November 1992. DEC began using the OpenVMS VAX name with the V6.0 release in June 1993.
During the 1980s, DEC planned to replace the VAX platform and the VMS operating system with the PRISM architecture and the MICA operating system. When these projects were cancelled in 1988, a team was set up to design new VAX/VMS systems of comparable performance to RISC-based Unix systems. After a number of failed attempts to design a faster VAX-compatible processor, the group demonstrated the feasibility of porting VMS and its applications to a RISC architecture based on PRISM. This led to the creation of the Alpha architecture. The project to port VMS to Alpha began in 1989, and first booted on a prototype Alpha EV3-based Alpha Demonstration Unit in early 1991. The main challenge in porting VMS to a new architecture was that VMS and the VAX were designed together, meaning that VMS was dependent on certain details of the VAX architecture. Furthermore, a significant amount of the VMS kernel, layered products, and customer-developed applications were implemented in VAX MACRO assembly code. Some of the changes needed to decouple VMS from the VAX architecture included the creation of the MACRO-32 compiler, which treated VAX MACRO as a high-level language, and compiled it to Alpha object code, and the emulation of certain low-level details of the VAX architecture in PALcode, such as interrupt handling and atomic queue instructions. The VMS port to Alpha resulted in the creation of two separate codebases: one for VAX, and another for Alpha. The Alpha code library was based on a snapshot of the VAX/VMS code base circa V5.4-2. 1992 saw the release of the first version of OpenVMS for Alpha AXP systems, designated OpenVMS AXP V1.0. In 1994, with the release of OpenVMS V6.1, feature (and version number) parity between the VAX and Alpha variants was achieved; this was the so-called Functional Equivalence release. The decision to use the 1.x version numbering stream for the pre-production quality releases of OpenVMS AXP confused some customers, and was not repeated in the subsequent ports of OpenVMS to new platforms. When VMS was ported to Alpha, it was initially left as a 32-bit only operating system. This was done to ensure backwards compatibility with software written for the 32-bit VAX. 64-bit addressing was first added for Alpha in the V7.0 release. In order to allow 64-bit code to interoperate with older 32-bit code, OpenVMS does not create a distinction between 32-bit and 64-bit executables, but instead allows for both 32-bit and 64-bit pointers to be used within the same code.
This is known as mixed pointer support. The 64-bit OpenVMS Alpha releases support a maximum virtual address space size of 8TiB (a 43-bit address space), which is the maximum supported by the Alpha 21064 and Alpha 21164. One of the more noteworthy Alpha-only features of OpenVMS was OpenVMS Galaxy, which allowed the partitioning of a single SMP server to run multiple instances of OpenVMS. Galaxy supported dynamic resource allocation to running partitions, and the ability to share memory between partitions.
In 2001, prior to its acquisition by Hewlett-Packard, Compaq announced the port of OpenVMS to the Intel Itanium architecture. The Itanium port was the result of Compaq's decision to discontinue future development of the Alpha architecture in favour of adopting the then-new Itanium architecture. The porting began in late 2001, and the first boot on took place on January 31, 2003. The first boot consisted of booting a minimal system configuration on a HP i2000 workstation, logging in as the SYSTEM user, and running the DIRECTORY command. The Itanium port of OpenVMS supports specific models and configurations of HPE Integrity Servers. The Itanium releases were originally named HP OpenVMS Industry Standard 64 for Integrity Servers, although the names OpenVMS I64 or OpenVMS for Integrity Servers are more commonly used. The Itanium port was accomplished using source code maintained in common within the OpenVMS Alpha source code library, with the addition of conditional code and additional modules where changes specific to Itanium were required. This required certain architectural dependencies of OpenVMS to be replaced, or emulated in software. Some of the changes included using the Extensible Firmware Interface (EFI) to boot the operating system, reimplementing the functionality previously provided by Alpha PALcode inside the kernel, using new executable file formats (Executable and Linkable Format and DWARF), and adopting IEEE 754 as the default floating point format. As with the VAX to Alpha port, a binary translator for Alpha to Itanium was made available, allowing user-mode OpenVMS Alpha software to be ported to Itanium in situations where it was not possible to recompile the source code. This translator is known as the Alpha Environment Software Translator (AEST), and it also supported translating VAX executables which had already been translated with VEST. Two pre-production releases, OpenVMS I64 V8.0 and V8.1, were available on June 30, 2003, and on December 18, 2003. These releases were intended for HP organizations and third-party vendors involved with porting software packages to OpenVMS I64. The first production release, V8.2, was released in February 2005. V8.2 was also released for Alpha; subsequent V8.x releases of OpenVMS have maintained feature parity between the Alpha and Itanium architectures.
The OpenVMS operating system has a layered architecture, consisting of a privileged Executive, an intermediately privileged Command Language Interpreter, and unprivileged utilities and run-time libraries (RTLs). Unprivileged code typically invokes the functionality of the Executive through system services (equivalent to system calls in other operating systems). OpenVMS' layers and mechanisms are built around certain features of the VAX architecture, including: The availability of four processor access modes (named Kernel, Executive, Supervisor and User, in order of decreasing privilege). Each mode has its own stack, and each memory page can have memory protections specified per-mode. A virtual address space which is partitioned between process-private space sections, and system space sections which are common to all processes. 32 interrupt priority levels which are used for synchronization. Hardware support for delivering asynchronous system traps to processes. These VAX architecture mechanisms are implemented on Alpha, Itanium and x86-64 by either mapping to corresponding hardware mechanisms on those architectures, or through emulation (via PALcode on Alpha, or in software on Itanium and x86-64).
The typical user and application interface into the file system is the Record Management Services (RMS), although applications can interface directly with the underlying file system through the QIO system services. The file systems supported by VMS are referred to as the Files-11 On-Disk Structures (ODS), the most significant of which are ODS-2 and ODS-5. VMS is also capable of accessing files on ISO 9660 CD-ROMs and magnetic tape with ANSI tape labels. Files-11 is limited to 2 TiB volumes. DEC attempted to replace it with a log-structured file system named Spiralog, first released in 1995. However, Spiralog was discontinued due to a variety of problems, including issues with handling full volumes. Instead, there has been discussion of porting the open-source GFS2 file system to OpenVMS.
OpenVMS supports clustering (first called VAXcluster and later VMScluster), where multiple computers run their own instance of the operating system. Clustered computers (nodes) may be fully independent from each other, or they may share devices like disk drives and printers. Communication across nodes provides a single system image abstraction. Nodes may be connected to each other via a proprietary hardware connection called Cluster Interconnect or via a standard Ethernet LAN.
OpenVMS supports up to 96 nodes in a single cluster. It also allows mixed-architecture clusters. OpenVMS clusters allow applications to function during planned or unplanned outages. Planned outages include hardware and software upgrades. The DECnet protocol suite is tightly integrated into VMS, allowing remote logins, as well as transparent access to files, printers and other resources on VMS systems over a network. VAX/VMS V1.0 featured support for DECnet Phase II, and modern versions of VMS support both the traditional Phase IV DECnet protocol, as well as the OSI-compatible Phase V (also known as DECnet-Plus). Support for TCP/IP is provided by the optional TCP/IP Services for OpenVMS layered product (originally known as the VMS/ULTRIX Connection, then as the ULTRIX Communications Extensions or UCX). TCP/IP Services is based on a port of the BSD network stack to OpenVMS, along with support for common protocols such as SSH, DHCP, FTP and SMTP. DEC sold a software package named PATHWORKS (originally known as the Personal Computer Systems Architecture or PCSA) which allowed personal computers running MS-DOS, Microsoft Windows or OS/2, or the Apple Macintosh to serve as a terminal for VMS systems, or to use VMS systems as a file or print server. PATHWORKS was later renamed to Advanced Server for OpenVMS, and was eventually replaced with a VMS port of Samba at the time of the Itanium port. DEC provided the Local Area Transport (LAT) protocol which allowed remote terminals and printers to be attached to a VMS system through a terminal server such as one of the DECserver family.
Among OpenVMS's notable features is the Common Language Environment, a strictly defined standard that specifies calling conventions for functions and routines, including use of stacks, registers, etc., independent of programming language. Because of this, it is possible to call a routine written in one language (for example, Fortran) from another (for example, COBOL), without needing to know the implementation details of the target language. OpenVMS itself is implemented in a variety of different languages and the common language environment and calling standard supports freely mixing these languages. DEC created a tool named the Structure Definition Language (SDL), which allowed data type definitions to be generated for different languages from a common definition. The set of languages available directly with the operating system is restricted to C, Fortran, Pascal, BASIC, C++, BLISS and COBOL. Freely available open source languages include Lua, PHP, Python, Scala and Java.
DEC provided a collection of software development tools in a layered product named DECset (originally named VAXset). This consisted of the following tools: Language-Sensitive Editor (LSE) Code Management System (CMS) a version control system Module Management System (MMS), a build tool the Source Code Analyzer (SCA), a static analyzer the Performance and Coverage Analyzer (PCA), a profiler Digital Test Manager (DTM), as a test manager In addition, a number of text editors are included in the operating system, including EDT, EVE and TECO. The OpenVMS Debugger supports all DEC compilers and many third-party languages. It allows breakpoints, watchpoints and interactive runtime program debugging using either a command line or graphical user interface. A pair of lower-level debuggers, named DELTA and XDELTA, can be used to debug privileged code in additional to normal application code. In 2019, VSI released an officially supported Integrated Development Environment for VMS based on Visual Studio Code. This allows VMS applications to be developed and debugged remotely from a Microsoft Windows, macOS or Linux workstation.
Rdb – A relational database system which originally used the proprietary Relational Data Operator (RDO) query interface, but later gained SQL support. DBMS – A database management system which uses the CODASYL network model and Data Manipulation Language (DML). Digital Standard MUMPS (DSM) – an integrated programming language and key-value database. Common Data Dictionary (CDD) – a central database schema repository, which allowed schemas to be shared between different applications, and data definitions to be generated for different programming languages. DATATRIEVE – a query and reporting tool which could access data from RMS files as well as Rdb and DBMS databases. Application Control Management System (ACMS) – A transaction processing monitor, which allows applications to be created using a high-level Task Description Language (TDL). Individual steps of a transaction can be implemented using DCL commands, or Common Language Environment procedures. User interfaces can be implemented using TDMS, DECforms or Digital's ALL-IN-1 office automation product. RALLY, DECadmire – Fourth-generation programming languages (4GLs) for generating database-backed applications. DECadmire featured integration with ACMS, and later provided support for generating Visual Basic client-server applications for Windows PCs. In 1994, DEC sold Rdb, DBMS and CDD to Oracle, where they remain under active development. In 1995, DEC sold DSM to InterSystems, who renamed it Open M, and eventually replaced it with their Caché product. Examples of third-party database management systems for OpenVMS include MariaDB, Mimer SQL (Itanium and x86-64), and System 1032.
2. System Architecture & Core Working Principles VMS was originally designed to be used and managed interactively using DEC's text-based video terminals such as the VT100, or hardcopy terminals such as the DECwriter series. Since the introduction of the VAXstation line in 1984, VMS has optionally supported graphical user interfaces for use with workstations or X terminals such as the VT1000 series.
The DIGITAL Command Language (DCL) has served as the primary command language interpreter (CLI) of OpenVMS since the first release. Other official CLIs available for VMS include the RSX-11 Monitor Console Routine (MCR) (VAX only), and various Unix shells. DEC provided tools for creating text-based user interface applications – the Form Management System (FMS) and Terminal Data Management System (TDMS), later succeeded by DECforms. A lower level interface named Screen Management Services (SMG$), comparable to Unix curses, also exists.
The original graphical user interface for VMS was a proprietary windowing system known as the VMS Workstation Software (VWS), which was first released for the VAXstation I in 1984. It exposed an API called the User Interface Services (UIS). It ran on a limited selection of VAX hardware. In 1989, DEC replaced VWS with a new X11-based windowing system named DECwindows. It was first included in VAX/VMS V5.1. Early versions of DECwindows featured an interface built on top of a proprietary toolkit named the X User Interface (XUI). A layered product named UISX was provided to allow VWS/UIS applications to run on top of DECwindows. Parts of XUI were subsequently used by the Open Software Foundation as the foundation of the Motif toolkit. In 1991, DEC replaced XUI with the Motif toolkit, creating DECwindows Motif. As a result, the Motif Window Manager became the default DECwindows interface in OpenVMS V6.0, although the XUI window manager remained as an option. In 1996, as part of OpenVMS V7.1, DEC released the New Desktop interface for DECwindows Motif, based on the Common Desktop Environment (CDE). On Alpha and Itanium systems, it is still possible to select the older MWM-based UI (referred to as the "DECwindows Desktop") at login time. The New Desktop was never ported to the VAX releases of OpenVMS. Versions of VMS running on DEC Alpha workstations in the 1990s supported OpenGL and Accelerated Graphics Port (AGP) graphics adapters. VMS also provides support for older graphics standards such as GKS and PHIGS. Modern versions of DECwindows are based on X.Org Server.
VMS Software: Current Roadmap and Future Releases VMS Software: Documentation HP OpenVMS FAQ at the Wayback Machine (archived January 12, 2020) comp.os.vms Usenet group, archives on Google Groups An interactive Bash-based system audit tool designed to perform basic security and system checks on Linux machines. This script is intended for learning, security auditing, and SOC fundamentals practice .
Linux system audit Bash script with interactive menu, privilege escalation checks, open ports detection, and security reporting. A comprehensive collection of Linux privilege escalation techniques, vectors, and exploitation methods for penetration testing and security auditing. This repository contains detailed notes on various Linux privilege escalation techniques, from misconfigurations to kernel exploits. Each section includes enumeration methods, exploitation techniques, and defensive measures.
A curated collection of Linux privilege escalation techniques, enumeration methods, and exploitation strategies for penetration testing and security auditing. LinPEAS is a widely used security auditing script designed to identify potential privilege escalation vectors on Linux systems. It is part of the PEASS-ng toolkit and is trusted by penetration testers, security researchers, and ethical hackers worldwide to perform deep system enumeration efficiently.
LinPEAS (Linux Privilege Escalation Awesome Script) is a powerful, automated post-exploitation enumeration tool designed to identify potential privilege escalation vectors on Linux systems. It performs an extensive audit of the target environment, scanning for misconfigurations, weak permissions, exposed sensitive data, and known security flaws that could be leveraged to gain elevated access.
It is commonly used during post-exploitation phases of penetration testing and Capture The Flag (CTF) challenges. The script provides color-coded output to help users quickly identify high-risk findings. LinPEAS performs a thorough analysis of the Linux system by examining installed packages, running services, environment variables, user accounts, and system configurations. It organizes the collected information into a structured output, helping security professionals quickly assess the system and identify potential misconfigurations or weaknesses.
LinPEAS identifies potential privilege escalation vectors by scanning for SUID and SGID binaries, weak file permissions, and insecure service configurations. It highlights critical findings that could allow unauthorized elevation of privileges, enabling penetration testers to prioritize high-risk vulnerabilities efficiently. LinPEAS searches for sensitive data such as hardcoded credentials, SSH keys, configuration files, and environment variables containing authentication details. This feature helps uncover insecure storage practices and exposes potential entry points that attackers may use to gain deeper access into the system.
LinPEAS evaluates scheduled tasks and cron jobs to detect insecure configurations and potential exploitation paths. It identifies scripts running with elevated privileges, checks for writable cron files, and highlights opportunities where attackers could inject malicious commands for privilege escalation or persistence. LinPEAS scans the filesystem to identify files and directories with weak or misconfigured permissions. It highlights writable or improperly secured resources, especially those owned by privileged users, helping security professionals detect potential vectors for unauthorized modification or privilege escalation.
LinPEAS analyzes the system’s kernel version and compares it against known vulnerabilities and exploit databases. It provides insights into potential kernel-level weaknesses, allowing penetration testers to determine whether privilege escalation can be achieved through publicly available exploits. Get the latest version from GitHub releases or use curl/wget to download directly to the target.
Run linpeas.sh with bash. No installation required it works out of the box on any Linux system. LinPEAS produces color-coded output highlighting different severity levels of findings. Use the identified vectors to escalate privileges during your authorized penetration test. LinPEAS is commonly used during penetration testing to automate system enumeration after gaining initial access. It helps testers quickly identify misconfigurations, weak permissions, and privilege escalation opportunities, allowing them to demonstrate real security risks effectively and efficiently.
LinPEAS supports security audits by scanning systems for vulnerabilities, insecure configurations, and permission issues. It provides valuable insights that help organizations strengthen their defenses, ensure compliance with security standards, and reduce the risk of unauthorized access. LinPEAS is widely used in cybersecurity training programs to teach students how to identify privilege escalation vectors. It provides hands-on experience with real-world scenarios, helping learners understand Linux security concepts and develop practical skills in ethical hacking.
In Capture The Flag challenges, LinPEAS helps participants quickly enumerate systems and uncover hidden vulnerabilities. It improves efficiency and accuracy during competitions, allowing users to focus on exploiting identified weaknesses and solving challenges within limited time constraints. Choosing the right security auditing tool is critical when working in Linux environments. LinPEAS has become a preferred choice among cybersecurity professionals because it combines depth, speed, and usability into a single, efficient script. Below are the key reasons why LinPEAS stands out.
LinPEAS performs extensive checks across the system to uncover misconfigurations, weak permissions, exposed credentials, and potential privilege escalation paths. It goes beyond basic enumeration by identifying both common and advanced security flaws. The tool is designed to run quickly without requiring complex installation. As a single script, LinPEAS can be executed in seconds, making it ideal for time-sensitive assessments and real-world penetration testing scenarios.
3. Software Implementation, Frameworks & Protocols One of LinPEAS’s strongest advantages is its color-coded output. Critical vulnerabilities are highlighted clearly, allowing users to quickly focus on high-risk issues without manually filtering large amounts of data. LinPEAS does not require installation or dependencies. Users can simply download the script, transfer it to a target system, and execute it, making it highly convenient for both beginners and professionals.
The tool is actively maintained and frequently updated to include new checks and techniques. This ensures it stays relevant against evolving security threats and modern Linux environments. LinPEAS is widely used in penetration testing, red teaming, and CTF challenges. Its reliability and effectiveness have made it a trusted tool within the global cybersecurity community.
Whether you are performing a vulnerability assessment, preparing for a certification, or securing a production server, LinPEAS adapts to different use cases with ease and efficiency. Being open-source, LinPEAS allows users to inspect, modify, and contribute to its code. This transparency not only builds trust but also encourages continuous improvement from the community.
When it comes to Linux privilege escalation and enumeration, several tools are available—but not all offer the same depth, usability, and efficiency. LinPEAS stands out due to its comprehensive scanning capabilities and user-friendly output. LinPEAS is a powerful security auditing tool intended strictly for ethical and authorized use. It is designed to help cybersecurity professionals, system administrators, and ethical hackers identify vulnerabilities and misconfigurations in Linux systems to improve overall security posture.
Users must only run LinPEAS on systems they own or have explicit permission to test. Unauthorized scanning, testing, or exploitation of systems without consent may violate local, national, or international laws and can result in serious legal consequences. The developers and contributors of LinPEAS are not responsible for any misuse, damage, or legal issues arising from improper use of the tool. It is the user’s responsibility to ensure compliance with all applicable laws and regulations.
Trusted by cybersecurity experts worldwide, LinPEAS delivers accurate, fast, and reliable insights to identify Linux privilege escalation vulnerabilities effectively. “LinPEAS has completely transformed how we perform Linux audits. It uncovers hidden vulnerabilities that manual checks often miss.” “As a red team operator, LinPEAS is one of my go-to tools. Its depth and speed are simply unmatched.” “The color-coded output makes analysis incredibly easy. Even complex privilege escalation paths become clear within minutes.” “We integrated LinPEAS into our internal security workflow, and it significantly improved our vulnerability detection process.” “Whether you’re a beginner or an expert, LinPEAS provides valuable insights that help strengthen Linux system security.” “LinPEAS consistently delivers reliable results. It’s an essential tool for anyone serious about Linux privilege escalation testing.” Find clear answers to common LinPEAS questions, covering installation, usage, features, safety, and best practices for effective Linux security auditing.
LinPEAS is a Linux privilege escalation auditing script used to identify misconfigurations and vulnerabilities in systems. LinPEAS is part of the PEASS-ng project, maintained by cybersecurity professionals and open-source contributors. It is used to detect potential privilege escalation paths during penetration testing and security assessments. Yes, beginners can use it, but basic Linux knowledge helps in understanding the results.
You have a shell on the target. It says lowpriv@target:~$ and you need it to say root@target:~# . That gap between unprivileged access and root is what privilege escalation is about. Every engagement, every box on Hack The Box, every OSCP exam machine has this phase. Initial foothold is just the beginning. This guide covers the techniques that consistently show up in real-world assessments, OSCP labs, and CTF challenges. We walk through SUID abuse, Linux capabilities, sudo misconfigurations, writable cron jobs, PATH hijacking, and automated enumeration with LinPEAS on a proper pentest lab . Every technique here was tested hands-on, with real command output captured from a vulnerable Debian 12 system.
The test system has several intentional misconfigurations: SUID binaries, a sudo entry with NOPASSWD, a writable cron script, and a binary with cap_setuid . These mirror what you find on OSCP exam machines and real-world servers that have been poorly hardened. Before touching anything else, gather context about where you landed. The first 30 seconds on a box should answer: who am I, what OS is this, and what’s running here? This tells you your UID, group memberships, the kernel version, and the hostname. The kernel version matters because certain kernel exploits only work on specific versions.
On our Debian 12 test box, this confirms bookworm with kernel 6.1. Knowing the exact distribution affects which exploits and package paths apply. Any user with /bin/bash or /bin/sh as their shell is worth investigating. Check if they have readable home directories, SSH keys, or history files with credentials.
Services listening on localhost (127.0.0.1) that aren’t exposed externally can be interesting. A MySQL instance on 127.0.0.1:3306 or a web admin panel on 127.0.0.1:8080 might have weak credentials. 4. Practical Deployment, Analysis & Case Studies Processes running as root are potential targets. If a root process reads from a file you can write to, or loads a library from a writable directory, that’s a vector.
A minimal server might have 200 packages. A desktop environment with hundreds of packages means more binaries to check for SUID bits, capabilities, and misconfigurations. While you’re gathering information, also check for Docker group membership and mounted filesystems: If your user is in the docker group, you can mount the host filesystem inside a container and read /etc/shadow or write SSH keys to /root/.ssh/ . The docker group is effectively root access. Same applies to the lxd group on Ubuntu systems.
Check for NFS shares with no_root_squash, which allows root on client machines to write as root on the NFS server: If you see no_root_squash on any export, you can mount it from your attack box, create a SUID binary as root, then execute it on the target. This is a classic OSCP vector. SUID (Set User ID) binaries execute with the permissions of the file owner, not the user who runs them. When a binary owned by root has the SUID bit set, it runs as root regardless of who invoked it. This is the single most common privilege escalation vector on Linux machines.
Most of these are standard system binaries ( passwd , mount , su , sudo ). The two that immediately stand out are /usr/local/bin/python3-suid and /usr/local/bin/find-suid . Anything in /usr/local/bin is non-standard, which means an admin installed it manually. That’s always worth investigating. Cross-reference every non-standard SUID binary against GTFOBins , the definitive reference for Unix binary exploitation.
GTFOBins documents how common binaries can be abused for privilege escalation when they have SUID, sudo, or capability permissions. The find command has an -exec flag that runs arbitrary commands. When find has the SUID bit and is owned by root, those commands run as root.
The -p flag tells bash to preserve the effective UID (root) instead of dropping privileges. Python with SUID is even more direct because you can call os.setuid(0) to switch to root, then spawn a shell: Languages like Python, Perl, and Ruby should never have the SUID bit set. They provide too much control over system calls. If you see any interpreted language binary with SUID, it’s almost certainly exploitable.
For SGID (Set Group ID) binaries, the concept is similar but you inherit the group rather than the user. Find them with: SGID escalation is less common but worth checking. If a binary runs with the shadow group, for instance, it can read /etc/shadow and you can extract password hashes for offline cracking with Hashcat or John the Ripper . Linux capabilities break the monolithic root privilege into fine-grained units. Instead of giving a binary full root access via SUID, an admin can assign specific capabilities. The problem is that some capabilities are just as dangerous as full root.
The ping binary with cap_net_raw is normal and expected. The dangerous one is python3-cap with cap_setuid=ep . The cap_setuid capability allows a process to change its UID to anything, including 0 (root). The ep suffix means the capability is both effective and permitted. The exploitation is identical to the SUID Python3 technique because cap_setuid allows the same os.setuid(0) call: If you find any of these on a binary you can execute, check GTFOBins for the specific exploitation technique.
This should be the very first thing you check on any target. If the current user has sudo permissions, you might be one command away from root. Many admins grant sudo access to specific binaries thinking it’s safe, without realizing those binaries can spawn shells. The user lowpriv can run vim as root without a password. This is a textbook misconfiguration. Vim (and vi) can execute shell commands from within the editor.
The -c flag executes a vim command on startup. The :! prefix runs an external command. The result: Root shell in one command. Alternatively, you can open vim first, then type :!/bin/bash inside the editor. These binaries are frequently misconfigured in sudo and can all be abused for shell access. Every one of them has an entry on GTFOBins with the exact exploitation command: The pattern here is clear: any binary that can execute subcommands or system calls is dangerous in a sudo context. When you see (root) NOPASSWD: followed by any of these, it’s almost always an instant root.
Cron jobs run on a schedule, and if they run as root while referencing a script you can write to, you can inject commands that execute as root the next time the job fires. Two things jump out. The cron job runs every minute as root. The script it executes is world-writable ( rwxrwxrwx ). Any user on the system can modify this script, and root will execute the modified version within 60 seconds.
To find other writable files that might be referenced by cron or other root processes: The cleanest exploitation technique is to append a command that creates a SUID copy of bash. This avoids reverse shells and gives you persistent root access: Wait for the cron job to fire (up to 60 seconds), then check if the SUID bash was created: 5. Performance Evaluation & Extended Technical Observations The euid=0(root) confirms effective root privileges. The -p flag is critical here because without it, bash drops the SUID privileges on startup.
In a real engagement, you would also want to clean up after yourself: remove the line you added to the cron script and delete /tmp/rootbash when done. Leaving SUID shells lying around is sloppy tradecraft. On modern Linux systems, passwords are stored in /etc/shadow which is readable only by root. But /etc/passwd still supports the legacy password field (the second column). If /etc/passwd is writable by your user, you can add a new user with UID 0.
This produces a hash like $1$evil$abc123... . Append a new root-equivalent user to /etc/passwd : Enter the password you chose (in this case password123 ), and you have root. This technique is rare on modern, properly configured systems because /etc/passwd is almost always owned by root with 644 permissions. It does appear on OSCP exam machines occasionally, and some older or embedded Linux systems have this misconfiguration.
PATH hijacking exploits SUID or root-owned binaries that call other programs without using their full path. If a SUID binary calls service instead of /usr/sbin/service , you can create a malicious service binary earlier in the PATH and it gets executed with root privileges. If you find that the binary calls, say, curl without the full path /usr/bin/curl , create a malicious version: Now execute the SUID binary. When it calls curl , it finds your malicious version first. The SUID bash gets created with root ownership, and you use /tmp/rootbash -p to get a root shell.
PATH hijacking appears frequently in CTF challenges and Hack The Box machines. In production environments, it’s less common because modern SUID binaries typically use absolute paths. Still worth checking, especially on custom in-house tools that weren’t written with security in mind. A variation of PATH hijacking involves shared library hijacking. If a SUID binary loads a shared library from a writable directory, you can replace that library with malicious code. Check what libraries a binary loads with: If any listed library path is in a directory you can write to, or if LD_LIBRARY_PATH is preserved across the SUID boundary (rare on modern systems), you have a vector. Create a malicious .so file that spawns a shell when loaded.
Manual enumeration is essential to understand, but in practice you want to run automated tools that check hundreds of vectors simultaneously. LinPEAS (Linux Privilege Escalation Awesome Script) is the gold standard. Transfer it to the target. If you have a web server on your attack box (10.0.1.50), the simplest method is: LinPEAS would have flagged every vulnerability we exploited above: the SUID find and python3 , the cap_setuid capability, the sudo vim entry, and the world-writable cron script. Running it saves time, but understanding the techniques manually is what matters for exams and real engagements where you need to know why something is exploitable.
On OSCP, you are allowed to use these tools. Bring all of them on your attack box and transfer whichever fits the situation. Kernel exploits are the nuclear option. They target vulnerabilities in the Linux kernel itself to gain root. They are powerful but carry real risk: a failed kernel exploit can crash the target or cause a kernel panic, which in an engagement means you just took down a production server, and in OSCP means you just lost your exam machine.
Our test kernel (6.1.0-38) is fully patched, so no kernel exploit was needed. This is the correct assessment order: exhaust all misconfiguration-based vectors before resorting to kernel exploits. Misconfigurations are reliable, repeatable, and don’t crash anything. Kernel exploits are fragile and version-specific. If you do need to compile a kernel exploit on the target, check that gcc or cc is available: If no compiler exists on the target, compile on your Kali machine for the target’s architecture and transfer the binary.
Sometimes the fastest path to root is finding credentials that someone left lying around. Admins reuse passwords. Developers hardcode secrets. Backup scripts store database credentials in plaintext. This is often overlooked by pentesters who jump straight to technical exploits. If you find a database password, try it with su root . Password reuse between services and the root account is disturbingly common.
Also check for readable backup files. Admins frequently create tarballs of /etc or database dumps and leave them in world-readable locations: A backup of /etc/shadow gives you password hashes for every user on the system. Extract them and crack them offline with Hashcat or John the Ripper . SHA-512 hashes (the default on modern Debian) are slow to crack, but weak passwords still fall quickly with good wordlists like rockyou.txt .
Don’t forget to check for writable /etc/shadow as well (extremely rare but worth the two-second check): If writable, you can replace the root password hash directly. Generate a new hash with openssl passwd -6 -salt xyz newpassword and substitute it into the root line of /etc/shadow . After running through all these techniques, here is the order of operations that works consistently across OSCP, CTFs, and real engagements. This is sorted by reliability and speed, not complexity: This methodology maps directly to what OSCP expects. The exam gives you 23 hours and 45 minutes. Spending 20 minutes running sudo -l , SUID checks, and LinPEAS on each machine before attempting anything else is the most time-efficient approach. Most OSCP machines fall to one of the first three steps.
One more thing worth emphasizing: document everything as you go. When you find the escalation vector, screenshot or copy the output immediately. In a real engagement, you need that evidence for the report. In OSCP, you need it for the proof screenshots. The number of people who root a box and then forget to capture the proof is higher than you’d expect. Keep this cheat sheet handy during engagements. These are the commands you will type on every single Linux target, in order: Bookmark GTFOBins and keep it open in a browser tab during every engagement. When you find a non-standard SUID binary, sudo entry, or capability, GTFOBins will tell you exactly how to exploit it in seconds.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Linux%20malware • https://en.wikipedia.org/wiki/BackTrack • https://en.wikipedia.org/wiki/OpenVMS • https://github.com/sanbita/Bash-System-Security-Audit-Script • https://github.com/JoramMalley/Linux-privilege-escalation • https://linpeas.org/ • https://computingforgeeks.com/linux-privilege-escalation-guide-kali/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Linux Privilege Escalation Auditing Script In Bash.
[*] Metasploit Scan Running on Target Subnet for Linux Privilege Escalation Auditing Script In Bash... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |