Complete Technical Paper Content — Lora And Lorawan Security And Packet Replay Detection
Overview & System Context
Lora And Lorawan Security And Packet Replay Detection: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~5245 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Shape the future of massive IoT with membership of the LoRa Alliance – Show me the membership benefits Securing an Internet of Things (IoT) deployment and keeping it safe and secure is not only a matter of choosing the right communication protocol, it also requires utilizing implementation best practices and adhering to industry security standards.
The LoRa Alliance has always kept security front and center in its development of the LoRaWAN specification, which has been designed from the outset with security as an essential aspect, providing state-of-the-art security properties that meet the needs of highly scalable low-power IoT networks. Security is a key feature of LoRaWAN. Learn how LoRaWAN is innately secure any why how you implement the protocol is important in the following article: The LoRa Alliance designed extensive security features and encryption into the LoRaWAN specification from the very beginning and continuously works to maintain this secure platform. LoRaWAN security design uses several principles to enable the connection of leading applications, including standardization, well-vetted algorithms and end-to-end encryption.
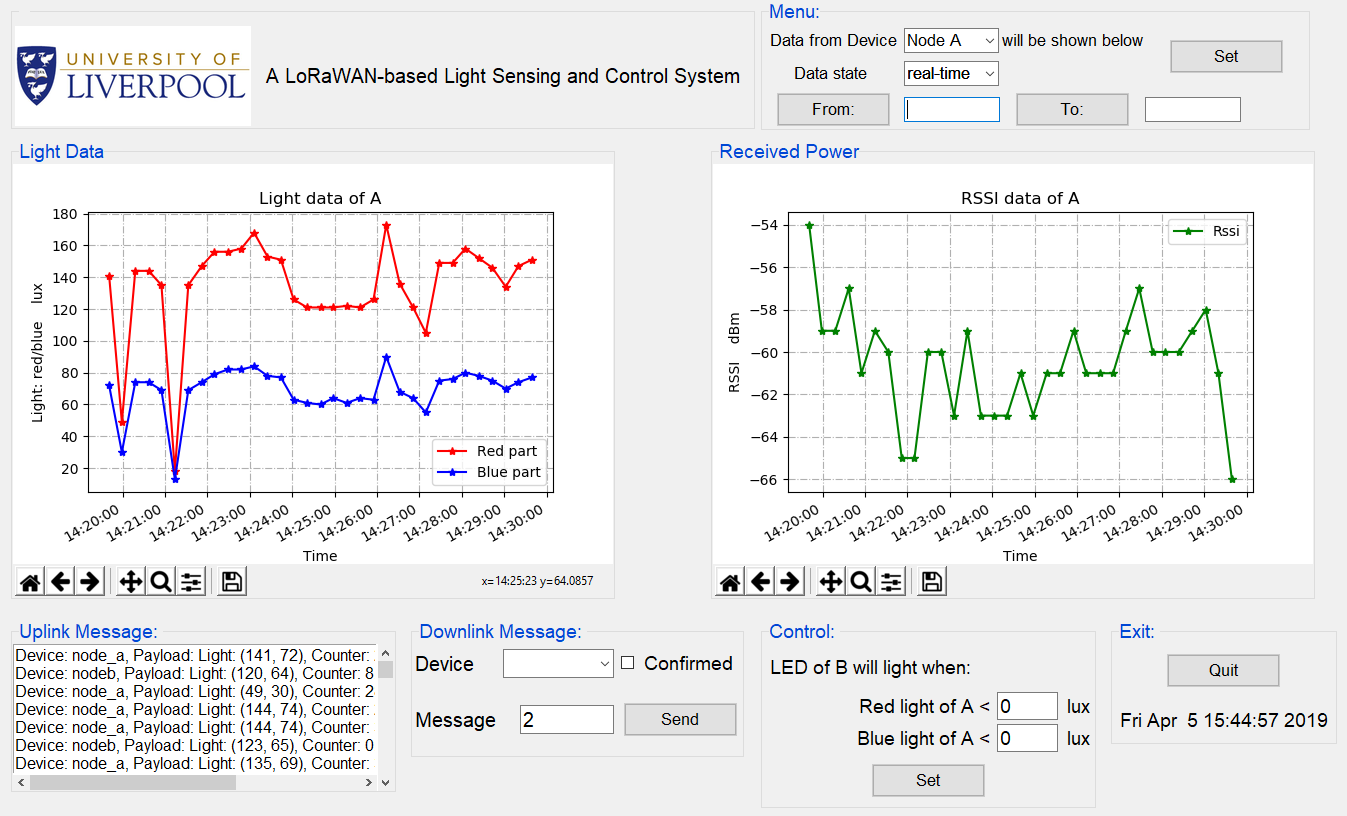
Join Semtech and Actility of the LoRa Alliance for an in-depth webinar on LoRaWAN-based connectivity for secure and reliable applications. This webinar is moderated by The Things Industries. Figure 1: LoRaWAN Demonstration - Shan Luo LoRaWAN certification is crucial as it ensures that your device complies with industry standards, providing customers with confidence in its performance and reliability. LoRaWAN certification not only helps to ensure device interoperability within the vast LoRaWAN ecosystem while assuring customers of its security and operational efficiency. By choosing certified devices, customers can minimize integration challenges and reduce the risks associated with network deployment. Ultimately, certification adds value by fostering trust and promoting a seamless user experience.
The LoRa Alliance offers unparalleled regulatory support to its members, actively engaging with global regulatory bodies to shape favorable spectrum policies and industry standards. As a member, you’ll benefit from the alliance’s expertise in navigating complex global and local regulations, ensuring compliance and accelerating your market entry. Joining the LoRa Alliance empowers your business to influence regulatory decisions and stay ahead of evolving standards, giving you a critical edge in deploying LoRaWAN solutions worldwide.
VendorID for unique identification of your products, ability to generate standard device-identifying QR codes (using own VendorID). As a member of the LoRa Alliance, your organization can engage in any of our working groups dedicated to enhancing and advancing the LoRaWAN standard while fostering global market awareness and adoption. Below is a list of our current working groups and task forces for your reference.
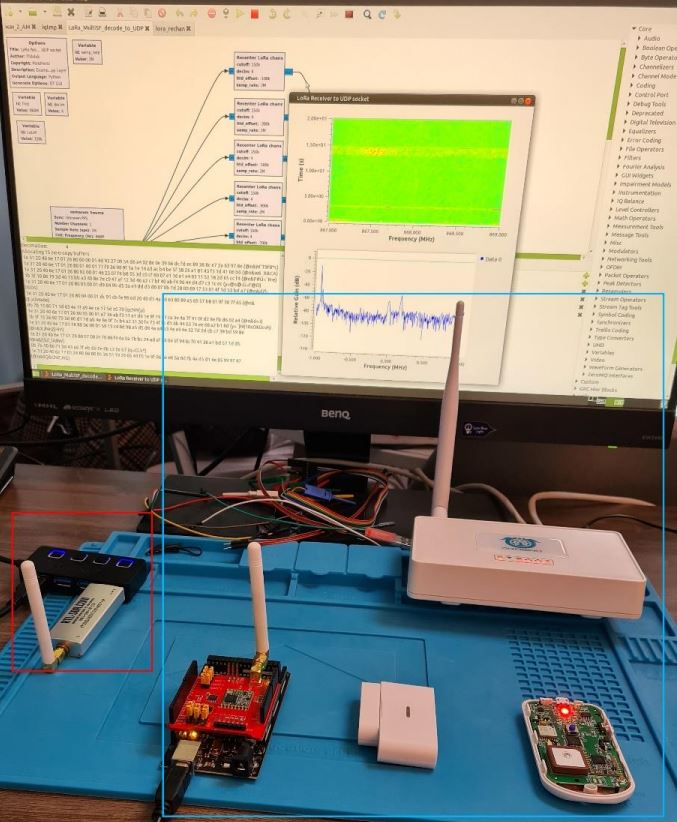
Figure 2: LoRa The tool is still actively under construction. The sniffer utility should be working well with 125kHz bandwidth, so feel free to test it out. Please note, that the transmission features require more testing as I currently do not own a LoRaWAN gateway. This repository provides a toolkit for assessing LoRaWAN network security. Here's what it offers: Follow the instructions on the GNU Radio wiki for your Linux distribution: https://wiki.gnuradio.org/index.php/InstallingGR This step ensures the virtual environment can access gnuradio installed outside the environment.
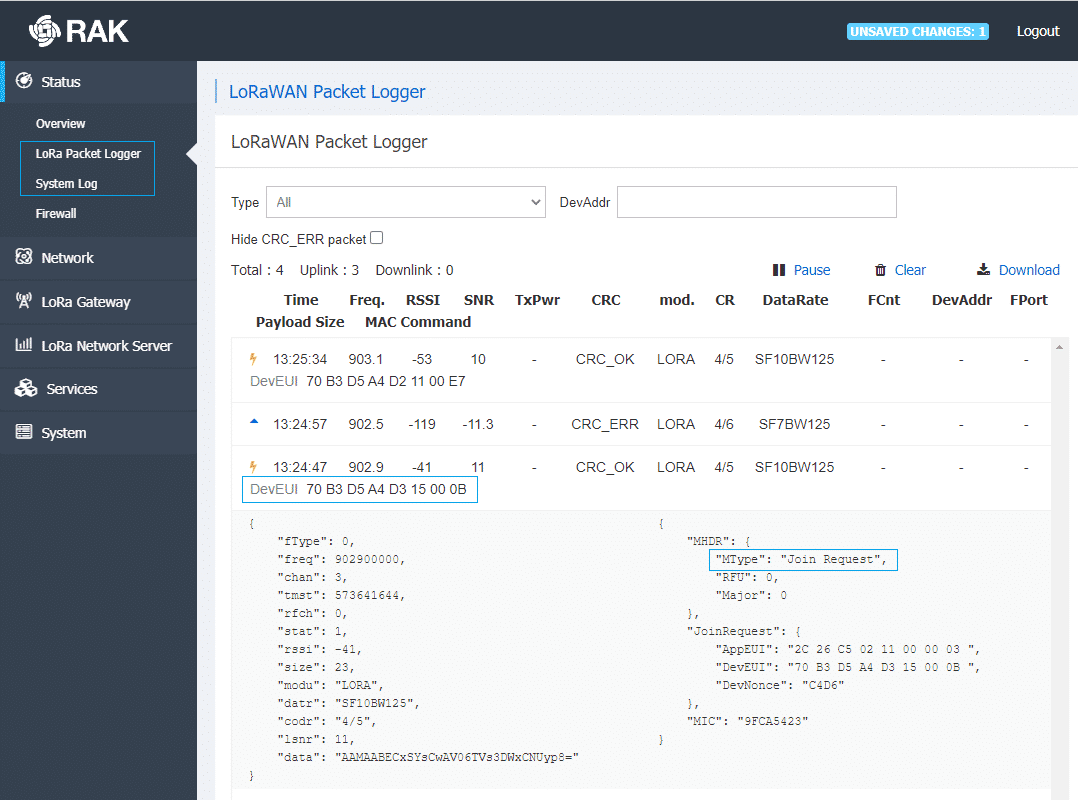
Figure 3: Online Issues Troubleshooting Guide For LoRa/LoRaWAN Gateway - Lansitec Note: Replace /usr/local/lib/python3.10 with the actual path to your Python 3 installation directory if it's different. Adjust the library path update ( export LD_LIBRARY_PATH... ) only if encountering issues related to missing libraries. Note: Refer to the toolkit's documentation (if available) for detailed usage instructions.
Separate sessions are important for decryption. Each session in LoRAttack extracts handshake data to derive unique keys for captured packets within that session, enabling detailed analysis. LoRAttack's sniffer captures LoRaWAN traffic across multiple channels around a specified center frequency, enabling real-time decoding and decryption (if keys are available).
The Analyzer submenu displays a list of PCAP files associated with your active session. Selecting a PCAP file initiates an analysis process: Configure transmitter: Refer to the Sniffer Configuration section for details on configuring transmitter parameters used during replay attacks (e.g., frequency, gain).
For penetration testing guidelines - refer to section LoRaWAN Security Testing Framework in my thesis here: https://dspace.cvut.cz/handle/10467/115255 LoRaWAN networks power mission-critical IoT deployments—from smart cities to industrial automation. While its lightweight design maximizes battery life and coverage, security must remain a top priority. This guide walks through the full LoRaWAN security stack, common threats, and concrete best practices to lock down your gateways, devices, and data end-to-end.
Impersonation (Forged Join Requests): Attackers may attempt unauthorized joins or replay old join frames. All keys are 128-bit AES, with a 4-byte MIC appended to each frame. By separating network and application security, LoRaWAN ensures gateways can’t read your sensor data. Use TLS for Backend Connections: Ensure TL S/HTTPS between gateways, network server, and application server.
Automated Integrity Checks: Monitor for spikes in join failures, frame loss, or abnormal ADR changes. Keep Software Up to Date: Apply patches for ChirpStack, The Things Stack, or proprietary NS to address vulnerabilities. Physical Tamper Resistance: Use sealed enclosures and tamper-evident labels on devices. 2. System Architecture & Core Working Principles Device Classification: Segment high-risk nodes (e.g., actuators) into separate network segments or VLANs.
End-to-End Encryption: Ensure the application server alone holds AppSKey—gateways and network server never see your data. Input Validation & Sanitization: Validate decoded payloads against schema (e.g., temperature: –40 to 85 °C) before storing or acting.
Signed Firmware Images: Sign each firmware build with a private key; validate signature on-device before flashing. Staged Rollouts: Deploy updates to a small cohort first, monitor for failures, then rollout network-wide. Rollback Mechanisms: Keep a known-good firmware copy to revert if an update fails or is malicious. Secure Gateway Installations: Mount indoor gateways in locked cabinets; outdoor gateways in tamper-resistant enclosures.
Power & Network Redundancy: Use UPS backups and secondary backhaul (e.g., cellular) to prevent gateway outages. Antenna Hardening: Lock antennas or use specialized mounts to prevent physical removal or tampering. Centralized Key Vault: ioX-Connect manages all DevEUI/AppEUI/AppKeys in a secure, access-controlled LNS. Automated Alerts: ioX-Connect will automatically notify you on repeated join failures or ADR anomalies.
Role-Based Access: ioX-Connect offers granular user roles to separate device provisioning from network operations. Assess Your Network Server: If you're managing your own server, ensure you’re on the latest patched version and TLS is enforced. Plan Your OTAU Strategy: If you're managing your own LoRaWAN Network, map out firmware update windows and rollback procedures.
Contact Our Security Team: Schedule a security workshop to tailor these best practices to your deployment . Implementing these layered controls will help you build a robust, future-proof LoRaWAN network—backed by the secure, enterprise-ready ioX-Connect platform. Please reach out to us at: sales@iox-connect.com if you have any additional questions that are not addressed below. You can also check out our content library for more information and content on wireless sensors and IoT.
I spent six months testing smart city sensors before realizing nobody was actually securing the LoRaWAN backbone connecting them. Devices were chattering away at 868MHz with default keys, unencrypted join procedures, and replay attacks happening in broad daylight. The infrastructure team insisted everything was “secured by obscurity” because LoRa operates outside typical WiFi ranges.
That assumption cost them. A single compromised sensor leaked building access patterns for three months before anyone noticed. If you’re building IoT security into critical infrastructure, smart agriculture, or industrial monitoring, you need a proper LoRaWAN penetration testing lab. Not a theoretical setup from vendor docs. A real testbed where you can capture packets, replay messages, forge joins, and understand exactly how these long-range networks fail under attack.
This guide walks through building that lab with hardware that actually works for security research. LoRaWAN operates in a fundamentally different threat model than WiFi or cellular. You’re looking at devices communicating over 2-15km ranges with extremely low power consumption. That range creates problems traditional wireless security didn’t anticipate.
The protocol uses AES-128 encryption with separate network and application session keys. Sounds solid until you examine the join procedure. Over-the-air activation (OTAA) involves transmitting a JoinRequest in plaintext containing the device’s DevEUI and AppEUI. An attacker 5km away can capture this, correlate it with device locations, and start building a network map without ever getting physically close.
I’ve tested networks where every device used activation by personalization (ABP) with hardcoded keys extracted from firmware updates published on the manufacturer’s support portal. You don’t need exotic exploits when the keys are sitting in a PDF titled “Quick Start Guide.” The real attack surface includes join procedure manipulation, frame counter bypass, downlink injection, gateway spoofing, and physical layer jamming. Your lab needs to test all of these, not just packet sniffing.
Building this lab requires understanding the difference between LoRa (the physical layer modulation) and LoRaWAN (the MAC layer protocol). You need hardware that handles both. 3. Software Implementation, Frameworks & Protocols Start with SDR capability for raw protocol analysis. The HackRF One covers 1MHz-6GHz, giving you complete visibility across LoRa’s sub-GHz bands (433MHz, 868MHz EU, 915MHz US). I burned through two hours on this before realizing the HackRF needs proper antenna matching for sub-GHz work. The included antennas are garbage below 800MHz.
Pair that with devices that actually speak LoRaWAN natively. Meshtastic devices like the LilyGO T-Deck or Heltec LoRa 32 give you legitimate LoRa radios you can reprogram for testing. The T-Deck particularly shines here because it includes a full keyboard and screen, making field testing significantly less painful than hauling a laptop everywhere. The T-Embed CC1101 adds another dimension. The CC1101 chipset handles multiple sub-GHz protocols beyond LoRa, letting you test adjacent attack surfaces like proprietary sensor networks that often share infrastructure with LoRaWAN deployments. https://x.com/FlipperDevices/status/1745678234567890123 Every LoRaWAN network has gateways. These are the bridge between end devices and the network server, typically positioned on rooftops or towers to maximize coverage. They’re also frequently the weakest link.
Gateway security testing requires running your own gateway infrastructure under controlled conditions. I use a Raspberry Pi 4 with a RAK2245 Pi HAT as my primary test gateway. This gives you a real LoRaWAN gateway that you can monitor, manipulate, and analyze without touching production infrastructure. The setup process is straightforward but critically important to document properly. Flash Raspbian, install the RAK Wireless gateway software, configure your frequency plan correctly for your region (868MHz for EU, 915MHz for US), and connect it to a local network server instance.
For the network server, ChirpStack is your best option for security research. It’s open source, well-documented, and gives you complete visibility into join procedures, frame counters, and encryption key exchanges. Install it on a separate machine or another Pi to keep the gateway and network server logically separated like they would be in production. The interesting testing starts when you realize most commercial gateways use MQTT with weak or default credentials for backhaul. I’ve encountered industrial LoRaWAN networks where every gateway used “admin/admin” for MQTT authentication because the installer followed the quick start guide verbatim.
Your lab needs to replicate this. Set up intentionally weak configurations, document them, then practice detecting and exploiting them. That’s how you build the muscle memory to spot issues during real assessments. Hardware captures packets. Software makes sense of them. Your analysis stack needs to handle raw RF through to decrypted application payloads.
Start with GNU Radio for SDR work. The gr-lora module gives you LoRa demodulation capability, though I’ll be honest, it’s finicky. You’ll spend time tuning parameters, especially spreading factor and bandwidth. LoRa uses chirp spread spectrum modulation, which means your SDR needs proper sample rate and enough processing power to handle the demodulation in real-time.
For that reason, I do most heavy SDR work on a proper desktop with the HackRF, not on battery-powered field equipment. A decent i7 with 16GB RAM minimum. The math gets heavy fast. Once you’re capturing and demodulating, you need protocol dissection. Wireshark with the LoRaWAN dissector plugin handles this, but understand its limitations. The dissector can’t decrypt packets without session keys. That’s by design, but it means you need to capture the join procedure where those keys are established or extract them from devices directly.
For device-side analysis, LoraSniffer gives you frame-level visibility on Meshtastic hardware. Flash it to a spare LoRa board, position it within range of your test devices, and you’re passively capturing all LoRaWAN traffic in the area. The spreading factor auto-detection is particularly useful when you’re reverse-engineering unknown deployments. The controversial part: you absolutely need a key extraction setup. For legitimate security testing, you’ll encounter devices where you need to verify encryption is actually happening. That requires firmware extraction and analysis. A proper setup includes a JTAG debugger, SPI flash programmer, and familiarity with ARM Cortex-M reverse engineering.
I use a Segger J-Link for JTAG work and a Raspberry Pi with flashrom for SPI extraction. Between those, I can pull firmware from probably 80% of commercial LoRaWAN sensors I encounter. Theory is worthless without practical attack scenarios. Your lab should replicate real vulnerabilities you’ll encounter in production environments.
The OTAA join procedure is your first target. Capture a legitimate JoinRequest, replay it after the device has successfully joined, and observe how the network server handles it. Properly configured networks should reject replays based on DevNonce tracking, but I’ve found servers that accept identical JoinRequests indefinitely. Set up a test device, capture its join with your HackRF and GNU Radio, then use a programmed Meshtastic device to replay that exact packet. Does the network server create a new session? Does it maintain proper frame counter state? These questions reveal whether the infrastructure team actually understands LoRaWAN security.
LoRaWAN uses frame counters to prevent replay attacks on data uplinks and downlinks. The spec requires strictly incrementing counters. In practice, many network servers accept counter resets or allow gaps for “device clock issues.” Your test: program a Meshtastic device to send frames with decreasing frame counters. A secure network should reject these. Document how the network server responds. Then test frame counter overflow conditions. What happens at 65,535 on a 16-bit counter? The spec says to trigger a rejoin. Most implementations crash or silently accept a rollover to zero.
Downlink attacks are nastier because they target devices directly. If you can impersonate a gateway or inject downlink messages, you can push malicious firmware updates, trigger device resets, or manipulate sensor readings. Set up a rogue gateway using your Raspberry Pi setup. Position it closer to test devices than the legitimate gateway. LoRa uses signal strength and timing for gateway selection in many implementations. Your closer rogue gateway wins.
Now craft downlink messages. You’ll need the device’s Network Session Key (NwkSKey) to properly encrypt them, but if you’ve captured the join procedure or extracted keys from firmware, you have that. Push a downlink commanding the device to transmit at maximum power continuously. Legitimate use case for testing battery drain. Also an effective DoS if abused. The legal and ethical boundaries here are critical. Everything I’m describing assumes you’re testing infrastructure you own or have explicit written authorization to test. LoRa’s long range means your signals can easily affect devices and networks outside your intended scope. A directional antenna pointed the wrong way can interfere with medical device telemetry 15km away. Don’t be that person.
Meshtastic devices deserve special attention for field testing. They’re originally designed for off-grid mesh communication, but the same hardware makes excellent portable LoRa security tools. 4. Practical Deployment, Analysis & Case Studies The LilyGO T-Deck gives you a full QWERTY keyboard, color display, and proper LoRa radio in a handheld form factor. Flash custom firmware and you’ve got a portable LoRa packet injector that fits in a jacket pocket. The battery lasts 8-12 hours depending on transmit power.
I use mine for wardriving LoRaWAN networks. Drive through an industrial park, passively capture all LoRa traffic, log GPS coordinates (the T-Deck has GPS built-in), then analyze correlation between physical locations and device density. You’d be surprised how many critical facilities leak their entire sensor network topology through unencrypted LoRa traffic. The Heltec LoRa 32 works as a cheaper alternative if you don’t need the keyboard. Pair it with a phone running Serial Bluetooth Terminal and you get similar capability for half the price.
Meshtastic’s mesh networking features also let you test multi-hop attack scenarios. Set up three devices as a mesh, compromise one, and see if you can pivot through the mesh to reach devices multiple hops away. Real LoRaWAN networks don’t use mesh topology, but many proprietary LoRa implementations do. Your lab should cover both. Beyond packet capture and replay, serious LoRaWAN testing requires understanding the physical layer. That means RF characterization, timing analysis, and modulation parameter testing.
Your HackRF captures raw IQ data. Feed that into inspectrum or Universal Radio Hacker for visual analysis. LoRa’s chirp spread spectrum creates distinctive waterfall patterns in spectrum analysis. Learn to recognize spreading factors by sight. SF7 looks different from SF12. Different bandwidths create different chirp rates. This visual analysis skills lets you identify LoRa traffic even when you don’t have the protocol parameters. I’ve identified unauthorized LoRa deployments on restricted frequencies just by recognizing the chirp pattern in spectrum scans.
Timing analysis reveals network architecture. Measure the delay between uplink and downlink messages. LoRaWAN Class A devices only open receive windows immediately after transmitting. Class B devices open scheduled receive windows. Class C devices listen continuously. By measuring timing patterns, you fingerprint device classes remotely. Use a Logic Analyzer on the SPI pins between the LoRa radio and microcontroller to capture raw protocol exchanges. This is particularly valuable when reverse-engineering devices with custom firmware. You can see exactly what commands the MCU sends to the LoRa transceiver, revealing undocumented features or backdoor channels.
The T-Embed CC1101 becomes useful here for testing adjacent protocols. Many deployments mix LoRaWAN with proprietary sub-GHz protocols. The CC1101’s flexibility lets you test cross-protocol attacks where you exploit a weaker proprietary protocol to gain initial access, then pivot to the LoRaWAN network. Your LoRaWAN lab shouldn’t exist in isolation. It needs to integrate with standard penetration testing methodology and tooling.
I keep my LoRa testing hardware in a go-bag alongside traditional pentest gear. Raspberry Pi running Kali with the LoRa gateway hat, two Meshtastic devices, HackRF with proper antennas, power banks, and a USB hub to run everything off a laptop in the field. The workflow looks like reconnaissance, scanning, enumeration, exploitation, and post-exploitation, same as any other assessment. LoRa-specific reconnaissance means RF scanning to identify frequencies in use, spreading factors, and bandwidth configurations. Use the HackRF with gqrx for wide-band monitoring, then narrow in once you identify LoRa signals.
Scanning means attempting to capture and decode LoRaWAN traffic. Your gateway setup passively listens and logs all devices it hears. Build a database of DevEUI, DevAddr, frame counters, and timing patterns. This is your target list. Enumeration involves capturing join procedures, identifying network server addresses, and mapping gateway coverage. Tools like lorawan-scanner automate much of this, but understand what they’re doing under the hood. I’ve had clients dispute findings because they didn’t understand how I identified devices that “weren’t supposed to be visible.” Documentation matters. Every capture, every exploit attempt, every configuration change gets logged. Screenshots of Wireshark captures, photos of hardware setups, GPS coordinates of testing locations. When you write the final report, you need evidence that’s specific, reproducible, and defensible.
What’s the legal risk of testing LoRaWAN networks without explicit authorization? Transmitting on ISM bands is generally legal, but intentionally interfering with existing networks or accessing systems without authorization violates computer fraud laws in most jurisdictions. Always get written permission before testing any network you don’t own. The long range of LoRa means your signals can easily affect unintended targets.
Can I use this setup to test LoRa devices that aren’t LoRaWAN compliant? Absolutely. Many industrial and agricultural IoT devices use raw LoRa without implementing the full LoRaWAN stack. Your HackRF and Meshtastic devices can capture and analyze these proprietary protocols. The T-Embed CC1101 handles additional sub-GHz protocols entirely outside the LoRa ecosystem, making it valuable for comprehensive IoT security assessments.
How do I extract encryption keys from LoRaWAN devices for testing? For devices you’re authorized to test, firmware extraction via JTAG or SPI flash reading typically reveals hardcoded keys. Many devices store AppKey, NwkKey, or session keys in plaintext in flash memory. Alternatively, capture the join procedure with your gateway setup to derive session keys from observed traffic if you control the network server.
What’s the actual range I should expect for LoRa security testing? Line of sight with proper antennas, you’ll capture signals 5-10km easily. Urban environments with buildings reduce that to 2-5km typically. Your HackRF with a tuned sub-GHz antenna significantly outperforms Meshtastic devices for passive listening range. I’ve captured LoRa packets from smart parking sensors 8km away using the HackRF at maximum gain with an outdoor yagi antenna.
The infrastructure is one thing. Actually running tests and generating findings is another. Start with a controlled environment where you own all the equipment, can document baseline behavior, then introduce vulnerabilities systematically. Your first project should be testing your own gateway and devices against the OWASP IoT Top 10. Weak credentials, insecure defaults, lack of update mechanisms, insufficient physical security. These aren’t exotic LoRa-specific vulnerabilities.
They’re fundamental issues that affect LoRaWAN deployments just like any other IoT system. Once you’ve documented those basics, move into protocol-specific testing. The frame counter attacks, join replay scenarios, downlink injection examples I covered earlier. Build a test matrix, work through each scenario, document results, and understand not just what failed but why it failed and how to fix it.
When you’re ready to start picking up client work, you’ll have a portable lab that demonstrates real capability. Walk into a meeting with a Meshtastic device, capture packets from their smart building sensors while sitting in the lobby, and show them decrypted sensor readings on your laptop. That demonstration buys credibility that vendor certifications never will. Your lab builds over time. I started with a single Meshtastic device and a cheap RTL-SDR dongle three years ago. Now I’ve got HackRF, LimeSDR, multiple Raspberry Pi gateways, and enough LoRa hardware to test most scenarios I encounter. Start small, test thoroughly, and expand based on what you’re actually finding in real assessments.
The complete hardware setup including Meshtastic devices, development boards, and SDR equipment sits at wai-works.com if you want to build this same capability without hunting components across multiple vendors. But more important than the specific hardware is understanding the methodology. The tools evolve. The approach to finding and documenting vulnerabilities remains constant.
5. Performance Evaluation & Extended Technical Observations Passive LoRa reconnaissance firmware for ESP32-S3 + SX1262 hardware. Scans 29 frequency configurations, captures and replays packets, tests 23 default Meshtastic PSKs, decrypts MeshCore public channels and hashtag rooms, extracts GPS coordinates, and serves a phone-accessible web UI — all from a low-cost board.
One-click flash from your browser (Chrome/Edge, no downloads): → https://haksht.github.io/lorecon/install/ Full setup (flash + WiFi + Python analysis tools): → docs/SETUP.md — three install paths, picks the one that fits Want to build or modify the firmware: → docs/developers/BUILDING.md — PlatformIO, serial monitor, OTA One afternoon in a hotel, one $20 board, receive-only: 3,630 packets, 266 devices, 57 readable messages — every one of them opened with a known or default channel key, nothing custom. There was no cheap, self-contained way to see which side of that line your own network is on, so we built one.
So this is it: low-cost, stand-alone LoRa reconnaissance with a phone-friendly web UI, default-key testing, and built-in export — passive, and honest about its limits (a default-key hit opens broadcasts; direct messages stay behind Curve25519). Point it at a mesh you own and a six-minute sweep tells you which side of that line you're on. This tool is for authorized security research, education, and testing on networks you own or have explicit permission to analyze.
Legitimate uses: Auditing your own Meshtastic/LoRa networks, security research with authorization, conference demonstrations, identifying devices using vulnerable default configurations. Not for: Intercepting private communications without consent, tracking individuals without authorization, jamming or disrupting networks, commercial exploitation of captured data.
US context: passive RF reception is generally legal; interception of content may implicate 18 U.S.C. § 2511. Laws vary by jurisdiction. Default PSKs are tested to demonstrate the risk of using factory-default encryption keys. See CONTRIBUTING.md . Keep modules focused, patches small, and include hardware details in bug reports. LoRa packet capture and analysis tool for ESP32-S3 + SX1262 radio. Focused reconnaissance, sniffing, capture, and replay capabilities with optional PSK testing and hardware stress validation.
Srivastava, Roopesh (2024) A comprehensive security approach to mitigate Replay and MITM attacks in LoRaWAN protocol. Masters thesis, Dublin, National College of Ireland. The development of numerous new Internet of Things (IoT) applications have been made possible by low-power, long range wide-area technology (LoRaWAN), which provides energy and cost-efficient wireless connectivity for large deployments of autonomous sensors. The security of LoRaWAN operating in the license-free frequency band, has received somewhat limited attention and numerous investigations have identified security flaws that makes it susceptible to network attacks such as Replay, Man in the Middle (MiTM) and bit-flipping attack. Current research has identified that LoRaWAN in its present form lacks synchronization between communicating parties, has a vulnerable key management and encryption process. The research has proposed an improvement in the form of dual encryption and time stamp-based synchronization check, which tends to negate these network attacks. This approach neither tampers with the core of the LoRaWAN nor the recommendations of the LoRa Alliance. The approach will lead to enhanced attack detection and mitigation capability of the protocol and make it robust for critical nodes and applications.
The development of numerous new Internet of Things (IoT) applications have been made possible by low-power, long range wide-area technology (LoRaWAN), which provides energy and cost-efficient wireless connectivity for large deployments of autonomous sensors. The security of LoRaWAN operating in the license-free frequency band, has received somewhat limited attention and numerous investigations have identified security flaws that makes it susceptible to network attacks such as Replay, Man in the Middle (MiTM) and bit-flipping attack. Current research has identified that LoRaWAN in its present form lacks synchronization between communicating parties, has a vulnerable key management and encryption process. The research has proposed an improvement in the form of dual encryption and time stamp-based synchronization check, which tends to negate these network attacks. This approach neither tampers with the core of the LoRaWAN nor the recommendations of the LoRa Alliance. The approach will lead to enhanced attack detection and mitigation capability of the protocol and make it robust for critical nodes and applications.
Shape the future of massive IoT with membership of the LoRa Alliance – Show me the membership benefits Securing an Internet of Things (IoT) deployment and keeping it safe and secure is not only a matter of choosing the right protocol, it relies on the implementation process as well as embracing best practices and industry standards. LoRaWAN is by design very secure—authentication and encryption are, in fact, mandatory—but networks and devices can be compromised if security keys are not kept safe, not randomized across devices or if cryptographic numbers used once (nonces) are reused, as is shown by numerous blog posts. That’s why it is critical to look for LoRaWAN CertifiedCM devices to ensure the device has been tested against the standard and works as expected.
The LoRa Alliance has always kept security front and center in its development of the LoRaWAN specification and has been highly transparent about the protocol’s security features (see Figure 1). The LoRaWAN specification has been designed from the outset with security as an essential aspect, providing state-of-the-art security properties that meet the needs of highly scalable low-power IoT networks. Unlike many other IoT technologies, the LoRaWAN specification already offers dedicated end-to-end encryption to application providers.
Using a unique 128-bit network session key shared between the end-device and network server Using a unique 128-bit application session key (AppSKey) shared end-to-end at the application level AES algorithms are used to provide authentication and integrity of packets to the network server and end-to-end encryption to the application server. By providing these two levels, it becomes possible to implement “multitenant” shared networks without the network operator having visibility of the users’ payload data. The devices can be activated by Personalization on the production line or during commissioning, or can be over the air activated (OTAA) in the field. OTAA allows device sessions to be rekeyed if necessary.
LoRaWAN has all the fundamental building blocks required and used by any modern wireless communications technology, and does so at AES-128 strength. LoRaWAN’s inherent security, as provided in the specification, needs to be accompanied by secure implementation and secure deployment of these devices and/or networks to maintain the protocol’s built-in security mechanisms. It should be pointed out that this is true of all secure device implementations using any communication technology.
As stated above, LoRaWAN relies on symmetric cryptography, which requires sharing keys in a safe and secure way. To further aid with this process, LoRa Alliance members have developed: LoRaWAN backend interfaces that isolate the storage of root keys in the join server, so that becomes a trusted player, regardless of network Secure element solutions that provide additional hardware physical protection against tampering To ensure device and network security, as with any technology, the best practice is always to use certified devices and work with proven and trusted service providers. LoRaWAN is no different, and end users can be confident in their deployment if they leverage resources that know how to correctly implement LoRaWAN solutions.
Security is a constantly moving target, with malicious actors continuously appearing, and LoRaWAN is always evolving to meet any new threats as well. Though LoRaWAN is inherently secure, the LoRa Alliance is constantly reviewing, designing and implementing security enhancements and best practices to ensure LoRaWAN stays ahead of the changing security landscape.
As such, and to assist the market in choosing the right implementation, the LoRa Alliance will publish a Recommended Practices document in the next month that will provide best practices for device makers to keep their devices secure. In addition, the Security Working Group, reporting to the LoRa Alliance Technical Committee responsible for the LoRaWAN specification, continuously reviews security aspects of technical specifications and documents. The Security Working Group consists of security experts from the LoRa Alliance membership and works with academia to review papers and discuss security challenges.
For more information about LoRaWAN security, please check out our updated Security FAQs , which address the common questions about how the specification has implemented security features. Harvested Online Documentation & Reference Sources • https://lora-alliance.org/security/ • https://github.com/konicst1/lorattack • https://www.iox-connect.com/lorawan-security • https://wai-works.com/blog/lorawan-penetration-testing-lab-setup-guide/ • https://github.com/haksht/lorecon • https://norma.ncirl.ie/7739/ • https://lora-alliance.org/resource_hub/lorawan-is-secure-but-implementation-matters/?utm
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Lora And Lorawan Security And Packet Replay Detection.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |