Complete Technical Paper Content — Mac Address Spoofing Detection Tool For Linux
Overview & System Context
Mac Address Spoofing Detection Tool For Linux: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8767 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background In computer networking, ARP spoofing (also ARP cache poisoning or ARP poison routing) is a technique by which an attacker sends (spoofed) Address Resolution Protocol (ARP) messages onto a local area network. Generally, the aim is to associate the attacker's MAC address with the IP address of another host, such as the default gateway, causing any traffic meant for that IP address to be sent to the attacker instead. ARP spoofing may allow an attacker to intercept data frames on a network, modify the traffic, or stop all traffic. Often, the attack is used as an opening for other attacks, such as denial of service, man in the middle, or session hijacking attacks. The attack can only be used on networks that use ARP, and requires the attacker to have direct access to the local network segment to be attacked.
The techniques that are used in ARP spoofing can also be used to implement redundancy of network services. For example, some software allows a backup server to issue a gratuitous ARP request in order to take over for a defective server and transparently offer redundancy. Circle and CUJO are two companies that have commercialized products centered around this strategy. ARP spoofing is often used by developers to debug IP traffic between two hosts when a switch is in use: if host A and host B are communicating through an Ethernet switch, their traffic would normally be invisible to a third monitoring host M.
The developer configures A to have M's MAC address for B, and B to have M's MAC address for A; and also configures M to forward packets. M can now monitor the traffic, exactly as in a man-in-the-middle attack. An Internet Protocol version 6 address (IPv6 address) is a numeric label that is used to identify and locate a network interface of a computer or a network node participating in a computer network using IPv6. IP addresses are included in the packet header to indicate the source and the destination of each packet. The IP address of the destination is used to make decisions about routing IP packets to other networks. IPv6 is the successor to the first addressing infrastructure of the Internet, Internet Protocol version 4 (IPv4). In contrast to IPv4, which defined an IP address as a 32-bit value, IPv6 addresses have a size of 128 bits. Therefore, in comparison, IPv6 has a vastly enlarged address space.
The network prefix (the routing prefix combined with the subnet ID) is contained in the most significant 64 bits of the address. The size of the routing prefix may vary; a larger prefix size means a smaller subnet ID size. The bits of the subnet ID field are available to the network administrator to define subnets within the given network. The 64-bit interface identifier is automatically established randomly, obtained from a DHCPv6 server, or assigned manually. (Historically, it was automatically generated from the interface's MAC address using the modified EUI-64 format, but this method is now not recommended for privacy reasons.) Unique local addresses are addresses analogous to IPv4 private network addresses.
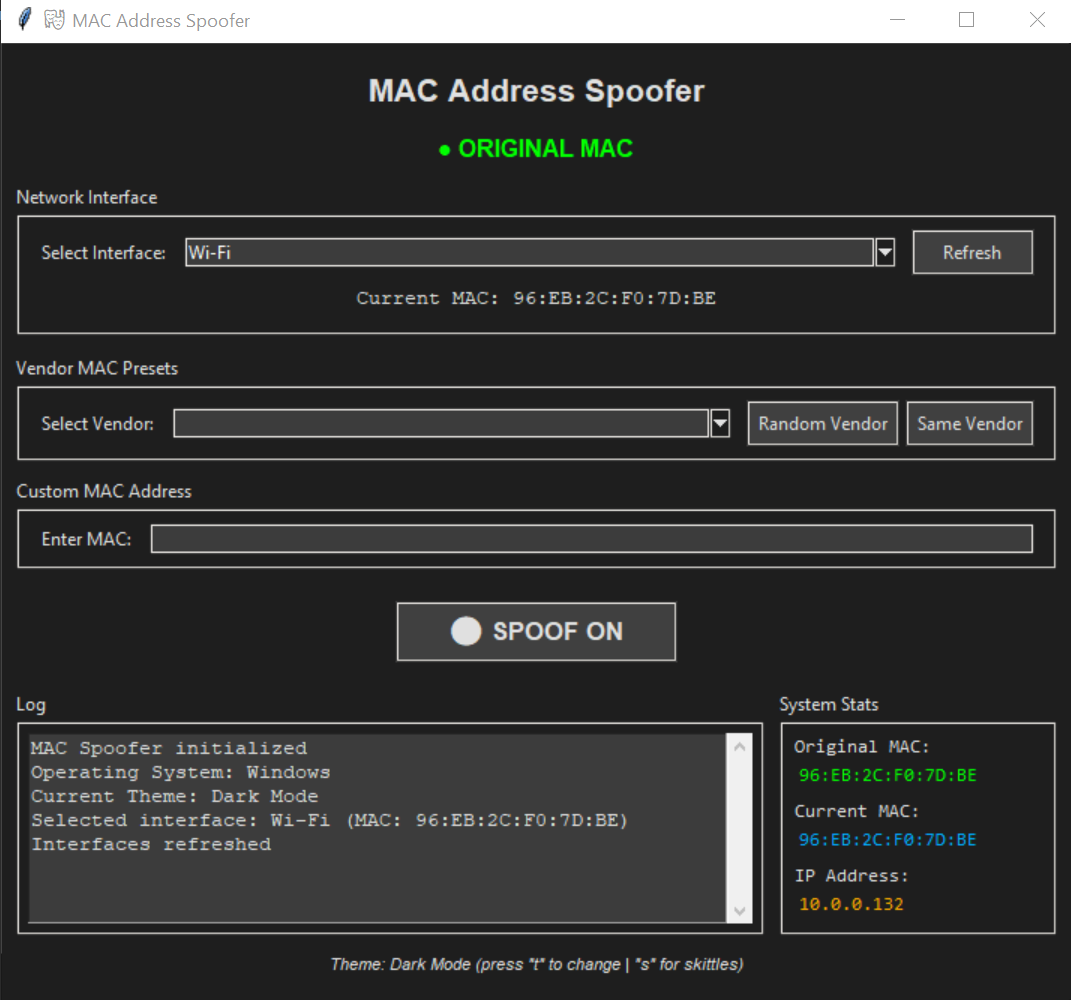
Figure 1: GitHub - Ringmast4r/MAC-SPOOFER: Cross-platform MAC address spoofing ... The prefix field contains the binary value 1111110. The L bit is one for locally assigned addresses; the address range with L set to zero is currently not defined. The random field is chosen randomly once, at the inception of the /48 routing prefix. A link-local address is also based on the interface identifier, but uses a different format for the network prefix.
The prefix field contains the binary value 1111111010. The 54 zeroes that follow make the total network prefix the same for all link-local addresses (fe80::/64 link-local address prefix), rendering them non-routable. Multicast addresses are formed according to several specific formatting rules, depending on the application. For all multicast addresses, the prefix field holds the binary value 11111111. Currently, three of the four flag bits in the flg field are defined; the most-significant flag bit is reserved for future use.
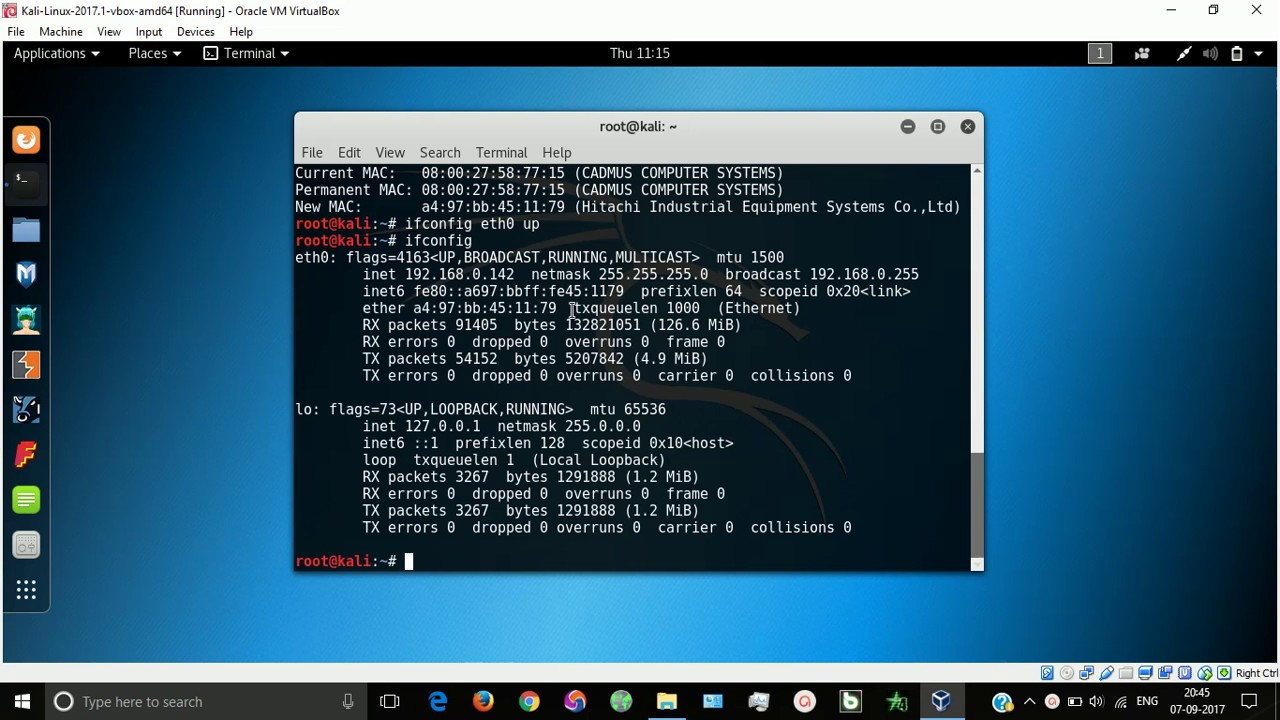
Figure 2: Mac Spoofing | kali linux | mac changer | hide mac address | spoof mac ... The four-bit scope field (sc) is used to indicate where the address is valid and unique. In addition, the scope field is used to identify special multicast addresses, like solicited node. The sc(ope) field holds the binary value 0010 (link-local). Solicited-node multicast addresses are computed as a function of a node's unicast or anycast addresses. A solicited-node multicast address is created by copying the last 24 bits of a unicast or anycast address to the last 24 bits of the multicast address.
The standards provide flexibility in the representation of IPv6 addresses. The full representation of eight four-digit groups may be simplified by several techniques, eliminating parts of the representation. In general, representations are shortened as much as possible. However, this practice complicates several common operations, namely searching for a specific address or an address pattern in text documents or streams, and comparing addresses to determine equivalence. For mitigation of these complications, the Internet Engineering Task Force (IETF) has defined a canonical format for rendering IPv6 addresses in text: The hexadecimal digits are always compared in a case-insensitive manner, but IETF recommendations suggest the use of only lower case letters. For example, 2001:db8::1 is preferred over 2001:DB8::1; Leading zeros in each 16-bit field are suppressed, but each group must retain at least one digit. For example, 2001:0db8::0001:0000 is rendered as 2001:db8::1:0; The longest sequence of consecutive all-zero fields is replaced with two colons (::). If the address contains multiple runs of all-zero fields of the same size, to prevent ambiguities, it is the leftmost that is compressed. For example, 2001:db8:0:0:1:0:0:1 is rendered as 2001:db8::1:0:0:1 rather than as 2001:db8:0:0:1::1. :: is not used to represent just a single all-zero field. For example, 2001:db8:0:0:0:0:2:1 is shortened to 2001:db8::2:1, but 2001:db8:0000:1:1:1:1:1 is rendered as 2001:db8:0:1:1:1:1:1. These methods can lead to very short representations for IPv6 addresses. For example, the localhost (loopback) address, 0:0:0:0:0:0:0:1, and the IPv6 unspecified address, 0:0:0:0:0:0:0:0, are reduced to ::1 and ::, respectively.
During the transition of the Internet from IPv4 to IPv6, it is typical to operate in a mixed addressing environment. For such use cases, a special notation has been introduced, which expresses IPv4-mapped and IPv4-compatible IPv6 addresses by writing the least-significant 32 bits of an address in the familiar IPv4 dot-decimal notation, whereas the 96 most-significant bits are written in IPv6 format. For example, the IPv4-mapped IPv6 address ::ffff:c000:0280 is written as ::ffff:192.0.2.128, thus expressing clearly the original IPv4 address that was mapped to IPv6.
Figure 3: Turn on MAC address spoofing protection by IoT fingerprinting The former (using an interface name) is customary on most Unix-like operating systems (e.g., BSD, Linux, macOS). The latter (using an interface number) is the only syntax on Microsoft Windows, but as support for this syntax is mandatory per standard, it is also available on other operating systems. BSD-based operating systems (including macOS) also support an alternative, non-standard syntax, where a numeric zone index is encoded in the second 16-bit word of the address. E.g.: In all operating systems mentioned above, the zone index for link-local addresses actually refers to an interface, not to a zone.
As multiple interfaces may belong to the same zone (e.g. when connected to the same network), in practice two addresses with different zone identifiers may actually be equivalent, and refer to the same host on the same link. When used in uniform resource identifiers (URI), the use of the percent sign causes a syntax conflict, therefore it must be escaped via percent-encoding, e.g.: This notation is automatically resolved locally by Microsoft software, without any queries to DNS name servers. If the IPv6 address contains a zone index, it is appended to the address portion after an 's' character: All other scopes are unassigned and available to administrators for defining additional regions.
There are a number of addresses with special meaning in IPv6. The IANA maintains a registry of these special-purpose addresses. They represent less than 2% of the entire address space: In the past ::ffff:0:0.0.0.0/96 (::ffff:0:0:0/96) was considered for IPv4/IPv6 translation, but it is no longer reserved. 2001::/32 — Used for Teredo tunneling, an IPv6 transition mechanism. 2001:1::1/128 — Port Control Protocol Anycast 2001:1::2/128 — Traversal Using Relays around NAT Anycast 2001:1::3/128 — DNS-SD Service Registration Protocol Anycast 2001:2::/48 — Used for benchmarking IPv6. Corresponds with 198.18.0.0/15 used for benchmarking IPv4. Assigned to the Benchmarking Methodology Working Group (BMWG). 2001:3::/32 — Automatic Multicast Tunneling, Relay Discovery 2001:20::/28 — Overlay Routable Cryptographic Hash Identifiers (ORCHIDv2). These are non-routed IPv6 addresses used for cryptographic hashes. 2001:30::/28 — Drone Remote ID Protocol Entity Tags (DETs) Prefix Furthermore, IANA has reserved the following two IPv6 prefixes for AS112 nameserver operations: 2620:4f:8000::/48 — Blackhole servers with the traditional authoritative zones configured 2001:4:112::/48 — Blackhole servers for the new blackholing approach involving DNAME records to empty.as112.arpa As the name "interface identifier" suggests, it can be the network adapter's 48-bit MAC address, which is guaranteed to be unique. A MAC address 00-0C-29-0C-47-D5 is turned into a 64-bit modified EUI-64 by first inserting FF-FE in the middle: 00-0C-29-FF-FE-0C-47-D5, and then inverting the Universal/Local bit, becoming 02-0C-29-FF-FE-0C-47-D5 (or :020c:29ff:fe0c:47d5 in IPv6 address notation). However, using the real MAC address of the adapter to derive the interface address is now discouraged in end-user devices because it exposes the MAC address to the wider Internet, making it easier to track the user across networks. As a result, it is now common to instead use a pseudorandom address. Existing options include the temporary address, the stable privacy address, and the cryptographically generated address. This is related to, but not the same mechanism as, MAC spoofing; the pseudo-random interface identifier does not need to match the MAC address, real or spoofed.
The default configuration places preference on IPv6 usage, and selects destination addresses within the smallest possible scope, so that link-local communication is preferred over globally routed paths when otherwise equally suitable. The prefix policy table is similar to a routing table, with the (inverse) precedence value serving as the role of a link cost; larger values result in higher precedence. Source addresses are preferred to have the same label value as the destination address.
Addresses are matched to prefixes based on the longest-matching most-significant bit sequence. Candidate source addresses are obtained from the operating system and candidate destination addresses may be queried via DNS. To minimize the time to establish a connection when multiple addresses are available for communication, the Happy Eyeballs algorithm was devised. It queries DNS for IPv6 and IPv4 addresses of the target host, sorts candidate addresses using the default address selection table, and tries to establish connections in parallel. The first established connection aborts current and future attempts to connect to other addresses.
f.1.0.0.0.0.0.0.0.0.0.0.0.0.0.0.4.0.0.0.3.2.0.0.1.c.c.5.a.d.d.f.ip6.arpa. IN PTR derrick.example.com. This pointer record may be defined in a number of zones, depending on the chain of delegation of authority in the zone d.f.ip6.arpa. The DNS protocol is independent of its transport layer protocol. Queries and replies may be transmitted over IPv6 or IPv4 transports regardless of the address family of the data requested.
In computer networking, a proxy server is an intermediary server application between a client requesting a resource and the server then providing that resource. Instead of connecting directly to a server that can fulfil a request for a resource, such as a file or web page, the client directs the request to the proxy server, which evaluates the request and performs the required network transactions. This serves as a method to control the complexity of the request or provide additional benefits such as load balancing, privacy or security. Proxies were devised to add structure and encapsulation to distributed systems.
An open proxy is a forwarding proxy server that is accessible by any Internet user. In 2008, network security expert Gordon Lyon estimated that "hundreds of thousands" of open proxies are operated on the Internet. Anonymous proxy: This server reveals its identity as a proxy server but does not disclose the originating IP address of the client. Although discovered easily as a proxy server, it can be beneficial for some users as it hides the originating IP address.
Forwarding headers: Some proxies append HTTP headers to disclose client or proxy information that would otherwise be lost when a request is forwarded. Historically this has often been done with non-standard fields such as X-Forwarded-For, while the standardised Forwarded field provides a defined syntax for similar information. Such headers are deployment-dependent and should not be treated as inherently trustworthy, since they may be absent, modified, or contain values added by multiple proxies.
A reverse proxy (or surrogate) is a proxy server that appears to clients to be an ordinary server. Reverse proxies send requests to one or more ordinary servers that handle the request. The response from the original server is returned as if it came directly from the proxy server, leaving the client with no knowledge of the original server. Reverse proxies are installed in the vicinity of one or more web servers. All traffic coming from the Internet and with a destination of one of the neighborhood's web servers goes through the proxy server. The use of "reverse" originates in its counterpart, the "forward" proxy. The reverse proxy sits closer to the web server and serves only a restricted set of websites. There are several reasons for installing reverse proxy servers: TLS termination: Reverse proxies often terminate TLS connections from clients and forward requests to backend servers. This can centralise certificate management, access control, logging, and request routing, and can reduce the TLS-related work performed by backend servers. Backend connections may use HTTP or HTTPS depending on the deployment and security requirements. Modern deployments usually perform TLS termination in software, optionally with hardware assistance, rather than requiring dedicated SSL acceleration hardware. Certificates for multiple names can be handled using mechanisms such as Subject Alternative Name certificates, wildcard certificates, and Server Name Indication (SNI). Load balancing: the reverse proxy can distribute the load to several web servers, each serving its own application area. In such a case, the reverse proxy may need to rewrite the URLs in each web page (translation from externally known URLs to the internal locations).
Serve/cache static content: A reverse proxy can offload the web servers by caching static content like pictures and other static graphical content. Compression: The proxy server can optimize and compress the content to speed up the load time. Spoon feeding: reduces resource usage caused by slow clients on the web servers by caching the content the web server sent and slowly "spoon feeding" it to the client. This especially benefits dynamically generated pages. Security: The proxy server is an additional layer of defense and can protect against some OS and web-server-specific attacks. However, it does not provide any protection from attacks against the web application or service itself, which is generally considered the larger threat.
Extranet publishing: a reverse proxy server facing the Internet can be used to communicate with a firewall server internal to an organization, providing extranet access to some functions while keeping the servers behind the firewalls. If used in this way, security measures should be considered to protect the rest of your infrastructure in case this server is compromised, as its web application is exposed to attack from the Internet.
A content-filtering web proxy server provides administrative control over the content that may be relayed in one or both directions through the proxy. It is commonly used in both commercial and non-commercial organizations (especially schools) to ensure that Internet usage conforms to acceptable use policy. Content filtering proxy servers will often support user authentication to control web access. It also usually produces logs, either to give detailed information about the URLs accessed by specific users or to monitor bandwidth usage statistics. It may also communicate to daemon-based or ICAP-based antivirus software to provide security against viruses and other malware by scanning incoming content in real-time before it enters the network. Many workplaces, schools, and colleges restrict websites and online services that are accessible and available in their buildings. Governments also censor undesirable content. This is done either with a specialized proxy, called a content filter (both commercial and free products are available), or by using a cache-extension protocol such as ICAP, which allows plug-in extensions to an open caching architecture. Websites commonly used by students to circumvent filters and access blocked content often include a proxy, from which the user can then access the websites that the filter is trying to block. Requests may be filtered by several methods, such as a URL or DNS blacklists, URL regex filtering, MIME filtering, or content keyword filtering. Blacklists are often provided and maintained by web-filtering companies, often grouped into categories (pornography, gambling, shopping, social networks, etc.). The proxy then fetches the content, assuming the requested URL is acceptable. At this point, a dynamic filter may be applied on the return path. For example, JPEG files could be blocked based on fleshtone matches, or language filters could dynamically detect unwanted language. If the content is rejected, then an HTTP fetch error may be returned to the requester. Most web filtering companies use an internet-wide crawling robot that assesses the likelihood that content is a certain type. Manual labor is used to correct the resultant database based on complaints or known flaws in the content-matching algorithms. Some proxies scan outbound content, e.g., for data loss prevention, or scan content for malicious software.
An anonymous proxy server (sometimes called a web proxy) generally attempts to anonymize web surfing. Anonymizers may be differentiated into several varieties. The destination server (the server that ultimately satisfies the web request) receives requests from the anonymizing proxy server and thus does not receive information about the end user's address. The requests are not anonymous to the anonymizing proxy server, however, and so a degree of trust is present between the proxy server and the user. Many proxy servers are funded through a continuous advertising link to the user. Access control: Some proxy servers implement a logon requirement. In large organizations, authorized users must log on to gain access to the web.
The organization can thereby track usage by individuals. Some anonymizing proxy servers may forward data packets with header lines such as HTTP_VIA, HTTP_X_FORWARDED_FOR, or HTTP_FORWARDED, which may reveal the IP address of the client. Other anonymizing proxy servers, known as elite or high-anonymity proxies, make it appear that the proxy server is the client. A website could still suspect a proxy is being used if the client sends packets that include a cookie from a previous visit that did not use the high-anonymity proxy server. Clearing cookies and possibly the cache would solve this problem.
This request is sent to the proxy server, the proxy makes the request specified, and returns the response. Some web proxies allow the HTTP CONNECT method to set up forwarding of arbitrary data through the connection; a common policy is to only forward port 443 to allow HTTPS traffic. Examples of web proxy servers include Apache (with mod_proxy or Traffic Server), HAProxy, IIS configured as proxy (e.g., with Application Request Routing), Nginx, Privoxy, Squid, Varnish (reverse proxy only), WinGate, Ziproxy, Tinyproxy, RabbIT and Polipo. For clients, the problem of complex or multiple proxy-servers is solved by a client-server Proxy auto-config protocol (PAC file).
By comparing the client's external IP address to the address seen by an external web server, or sometimes by examining the HTTP headers received by a server. A number of sites have been created to address this issue by reporting the user's IP address as seen by the site back to the user on a web page. Google also returns the IP address as seen by the page if the user searches for "IP". By comparing the results of online IP checkers when accessed using HTTPS vs. HTTP, as most intercepting proxies do not intercept SSL. If there is suspicion of SSL being intercepted, one can examine the certificate associated with any secure website; the root certificate should indicate whether it was issued for interception. By comparing the sequence of network hops reported by a tool such as traceroute for a proxied protocol such as HTTP (port 80) with that for a non-proxied protocol such as SMTP (port 25). By attempting to make a connection to an IP address at which there is known to be no server. The proxy will accept the connection and then attempt to proxy it on. When the proxy finds no server to accept the connection, it may return an error message or simply close the connection to the client. This difference in behavior is simple to detect. For example, most web browsers will generate a browser-created error page in the case where they cannot connect to an HTTP server, but will return a different error in the case where the connection is accepted and then closed. By serving the end-user specially programmed Adobe Flash SWF applications or Sun Java applets that send HTTP calls back to their server.
Tor is a system intended to provide online anonymity. Tor client software routes Internet traffic through a worldwide volunteer network of servers for concealing a user's computer location or usage from someone conducting network surveillance or traffic analysis. Using Tor makes tracing Internet activity more difficult, and is intended to protect users' personal freedom and their online privacy. "Onion routing" refers to the layered nature of the encryption service: The original data are encrypted and re-encrypted multiple times, then sent through successive Tor relays, each one of which decrypts a "layer" of encryption before passing the data on to the next relay and ultimately the destination. This reduces the possibility of the original data being unscrambled or understood in transit.
A residential proxy (RESIP) is an intermediary that uses a real IP address provided by an Internet service provider with physical devices such as mobile phones and end-user computers. Instead of connecting directly to a server, residential proxy users connect to the target through residential IP addresses. The target then identifies them as organic internet users. It does not let any tracking tool identify the reallocation of the user. Any residential proxy can send any number of concurrent requests, and IP addresses are directly related to a specific region. Unlike regular residential proxies, which hide the user's real IP address behind another IP address, rotating residential proxies, also known as backconnect proxies, conceal the user's real IP address behind a pool of proxies. These proxies switch between themselves at every session or at regular intervals. Despite providers' assertions that the proxy hosts are voluntarily participating, numerous proxies are operated on potentially compromised hosts, including Internet of things devices. Through the process of cross-referencing the hosts, researchers have identified and analyzed logs that have been classified as potentially unwanted program and exposed a range of unauthorized activities conducted by RESIP hosts. These activities encompassed illegal promotion, fast fluxing, phishing, hosting malware, and more.
A network outage at 2:10 AM rarely starts with a dramatic alarm. In my experience, it starts with small signals: login prompts that fail for no reason, random TLS warnings on internal apps, or one workstation that suddenly talks to everything. When I open Wireshark and inspect packets directly, those vague symptoms become concrete facts. I can see who is talking, what protocol is involved, and whether the traffic pattern is normal or manipulated.
2. System Architecture & Core Working Principles That is why I treat sniffing and spoofing as one connected topic. Sniffing is my microscope. Spoofing is one of the major threats I am trying to detect with that microscope. If I only learn packet capture without learning spoofing indicators, I miss the point. If I only read about spoofing without packet-level evidence, incident response becomes guesswork.
In this guide, I walk through the exact workflow I use on Linux with Wireshark: legal setup, focused capture, high-signal display filters, ARP-centric spoofing detection, and practical response steps. I also add what most quick guides skip: edge cases, false positives, storage strategy, and operational decision rules for real incidents. Sniffing means intercepting and reading packets that move across my network interface. I think of it like listening to a busy office hallway. I am not changing the conversation; I am observing who speaks, how often, and what language they use.
Spoofing means someone is lying about identity data in those packets. On a local network, that often means forged ARP replies or changed MAC/IP relationships. On wider networks, that can include forged source IP values, manipulated DNS responses, or fake sender identity in email flows. A lot of teams blend those into one giant activity and get stuck. They capture everything, panic at packet volume, and fail to extract a decision. My goal is never to read every packet. My goal is to gather enough packet evidence to make one correct operational decision at a time.
On Linux, I validate interfaces first using ip -br link . I then verify IP assignment with ip -br addr so I do not capture on the wrong interface. If I need continuous evidence during incident response, I run ring-buffer capture from terminal so I do not lose early activity and do not fill disk: For lab practice, I simulate permission discipline too. Treating a lab like production makes incident behavior reliable later.
I start Wireshark, choose the active interface, and capture 60 to 120 seconds of known-good activity first. I call this my baseline window. During that minute I do predictable actions: one DNS lookup, one app login, one internal API request, one file access. I inspect protocol dominance. If I expect HTTPS and see Telnet or FTP, risk is immediate. I do not need advanced forensics to flag it.
I open conversations and endpoints to identify top talkers. One host with unusual volume can indicate malware, misconfiguration, or scanning. I scan for abrupt packet-rate jumps. Spoofing, scanning, and retransmission storms usually leave visible bursts. When people paste ten filters in a row, context disappears. I force one active question at a time: That keeps analysis short and defensible. I can explain every containment action with packet evidence.
Not every packet matters equally. I prioritize weak or high-value protocols because they produce fast signal. I compare responders over time. If a host that is not a resolver starts answering many queries, I treat that as high-priority anomaly. If a protocol can carry credentials in cleartext, it becomes high priority immediately. One quick packet finding can prevent hours of uncertain investigation.
When most teams say spoofing on a LAN incident, they usually mean ARP spoofing. ARP maps IP addresses to MAC addresses in local broadcast domains. If an attacker poisons ARP caches, devices send traffic to the wrong MAC, often through an attacker-controlled host. Important point: Wireshark does not perform spoofing attacks by itself. In operations, I use Wireshark as a defensive detection and validation tool.
Healthy segments usually have stable IP-to-MAC mappings for gateway and DNS infrastructure. During poisoning, mappings flip or conflicting replies appear. Then I compare eth.src values across those packets. Multiple MAC addresses claiming the gateway IP in a tight window is a serious indicator.
If hosts in the same segment disagree on gateway MAC mapping, I assume active manipulation or severe misconfiguration until proven otherwise. The biggest practical problem is not filter syntax. It is operational capture design. On active networks, naive capture setups either miss bursts or drown storage.
BPF capture filters reduce ingest load before packets ever hit disk. Display filters are for analysis after capture. Mixing those concepts causes performance pain. This is where many investigations go wrong. Not every unusual ARP pattern is malicious. In HA environments, a virtual IP may move between nodes during failover. That creates MAC shift events that resemble poisoning.
Virtual switches, MAC masquerading, and overlay fabrics can produce surprising mappings. Theory is useful, but decisions are made inside specific scenarios. These are common cases I see. In 2026, surrounding tooling changed how fast I move, but packet logic stayed the same. My operating principle is simple: automation summarizes, humans decide. In spoofing incidents, false confidence is expensive.
Most packet workflows fail quietly on performance. Either capture drops packets under load, or analysis becomes too slow to support real-time response. I watch for dropped packets in capture statistics. Even a small drop rate can hide critical attack evidence during bursts. Large files make Wireshark navigation slow. I pre-trim with tshark or editcap before deep analysis.
If one host sends repeated unsolicited ARP replies, I isolate that port or VLAN quickly. I capture a short post-containment window and verify that critical IPs map consistently to expected MAC addresses. I keep original captures immutable, hash them, and record chain-of-custody notes. This matters if incidents escalate to formal investigation.
If I need long-window behavioral analysis, I use Zeek logs alongside packet captures. It is easier to query historical patterns at scale. 3. Software Implementation, Frameworks & Protocols For continuous spoofing-adjacent detections, IDS tooling can raise early alerts. I still verify with packet evidence before major containment.
ARP inspection, DHCP snooping logs, and MAC flapping events from switches often confirm root cause quickly. If endpoint EDR shows process-level network behavior, I map packet anomalies back to process lineage to accelerate remediation. Sniffing is strongest when I need protocol truth under uncertainty. I use it when logs disagree, endpoint telemetry is incomplete, or network identity looks suspicious. It is also ideal for validating whether a control change worked. If I disable a risky protocol, packet capture is my final proof.
I do not start with packet capture for every issue. If an outage is clearly tied to one failed deployment and application logs already show root cause, Wireshark may add delay. I also avoid broad sniffing in sensitive environments unless scope and handling rules are agreed first. Those habits can reduce investigation time from hours to minutes in many LAN spoofing incidents.
If you want this to become operational muscle, not just a one-off skill, I suggest a staged rollout. By the end of 90 days, teams usually move from reactive packet browsing to repeatable, evidence-driven response. When spoofing is suspected, speed matters, but accuracy matters more. I rely on Wireshark and tshark because packets show what actually happened, not what systems guessed happened. The best results come from a disciplined pattern: legal scope, focused capture, hypothesis-driven filters, quick containment, and post-incident hardening.
Your next practical step is simple: run a 15-minute controlled capture on a non-production segment, apply the filters in this guide, and document what normal looks like. That baseline becomes your reference the day suspicious ARP behavior appears. When that day comes, you will not be guessing. You will be reading evidence and making fast, defensible decisions. I still see strong C++ teams ship avoidable bugs because type assumptions stay implicit. A function quietly expects an integer, another expects a trivially copyable… You can write C++ that “works” and still ship subtle type bugs: accidental copies instead of moves, the wrong overload selected, a template accepting floating-point… I still remember the first time I saw #include in a teammate’s solution. The code looked almost suspiciously clean: one include, a using namespace std;,… You can run a Git repository for years and still get bitten by two tiny files: .gitignore and .gitattributes. I see this constantly when teams… Most performance problems I see in Python services aren’t “Python is slow” problems—they’re “we’re waiting on the network” problems. You call an HTTP API, the… I still see experienced Python developers lose time to one tiny operator: is. The bug usually looks harmless: a conditional that “obviously” should be true,… Sniffing and spoofing are two fundamental techniques used during network security assessments to analyze, monitor and evaluate network communication. In Kali Linux, these techniques help penetration testers identify insecure protocols, misconfigurations, weak authentication mechanisms and vulnerabilities in local networks.
Sniffing is the process of capturing and analyzing network packets traveling across a network. It enables security professionals to inspect communication between systems, identify insecure protocols, troubleshoot network issues and detect sensitive information transmitted without encryption. Types of Sniffing: A structured packet sniffing workflow helps security professionals capture and analyze network traffic efficiently while minimizing unnecessary data collection. The following steps outline the standard process used during network security assessments.
Spoofing is the technique of forging network identities to impersonate trusted devices, users or services. The objective is to redirect traffic, bypass security mechanisms or evaluate the effectiveness of network defenses. Types of Spoofing: Ettercap is an open-source network analysis framework designed to intercept, inspect and manipulate network traffic. It primarily targets Local Area Networks (LANs) by placing the attacker's system between communicating devices using techniques such as ARP spoofing.
Ettercap features a comprehensive suite of capabilities for network security analysis: Ettercap executes this man-in-the-middle (MITM) workflow through a precise sequence of network-level maneuvers. By manipulating how switches and devices route traffic, it forces network data to flow through the attacker's machine before reaching its final destination. Step-by-Step Technical Execution: Ettercap categorizes its sniffing operations into two distinct modalities, depending on the architecture of the network infrastructure being analyzed.
When traffic flows through Ettercap, it processes the packets through specialized decoders to extract specific plaintext data types: ARP spoofing is the mechanism that transitions Ettercap from a passive listener into an active intermediary. By exploiting the trust-based design of the Address Resolution Protocol, it re-routes data paths at the Link Layer of the OSI model. Key Aspects of Ettercap Spoofing: Ettercap is pre-installed in most Kali Linux releases. To verify its installation, run: If Ettercap is not installed or you want the latest package from the Kali repositories, update the package list and install it: Media Access Control (MAC) address spoofing is a fundamental technique in both offensive security operations and defensive network hardening. By altering a network interface’s hardware identifier, security professionals can test access controls, enhance privacy, and simulate attacker movements, while defenders must understand these tactics to detect and prevent unauthorized network presence. This comprehensive guide explores the practical implementation of MAC address modification across various platforms, providing verified commands for penetration testers, network administrators, and cybersecurity enthusiasts.
Step-by-step guide explaining what this does and how to use it: First, identify your network interface using ip link show . The `ip link set` method provides temporary MAC modification that resets after reboot – ideal for penetration testing engagements. For more advanced functionality, macchanger offers vendor-specific randomization and permanent MAC restoration. Permanent changes require systemd network configuration modifications, ensuring the spoofed MAC persists across reboots for long-term operational security.
Step-by-step guide explaining what this does and how to use it: Windows provides multiple MAC spoofing avenues with different persistence levels. The `getmac /v` command reveals current MAC addresses and interface names. Registry modification offers the most permanent solution but requires identifying the correct interface GUID from the registry class. PowerShell’s `Set-NetAdapter` provides quick temporary changes ideal for security testing, while the Device Manager GUI method offers straightforward point-and-click configuration for less technical users.
Step-by-step guide explaining what this does and how to use it: macOS utilizes the `ifconfig` command with the `ether` parameter for MAC address modification. The `networksetup` command helps identify correct interface names (typically en0, en1). For operational security, security professionals can implement automated MAC rotation using the provided script, which changes the MAC address at regular intervals to avoid persistent tracking on monitored networks.
Step-by-step guide explaining what this does and how to use it: Defensive monitoring requires establishing MAC address baselines and detecting anomalies. The Linux script continuously logs MAC addresses for comparison, while arpwatch provides enterprise-level MAC-IP pairing monitoring. SNORT rules can detect suspicious MAC patterns, particularly the all-zero MAC address often used in testing or malicious activities. Regular auditing of these detection mechanisms is crucial for identifying potential network intrusions.
Step-by-step guide explaining what this does and how to use it: Advanced persistence mechanisms ensure MAC address changes survive reboots and network resets. Linux udev rules automatically apply MAC changes when interfaces are detected, while systemd services can randomize addresses at boot time. Windows Group Policy can restrict network connectivity based on MAC addresses, providing defensive countermeasures. These techniques represent enterprise-level implementations suitable for red team operations and advanced security testing.
Step-by-step guide explaining what this does and how to use it: Programmatic MAC address manipulation enables automation and integration with larger security toolkits. The Python script demonstrates cross-platform compatibility, while API integration with MAC address databases ensures vendor-appropriate addresses that appear legitimate during network reconnaissance. These scripting approaches allow security teams to incorporate MAC spoofing into automated penetration testing frameworks and continuous security validation pipelines.
Step-by-step guide explaining what this does and how to use it: Wireless networks present unique MAC spoofing challenges due to association requirements and monitoring capabilities. The wireless tools command sequence ensures proper interface management before MAC modification, while monitor mode operations require special consideration for packet injection capabilities. WPA2-Enterprise networks often track MAC addresses for authentication persistence, requiring additional configuration parameters in wpa_supplicant for successful connectivity with spoofed addresses.
The evolution of MAC address spoofing reflects the broader cat-and-mouse game between offensive security practitioners and defensive technologies. While the technical capability to modify MAC addresses has existed for decades, modern implementations focus on persistence, automation, and anti-forensics. Defensive technologies have similarly advanced, with machine learning algorithms now capable of detecting MAC randomization patterns and vendor identifier inconsistencies. The operational security implications are significant – temporary MAC changes suffice for basic privacy concerns, but sophisticated red team operations require the persistent modification techniques outlined in this guide. As network access control systems increasingly incorporate behavioral analytics, the future of MAC spoofing lies in more sophisticated emulation of legitimate device behavior rather than simple address modification.
4. Practical Deployment, Analysis & Case Studies The increasing integration of MAC address analysis with behavioral biometrics and machine learning will render basic spoofing techniques detectable within 24-36 months. Next-generation network access control systems will correlate MAC addresses with device fingerprinting, TCP stack implementation differences, and timing analysis to identify spoofed presence.
However, advanced frameworks incorporating comprehensive device emulation will emerge, creating an arms race between detection and evasion capabilities. Regulatory frameworks will likely evolve to mandate MAC randomization for consumer privacy protection, potentially normalizing the technique while simultaneously driving innovation in enterprise detection capabilities.
Reported By: Md Minhaj – Hackers Feeds Extra Hub: Undercode MoN Basic Verification: Pass I We do not sell your personal data. If you wish to exercise your rights under applicable privacy laws, please visit our Do Not Sell My Personal Information page. A MAC address is a 48-bit (6 bytes) address that is usually assigned by the manufacturer of a network interface card (NIC). It is typically represented in hexadecimal notation, with six pairs of characters separated by colons (e.g., 00:11:22:33:44:55).
The first three bytes are known as the Organizationally Unique Identifier (OUI), which identifies the manufacturer, while the last three bytes are device-specific. MAC address spoofing involves changing the MAC address that a network interface presents to the network. When you spoof a MAC address, the network sees your device as if it were another device with the spoofed MAC address. This can be useful in situations where a network restricts access based on MAC addresses or when you want to hide your true identity on the network.
The ip command (part of the iproute2 package) is the modern and recommended networking utility in Linux for configuring network interfaces. It replaces the older ifconfig command. Here's how you can use it to spoof a MAC address: Replace 00:11:22:33:44:55 with the MAC address you want to use. For best results, use a real vendor prefix (the first three bytes) with random values for the last three bytes to avoid detection by networks that validate OUIs.
GNU MAC Changer ( macchanger ) is a dedicated utility that makes manipulating MAC addresses easier. It provides features such as setting a fully random MAC, setting a MAC from a specific vendor, or returning to the original hardware address. Note: The network interface must be down before changing the MAC address with macchanger. Bring it down with sudo ip link set eth0 down first, or macchanger will handle this automatically on some distributions.
The ifconfig command is a legacy networking utility in Linux. It has been deprecated in favor of the ip command from the iproute2 package, and may not be installed by default on newer distributions. However, if you still have it available, here's how to use it: The above methods only change the MAC address temporarily (until reboot). To make the change permanent, you have several options depending on your distribution and init system.
Using systemd.link (works on any systemd-based distribution): Create a file /etc/systemd/network/01-mac.link : To randomize the MAC on every boot, use MACAddressPolicy=random instead of specifying a static address. Enable with sudo systemctl enable [email protected] . This runs before your network manager starts. On desktop Linux distributions using NetworkManager (GNOME, KDE, etc.), MAC address randomization is built in.
NetworkManager supports two types of randomization: Randomization during Wi-Fi scanning (enabled by default): Prevents tracking while scanning for networks. Randomization for network connections : Configure via /etc/NetworkManager/conf.d/wifi_rand_mac.conf : The stable mode generates a random MAC per network and reuses it on reconnect. The random mode generates a new MAC every time you connect.
You can also configure per-connection MAC randomization through the NetworkManager GUI or nmcli : Note: When using iwd as a Wi-Fi backend, NetworkManager ignores MAC spoofing options. Configure MAC randomization in /etc/iwd/main.conf instead. Some networks restrict access based on MAC addresses. For example, a Wi-Fi network may only allow devices with specific MAC addresses to connect. By spoofing the MAC address of an allowed device, you can bypass this restriction and gain access to the network.
When you connect to a network, your MAC address is visible to other devices on the network. By spoofing your MAC address, you can hide your true identity and make it more difficult for others to track your device across different networks. Modern operating systems, including Linux, Android, iOS, and Windows, now randomize MAC addresses by default when scanning for Wi-Fi networks to enhance user privacy.
Network administrators can use MAC address spoofing to test the security of their networks. By attempting to spoof MAC addresses and gain unauthorized access, they can identify vulnerabilities in their network security policies and verify that port security or MAC filtering is properly configured. MAC address spoofing in Linux is a powerful technique that can be used for various legitimate purposes. By understanding the fundamental concepts, usage methods, common practices, and best practices, you can effectively use MAC address spoofing to bypass network restrictions, enhance privacy, or test network security. The ip link command and macchanger are the most commonly used tools, while NetworkManager provides built-in randomization for desktop users. However, it's important to use this technique responsibly and in compliance with the law.
This article explores how the Linux operating system prevents and mitigates Media Access Control (MAC) address spoofing directly at the network interface layer. It covers core kernel configurations, bridge security parameters, Virtual Function (VF) hardware controls via iproute2 , and low-level packet filtering frameworks such as eBPF/XDP and nftables . By implementing these interface-level mechanisms, administrators can enforce strict identity validation and drop unauthorized Layer 2 frames before they traverse the host or virtualized network infrastructure.
In virtualized environments utilizing Single Root I/O Virtualization (SR-IOV), the Linux kernel delegates interface management to Virtual Functions (VFs) mapped directly to virtual machines or containers. Linux mitigates MAC spoofing here by leveraging the physical network card's hardware capabilities through the ip link tool. Administrators configure the physical function (PF) to enforce static MAC addresses on child VFs and enable hardware-level spoof checking: When spoofchk on is active, the network interface controller (NIC) firmware inspects the source MAC address of every outbound Ethernet frame originating from the VF. If the frame's source address does not match the administratively assigned MAC address, the NIC drops the packet in hardware, preventing it from ever reaching the physical switch.
When Linux operates as a software bridge (using bridge-utils or the native kernel bridge module), it can enforce Layer 2 port restrictions using ebtables or the modern nftables bridge family. Using nftables in the bridge family allows rules to intercept frames traversing bridge ports. Administrators can tie specific incoming switch ports to specific allowed MAC addresses: Any frame entering via veth-guest1 with an unapproved source MAC is immediately dropped at the ingress hook, neutralizing spoofing attempts across internal bridge ports.
For high-throughput environments, Linux supports eXpress Data Path (XDP) and extended Berkeley Packet Filters (eBPF). XDP executes directly at the network device driver level before the packet buffer ( sk_buff ) is allocated by the kernel. An XDP program attached to an interface can read the Ethernet header and cross-reference the source MAC against an approved kernel BPF map: This approach mitigates MAC spoofing with near-zero CPU overhead and prevents cache pollution in the kernel network stack.
Linux provides the macvlan driver to create multiple virtual network interfaces with distinct MAC addresses tied to a single physical interface. To control MAC spoofing in these architectures, Linux supports macvlan in private, VEPA (Virtual Ethernet Port Aggregator), or bridge mode. In private mode, the driver prevents endpoints on the same physical link from communicating directly with each other, forcing traffic to an external upstream switch that handles Layer 2 policy enforcement. Additionally, the driver discards frames if the guest environment attempts to transmit traffic with source MACs unmapped to that specific macvlan device endpoint.
This project demonstrates the use of the macchanger tool in Kali Linux to simulate MAC address spoofing, and the detection of such activities using Wazuh SIEM. The project was conducted as part of a cybersecurity internship (Skillogic, Phase 3) with a goal to enhance endpoint visibility and security monitoring. 5. Performance Evaluation & Extended Technical Observations This simulation validated the effectiveness of MAC spoofing and how it can be monitored using a SIEM. It reinforced the importance of real-time endpoint monitoring and anomaly detection for network security teams.
Media Access Control (MAC) randomization can be used for increased privacy by not disclosing your real MAC address to the network. This article gives several methods to spoof a MAC address. There are two methods for spoofing a MAC address: installing and configuring either iproute2 or macchanger . Both of them are outlined below.
The section that interests us at the moment is the one that has "link/ether" followed by a 6-byte number. It will probably look something like this: The first step to spoofing the MAC address is to bring the network interface down. It can be accomplished with the command: Next, we actually spoof our MAC. Any hexadecimal value will do, but some networks may be configured to refuse to assign IP addresses to a client whose MAC does not match up with any of known vendors. Therefore, unless you control the network(s) you are connecting to, use MAC prefix of any real vendor (basically, the first three bytes), and use random values for next three bytes. For more information please read Wikipedia:Organizationally unique identifier .
The final step is to bring the network interface back up. This can be accomplished by running the command: If you want to verify that your MAC has been spoofed, simply run ip link show interface again and check the value for 'link/ether'. If it worked, 'link/ether' should be whatever address you decided to change it to. Another method uses macchanger (a.k.a., the GNU MAC Changer). It provides a variety of features such as changing the address to match a certain vendor or completely randomizing it.
The spoofing is done on per-interface basis, specify network interface name as interface in each of the following commands. To randomize only device-specific bytes of current MAC address (that is, so that if the MAC address was checked it would still register as being from the same vendor), you would run the command: udev allows you to perform MAC address spoofing by creating systemd.link(5) files or udev rules.
To randomize the MAC address on every boot, set MACAddressPolicy=random instead of MACAddress= spoofed MAC . Use address attribute to match the correct device by its original MAC address and change it using the ip command: Below you find two examples of systemd units to change a MAC address at boot, one sets a static MAC using ip and one uses macchanger to assign a random MAC address. The systemd network-pre.target is used to ensure the MAC is changed before a network manager like Netctl or NetworkManager , systemd-networkd or dhcpcd service starts.
systemd unit setting a random address while preserving the original NIC vendor bytes. Ensure that macchanger is installed : Append the desired network interface to the service name (e.g. eth0 ) and enable the service (e.g. macspoof@eth0.service ). Reboot, or stop and start the prerequisite and requisite services in the proper order. If you are in control of your network, verify that the spoofed MAC has been picked up by your router by examining the static, or DHCP address tables within the router.
You can use a netctl hook to run a command each time a netctl profile is re-/started for a specific network interface. Replace interface accordingly: NetworkManager supports two types MAC Address Randomization: randomization during scanning, and for network connections. Both modes can be configured by modifying /etc/NetworkManager/NetworkManager.conf or by creating a separate configuration file in /etc/NetworkManager/conf.d/ which is recommended since the aforementioned configuration file may be overwritten by NetworkManager.
Randomization during Wi-Fi scanning is enabled by default, but it may be disabled by adding the following lines to /etc/NetworkManager/NetworkManager.conf or a dedicated configuration file under /etc/NetworkManager/conf.d : MAC randomization for network connections can be set to different modes for both wireless and ethernet interfaces. In terms of MAC randomization the most important modes are stable and random . stable generates a random MAC address when you connect to a new network and associates the two permanently. This means that you will use the same MAC address every time you connect to that network. In contrast, random will generate a new MAC address every time you connect to a network, new or previously known. You can configure the MAC randomization by adding the desired configuration under /etc/NetworkManager/conf.d : To configure MAC randomization for a specific connection (for example, if the network does not like random MAC addresses), edit the connection to set 802-11-wireless.cloned-mac-address to one of the modes (e.g. stable or random ).
wpa_supplicant can use random MAC address for each ESS connection(AP) (see [2] for details). Specifying AddressRandomization enables control over when MAC address is randomized. If set to disabled MAC is not spoofed and AddressRandomizationRange is ignored. If set to once MAC is assigned every time iwd is started. If set to network MAC is spoofed once for each network and reused for each connection to a known network.
Specifying AddressRandomizationRange enables control over which part of the address is randomized. If set to nic , only the NIC specific octets (last three octets) are randomized. The permanent mac address of the network interface is used for the initial 3 octets. If set to full , all six octets of the address are randomized. If you cannot connect to a DHCPv4 network and you are using dhcpcd, you might need to modify the dhcpcd configuration to obtain a lease.
MAC stands for Media Access Control — a six-byte identifier (usually written as twelve hexadecimal digits) that uniquely identifies a network interface on a LAN. The Address Resolution Protocol (ARP) maps IP addresses to MAC addresses at layer 2. The ifconfig command is deprecated. Use ip instead, which works on all modern distributions: For permanent MAC spoofing, configure it in your network management layer rather than relying on runtime commands.
Persistence: Runtime changes with ip are lost on reboot. Use systemd-networkd, NetworkManager, or udev rules for persistence. Virtualization: In VMs, MAC changes may be restricted by the hypervisor. Check your VM settings. DHCP complications: Some DHCP servers cache leases by MAC address. After spoofing, you may need to release and renew: Interface naming: Modern systemd uses predictable interface naming (eno1, enp3s0, etc.). Adjust commands accordingly.
Use ip link to list all interfaces. Wireless interfaces: MAC spoofing on WiFi requires the interface to be down and may be blocked by some drivers. Check iw capabilities: SELinux/AppArmor: Confined systems may restrict macchanger or ip link set address . Check policy rules if commands fail.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/ARP%20spoofing • https://en.wikipedia.org/wiki/IPv6%20address • https://en.wikipedia.org/wiki/Proxy%20server • https://thelinuxcode.com/wireshark-sniffing-and-spoofing-a-practical-incident-ready-playbook/ • https://www.geeksforgeeks.org/linux-unix/kali-linux-sniffing-and-spoofing/ • https://www.geeksforgeeks.org/linux-unix/ettercap-sniffing-and-spoofing/ • https://undercodetesting.com/the-ultimate-mac-address-spoofing-guide-offensive-and-defensive-tactics-exposed/ • https://linuxvox.com/blog/linux-spoof-mac-address/ • https://salivity.github.io/linux/article/linux-mac-spoofing-mitigation-at-interface-level • https://github.com/siddh358/macchanger-network-security
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Mac Address Spoofing Detection Tool For Linux.
[*] Metasploit Scan Running on Target Subnet for Mac Address Spoofing Detection Tool For Linux... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |