Complete Technical Paper Content — Mac Filtering Bypass Alert System
Overview & System Context
Mac Filtering Bypass Alert System: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~7774 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background An Internet filter is software that removes certain network traffic, which can be done with or without informed consent of the end user. Restrictions can be applied at various levels: a government can attempt to apply them nationwide (see Internet censorship), or they can, for example, be applied by an Internet service provider to its clients, by an employer to its personnel, by a school to its students, by a library to its visitors, by a parent to a child's computer, or by an individual user to their own computers. The motive is often to prevent access to content which the computer's owner(s) or other authorities may consider objectionable. When imposed without the consent of the user, content control can be characterized as a form of internet censorship. Some filter software includes time control functions that empowers parents to set the amount of time that child may spend accessing the Internet or playing games or other computer activities.
The Internet does not intrinsically provide content blocking, and therefore there is much content on the Internet that is considered unsuitable for children, given that much content is given certifications as suitable for adults only, e.g. 18-rated games and movies. Internet service providers (ISPs) that block material containing pornography, or controversial religious, political, or news-related content en route are often utilized by parents who do not permit their children to access content not conforming to their personal beliefs. Content filtering software can, however, also be used to block malware and other content that is or contains hostile, intrusive, or annoying material including adware, spam, computer viruses, worms, trojan horses, and spyware. Most content control software is marketed to organizations or parents. It is, however, also marketed on occasion to facilitate self-censorship, for example by people struggling with addictions to online pornography, gambling, chat rooms, etc. Self-censorship software may also be utilised by some in order to avoid viewing content they consider immoral, inappropriate, or simply distracting. A number of accountability software products are marketed as self-censorship or accountability software. These are often promoted by religious media and at religious gatherings.
Content filtering technology exists in two major forms: application gateway or packet inspection. For HTTP access the application gateway is called a web-proxy or just a proxy. Such web-proxies can inspect both the initial request and the returned web page using arbitrarily complex rules and will not return any part of the page to the requester until a decision is made. In addition they can make substitutions in whole or for any part of the returned result. Packet inspection filters do not initially interfere with the connection to the server but inspect the data in the connection as it goes past, at some point the filter may decide that the connection is to be filtered and it will then disconnect it by injecting a TCP-Reset or similar faked packet.
The two techniques can be used together with the packet filter monitoring a link until it sees an HTTP connection starting to an IP address that has content that needs filtering. The packet filter then redirects the connection to the web-proxy which can perform detailed filtering on the website without having to pass through all unfiltered connections. This combination is quite popular because it can significantly reduce the cost of the system. There are constraints to IP level packet-filtering, as it may result in rendering all web content associated with a particular IP address inaccessible. This may result in the unintentional blocking of legitimate sites that share the same IP address or domain. For instance, university websites commonly employ multiple domains under one IP address. Moreover, IP level packet-filtering can be surpassed by using a distinct IP address for certain content while still being linked to the same domain or server. Gateway-based content control software may be more difficult to bypass than desktop software as the user does not have physical access to the filtering device. However, many of the techniques in the Bypassing filters section still work.
Content filtering in general can "be bypassed entirely by tech-savvy individuals." Blocking content on a device "[will not]…guarantee that users won't eventually be able to find a way around the filter." Content providers may change URLs or IP addresses to circumvent filtering. Individuals with technical expertise may use a different method by employing multiple domains or URLs that direct to a shared IP address where restricted content is present. This strategy doesn't circumvent IP packet filtering, however can evade DNS poisoning and web proxies. Additionally, perpetrators may use mirrored websites that avoid filters. Some software may be bypassed successfully by using alternative protocols such as FTP or telnet or HTTPS, conducting searches in a different language, using a proxy server or a circumventor such as Psiphon. Also cached web pages returned by Google or other searches could bypass some controls as well. Web syndication services may provide alternate paths for content. Some of the more poorly designed programs can be shut down by killing their processes: for example, in Microsoft Windows through the Windows Task Manager, or in Mac OS X using Force Quit or Activity Monitor.
Numerous workarounds and counters to workarounds from content-control software creators exist. Google services are often blocked by filters, but these may most often be bypassed by using https:// in place of http:// since content filtering software is not able to interpret content under secure connections (in this case SSL). An encrypted VPN can be used as means of bypassing content control software, especially if the content control software is installed on an Internet gateway or firewall.
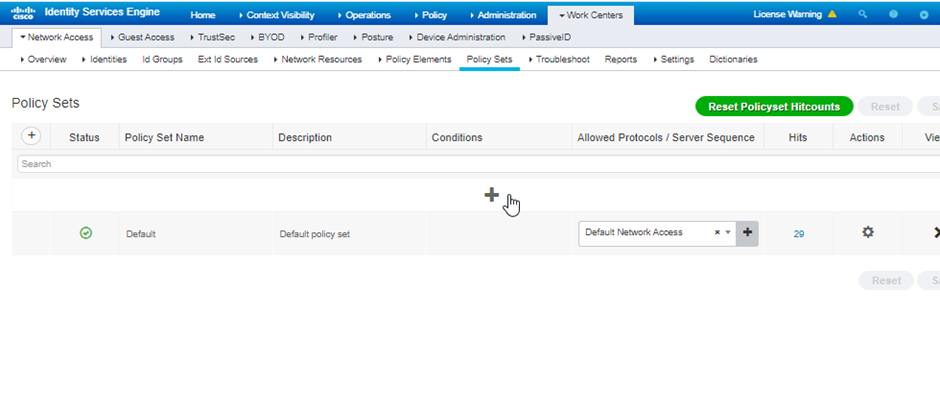
Other ways to bypass a content control filter include translation sites and establishing a remote connection with an uncensored device. Figure 1: Configuring MAC Authentication Bypass(MAB) in Cisco ISE:A Simple Guide ... Adultism Ad filtering Comparison of content-control software and providers (incl. parental control software) Computer and network surveillance Content moderation David Burt, a former librarian and advocate for content-control software Deep content inspection Egress filtering, control of outbound network traffic Financial Coalition Against Child Pornography Internet safety Nymwar Opposition to pornography Peacefire, a U.S.-based website dedicated to "preserving First Amendment rights for Internet users, particularly those younger than 18" Russian State Duma Bill 89417-6 - a proposed bill that would mandate content control software Scunthorpe problem Wordfilter, generic name for scripts typically used on Internet forums or chat rooms that automatically scans users' posts or comments as they are submitted and automatically changes or censors particular words or phrases Follow these steps to configure a wired device to authenticate devices based on their MAC addresses.
You can use MAC authentication along with certificate-based or credential-based authentication as an additional layer of security. HPE Mist Networking Access Assurance supports MAC Authentication Bypass (MAB) for uniform access control across wired and wireless networks. This topic provides an example for configuring MAB for a wired device.
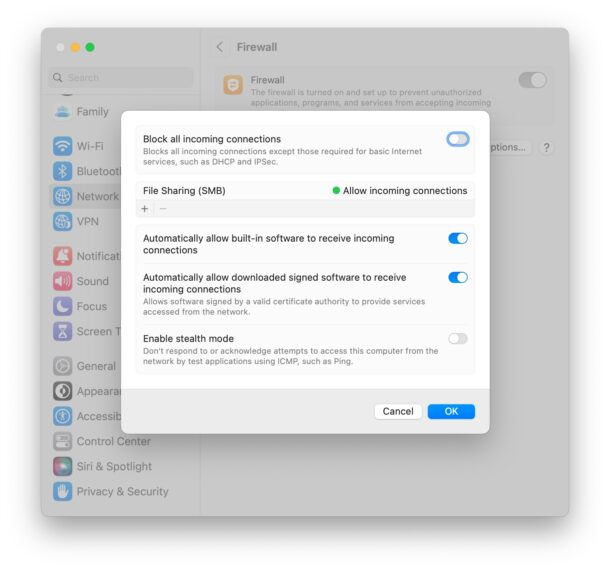
Figure 2: How to Enable or Disable Firewall on MacOS Ventura - OS X Daily The example shows you how to create MAC authentication for a wired device in addition to certificate-based EAP-TLS authentication. The task also includes the steps to create an authentication policy for a wired-side device that does not support dot 1x (such as a Phillips hub).
You must have already configured certificate-based authentication. See Configure Certificate-Based (EAP-TLS) Authentication for Wireless Network Learn how to configure and validate MAC-based authentication for wired devices by watching the following videos: Well, what about wired devices? How do we authenticate an authorized wired client? Well, it turns out we could do it right here in the same place. So we could create a couple of more rules. So we can say OK, if we look at wired devices that are using certificates to authenticate , we could just call this rule wired certificate authentication. We can effectively apply the same matching criteria as for wireless. There's no difference whatsoever here.
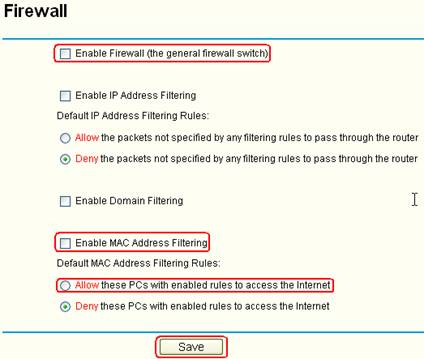
Figure 3: How to Configure MAC Filtering on TP-Link SMB Router (Old UI) On the right-hand side, we'll decide where we want to move these devices after authentication and the right policy match. And finally, what about non-.1x capable devices on the wired side? So for example, I have here a Phillips hub that does not support .1x. How can I authenticate a Phillips app? So I could create a label for the Phillips device. The label will be client list.
And I'll just say approved Phillips app. And I'll just put the MAC address of that device in. Oh. And you could put a list of MAC addresses. You can put the list of Mac OUIs. And remember that all of these labels that I'm creating in the UI - they're all available through the REST API. So there is always an endless possibility of integration with existing, say, inventory management systems that can just put all the new device MAC addresses in those lists for authentication and authorization.
So we'll just click Create. Create this label. And we'll create a rule. We'll call it approved Phillips devices. And here we are matching on wired devices that are doing MAC address authentication bypass that are part of this client list label. And in this case, we will move them to - well, I don't want to move them to Corp VLAN. That's not what I want. I will create an IoT VLAN. And in our case, that's going to be VLAN 3000. And I'm going to add this to an IoT VLAN. And now, we have our authentication policies configuration done.
OK, so how do we validate, right? So we've connected a couple of clients to the switch. One is a laptop that's doing .1x using certificate. Another one is the Phillips Hue app. That doesn't do any .1x, and just doing MAC authentication. So we could see those two clients are connected. Let's take a look at the laptop one. So we could click on the port. We see that there is a client with a username flashing up.
Let's take a look at the wired client insights. And what we can see here is that the user has been authenticated. You could see the port up and down events from the switch side. We see all the authentication phases, same as we saw in the wireless side. The client trusts the server. The server trusts the client certificate. We get all the metadata here. We then are saying client access is allowed. And voila. We matched the same authentication policy rule. Great. So now, we know that this part is working.
Now, we go to switch back. And let's look at the Philips device. That device is not doing any form of .1x authentication. So let's just take a look at the wired client insights. Yeah, and we are seeing that here the user is authenticated. And there is a client access allowed event here as well. And in this case, the authentication type is Mac address bypass - the MAC address that we've added to the client list. And voila. We are matching the right approved Phillips device rule.
This example uses the default values for the remaining fields. In the Select Switches Configuration section, on the Port Config tab, click Add Port Range to associate a port profile with a port. Enter a port ID and select the configuration profile that you created in the previous step.
Now your network is ready to securely authenticate clients. The HPE Mist cloud verifies the client certificates and grants access and authorization based on the authentication policy configuration. You reached this page when trying to access http://networklessons.com/switching/mac-authentication-bypass-mab from 34.24.219.195 on October 19 2026, 09:07:24 UTC Network Access Control solutions are a simple idea, 802.1X cert based authentication, great! works like a charm. However, businesses are complex beasts and not all systems on that network support 802.1X and/or cert based authenticaiton.
So if lets say your IP phones are on the same network, if we can find the correct MAC address we can essential spoof that address and access the network. This utility was designed for exactly this, MAC address manipulation and brute forcing. You’ve likely seen MAC filtering in action. The idea is simple: your router has a list of approved device MAC addresses. Only those devices get to join your Wi-Fi. It feels like a decent security measure, right? A digital bouncer at the door.
This isn’t about cracking Wi-Fi passwords, which is a whole different, and often much harder, beast. This is about bypassing a different kind of gate. The kind that checks your ID, but the ID is printed on your device’s network card and is surprisingly easy to counterfeit. Think of it like this: MAC addresses are the serial numbers of your network interfaces . Every Wi-Fi card, every Ethernet port, has one, burned into its hardware. It’s supposed to be unique, a global identifier. Like a fingerprint.
This is the core of MAC filtering evasion. The router trusts the MAC address presented by the device. It doesn’t inherently know if that MAC address truly belongs to the device it claims to be. It’s a trust system based on a mutable identifier. Maybe you’re physically near the network and can see a list of connected devices on the router’s admin page. Or perhaps you’ve previously been on the network and can see your own MAC address listed there.
Sometimes, you can even sniff the network traffic. If a device that is allowed on the network is broadcasting packets, you can potentially see its MAC address in the packet headers. Tools like Wireshark are fantastic for this, letting you see the digital whispers flying through the air. On Linux, this is often done with the ip link set dev
It’s like walking up to the bouncer, who’s expecting "Bob," and you just put on a "Bob" nametag. The bouncer sees "Bob," doesn’t ask for further ID, and lets you in. The impact? You’re now on the network. You can see other devices . You can potentially access shared resources. You can start sniffing traffic from inside the network.
Imagine a corporate network where only authorized laptops can join. Someone with physical access, or even someone who’s managed to get a rogue device onto the network once, can then clone the MAC address of an authorized laptop. 2. System Architecture & Core Working Principles Suddenly, they have access to sensitive internal systems, file shares, or even the ability to pivot to other parts of the network.
The MAC filter, which was supposed to be a layer of defense, becomes a non-issue. The failure mode is subtle. It’s not a crash. It’s not a denial of service. It’s a quiet, uninvited guest slipping through the front door because the doorman was a bit too trusting of the name tag. The realization hits when you’re troubleshooting why an unauthorized device is suddenly able to access resources it shouldn’t, and you discover its MAC address is identical to an authorized one. It’s the digital equivalent of finding a wolf wearing sheep’s clothing, but the sheep was just a name tag.
This is why MAC filtering alone is almost never considered a robust security measure. It’s a weak form of authentication. It’s like locking your front door but leaving the key under the mat. MAC filtering can be part of a defense. But it needs to be combined with stronger authentication methods . Think about WPA2-Enterprise or WPA3-Enterprise. These use RADIUS servers and individual user credentials (like usernames and passwords, or certificates). The network doesn’t just trust the device’s MAC address; it trusts the user or device identity validated by a central authority.
Or, consider network access control (NAC) solutions. These systems can go much further, checking not just the MAC address, but also the security posture of the device: is the antivirus up to date? Is the operating system patched? If not, even with a valid MAC address, access can be denied or restricted. The "aha!" moment for many engineers comes when they realize that a simple list of MAC addresses is like a list of names.
Anyone can write a name on a piece of paper. The real security comes from verifying who is behind that name. The irony is that MAC addresses are supposed to be unique. The first half of the MAC address (the OUI, or Organizationally Unique Identifier) is assigned by the IEEE to hardware manufacturers. The second half is supposed to be unique per device from that manufacturer.
But hardware manufacturers sometimes make mistakes. They might reuse OUIs, or their serial number generation might not be as robust as advertised. So, even the "unique" part can be less unique than you think. It’s a bit like finding out the unique serial number on your passport was accidentally printed on a dozen other passports. This means that even if you don’t know an authorized MAC address, there’s a non-zero chance of accidentally stumbling upon one if you’re trying to connect to a network with many devices. It’s like a lottery where the prize is unauthorized access.
The takeaway is that the simplicity of MAC filtering is its undoing. It’s easy to implement, which makes it appealing. But it’s also easy to circumvent because it relies on a single, easily spoofed piece of information. It’s a good first step, perhaps, but it’s a step that needs to be followed by many, much more rigorous ones. The world of network security is a constant game of cat and mouse. Attackers find a loophole, defenders patch it, attackers find a new one. MAC filtering evasion is just one of the many, many ways this dance plays out.
Learn how to enable MAC address filtering and how to configure MAC address accounting on Ethernet interfaces. MAC address filtering is a security feature that controls network access by filtering MAC addresses. To block all incoming packets from a specific MAC address, you can enable MAC address filtering. You can configure an Ethernet Interface to dynamically learn source or destination MAC addresses.
On Ethernet interfaces with SFPs, you can enable source address filtering to block all incoming packets from a specific MAC address. When you filter logical and physical interfaces, you can specify up to 1000 MAC source addresses per port. On aggregated Ethernet interfaces, Fast Ethernet, Gigabit Ethernet, Gigabit Ethernet IQ, and Gigabit Ethernet PICs with SFPs, you can enable source address filtering to block all incoming packets from a specific MAC address.
To enable the filtering, include the source-filtering statement at the [edit interfaces interface-name aggregated-ether-options | fastether-options | gigether-options] hierarchy level. When source address filtering is enabled, you can configure the interface to receive packets from specific MAC addresses. To do this, specify the MAC addresses in the source-address-filter mac-address statement at the [edit interfaces interface-name aggregated-ether-options | fastether-options | gigether-options] hierarchy levels.
You can specify the MAC address as nn : nn : nn : nn : nn : nn or nnnn . nnnn . nnnn , where n is a hexadecimal number. You can configure up to 64 source addresses. To specify more than one address, include the source-address-filter statement multiple times. Source address filtering does not work when Link Aggregation Control Protocol (LACP) is enabled.
If the remote Ethernet card is changed, the interface cannot receive packets from the new card because it has a different MAC address. To configure MAC address accounting on an individual Ethernet interface, include the mac-learn-enable statement at the [edit interfaces interface-name gigether-options ethernet-switch-profile] hierarchy level: To configure MAC address accounting on an aggregated Ethernet interface, include the mac-learn-enable statement at the [edit interfaces ae x aggregated-ether-options ethernet-switch-profile] hierarchy level.
To prohibit an interface from dynamically learning source and destination MAC addresses, do not include the mac-learn-enable statement. To disable dynamic learning of the source and destination MAC addresses after it has been configured, you must delete mac-learn-enable from the configuration.
MPCs support MAC address accounting for an individual interface or an aggregated Ethernet interface member link only after the interface has received traffic from the MAC source. If traffic is only exiting an interface, the MAC address is not learned and MAC address accounting does not occur. MAC-based access control admits or denies wireless association based on the connecting device’s MAC address. In this authentication method wireless devices use their MAC address as the username and password. Follow the steps below to configure an SSID to require MAC-based access control with RADIUS.
Note: To enable MAC-based access control without a RADIUS server, a Sign-on Splash page can be used in a similar fashion . 3. For Splash page choose None (direct access) . Click-through can be selected if desired. Select Cisco Identity Services Engine (ISE) Authentication if your setup uses the AVP Service Type - Call Check, otherwise the access points won't include it in their access-request packets.
4. For RADIUS servers , click Add server . Enter the RADIUS server IP address, listening port, and RADIUS shared secret to be used by your access points which are configured RADIUS clients on the server. 5. For Client IP and VLAN , choose External DHCP server assigned in a VLAN environment. Meraki AP assigned (NAT mode) could be used without VLANs if desired.
3. Software Implementation, Frameworks & Protocols 6. An SSID can bridge wireless devices onto different VLANs. A default SSID VLAN can be set using the VLAN tag drop down. Then by setting the RADIUS override it can override VLAN tag from VLAN override drop down . RADIUS accept messages containing a different VLAN tag will be able to override the default VLAN for the SSID.
This feature allows the use of a guest vlan for customers that do not complete authentication or when the RADIUS server is unreachable. A configuration where authenticated devices are desired to be on a designated VLAN and everything else, using the same SSID, would be placed in a Guest VLAN. This configuration can be used with VLAN tagging or without it, meaning the authorized clients can be put in the designated VLAN by VLAN tagging option, or can use the untagged VLAN the access point is using (default behavior without using vlan tagging).
In order to configure this feature, a new option can be found on Wireless > Configure > Access Control when MAC-based access control (no encryption) is selected. You will see the following option, where it can be enabled: Once enabled, the option to fill the Guest VLAN ID will be displayed where the VLAN ID can be input. In an SSID using MAC authentication with a VLAN tagging of 10, using RADIUS Guest VLAN with a Guest VLAN of 1.
When a client completes the authentication, meaning the RADIUS server is reachable and it received "Access-Accept" as a result of the authorization process. TL-WA860RE , TL-WA850RE , RE300 , RE190 , RE205 , RE750C , RE580D , RE590T , RE200 , RE210 , TL-WA854RE , TL-WA865RE Recent updates may have expanded access to feature(s) discussed in this FAQ. Visit your product's support page, select the correct hardware version for your device, and check either the Datasheet or the firmware section for the latest improvements added to your product. Please note that product availability varies by region, and certain models may not be available in your region.
Some customers tried to set up Mac Filtering on the main router to control the clients connected to the Range Extender, but they eventually found that their settings didn’t work normally. Here we will explain the reason and introduce the detailed steps to make it work. Actually Blue UI version of router already remove MAC filtering instead of Access control, and the guidance is only available for Green UI router.
Please make sure your Range Extender has connected to the router successfully and check which mode that your Range Extender is working on: Note: Most models of RE adopt Proxy mode by default and cannot be changed. RE355 and RE450 only support Universal Mode.
TL-WA830RE_V1,V2/TL-WA730RE/TL-WA750RE support Universal Mode and WDS mode.
TL-WA850RE_V1,V1.2/TL-WA860RE except of EU version could change among three modes. In the article, we will take RE210 and C7 as the example. Below is the network topology: Note: In this article, Mac Filtering aims to control the clients connected to the Range Extender, not the device connected to the router directly.
In Proxy Mode, Range Extender will replace each of its clients’ MAC address with a virtual MAC address generated automatically by Range Extender. Thus the router will take the virtual MAC address of the clients as their real MAC address, so that we need type the virtual MAC addresses of these clients in the MAC Filtering of the router instead of their real MAC addresses. By comparing the figures below, you can better understand the process.
a. Please check your computer’s MAC address just like this. Here is your computer’s real MAC address (XX-XX-XX–CE–14-93). b. Then check the MAC address of your computer shown on your Router’s Web page. Here is your computer’s virtual MAC address (XX-XX-XX–CE–14-93).
c. Now you can see the Router can only see your computer’s virtual MAC address but not real MAC address. But there is one important thing you should be aware of, which is the latter 24bits of each client’s virtual MAC address are exactly the same as the latter 24bits of client’s real MAC address. You can easily find the rule by comparing the above computer’s real MAC address (XX-XX-XX–CE–14-93) with its virtual MAC address (XX-XX-XX–CE–14-93).
a. Check your client devices’ real MAC address, and write them down. You will need them to find these client devices’ virtual MAC address. b. Log into the Web GUI of your router and go to DHCP Clients List . Here we can see all MAC addresses of devices associated to the router. By comparing these MAC addresses’ latter 24bits with your client devices’ real MAC address’ latter 24bits, you can easily find your client devices’ virtual MAC address. Then write them down. You will need them.
Note: If you have no idea how to check the DHCP Clients List of your router, please contact the vendor of your router for help. Single band Range Extender like TL-WA850RE has one 2.4GHz MAC address, and dual band Range Extender has two MAC addresses which are used on 2.4GHz and 5GHz respectively. a. Log into the Web GUI of your router and select Wireless 2.4GHz -> Wireless Statistics , you can see the MAC addresses of the devices associated to your router on 2.4GHz band. By comparing these MAC addresses with the MAC address printed on the back of your Range Extender, you can easily find that“XX-XX-XX-42-B8-E5” is the MAC address your range extender uses at 2.4GHz.
b. If your Range Extender is dual band Range Extender, then you will still need to find its 5GHz MAC address. Almost same step as step a) , you can easily find your Range Extender’s 5GHz MAC address (XX-XX-XX-42-B8-E7). Actually Range Extender’s 2.4GHz MAC address is very similar with its 5GHz MAC address. You can easily find the rule by comparing the Range Extender’s 2.4GHz MAC address (XX-XX-XX-42-B8-E5) with its 5GHz MAC address (XX-XX-XX-42-B8-E7).
Note: If you have no idea how to check the Wireless Statistics of your router, please contact the vendor of your router for help. 4. Configure MAC filtering (Black List): block the stations specified by enabled entries in the list to access Internet. Here we’ll take the White List of Archer C7 as an example to introduce how to use virtual MAC address to set MAC Filtering. a. Log into Web GUI of the router and select Wireless 2.4GHz -> wireless M ac filtering -> Add new. Then type in the Virtual MAC Address of your PC and select status as Enabled->Save .
b. Now you should click enable. Then only the computer you have specified in the list cannot access to the Internet. c. It is not recommended to configure White list on router, in view of that RE’s MAC addresses are too complicate to find and add completely. Note: If you have no idea how to configure MAC filtering of your router, please contact the vendor of your router for help.
In this mode, Range Extender will replace all its clients’ MAC addresses with RE’s own MAC address! That means we only need to type RE’s MAC address in the MAC Filtering of the router: 4. Practical Deployment, Analysis & Case Studies If your Ranger Extender is working in WDS Mode, Range Extender won’t replace clients’ MAC address with either a virtual MAC or RE’s own MAC address while it will use the real MAC address of these clients. Therefore, we only need to type these client devices’ real MAC address in MAC Filtering of the router. No other special configuration needed.
Get to know more details of each function and configuration please go to Download Center to download the manual of your product. Still need help? Search for answers, ask questions, and get help from TP-Link experts and other users around the world. accepted_local_switcher, tp_privacy_banner, tp_privacy_base, tp_privacy_marketing, tp_top-banner, tp_popup-bottom, tp_popup-center, tp_popup-right-middle, tp_popup-right-bottom, tp_productCategoryType id, VISITOR_INFO1_LIVE, LOGIN_INFO, SIDCC, SAPISID, APISID, SSID, SID, YSC, __Secure-1PSID, __Secure-1PAPISID, __Secure-1PSIDCC, __Secure-3PSID, __Secure-3PAPISID, __Secure-3PSIDCC, 1P_JAR, AEC, NID, OTZ Gatekeeper has been a frequent target of threat activity in recent years, and researchers, as part of their proof of concept exploit, identified different mechanisms to bypass the security feature. Threat actors can: Microsoft researchers pointed out a few examples of Gatekeeper bypass that were previously assigned common vulnerability and exposure (CVE) numbers.
In one example, CVE-2021-1810 involved the assignment of the quarantine attribute. In this example, a path longer than 886 characters fails to inherit the com.apple.quarantine extended attribute, as outlined by researchers from With Secure . Microsoft shared research about the issue with Apple in July through coordinated vulnerability disclosure and Apple released fixes to all its operating systems, according to the blog. Apple did not immediately return a request for comment.
Researchers from Zimperium said Gatekeeper is a strong process to make sure apps going through macOS are legit, but this layer of security is not enough by itself. “Whether they are targeting iOS or macOS, threat actors are looking for new and novel ways to bypass these OEM security tools that provide zero advanced threat protection and risk telemetry back to their security teams, leaving critical data and systems at great risk,” Richard Melick, director of threat reporting at Zimperium, said via email.
The directive represents an about-face for an administration that previously repudiated government AI reviews. Google researchers say the hackers abused a third-party tool in an attack spree designed to harvest credentials. A catastrophic cyberattack at Jaguar Land Rover is forcing governments and industrial leaders to address urgent demands for business resilience and accountability.
Google researchers say the hackers abused a third-party tool in an attack spree designed to harvest credentials. Mac Monitor, our newly released free collection tool, helped us discover a pair of vulnerabilities that we disclosed to Apple Earlier this year, each member of the Red Canary threat research team had the opportunity to choose a featured MITRE ATT&CK® technique and analyze it for the 2023 Threat Detection Report . On the macOS end of the spectrum, we decided to take a closer look at Apple’s software inspection and verification technology, Gatekeeper.
We’re no stranger to Gatekeeper at Red Canary—having written extensively about it and helped influence ATT&CK’s technique (T1553.001) for it. However, in the process of conducting threat research with a then-private version of our Mac Monitor tool to develop a pair of detection heuristics that’ve been on our wishlist for a while, we discovered two novel and exploitable vulnerabilities.
Both vulnerabilities could enable an adversary to bypass Gatekeeper by evading a related security control called File Quarantine. We needed a way of validating that macOS was quarantining and inspecting the files that were supposed to be quarantined and inspected. So we developed these detection analytics and implemented them in Mac Monitor to do exactly that. In the process of testing these analytics, we found a way to trick macOS into mismanaging the application of quarantine flags that prompt inspection by Gatekeeper.
The “quarantine flag” ( com.apple.quarantine ) is an extended attribute whose data is stored in resource forks. After digging in for a short while, we came across an interesting bit of code from the “virtual file system” implementation: darwin-xnu/bsd/vfs/vfs_xattr.c This same concept shows up elsewhere in the code. Naturally, we wanted to know what would happen if we crafted a Mach-O binary named with the prefix of a resource fork file, ._ . So we compiled a simple Mach-O with that prefix, compressed it into an archive, downloaded it with Safari (a File Quarantine-aware app), and immediately noticed the file was not quarantined—but in fact, readily executable.
We reported this to Apple on January 27. They later acknowledged the bug, codified it as an archive utility problem with CVE-2023-27951 , patched it, and recognized us and Csaba Fitzl ( @theevilbit ) for discovering and disclosing it. After reporting this issue to Apple, we also noticed some of our favorite software was not File Quarantine-aware (i.e., it failed to apply the file quarantine attribute to downloads). One of these was Arc, a web browser developed by The Browser Company. The team quickly responded to our security feature request and enabled File Quarantine for Arc by adding LSFileQuarnatineEnabled to the Info.plist of Arc itself and all of its helpers. This, according to Apple, opts the application into File Quarantine, and nothing else is needed to be done by the developers.
However, we noticed something curious: After we updated Arc to the File Quarantine-aware version, it still was not quarantining downloaded files. Initially, we thought this was an issue with Arc itself, so we reported it and waited. Finally, after directly posing the question on Apple’s developer forums , we decided to submit the issue to Apple Product Security on March 4 with what we knew, including the telemetry from Mac Monitor. Apple promptly assigned CVE-2023-27943 to it, said it impacted LaunchServices , fixed it, and credited an anonymous researcher, us, Milan Tenk, and Arthur Valiev for its discovery.
The heuristics mentioned in our Threat Detection Report page on Gatekeeper Bypass are baked into Mac Monitor by default. Here are two of them in operation detecting each of these zero days. These vulnerabilities were patched with the release of macOS 13.3 (Ventura) , 12.6.4 (Monterey) , 11.7.5 (Big Sur) , and *OS 13.4 (for CVE-2023-27943 only).
Huge thanks to Apple and The Browser Company for promptly fixing the vulnerabilities and bugs mentioned in this article, and to all the great researchers out there who find and responsibly disclose security vulnerabilities! Stay tuned for additional blogs, videos, and more exploring the many use cases for our newly released (and free!) dynamic analysis and collection tool, Mac Monitor .
Our free collection tool helps users dig deeper into the telemetry generated on macOS to enhance both immediate threat detection and broader security research. Disclaimer: This blog post has been created by Zscaler for informational purposes only and is provided "as is" without any guarantees of accuracy, completeness or reliability. Zscaler assumes no responsibility for any errors or omissions or for any actions taken based on the information provided. Any third-party websites or resources linked in this blog post are provided for convenience only, and Zscaler is not responsible for their content or practices. All content is subject to change without notice.
By accessing this blog, you agree to these terms and acknowledge your sole responsibility to verify and use the information as appropriate for your needs. On July 27, 2022, Microsoft discovered a vulnerability in macOS that can allow attackers to bypass application execution restrictions imposed by Apple’s Gatekeeper security mechanism, designed to ensure only trusted apps run on Mac devices.
We developed a proof-of-concept exploit to demonstrate the vulnerability, which we call “Achilles”. Gatekeeper bypasses such as this could be leveraged as a vector for initial access by malware and other threats and could help increase the success rate of malicious campaigns and attacks on macOS. After carefully reviewing the implications, we shared the vulnerability with Apple in July 2022 through Coordinated Vulnerability Disclosure (CVD) via Microsoft Security Vulnerability Research (MSVR). Fixes for the vulnerability, now identified as CVE-2022-42821 , were quickly released by Apple to all their OS versions. We note that Apple’s Lockdown Mode , introduced in macOS Ventura as an optional protection feature for high-risk users that might be personally targeted by a sophisticated cyberattack, is aimed to stop zero-click remote code execution exploits, and therefore does not defend against Achilles. End-users should apply the fix regardless of their Lockdown Mode status. We thank Apple for the collaboration in addressing this issue.
In this blog post, we share information about Gatekeeper and the vulnerability able to bypass it. We also share this research to emphasize the importance of collaboration among researchers and the security community to improve defenses for the larger ecosystem. 5. Performance Evaluation & Extended Technical Observations Many macOS infections are the result of users running malware, oftentimes inadvertently. Fake app bundles might masquerade themselves as different apps, like Flash Player, or as a legitimate file, such as using a PDF icon and using the app name “Resume”. To combat this highly popular infection vector, Apple has imposed strong security mechanisms. When downloading apps from a browser, like Safari, the browser assigns a special extended attribute to the downloaded file. That attribute is named com.apple.quarantine and is later used to enforce policies such as Gatekeeper or certain mitigations that prevent sandbox escapes . In recent years, Apple has tightened the security policies even further, and the current Gatekeeper design dictates the following behavior for downloaded apps: Extended attributes are a filesystem feature supported on common macOS filesystems, like APFS and HFS+, and their main purpose is to save file metadata. Specifically, the com.apple.quarantine attribute saves information regarding the source of the downloaded file, as well as data instructing Gatekeeper how to process the file. The attribute format is generally: A flag value of “0083” enforces Gatekeeper restrictions on the file, as displayed below: Due to its essential role in stopping malware on macOS, Gatekeeper is a helpful and effective security feature. However, considering there have been numerous bypass techniques targeting the security feature in the past, Gatekeeper is not bulletproof. Gaining the ability to bypass Gatekeeper has dire implications as sometimes malware authors leverage those techniques for initial access.
Numerous Gatekeeper bypasses have been identified in the past years, some even abused by malware families such as Shlayer. When examining Gatekeeper bypasses from recent years, we see two approaches: Here are some examples of Gatekeeper bypass vulnerabilities discovered over the last several years: Intrigued by CVE-2021-1810 , as listed in the above table, we wondered what mechanism could be leveraged in archives.
Considering symbolic links are preserved in archives and aren’t assigned with quarantine attributes—we looked for a mechanism that could persist different kinds of metadata over archives. After some investigation, we discovered a way to persist important file metadata through a mechanism called AppleDouble. Even though extended attributes are common on different filesystems, they might be implemented differently or even not supported, so copying files with their metadata becomes a challenging task. To solve this problem, back in 1994 , Apple introduced the concept of AppleSingle and AppleDouble formats. In a nutshell, AppleSingle is a binary blob that is added as a part of the original file contents so that there’s only a “single” file to process, whereas AppleDouble saves the metadata in a different file side-by-side next to the original file, with a “._” prefix.
Interestingly, when extracting an archive, macOS processes any attached AppleDouble file and assigns the target file with the appropriate metadata. The AppleDouble binary file format is quite complicated, but the code that parses it can be read in the XNU git repository in the file that handles extended attributes, which also includes ASCII-art depiction of the format. To demonstrate the AppleDouble file information, we used the ditto utility as such: When the file is archived alongside its original file and then extracted by macOS, extended attributes are fully restored, as demonstrated here: Using this newfound knowledge, we examined how we could use the AppleDouble mechanism to trick Gatekeeper in some way.
Our first approach was to generate many large extended attributes in the AppleDouble format such that there won’t be enough space to assign the com.apple.quarantine extended attribute. Interestingly, it doesn’t work—AppleDouble is ignored if the overall size is over 2 GB, and there is no limitation on the number of extended attributes a file could get (besides the size of the disk).
Researching further, we decided to examine the source code of the unarchiving mechanism. Carefully studying the copyfile_unpack implementation, we discovered an option for a special extended attribute named com.apple.acl.text (saved in the XATTR_SECURITY_NAME constant in the source code), which is used to set arbitrary Access Control Lists. Access Control Lists (ACLs) are a mechanism in macOS that further extends the traditional permission model. The traditional permission model saves permission for each file in a file “mode”, which can be changed by using the chmod utility. It enforces permissions on the owning user, owning group, and others in terms of reading (r), writing (w) and launching (x). A file’s mode can be viewed by listing files with the “ -l ” (long) flag: Unlike the traditional permission mechanism, ACLs allow fine-grained permissions to files and directories. Each ACL has one or more Access Control Entries (ACEs) that dictate what each principal can or cannot do, much like firewall rules. Like the file mode, ACLs can be modified with the chmod utility and viewed with the ls utility. It’s important to note that file access checks are dictated by both ACLs and the traditional permission model mechanisms, as demonstrated by the following example: The set of authorizations supported by ACLs is well-documented by Apple in the chmod manual, which contain more than the traditional reading, writing, or launching abilities, including: Equipped with this information, we decided to add very restrictive ACLs to the downloaded files. Those ACLs prohibit Safari (or any other program) from setting new extended attributes, including the com.apple.quarantine attribute.
Two minor challenges that we had to overcome during the proof-of-concept (POC) development were: We named our POC exploit Achilles after its use of ACLs to bypass Gatekeeper. Our POC recorded video can be viewed here: The AppleDouble file we used for this Gatekeeper bypass can be generated, as displayed below: The threat landscape continues to evolve, delivering new threats and attack capabilities that take advantage of unpatched vulnerabilities and misconfigurations as a vector to access systems and data. Our data shows that fake apps remain one of the top entry vectors on macOS, indicating Gatekeeper bypass techniques are an attractive and even a necessary capability for adversaries to leverage in attacks. Nonetheless, through research-driven protections and collaboration with customers, partners, and industry experts, we strive to enrich our protection technologies to defend against such issues—regardless of the platform or device in use.
As environments continue to rely on a diverse range of devices and operating systems, organizations need security solutions that can provide protection across platforms and a complete picture of their security posture. Collaborative research such as this informs our comprehensive protection capabilities across platforms, allowing Microsoft Defender for Endpoint to deliver and coordinate threat defense across all major OS platforms including Windows, macOS, Linux, Android, and iOS. On macOS devices, Microsoft Defender for Endpoint detects and exposes threats and vulnerabilities, including CVE-2022-42821, using antivirus, endpoint detection and response (EDR), and threat and vulnerability management capabilities. This research also improved Microsoft Defender’s Vulnerability Management capabilities to discover, prioritize, and remediate misconfigurations and vulnerabilities. This includes detecting CVE-2022-42821 on macOS devices by examining AppleDouble files misusing ACLs.
This case also emphasized the need for responsible vulnerability disclosures and expert, cross-platform collaboration to effectively mitigate issues, protecting users against present and future threats. We wish to again thank the Apple product security team for their efforts and responsiveness in addressing the issue. Our Microsoft security researchers continue to discover new threats and vulnerabilities as part of our effort to secure users’ computing experiences, be it a Windows or non-Windows device. In the effort to improve security for all, we will continue to share intelligence and work with the security community to create and improve upon solutions that protect users and organizations across platforms every single day.
Protect your people, data, and infrastructure with AI-powered, end-to-end security from Microsoft. MAC address filtering will block a device when its hardware address is not listed in the allow list, is entered incorrectly, or is randomized by the OS. Log in to your router, go to Access Control, manually add the MAC address that appears when you run ipconfig /all or in the Wi-Fi settings, and turn off client private address rotation.
Filtering is set to "allow listed only" and the client's hardware address was never added. Common right after a router reset or firmware update wipes the list. iOS 14+, Android 10+ and Windows 11 rotate a fake MAC per SSID for privacy. Each rotation looks like a new, unlisted device to the router.
A single wrong hex character, or colons entered as dashes on a router that expects colons, silently rejects the client. Copy-paste beats retyping. Someone added the MAC to a blocklist rather than an allow list, or inverted the rule. The device is explicitly banned rather than simply missing.
Docking stations, USB-Ethernet adapters, VPN clients and hypervisors expose their own MAC. The address the router sees is not the one printed on the laptop. Not likely. MAC addresses are included, unencrypted, in Wi-Fi frames and can be spoofed with a few lines of script in most OSes. Consider filtering a feeble resistance to an attacker. WPA3-Personal, or WPA2-AES with a long passphrase, does the heavy lifting. Keep filtering only if you need to for compliance.
As of iOS 14, iPhones create a per-SSID Private Wi-Fi Address to reduce tracking from network to network. When you connect to a router, you get a new, unknown, unlisted MAC address, and the router rejects it. To disable it on a network: Open Settings > Wi-Fi, tap the (i) for the network, and turn Private Wi-Fi Address off for that SSID only. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Internet%20filter • https://www.juniper.net/documentation/us/en/software/mist/mist-access/topics/topic-map/access-assurance-mac-auth-wired- devices.html • https://networklessons.com/switching/mac-authentication-bypass-mab • https://github.com/Laneden-Labs/macutil • https://adhdecode.com/network-security/hands-on-labs/lab-27-mac-filtering-evasion/ • https://www.juniper.net/documentation/us/en/software/junos/interfaces-ethernet/topics/topic-map/mac-address-filtering-acco unting-ethernet-interfaces.html • https://documentation.meraki.com/Wireless/Design_and_Configure/Deployment_Guides/MAC-Based_Access_Control_Usin g_Microsoft_NPS_-_MR_Access_Points/Enabling_MAC-based_access_control_on_an_SSID • https://www.tp-link.com/in/support/faq/927/ • https://www.cybersecuritydive.com/news/vulnerability-bypass-security-apple-gatekeeper/639207/ • https://www.zscaler.com/blogs/cybersecurity-best-practices/gatekeeper-bypass-vulnerabilities
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Mac Filtering Bypass Alert System.
[*] Metasploit Scan Running on Target Subnet for Mac Filtering Bypass Alert System... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |