Complete Technical Paper Content — Malware Dynamic Analysis Using Sandbox And Machine Learning
Overview & System Context
Malware Dynamic Analysis Using Sandbox And Machine Learning: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~5253 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Malware analysis is a time-consuming and resource-intensive task that requires expert knowledge and careful investigation.
Security analysts must decide which analytical techniques to apply from basic file inspection to deep memory dumps while balancing thoroughness against time constraints. Traditional automated systems either perform exhaustive analysis on every sample (slow and expensive) or use rigid rule-based heuristics (fast but inflexible). This project explores a different approach: What if an AI agent could learn the analysis process itself? Instead of telling the system what to check, we train a reinforcement learning agent that autonomously decides which analytical actions to take, mimicking how human analysts progressively investigate suspicious files.
The system represents a proof-of-concept for applying reinforcement learning to cybersecurity workflows, demonstrating that AI agents can learn complex sequential decision-making processes in the malware analysis domain. All code, models, and documentation are available in the GitHub repository: Dynamic Malware Analysis using AI Agent and Reinforcement Learning .
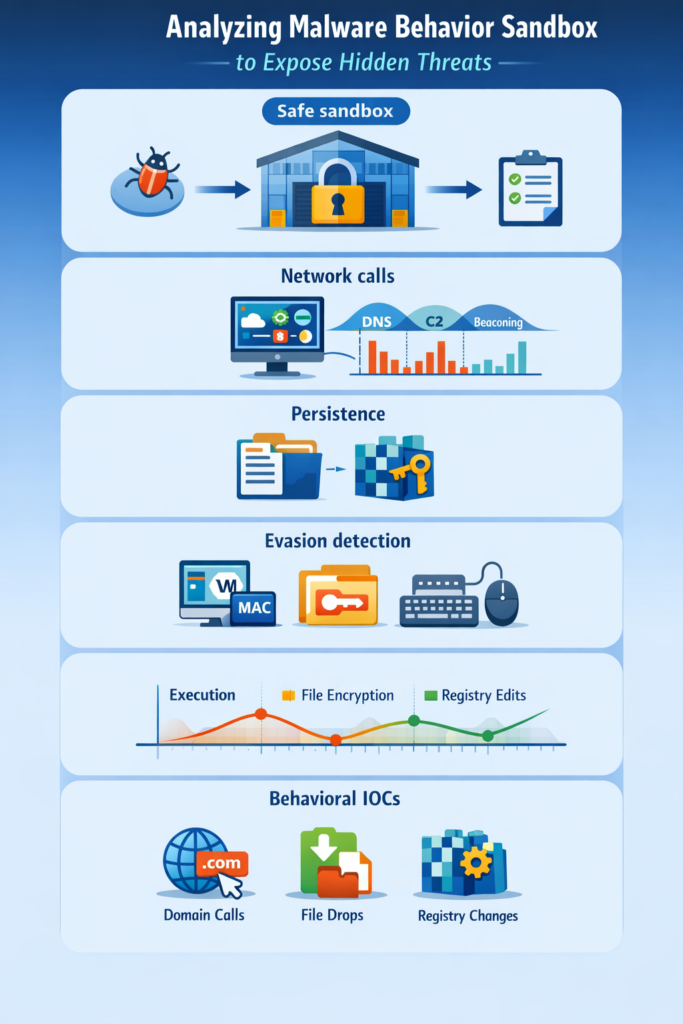
Figure 1: Analyzing Malware Behavior Sandbox to Expose Hidden Threats - Network ... This article will walk you through the complete system from CAPEv2 integration and feature engineering, to the RL environment design, DQN architecture, and deployment as a command-line tool. The core idea behind this project is to apply reinforcement learning to the malware analysis workflow itself. Traditional approaches fall into two categories: CAPEv2 (Configuration And Payload Extraction) is an advanced malware sandbox that executes suspicious files in isolated virtual machines and records their behavior.
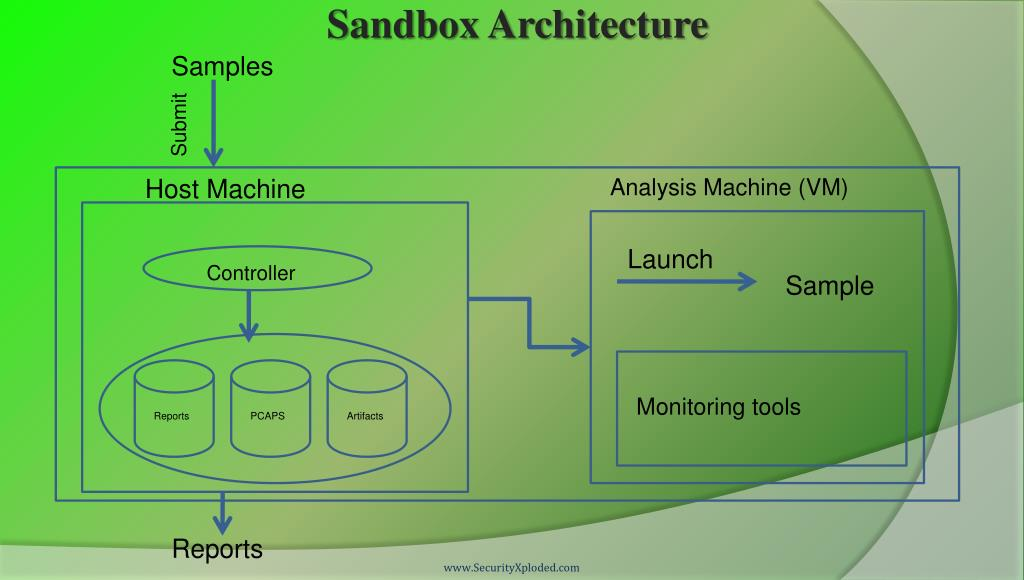
The feature extractor ( ai_agent.py: CAPEFeatureExtractor class) converts CAPE’s large JSON reports into fixed-size numerical vectors that the neural network can process. Figure 2: PPT - Malware Sandbox Analysis PowerPoint Presentation, free download ... Progressive Revelation : Not all features are available immediately. The agent must take specific actions to “unlock” feature groups: The AI agent uses a Dueling Deep Q-Network architecture an advanced reinforcement learning algorithm.
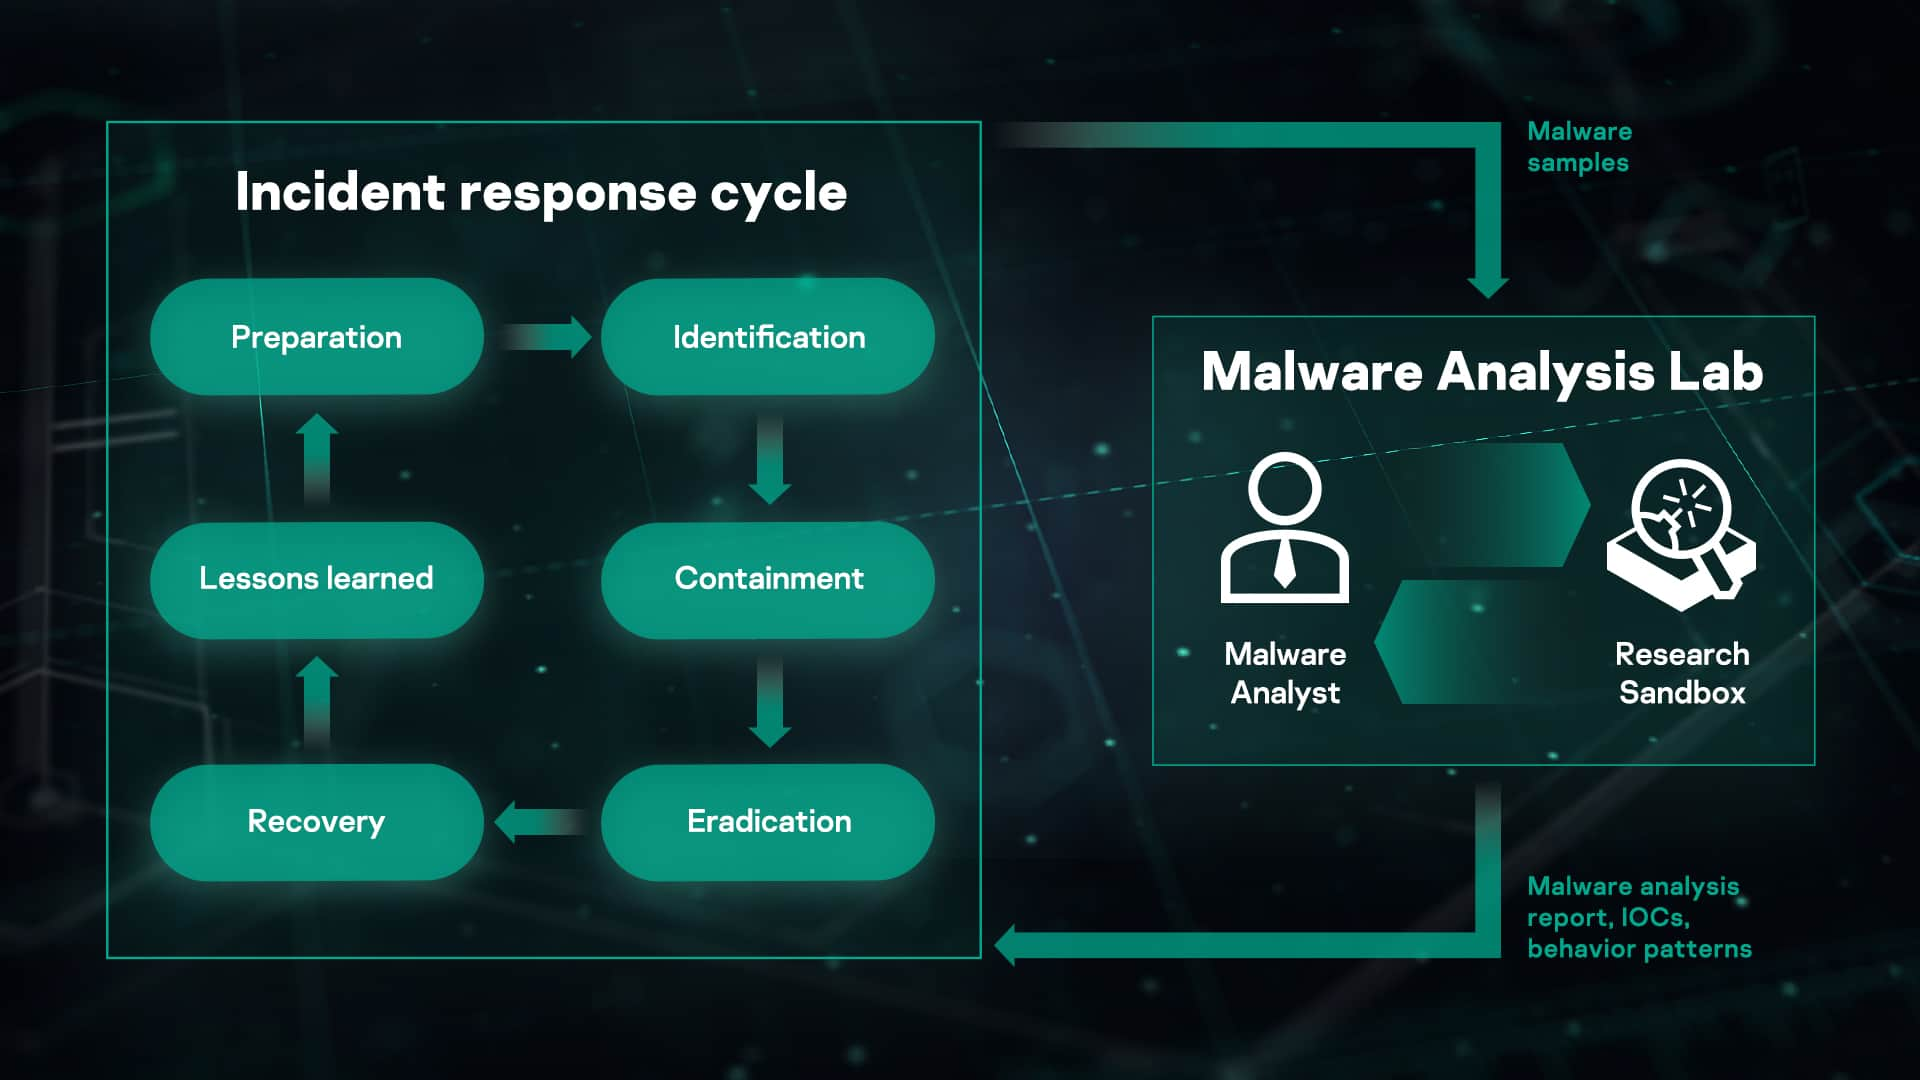
Training data comes from WinMET (Windows Malware Execution Traces) , a dataset of CAPE analysis reports. The training environment models the analysis process as a Markov Decision Process (MDP). Figure 3: Kaspersky Research Sandbox | AVDefender.com This project demonstrates that reinforcement learning can be successfully applied to malware analysis workflows. By training a DQN agent to make sequential analytical decisions, we’ve created a system that: While this is a proof-of-concept with limitations, it points toward a future where AI agents augment human security analysts handling routine cases efficiently while flagging ambiguous samples for expert review.
The complete code, trained models, and documentation are fully open-source. Whether you’re interested in reinforcement learning, cybersecurity automation, or AI applications in security, this project provides a working example. Thank you for reading! If you found this project interesting or useful, please consider giving it a I on GitHub. Questions, issues, and contributions are welcome! Welcome to the Malware Analysis Lab repository. This lab demonstrates hands-on skills in analyzing and understanding malicious software in a safe, controlled environment . The lab covers static analysis, dynamic sandboxing, and malware network traffic capture using industry-recognized tools.
The lab is organized into multiple sections to cover the main aspects of malware analysis: Each tool has a dedicated markdown file in the tools/ folder explaining installation, setup, and usage. All references, guides, and MITRE ATT&CK mappings are included in the docs/references.md file. Note: This lab is designed for educational purposes only . Do not attempt on production or unauthorized systems.
Hands-on Malware Analysis Lab covering static analysis, dynamic sandboxing, and malware network traffic capture. Includes Ghidra, IDA Free, Cuckoo Sandbox, and Wireshark exercises with screenshots and detailed documentation. All analysis described here is for defensive security purposes — understanding malware to build better detection and response capability. Never analyze suspected malware on production systems or outside an isolated environment.
Dynamic malware analysis — running a suspicious sample and observing its behavior in a controlled environment — is one of the highest-value activities in incident response and threat intelligence. It tells you what the malware actually does rather than what you think it might do based on static indicators. A sandbox collapses analysis time from hours to minutes and provides behavioral IOCs that static analysis frequently misses.
This module is one piece of a complete home lab setup — see the full guide to building a home cybersecurity lab for how it fits with network isolation, offensive practice, and detection modules. 2. System Architecture & Core Working Principles For most analysts, cloud sandboxes are the right starting point. Zero infrastructure, instant results, and most are free for individual use.
The most interactive cloud sandbox available. Any.run runs samples in a real Windows VM (7, 8.1, 10, 11) or Linux environment and provides a live interactive session — you can click, type, and interact with the malware’s UI in real time, which is critical for samples that require user interaction to detonate (phishing documents that need a macro enabled, installers that need clicks through a wizard).
The free tier is public (your sample and results are visible to other users — critical consideration for sensitive or internal files). The paid tier provides private analysis. For malware from the wild, public analysis is generally fine and contributes to the community. More automated and less interactive than Any.run, but extraordinarily detailed reporting. Joe Sandbox’s reports include behavioral signatures, YARA rule matches, Sigma rule matches, network IOCs, and a full behavioral graph. The free community tier has limits but is useful. Joe Sandbox is the choice when you want depth over interactivity.
Powered by CrowdStrike Falcon Sandbox. Free tier is generous. Reports include VxStream behavioral analysis, network IOCs, extracted strings, and threat scoring. Integrates well with VirusTotal lookups. Good general-purpose option. Run by Hatching, which was acquired by Recorded Future. Fast analysis, strong community data integration, and good API access on the free tier. Particularly strong for ransomware and banking trojan families.
Cuckoo Sandbox is the standard open-source dynamic analysis platform. It runs samples in isolated VMs, captures network traffic via tcpdump, hooks API calls via its monitoring agent, and generates detailed reports. Cuckoo’s actively maintained fork, Cape (Automated Payload Extraction), adds unpacking and config extraction capabilities. The recommended installation: Cape adds automatic unpacking of packed malware, config extraction for known families (Emotet, Qakbot, Cobalt Strike, etc.), and YARA rule integration.
Hash the sample immediately (SHA256) before any analysis. This is the authoritative identifier. Check the hash against VirusTotal first — if it’s a known sample, you may have all the intelligence you need without running it. If it’s novel, proceed. Static indicators (hardcoded IPs, domains, registry keys, mutex names) sometimes give you IOCs without executing anything.
For Any.run: upload via web interface, select OS and configuration, enable MITM if you want TLS decryption, start analysis. Watch the interactive session. Network IOCs: domains, IPs, user agents, URL patterns. These are your fastest-value takeaways — block them at the firewall and DNS level immediately.
Process behavior: What did it spawn? powershell.exe spawned by winword.exe is a macro execution indicator. cmd.exe spawned by svchost.exe in unusual paths is a process injection indicator. Persistence mechanisms: Registry run keys, scheduled tasks, service installation — document these for detection rules. Dropped files: Secondary payloads the initial dropper wrote to disk. Hash and analyze each one.
Getting CAPEv2 running in my home lab took two attempts, not one, and the failure the first time was entirely my fault. I’d built the Windows analysis VM straight out of a fresh ISO — no Office, no Chrome, default wallpaper, hostname still set to WIN-something-random. Every sample I threw at it either did nothing or exited immediately. It took an embarrassingly long time to realize the malware wasn’t being lazy — it was correctly identifying a sandbox and refusing to detonate. Sandboxes need to look lived-in, and mine looked like it had been unboxed five minutes earlier, because it had been.
The fix was tedious in exactly the way the setup guides undersell: install real software, generate some fake browsing history, rename the host to something a normal employee’s laptop would be named, let some innocuous background noise exist on the disk. Samples that had gone completely inert against the sterile VM started behaving normally once the environment looked like an actual machine somebody used.
The other lesson, learned the hard way: don’t skip the isolated network setup even for “obviously harmless” samples. I got complacent once with a sample I was fairly confident was a low-effort commodity dropper, ran it bridged to my regular network out of laziness, and watched it immediately start scanning for SMB shares. Nothing came of it because the network segmentation elsewhere caught it, but it was a needless risk for a five-minute time save, and I don’t take that shortcut anymore.
Malware Analysis Reference: Practical Malware Analysis by Sikorski and Honig on Amazon — the standard textbook for malware analysis, covering static and dynamic analysis methodology, disassembly, and debugging in depth. Essential reading for anyone doing regular analysis work. My sterile-VM mistake cost me an afternoon of confusion before I figured out what was actually happening. Building a convincingly “used” analysis environment up front costs less time than debugging a sample that’s just quietly refusing to run.
This Python script provides a comprehensive solution for malware detection and dynamic analysis. It allows you to analyze malware samples and benign files, classify them using a pre-trained machine learning model, and perform dynamic analysis on detected malware. Malware Detection : This code includes a pre-trained machine learning model that can classify files as malware or benign based on extracted features.
Dynamic Analysis : It performs dynamic analysis on detected malware samples using a sandboxing tool and stores the analysis results in a specified directory. 3. Software Implementation, Frameworks & Protocols File System Monitoring : The script continuously monitors a specified directory for incoming files and automatically analyzes newly created files.
Modify the script to specify the directories where your malware samples ( MALWARE_DIR ), benign files ( BENIGN_DIR ), and dynamic analysis reports ( DYNAMIC_ANALYSIS_DIR ) should be located. The script will start monitoring the specified directories for new files and perform malware detection and dynamic analysis as needed.
Ensure that your malware samples are placed in the MALWARE_DIR directory and your benign files in the BENIGN_DIR directory. The script will classify these files and print a classification report and confusion matrix. When malware is detected, dynamic analysis is initiated, and the results are stored in the DYNAMIC_ANALYSIS_DIR directory.
If you want to contribute to this project, please open an issue or create a pull request. A comprehensive malware detection and dynamic analysis system, designed to analyse malware samples and benign files & classify them using a pre-trained machine learning model, and perform dynamic analysis on the detected malware. Dynamic malware analysis is the technique of executing a malware sample inside a controlled, instrumented environment and recording everything the sample does at runtime. Where static analysis reads the binary without running it, dynamic analysis lets the code run and captures the consequences: files created, registry keys written, network connections opened, processes spawned, and persistence mechanisms installed.
The primary tool is a sandbox, an isolated virtual or physical environment that presents the sample with a plausible host and collects a behavioural log. Analysis platforms such as Cuckoo, Any.Run, and Joe Sandbox automate this process and produce structured reports that investigators and incident responders use to characterise unknown samples quickly. The value of dynamic analysis is that it bypasses obfuscation and packing. A binary that is encrypted or compressed will not yield useful information from string extraction or disassembly in its packed form, but when it executes in a sandbox it must decompress and decrypt itself before it can act, at which point the instrumentation sees the real code behaviour. Dynamic analysis is therefore the first-pass technique for unknown or suspected-packed samples in most incident-response workflows.
Dynamic analysis has clear limits. A sandbox only captures behaviour that the sample triggers during the observation window, typically two to five minutes. Malware programmed to sleep before acting, to phone home for instructions, or to check the system clock before activating will appear benign. Modern malware families also incorporate environment detection routines that check for virtual-machine artefacts, analyst tools, or unrealistic system conditions and go dormant when they detect them. Investigators must understand these limits to avoid treating a clean sandbox report as evidence that a sample is safe.
Static analysis examines a binary without executing it. Tools such as strings extractors, disassemblers (IDA Pro, Ghidra), and import-table viewers expose the file's structure, embedded strings, function calls, and metadata. Static analysis is safe because the code never runs, it is fast on small binaries, and it can reveal code paths that a dynamic run may never trigger. Its weakness is obfuscation: any packer or encryptor reduces the visible content to near-noise, and a well-obfuscated binary may yield almost no useful static information.
Dynamic analysis solves the obfuscation problem. Once the sample runs, it must unpack and decrypt itself before it can do anything useful, and the sandbox records what it does after that point. Dynamic analysis also reveals behaviour that is not encoded in the binary at all, such as instructions downloaded from a command-and-control server at runtime. The cost is coverage: a sandbox run can only observe the code paths the sample actually executes during the observation window. Branches that require specific conditions, a particular date, a certain victim username, or a network response that never arrives will not be explored.
In practice, analysts use both methods together. Static analysis first to check whether the binary is packed and to extract any plaintext indicators; dynamic analysis to observe runtime behaviour and confirm static hypotheses. For incident-response triage, a dynamic sandbox run is often the first step because it produces an actionable report in minutes without requiring reverse-engineering skill.
Sandboxes fall into two broad categories based on how they monitor the sample. User-mode sandboxes, the most common type, intercept API calls at the user-mode level using hooking libraries injected into the monitored process. Kernel-mode sandboxes operate at a lower level, intercepting system calls directly, which is harder for malware to detect but more complex to build and maintain. A third approach, bare-metal sandboxes, runs the sample on a physical host rather than a virtual machine, eliminating the most reliable class of VM-detection checks at the cost of much slower reset cycles.
Cloud-based platforms such as Any.Run, Joe Sandbox Cloud, and VirusTotal's file-analysis pipeline are the fastest way to get a behavioural report on a sample with no infrastructure overhead. Investigators upload the file or a URL and receive a report within minutes. The trade-off is that the sample leaves the investigator's control, which may be inappropriate for sensitive evidence or classified material. On-premise platforms such as Cuckoo Sandbox (open-source) or CAPE Sandbox give full control over the analysis environment, network simulation, and report format, at the cost of infrastructure management.
Sandbox configuration matters as much as sandbox type. A sample targeting Windows 10 enterprise environments will behave differently, or not at all, on a Windows 7 VM. Malware that checks for a domain-joined machine will go dormant on a standalone workgroup host. Investigators should configure the sandbox to resemble the victim environment as closely as possible: same OS version, same patch level, same installed applications, and the same locale and language settings. Many commercial sandbox products offer environment profiles for common configurations.
A sandbox monitoring framework captures activity across several categories simultaneously. Each category maps to a class of attacker behaviour and generates artefacts that can be used as indicators of compromise or as evidence in a prosecution. 4. Practical Deployment, Analysis & Case Studies Network monitoring inside a sandbox requires a decision about connectivity. A fully isolated sandbox captures DNS queries and TCP connections but cannot receive responses, so any sample that requires a live C2 response before proceeding will halt.
A simulated network, using tools such as INetSim or FakeNet-NG, provides plausible responses to common protocols: it answers DNS queries with a local IP, accepts HTTP requests and returns generic responses, and simulates SMTP to capture any outgoing mail. Simulated networks allow more malware to proceed past initial network checks while keeping the sandbox isolated from real infrastructure.
Malware authors have known about automated sandboxes for over a decade. Modern malware, particularly commodity ransomware-as-a-service payloads and targeted nation-state tools, includes environment-detection routines designed to identify sandbox conditions and suppress payload behaviour. Understanding these routines helps investigators choose countermeasures and interpret a clean sandbox result appropriately.
Time-based evasion is the most common category. The malware calls a sleep function for an interval longer than the sandbox timeout, typically ten minutes or more, then checks whether real time has advanced by that amount. Sandbox platforms that fast-forward the system clock to skip sleep calls are detected by this check. Countermeasure: configure the sandbox to advance the clock at human speed for the full sleep duration, extending analysis time, or use a platform with transparent sleep-skipping that also advances the measured time.
Virtual machine artefacts are the second major category. Most consumer virtual machine platforms leave detectable traces: registry keys referencing VMware or VirtualBox guest tools, device names such as VBOX or VMWARE in the hardware enumeration, a known set of MAC address prefixes for virtual NICs, and disk names that do not match real hardware. Countermeasure: harden the VM by renaming artefacts, replacing generic MAC addresses with realistic values, and removing or renaming guest-tool registry keys. Bare-metal sandboxes eliminate most of these checks at the cost of much slower reset cycles.
CPU and memory checks are increasingly common in targeted malware. A sample may count logical CPU cores and refuse to run on a single-core VM, check available RAM and refuse to run on less than four gigabytes, or enumerate running processes looking for analysis tools such as Wireshark, Process Monitor, or known sandbox agent names. Countermeasure: allocate realistic resources to the sandbox VM and ensure no analysis tools are visible in the process list from within the guest.
A sandbox report is evidence of observed behaviour during a specific execution window in a specific environment. It is not a definitive characterisation of everything the sample can do. Investigators reading sandbox reports must apply several critical filters before drawing conclusions. A malicious verdict from a sandbox is strong evidence that the sample is harmful, but the specific actions recorded may not represent all possible actions. The sample may have additional payloads triggered by conditions not present in the sandbox run.
A clean verdict, meaning the sandbox observed nothing harmful, is weaker evidence: it could mean the sample is benign, but it could also mean the sample evaded the sandbox, required a network response that did not arrive, or was waiting for a trigger condition not present in the test. Network indicators from a sandbox report, DNS hostnames, IP addresses, and URL patterns, should be treated as high-value leads but verified before blocking at scale. A C2 domain seen in a sandbox run may be a legitimate domain hijacked temporarily, a sinkholed domain already under law-enforcement control, or a shared hosting address used by multiple actors.
Cross-referencing with threat-intelligence feeds such as VirusTotal, AlienVault OTX, or commercial platforms before adding to block-lists reduces false positives. MITRE ATT&CK mapping in a sandbox report translates observed API calls and behaviours into standardised technique identifiers. A report that tags a sample with T1059.001 (PowerShell execution) and T1082 (System Information Discovery) tells an investigator which detection rules to check and which threat-intelligence entries to search. ATT&CK mapping is a normalisation layer: it makes sandbox output comparable across platforms and across investigations.
Running malware in a sandbox raises legal questions in several jurisdictions. The most common concern is outbound network activity: if the sandbox connects to real external infrastructure and the malware sends requests to a legitimate server, the investigator may have accessed a computer system without authorisation. In India, the Information Technology Act 2000 (as amended) and its successor framework under the Bharatiya Nagarik Suraksha Sanhita 2023 govern such access.
In the United States, the Computer Fraud and Abuse Act creates liability for unauthorised access even when the access is accidental. In the United Kingdom, the Computer Misuse Act 1990 applies. The standard safeguard is complete network isolation: the sandbox must not route any outbound traffic to live internet infrastructure. Evidence integrity is a separate concern. Malware samples collected from victim systems are forensic exhibits. Running a sample in a sandbox without hashing and documenting it first, or running it on a system that is not clean-image-restored between runs, risks contaminating the exhibit or introducing artefacts that undermine the chain of custody.
Investigators should hash the sample before analysis, run it only on a freshly restored sandbox image, and document the analysis environment and configuration in the case file. Courts in India, the UK, the EU, and the US have all considered the admissibility of digital evidence obtained through analysis tools, and documented methodology is the primary defence against admissibility challenges.
Sandbox analysis findings can support multiple legal outcomes: criminal prosecution under computer-misuse statutes, civil litigation, regulatory enforcement, or intelligence reporting. The applicable statute and the standard of evidence differ across outcomes. Criminal prosecutions in India under the Information Technology Act 2000 or the Bharatiya Nagarik Suraksha Sanhita 2023 require evidence that meets the threshold of the Bharatiya Sakshya Adhiniyam 2023.
US federal cases under 18 U.S.C. § 1030 and UK cases under the Computer Misuse Act each have their own procedural requirements. Understanding which framework governs the case before beginning analysis allows the investigator to document the sandbox methodology in the terms courts in that jurisdiction will expect. A malware sample is submitted to a sandbox and the report shows no suspicious activity. What is the most cautious conclusion an investigator should draw? Practice with mock tests, learn from structured notes, and get your questions answered by a global forensic community, all in one place.
In a controlled study by Horizon3 researchers, models that explicitly identified a trap in their reasoning still attacked it 73.4% of the time. Read the findings and see what they mean for canaries, decoys, and early detection. When a suspicious file lands in your environment — a questionable email attachment, a file flagged by EDR, a download from a suspicious link — the fastest path to understanding what it does is detonating it in a sandbox. Malware sandboxes execute the sample in an isolated virtual environment and record everything: process creation, file system changes, network connections, registry modifications, and API calls.
Sandbox analysis is not a replacement for reverse engineering — a skilled malware analyst extracting code-level behavior from a disassembler gets deeper visibility. It is a rapid triage tool that takes a suspicious binary from 'unknown' to 'here is what it does, here are its network indicators, and here is how it achieves persistence' in under five minutes. This guide covers the submission workflow, how to read the output, and the limits of sandbox analysis.
Several sandboxes are available for different use cases, each with trade-offs in cost, privacy, and depth. 5. Performance Evaluation & Extended Technical Observations Any.Run is a browser-based interactive sandbox where you can watch malware execute in real time and interact with it (click dialog boxes, enter credentials to observe keylogger behavior). Excellent for: phishing document analysis (can interact with macros), stealer malware (observe credential harvest in progress), and samples that require user interaction to detonate. Free tier: public submissions visible to all users. Paid tier: private submissions. Do not submit internal files or files containing organizational data to the free (public) tier.
Hybrid Analysis provides free automated dynamic analysis reports powered by CrowdStrike's Falcon Sandbox engine. Strong coverage for Windows PE malware and script-based threats. Free public API access allows automated submission from SOAR playbooks. Produces threat scores, MITRE ATT&CK mapping, and extracted network IOCs. Private submissions require a paid plan.
Joe Sandbox analyzes files across Windows, Linux, macOS, Android, and iOS — the broadest platform coverage. Community (free) tier provides limited analyses per day with public reports. Enterprise tier supports on-premise deployment for sensitive file analysis. Joe Sandbox excels at: cross-platform mobile malware, document exploits, and enterprise-grade behavioral analysis depth.
Cuckoo is the leading open source self-hosted sandbox. Run it in your own infrastructure for analyzing files that must not leave your environment (sensitive organizational documents suspected of being weaponized, files from high-value incidents). Setup requires technical investment: a Linux host, KVM or VirtualBox guest VMs, and configuration. Return: private analysis with no data sharing, and the ability to customize the analysis environment to match your exact OS/software configuration for higher-fidelity detonation.
Before submitting a sample, make these decisions to ensure the analysis is accurate and does not expose sensitive data. Public submissions are visible to anyone using the sandbox platform. Never submit: files that contain organizational data (a Word document with internal content), files from internal systems that would reveal infrastructure details, or anything that would benefit an attacker knowing your environment was analyzed. Private submissions (paid tier or self-hosted) are appropriate for sensitive samples. For public sandboxes: submit the binary/executable itself, not the document containing internal data it was delivered in.
Most sandboxes run in isolated environments where outbound network connections are either blocked (preventing actual C2 communication) or simulated (a fake DNS/HTTP server that responds to all requests). Full internet connectivity is available on some platforms. For analyzing C2 infrastructure and exfiltration behavior, choose a sandbox with simulated network responses — this lets the malware proceed through its network communication flow without actually connecting to attacker infrastructure.
Malware often targets specific OS versions, language settings, or installed applications. A banking trojan targeting German-language Windows 10 machines may not detonate correctly in an English-language Windows 11 sandbox. When possible, match the sandbox environment to the environment where the file was found: OS version, language, installed applications. Many sandboxes allow environment selection (Windows 7, 10, 11; Office version; browser version).
Sandbox reports contain extensive output. For triage purposes, focus on these sections first. The process tree shows which processes the malware created. Key patterns: cmd.exe or PowerShell spawned by a Word document indicates macro-based execution; a legitimate Windows binary (svchost.exe, explorer.exe) spawned as a child of an unexpected process indicates process injection; multiple child processes with random names in Temp directories indicate dropper behavior. The process tree tells you the execution chain — how the malware gets from the initial file to its active payload.
Extract all DNS queries and TCP/UDP connections from the network section. DNS queries to random-looking domains (domain generation algorithm patterns: 16-character strings of lowercase letters and numbers) indicate DGA-based C2. Connections to legitimate services (Discord CDN, Telegram API, GitHub Gist) indicate commodity malware using abuse-resistant C2 channels. These are your network IOCs — add confirmed malicious domains and IPs to your firewall blocklist and threat intelligence platform.
How does the malware survive a reboot? Common mechanisms in sandbox reports: Registry Run key creation (HKCU\Software\Microsoft\Windows\CurrentVersion\Run), scheduled task creation (schtasks.exe calls or COM-based task creation), service installation (sc.exe create), startup folder file drops (C:\Users\*\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Startup\). Each persistence mechanism corresponds to a detection rule and a remediation step.
Many first-stage samples (droppers, loaders) download and execute a second-stage payload. The sandbox shows: files written to disk, including names, paths, and hashes. Submit all hashes from dropped files to VirusTotal. If the sandbox captured the second-stage binary, analyze it in a separate submission. The dropped file list often contains the final payload — the ransomware, the RAT, or the infostealer — which has richer detection coverage than the loader.
Most modern sandboxes produce a MITRE ATT&CK technique mapping for observed behaviors. Use this to: understand the attack phases the sample covers (T1059 Command and Scripting Interpreter for macro execution; T1055 Process Injection; T1071 Application Layer Protocol for C2), identify which of your detections would have caught this (compare techniques against your detection coverage), and prioritize detection rule development for missing coverage.
Modern malware increasingly detects sandbox environments and modifies behavior — or terminates — when it believes it is being analyzed. Understanding evasion techniques helps interpret sandbox reports where detonation appears incomplete. Malware that calls Sleep() for extended periods (60 minutes or more) before executing malicious behavior evades many sandbox environments that time out at 2-5 minutes. Some sandboxes accelerate system time to trigger sleep-based evasion.
If a sandbox report shows minimal behavior for an executable that has multiple detection hits on VirusTotal, extended sleep evasion is a likely cause. Manually check the import table for Sleep or NtDelayExecution calls, or use a sandbox with time-warp capabilities. Malware that checks for mouse movement, screen resolution (VMs often have low-resolution displays), running process count (VMs have few processes), or registry keys associated with VMware/VirtualBox before executing is detecting the sandbox environment. Any.Run's interactive sandbox mitigates some of these checks by allowing mouse movement and window interaction. Hybrid-analysis results showing no network activity or no file drops on a file with multiple AV detections suggest VM detection evasion.
If sandbox analysis shows minimal activity for a file that appears suspicious: submit to multiple sandboxes (different environments evade different checks), try an interactive sandbox where you can trigger execution manually, check VirusTotal for static detections even when dynamic analysis is blank, and escalate to static analysis (examine strings, imports, and packer signatures in the file without executing it using tools like PEStudio or floss).
Malware sandbox analysis converts a suspicious file from an unknown threat to a characterized threat in under five minutes. For SOC analysts and incident responders, knowing which sandbox to use, what to submit and what not to, and which sections of the report contain actionable intelligence is a foundational skill. The free tiers of Any.Run, Hybrid Analysis, and Joe Sandbox provide production-quality analysis at no cost — the only investment is the time to learn how to read the output.
Submitting the malware binary itself to a public sandbox is generally safe — the binary executes in an isolated environment. The privacy concern is whether the submission reveals organizational information: the filename (rename samples before submission), metadata in the file, or content in the case of weaponized documents containing internal data. Do not submit internal documents, even if they are suspected of containing malware — submit only the binary payload extracted from the document, or use a private/self-hosted sandbox for document analysis.
Static analysis examines the file without executing it: inspecting strings, import tables, code disassembly, and packer signatures. Dynamic analysis (sandbox analysis) executes the file and observes behavior. Static analysis is useful when the sample evades dynamic analysis, for understanding code-level behavior, and for unpacking obfuscated samples. Dynamic analysis is faster, requires less expertise, and produces behavioral IOCs (network indicators, persistence mechanisms) directly observable without reverse engineering. Both are complementary — start with dynamic analysis for triage; use static analysis for deep investigation.
Most sandboxes offer JSON/XML export of the full report, which includes structured IOC data: IP addresses, domains, file hashes, registry keys, and YARA matches. The Any.Run API, Hybrid Analysis API, and Joe Sandbox API all support programmatic IOC extraction for integration into SOAR playbooks. For manual extraction: network section for IP/domain IOCs, dropped files section for file hash IOCs, and the registry/persistence section for endpoint detection IOCs. Add confirmed IOCs to your threat intelligence platform and SIEM blocklists within 2 hours of analysis.
25 actively exploited vulnerabilities with CVSS scores, exploit status, and patch availability. Print it, pin it, share it with your SOC team. Step-by-step 24-hour IR checklist covering detection, containment, eradication, and recovery. Built for SOC teams, IR leads, and CISOs.
50,000+ security professionals read Decryption Digest for early warnings on zero-days, ransomware, and nation-state campaigns. Free, daily, no spam. Harvested Online Documentation & Reference Sources • https://ammarlouah.github.io/posts/dynamic-malware-analysis-using-ai-agent-and-reinforcement-learning/ • https://github.com/Loksharan-soc/Malware-Analysis-Lab • https://lancegrover.com/malware-analysis-sandbox/ • https://github.com/cyph3rryx/Malware-Detection-System • https://forensicspot.com/topics/cyber-forensics/dynamic-malware-analysis • https://www.decryptiondigest.com/blog/malware-sandbox-analysis-dynamic-behavior-any-run-cuckoo-guide
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Malware Dynamic Analysis Using Sandbox And Machine Learning.
[*] Metasploit Scan Running on Target Subnet for Malware Dynamic Analysis Using Sandbox And Machine Learning... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |